Upgrade to Pro — share decks privately, control downloads, hide ads and more …

Using Python to Fight Cybercrime

Sponsored · Ship Features Fearlessly Turn features on and off without deploys. Used by thousands of Ruby developers. →

Using Python to Fight Cybercrime

A survey of the ways I use Python as a DFIR / threat intel professional

Kyle Maxwell

April 26, 2015

Transcript

18 slides
  1. Using Python to Fight Cybercrime Kyle Maxwell, PyData Dallas April

    26, 2015 @kylemaxwell http://goo.gl/oPQ8k2
  2. Triage Malware What is it? ➔ hashing ➔ IOC matching

    What does it do? ➔ behavioral analysis
  3. Manage Malware Maltrieve [ maltrieve.org ] ➔ web crawler to

    fetch malware Viper [ viper.li ] ➔ store and classify malware
  4. Cuckoo Sandbox [ cuckoosandbox.org ] “Throw any suspicious file at

    it and in a matter of seconds Cuckoo will provide you back some detailed results outlining what such file did when executed inside an isolated environment.” Analyze Malware
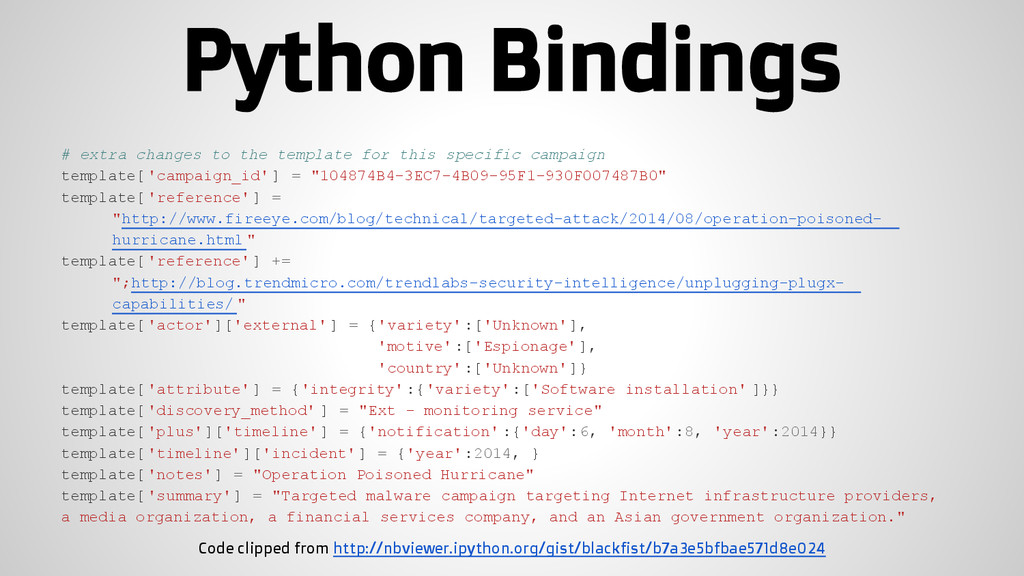
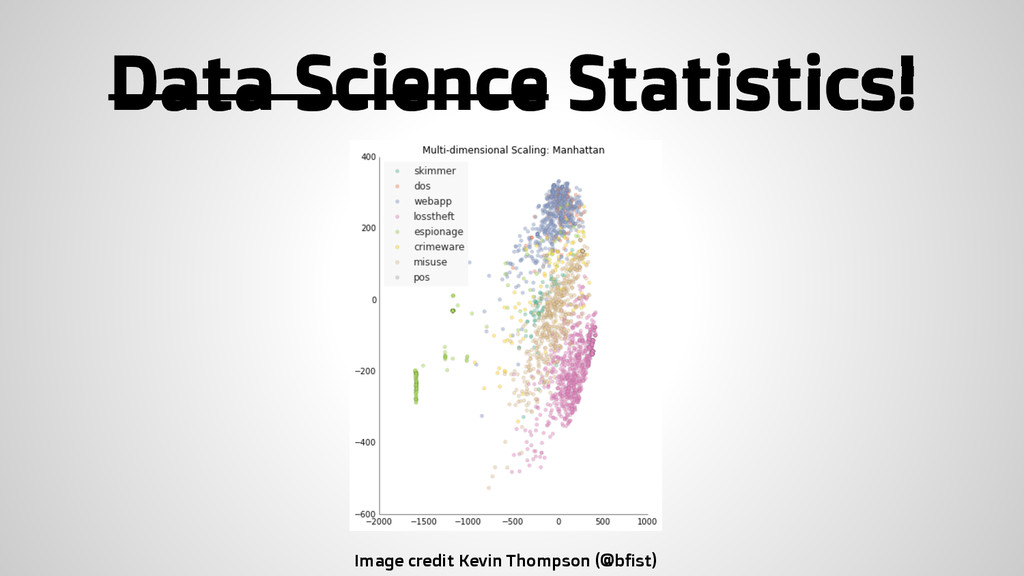
  5. Python Bindings # extra changes to the template for this

    specific campaign template['campaign_id' ] = "104874B4-3EC7-4B09-95F1-930F007487B0" template['reference' ] = "http://www.fireeye.com/blog/technical/targeted-attack/2014/08/operation-poisoned- hurricane.html " template['reference' ] += ";http://blog.trendmicro.com/trendlabs-security-intelligence/unplugging-plugx- capabilities/ " template['actor']['external'] = {'variety':['Unknown'], 'motive':['Espionage' ], 'country':['Unknown']} template['attribute' ] = {'integrity' :{'variety':['Software installation' ]}} template['discovery_method' ] = "Ext - monitoring service" template['plus']['timeline'] = {'notification' :{'day':6, 'month':8, 'year':2014}} template['timeline']['incident'] = {'year':2014, } template['notes'] = "Operation Poisoned Hurricane" template['summary'] = "Targeted malware campaign targeting Internet infrastructure providers, a media organization, a financial services company, and an Asian government organization." Code clipped from http://nbviewer.ipython.org/gist/blackfist/b7a3e5bfbae571d8e024
  6. So much else! ➔ Log analysis ➔ Web interfaces ➔

    Forensic examinations ➔ Red teaming / pentesting
  7. Q&A @kylemaxwell || xwell.org github.com/krmaxwell Icons made by Freepik from

    www.flaticon.com and used under Creative Commons license

More Decks by Kyle Maxwell

Other Decks in Technology