Share
Embed
Transcript
25 slides
-
Incident Patterns Kevin Thompson, Verizon Kyle Maxwell, Verisign SANS DFIR
Summit 2014 Daniel Greis -
Agenda ➔ Who we are and what this is ➔
Data Alchemy ➔ Patterns: TTPs and Countermeasures ➔ Conclusions and Q&A anarchosyn -
About us Kevin is a data alchemist for Verizon with
a background in risk management. Kyle is a malware researcher for Verisign with a background in Unix and incident response. Sam Shennan -
Confidential and proprietary materials for authorized Verizon personnel and outside
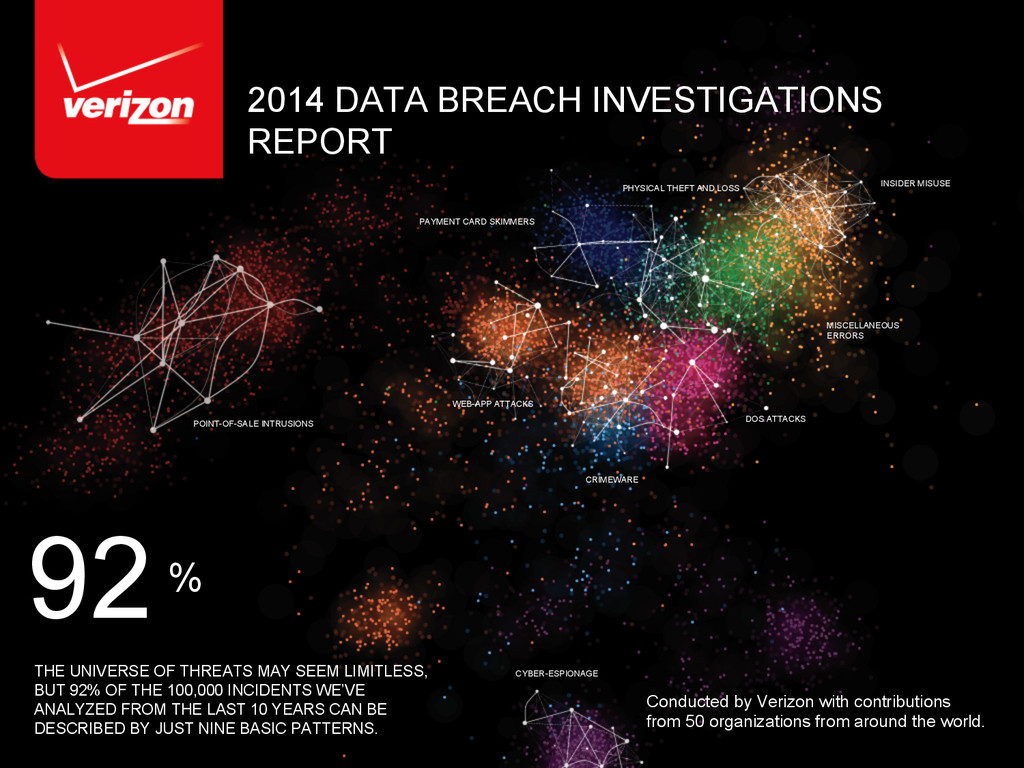
agencies only. Use, disclosure or distribution of this material is not permitted to any unauthorized persons or third parties except by written agreement. MAIN REPORT 2014 DATA BREACH INVESTIGATIONS REPORT 92 THE UNIVERSE OF THREATS MAY SEEM LIMITLESS, BUT 92% OF THE 100,000 INCIDENTS WE’VE ANALYZED FROM THE LAST 10 YEARS CAN BE DESCRIBED BY JUST NINE BASIC PATTERNS. Conducted by Verizon with contributions from 50 organizations from around the world. POINT-OF-SALE INTRUSIONS WEB-APP ATTACKS PAYMENT CARD SKIMMERS CRIMEWARE DOS ATTACKS INSIDER MISUSE PHYSICAL THEFT AND LOSS CYBER-ESPIONAGE % MISCELLANEOUS ERRORS -
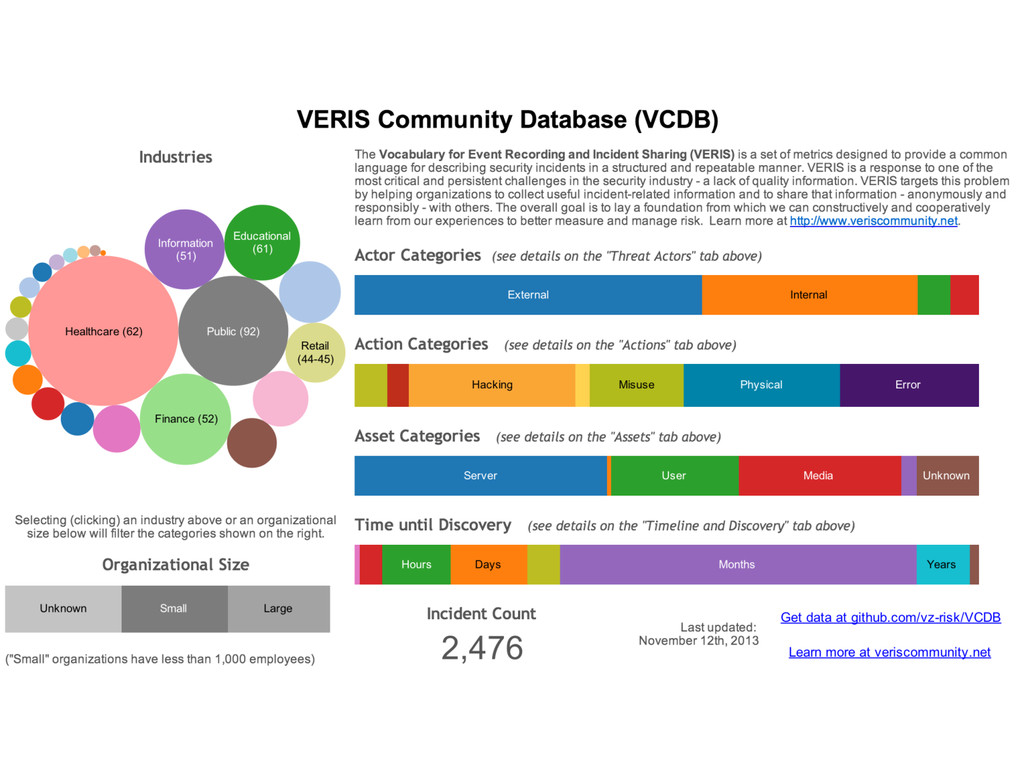
Powered by VERIS Both DBIR and VCDB use VERIS to
model incidents. Vocabulary for Event Recording and Incident Sharing duncan c -
Powered by VERIS ➔ Models ORGANIZATION incidents ➔ Strategic ➔
After-action ➔ Creative Commons license duncan c -
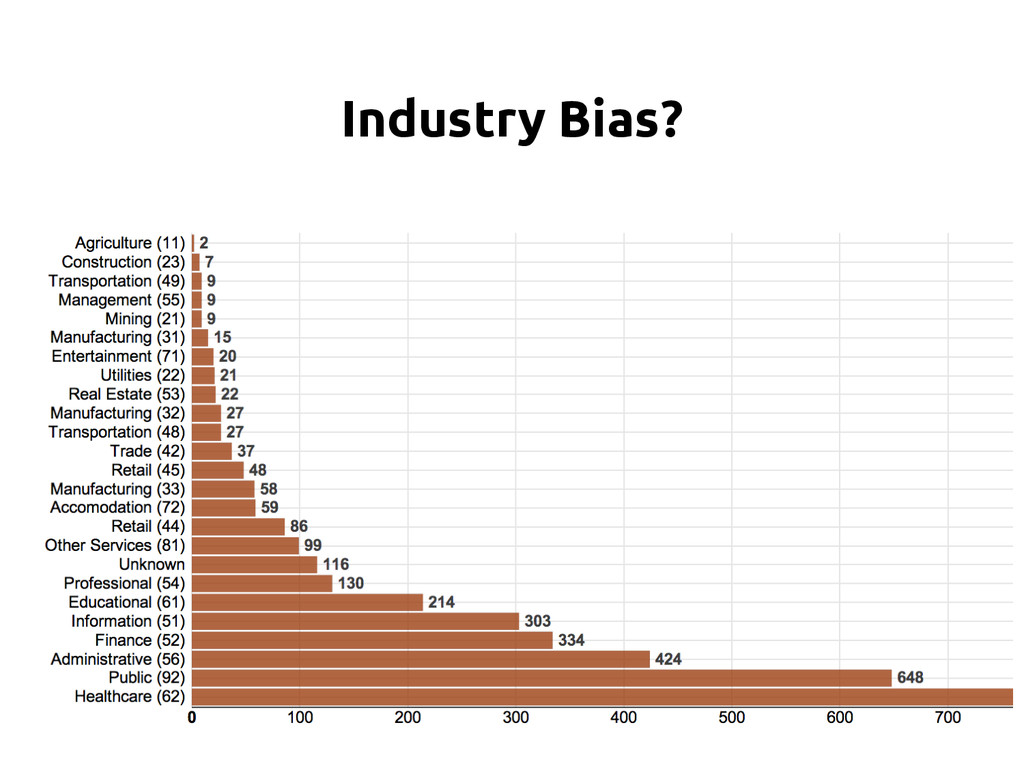
Sample bias & limitations ➔ Public sources ➔ Not every
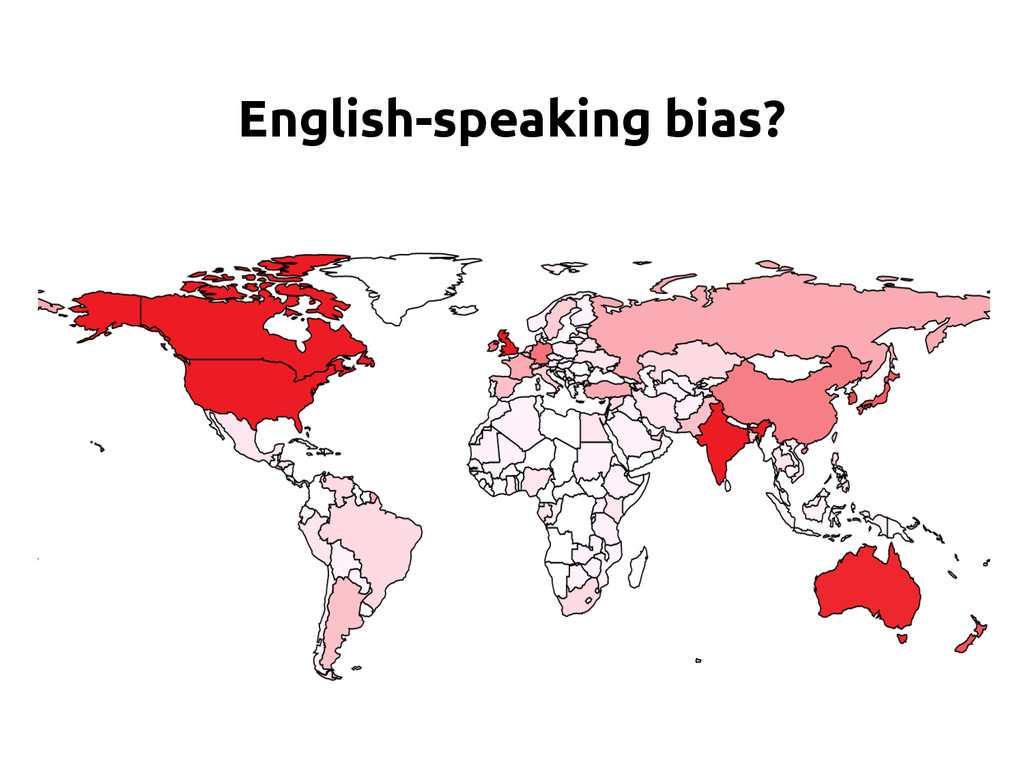
reporter is Krebs ➔ English-speaking ➔ Sparse data (high unknowns for some attributes) Franco Folini -
➔ Ran Somewhere ➔ I Spy ➔ Snow Job Others
exist in the data but not necessarily interesting for the DFIR Summit (lost laptops) Patterns to examine McKay Savage -
Pattern: Ran somewhere action.malware.variety == ‘Ransomware’ or action.malware.variety == ‘Destroy
data’ Summary: ➔ 19 incidents ➔ Primarily Cryptolocker ➔ Email vector in 13 of these ➔ Reaches out to C2 server in 5 incidents steve_l / Banksy -
Pattern: Ran somewhere Countermeasures: ➔ Examine / block executable attachments
➔ Perform regular endpoint backups ➔ Intelligence on C2 addresses ➔ Many DNS queries (NXDOMAIN results) steve_l / Banksy -
Pattern: I Spy Matt Biddulph actor.external.motive == ‘Espionage’ Summary: ➔
199 publicly-described incidents ➔ Primarily South Korea, USA, Russia ➔ Majority of public data from Red October, MiniDuke, and Kimsuky (thanks Kaspersky!) -
Pattern: I Spy TTP: ➔ Targeted phishing via email ➔
Strategic web compromise (watering hole) ➔ Attachment or web page exploits vuln ➔ Drop local malware ➔ Connect to C2 (often resilient) ➔ Locate and exfiltrate data from internal net Matt Biddulph -
Pattern: I Spy Countermeasures: ➔ Stop using email for file
sharing ➔ Look for attachments from “new” outside addresses ➔ Examine attachments in a hardened sandbox ➔ Seriously: Adobe? Java? In 2014? ➔ Monitor endpoints for exploitation & disabled security ➔ EMET prevents many of these null-days ➔ Targeted sectors need to develop lots of threat intel, possibly with external providers Matt Biddulph -
Pattern: Snow Job actor == ‘Internal’ and action == ‘Misuse’
Summary: ➔ 477 incidents (note that Error is excluded) ➔ Known motives overwhelmingly financial Chris Hartman -
Pattern: Snow Job TTP: ➔ Vector: LAN or physical access
➔ Variety usually “Privilege abuse”, followed by “knowledge” and “possession” abuses ➔ Largely tax return fraud Chris Hartman -
Pattern: Snow Job Countermeasures: ➔ Challenge: user has legitimate access
➔ Audit log review is tough, ask the NSA! ➔ Beware snake oil “anomaly” solutions ➔ Targeted analysis of specific use cases ➔ Monitor for social media disclosures Chris Hartman -
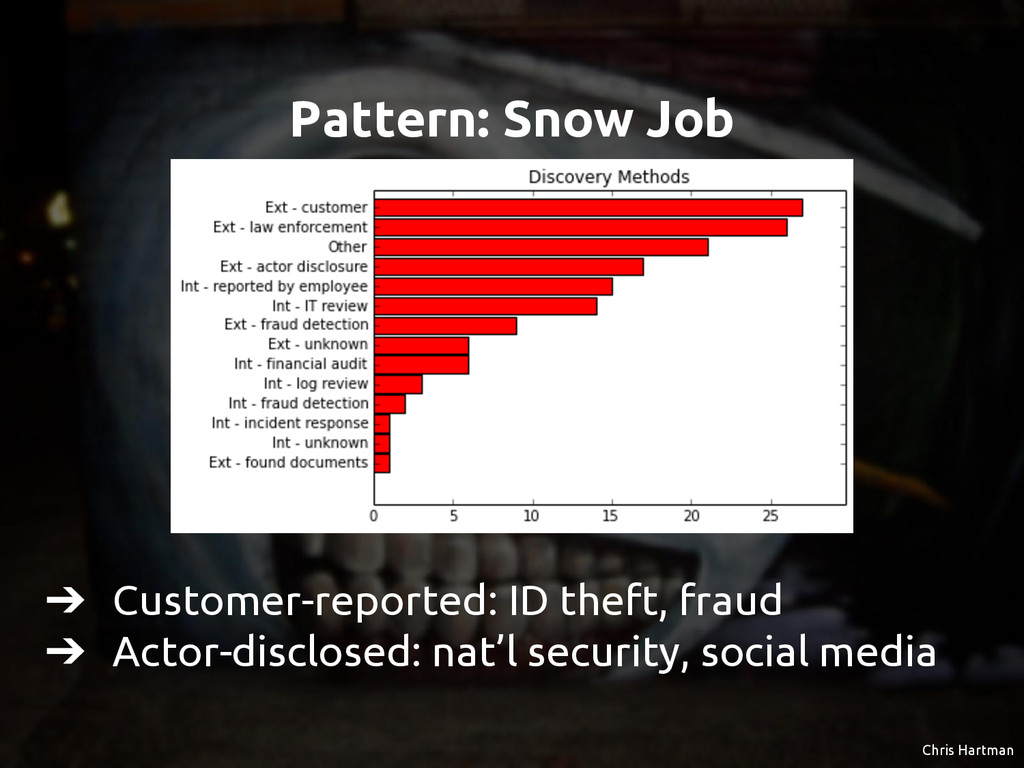
Pattern: Snow Job Chris Hartman ➔ Customer-reported: ID theft, fraud
➔ Actor-disclosed: nat’l security, social media -
But wait, there’s more! http://threatic.us/incident-patterns/ Full data and IPython notebooks
for reproducibility and collaboration Michael Coghlan -
Your gift of a few contributions... ...can help a “starving”
data scientist.