Share
Embed
Switching the LDAP from Domino to Active Directory in Connections without nightmares
You may encounter that the LDAP used will be replaced by a different technology and you want to perform that without data loss. We will present you details of switching Connections on-premise from Domino LDAP to AD LDAP for 130.000 users. What are the pre-requisites and which steps have to be taken during the migration? Failure is not an option.
LetsConnect
September 17, 2019
Transcript
33 slides
-
Switching the LDAP from Domino to Active Directory in Connections
without nightmares Andreas Weinbrecht, Martin Schmidt Beck et al. GmbH @beck_et_al -
Social Connections 15 Munich, September 16-18 2019 Andreas Weinbrecht Account
Manager [email protected] Martin Schmidt Senior IT Architect [email protected] -
Social Connections 15 Munich, September 16-18 2019 ConNext - ESN
based on HCL Connections • Implementation in 2013 • Beck et al. as implementation partner and provider • Adoption Rate • More than 130.000 enabled profiles • More than 70.000 unique users per week • Success • Easy access – everyone is enabled • Keep colleagues on the same page • Share ideas, knowledge and experience faster • Connect with people and teams across the organization • Find experts faster • Information can go viral -
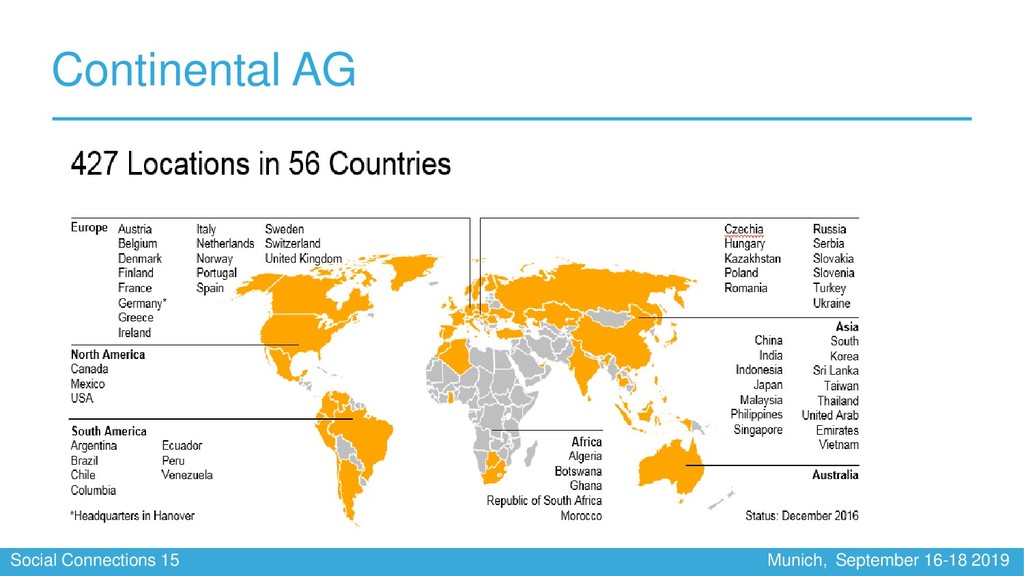
Social Connections 15 Munich, September 16-18 2019 Beck et al.
and Continental -
Social Connections 15 Munich, September 16-18 2019 Why switching from
Domino LDAP to AD? -
Social Connections 15 Munich, September 16-18 2019 Domino is no
longer single source of truth • Customer has switched its messaging system from IBM Domino to MS O365 • Domino accounts should only exist for access to Domino applications • No need for Single-Sign-On setup anymore -
Social Connections 15 Munich, September 16-18 2019 Corporate Phonebook as
data broker • Corp. Phonebook is a Domino application • Corp. Phonebook is getting its data from Domino Directories, SAP GHR and user updates • Corp. Phonebook is the source for many systems including Connections • Data available in Corp. Phonebook and required for Connections need to be available in Active Directory -
Social Connections 15 Munich, September 16-18 2019 Data required for
Connections • Schema Extension required in AD for • Contact Address (not maintained in SAP GHR) • Manager Information (hierarch. and functional) • Dedicates attributes used in Connections backend • New process to be established for updating the contact address and manager information -
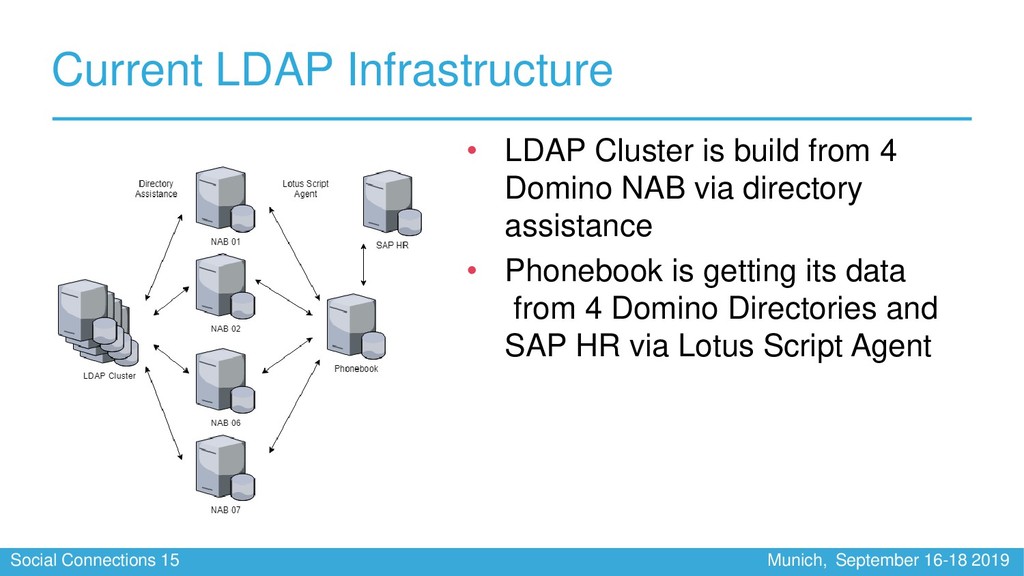
Social Connections 15 Munich, September 16-18 2019 Current LDAP Infrastructure
• LDAP Cluster is build from 4 Domino NAB via directory assistance • Phonebook is getting its data from 4 Domino Directories and SAP HR via Lotus Script Agent -
Social Connections 15 Munich, September 16-18 2019 Future LDAP Infrastructure
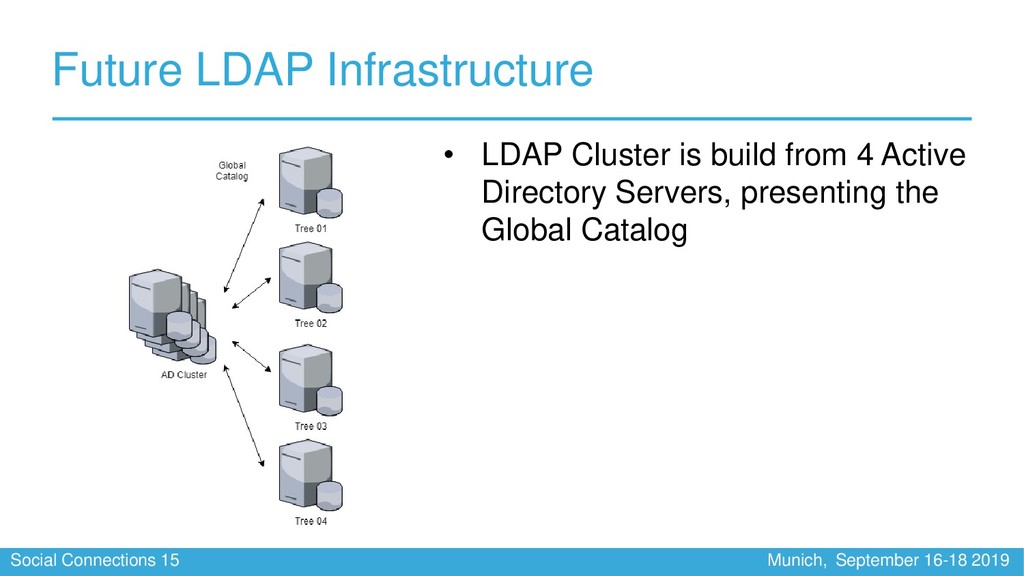
• LDAP Cluster is build from 4 Active Directory Servers, presenting the Global Catalog -
Social Connections 15 Munich, September 16-18 2019 Current Authentication and
Profile Data • Authentication against Domino LDAP Cluster • Profiles Data from Phonebook via TDI • Phonebook due to Attributes not in Domino NAB • Custom TDI AL as Notes Change Connector is used • Extension Attributes are heavily used • SSO with Active Directory is possible - match of Domino Short Name - samAccountName required -
Social Connections 15 Munich, September 16-18 2019 Future Authentication and
Profile Data • Authentication against Active Directory LDAP Cluster - Global Catalog • Profiles Data from Active Directory via TDI • Schema Extenstion due to attributes not in standard AD User. -
Social Connections 15 Munich, September 16-18 2019 People DB -
Technical Keys • PROF_KEY - Internal Key, Instance specific • PROF_UID - Organization Key, LDAP unique • PROF_MAIL - Organization Key, LDAP unique • PROF_GUID - LDAP Key, LDAP unique • PROF_LOGIN - Organization Key, LDAP unique • PROF_SOURCE_UID - LDAP, LDAP unique • PROF_SOURCE_URL - TDI, Source LDAP -
Social Connections 15 Munich, September 16-18 2019 Profiles Configuration •
https://xxx.beaslabs.com/profiles/html/profileView.do?userid=2E96885470B 28BBCC1258412003840B1 • profiles-config.xml <!-- Directory integration configuration --> <directory> <!-- Specifies the profiles field that is used to resolve person records via WALTZ / Javelin --> <lconnUserIdField>guid</lconnUserIdField> <!-- Lists fields that will be used to resolve user at login time --> <loginAttributes> <loginAttribute>email</loginAttribute> <loginAttribute>uid</loginAttribute> <loginAttribute>loginId</loginAttribute> </loginAttributes> </directory> • https://www.ibm.com/support/knowledgecenter/en/SSYGQH_6.0.0/admin/a dmin/t_admin_profiles_manage_users.html -
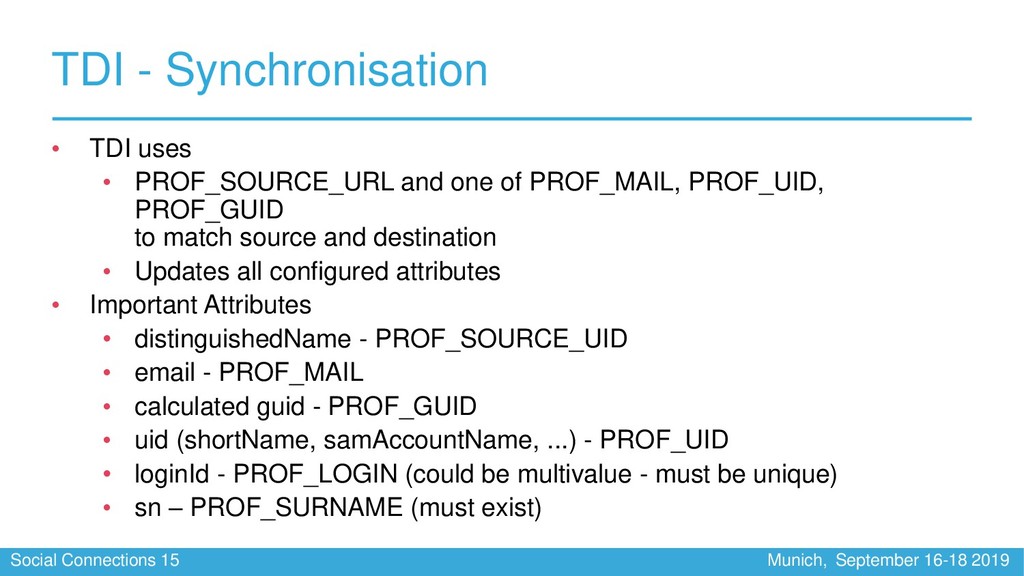
Social Connections 15 Munich, September 16-18 2019 TDI - Synchronisation
• TDI uses • PROF_SOURCE_URL and one of PROF_MAIL, PROF_UID, PROF_GUID to match source and destination • Updates all configured attributes • Important Attributes • distinguishedName - PROF_SOURCE_UID • email - PROF_MAIL • calculated guid - PROF_GUID • uid (shortName, samAccountName, ...) - PROF_UID • loginId - PROF_LOGIN (could be multivalue - must be unique) • sn – PROF_SURNAME (must exist) -
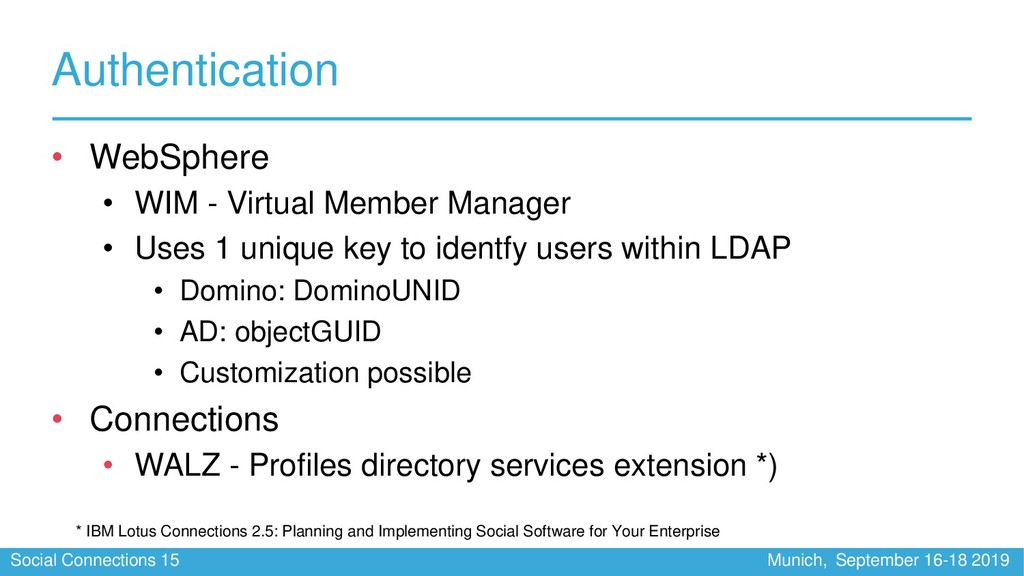
Social Connections 15 Munich, September 16-18 2019 Authentication • WebSphere
• WIM - Virtual Member Manager • Uses 1 unique key to identfy users within LDAP • Domino: DominoUNID • AD: objectGUID • Customization possible • Connections • WALZ - Profiles directory services extension *) * IBM Lotus Connections 2.5: Planning and Implementing Social Software for Your Enterprise -
Social Connections 15 Munich, September 16-18 2019 LDAP Switch Documentation
• Updating Profiles when changing LDAP directory https://www.ibm.com/support/knowledgecenter/en/SSYGQH_6.0.0/admin/admin/t_admin_profiles_change_ldaps.html • Change LDAP directory syncing with Connections https://www.ibm.com/developerworks/community/blogs/4021cbfe-77ed-4a39-89de- 59b2fd63adb5/entry/change_ldap_directory_syncing_with_connections?lang=en • Social Connections 9: https://de.slideshare.net/soccnx/managing-ldap-changes-in-connections-54924817 • Specifying a custom ID attribute for users or groups: https://www.ibm.com/support/knowledgecenter/en/SSYGQH_6.0.0/admin/install/t_specify_dif_guid.html -
Social Connections 15 Munich, September 16-18 2019 Other information regarding
LDAP • IBM Connections using Active Directory and Nested Groups http://www.infoware.eu/ibm-connections-using-active-directory-and-nested- groups • Christoph Stoettner (panagenda) My presentations at IBM Connect 2016 https://stoeps.de/my-presentations-at-ibm-connect-2016/ -
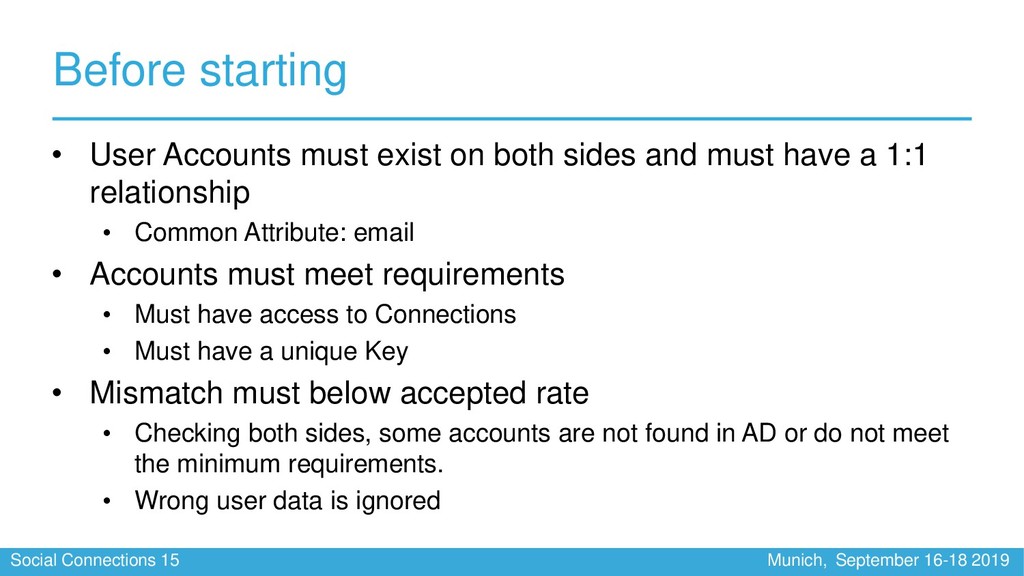
Social Connections 15 Munich, September 16-18 2019 • User Accounts
must exist on both sides and must have a 1:1 relationship • Common Attribute: email • Accounts must meet requirements • Must have access to Connections • Must have a unique Key • Mismatch must below accepted rate • Checking both sides, some accounts are not found in AD or do not meet the minimum requirements. • Wrong user data is ignored Before starting -
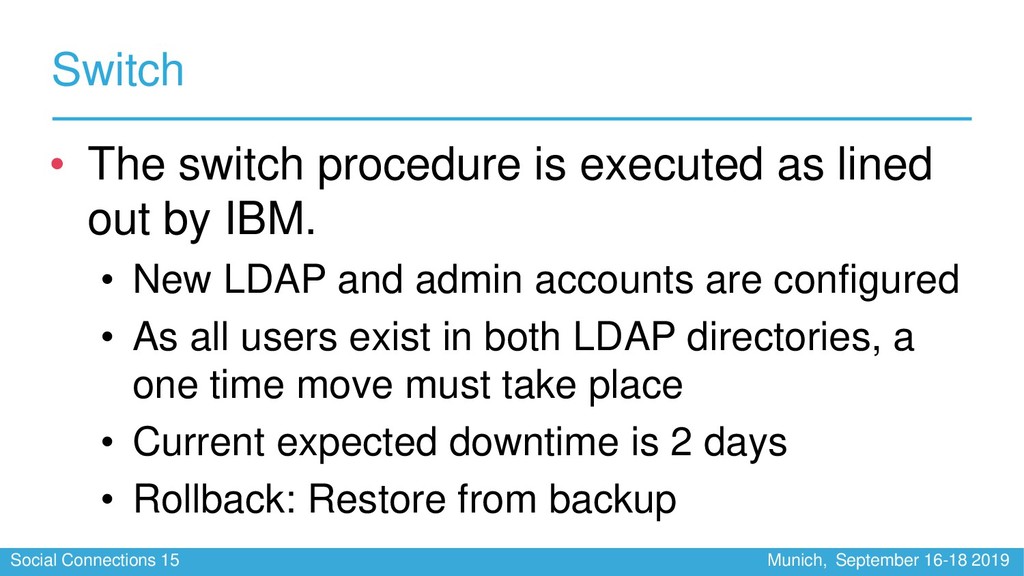
Social Connections 15 Munich, September 16-18 2019 Switch • The
switch procedure is executed as lined out by IBM. • New LDAP and admin accounts are configured • As all users exist in both LDAP directories, a one time move must take place • Current expected downtime is 2 days • Rollback: Restore from backup -
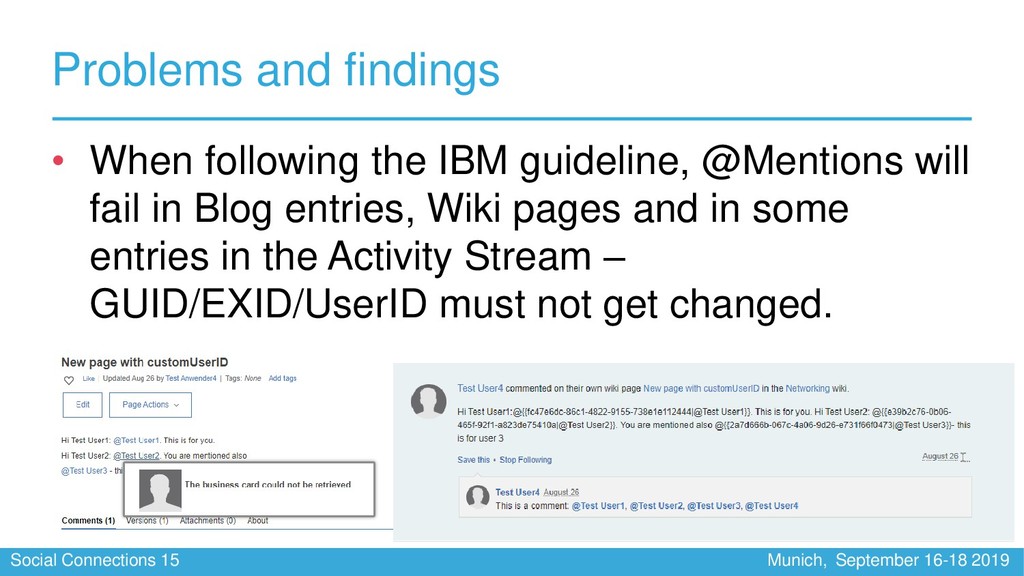
Social Connections 15 Munich, September 16-18 2019 Problems and findings
• When following the IBM guideline, @Mentions will fail in Blog entries, Wiki pages and in some entries in the Activity Stream – GUID/EXID/UserID must not get changed. -
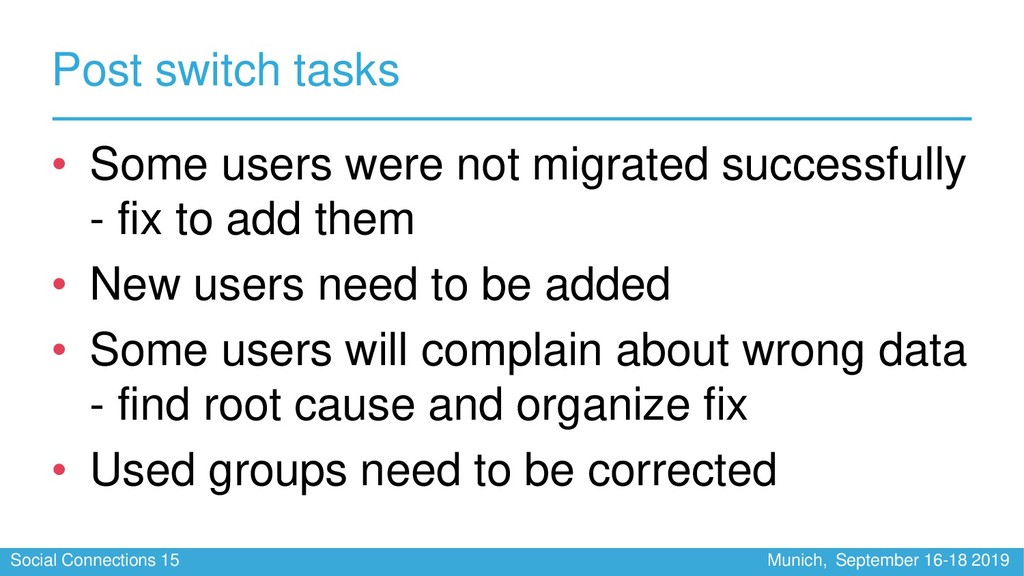
Social Connections 15 Munich, September 16-18 2019 Post switch tasks
• Some users were not migrated successfully - fix to add them • New users need to be added • Some users will complain about wrong data - find root cause and organize fix • Used groups need to be corrected