SiteGround - Reliable hosting with speed, security, and support you can count on.
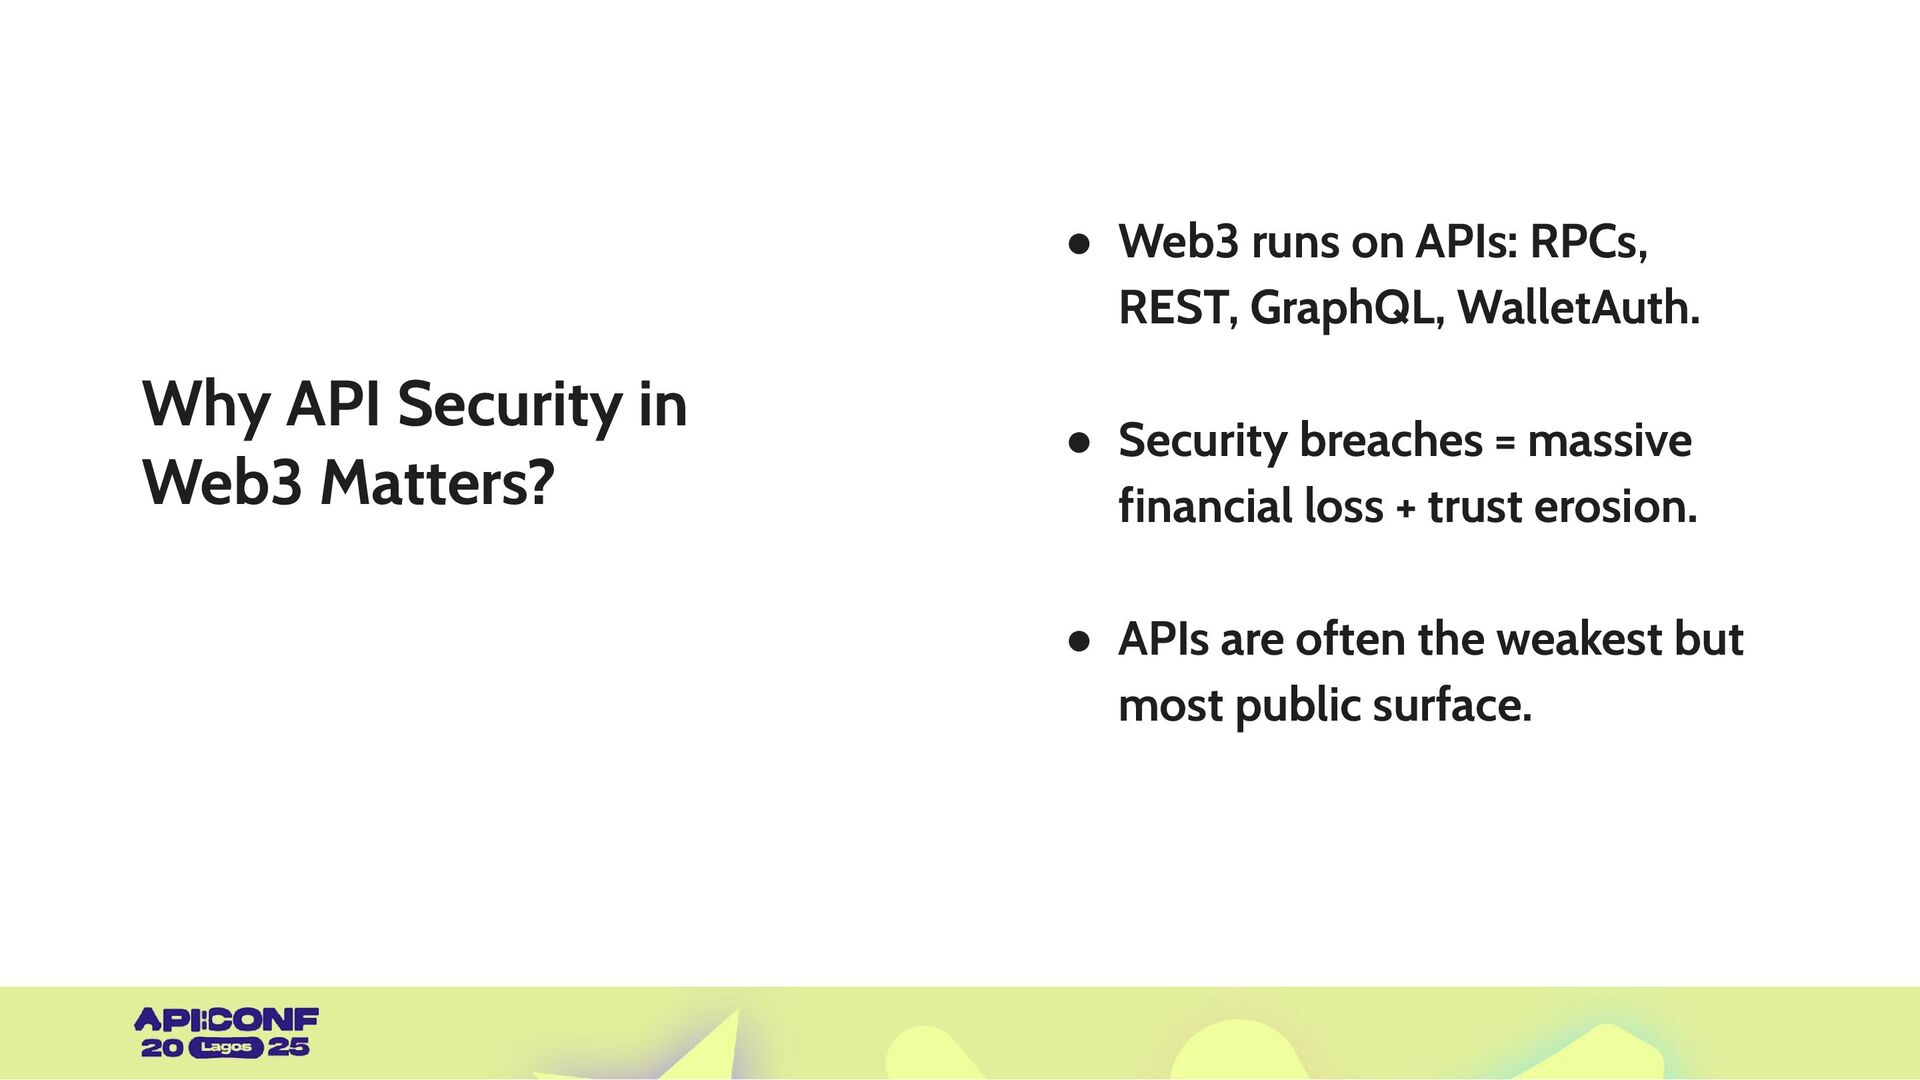
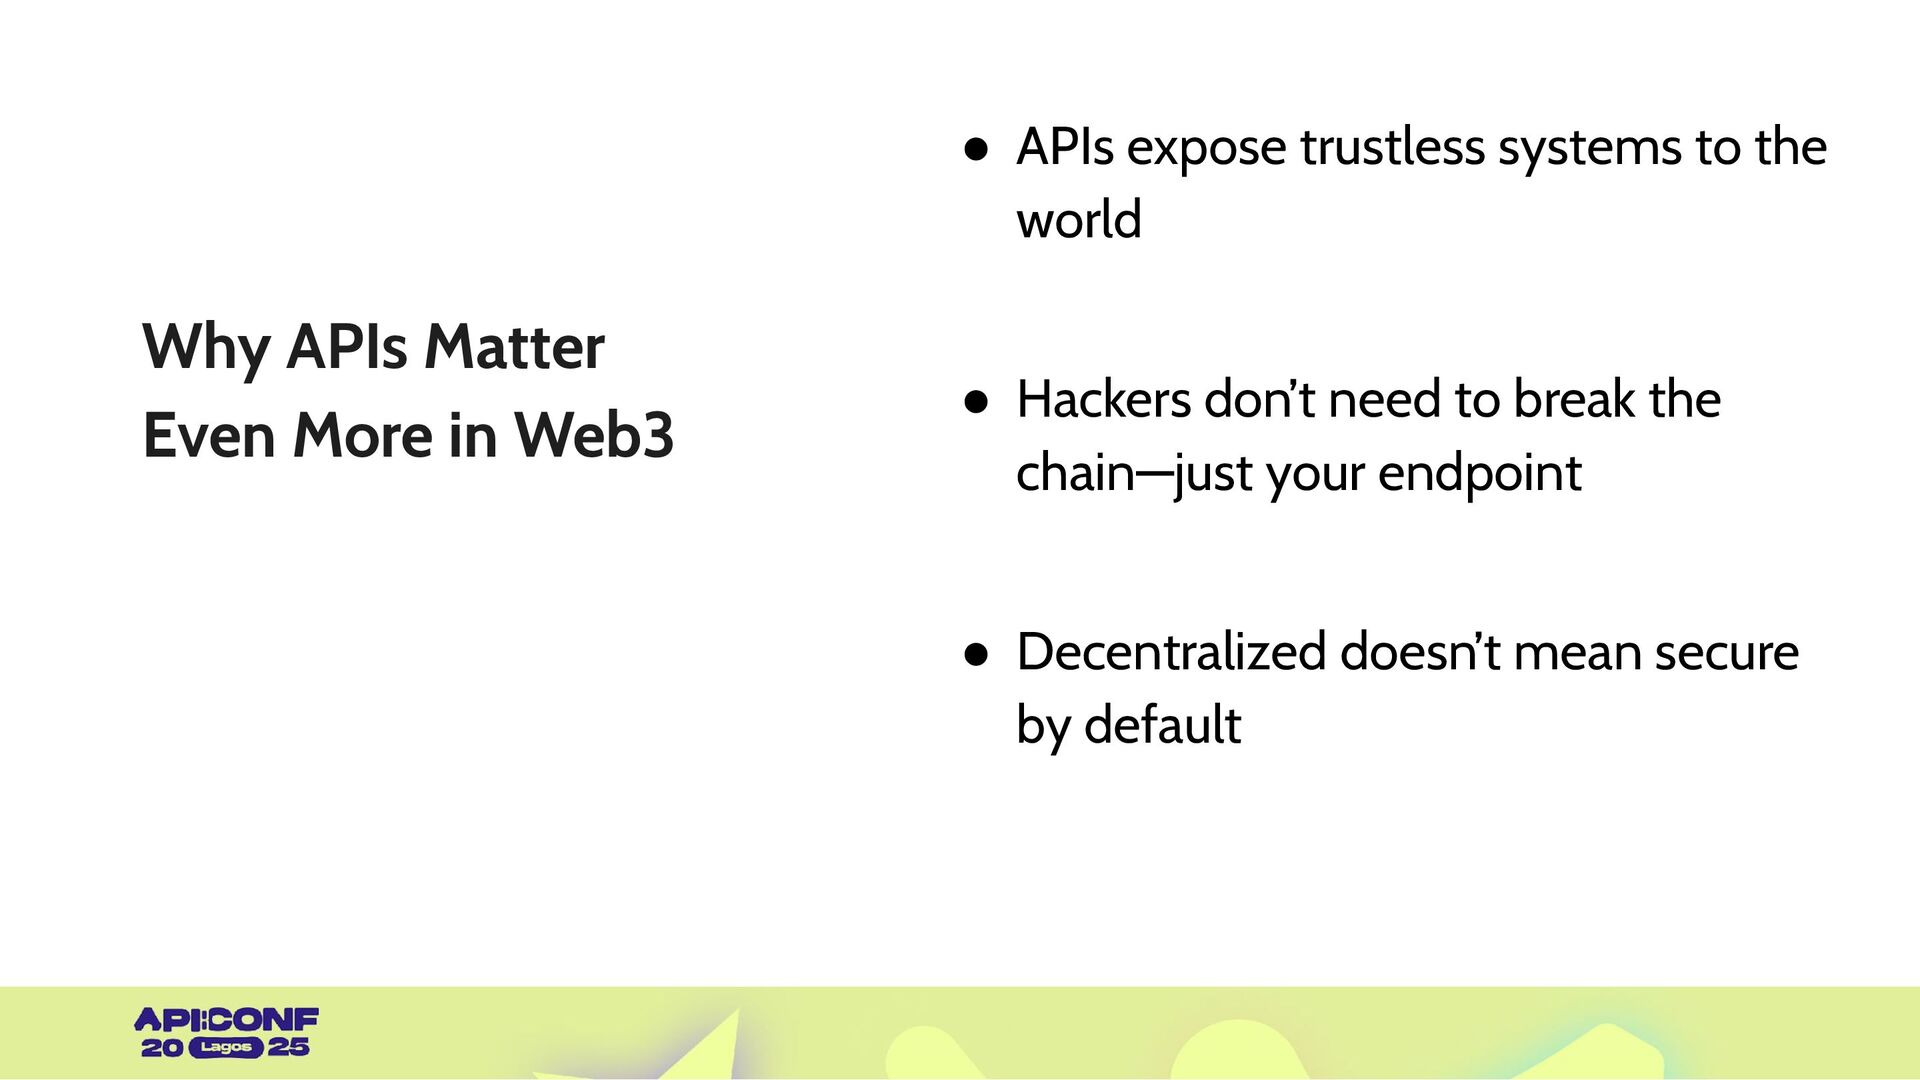
In this lightning talk, Daniel Anomfueme (Technical Project Manager & Web3 tinkerer) unpacks the critical importance of API security in decentralized applications. While blockchains themselves may be secure, the APIs that connect wallets, dApps, and bridges often become the weakest, and most exposed, attack surface.
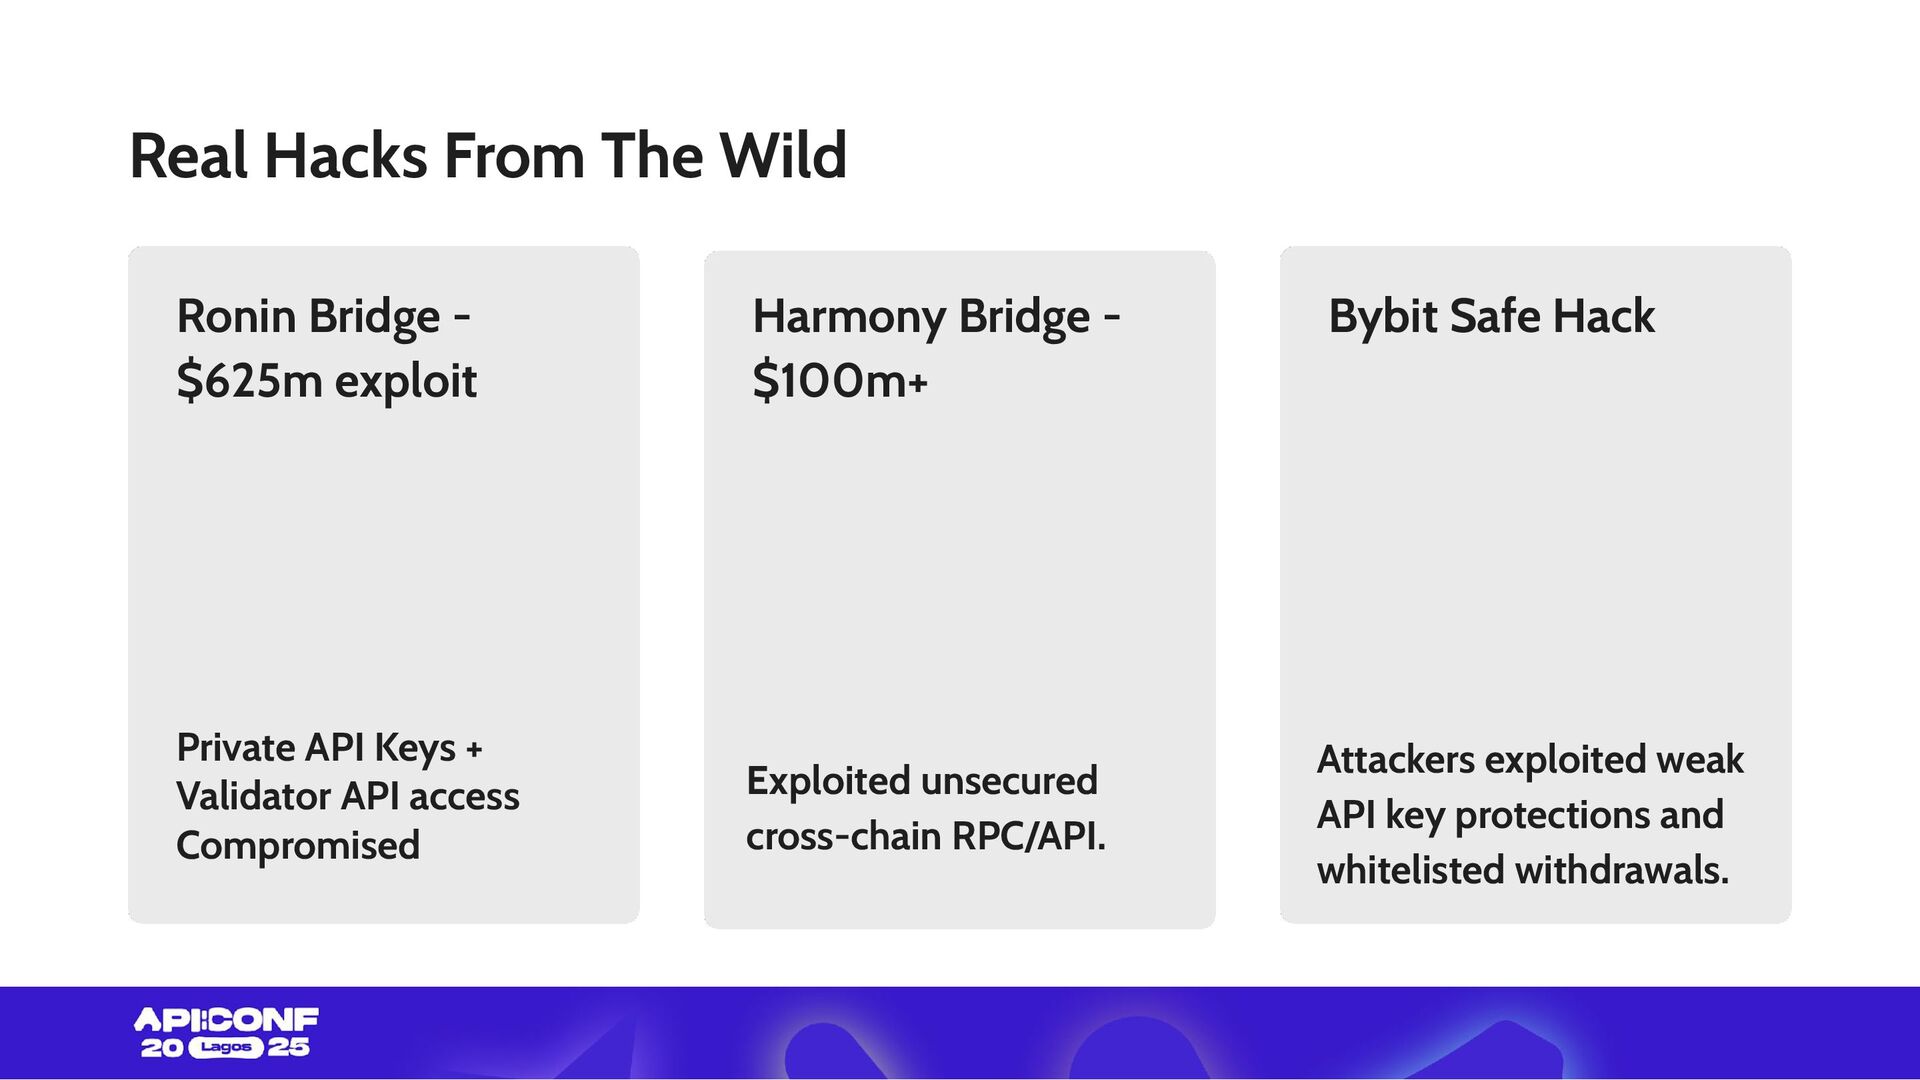
Daniel walks through real-world Web3 hacks including the Ronin Bridge exploit ($625M), Harmony Bridge ($100M+), and Bybit Safe API compromise, showing how attackers exploited unsecured endpoints, exposed keys, and weak access controls.
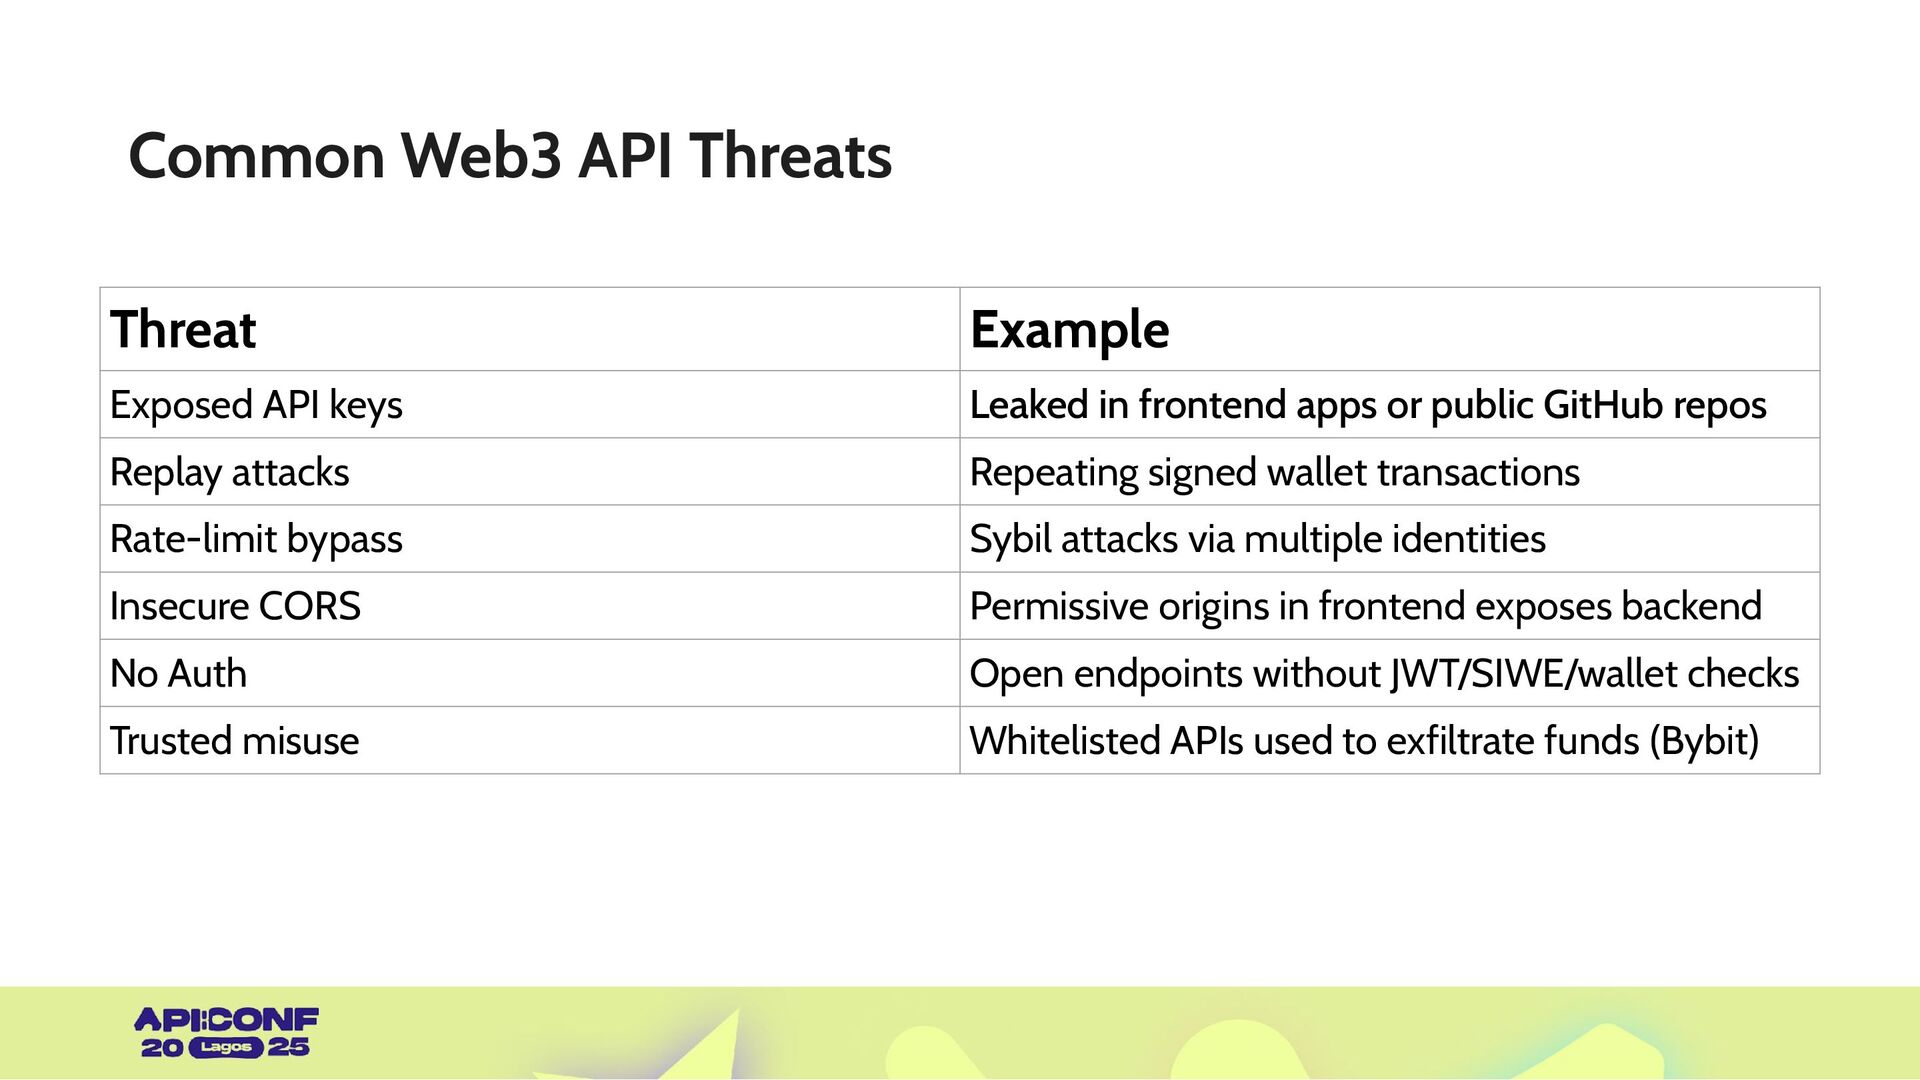
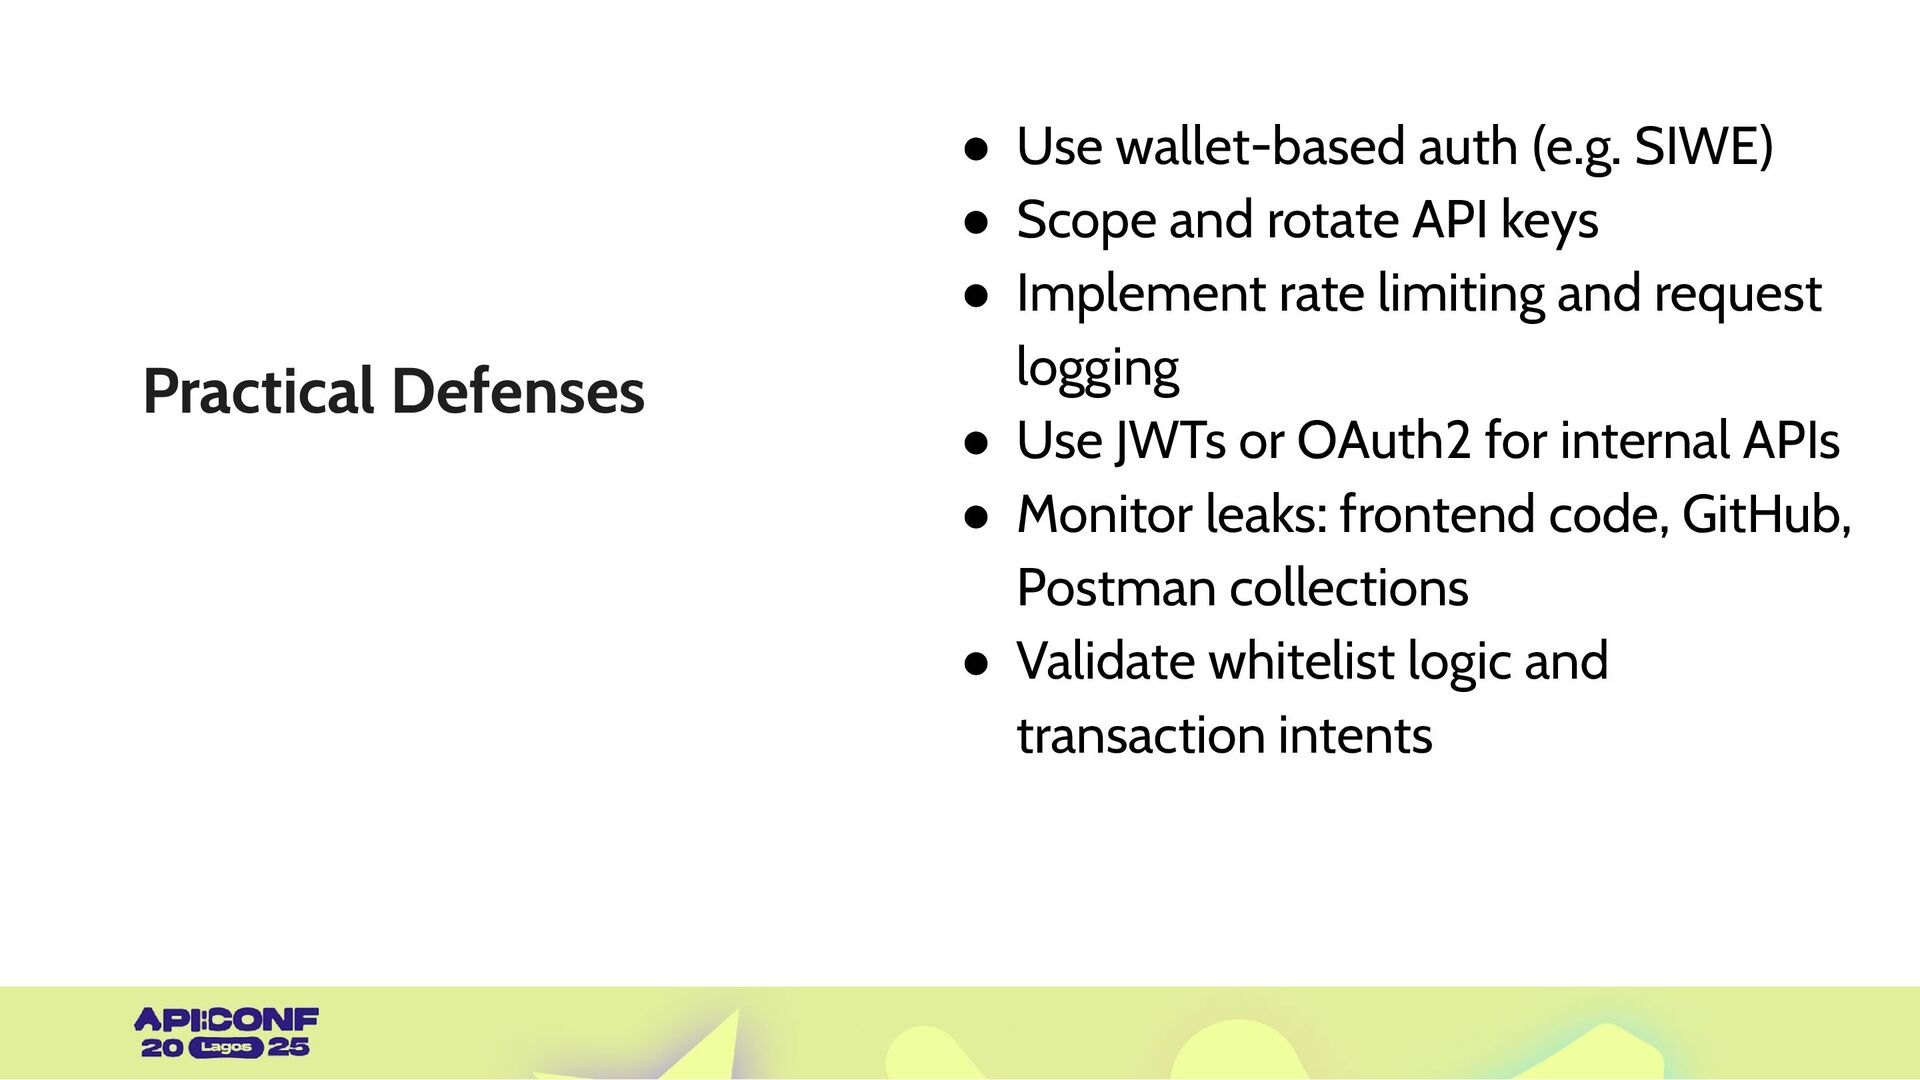
The talk identifies common Web3 API threats such as leaked keys, replay attacks, insecure CORS, rate-limit bypasses, and trusted misuse. Daniel then shares practical defenses, from wallet-based authentication (SIWE) to scoped/rotated API keys, JWT/OAuth2 enforcement, rate limiting, and active monitoring for leaks.
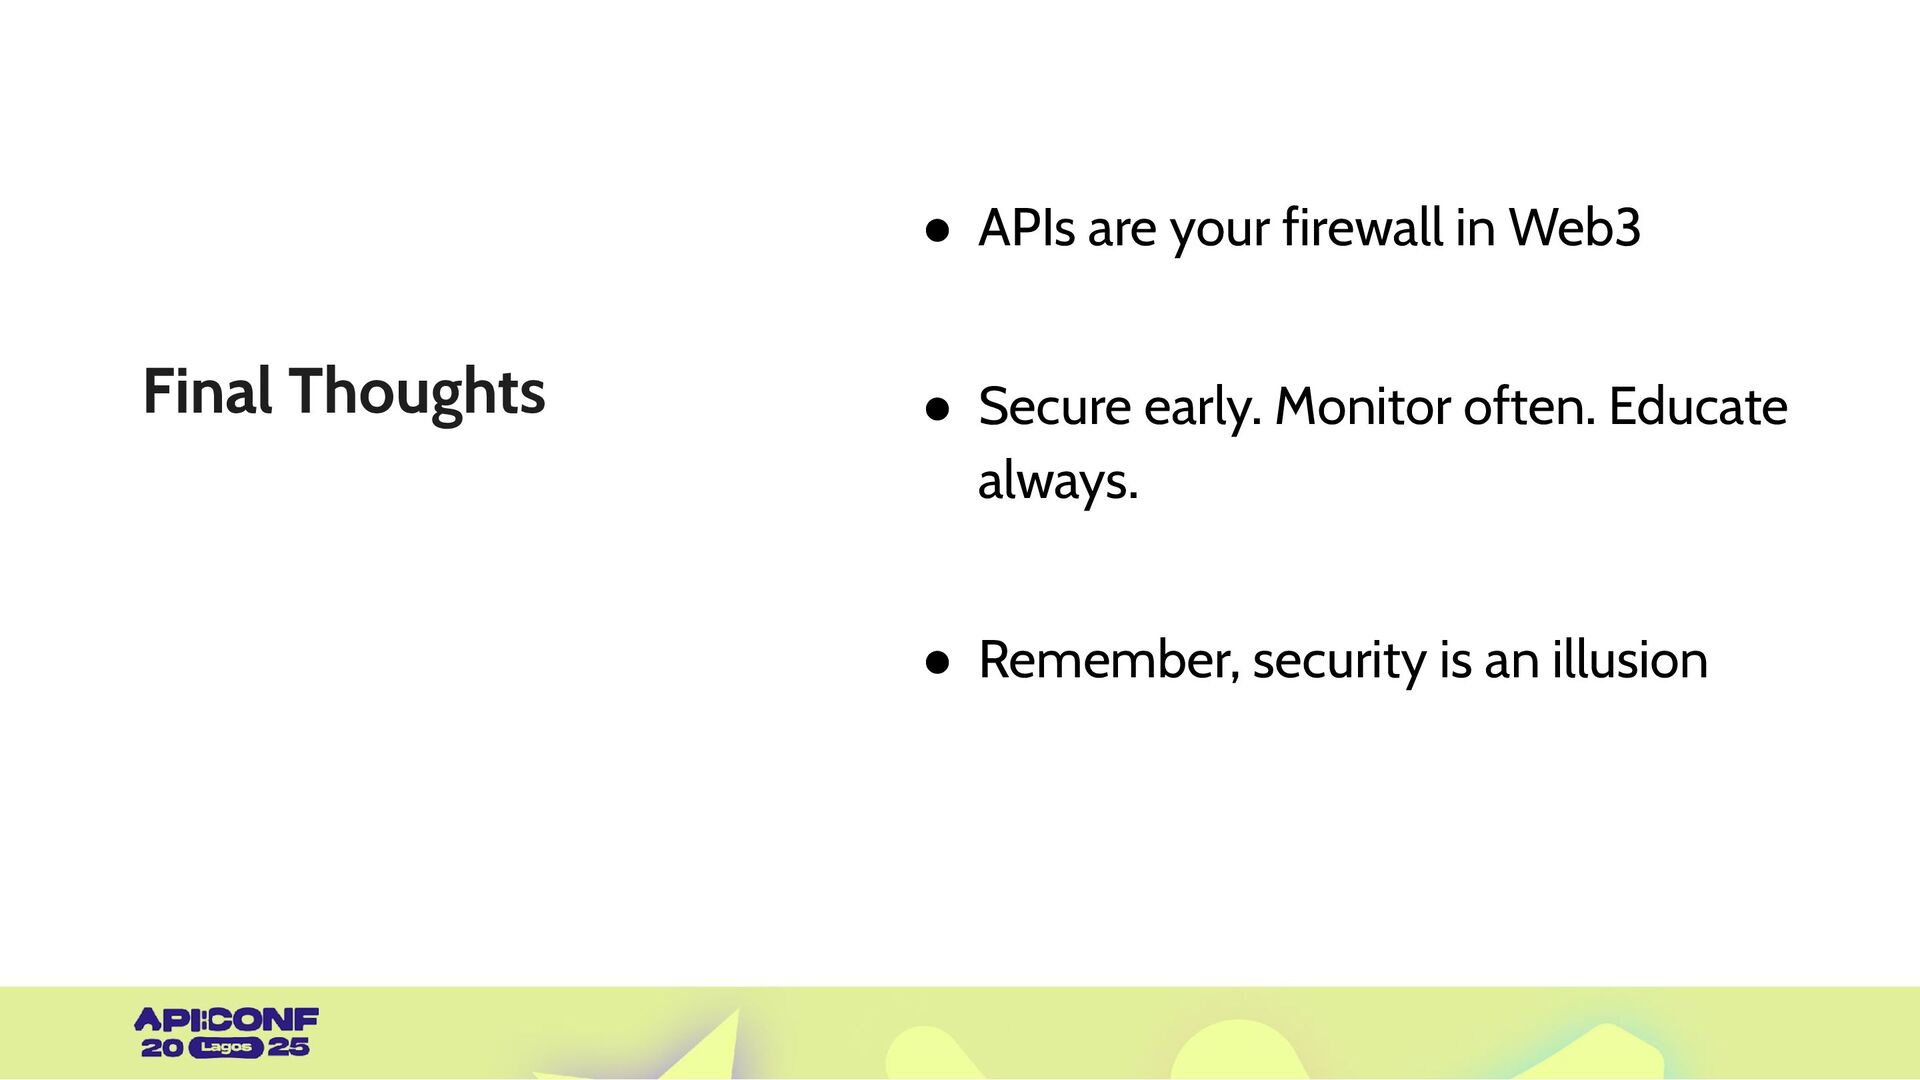
For builders, security researchers, and anyone working in Web3 infrastructure, this session is a concise but powerful guide to protecting APIs, the true firewall of decentralized systems.


 lifeofdan_el
 satoshi7
 camiha
 mohab1
 iktakahiro
 occhi
 bgpat
 bitkey
 namiki64
 nealle
 mhrtech
 moznion
 orderedlist
 productmarketing
 aleyda
 charlesmeaden
 hannesfritz
 techseoconnect
 tmiket
 retrage
 palkan
 shpigford
 emna__ayadi
 wayneb77