Share
Embed
[ICE71 CyberSecurity Networking Night] Mobile App Security: A developer's introduction
Marc Obrador
November 14, 2019
Transcript
23 slides
-
Mobile App Security A Developer Introduction Marc Obrador Head of
Product Architecture @ Build38 -
Who am I? 2 Marc Obrador Head of Product Architecture
@ Build38 Barcelona [email protected] @marcobrador /in/marc-obrador Build38 | Intro to Mobile App Security November 2019 -
The basics 3 Build38 | Intro to Mobile App Security
November 2019 -
Mobile-first world Why do I need to care about Mobile
App Security? 4 Smartphone = untrusted device Regulation (depending on market) Desktop Mobile 2009 2015 2020 0 20 40 60 80 100 Source: www.gs.statcounter.com Build38 | Intro to Mobile App Security November 2019 -
What do I need to protect? 5 Build38 | Intro
to Mobile App Security November 2019 -
It depends What do I need to protect? 6 Build38
| Intro to Mobile App Security November 2019 -
What do I need to protect? Build38 | Intro to
Mobile App Security 7 User Data Your Business DRM November 2019 -
Let’s first switch our perspective How can I protect my
app? Build38 | Intro to Mobile App Security 8 November 2019 -
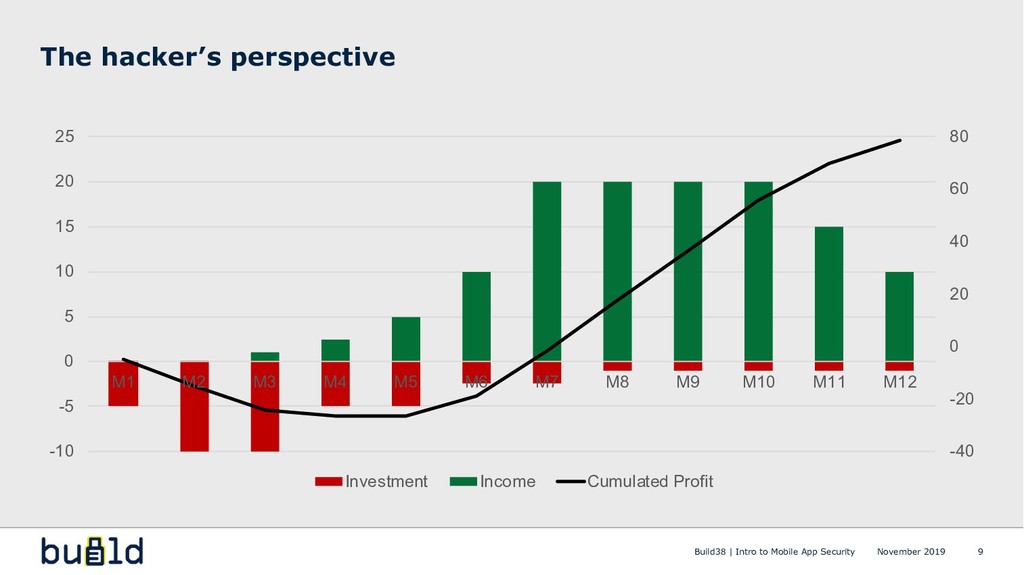
-40 -20 0 20 40 60 80 -10 -5 0
5 10 15 20 25 M1 M2 M3 M4 M5 M6 M7 M8 M9 M10 M11 M12 Investment Income Cumulated Profit The hacker’s perspective Build38 | Intro to Mobile App Security 9 November 2019 -
How can I protect my app? Build38 | Intro to
Mobile App Security 10 November 2019 -
Make it unattractive for the hacker How can I protect
my app? Build38 | Intro to Mobile App Security 11 November 2019 -
-40 -20 0 20 40 60 80 -10 -5 0
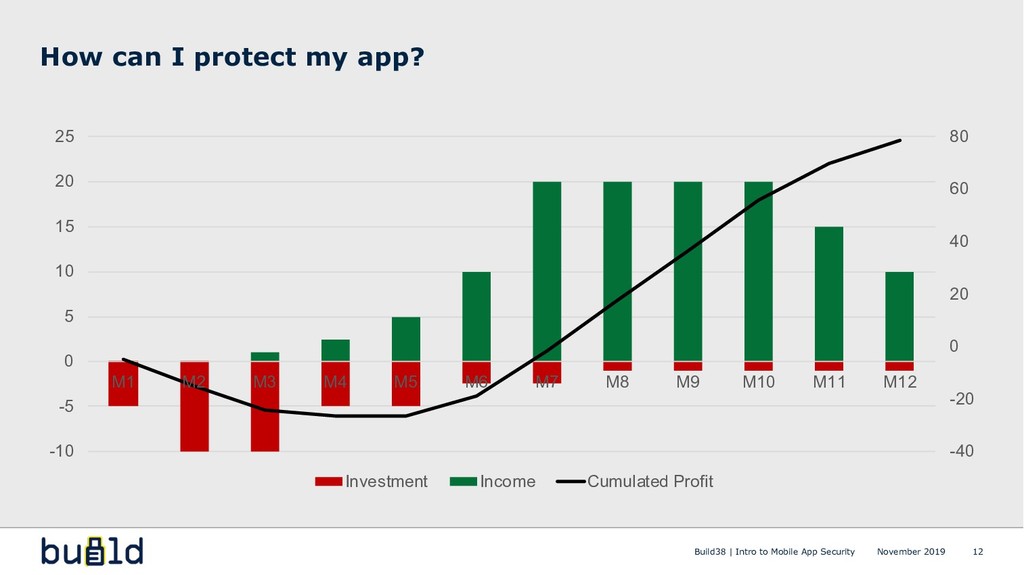
5 10 15 20 25 M1 M2 M3 M4 M5 M6 M7 M8 M9 M10 M11 M12 Investment Income Cumulated Profit How can I protect my app? Build38 | Intro to Mobile App Security 12 November 2019 -
-40 -20 0 20 40 60 80 -10 -5 0
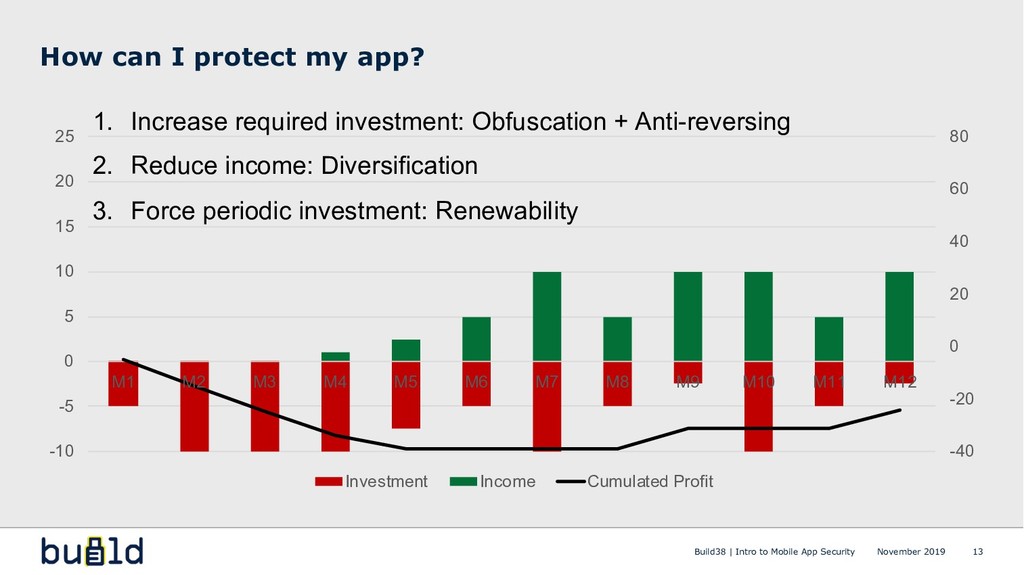
5 10 15 20 25 M1 M2 M3 M4 M5 M6 M7 M8 M9 M10 M11 M12 Investment Income Cumulated Profit How can I protect my app? Build38 | Intro to Mobile App Security 13 1. Increase required investment: Obfuscation + Anti-reversing 2. Reduce income: Diversification 3. Force periodic investment: Renewability November 2019 -
Some Common Threads (and their countermeasures) Build38 | Intro to
Mobile App Security 14 November 2019 -
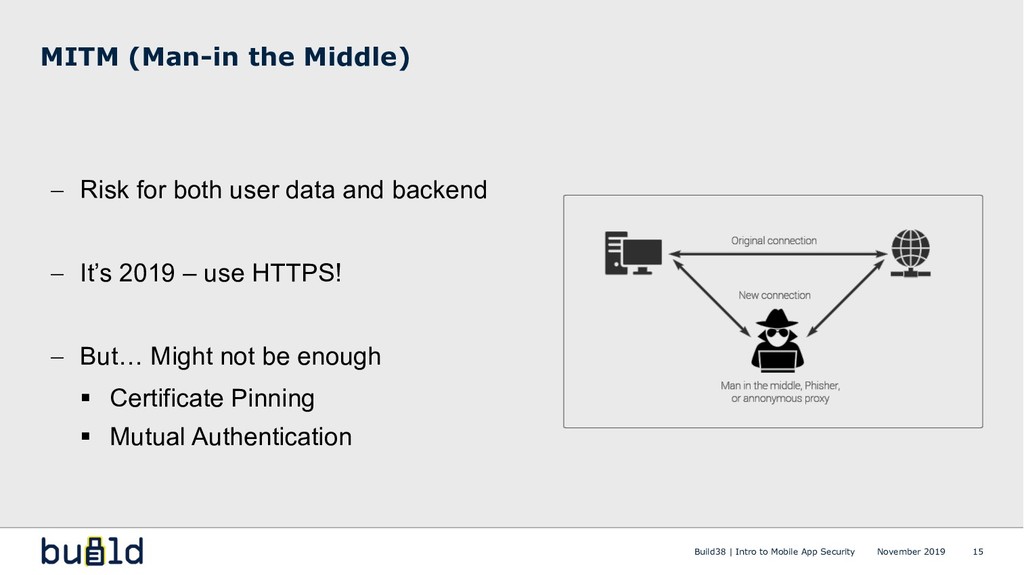
- Risk for both user data and backend - It’s
2019 – use HTTPS! - But… Might not be enough § Certificate Pinning § Mutual Authentication MITM (Man-in the Middle) Build38 | Intro to Mobile App Security 15 November 2019 -
- Modifying an App and redistributing it for malicious purposes,
in order to: § Modify original behavior o Getting paid features for free o Cheating on a game (Pokémon GO) o … § Stealing user data - How? § Android: modify smali code § iOS: dynamic library injection App Repackaging (1/2) 16 Build38 | Intro to Mobile App Security November 2019 -
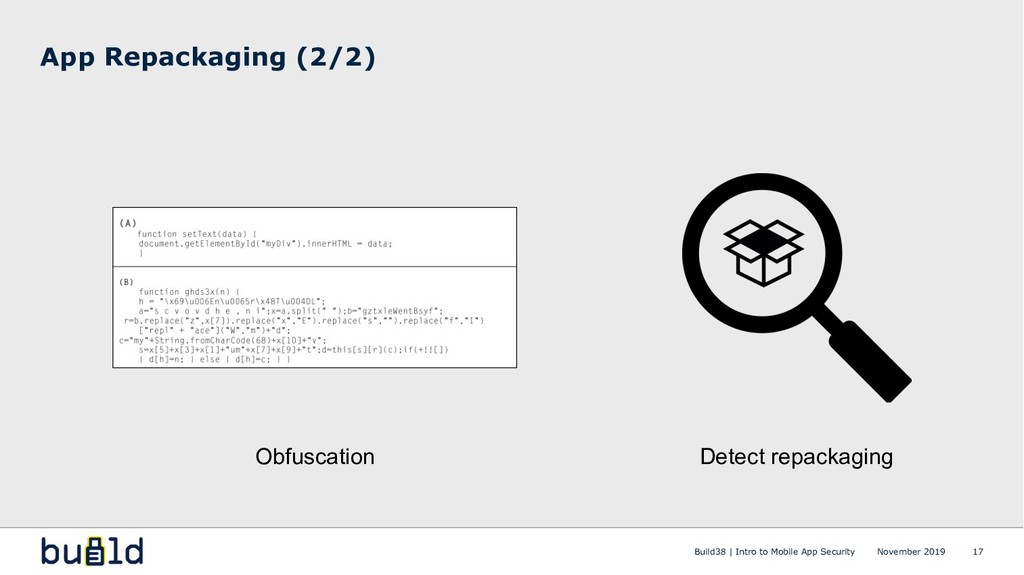
App Repackaging (2/2) 17 Obfuscation Detect repackaging Build38 | Intro
to Mobile App Security November 2019 -
- Sandbox model: basis of the security model in Android
and iOS § Each app runs and stores data in isolation from other apps - Root / Jailbreak means “escaping” this isolation Rooted / Jailbroken devices (1/2) Build38 | Intro to Mobile App Security 18 November 2019 -
Root == GOD Build38 | Intro to Mobile App Security
19 November 2019 -
- User may have legitimately rooted its device - Remote
root exploits are a thing - No clear action… § Restrict some sensitive functionality § Design your security model assuming that root can (will) happen Rooted / Jailbroken devices (2/2) 20 Source: - https://techcrunch.com/2019/08/29/google-iphone-secretly-hacked/ - https://googleprojectzero.blogspot.com/2019/08/a-very-deep-dive-into-ios-exploit.html Build38 | Intro to Mobile App Security November 2019 -
- Know what you need to protect - 100% protection
does not exist – aim for “good enough” - Secure Networking is a must - Apps can be reverse engineered and repackaged § Move security-relevant logic to backend or write it in native C - Root can be really bad – come up with a plan Recap 22 Build38 | Intro to Mobile App Security November 2019