Upgrade to Pro — share decks privately, control downloads, hide ads and more …

Holding the Core — Security Engineering Through...

Holding the Core — Security Engineering Through Darkwaar40: Breach

A Darkwood technical presentation connecting the Breach game mechanics with attack surfaces, detection, patching, identity and continuous security operations. The game is a learning metaphor; technical limits and implementation status are stated in the slides.

Canonical interactive presentation: https://slides.darkwood.com/slides/holding-the-core-security-engineering-through-darkwaar40-breach

Avatar for Mathieu Ledru

Mathieu Ledru

November 08, 2026

More Decks by Mathieu Ledru

Other Decks in Programming

Transcript

  1. Slide 1 · 1/2 · représentation statique Darkwood · Security

    Engineering · Darkwaar40 Holding the Core Security Engineering Through Darkwaar40 — Breach 01 · Holding the Core · 20–25 min Version interactive : https://slides.darkwood.com/slides/holding-the-core-security-engineering-through-darkwaar40-breach @matyo91
  2. Slide 1 · 2/2 · représentation statique Darkwood · Security

    Engineering · Darkwaar40 Holding the Core Security Engineering Through Darkwaar40 — Breach DARK WOOD TECHNICAL SESSION · @MAT YO91 01 · Holding the Core · 20–25 min Version interactive : https://slides.darkwood.com/slides/holding-the-core-security-engineering-through-darkwaar40-breach @matyo91
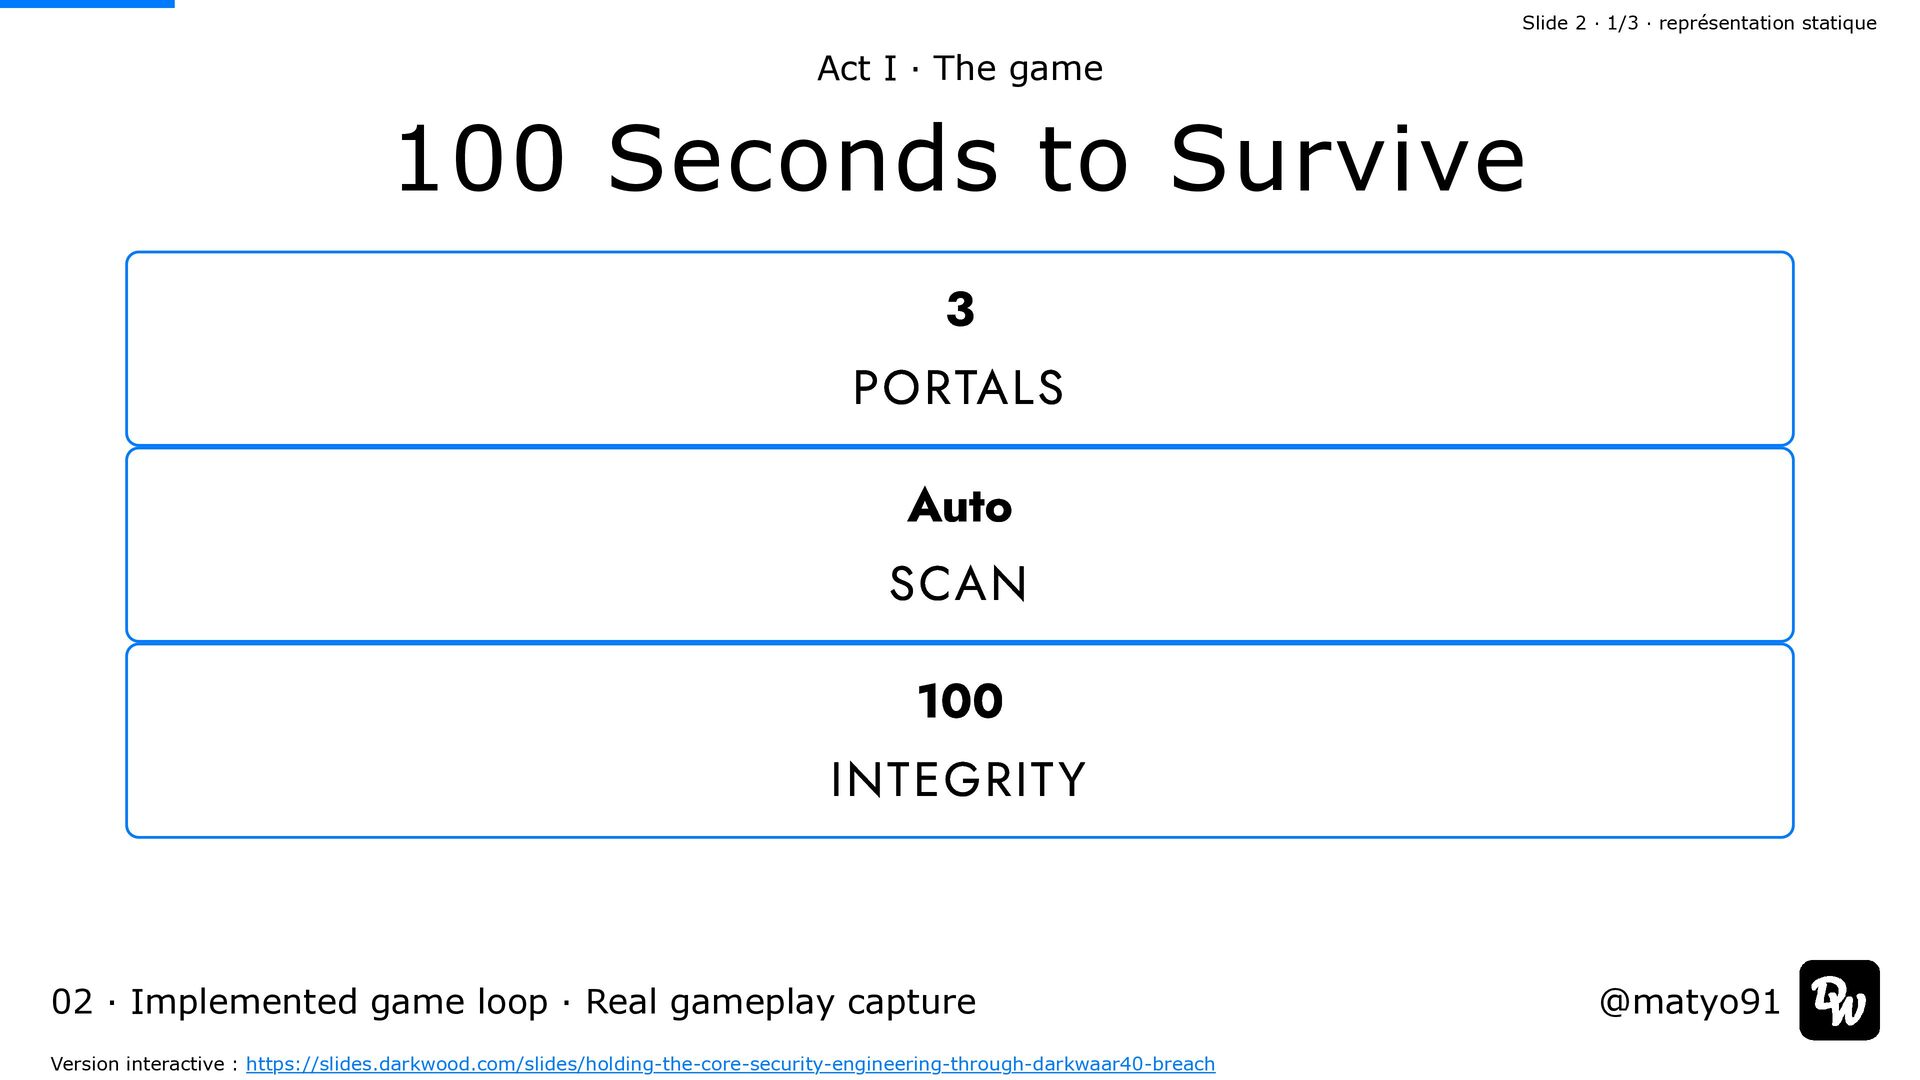
  3. Slide 2 · 1/3 · représentation statique Act I ·

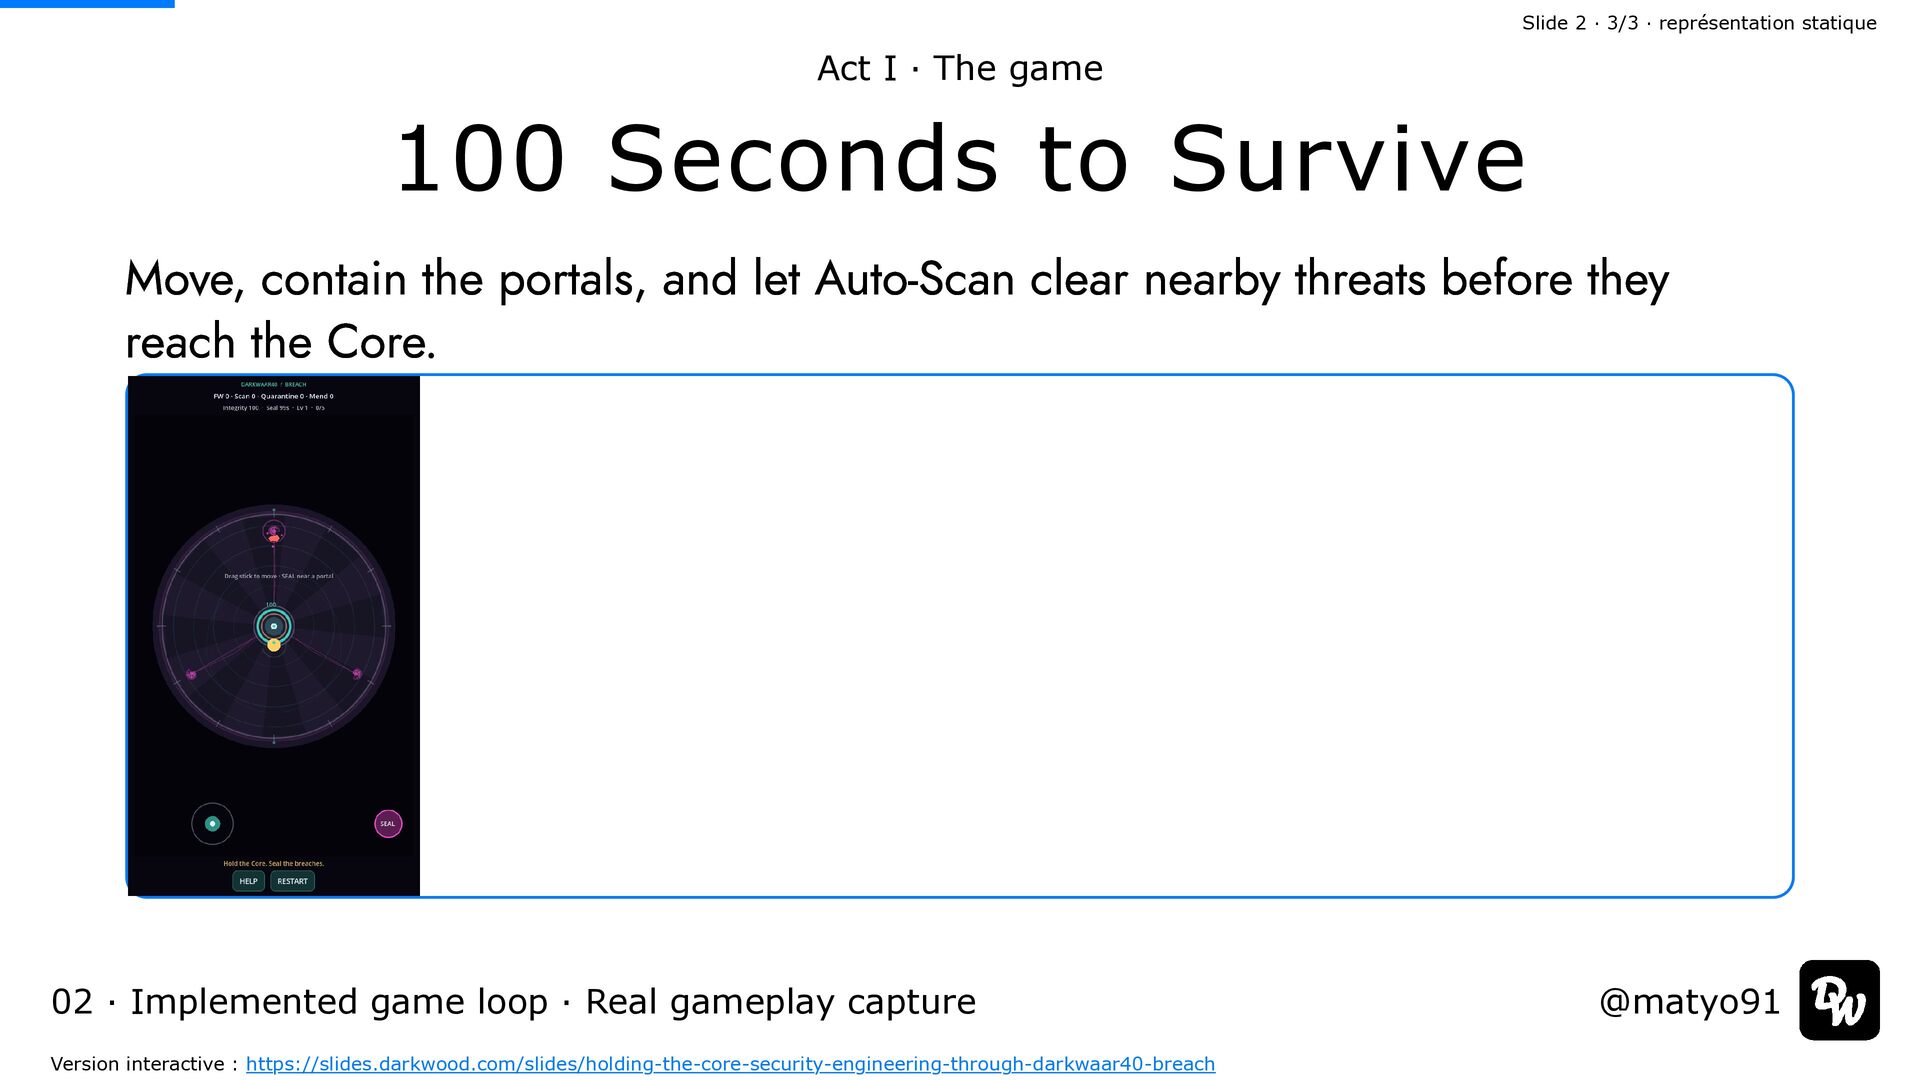
    The game 100 Seconds to Survive 3 PORTALS Auto SCAN 100 INTEGRIT Y 02 · Implemented game loop · Real gameplay capture Version interactive : https://slides.darkwood.com/slides/holding-the-core-security-engineering-through-darkwaar40-breach @matyo91
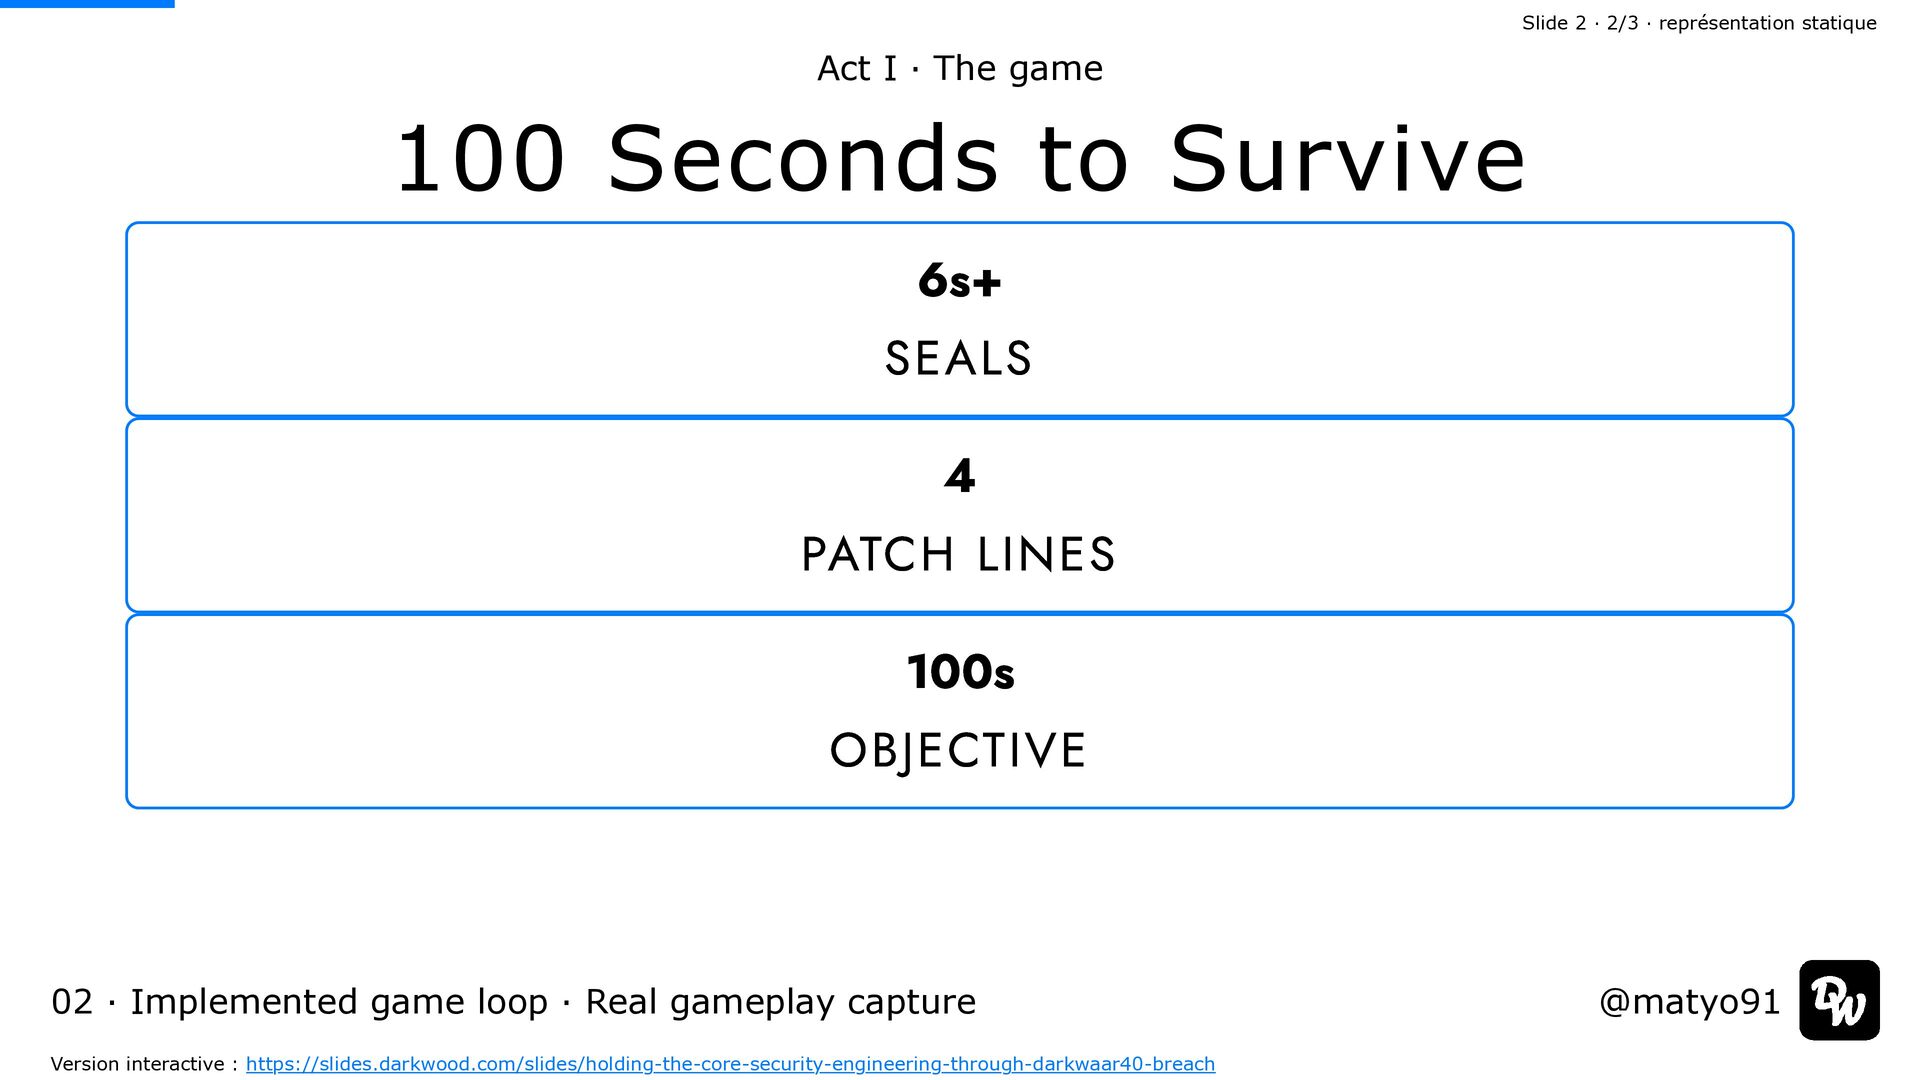
  4. Slide 2 · 2/3 · représentation statique Act I ·

    The game 100 Seconds to Survive 6s+ SEALS 4 PATCH LINES 100s OBJECTIVE 02 · Implemented game loop · Real gameplay capture Version interactive : https://slides.darkwood.com/slides/holding-the-core-security-engineering-through-darkwaar40-breach @matyo91
  5. Slide 2 · 3/3 · représentation statique Act I ·

    The game 100 Seconds to Survive Move, contain the portals, and let Auto-Scan clear nearby threats before they reach the Core. 02 · Implemented game loop · Real gameplay capture Version interactive : https://slides.darkwood.com/slides/holding-the-core-security-engineering-through-darkwaar40-breach @matyo91
  6. The thesis Security is not a wall. Reduce exposure →

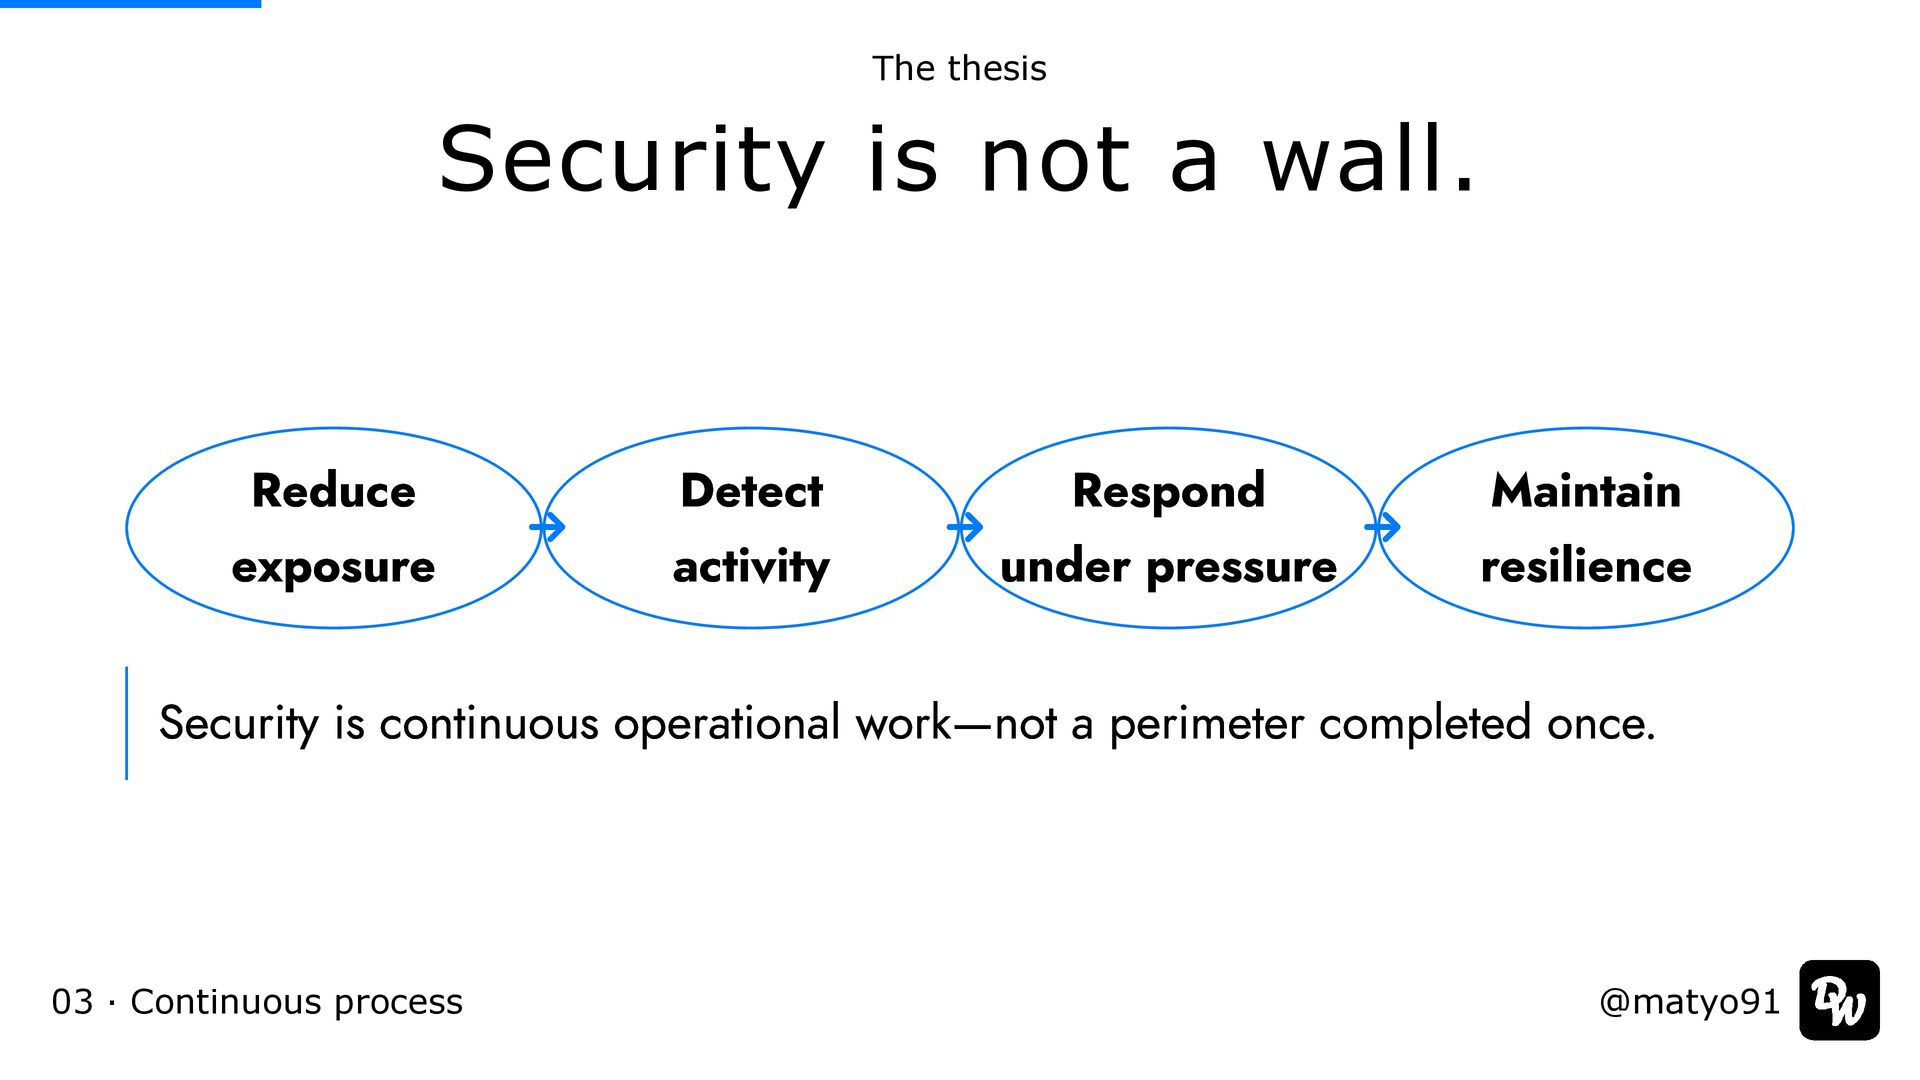
    Detect activity → under pressure → Respond Maintain resilience Security is continuous operational work—not a perimeter completed once. 03 · Continuous process @matyo91
  7. Slide 4 · 1/1 · représentation statique The security model

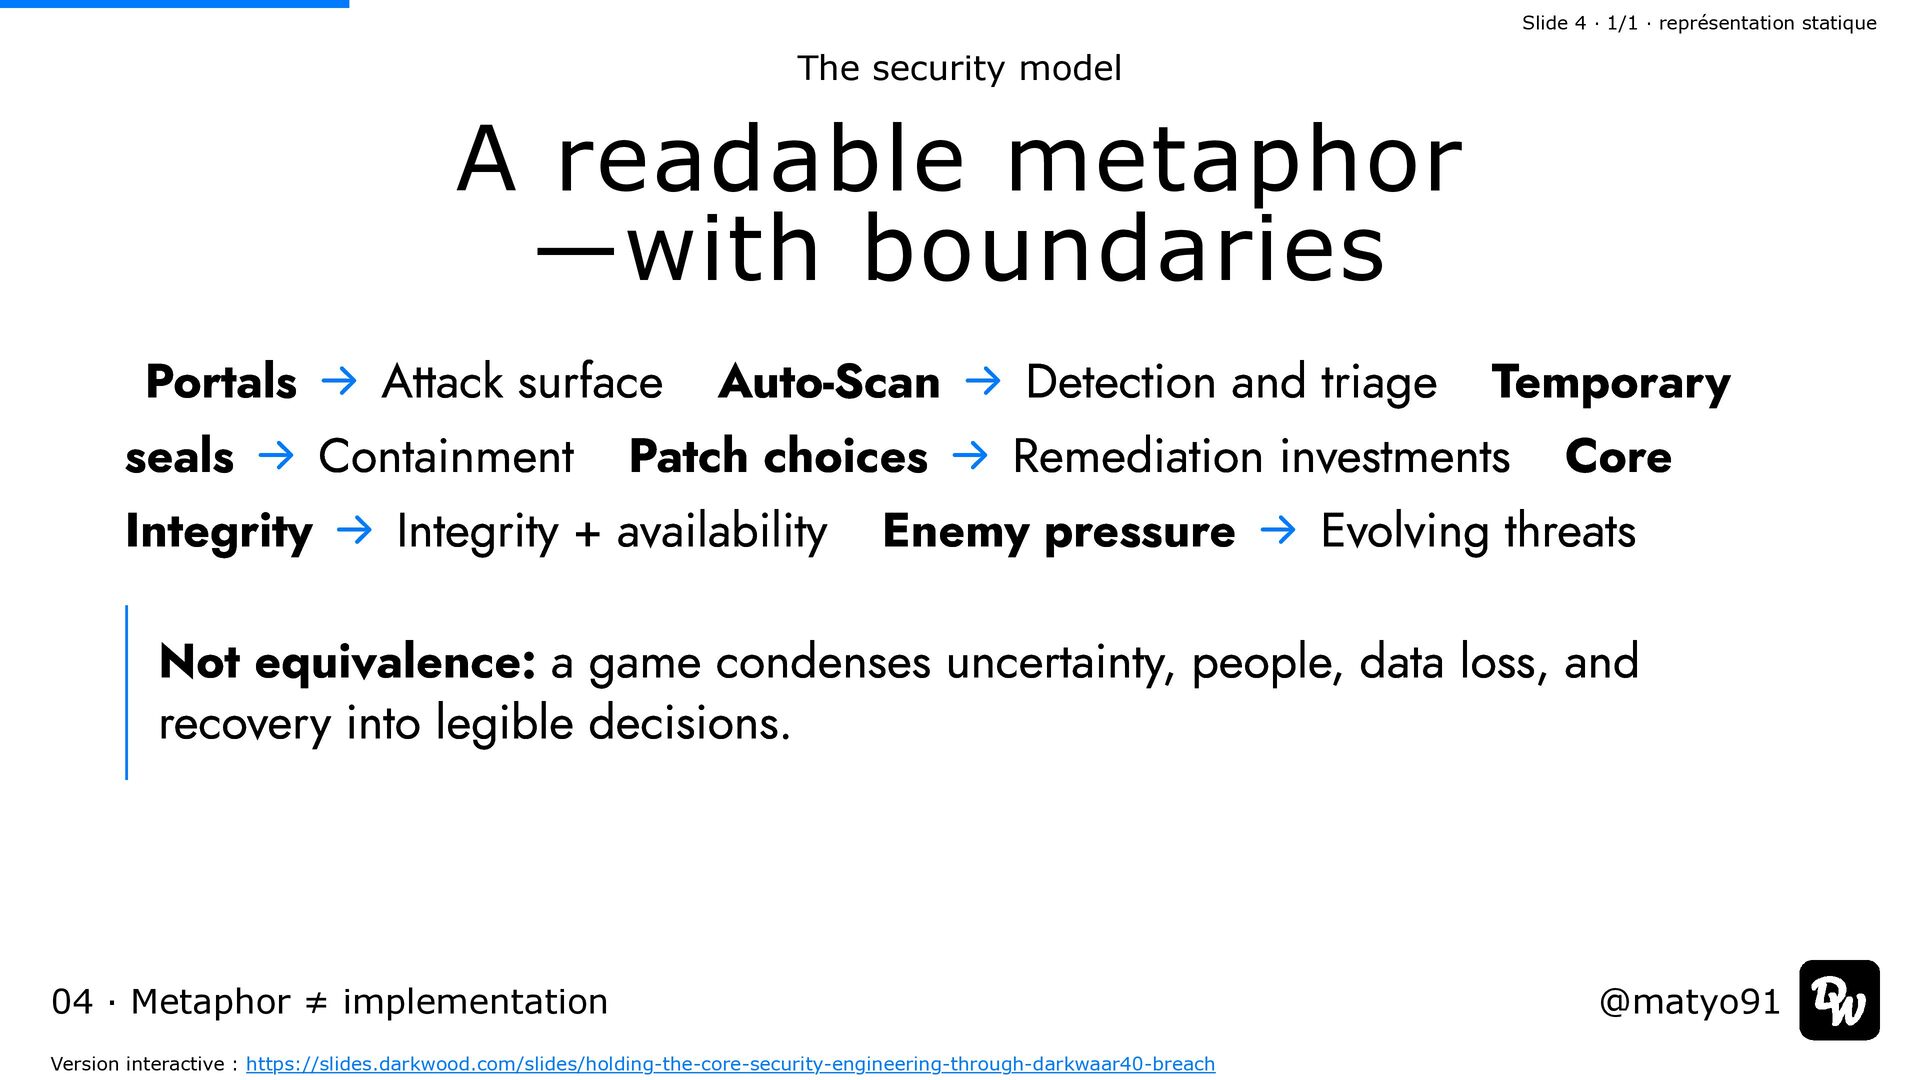
    A readable metaphor —with boundaries → Attack surface Auto-Scan → Detection and triage Temporary seals → Containment Patch choices → Remediation investments Core Integrity → Integrity + availability Enemy pressure → Evolving threats Portals Not equivalence: a game condenses uncertainty, people, data loss, and recovery into legible decisions. 04 · Metaphor ≠ implementation Version interactive : https://slides.darkwood.com/slides/holding-the-core-security-engineering-through-darkwaar40-breach @matyo91
  8. Act II · Defensive security Detection is not prevention. Preventive

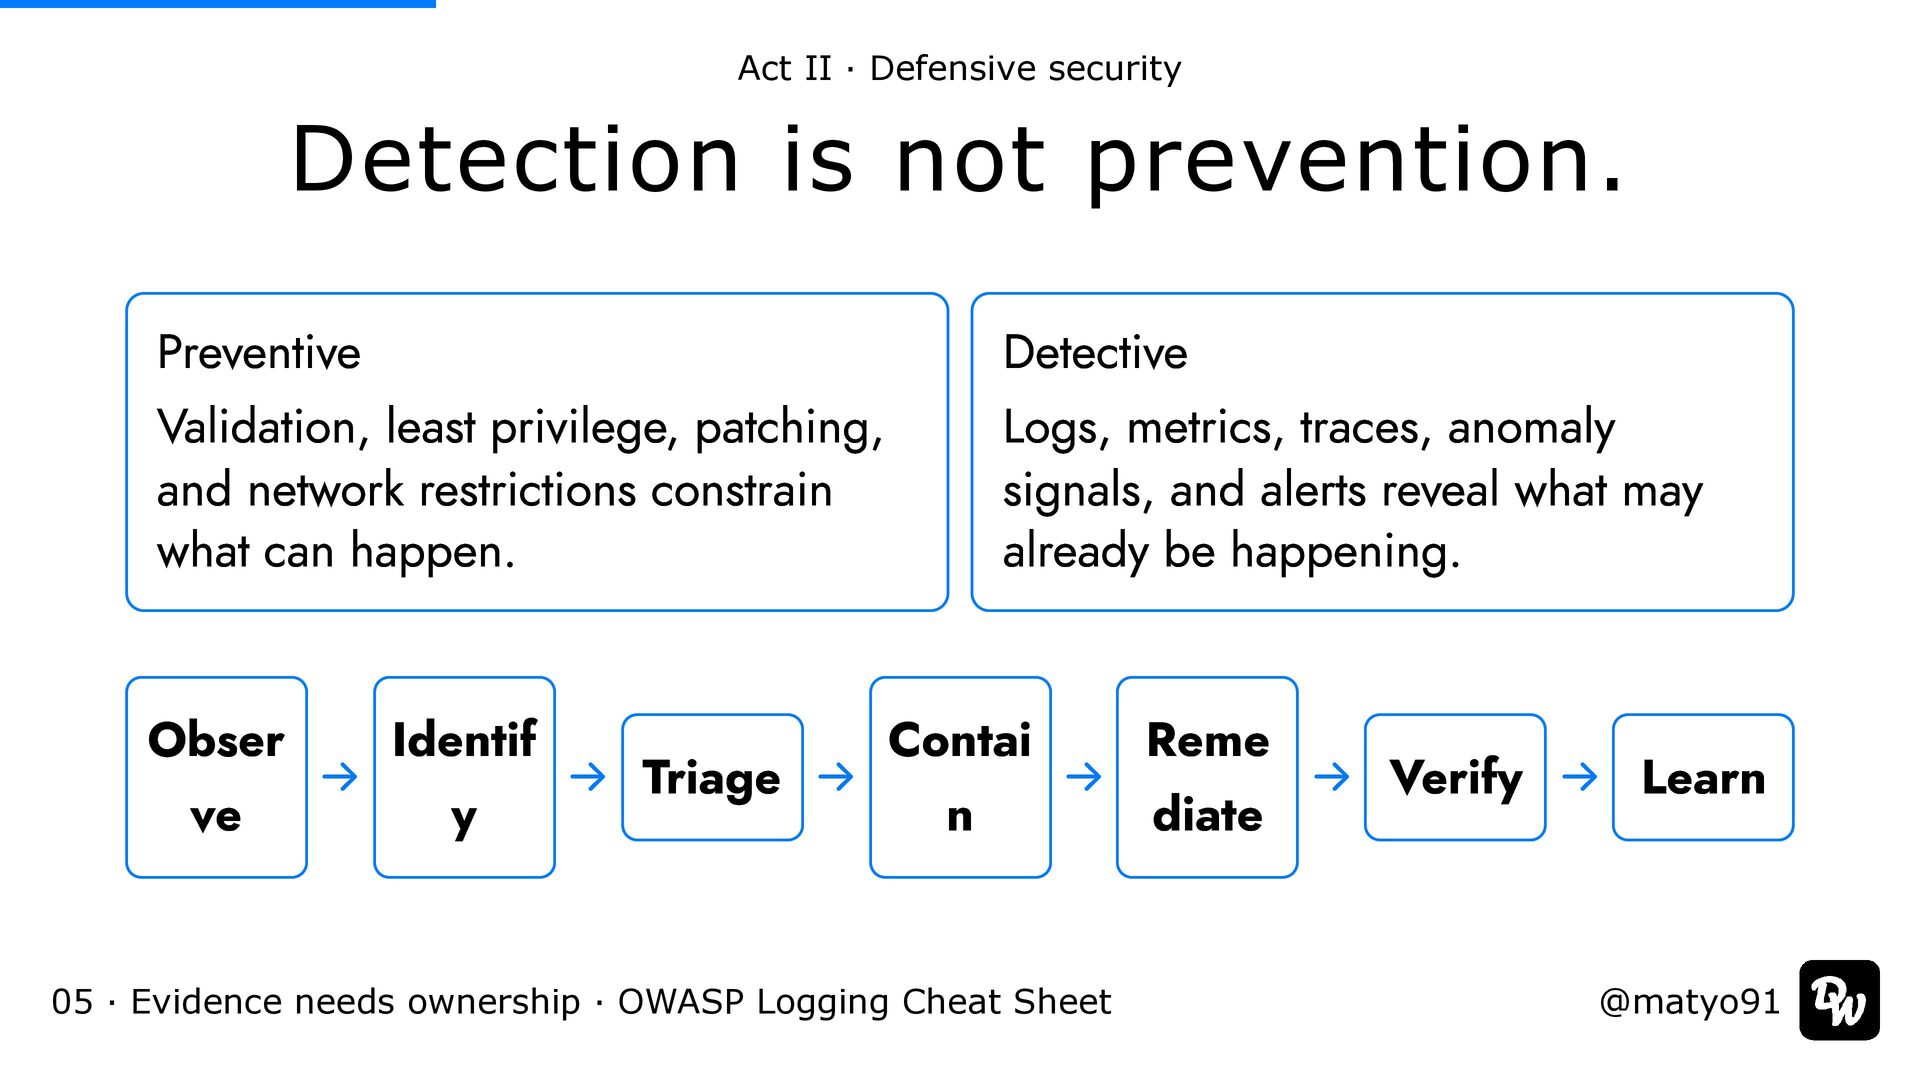
    Detective Validation, least privilege, patching, and network restrictions constrain what can happen. Logs, metrics, traces, anomaly signals, and alerts reveal what may already be happening. Obser ve → Identif y → Triage → Contai n → diate → Verify → Learn 05 · Evidence needs ownership · OWASP Logging Cheat Sheet Reme @matyo91
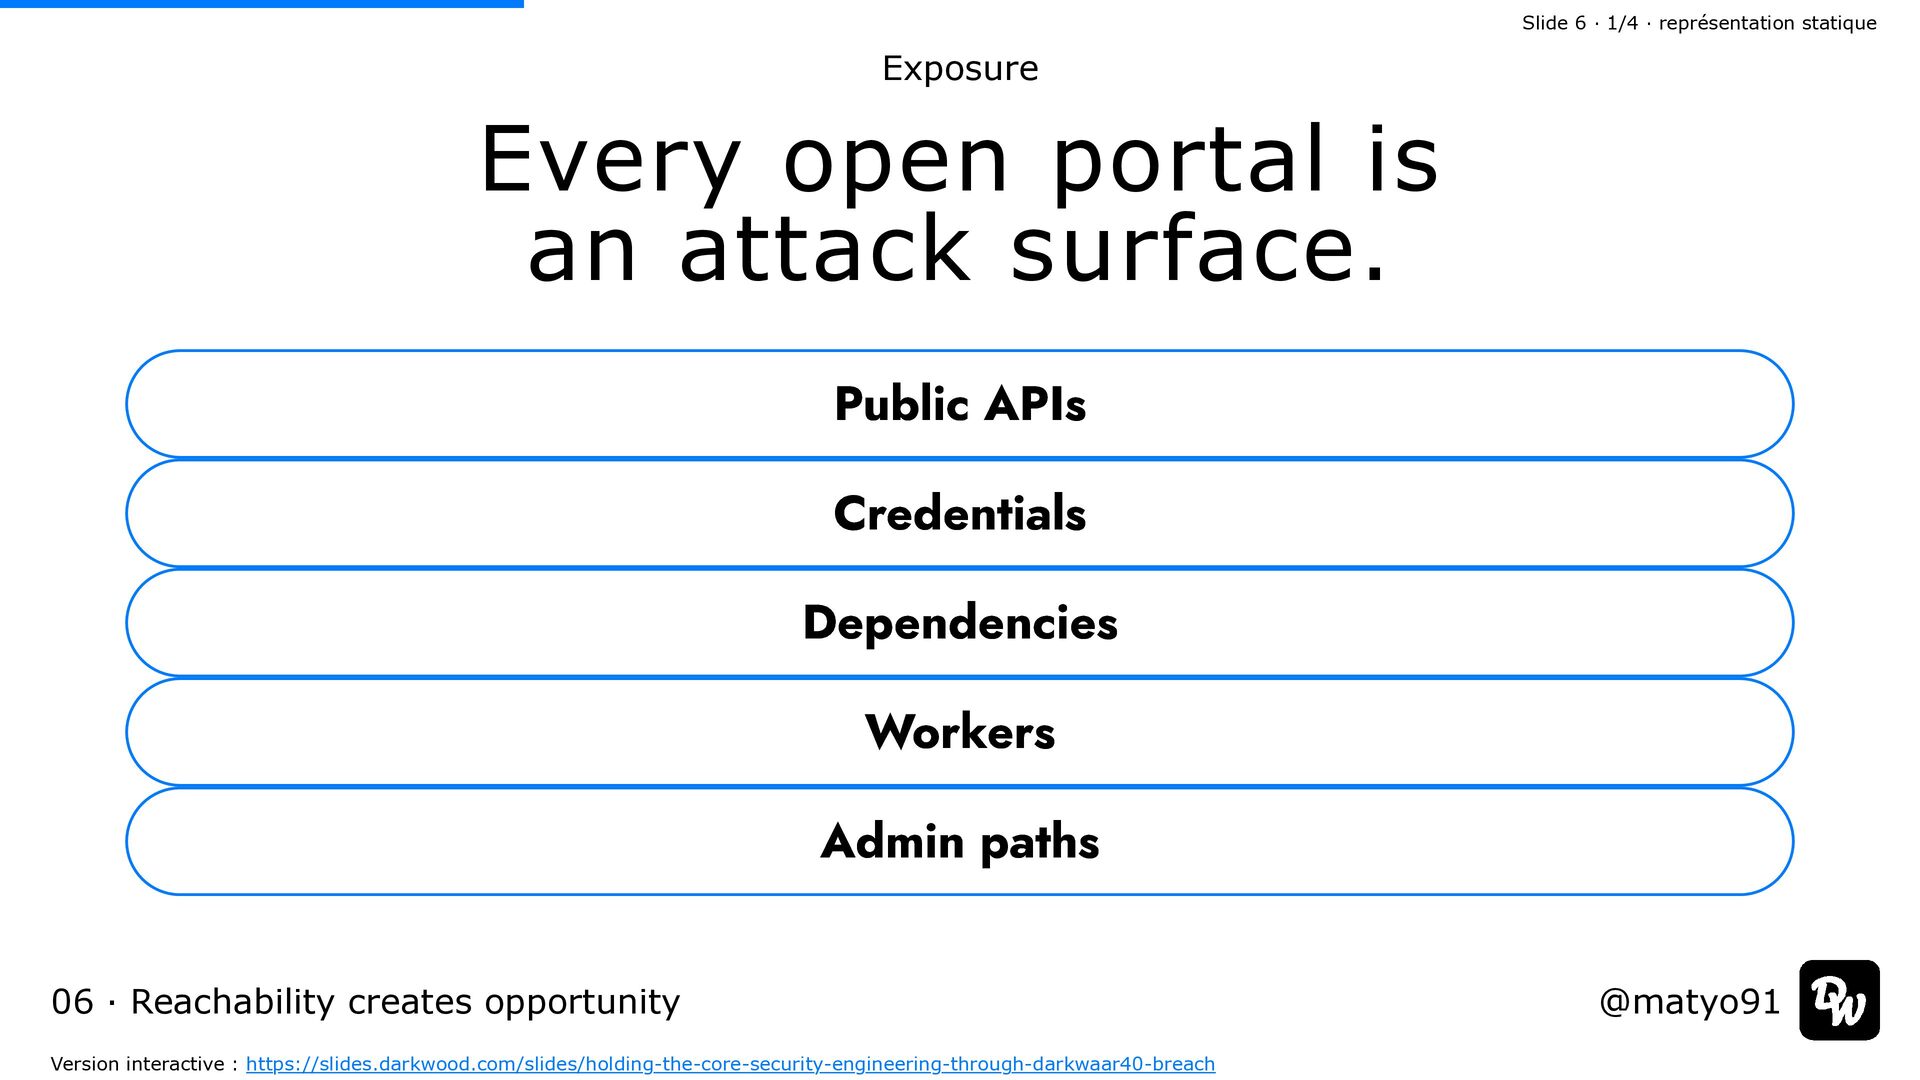
  9. Slide 6 · 1/4 · représentation statique Exposure Every open

    portal is an attack surface. Public APIs Credentials Dependencies Workers Admin paths 06 · Reachability creates opportunity Version interactive : https://slides.darkwood.com/slides/holding-the-core-security-engineering-through-darkwaar40-breach @matyo91
  10. Slide 6 · 2/4 · représentation statique Exposure Every open

    portal is an attack surface. Infrastructure 06 · Reachability creates opportunity Version interactive : https://slides.darkwood.com/slides/holding-the-core-security-engineering-through-darkwaar40-breach @matyo91
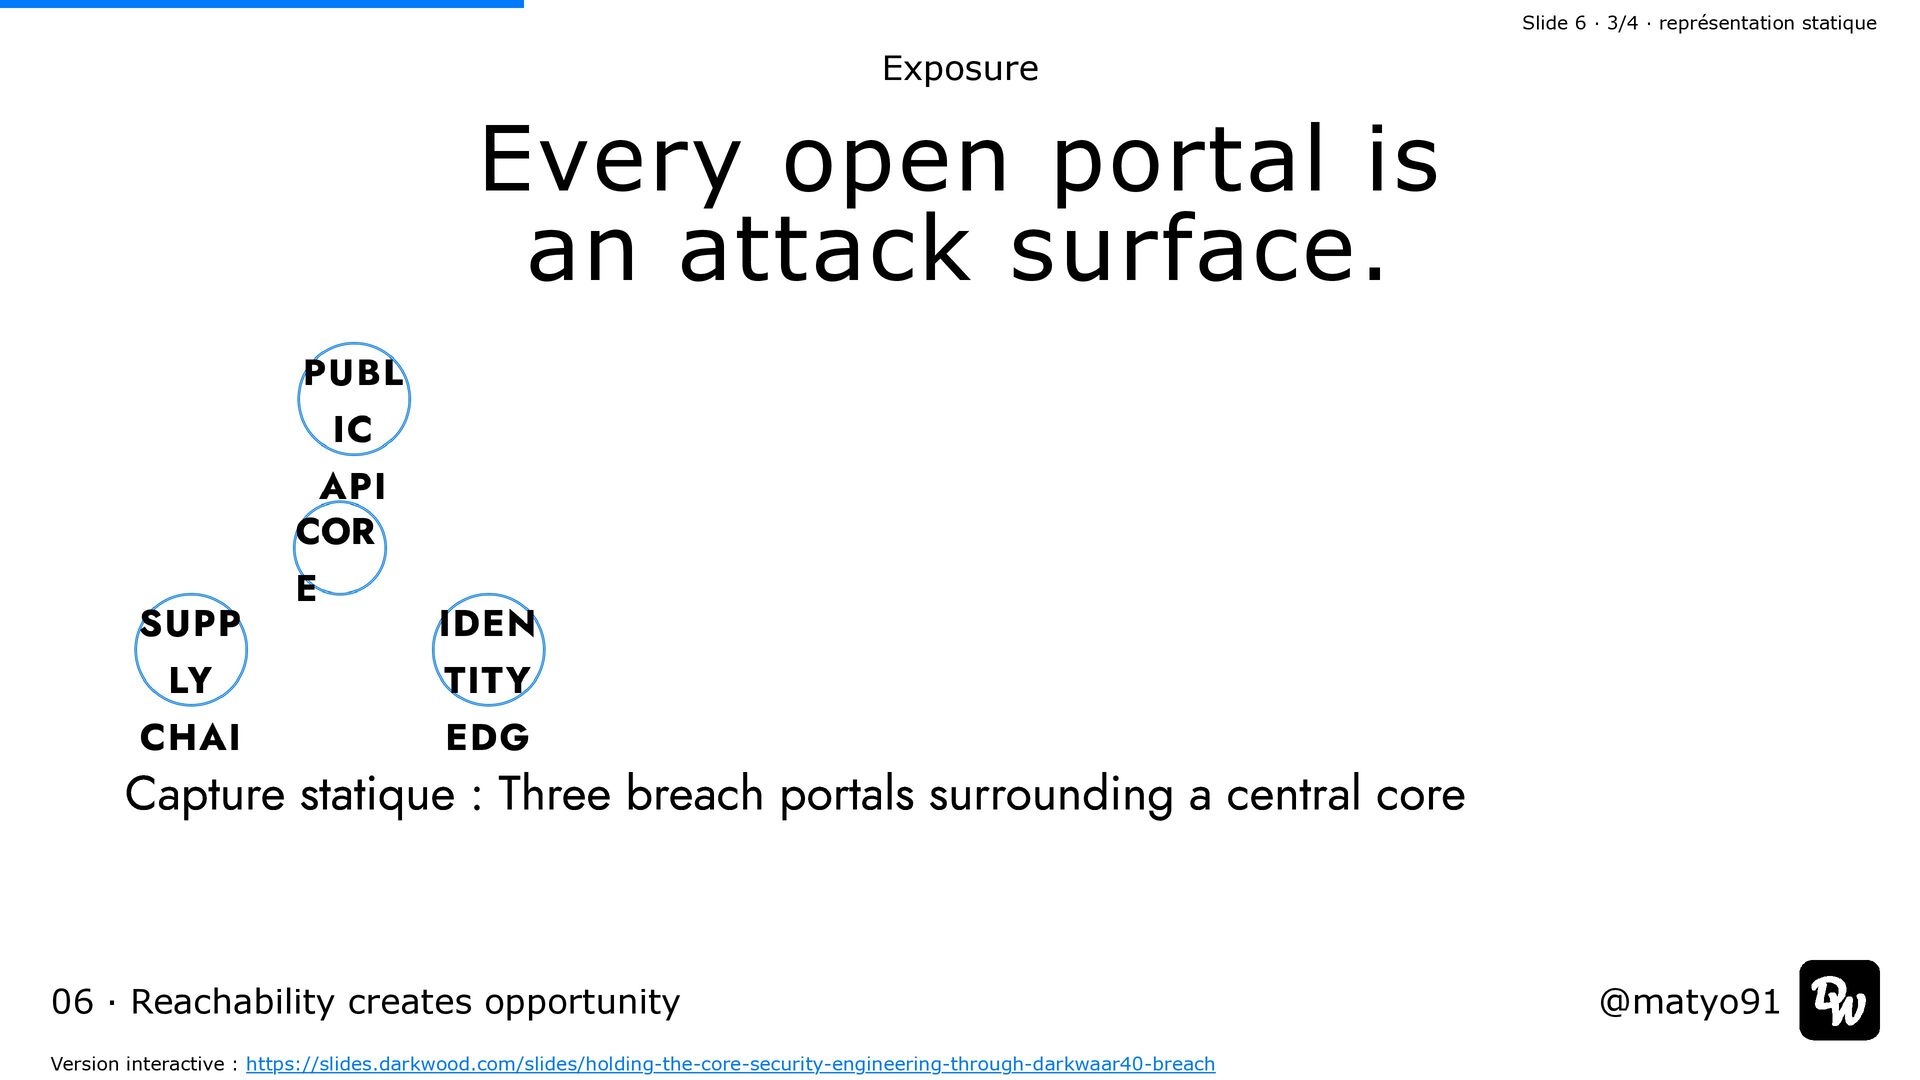
  11. Slide 6 · 3/4 · représentation statique Exposure Every open

    portal is an attack surface. Capture statique : Three breach portals surrounding a central core 06 · Reachability creates opportunity Version interactive : https://slides.darkwood.com/slides/holding-the-core-security-engineering-through-darkwaar40-breach @matyo91
  12. Slide 6 · 4/4 · représentation statique Exposure Every open

    portal is an attack surface. Lecture du schéma : CORE PUBLIC API SUPPLY CHAIN IDENTITY EDGE 06 · Reachability creates opportunity Version interactive : https://slides.darkwood.com/slides/holding-the-core-security-engineering-through-darkwaar40-breach @matyo91
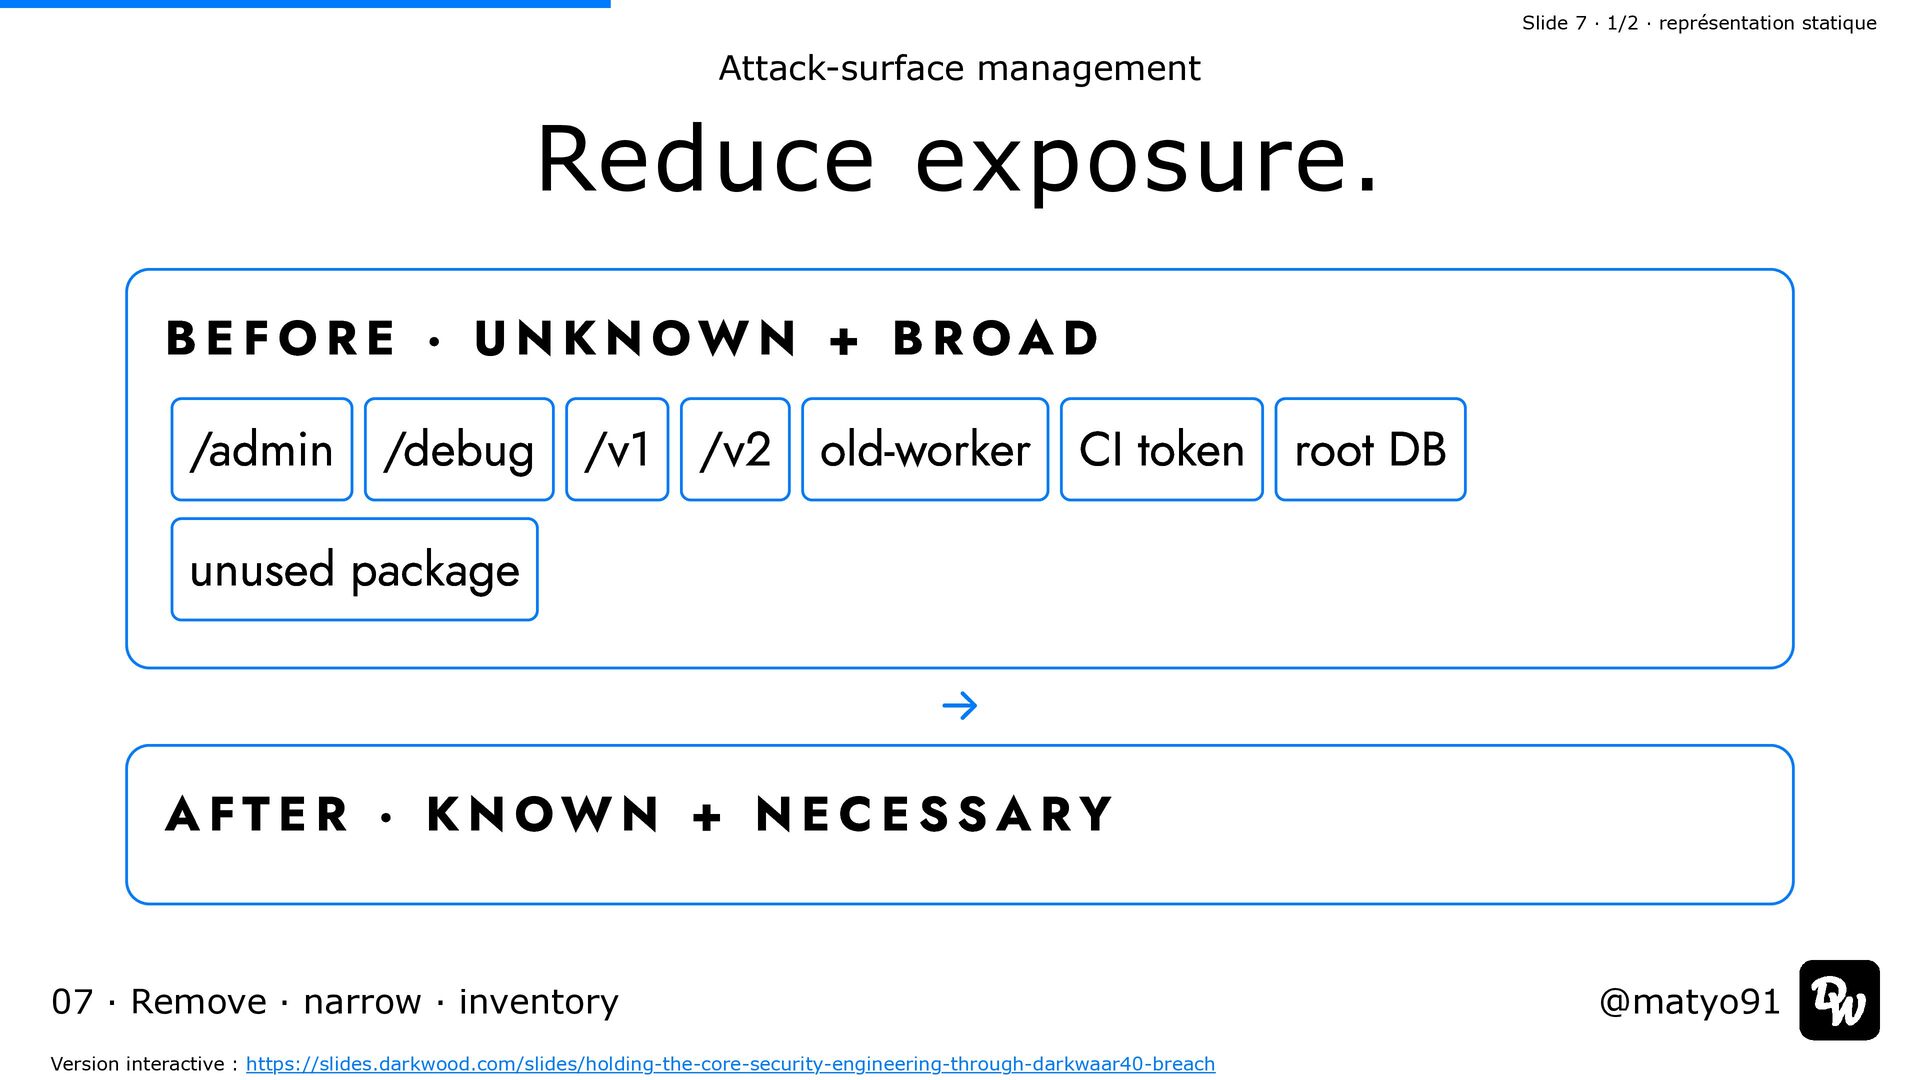
  13. Slide 7 · 1/2 · représentation statique Attack-surface management Reduce

    exposure. BEFORE · UNKNOWN + BROAD /admin /debug /v1 /v2 old-worker CI token root DB unused package → AFTER · KNOWN + NECESSARY 07 · Remove · narrow · inventory Version interactive : https://slides.darkwood.com/slides/holding-the-core-security-engineering-through-darkwaar40-breach @matyo91
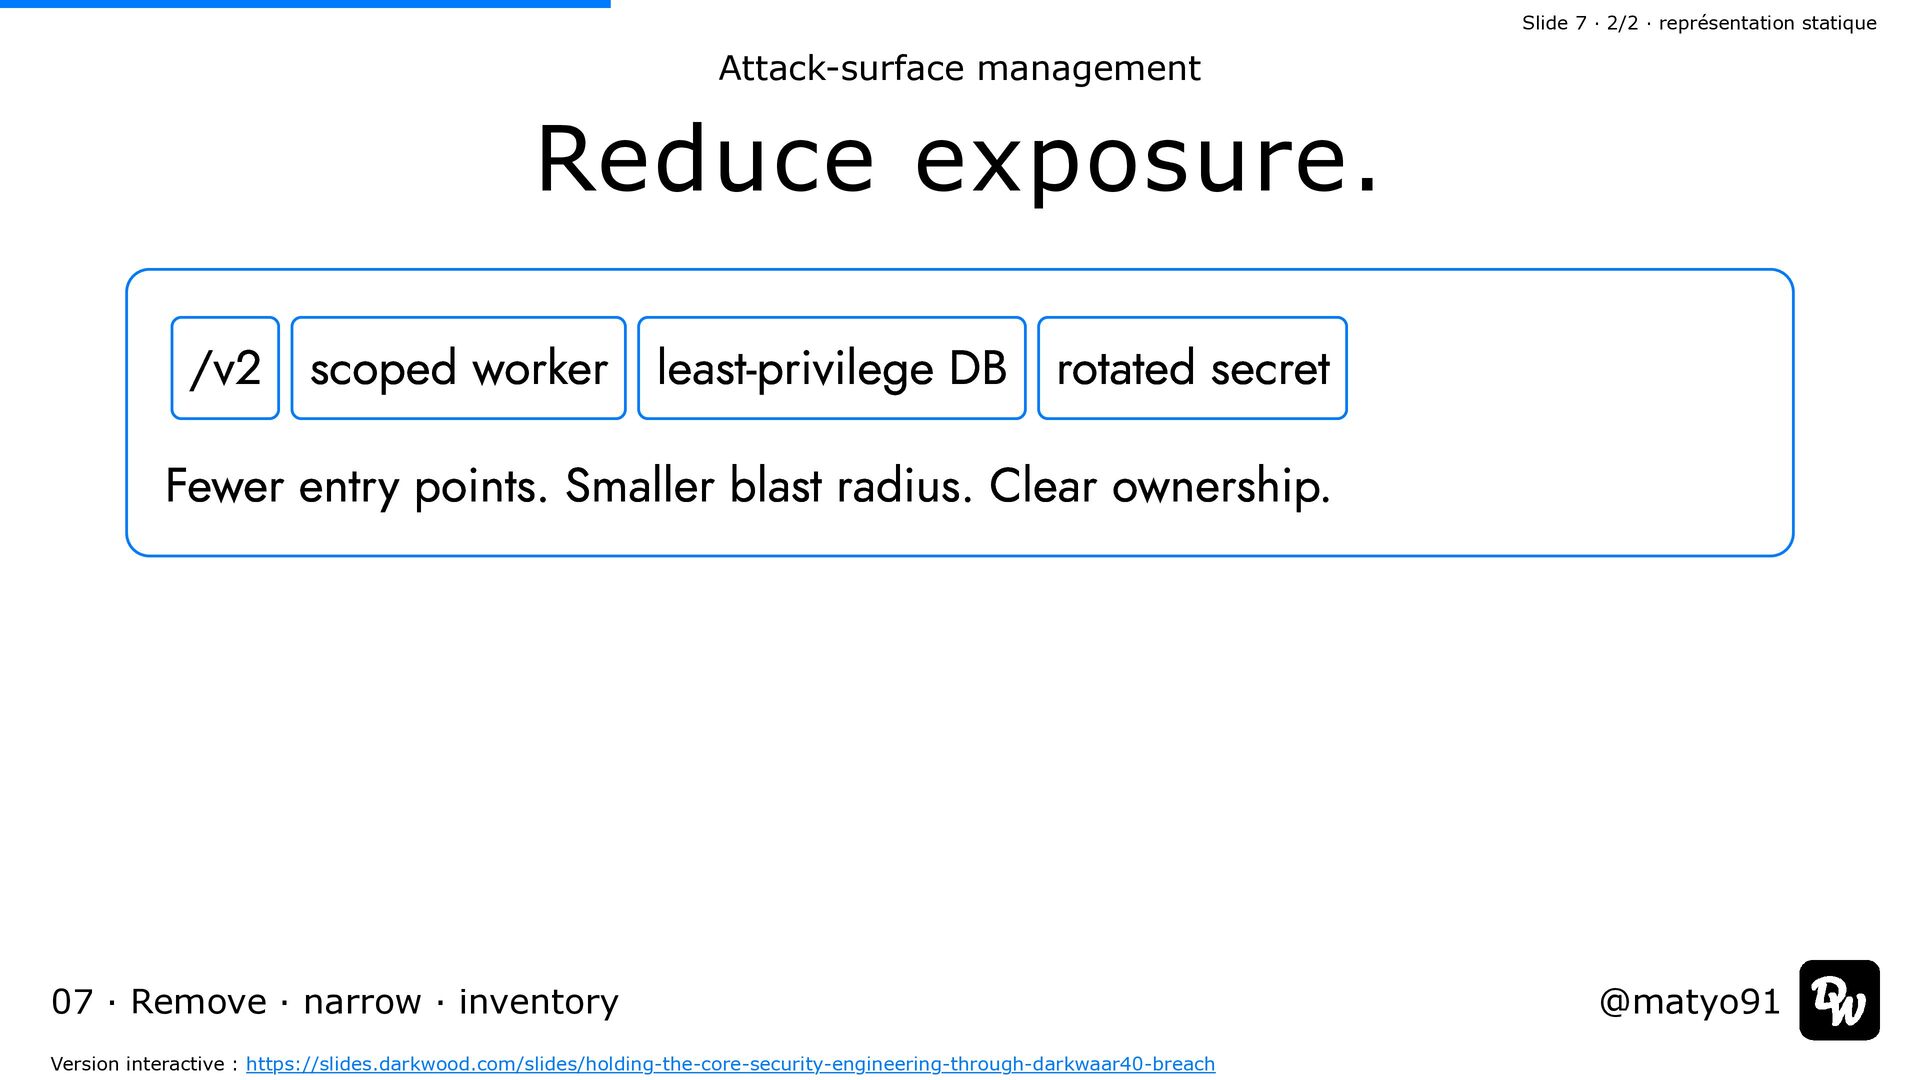
  14. Slide 7 · 2/2 · représentation statique Attack-surface management Reduce

    exposure. /v2 scoped worker least-privilege DB rotated secret Fewer entry points. Smaller blast radius. Clear ownership. 07 · Remove · narrow · inventory Version interactive : https://slides.darkwood.com/slides/holding-the-core-security-engineering-through-darkwaar40-breach @matyo91
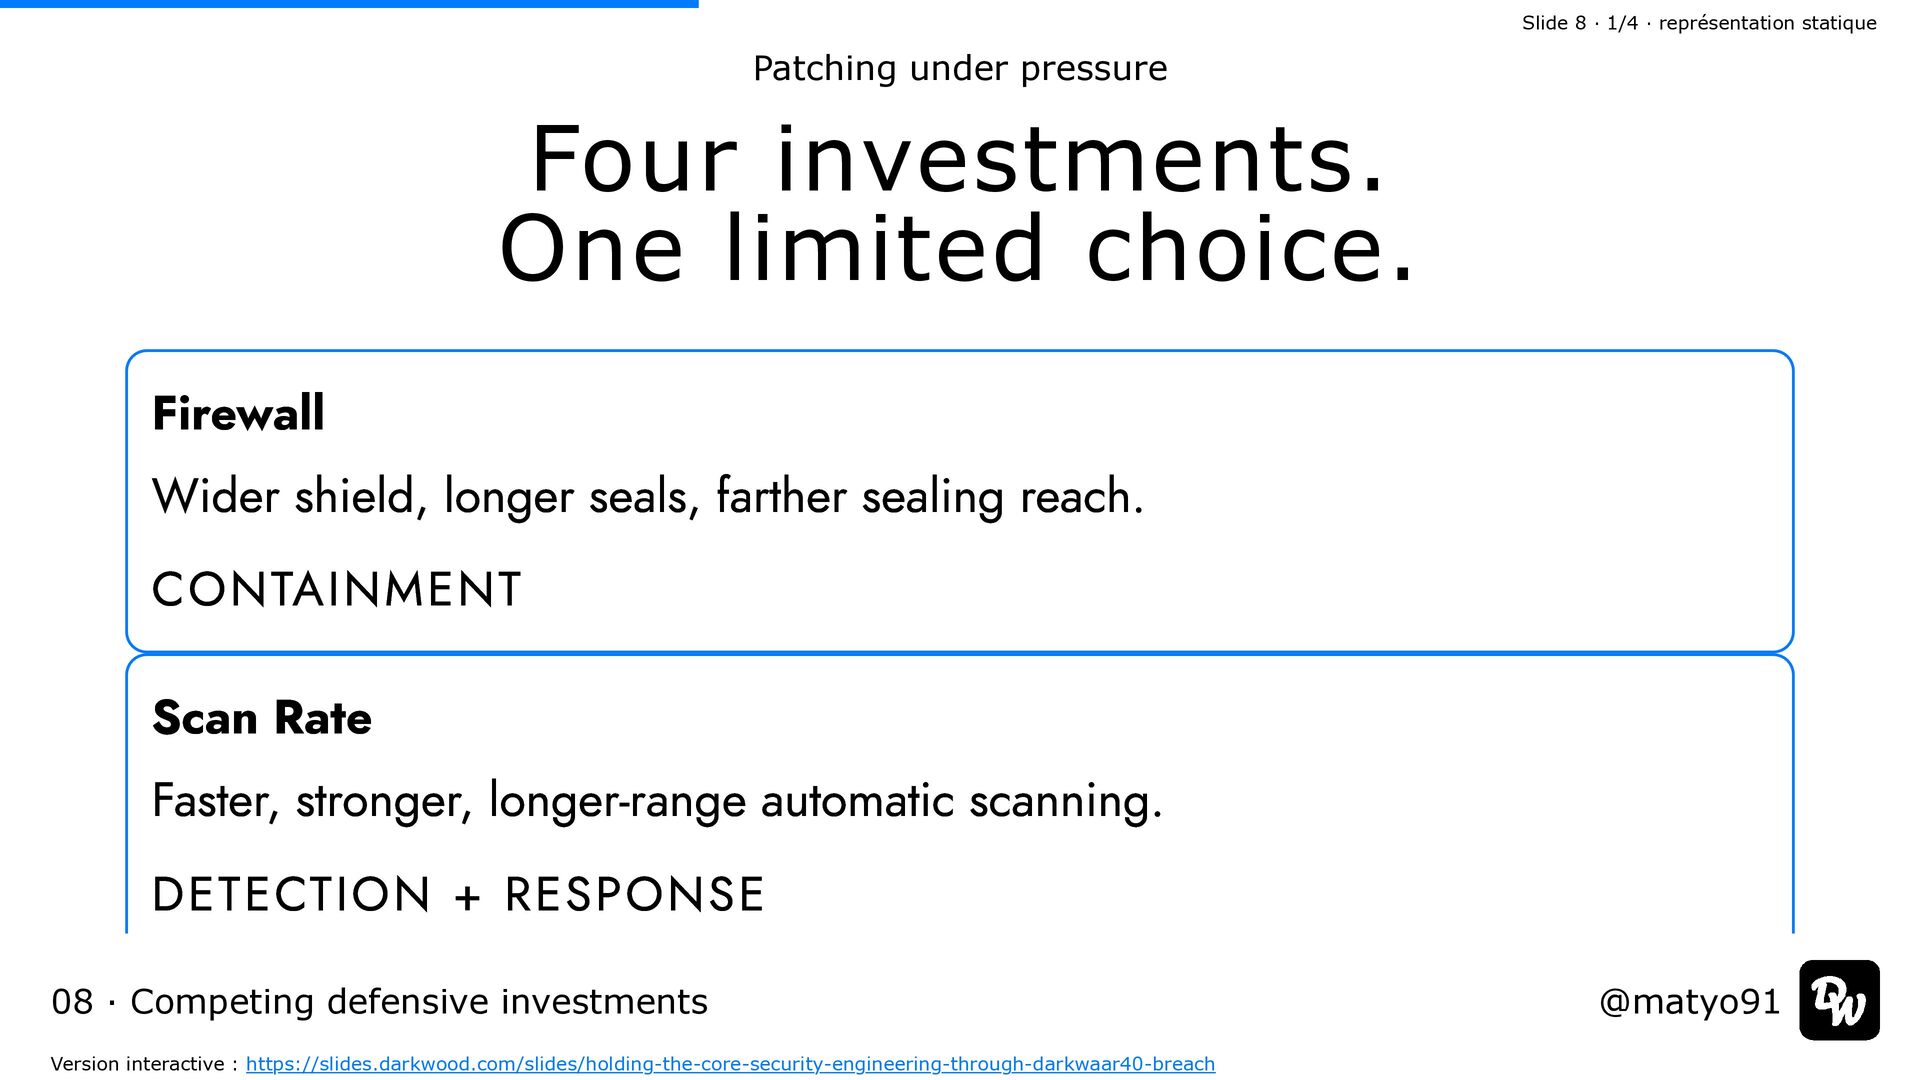
  15. Slide 8 · 1/4 · représentation statique Patching under pressure

    Four investments. One limited choice. Firewall Wider shield, longer seals, farther sealing reach. CONTAINMENT Scan Rate Faster, stronger, longer-range automatic scanning. DETECTION + RESPONSE 08 · Competing defensive investments Version interactive : https://slides.darkwood.com/slides/holding-the-core-security-engineering-through-darkwaar40-breach @matyo91
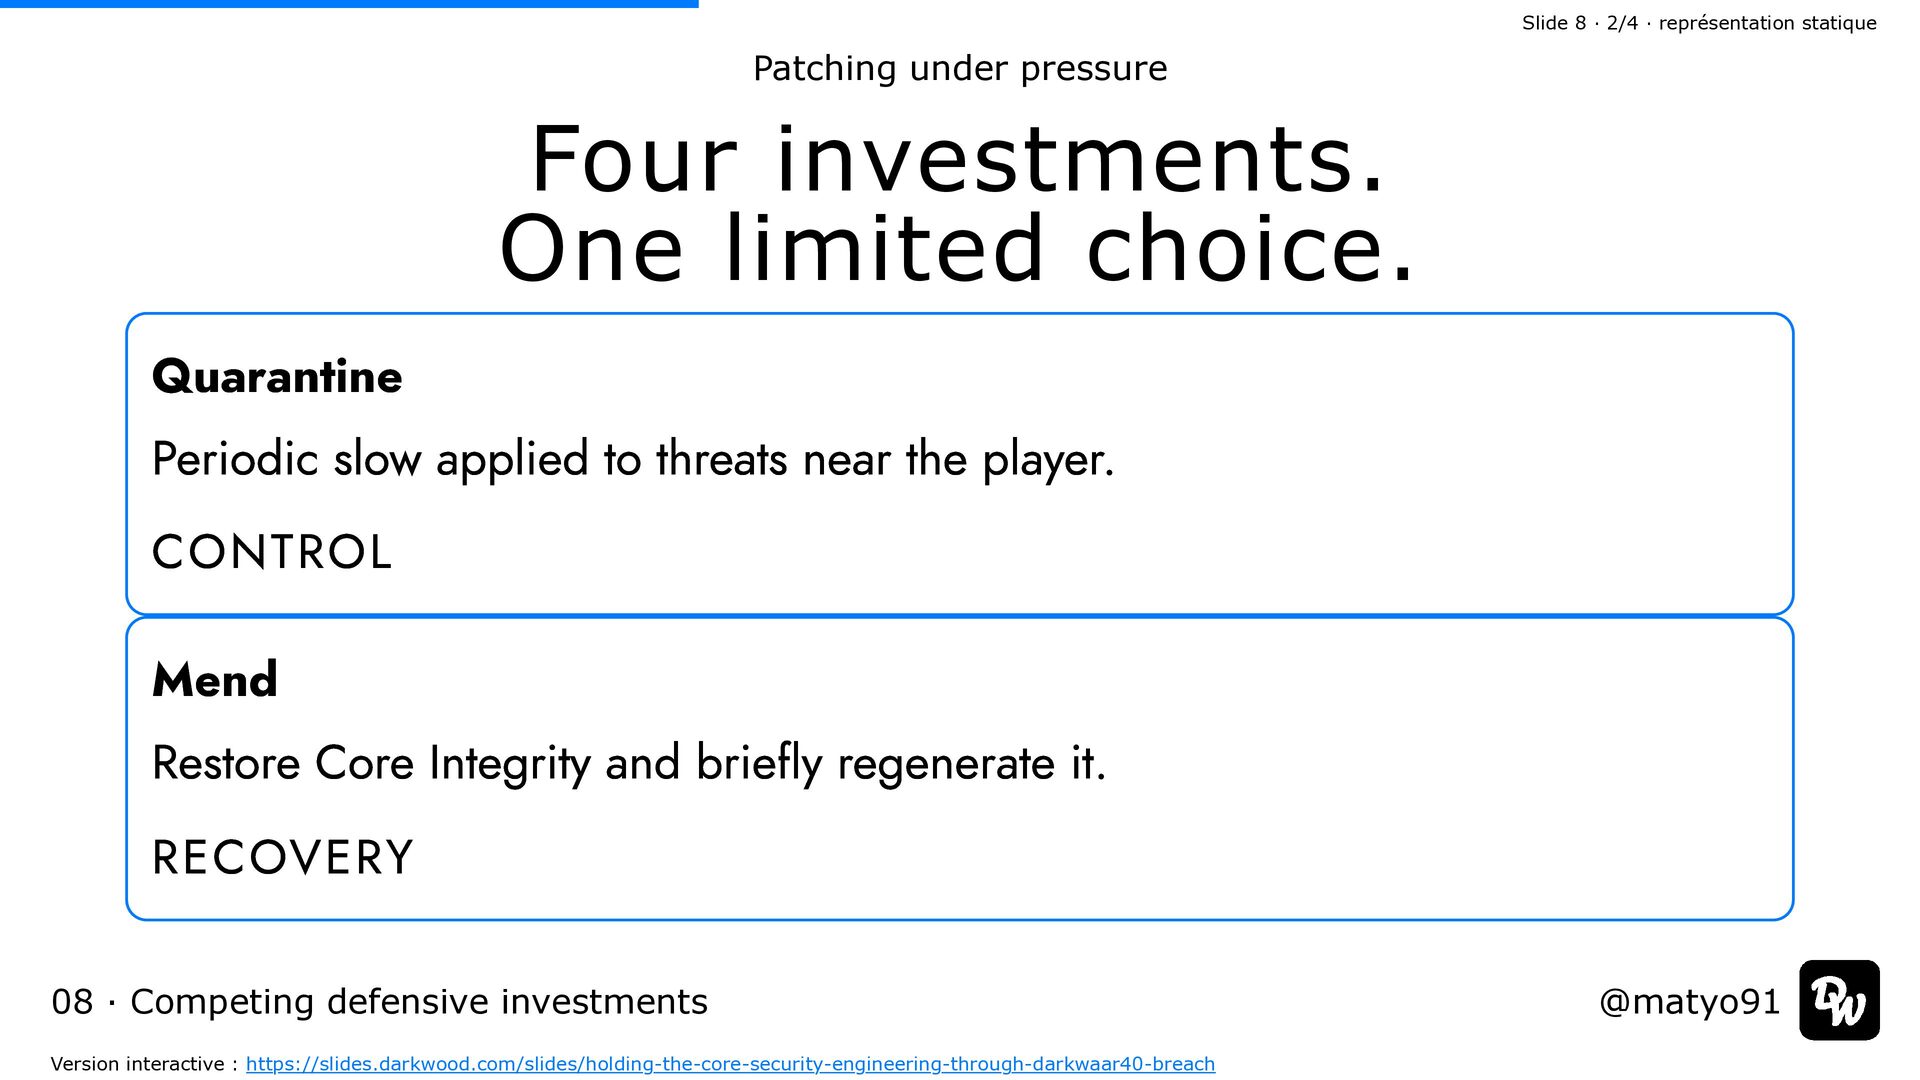
  16. Slide 8 · 2/4 · représentation statique Patching under pressure

    Four investments. One limited choice. Quarantine Periodic slow applied to threats near the player. CONTROL Mend Restore Core Integrity and briefly regenerate it. RECOVERY 08 · Competing defensive investments Version interactive : https://slides.darkwood.com/slides/holding-the-core-security-engineering-through-darkwaar40-breach @matyo91
  17. Slide 8 · 3/4 · représentation statique Patching under pressure

    Four investments. One limited choice. 08 · Competing defensive investments Version interactive : https://slides.darkwood.com/slides/holding-the-core-security-engineering-through-darkwaar40-breach @matyo91
  18. Slide 8 · 4/4 · représentation statique Patching under pressure

    Four investments. One limited choice. Game upgrade ≠ software patch. Real remediation changes code or configuration, then requires testing, deployment, rollback, and verification. 08 · Competing defensive investments Version interactive : https://slides.darkwood.com/slides/holding-the-core-security-engineering-through-darkwaar40-breach @matyo91
  19. Slide 9 · 1/2 · représentation statique 21 October 2026

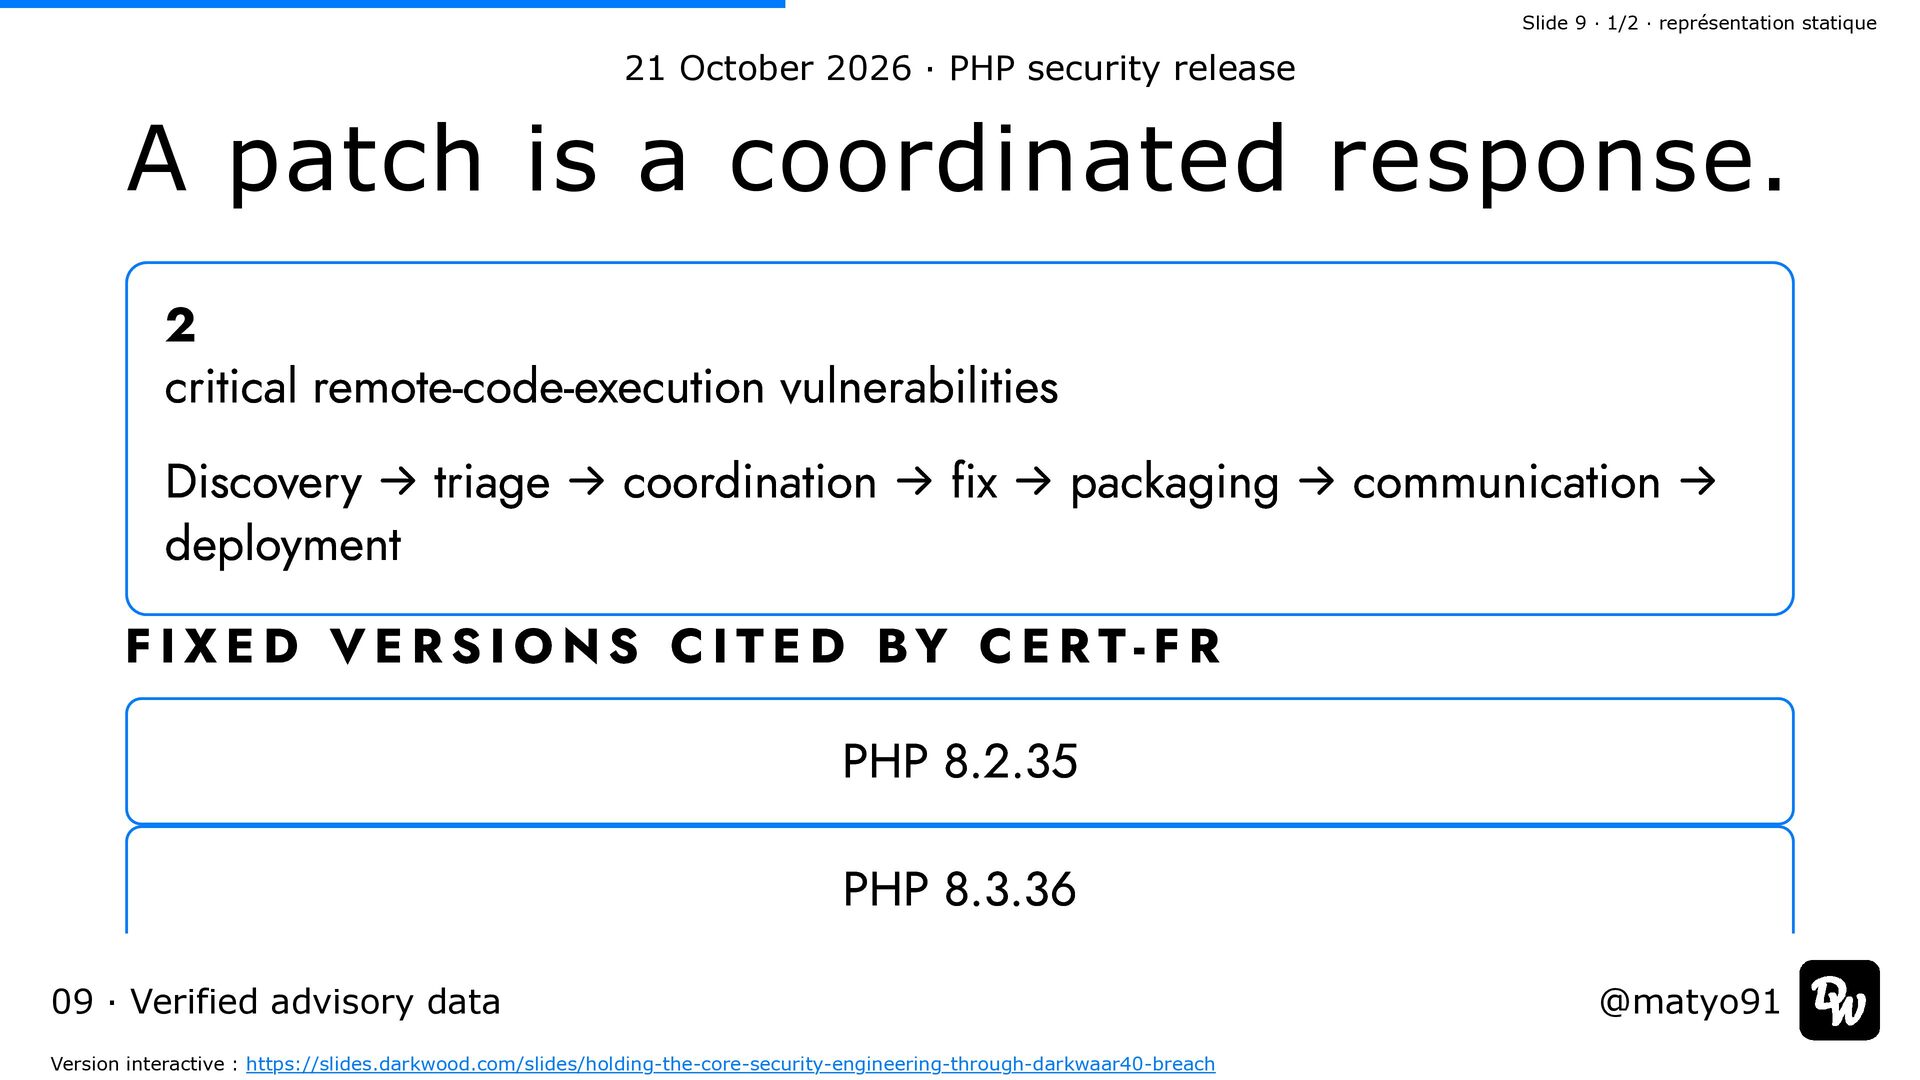
    · PHP security release A patch is a coordinated response. 2 critical remote-code-execution vulnerabilities → Discovery triage deployment → coordination → fix → packaging → communication → FIXED VERSIONS CITED BY CERT-FR PHP 8.2.35 PHP 8.3.36 09 · Verified advisory data Version interactive : https://slides.darkwood.com/slides/holding-the-core-security-engineering-through-darkwaar40-breach @matyo91
  20. Slide 9 · 2/2 · représentation statique 21 October 2026

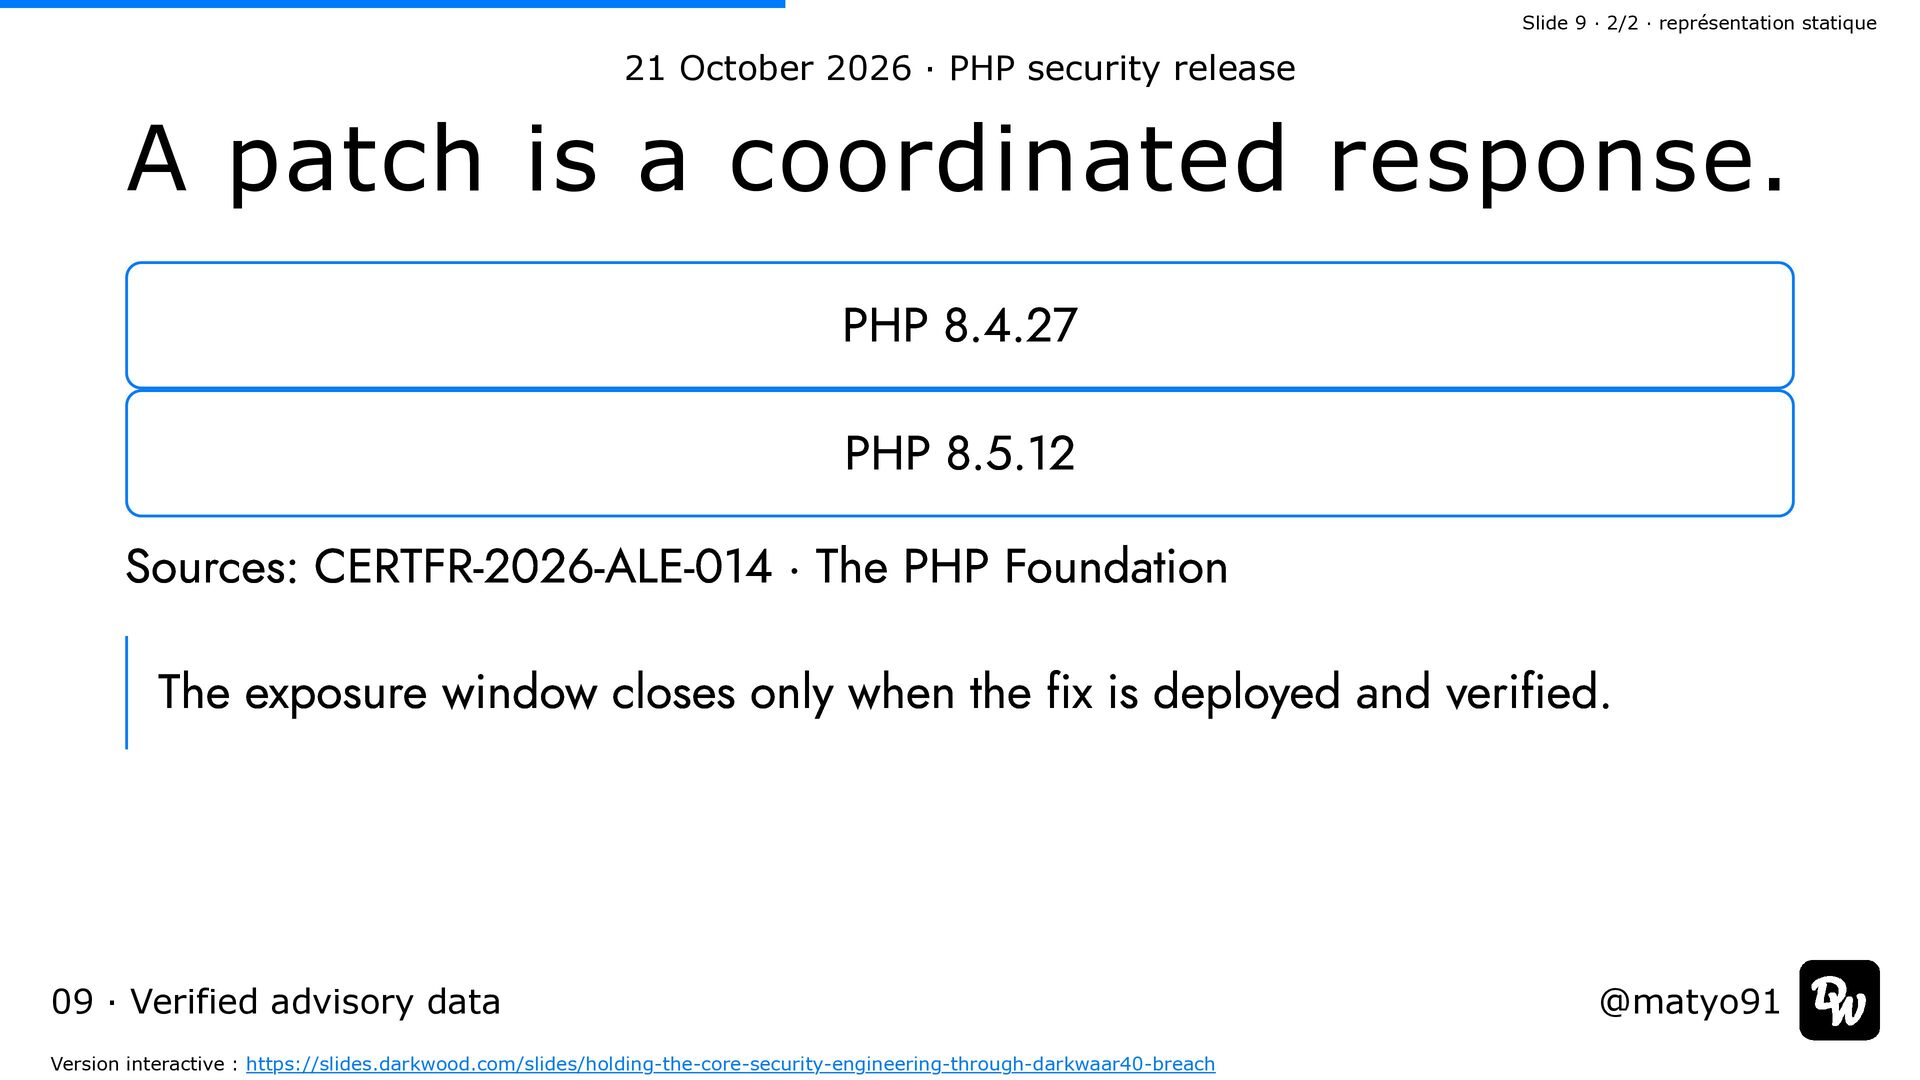
    · PHP security release A patch is a coordinated response. PHP 8.4.27 PHP 8.5.12 Sources: CERTFR-2026-ALE-014 · The PHP Foundation The exposure window closes only when the fix is deployed and verified. 09 · Verified advisory data Version interactive : https://slides.darkwood.com/slides/holding-the-core-security-engineering-through-darkwaar40-breach @matyo91
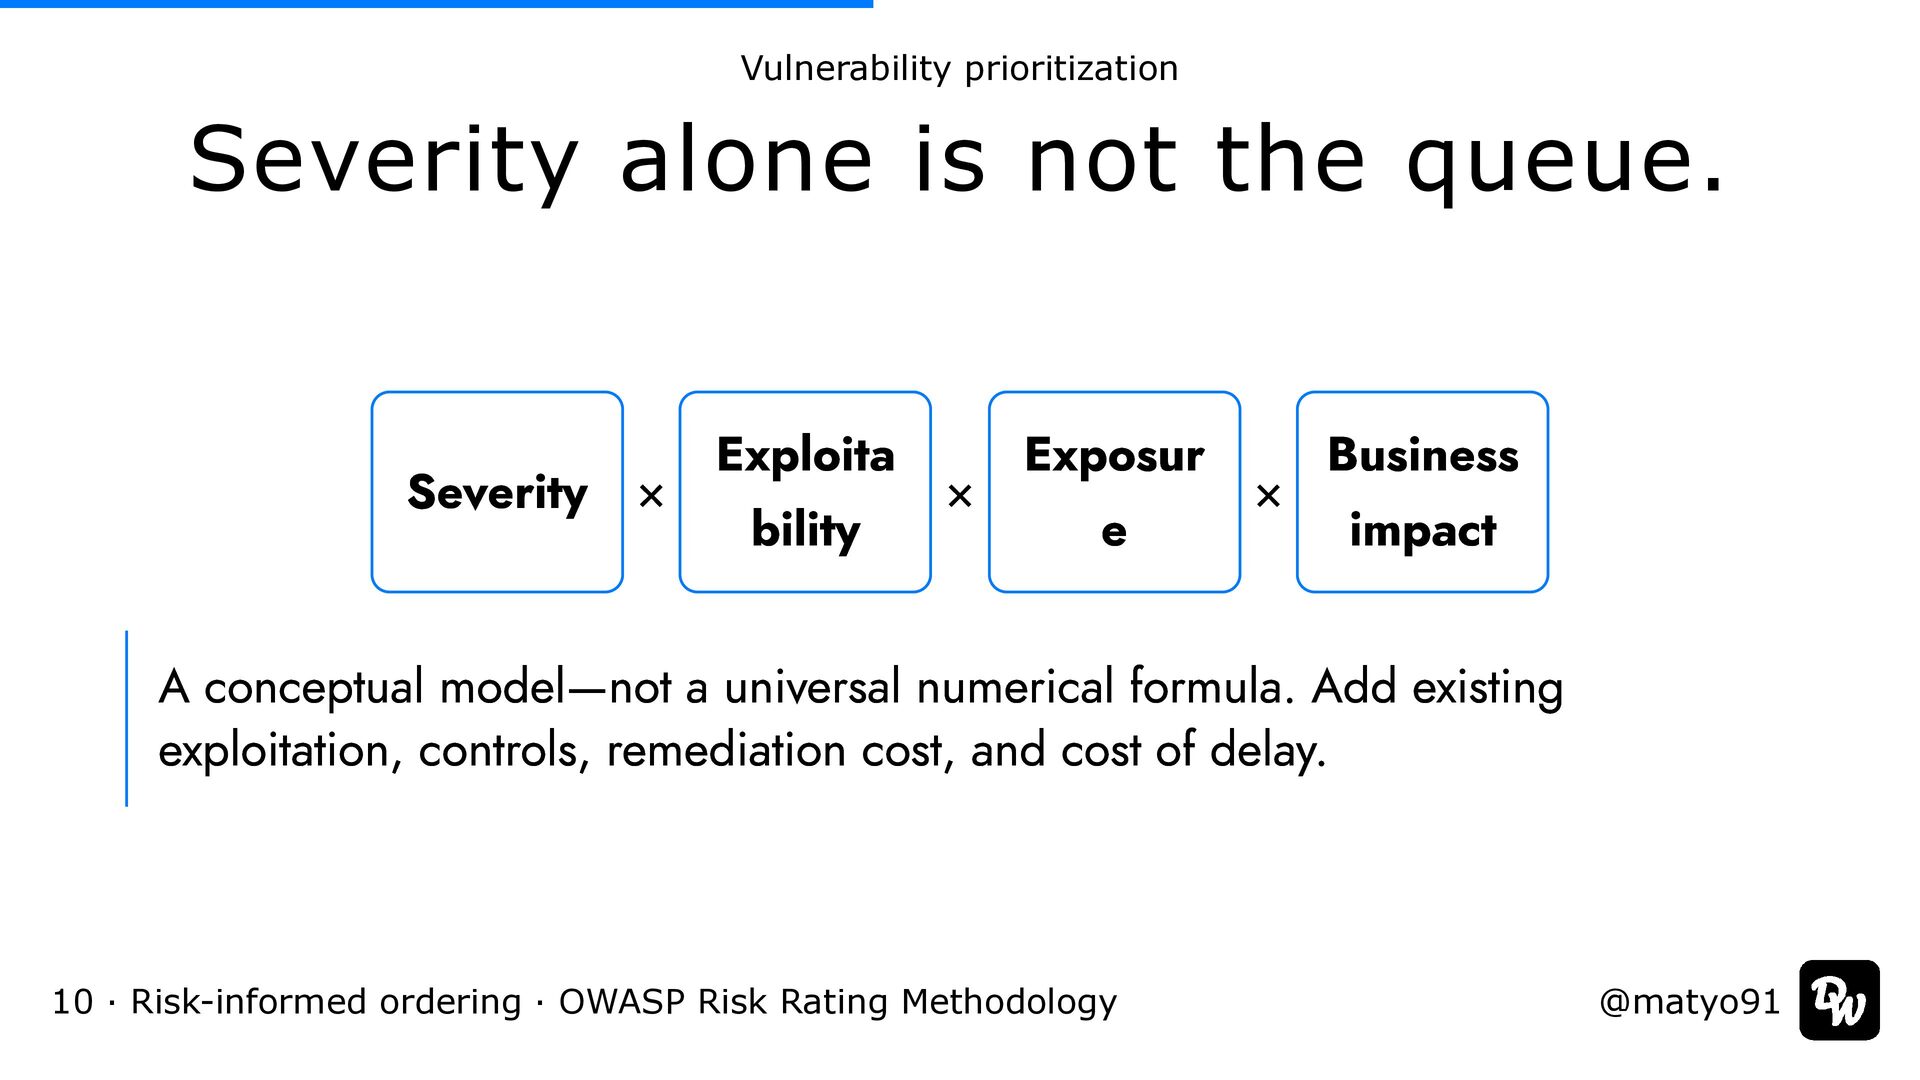
  21. Vulnerability prioritization Severity alone is not the queue. Severity ×

    Exploita bility × Exposur e × Business impact A conceptual model—not a universal numerical formula. Add existing exploitation, controls, remediation cost, and cost of delay. 10 · Risk-informed ordering · OWASP Risk Rating Methodology @matyo91
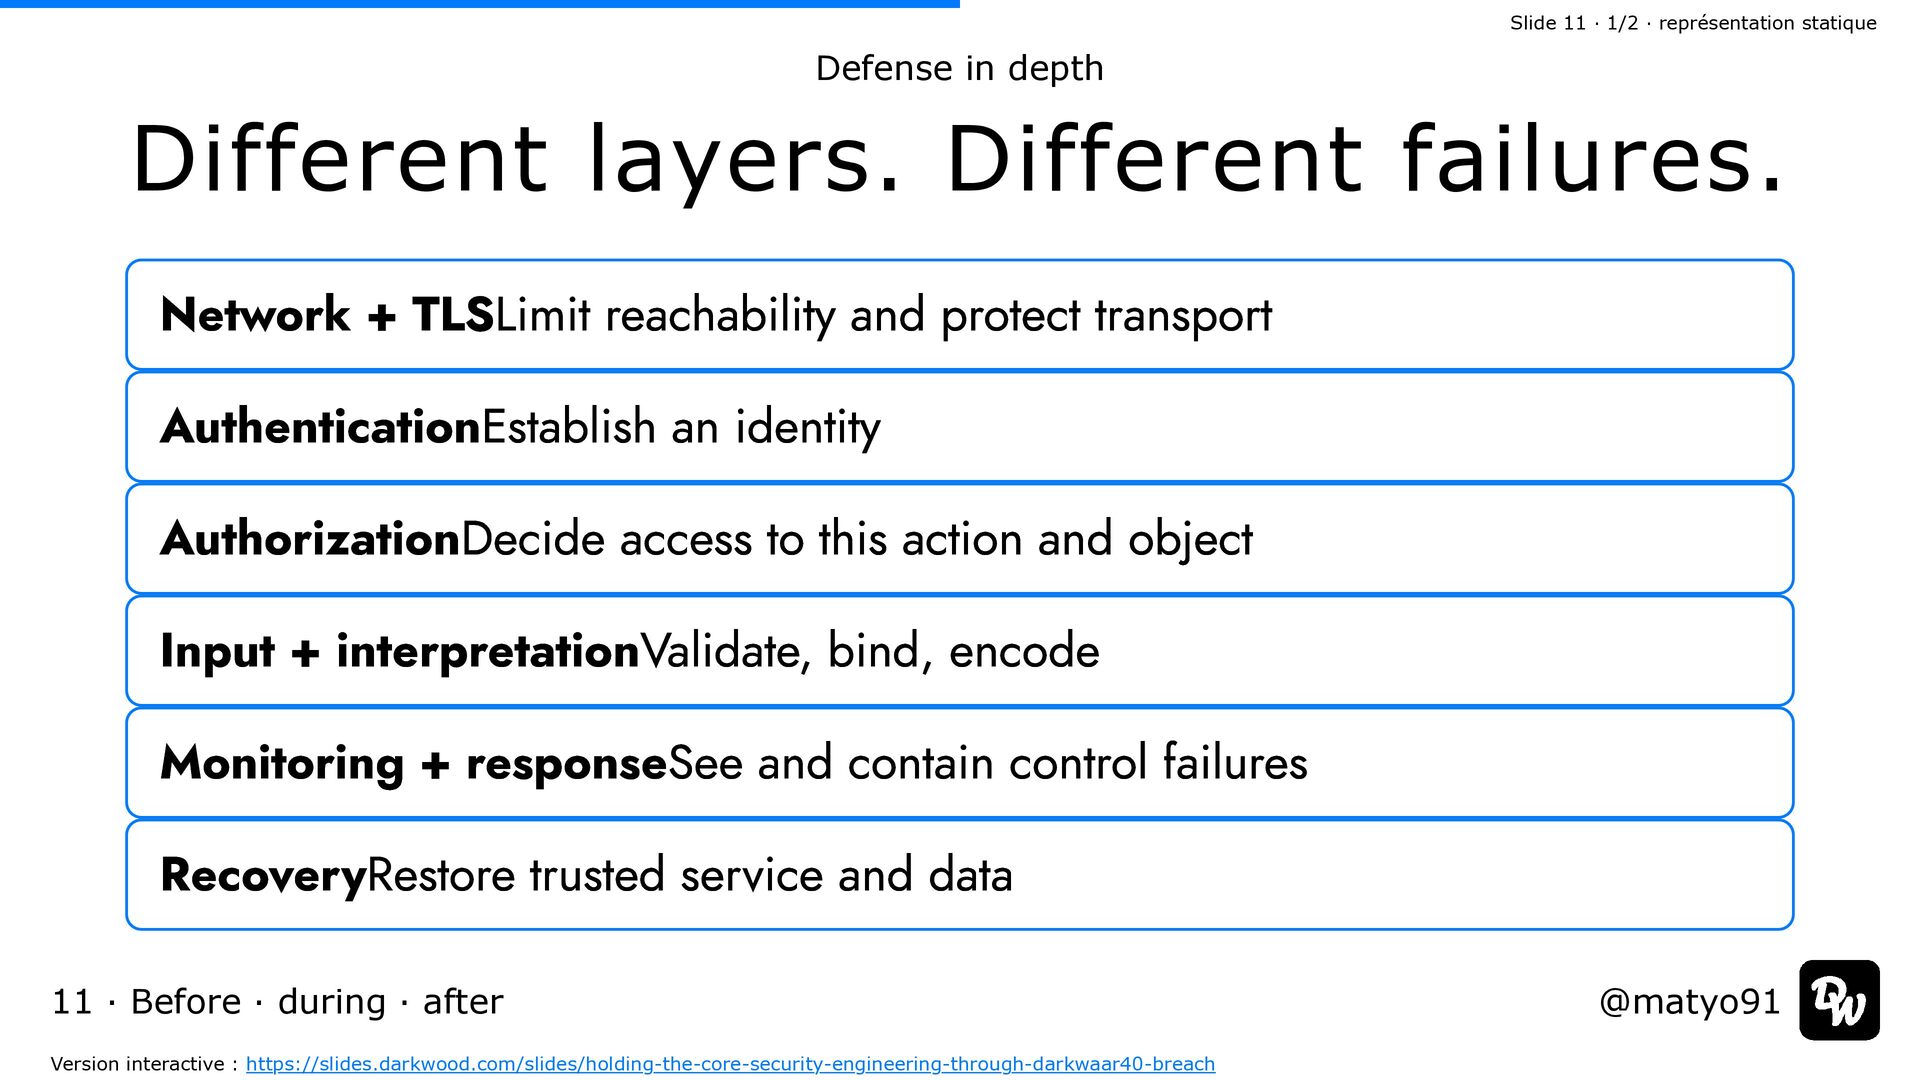
  22. Slide 11 · 1/2 · représentation statique Defense in depth

    Different layers. Different failures. Network + TLSLimit reachability and protect transport AuthenticationEstablish an identity AuthorizationDecide access to this action and object Input + interpretationValidate, bind, encode Monitoring + responseSee and contain control failures RecoveryRestore trusted service and data 11 · Before · during · after Version interactive : https://slides.darkwood.com/slides/holding-the-core-security-engineering-through-darkwaar40-breach @matyo91
  23. Slide 11 · 2/2 · représentation statique Defense in depth

    Different layers. Different failures. Layering reduces the chance that one defect becomes total compromise. 11 · Before · during · after Version interactive : https://slides.darkwood.com/slides/holding-the-core-security-engineering-through-darkwaar40-breach @matyo91
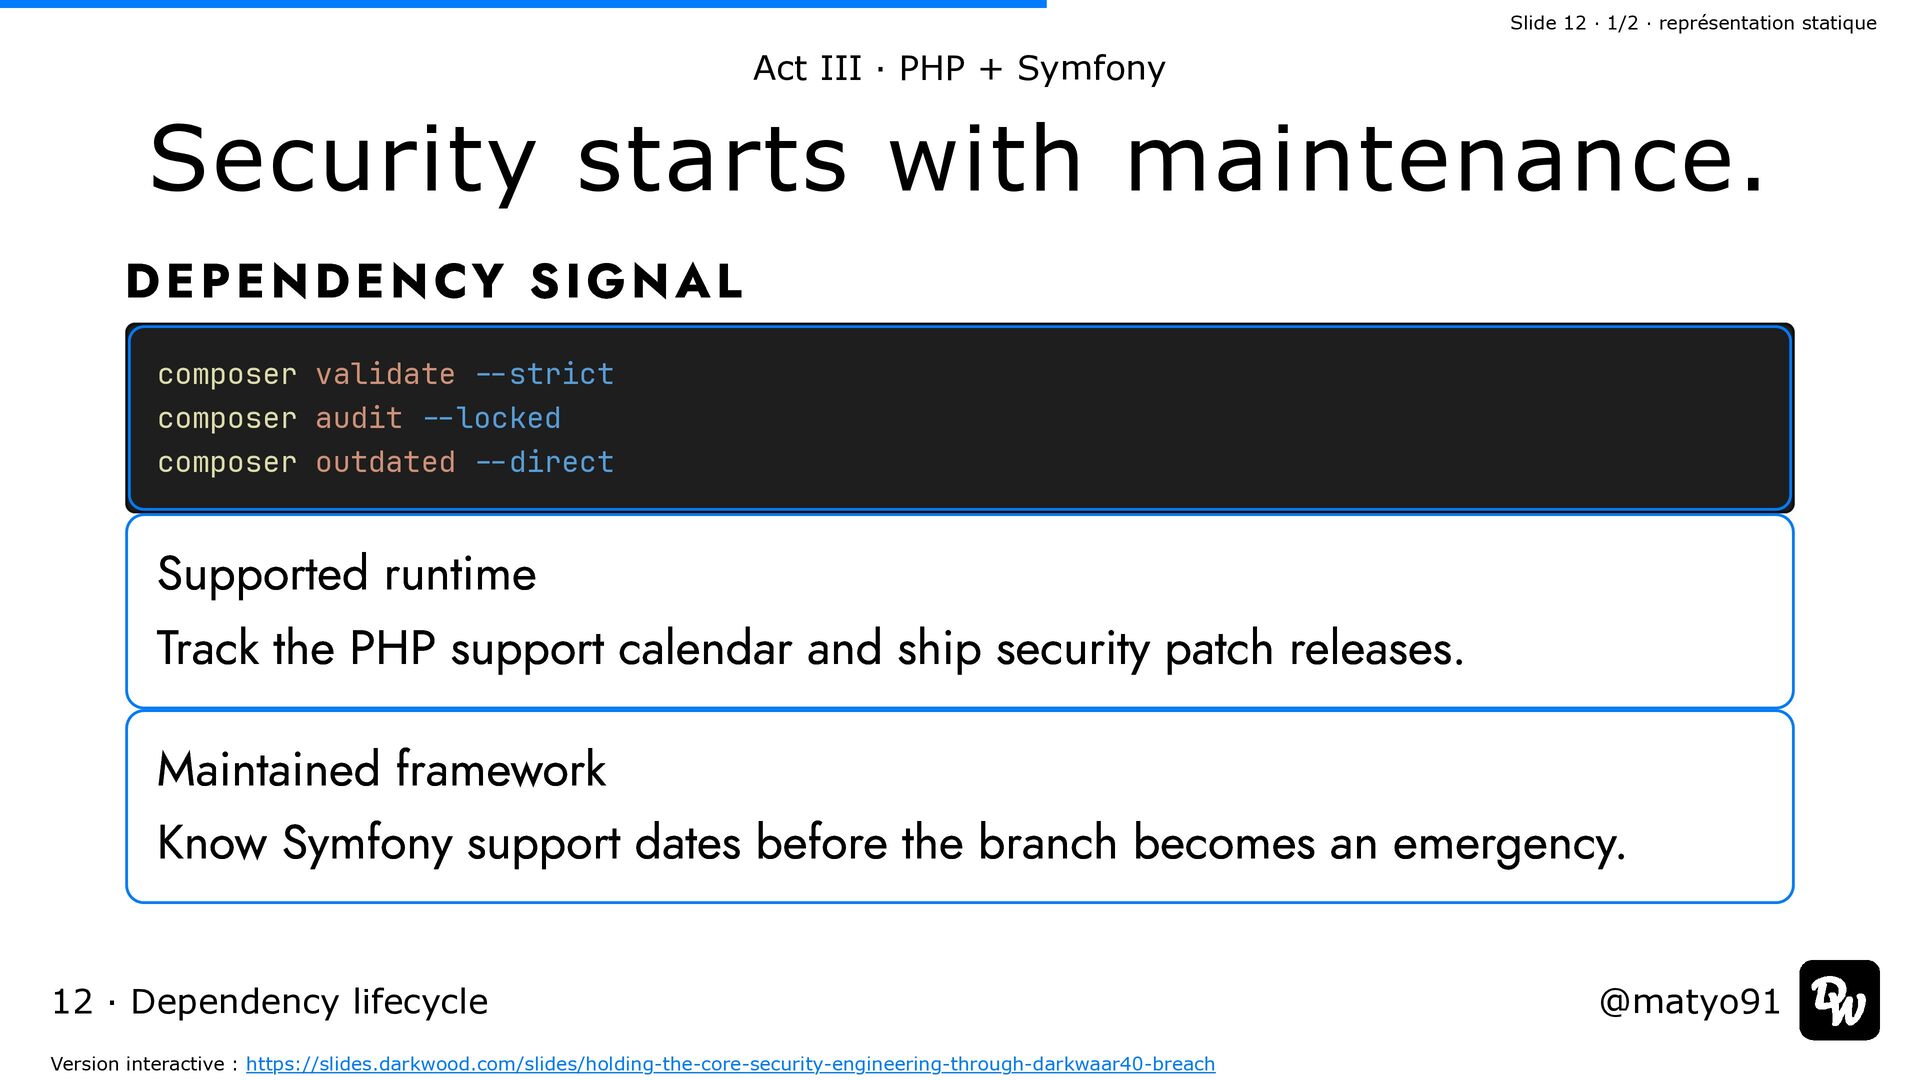
  24. Slide 12 · 1/2 · représentation statique Act III ·

    PHP + Symfony Security starts with maintenance. D E P E N D E N CY S I G N A L composer validate --strict composer audit --locked composer outdated --direct Supported runtime Track the PHP support calendar and ship security patch releases. Maintained framework Know Symfony support dates before the branch becomes an emergency. 12 · Dependency lifecycle Version interactive : https://slides.darkwood.com/slides/holding-the-core-security-engineering-through-darkwaar40-breach @matyo91
  25. Slide 12 · 2/2 · représentation statique Act III ·

    PHP + Symfony Security starts with maintenance. Continuous audit Run Composer audit in CI and on a schedule—not from memory. Sources: php.net/supported-versions.php · symfony.com/releases · getcomposer.org/doc/03-cli.md#audit 12 · Dependency lifecycle Version interactive : https://slides.darkwood.com/slides/holding-the-core-security-engineering-through-darkwaar40-breach @matyo91
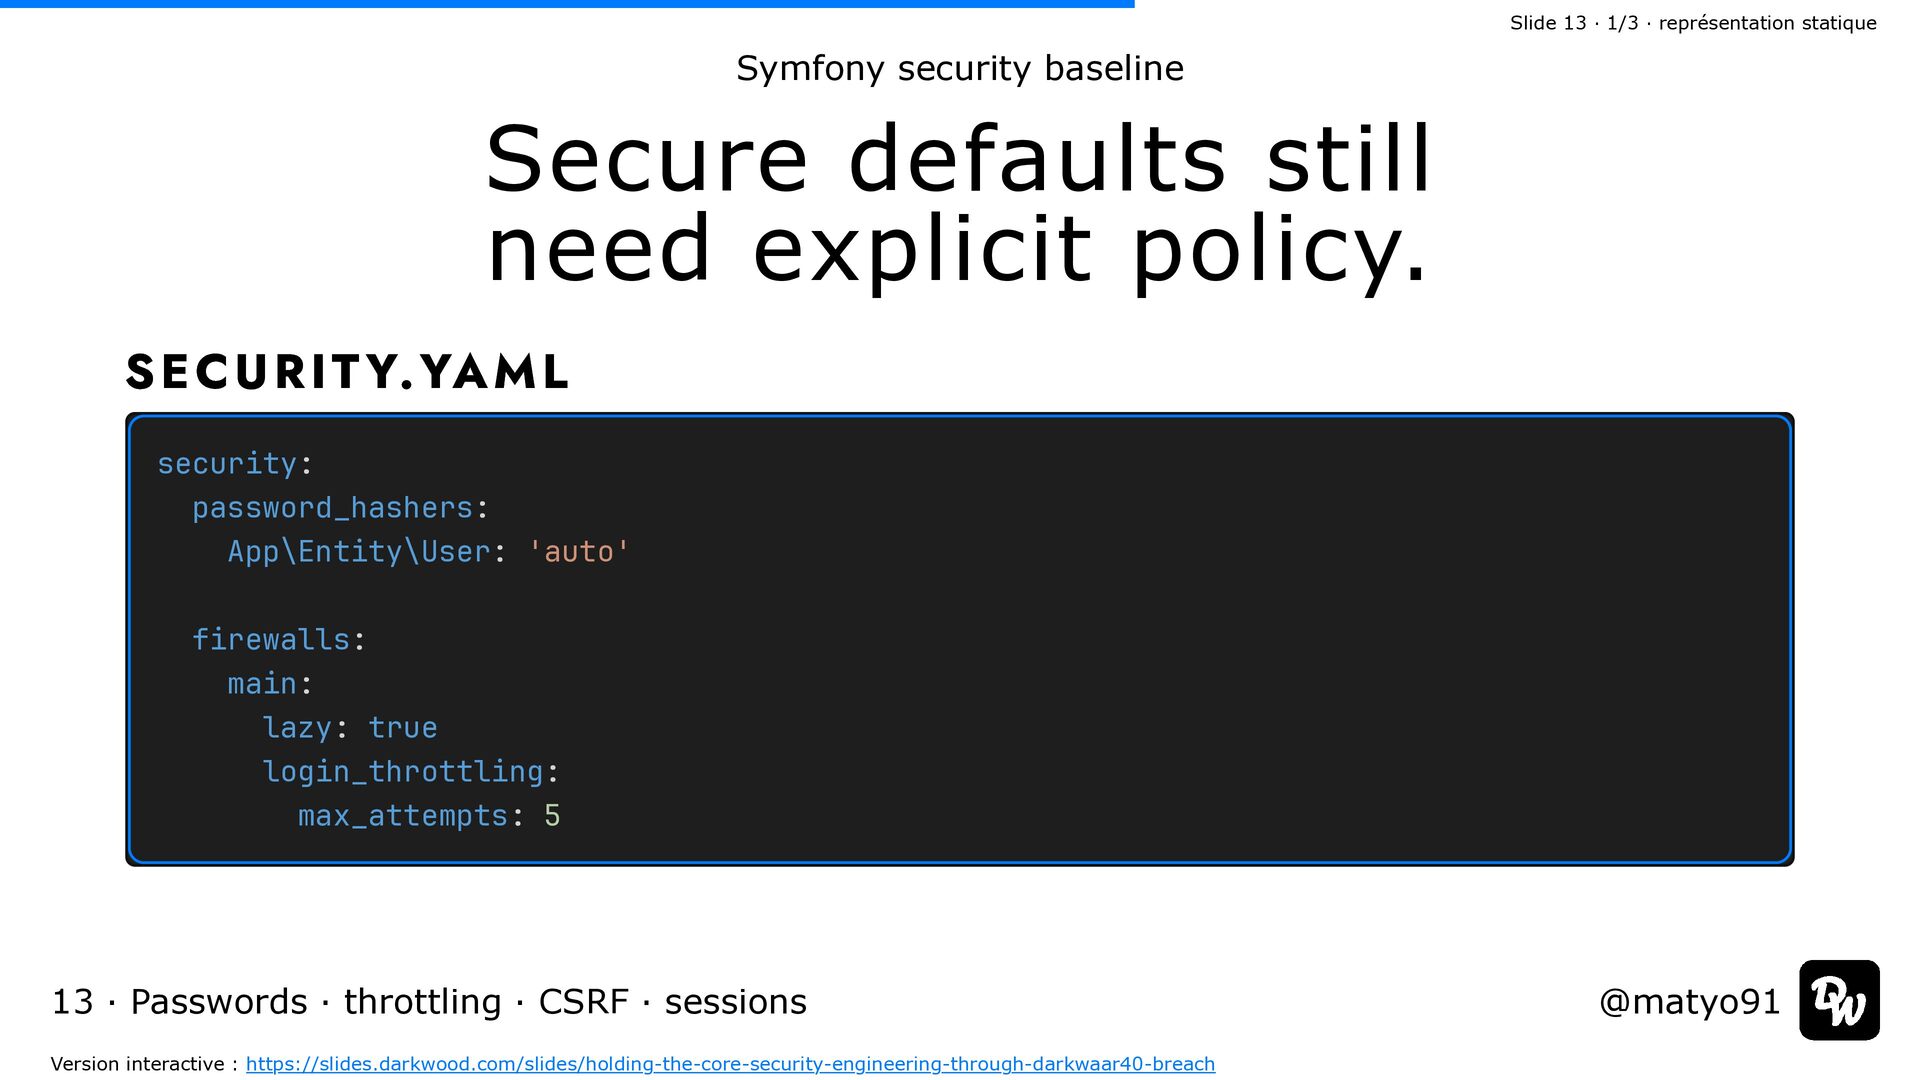
  26. Slide 13 · 1/3 · représentation statique Symfony security baseline

    Secure defaults still need explicit policy. S E C U R I T Y. YA M L security: password_hashers: App\Entity\User: 'auto' firewalls: main: lazy: true login_throttling: max_attempts: 5 13 · Passwords · throttling · CSRF · sessions Version interactive : https://slides.darkwood.com/slides/holding-the-core-security-engineering-through-darkwaar40-breach @matyo91
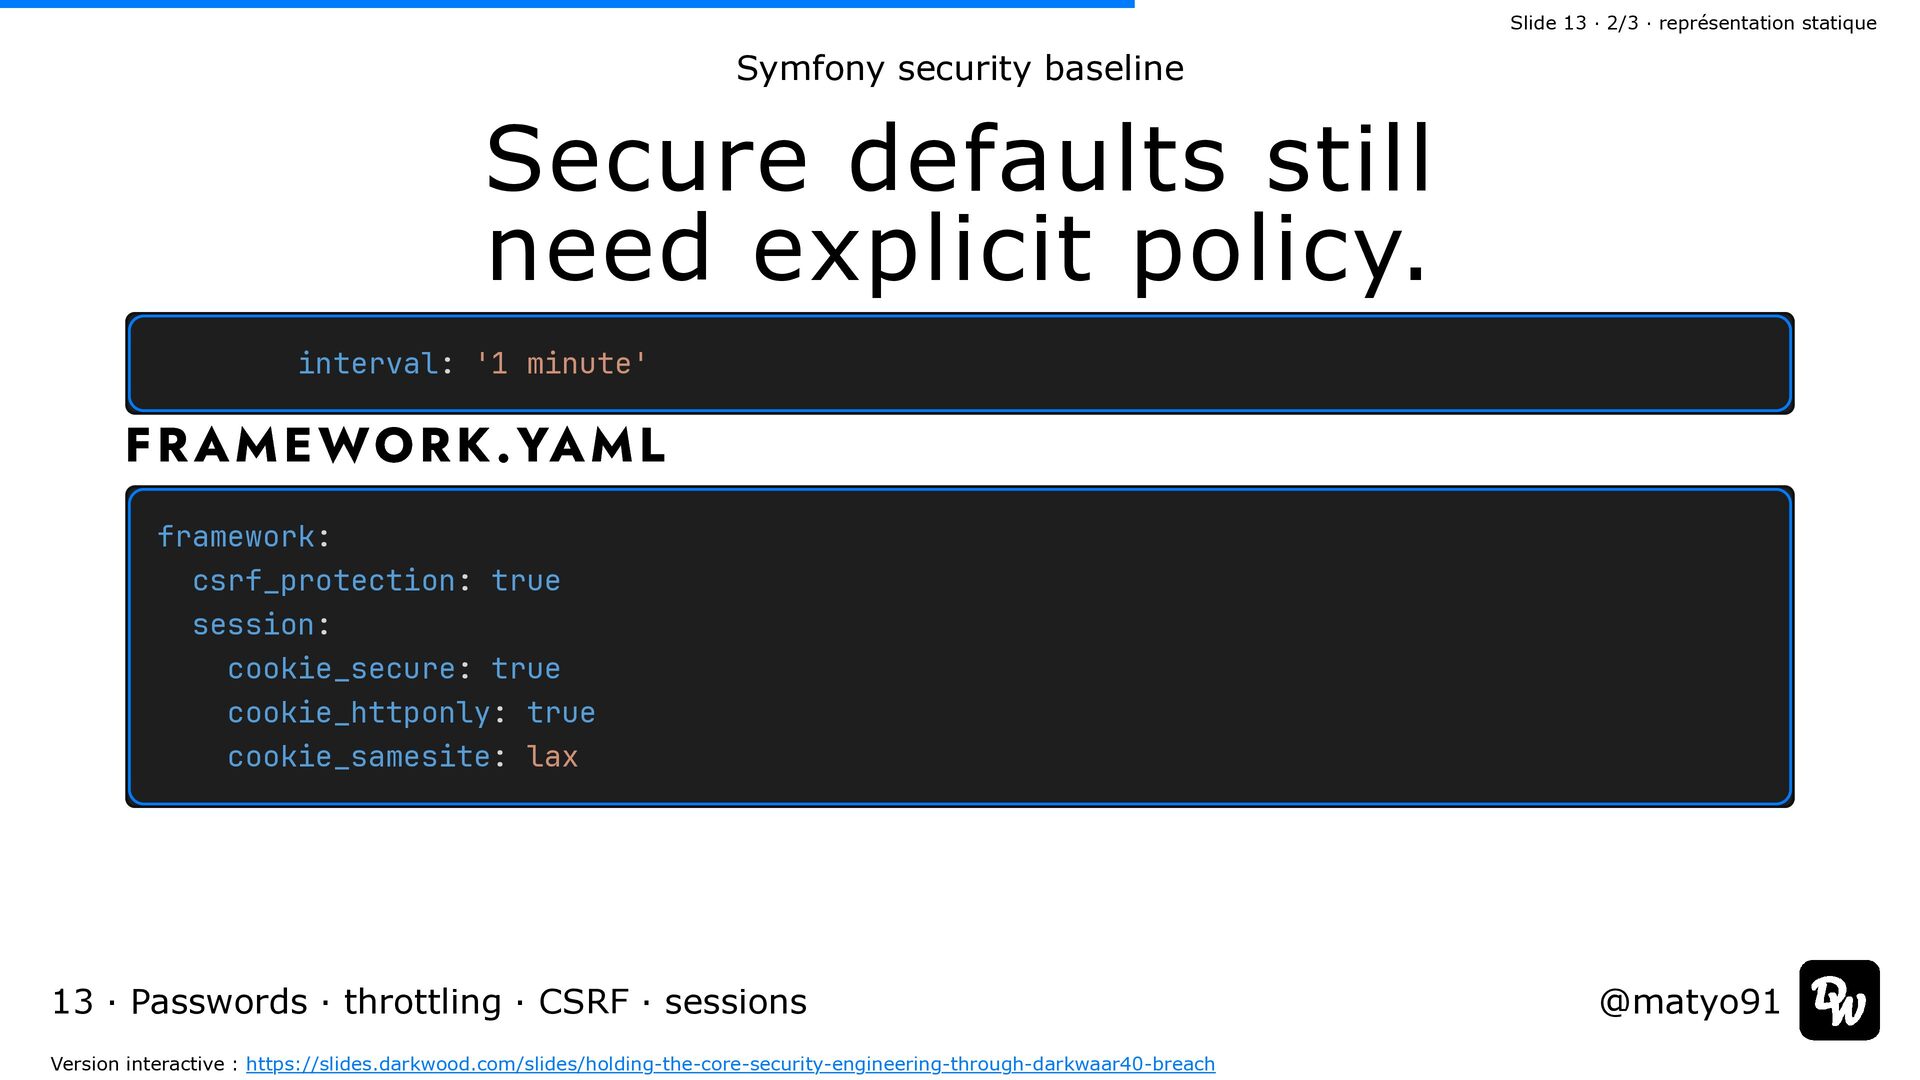
  27. Slide 13 · 2/3 · représentation statique Symfony security baseline

    Secure defaults still need explicit policy. interval: '1 minute' F R A M E W O R K . YA M L framework: csrf_protection: true session: cookie_secure: true cookie_httponly: true cookie_samesite: lax 13 · Passwords · throttling · CSRF · sessions Version interactive : https://slides.darkwood.com/slides/holding-the-core-security-engineering-through-darkwaar40-breach @matyo91
  28. Slide 13 · 3/3 · représentation statique Symfony security baseline

    Secure defaults still need explicit policy. Application throttling raises brute-force cost. DDoS protection belongs at a cheaper edge. 13 · Passwords · throttling · CSRF · sessions Version interactive : https://slides.darkwood.com/slides/holding-the-core-security-engineering-through-darkwaar40-breach @matyo91
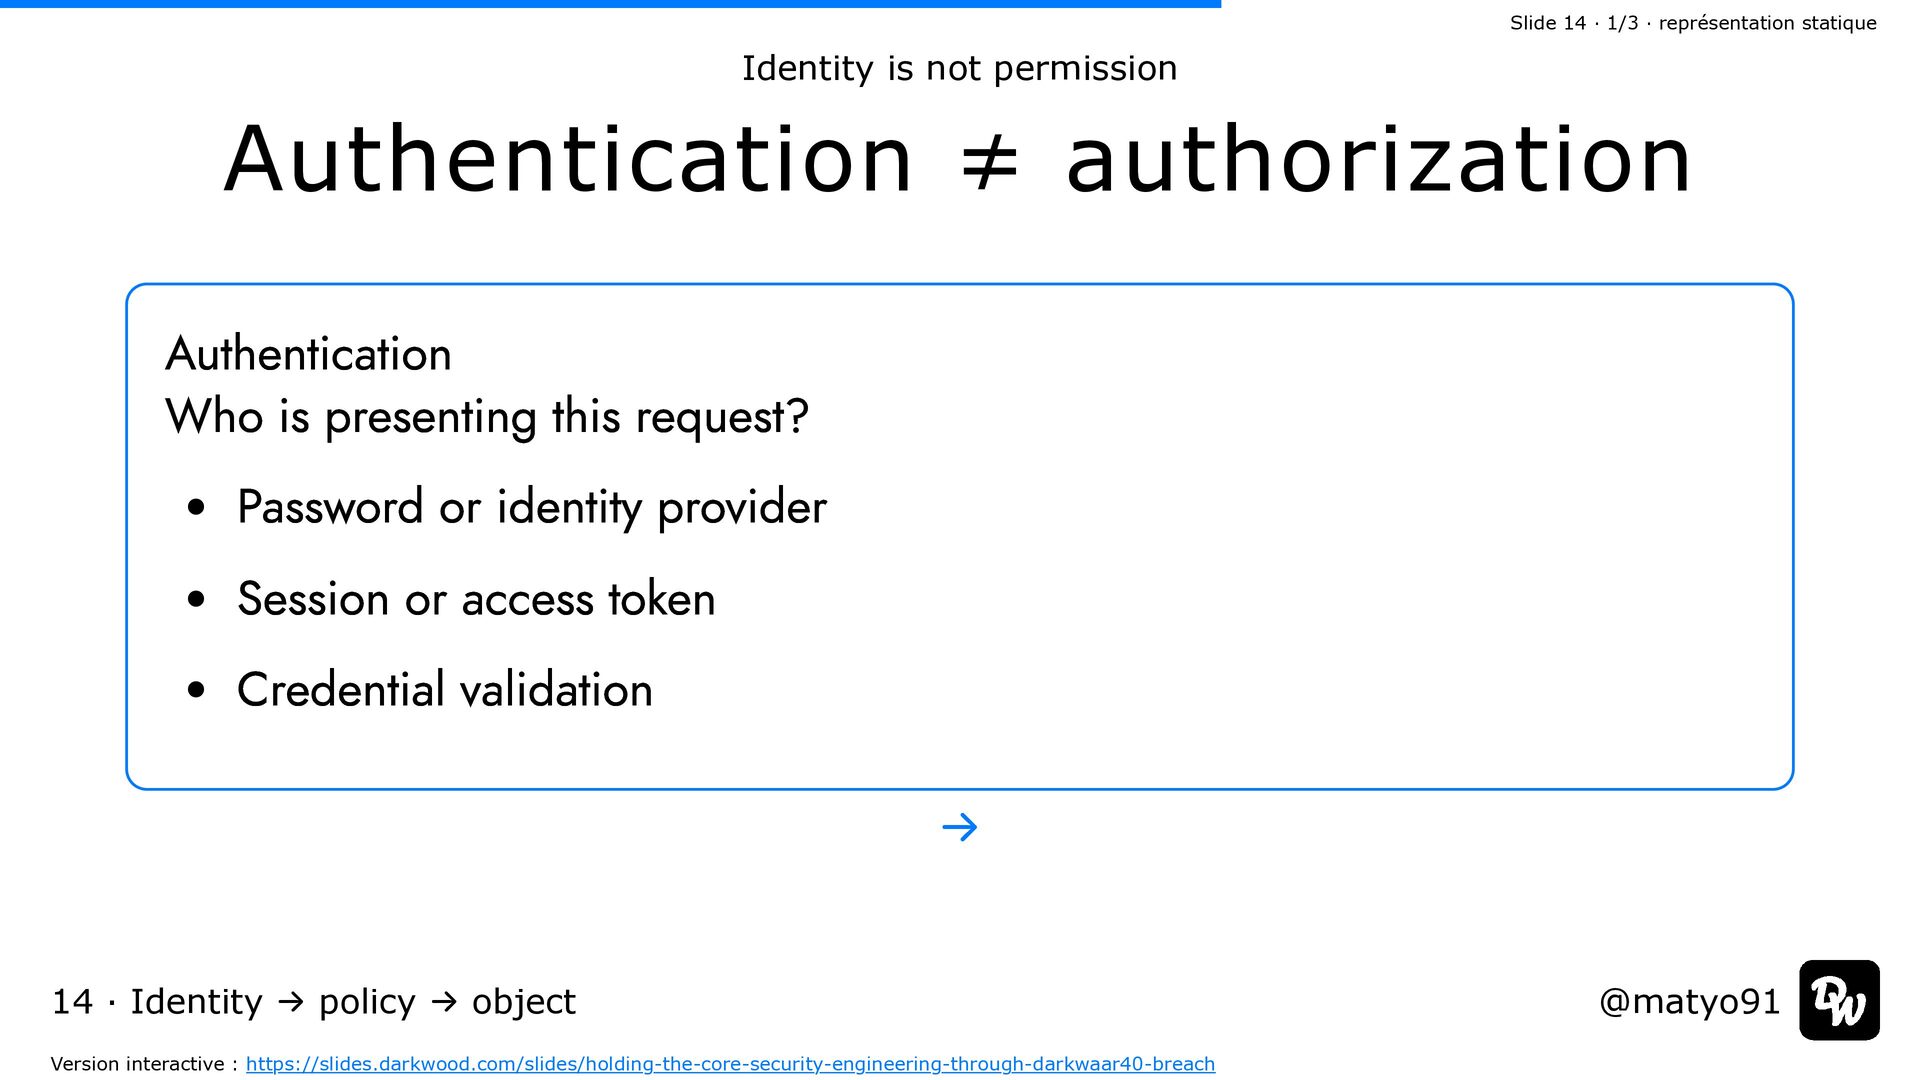
  29. Slide 14 · 1/3 · représentation statique Identity is not

    permission Authentication ≠ authorization Authentication Who is presenting this request? Password or identity provider Session or access token Credential validation → 14 · Identity → policy → object Version interactive : https://slides.darkwood.com/slides/holding-the-core-security-engineering-through-darkwaar40-breach @matyo91
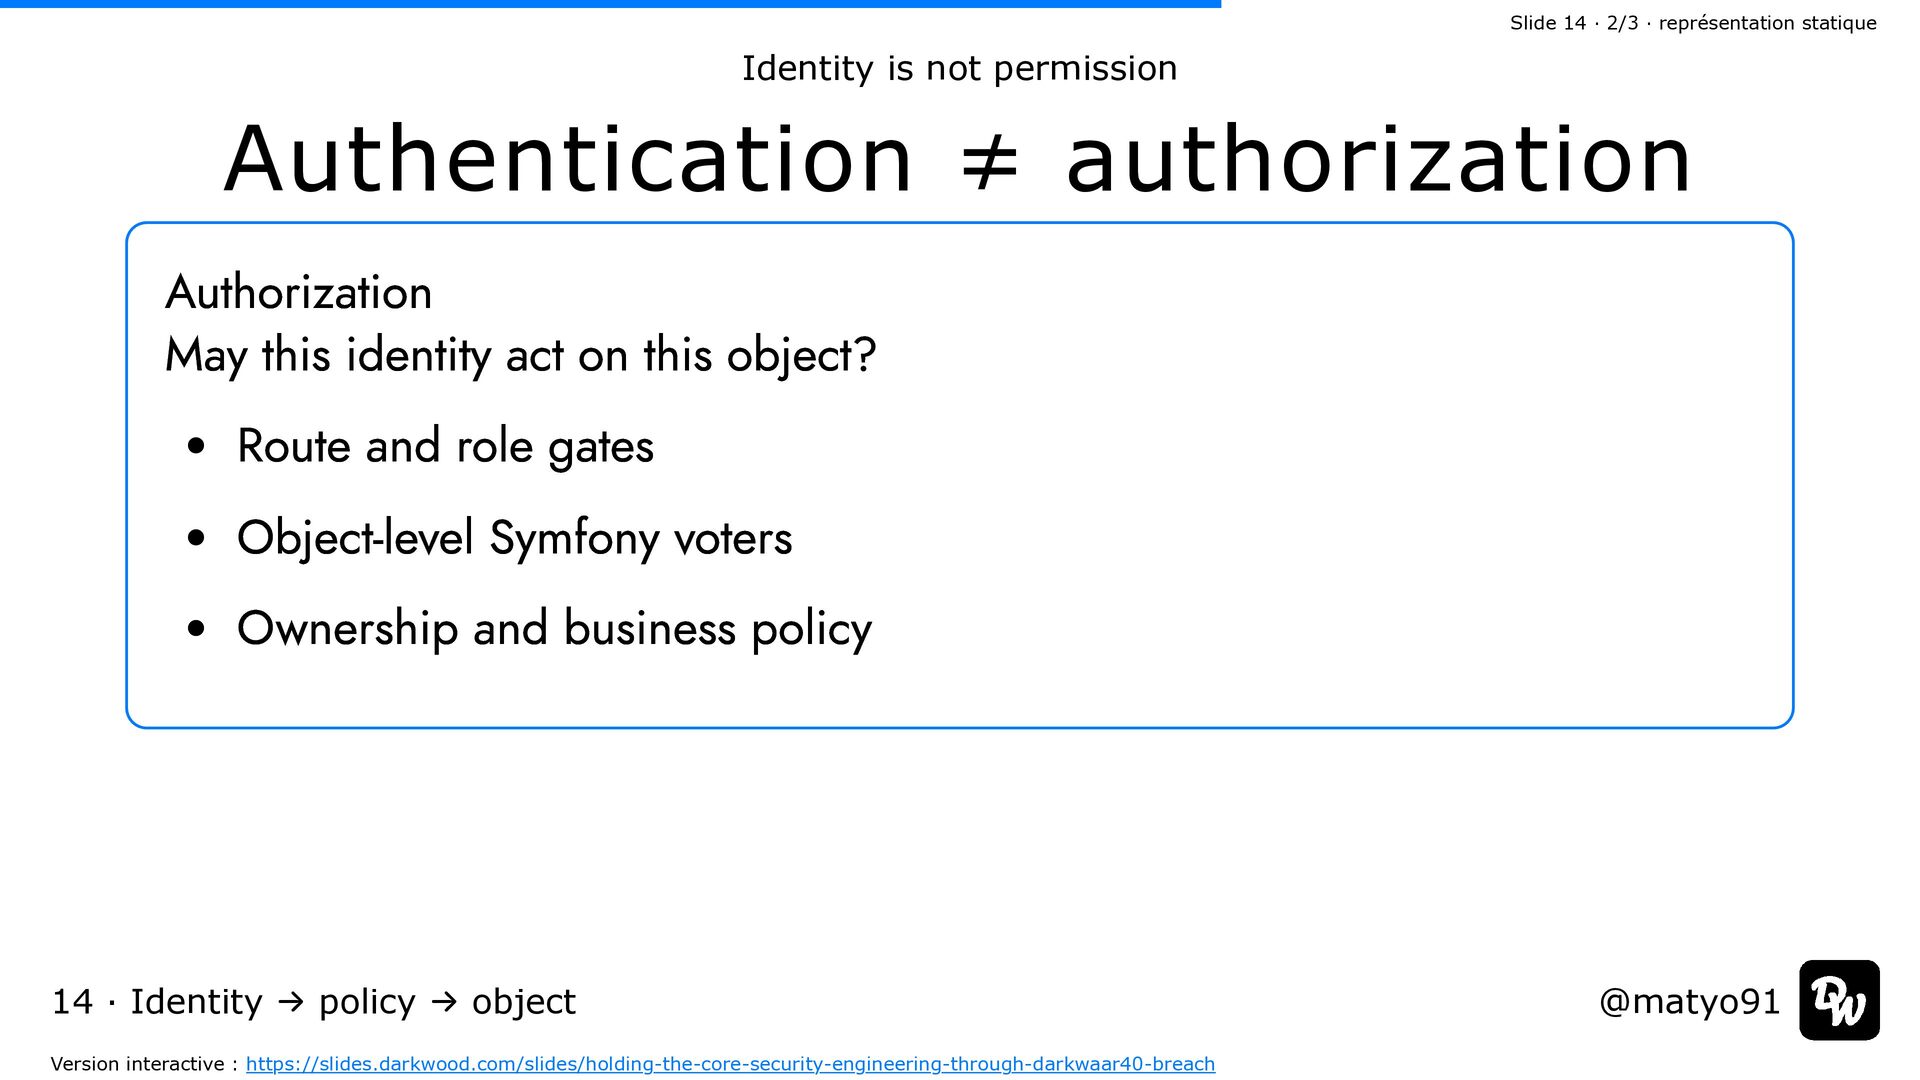
  30. Slide 14 · 2/3 · représentation statique Identity is not

    permission Authentication ≠ authorization Authorization May this identity act on this object? Route and role gates Object-level Symfony voters Ownership and business policy 14 · Identity → policy → object Version interactive : https://slides.darkwood.com/slides/holding-the-core-security-engineering-through-darkwaar40-breach @matyo91
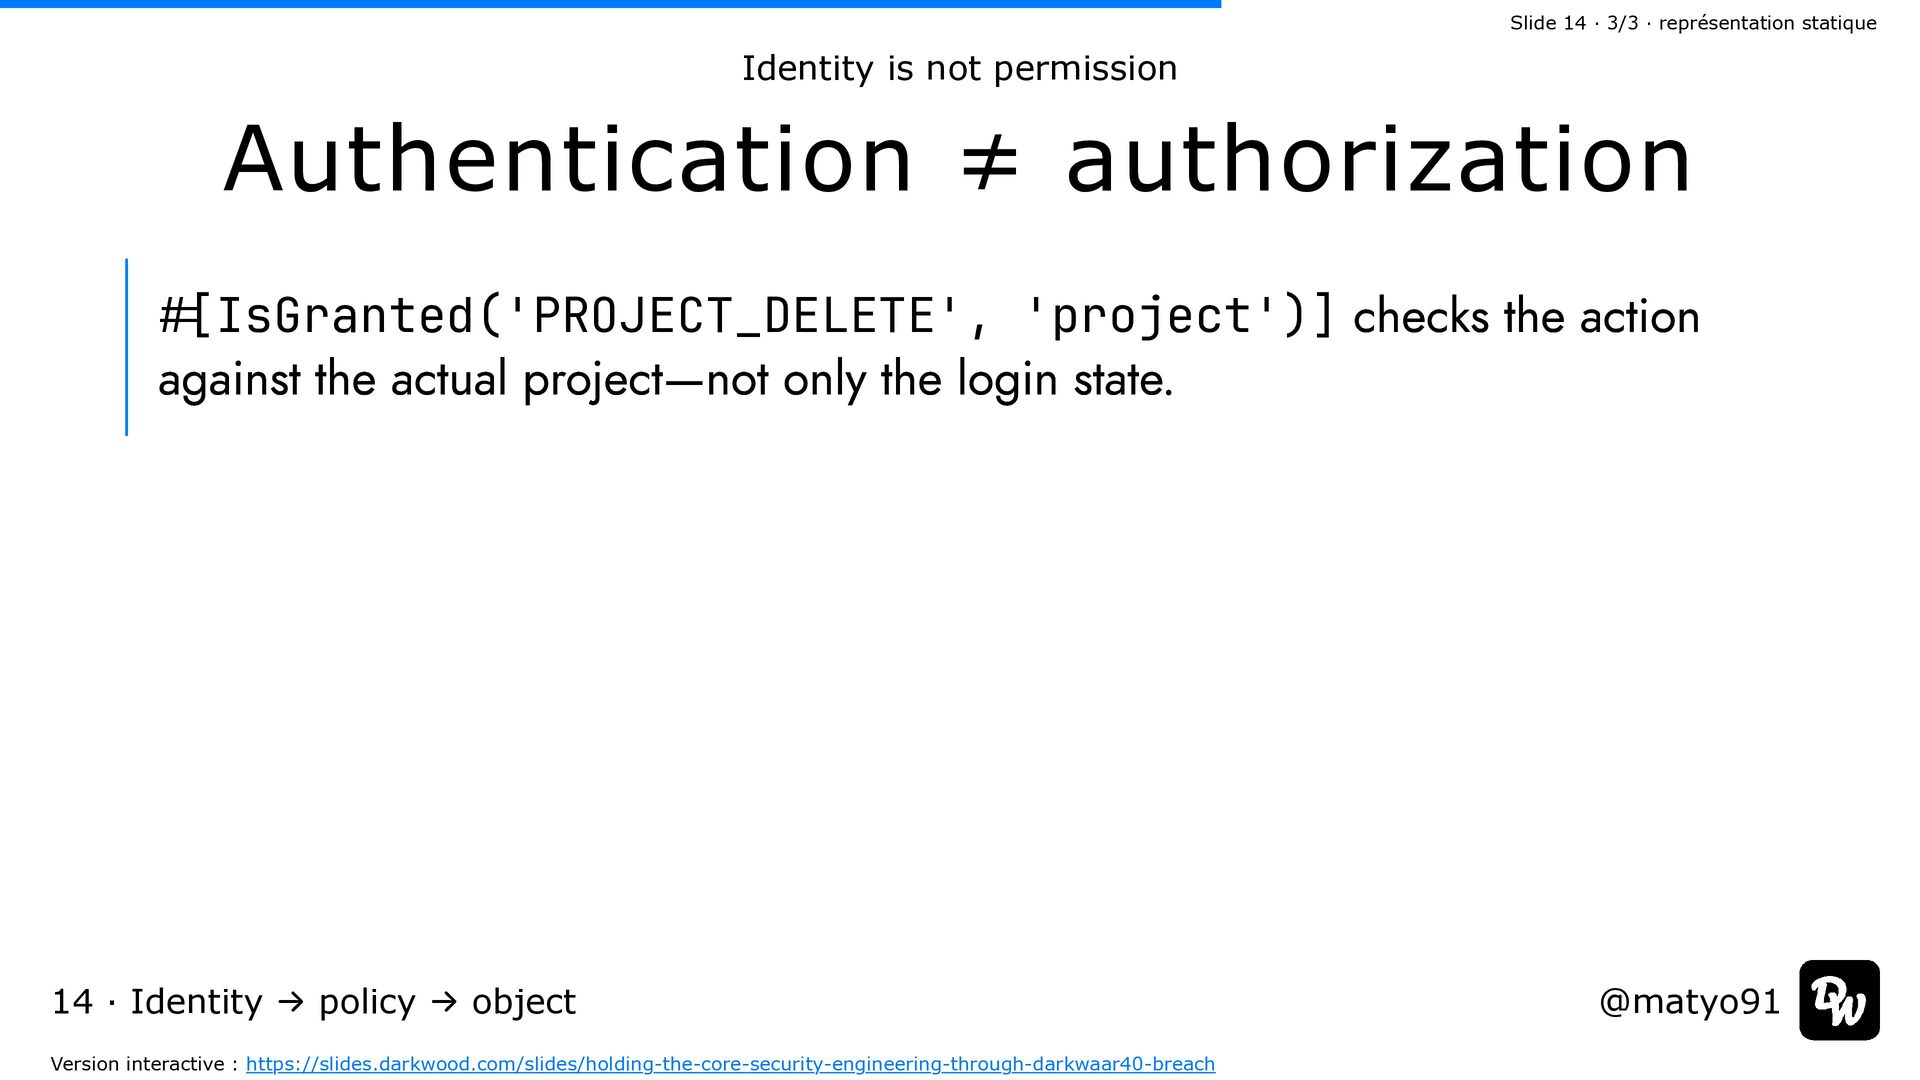
  31. Slide 14 · 3/3 · représentation statique Identity is not

    permission Authentication ≠ authorization #[IsGranted('PROJECT_DELETE', 'project')] checks the action against the actual project—not only the login state. 14 · Identity → policy → object Version interactive : https://slides.darkwood.com/slides/holding-the-core-security-engineering-through-darkwaar40-breach @matyo91
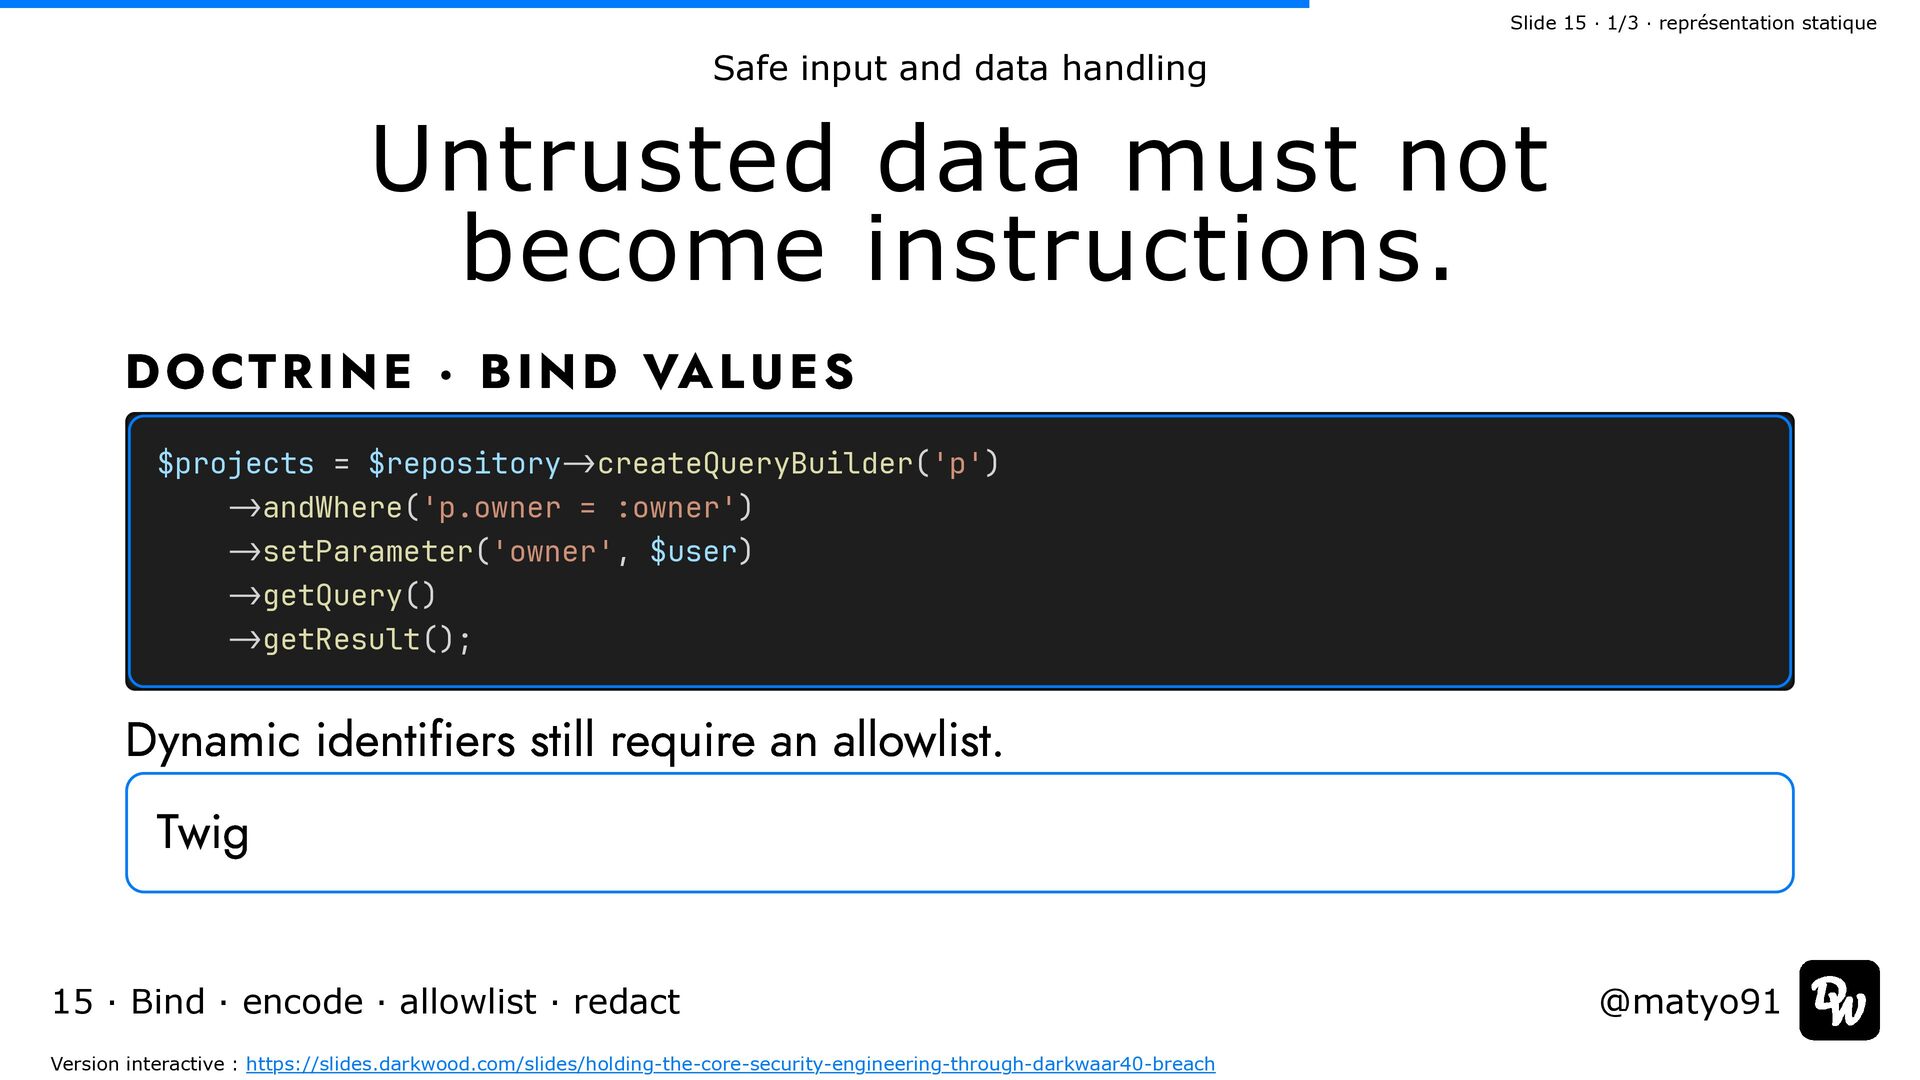
  32. Slide 15 · 1/3 · représentation statique Safe input and

    data handling Untrusted data must not become instructions. D O CT R I N E · B I N D VA L U E S $projects = $repository->createQueryBuilder('p') ->andWhere('p.owner = :owner') ->setParameter('owner', $user) ->getQuery() ->getResult(); Dynamic identifiers still require an allowlist. Twig 15 · Bind · encode · allowlist · redact Version interactive : https://slides.darkwood.com/slides/holding-the-core-security-engineering-through-darkwaar40-breach @matyo91
  33. Slide 15 · 2/3 · représentation statique Safe input and

    data handling Untrusted data must not become instructions. Keep contextual auto-escaping. Audit every |raw. Secrets Use a deployment manager or Symfony vault; keep keys separate. Logs Exclude passwords, session IDs, access tokens, and private keys. 15 · Bind · encode · allowlist · redact Version interactive : https://slides.darkwood.com/slides/holding-the-core-security-engineering-through-darkwaar40-breach @matyo91
  34. Slide 15 · 3/3 · représentation statique Safe input and

    data handling Untrusted data must not become instructions. Deploy Production mode, least privilege, narrow web root, tested headers. 15 · Bind · encode · allowlist · redact Version interactive : https://slides.darkwood.com/slides/holding-the-core-security-engineering-through-darkwaar40-breach @matyo91
  35. Slide 16 · 1/3 · représentation statique Act IV ·

    Darkwood Identity Why replace custom SSO? Custom protocol Locally designed redirect rules Custom token semantics Private key-rotation behavior Application-specific testing surface Long-term maintenance ownership → 16 · Reduce custom authentication behavior Version interactive : https://slides.darkwood.com/slides/holding-the-core-security-engineering-through-darkwaar40-breach @matyo91
  36. Slide 16 · 2/3 · représentation statique Act IV ·

    Darkwood Identity Why replace custom SSO? OpenID Connect Authorization Code flow PKCE S256, state, nonce Discovery and JWKS Standard token claims Interoperable libraries and tooling 16 · Reduce custom authentication behavior Version interactive : https://slides.darkwood.com/slides/holding-the-core-security-engineering-through-darkwaar40-breach @matyo91
  37. Slide 16 · 3/3 · représentation statique Act IV ·

    Darkwood Identity Why replace custom SSO? Standards do not remove security work. They make the required work explicit and reviewable. 16 · Reduce custom authentication behavior Version interactive : https://slides.darkwood.com/slides/holding-the-core-security-engineering-through-darkwaar40-breach @matyo91
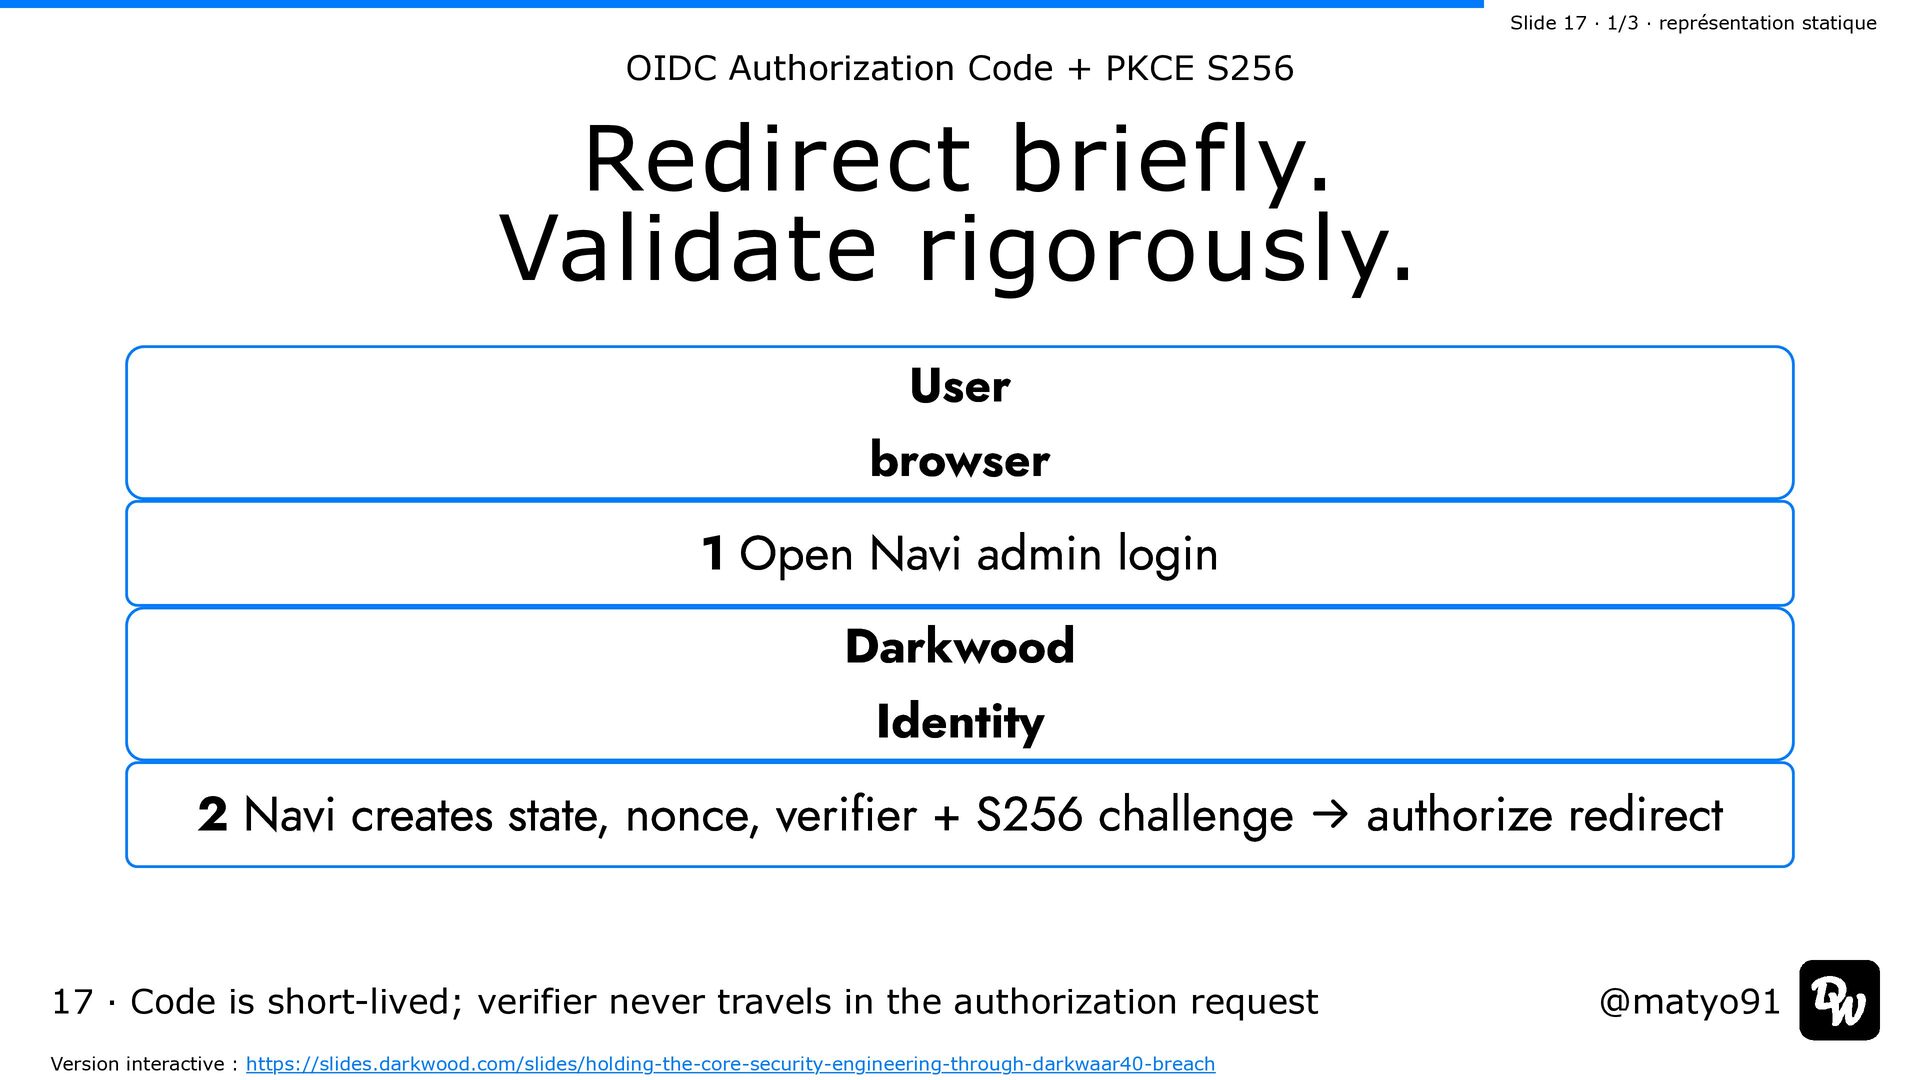
  38. Slide 17 · 1/3 · représentation statique OIDC Authorization Code

    + PKCE S256 Redirect briefly. Validate rigorously. User browser 1 Open Navi admin login Darkwood Identity 2 Navi creates state, nonce, verifier + S256 challenge → authorize redirect 17 · Code is short-lived; verifier never travels in the authorization request Version interactive : https://slides.darkwood.com/slides/holding-the-core-security-engineering-through-darkwaar40-breach @matyo91
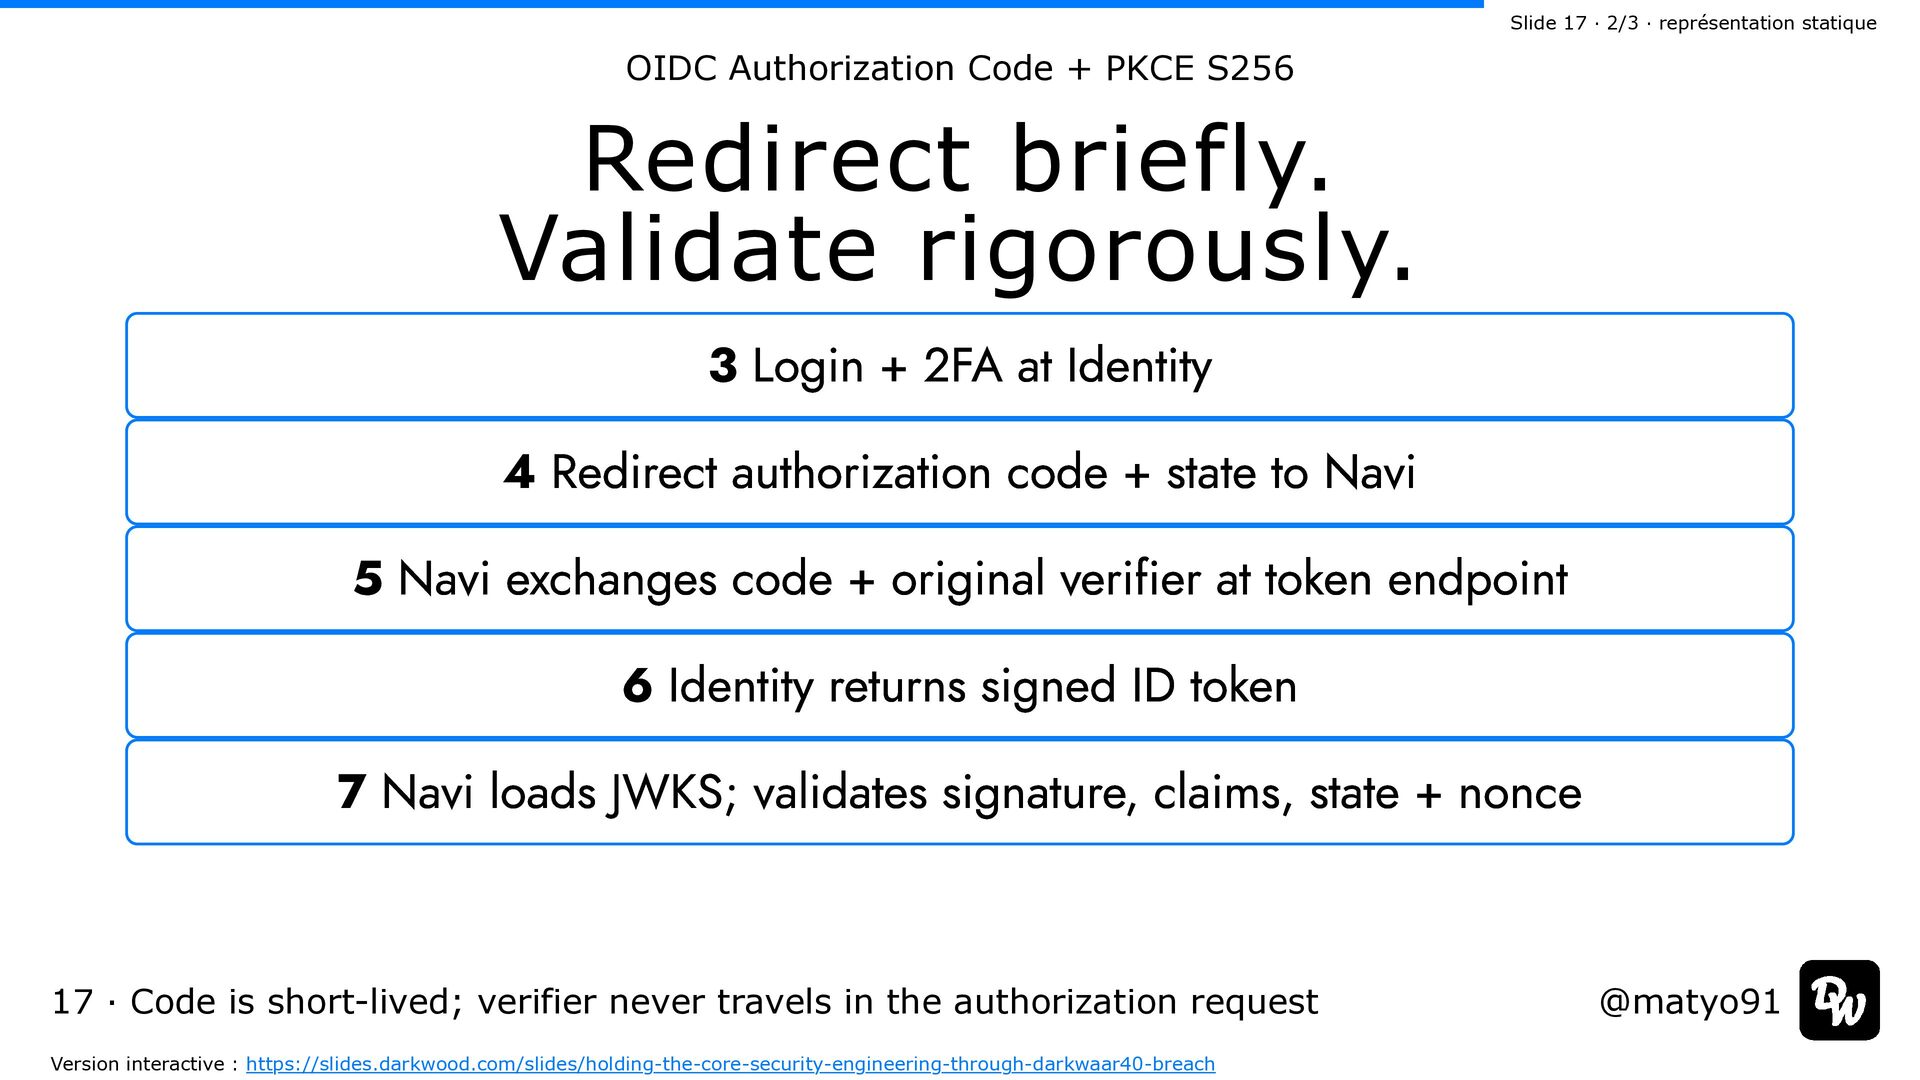
  39. Slide 17 · 2/3 · représentation statique OIDC Authorization Code

    + PKCE S256 Redirect briefly. Validate rigorously. 3 Login + 2FA at Identity 4 Redirect authorization code + state to Navi 5 Navi exchanges code + original verifier at token endpoint 6 Identity returns signed ID token 7 Navi loads JWKS; validates signature, claims, state + nonce 17 · Code is short-lived; verifier never travels in the authorization request Version interactive : https://slides.darkwood.com/slides/holding-the-core-security-engineering-through-darkwaar40-breach @matyo91
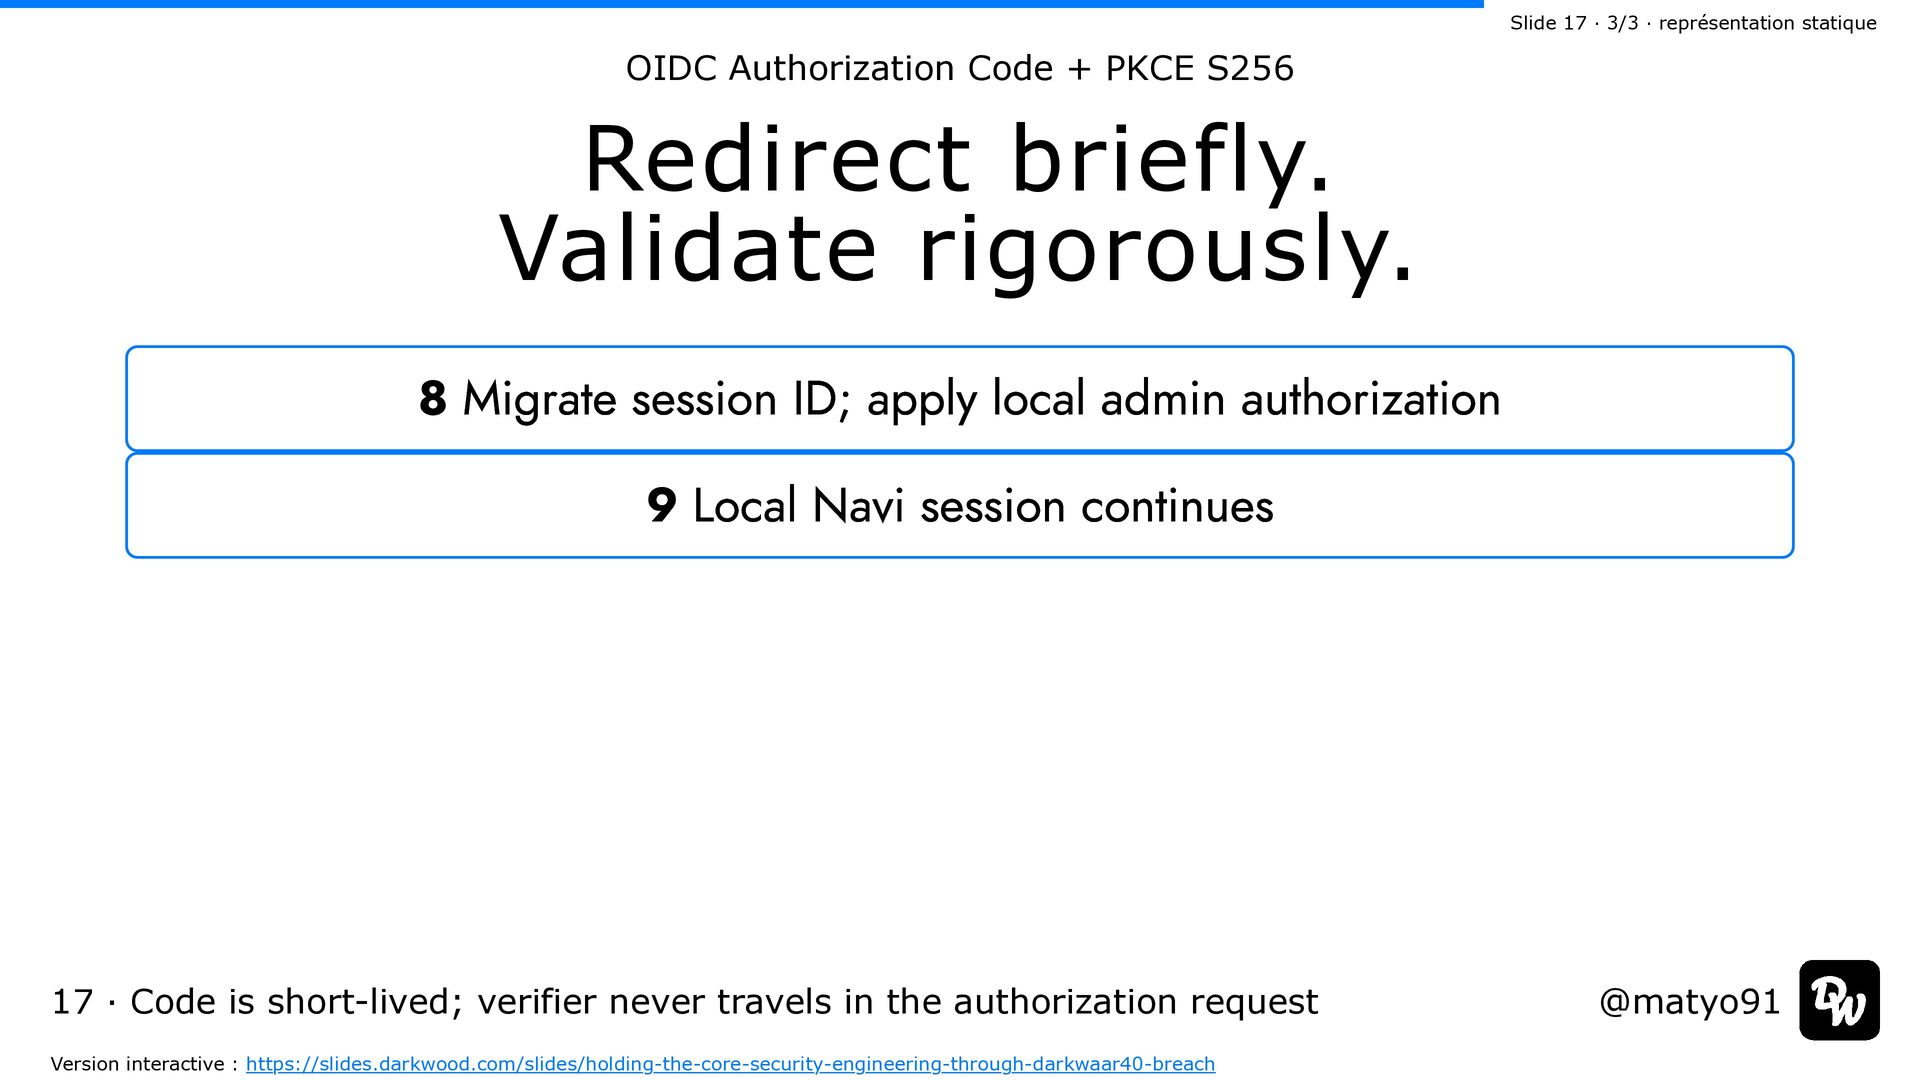
  40. Slide 17 · 3/3 · représentation statique OIDC Authorization Code

    + PKCE S256 Redirect briefly. Validate rigorously. 8 Migrate session ID; apply local admin authorization 9 Local Navi session continues 17 · Code is short-lived; verifier never travels in the authorization request Version interactive : https://slides.darkwood.com/slides/holding-the-core-security-engineering-through-darkwaar40-breach @matyo91
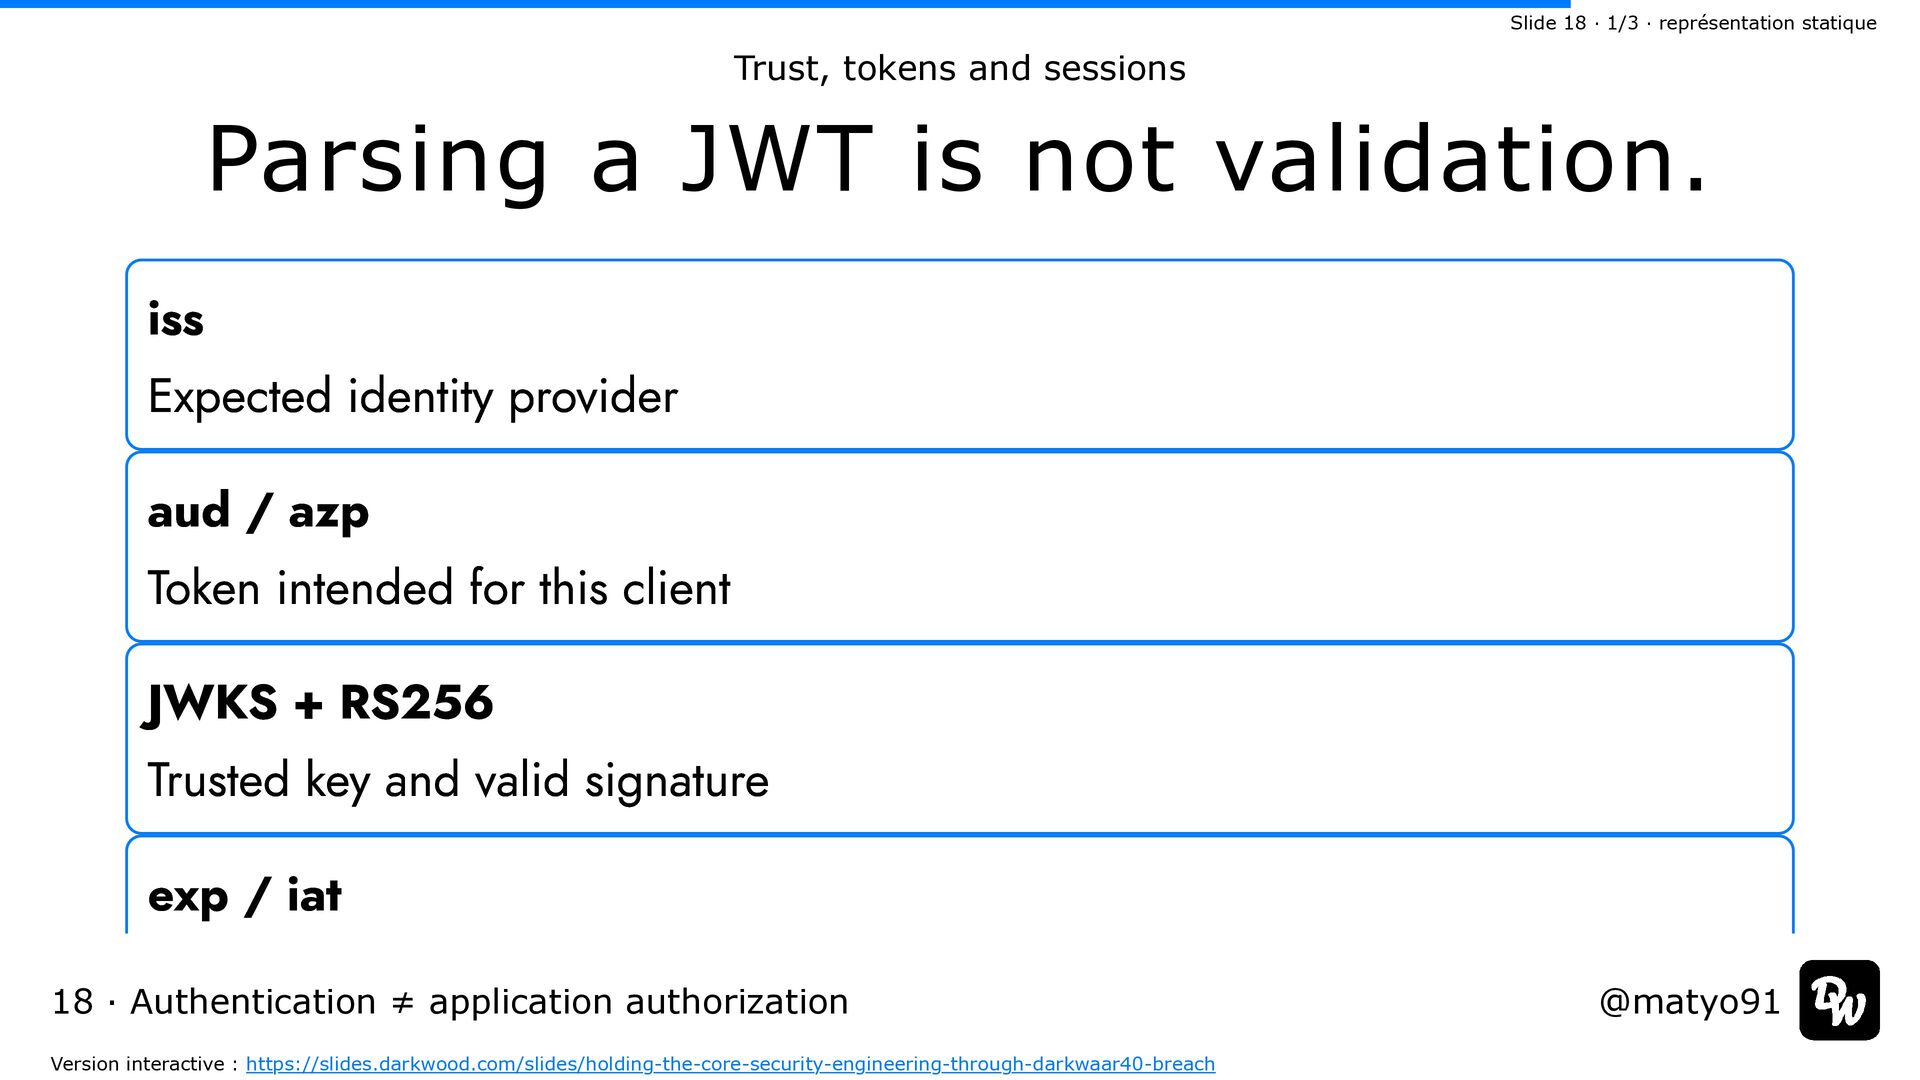
  41. Slide 18 · 1/3 · représentation statique Trust, tokens and

    sessions Parsing a JWT is not validation. iss Expected identity provider aud / azp Token intended for this client JWKS + RS256 Trusted key and valid signature exp / iat 18 · Authentication ≠ application authorization Version interactive : https://slides.darkwood.com/slides/holding-the-core-security-engineering-through-darkwaar40-breach @matyo91
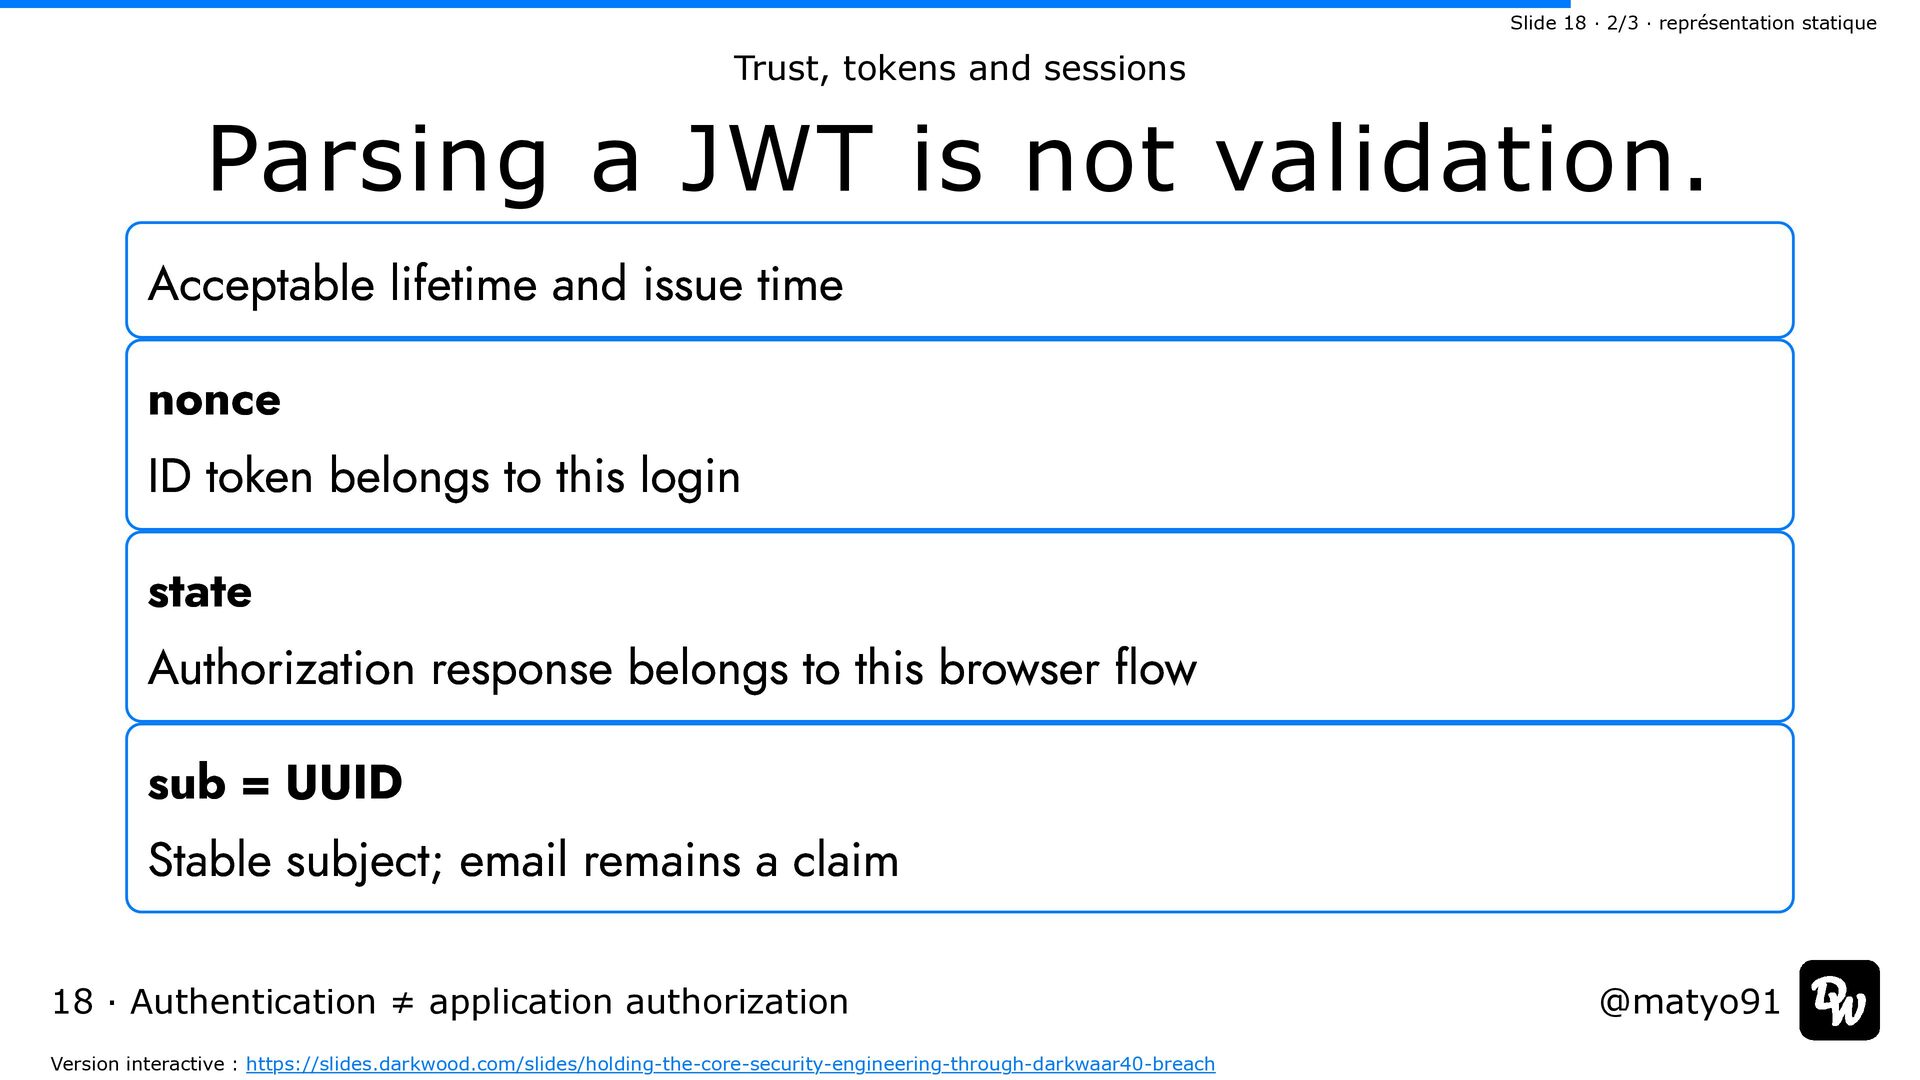
  42. Slide 18 · 2/3 · représentation statique Trust, tokens and

    sessions Parsing a JWT is not validation. Acceptable lifetime and issue time nonce ID token belongs to this login state Authorization response belongs to this browser flow sub = UUID Stable subject; email remains a claim 18 · Authentication ≠ application authorization Version interactive : https://slides.darkwood.com/slides/holding-the-core-security-engineering-through-darkwaar40-breach @matyo91
  43. Slide 18 · 3/3 · représentation statique Trust, tokens and

    sessions Parsing a JWT is not validation. local session Navi owns authorization and session policy OIDC authenticates identity claims. Navi still decides who may administer Navi. 18 · Authentication ≠ application authorization Version interactive : https://slides.darkwood.com/slides/holding-the-core-security-engineering-through-darkwaar40-breach @matyo91
  44. Slide 19 · 1/3 · représentation statique Actual repository state

    · inspected 24 Oct 2026 Implemented now. Target next. Implemented in source Darkwood OIDC discovery, authorize, token, JWKS, end-session routes Authorization Code; implicit and password grants disabled Navi PKCE S256, state, nonce, JWKS cache + retry RS256 and claim validation Local role gate and session migration → 19 · Current implementation vs future plan Version interactive : https://slides.darkwood.com/slides/holding-the-core-security-engineering-through-darkwaar40-breach @matyo91
  45. Slide 19 · 2/3 · représentation statique Actual repository state

    · inspected 24 Oct 2026 Implemented now. Target next. Target architecture Move Navi onto a maintained Symfony branch Adopt Symfony 8.2 native oidc_login Delete more custom relying-party code Preserve local authorization policy Planned in repository design documentation; Symfony 8.2 was still under development. 19 · Current implementation vs future plan Version interactive : https://slides.darkwood.com/slides/holding-the-core-security-engineering-through-darkwaar40-breach @matyo91
  46. Slide 19 · 3/3 · représentation statique Actual repository state

    · inspected 24 Oct 2026 Implemented now. Target next. Repository code confirms implementation—not deployed production rollout or a completed live login. 19 · Current implementation vs future plan Version interactive : https://slides.darkwood.com/slides/holding-the-core-security-engineering-through-darkwaar40-breach @matyo91
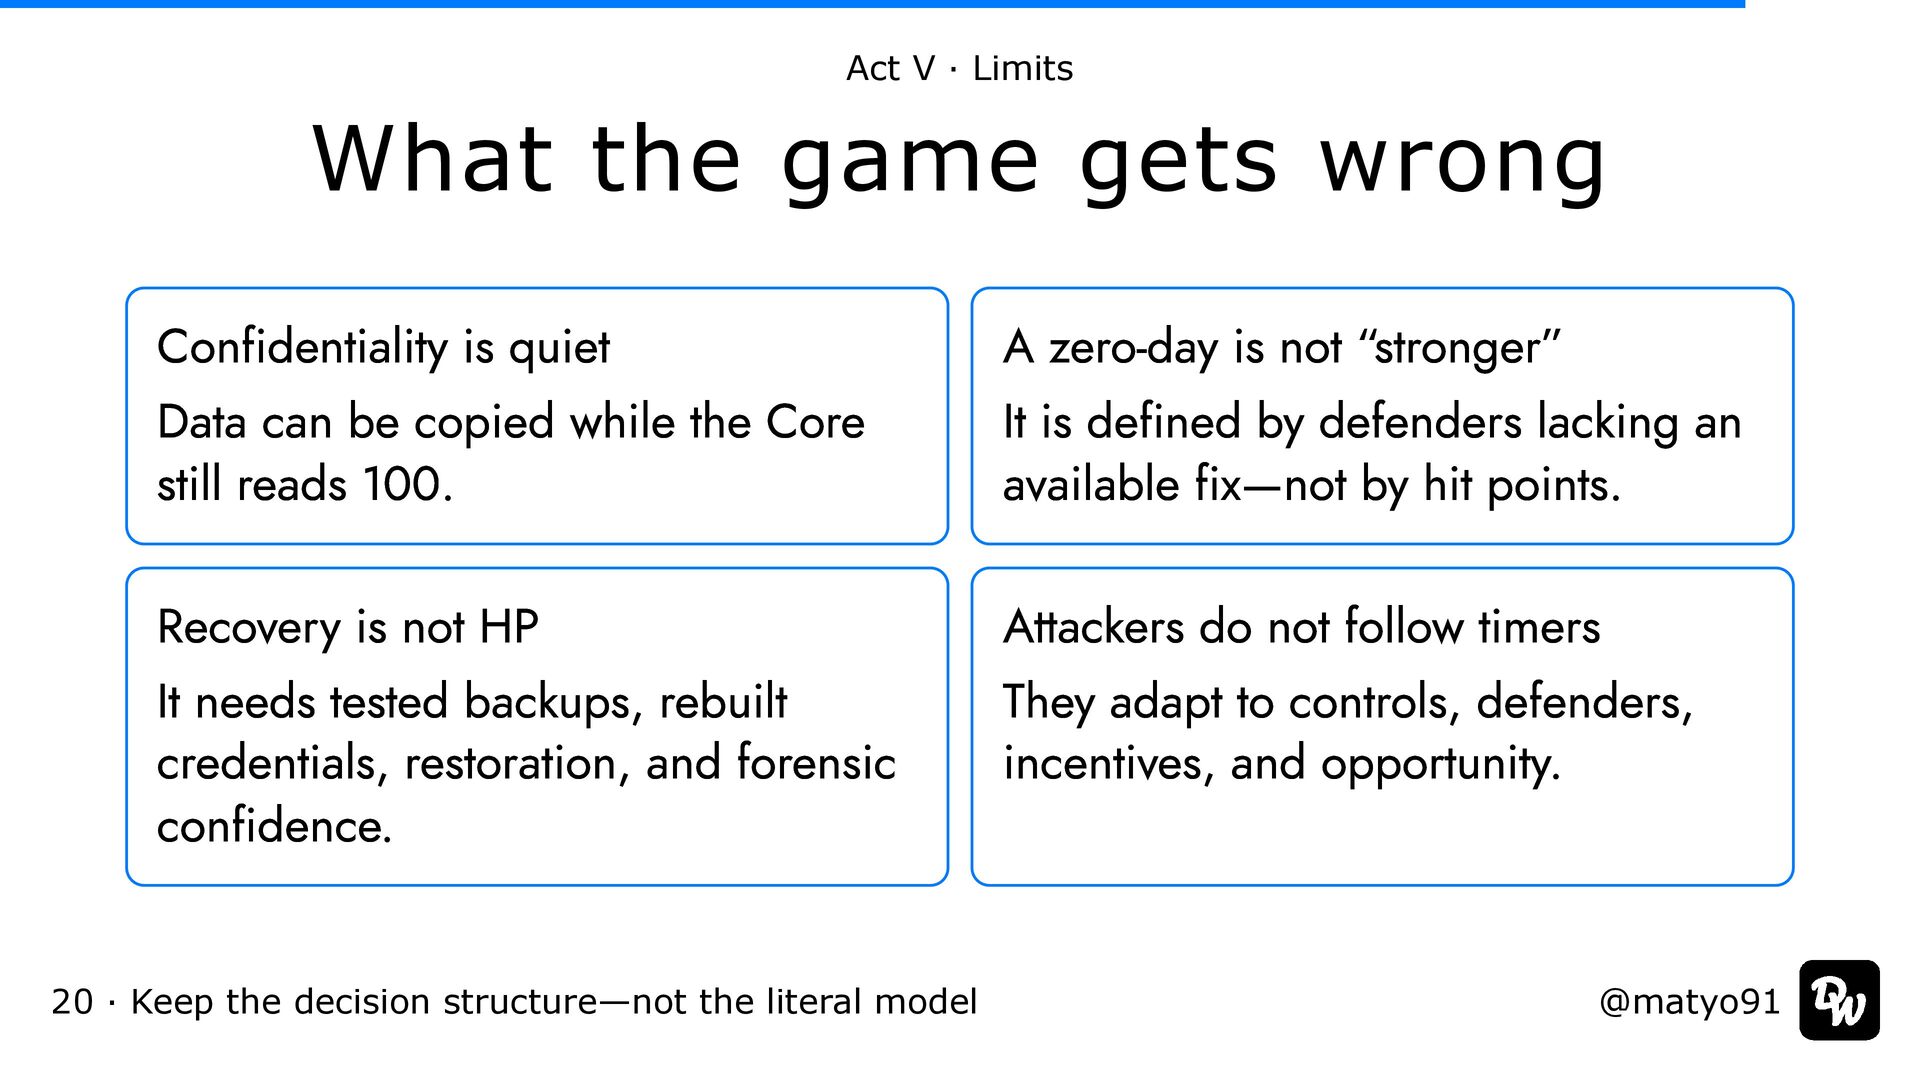
  47. Act V · Limits What the game gets wrong Confidentiality

    is quiet A zero-day is not “stronger” Data can be copied while the Core still reads 100. It is defined by defenders lacking an available fix—not by hit points. Recovery is not HP Attackers do not follow timers It needs tested backups, rebuilt credentials, restoration, and forensic confidence. They adapt to controls, defenders, incentives, and opportunity. 20 · Keep the decision structure—not the literal model @matyo91
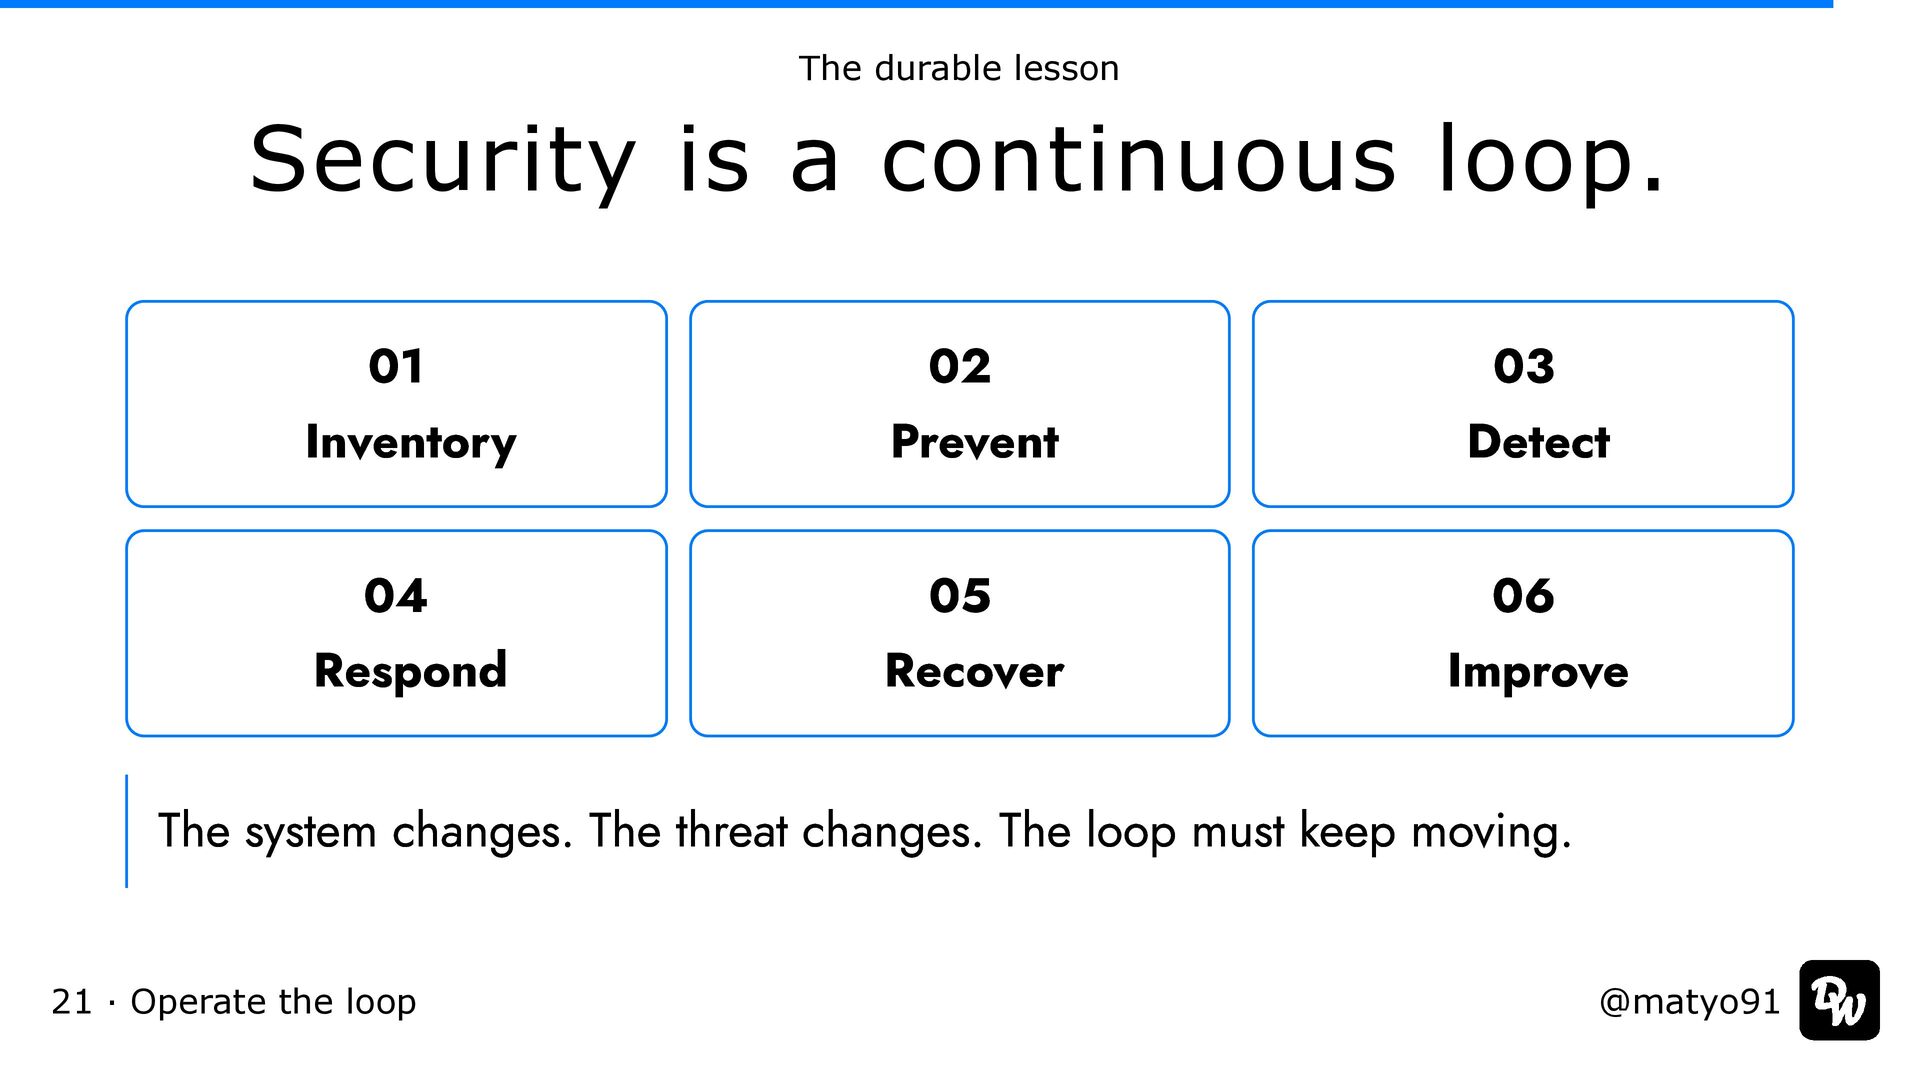
  48. The durable lesson Security is a continuous loop. 01 02

    03 Inventory Prevent Detect 04 05 06 Respond Recover Improve The system changes. The threat changes. The loop must keep moving. 21 · Operate the loop @matyo91
  49. Play Darkwaar40 — Breach Keep moving. Keep the Core alive.

    darkwaar.com/games/01a16e69-3593-7df1-b460e25c4912eae1 DARK WOOD · @MAT YO91 22 · Holding the Core · Thank you @matyo91