Upgrade to Pro
— share decks privately, control downloads, hide ads and more …
Speaker Deck
Sign up for free
Menu
Search
Features
All features
Private URLs
Password Protection
Custom URLS
Scheduled publishing
Remove Branding
Restrict embedding
Deck Collections
Notes
Features
All features
Private URLs
Password Protection
Custom URLS
Scheduled publishing
Remove Branding
Restrict embedding
Deck Collections
Notes
Explore
Featured decks
Featured speakers
Programming
Technology
Storyboards
Explore
Featured decks
Featured speakers
Programming
Technology
Storyboards
Pricing
Search
Sign in
Sign up for free
Don't Commit Your Secrets
Search
Nicholas Henry
June 17, 2014
Programming
7.8k
0
Share
Embed
Copy iframe code
Copy JS code
Copy link
Start on current slide
Don't Commit Your Secrets
How to keep your application secrets safe
Nicholas Henry
June 17, 2014
Transcript
15 slides
Don’t Commit Your Secrets How to keep your application
secrets safe ! Nicholas Henry
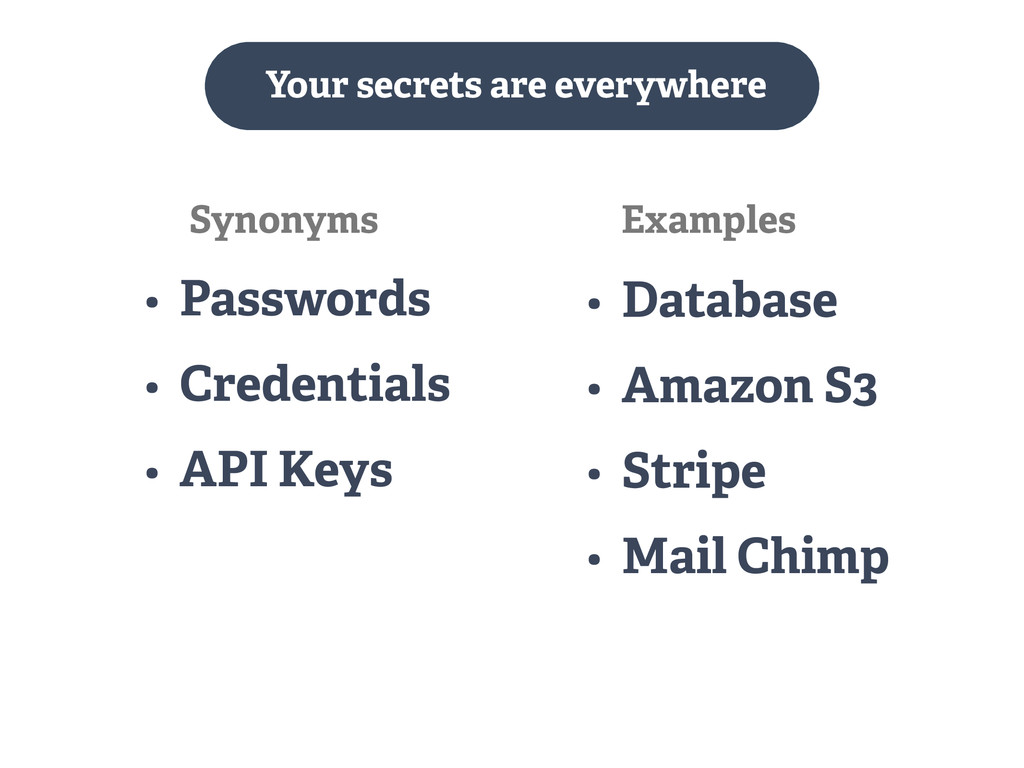
Your secrets are everywhere • Passwords • Credentials • API
Keys • Database • Amazon S3 • Stripe • Mail Chimp Examples Synonyms
None
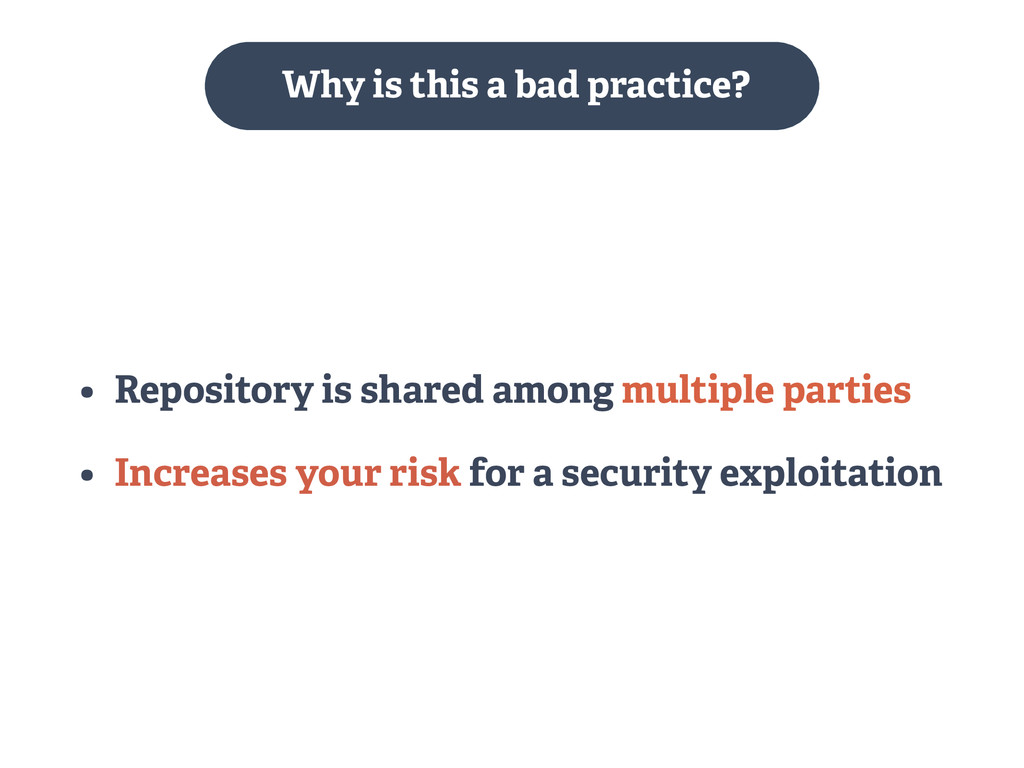
• Repository is shared among multiple parties • Increases your
risk for a security exploitation Why is this a bad practice?
• application is open source • application requires a high
level of governance e.g. financial, healthcare • application involves transient contractors e.g. agency • application located on multiple services e.g. CodeClimate When is this a bad practice?
When is this a bad practice? ALWAYS!
• Environment Variables • Configuration files Your options
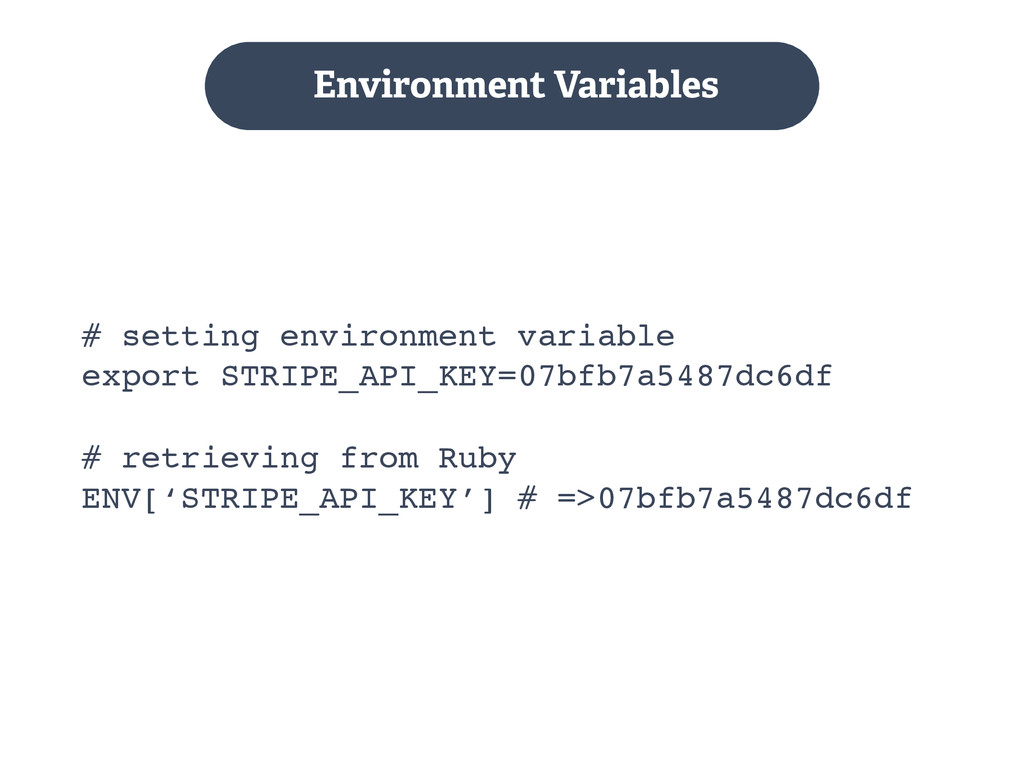
Environment Variables # setting environment variable export STRIPE_API_KEY=07bfb7a5487dc6df" # retrieving
from Ruby ENV[‘STRIPE_API_KEY’] # =>07bfb7a5487dc6df
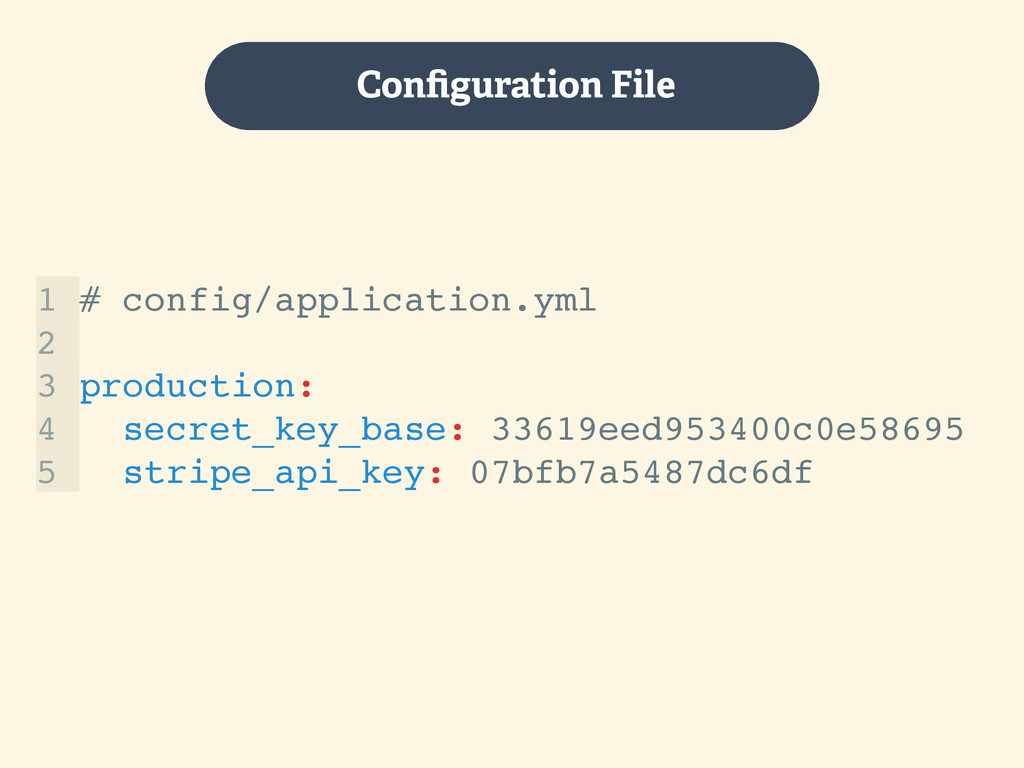
1 # config/application.yml" 2 " 3 production:" 4 secret_key_base: 33619eed953400c0e58695"
5 stripe_api_key: 07bfb7a5487dc6df Configuration File
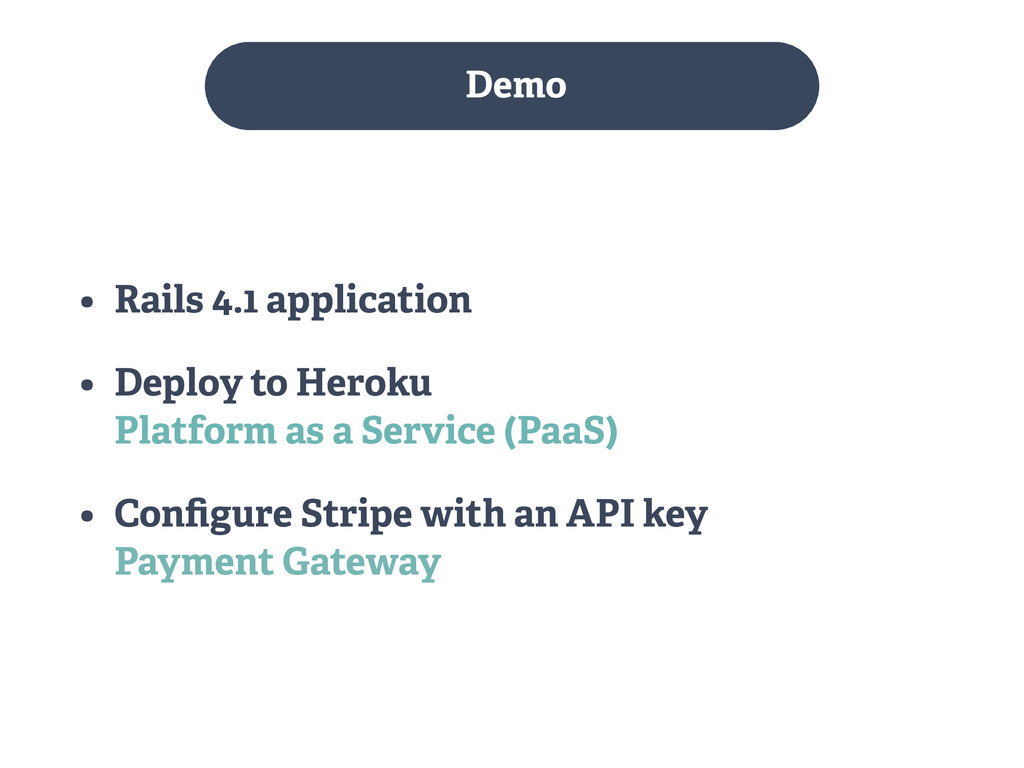
• Rails 4.1 application • Deploy to Heroku Platform as
a Service (PaaS) • Configure Stripe with an API key Payment Gateway Demo
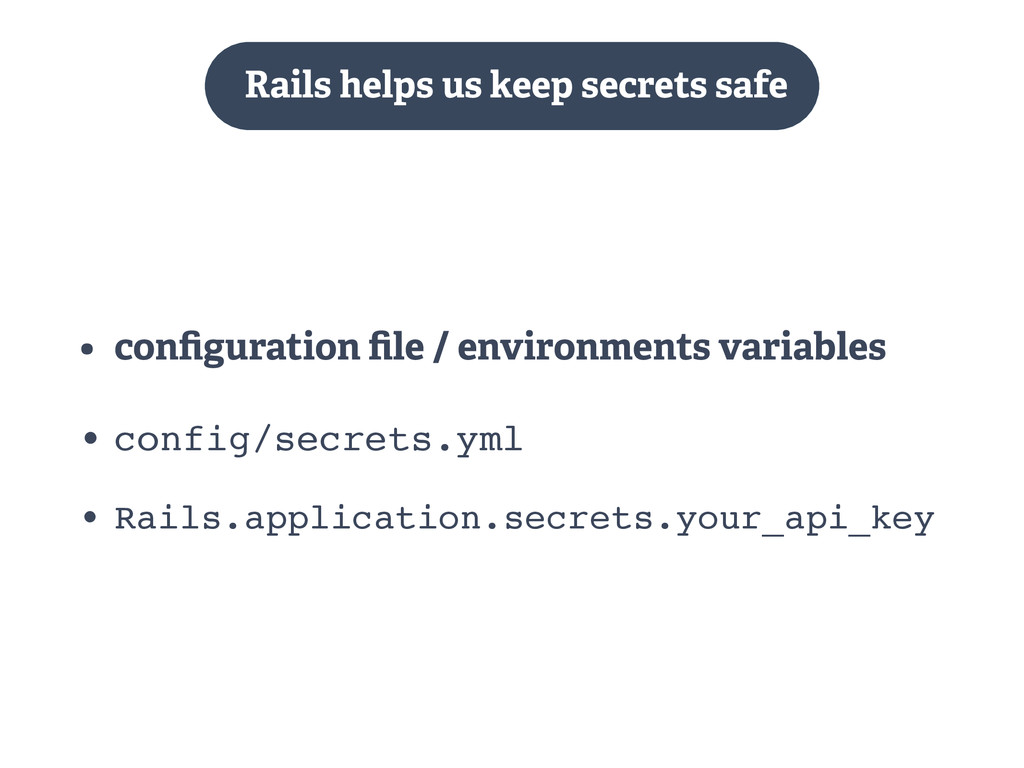
• configuration file / environments variables • config/secrets.yml" • Rails.application.secrets.your_api_key
Rails helps us keep secrets safe
None
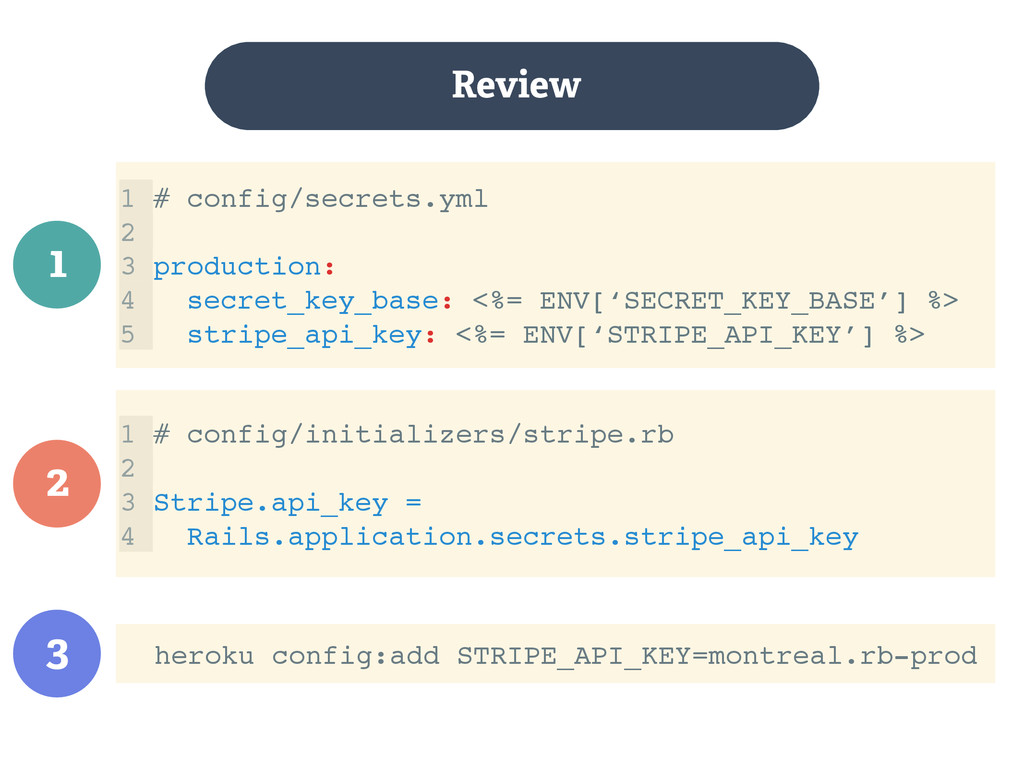
Review 1 # config/secrets.yml" 2 " 3 production:" 4 secret_key_base:
<%= ENV[‘SECRET_KEY_BASE’] %>" 5 stripe_api_key: <%= ENV[‘STRIPE_API_KEY’] %> 1 2 3 heroku config:add STRIPE_API_KEY=montreal.rb-prod 1 # config/initializers/stripe.rb" 2 " 3 Stripe.api_key = " 4 Rails.application.secrets.stripe_api_key
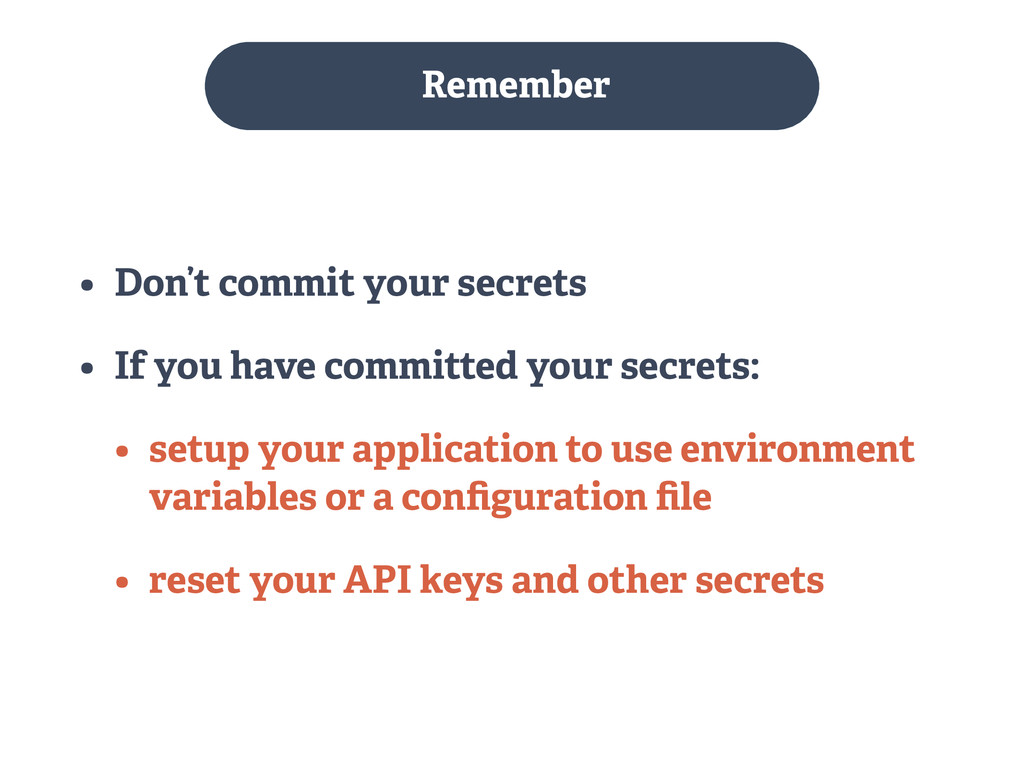
• Don’t commit your secrets • If you have committed
your secrets: • setup your application to use environment variables or a configuration file • reset your API keys and other secrets Remember
nicholas@firsthand.ca @nicholasjhenry Nicholas Henry http://blog.firsthand.ca
More Decks by Nicholas Henry
See All by Nicholas Henry
Mise en Place for Ecto
nicholasjhenry
0
54
Beyond Mocks - Messing with Our Preconceptions of Testing
nicholasjhenry
0
52
Preventing Brain Freeze: Onboarding New Developers with Living Documentation
nicholasjhenry
0
150
The Upside Down Dimension of Elixir - ElixirConf
nicholasjhenry
0
41
The Upside Down Dimension of Elixir - An introduction to metaprogramming
nicholasjhenry
1
260
Building the Montreal Elixir Community
nicholasjhenry
0
66
How Elixir is Transforming My Mind
nicholasjhenry
1
6.9k
Modeling on the Right Side of the Brain
nicholasjhenry
1
10k
Other Decks in Programming
See All in Programming
Spec-driven Development with AI
simas
PRO
0
2.3k
Python Lambdaにおけるテストしやすい設計とAI支援の活用 / Designing Testable Python Lambda Functions with AI
kitano_yuichi
1
330
AI-Powered Domain-Driven Design
ziobrando
0
460
SODA - FACT BOOK(JP)
sodainc
1
40k
社内AIエージェント「Askワンバン」における コストチューニングの取り組み
t0yohei
0
170
AI時代のシニアエンジニアとは
yosuke_furukawa
PRO
15
12k
protojson における文字化けの扱い
kazuki1023
0
440
AI駆動開発4年目の現在地(『あなたはFDEになるべきか?』イベント資料)
kumaiu
0
640
Beyond Chatbots: Agentic UI with Open Standards @W-JAX 2026, München
manfredsteyer
PRO
0
110
SODA - FACT BOOK(EN)
sodainc
1
250
自作Discord音声botをLambda MicroVMsに移行した話 / Migrating My Discord Voice Bot to Lambda MicroVMs
akihisaikeda
1
350
Getting Started with Vibe Coding
miccheng
0
230
Featured
See All Featured
Prompt Engineering for Job Search
mfonobong
0
590
Tips & Tricks on How to Get Your First Job In Tech
honzajavorek
1
850
Art, The Web, and Tiny UX
lynnandtonic
304
22k
Applied NLP in the Age of Generative AI
inesmontani
PRO
4
2.6k
コードの90%をAIが書く世界で何が待っているのか / What awaits us in a world where 90% of the code is written by AI
rkaga
63
48k
Keith and Marios Guide to Fast Websites
keithpitt
413
23k
Distributed Sagas: A Protocol for Coordinating Microservices
caitiem20
333
23k
Lightning talk: Run Django tests with GitHub Actions
sabderemane
0
320
Between Models and Reality
mayunak
4
580
Deep Space Network (abreviated)
tonyrice
0
420
Accessibility Awareness
sabderemane
1
300
Intergalactic Javascript Robots from Outer Space
tanoku
273
28k


 nicholasjhenry
 simas
 kitano_yuichi
 ziobrando
 sodainc
 t0yohei
 yosuke_furukawa
 kazuki1023
 kumaiu
 manfredsteyer
 akihisaikeda
 miccheng
 mfonobong
 honzajavorek
 lynnandtonic
 inesmontani
 rkaga
 keithpitt
 caitiem20
 sabderemane
 mayunak
 tonyrice
 tanoku