Upgrade to Pro — share decks privately, control downloads, hide ads and more …

Can You Keep a Secret?

Can You Keep a Secret?

Session on secrets management in Drupal at HackCamp in Bucharest, June 2018.

Nick Santamaria

June 10, 2018

Transcript

61 slides
  1. Nick Santamaria • Drupal developer since 2006 • SysOps Engineer

    at PreviousNext • Based in Melbourne, Australia • @nicksanta • drupal.org/user/87915 • github.com/nicksantamaria
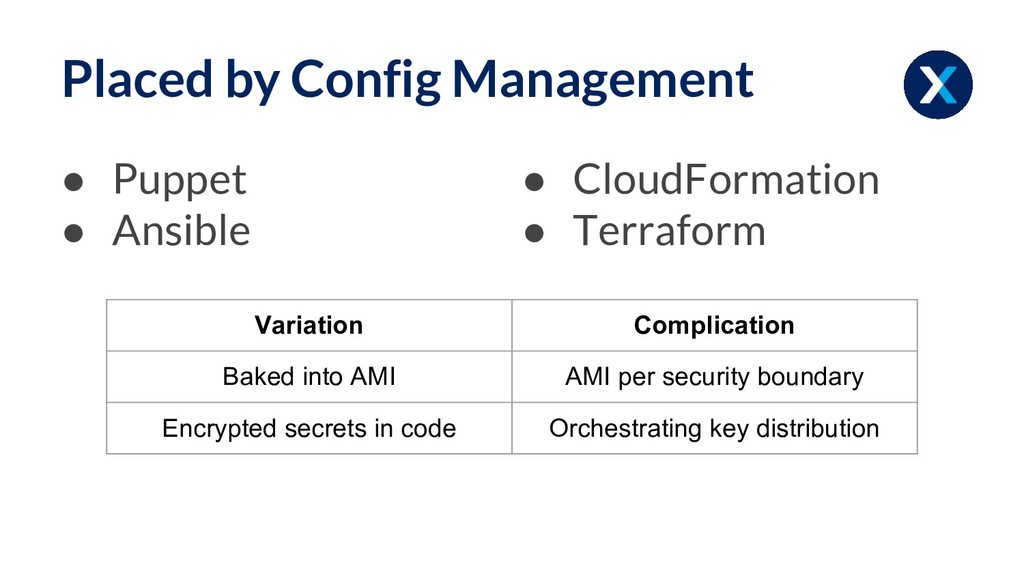
  2. Placed by Config Management • Puppet • Ansible • CloudFormation

    • Terraform Variation Complication Baked into AMI AMI per security boundary Encrypted secrets in code Orchestrating key distribution
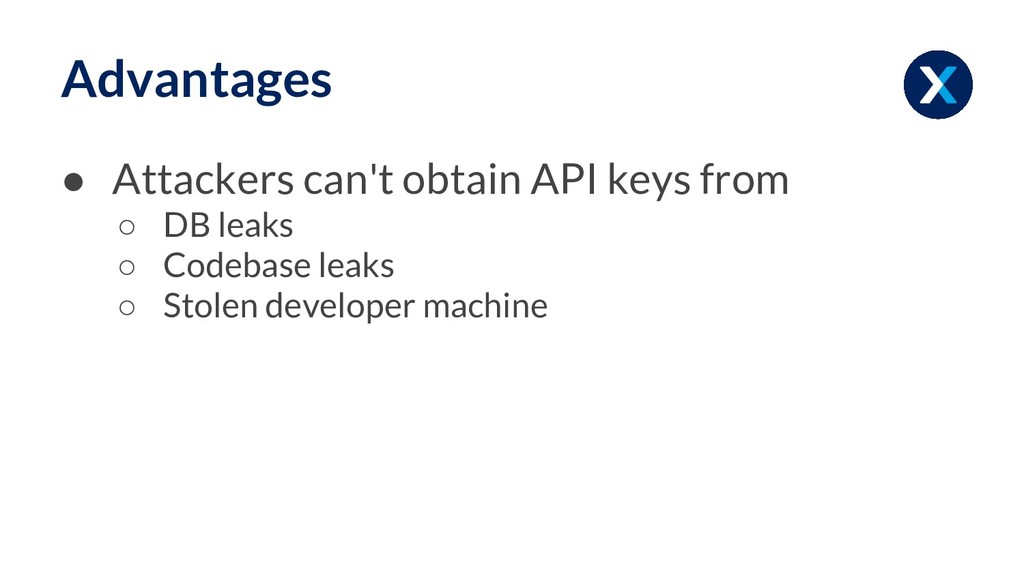
  3. • Attackers can't obtain API keys from ◦ DB leaks

    ◦ Codebase leaks ◦ Stolen developer machine Advantages
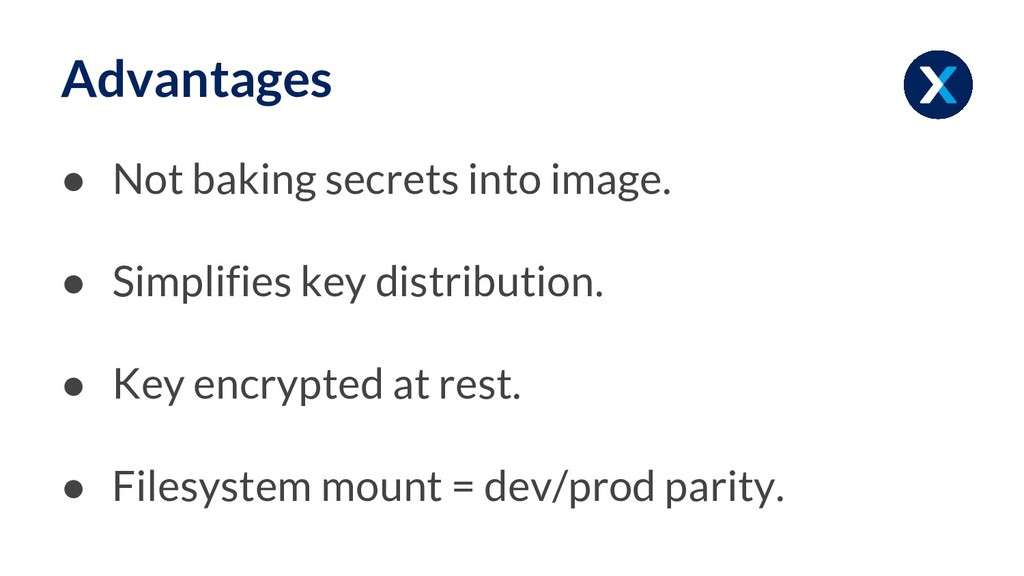
  4. • Not baking secrets into image. • Simplifies key distribution.
    • Key encrypted at rest. • Filesystem mount = dev/prod parity. Advantages
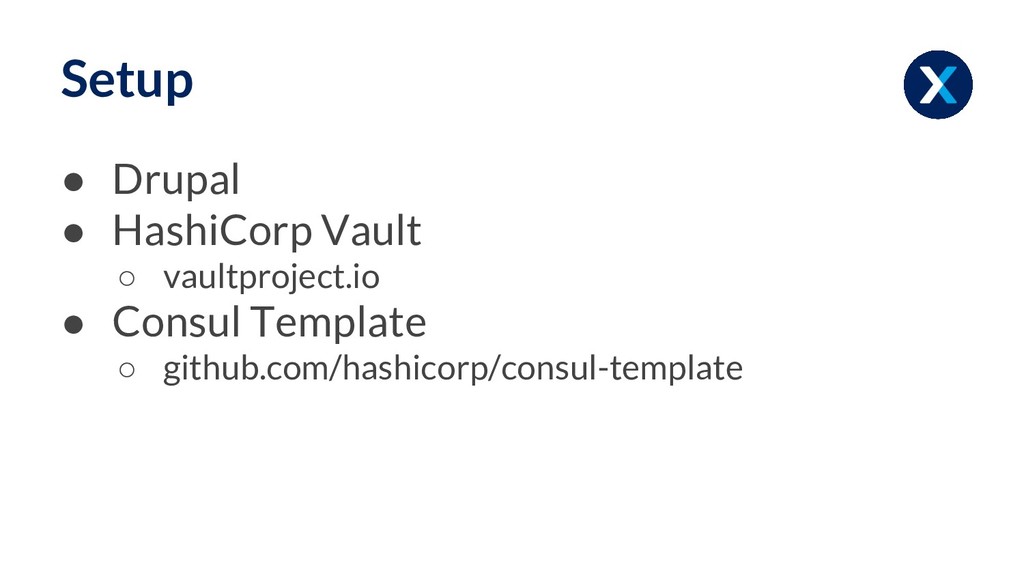
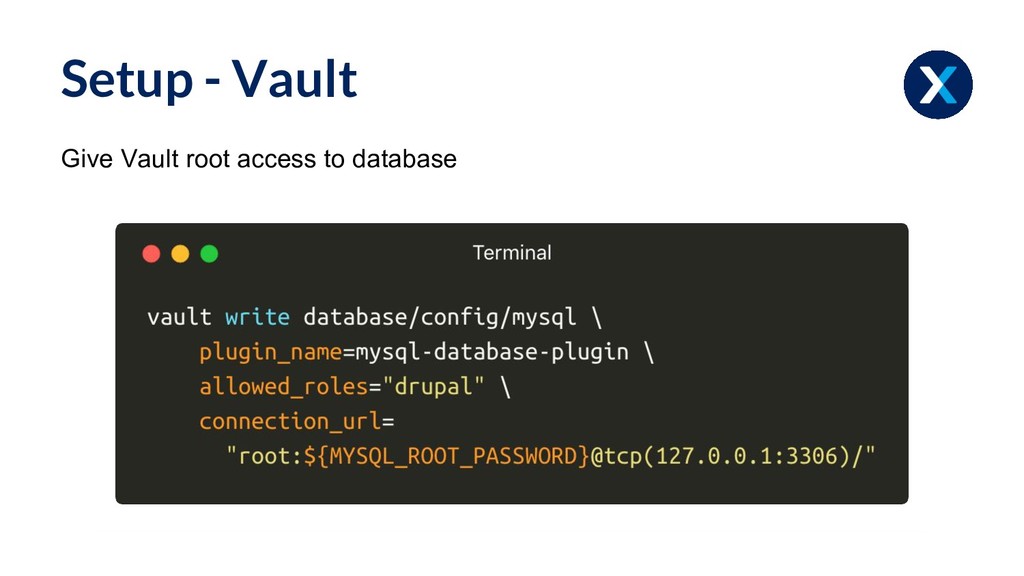
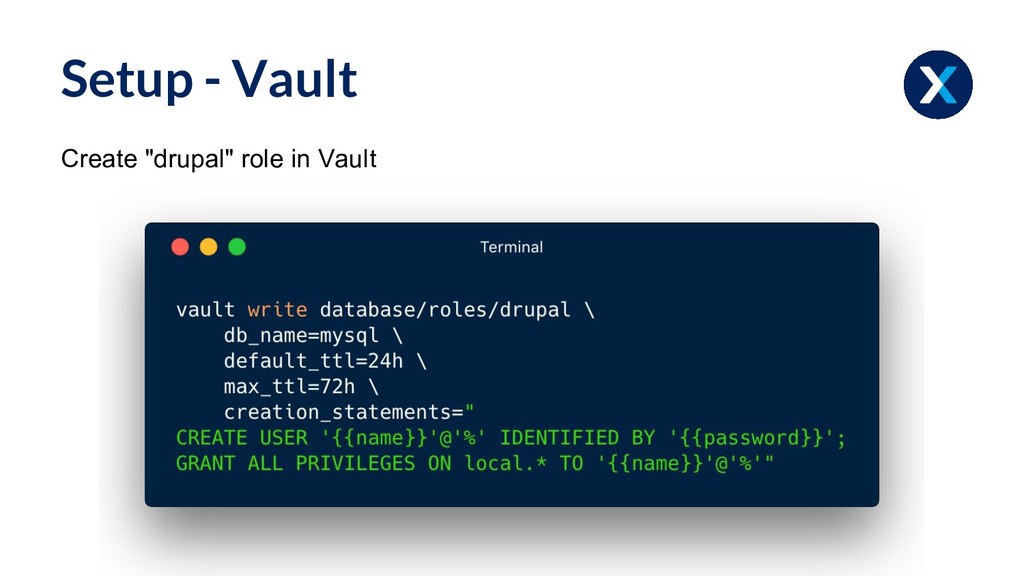
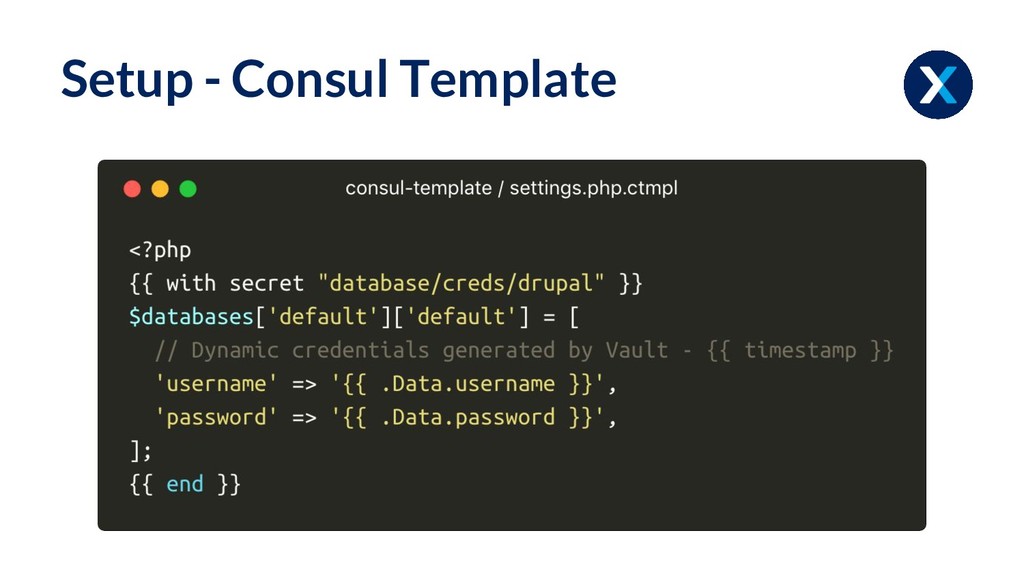
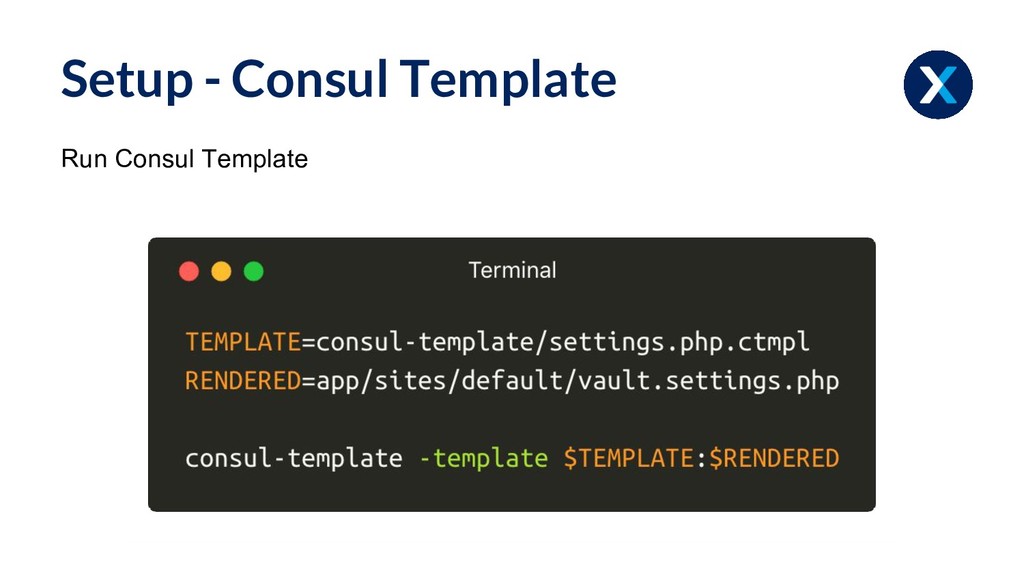
  5. Setup • Drupal • HashiCorp Vault ◦ vaultproject.io • Consul

    Template ◦ github.com/hashicorp/consul-template
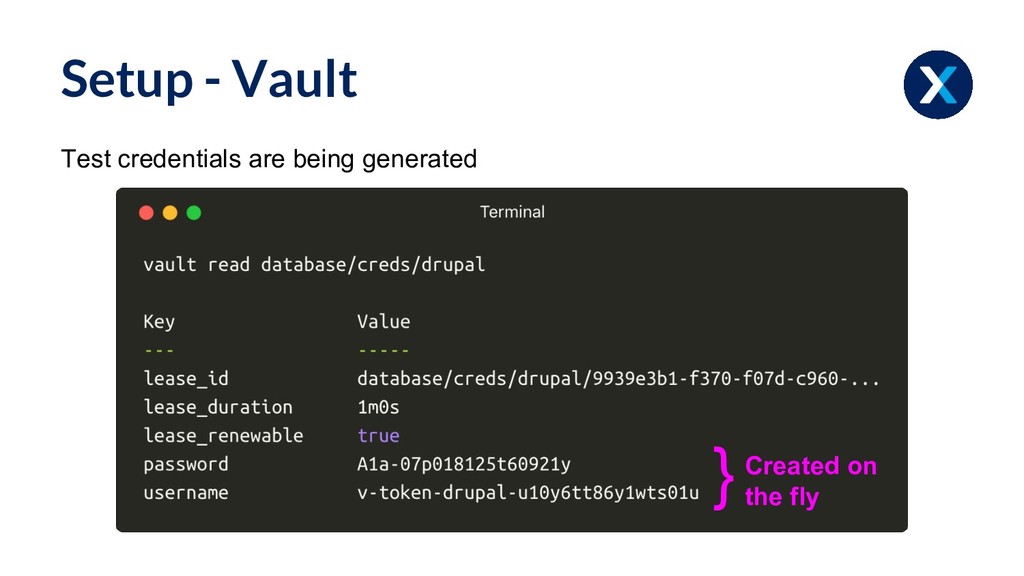
  6. • Constant rotation of secrets • Credentials probably junk by

    time Attacker tries to use them. • Risk posed by "Hoarders" mitigated. Advantages
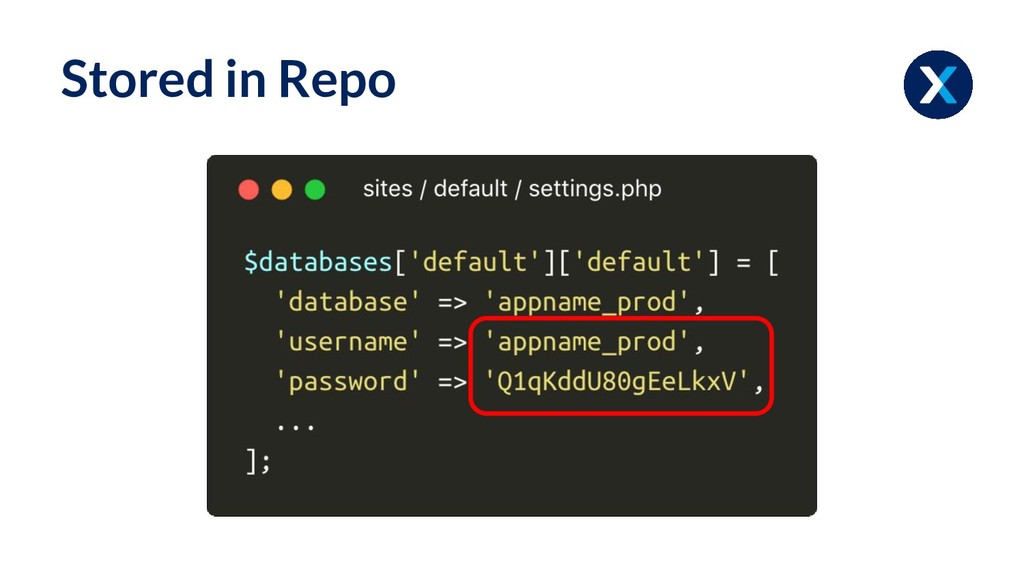
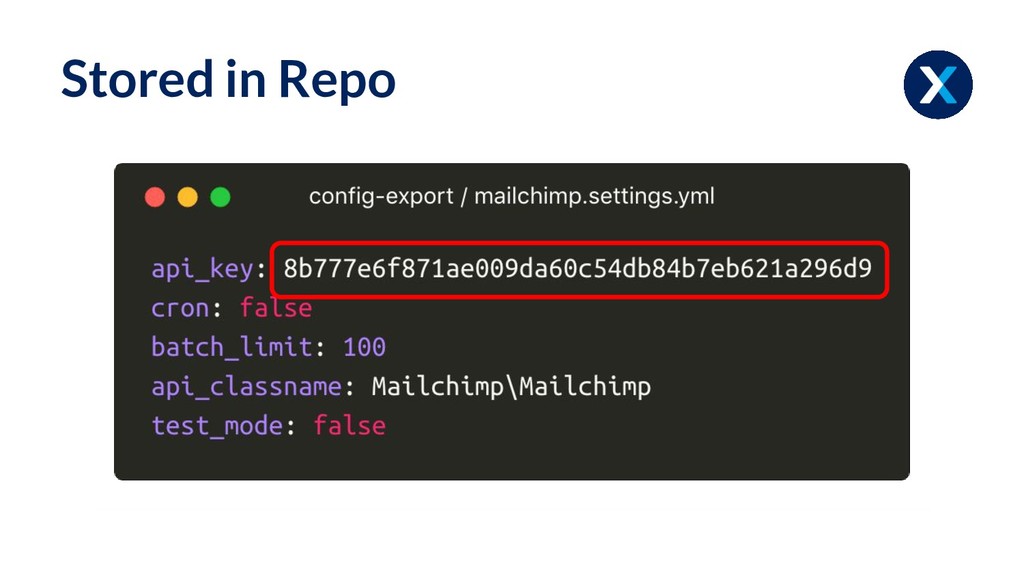
  7. • Audit your application for insecurely stored secrets. Fix! •

    “Data Security in Drupal 8” at 2pm. • Key in Drupal Core?? What Next?

More Decks by Nick Santamaria

Other Decks in Programming