Building a Secure Java Supply Chain in the Era of the Cyber Resilience Act
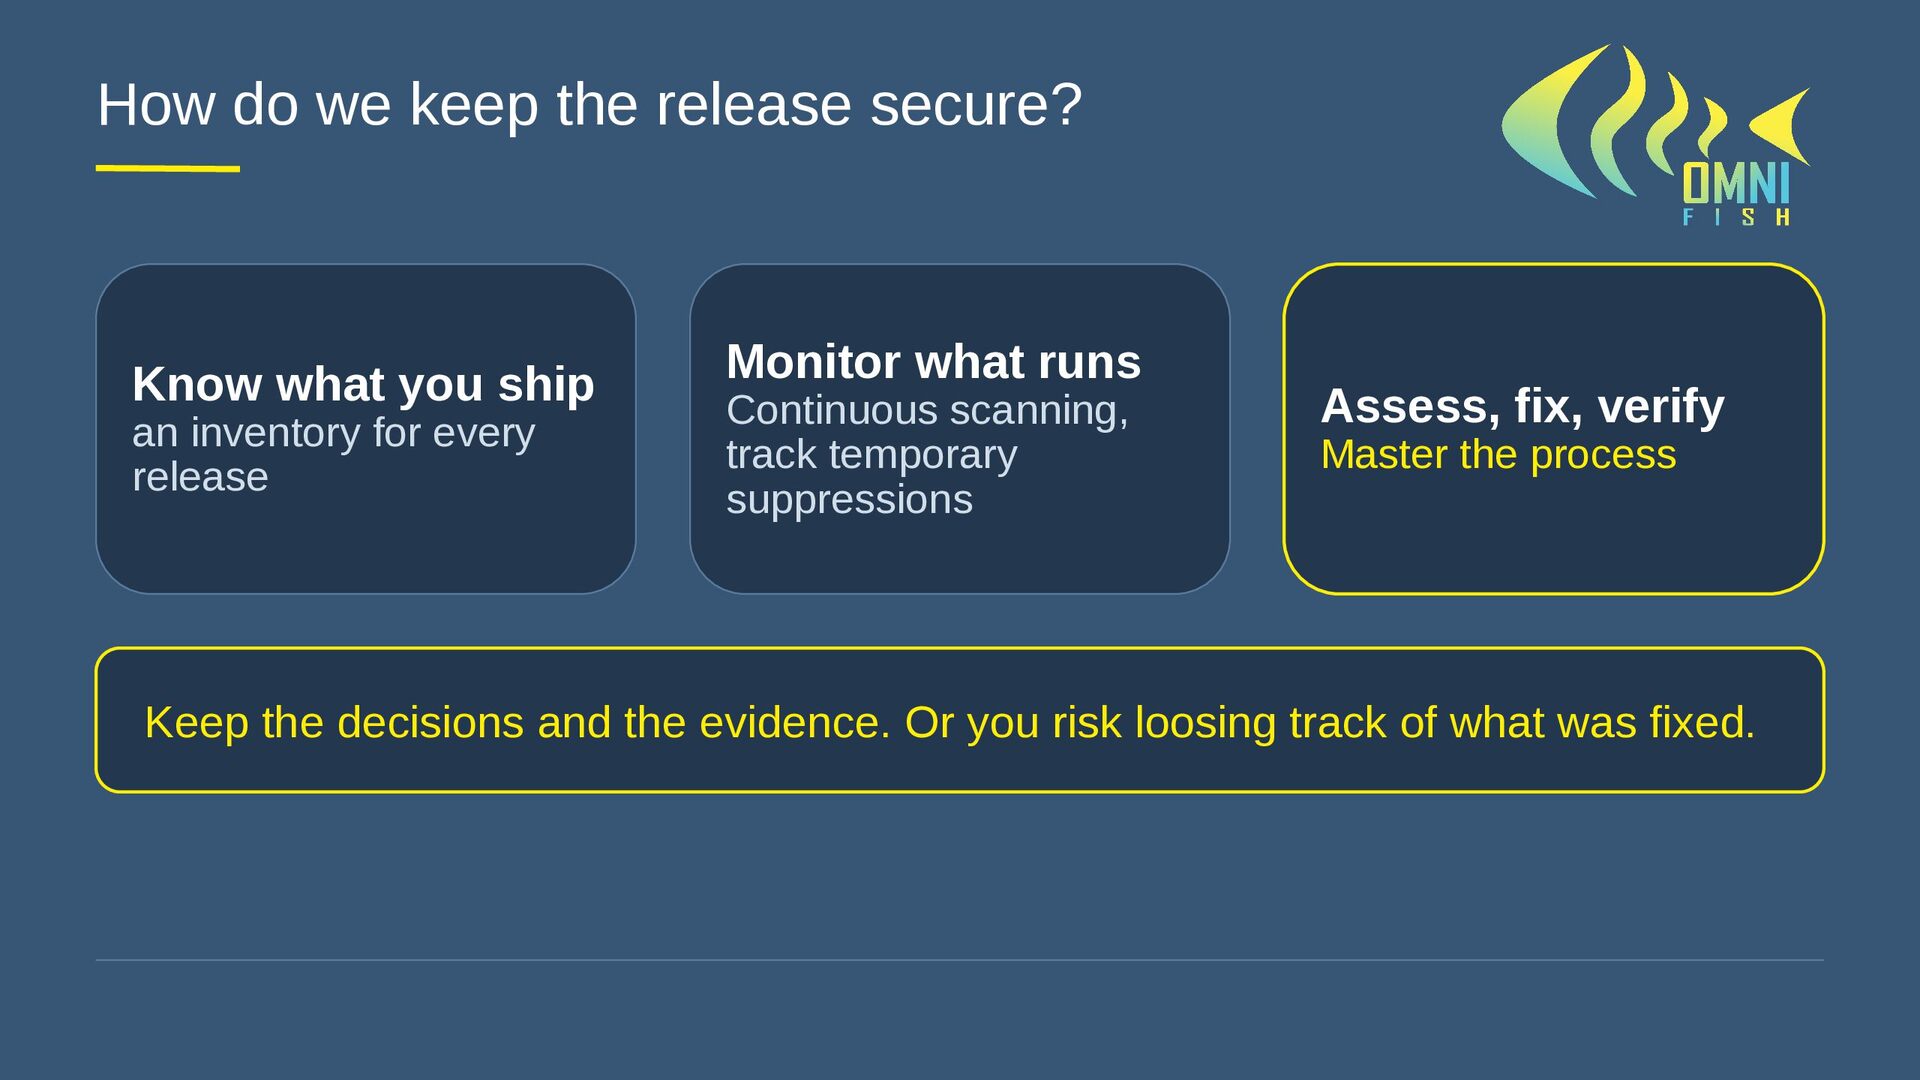
Modern Java applications ship with many dependencies, making CVE tracking and remediation a continuous challenge. While many tools exist to detect vulnerabilities, managing them effectively across the full software lifecycle remains difficult. This talk describes how to build a secure Java supply chain using existing open-source tools.
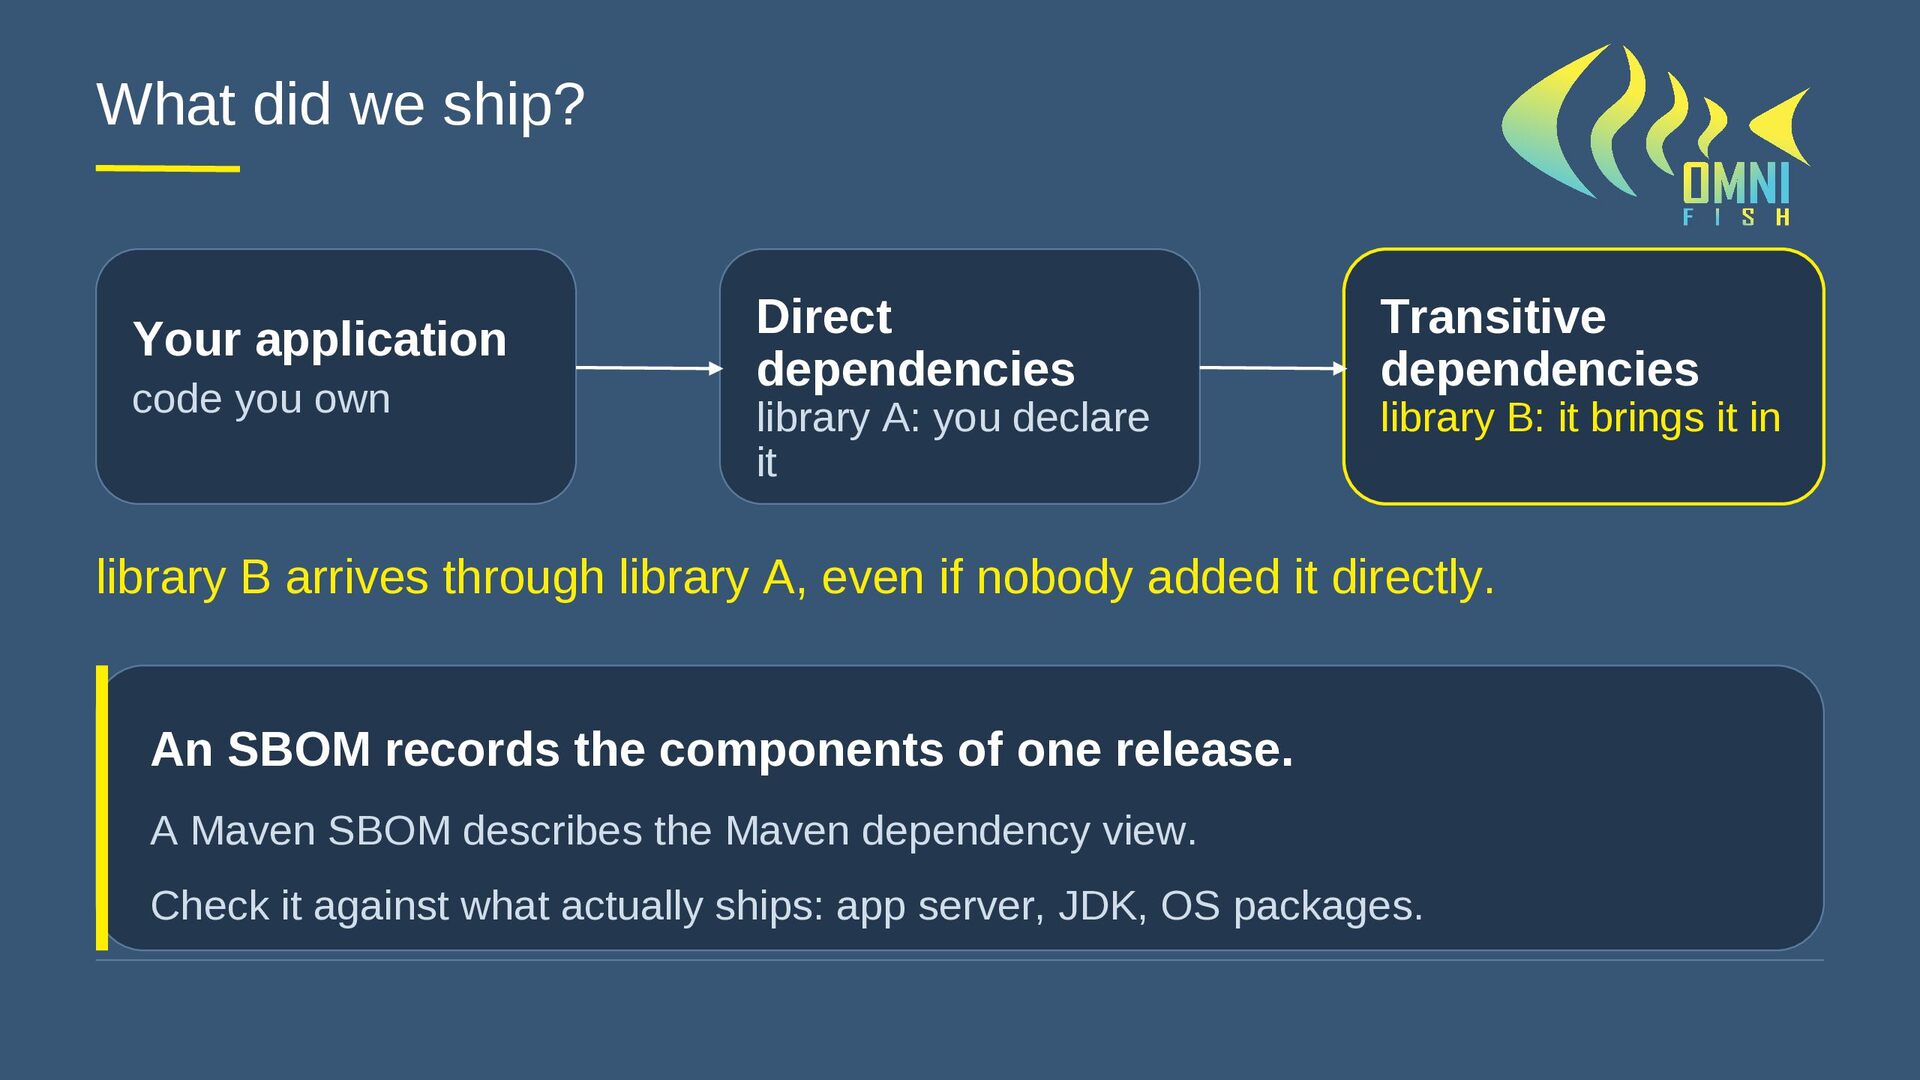
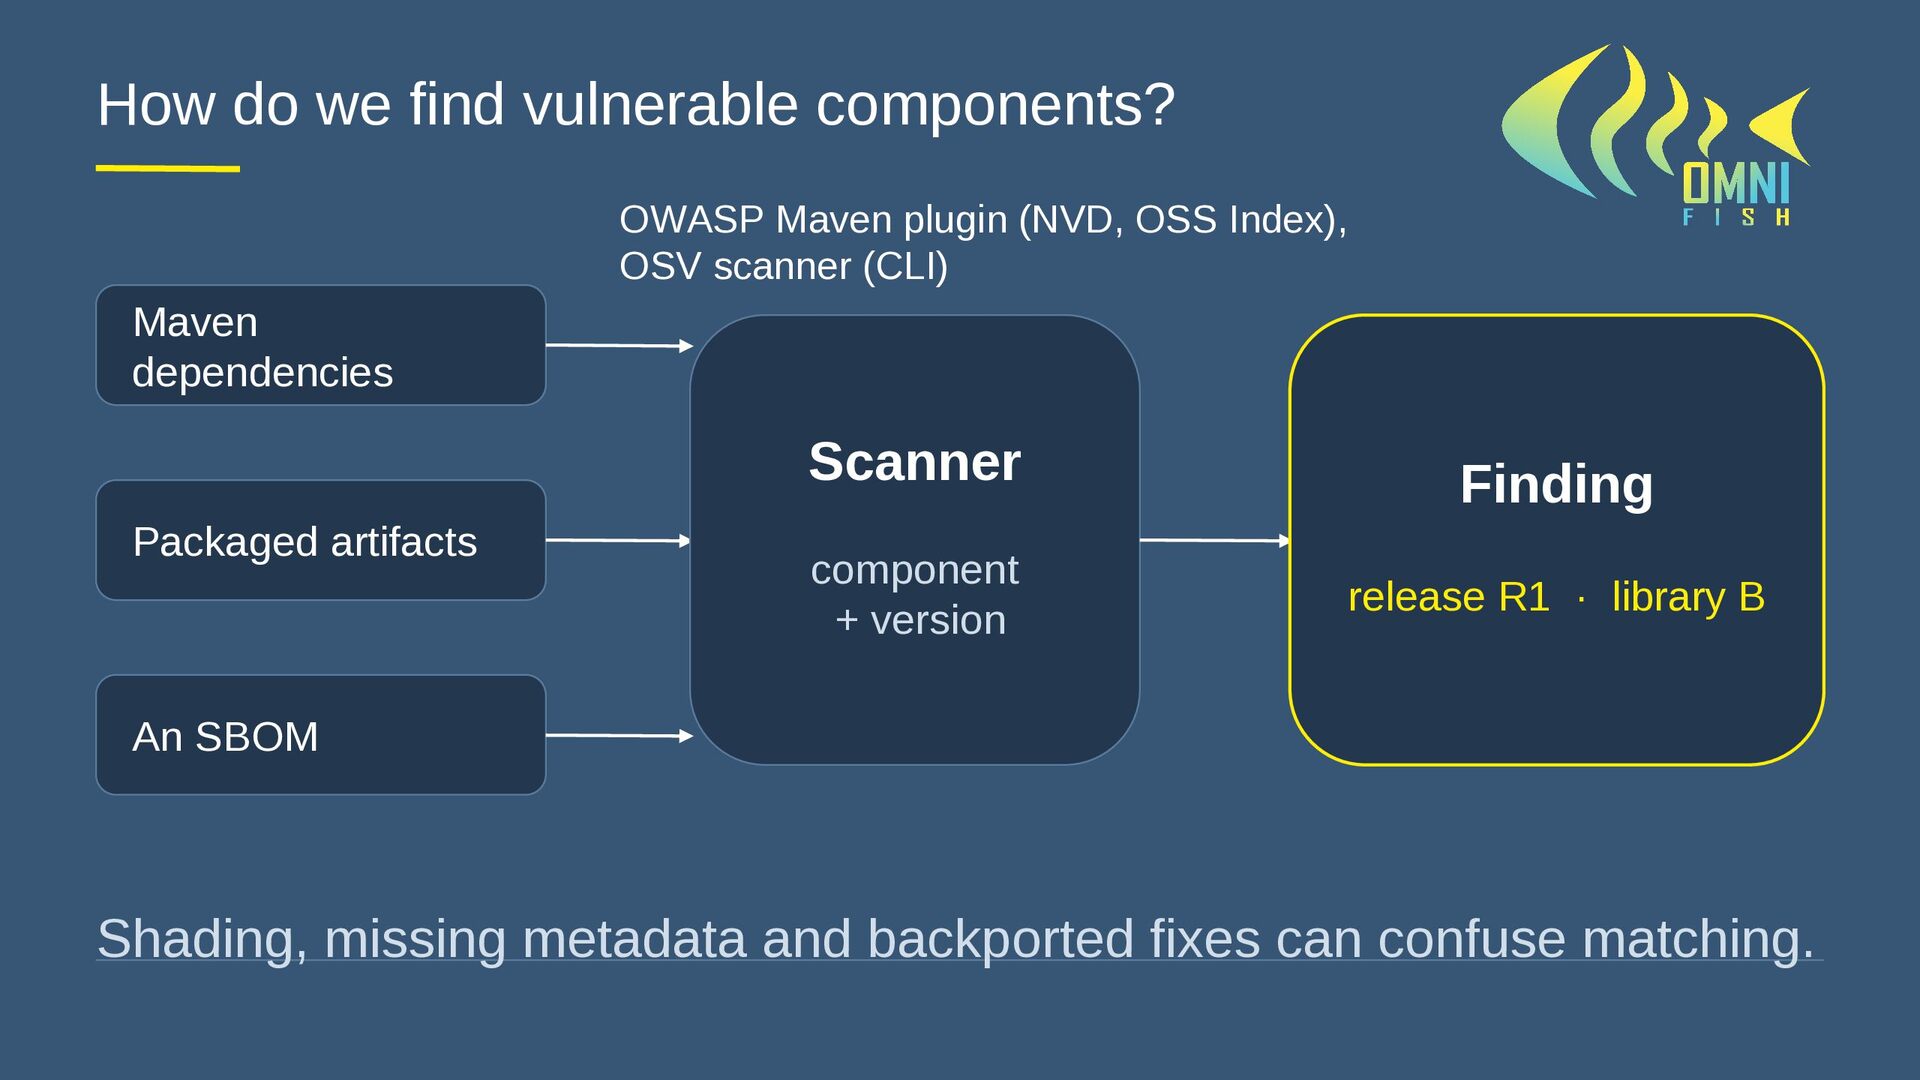
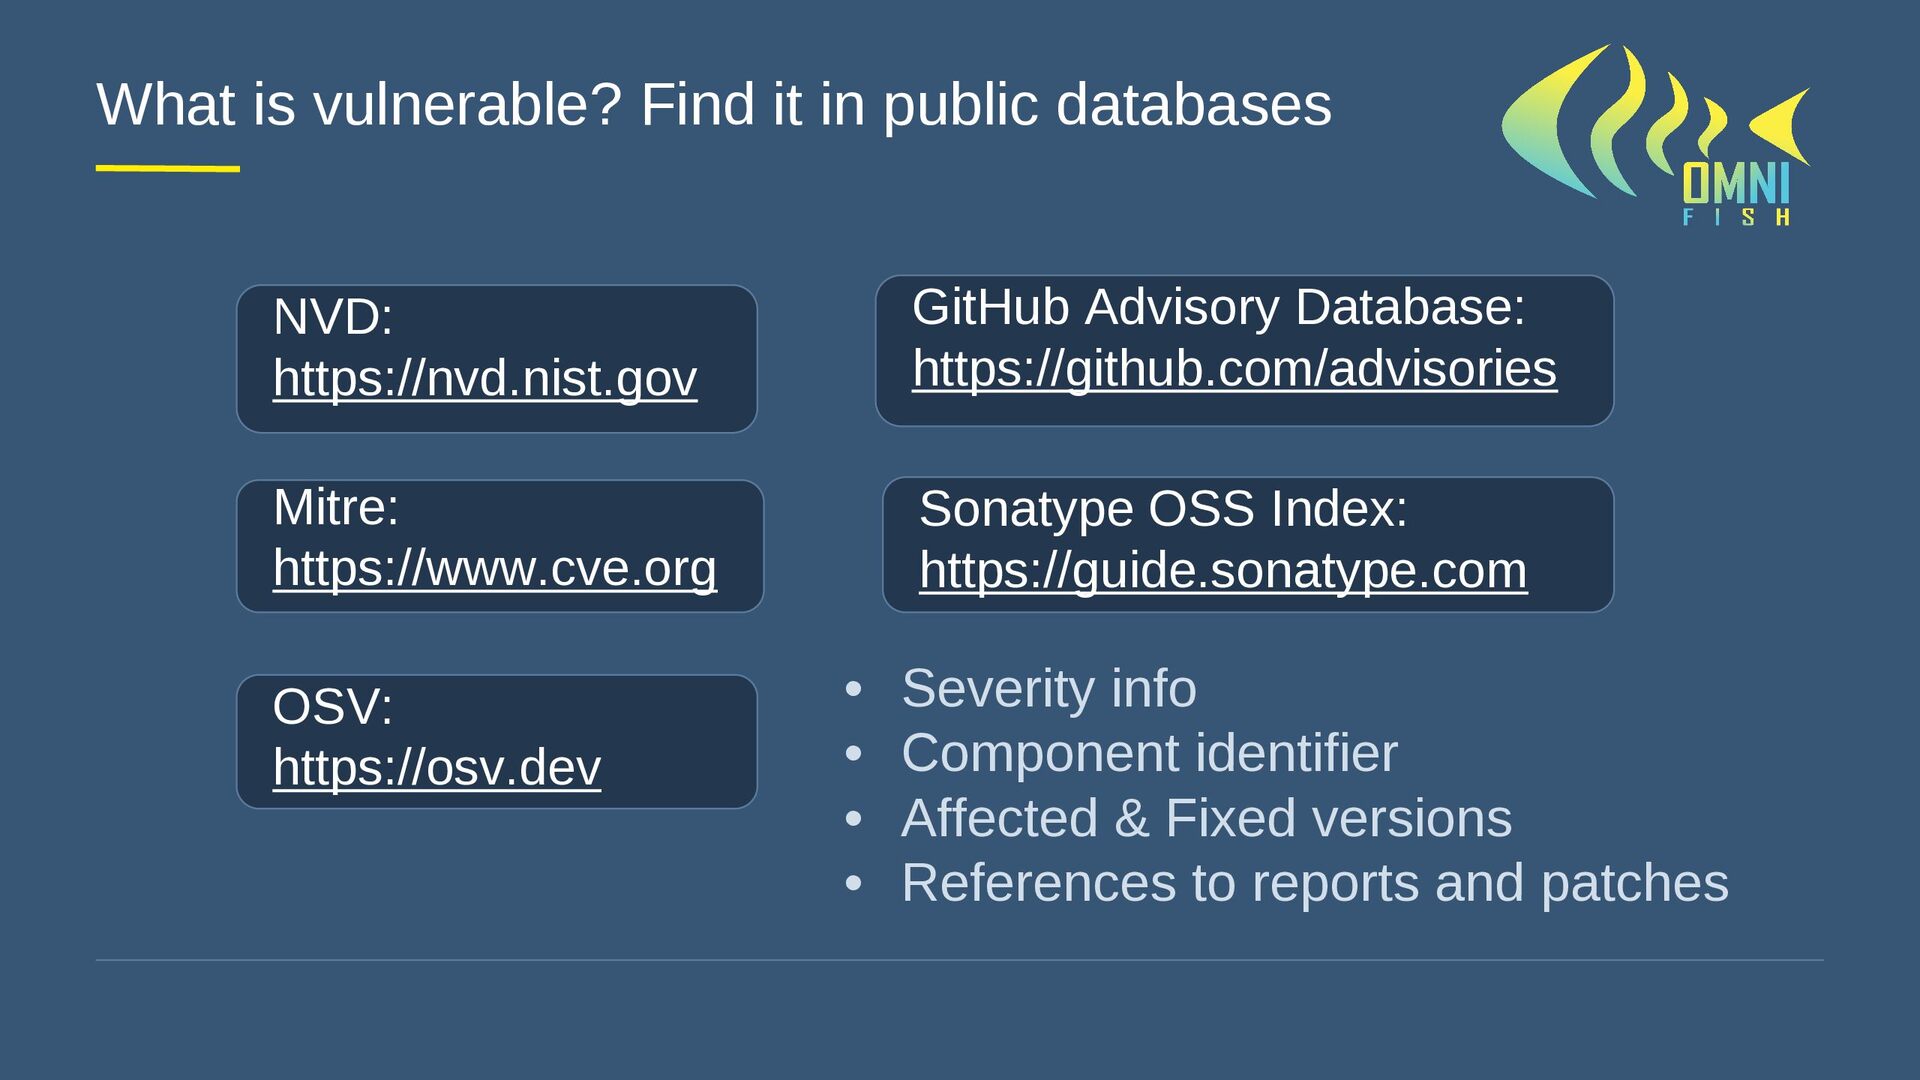
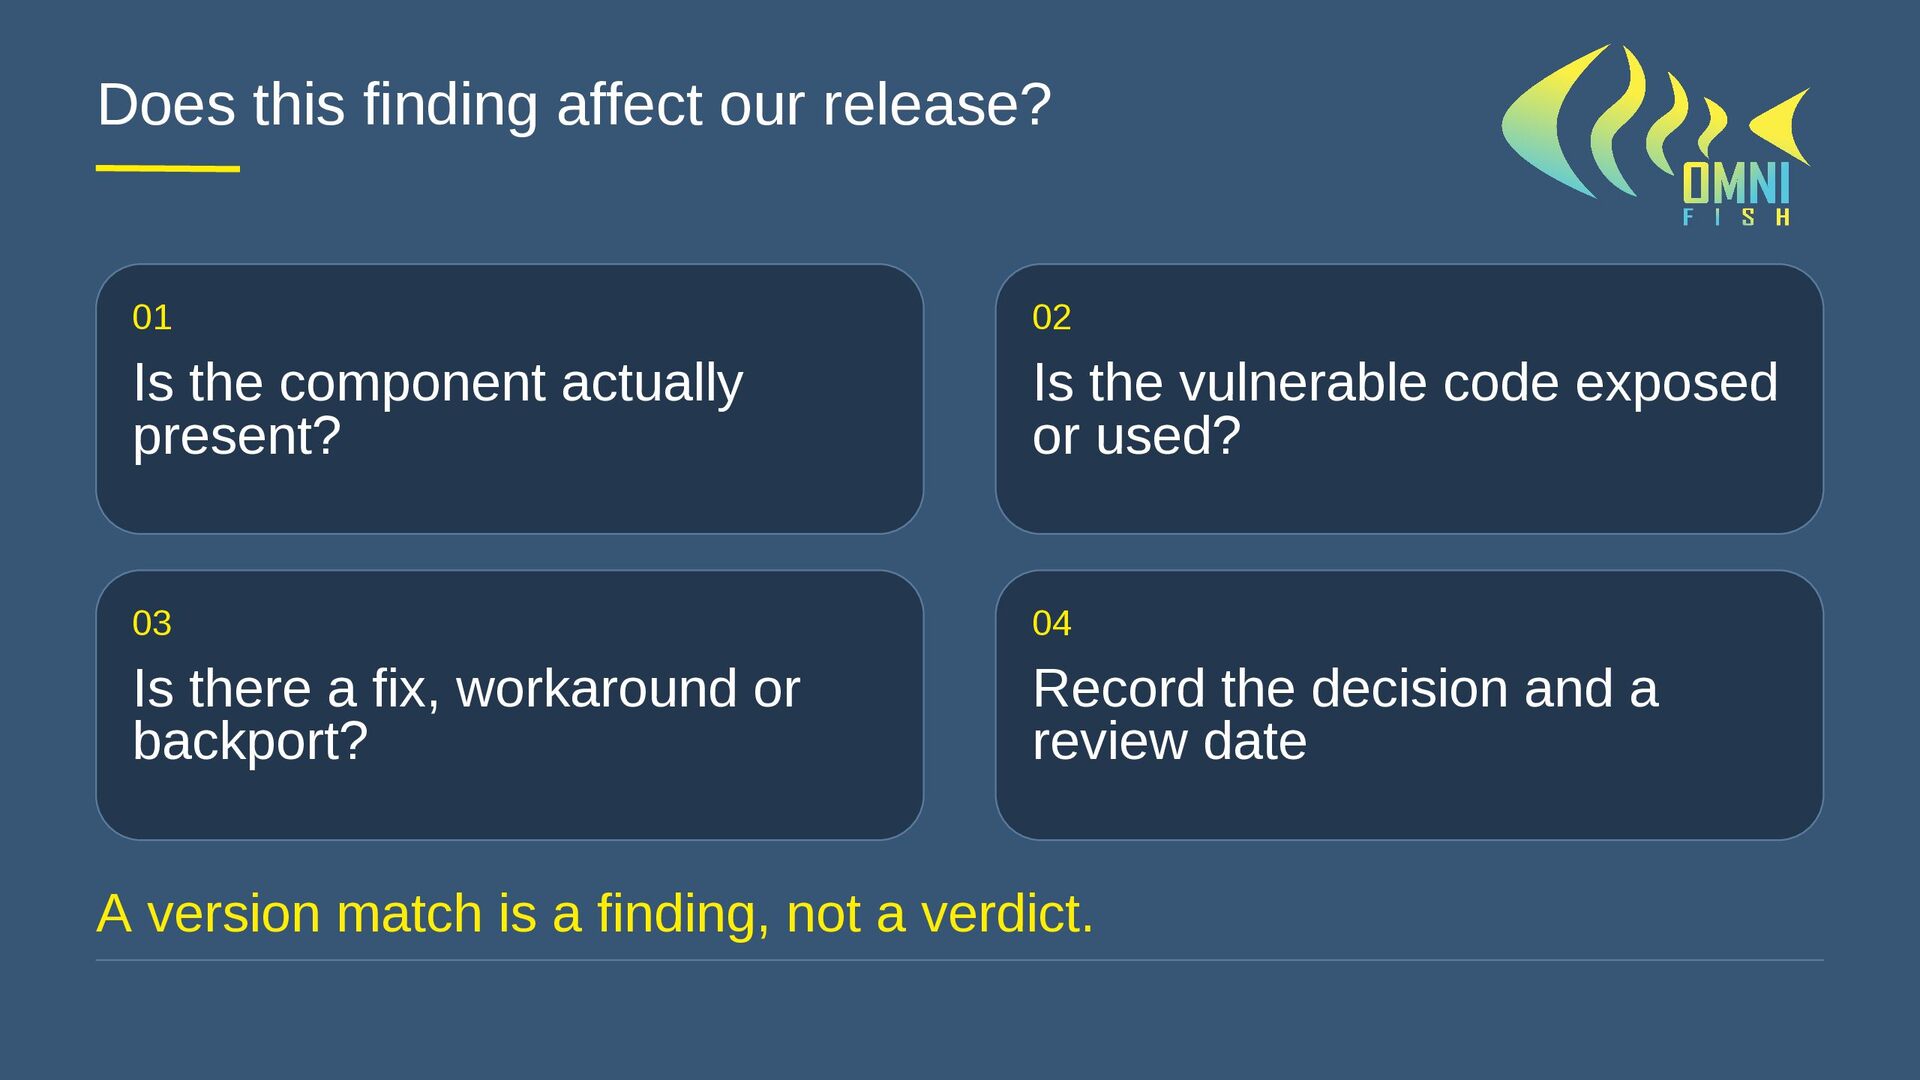
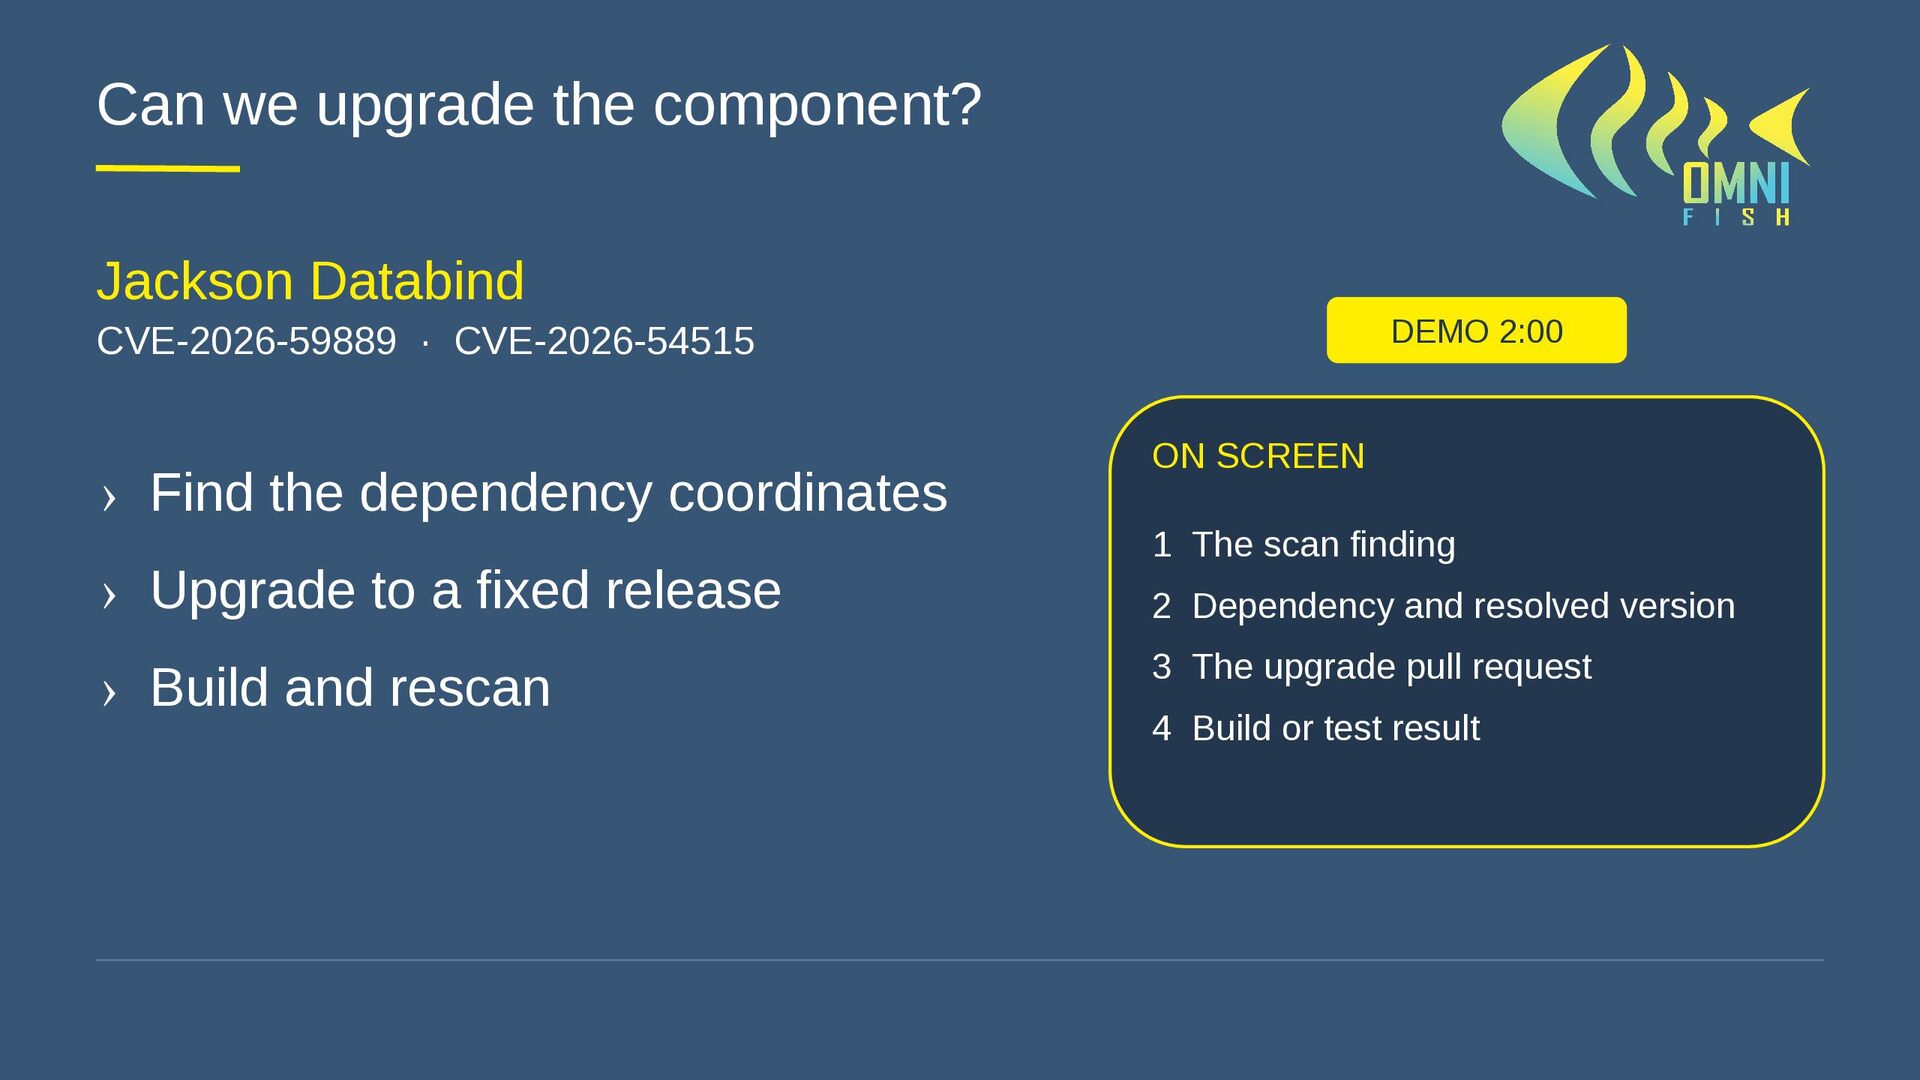
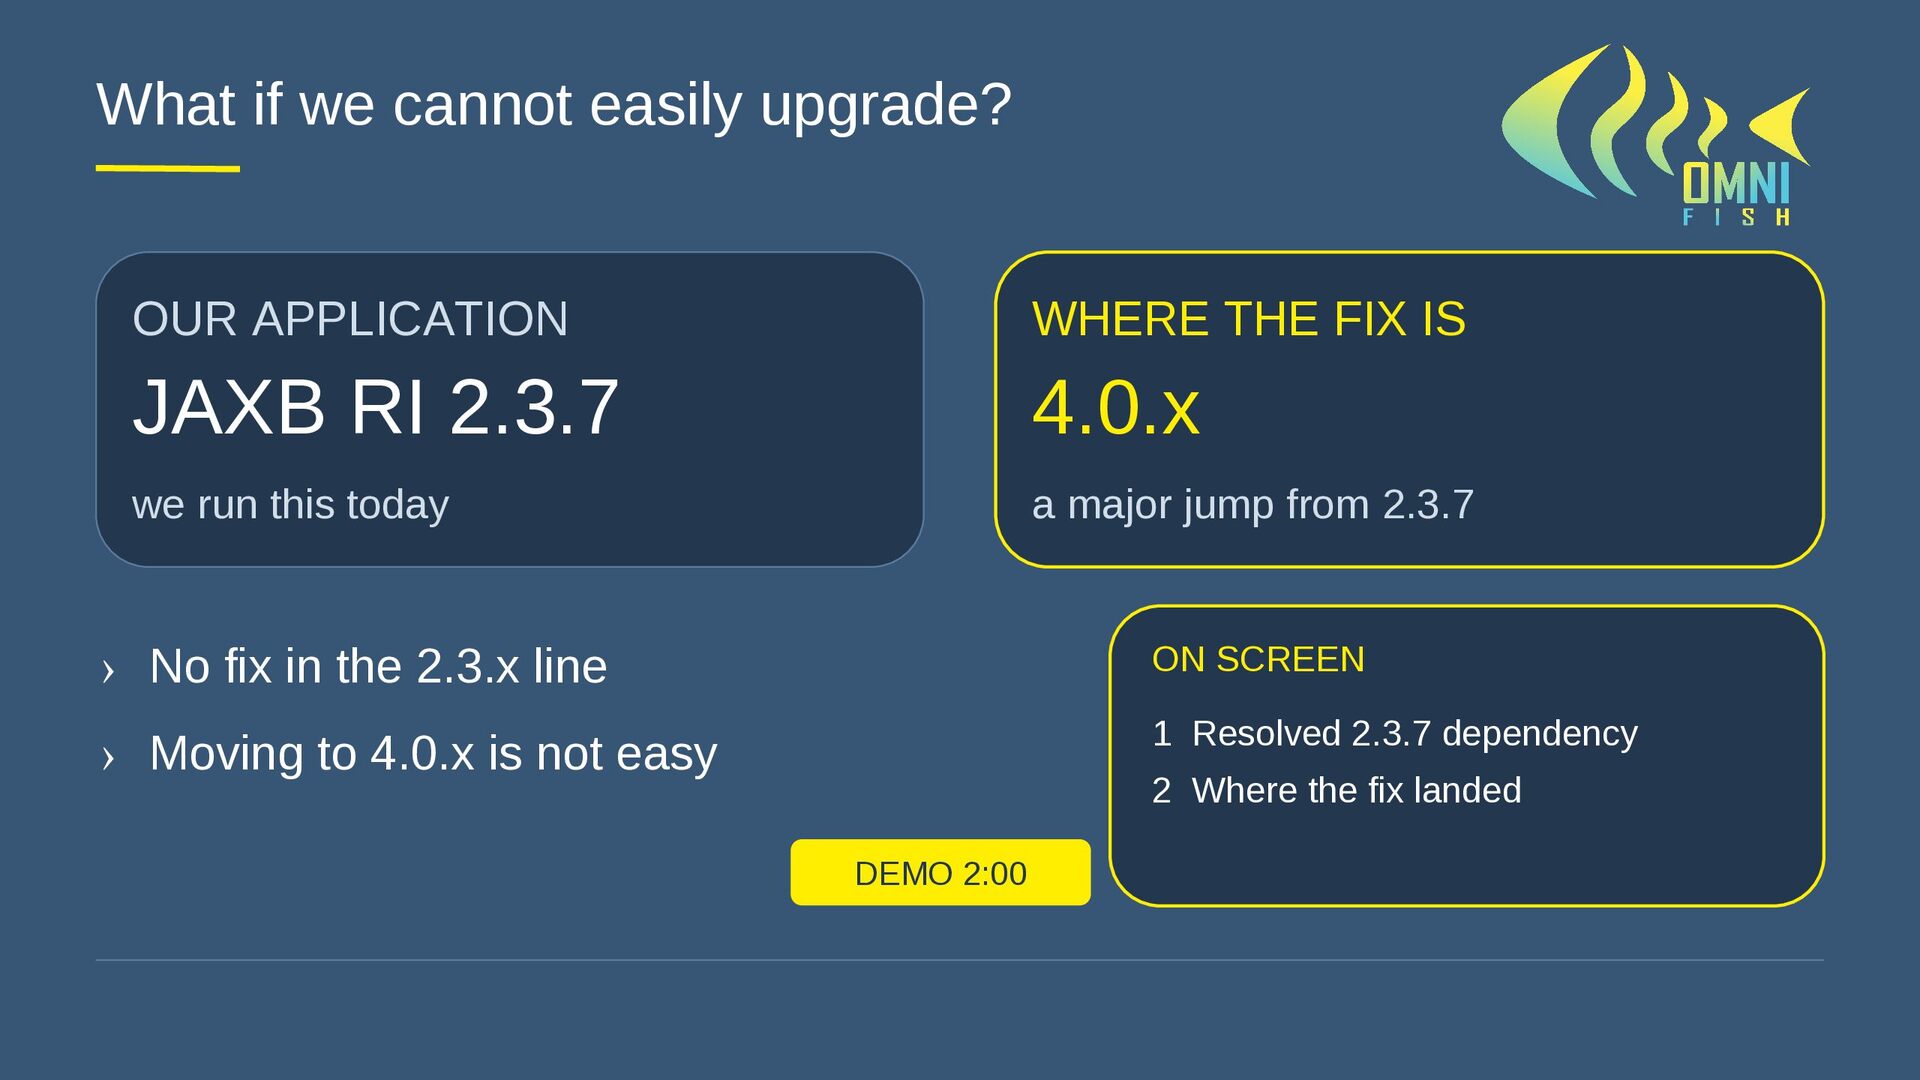
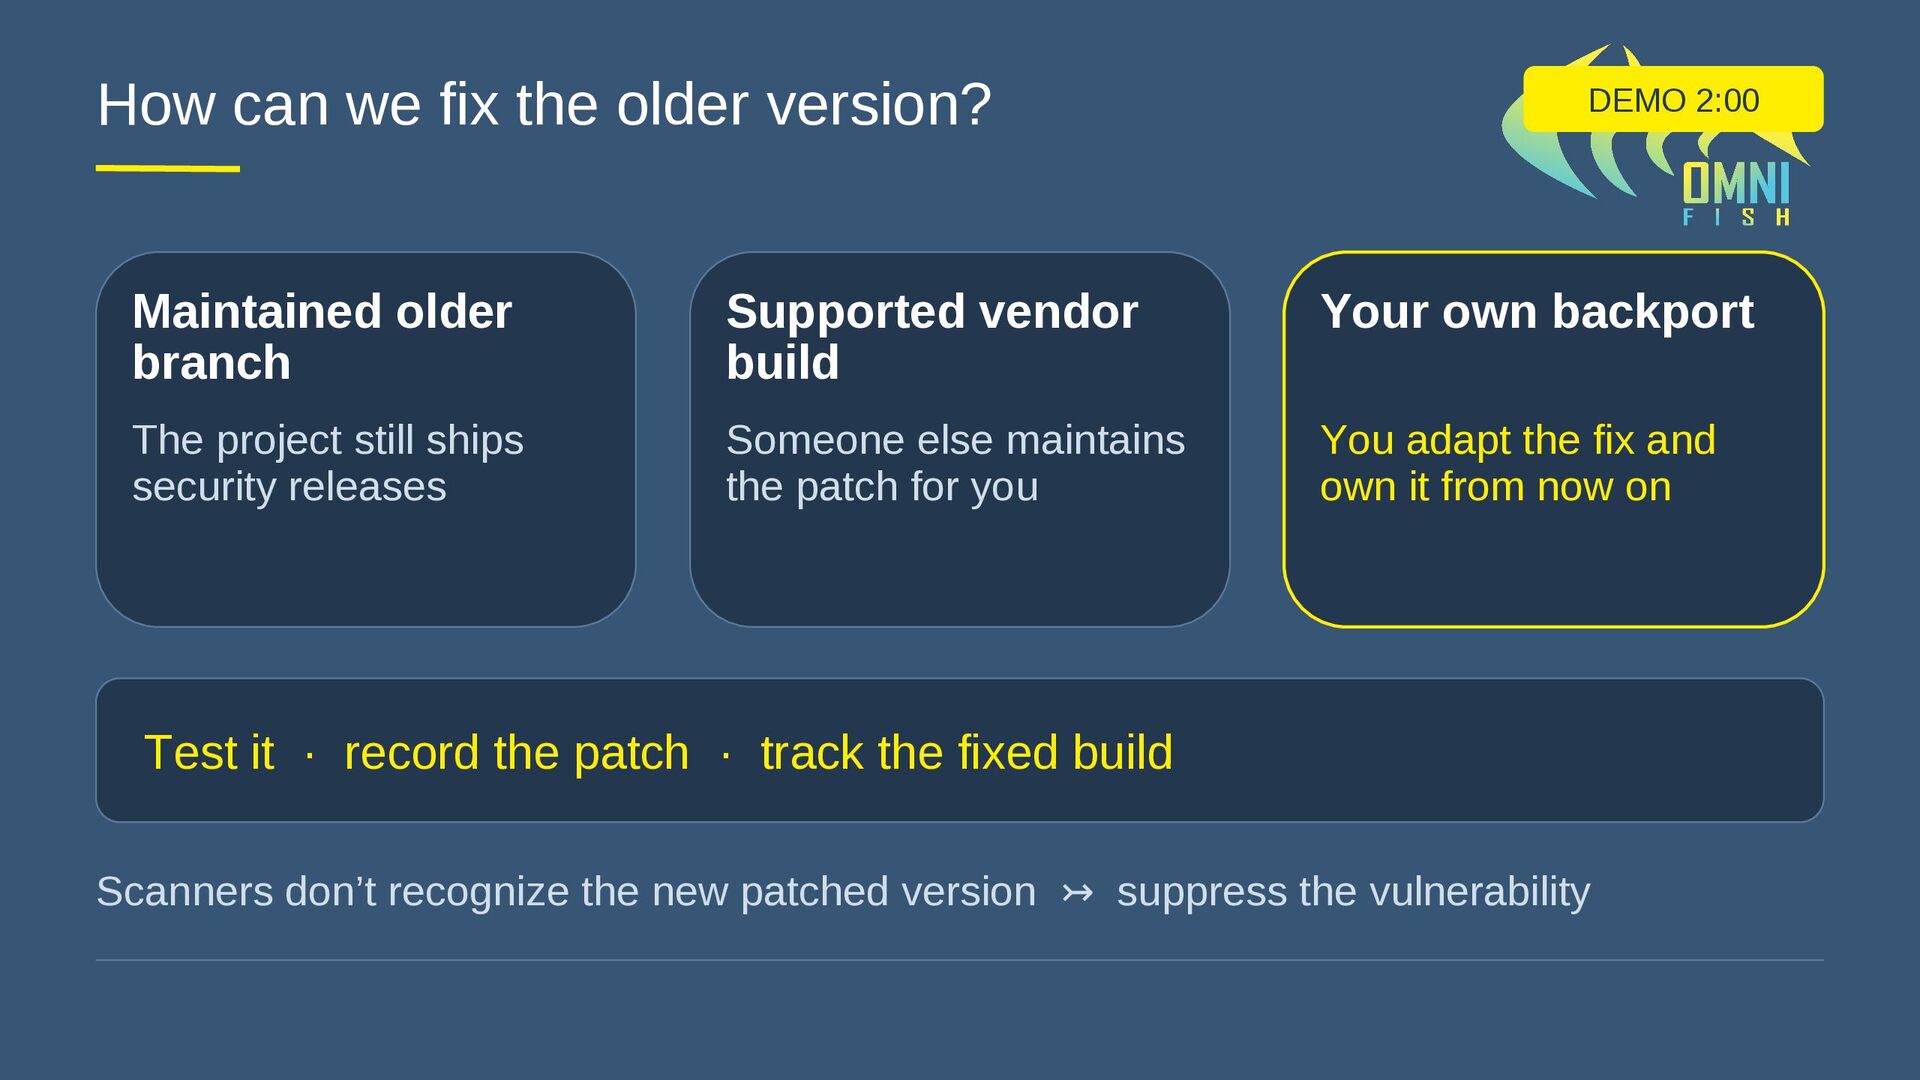
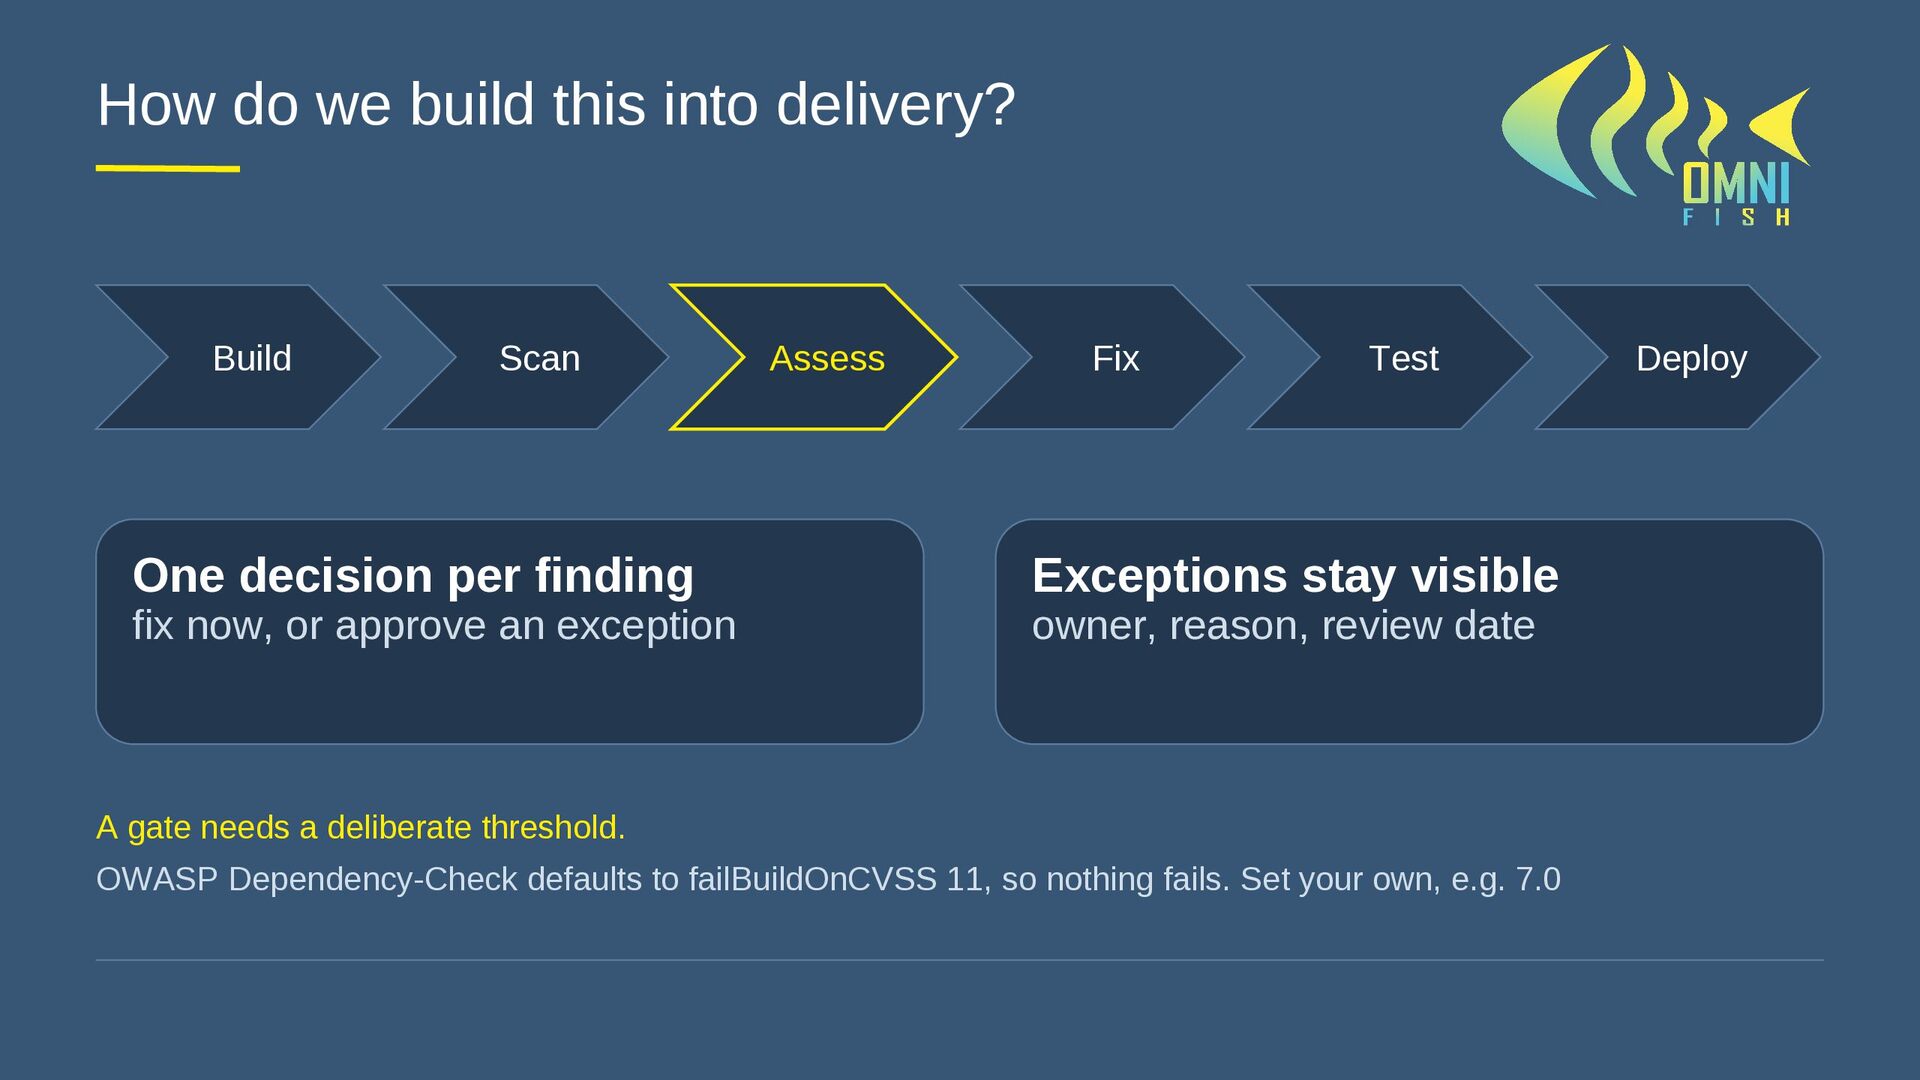
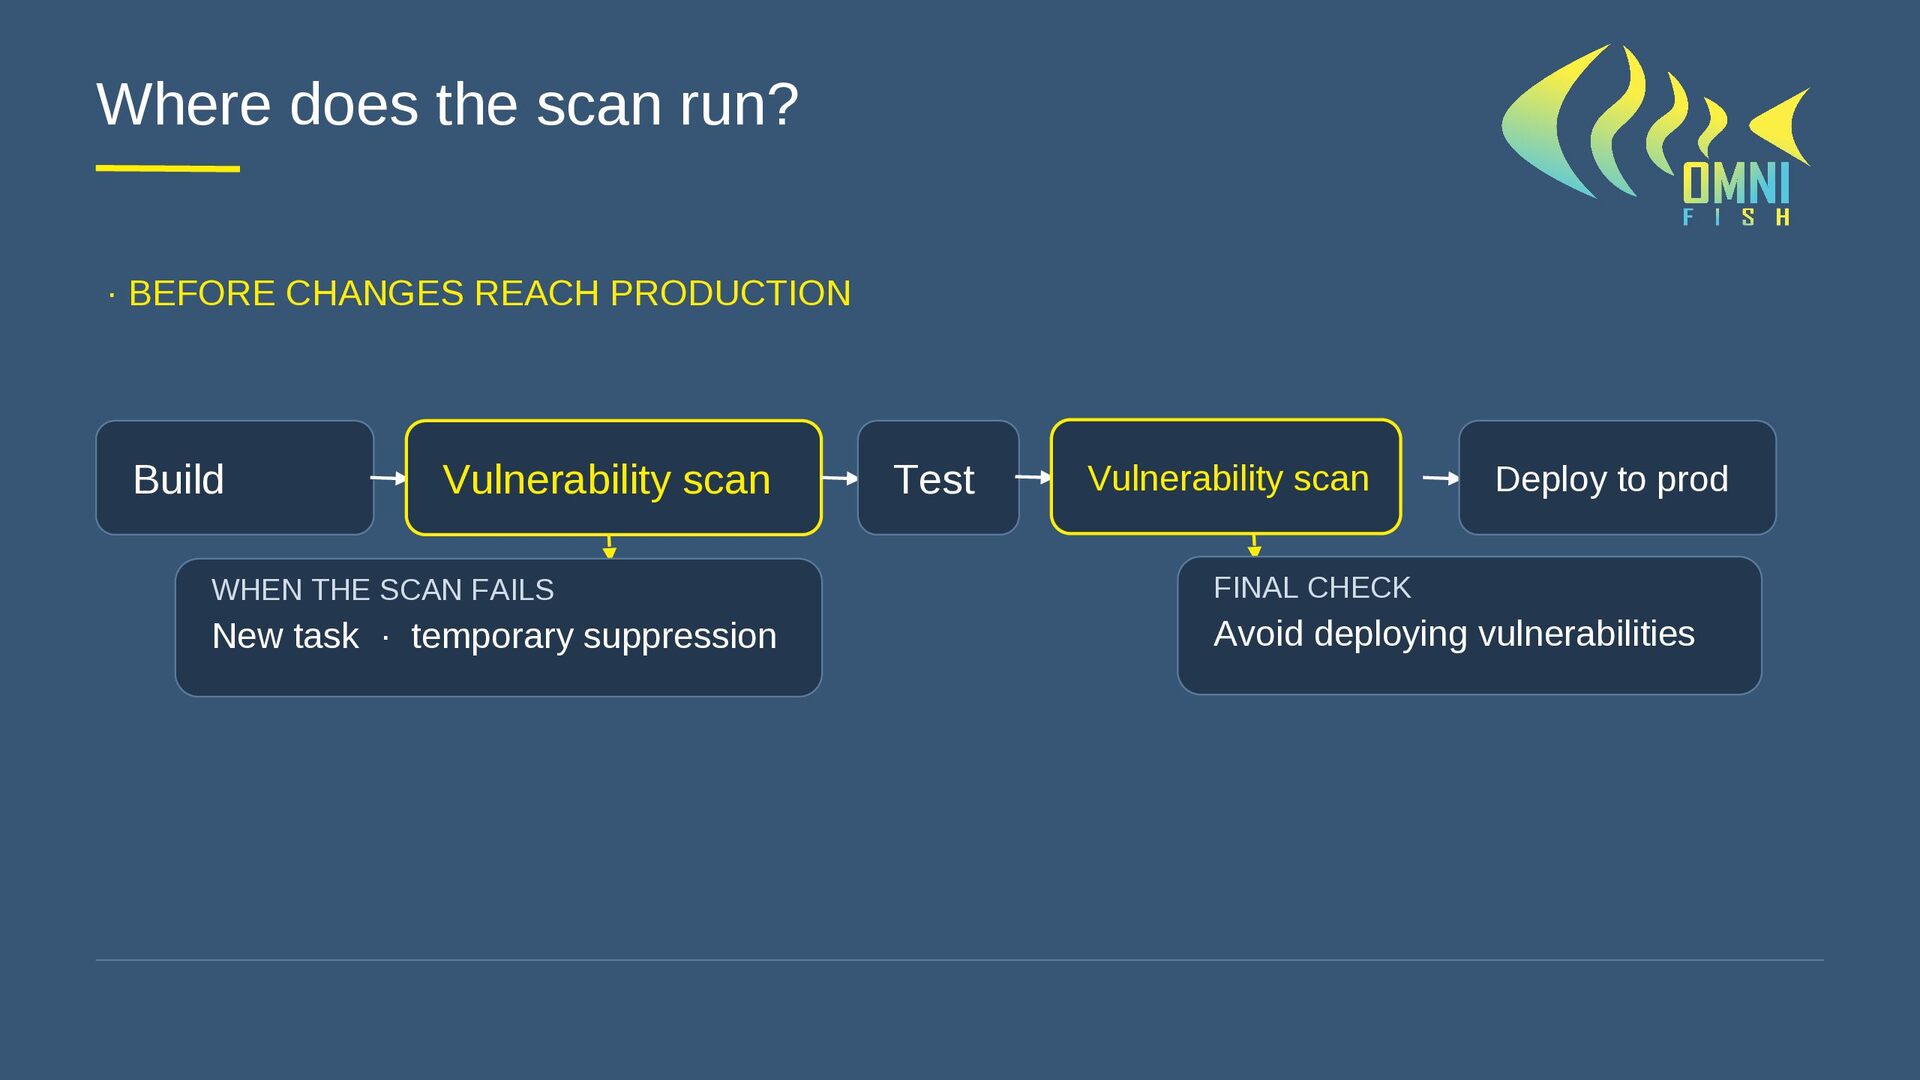
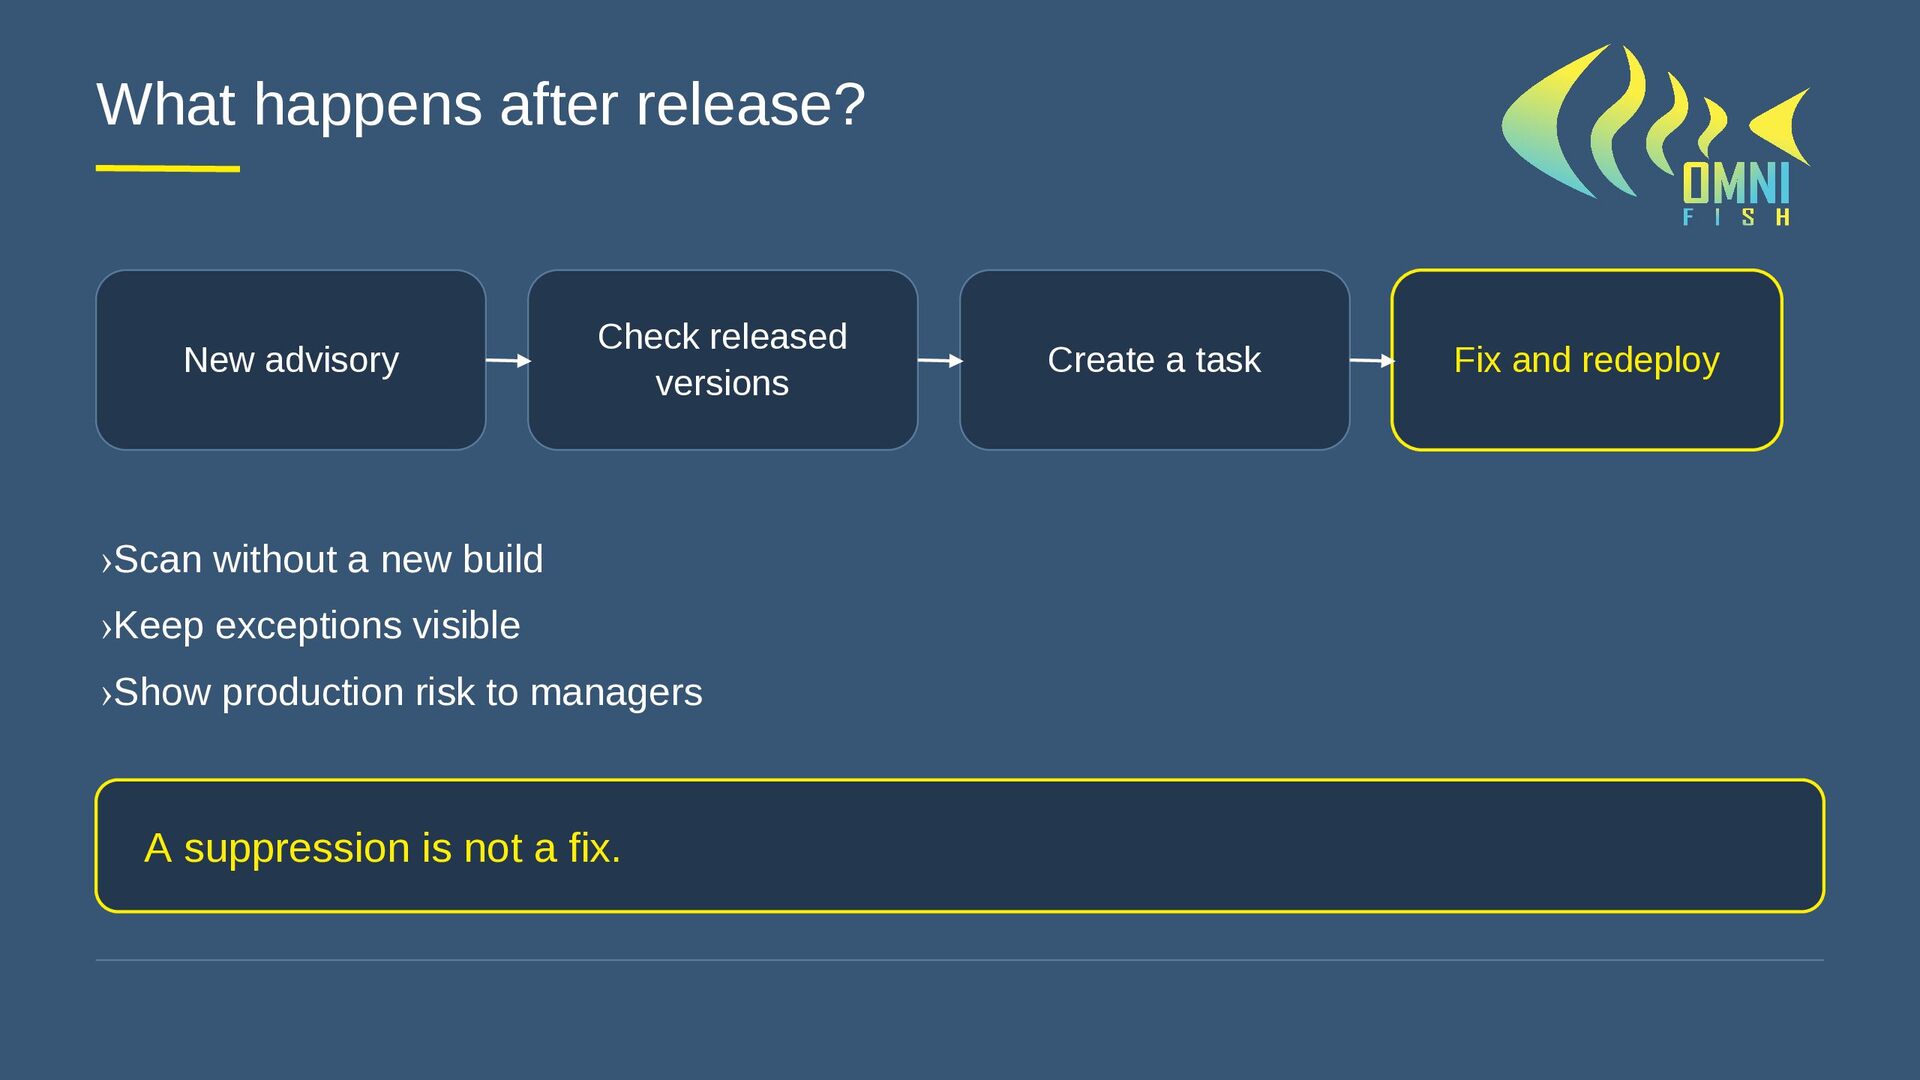
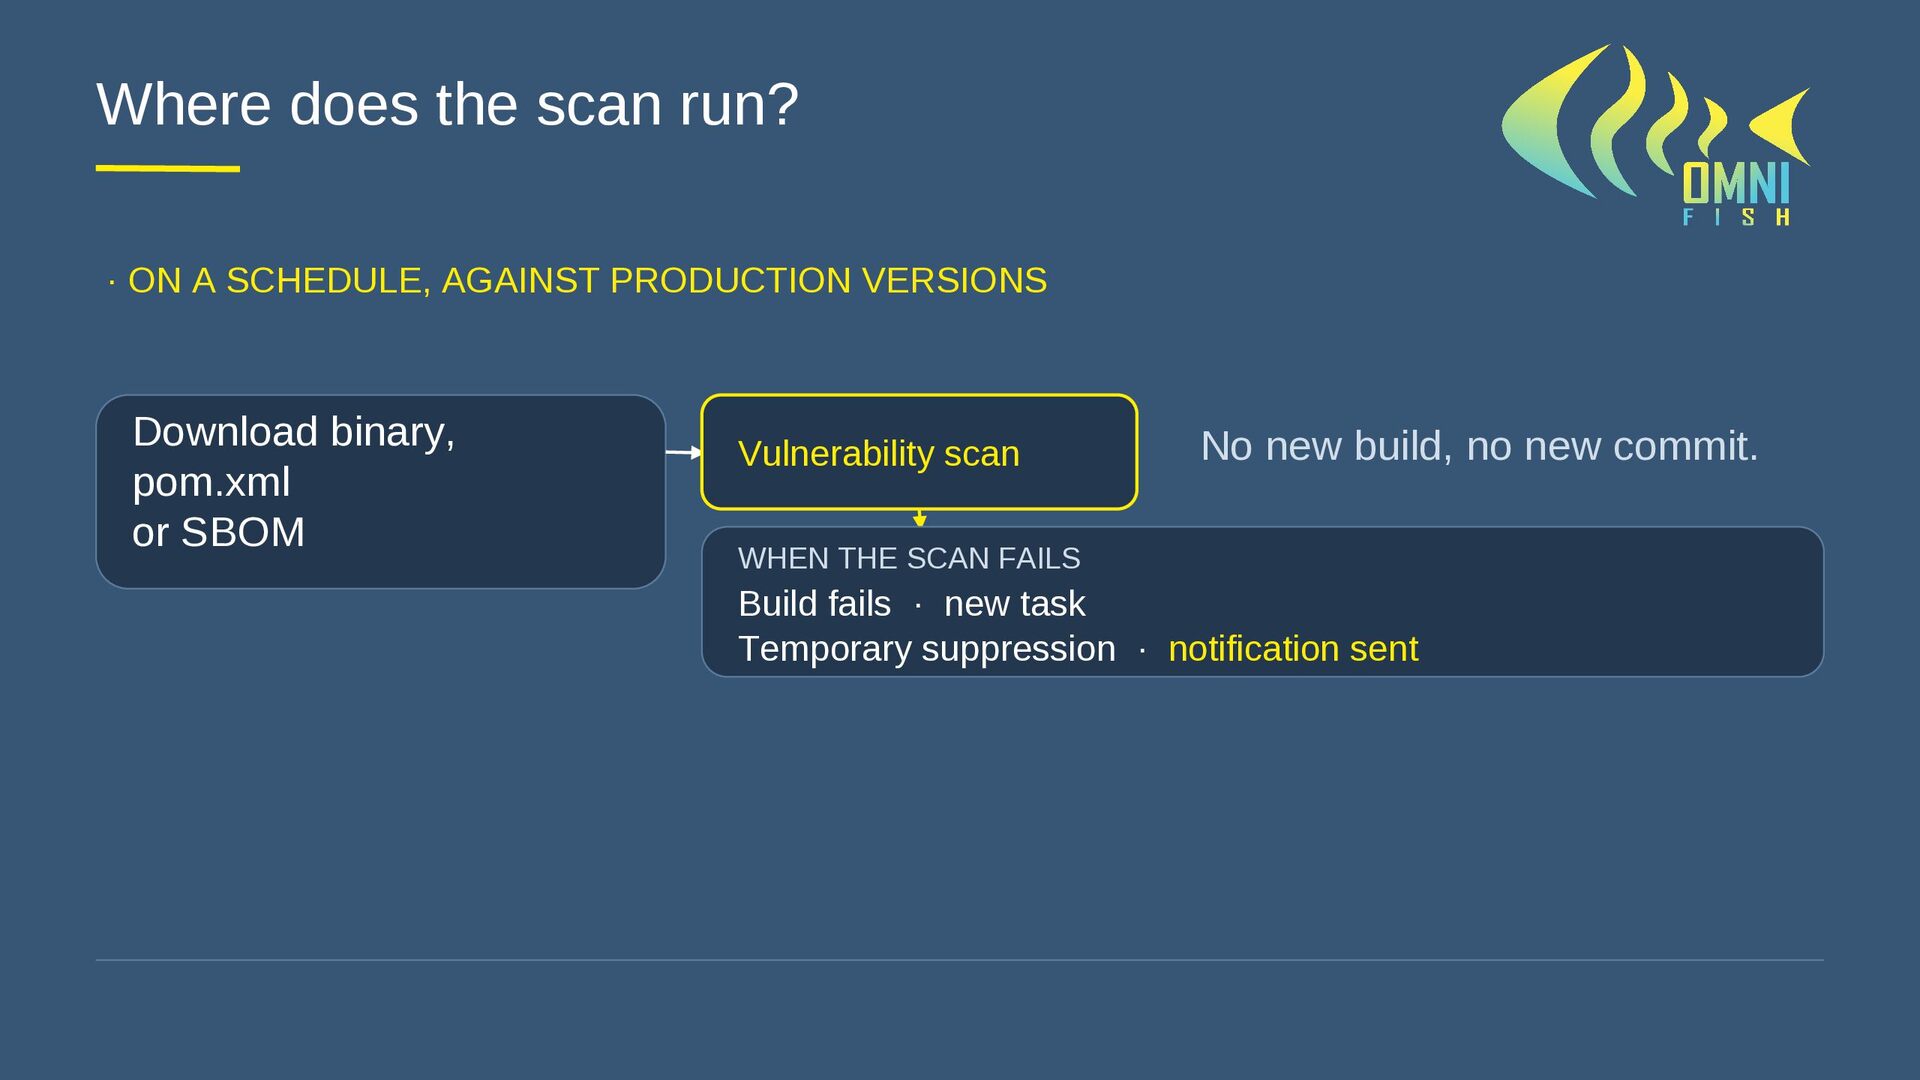
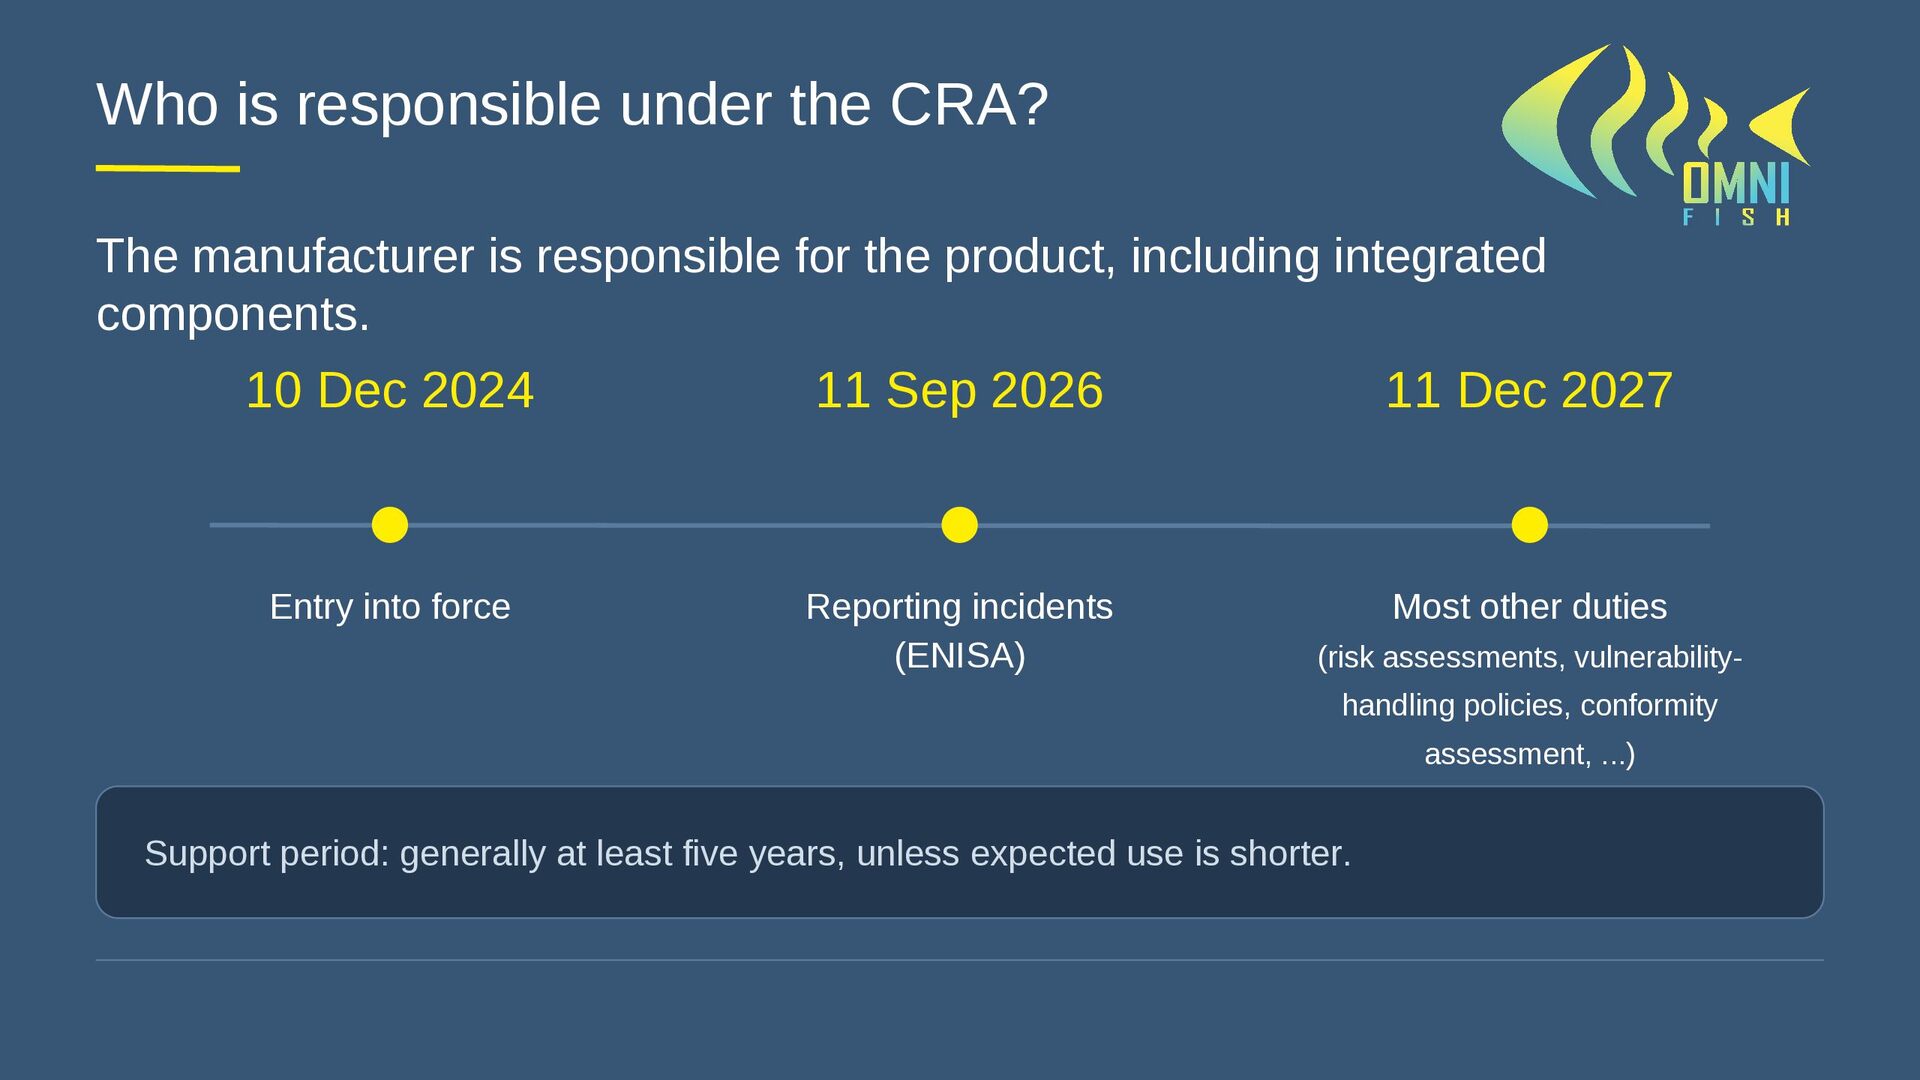
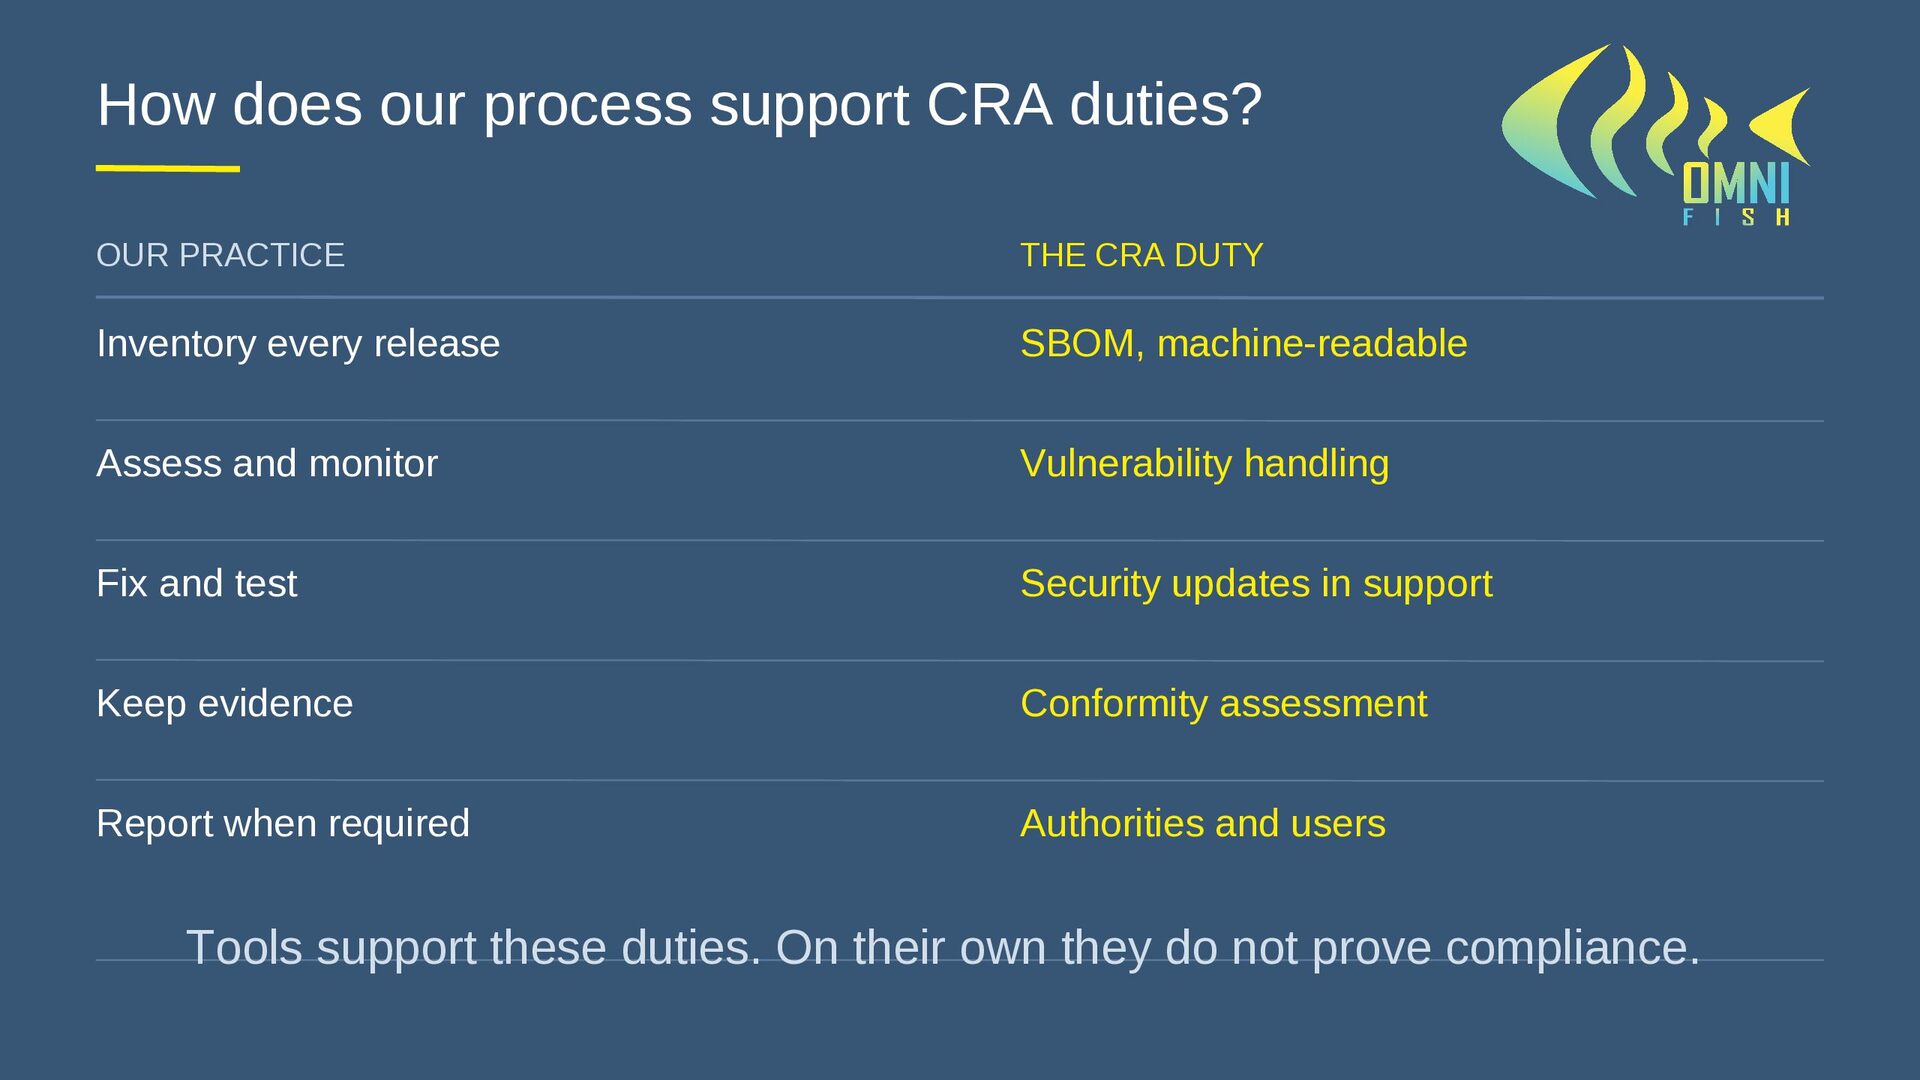
We start by understanding what is inside our applications and how to detect CVE vulnerabilities. We then extend this into automated detection and remediation workflows. We end up exploring various real-life cases of treating vulnerabilities, from simple component upgrades to backporting patches if we cannot upgrade a component. Finally, we connect these practices to the EU Cyber Resilience Act, which introduces formal requirements for vulnerability management and software transparency.
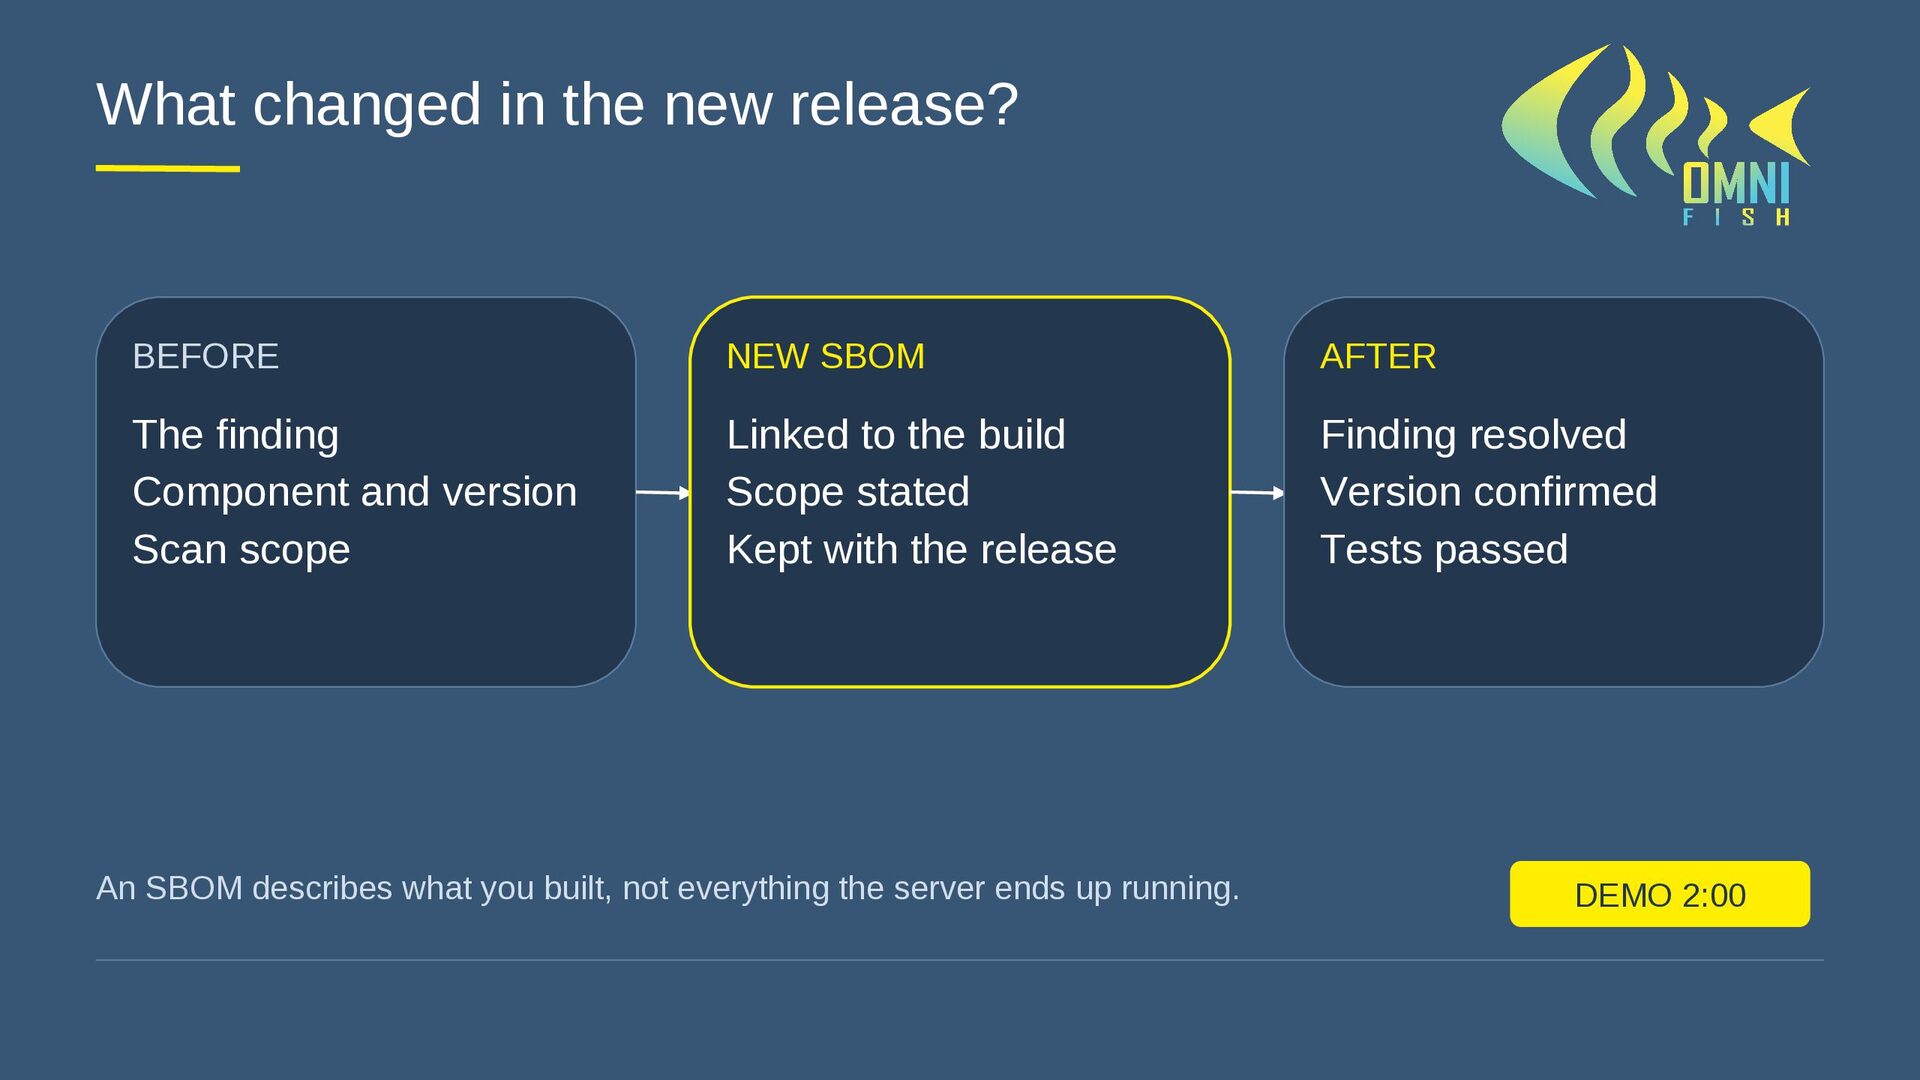
You will understand how these legal requirements affect software producers and how the presented process maps directly to them. A live demo demonstrates CVE detection, fixing, SBOM generation, and redeployment in a Java application pipeline, showing how to turn security into a continuous part of delivery rather than an occasional audit.

 omnifish
 goyoki
 yuutosi
 minorun365
 kworkdev
 jacopen
 pauli
 amarelo_n24
 biwashi
 nejumi
 lamb_moko
 ttelltte
 yappli_developers
 panda_program
 stephenakadiri
 wjessup
 uxyall
 jonrohan
 davidcarrasco
 aleyda
 trallard
 nikkihalliwell
 speakerdeck
 codingconduct
 gurzu