Share
Embed
«OWASP Сheat Sheet Series. Microservices-based security architecture documentation», Александр Барабанов
Видео: https://youtu.be/kUZGBCvuvcQ
OWASP Moscow 2020/1 (https://habr.com/ru/company/owasp/blog/497830/)
OWASP Moscow
March 05, 2020
Transcript
14 slides
-
About me • Principal Security Engineer at Huawei Advanced Security
Research Team/Moscow Advanced Software Technology Lab • Associate Professor at Bauman MSTU, Information Security Department • Prior: Application security architect at Baker Hughes/Rosneft, Security expert at NPO Echelon • Ph.D in CS, CISSP, CSSLP • OWASP contributor: CS series -
Objective and motivations Typical questions for security architects: 1. Threat
modeling and enforcement of the principle of least privilege: – What scopes or API keys does microservice minimally need to access other microservice APIs? – What grants does microservice minimally need to access database or message queue? 2. Data leakage analysis: – What storages or message queues do contain sensitive data? – Does microservice read/write date from/to specific database or message queue? – What microservices are invoked by dedicated microservice? What data is passed between microservices? 3. Attack surface analysis: – What microservices endpoints need to be tested during security testing? -
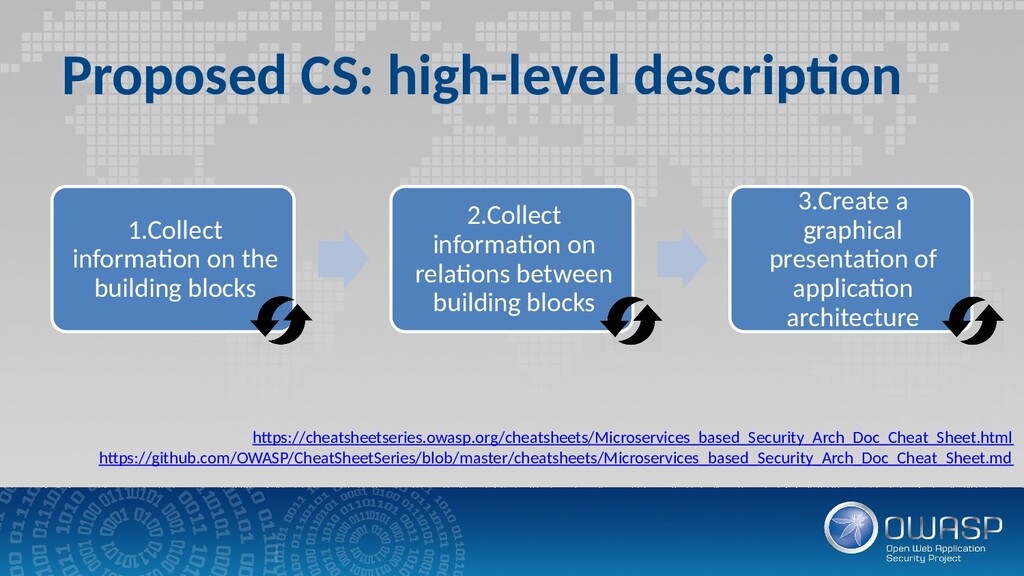
Proposed CS: high-level description 1.Collect information on the building blocks
2.Collect information on relations between building blocks 3.Create a graphical presentation of application architecture https://cheatsheetseries.owasp.org/cheatsheets/Microservices_based_Security_Arch_Doc_Cheat_Sheet.html https://github.com/OWASP/CheatSheetSeries/blob/master/cheatsheets/Microservices_based_Security_Arch_Doc_Cheat_Sheet.md -
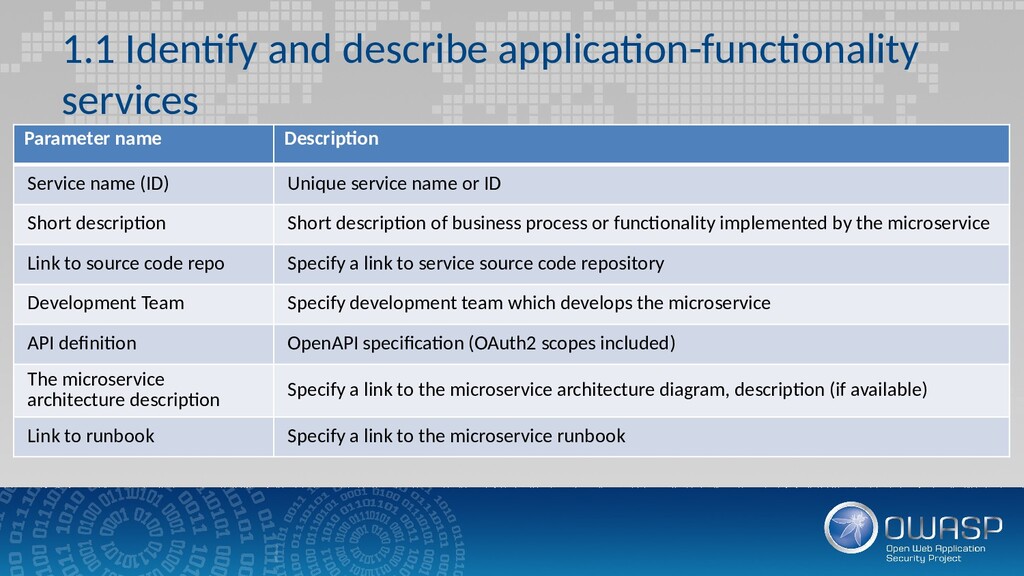
1.1 Identify and describe application-functionality services Parameter name Description Service
name (ID) Unique service name or ID Short description Short description of business process or functionality implemented by the microservice Link to source code repo Specify a link to service source code repository Development Team Specify development team which develops the microservice API definition OpenAPI specification (OAuth2 scopes included) The microservice architecture description Specify a link to the microservice architecture diagram, description (if available) Link to runbook Specify a link to the microservice runbook -
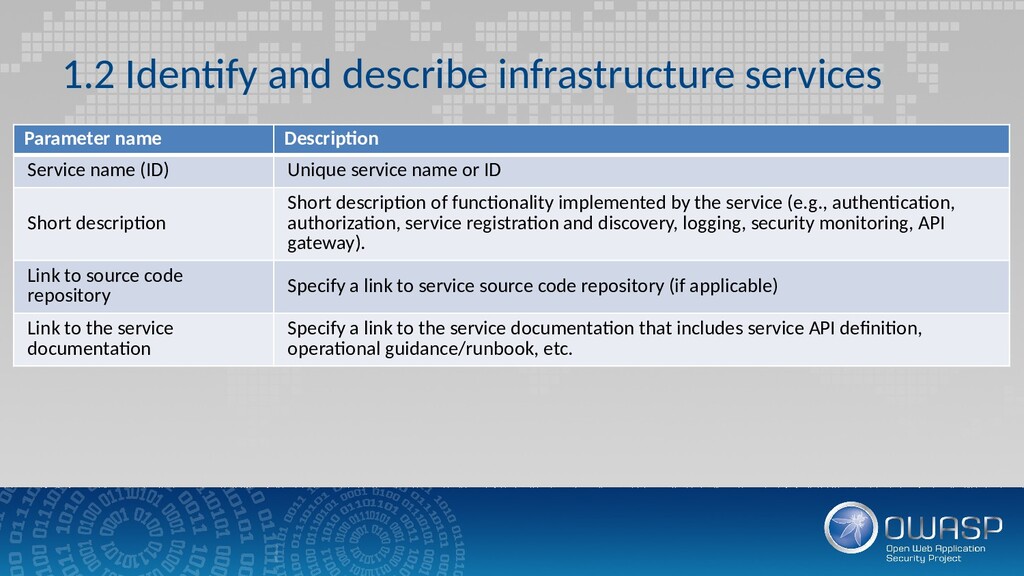
1.2 Identify and describe infrastructure services Parameter name Description Service
name (ID) Unique service name or ID Short description Short description of functionality implemented by the service (e.g., authentication, authorization, service registration and discovery, logging, security monitoring, API gateway). Link to source code repository Specify a link to service source code repository (if applicable) Link to the service documentation Specify a link to the service documentation that includes service API definition, operational guidance/runbook, etc. -
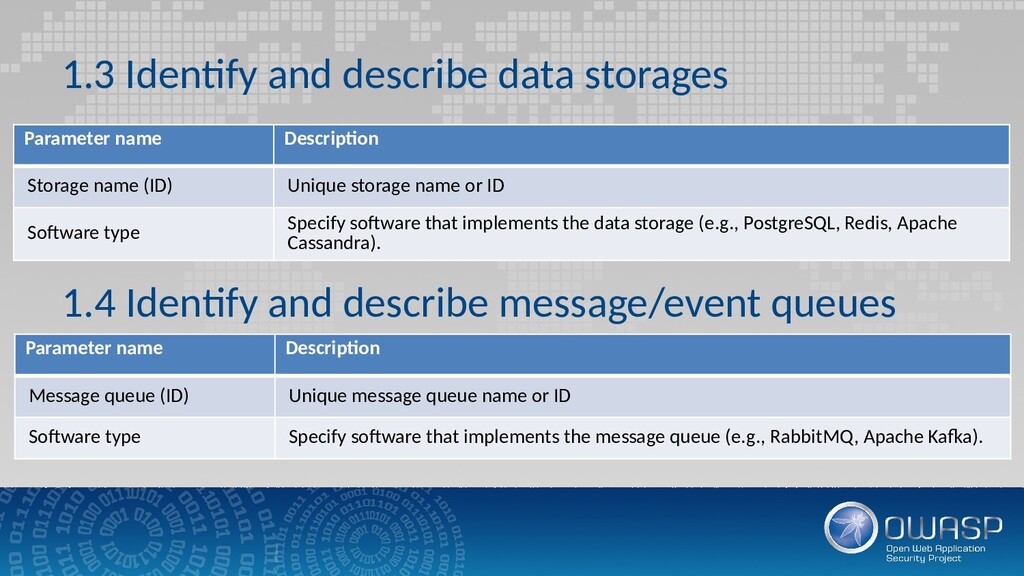
1.3 Identify and describe data storages Parameter name Description Storage
name (ID) Unique storage name or ID Software type Specify software that implements the data storage (e.g., PostgreSQL, Redis, Apache Cassandra). 1.4 Identify and describe message/event queues Parameter name Description Message queue (ID) Unique message queue name or ID Software type Specify software that implements the message queue (e.g., RabbitMQ, Apache Kafka). -
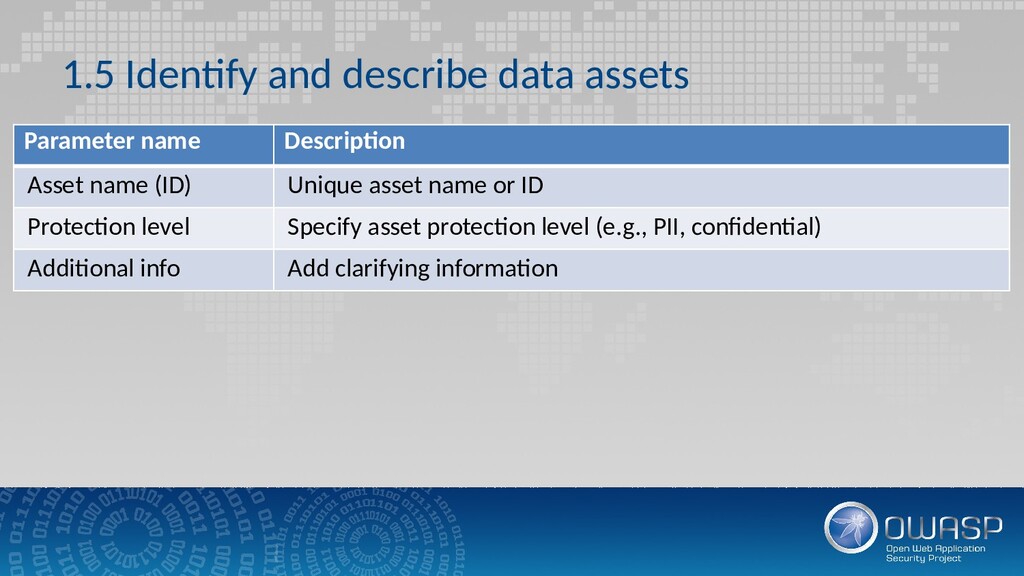
1.5 Identify and describe data assets Parameter name Description Asset
name (ID) Unique asset name or ID Protection level Specify asset protection level (e.g., PII, confidential) Additional info Add clarifying information -
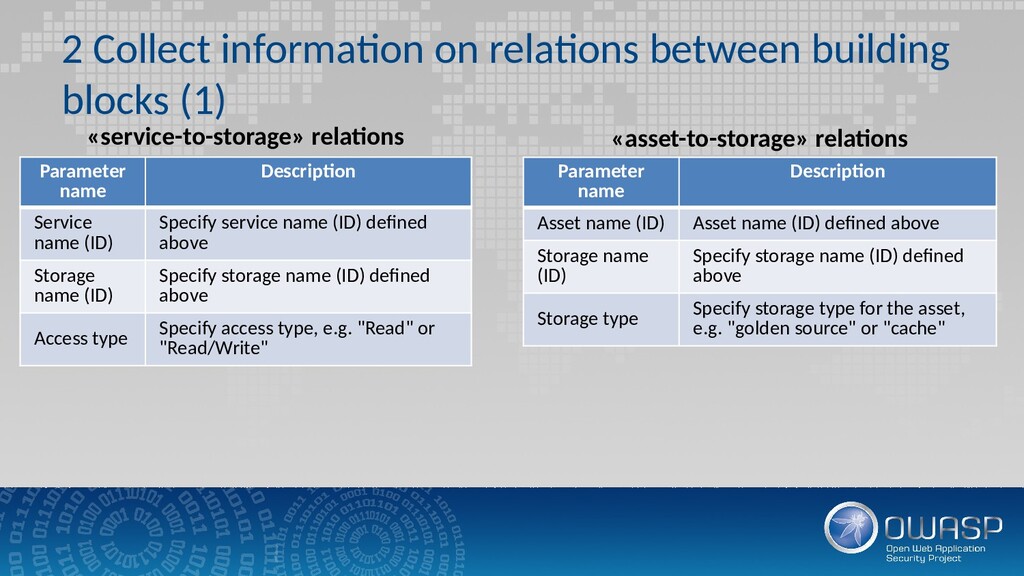
2 Collect information on relations between building blocks (1) Parameter
name Description Service name (ID) Specify service name (ID) defined above Storage name (ID) Specify storage name (ID) defined above Access type Specify access type, e.g. "Read" or "Read/Write" Parameter name Description Asset name (ID) Asset name (ID) defined above Storage name (ID) Specify storage name (ID) defined above Storage type Specify storage type for the asset, e.g. "golden source" or "cache" «service-to-storage» relations «asset-to-storage» relations -
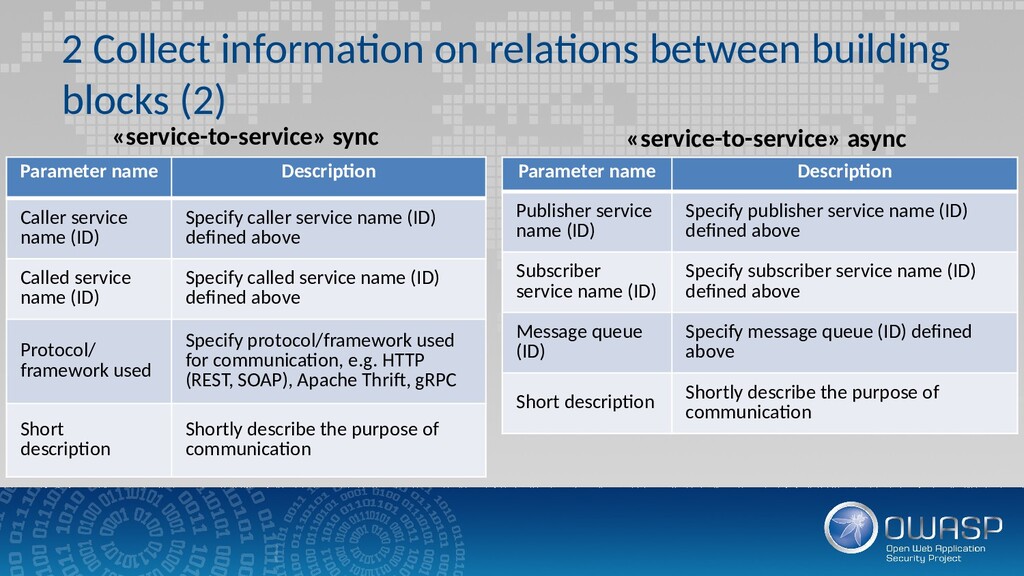
2 Collect information on relations between building blocks (2) Parameter
name Description Caller service name (ID) Specify caller service name (ID) defined above Called service name (ID) Specify called service name (ID) defined above Protocol/ framework used Specify protocol/framework used for communication, e.g. HTTP (REST, SOAP), Apache Thrift, gRPC Short description Shortly describe the purpose of communication Parameter name Description Publisher service name (ID) Specify publisher service name (ID) defined above Subscriber service name (ID) Specify subscriber service name (ID) defined above Message queue (ID) Specify message queue (ID) defined above Short description Shortly describe the purpose of communication «service-to-service» sync «service-to-service» async -
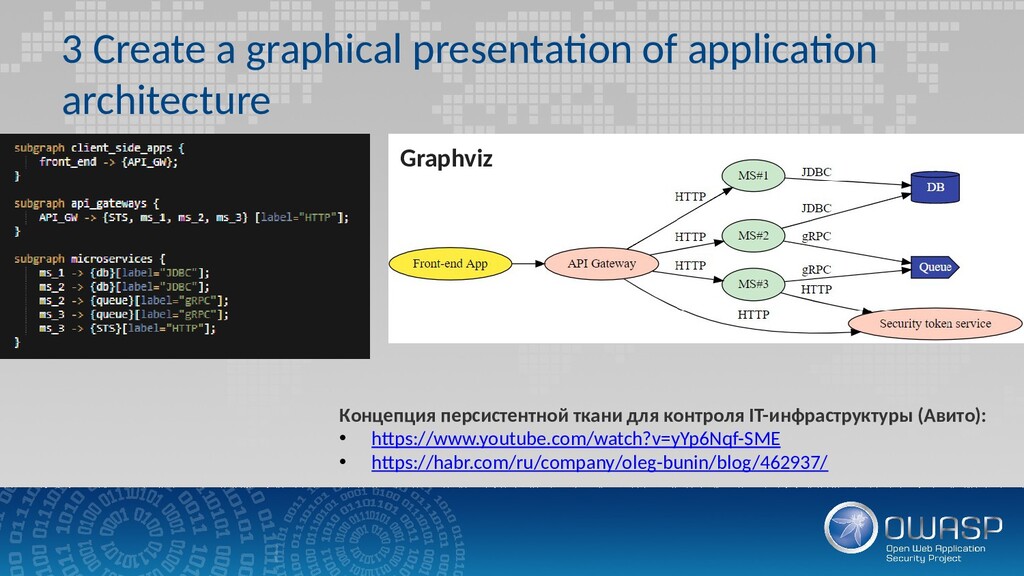
3 Create a graphical presentation of application architecture Концепция персистентной
ткани для контроля IT-инфраструктуры (Авито): • https://www.youtube.com/watch?v=yYp6Nqf-SME • https://habr.com/ru/company/oleg-bunin/blog/462937/ Graphviz -
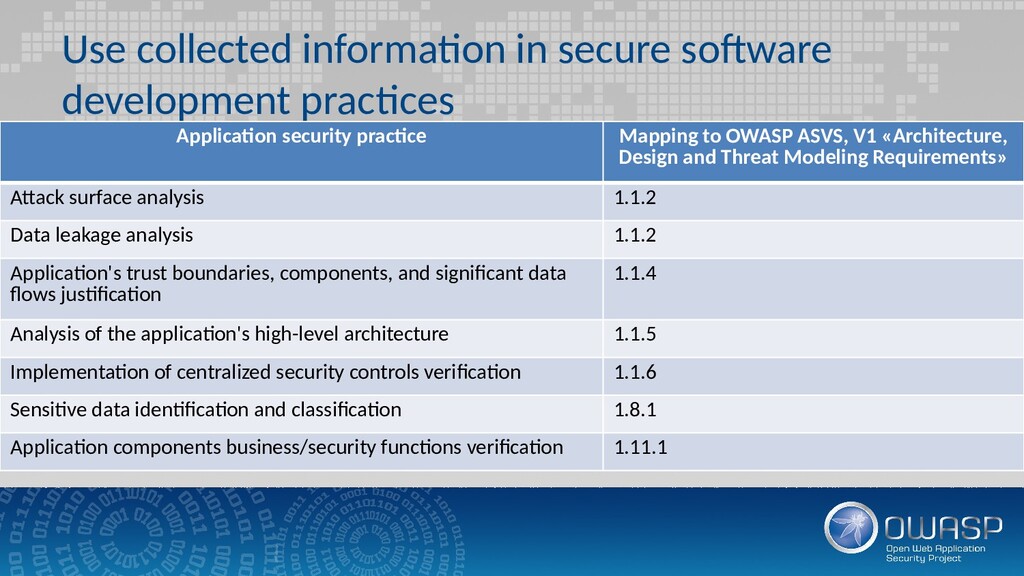
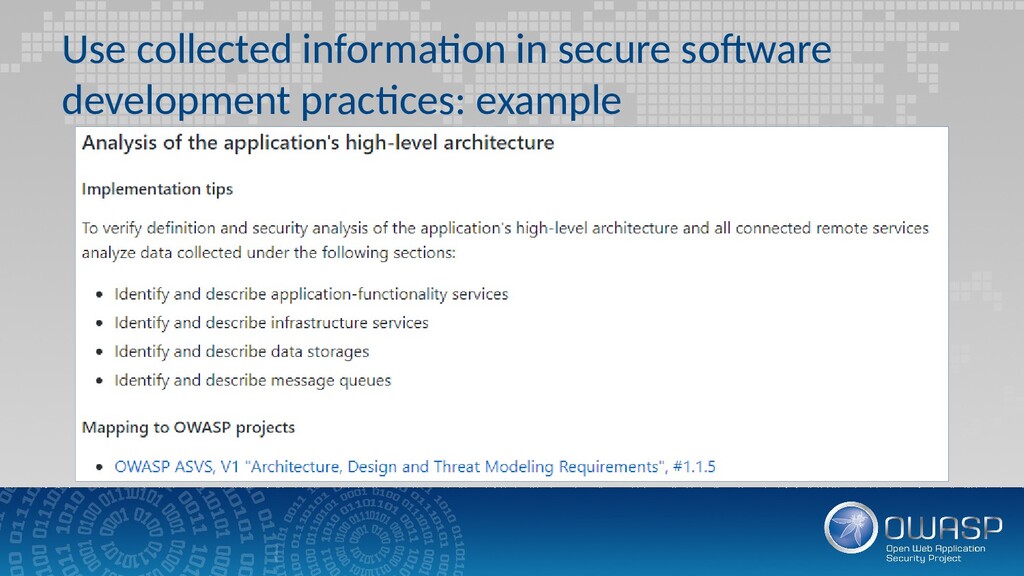
Use collected information in secure software development practices Application security
practice Mapping to OWASP ASVS, V1 «Architecture, Design and Threat Modeling Requirements» Attack surface analysis 1.1.2 Data leakage analysis 1.1.2 Application's trust boundaries, components, and significant data flows justification 1.1.4 Analysis of the application's high-level architecture 1.1.5 Implementation of centralized security controls verification 1.1.6 Sensitive data identification and classification 1.8.1 Application components business/security functions verification 1.11.1