Upgrade to Pro
— share decks privately, control downloads, hide ads and more …
Speaker Deck
Sign up for free
Menu
Search
Features
All features
Private URLs
Password Protection
Custom URLS
Scheduled publishing
Remove Branding
Restrict embedding
Deck Collections
Notes
Features
All features
Private URLs
Password Protection
Custom URLS
Scheduled publishing
Remove Branding
Restrict embedding
Deck Collections
Notes
Explore
Featured decks
Featured speakers
Programming
Technology
Storyboards
Explore
Featured decks
Featured speakers
Programming
Technology
Storyboards
Pricing
Search
Sign in
Sign up for free
iOS Security - Hacking iOS Apps
Search
Bruno Rocha
June 11, 2017
Technology
22
0
Share
Embed
Copy iframe code
Copy JS code
Copy link
Start on current slide
iOS Security - Hacking iOS Apps
TDC 2017
Bruno Rocha
June 11, 2017
More Decks by Bruno Rocha
See All by Bruno Rocha
BuckOutsideValley.pdf
rockbruno
1
120
Avoiding Release Anxiety
rockbruno
0
39
Creating Scalable iOS Apps
rockbruno
0
20
Other Decks in Technology
See All in Technology
10年後、Engineering 行為を剥奪されるとして、わたしたちは、どう、何を創ればいいだろうか。 / If Engineering Is Taken Away in 10 Years, How and What Should We Create?
bitkey
PRO
1
190
分析AIエージェントを育てる、動く環境を育てる
codatum
1
1.1k
DGX Spark でどこまでハッキングができるのか?
kash1064
3
1.3k
継続的なAIコスト最適化
bgpat
1
340
Rust で関数型ドメインモデリング
takonda
0
140
TinyGoでオブザーバビリティ?OpenTelemetryはTinyGoで使えるのか / Is OpenTelemetry available in TinyGo environment?
ymotongpoo
2
140
日本語に強いオープンな大規模言語モデル「LLM-jp」
odashi
4
1.1k
サブエージェントと Claude Mods で作る独自 Advisor ツールの話
kenichiodo
2
160
Getting Started with Google Antigravity
glaforge
0
310
WasmをRustにする
sansantech
PRO
0
250
CTO Night|NotionのAIエージェントとFDE
kzkhykw1991
0
120
フロントエンドカンファレンス関西2026 - 速すぎるUIに、待ち時間を
teamlab
PRO
0
130
Featured
See All Featured
Making the Leap to Tech Lead
cromwellryan
135
10k
A Modern Web Designer's Workflow
chriscoyier
699
190k
Side Projects
sachag
456
43k
Improving Core Web Vitals using Speculation Rules API
sergeychernyshev
21
1.7k
Chasing Engaging Ingredients in Design
codingconduct
0
360
Fireside Chat
paigeccino
43
4.1k
State of Search Keynote: SEO is Dead Long Live SEO
ryanjones
0
320
Git: the NoSQL Database
bkeepers
PRO
433
67k
[SF Ruby Conf 2025] Rails X
palkan
3
1.5k
Stop Working from a Prison Cell
hatefulcrawdad
274
21k
Navigating Algorithm Shifts & AI Overviews - #SMXNext
aleyda
1
1.7k
Tell your own story through comics
letsgokoyo
1
1.1k
Transcript
iOS Security Bruno Rocha iOS Developer @ Movile
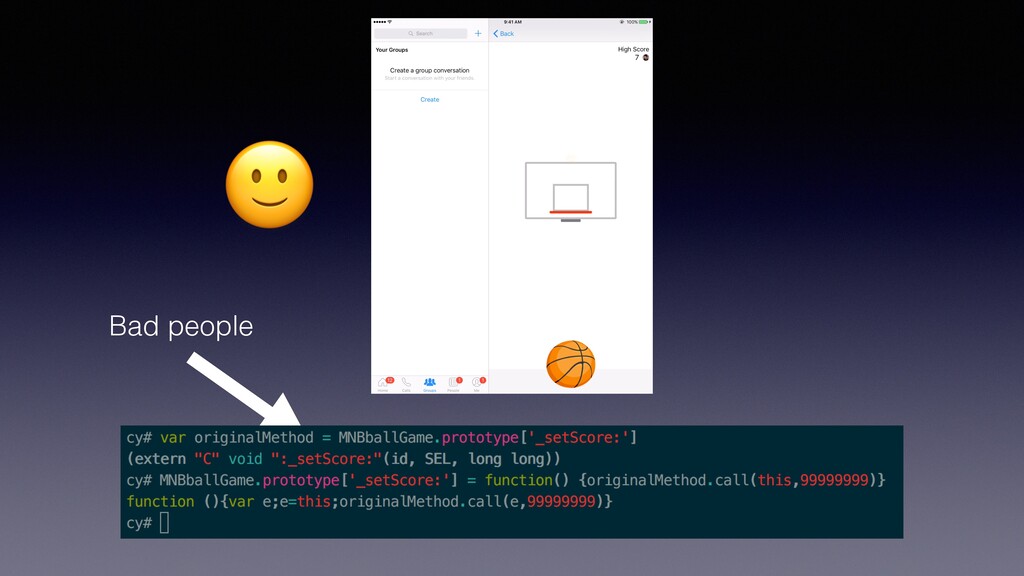
Bad people
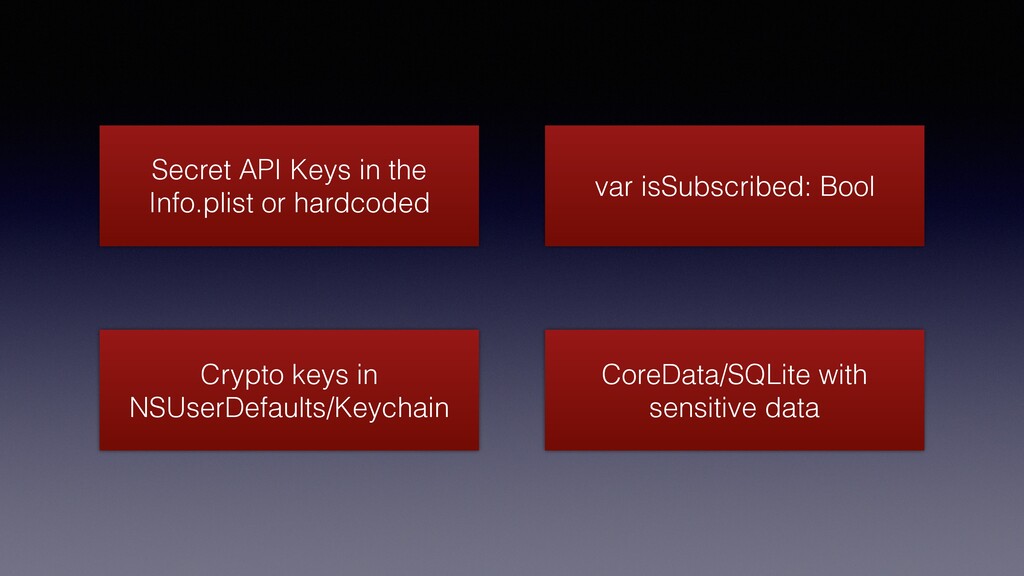
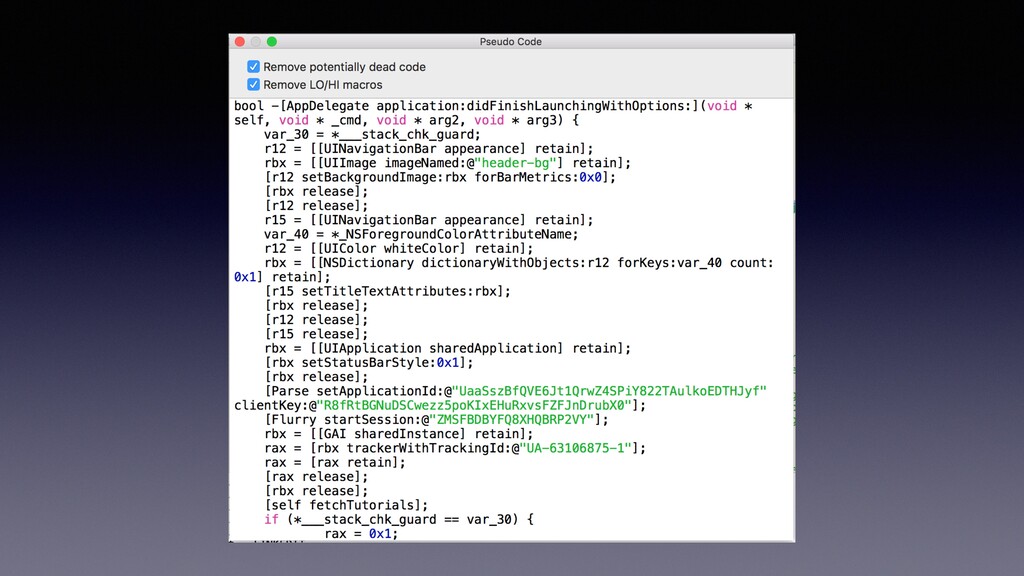
Crypto keys in NSUserDefaults/Keychain Secret API Keys in the Info.plist
or hardcoded CoreData/SQLite with sensitive data var isSubscribed: Bool
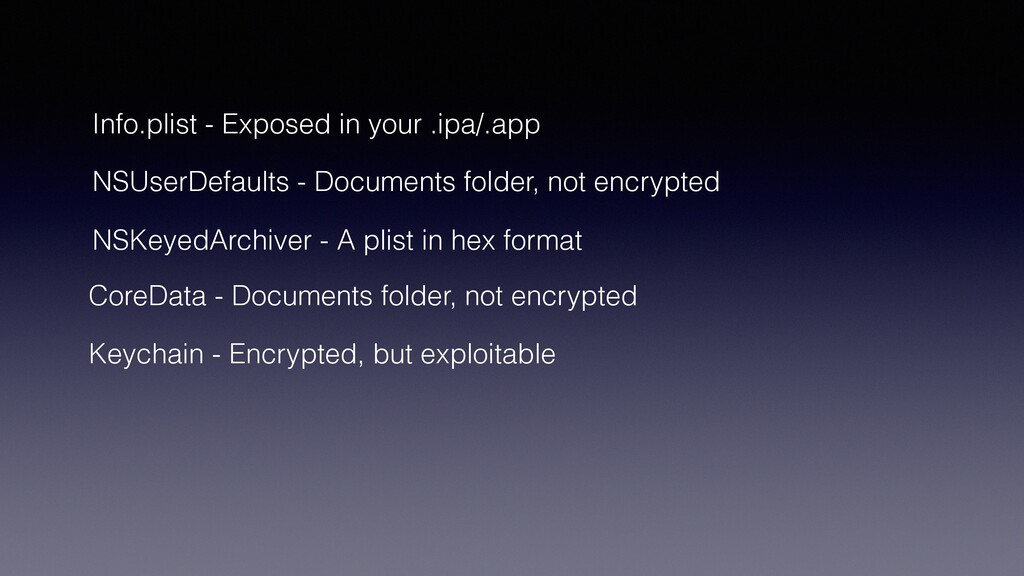
NSUserDefaults - Documents folder, not encrypted CoreData - Documents folder,
not encrypted Info.plist - Exposed in your .ipa/.app Keychain - Encrypted, but exploitable NSKeyedArchiver - A plist in hex format
None
None
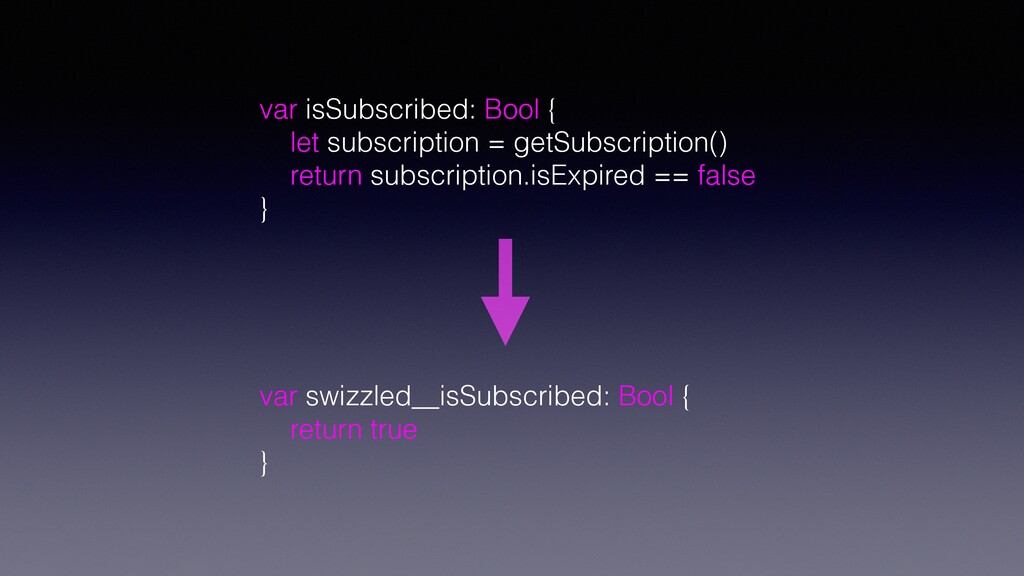
var isSubscribed: Bool { let subscription = getSubscription() return subscription.isExpired
== false } var swizzled__isSubscribed: Bool { return true }
None
Demo 1: Insecure Data Storages
Protecting apps from Storage Attacks • Encrypt/Encode data before saving/
hardcoding (Careful! This will not prevent attacks, only slow them down.) • Treat critical data (like secret API keys) server-side if possible • Open Source “String obfuscation" libs: Hackers have Google too.
Demo 2: Runtime Manipulation
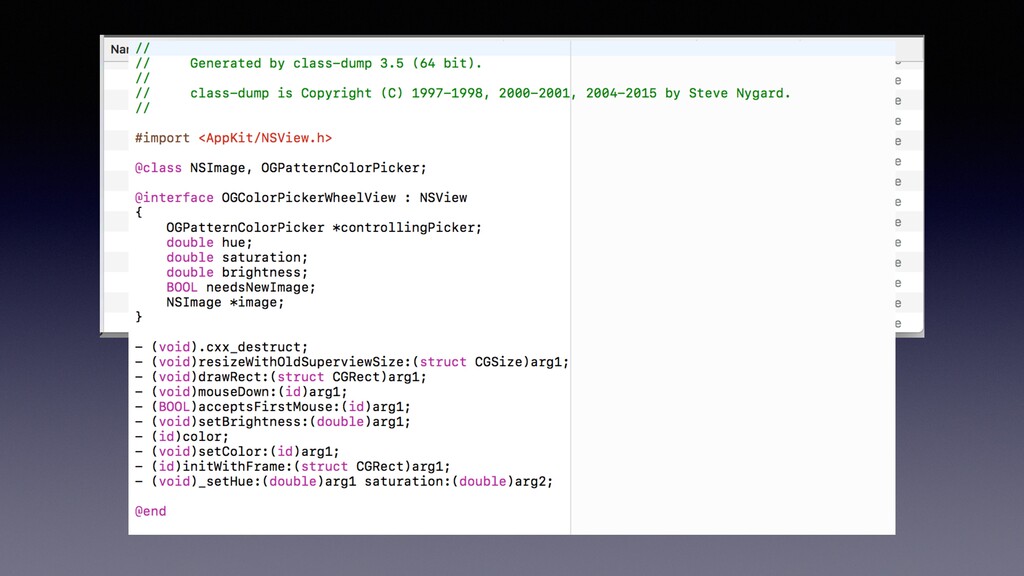
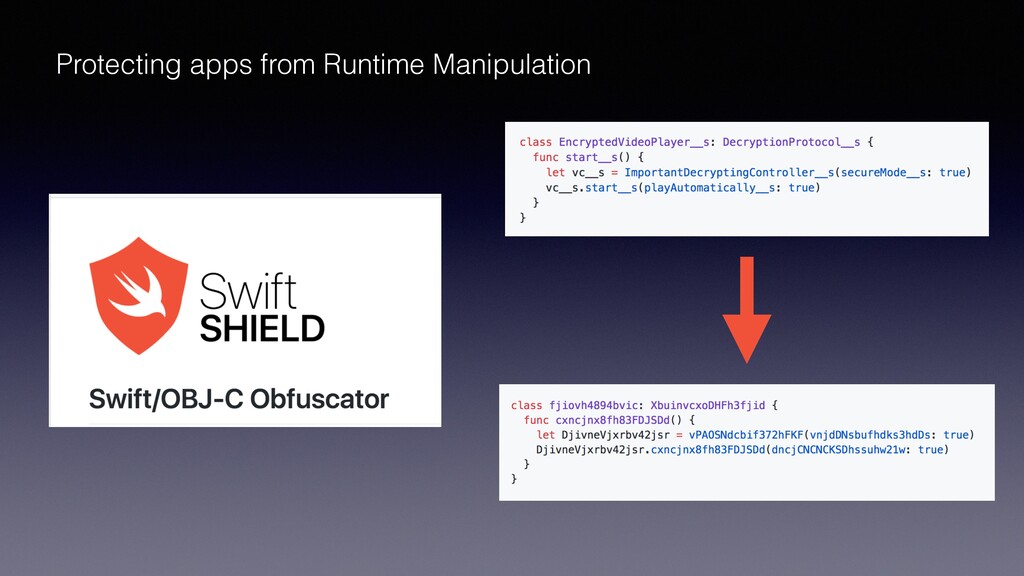
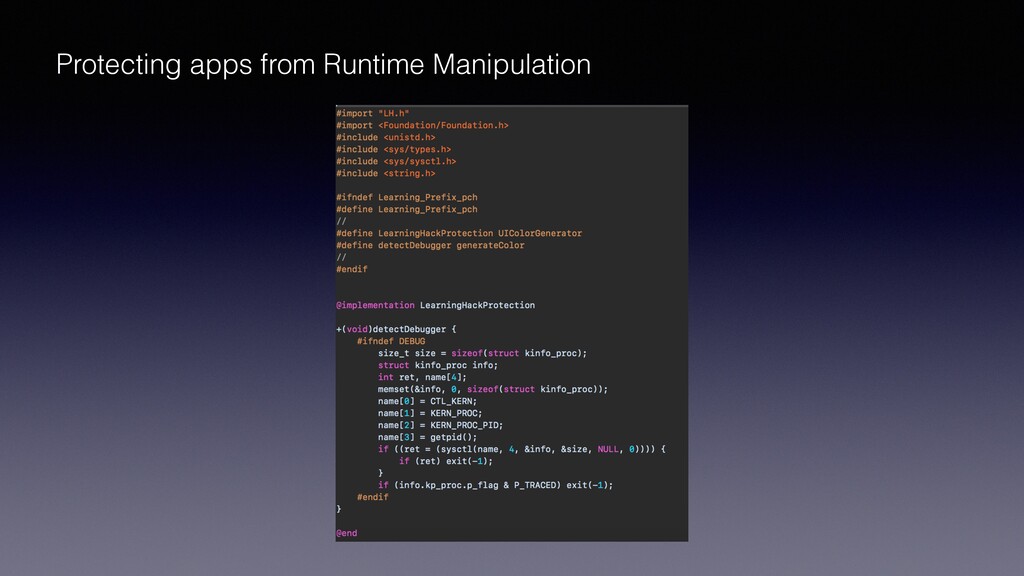
Protecting apps from Runtime Manipulation Important logic should be treated/
checked server-side! (eg: API Tokens)
Protecting apps from Runtime Manipulation
Protecting apps from Runtime Manipulation
What about the real world?


 rockbruno
 bitkey
 codatum
 kash1064
 bgpat
 takonda
 ymotongpoo
 odashi
 kenichiodo
 glaforge
 sansantech
 kzkhykw1991
 teamlab
 cromwellryan
 chriscoyier
 sachag
 sergeychernyshev
 codingconduct
 paigeccino
 ryanjones
 bkeepers
 palkan
 hatefulcrawdad
 aleyda
 letsgokoyo