Upgrade to Pro
— share decks privately, control downloads, hide ads and more …
Speaker Deck
Sign up for free
Menu
Search
Features
All features
Private URLs
Password Protection
Custom URLS
Scheduled publishing
Remove Branding
Restrict embedding
Deck Collections
Notes
Features
All features
Private URLs
Password Protection
Custom URLS
Scheduled publishing
Remove Branding
Restrict embedding
Deck Collections
Notes
Explore
Featured decks
Featured speakers
Programming
Technology
Storyboards
Explore
Featured decks
Featured speakers
Programming
Technology
Storyboards
Pricing
Search
Sign in
Sign up for free
Securing Single Page Applications
Search
Zakiullah Khan
December 07, 2014
Programming
390
2
Share
Embed
Copy iframe code
Copy JS code
Copy link
Start on current slide
Securing Single Page Applications
Slide deck used for recent presentation at Hydeabad's AngularJS User Group meetup.
Zakiullah Khan
December 07, 2014
More Decks by Zakiullah Khan
See All by Zakiullah Khan
Project Manager v/s Program Manager
simplyzaki
0
310
Distributed Messaging with ZeroMQ
simplyzaki
1
330
Designing Big Data Solutions Using AWS
simplyzaki
1
510
Other Decks in Programming
See All in Programming
dotNET_vulnclicker_intro.pdf
deka_morita
0
140
ソニーのクラウド共通基盤の変遷と AI時代の開発スタイルに合わせた進化 / The Journey of Sony’s Common Cloud Platform and Its Evolution for AI-Native Development
kenjiyoneyama
0
270
Next.js: The final boss of Web Performance
guaca
0
260
TechTown - Creating Composable Callables in Contemporary C++
rollbear
0
130
RAG の “R” を Swift で覗いてみる 〜「意味から探す」検索の仕組み〜
nao_randd
0
160
Railsのためのパスキー実践入門 〜マルチテナントSaaSでの意思決定〜
utakaha
2
600
PumaからFalconに移行したRailsアプリケーションでの実践
falcon8823
0
170
Event is what happens
moro
2
810
Kotlinの15年とServer-Side Kotlin
n_takehata
1
150
當我們開始不讀 Code - AI Agent 時代,Code Review 與 Clean Code 還剩下什麼?
jame2408
1
230
AI主導のプログラミング学習アプリを作ってみた
econanringo
0
180
カツオ、ご期待ください
suneo3476
0
190
Featured
See All Featured
ラッコキーワード サービス紹介資料
rakko
1
5.4M
So, you think you're a good person
axbom
PRO
2
2.2k
VelocityConf: Rendering Performance Case Studies
addyosmani
331
25k
How to audit for AI Accessibility on your Front & Back End
davetheseo
0
600
A Modern Web Designer's Workflow
chriscoyier
699
190k
The SEO identity crisis: Don't let AI make you average
varn
0
590
A Tale of Four Properties
chriscoyier
163
24k
Distributed Sagas: A Protocol for Coordinating Microservices
caitiem20
333
23k
Learning to Love Humans: Emotional Interface Design
aarron
275
41k
No one is an island. Learnings from fostering a developers community.
thoeni
21
3.9k
SERP Conf. Vienna - Web Accessibility: Optimizing for Inclusivity and SEO
sarafernandez
2
1.6k
Bash Introduction
62gerente
615
220k
Transcript
Securing Single Page Applications By Zakiullah Khan Mohammed @khan_io
Disclaimer I’m not a Security Expert.
#ngHYD Twitter Hash Tag
About Me Technical Manager @ Fission Labs http://www.khanio.com
Agenda AppSec - OWASP - JWT
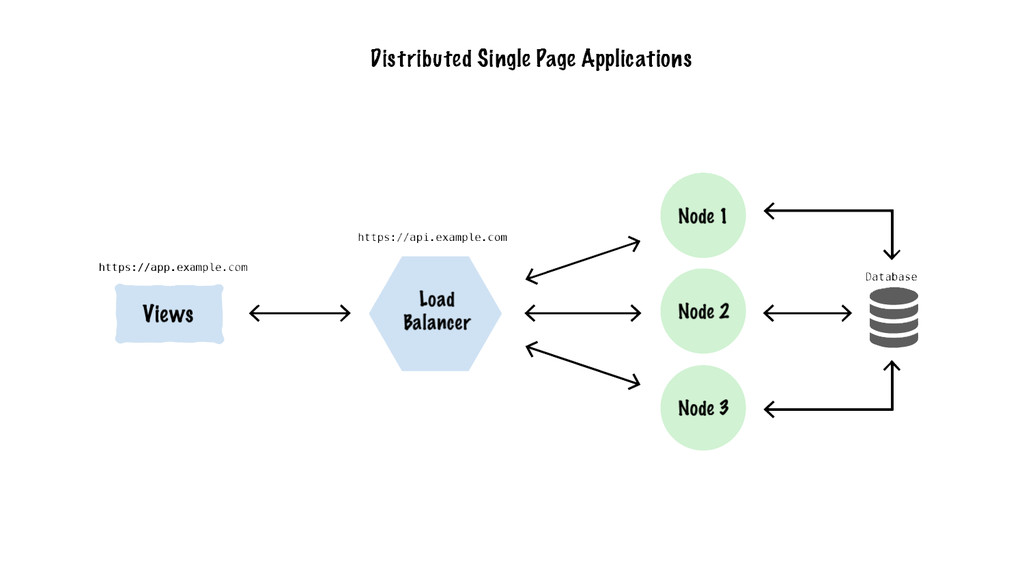
Single Page Applications (SPAs) Currently trending ...
None
None
Application Security Who knows it all in your team ?
OWASP Open Web Application Security Project
OWASP Online community dedicated to web application security
OWASP Identify Vulnerabilities Recommend Solutions Document Best Practices
OWASP 2013 Top 10 http://j.mp/OWASP-2013-Top10
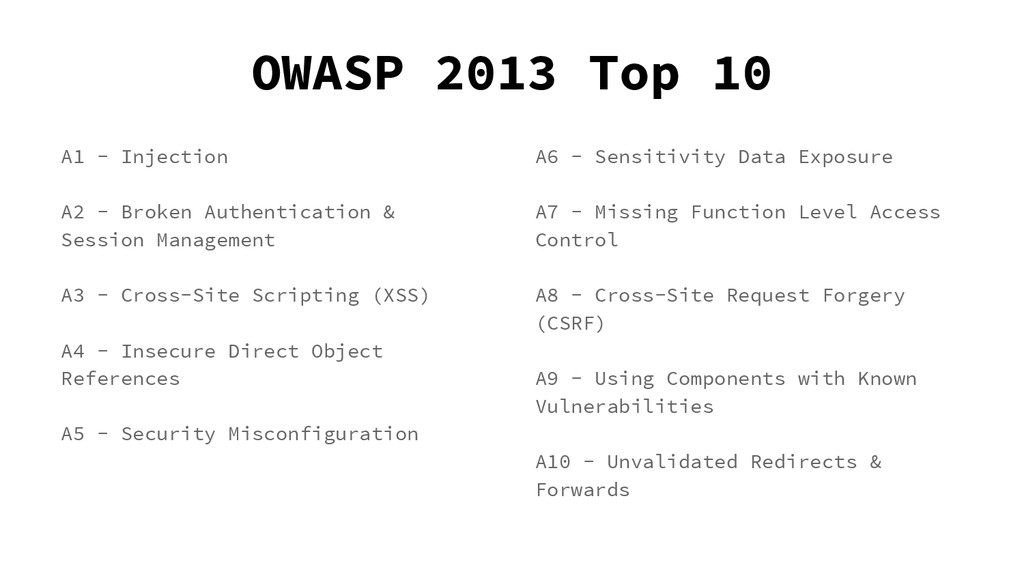
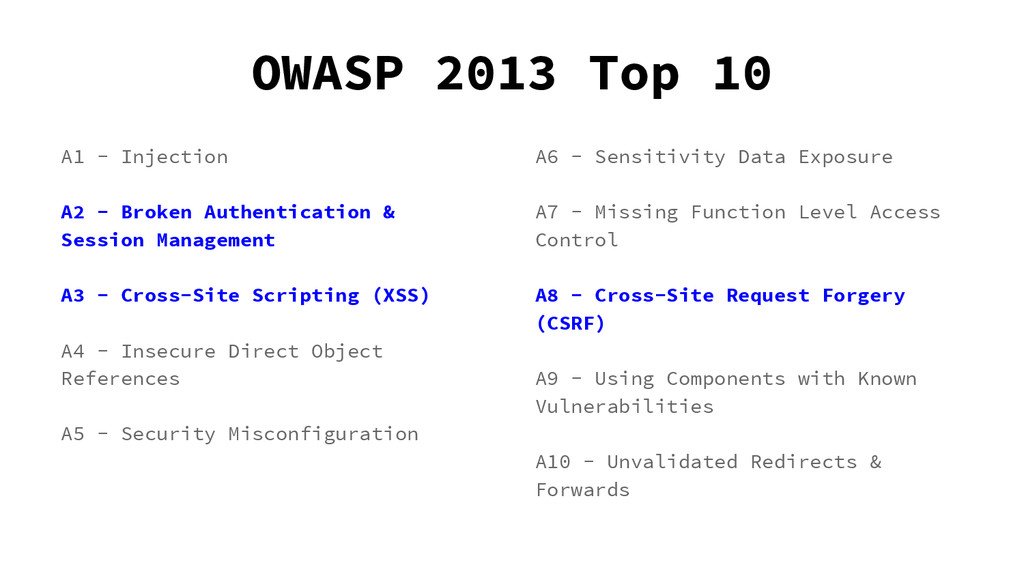
OWASP 2013 Top 10 A1 - Injection A2 - Broken
Authentication & Session Management A3 - Cross-Site Scripting (XSS) A4 - Insecure Direct Object References A5 - Security Misconfiguration A6 - Sensitivity Data Exposure A7 - Missing Function Level Access Control A8 - Cross-Site Request Forgery (CSRF) A9 - Using Components with Known Vulnerabilities A10 - Unvalidated Redirects & Forwards
A2 Broken Authentication and Session management Credentials - Session -
Browser Caching - Trust
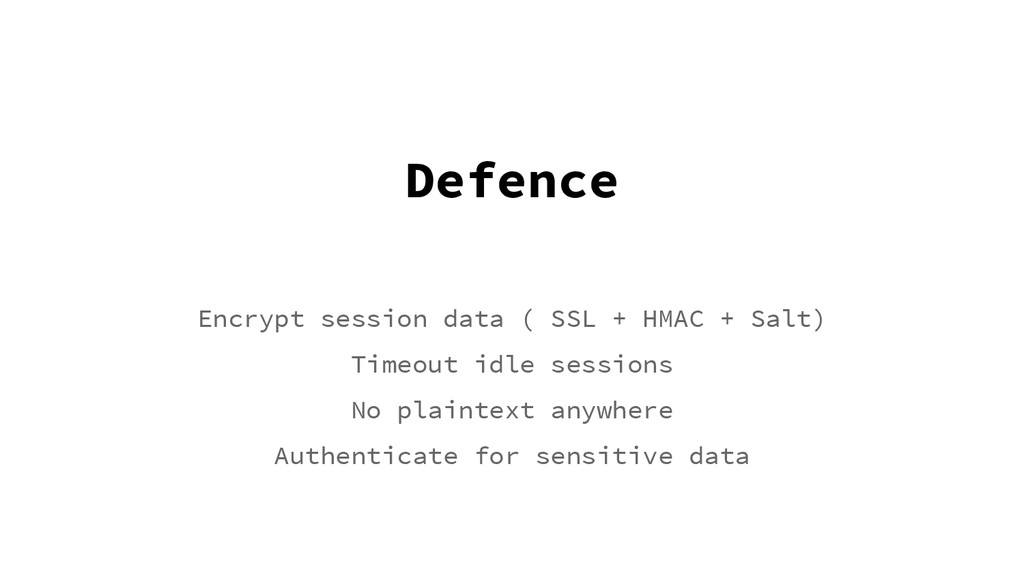
Defence Encrypt session data ( SSL + HMAC + Salt)
Timeout idle sessions No plaintext anywhere Authenticate for sensitive data
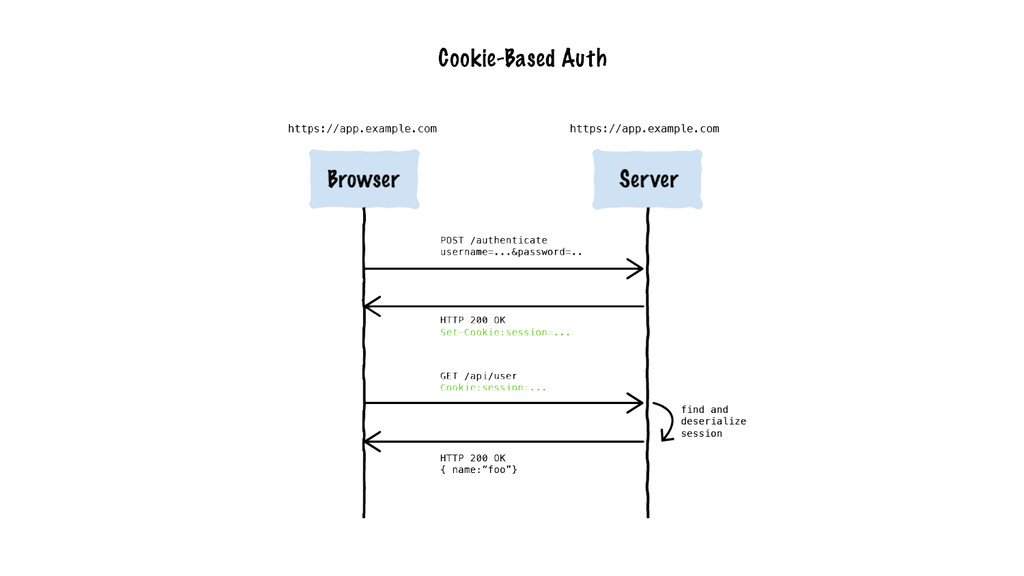
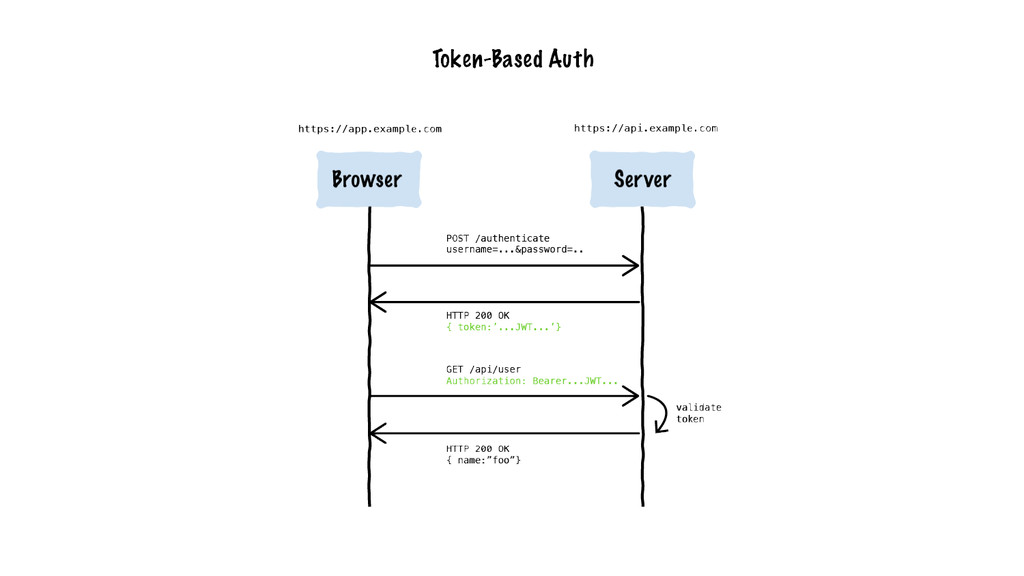
Cookie vs Token Does it matter ?
None
None
None
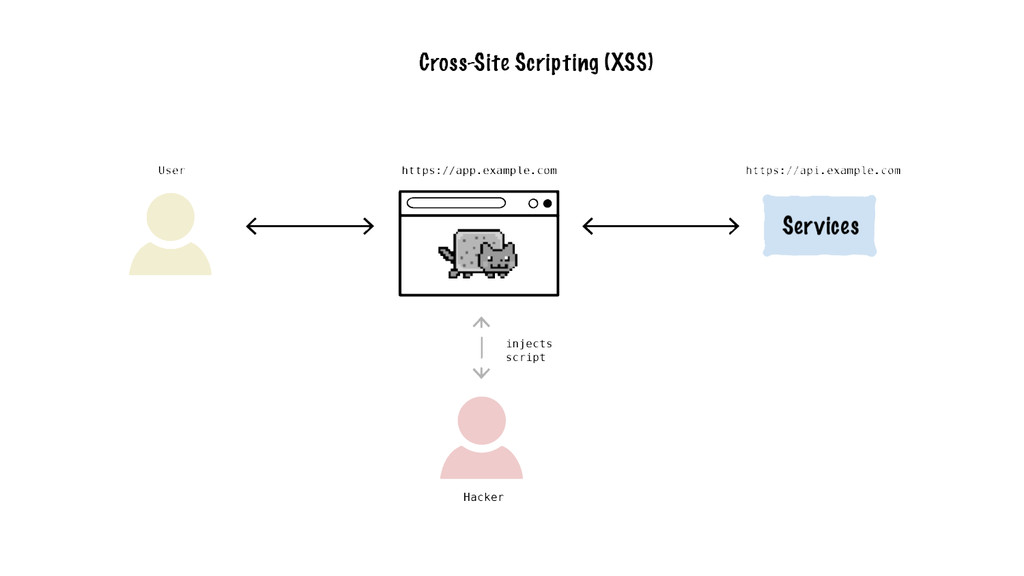
A3 Cross-Site Scripting (XSS) Malicious content delivered to user using
Javascript
None
Defence Always validate user input Escape out URLs, JS data
and Error pages Rely on program data, not user data
Content Security Policy Whitelisting sources within browser
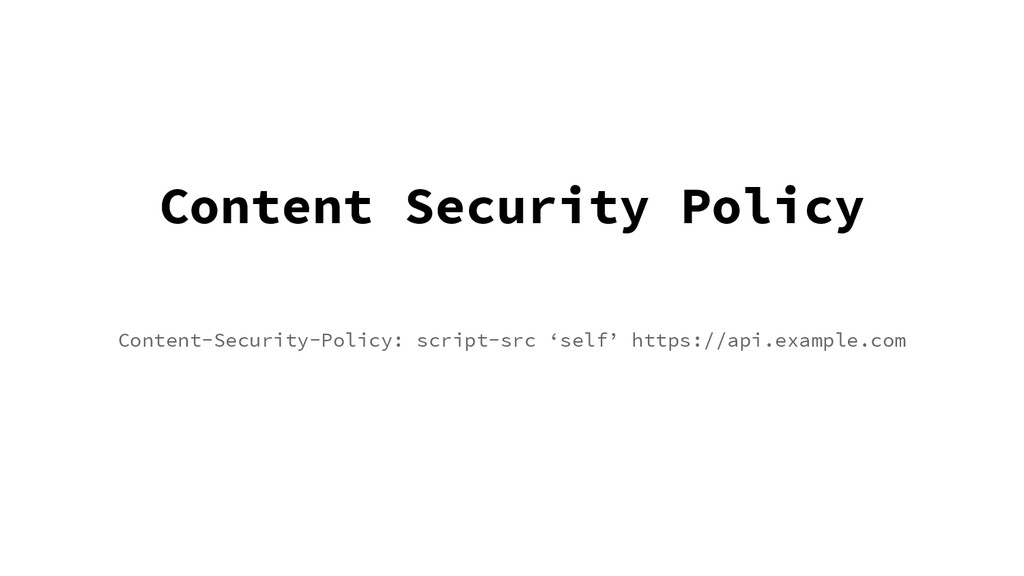
Content Security Policy Content-Security-Policy: script-src ‘self’ https://api.example.com
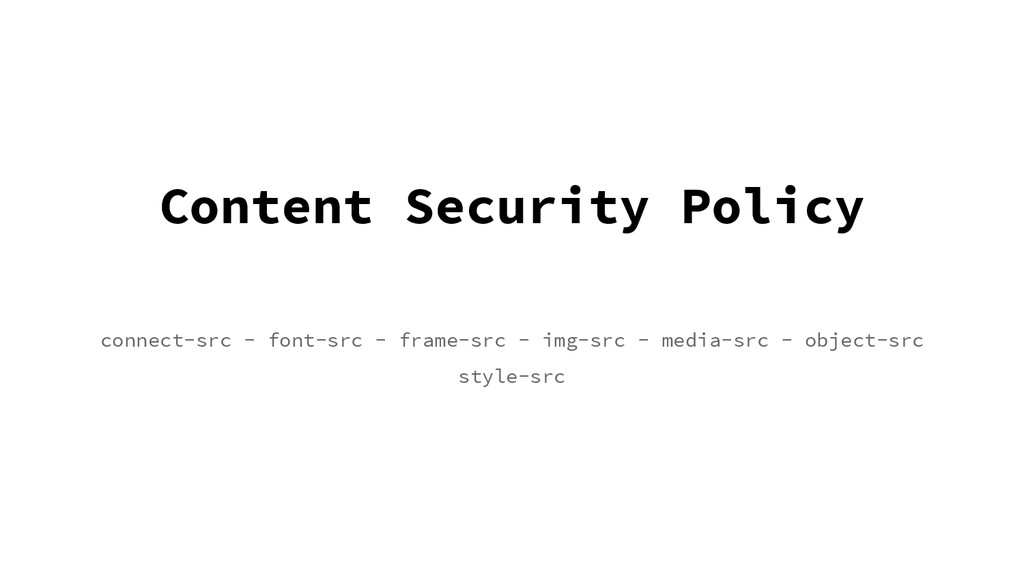
Content Security Policy connect-src - font-src - frame-src - img-src
- media-src - object-src style-src
ngCSP Content Security Policy within AngularJS
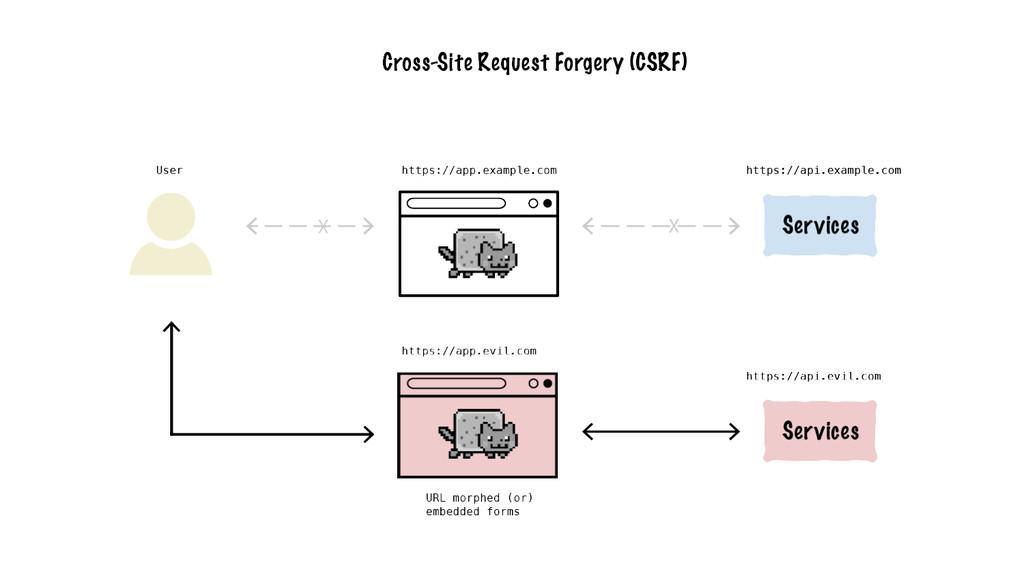
A8 Cross-Site Request Forgery (XSRF) Tricks user in submitting data
to evil endpoint
None
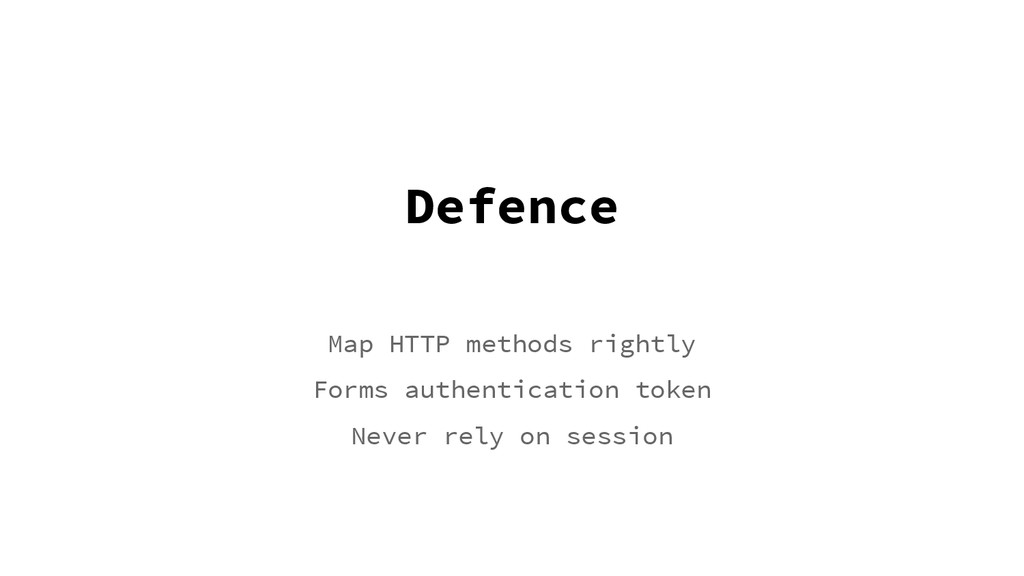
Defence Map HTTP methods rightly Forms authentication token Never rely
on session
$http XSRF protection within AngularJS using X-XSRF-TOKEN
How to fix all three ? Let’s talk about JWT
JSON Web Token (JWT) Pronounced as JOT
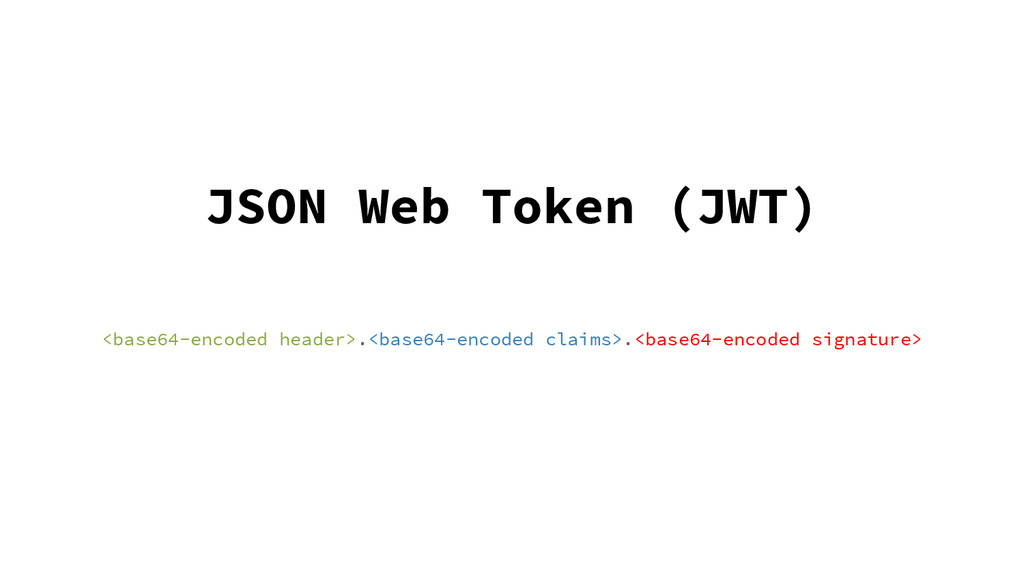
JSON Web Token (JWT) Compact URL-safe means of representing claims
to be transferred between two parties. The claims in JWT are encoded as JSON object that is digitally signed using JWS.
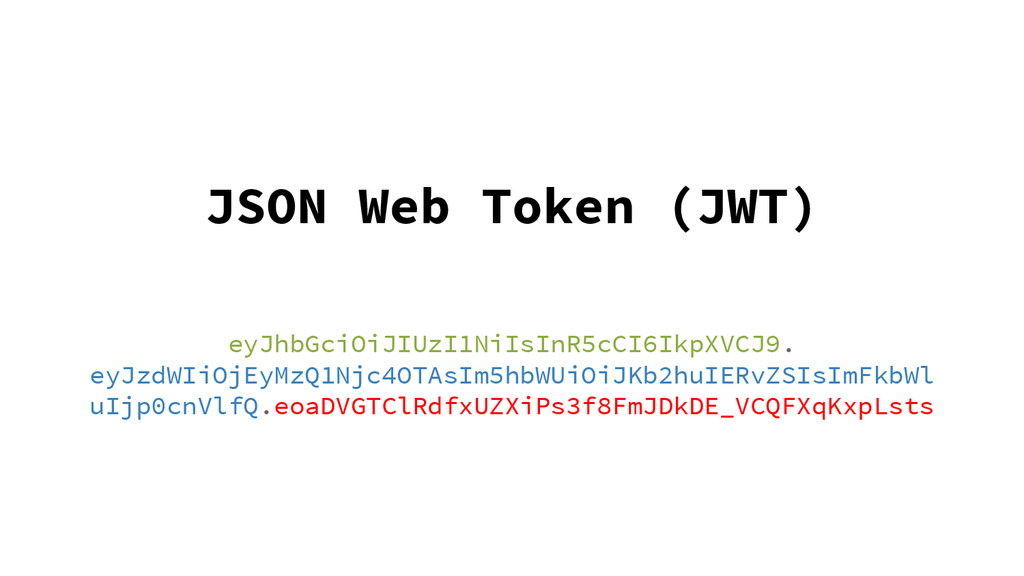
JSON Web Token (JWT) eyJhbGciOiJIUzI1NiIsInR5cCI6IkpXVCJ9. eyJzdWIiOjEyMzQ1Njc4OTAsIm5hbWUiOiJKb2huIERvZSIsImFkbWl uIjp0cnVlfQ.eoaDVGTClRdfxUZXiPs3f8FmJDkDE_VCQFXqKxpLsts
JSON Web Token (JWT) <base64-encoded header>.<base64-encoded claims>.<base64-encoded signature>
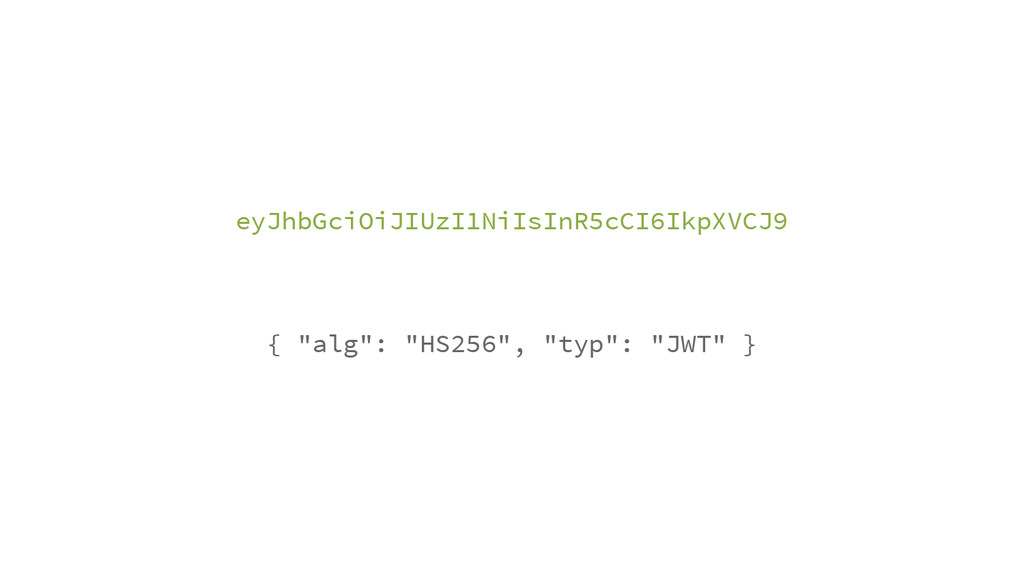
eyJhbGciOiJIUzI1NiIsInR5cCI6IkpXVCJ9 { "alg": "HS256", "typ": "JWT" }
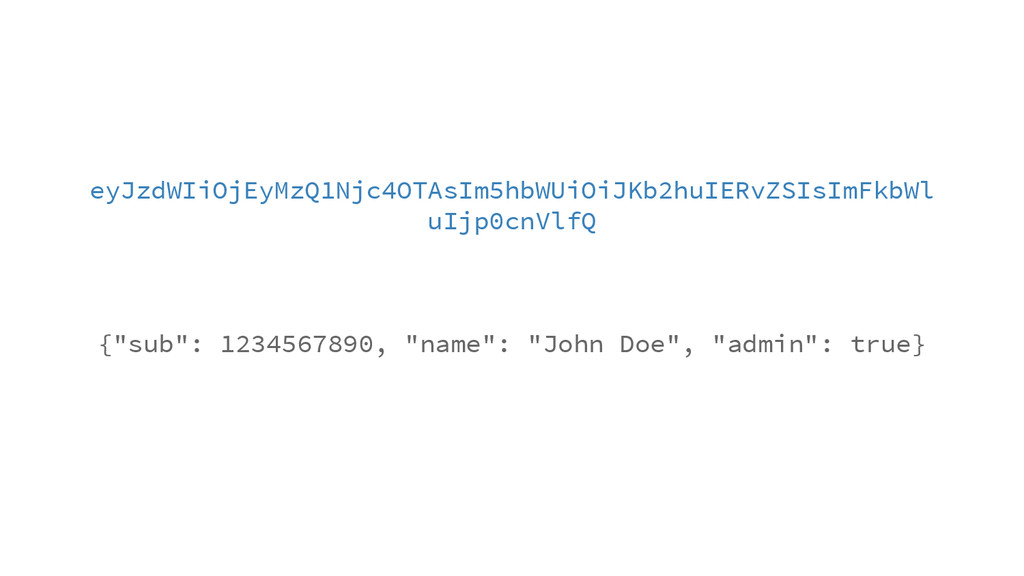
eyJzdWIiOjEyMzQ1Njc4OTAsIm5hbWUiOiJKb2huIERvZSIsImFkbWl uIjp0cnVlfQ {"sub": 1234567890, "name": "John Doe", "admin": true}
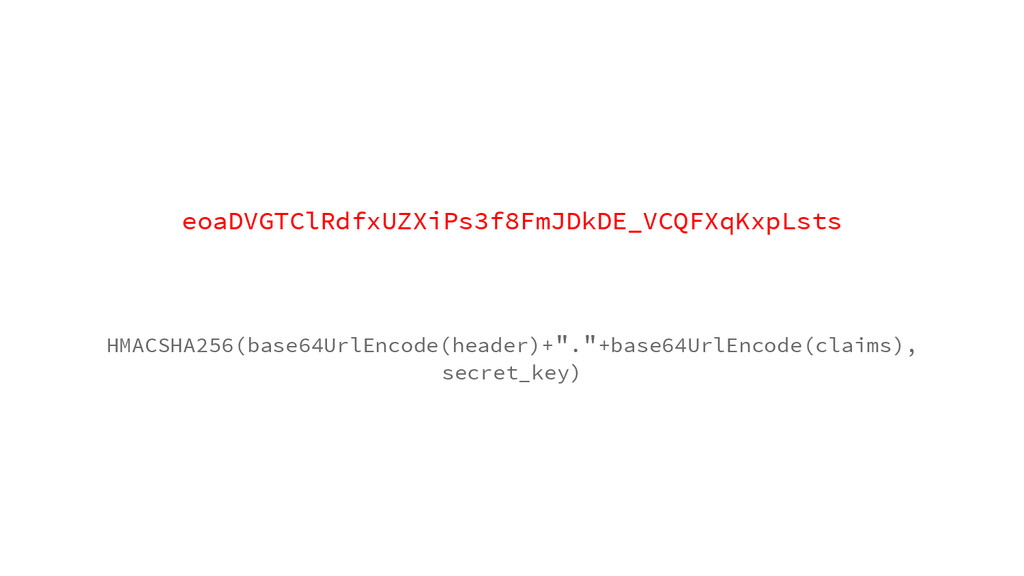
eoaDVGTClRdfxUZXiPs3f8FmJDkDE_VCQFXqKxpLsts HMACSHA256(base64UrlEncode(header)+"."+base64UrlEncode(claims), secret_key)
JSON Web Token (JWT) NO CSRF - NO XSS
angular-jwt https://github.com/auth0/angular-jwt
Thank You Q&A


 simplyzaki
 deka_morita
 kenjiyoneyama
 guaca
 rollbear
 nao_randd
 utakaha
 falcon8823
 moro
 n_takehata
 jame2408
 econanringo
 suneo3476
 rakko
 axbom
 addyosmani
 davetheseo
 chriscoyier
 varn
 caitiem20
 aarron
 thoeni
 sarafernandez
 62gerente