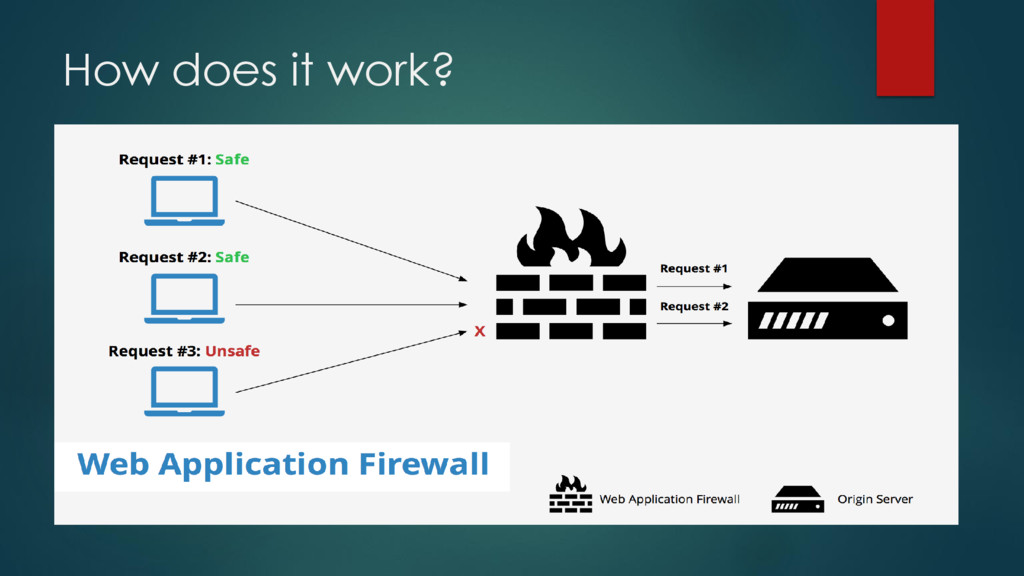
(WAF) is a firewall that monitors, filters or blocks the HTTP traffic to and from a Web application. A WAF protects a Web application by controlling its input and output and the access to and from the application. Running as an appliance, server plug-in or cloud-based service, a WAF inspects every HTML, HTTPS, SOAP and XML-RPC data packet. Through customizable inspection, it is able to prevent attacks such as XSS, SQL injection, session hijacking and buffer overflows, which network firewalls and intrusion detection systems are often not capable of doing. A WAF is also able to detect and prevent new unknown attacks by watching for unfamiliar patterns in the traffic data.
WAF’s is “Appliance Based Firewalls”. The appliance is physically deployed in between the Web application Appliance Based Firewalls and the clients accessing it. WAF’s such as F5 BIG IP ASM, Palo Alto, Imperva secure sphere etc are some of well-known Appliance Based WAF’s. The advantage of this WAF is that it offers a greater level of control over the availability. The downside of this particular approach is that they are pretty expensive and require necessary changes to the network infrastructure.
as reverse proxy between the Client and the Web application. Cloud Based WAF’s as compared to Appliance Based Firewalls are easy to deploy as they only require the DNS servers to point to the WAF provider’s Cloud. Any traffic sent to the application is first sent to the WAF’s name servers so that the traffic is passed through WAF’s cloud where it is checked against WAF’s database. The advantage of Cloud Based WAF’s is that it does not require any changes to network infrastructure. The downside is that if Cloud provider’s servers go down, so do the web applications behind it.
is an integrated WAF, an integrated WAF is hosted upon the application server itself or it might be present in the application code itself. ModSecurity is an idle example of integrated WAF’s. ModSecurity is an Apache server’s module. Another, example of an integrated WAF is “Ninja Firewall” which is based upon.htaccess rule sets. These WAF’s are ideal as they don’t require a network infrastructure change as well as DNS redirection.
firewalls and intrusion prevention systems don't provide sufficient protections for Internet-facing websites, internal business- critical applications and Web Services. WAFs are most often the only control that is able to inspect encrypted and unencrypted inbound Web traffic at the application layer (Layer 7). Web Application Firewall can detect common vulnerabilities on Web App such as SQLi, XSS, CSRF,RCE, LFI, Buffer Overflow and more(TOP 10 OWASP).
distinct aspects that make web application security such a challenge: The organization’s network infrastructure provides access to the web application, by default, it exposes all potential vulnerabilities to attack including web forms, input fields, logical web vulnerabilities and more. The only realistic solution is to work towards the elimination of all vulnerabilities and prevent exploit. The second problem is that from a network perspective it is very difficult to differentiate hackers from legitimate traffic, even with the help of a sophisticated firewall security appliance
security. The ideal approach takes into account both networks and web applications. Historically, a greater emphasis has been placed on network security, and this is an approach that has worked well. However, as the trend towards depending more on increasingly complicated web applications and improved access to information continues, it has become critically important to manage all aspects of security — reducing overall risk to the greatest extent possible.


 makocchi
 takuroabe
 odashi
 techtekt
 tokuty
 carta_engineering
 yuuuuuuu168
 mohab1
 grimoh
 pfn
 codatum
 jozono
 kneath
 addyosmani
 mfonobong
 csswizardry
 codingconduct
 chriscoyier
 aleyda
 tomoyanonymous
 ianozsvald
 mkilby
 ammeep