Share
Embed
Are Agile Development Methodologies Eroding your Application's Security?
A look at the good and bad of agile from an application and DevSecOps point of view
Tony Rice
October 28, 2019
Transcript
23 slides
-
Are Agile Development Methodologies Eroding your Application's Security? Tony Rice
Cisco InfoSec Photo: Katie Lips -
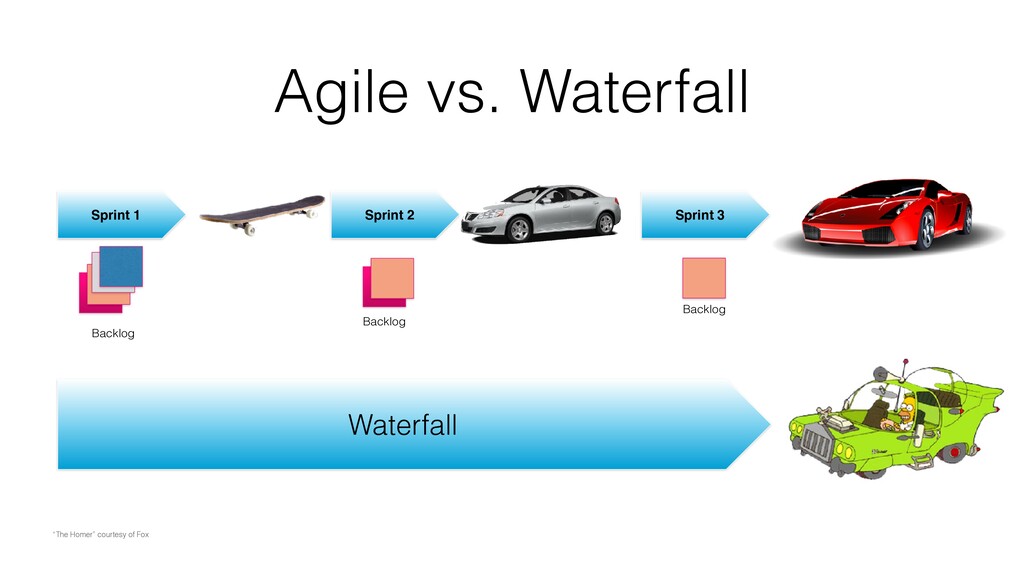
Agile vs. Waterfall “The Homer” courtesy of Fox Sprint 2
Waterfall Sprint 1 Sprint 3 Backlog Backlog Backlog -
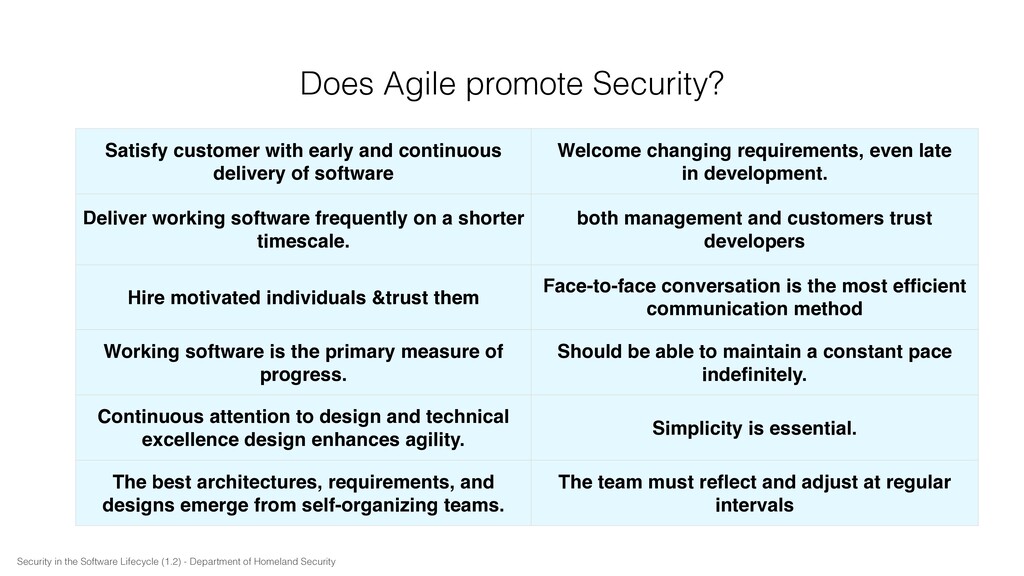
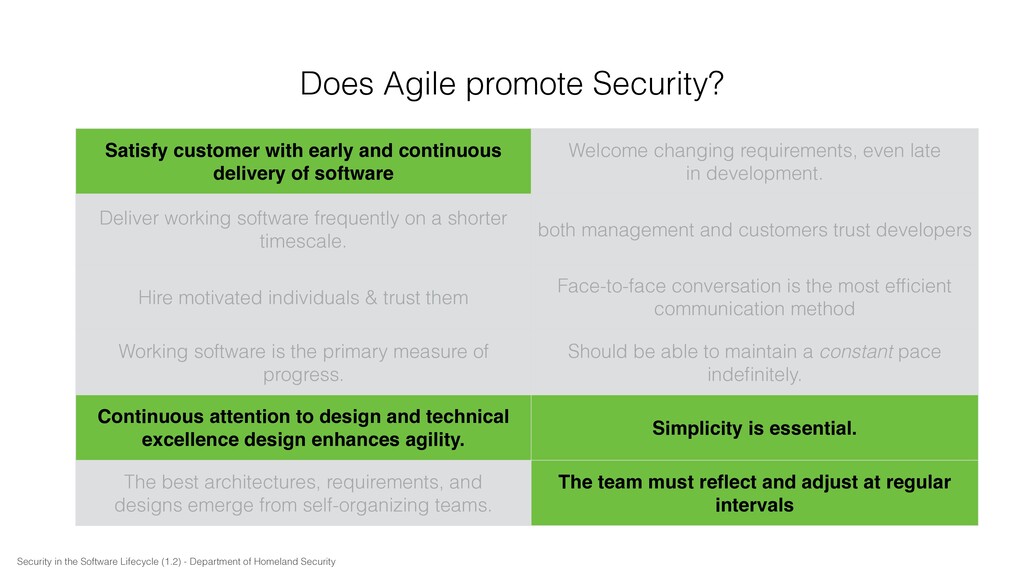
Does Agile promote Security? Security in the Software Lifecycle (1.2)
- Department of Homeland Security Satisfy customer with early and continuous delivery of software Welcome changing requirements, even late in development. Deliver working software frequently on a shorter timescale. both management and customers trust developers Hire motivated individuals &trust them Face-to-face conversation is the most efficient communication method Working software is the primary measure of progress. Should be able to maintain a constant pace indefinitely. Continuous attention to design and technical excellence design enhances agility. Simplicity is essential. The best architectures, requirements, and designs emerge from self-organizing teams. The team must reflect and adjust at regular intervals -
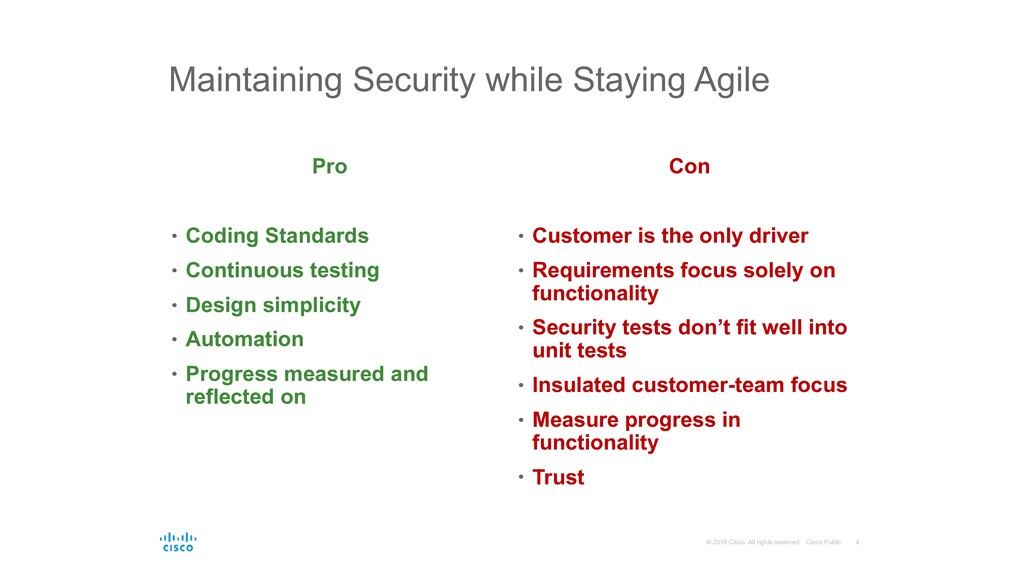
© 2016 Cisco. All rights reserved. Cisco Public 4 Pro
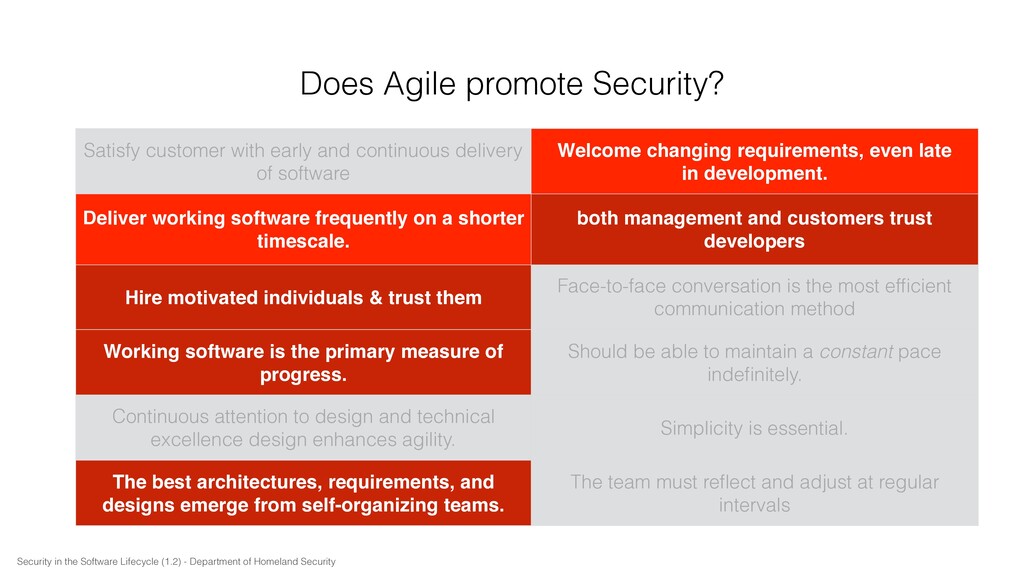
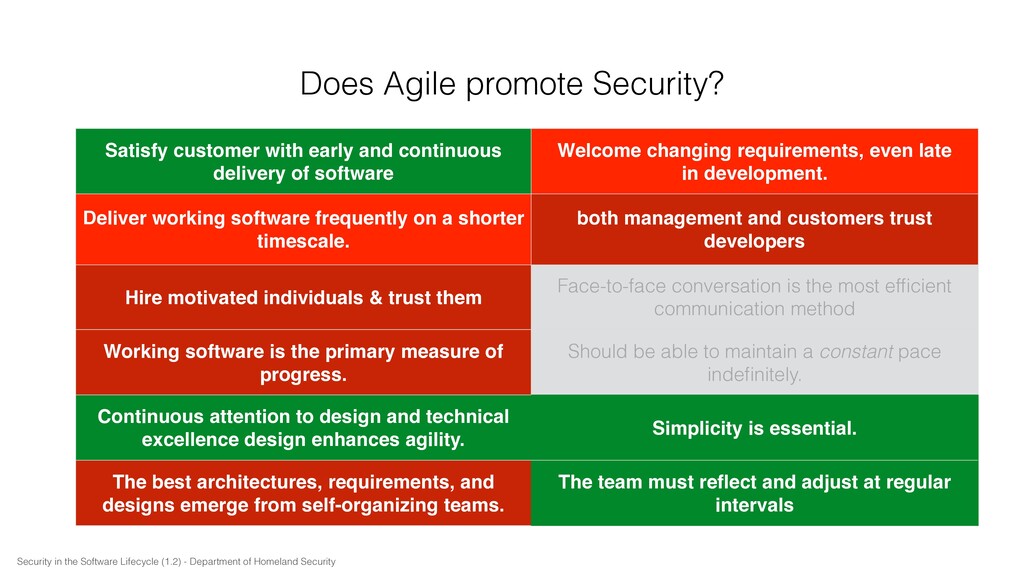
• Coding Standards • Continuous testing • Design simplicity • Automation • Progress measured and reflected on Con • Customer is the only driver • Requirements focus solely on functionality • Security tests don’t fit well into unit tests • Insulated customer-team focus • Measure progress in functionality • Trust Maintaining Security while Staying Agile -
Does Agile promote Security? Security in the Software Lifecycle (1.2)
- Department of Homeland Security Satisfy customer with early and continuous delivery of software Welcome changing requirements, even late in development. Deliver working software frequently on a shorter timescale. both management and customers trust developers Hire motivated individuals & trust them Face-to-face conversation is the most efficient communication method Working software is the primary measure of progress. Should be able to maintain a constant pace indefinitely. Continuous attention to design and technical excellence design enhances agility. Simplicity is essential. The best architectures, requirements, and designs emerge from self-organizing teams. The team must reflect and adjust at regular intervals -
Does Agile promote Security? Security in the Software Lifecycle (1.2)
- Department of Homeland Security Satisfy customer with early and continuous delivery of software Welcome changing requirements, even late in development. Deliver working software frequently on a shorter timescale. both management and customers trust developers Hire motivated individuals & trust them Face-to-face conversation is the most efficient communication method Working software is the primary measure of progress. Should be able to maintain a constant pace indefinitely. Continuous attention to design and technical excellence design enhances agility. Simplicity is essential. The best architectures, requirements, and designs emerge from self-organizing teams. The team must reflect and adjust at regular intervals -
Does Agile promote Security? Security in the Software Lifecycle (1.2)
- Department of Homeland Security Satisfy customer with early and continuous delivery of software Welcome changing requirements, even late in development. Deliver working software frequently on a shorter timescale. both management and customers trust developers Hire motivated individuals & trust them Face-to-face conversation is the most efficient communication method Working software is the primary measure of progress. Should be able to maintain a constant pace indefinitely. Continuous attention to design and technical excellence design enhances agility. Simplicity is essential. The best architectures, requirements, and designs emerge from self-organizing teams. The team must reflect and adjust at regular intervals -
Does Agile promote Security? Security in the Software Lifecycle (1.2)
- Department of Homeland Security Satisfy customer with early and continuous delivery of software Welcome changing requirements, even late in development. Deliver working software frequently on a shorter timescale. both management and customers trust developers Hire motivated individuals & trust them Face-to-face conversation is the most efficient communication method Working software is the primary measure of progress. Should be able to maintain a constant pace indefinitely. Continuous attention to design and technical excellence design enhances agility. Simplicity is essential. The best architectures, requirements, and designs emerge from self-organizing teams. The team must reflect and adjust at regular intervals -
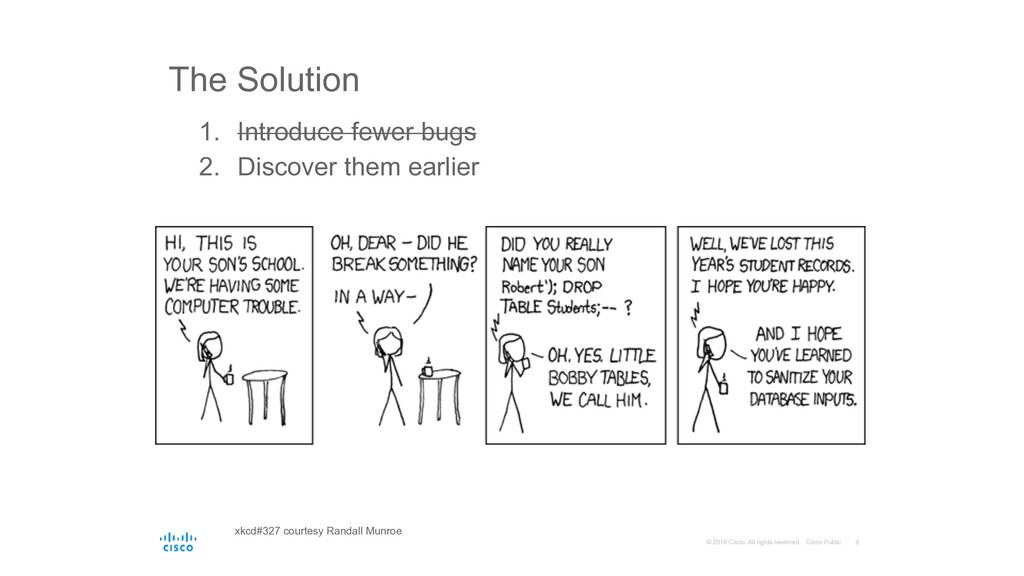
© 2016 Cisco. All rights reserved. Cisco Public 9 The
Solution xkcd#327 courtesy Randall Munroe 1. Introduce fewer bugs 2. Discover them earlier -
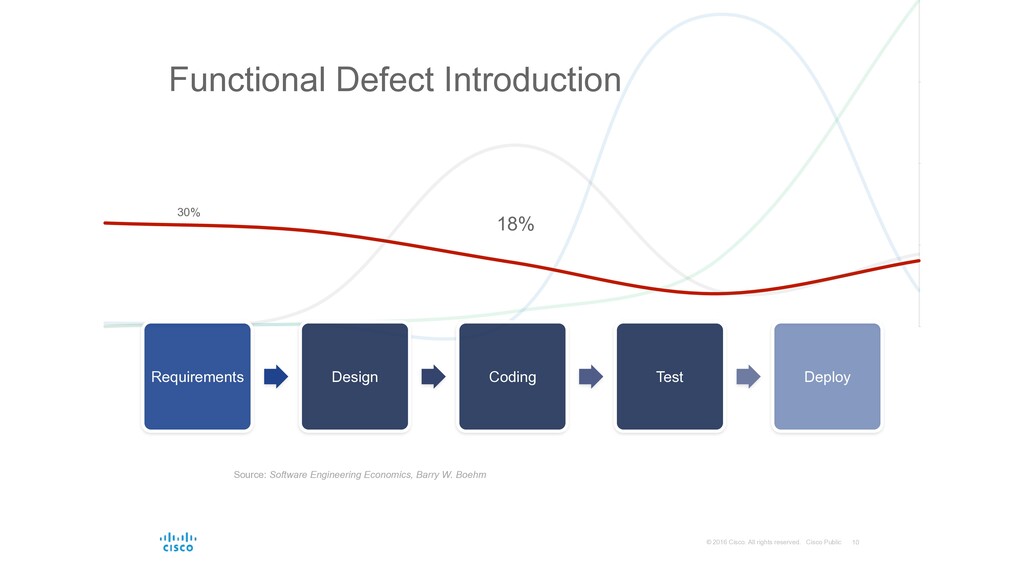
© 2016 Cisco. All rights reserved. Cisco Public 10 Cost
to Fix $1 $100-1000 $15 $30 Source: Software Engineering Economics, Barry W. Boehm 30% 18% Requirements Design Coding Test Deploy Functional Defect Introduction -
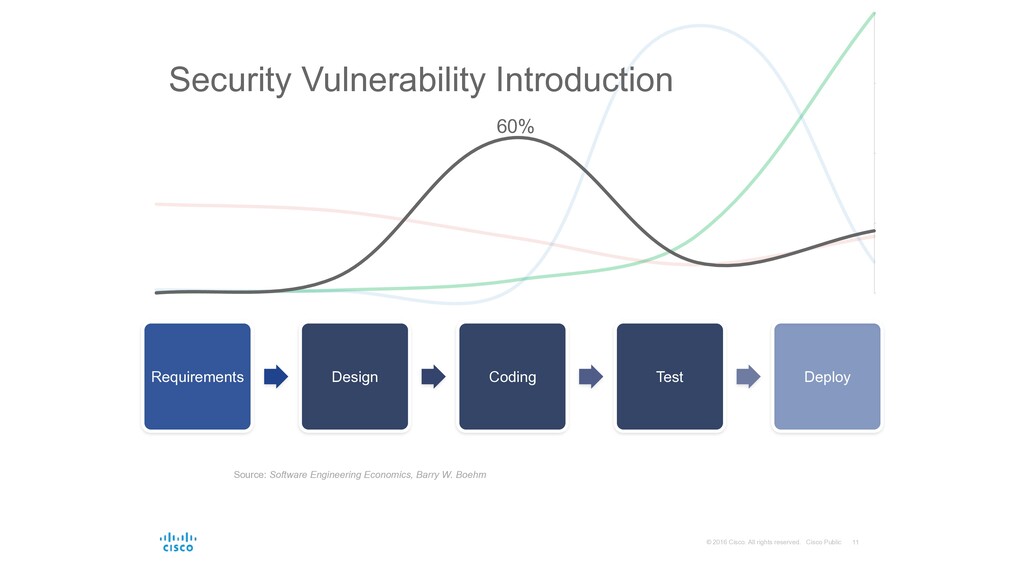
© 2016 Cisco. All rights reserved. Cisco Public Security Vulnerability
Introduction Requirements Design Coding Test Deploy 11 Source: Software Engineering Economics, Barry W. Boehm 60% -
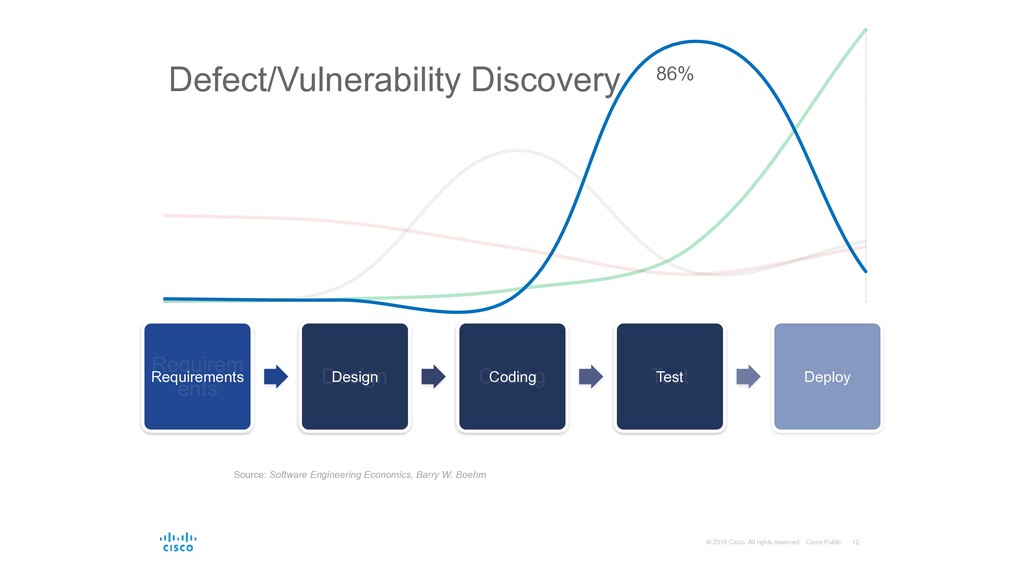
© 2016 Cisco. All rights reserved. Cisco Public 12 Cost
to Fix $1 $100-1000 $15 $30 Source: Software Engineering Economics, Barry W. Boehm 86% Requirem ents Design Coding Test Defect/Vulnerability Discovery Requirements Design Coding Test Deploy -
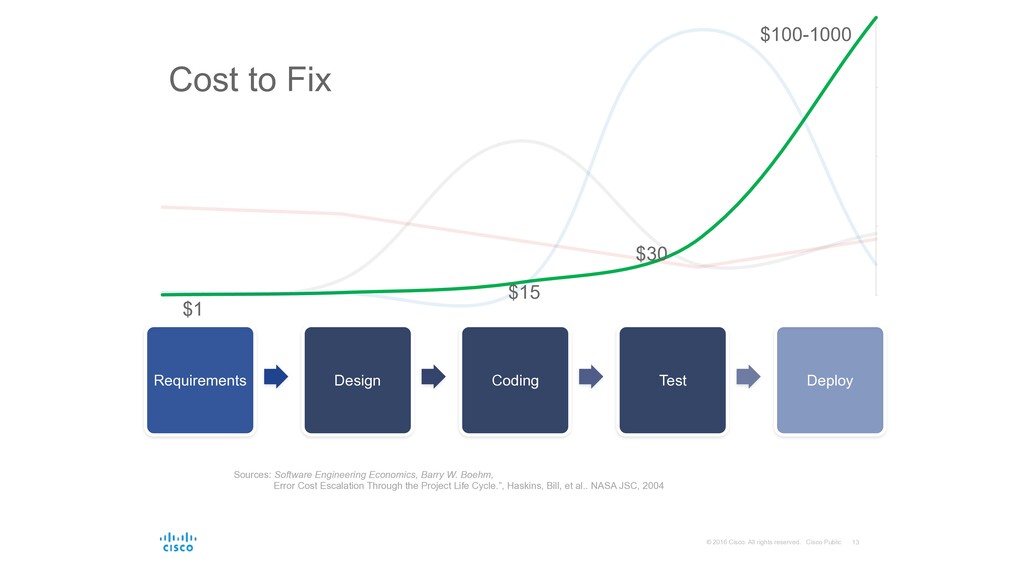
© 2016 Cisco. All rights reserved. Cisco Public Requirements Design
Coding Test Deploy 13 Cost to Fix $1 $100-1000 $15 $30 Sources: Software Engineering Economics, Barry W. Boehm, Error Cost Escalation Through the Project Life Cycle.”, Haskins, Bill, et al.. NASA JSC, 2004 $1 $100-1000 $15 $30 Cost to Fix -
© 2016 Cisco. All rights reserved. Cisco Public 14 Keeping
up with DevOps -
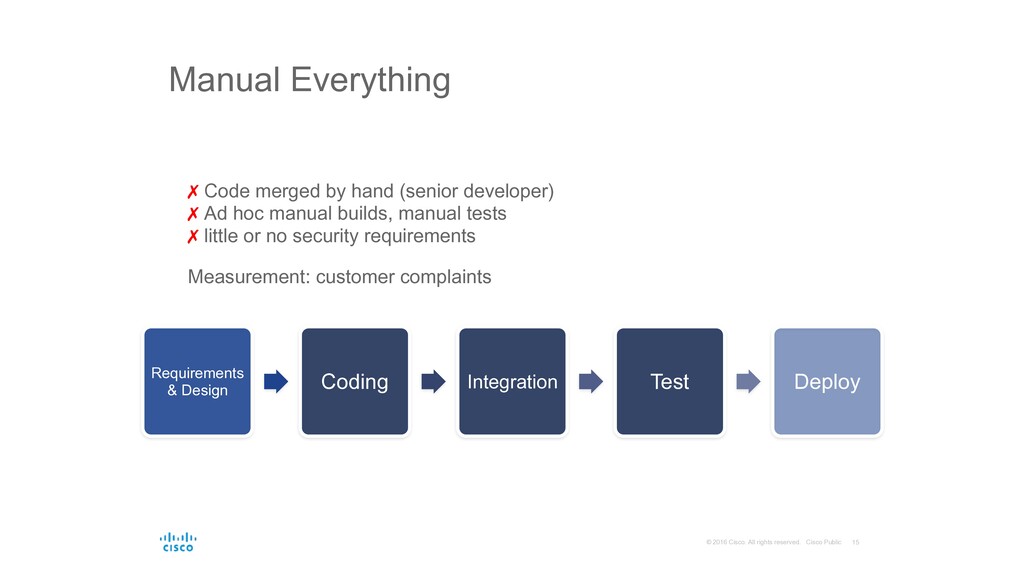
© 2016 Cisco. All rights reserved. Cisco Public 15 Requirements
& Design Coding Integration Test Deploy ✗ Code merged by hand (senior developer) ✗ Ad hoc manual builds, manual tests ✗ little or no security requirements Measurement: customer complaints Manual Everything -
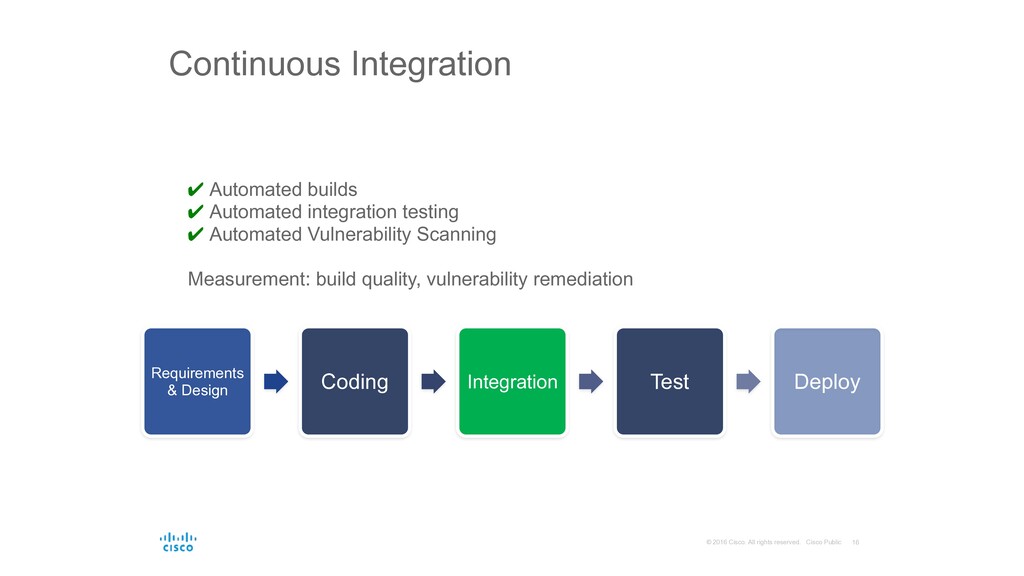
© 2016 Cisco. All rights reserved. Cisco Public 16 Requirements
& Design Coding Integration Test Deploy ✔ Automated builds ✔ Automated integration testing ✔ Automated Vulnerability Scanning Measurement: build quality, vulnerability remediation Continuous Integration -
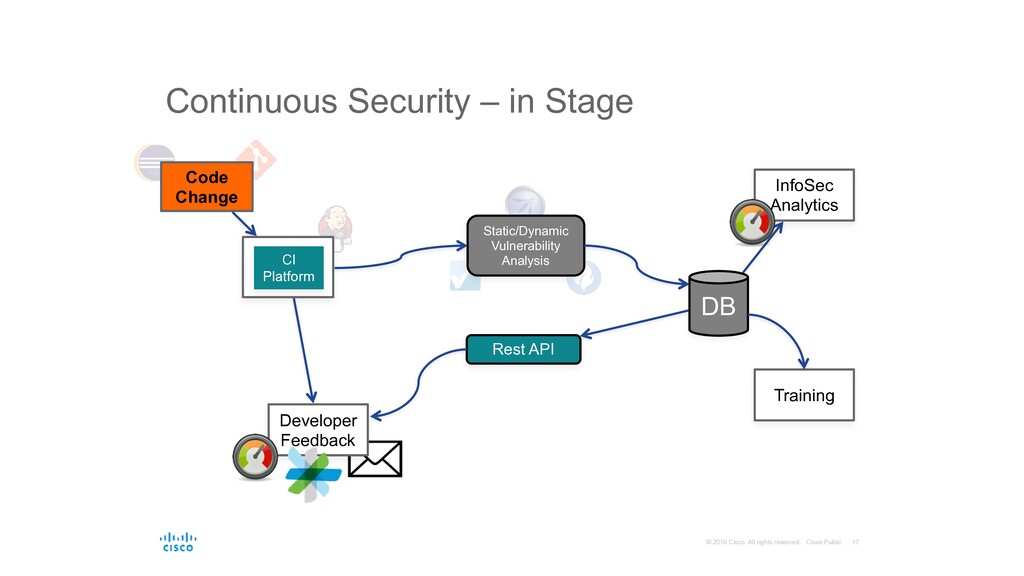
© 2016 Cisco. All rights reserved. Cisco Public 17 CI
Platform CI Platform Static/Dynamic Vulnerability Analysis Rest API Code Change DB Developer Feedback Continuous Security – in Stage InfoSec Analytics Training -
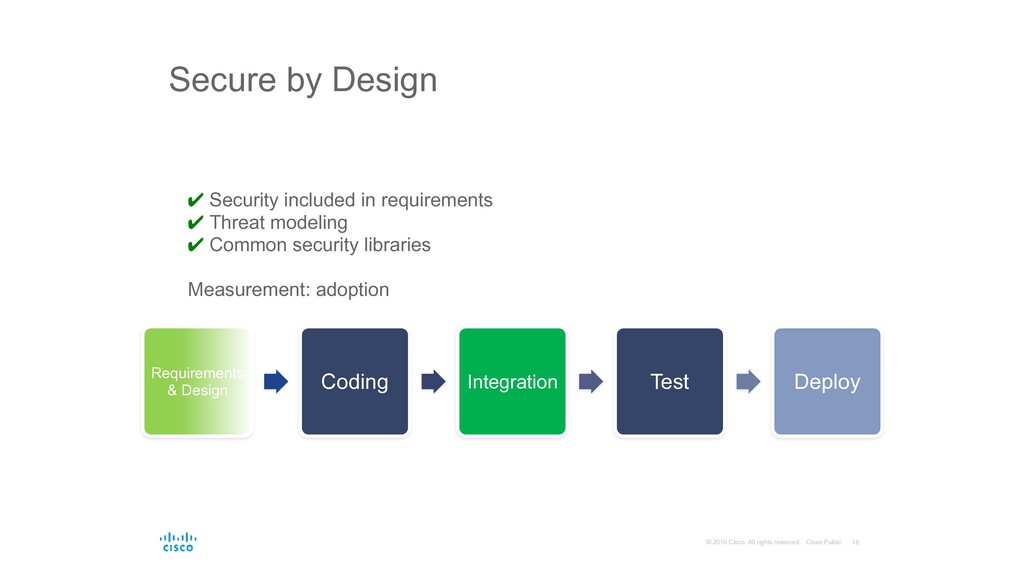
© 2016 Cisco. All rights reserved. Cisco Public 18 Requirements
& Design Coding Integration Test Deploy ✔ Security included in requirements ✔ Threat modeling ✔ Common security libraries Measurement: adoption Secure by Design -
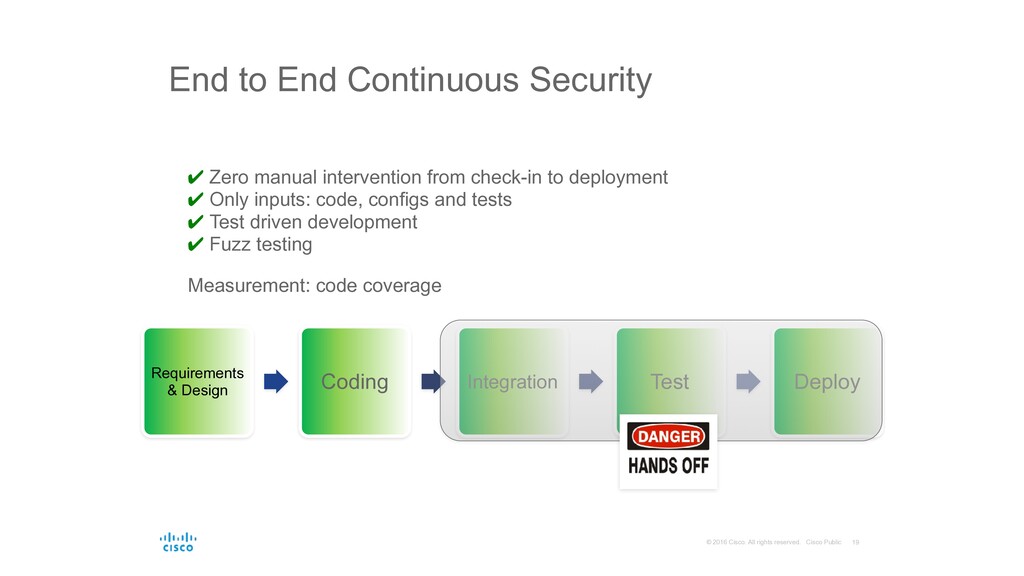
© 2016 Cisco. All rights reserved. Cisco Public 19 ✔
Zero manual intervention from check-in to deployment ✔ Only inputs: code, configs and tests ✔ Test driven development ✔ Fuzz testing Measurement: code coverage End to End Continuous Security Requirements & Design Coding Integration Test Deploy -
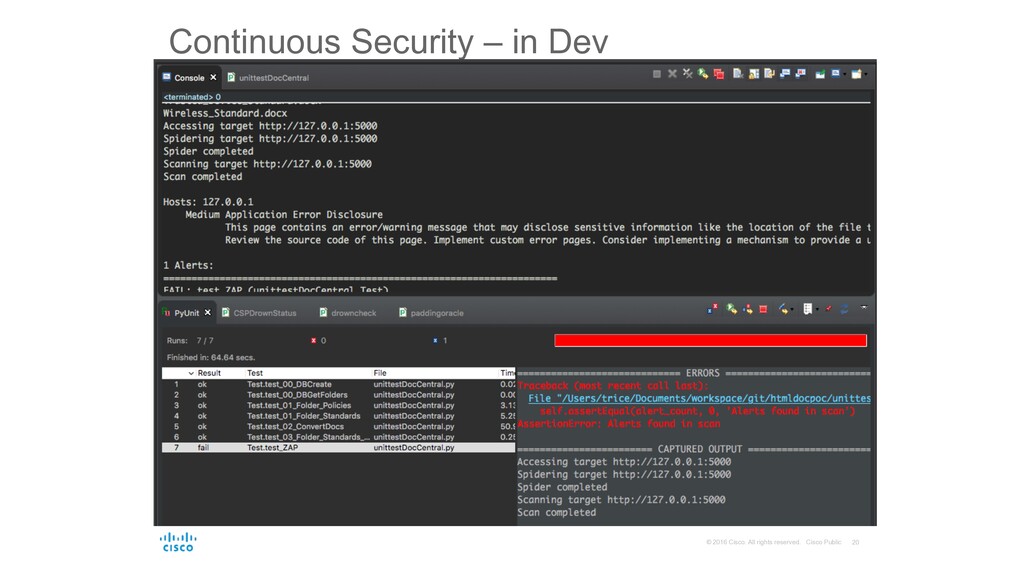
© 2016 Cisco. All rights reserved. Cisco Public 20 Continuous
Security – in Dev -
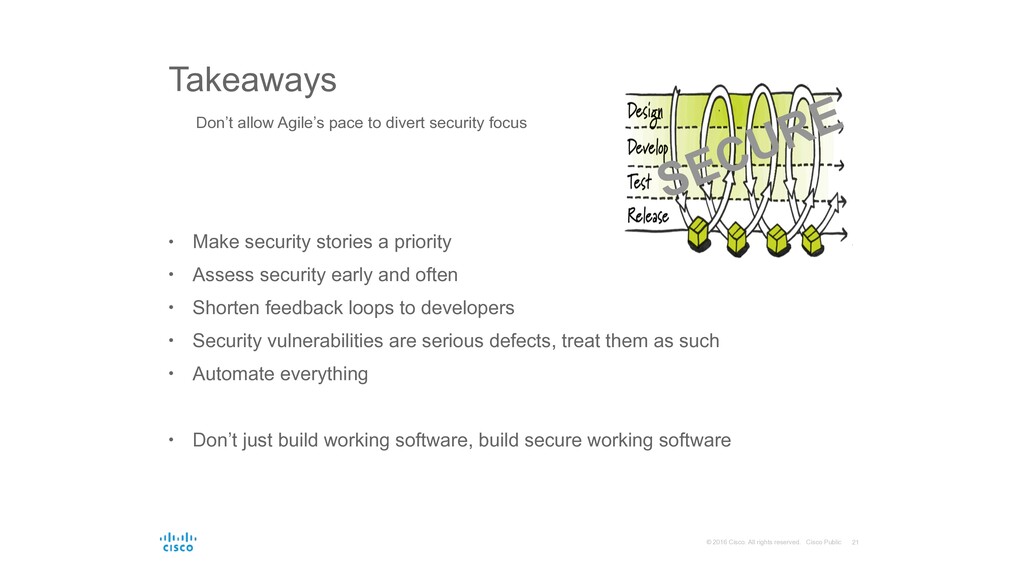
© 2016 Cisco. All rights reserved. Cisco Public 21 •
Make security stories a priority • Assess security early and often • Shorten feedback loops to developers • Security vulnerabilities are serious defects, treat them as such • Automate everything • Don’t just build working software, build secure working software Takeaways Don’t allow Agile’s pace to divert security focus SECURE -
© 2016 Cisco. All rights reserved. Cisco Public 23 Additional
Reading • How Cisco IT Developed a Self-Service Model for Build and Deploy – Cisco IT • Haskins, Bill, et al.. "8.4.2 Error Cost Escalation Through the Project Life Cycle." INCOSE International Symposium 14.1 (2004): 1723-737. NASA Technical Reports Server. NASA Johnson Space Center. • Boehm, Barry W. Software Engineering Economics. Englewood Cliffs, NJ: Prentice-Hall, 1981. ISBN 0138221227 • Puppet Labs. State of DevOps Report (2016) • Martin, James. An Information Systems Manifesto. Englewood Cliffs, NJ: Prentice-Hall, 1984. ISBN 0134647696. • Security in the Software Lifecycle, Department of Homeland Security (August 2006) • Moving Targets: Security and Rapid-Release in Firefox, Sandy Clark, et al. • Risk, Loss and Security Spending in the Financial Sector, Sans Institute