Share
Embed
Securiing Microservices
Best practices, patterns and gotchas for securing Microservices.
Tony Rice
October 27, 2017
Transcript
22 slides
-
Cisco Public 2017 All Rights Reserved Securing Microservices Tony Rice
Cisco Security & Trust Organization -
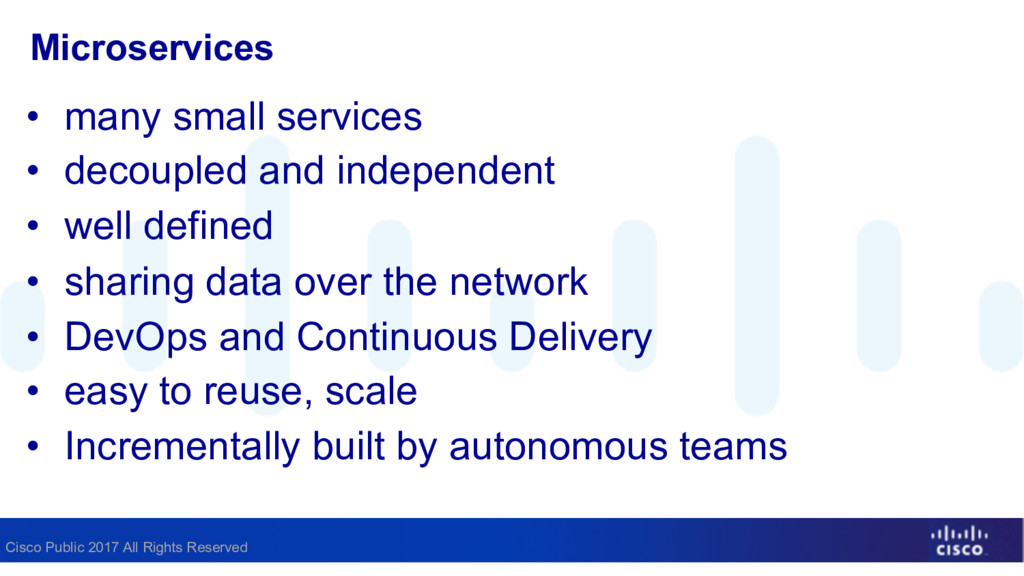
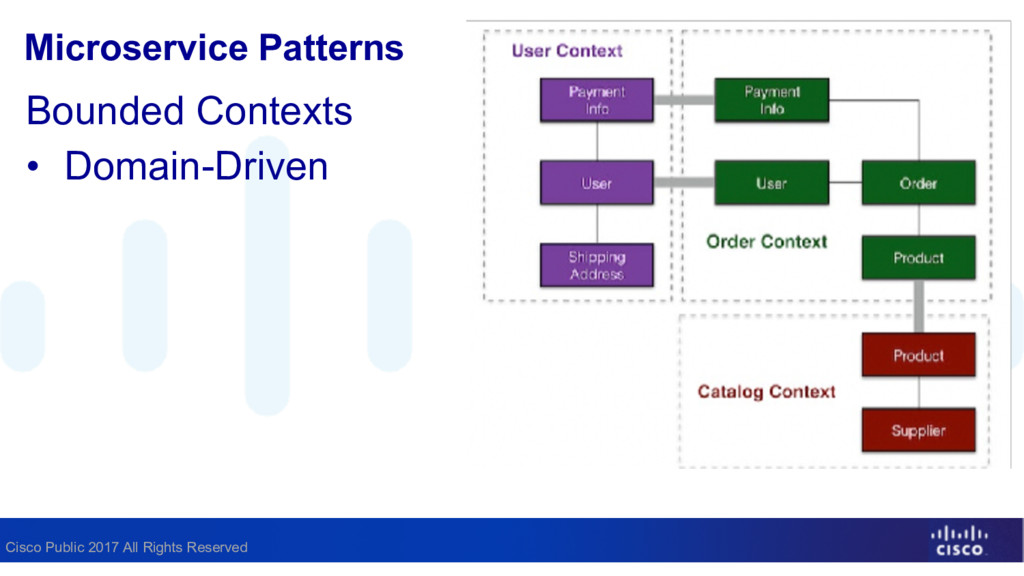
Cisco Public 2017 All Rights Reserved Microservices • many small
services • decoupled and independent • well defined • sharing data over the network • DevOps and Continuous Delivery • easy to reuse, scale • Incrementally built by autonomous teams -
Cisco Public 2017 All Rights Reserved Why Microservices? “Write programs
that do one thing and do it well.” Ken Thompson Bell System Technical Journal, 1978 -
Cisco Public 2017 All Rights Reserved Why Microservices? “small, sharp
tools” Andrew Hunt The Pragmatic Programmer, 1999 -
Cisco Public 2017 All Rights Reserved Microservices weaken AppSec •
Larger, varied attack surface • More complex • adds complexity to smaller organizations, more stacks to track and patch • API contracts • Distributed attacks more difficult to detect • Integration tests are critical -
Cisco Public 2017 All Rights Reserved Microservices strengthen AppSec •
Defense in depth, isolation • Less complex • Easier, faster, cheaper security patch distribution • Encourages automated testing • Smaller, bounded, attack surface • Simpler code, handled by focused smaller teams • Fewer stateful sessions • longer app lifetime -
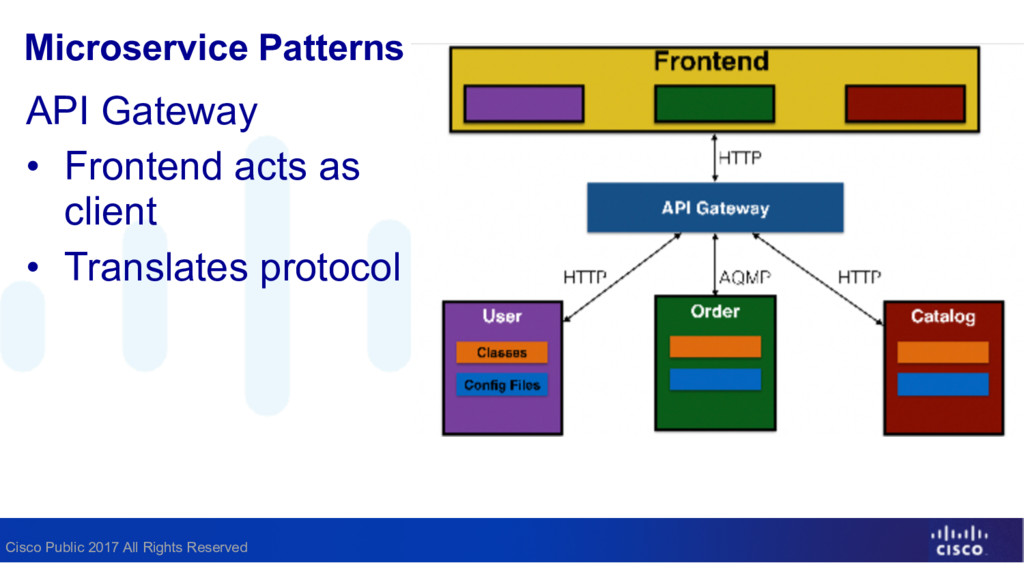
Cisco Public 2017 All Rights Reserved Microservice Patterns API Gateway
• Frontend acts as client • Translates protocol -
Cisco Public 2017 All Rights Reserved Complexity • Database per
service? • Data/Message integrity • Rapid change -
Cisco Public 2017 All Rights Reserved More Gotchas • Cross
Service Microservice Injection • Serialization / Deserialization • Dont pass credentials around in the clear • Dont hardcode credentials ANYWHERE (source code, docker configs) • ENV is not interprocess communication -
Cisco Public 2017 All Rights Reserved Best Practices - centralize
commonalities Centralize, externalize and apply across all microservices • Authentication, Authorization, and Accounting (AAA) • Configuration • reduces disparities which lead to exploitable vulnerabilities / escalation of privileges -
Cisco Public 2017 All Rights Reserved Best Practices - Developers^3
• Development team structure should reflect service architecture. -
Cisco Public 2017 All Rights Reserved Best Practices - minimalism
• Segment functions and environments • Grant only the level of access needed • “Need to know”, “least privilege” • Offload network functions to edge (rate-limiting, reputation, etc.) Untitled (in honor of Harold Joachim) 3, 1977 by Dan Flavin -
Cisco Public 2017 All Rights Reserved Best Practices - Secrets
• Don’t store secrets, manage them -
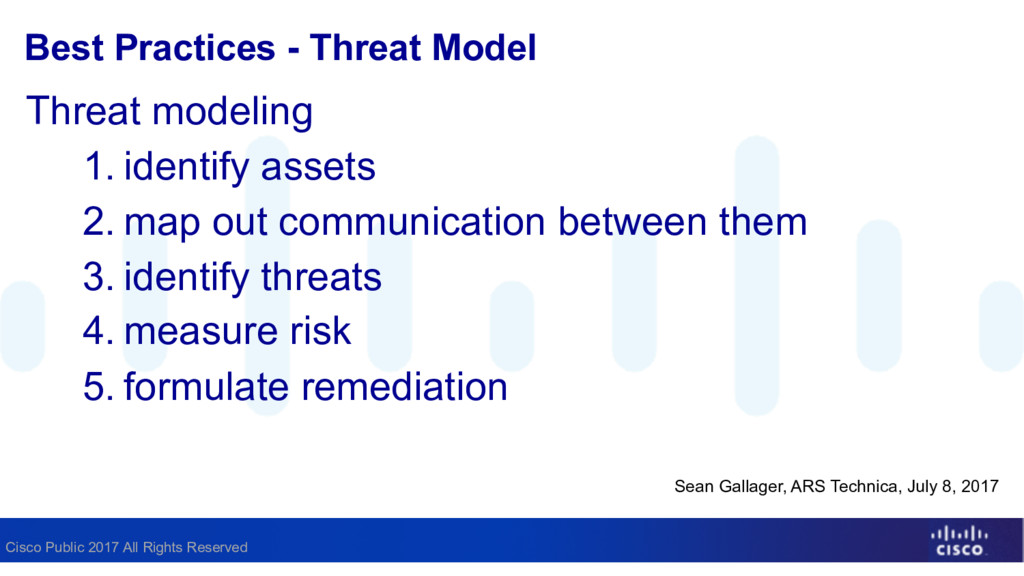
Cisco Public 2017 All Rights Reserved Best Practices - Threat
Model Threat modeling 1. identify assets 2. map out communication between them 3. identify threats 4. measure risk 5. formulate remediation Sean Gallager, ARS Technica, July 8, 2017 -
Cisco Public 2017 All Rights Reserved Best Practices • Review,
review, review • Code reviews during development • Usage reviews after • Remove dead code and underutilized services promptly -
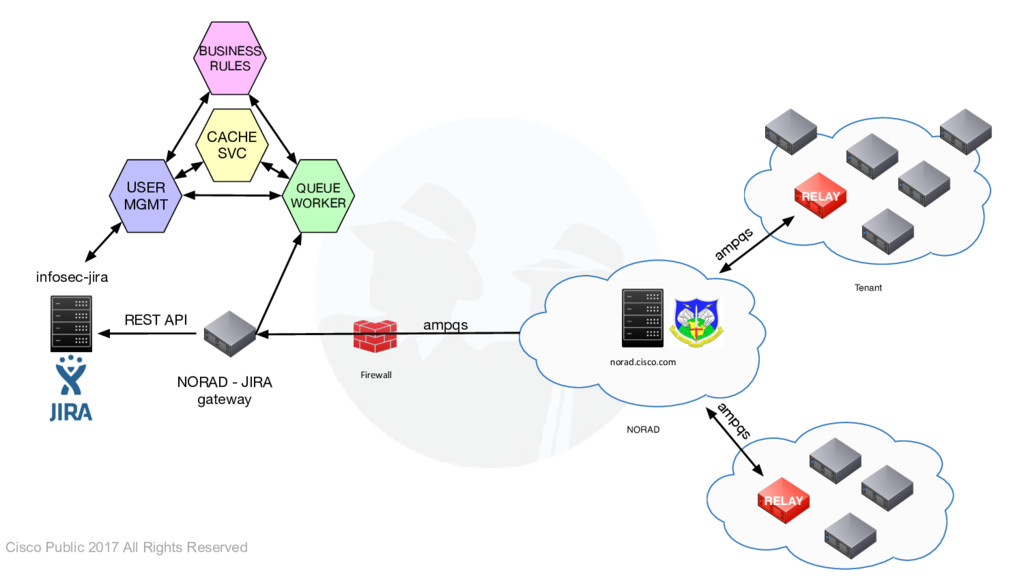
Cisco Public 2017 All Rights Reserved NORAD norad.cisco.com Firewall ampqs
Tenant RELAY RELAY am pqs am pqs NORAD - JIRA gateway REST API infosec-jira CACHE SVC QUEUE WORKER BUSINESS RULES USER MGMT -
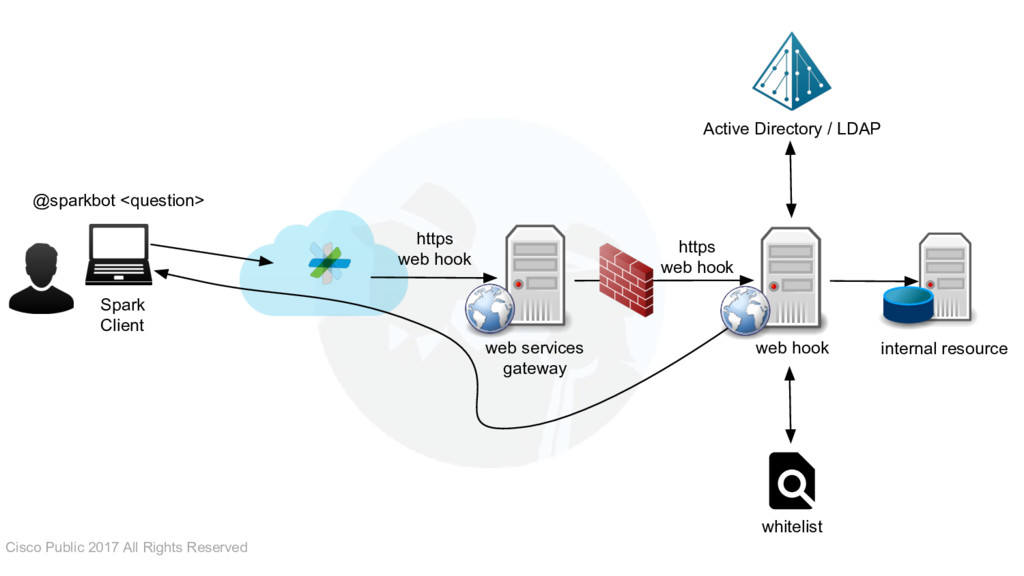
Cisco Public 2017 All Rights Reserved Active Directory / LDAP
Spark Client https web hook web hook web services gateway internal resource whitelist @sparkbot <question> https web hook -
Cisco Public 2017 All Rights Reserved Resources • REST Cheat
Sheet • Mobile Cheat Sheet • Network Cheat Sheet • http://microservices.io/ owasp.org