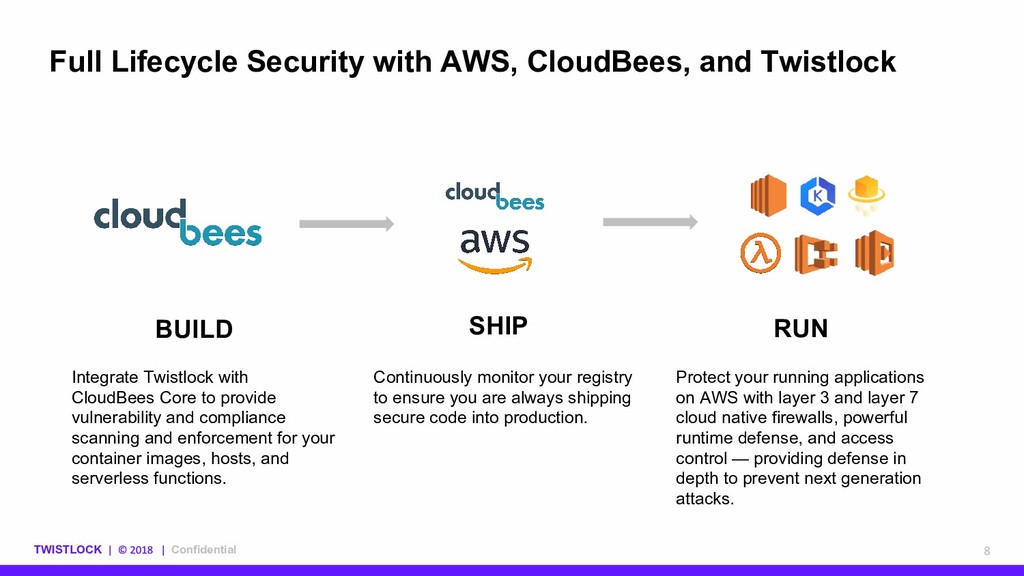
Integrate Twistlock with CloudBees Core to provide vulnerability and compliance scanning and enforcement for your container images, hosts, and serverless functions. Continuously monitor your registry to ensure you are always shipping secure code into production. Protect your running applications on AWS with layer 3 and layer 7 cloud native firewalls, powerful runtime defense, and access control — providing defense in depth to prevent next generation attacks. BUILD SHIP RUN
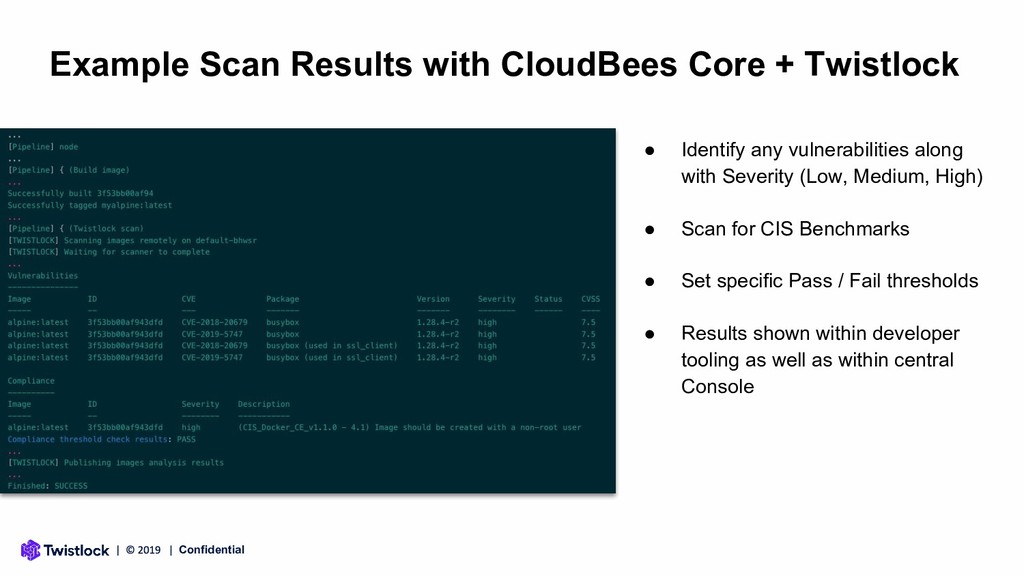
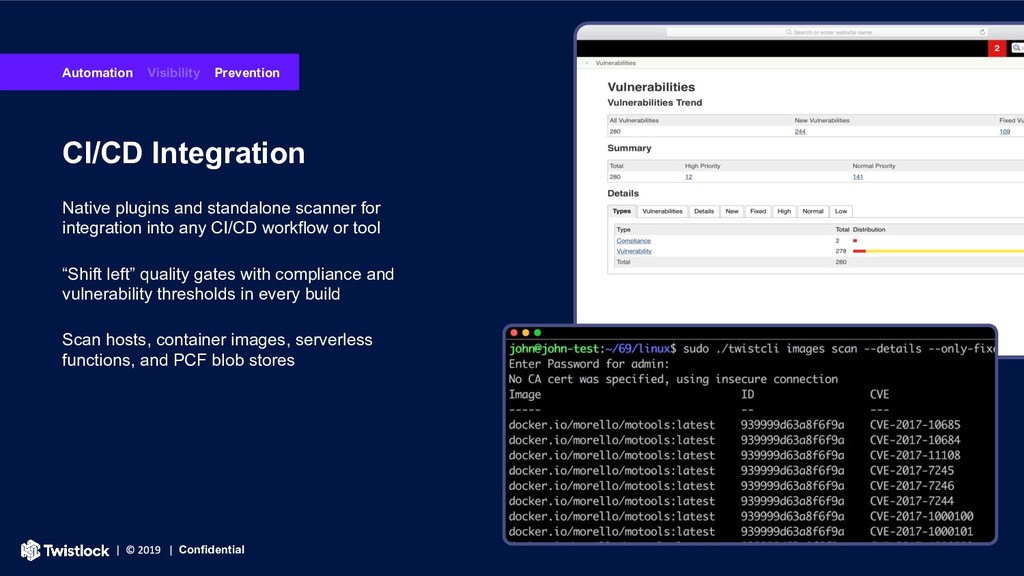
Identify any vulnerabilities along with Severity (Low, Medium, High) • Scan for CIS Benchmarks • Set specific Pass / Fail thresholds • Results shown within developer tooling as well as within central Console
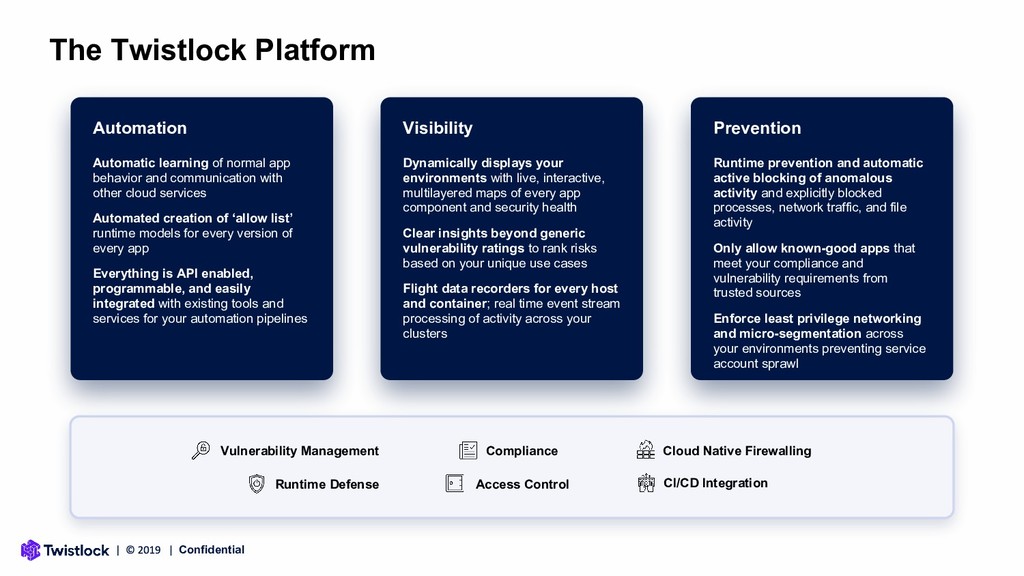
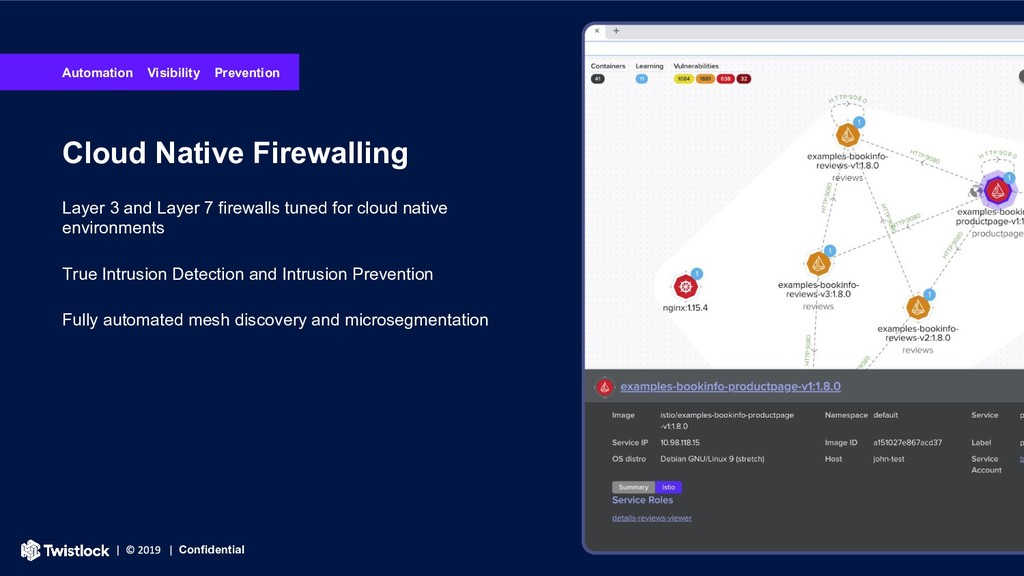
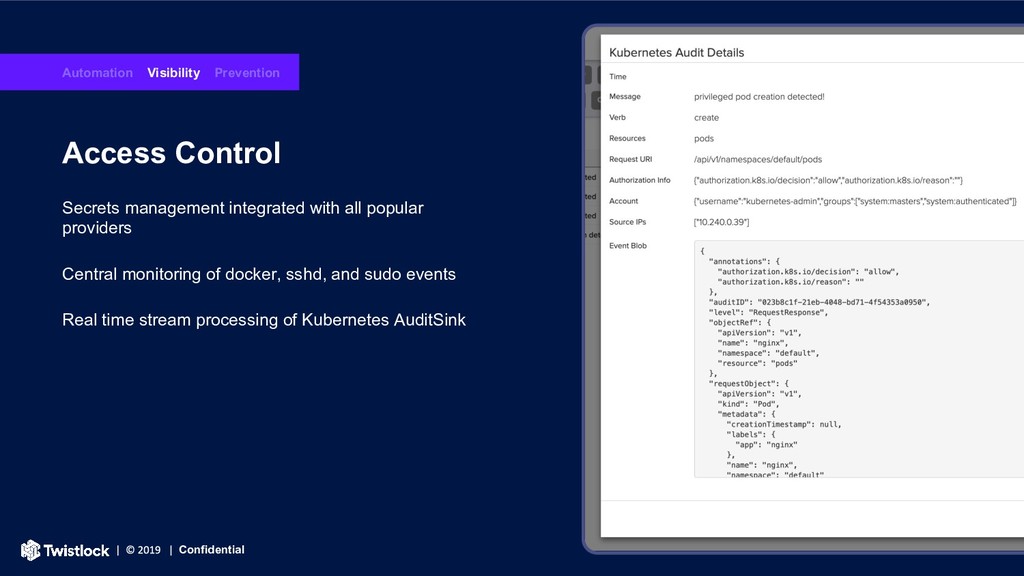
other cloud services Automated creation of ‘allow list’ runtime models for every version of every app Everything is API enabled, programmable, and easily integrated with existing tools and services for your automation pipelines Automation Dynamically displays your environments with live, interactive, multilayered maps of every app component and security health Clear insights beyond generic vulnerability ratings to rank risks based on your unique use cases Flight data recorders for every host and container; real time event stream processing of activity across your clusters Visibility Runtime prevention and automatic active blocking of anomalous activity and explicitly blocked processes, network traffic, and file activity Only allow known-good apps that meet your compliance and vulnerability requirements from trusted sources Enforce least privilege networking and micro-segmentation across your environments preventing service account sprawl Prevention Vulnerability Management Cloud Native Firewalling Runtime Defense Access Control Compliance CI/CD Integration The Twistlock Platform
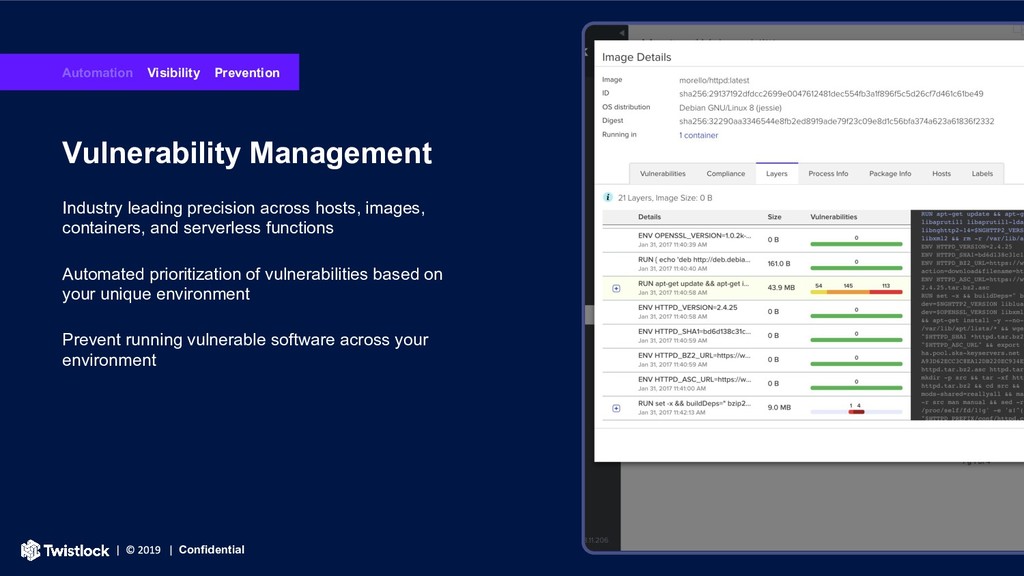
functions Automated prioritization of vulnerabilities based on your unique environment Prevent running vulnerable software across your environment Vulnerability Management Automation Visibility Prevention
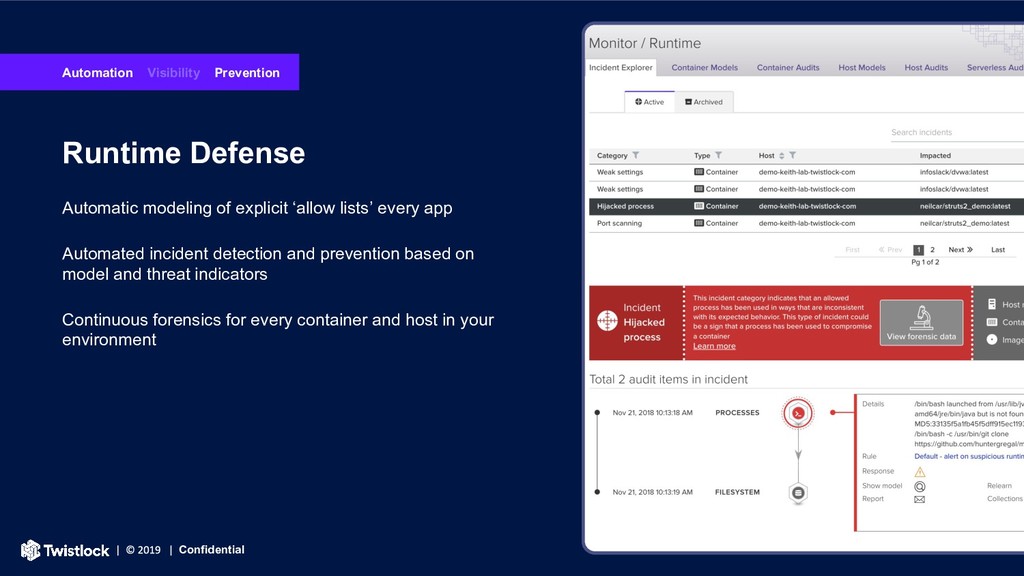
incident detection and prevention based on model and threat indicators Continuous forensics for every container and host in your environment Runtime Defense Automation Visibility Prevention
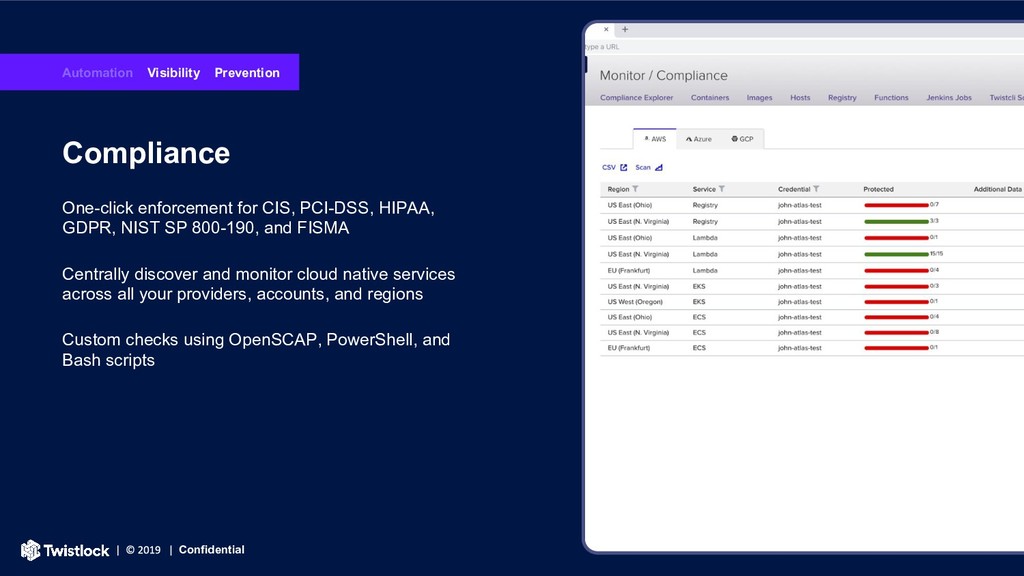
800-190, and FISMA Centrally discover and monitor cloud native services across all your providers, accounts, and regions Custom checks using OpenSCAP, PowerShell, and Bash scripts Compliance Automation Visibility Prevention
dev round trip • Automated policy creation that adapts as the application changes • No manual steps! • Include security as part of the application scaffolding and fabric. Don’t wait until the application is ready for production to think about security Defining Scalable Security
in the container image to make it available when running • Downsides ◦ Anyone can modify the image ◦ Trusting the developers to embed the proper security • You need to employ a trusted images approach Embedding an agent
container • Sidecar approach does not require modifying any of the application images • Security is decided by the security team and deployed by the team deploying the applications, the same way you do things today Loading from a sidecar
do for other containers and images • Vulnerabilities, Compliance and runtime • What is different? ◦ Deployment of Defender via sidecar ◦ Modify only the task definition, don’t modify the image! ◦ Policies are dynamic Securing Fargate with Twistlock
monitor your serverless repos • Identify vulnerability and compliance issues at runtime • Runtime protection against process and network manipulation • Architecture components: deployment of Defender as part of the function Securing Lambda with Twistlock


 twistlock
 ma2shita
 cloudace
 masakiokuda
 ufried
 kameitomohiro
 genshun9
 aoi1
 philipz
 raybugg
 shunsock
 maguroalternative
 nwiizo
 ipullrank
 carmenintech
 tammyeverts
 aleyda
 kristinabergwall1
 kimpetersen
 eileencodes
 stephaniewalter
 holman
 ryanjones
 signer