Upgrade to Pro
— share decks privately, control downloads, hide ads and more …
Speaker Deck
Sign up for free
Menu
Search
Features
All features
Private URLs
Password Protection
Custom URLS
Scheduled publishing
Remove Branding
Restrict embedding
Deck Collections
Notes
Features
All features
Private URLs
Password Protection
Custom URLS
Scheduled publishing
Remove Branding
Restrict embedding
Deck Collections
Notes
Explore
Featured decks
Featured speakers
Programming
Technology
Storyboards
Explore
Featured decks
Featured speakers
Programming
Technology
Storyboards
Pricing
Search
Sign in
Sign up for free
Bitcoin Ops & Security Primer
Search
Russell Smith
April 07, 2014
Technology
190
1
Share
Embed
Copy iframe code
Copy JS code
Copy link
Start on current slide
Bitcoin Ops & Security Primer
Russell Smith
April 07, 2014
More Decks by Russell Smith
See All by Russell Smith
Ops Skills and Tools for Beginners [MongoDB World 2014]
ukd1
0
150
3 Infrastructure + workflow lessons from an early stage startup
ukd1
0
140
Gearman & Kohana
ukd1
2
1k
Geo & capped collections with MongoDB
ukd1
1
170
Cassandra London UG July 2011 - Riak vs Cassandra
ukd1
1
340
MongoDB - Map Reduce
ukd1
2
270
MongoDB London UG, April 2011 - MongoDB Introduction
ukd1
1
140
MongoDB London 2011 - MongoDB Command Line Tools
ukd1
1
210
Seedhack 2011 - Introducing MongoDB
ukd1
1
160
Other Decks in Technology
See All in Technology
エージェントはローカル、検証はMicroVM — Lambda MicroVMsでつくるServerless CI
fujioka6789
3
350
開発投資の期待値を上げるプロダクトロードマップづくり ~プロダクトエンジニアが越境して事業を伸ばす~
kekekenta
1
210
アプリをもっと"iOSアプリっぽく"する小さな工夫 / Small Touches That Make Your App Feel More Like an iOS App
matsuji
2
950
あけおめLINE 傾向とその対策
nasa9084
0
150
What the customer really needed
kawaguti
PRO
3
210
空間オーディオで過去の 自分(ゴースト)と競うランニング 〜HealthKitのルートを足音に変える実装〜
nao_randd
0
230
積み重なった技術負債への挑戦 〜初手としての全社ゴト化〜
techtekt
PRO
0
1.3k
ソフトウェアDNAとクラウドエージェントのススメ
cloudace
0
110
AIによるクリエイティブ生成を行う上での試行錯誤
plaidtech
PRO
0
160
Railsのように考える: See through the Master
snoozer05
PRO
4
1.1k
作って終わりじゃないサーバーレス 〜9年運用する大規模EC物流API基盤の設計・運用のリアル〜
zozotech
PRO
0
170
Issue 駆動でスペシャリストの意図を届ける、AI 実装のアクセシビリティ向上
thkt
0
120
Featured
See All Featured
Joys of Absence: A Defence of Solitary Play
codingconduct
1
520
The State of eCommerce SEO: How to Win in Today's Products SERPs - #SEOweek
aleyda
2
12k
HU Berlin: Industrial-Strength Natural Language Processing with spaCy and Prodigy
inesmontani
PRO
0
700
Faster Mobile Websites
deanohume
310
32k
The Invisible Side of Design
smashingmag
301
52k
The Language of Interfaces
destraynor
162
27k
No one is an island. Learnings from fostering a developers community.
thoeni
21
3.8k
Ten Tips & Tricks for a 🌱 transition
stuffmc
1
230
Unsuck your backbone
ammeep
672
58k
DevOps and Value Stream Thinking: Enabling flow, efficiency and business value
helenjbeal
1
390
Practical Orchestrator
shlominoach
192
12k
Principles of Awesome APIs and How to Build Them.
keavy
128
18k
Transcript
rainforest @rainforestqa Bitcoin + Ops Primer:! Understand your risk Manage
attacks
@rainforestqa rainforest Rainforest Human powered QA SaaS Designed for ‘Continuous
QA’ Built for PMs and Developers
@rainforestqa rainforest Us Team of 6 in SoMa All developers
YC S12
@rainforestqa rainforest Understanding risk
rainforest @rainforestqa Understand the trade off More secure generally means
more effort
@rainforestqa rainforest Risk vs Exposure
@rainforestqa rainforest High Risks Hot wallets / key storage Outgoing
payments Physically shipped items Reversible payments (e.g. chargebacks)
@rainforestqa rainforest …more risks Shared hosting / VPS / “physical”
security Staff
@rainforestqa rainforest Limiting Exposure Storing keys Hot wallets -> Cold
wallets, where poss Principle of least privilege
@rainforestqa rainforest What risks?
rainforest @rainforestqa Internet connected = hackable (Though, the NSA can
spy on you, even if you're not connected to the Internet)
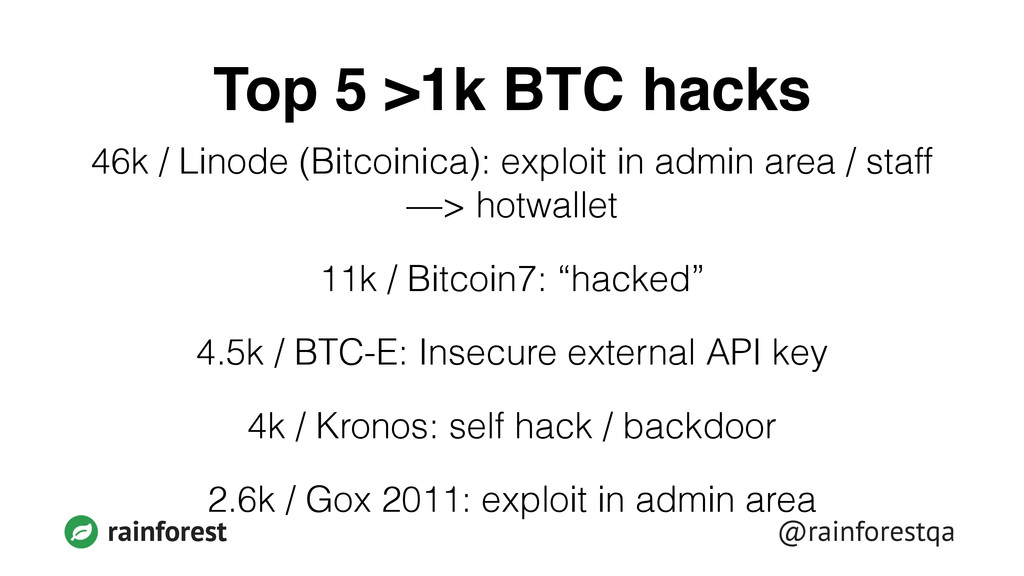
@rainforestqa rainforest Top 5 >1k BTC hacks 46k / Linode
(Bitcoinica): exploit in admin area / staff —> hotwallet 11k / Bitcoin7: “hacked” 4.5k / BTC-E: Insecure external API key 4k / Kronos: self hack / backdoor 2.6k / Gox 2011: exploit in admin area
@rainforestqa rainforest Top 3 reasons:
@rainforestqa rainforest Badly configured servers / services
@rainforestqa rainforest Poorly written software
@rainforestqa rainforest Exploits
@rainforestqa rainforest Attack vectors Your service Your customers You &
your team
@rainforestqa rainforest Your service Domain Email Servers (app, db, etc)
Network External services Backups
@rainforestqa rainforest Domain DNS hijacking MITM attacks Doppelganger domains /
Typo-squatting Renewals
@rainforestqa rainforest HSTS Pinning / force-ssl Cloudflare, imho Firewall +
IDS
@rainforestqa rainforest Email DKIM / SPF Account state Clear email
policies Lockout policy
@rainforestqa rainforest Servers Shared / VPS / AWS Dedicated Co-lo
>
@rainforestqa rainforest OS + software updates Automate provisioning Hire pen-testing
Have a security program
@rainforestqa rainforest Transactions & locking (see Flexcoin / Poloniex)
@rainforestqa rainforest Network IDS / IDPS / HIDS Firewall (both
ways) -complex-
@rainforestqa rainforest External services Verify SSL certs Limit IPs Work
out what + who you can trust
@rainforestqa rainforest Backups Major security issue Encrypt them Test them
@rainforestqa rainforest Your customers Understand their behavior (Progressive) Account limits
Policies KYC
@rainforestqa rainforest Primer
@rainforestqa rainforest Educate yourself
@rainforestqa rainforest Pick secure by default tech
@rainforestqa rainforest 2FA
@rainforestqa rainforest Avoid shared servers
@rainforestqa rainforest Honey pots
@rainforestqa rainforest Automate deployment
@rainforestqa rainforest Use SSH keys, rotate them
@rainforestqa rainforest Use a Firewall
@rainforestqa rainforest Use an IDS
@rainforestqa rainforest Encrypt (and take!) backups
@rainforestqa rainforest Subscribe to security lists
@rainforestqa rainforest Do as little as possible
@rainforestqa rainforest Staff opsec
@rainforestqa rainforest Principle of least privilege
@rainforestqa rainforest Split your servers
@rainforestqa rainforest Or consider LXC / KVM
@rainforestqa rainforest Split your app
@rainforestqa rainforest Server: partitions + noexec + nosuid split running
users disable root remove packages SELinux
@rainforestqa rainforest Starting points Figure out your risk + exposure
Implement low hanging fruit Reduce surface Plan the rest
@rainforestqa rainforest Conclusions Simpler = better Understand your exposure and
limit it
@rainforestqa rainforest Further reading Hacks: https://bitcointalk.org/index.php?topic=83794.0 Flexcoin: http://hackingdistributed.com/2014/04/06/another-one-bites-the-dust- flexcoin/ Docker:
http://www.slideshare.net/jpetazzo/linux-containers-lxc-docker-and- security CVE: http://web.nvd.nist.gov/view/vuln/search?execution=e2s1
rainforest @rainforestqa Questions? @rainforestqa @rhs


 ukd1
 fujioka6789
 kekekenta
 matsuji
 nasa9084
 kawaguti
 nao_randd
 techtekt
 cloudace
 plaidtech
 snoozer05
 zozotech
 thkt
 codingconduct
 aleyda
 inesmontani
 deanohume
 smashingmag
 destraynor
 thoeni
 stuffmc
 ammeep
 helenjbeal
 shlominoach
 keavy