Upgrade to Pro
— share decks privately, control downloads, hide ads and more …
Speaker Deck
Sign up for free
Menu
Search
Features
All features
Private URLs
Password Protection
Custom URLS
Scheduled publishing
Remove Branding
Restrict embedding
Deck Collections
Notes
Features
All features
Private URLs
Password Protection
Custom URLS
Scheduled publishing
Remove Branding
Restrict embedding
Deck Collections
Notes
Explore
Featured decks
Featured speakers
Programming
Technology
Storyboards
Explore
Featured decks
Featured speakers
Programming
Technology
Storyboards
Pricing
Search
Sign in
Sign up for free
OSS の脆弱性対応の舞台裏
Search
Sponsored
·
Your Podcast. Everywhere. Effortlessly.
Share. Educate. Inspire. Entertain. You do you. We'll handle the rest.
→
うたもく
December 19, 2025
1.5k
2
Share
Embed
Copy iframe code
Copy JS code
Copy link
Start on current slide
OSS の脆弱性対応の舞台裏
3-shake SRE Tech Talk #14 オンサイト での発表資料です。
https://3-shake.connpass.com/event/373259/
うたもく
December 19, 2025
More Decks by うたもく
See All by うたもく
オープンソースソフトウェアへの解像度🔬
utam0k
18
5.7k
CNCF Project の作者が考えている OSS の運営
utam0k
7
1.2k
Podman with WebAssembly
utam0k
2
1.1k
クラウドネイティブの基盤要素、コンテナの今と未来
utam0k
21
7.3k
Possibility of OCI Container Runtime with Rust
utam0k
3
1.7k
Container-related technologies supporting Gitpod
utam0k
1
1.4k
詳説 OCIコンテナランタイム youki@第15回 コンテナ技術の情報交換会
utam0k
5
2.4k
Rust 🤝 Container Runtime @ Rust.Tokyo 2021
utam0k
2
2k
「あれ、コンテナって何だっけ?」から生まれた Rust で書かれた コンテナランタイム youkiの話@ODC2021
utam0k
6
4.4k
Featured
See All Featured
Bootstrapping a Software Product
garrettdimon
PRO
306
120k
Navigating the Design Leadership Dip - Product Design Week Design Leaders+ Conference 2024
apolaine
2
450
Design of three-dimensional binary manipulators for pick-and-place task avoiding obstacles (IECON2024)
konakalab
0
610
Accessibility Awareness
sabderemane
1
230
Designing Powerful Visuals for Engaging Learning
tmiket
1
590
Exploring the Power of Turbo Streams & Action Cable | RailsConf2023
kevinliebholz
37
6.6k
How To Stay Up To Date on Web Technology
chriscoyier
790
250k
The SEO identity crisis: Don't let AI make you average
varn
0
570
Building a A Zero-Code AI SEO Workflow
portentint
PRO
0
750
Odyssey Design
rkendrick25
PRO
2
850
The AI Revolution Will Not Be Monopolized: How open-source beats economies of scale, even for LLMs
inesmontani
PRO
3
3.7k
Bridging the Design Gap: How Collaborative Modelling removes blockers to flow between stakeholders and teams @FastFlow conf
baasie
0
710
Transcript
OSS の脆弱性対応の舞台裏 SRE Tech Talk # 14 Toru Komatsu(@utam 0
k) 1
3 -shake 技術顧問 OSS Activities Maintainer: youki-dev/youki opencontainers/runtime-spec Reviewer: Kubernetes
SIG-Scheduling containerd/runwasi Community: CNCF Ambassador, CNCJ Board Member @utam0k Toru Komatsu 2
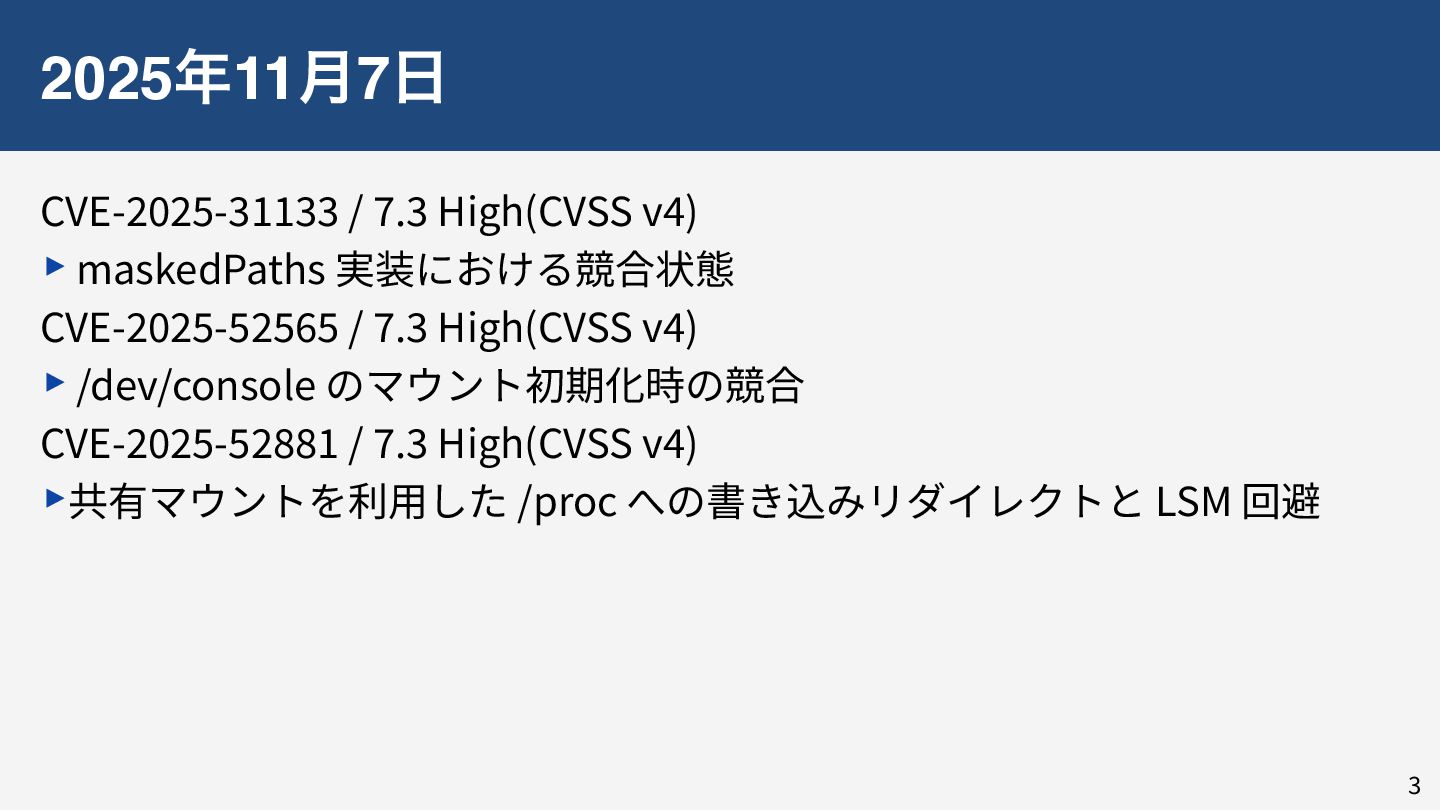
202511݄7 CVE- 202 5 - 31 1 3 3 /
7 . 3 High(CVSS v 4 ) ‣maskedPaths 実装における競合状態 CVE- 202 5 - 52 5 6 5 / 7 . 3 High(CVSS v 4 ) ‣/dev/console のマウント初期化時の競合 CVE- 202 5 - 52 8 8 1 / 7 . 3 High(CVSS v 4 ) ‣共有マウントを利 用 した /proc への書き込みリダイレクトと LSM 回避 3
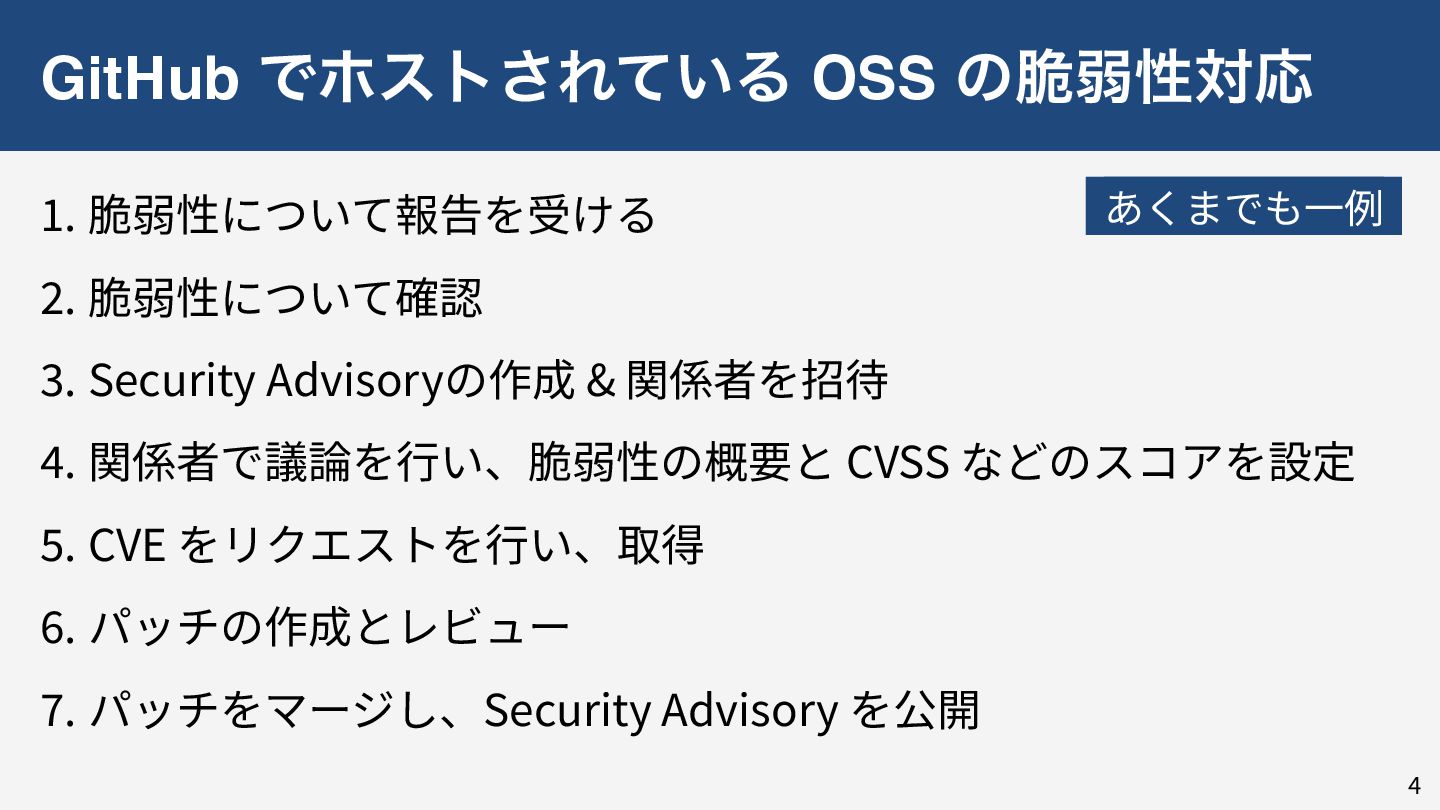
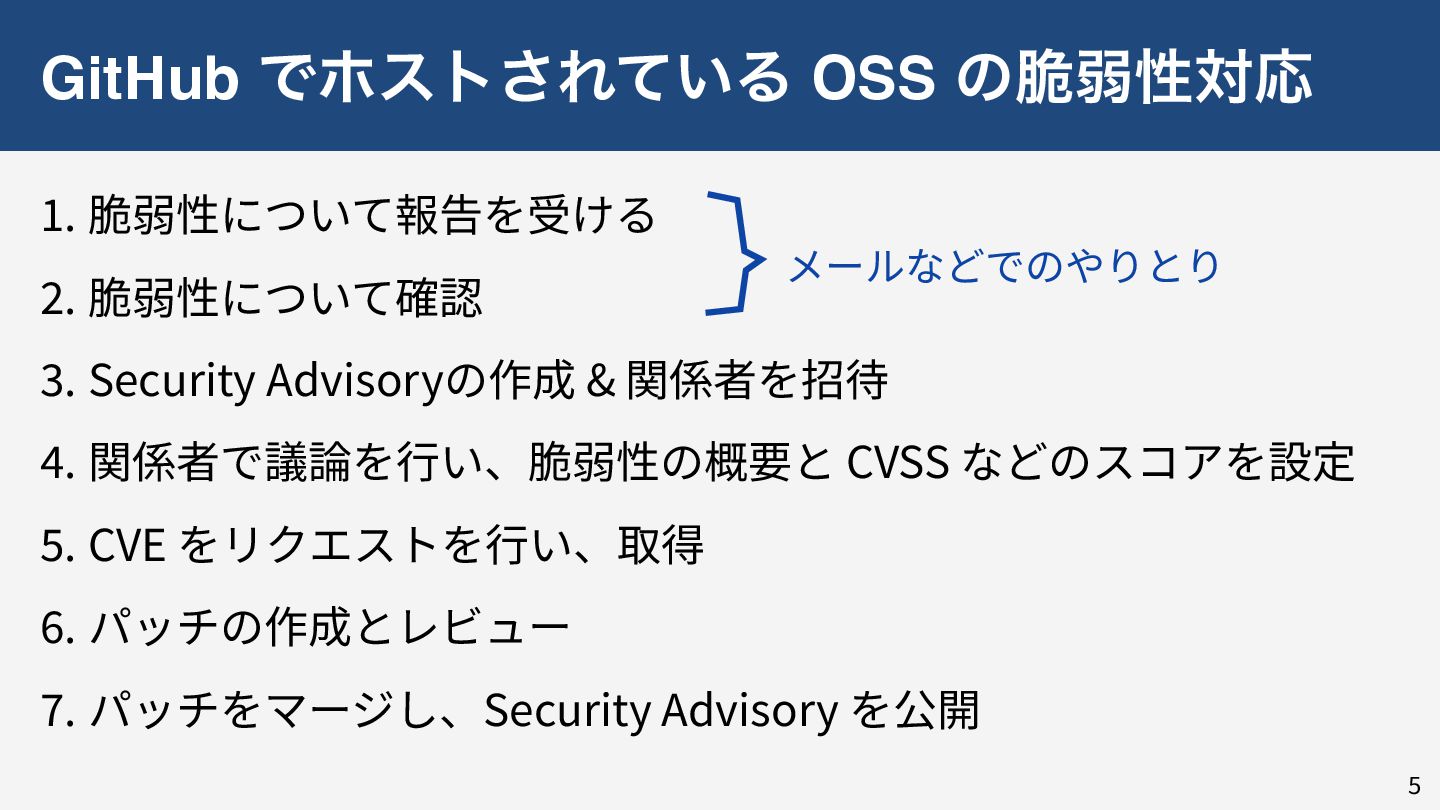
GitHub Ͱϗετ͞Ε͍ͯΔ OSS ͷ੬ऑੑରԠ 4 あくまでも 一 例 1 .
脆弱性について報告を受ける 2 . 脆弱性について確認 3 . Security Advisoryの作成 & 関係者を招待 4 . 関係者で議論を 行 い、脆弱性の概要と CVSS などのスコアを設定 5 . CVE をリクエストを 行 い、取得 6 . パッチの作成とレビュー 7 . パッチをマージし、Security Advisory を公開
1 . 脆弱性について報告を受ける 2 . 脆弱性について確認 3 . Security Advisoryの作成
& 関係者を招待 4 . 関係者で議論を 行 い、脆弱性の概要と CVSS などのスコアを設定 5 . CVE をリクエストを 行 い、取得 6 . パッチの作成とレビュー 7 . パッチをマージし、Security Advisory を公開 GitHub Ͱϗετ͞Ε͍ͯΔ OSS ͷ੬ऑੑରԠ 5 メールなどでのやりとり
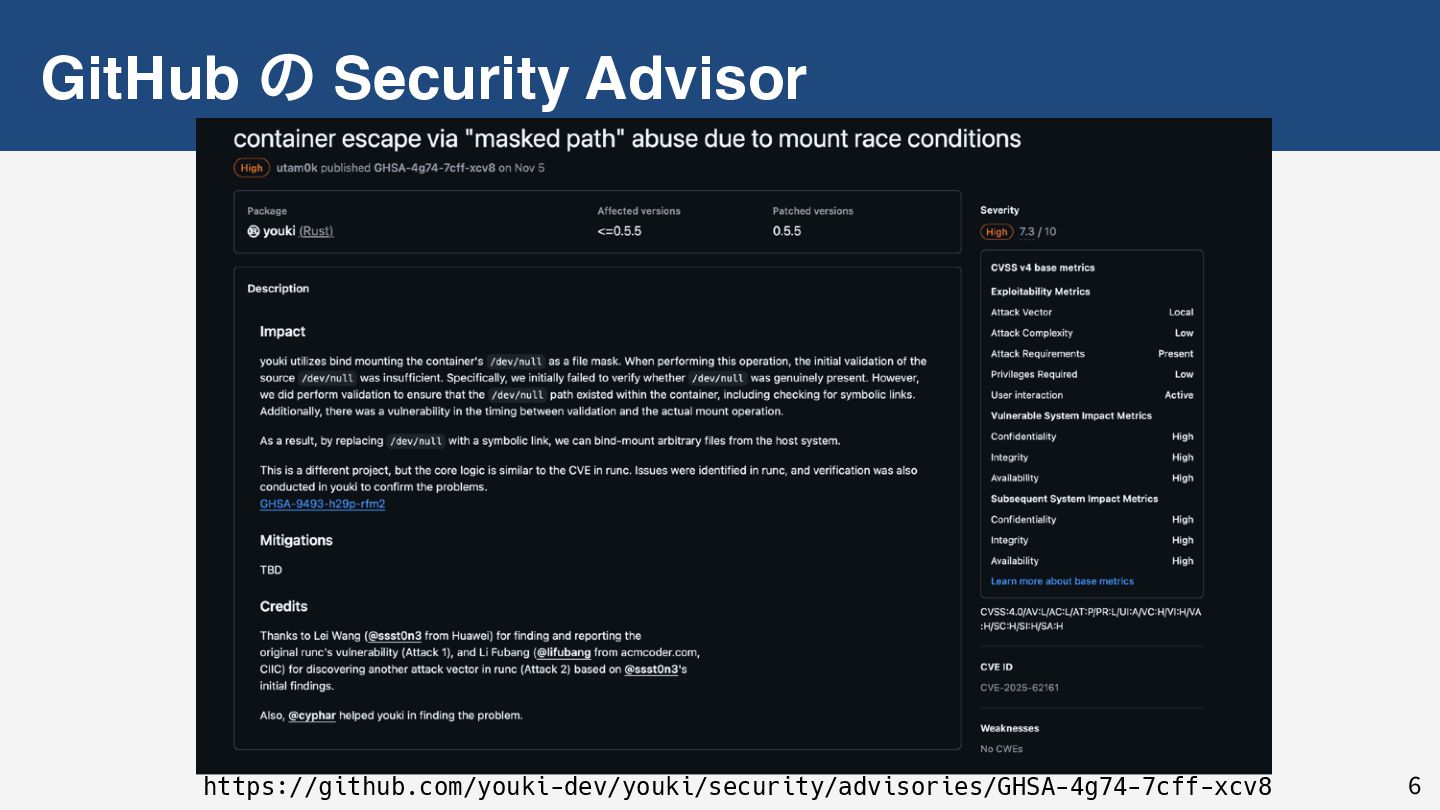
GitHub ͷ Security Advisor https://github.com/youki-dev/youki/security/advisories/GHSA-4g74-7cff-xcv8 6
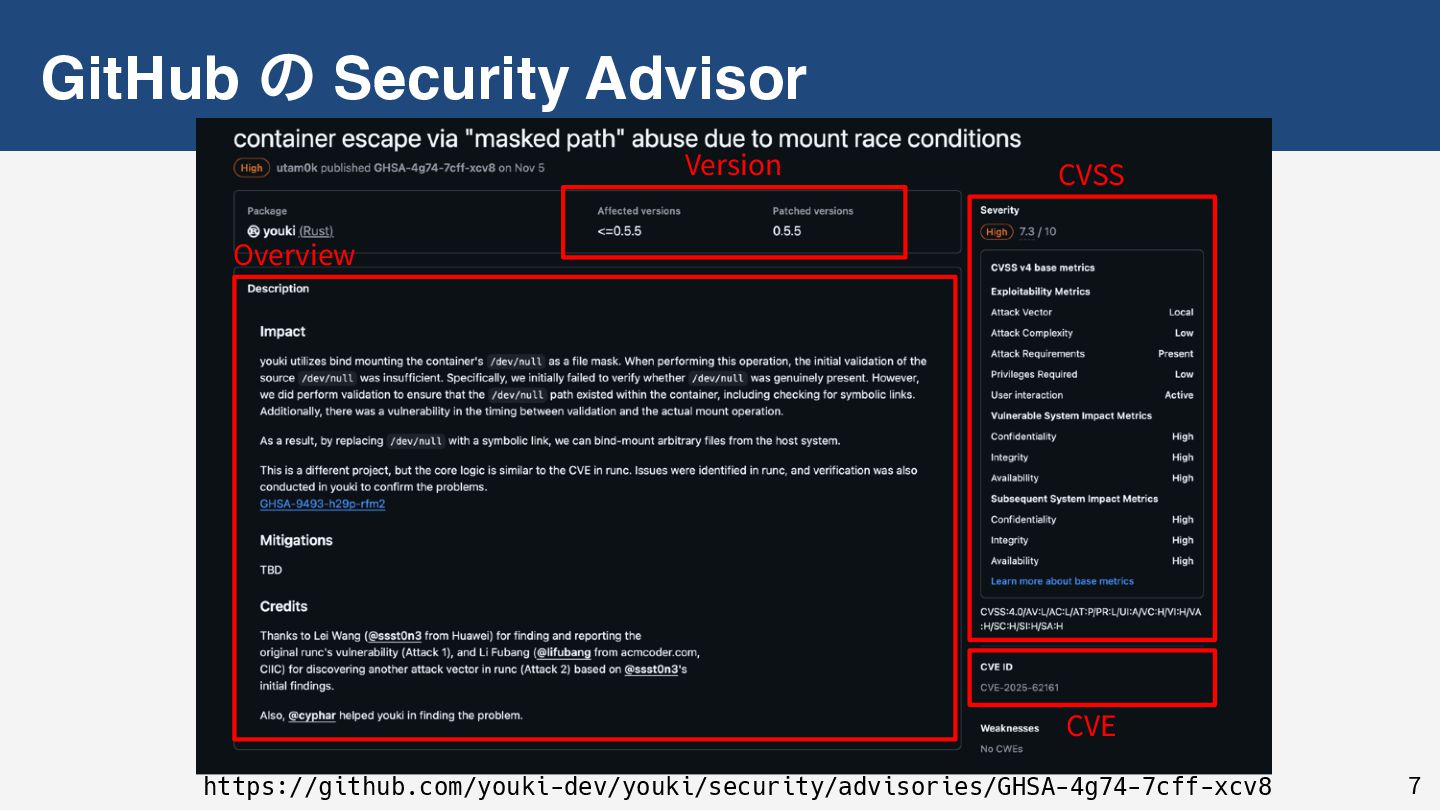
GitHub ͷ Security Advisor https://github.com/youki-dev/youki/security/advisories/GHSA-4g74-7cff-xcv8 7 CVSS CVE
Overview Version
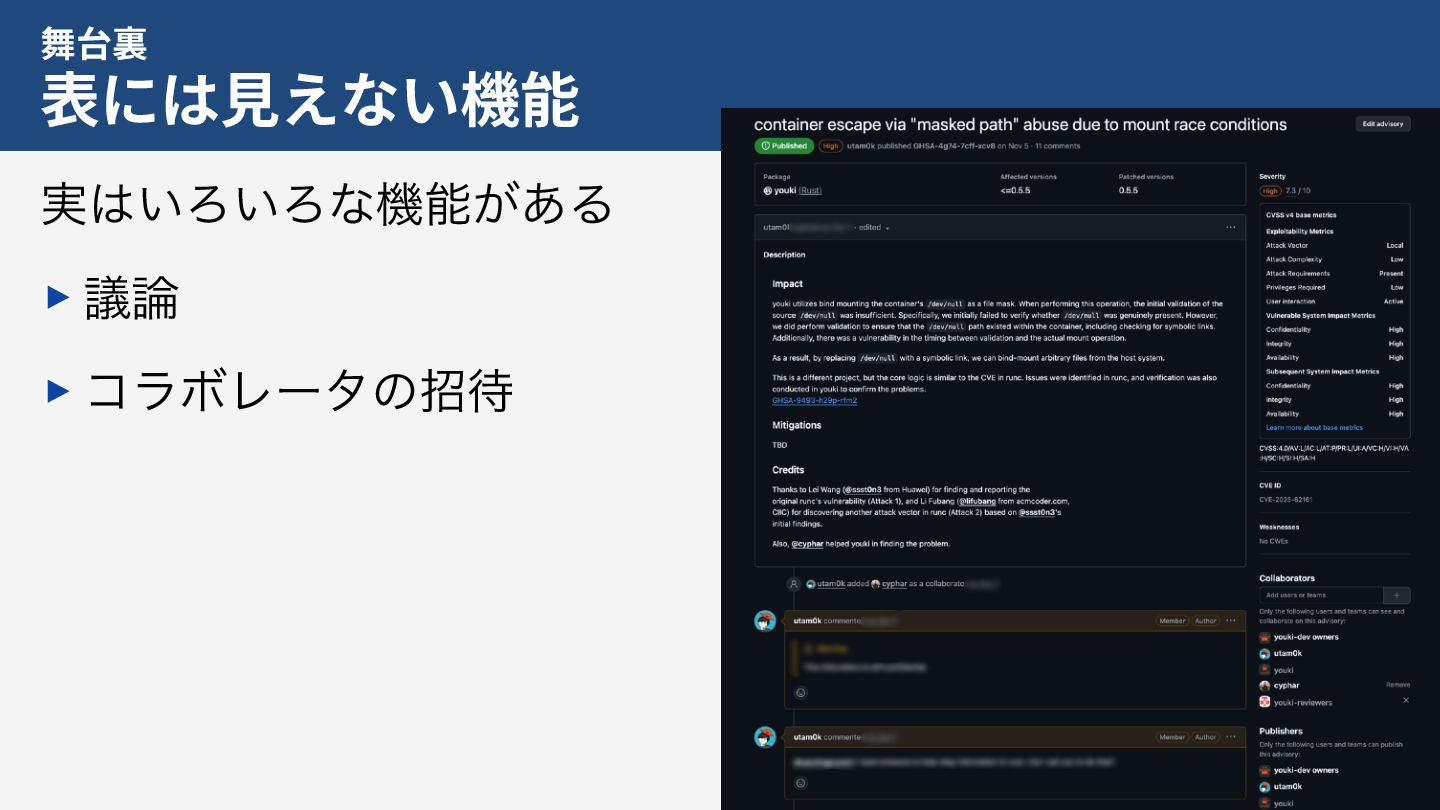
舞台裏 表には 見 えない機能 ࣮͍Ζ͍Ζͳػೳ͕͋Δ ‣ٞ ‣ίϥϘϨʔλͷট 8
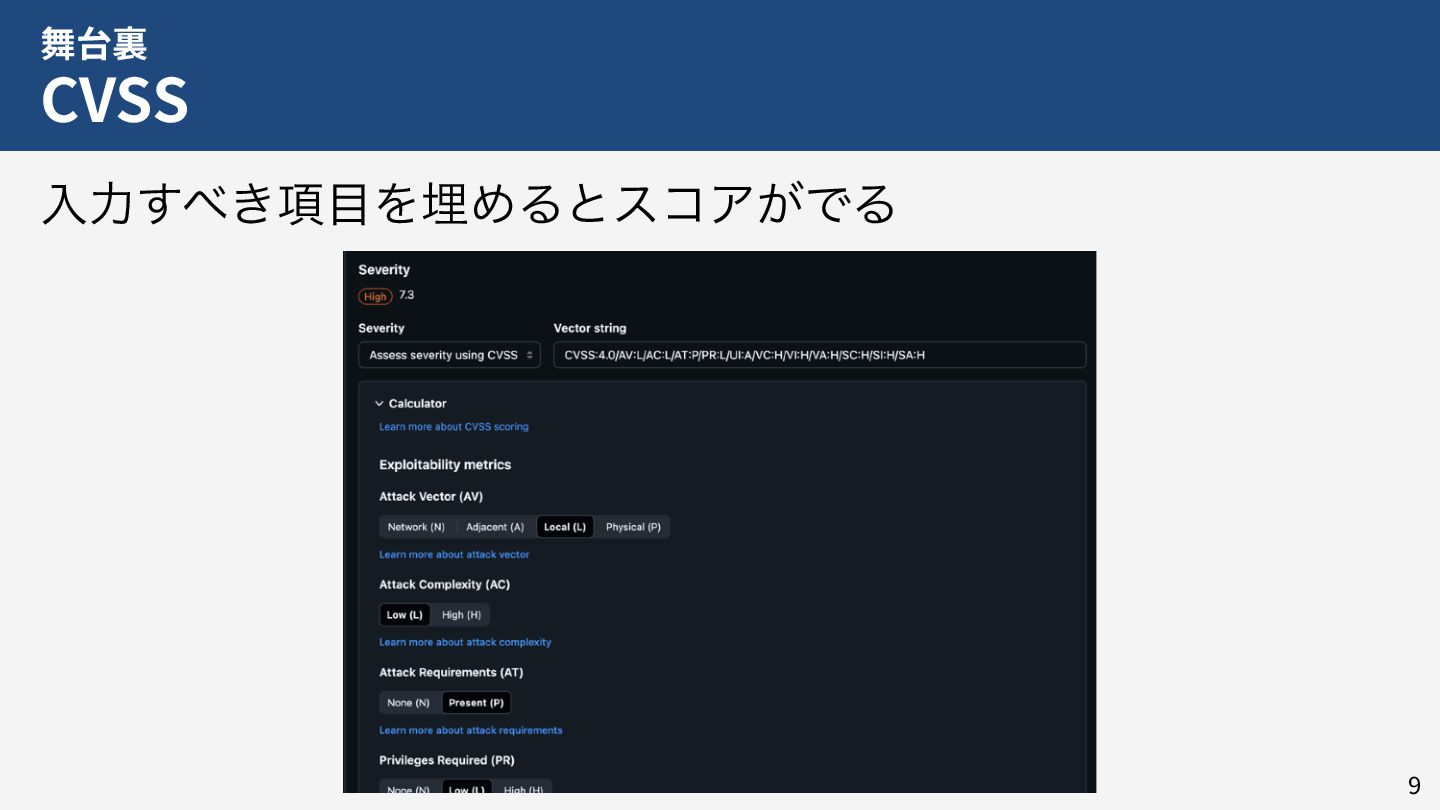
ೖྗ͖߲͢ΛຒΊΔͱείΞ͕ͰΔ 9 舞台裏 CVSS
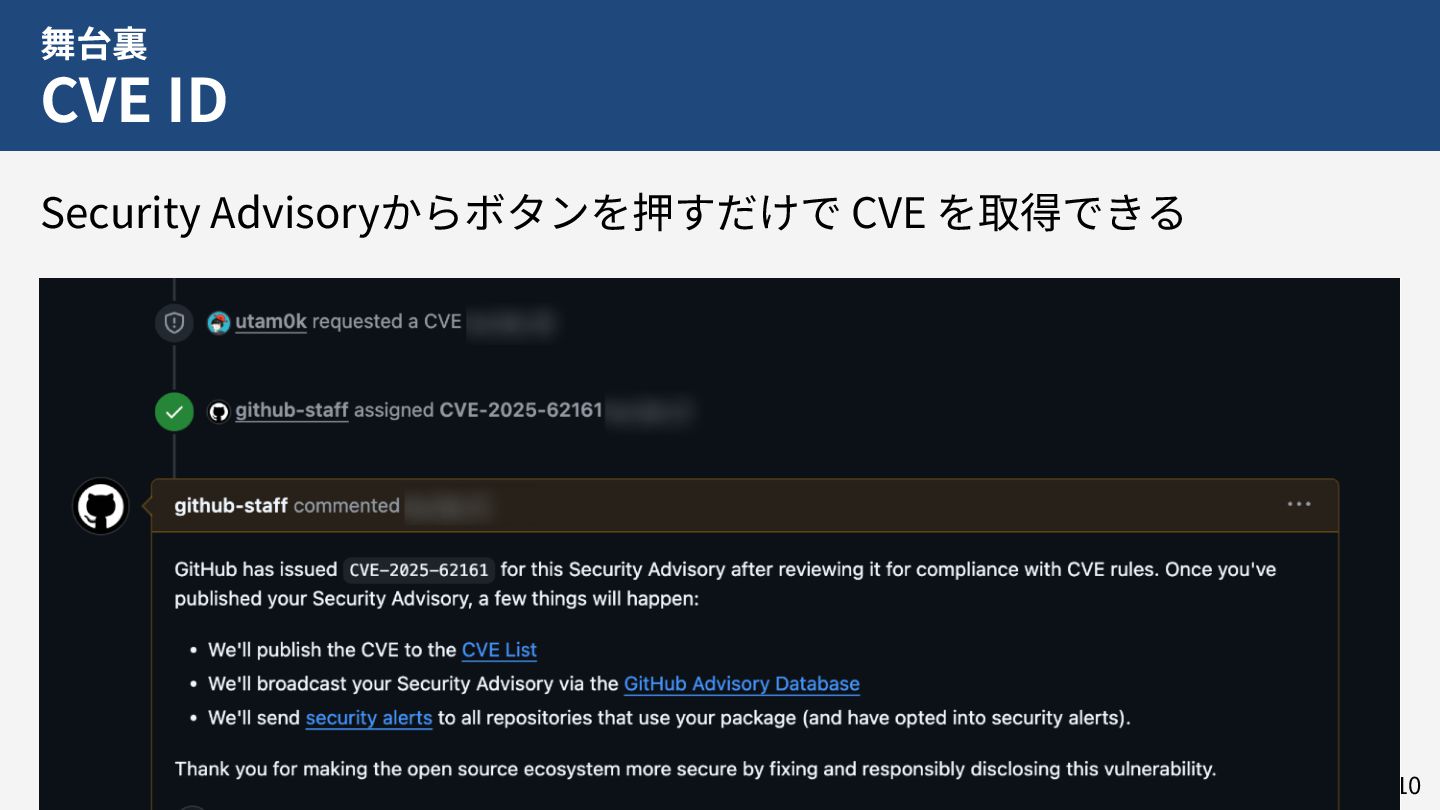
舞台裏 CVE ID Security Advisoryからボタンを押すだけで CVE を取得できる 1 0
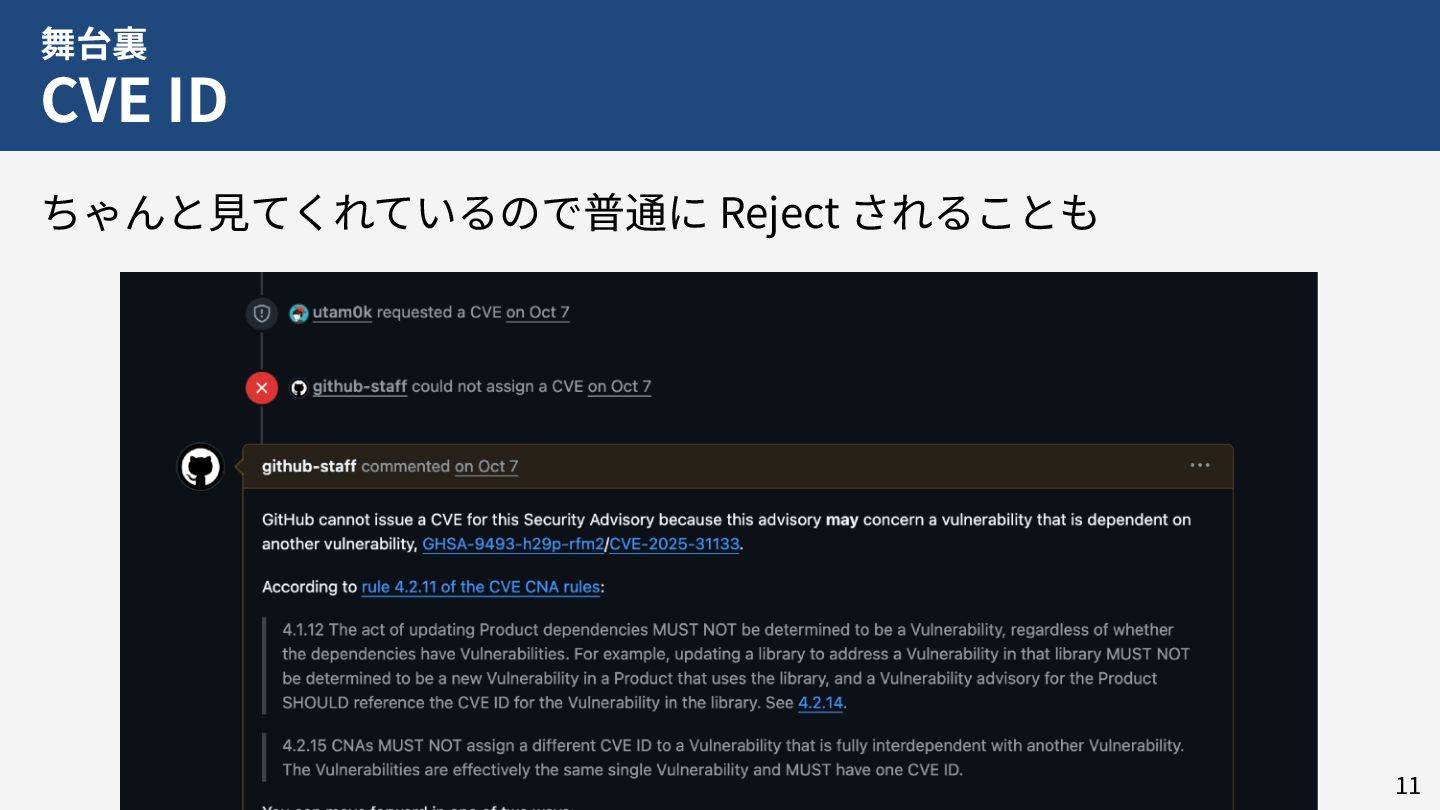
ちゃんと 見 てくれているので普通に Reject されることも 1 1 舞台裏 CVE ID
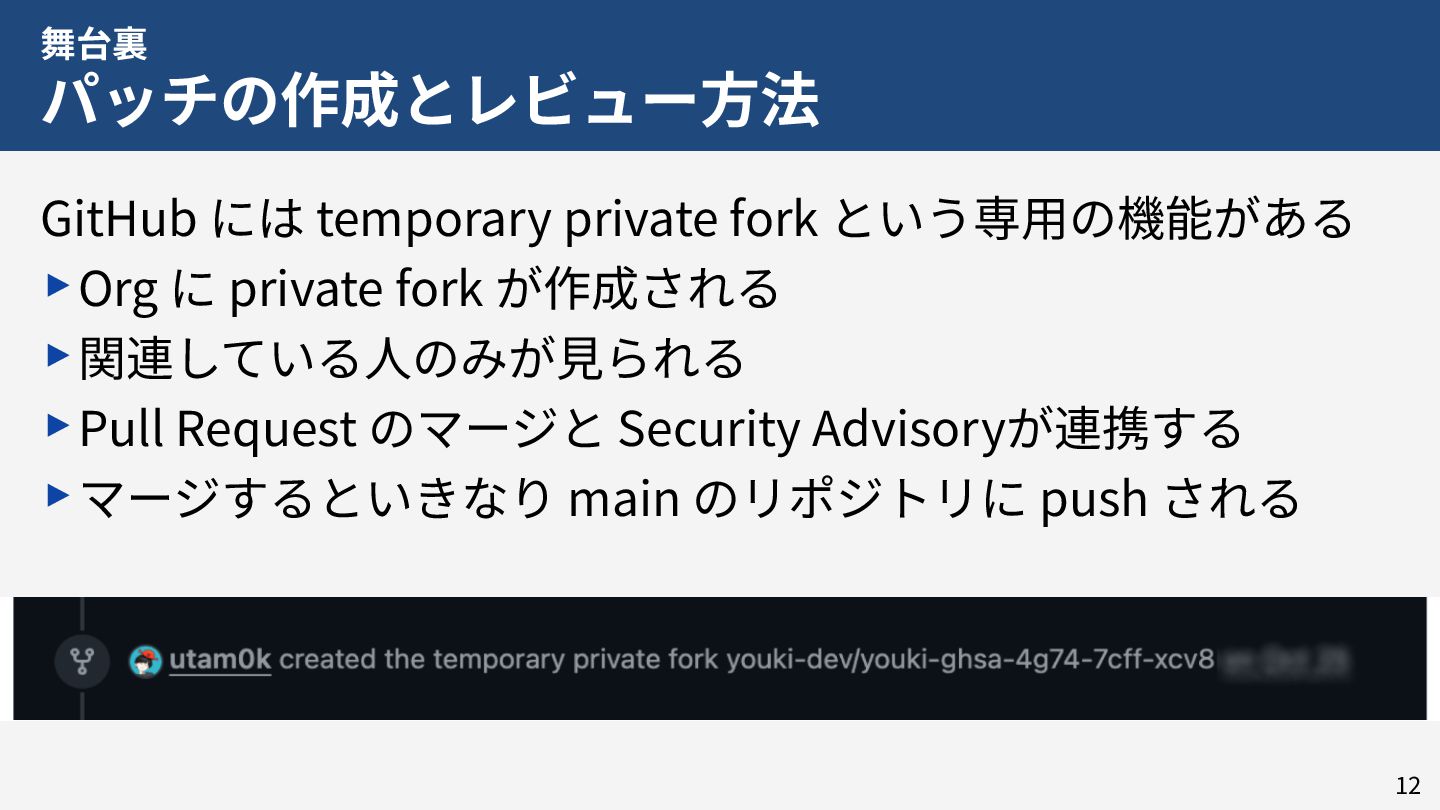
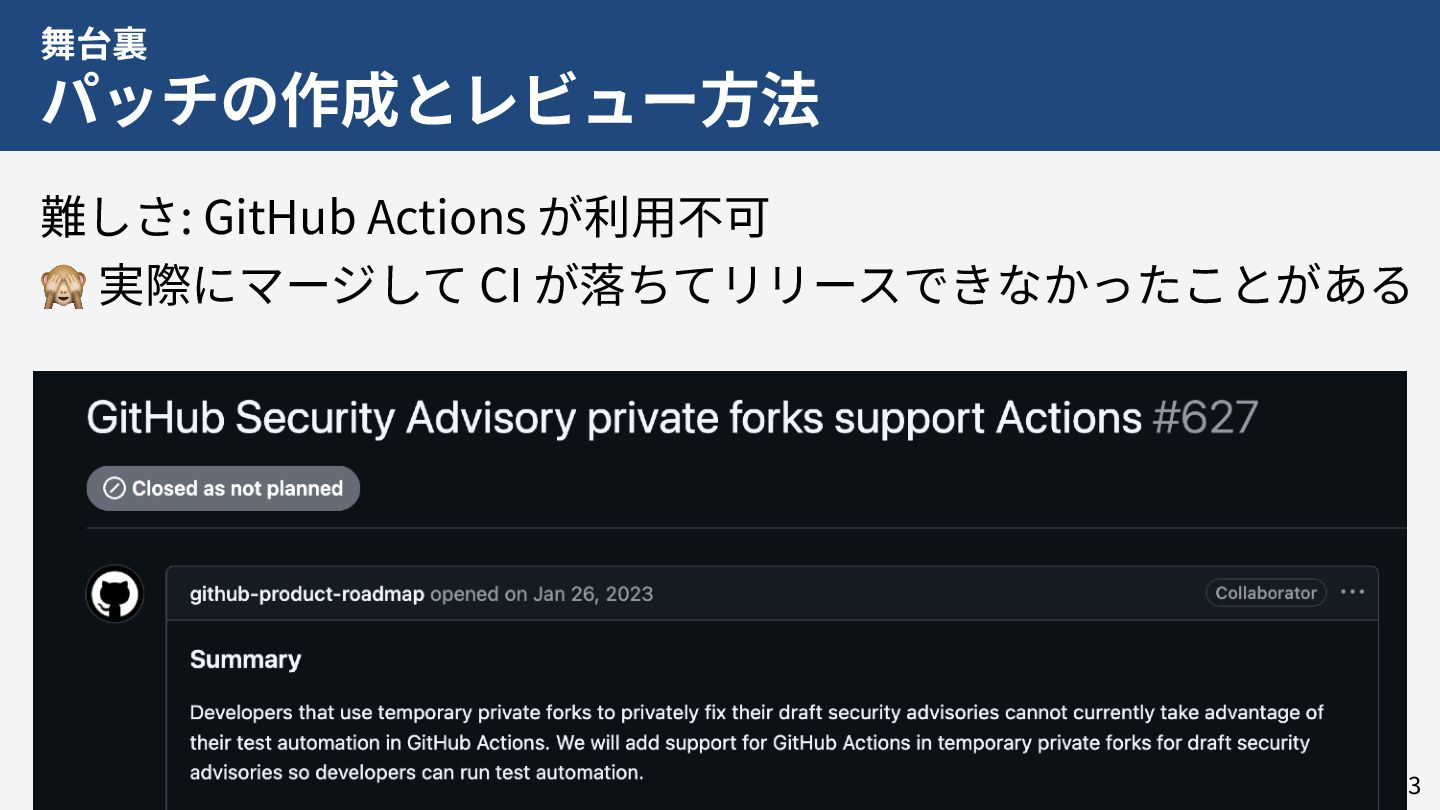
舞台裏 パッチの作成とレビュー 方 法 GitHub には temporary private fork という専
用 の機能がある ‣Org に private fork が作成される ‣関連している 人 のみが 見 られる ‣Pull Request のマージと Security Advisoryが連携する ‣マージするといきなり main のリポジトリに push される 1 2
舞台裏 パッチの作成とレビュー 方 法 難しさ: GitHub Actions が利 用 不可
🙈 実際にマージして CI が落ちてリリースできなかったことがある 1 3
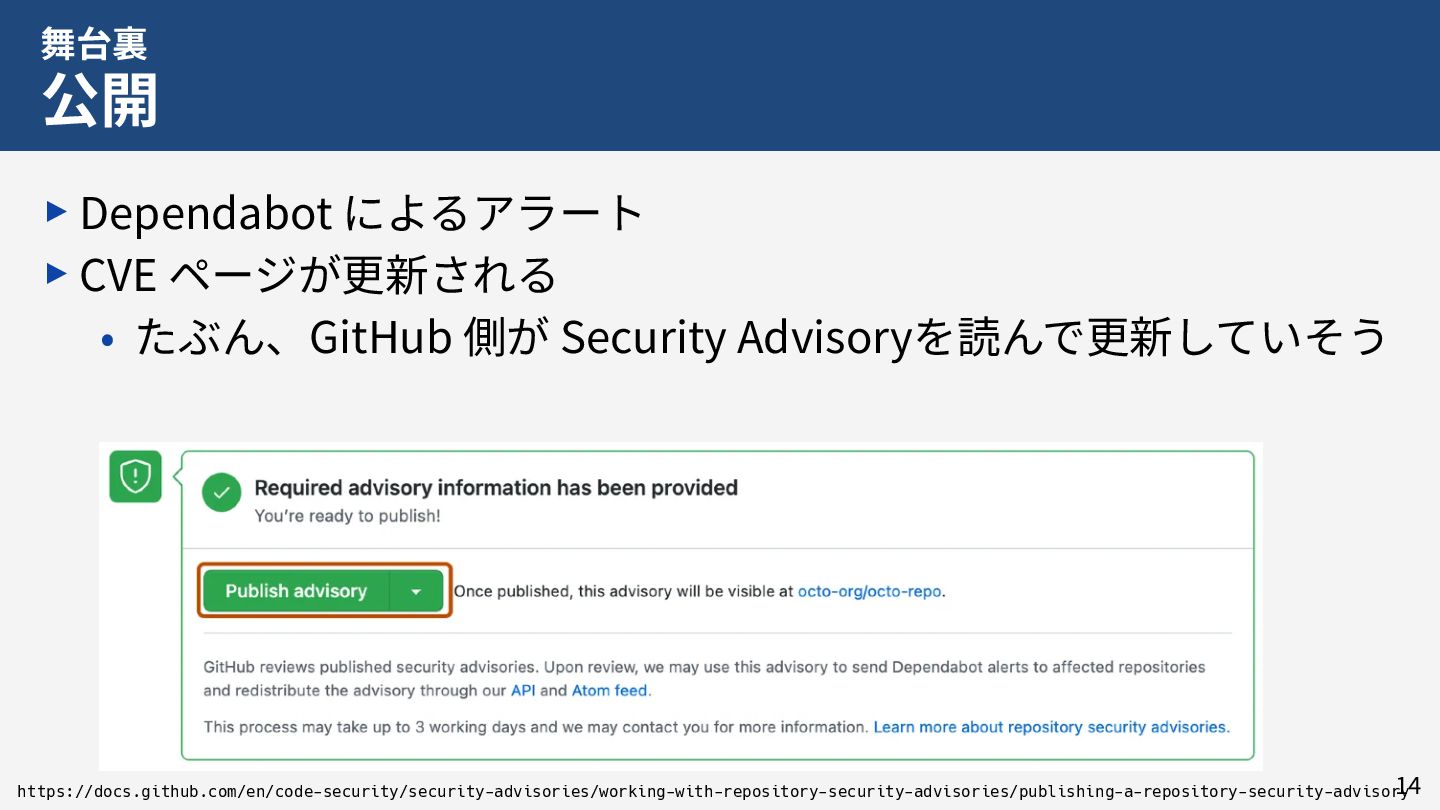
舞台裏 公開 ‣Dependabot によるアラート ‣CVE ページが更新される • たぶん、GitHub 側が Security
Advisoryを読んで更新していそう 1 4 https://docs.github.com/en/code-security/security-advisories/working-with-repository-security-advisories/publishing-a-repository-security-advisory
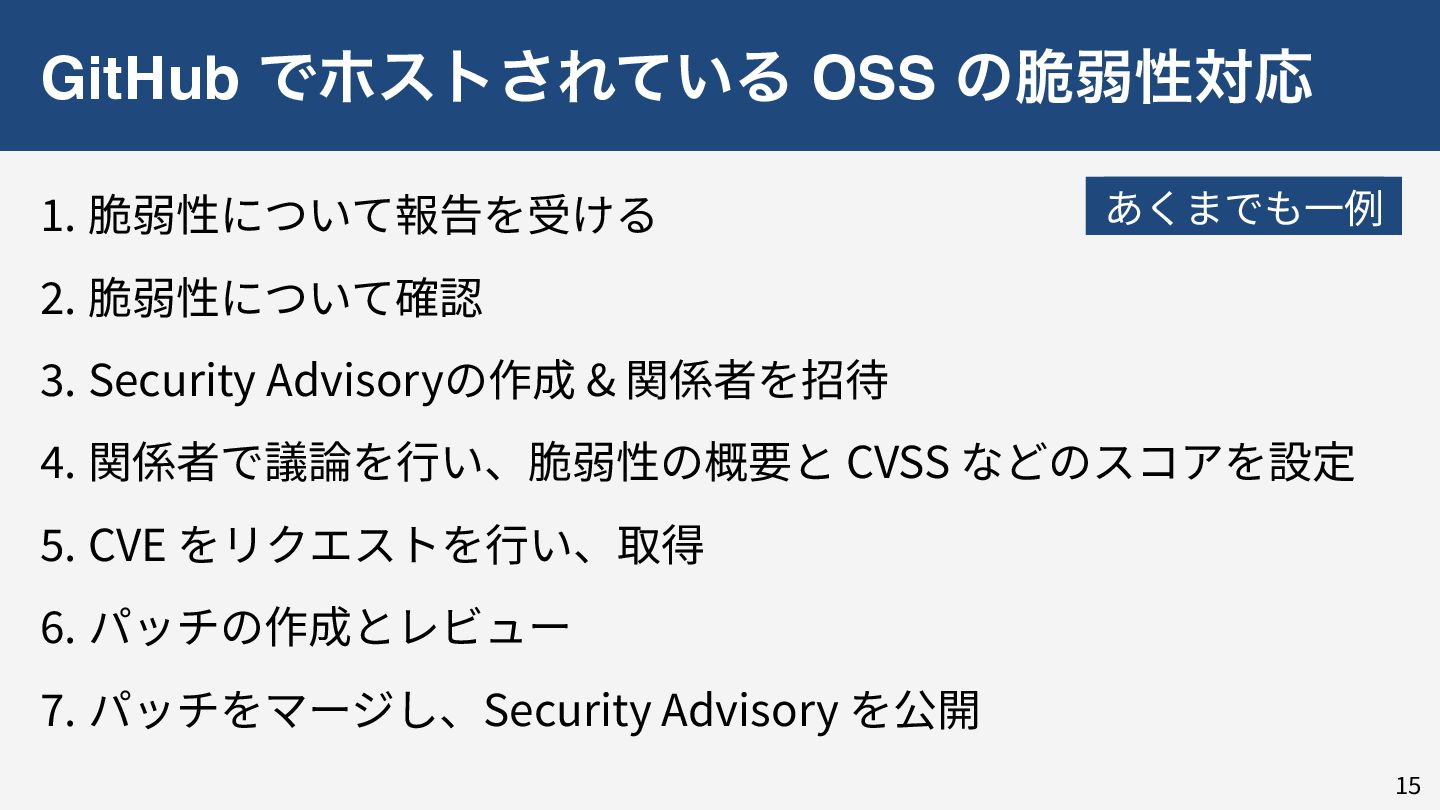
GitHub Ͱϗετ͞Ε͍ͯΔ OSS ͷ੬ऑੑରԠ 1 . 脆弱性について報告を受ける 2 . 脆弱性について確認
3 . Security Advisoryの作成 & 関係者を招待 4 . 関係者で議論を 行 い、脆弱性の概要と CVSS などのスコアを設定 5 . CVE をリクエストを 行 い、取得 6 . パッチの作成とレビュー 7 . パッチをマージし、Security Advisory を公開 1 5 あくまでも 一 例
おしまい 16


 utam0k
 garrettdimon
 apolaine
 konakalab
 sabderemane
 tmiket
 kevinliebholz
 chriscoyier
 varn
 portentint
 rkendrick25
 inesmontani
 baasie