Share
Embed
Transcript
82 slides
-
AIS3 ★ Introduction - What’s APT ‣ Purpose, Target ‣
Case study ★ Red Team Technical ‣ Discovery ‣ Lateral movement ‣ Privilege escalation Content ★ Basic Forensic ‣ System Forensic ‣ Traffic Forensic ‣ Malware Reverse -
AIS3 ★ Advanced Persistent Threat ★ A stealthy threat actor,
which gains unauthorized access to a computer network and remains undetected for an extended period. [ ★ Cyber crime VS APT group VS security researcher What’s APT -
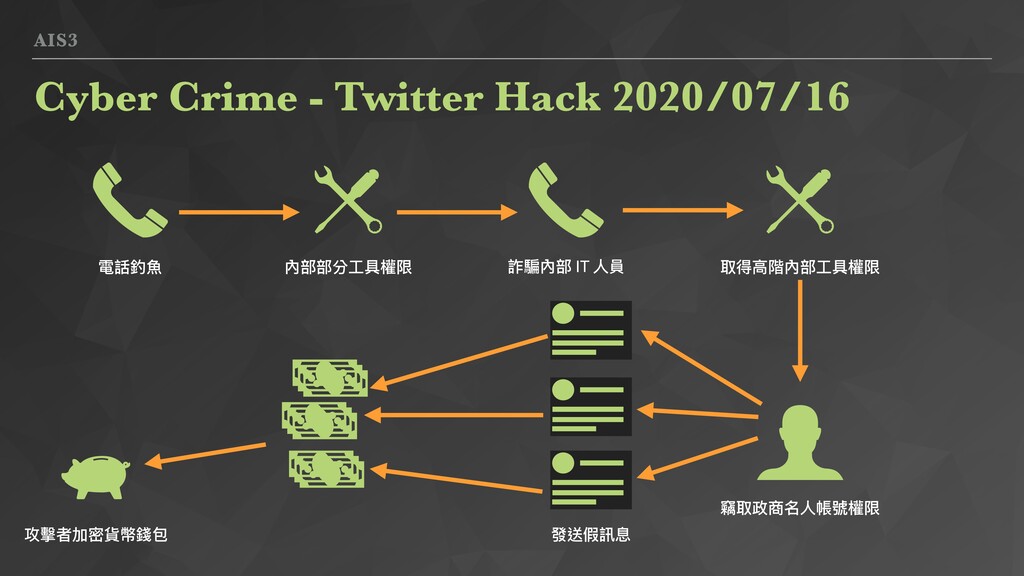
AIS3 Cyber Crime - Twitter Hack 2020/07/16 電話釣⿂ 內部部分⼯具權限 取得⾼階內部⼯具權限
詐騙內部 IT ⼈員 竊取政商名⼈帳號權限 發送假訊息 攻擊者加密貨幣錢包 -
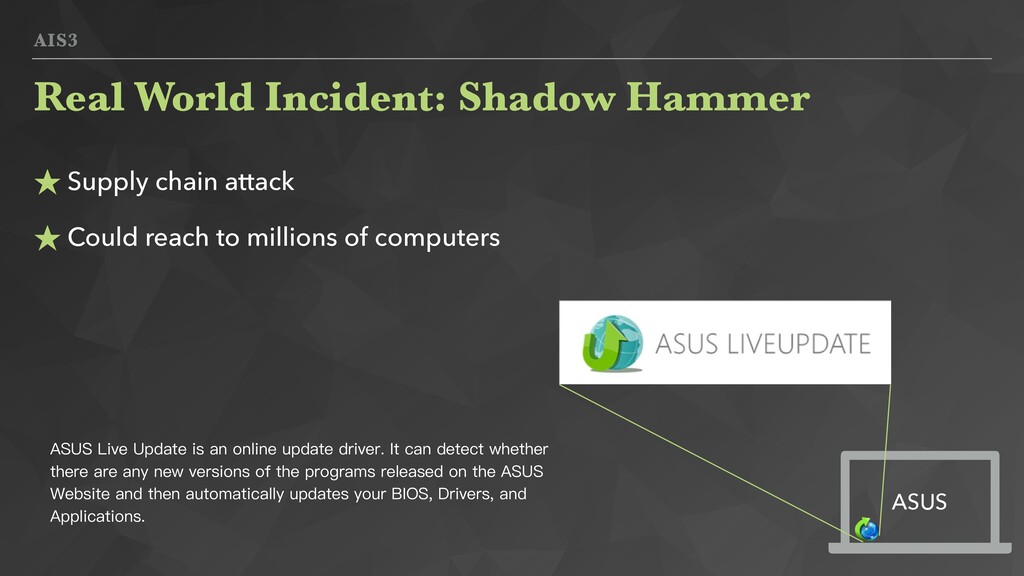
AIS3 ★ Supply chain attack ★ Could reach to millions
of computers Real World Incident: Shadow Hammer ASUS ASUS Live Update is an online update driver. It can detect whether there are any new versions of the programs released on the ASUS Website and then automatically updates your BIOS, Drivers, and Applications. -
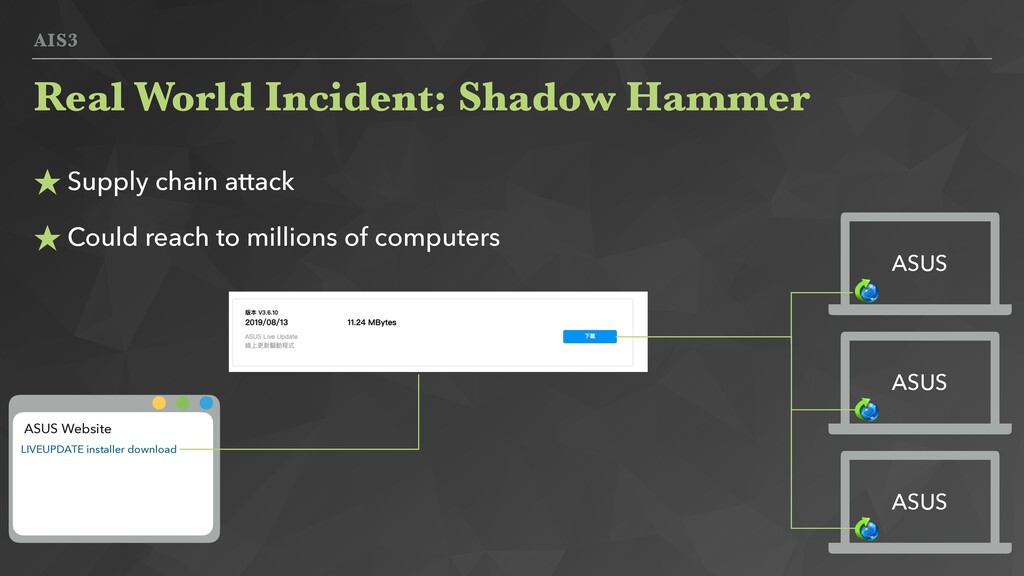
AIS3 ★ Supply chain attack ★ Could reach to millions
of computers Real World Incident: Shadow Hammer ASUS LIVEUPDATE installer download ASUS Website ASUS ASUS -
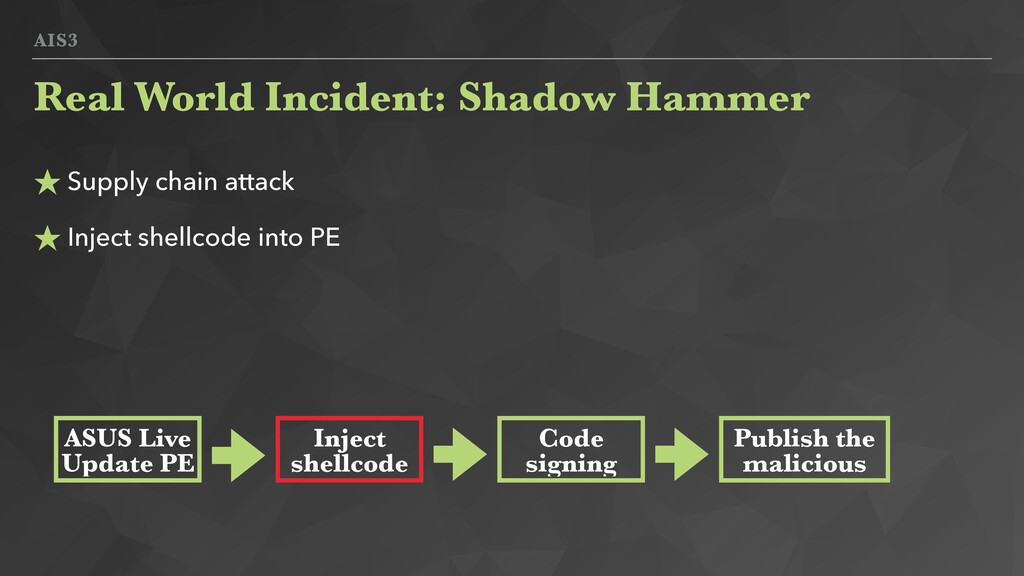
AIS3 ★ Supply chain attack ★ Inject shellcode into PE
Real World Incident: Shadow Hammer ASUS Live Update PE Inject shellcode Code signing Publish the malicious -
AIS3 ★ Supply chain attack ★ Could reach to millions
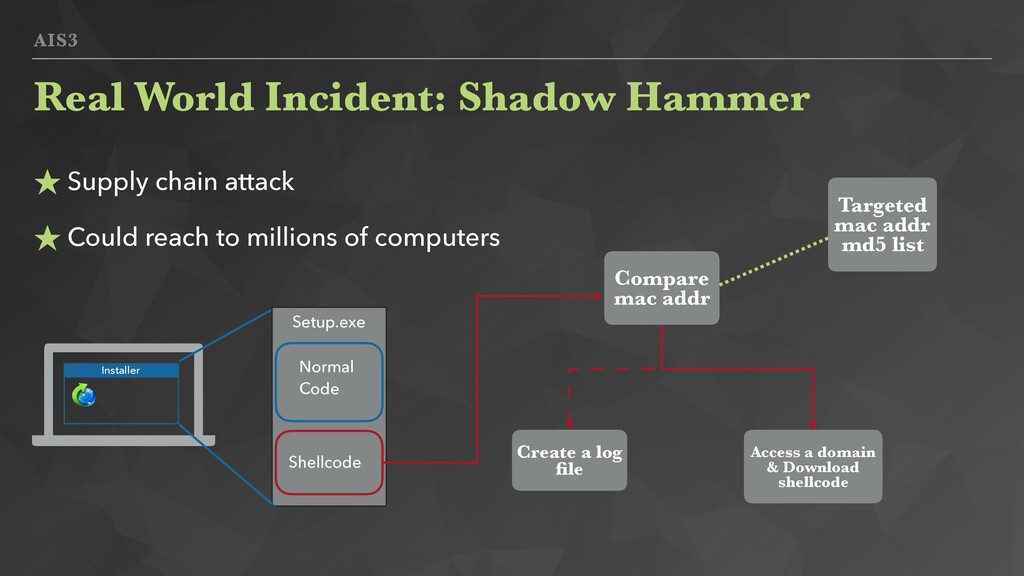
of computers Real World Incident: Shadow Hammer Installer Setup.exe Normal Code Shellcode Compare mac addr Create a log file Access a domain & Download shellcode Targeted mac addr md5 list -
AIS3 Real World Incident: Shadow Hammer Installer Setup.exe Normal Code
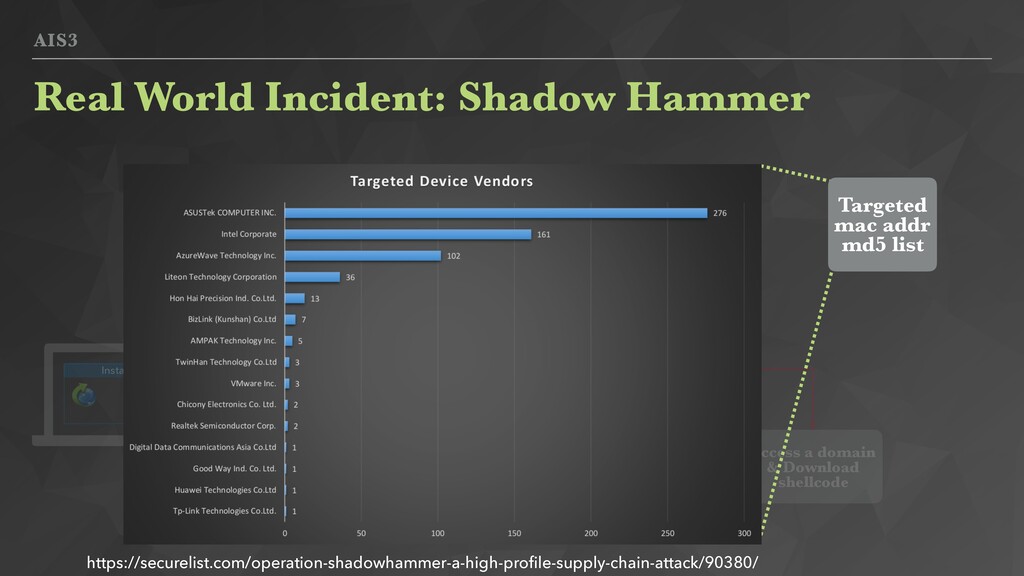
Shellcode Compare mac addr Create a log file Access a domain & Download shellcode Targeted mac addr md5 list https://securelist.com/operation-shadowhammer-a-high-profile-supply-chain-attack/90380/ -
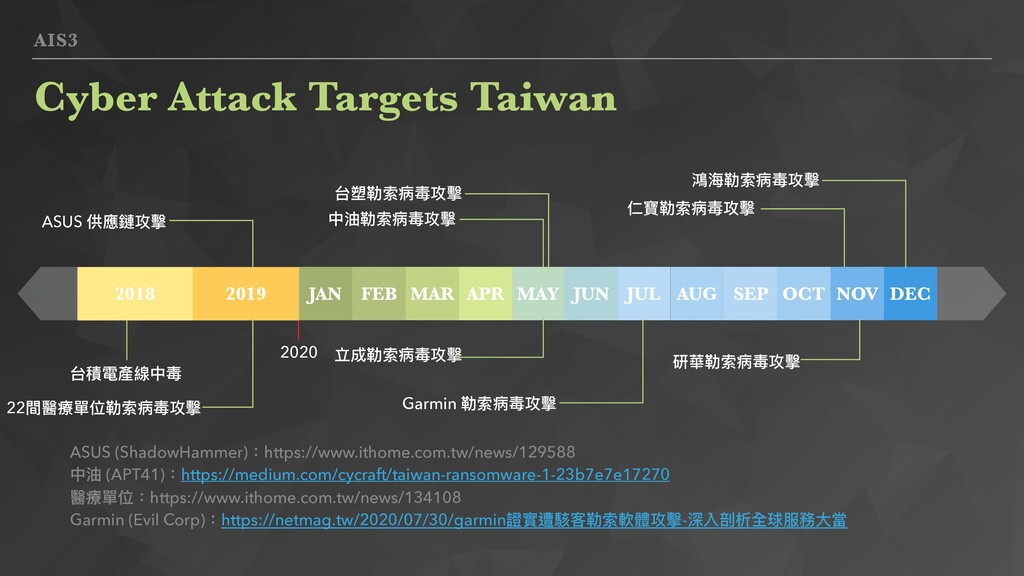
AIS3 Cyber Attack Targets Taiwan JAN DEC NOV JUL SEP
AUG OCT JUN MAY APR MAR FEB 中油勒索病毒攻擊 ASUS (ShadowHammer):https://www.ithome.com.tw/news/129588 中油 (APT41):https://medium.com/cycraft/taiwan-ransomware-1-23b7e7e17270 醫療單位:https://www.ithome.com.tw/news/134108 Garmin (Evil Corp):https://netmag.tw/2020/07/30/garmin證實遭駭客勒索軟體攻擊-深入剖析全球服務⼤當 台塑勒索病毒攻擊 Garmin 勒索病毒攻擊 仁寶勒索病毒攻擊 2018 2019 2020 台積電產線中毒 ASUS 供應鏈攻擊 研華勒索病毒攻擊 鴻海勒索病毒攻擊 立成勒索病毒攻擊 22間醫療單位勒索病毒攻擊 -
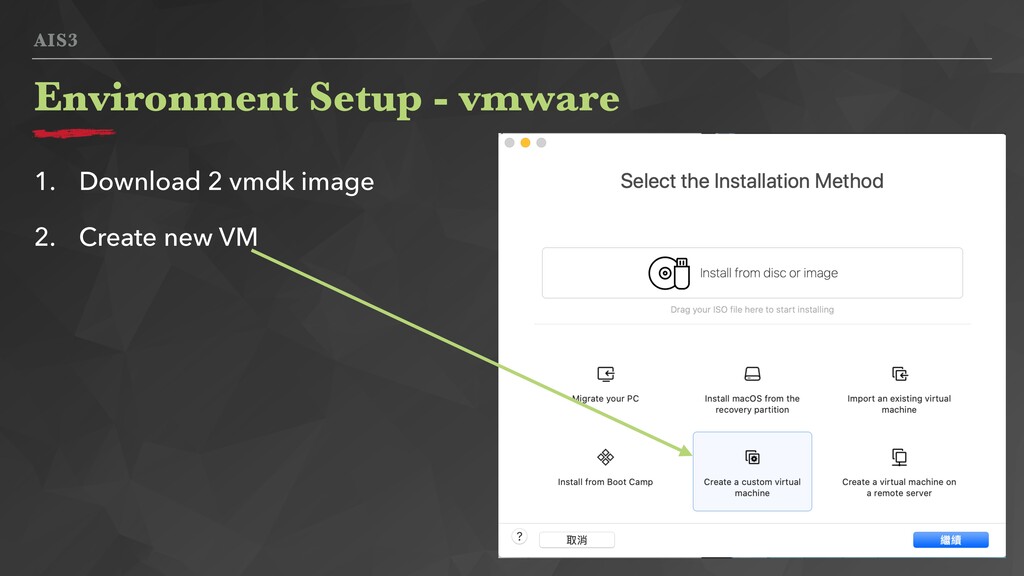
AIS3 1. Download 2 vmdk image 2. Create new VM
Environment Setup - vmware -
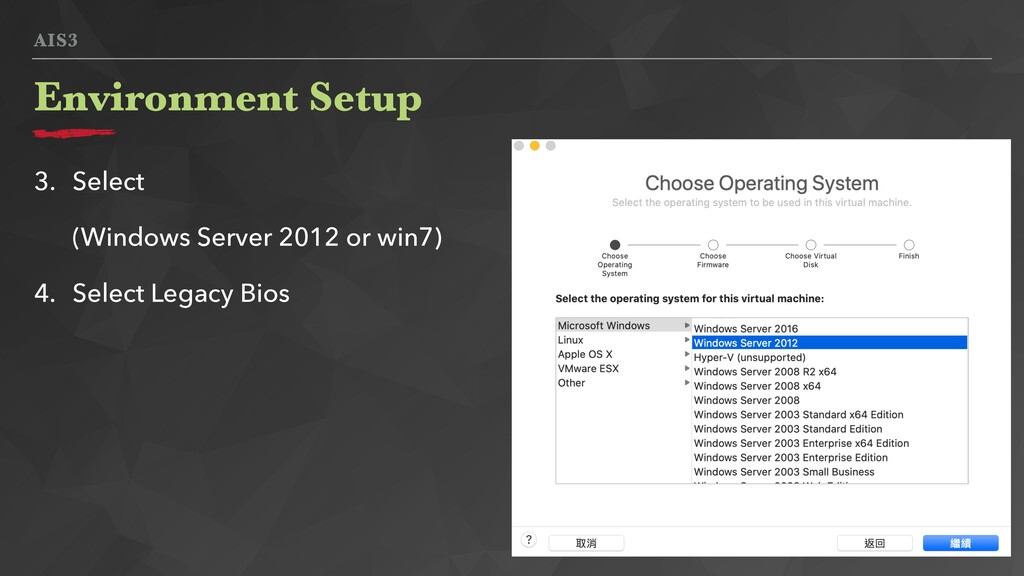
AIS3 Environment Setup 3. Select (Windows Server 2012 or win7)
4. Select Legacy Bios -
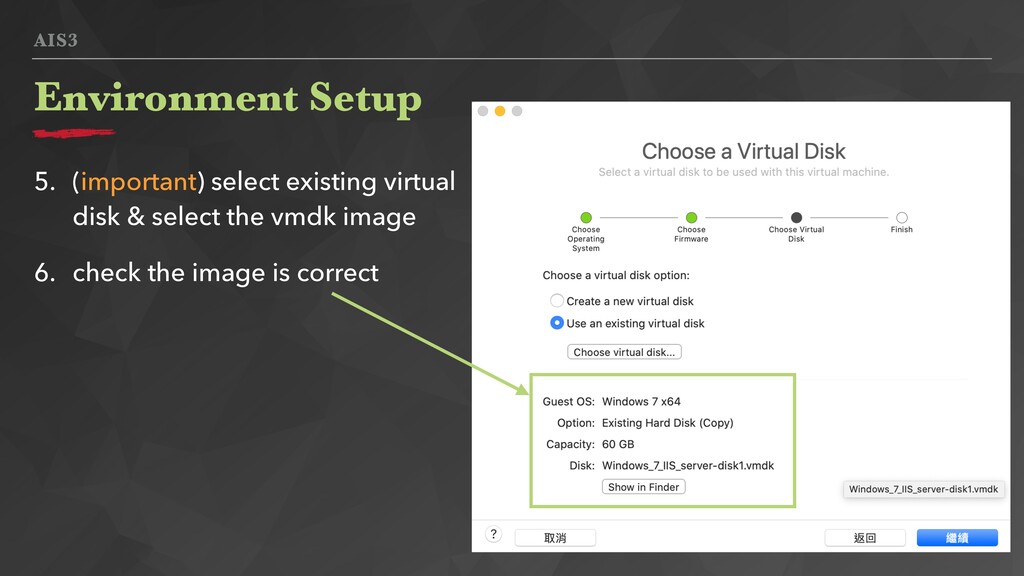
AIS3 Environment Setup 5. (important) select existing virtual disk &
select the vmdk image 6. check the image is correct -
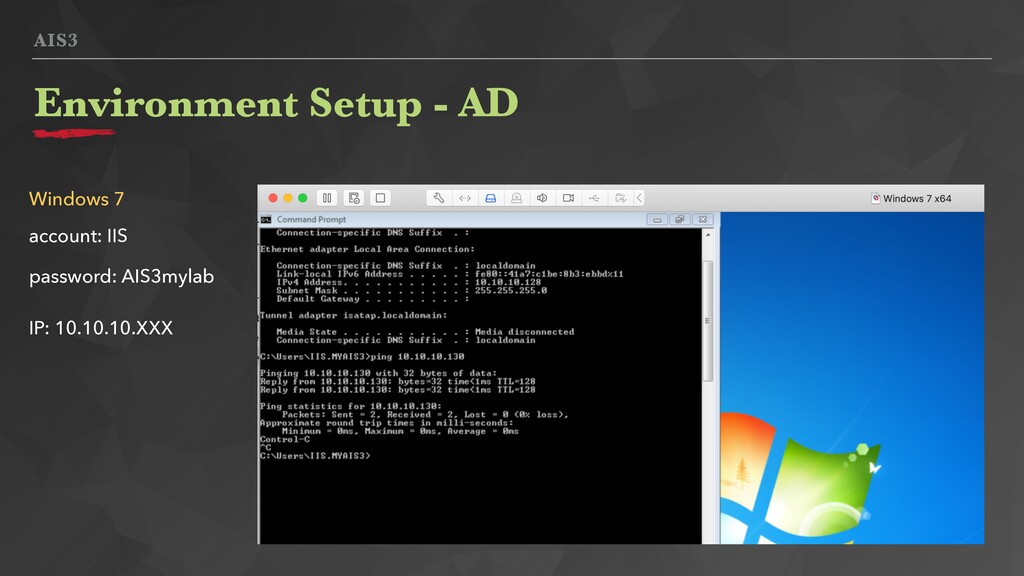
AIS3 Environment Setup - AD Windows 7 IP: 10.10.10.XXX account:
IIS password: AIS3mylab -
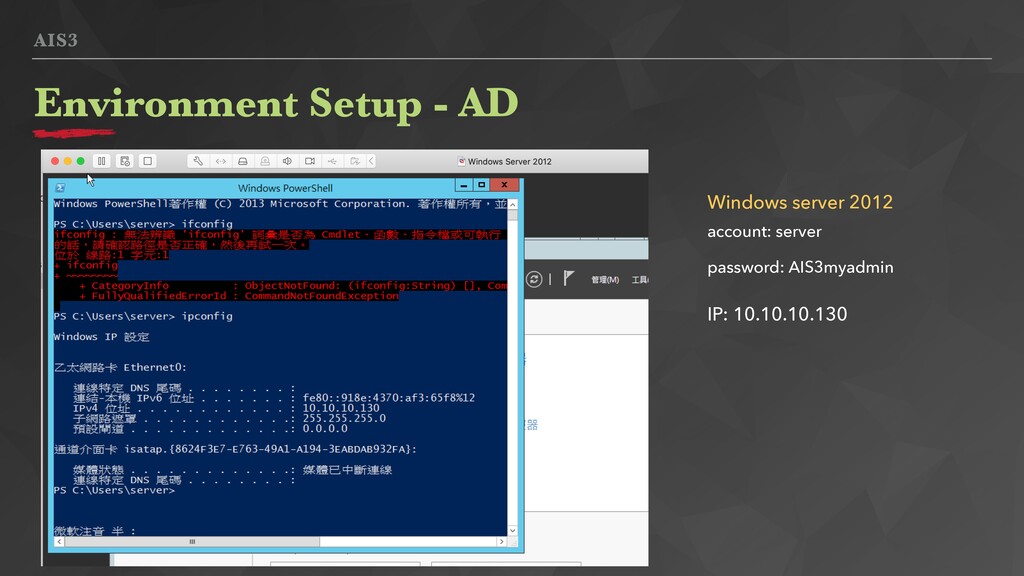
AIS3 Environment Setup - AD Windows server 2012 IP: 10.10.10.130
account: server password: AIS3myadmin -
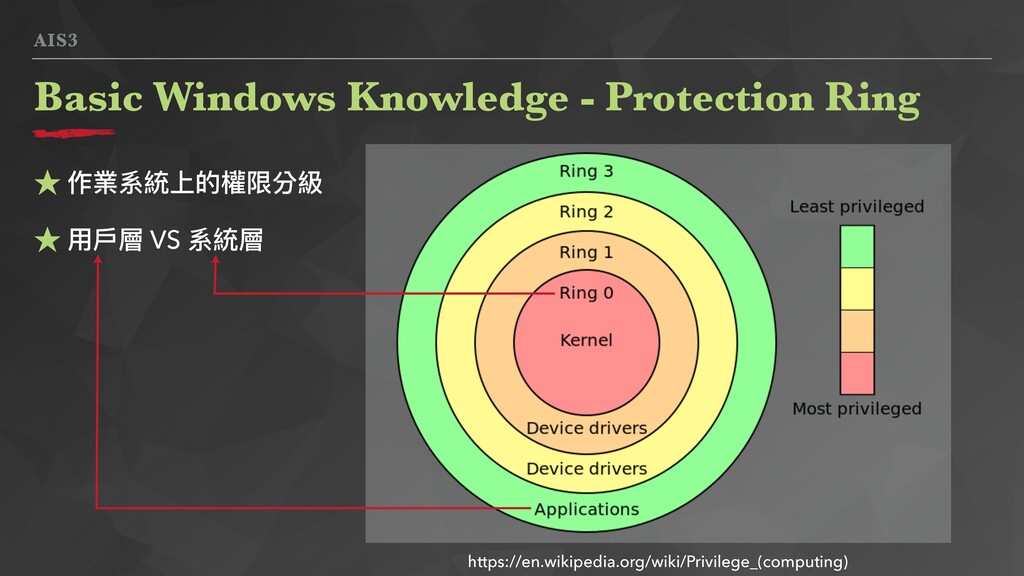
AIS3 Basic Windows Knowledge - Protection Ring ★ 作業系統上的權限分級 ★
⽤⼾層 VS 系統層 https://en.wikipedia.org/wiki/Privilege_(computing) -
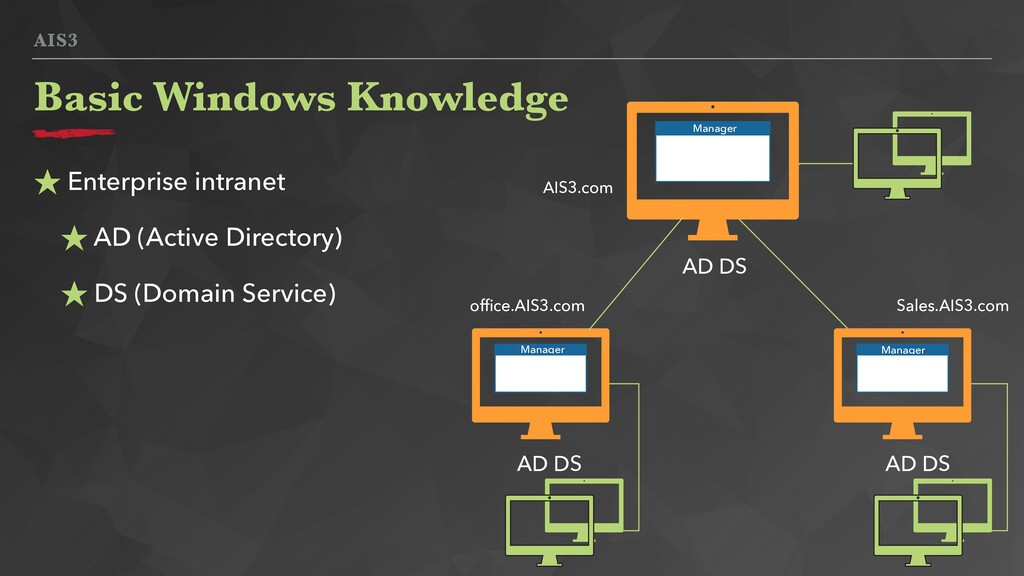
AIS3 ★ Enterprise intranet ★ AD (Active Directory) ★ DS
(Domain Service) Basic Windows Knowledge AD DS Manager AD DS Manager AD DS Manager AIS3.com office.AIS3.com Sales.AIS3.com -
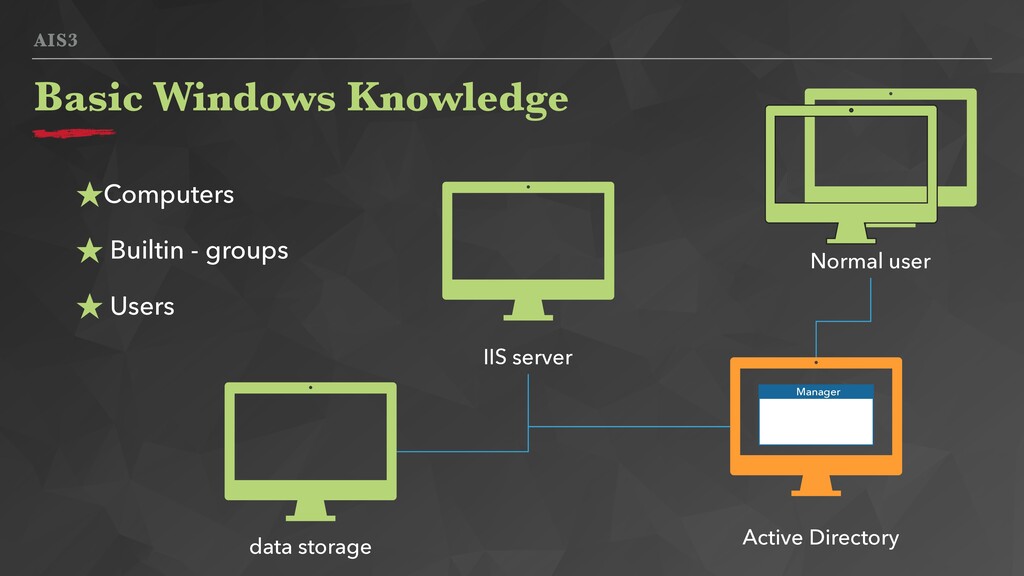
AIS3 Basic Windows Knowledge Active Directory IIS server data storage
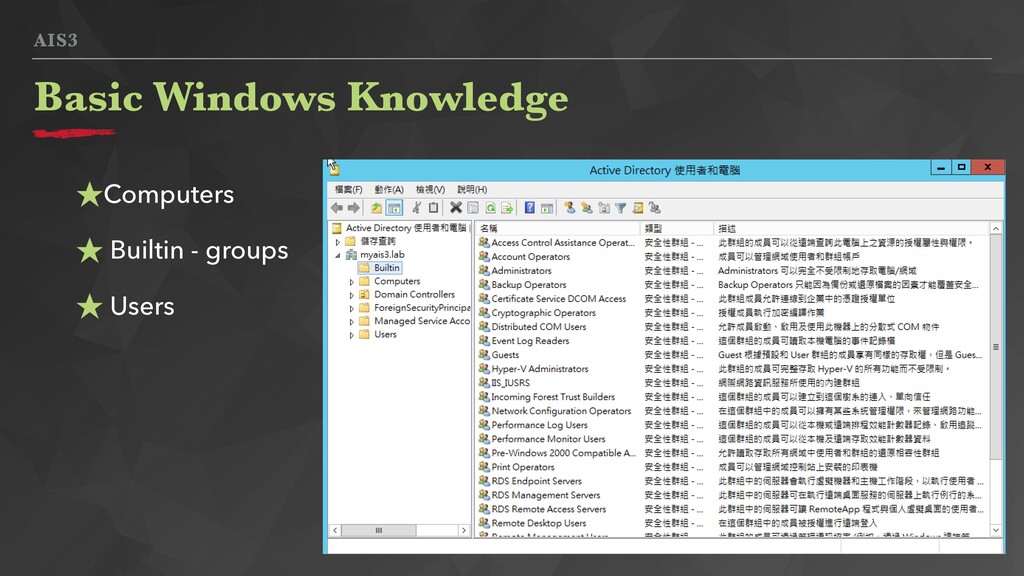
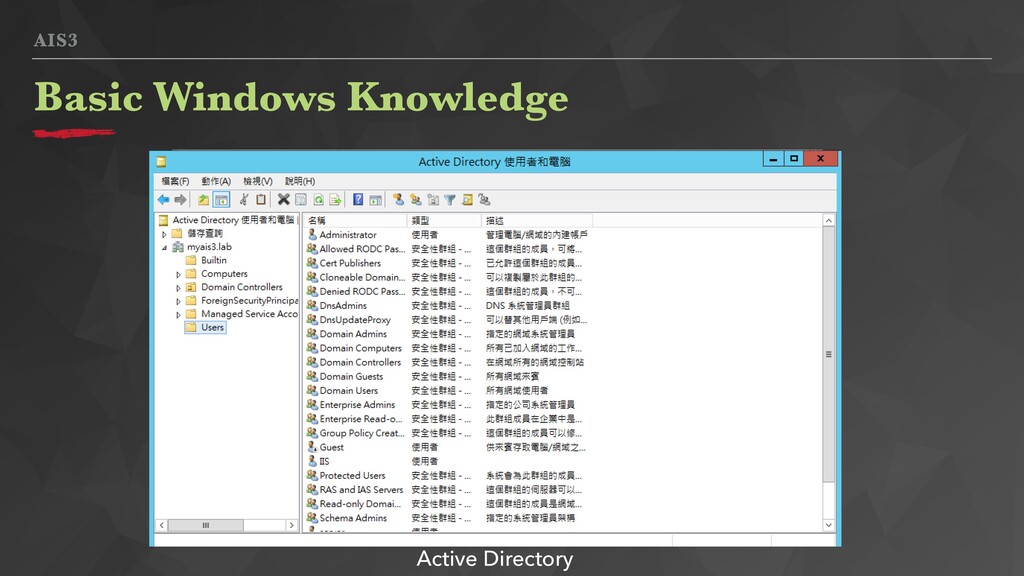
Normal user Manager ★Computers ★ Builtin - groups ★ Users -
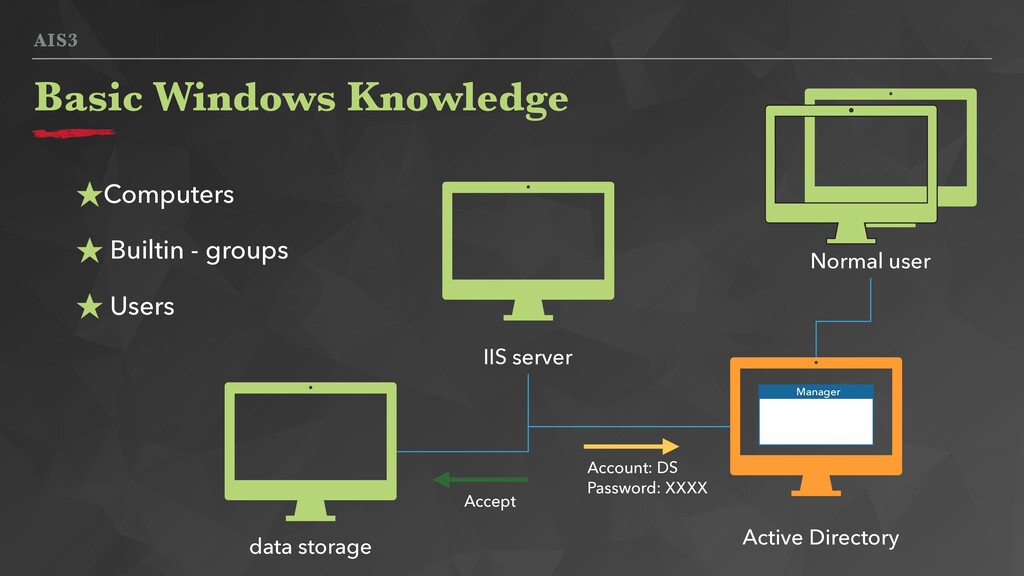
AIS3 Basic Windows Knowledge Active Directory IIS server data storage
Normal user Manager ★Computers ★ Builtin - groups ★ Users Account: DS Password: XXXX Accept -
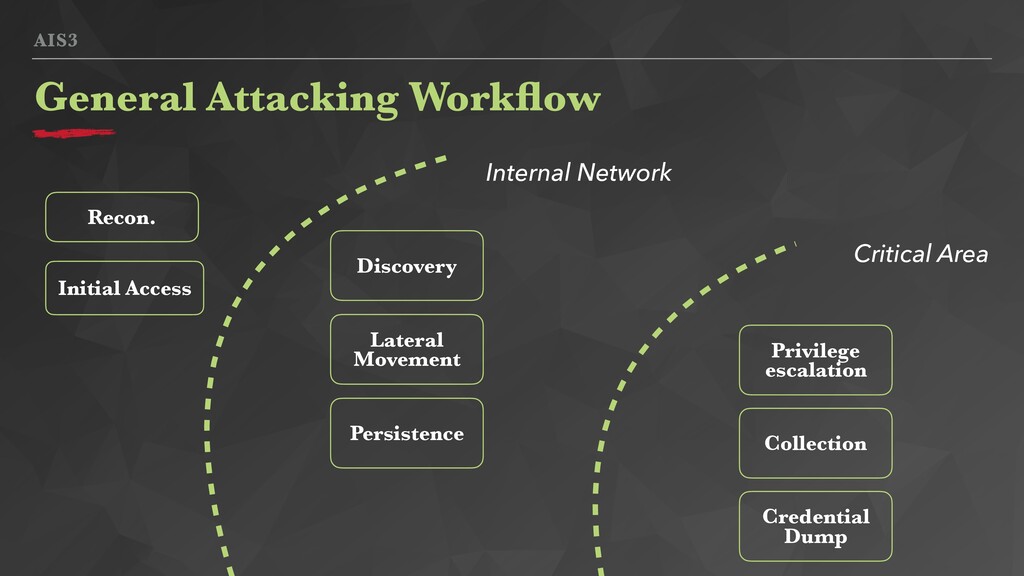
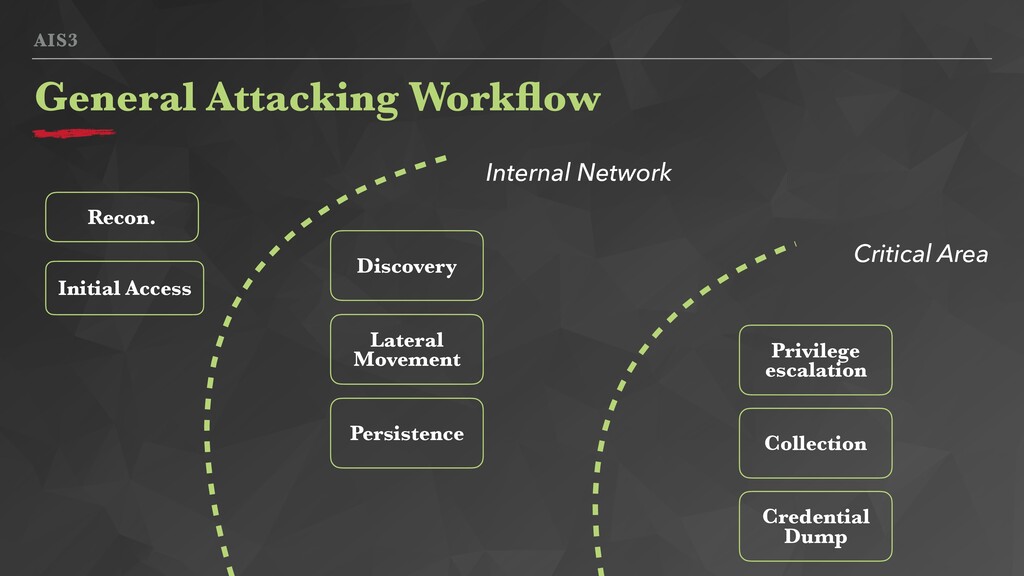
AIS3 General Attacking Workflow Lateral Movement Privilege escalation Credential Dump
Persistence Critical Area Internal Network Initial Access Recon. Collection Discovery -
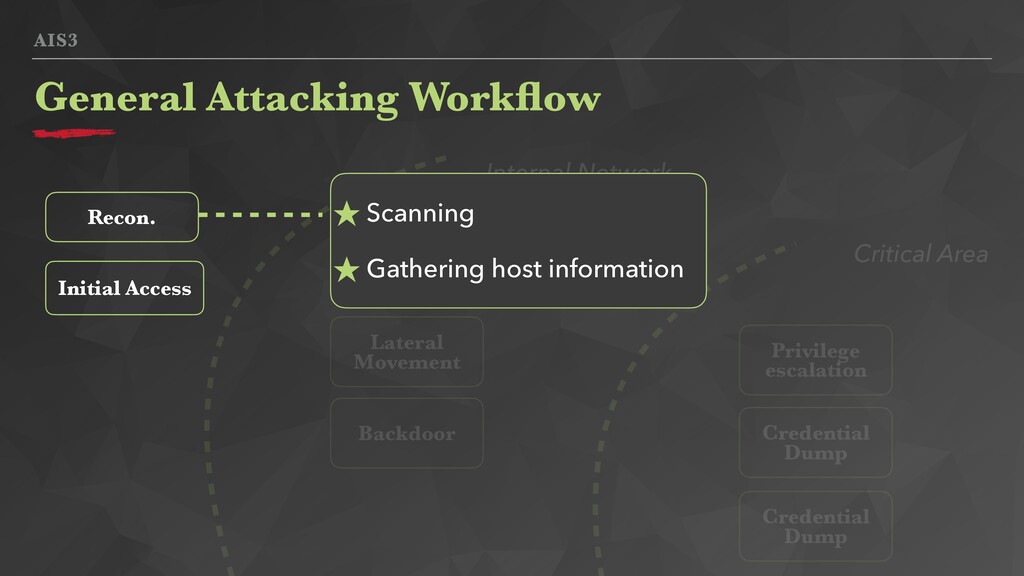
AIS3 General Attacking Workflow Initial Access Inside Information gathering Lateral
Movement Privilege escalation Credential Dump Credential Dump Backdoor Recon. Critical Area Internal Network ★ Scanning ★ Gathering host information -
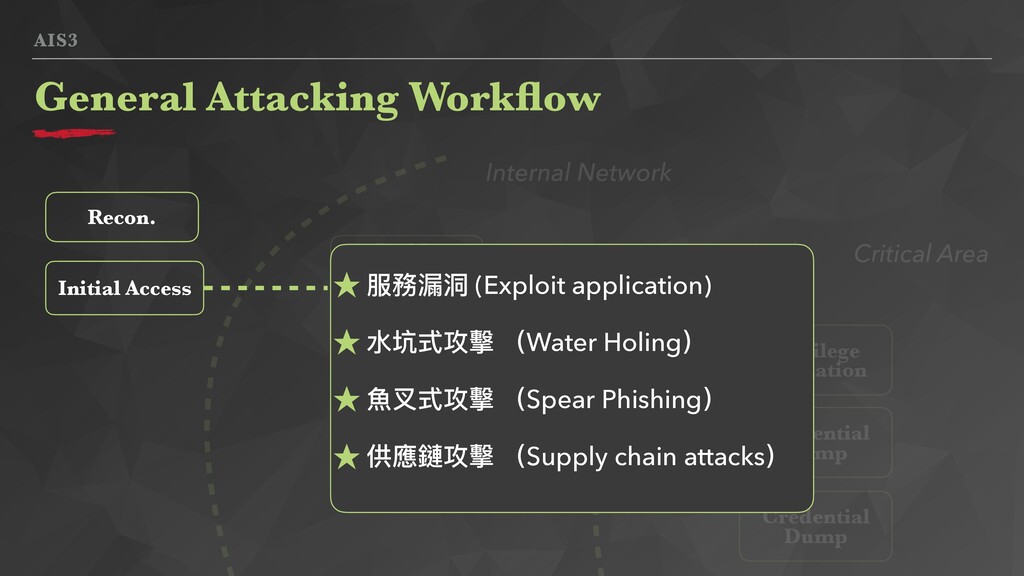
AIS3 General Attacking Workflow Initial Access Inside Information gathering Lateral
Movement Privilege escalation Credential Dump Credential Dump Backdoor Recon. Critical Area Internal Network ★ 服務漏洞 (Exploit application) ★ ⽔坑式攻擊 (Water Holing) ★ ⿂叉式攻擊 (Spear Phishing) ★ 供應鏈攻擊 (Supply chain attacks) -
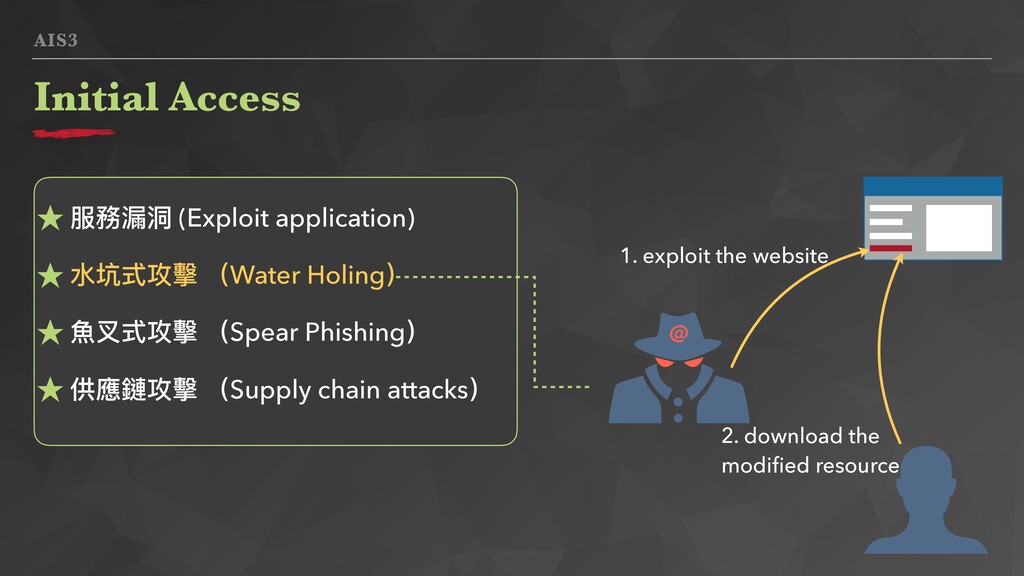
AIS3 Initial Access ★ 服務漏洞 (Exploit application) ★ ⽔坑式攻擊 (Water
Holing) ★ ⿂叉式攻擊 (Spear Phishing) ★ 供應鏈攻擊 (Supply chain attacks) 1. exploit the website 2. download the modified resource -
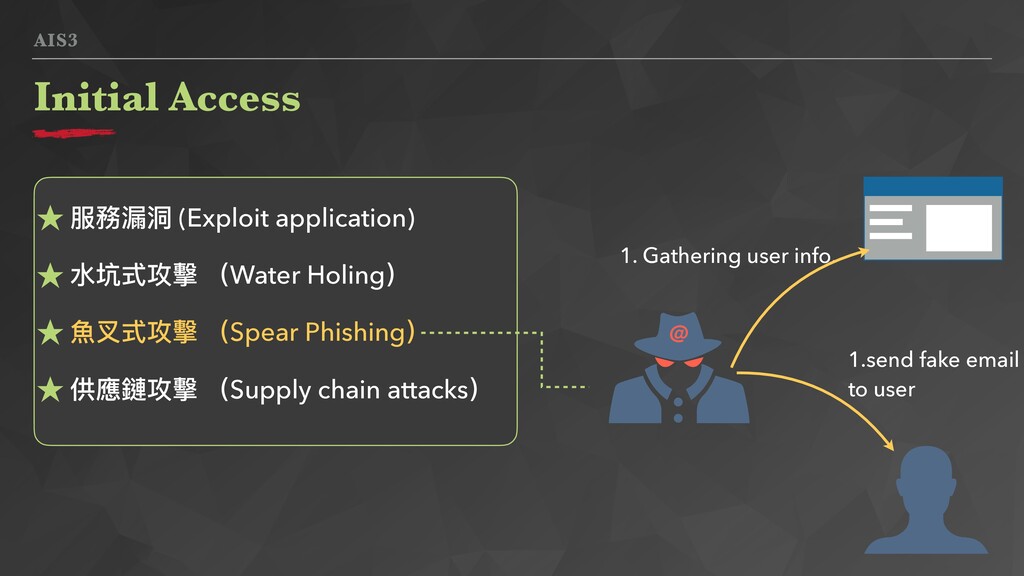
AIS3 Initial Access ★ 服務漏洞 (Exploit application) ★ ⽔坑式攻擊 (Water
Holing) ★ ⿂叉式攻擊 (Spear Phishing) ★ 供應鏈攻擊 (Supply chain attacks) 1. Gathering user info. 1.send fake email to user -
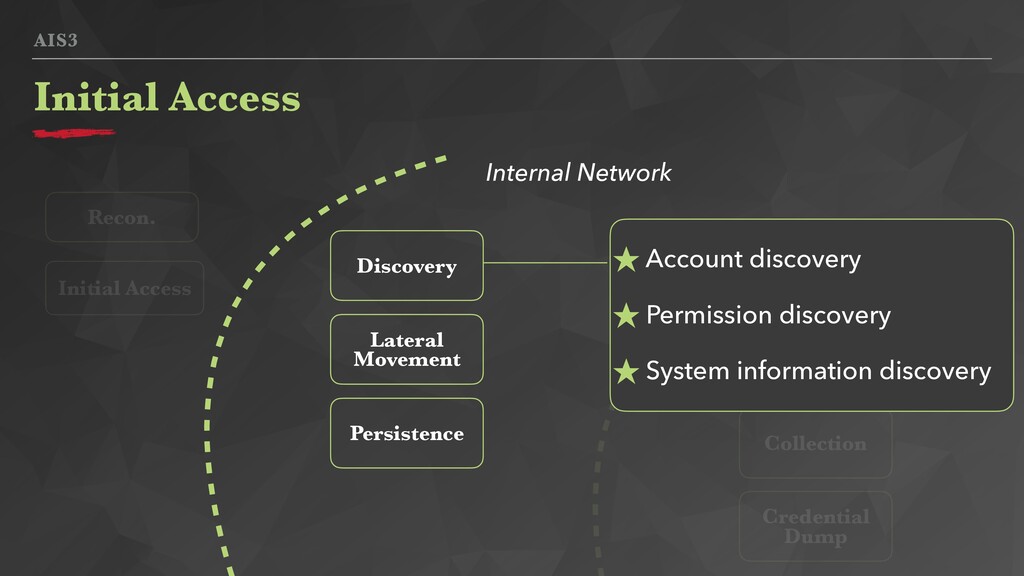
AIS3 Initial Access Lateral Movement Privilege escalation Credential Dump Persistence
Critical Area Internal Network Initial Access Recon. Collection Discovery ★ Account discovery ★ Permission discovery ★ System information discovery -
AIS3 ★ Find Domain ★ Find AD ip address ★
Find all user in the domain LAB0 - Find ME -
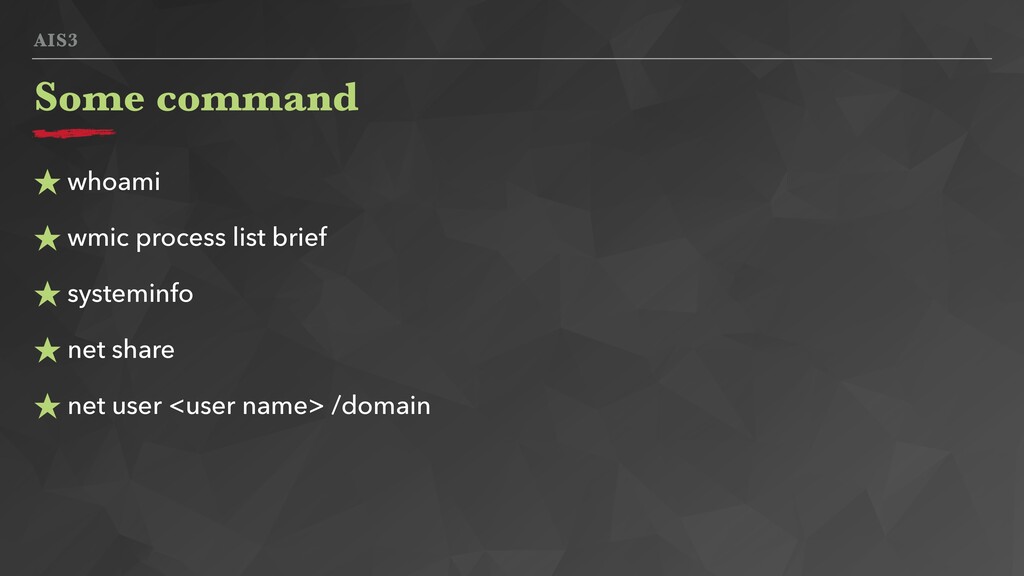
AIS3 ★ whoami ★ wmic process list brief ★ systeminfo
★ net share ★ net user <user name> /domain Some command -
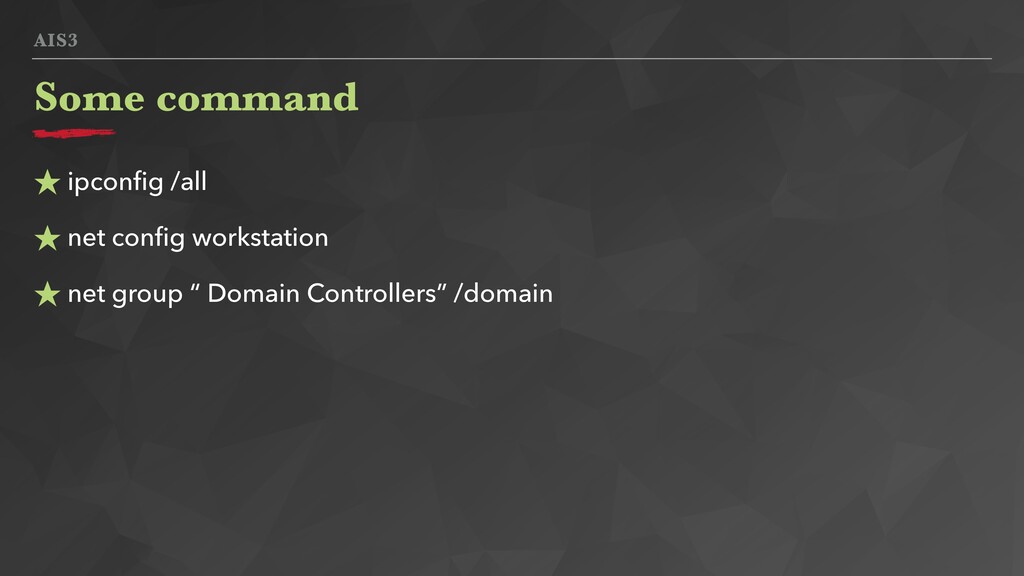
AIS3 ★ ipconfig /all ★ net config workstation ★ net
group “ Domain Controllers” /domain Some command -
AIS3 General Attacking Workflow Lateral Movement Privilege escalation Credential Dump
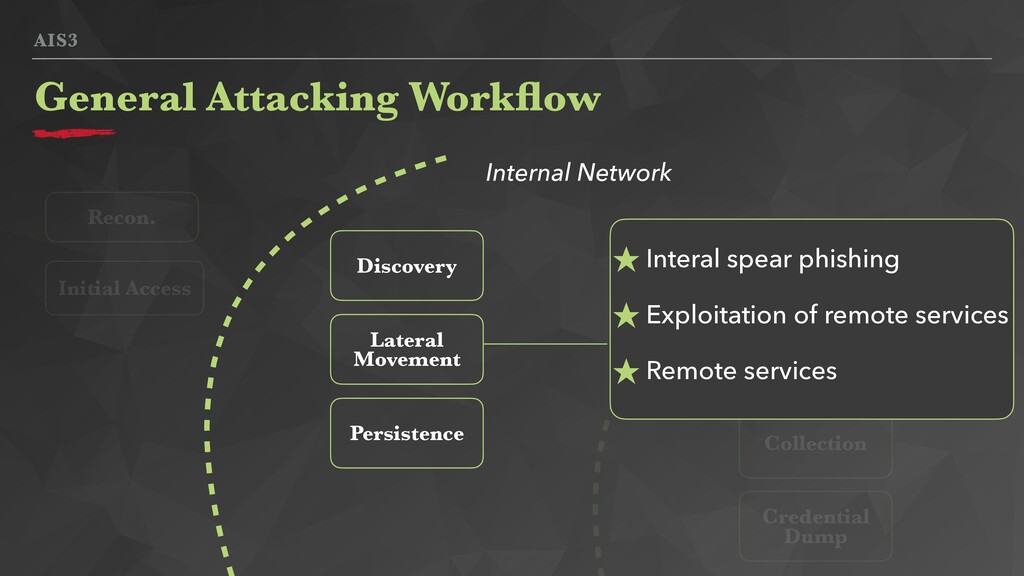
Persistence Critical Area Internal Network Initial Access Recon. Collection Discovery ★ Interal spear phishing ★ Exploitation of remote services ★ Remote services -
AIS3 General Attacking Workflow Lateral Movement Privilege escalation Credential Dump
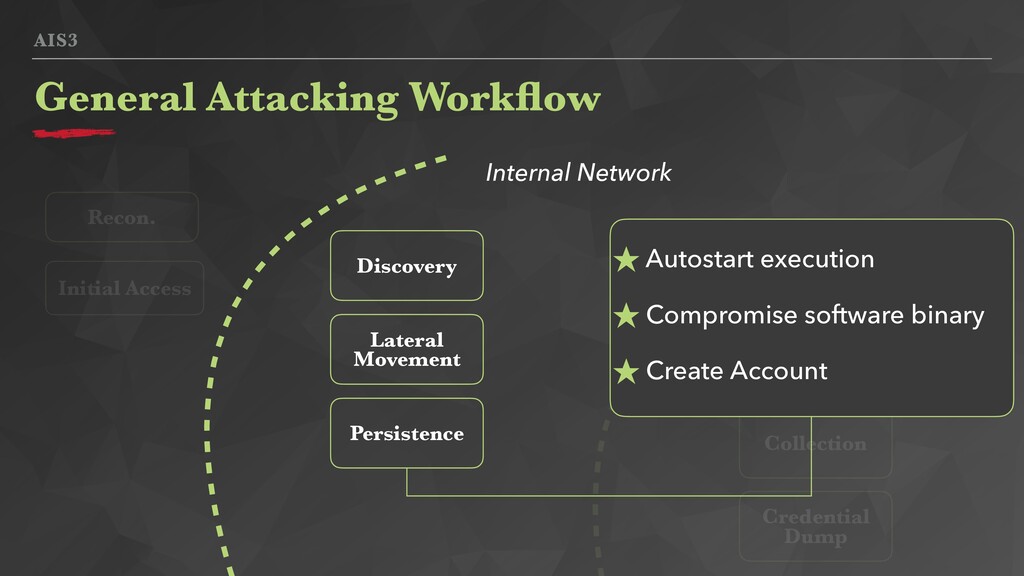
Persistence Critical Area Internal Network Initial Access Recon. Collection Discovery ★ Autostart execution ★ Compromise software binary ★ Create Account -
AIS3 Persistence ★ Create account ★ Autostart execution ★ Compromise
software binary ★ Inject service -
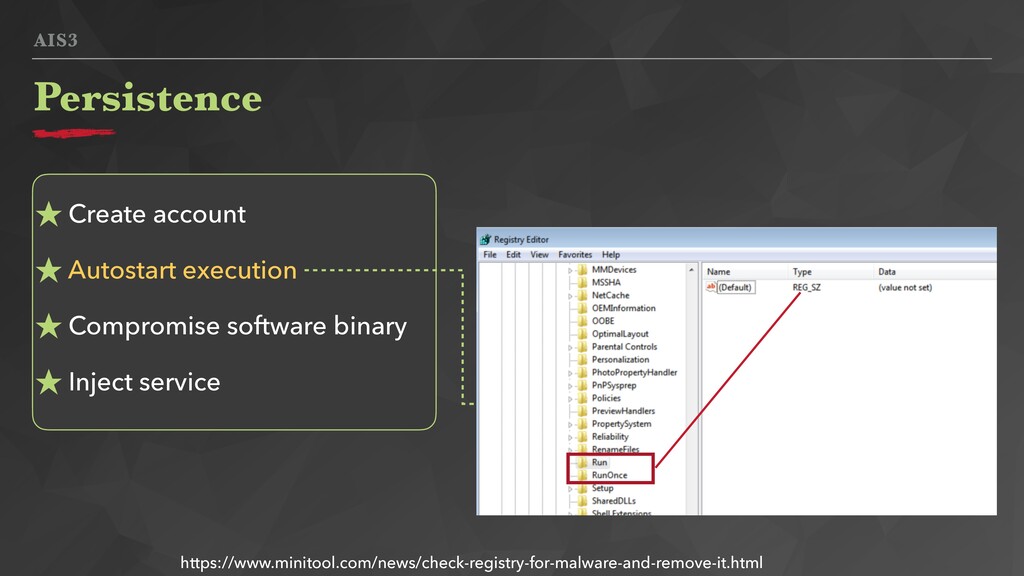
AIS3 Persistence ★ Create account ★ Autostart execution ★ Compromise
software binary ★ Inject service https://www.minitool.com/news/check-registry-for-malware-and-remove-it.html -
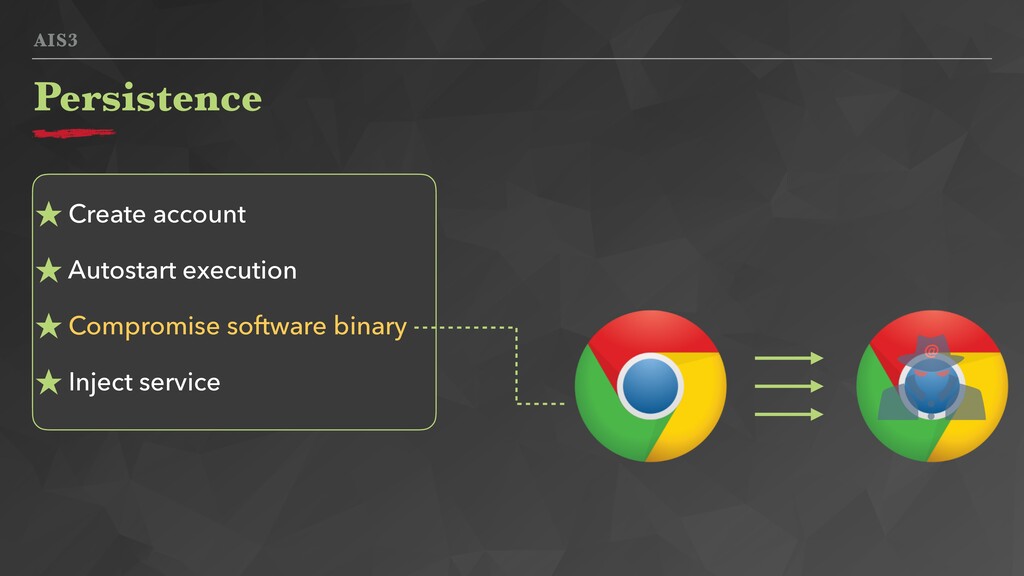
AIS3 Persistence ★ Create account ★ Autostart execution ★ Compromise
software binary ★ Inject service -
AIS3 General Attacking Workflow Lateral Movement Privilege escalation Credential Dump
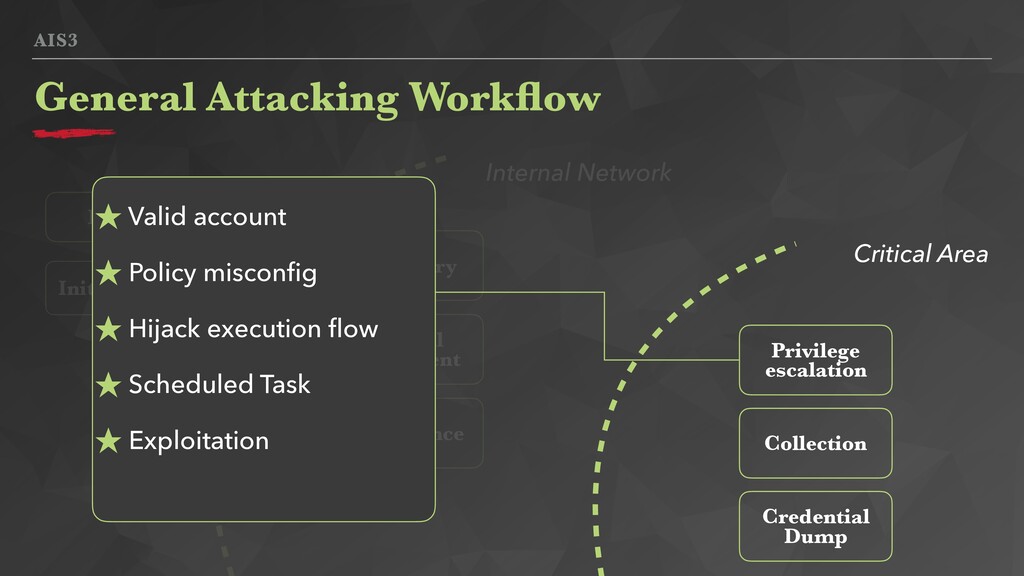
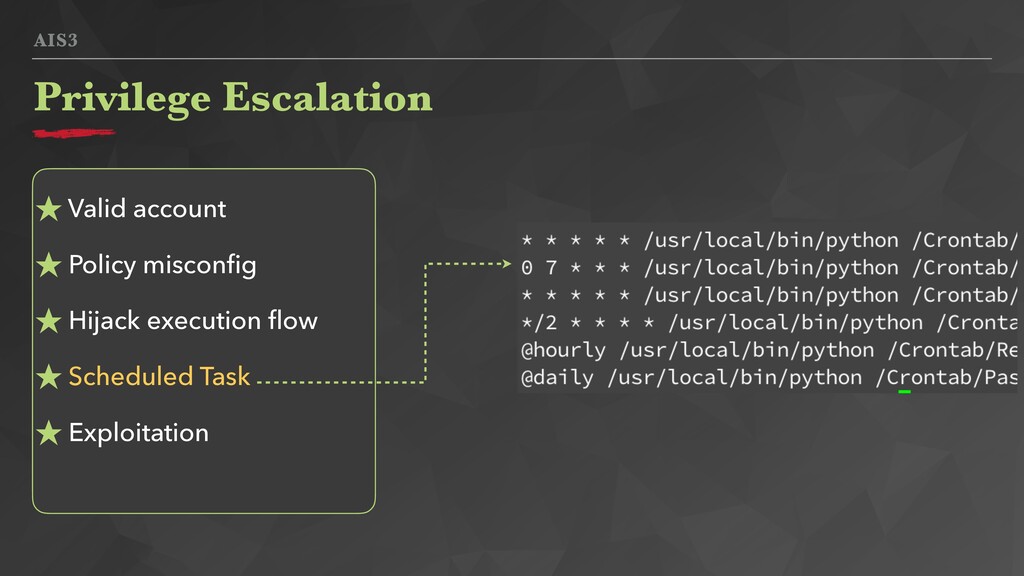
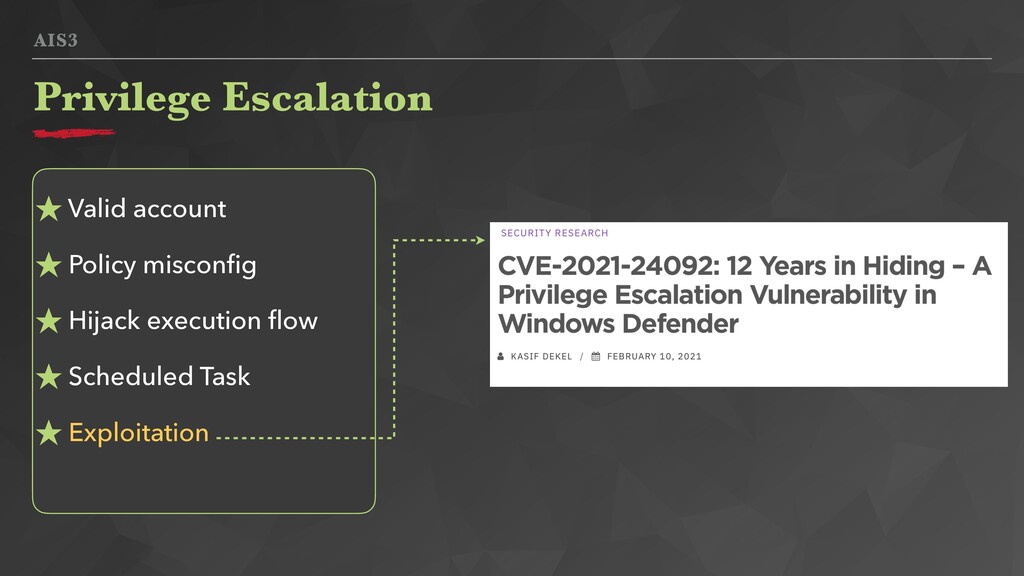
Persistence Critical Area Internal Network Initial Access Recon. Collection Discovery ★ Valid account ★ Policy misconfig ★ Hijack execution flow ★ Scheduled Task ★ Exploitation -
AIS3 ★ Valid account ★ Policy misconfig ★ Hijack execution
flow ★ Scheduled Task ★ Exploitation Privilege Escalation -
AIS3 ★ Valid account ★ Policy misconfig ★ Hijack execution
flow ★ Scheduled Task ★ Exploitation Privilege Escalation -
AIS3 ★ Try to read the secret.txt and get flag
LAB1 - Privilege Escalation (local system) -
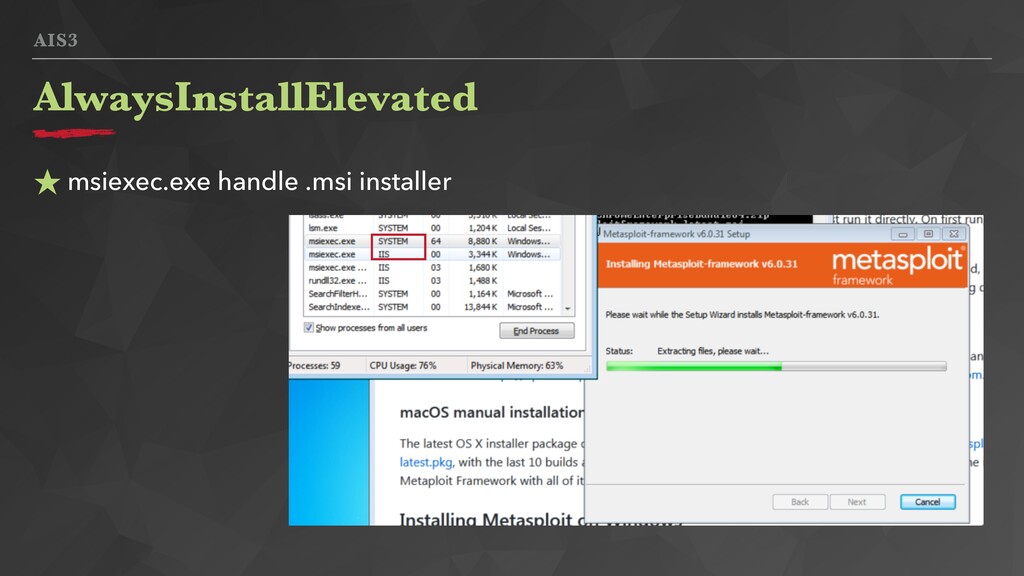
AIS3 ★ Windows misconfiguration ★ If admin enabled this feature,
windows will use system mode to install .msi installer ★ Path: Local group policy edit -> admin templete -> windows installer -> Always install with elevated privileges AlwaysInstallElevated -
AIS3 ★(old) https://github.com/PowerShellEmpire/PowerTools ★(new) https://github.com/PowerShellMafia/PowerSploit/ ★ A collection of Microsoft
PowerShell modules that can be used to aid penetration testers during all phases of an assessment Powerup -
AIS3 ★ cd C:\Users\IIS.MYAIS3\Desktop\package\PowerTools-master ★ into powerup folder ★ Import-Module
PowerUp.ps1 ★ Write-UserAddMSI Powerup -
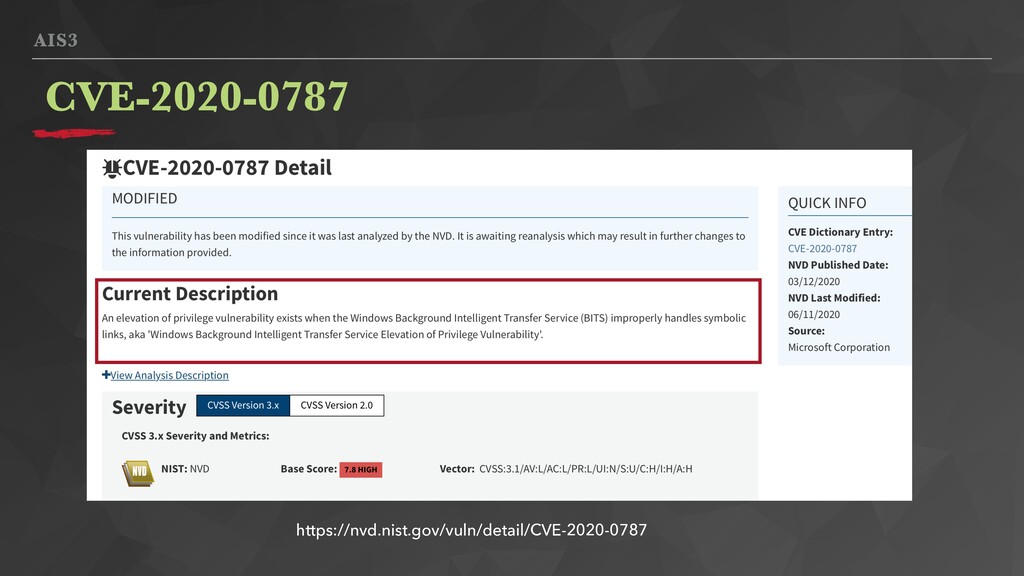
AIS3 ★ Background Intelligent Transfer Service(BITS,後端智能傳輸服務) ★ For download files
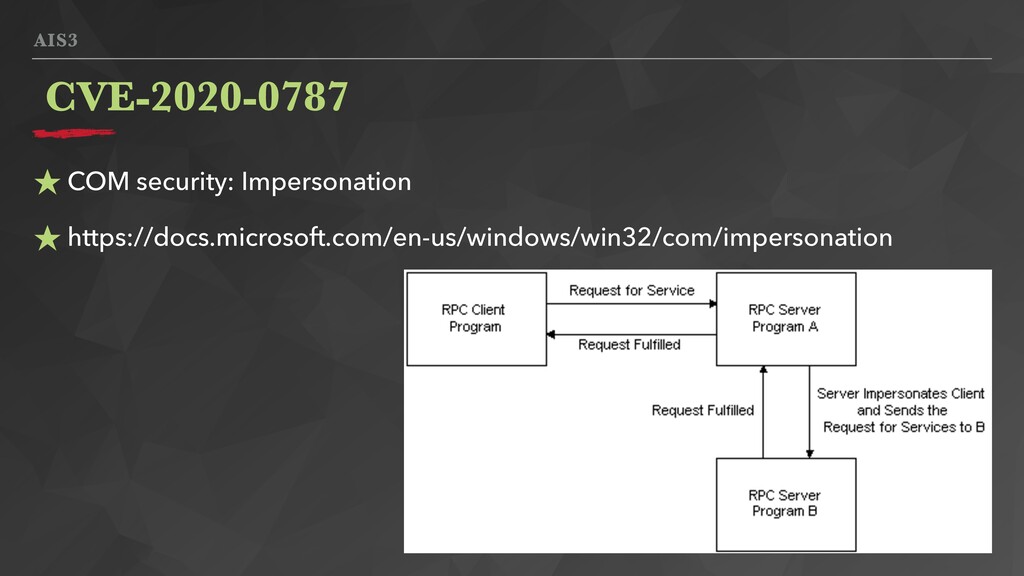
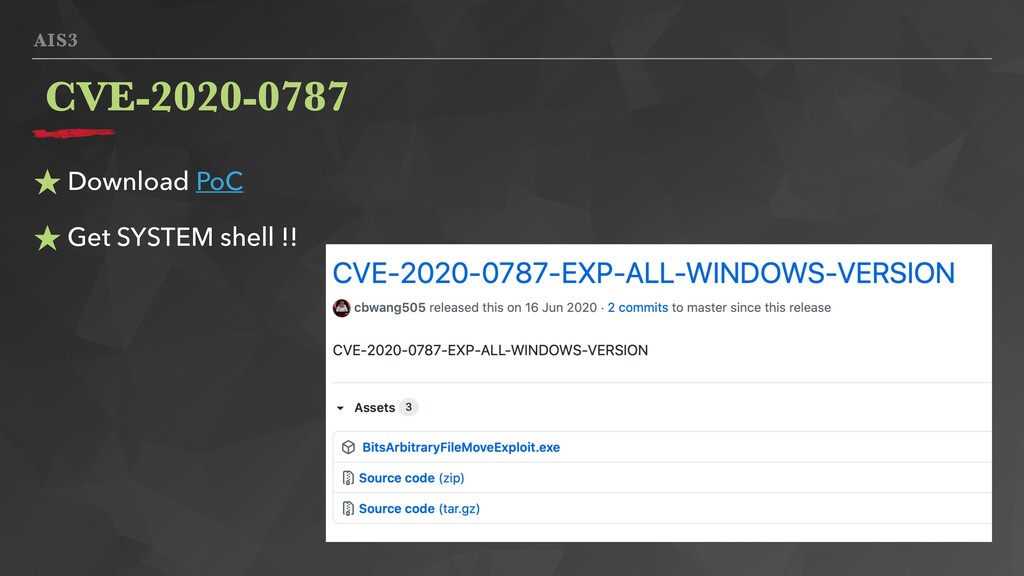
from or upload files to HTTP web servers and SMB file shares ★ Privileged file operation abuse CVE-2020-0787 https://www.anquanke.com/post/id/200742 -
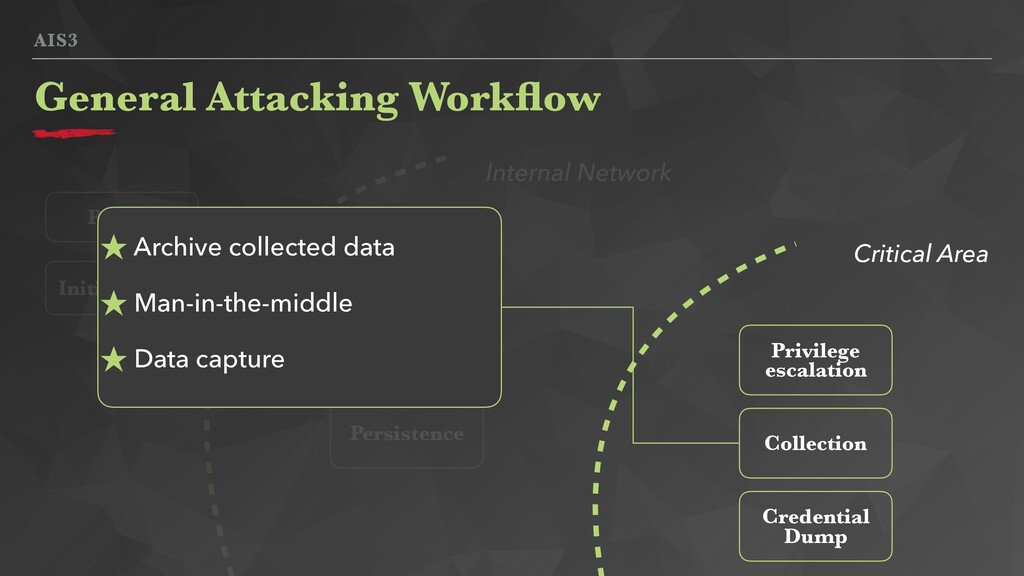
AIS3 General Attacking Workflow Lateral Movement Privilege escalation Credential Dump
Persistence Critical Area Internal Network Initial Access Recon. Collection Discovery ★ Archive collected data ★ Man-in-the-middle ★ Data capture -
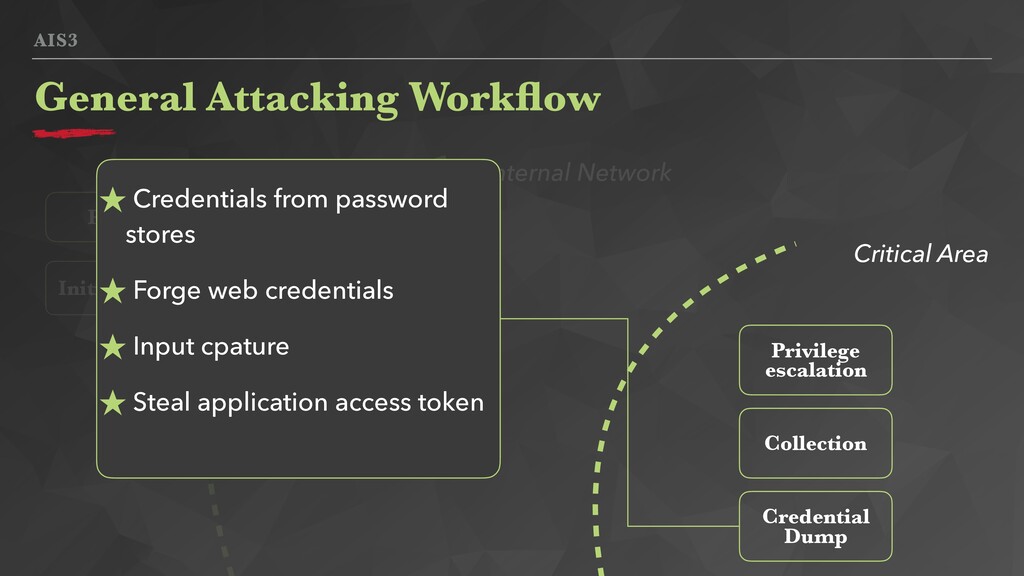
AIS3 General Attacking Workflow Lateral Movement Privilege escalation Credential Dump
Persistence Critical Area Internal Network Initial Access Recon. Collection Discovery ★ Credentials from password stores ★ Forge web credentials ★ Input cpature ★ Steal application access token -
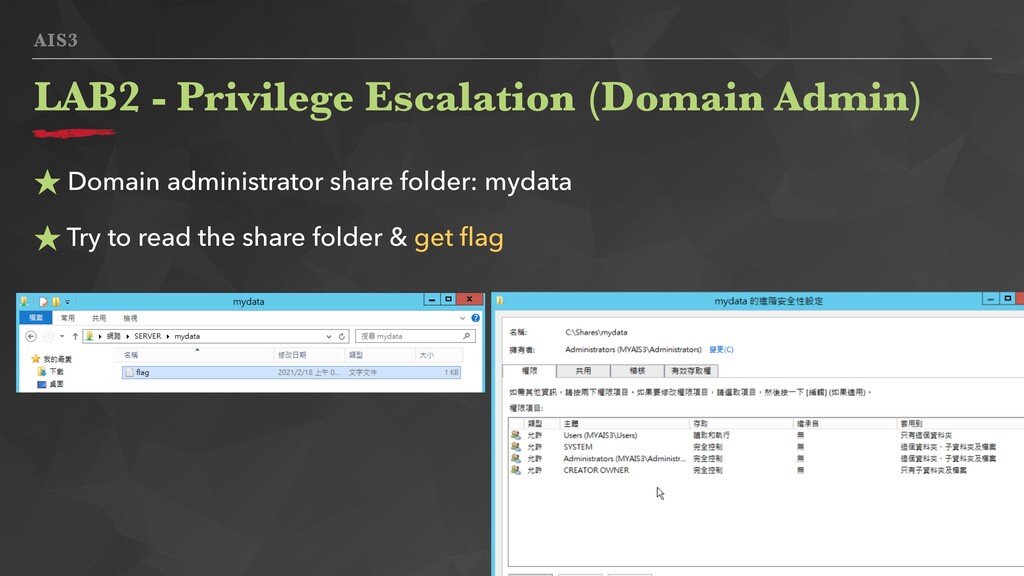
AIS3 ★ Domain administrator share folder: mydata ★ Try to
read the share folder & get flag LAB2 - Privilege Escalation (Domain Admin) -
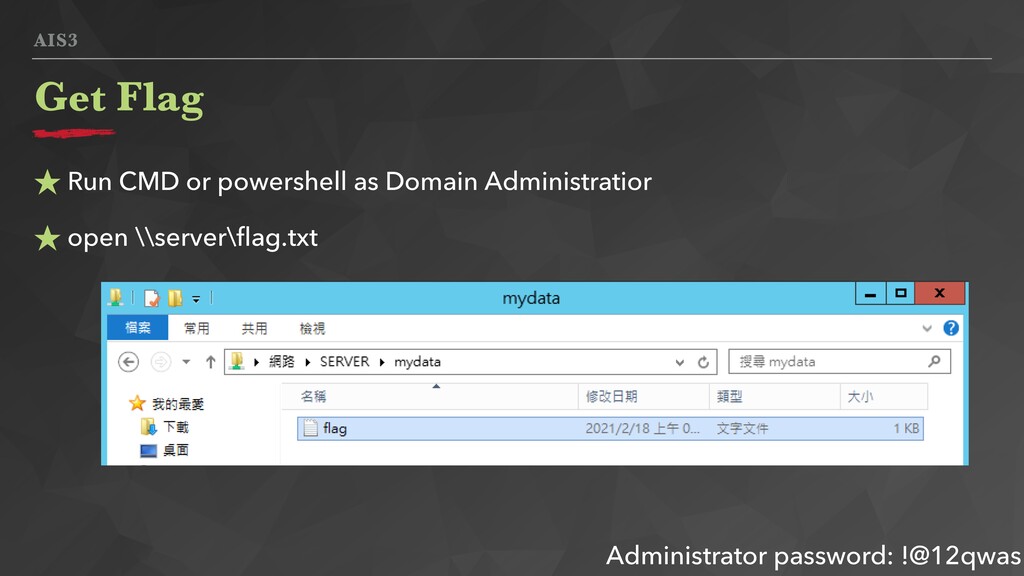
AIS3 ★ Run CMD or powershell as Domain Administratior ★
open \\server\flag.txt Get Flag Administrator password: !@12qwas -
AIS3 General Attacking Workflow Lateral Movement Privilege escalation Credential Dump
Persistence Critical Area Internal Network Initial Access Recon. Collection Discovery -
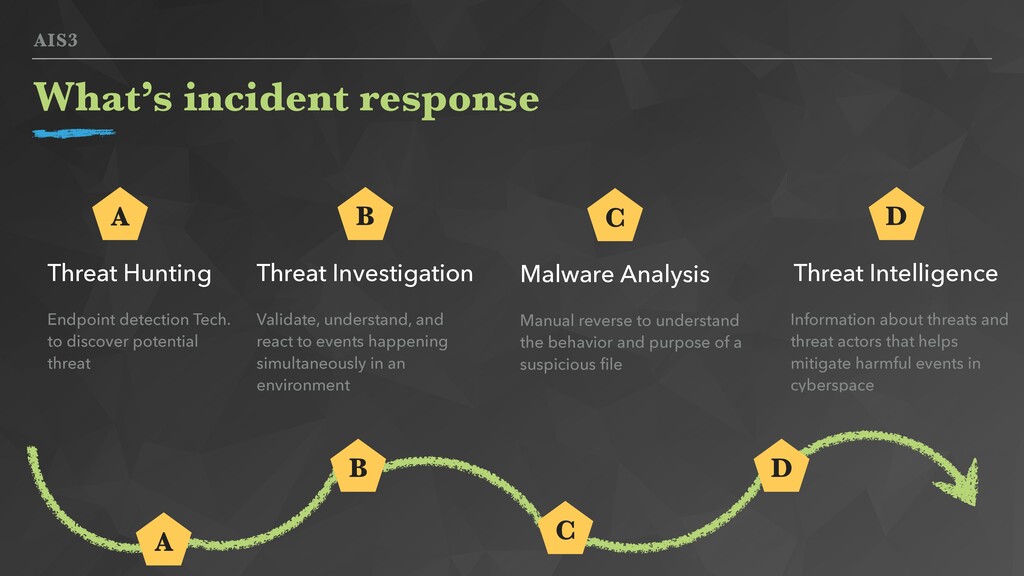
AIS3 What’s incident response Threat Hunting Malware Analysis Threat Investigation
Threat Intelligence A B C D D C B A Endpoint detection Tech. to discover potential threat Validate, understand, and react to events happening simultaneously in an environment Manual reverse to understand the behavior and purpose of a suspicious file Information about threats and threat actors that helps mitigate harmful events in cyberspace -
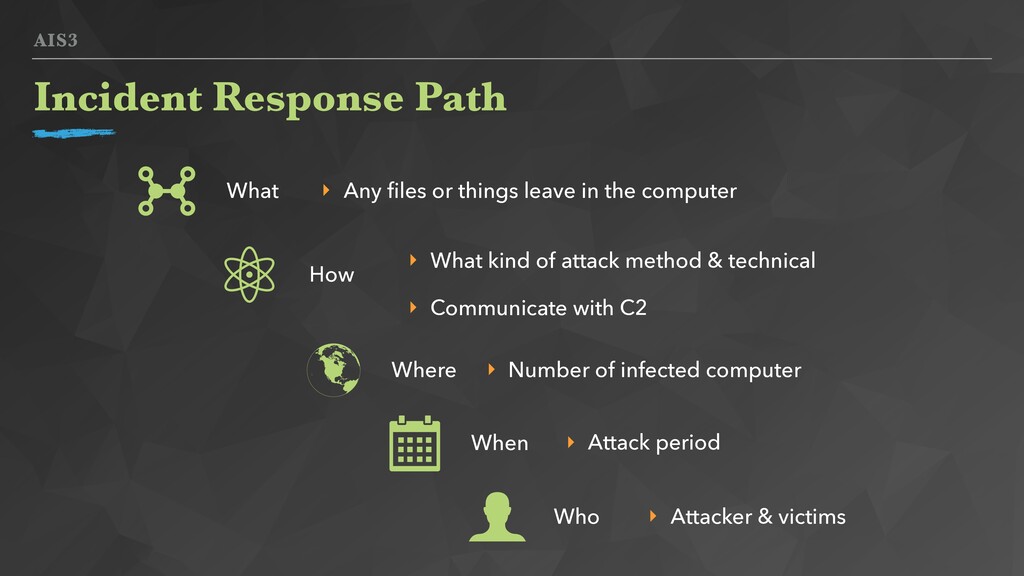
AIS3 Incident Response Path Who When Where How What ‣
Attacker & victims ‣ Attack period ‣ Number of infected computer ‣ Any files or things leave in the computer ‣ What kind of attack method & technical ‣ Communicate with C2 -
AIS3 ★ Networking ★ Process & Memory ★ Files When
a Attack Happen - What -
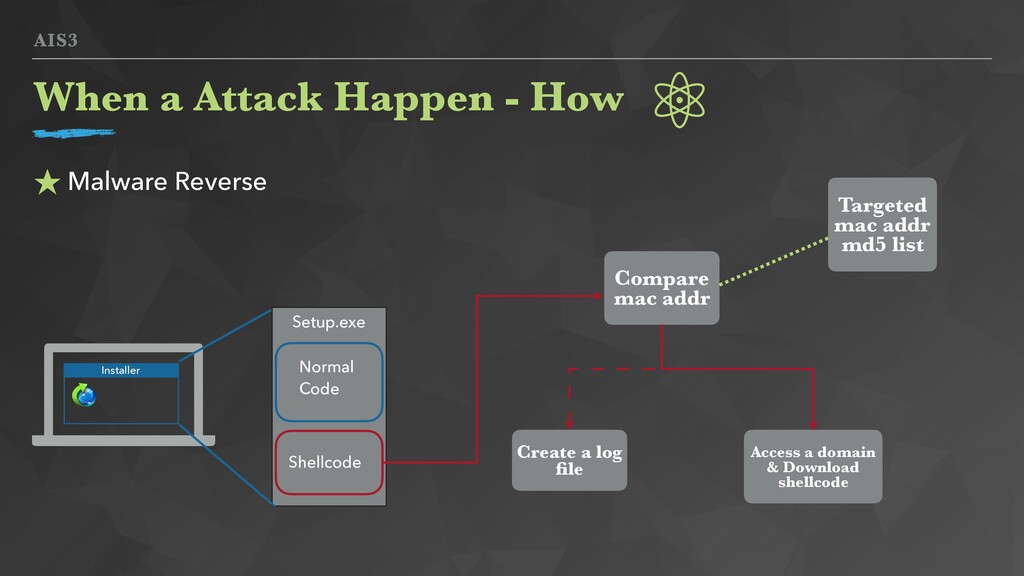
AIS3 ★ Malware Reverse When a Attack Happen - How
Installer Setup.exe Normal Code Shellcode Compare mac addr Create a log file Access a domain & Download shellcode Targeted mac addr md5 list -
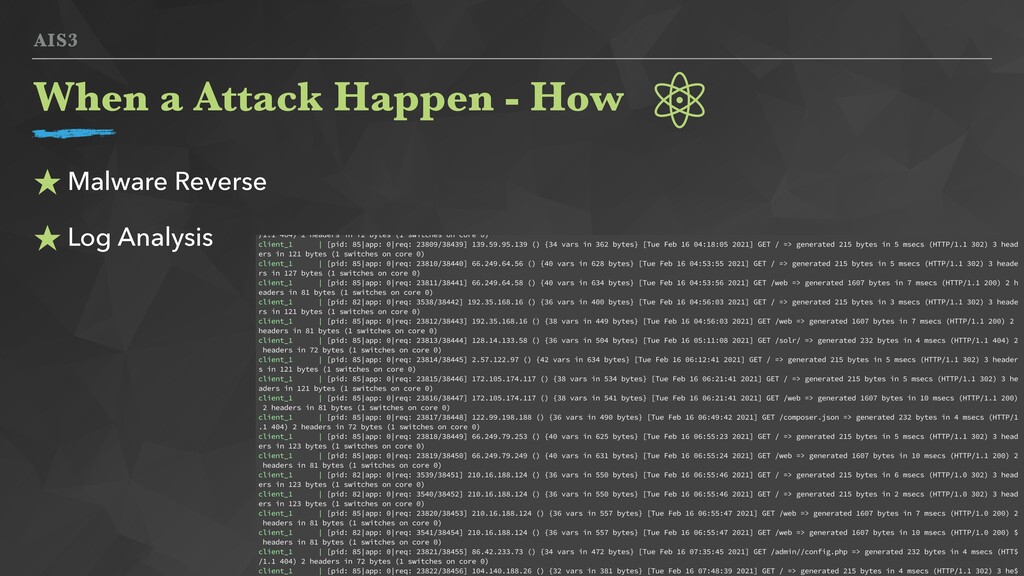
AIS3 ★ Malware Reverse ★ Log Analysis When a Attack
Happen - How -
AIS3 ★ Sysmon ★ Windows Audit Log ★ ELK (
Elasticsearch + Logstash + Kibana ) Tools -
AIS3 ★ Download from website ★ Install security patch KB3033929,
KB2533623 for fixing signature issue ★ ‘sysmon -accepteula -i’ ✦ Install with default settings (process images hashed with sha1 and no network monitoring) Install sysmon https://social.technet.microsoft.com/Forums/en-US/81dc8039-224a-4709-a14f-32f6a052cf9b/sysmon-1041-installation-issue? forum=miscutils -
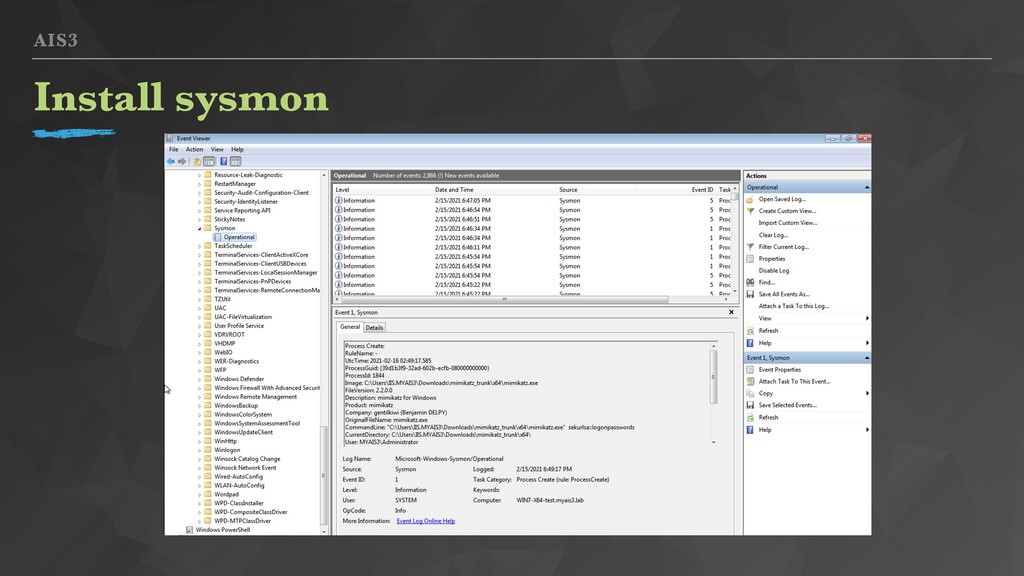
AIS3 ★ Open event log ★ Applications and Services Logs
-> Microsoft -> Windows -> Sysmon -> Operational Install sysmon -
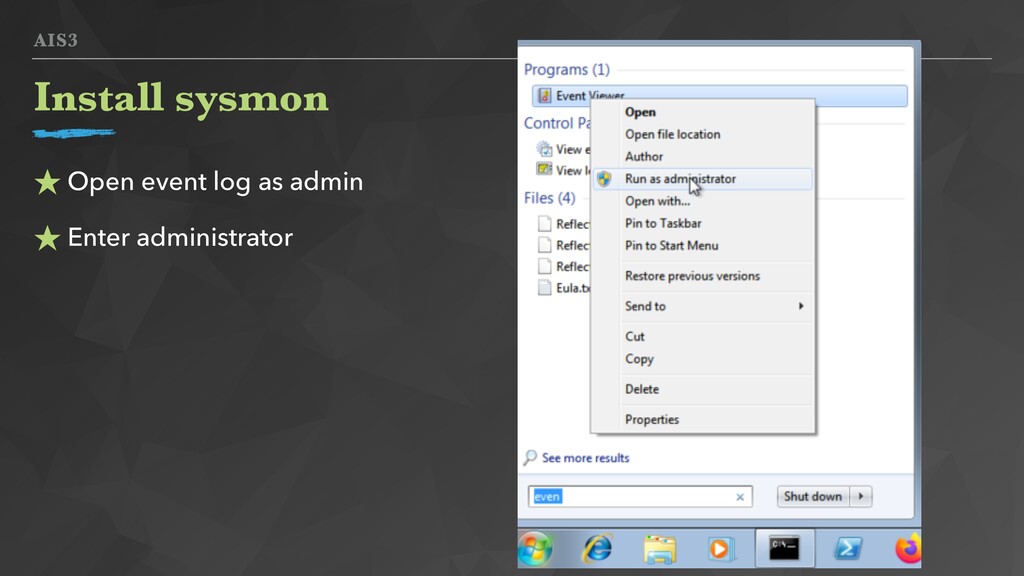
AIS3 ★ Open event log as admin ★ Enter administrator
Install sysmon -
AIS3 ★ Find CVE-2020-0787 execution path ★ Find Mimikatz Password
& hash dump log Leb3: Let’s Hunting