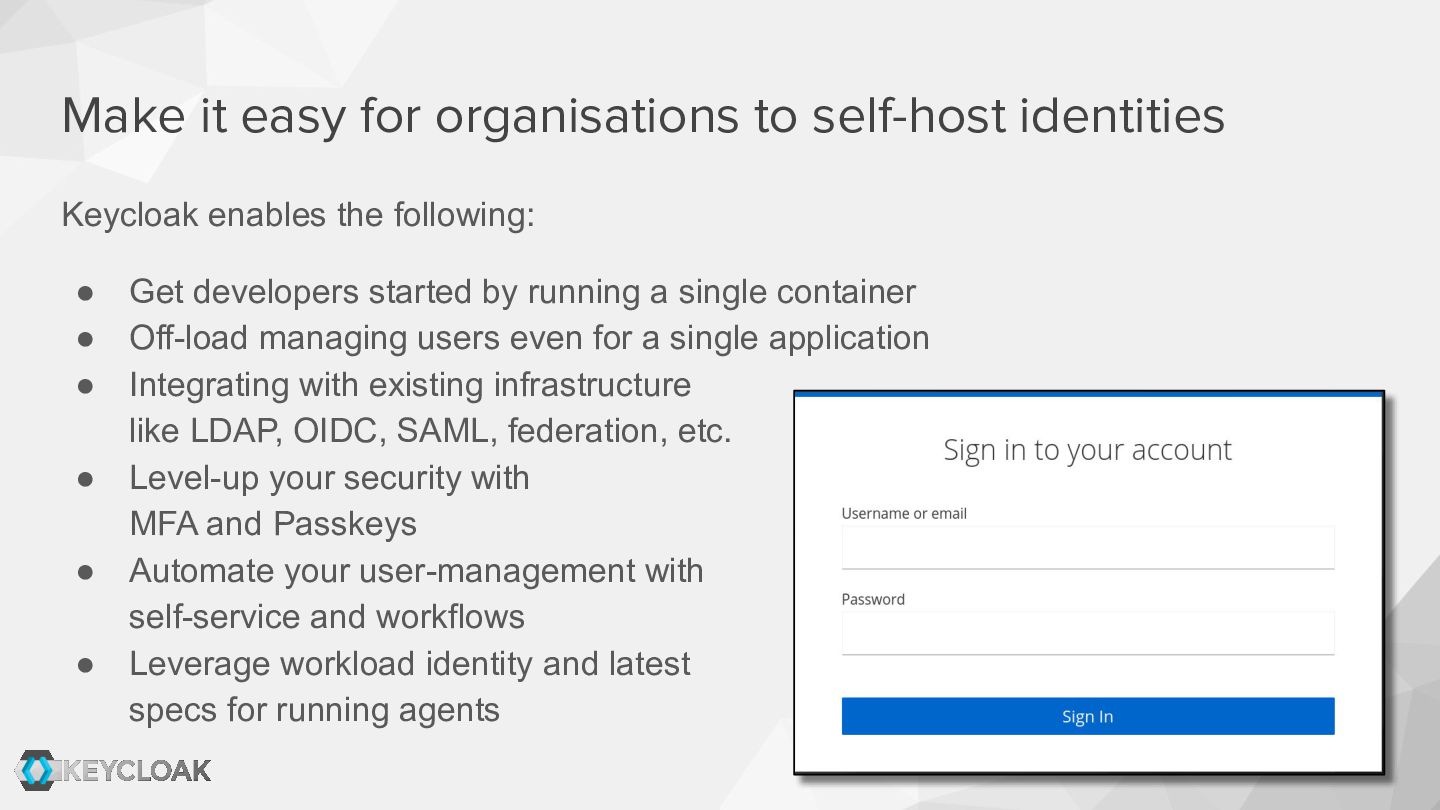
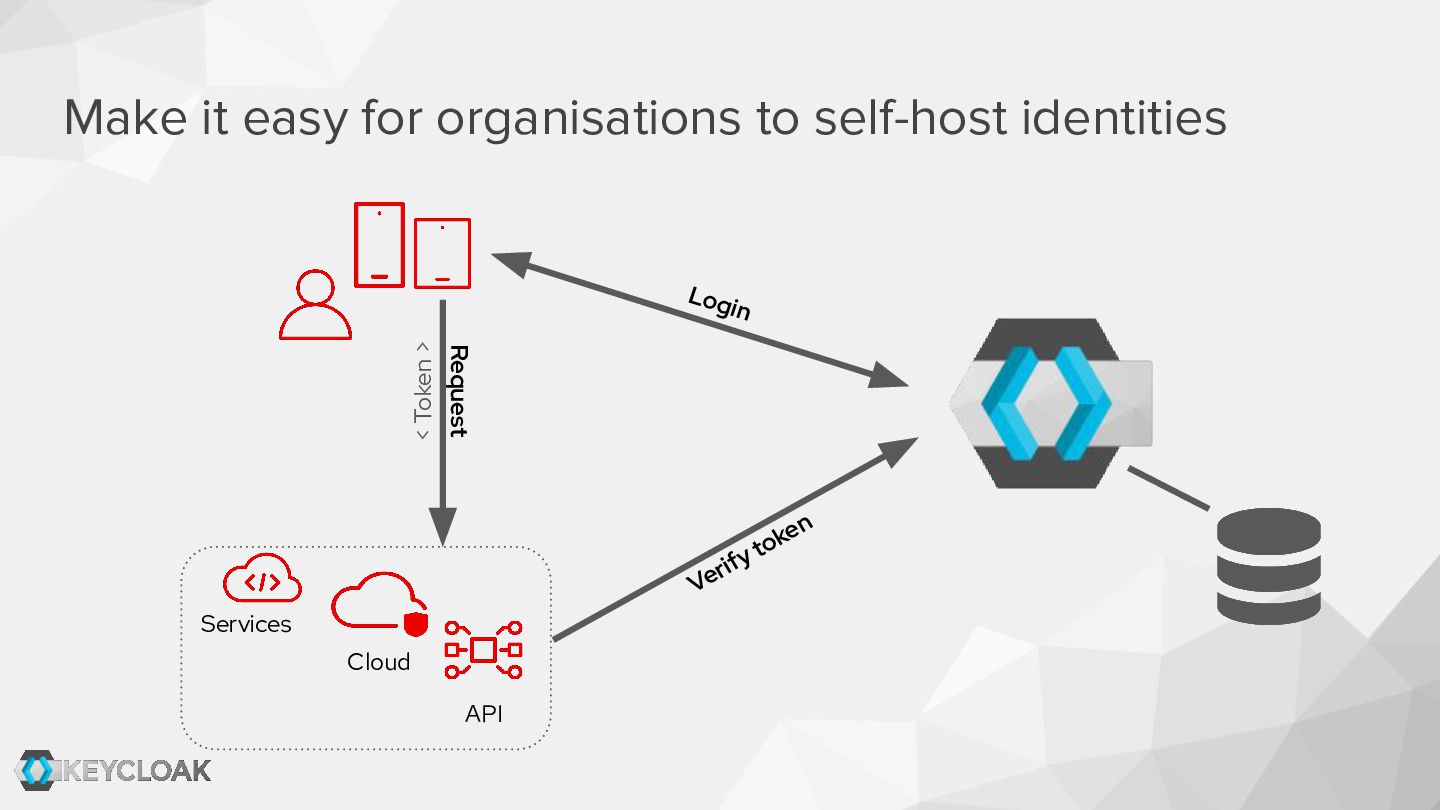
the following: • Get developers started by running a single container • Off-load managing users even for a single application • Integrating with existing infrastructure like LDAP, OIDC, SAML, federation, etc. • Level-up your security with MFA and Passkeys • Automate your user-management with self-service and workflows • Leverage workload identity and latest specs for running agents
security easier OpenTalk achieves versatile and compliant user authentication with Keycloak BRZ migrated the Austrian Business Service Portal with 2M+ users to Keycloak https://www.keycloak.org/case-studies
to improve: 1. Challenges that users and admins struggle with? 2. Features on the road map that are exciting and should be prioritized? 3. Features are already used, but should be promoted more?
(since 26.4, and enhanced in each release) ⚙ User lifecycle management with workflows (since 26.6, extendable with own steps) 🏢 Organisations with FGAP delegation (since 26.7) 🛂 Zero-Trust ephemeral credentials for machines (JWT Authorization grant, SPIFFE, KSA, 26.6+) 🛑 Shared Signals Framework (terminate sessions on RISC/CAEP signals, 26.7) ♻ Split-brain detection and rolling updates (since 26.6 for patch releases) 🦋 Graceful shutdown and proxy documentation (Avoiding 503 error when instances shut down)
wallets (preview OID4VCI, experimental OID4VP) ⚙ User lifecycle management with workflows (now with automatic invite emails) 🗂 SCIM to pre-provision users and groups (supported) 💫 Stateless Keycloak for multi-cluster setups (supported) 「」 Parameterized Scopes (preview, used to be called dynamic scopes) 🔐 Client Secret Rotation (supported) 🤖 Token exchange delegation with consent ( preview) (consent, authorization, audit trail) 🗄 Automatic creation of missing indexes (even concurrently if DB supports it)
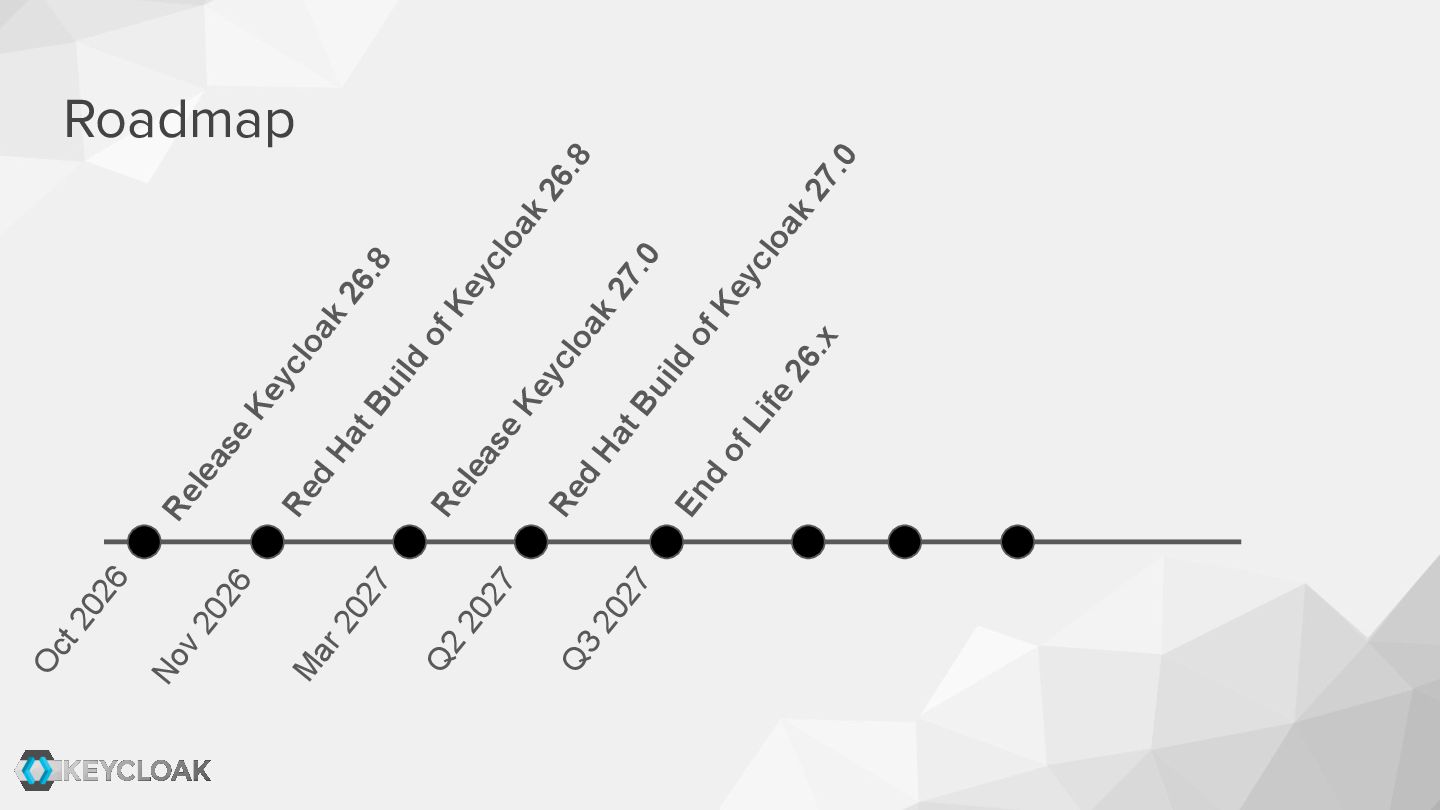
27 20 26 20 6 02 t2 Oc d En d Re se of of 26 cl oa k Ke y 27 .0 cl oa k .8 Ke y ak x 26 . ui ld Li fe of yc lo Ke tB Ha le a Re ui ld ak lo yc Ke tB Ha se ea d Re Re l .0 27 .8 26 Roadmap
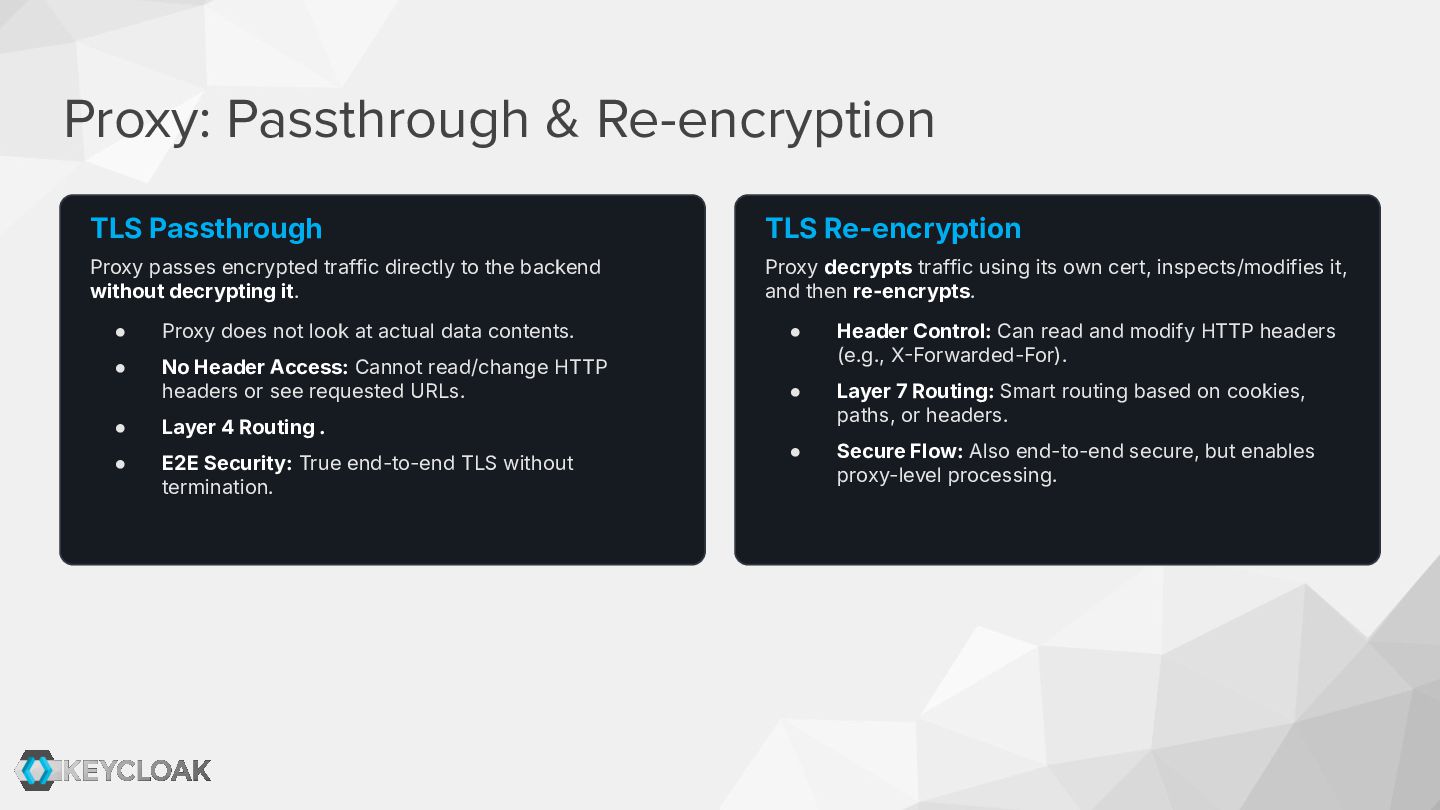
encrypted traffic directly to the backend without decrypting it. Proxy decrypts traffic using its own cert, inspects/modifies it, and then re-encrypts. • Proxy does not look at actual data contents. • • No Header Access: Cannot read/change HTTP headers or see requested URLs. Header Control: Can read and modify HTTP headers (e.g., XForwarded-For). • Layer 7 Routing: Smart routing based on cookies, paths, or headers. • Secure Flow: Also end-to-end secure, but enables proxy-level processing. • Layer 4 Routing . • E2E Security: True end-to-end TLS without termination.
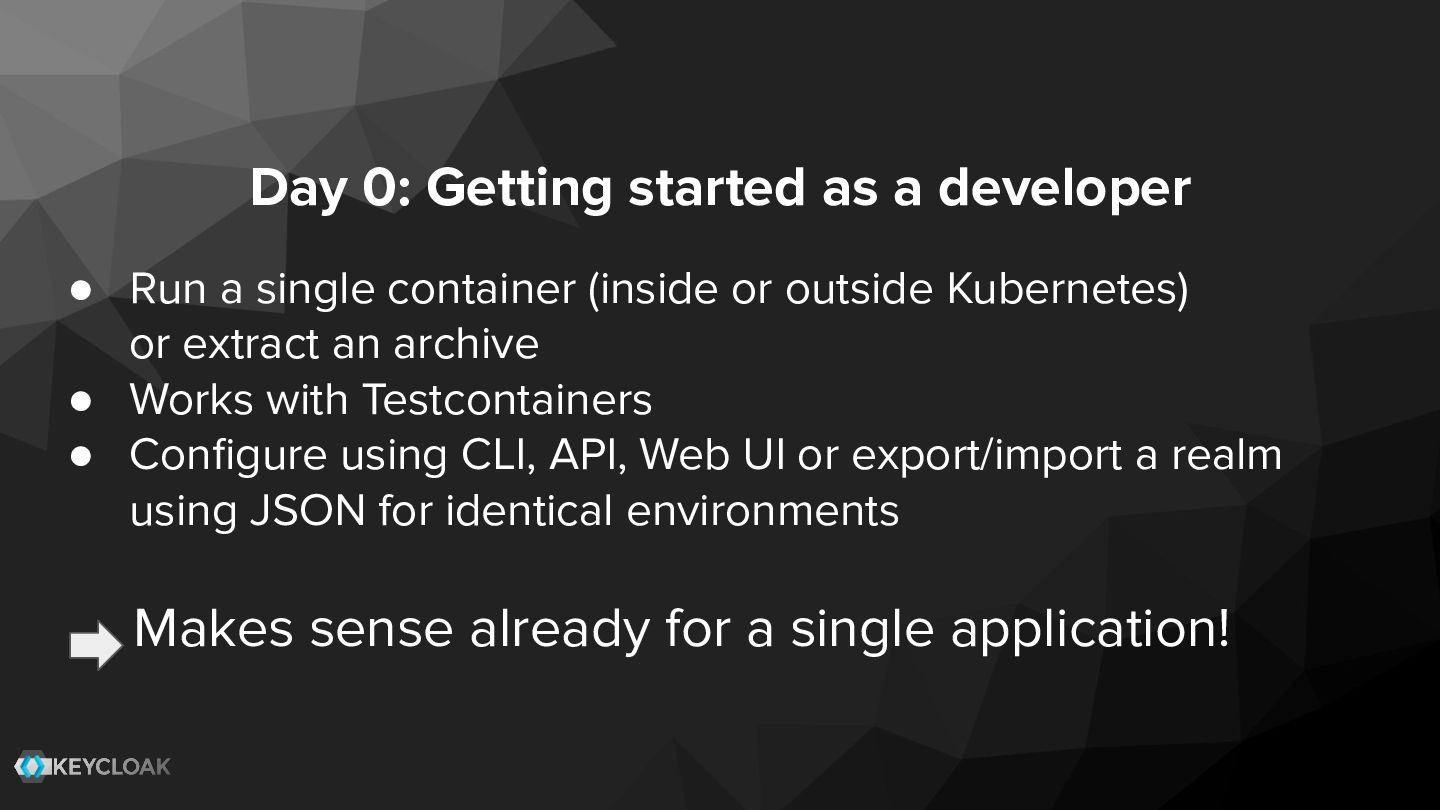
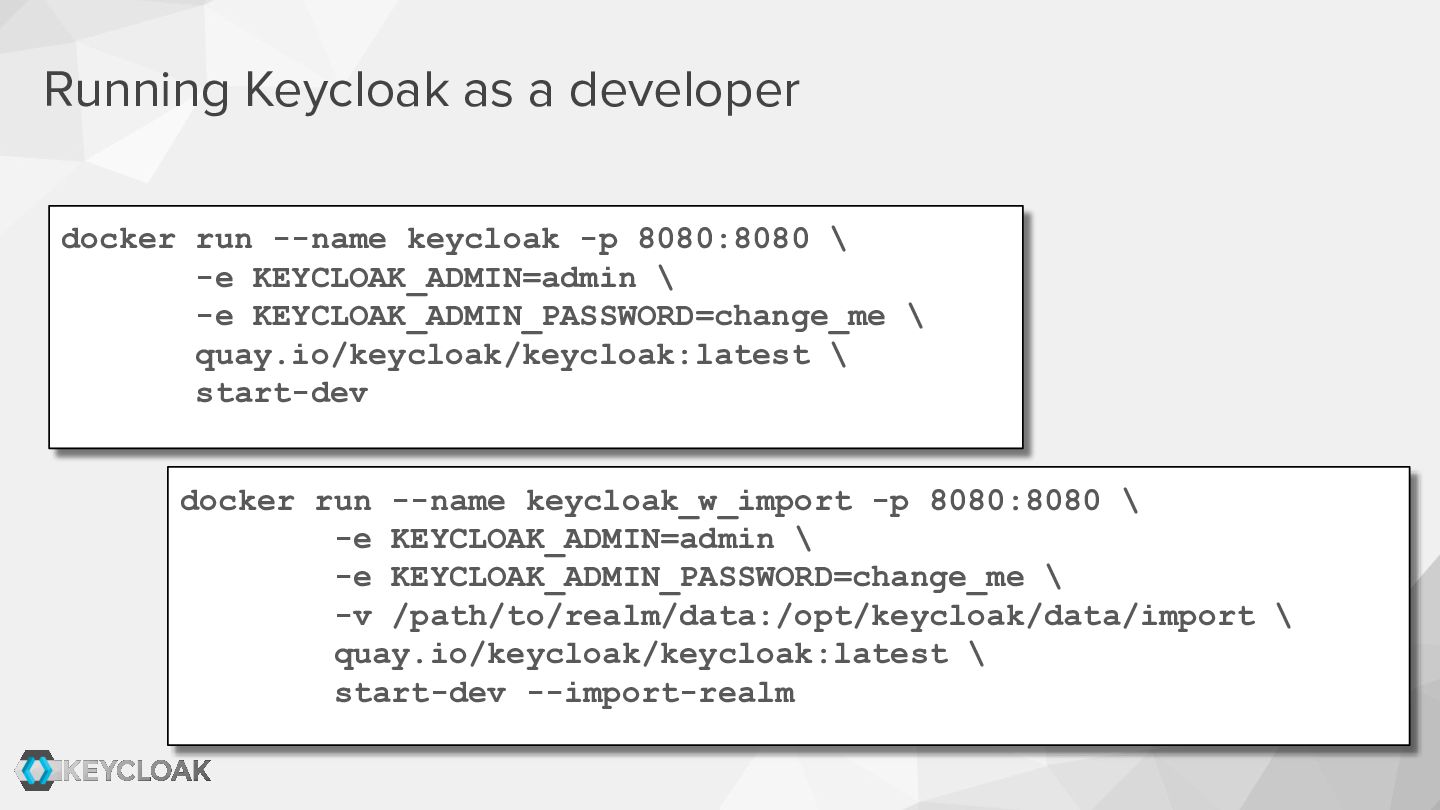
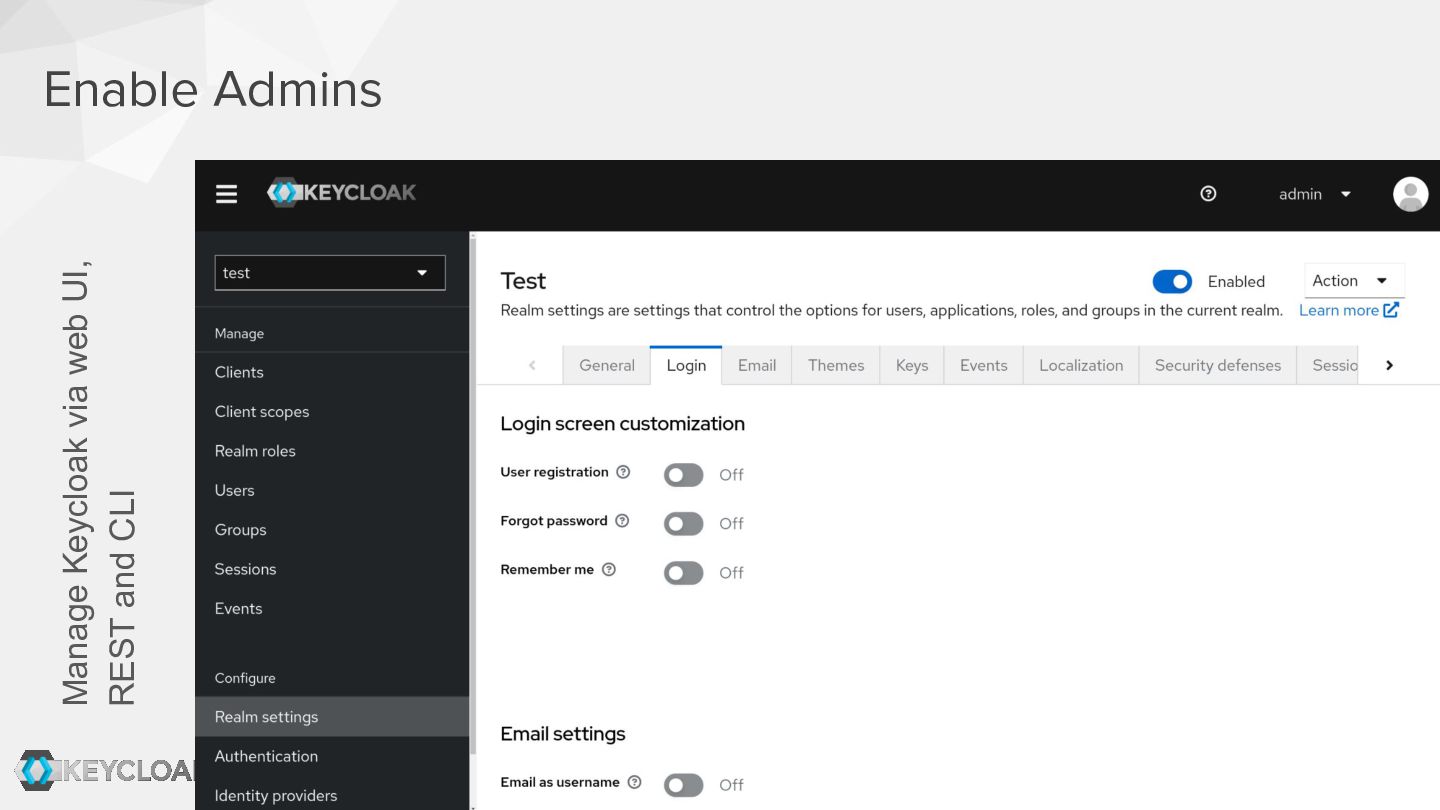
single container (inside or outside Kubernetes) or extract an archive • Works with Testcontainers • Configure using CLI, API, Web UI or export/import a realm using JSON for identical environments Makes sense already for a single application!
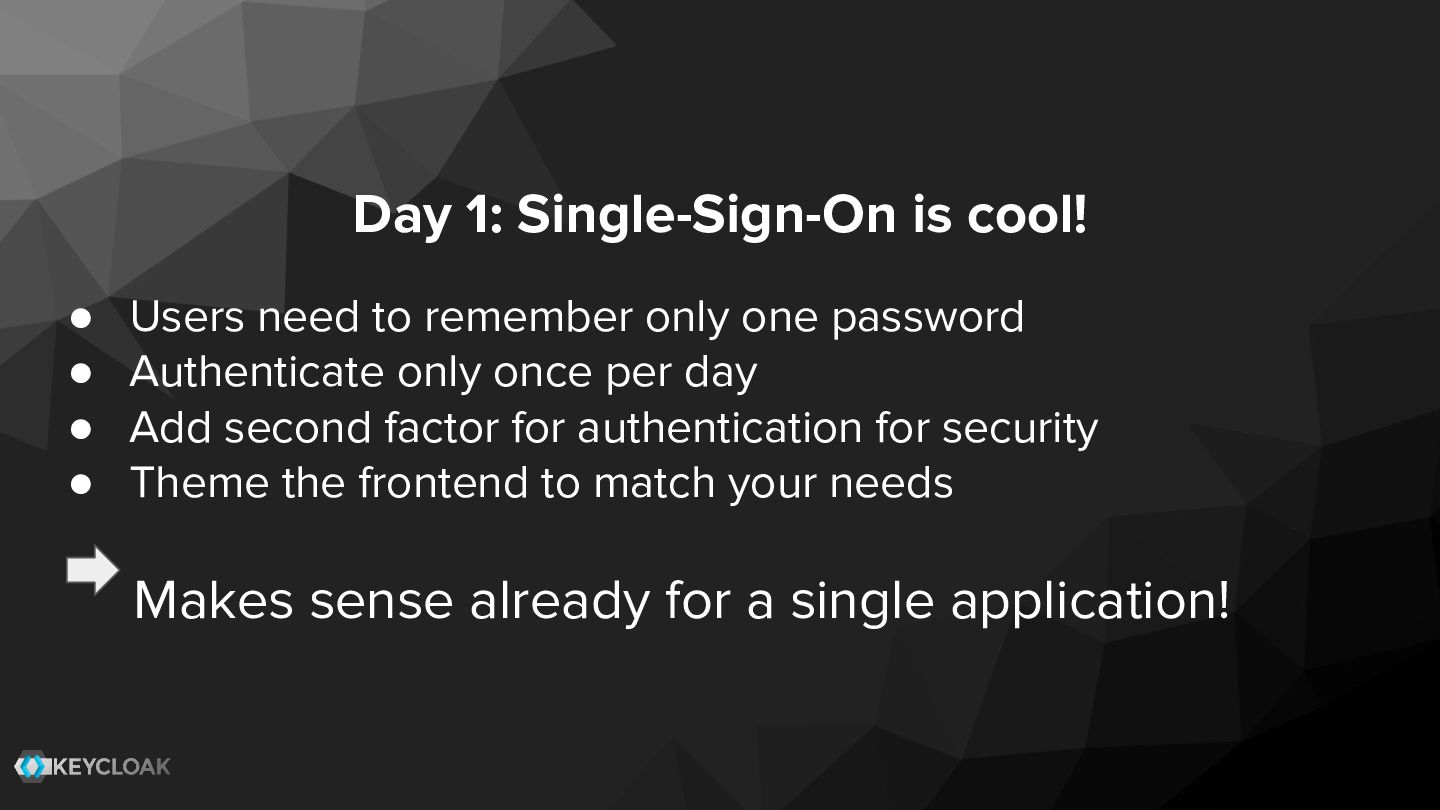
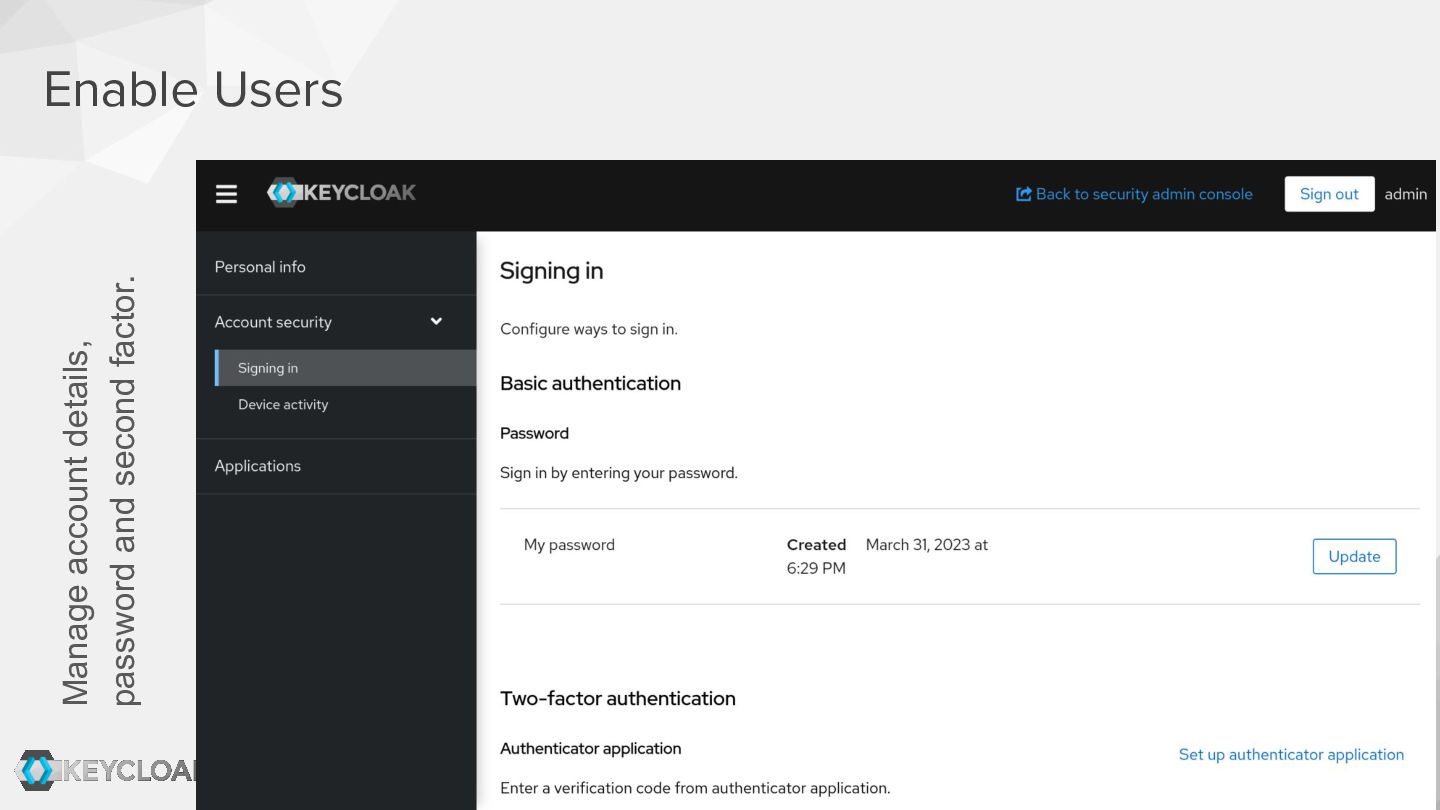
need to remember only one password Authenticate only once per day Add second factor for authentication for security Theme the frontend to match your needs Makes sense already for a single application!
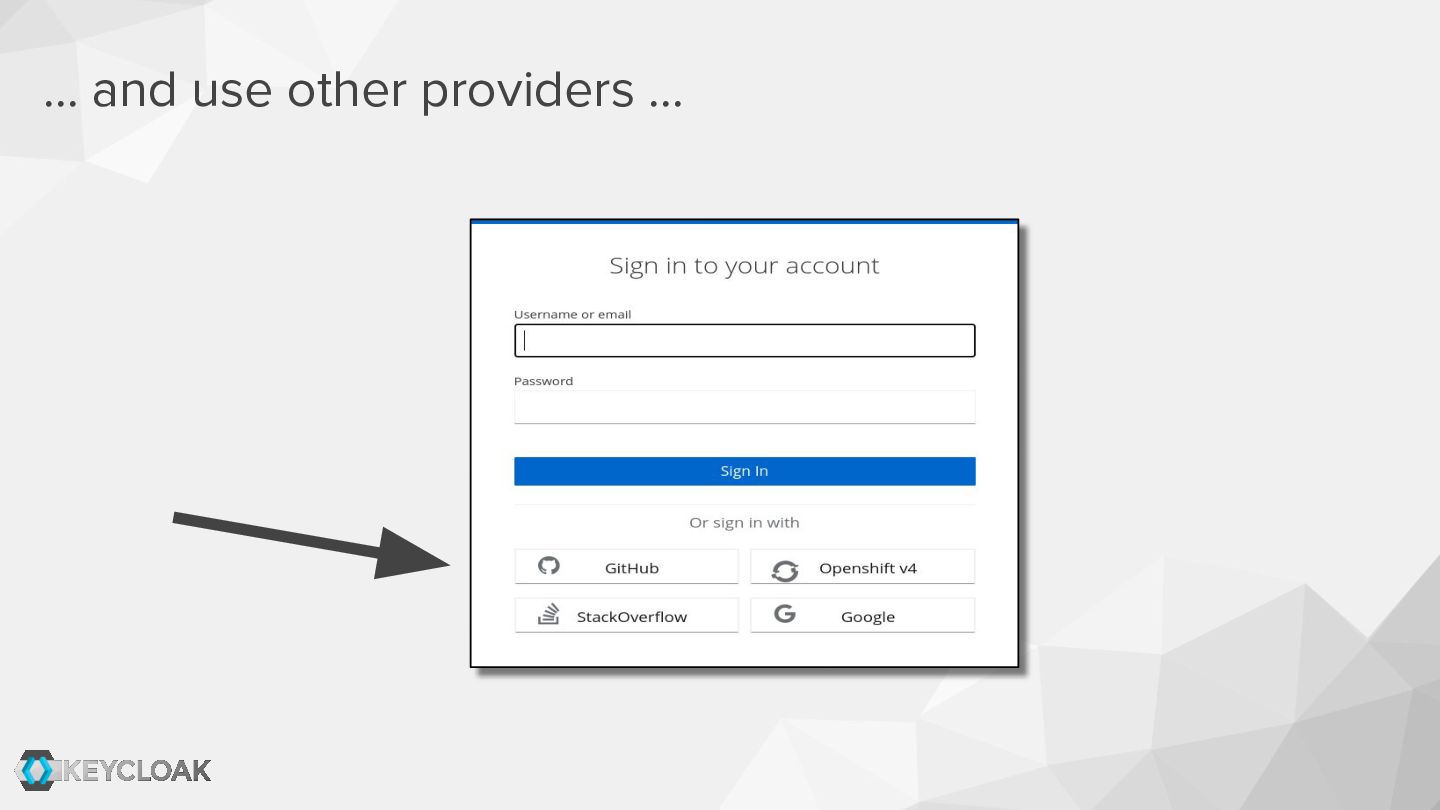
• Integrate LDAP and Kerberos Brokerage to existing SAML services Brokerage to existing OIDC services Integrate existing custom stores Reuse the existing user infrastructure!
required actions User password recovery (even when using LDAP) Self-registration for users User data self-management Resolve the need for calls and tickets!


 ahus1
 sh_fk2
 kworkdev
 ufried
 yoshiiryo1
 rmetzger
 asmz
 henteko
 shunghsiyu
 sakusaku3939
 tgidgd
 akosma
 jozono
 wjessup
 scottboms
 jonoalderson
 codingconduct
 morganepeng
 livdayseo
 popppiees
 mza
 orderedlist
 gr2m
 akihiro_kokubo