Upgrade to Pro — share decks privately, control downloads, hide ads and more …

Simplifying Workload Identity within the Red Ha...

Sponsored · SiteGround - Reliable hosting with speed, security, and support you can count on. →

Simplifying Workload Identity within the Red Hat build of Keycloak with the SPIFFE Identity Provider

Using SPIFFE/SPIRE based identities using Red Hat Zero Trust Workload Identity Manager to authenticate to the Red Hat build of Keycloak harden the security of applications. By using short lived, auto-rotated credentials, applications and the platforms they interact with are inherently more secure

Alexander Schwartz PRO

May 12, 2026

Transcript

37 slides
  1. Simplifying Workload Identity within the Red Hat build of Keycloak

    with the SPIFFE Identity Provider Andrew Block Alexander Schwartz Distinguished Architect Principal Software Engineer Red Hat IBM
  2. Simplifying Workload Identity within the Red Hat build of Keycloak

    with the SPIFFE Identity Provider Evolution of the “workload” Monolithic Applications 2
  3. Simplifying Workload Identity within the Red Hat build of Keycloak

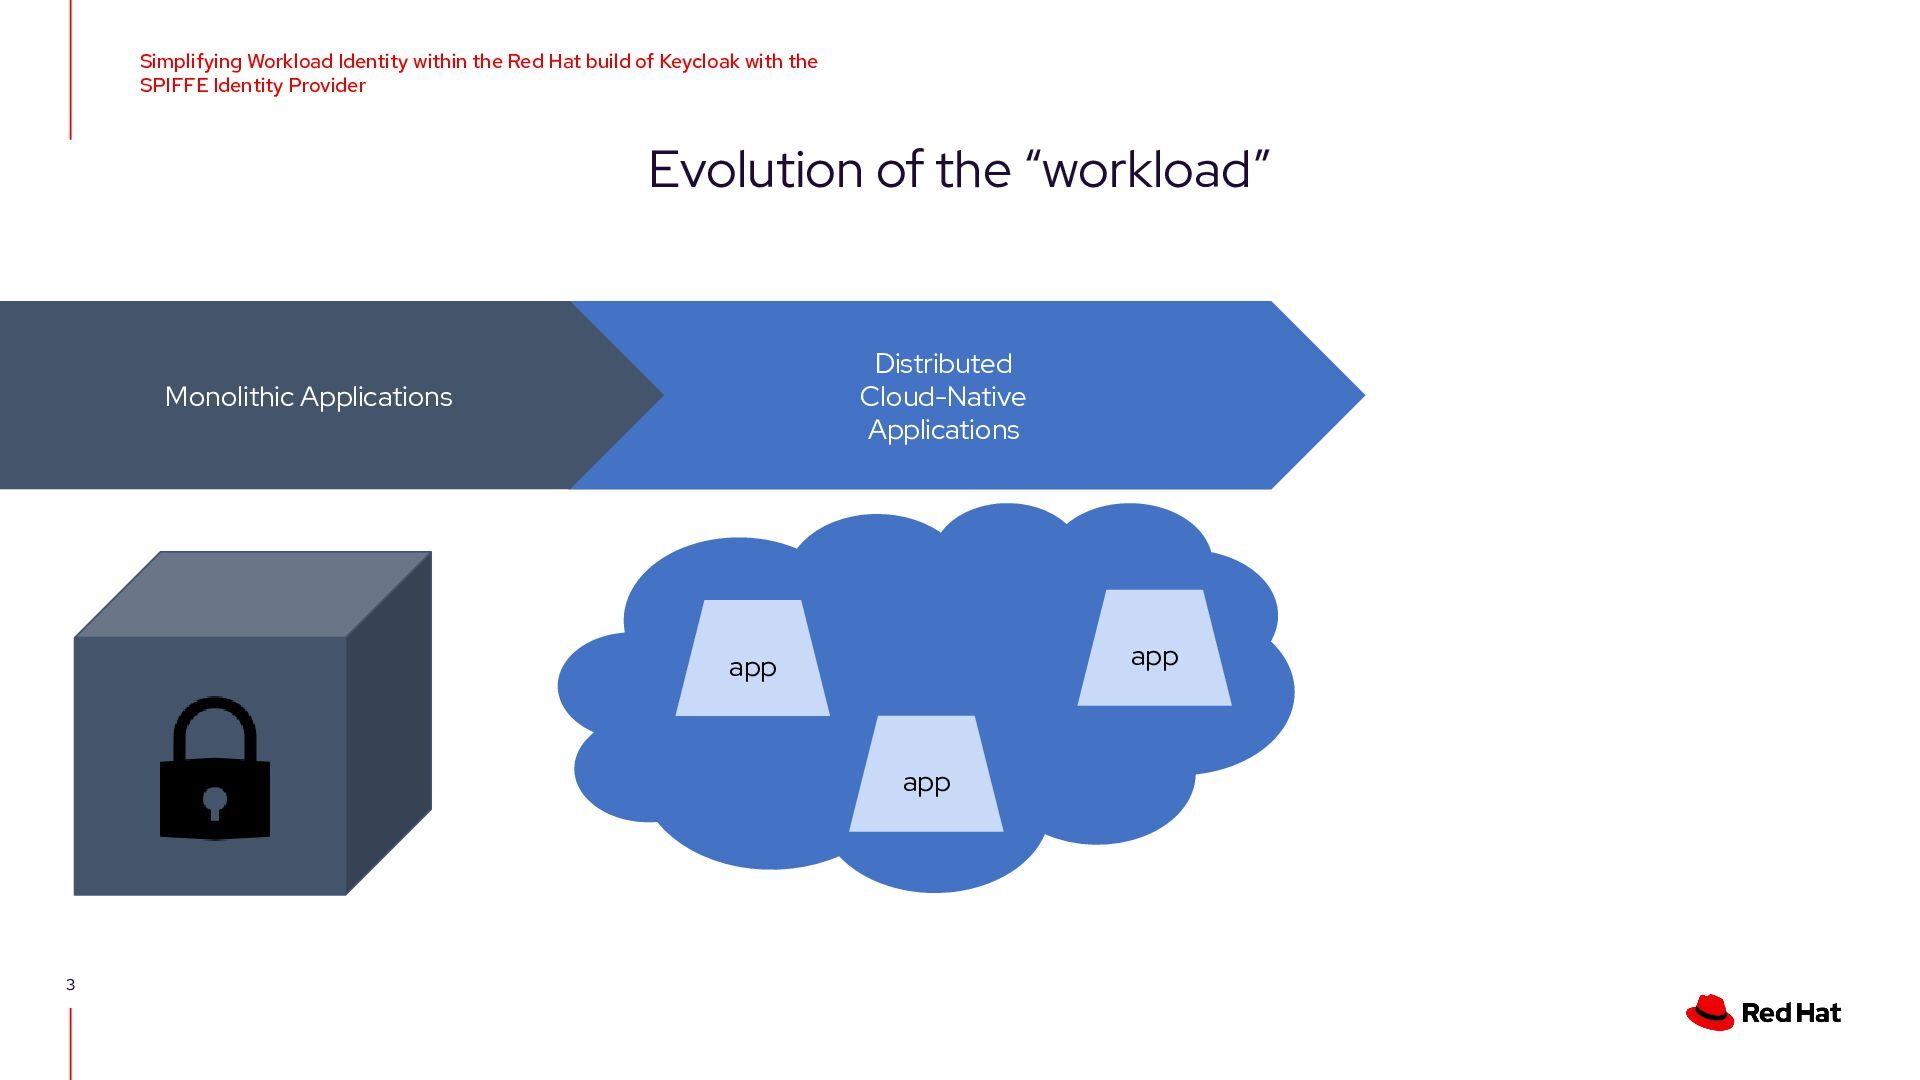
    with the SPIFFE Identity Provider Evolution of the “workload” Distributed Cloud-Native Applications Monolithic Applications app app app 3
  4. Simplifying Workload Identity within the Red Hat build of Keycloak

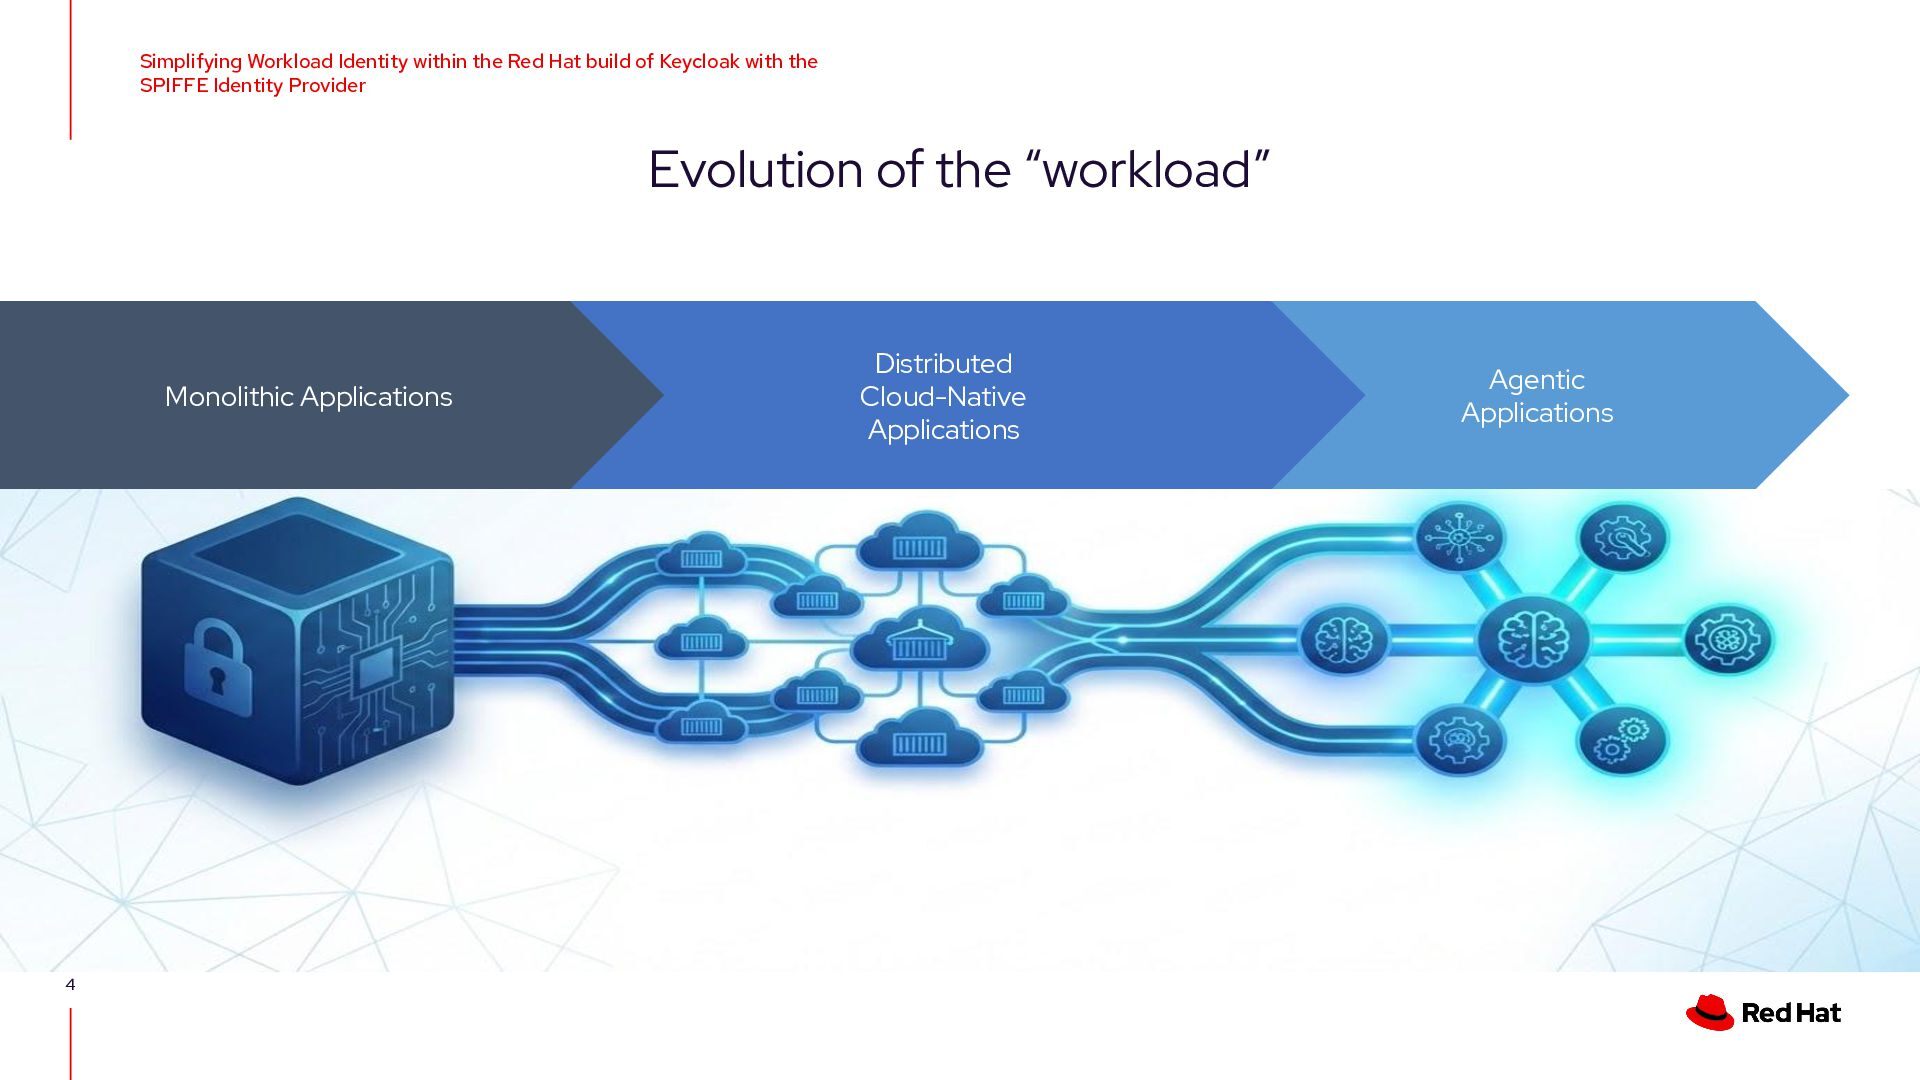
    with the SPIFFE Identity Provider Evolution of the “workload” Monolithic Applications 4 Distributed Cloud-Native Applications Agentic Applications
  5. Simplifying Workload Identity within the Red Hat build of Keycloak

    with the SPIFFE Identity Provider Zero Trust: set of principles enforcing least-privilege, per-request access 5
  6. Simplifying Workload Identity within the Red Hat build of Keycloak

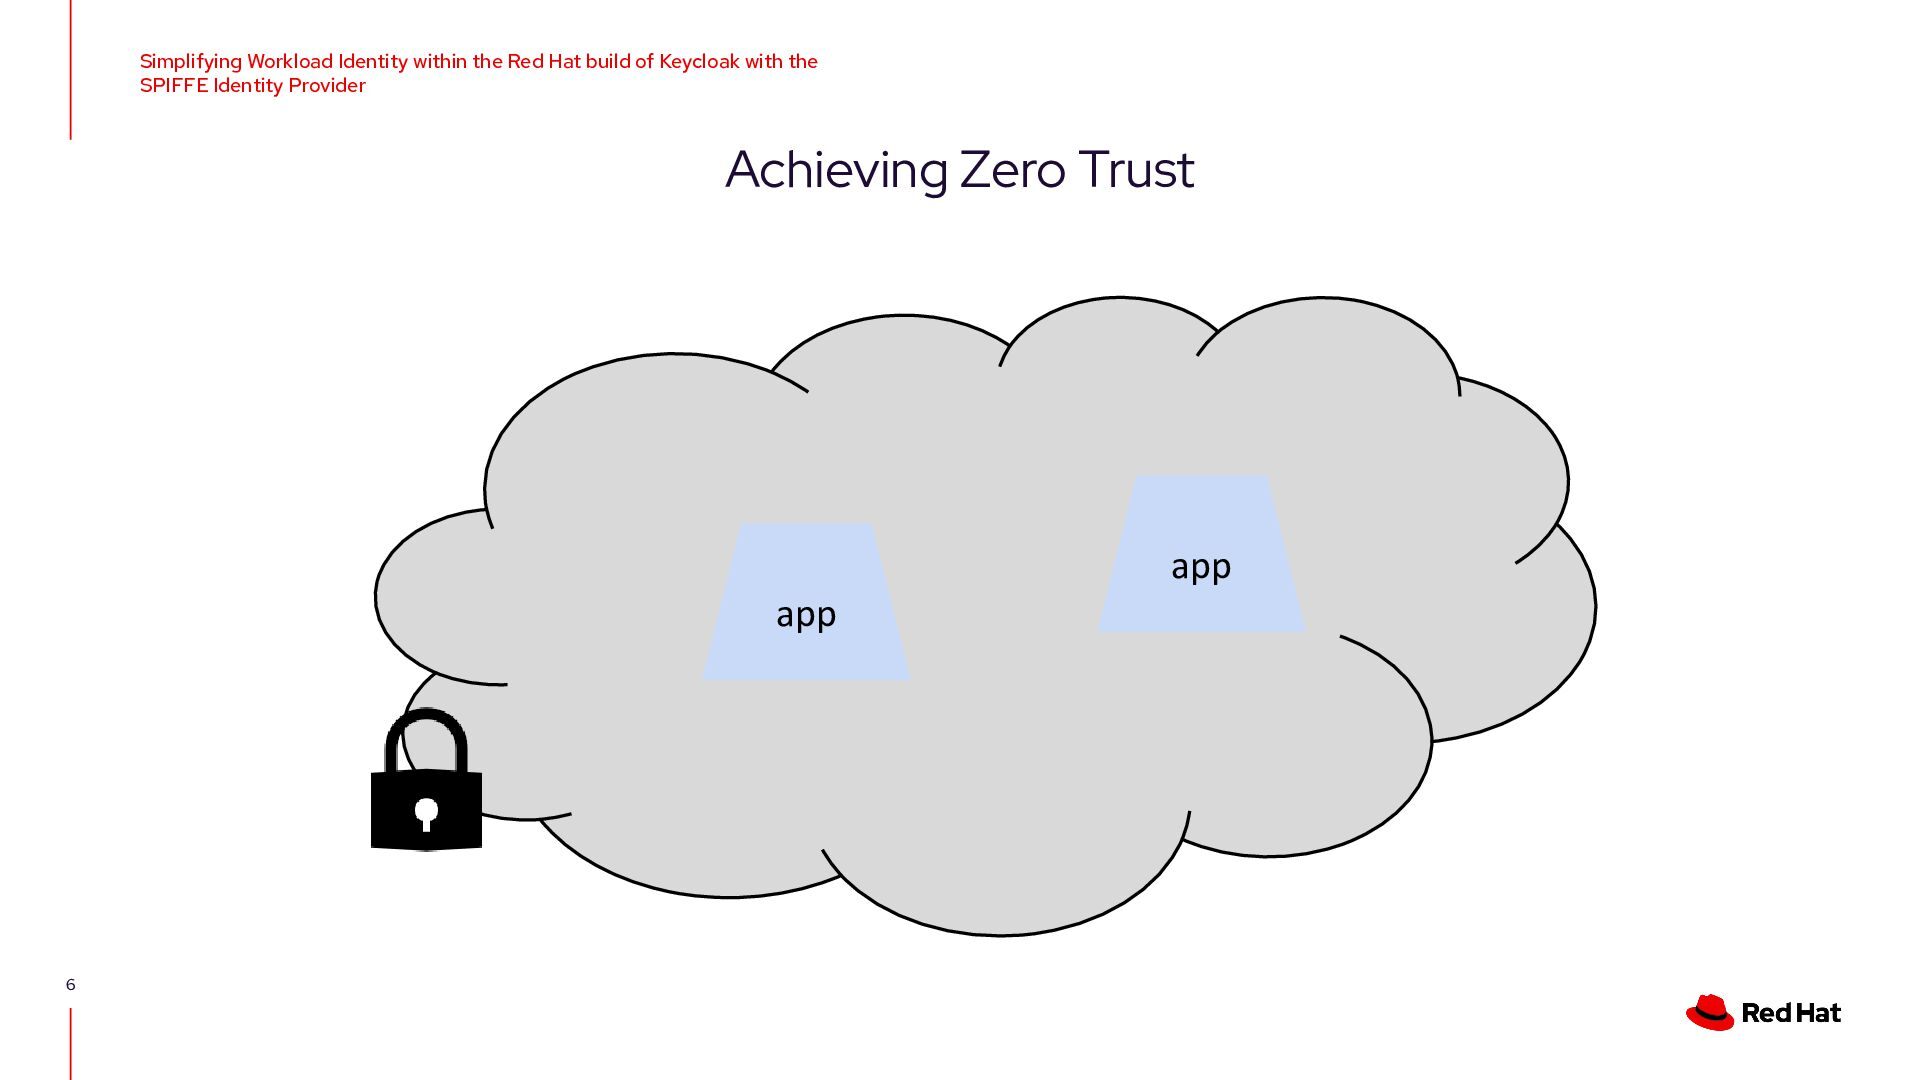
    with the SPIFFE Identity Provider Achieving Zero Trust app app 6
  7. Simplifying Workload Identity within the Red Hat build of Keycloak

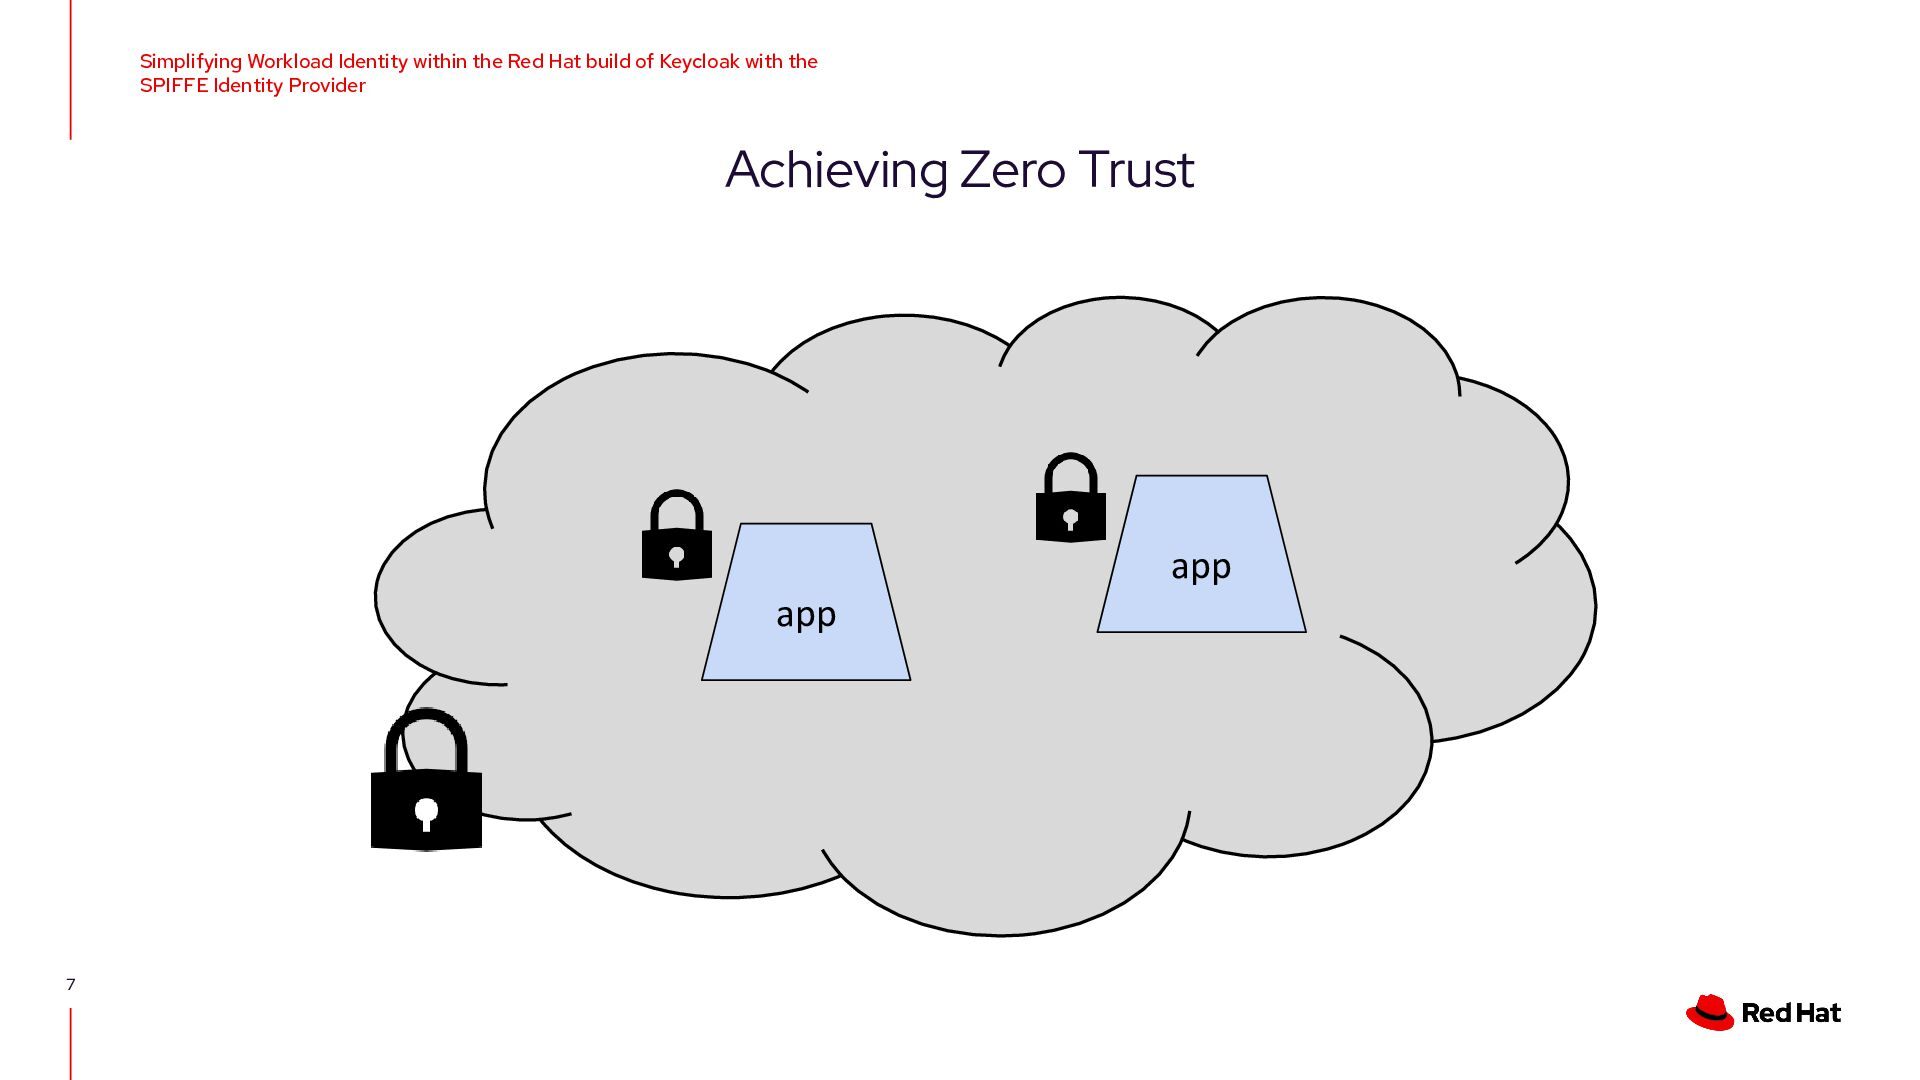
    with the SPIFFE Identity Provider Achieving Zero Trust app app 7
  8. Simplifying Workload Identity within the Red Hat build of Keycloak

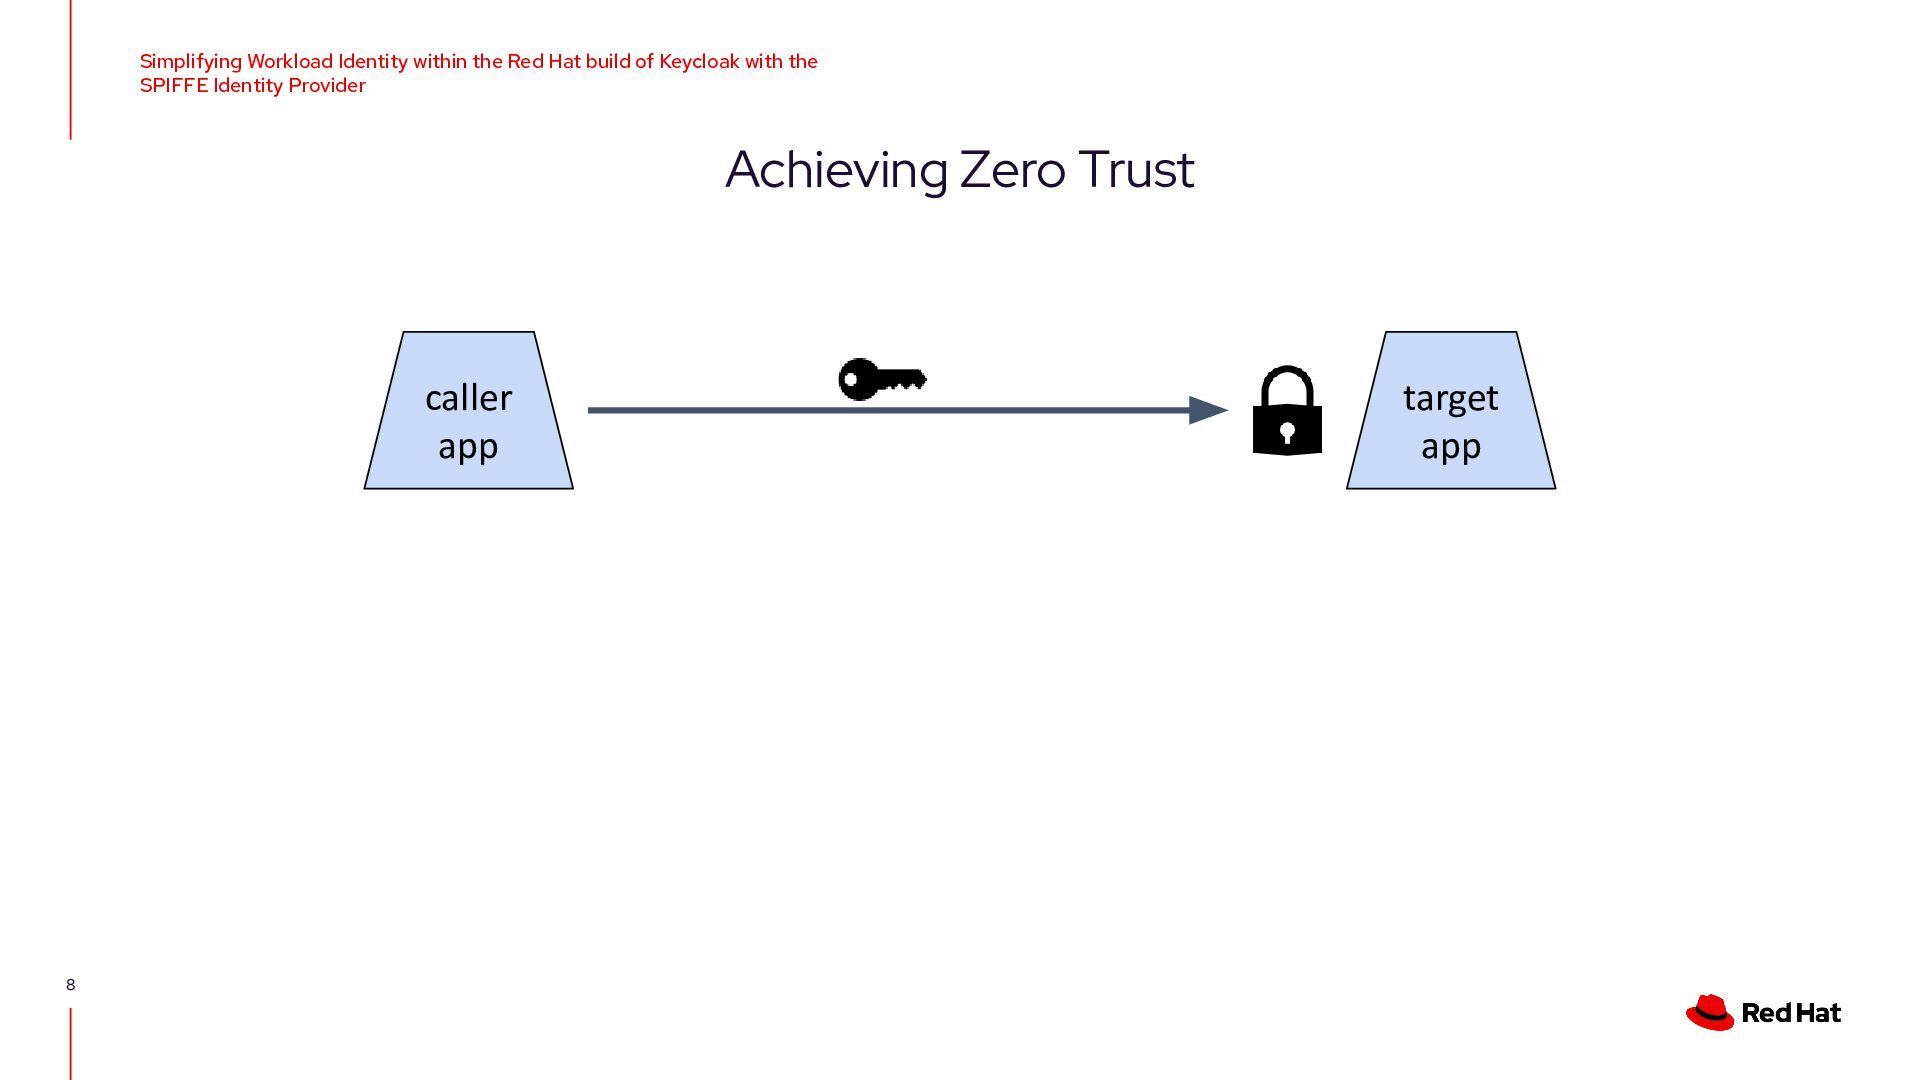
    with the SPIFFE Identity Provider Achieving Zero Trust caller app 8 target app
  9. Simplifying Workload Identity within the Red Hat build of Keycloak

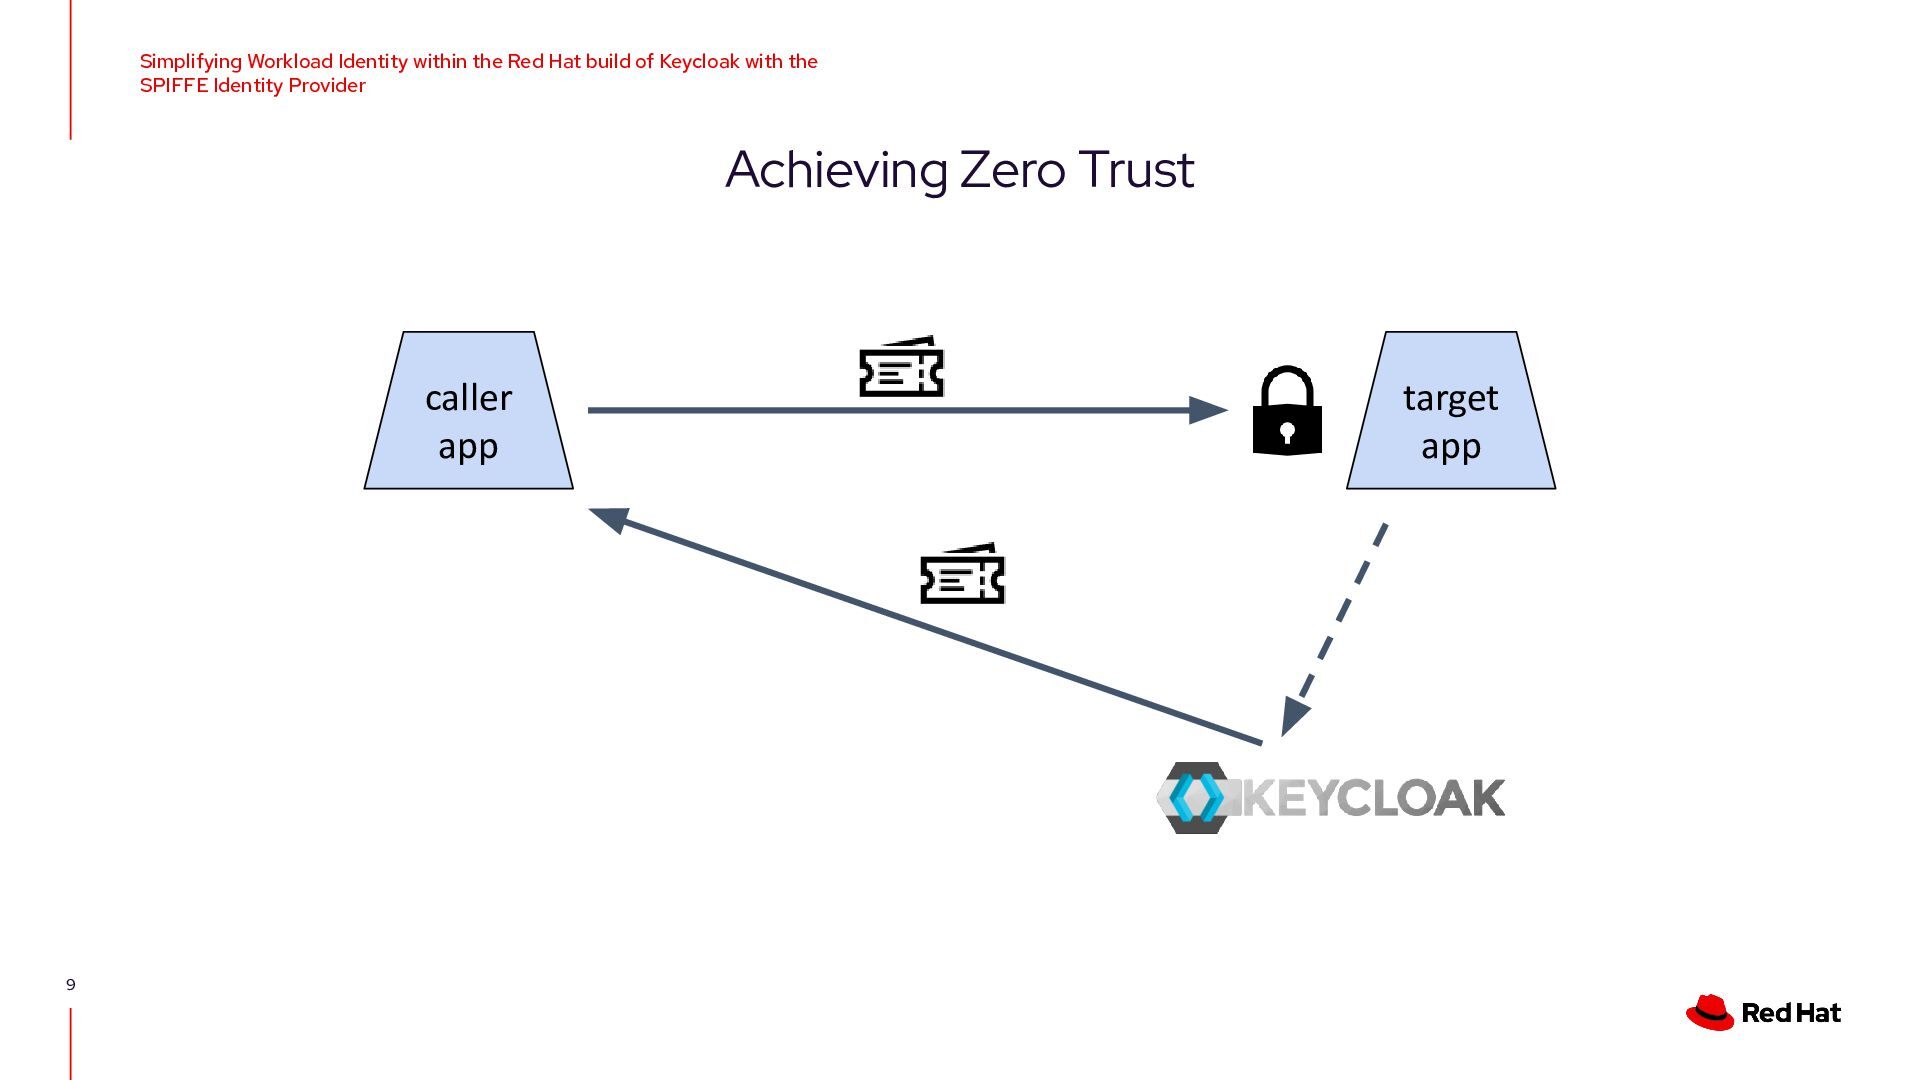
    with the SPIFFE Identity Provider Achieving Zero Trust caller app 9 target app
  10. Simplifying Workload Identity within the Red Hat build of Keycloak

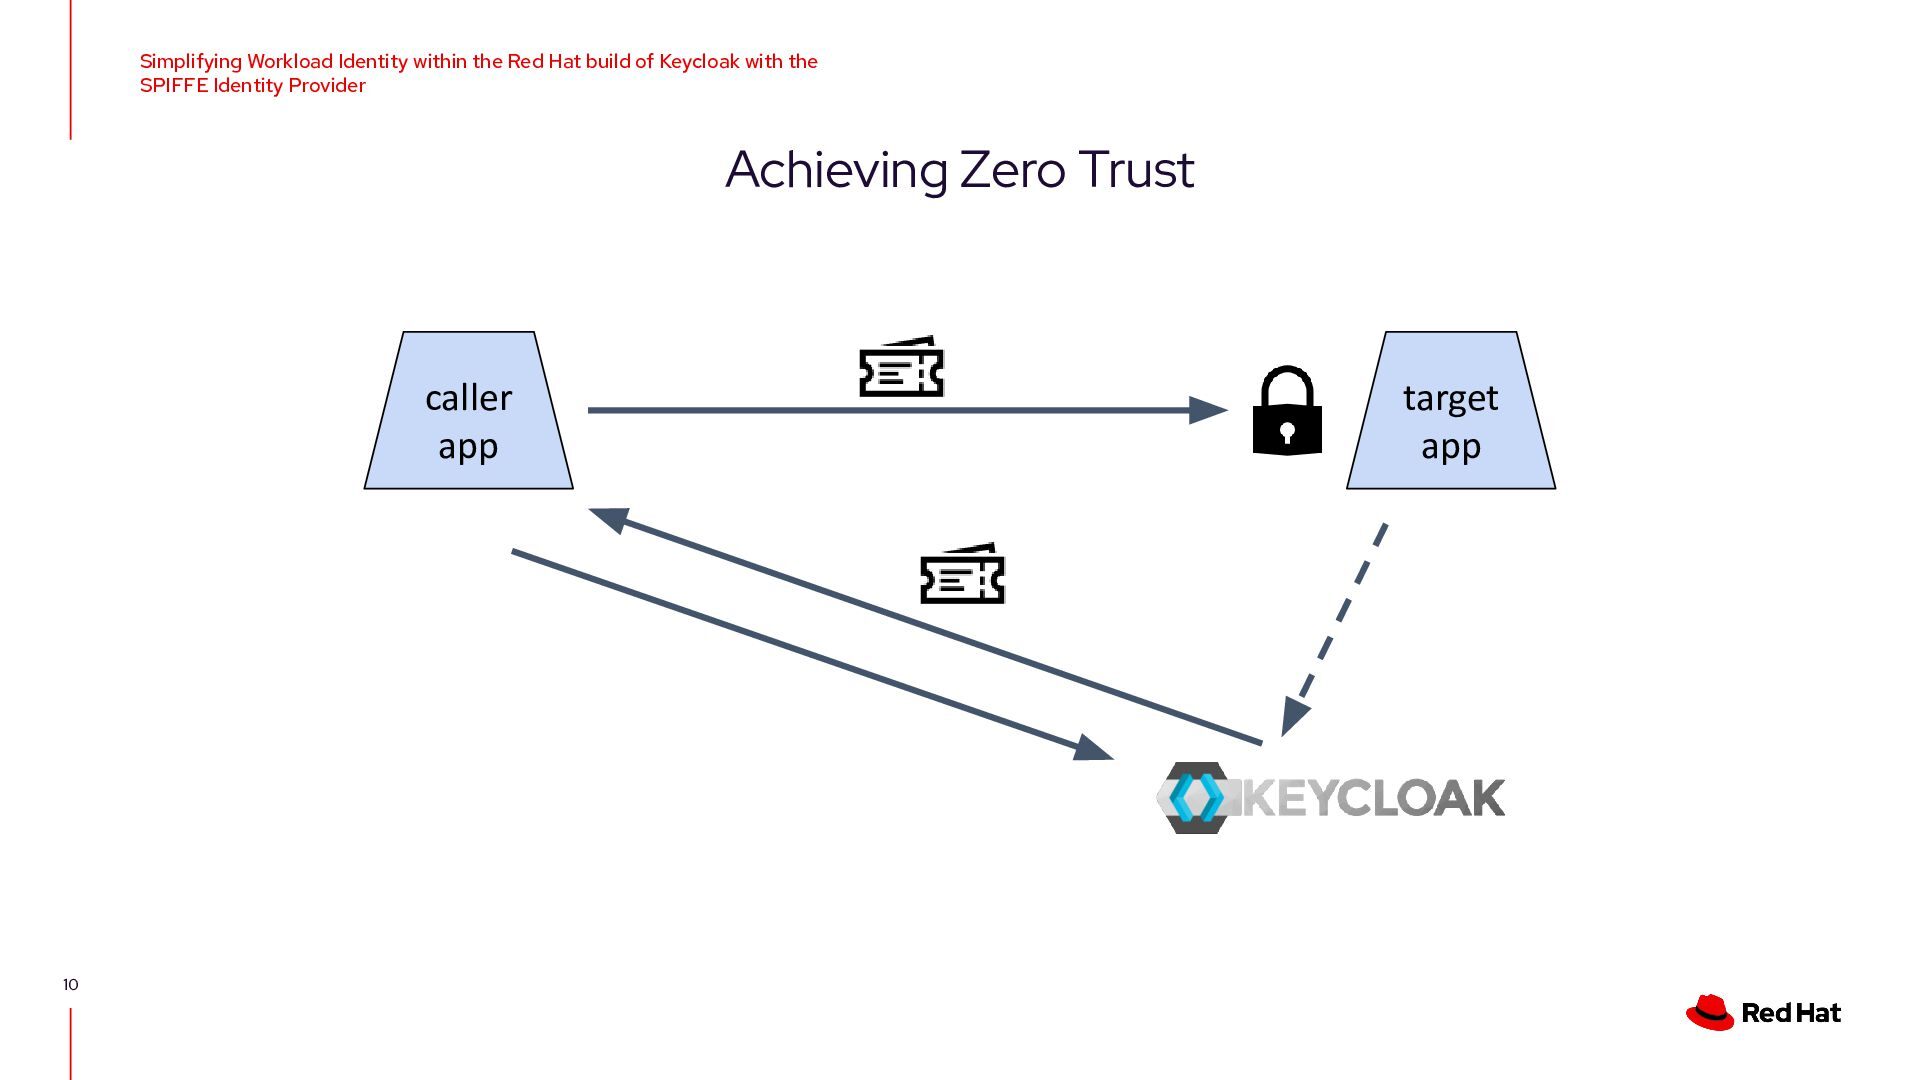
    with the SPIFFE Identity Provider Achieving Zero Trust caller app 10 target app
  11. Simplifying Workload Identity within the Red Hat build of Keycloak

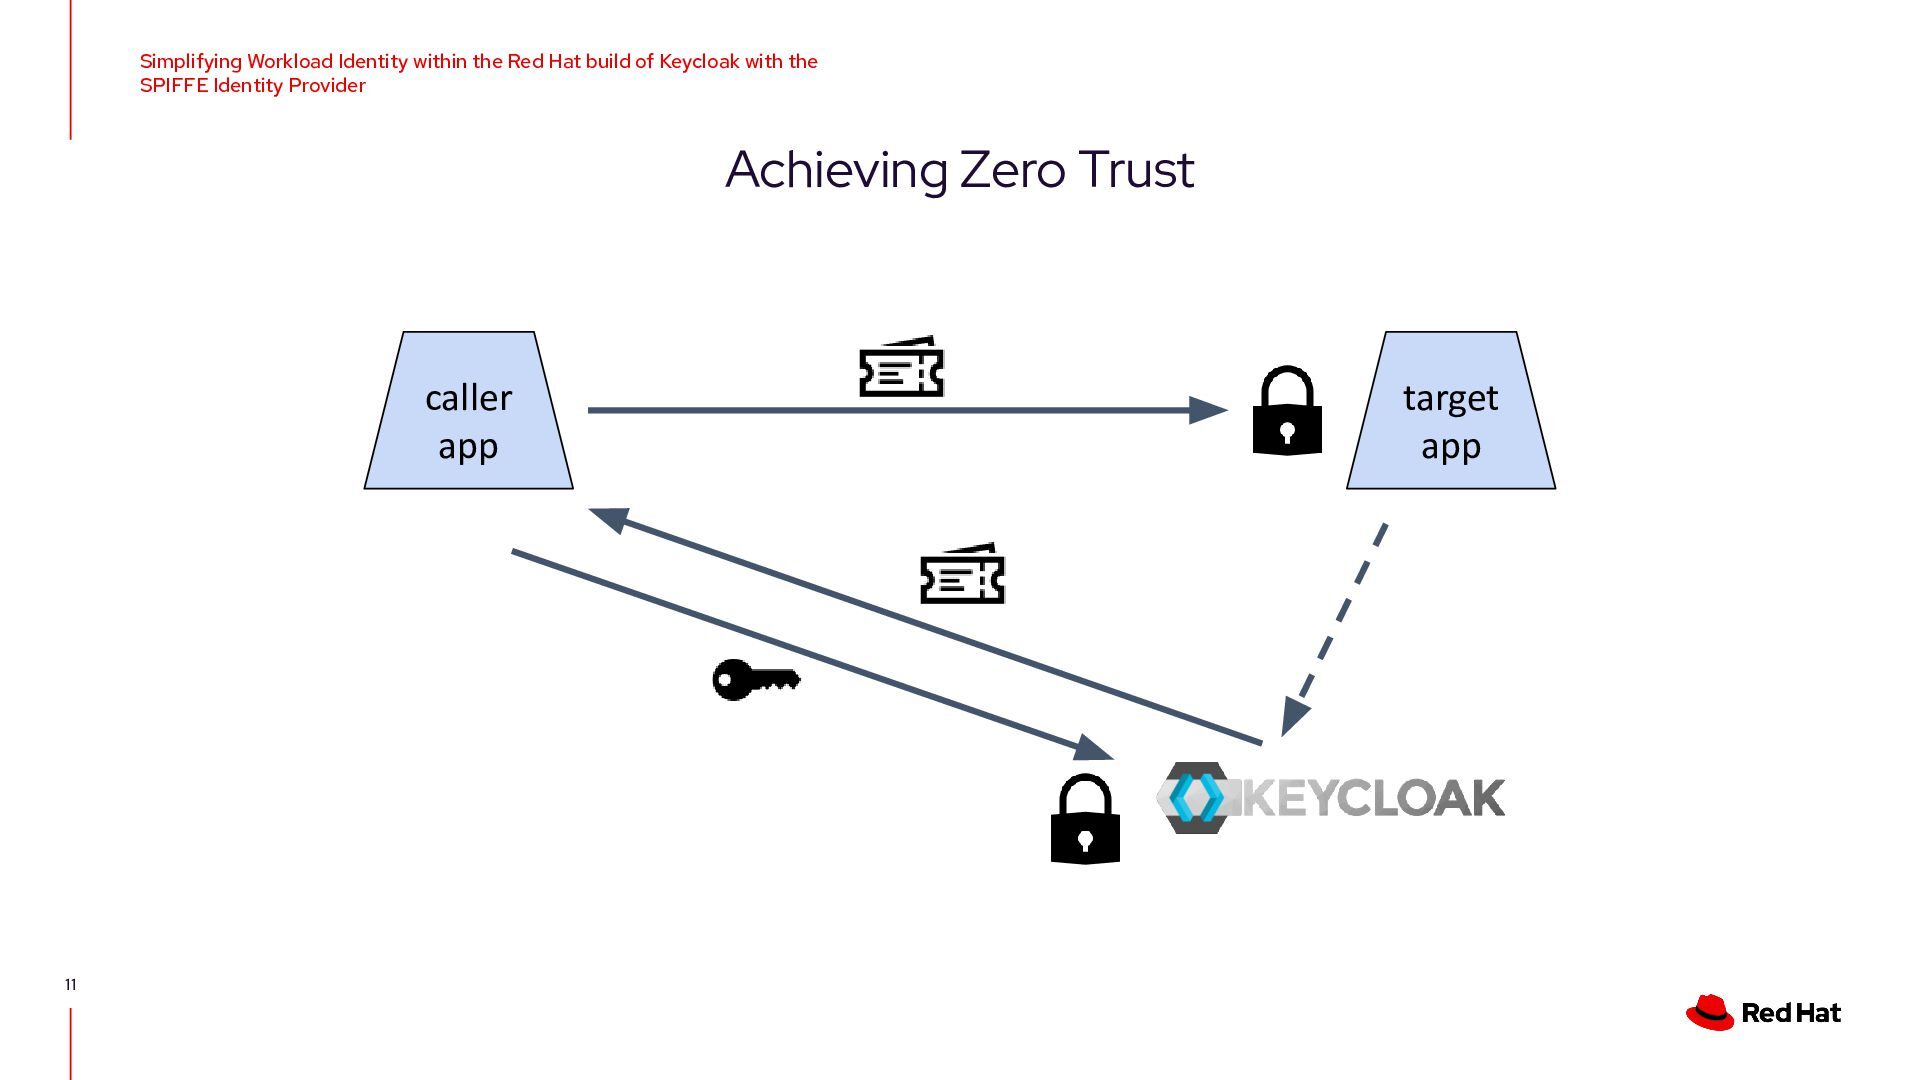
    with the SPIFFE Identity Provider Achieving Zero Trust caller app 11 target app
  12. Simplifying Workload Identity within the Red Hat build of Keycloak

    with the SPIFFE Identity Provider Crash Course on SPIFFE/SPIRE Secure Production Identity Framework For Everyone 12 SPIFFE Runtime Environment
  13. Simplifying Workload Identity within the Red Hat build of Keycloak

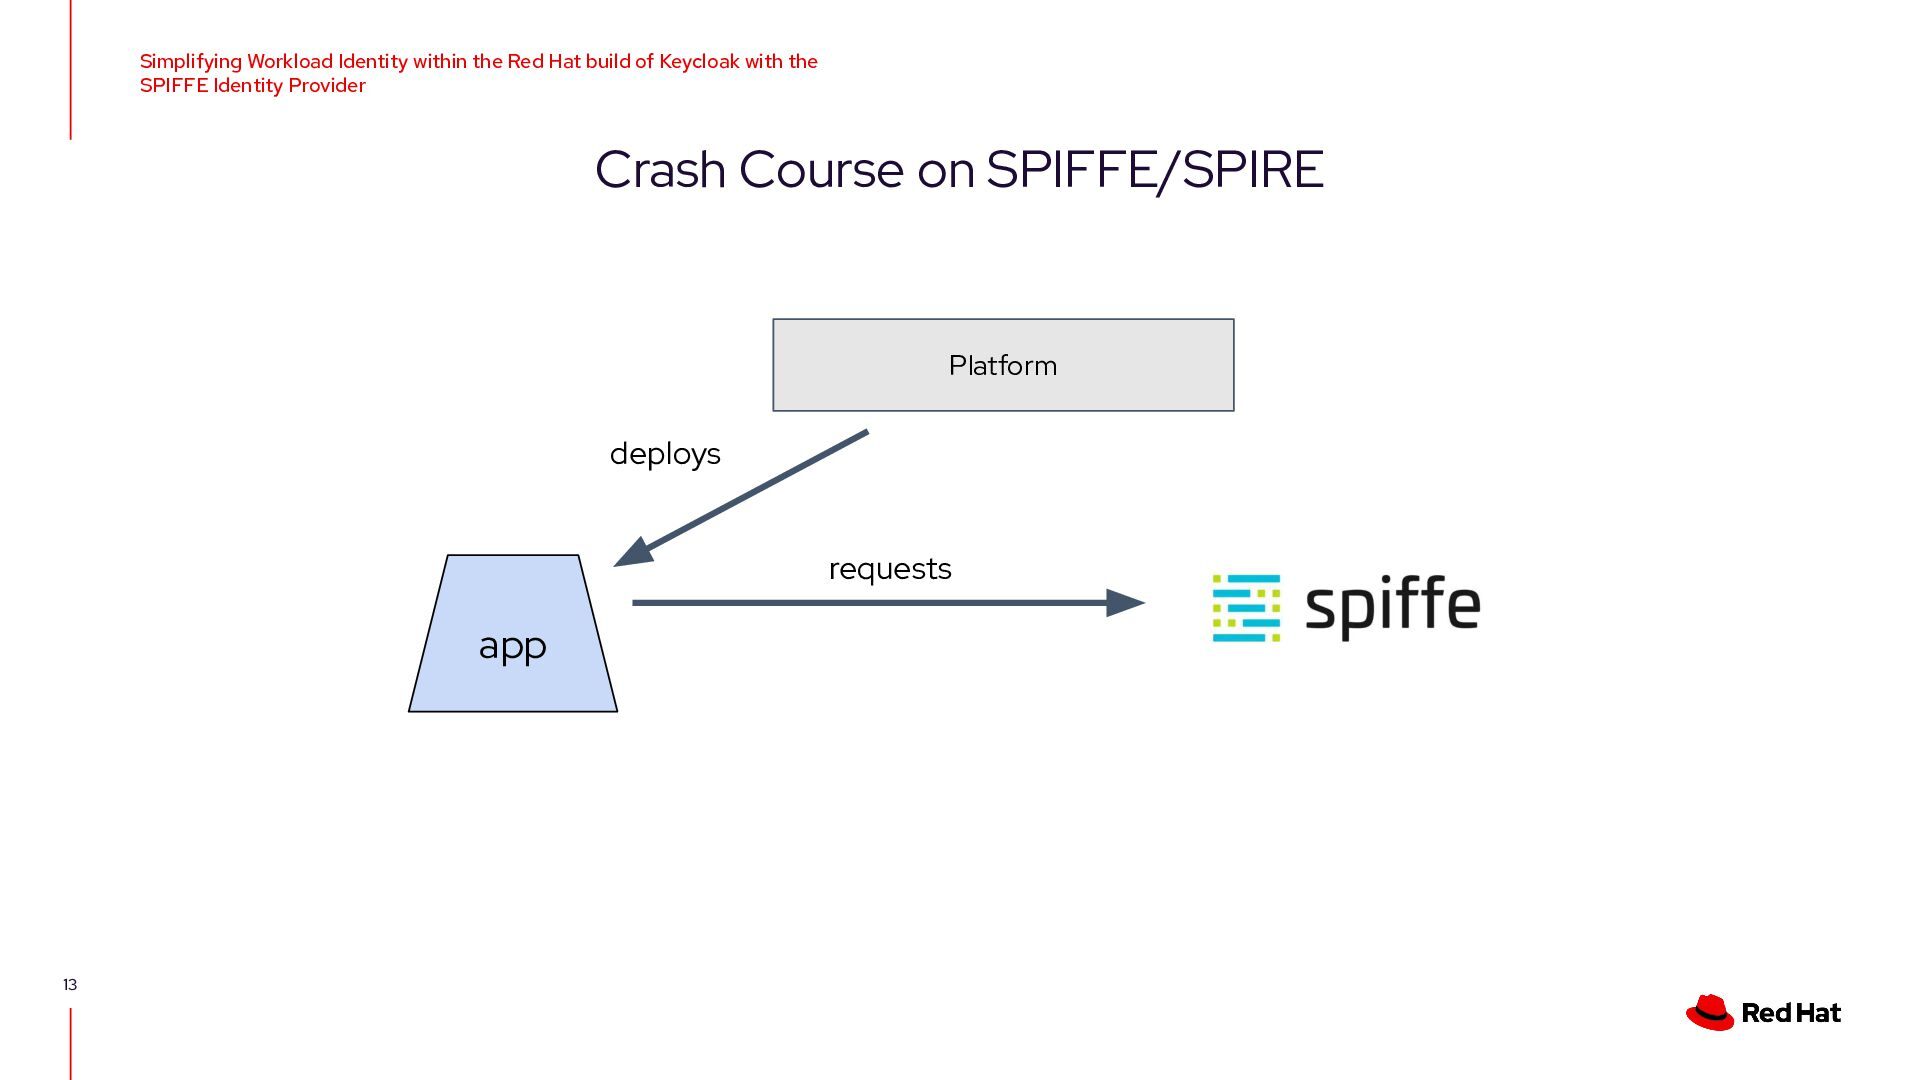
    with the SPIFFE Identity Provider Crash Course on SPIFFE/SPIRE Platform deploys requests app 13
  14. Simplifying Workload Identity within the Red Hat build of Keycloak

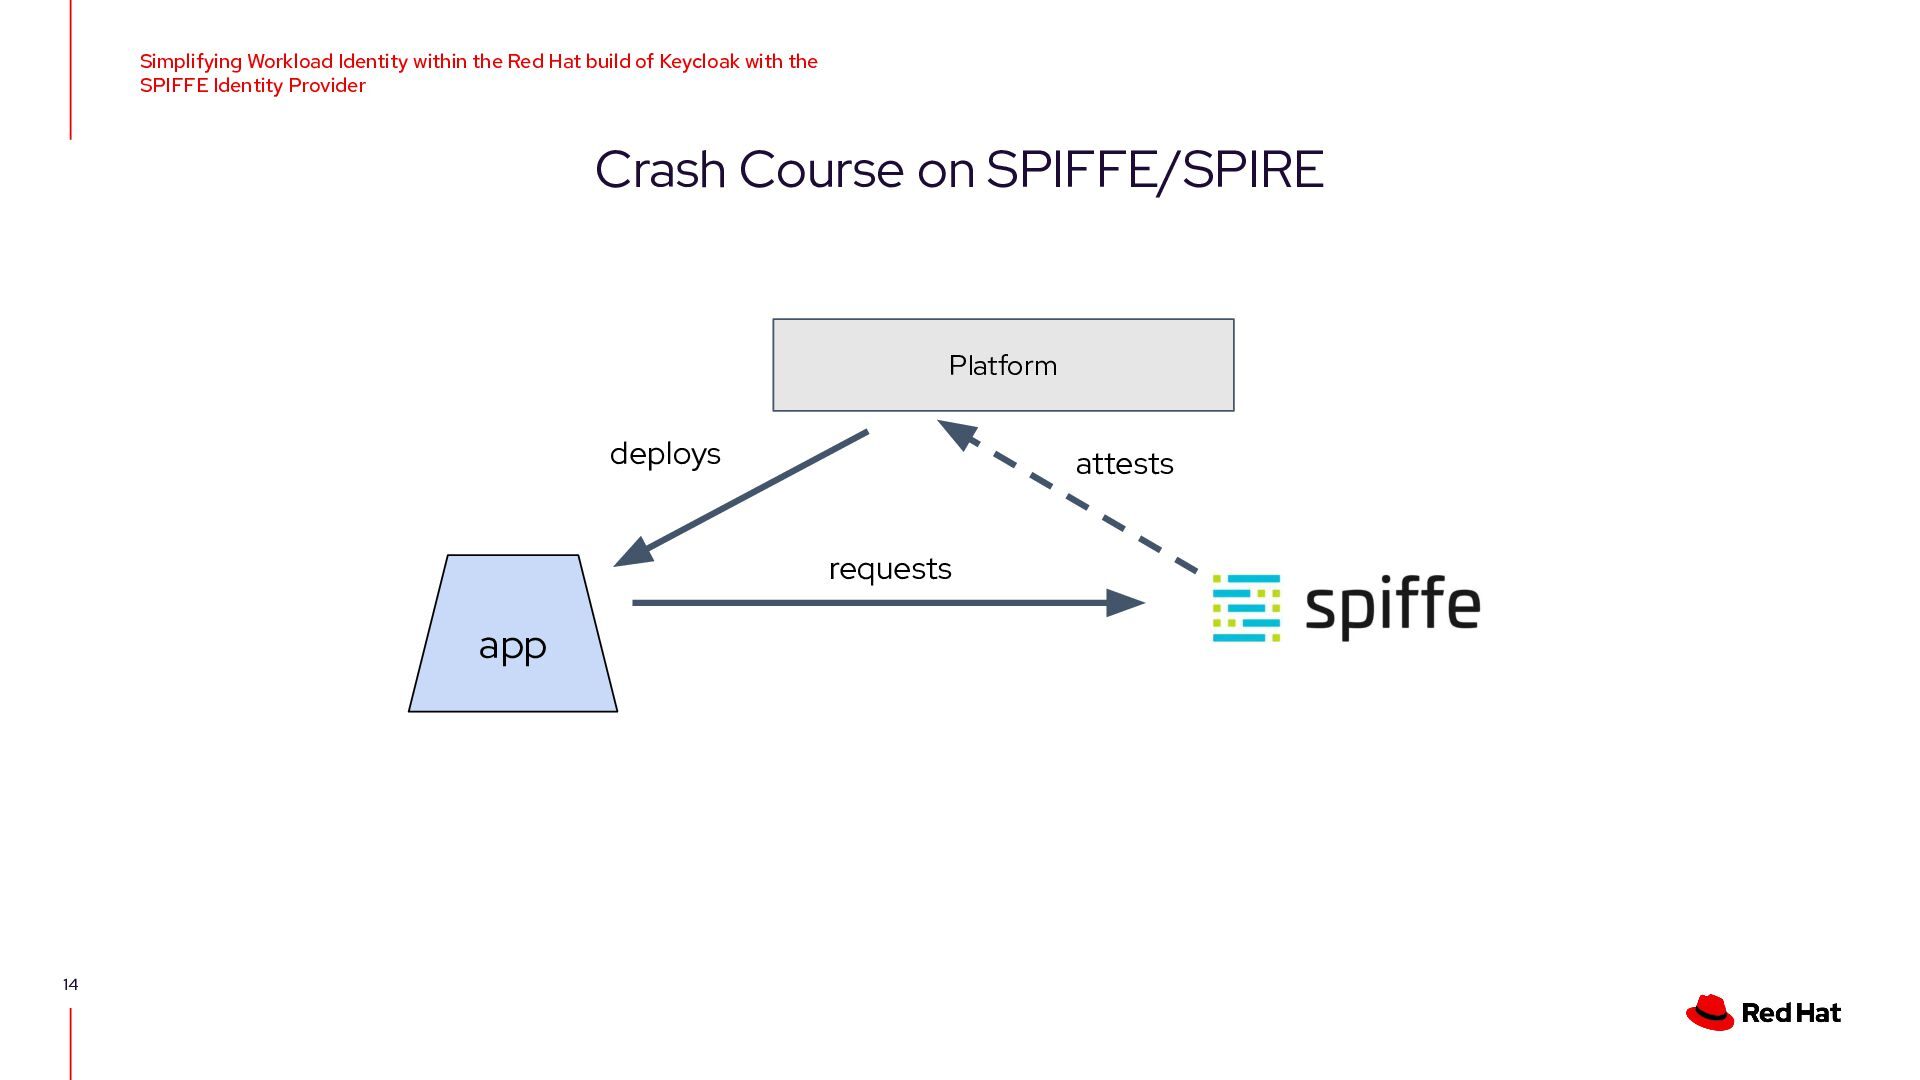
    with the SPIFFE Identity Provider Crash Course on SPIFFE/SPIRE Platform deploys attests requests app 14
  15. Simplifying Workload Identity within the Red Hat build of Keycloak

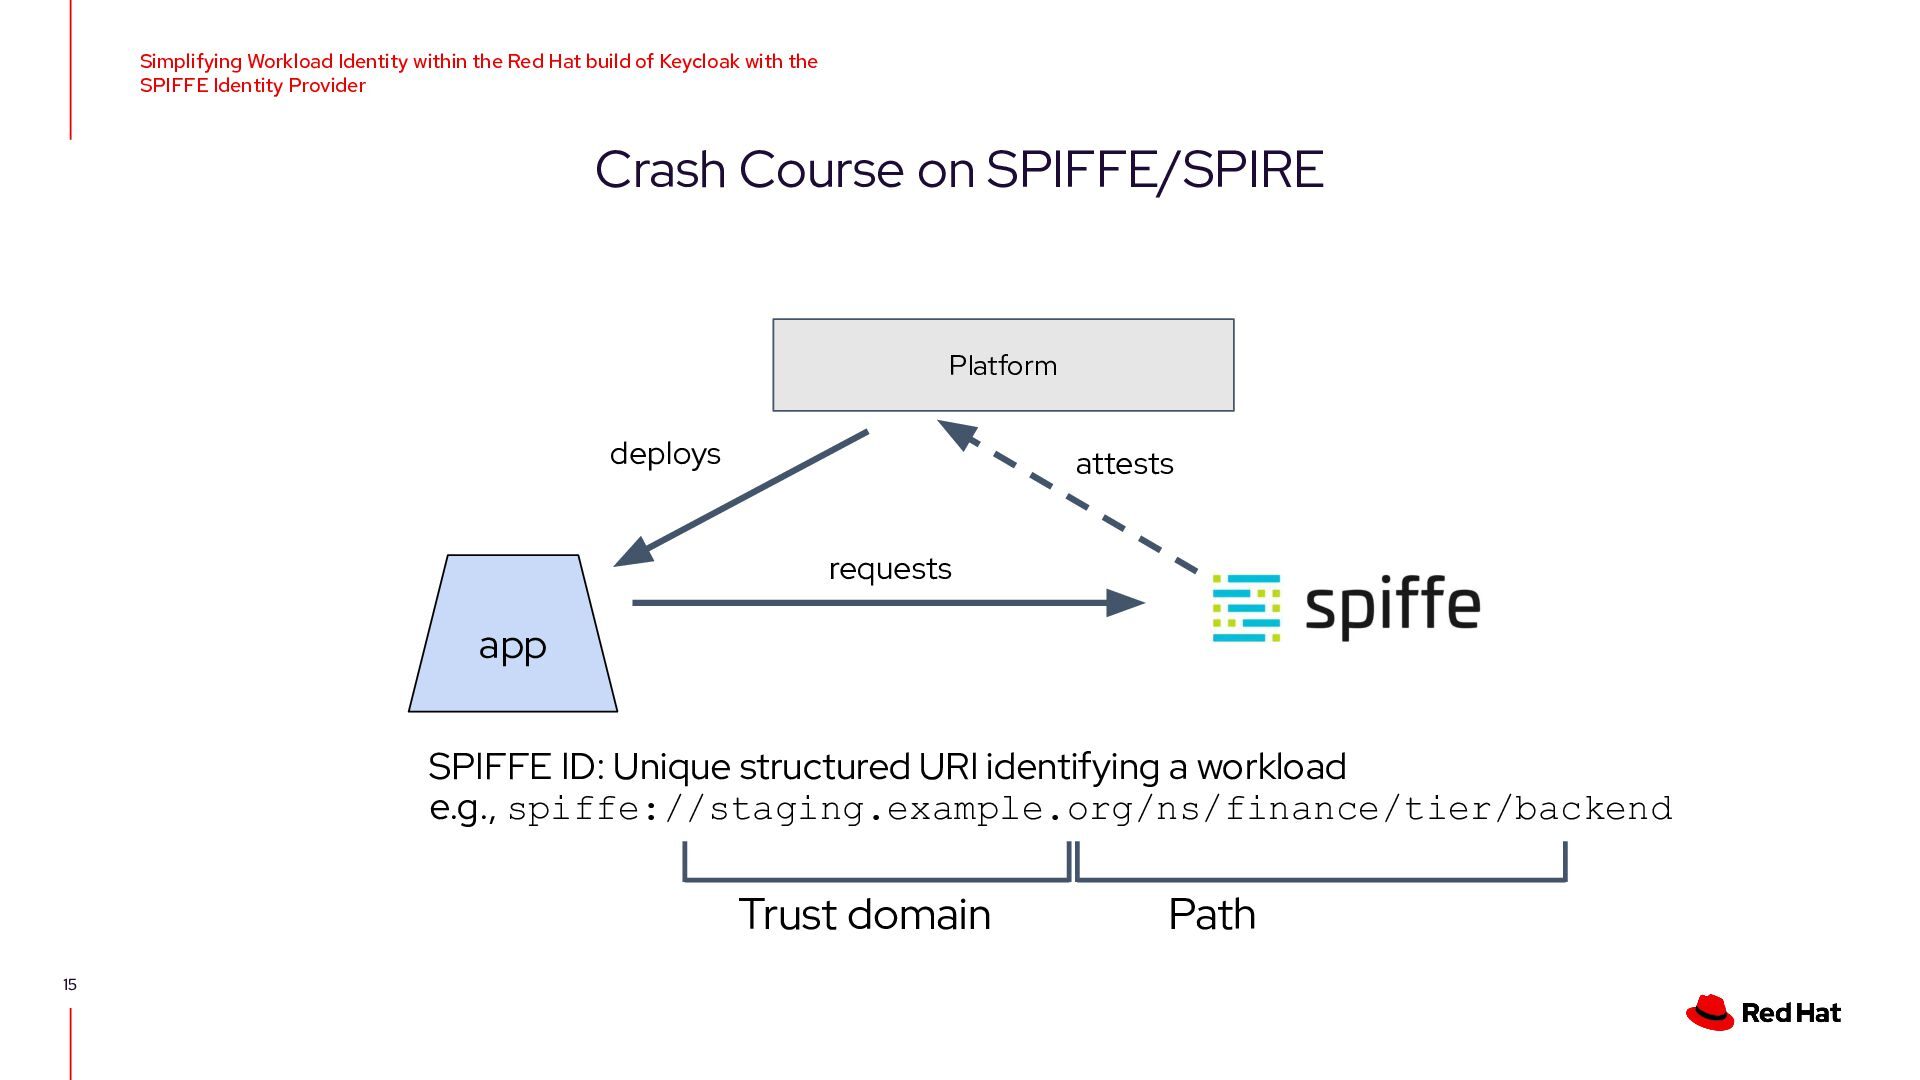
    with the SPIFFE Identity Provider Crash Course on SPIFFE/SPIRE Platform deploys attests requests app SPIFFE ID: Unique structured URI identifying a workload e.g., spiffe://staging.example.org/ns/finance/tier/backend Trust domain 15 Path
  16. Simplifying Workload Identity within the Red Hat build of Keycloak

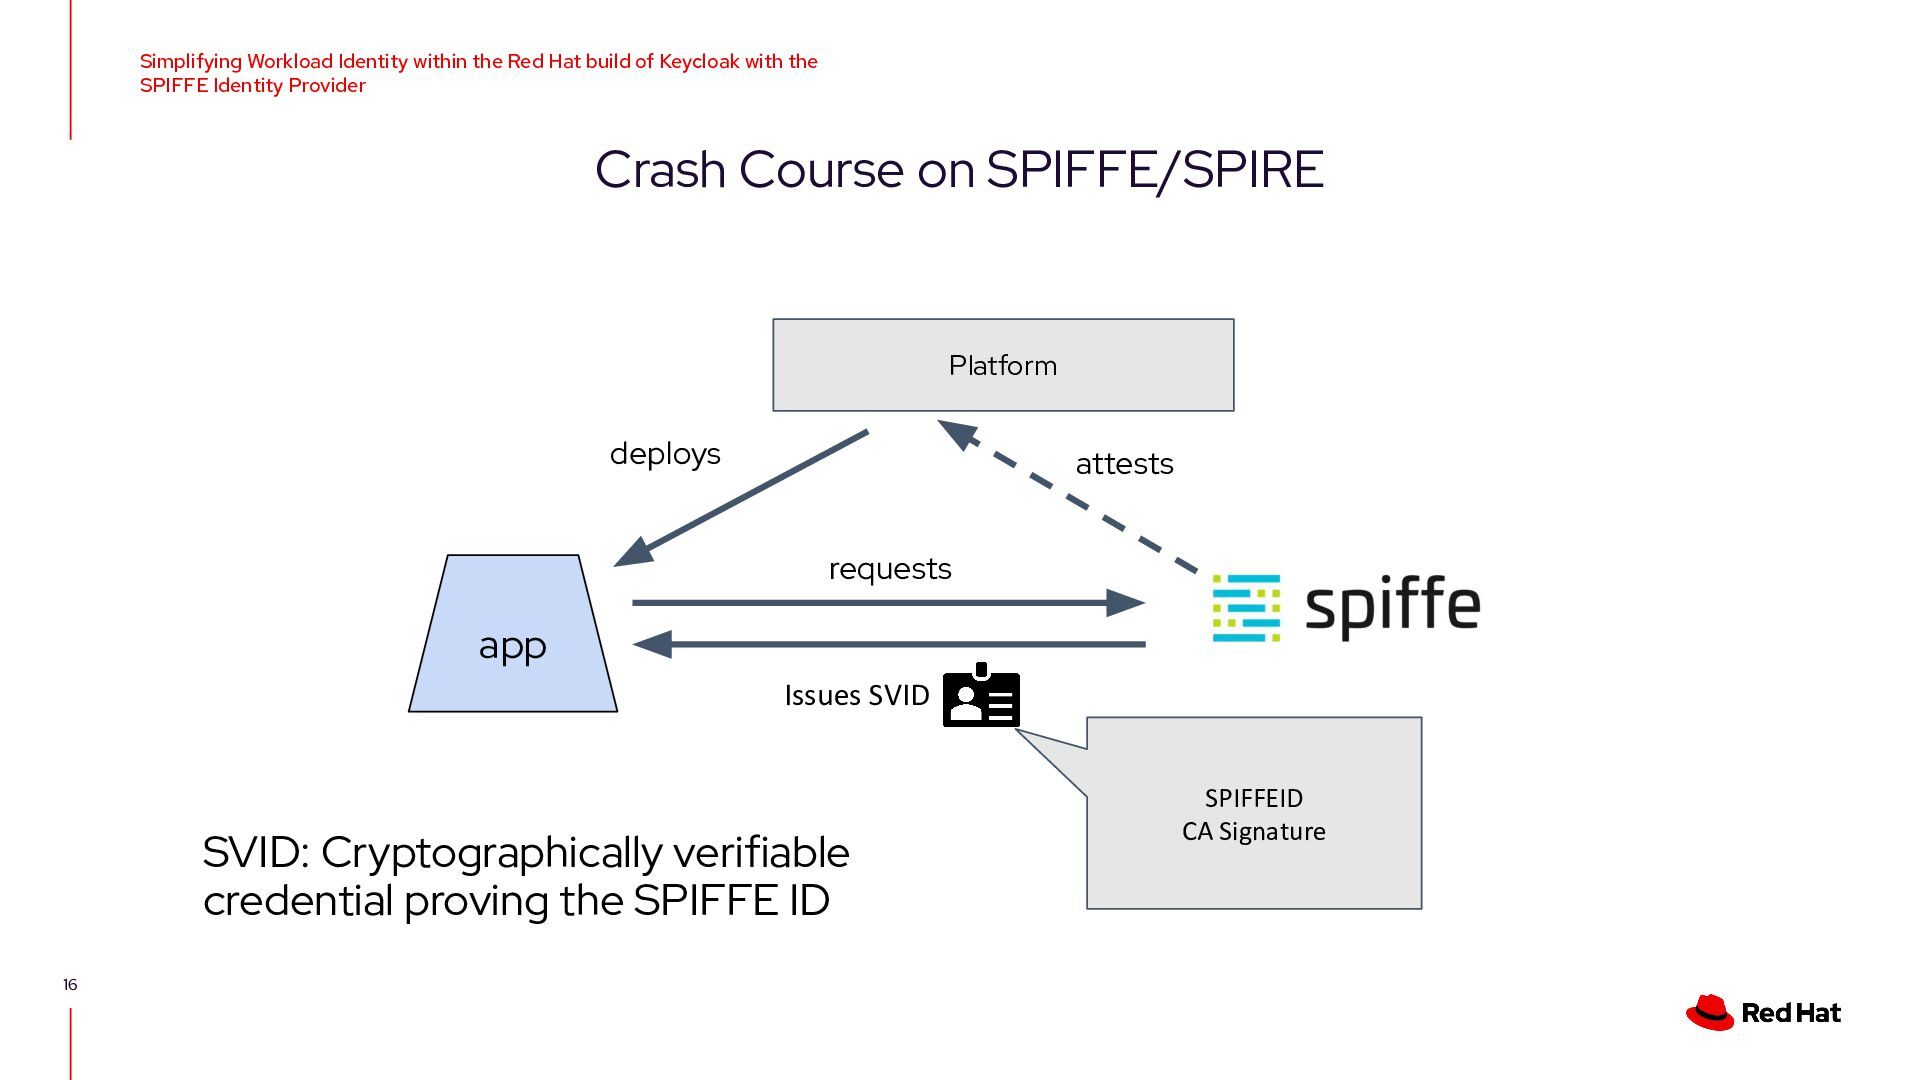
    with the SPIFFE Identity Provider Crash Course on SPIFFE/SPIRE Platform deploys attests requests app Issues SVID SVID: Cryptographically verifiable credential proving the SPIFFE ID 16 SPIFFEID CA Signature
  17. Simplifying Workload Identity within the Red Hat build of Keycloak

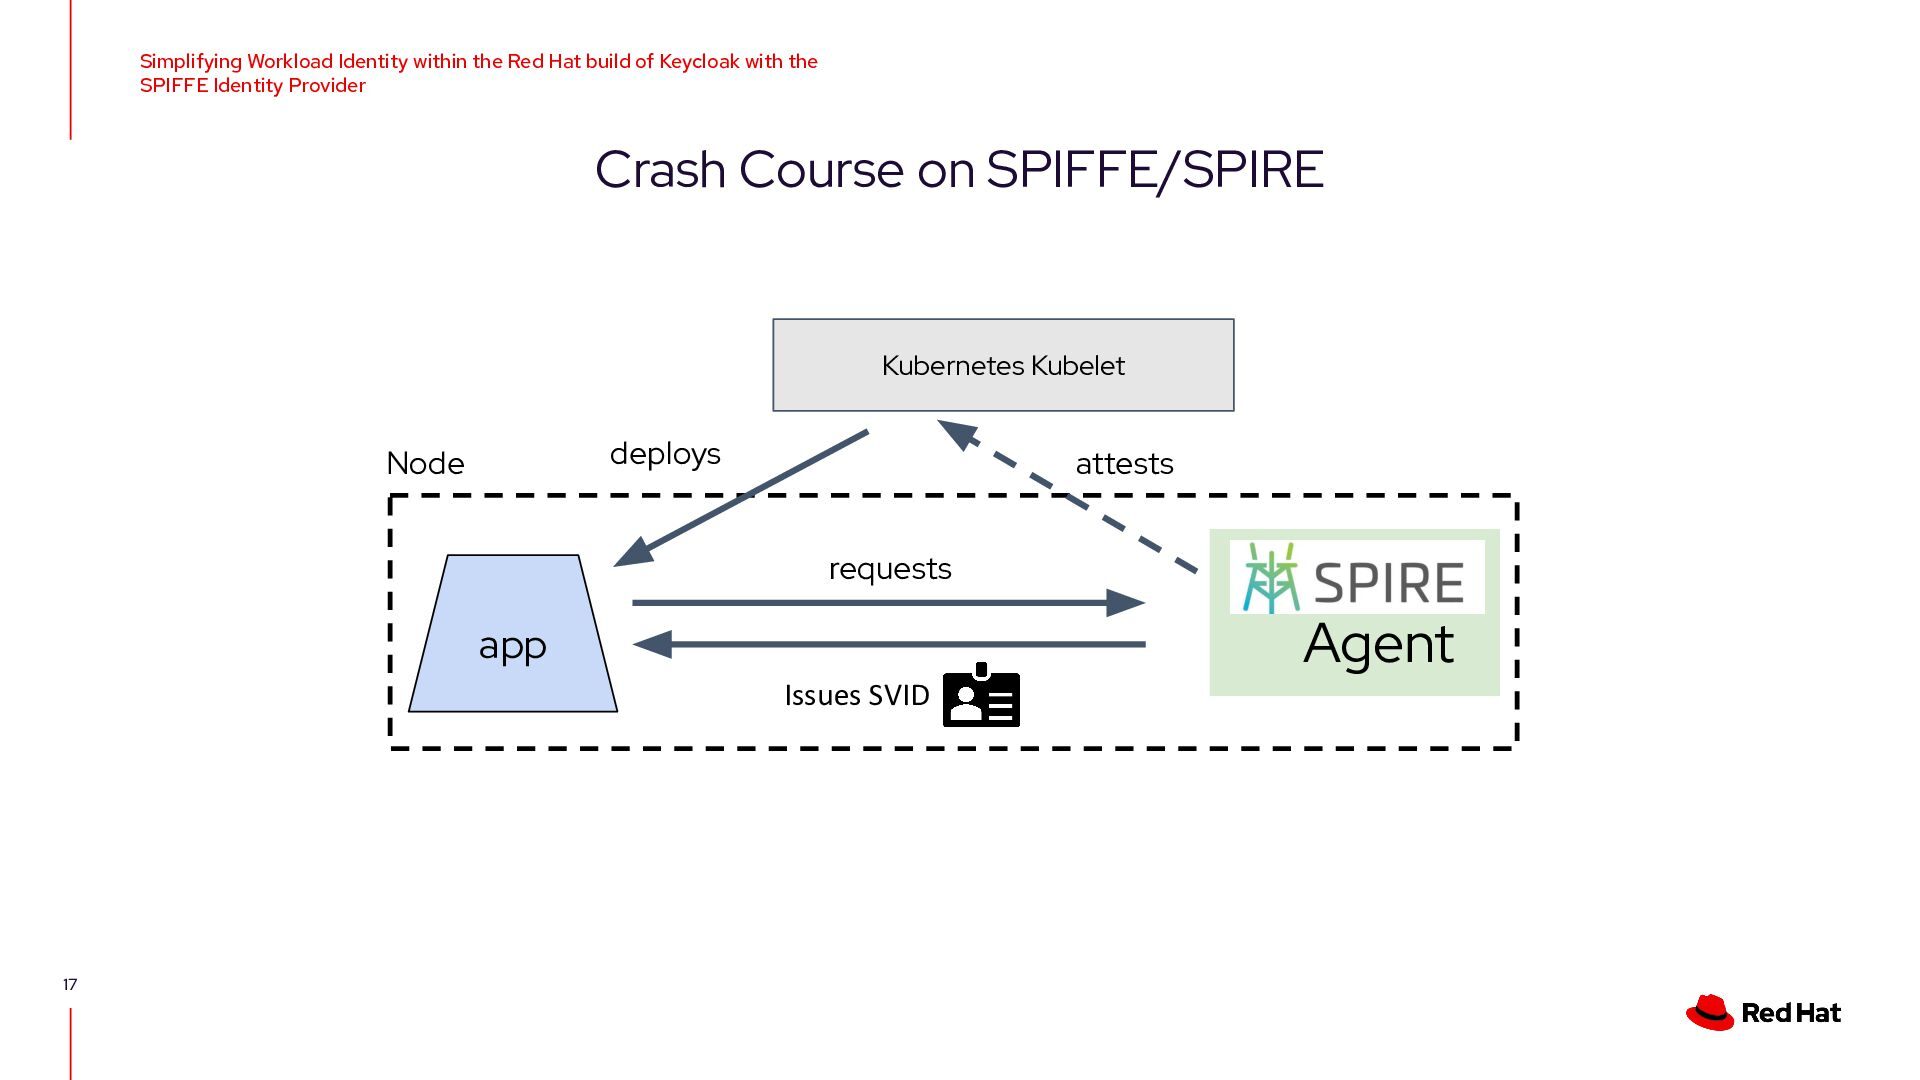
    with the SPIFFE Identity Provider Crash Course on SPIFFE/SPIRE Kubernetes Kubelet deploys Node attests requests Agent app Issues SVID 17
  18. Simplifying Workload Identity within the Red Hat build of Keycloak

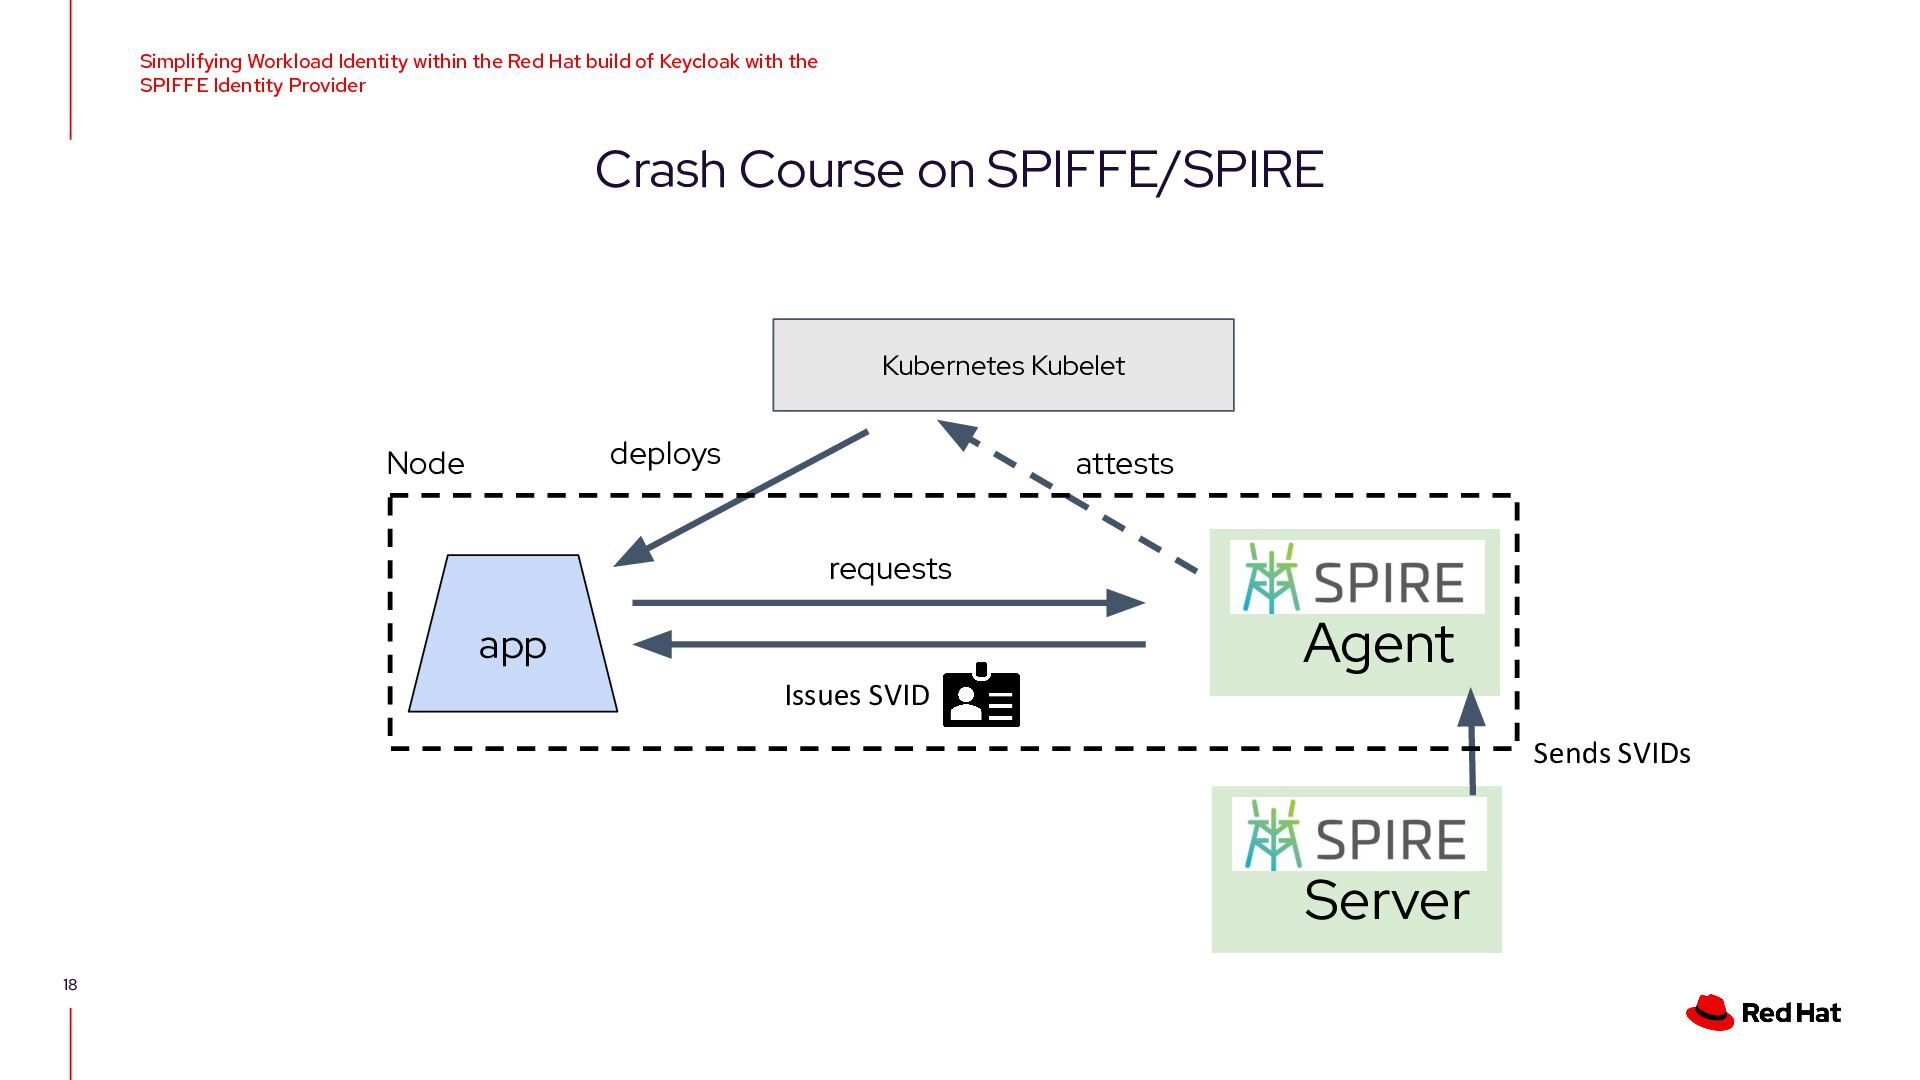
    with the SPIFFE Identity Provider Crash Course on SPIFFE/SPIRE Kubernetes Kubelet deploys Node attests requests Agent app Issues SVID Sends SVIDs Server 18
  19. Simplifying Workload Identity within the Red Hat build of Keycloak

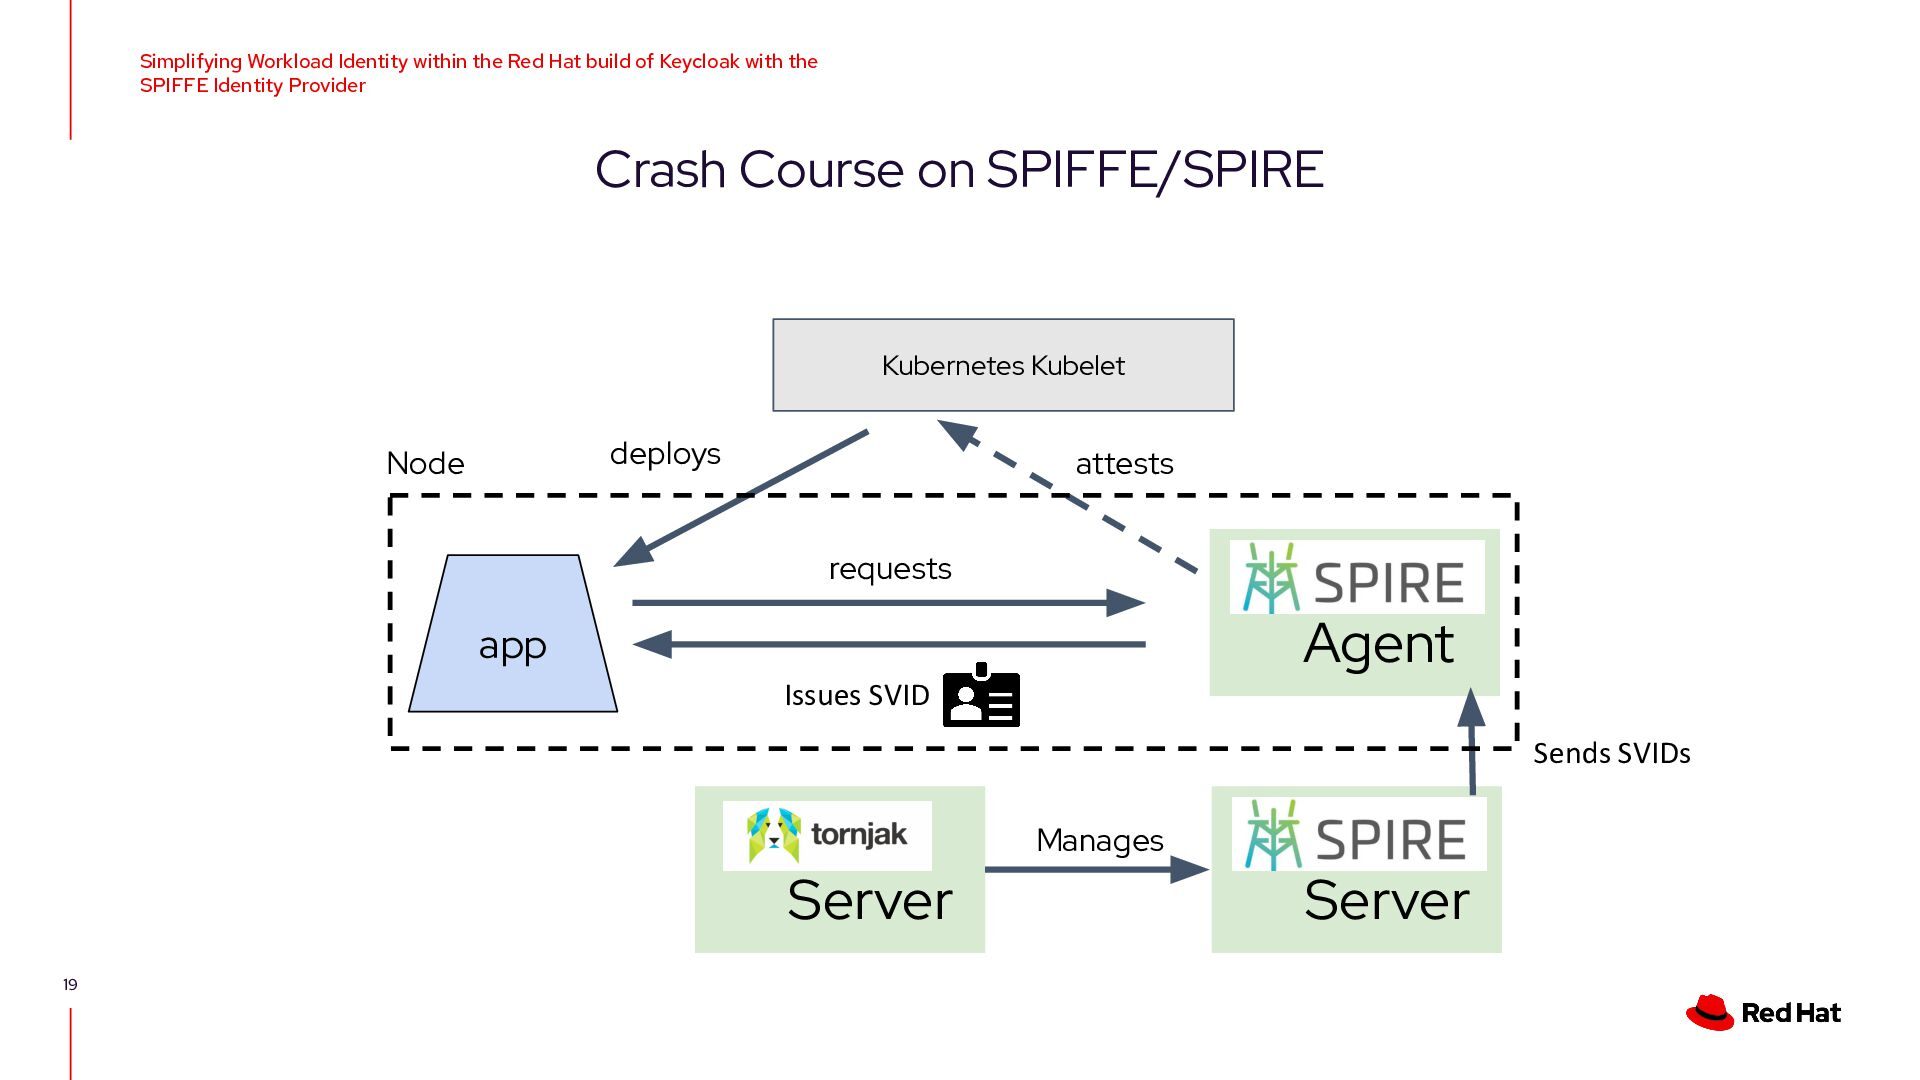
    with the SPIFFE Identity Provider Crash Course on SPIFFE/SPIRE Kubernetes Kubelet deploys Node attests requests Agent app Issues SVID Sends SVIDs Manages Server 19 Server
  20. Simplifying Workload Identity within the Red Hat build of Keycloak

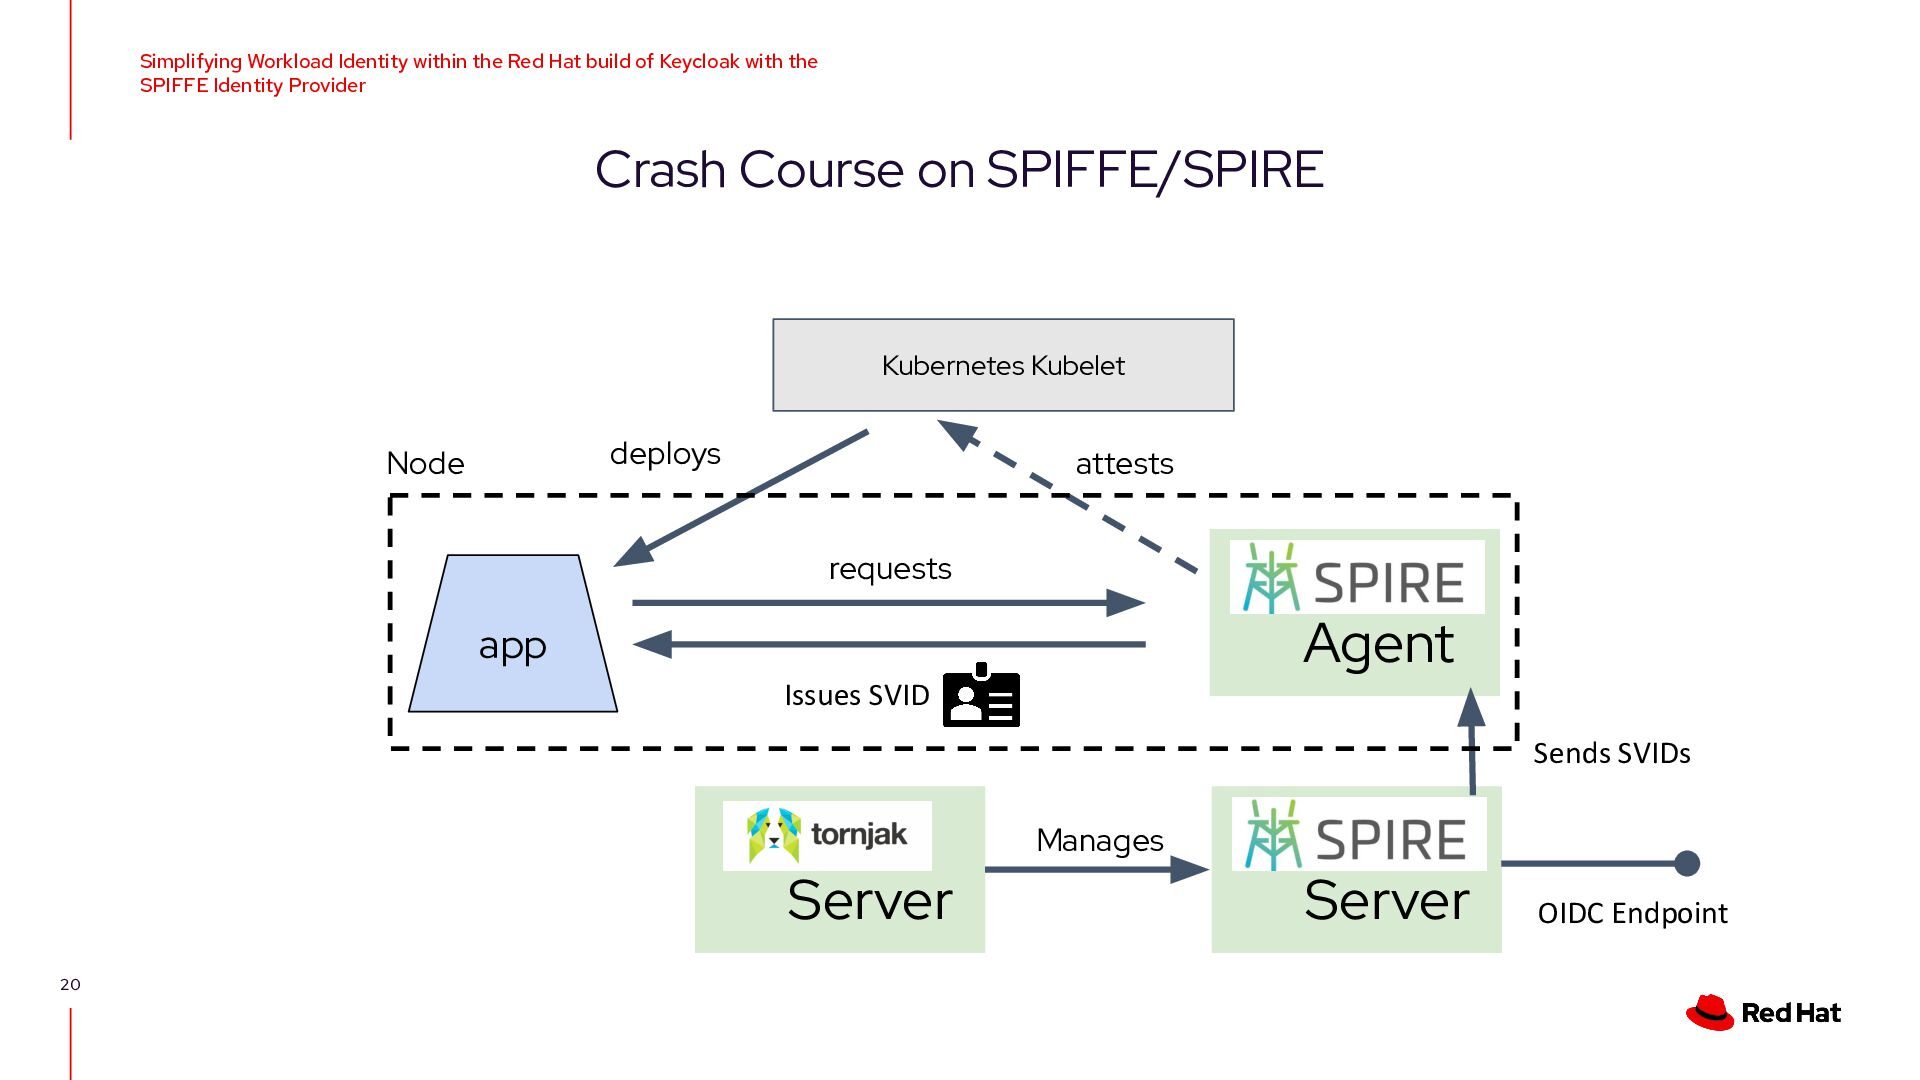
    with the SPIFFE Identity Provider Crash Course on SPIFFE/SPIRE Kubernetes Kubelet deploys Node attests requests Agent app Issues SVID Sends SVIDs Manages Server 20 Server OIDC Endpoint
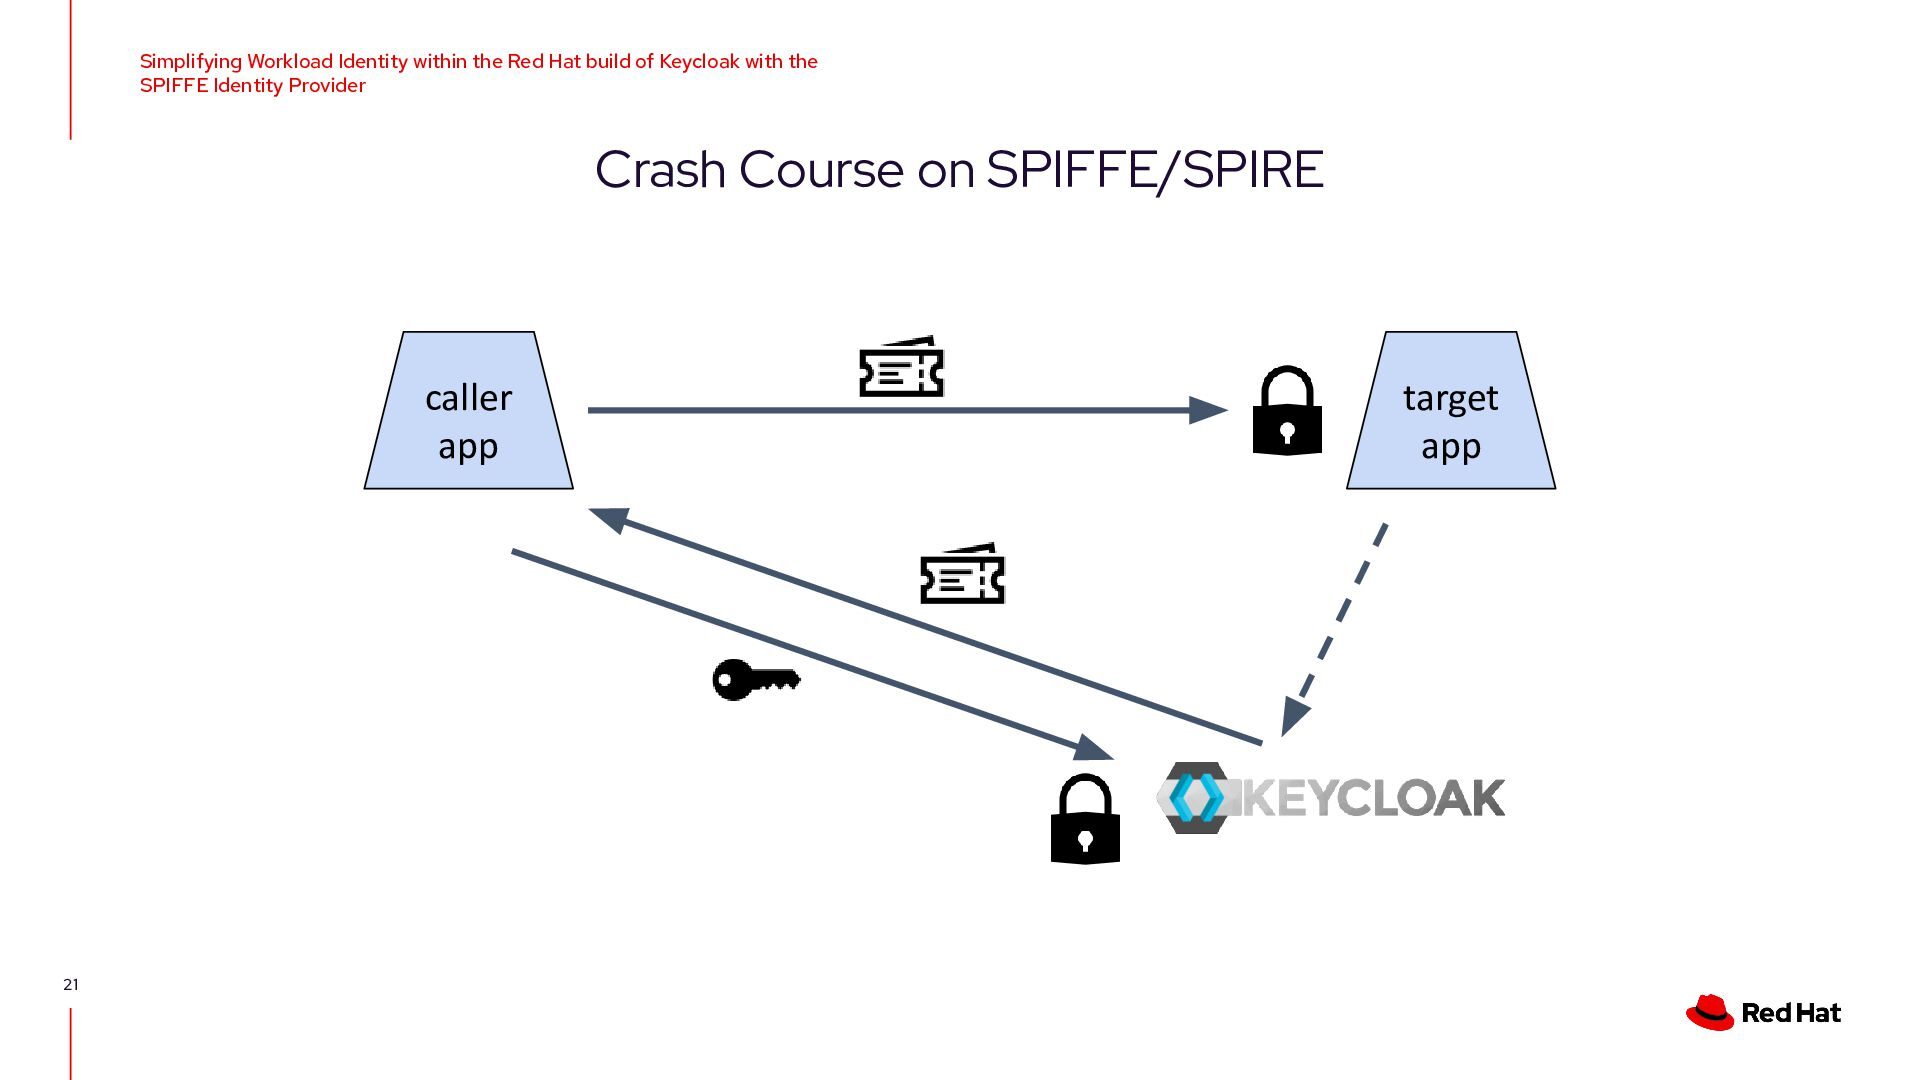
  21. Simplifying Workload Identity within the Red Hat build of Keycloak

    with the SPIFFE Identity Provider Crash Course on SPIFFE/SPIRE caller app 21 target app
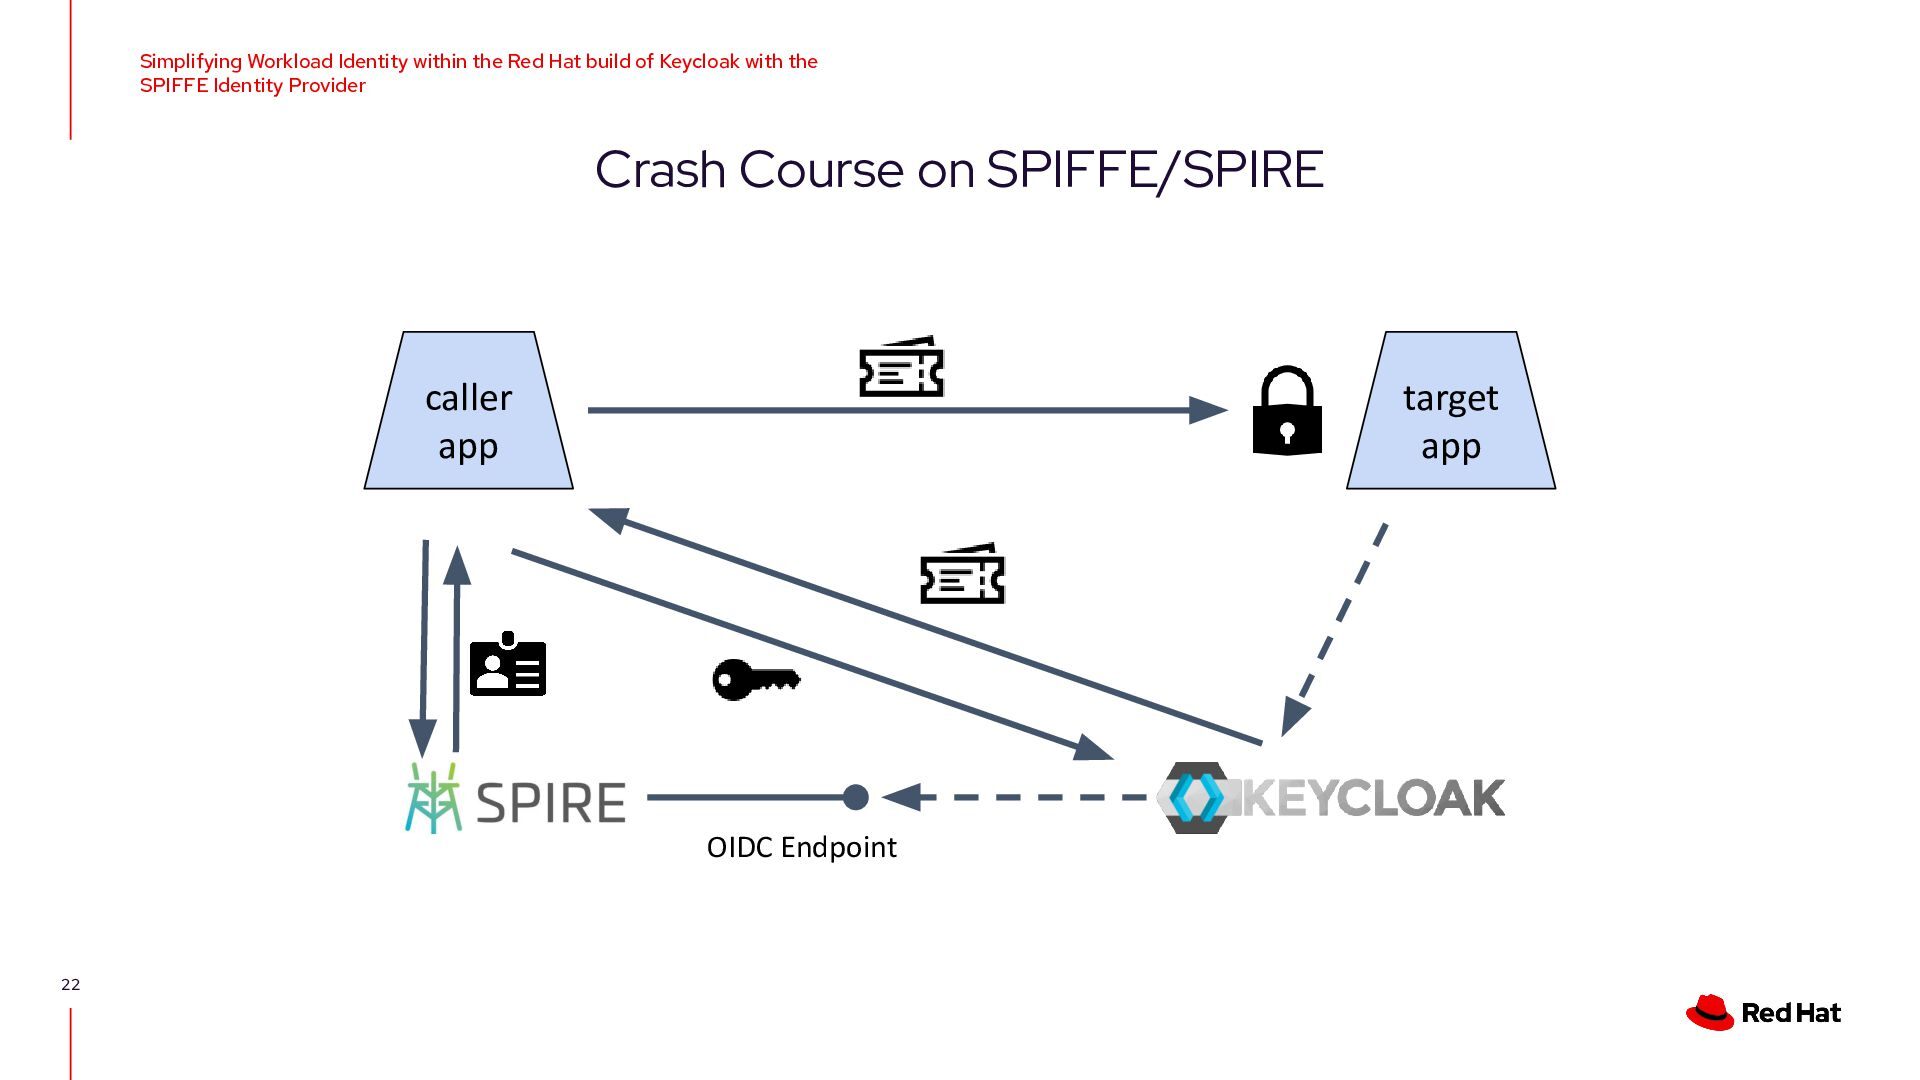
  22. Simplifying Workload Identity within the Red Hat build of Keycloak

    with the SPIFFE Identity Provider Crash Course on SPIFFE/SPIRE caller app target app OIDC Endpoint 22
  23. Simplifying Workload Identity within the Red Hat build of Keycloak

    with the SPIFFE Identity Provider Red Hat Zero Trust Workload Identity Manager Red Hat’s Supported SPIFFE/SPIRE Distribution Key Features 23 • Operator Based Deployment and Lifecycle Management • Secure by Default Deployment with read only file systems and SCC enforcement • Automatic Workload Registration using the SPIRE Controller Manager • SPIRE Federation enables universal trust across hybrid cloud environments • OIDC Federation enables workloads to integrate with existing identity solutions • Integrates with OpenShift cluster provided Monitoring and Alerting Available with OpenShift Platform Plus
  24. Simplifying Workload Identity within the Red Hat build of Keycloak

    with the SPIFFE Identity Provider SPIFFE @ Keycloak in action
  25. Simplifying Workload Identity within the Red Hat build of Keycloak

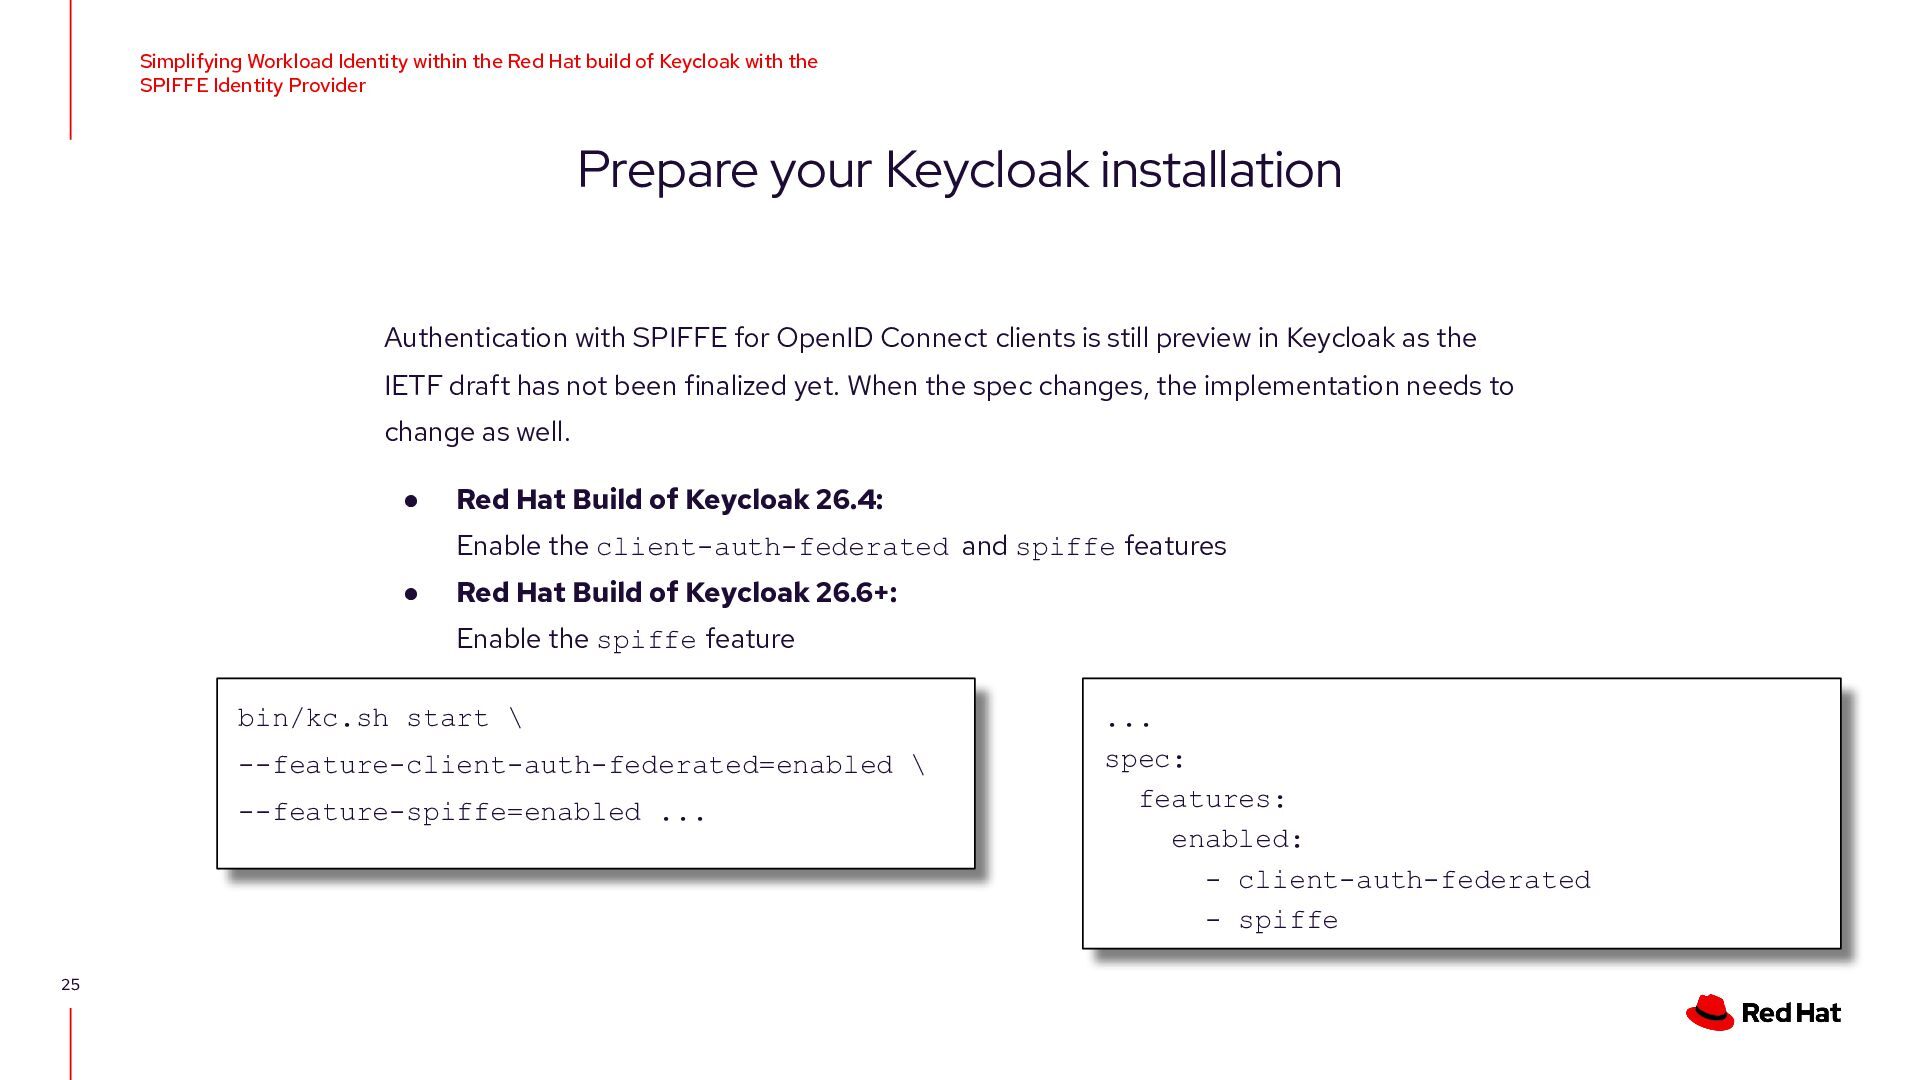
    with the SPIFFE Identity Provider Prepare your Keycloak installation Authentication with SPIFFE for OpenID Connect clients is still preview in Keycloak as the IETF draft has not been finalized yet. When the spec changes, the implementation needs to change as well. • Red Hat Build of Keycloak 26.4: Enable the client-auth-federated and spiffe features • Red Hat Build of Keycloak 26.6+: Enable the spiffe feature bin/kc.sh start \ --feature-client-auth-federated=enabled \ --feature-spiffe=enabled ... 25 ... spec: features: enabled: - client-auth-federated - spiffe
  26. Simplifying Workload Identity within the Red Hat build of Keycloak

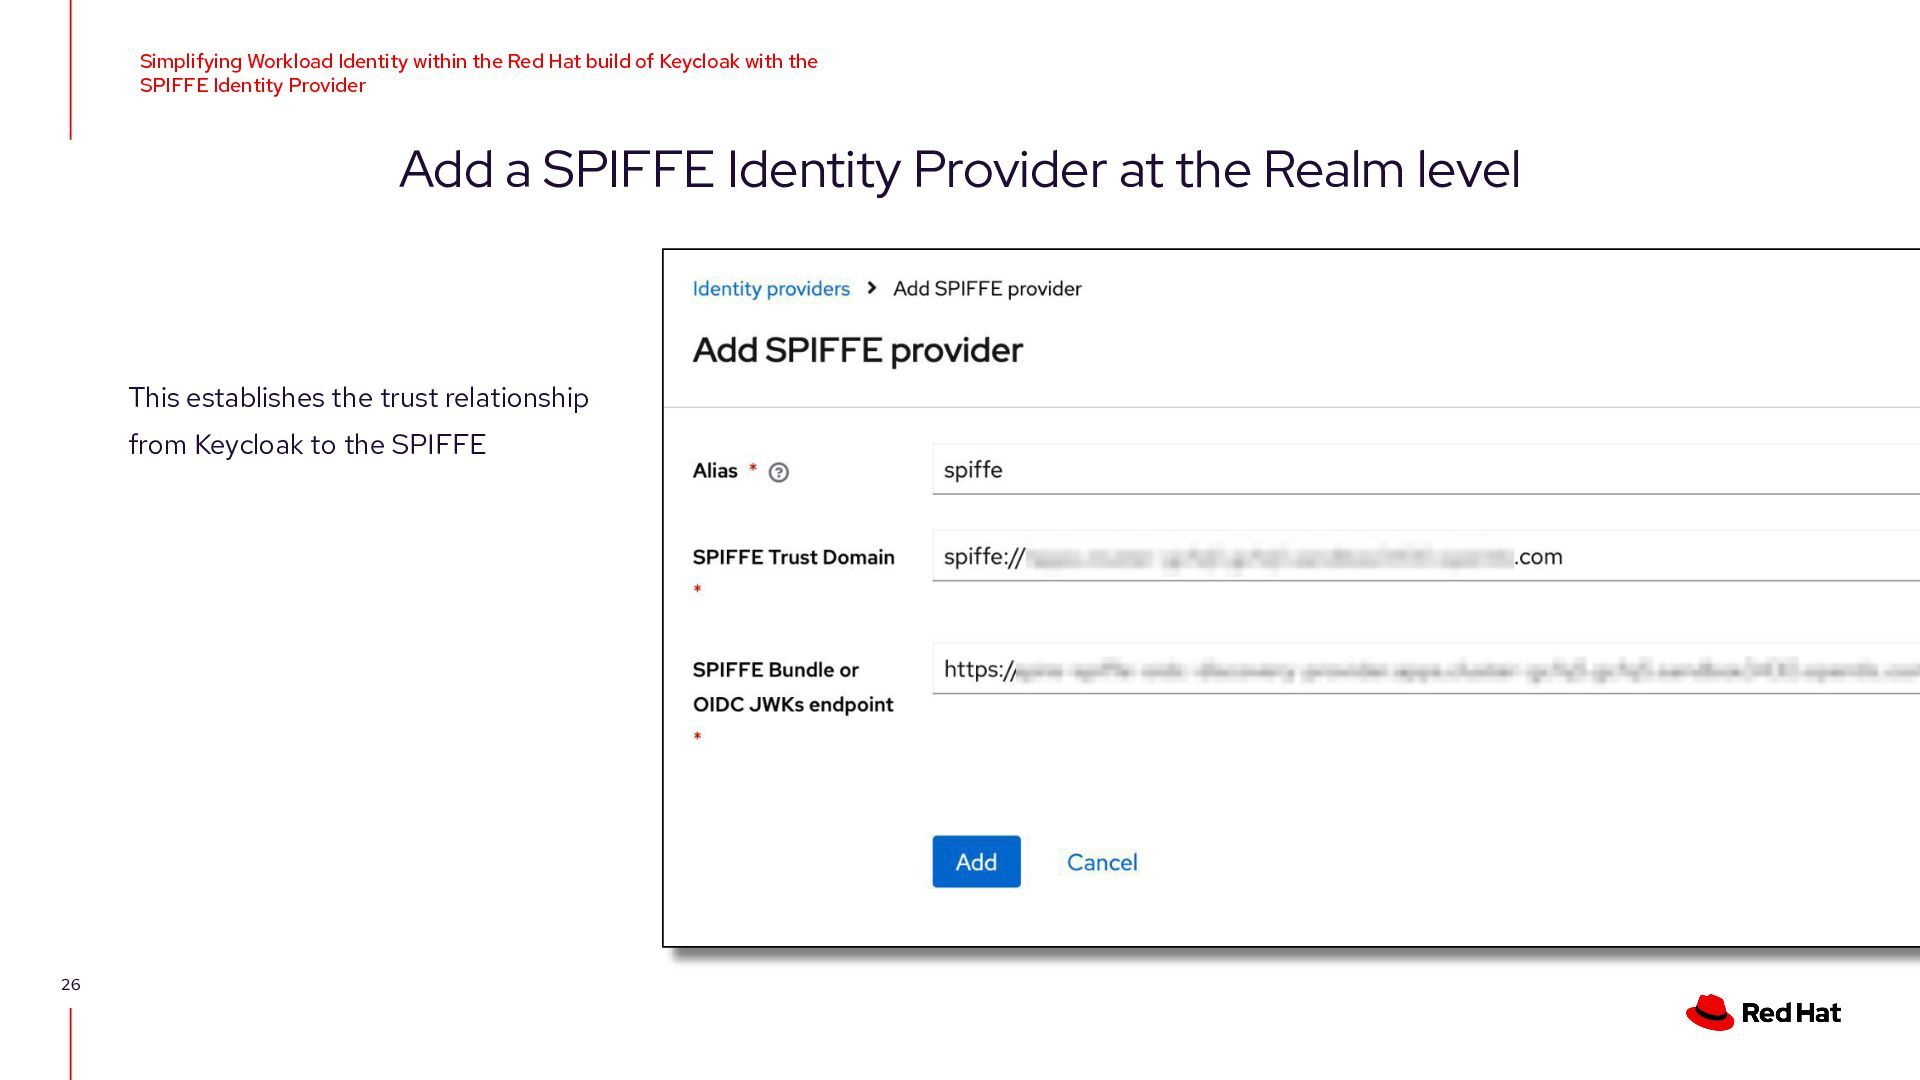
    with the SPIFFE Identity Provider Add a SPIFFE Identity Provider at the Realm level This establishes the trust relationship from Keycloak to the SPIFFE 26
  27. Simplifying Workload Identity within the Red Hat build of Keycloak

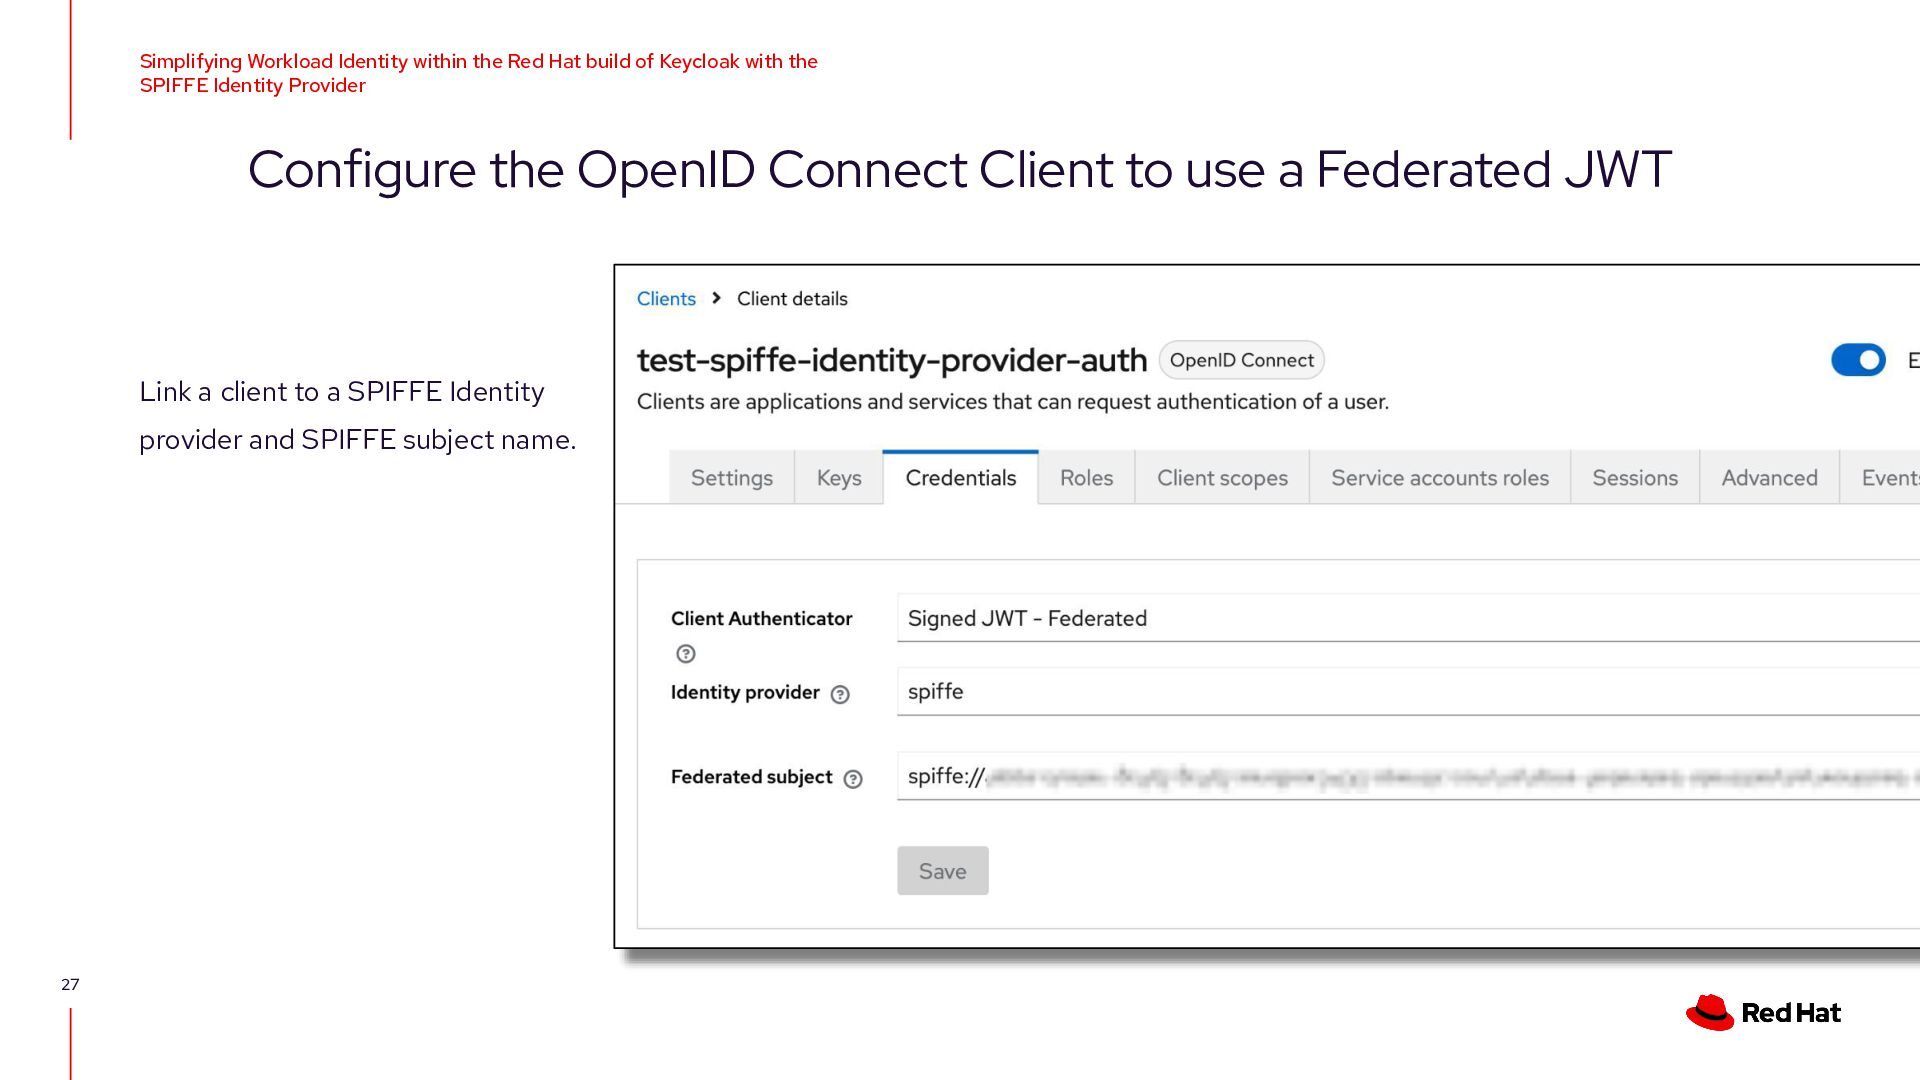
    with the SPIFFE Identity Provider Configure the OpenID Connect Client to use a Federated JWT Link a client to a SPIFFE Identity provider and SPIFFE subject name. 27
  28. Simplifying Workload Identity within the Red Hat build of Keycloak

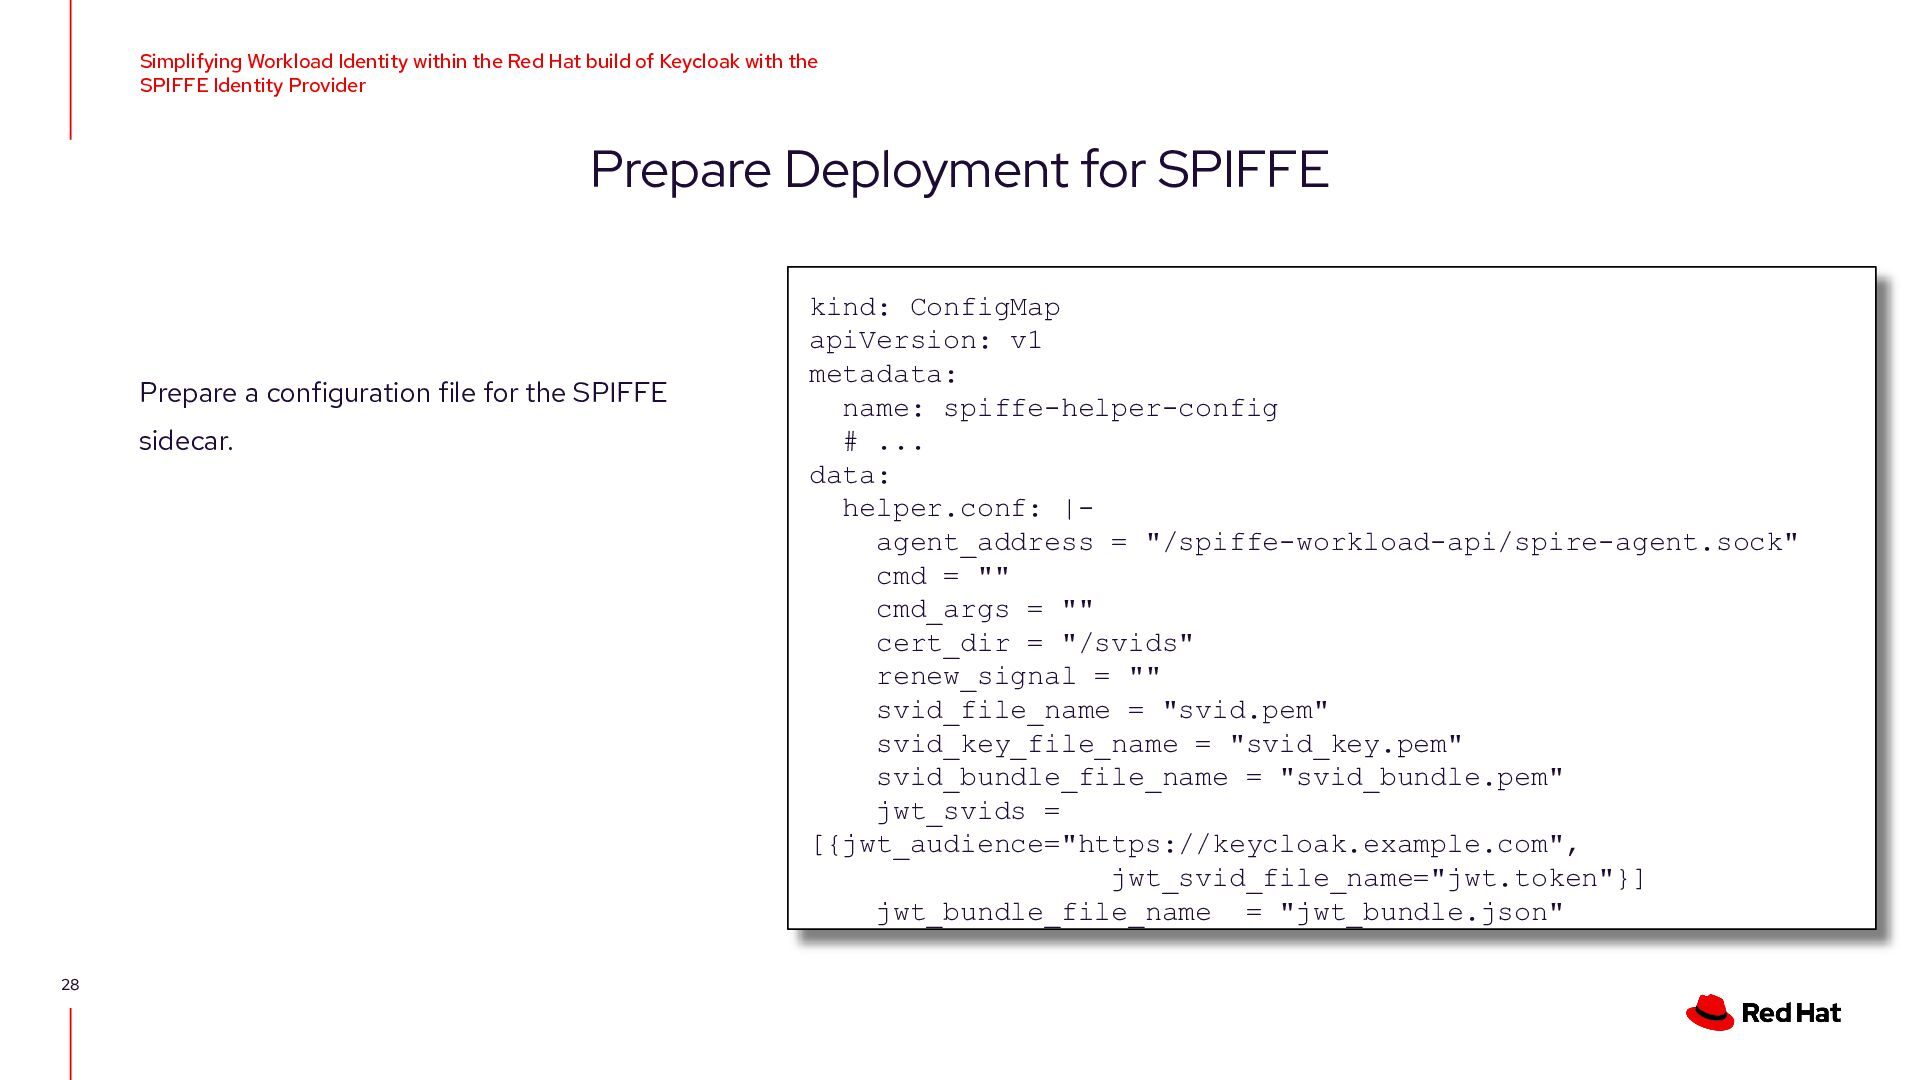
    with the SPIFFE Identity Provider Prepare Deployment for SPIFFE Prepare a configuration file for the SPIFFE sidecar. 28 kind: ConfigMap apiVersion: v1 metadata: name: spiffe-helper-config # ... data: helper.conf: |agent_address = "/spiffe-workload-api/spire-agent.sock" cmd = "" cmd_args = "" cert_dir = "/svids" renew_signal = "" svid_file_name = "svid.pem" svid_key_file_name = "svid_key.pem" svid_bundle_file_name = "svid_bundle.pem" jwt_svids = [{jwt_audience="https://keycloak.example.com", jwt_svid_file_name="jwt.token"}] jwt_bundle_file_name = "jwt_bundle.json"
  29. Simplifying Workload Identity within the Red Hat build of Keycloak

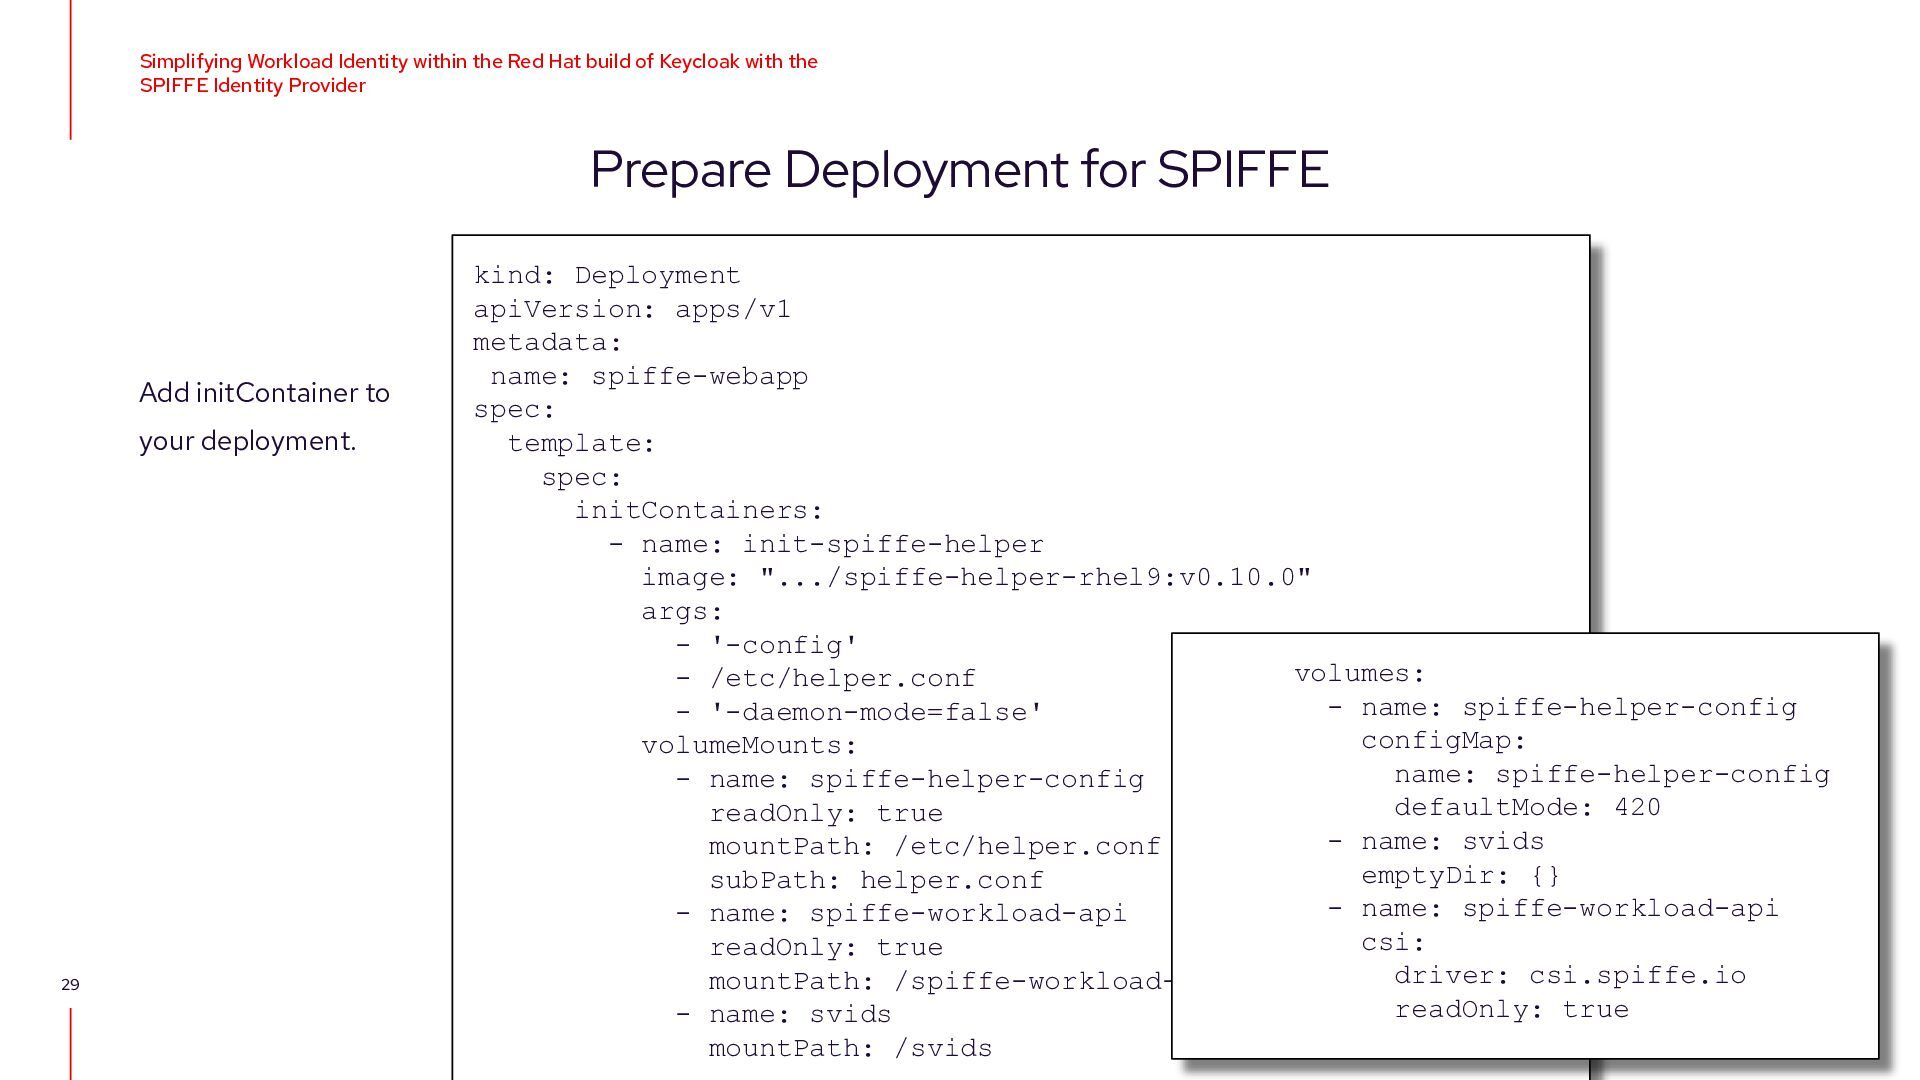
    with the SPIFFE Identity Provider Prepare Deployment for SPIFFE Add initContainer to your deployment. 29 kind: Deployment apiVersion: apps/v1 metadata: name: spiffe-webapp spec: template: spec: initContainers: - name: init-spiffe-helper image: ".../spiffe-helper-rhel9:v0.10.0" args: - '-config' volumes: - /etc/helper.conf - name: spiffe-helper-config - '-daemon-mode=false' configMap: volumeMounts: name: spiffe-helper-config - name: spiffe-helper-config defaultMode: 420 readOnly: true - name: svids mountPath: /etc/helper.conf emptyDir: {} subPath: helper.conf - name: spiffe-workload-api - name: spiffe-workload-api csi: readOnly: true driver: csi.spiffe.io mountPath: /spiffe-workload-api readOnly: true - name: svids mountPath: /svids
  30. Simplifying Workload Identity within the Red Hat build of Keycloak

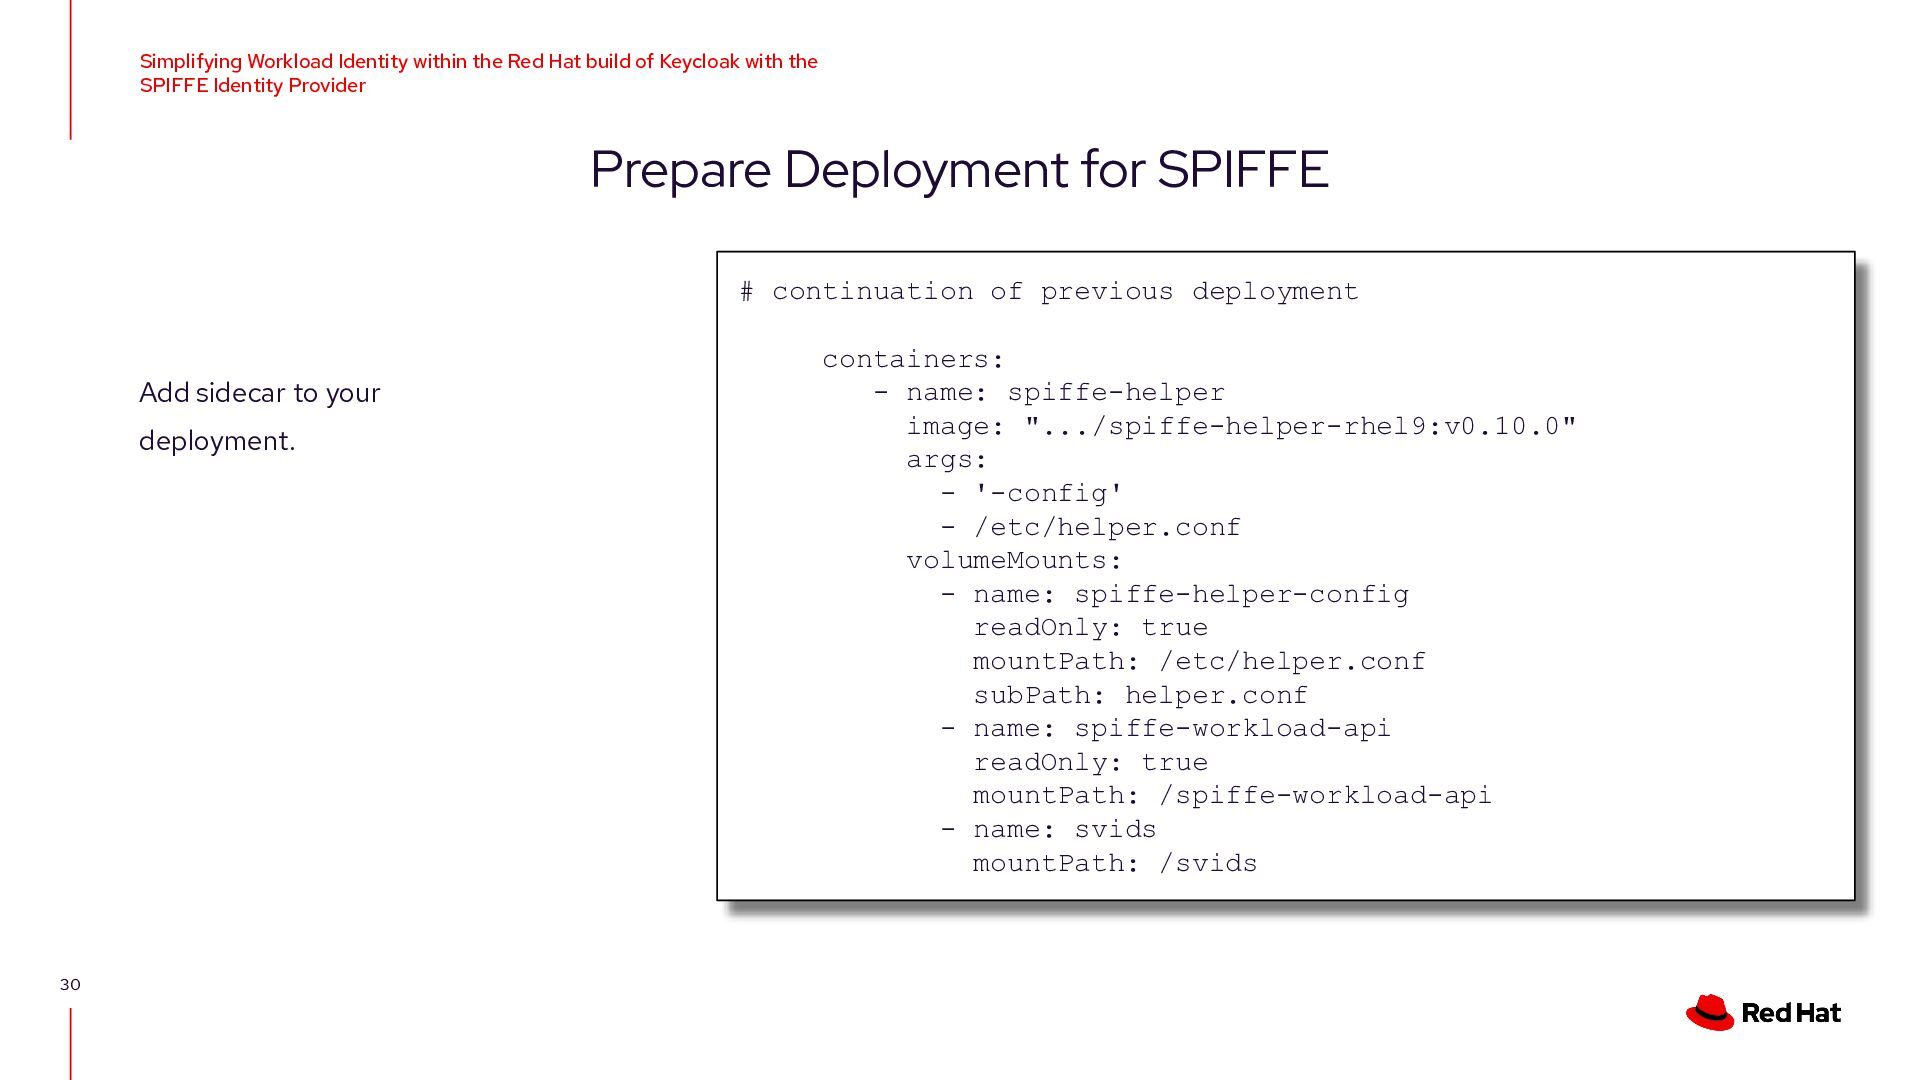
    with the SPIFFE Identity Provider Prepare Deployment for SPIFFE # continuation of previous deployment Add sidecar to your deployment. 30 containers: - name: spiffe-helper image: ".../spiffe-helper-rhel9:v0.10.0" args: - '-config' - /etc/helper.conf volumeMounts: - name: spiffe-helper-config readOnly: true mountPath: /etc/helper.conf subPath: helper.conf - name: spiffe-workload-api readOnly: true mountPath: /spiffe-workload-api - name: svids mountPath: /svids
  31. Simplifying Workload Identity within the Red Hat build of Keycloak

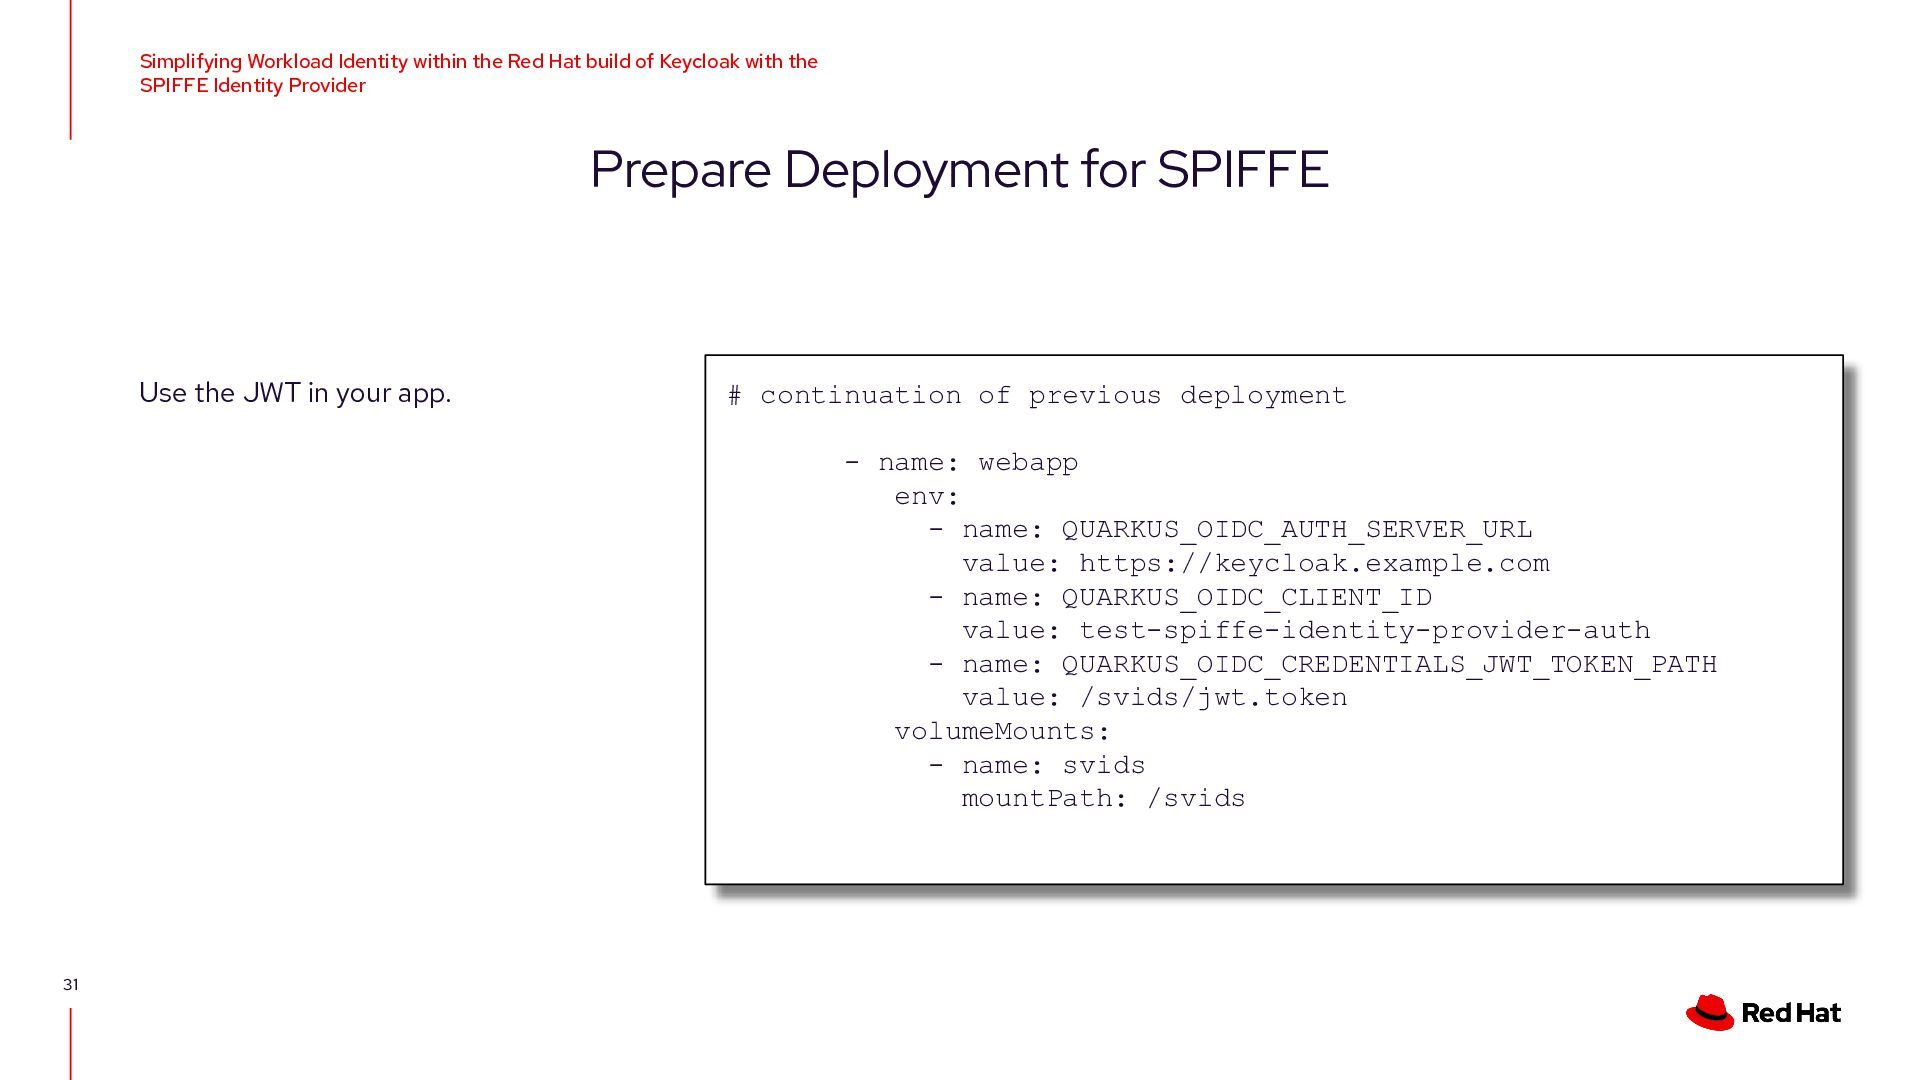
    with the SPIFFE Identity Provider Prepare Deployment for SPIFFE Use the JWT in your app. # continuation of previous deployment - name: webapp env: - name: QUARKUS_OIDC_AUTH_SERVER_URL value: https://keycloak.example.com - name: QUARKUS_OIDC_CLIENT_ID value: test-spiffe-identity-provider-auth - name: QUARKUS_OIDC_CREDENTIALS_JWT_TOKEN_PATH value: /svids/jwt.token volumeMounts: - name: svids mountPath: /svids 31
  32. Simplifying Workload Identity within the Red Hat build of Keycloak

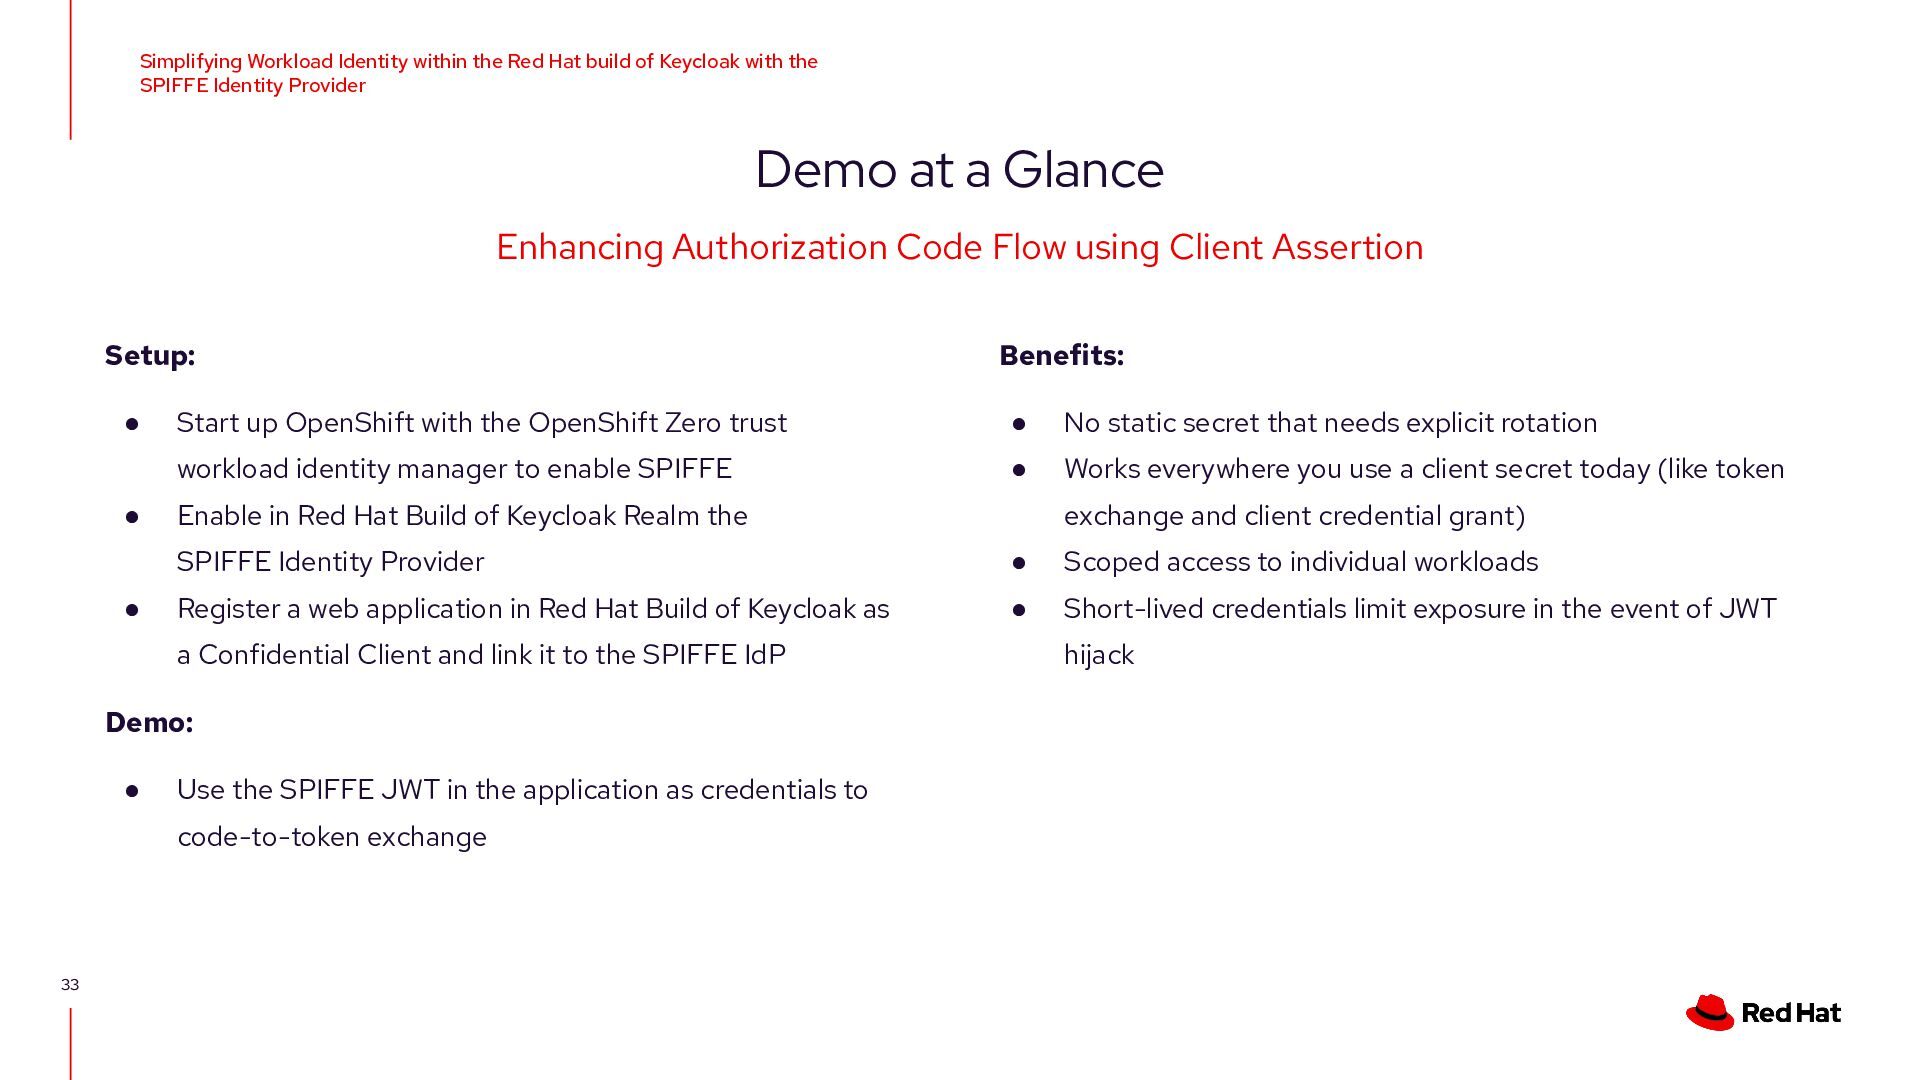
    with the SPIFFE Identity Provider Demo at a Glance Enhancing Authorization Code Flow using Client Assertion Setup: • • • Start up OpenShift with the OpenShift Zero trust • No static secret that needs explicit rotation workload identity manager to enable SPIFFE • Works everywhere you use a client secret today (like token Enable in Red Hat Build of Keycloak Realm the • Scoped access to individual workloads Register a web application in Red Hat Build of Keycloak as • Short-lived credentials limit exposure in the event of JWT Demo: Use the SPIFFE JWT in the application as credentials to code-to-token exchange 33 exchange and client credential grant) SPIFFE Identity Provider a Confidential Client and link it to the SPIFFE IdP • Benefits: hijack
  33. Simplifying Workload Identity within the Red Hat build of Keycloak

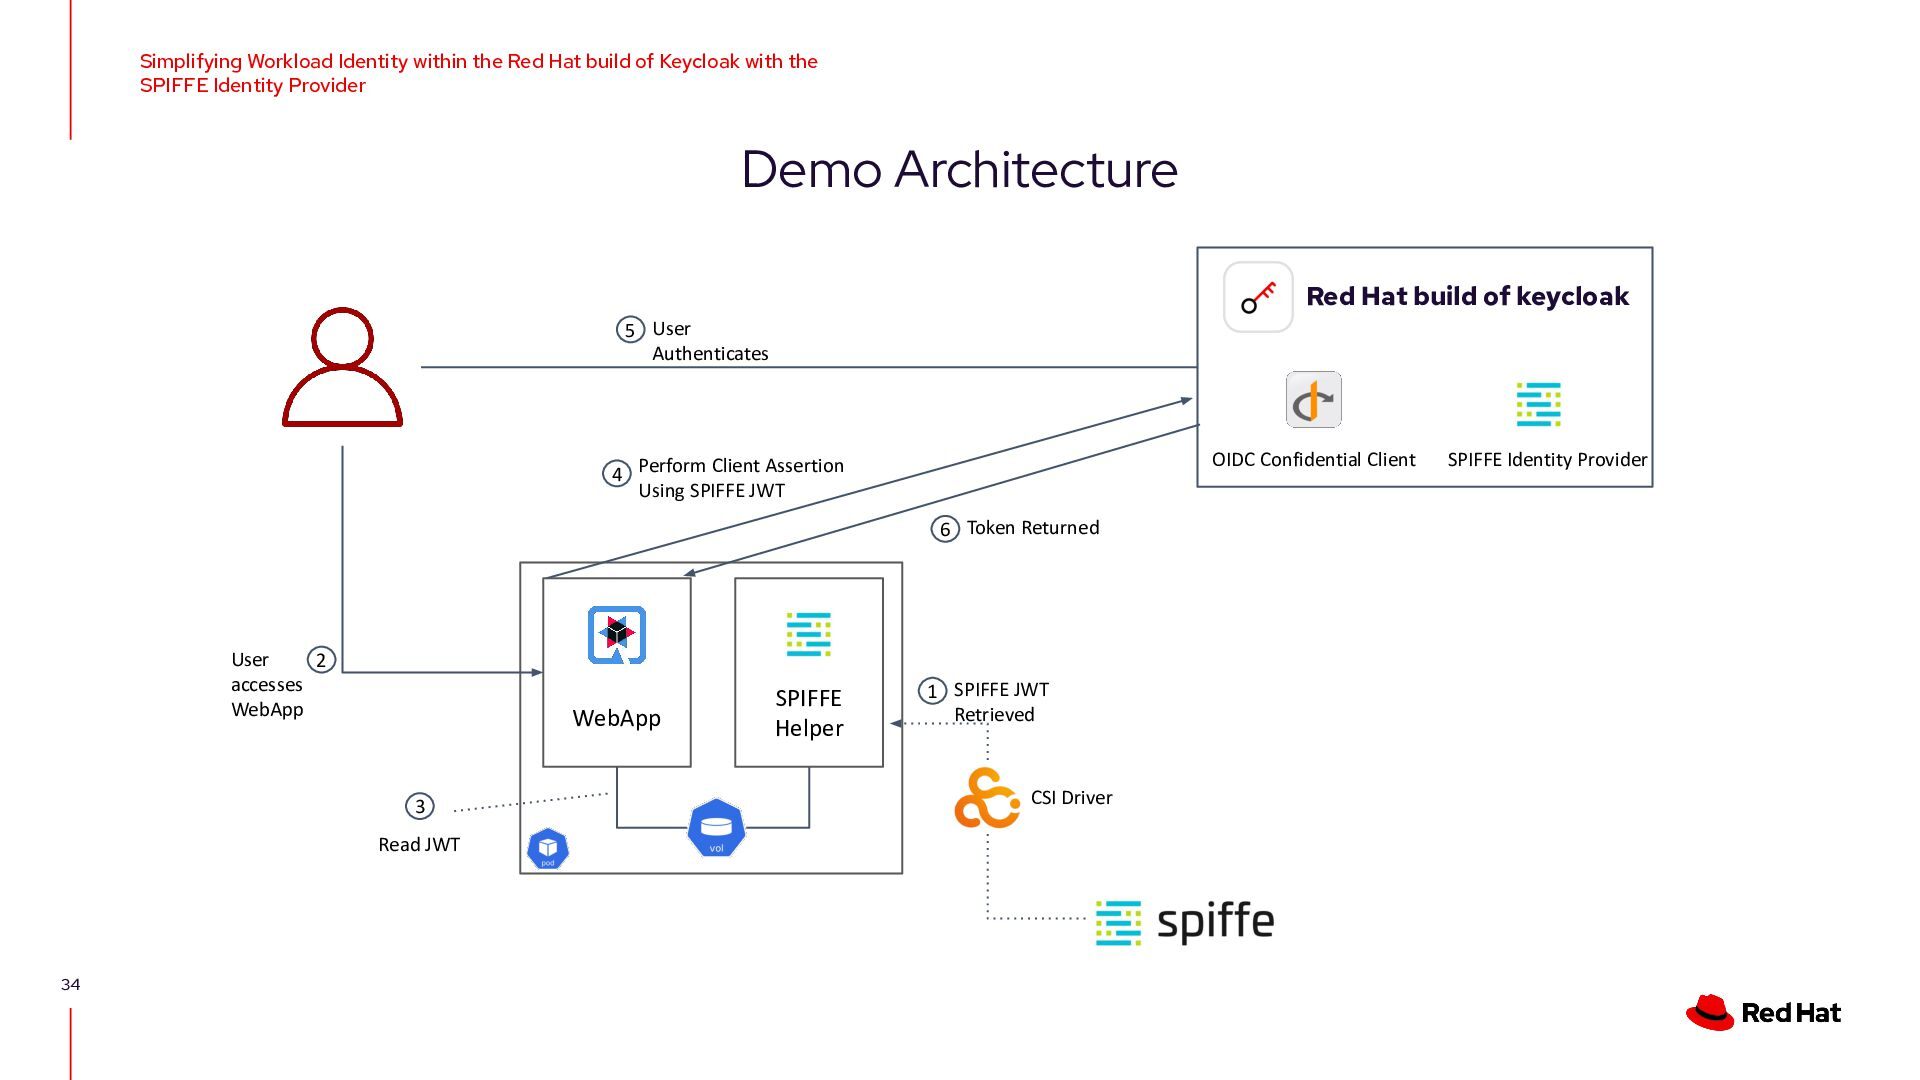
    with the SPIFFE Identity Provider Demo Architecture Red Hat build of keycloak 5 User Authenticates OIDC Confidential Client 4 Perform Client Assertion Using SPIFFE JWT 6 Token Returned User 2 accesses WebApp WebApp 3 Read JWT 34 SPIFFE Helper 1 SPIFFE JWT Retrieved CSI Driver SPIFFE Identity Provider
  34. Simplifying Workload Identity within the Red Hat build of Keycloak

    with the SPIFFE Identity Provider Looking Ahead • Waiting for the IETF RFC to be finalized to make SPIFFE IdPs generally available in Red Hat Build of Keycloak • Demo Code at https://github.com/sabre1041/keycloakcon-spiffe ◦ • rhsummit-2026 branch With SPIFFE working great inside and outside of OpenShift and across organizations, also check out the option to use Kubernetes Service Account tokens to authenticate workloads within an OpenShift cluster. 35
  35. Simplifying Workload Identity within the Red Hat build of Keycloak

    with the SPIFFE Identity Provider Looking Ahead • Waiting for the IETF RFC to be finalized to make SPIFFE IdPs generally available in Red Hat Build of Keycloak • Demo Code at https://github.com/sabre1041/keycloakcon-spiffe ◦ • rhsummit-2026 branch With SPIFFE working great inside and outside of OpenShift and across organizations, also check out the option to use Kubernetes Service Account tokens to authenticate workloads within an OpenShift cluster. 36

More Decks by Alexander Schwartz

Other Decks in Technology