Upgrade to Pro
— share decks privately, control downloads, hide ads and more …
Speaker Deck
Sign up for free
Menu
Search
Features
All features
Private URLs
Password Protection
Custom URLS
Scheduled publishing
Remove Branding
Restrict embedding
Deck Collections
Notes
Features
All features
Private URLs
Password Protection
Custom URLS
Scheduled publishing
Remove Branding
Restrict embedding
Deck Collections
Notes
Explore
Featured decks
Featured speakers
Programming
Technology
Storyboards
Explore
Featured decks
Featured speakers
Programming
Technology
Storyboards
Pricing
Search
Sign in
Sign up for free
Terraform
Search
Andy Gale
October 08, 2014
Technology
1.1k
0
Share
Embed
Copy iframe code
Copy JS code
Copy link
Start on current slide
Terraform
Lightening introduction to Terraform given at PHPSW on 8th October
Andy Gale
October 08, 2014
More Decks by Andy Gale
See All by Andy Gale
TekCurious
andygale
0
93
Mitigating DDOS Attacks with Terraform
andygale
0
900
Container Security
andygale
0
590
Nobody likes you Jenkins
andygale
2
1.2k
PHP Migrations with Phinx
andygale
1
2.1k
Test-Driven Infrastructure
andygale
2
670
Chef and Docker
andygale
3
570
Auto-scaling PHP applications using Chef and AWS
andygale
2
1.3k
Testing Javascript
andygale
9
1.5k
Other Decks in Technology
See All in Technology
アラートを見直していたら営業組織への理解にちょっとだけ繋がった話
z63d
0
170
ライフワーク「猫でもわかるDirectConnect」
kentapapa
0
310
「AIチャットからもできないの?」と言われたら ~業務アプリをMCP対応するときの認証・認可の勘所
oidfj
0
290
自治体AIコンタクトセンター、何をどこに任せる?~Amazon Connect Customer +Amazon Bedrockの実践知~ / 20261107 Satoshi Torano
shift_evolve
PRO
1
130
これからのデータエンジニアの役割について考える / Rethinking the Role of Data Engineers in the AI Era
okiyuki99
0
300
AIエージェントの監視、思考を見るか行動を見るか / Monitoring AI Agents: Thoughts or Actions
yusukeshimizu
2
180
MCPでAIが自分で調べに行く
cdataj
0
140
現場を動かすAIエージェント#2_製造業現場でのAI活用から見た、ハマる罠と実践知
kintotechdev
2
210
BALLAS Technology Deck
ballas_inc
0
460
[JAWS Festa 2026]一番いい仕事は、請求書に現れない / jawsfesta2026
sh_fk2
2
440
Content Mapper APIの応用例~CSS Modules、言語ファイル~
uhyo
2
640
Active Directory と Entra ID のむむむな関係
murachiakira
PRO
4
1.8k
Featured
See All Featured
Navigating the moral maze — ethical principles for Al-driven product design
skipperchong
2
680
How to Think Like a Performance Engineer
csswizardry
28
2.9k
Connecting the Dots Between Site Speed, User Experience & Your Business [WebExpo 2025]
tammyeverts
11
1.1k
A Guide to Academic Writing Using Generative AI - A Workshop
ks91
PRO
1
560
Done Done
chrislema
187
17k
Effective software design: The role of men in debugging patriarchy in IT @ Voxxed Days AMS
baasie
1
600
Tell your own story through comics
letsgokoyo
1
1.1k
ReactJS: Keep Simple. Everything can be a component!
pedronauck
666
130k
How to Grow Your eCommerce with AI & Automation
katarinadahlin
PRO
2
350
ピンチをチャンスに:未来をつくるプロダクトロードマップ #pmconf2020
aki_iinuma
128
56k
Deep Space Network (abreviated)
tonyrice
0
410
Beyond borders and beyond the search box: How to win the global "messy middle" with AI-driven SEO
davidcarrasco
3
300
Transcript
Terraform Andy Gale DevOps Consultancy
About me Andy Gale Web Consultant Hello Future http://hellofutu.re !
@andygale @hellofutur3 DevOps Consultancy
Infrastructure as code • AWS ec2 instances • Digital Ocean
droplets • Google Cloud Compute Engine • Dedicated boxes Ansible, Puppet, Chef DevOps Consultancy
Terraform • AWS security groups, VPC, VPC Subnets, Amazon RDS
• DNS with Digital Ocean, DNSimple, Route 53 DevOps Consultancy
Terraform http://www.terraform.io/downloads.html Install DevOps Consultancy
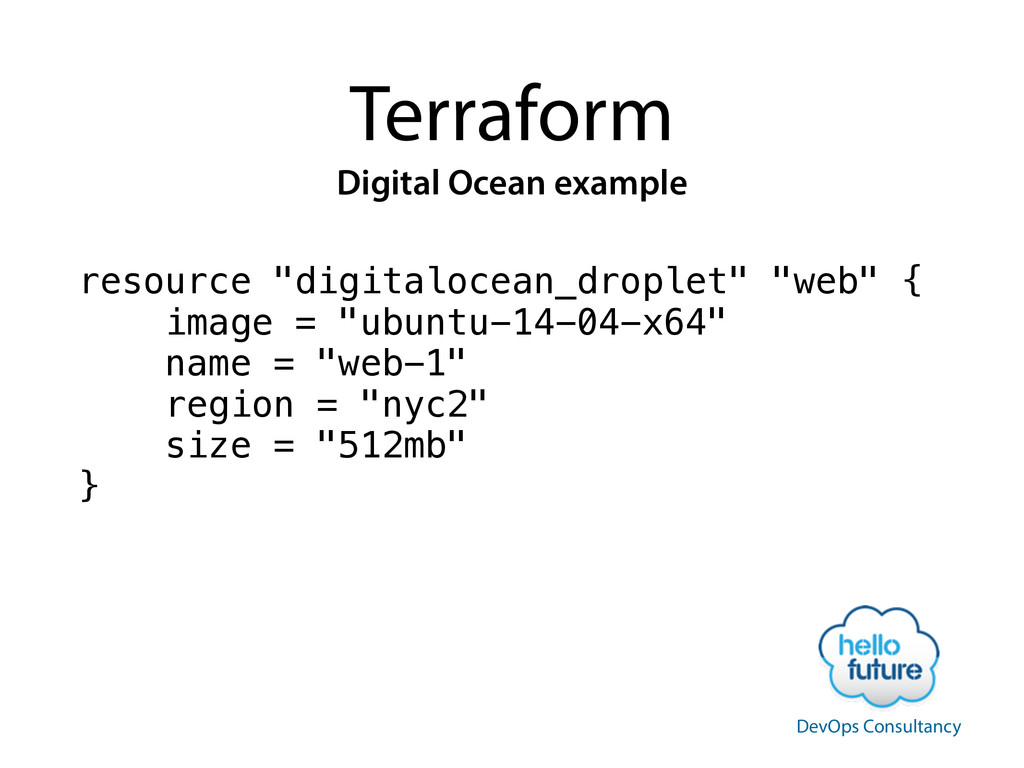
Terraform Digital Ocean example resource "digitalocean_droplet" "web" { image =
"ubuntu-14-04-x64" name = "web-1" region = "nyc2" size = "512mb" } DevOps Consultancy
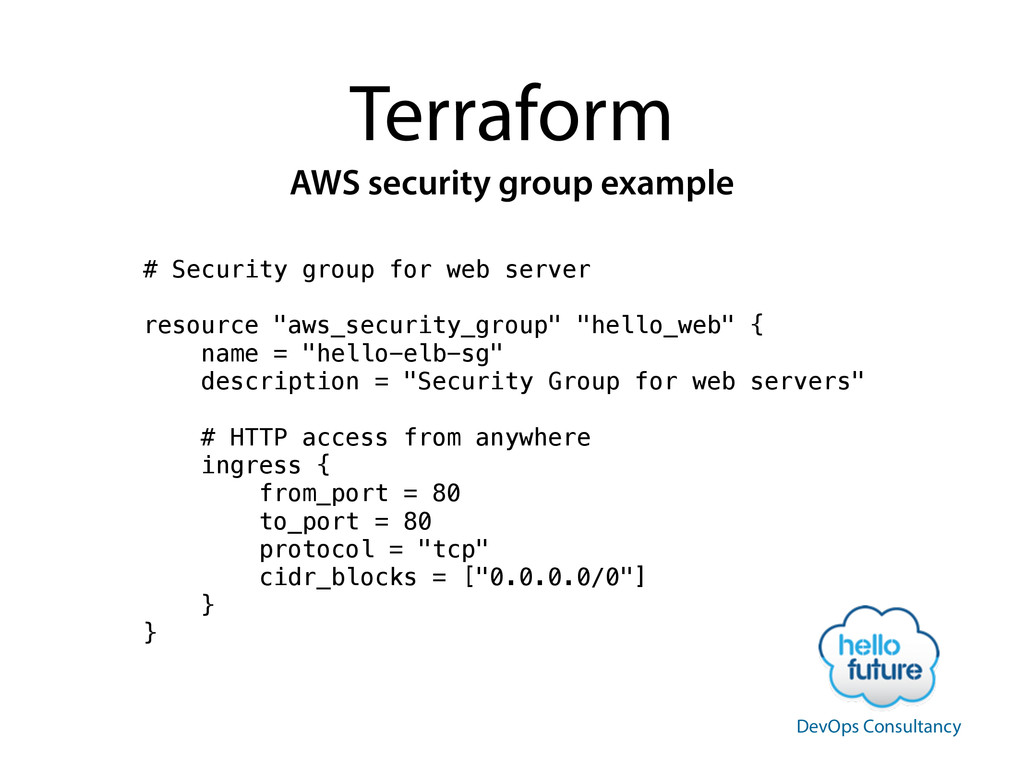
Terraform AWS security group example # Security group for web
server ! resource "aws_security_group" "hello_web" { name = "hello-elb-sg" description = "Security Group for web servers" ! # HTTP access from anywhere ingress { from_port = 80 to_port = 80 protocol = "tcp" cidr_blocks = ["0.0.0.0/0"] } } DevOps Consultancy
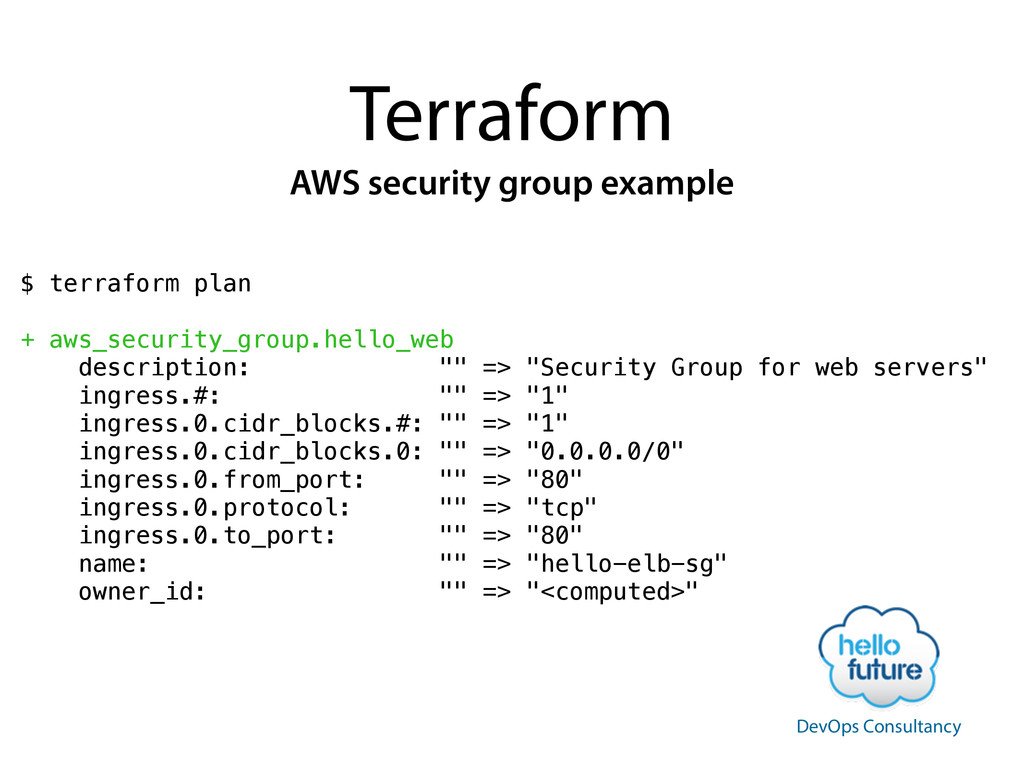
Terraform AWS security group example $ terraform plan ! +
aws_security_group.hello_web description: "" => "Security Group for web servers" ingress.#: "" => "1" ingress.0.cidr_blocks.#: "" => "1" ingress.0.cidr_blocks.0: "" => "0.0.0.0/0" ingress.0.from_port: "" => "80" ingress.0.protocol: "" => "tcp" ingress.0.to_port: "" => "80" name: "" => "hello-elb-sg" owner_id: "" => "<computed>" ! DevOps Consultancy
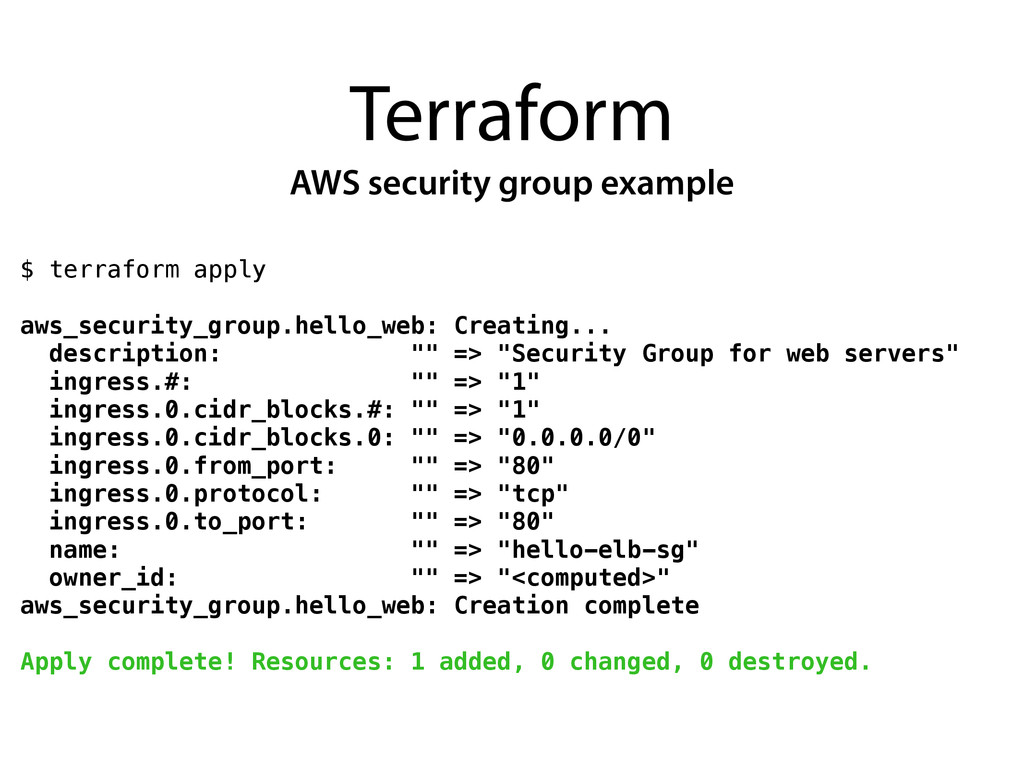
Terraform AWS security group example $ terraform apply ! aws_security_group.hello_web:
Creating... description: "" => "Security Group for web servers" ingress.#: "" => "1" ingress.0.cidr_blocks.#: "" => "1" ingress.0.cidr_blocks.0: "" => "0.0.0.0/0" ingress.0.from_port: "" => "80" ingress.0.protocol: "" => "tcp" ingress.0.to_port: "" => "80" name: "" => "hello-elb-sg" owner_id: "" => "<computed>" aws_security_group.hello_web: Creation complete ! Apply complete! Resources: 1 added, 0 changed, 0 destroyed.
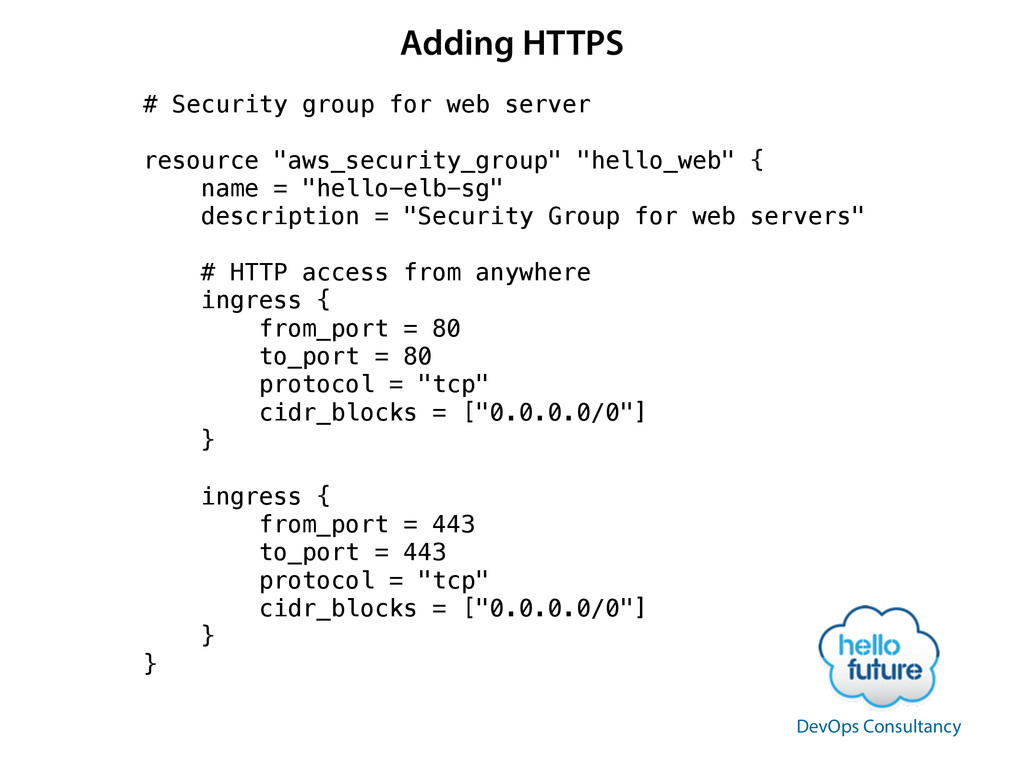
# Security group for web server ! resource "aws_security_group" "hello_web"
{ name = "hello-elb-sg" description = "Security Group for web servers" ! # HTTP access from anywhere ingress { from_port = 80 to_port = 80 protocol = "tcp" cidr_blocks = ["0.0.0.0/0"] } ! ingress { from_port = 443 to_port = 443 protocol = "tcp" cidr_blocks = ["0.0.0.0/0"] } } Adding HTTPS DevOps Consultancy
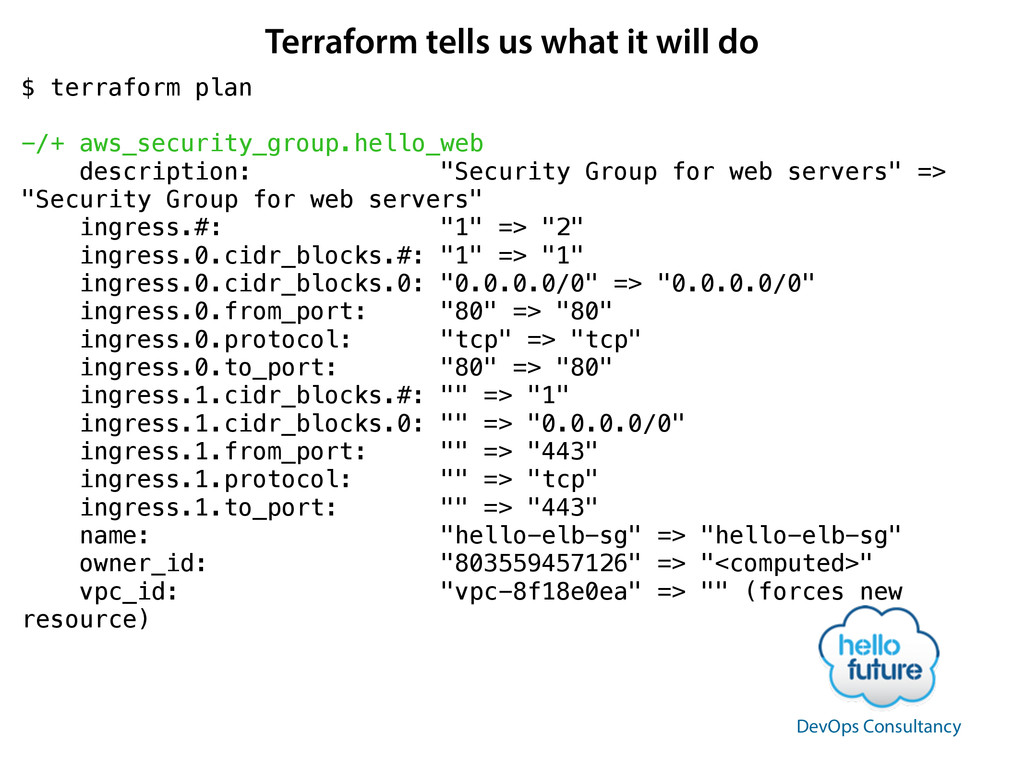
$ terraform plan ! -/+ aws_security_group.hello_web description: "Security Group for
web servers" => "Security Group for web servers" ingress.#: "1" => "2" ingress.0.cidr_blocks.#: "1" => "1" ingress.0.cidr_blocks.0: "0.0.0.0/0" => "0.0.0.0/0" ingress.0.from_port: "80" => "80" ingress.0.protocol: "tcp" => "tcp" ingress.0.to_port: "80" => "80" ingress.1.cidr_blocks.#: "" => "1" ingress.1.cidr_blocks.0: "" => "0.0.0.0/0" ingress.1.from_port: "" => "443" ingress.1.protocol: "" => "tcp" ingress.1.to_port: "" => "443" name: "hello-elb-sg" => "hello-elb-sg" owner_id: "803559457126" => "<computed>" vpc_id: "vpc-8f18e0ea" => "" (forces new resource) ! ! ! DevOps Consultancy Terraform tells us what it will do
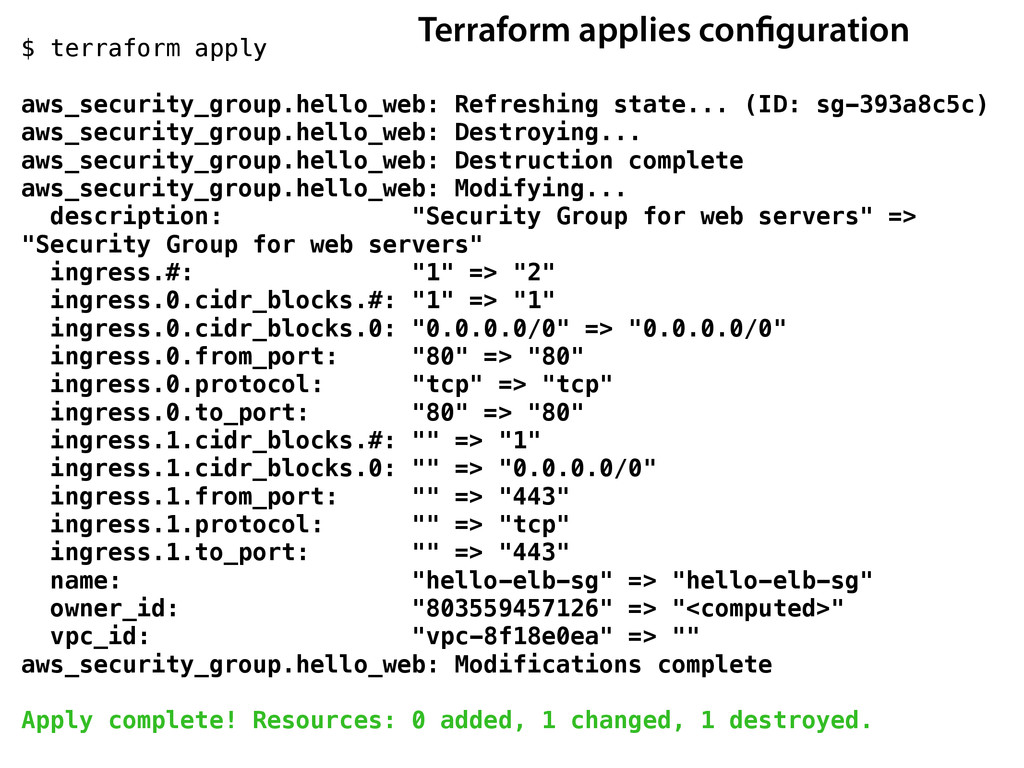
$ terraform apply ! aws_security_group.hello_web: Refreshing state... (ID: sg-393a8c5c) aws_security_group.hello_web:
Destroying... aws_security_group.hello_web: Destruction complete aws_security_group.hello_web: Modifying... description: "Security Group for web servers" => "Security Group for web servers" ingress.#: "1" => "2" ingress.0.cidr_blocks.#: "1" => "1" ingress.0.cidr_blocks.0: "0.0.0.0/0" => "0.0.0.0/0" ingress.0.from_port: "80" => "80" ingress.0.protocol: "tcp" => "tcp" ingress.0.to_port: "80" => "80" ingress.1.cidr_blocks.#: "" => "1" ingress.1.cidr_blocks.0: "" => "0.0.0.0/0" ingress.1.from_port: "" => "443" ingress.1.protocol: "" => "tcp" ingress.1.to_port: "" => "443" name: "hello-elb-sg" => "hello-elb-sg" owner_id: "803559457126" => "<computed>" vpc_id: "vpc-8f18e0ea" => "" aws_security_group.hello_web: Modifications complete ! Apply complete! Resources: 0 added, 1 changed, 1 destroyed. Terraform applies configuration
Adding an instance DevOps Consultancy
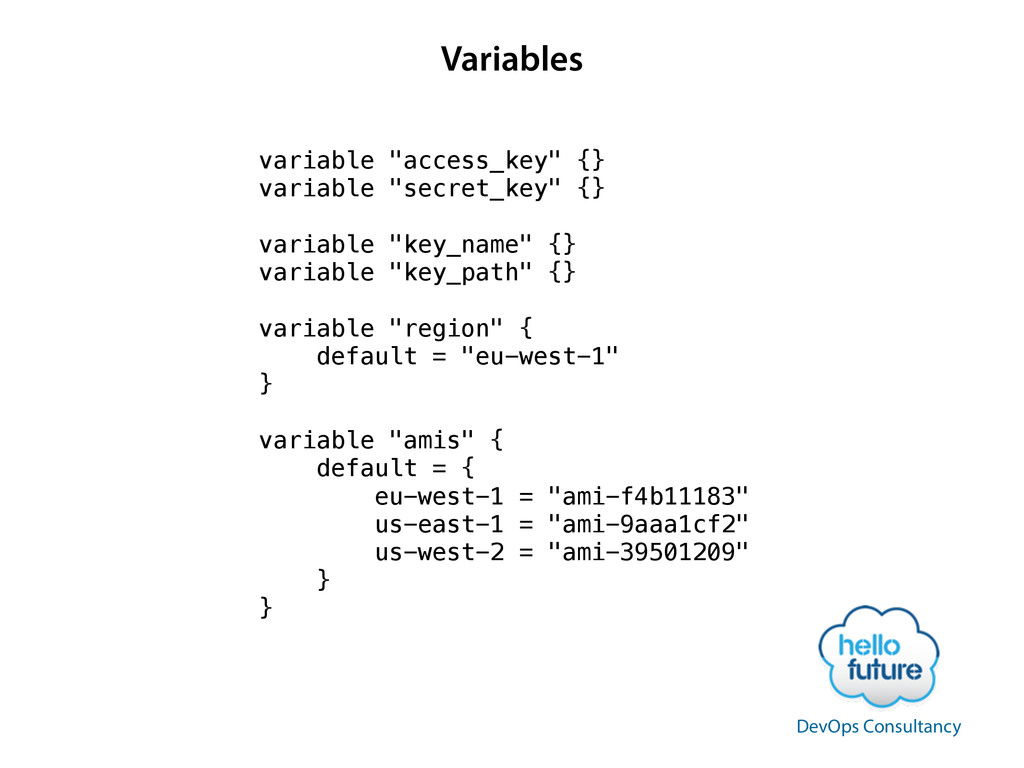
Variables variable "access_key" {} variable "secret_key" {} ! variable "key_name"
{} variable "key_path" {} ! variable "region" { default = "eu-west-1" } ! variable "amis" { default = { eu-west-1 = "ami-f4b11183" us-east-1 = "ami-9aaa1cf2" us-west-2 = "ami-39501209" } } DevOps Consultancy
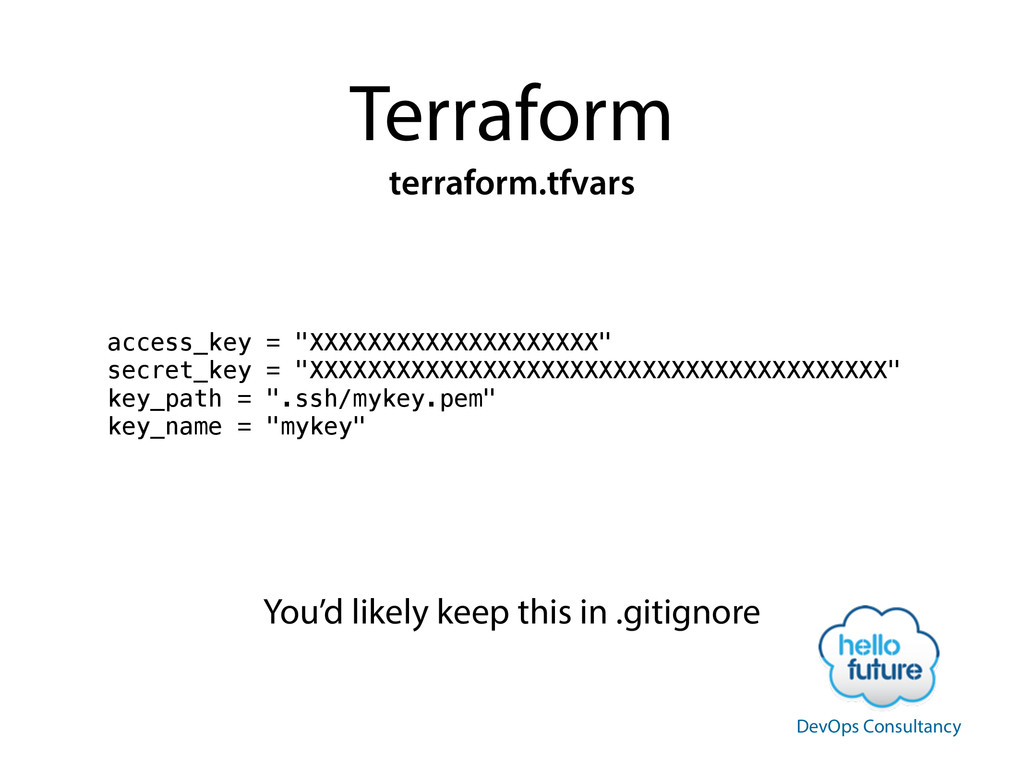
Terraform terraform.tfvars access_key = "XXXXXXXXXXXXXXXXXXXX" secret_key = "XXXXXXXXXXXXXXXXXXXXXXXXXXXXXXXXXXXXXXXX" key_path =
".ssh/mykey.pem" key_name = "mykey" You’d likely keep this in .gitignore DevOps Consultancy
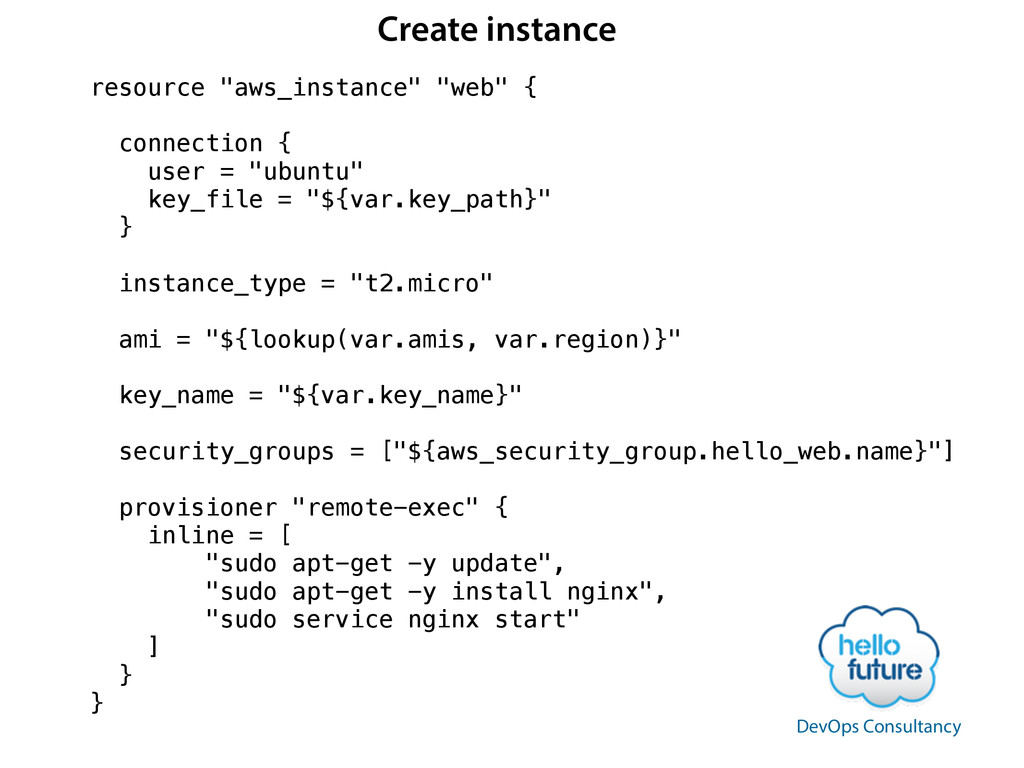
resource "aws_instance" "web" { ! connection { user = "ubuntu"
key_file = "${var.key_path}" } ! instance_type = "t2.micro" ami = "${lookup(var.amis, var.region)}" ! key_name = "${var.key_name}" ! security_groups = ["${aws_security_group.hello_web.name}"] ! provisioner "remote-exec" { inline = [ "sudo apt-get -y update", "sudo apt-get -y install nginx", "sudo service nginx start" ] } } DevOps Consultancy Create instance
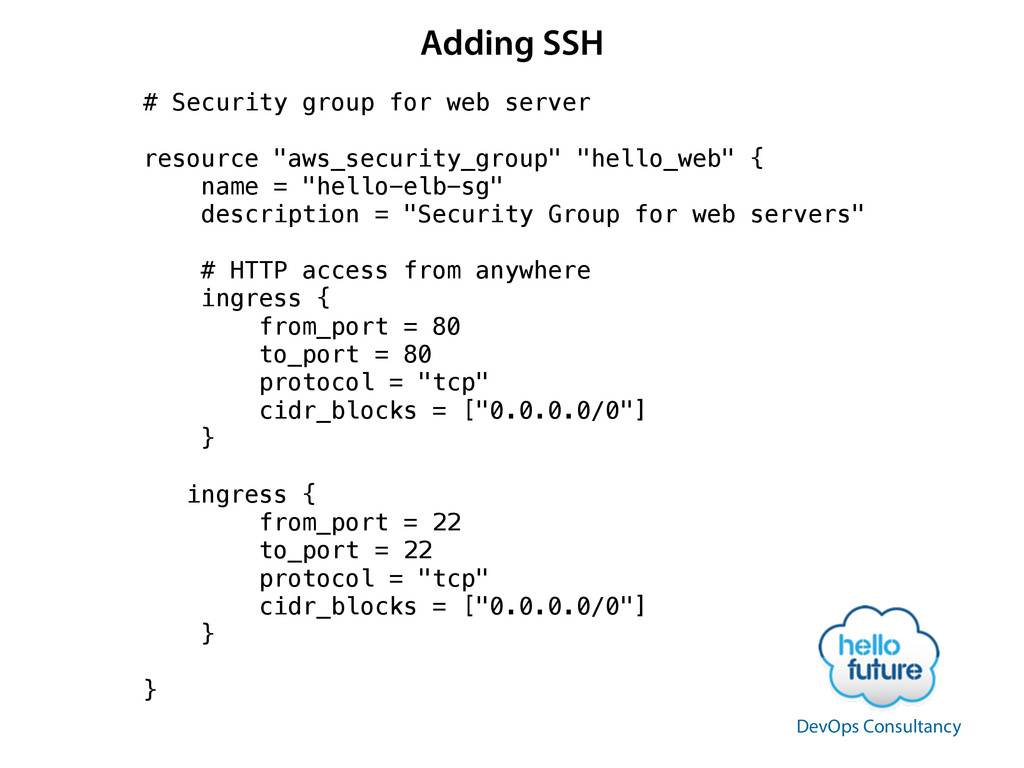
# Security group for web server ! resource "aws_security_group" "hello_web"
{ name = "hello-elb-sg" description = "Security Group for web servers" ! # HTTP access from anywhere ingress { from_port = 80 to_port = 80 protocol = "tcp" cidr_blocks = ["0.0.0.0/0"] } ! ingress { from_port = 22 to_port = 22 protocol = "tcp" cidr_blocks = ["0.0.0.0/0"] } ! } Adding SSH DevOps Consultancy
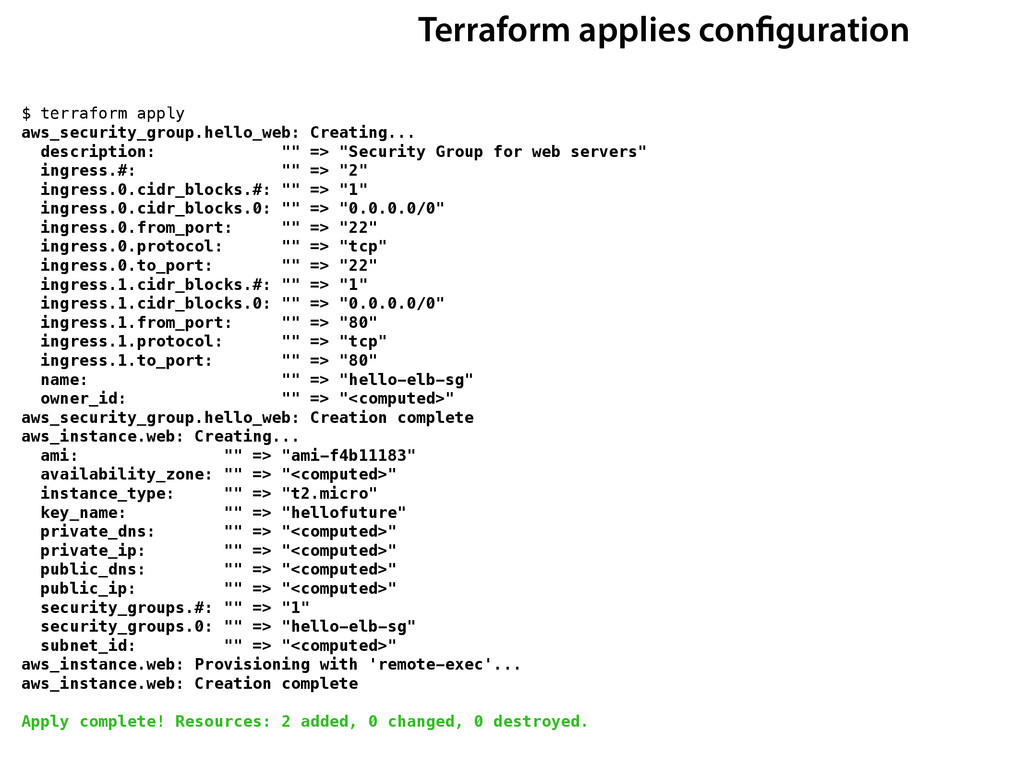
$ terraform apply aws_security_group.hello_web: Creating... description: "" => "Security Group
for web servers" ingress.#: "" => "2" ingress.0.cidr_blocks.#: "" => "1" ingress.0.cidr_blocks.0: "" => "0.0.0.0/0" ingress.0.from_port: "" => "22" ingress.0.protocol: "" => "tcp" ingress.0.to_port: "" => "22" ingress.1.cidr_blocks.#: "" => "1" ingress.1.cidr_blocks.0: "" => "0.0.0.0/0" ingress.1.from_port: "" => "80" ingress.1.protocol: "" => "tcp" ingress.1.to_port: "" => "80" name: "" => "hello-elb-sg" owner_id: "" => "<computed>" aws_security_group.hello_web: Creation complete aws_instance.web: Creating... ami: "" => "ami-f4b11183" availability_zone: "" => "<computed>" instance_type: "" => "t2.micro" key_name: "" => "hellofuture" private_dns: "" => "<computed>" private_ip: "" => "<computed>" public_dns: "" => "<computed>" public_ip: "" => "<computed>" security_groups.#: "" => "1" security_groups.0: "" => "hello-elb-sg" subnet_id: "" => "<computed>" aws_instance.web: Provisioning with 'remote-exec'... aws_instance.web: Creation complete ! Apply complete! Resources: 2 added, 0 changed, 0 destroyed. Terraform applies configuration
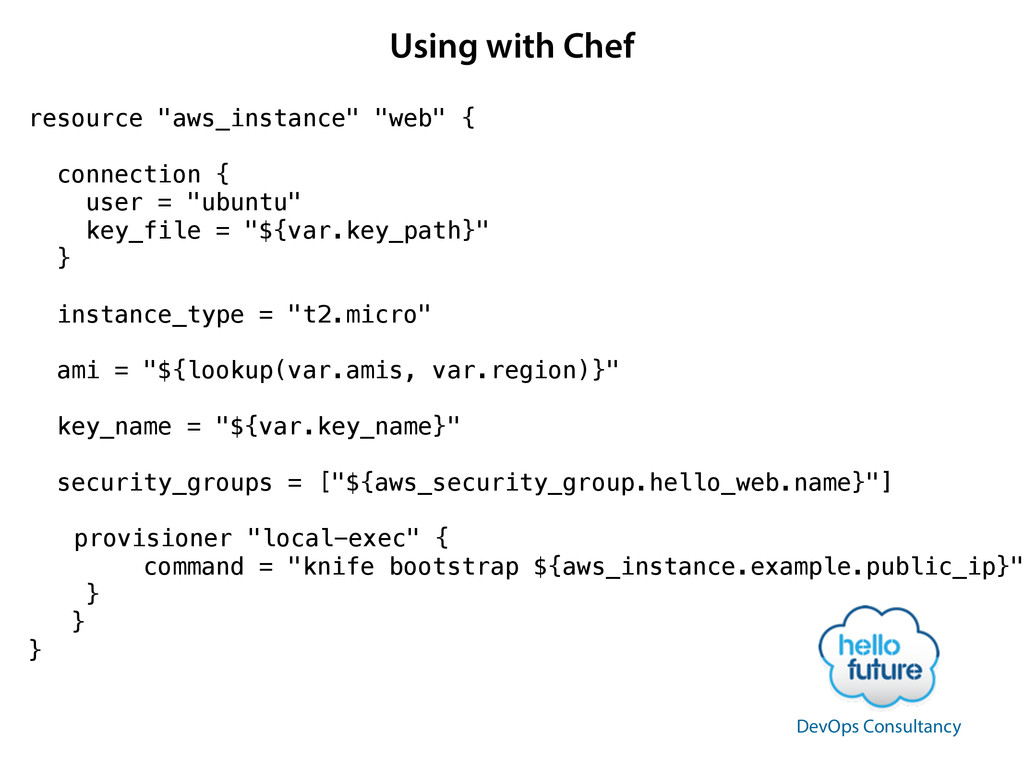
resource "aws_instance" "web" { ! connection { user = "ubuntu"
key_file = "${var.key_path}" } ! instance_type = "t2.micro" ami = "${lookup(var.amis, var.region)}" ! key_name = "${var.key_name}" ! security_groups = ["${aws_security_group.hello_web.name}"] ! provisioner "local-exec" { command = "knife bootstrap ${aws_instance.example.public_ip}" } } } DevOps Consultancy Using with Chef
Packer • Terraform works well with AMIs generated by Packer
• http://www.packer.io/ DevOps Consultancy
Terraform • Amazon autoscaling groups, RDS, ELB, EIP, S3, VPC
• Cloudflare DNS • Consul • Digital Ocean DNS • Google Cloud • Herkou • Mailgun DevOps Consultancy What else can you do


 andygale
 z63d
 kentapapa
 oidfj
 shift_evolve
 okiyuki99
 yusukeshimizu
 cdataj
 kintotechdev
 ballas_inc
 sh_fk2
 uhyo
 murachiakira
 skipperchong
 csswizardry
 tammyeverts
 ks91
 chrislema
 baasie
 letsgokoyo
 pedronauck
 katarinadahlin
 aki_iinuma
 tonyrice
 davidcarrasco