Upgrade to Pro — share decks privately, control downloads, hide ads and more …

Beginner’s Roadmap to Ethical Hacking and Penet...

Beginner’s Roadmap to Ethical Hacking and Penetration Testing: Understanding Cybersecurity Basics, Security Tools, Threat Detection, Vulnerability Management, and Certification Paths for Career Growth

This content explains ethical hacking and penetration testing in a simple and practical way. It includes an overview of testing phases, commonly used tools, and different types of vulnerabilities. It also provides a step-by-step roadmap and certification insights to help beginners enter the cybersecurity field confidently.

Avatar for Archa Salimon

Archa Salimon

April 25, 2026

Other Decks in Technology

Transcript

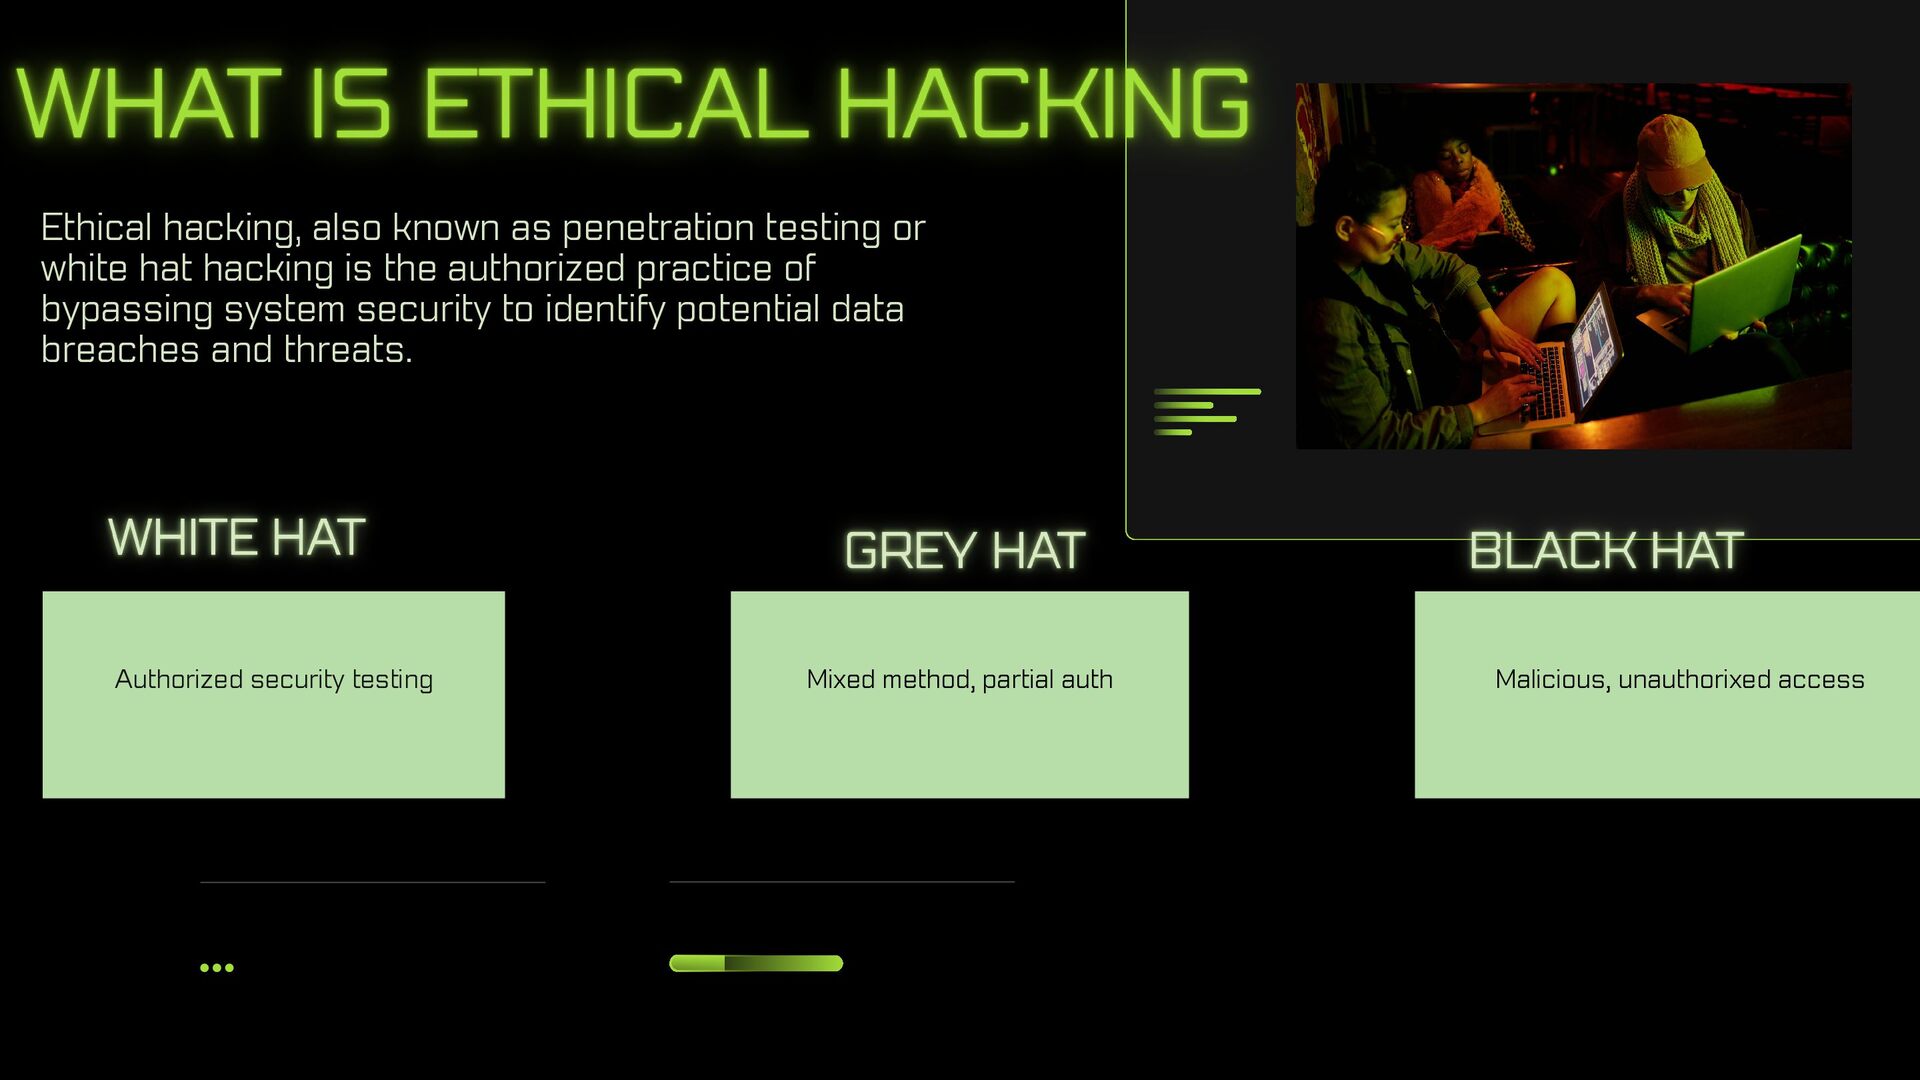
  1. WHAT IS ETHICAL HACKING WHITE HAT Ethical hacking, also known

    as penetration testing or white hat hacking is the authorized practice of bypassing system security to identify potential data breaches and threats. GREY HAT BLACK HAT Authorized security testing Mixed method, partial auth Malicious, unauthorixed access
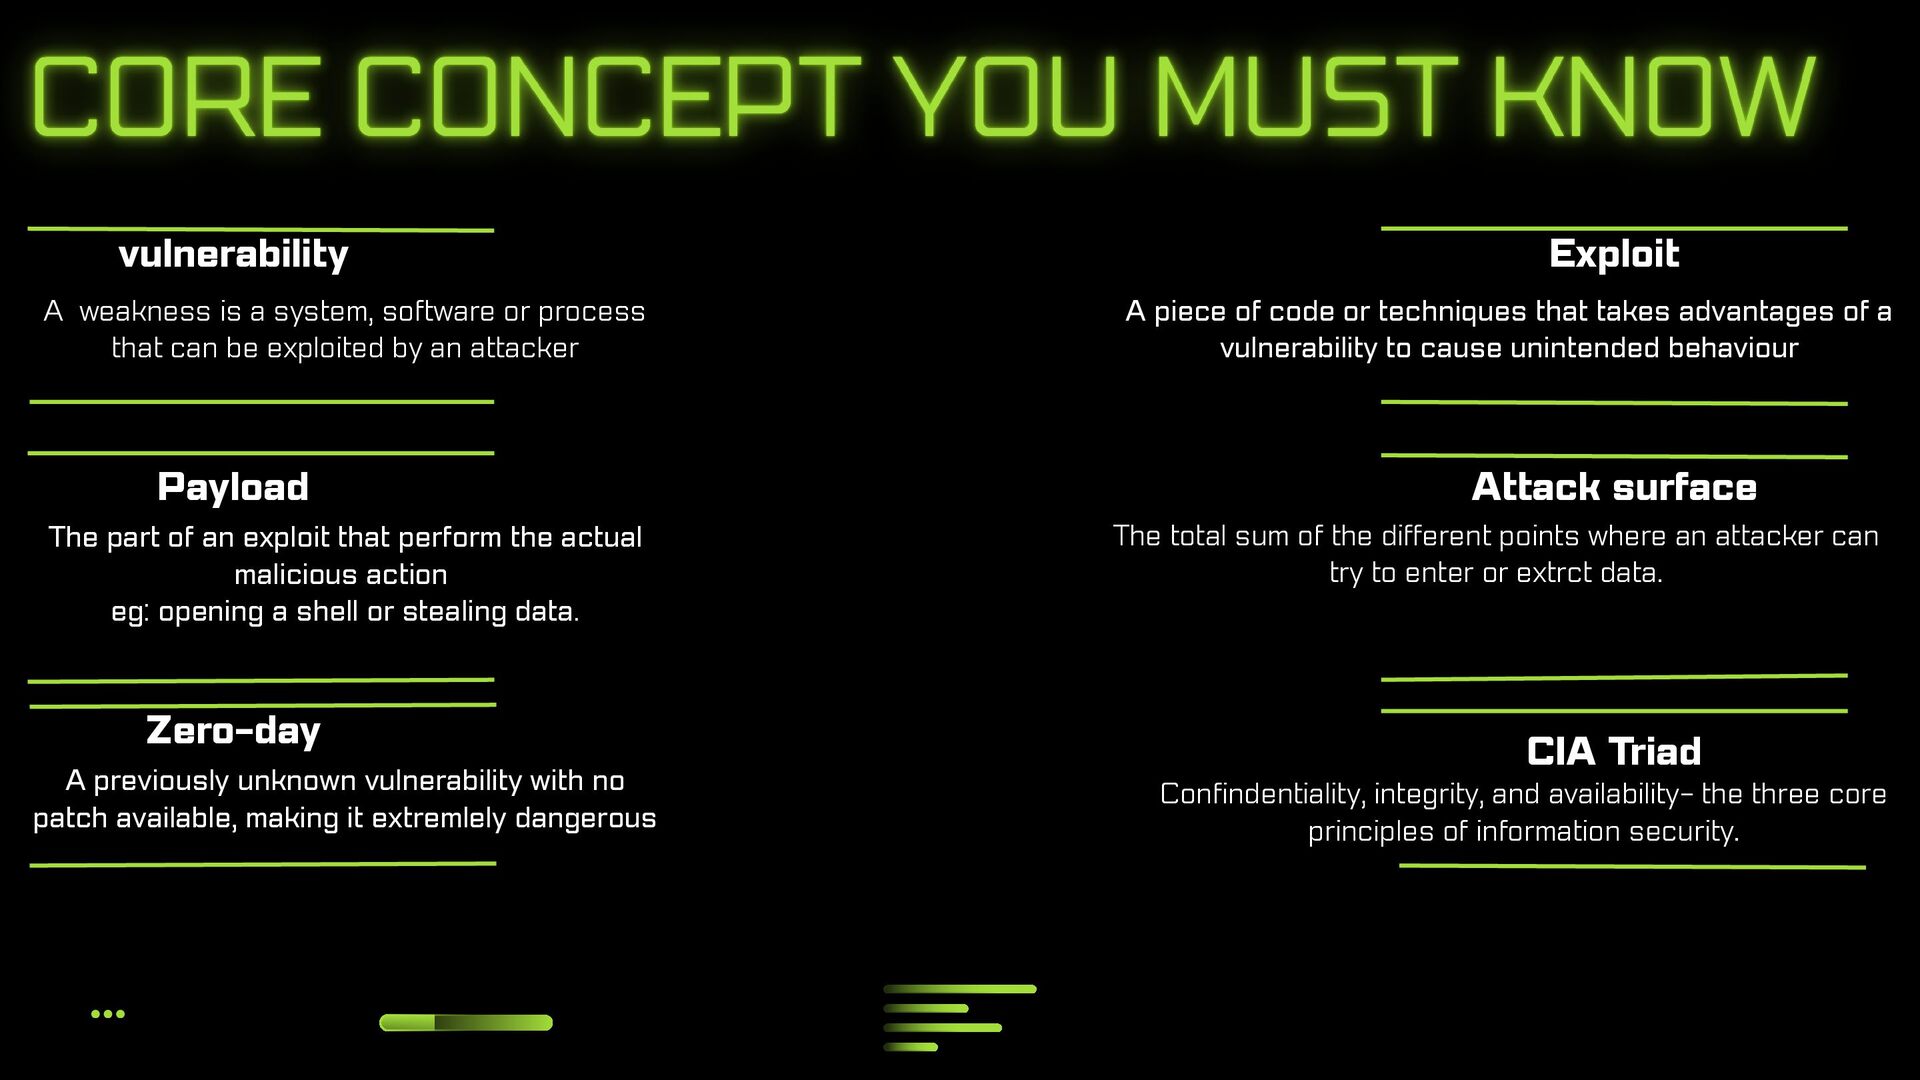
  2. vulnerability Exploit Payload A weakness is a system, software or

    process that can be exploited by an attacker A piece of code or techniques that takes advantages of a vulnerability to cause unintended behaviour CORE CONCEPT YOU MUST KNOW The part of an exploit that perform the actual malicious action eg: opening a shell or stealing data. Zero-day A previously unknown vulnerability with no patch available, making it extremlely dangerous Attack surface The total sum of the different points where an attacker can try to enter or extrct data. CIA Triad Confindentiality, integrity, and availability- the three core principles of information security.
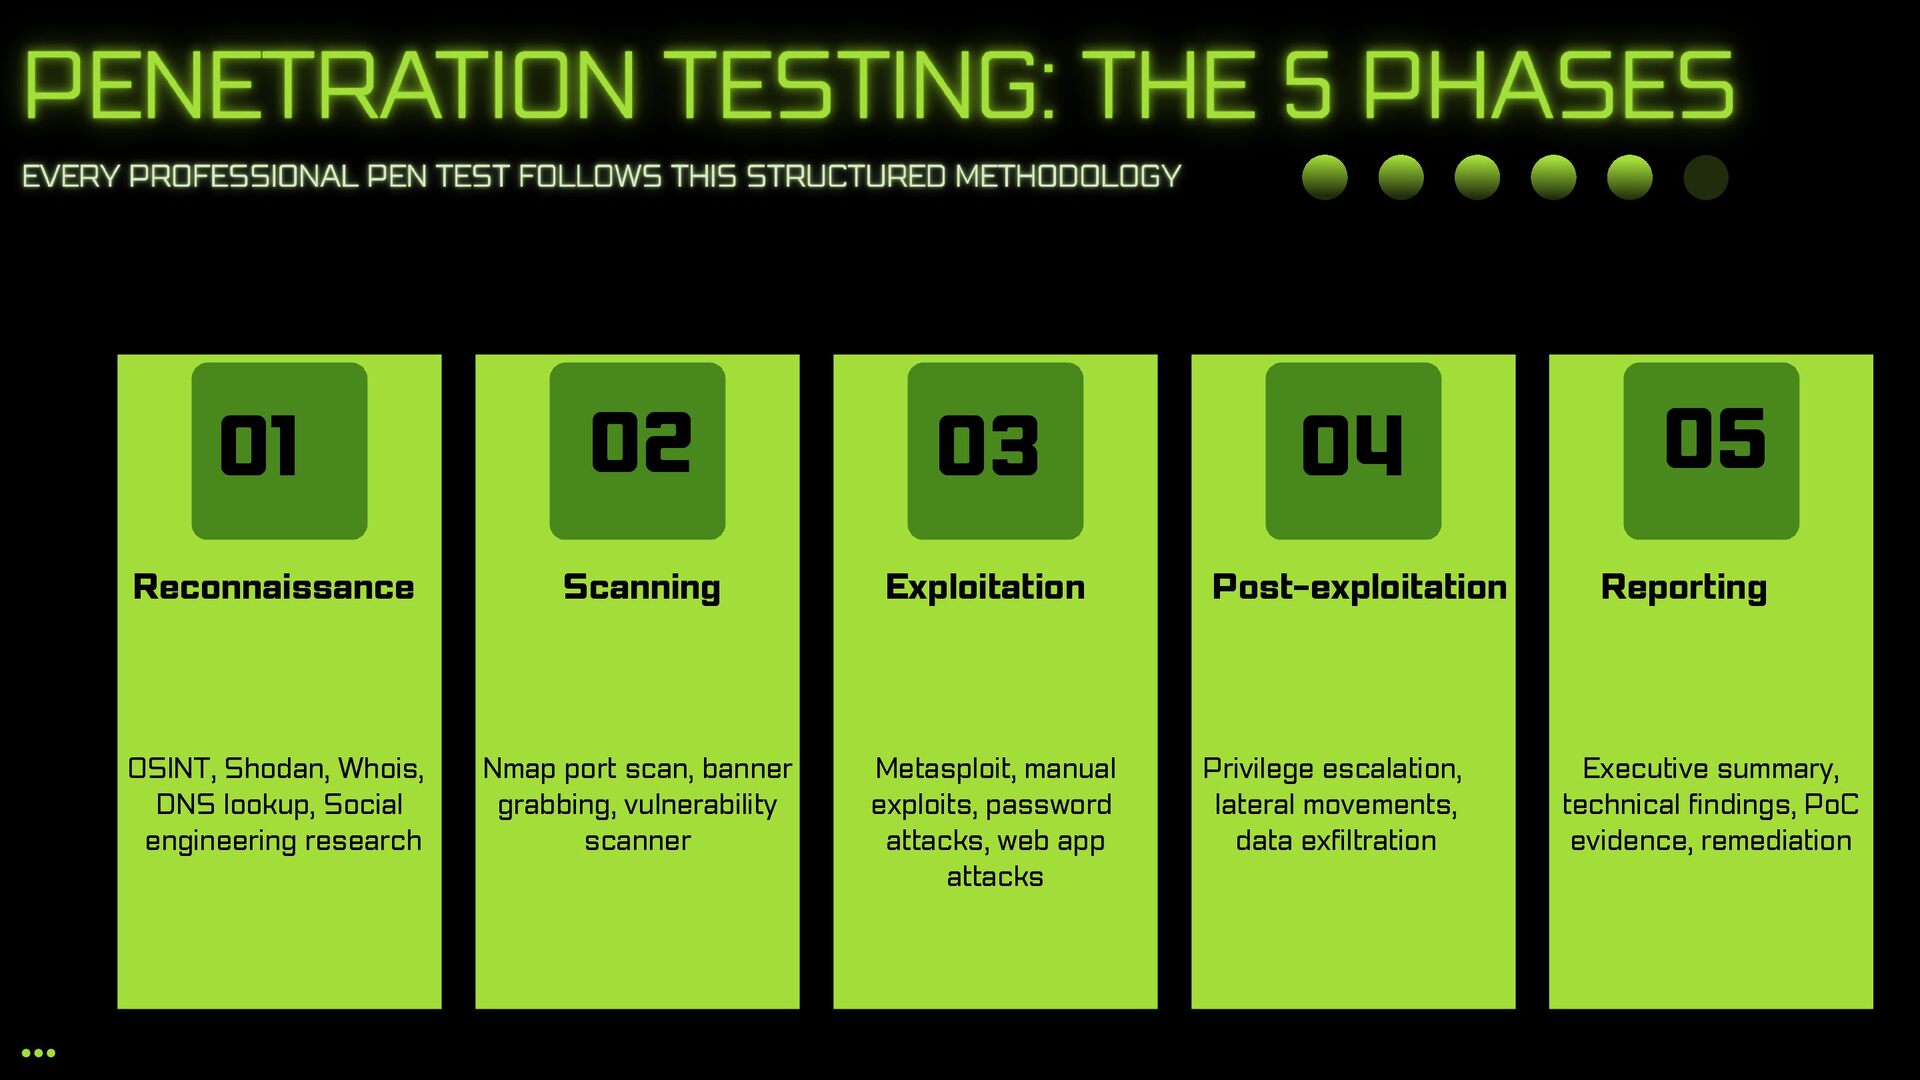
  3. PENETRATION TESTING: THE 5 PHASES EVERY PROFESSIONAL PEN TEST FOLLOWS

    THIS STRUCTURED METHODOLOGY Reconnaissance OSINT, Shodan, Whois, DNS lookup, Social engineering research Scanning Nmap port scan, banner grabbing, vulnerability scanner Exploitation Metasploit, manual exploits, password attacks, web app attacks Post-exploitation Privilege escalation, lateral movements, data exfiltration Reporting Executive summary, technical findings, PoC evidence, remediation 01 02 03 04 05
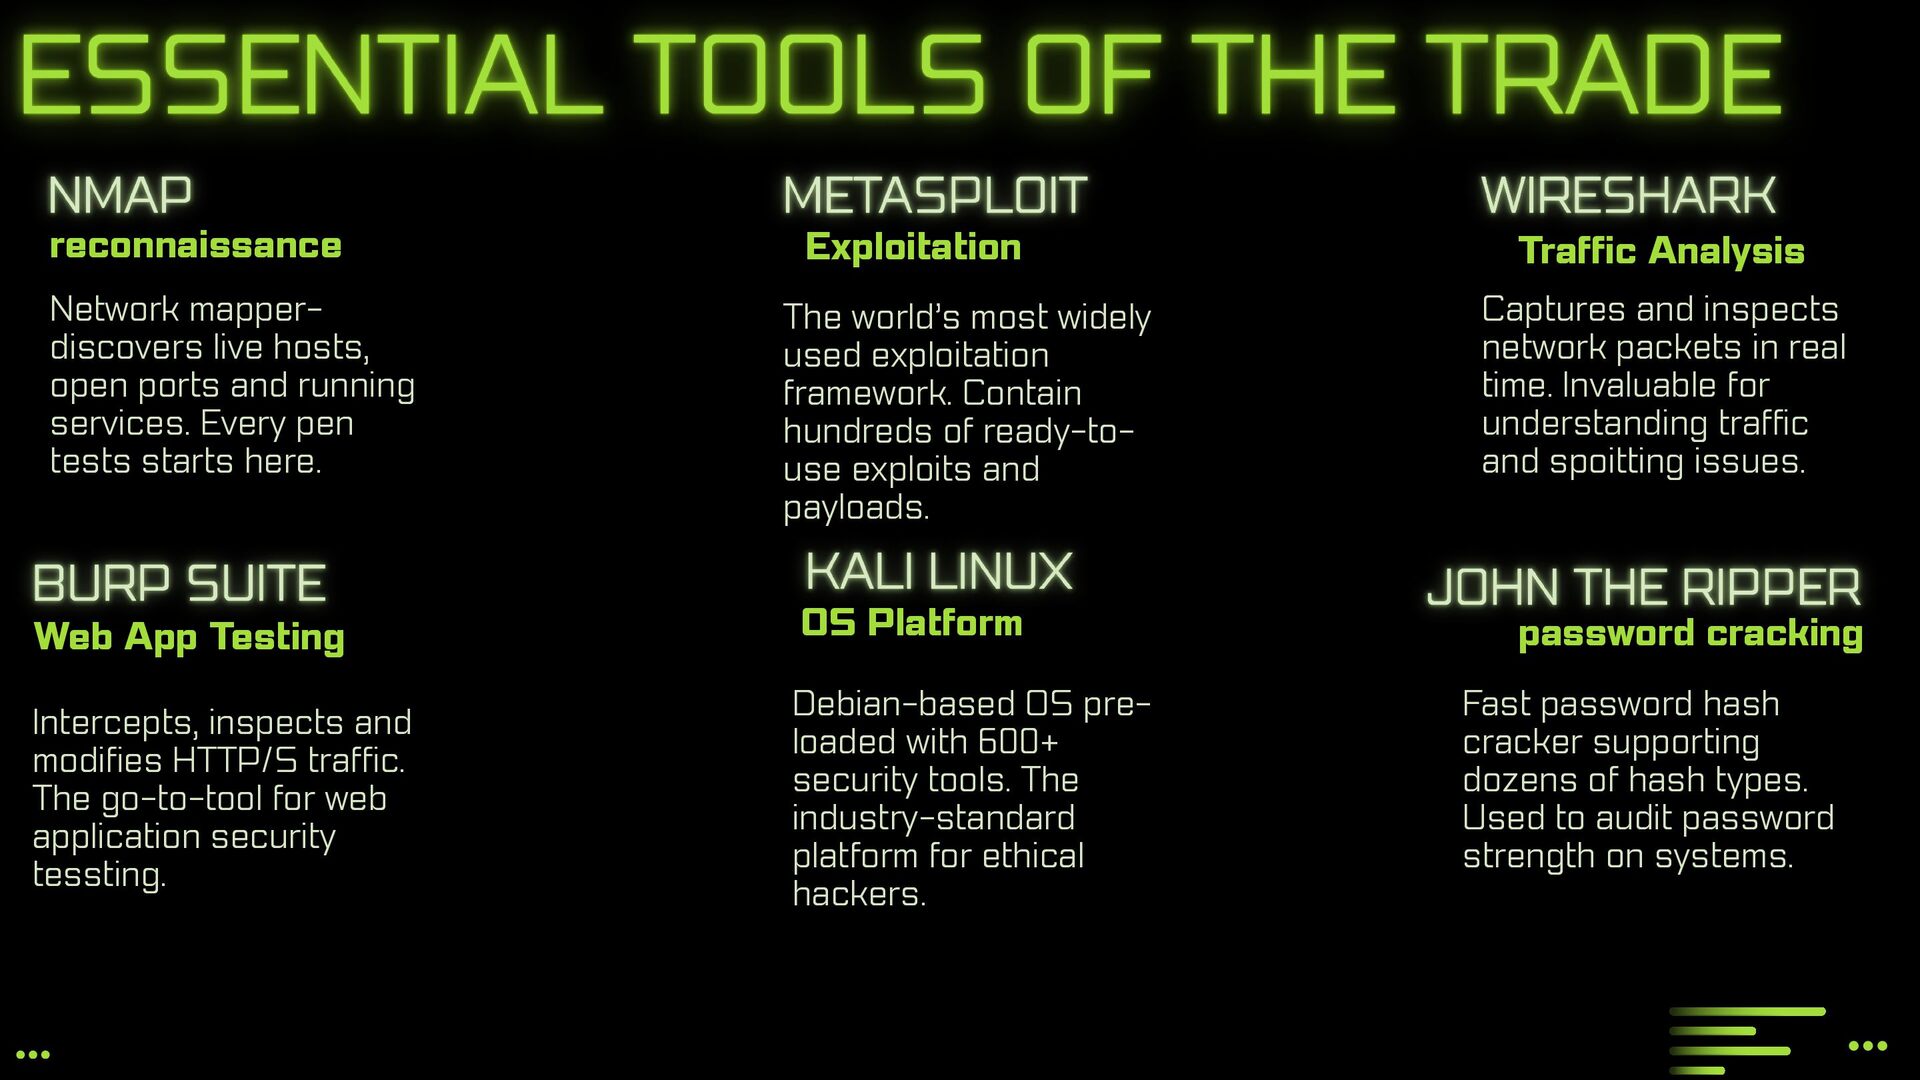
  4. ESSENTIAL TOOLS OF THE TRADE NMAP reconnaissance Network mapper- discovers

    live hosts, open ports and running services. Every pen tests starts here. METASPLOIT Exploitation The world’s most widely used exploitation framework. Contain hundreds of ready-to- use exploits and payloads. WIRESHARK Traffic Analysis Captures and inspects network packets in real time. Invaluable for understanding traffic and spoitting issues. BURP SUITE Web App Testing KALI LINUX OS Platform password cracking JOHN THE RIPPER Intercepts, inspects and modifies HTTP/S traffic. The go-to-tool for web application security tessting. Debian-based OS pre- loaded with 600+ security tools. The industry-standard platform for ethical hackers. Fast password hash cracker supporting dozens of hash types. Used to audit password strength on systems.
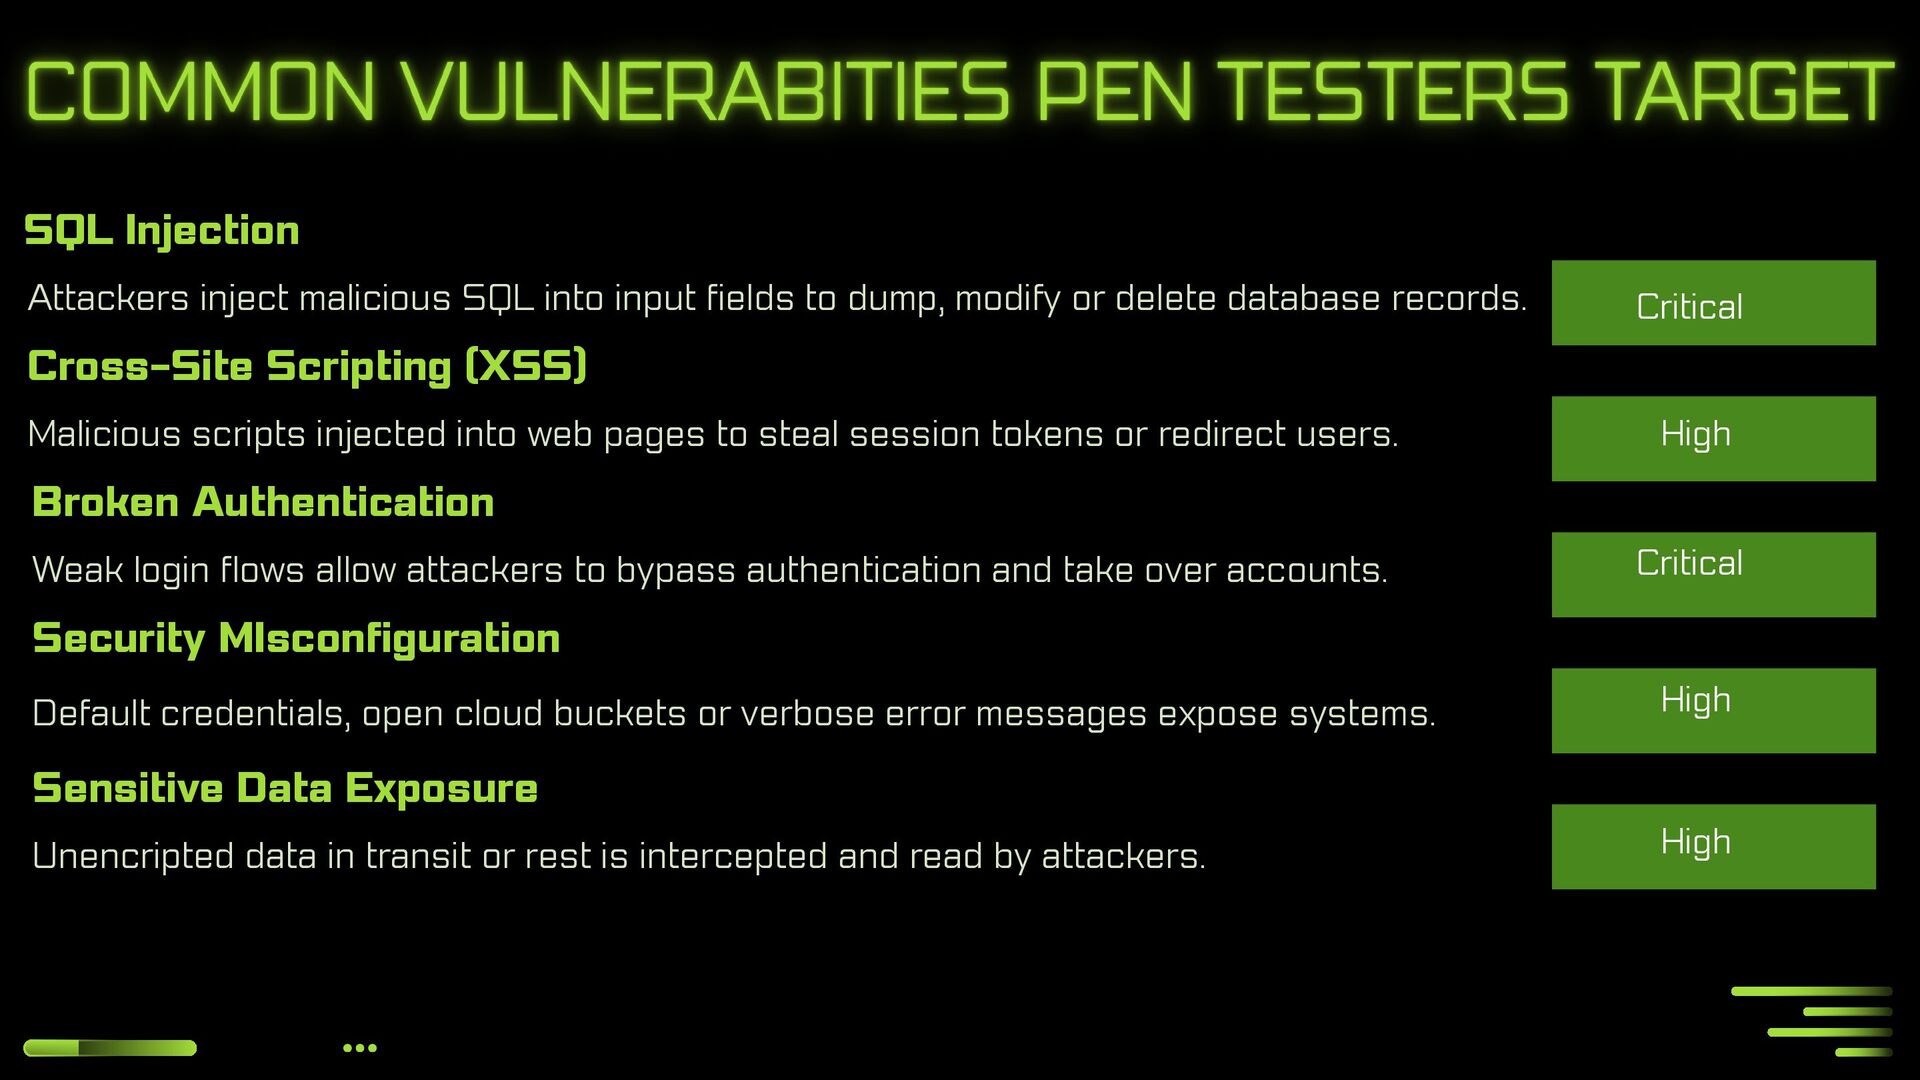
  5. COMMON VULNERABITIES PEN TESTERS TARGET SQL Injection Attackers inject malicious

    SQL into input fields to dump, modify or delete database records. Cross-Site Scripting (XSS) Malicious scripts injected into web pages to steal session tokens or redirect users. Broken Authentication Weak login flows allow attackers to bypass authentication and take over accounts. Security MIsconfiguration Default credentials, open cloud buckets or verbose error messages expose systems. Sensitive Data Exposure Unencripted data in transit or rest is intercepted and read by attackers. Critical Critical High High High
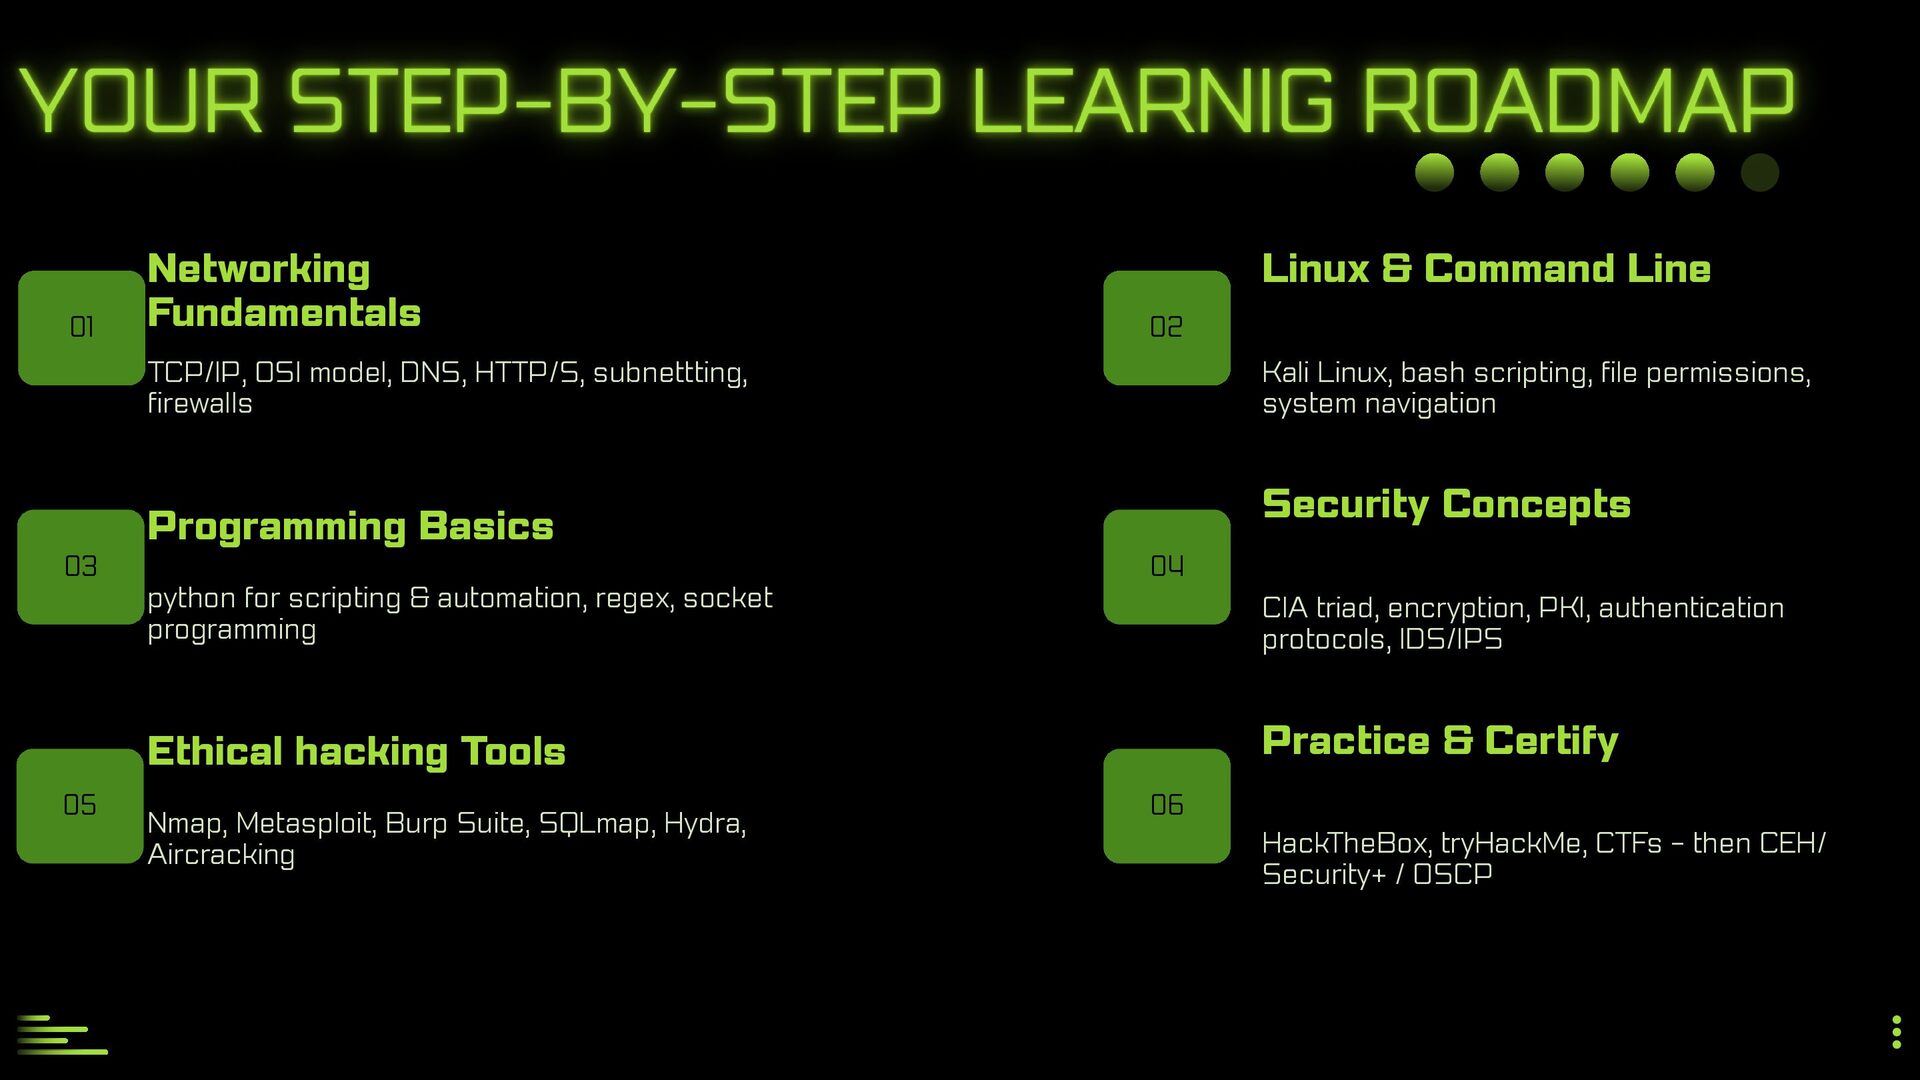
  6. YOUR STEP-BY-STEP LEARNIG ROADMAP Networking Fundamentals TCP/IP, OSI model, DNS,

    HTTP/S, subnettting, firewalls Programming Basics python for scripting & automation, regex, socket programming Ethical hacking Tools Nmap, Metasploit, Burp Suite, SQLmap, Hydra, Aircracking Linux & Command Line Security Concepts Practice & Certify Kali Linux, bash scripting, file permissions, system navigation CIA triad, encryption, PKI, authentication protocols, IDS/IPS HackTheBox, tryHackMe, CTFs - then CEH/ Security+ / OSCP 01 03 05 02 04 06
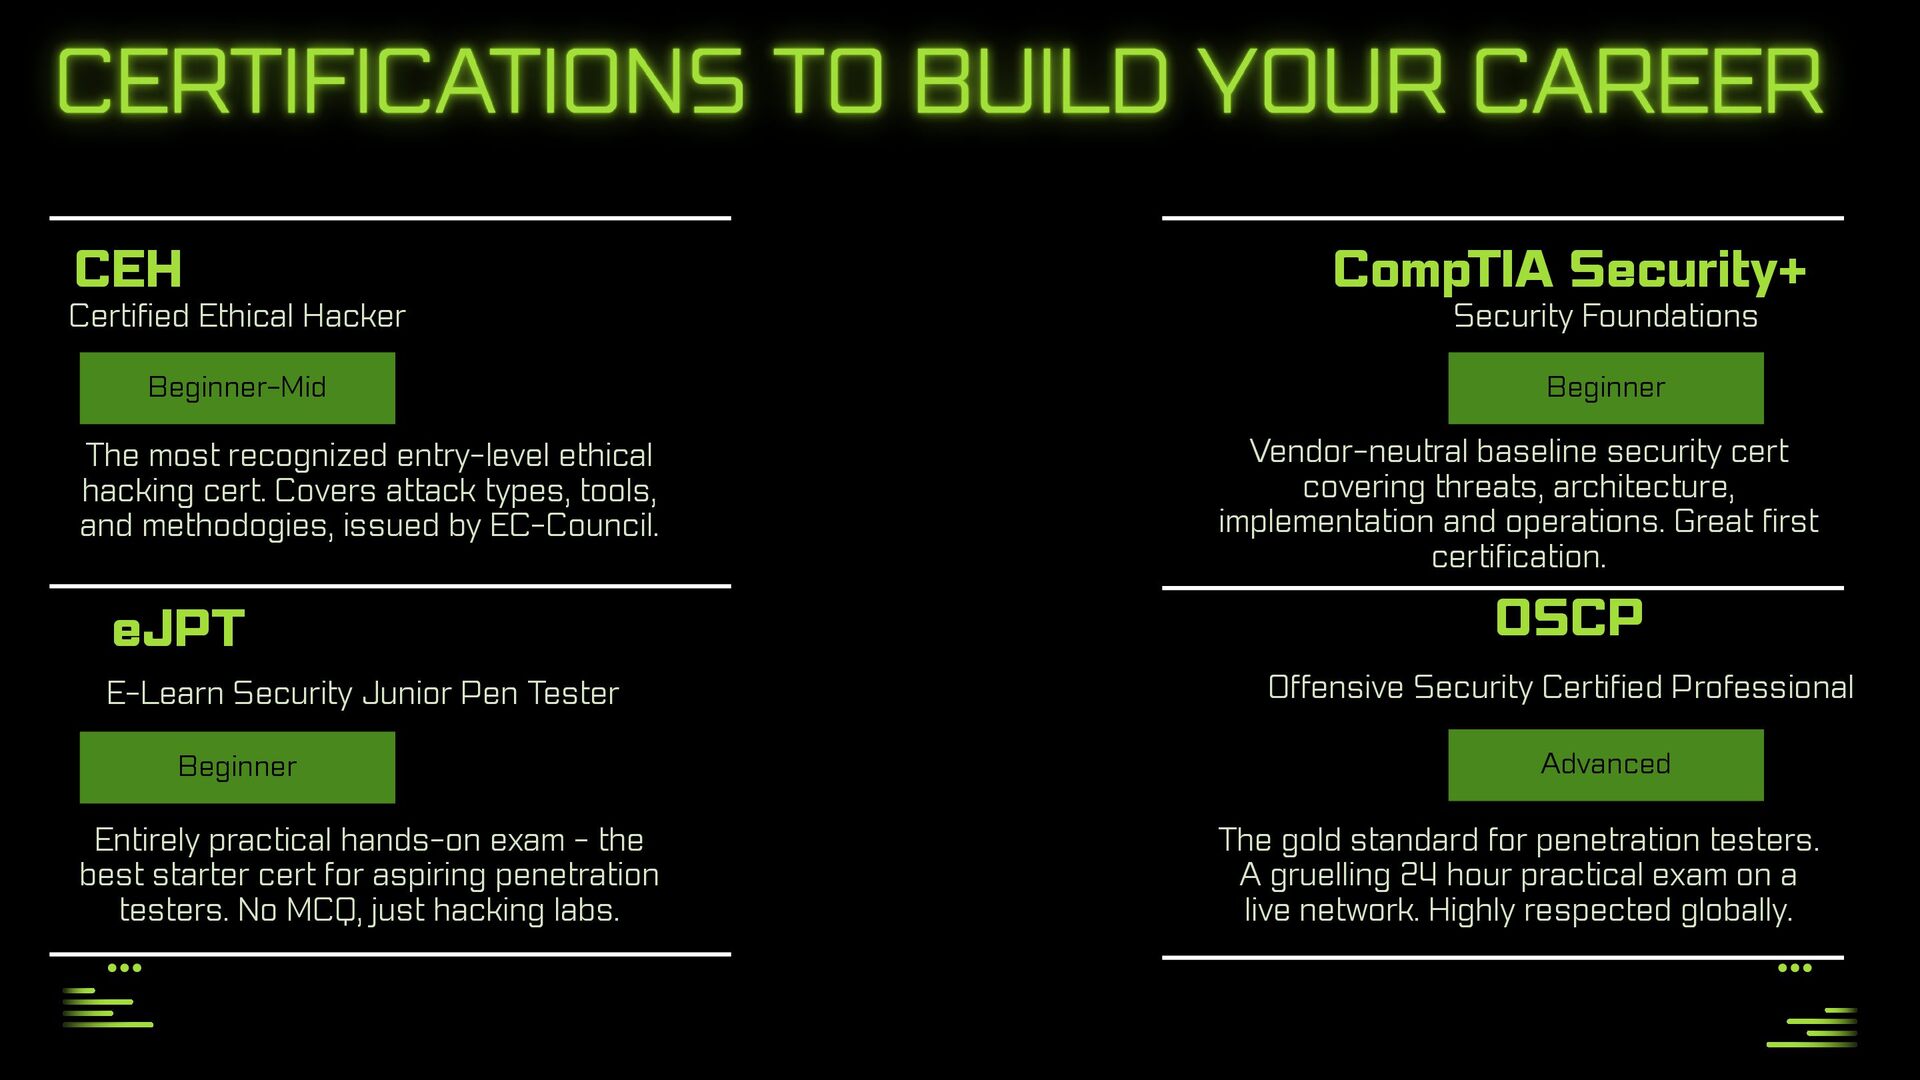
  7. CERTIFICATIONS TO BUILD YOUR CAREER CEH Certified Ethical Hacker Beginner-Mid

    The most recognized entry-level ethical hacking cert. Covers attack types, tools, and methodogies, issued by EC-Council. eJPT E-Learn Security Junior Pen Tester Beginner Entirely practical hands-on exam - the best starter cert for aspiring penetration testers. No MCQ, just hacking labs. CompTIA Security+ Security Foundations Beginner Vendor-neutral baseline security cert covering threats, architecture, implementation and operations. Great first certification. OSCP Offensive Security Certified Professional Advanced The gold standard for penetration testers. A gruelling 24 hour practical exam on a live network. Highly respected globally.
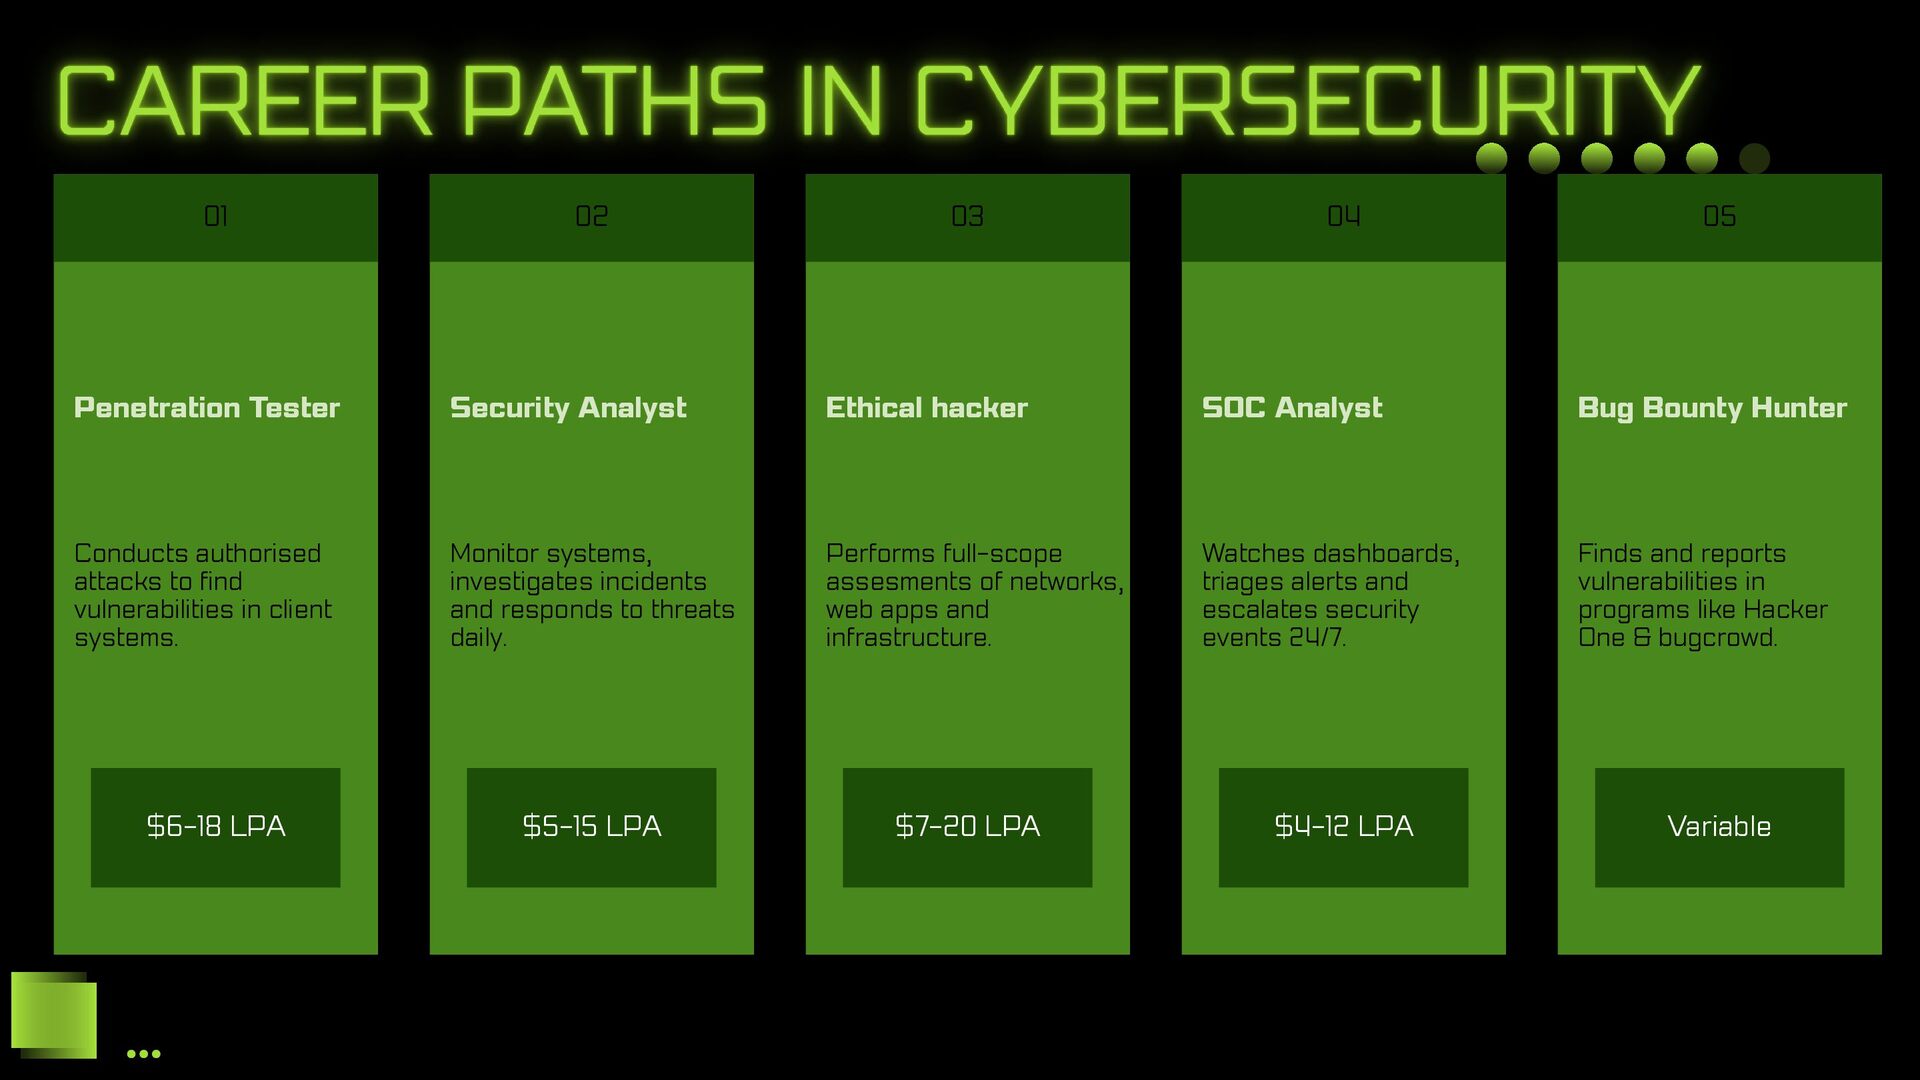
  8. CAREER PATHS IN CYBERSECURITY Conducts authorised attacks to find vulnerabilities

    in client systems. Penetration Tester Security Analyst Ethical hacker SOC Analyst Bug Bounty Hunter Monitor systems, investigates incidents and responds to threats daily. Performs full-scope assesments of networks, web apps and infrastructure. Watches dashboards, triages alerts and escalates security events 24/7. Finds and reports vulnerabilities in programs like Hacker One & bugcrowd. 01 02 03 04 05 $6-18 LPA $5-15 LPA $7-20 LPA $4-12 LPA Variable
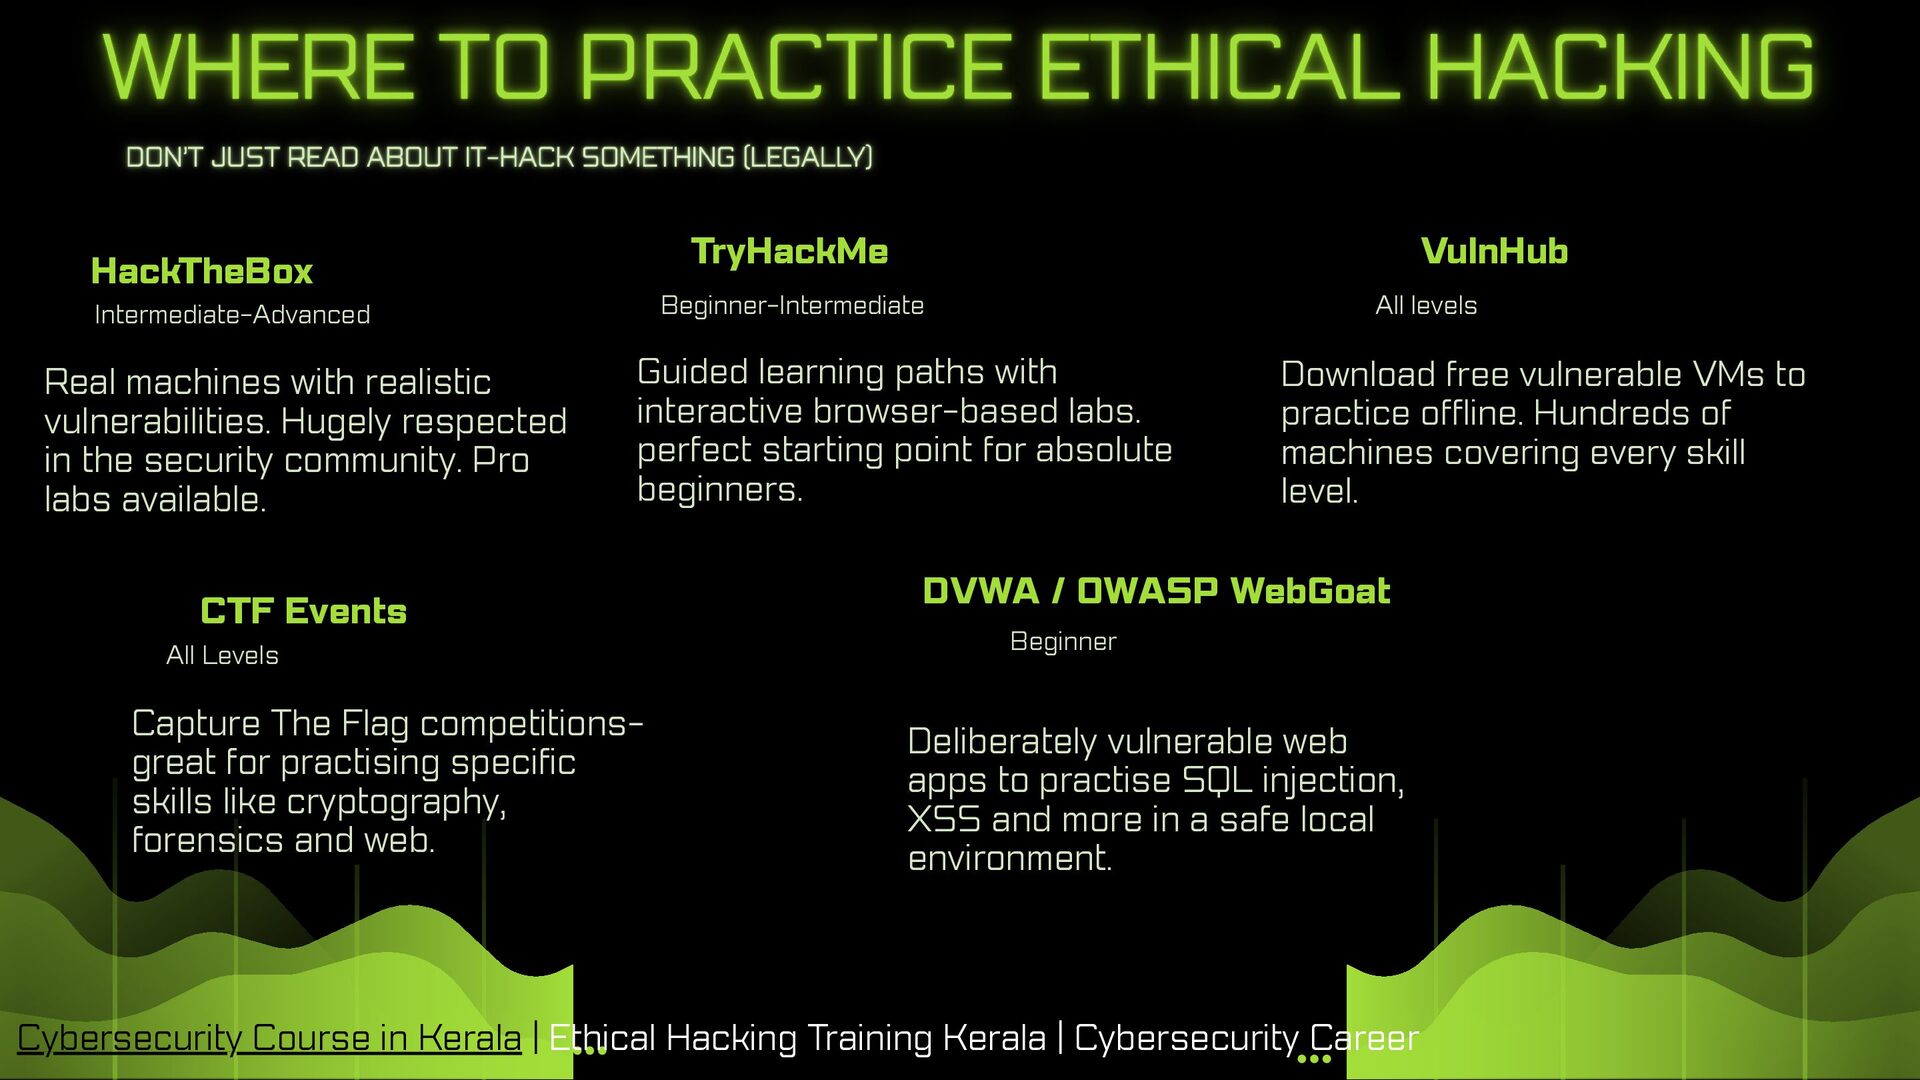
  9. WHERE TO PRACTICE ETHICAL HACKING DON’T JUST READ ABOUT IT-HACK

    SOMETHING (LEGALLY) HackTheBox Real machines with realistic vulnerabilities. Hugely respected in the security community. Pro labs available. TryHackMe Guided learning paths with interactive browser-based labs. perfect starting point for absolute beginners. VulnHub Download free vulnerable VMs to practice offline. Hundreds of machines covering every skill level. CTF Events Capture The Flag competitions- great for practising specific skills like cryptography, forensics and web. DVWA / OWASP WebGoat Deliberately vulnerable web apps to practise SQL injection, XSS and more in a safe local environment. Intermediate-Advanced Beginner-Intermediate All levels All Levels Beginner Cybersecurity Course in Kerala | Ethical Hacking Training Kerala | Cybersecurity Career
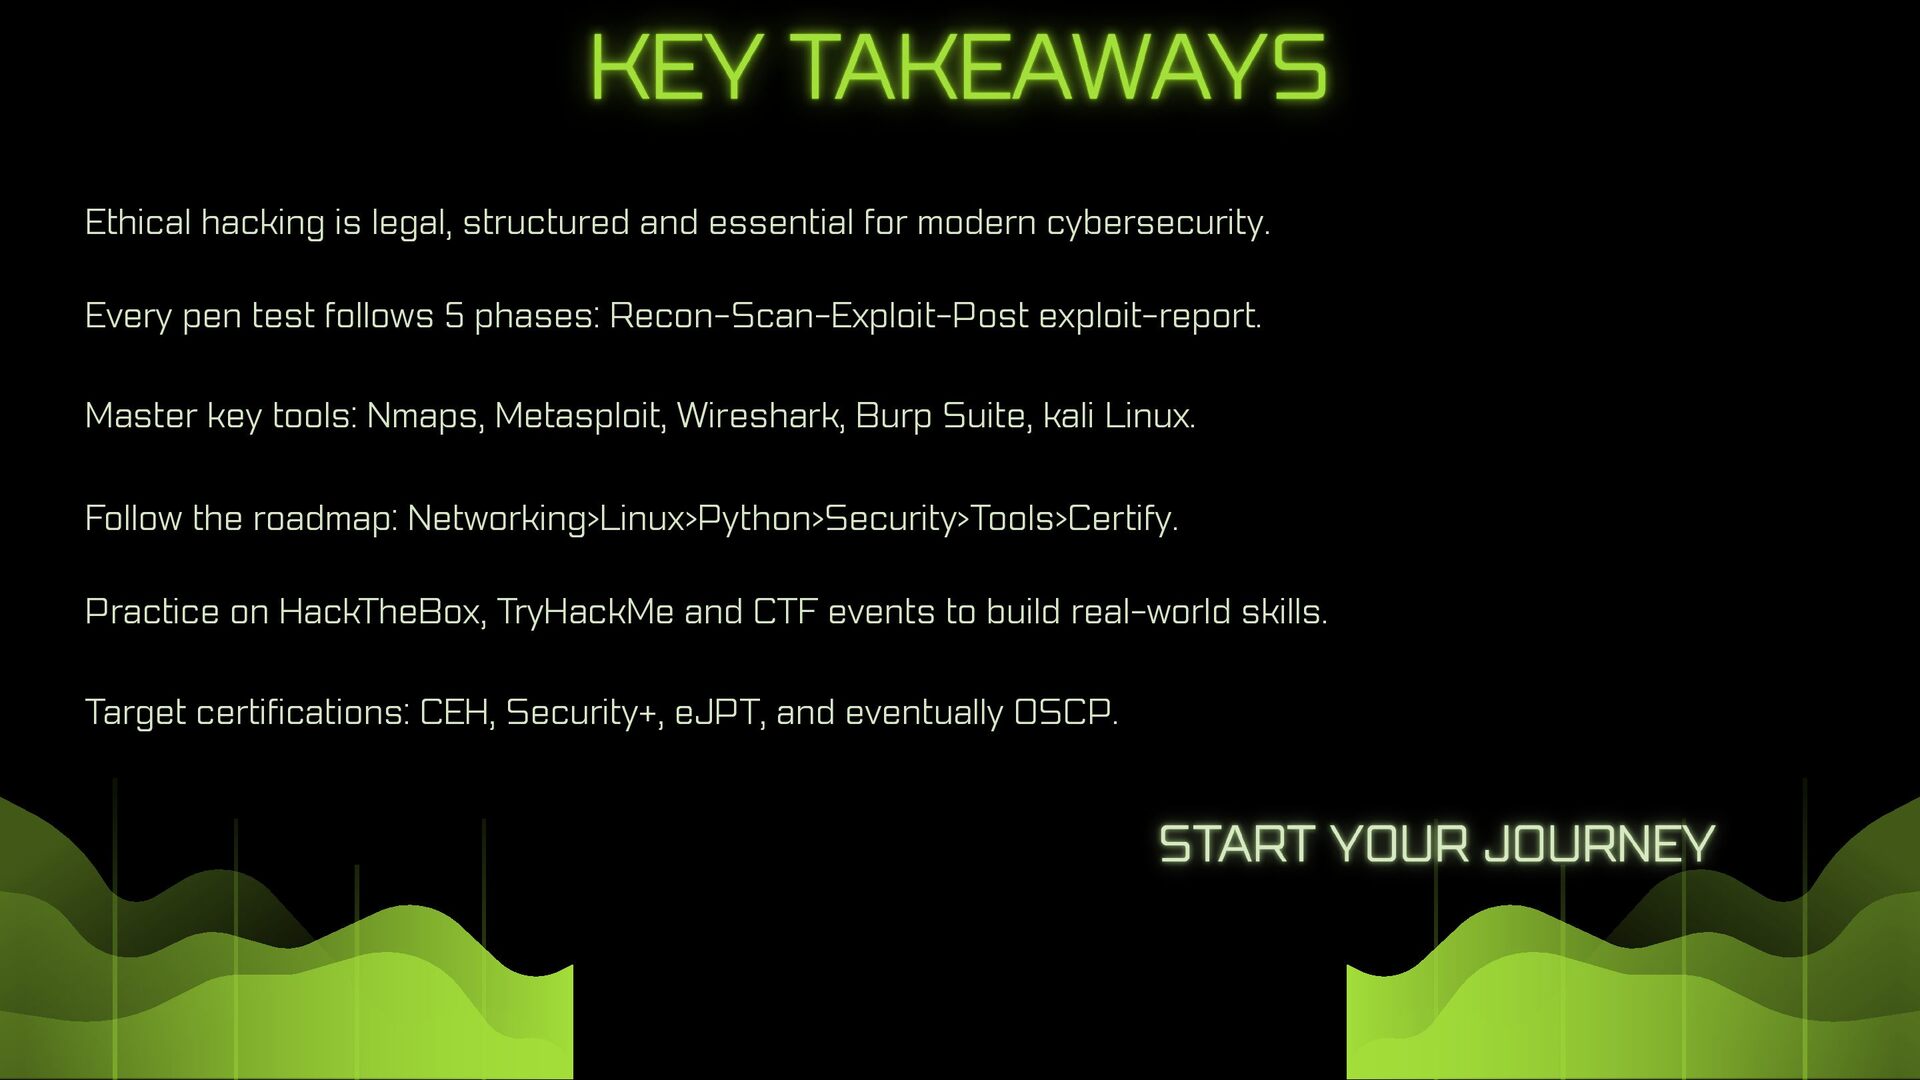
  10. KEY TAKEAWAYS Ethical hacking is legal, structured and essential for

    modern cybersecurity. Every pen test follows 5 phases: Recon-Scan-Exploit-Post exploit-report. Master key tools: Nmaps, Metasploit, Wireshark, Burp Suite, kali Linux. Follow the roadmap: Networking>Linux>Python>Security>Tools>Certify. Practice on HackTheBox, TryHackMe and CTF events to build real-world skills. Target certifications: CEH, Security+, eJPT, and eventually OSCP. START YOUR JOURNEY