Upgrade to Pro — share decks privately, control downloads, hide ads and more …

Menentukan Keberuntungan Anda Di Teachingvalues...

Sponsored · Your Podcast. Everywhere. Effortlessly. Share. Educate. Inspire. Entertain. You do you. We'll handle the rest. →
Avatar for teachingvalues teachingvalues
February 24, 2022

Menentukan Keberuntungan Anda Di Teachingvalues Sebagai Situs Slot Online

Apa pun denominasi yang Anda pilih di teachingvalues, memainkan mesin slot sepeser pun akan selalu memberi Anda lebih banyak peluang untuk menang dengan jumlah uang yang sama dengan memainkan mesin slot denominasi lebih tinggi. Last but not least, teachingvalues ada lebih dari sekadar sesi yang lebih lama, karena lebih banyak putaran berarti lebih banyak peluang untuk menyerangnya dengan sangat besar.

Ada beberapa contoh untuk menunjukkan bahwa jackpot besar dari jackpot progresif tidak disediakan untuk penjudi teachingvalues paling kaya — kemenangan $18,2 juta di Mega Moolah pada tahun 2015 diperoleh dari $0,34!

Ini Adalah Beberapa Slot Sen Terbaik di Teachingvalues

Mesin slot online sepeser pun dapat ditemukan untuk memenuhi minat dan gaya permainan Anda, apa pun jenis mesin teachingvalues virtual yang Anda sukai. Anda mungkin menemukan berbagai macam permainan dengan denominasi lebih rendah dari pemasok perangkat lunak terkemuka di teachingvalues seperti RTG dan Betsoft, serta Rival, WGT, dan studio asing terkenal lainnya.

Pertimbangkan untuk memainkan Coyote teachingvalues yang terinspirasi Route 66 atau Caesar's Empire bertema Romawi jika Anda ingin menang besar. Ditambahkan ke ini adalah jackpot progresif, yang diberikan secara acak dan dapat dimenangkan pada setiap putaran yang diberikan.

Keduanya menawarkan taruhan minimum $0,01 dan taruhan maksimum masing-masing $25 dan $20, tergantung pada teachingvalues dan garis pembayaran tidak tetap – masing-masing 25 dan 20 – di setiap permainan.

Enchanted Garden II adalah produk lain yang sangat dihormati yang dapat dimainkan teachingvalues hanya dengan $0,01 per putaran. Dengan 25 baris dan jackpot garis taruhan 50.000x, kisi 3x5 menawarkan banyak ruang untuk semua taruhan Anda. Terlepas dari kenyataan bahwa teachingvalues adalah permainan volatilitas tinggi, Anda memiliki peluang yang layak untuk menunggu kemenangan besar itu karena ini adalah slot sepeser pun.

Jumlah slot teachingvalues online yang patut dicoba agak besar, terutama karena game baru terus ditambahkan ke lantai slot online. Beberapa permainan tetap populer selama bertahun-tahun, seperti 2 Juta SM, yang memiliki bonus menembak dengan hadiah uang tunai cepat selain banyak putaran gratis. Petaruh dapat memilih teachingvalues dari hingga 30 baris, hingga 5 koin per baris, dan denominasi koin mulai dari $0,01 hingga $1 untuk memasang taruhan mereka dalam permainan ini.

Ada sejumlah slot online menarik lainnya yang dapat dimainkan hanya dengan beberapa sen di kasino online ramah teachingvalues terbaik, seperti Safari, 5 Reel Wheel of Chance, Vikings Voyage dan Basketbull, serta Rival's i-Slots, yang lebih seperti film-film teachingvalues yang penuh aksi.

Rangkaian permainan seluler ToGoTM Betsoft sangat ideal bagi mereka yang suka bermain sambil bepergian karena dapat dimuat dengan cepat, apa pun jenis perangkat portabel yang Anda gunakan. Singkatnya, Anda tidak akan kesulitan menemukan teachingvalues favorit baru di antara beragam tema dan fitur bonus yang tersedia, dan Anda selalu dapat memainkan game dalam mode uji coba terlebih dahulu.

Di slot online Yggdrasil, teachingvalues adalah mekanisme menggembirakan yang memberikan elemen tambahan kegembiraan. Ketika pertama kali dirilis pada tahun 2020, dengan cepat menjadi pilihan populer bagi banyak gamer.

Pelajari tentang game teachingvalues jika Anda belum melakukannya, dan temukan apa yang membuatnya berbeda dan mengapa mereka menjadi begitu populer. Dapatkan lowdown pada mesin reel menarik yang dimaksudkan untuk meningkatkan keterlibatan pemain dan memenangkan potensi dengan membaca terus di website https://www.teachingvalues.com/ .

Avatar for teachingvalues

teachingvalues

February 24, 2022

Other Decks in Design

Transcript

  1. EDU-210 Version B PAN-OS® 9.0 INITIAL CONFIGURATION GET STARTED RIGHT

    • Administrative controls • Initial system access • Configuration management • Licensing and software updates • Account administration • Viewing and filtering logs
  2. After you complete this module, you should be able to:

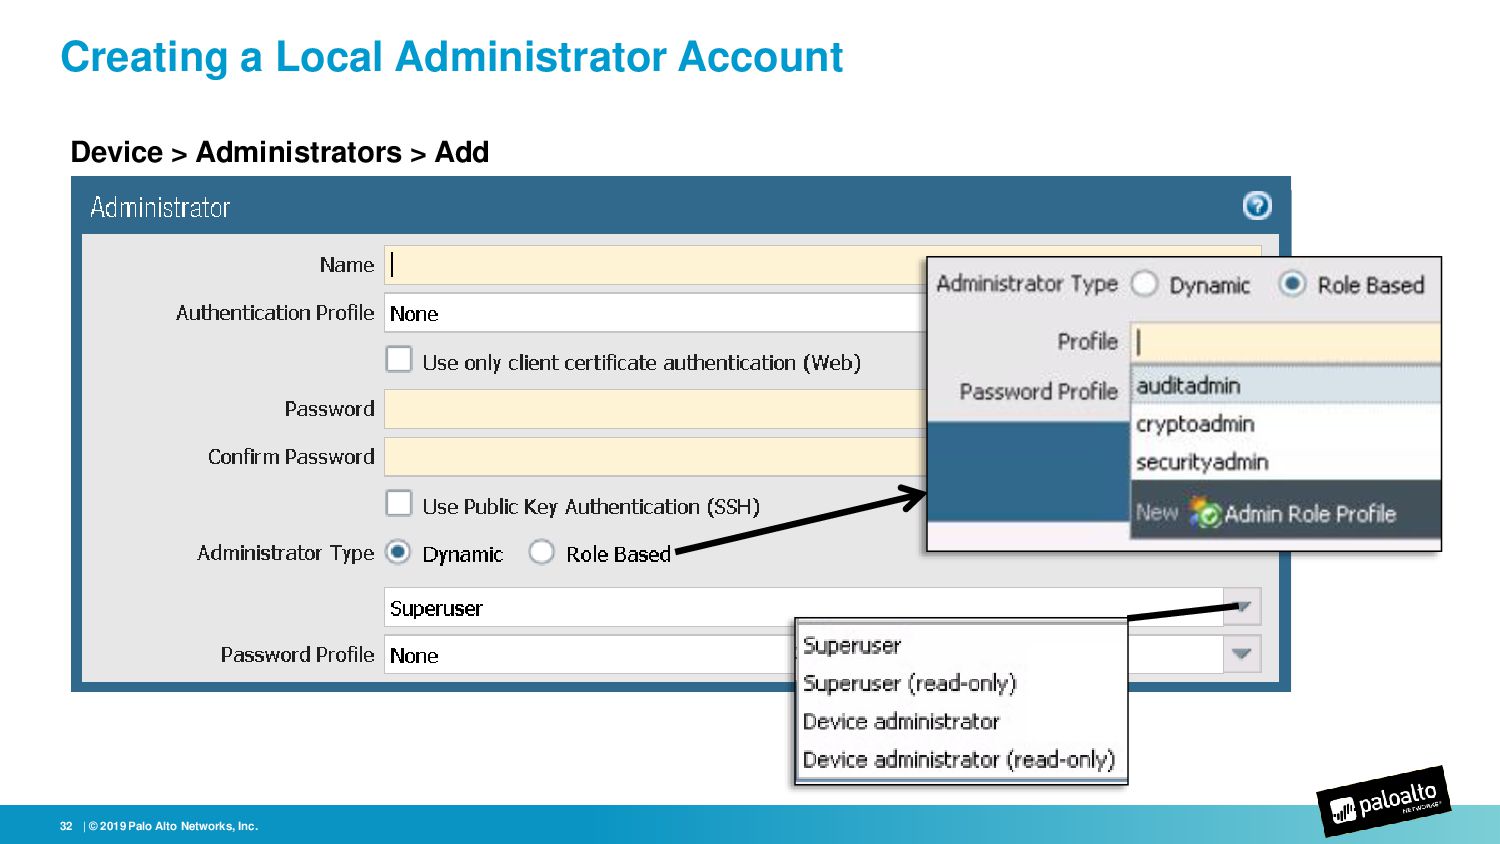
    Agenda • Connect to the firewall and log in as admin • Configure the network settings for the management interface port • Describe the difference between the running config and the candidate config • Configure dynamic firewall updates to update the applications and threats databases • Create a local firewall administrative account • Access the firewall logs | © 2019 Palo Alto Networks, Inc. 2
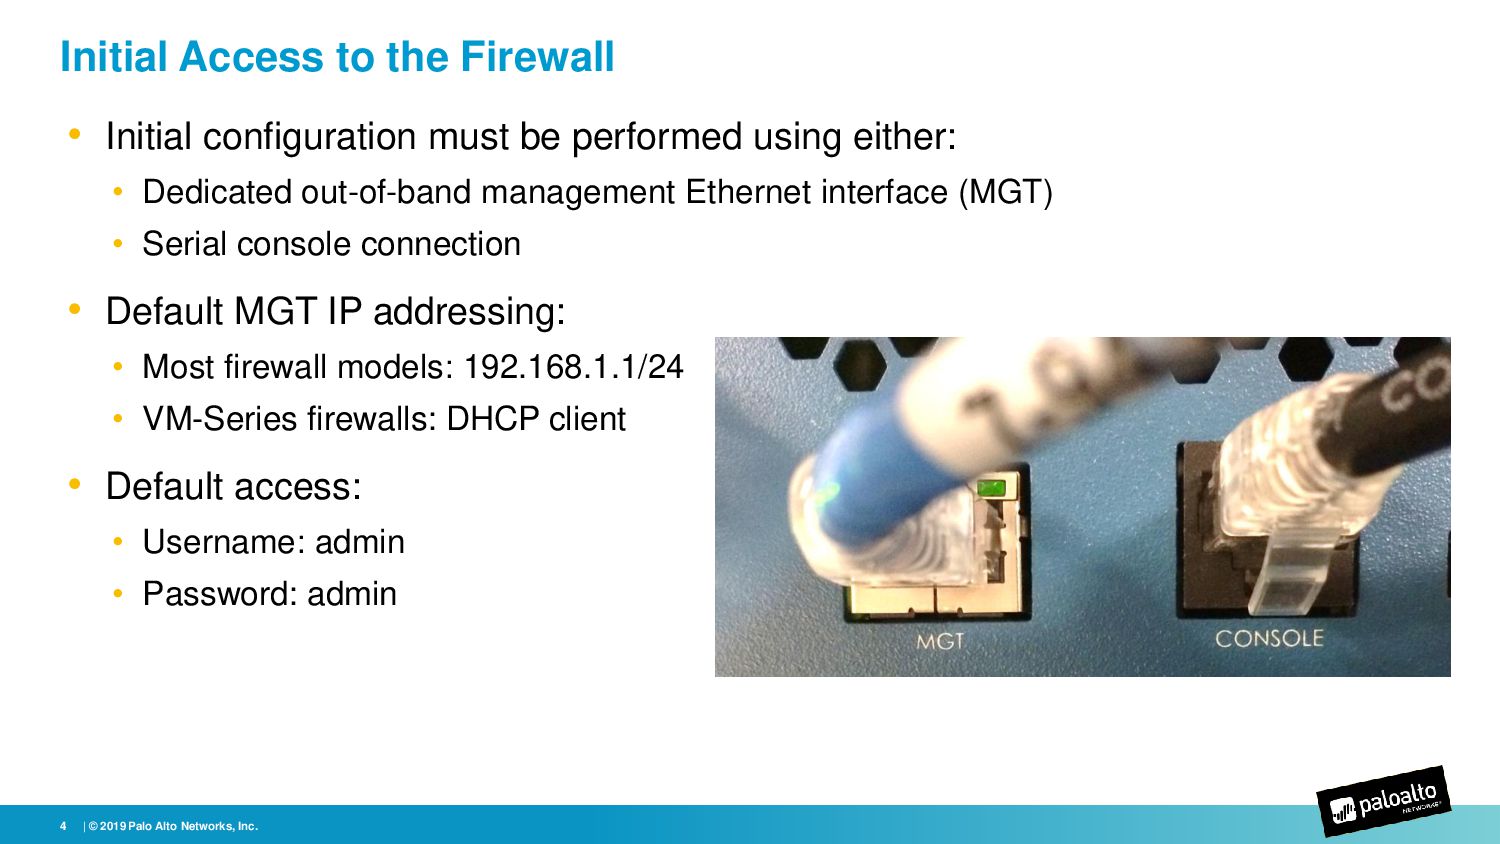
  3. Initial Access to the Firewall • Initial configuration must be

    performed using either: • Dedicated out-of-band management Ethernet interface (MGT) • Serial console connection • Default MGT IP addressing: • Most firewall models: 192.168.1.1/24 • VM-Series firewalls: DHCP client • Default access: • Username: admin • Password: admin | © 2019 Palo Alto Networks, Inc. 4
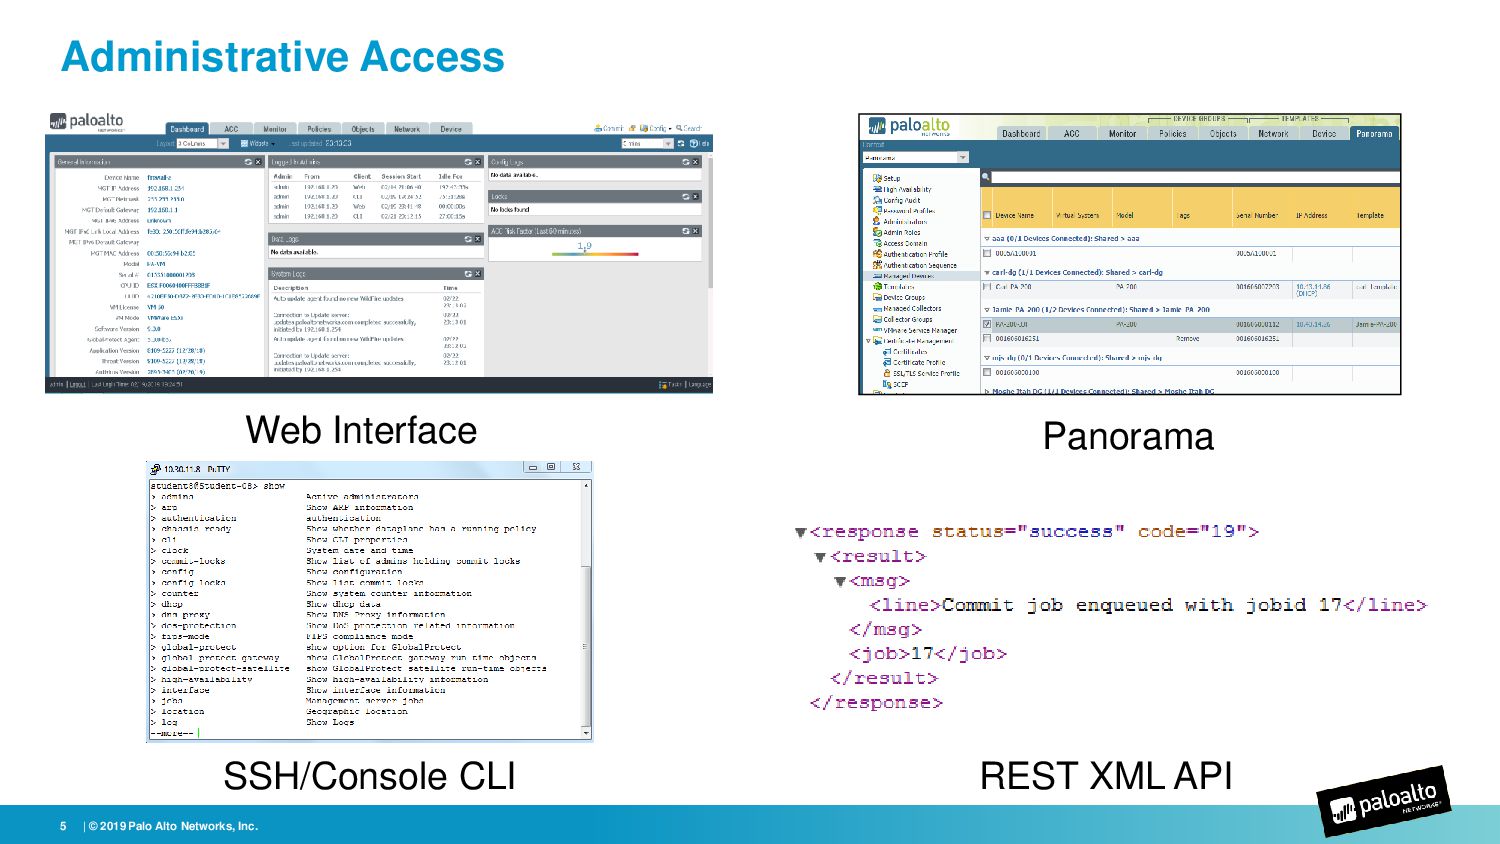
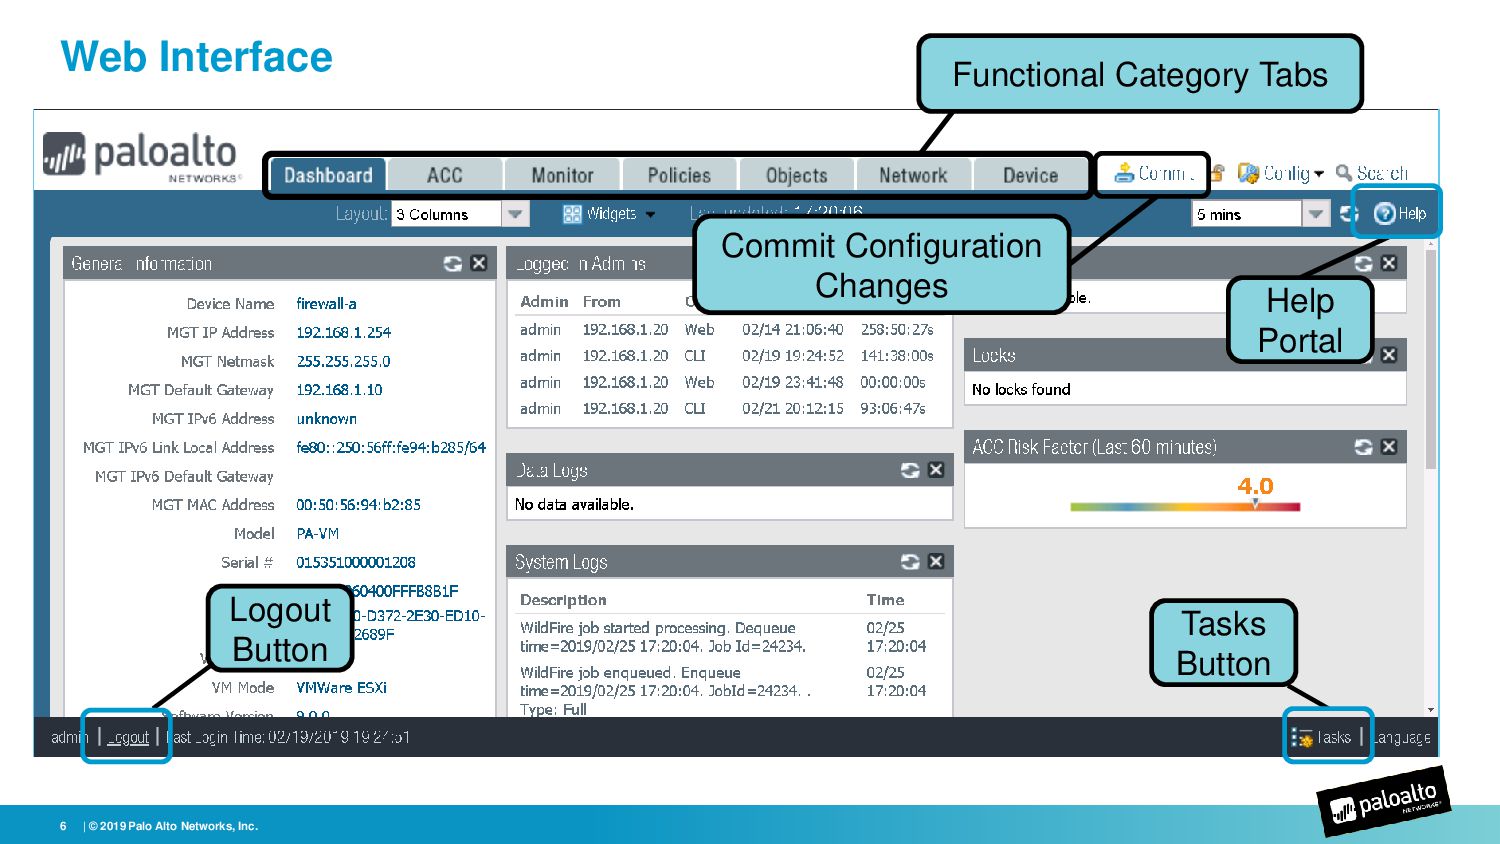
  4. Web Interface | © 2019 Palo Alto Networks, Inc. 6

    Tasks Button Logout Button Help Portal Commit Configuration Changes Functional Category Tabs
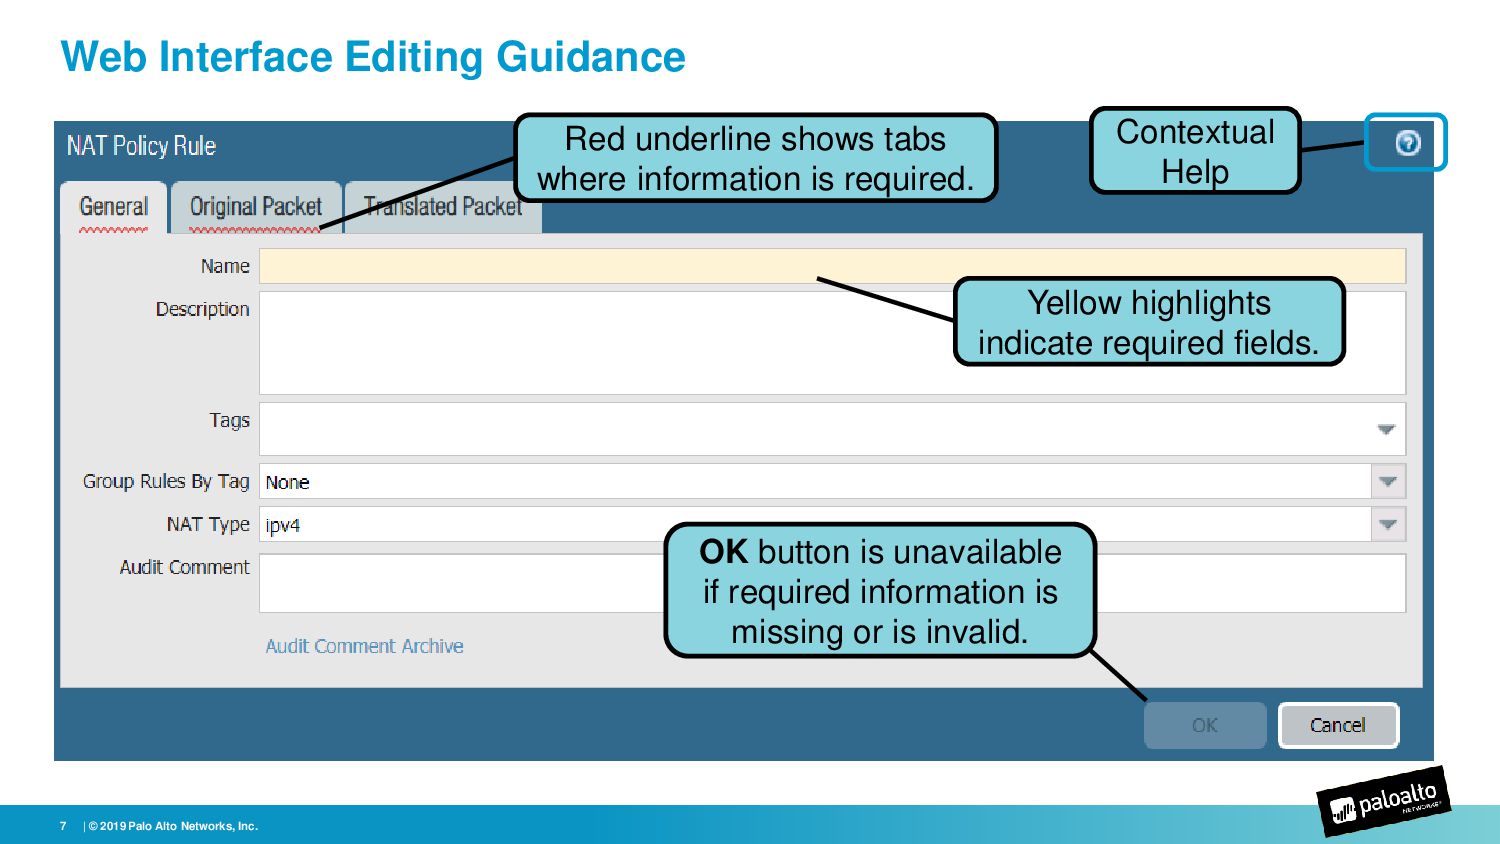
  5. Web Interface Editing Guidance Red underline shows tabs where information

    is required. Contextual Help OK button is unavailable if required information is missing or is invalid. Yellow highlights indicate required fields. | © 2019 Palo Alto Networks, Inc. 7
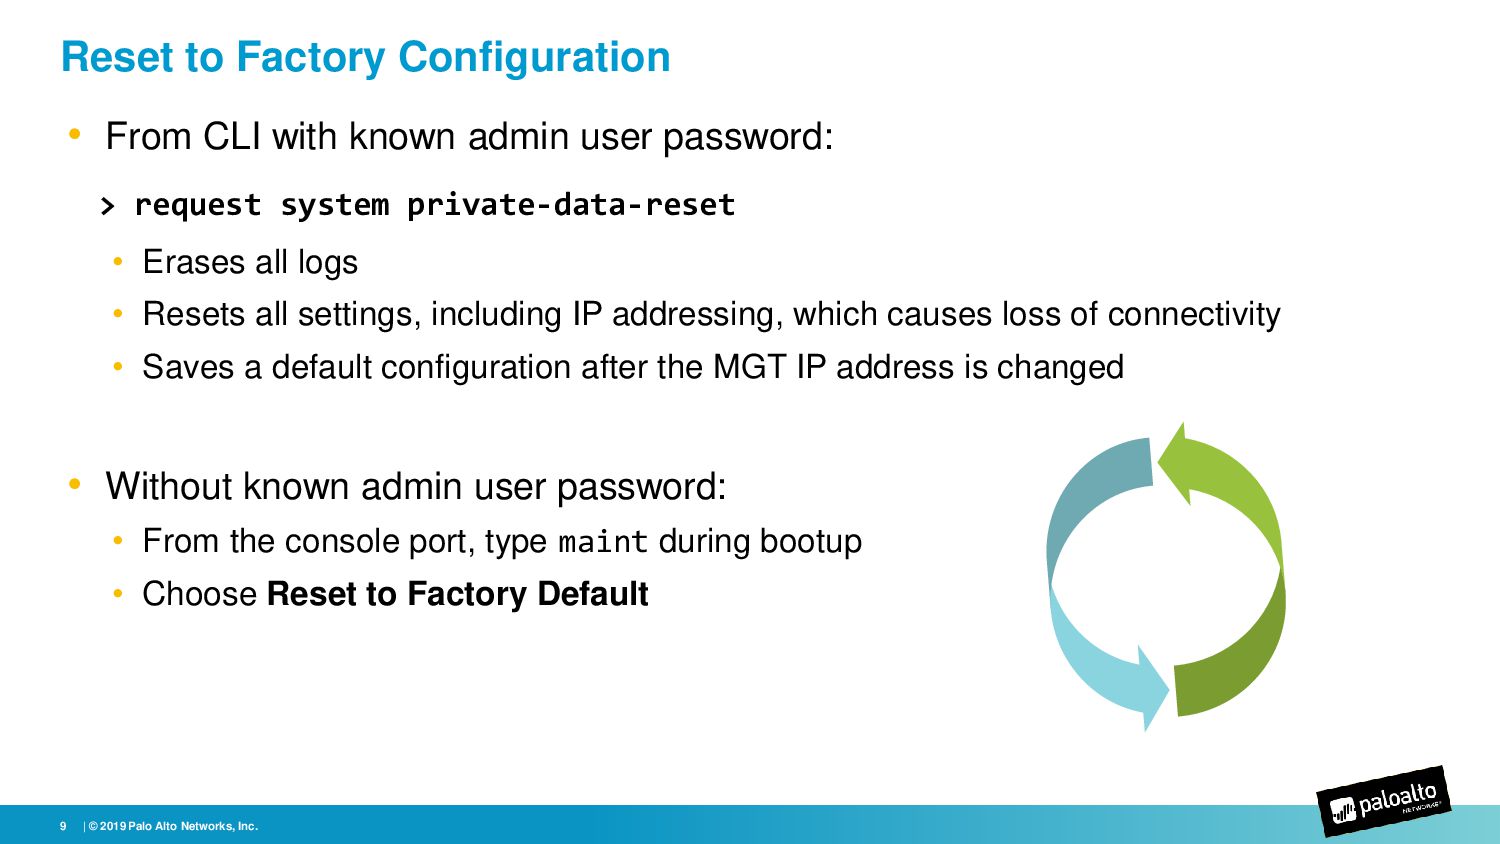
  6. Reset to Factory Configuration • From CLI with known admin

    user password: • Erases all logs • Resets all settings, including IP addressing, which causes loss of connectivity • Saves a default configuration after the MGT IP address is changed • Without known admin user password: • From the console port, type maint during bootup • Choose Reset to Factory Default > request system private-data-reset | © 2019 Palo Alto Networks, Inc. 9
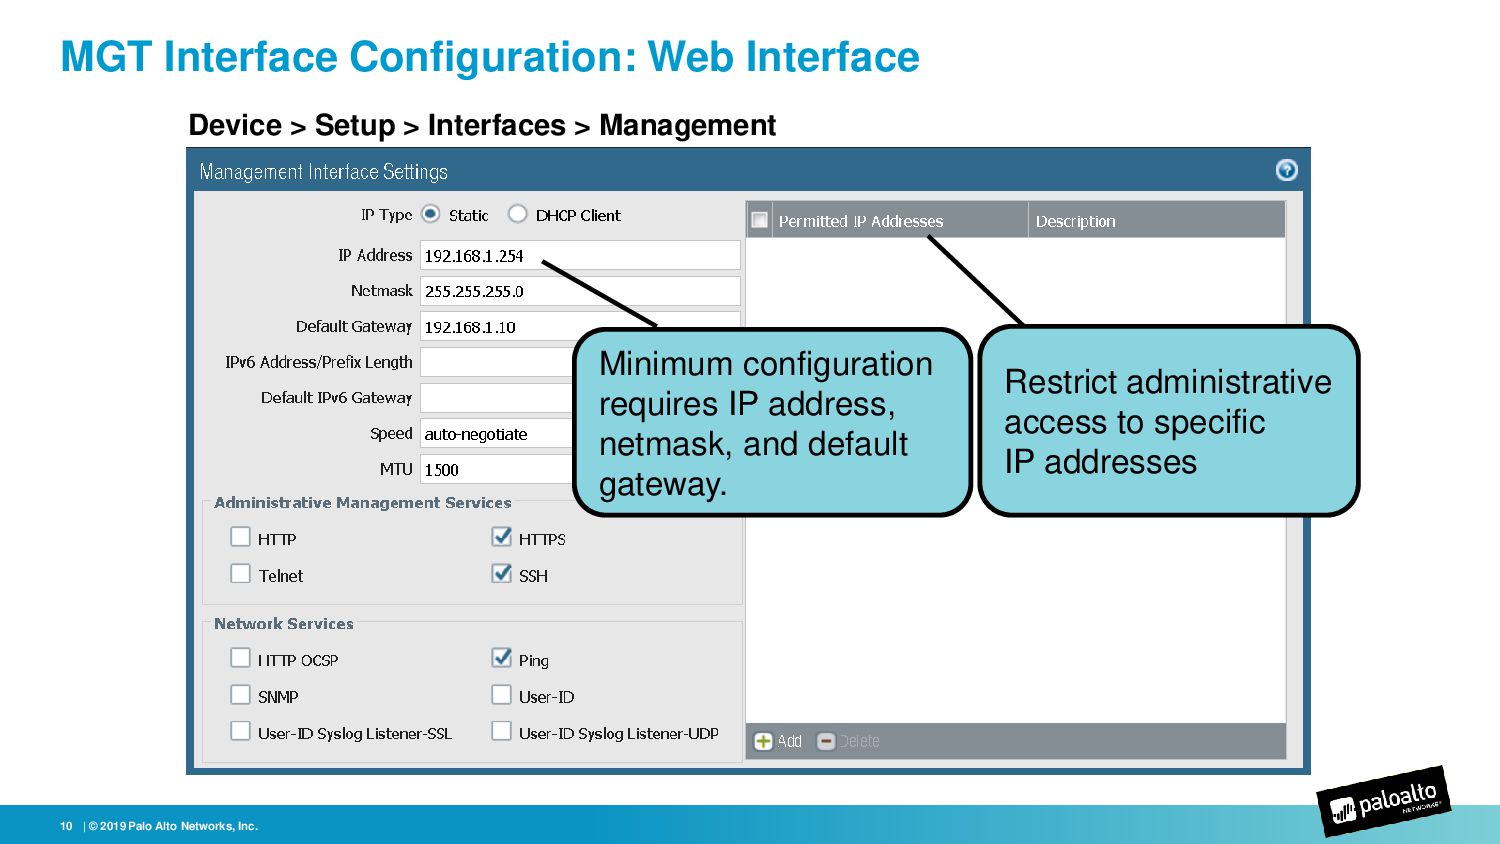
  7. MGT Interface Configuration: Web Interface Device > Setup > Interfaces

    > Management Minimum configuration requires IP address, netmask, and default gateway. Restrict administrative access to specific IP addresses | © 2019 Palo Alto Networks, Inc. 10
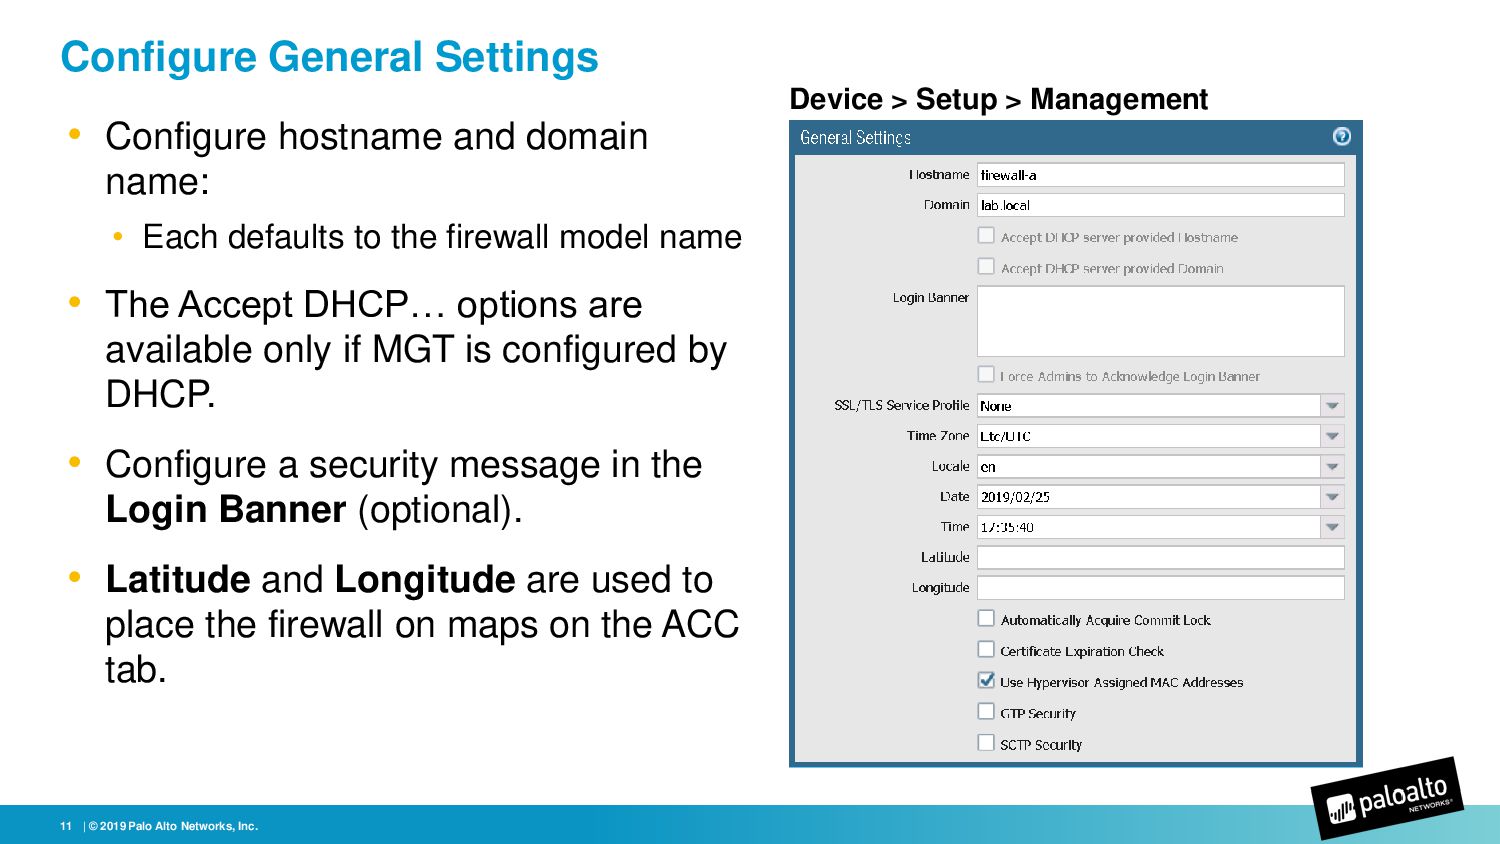
  8. Configure General Settings • Configure hostname and domain name: •

    Each defaults to the firewall model name • The Accept DHCP… options are available only if MGT is configured by DHCP. • Configure a security message in the Login Banner (optional). • Latitude and Longitude are used to place the firewall on maps on the ACC tab. Device > Setup > Management | © 2019 Palo Alto Networks, Inc. 11
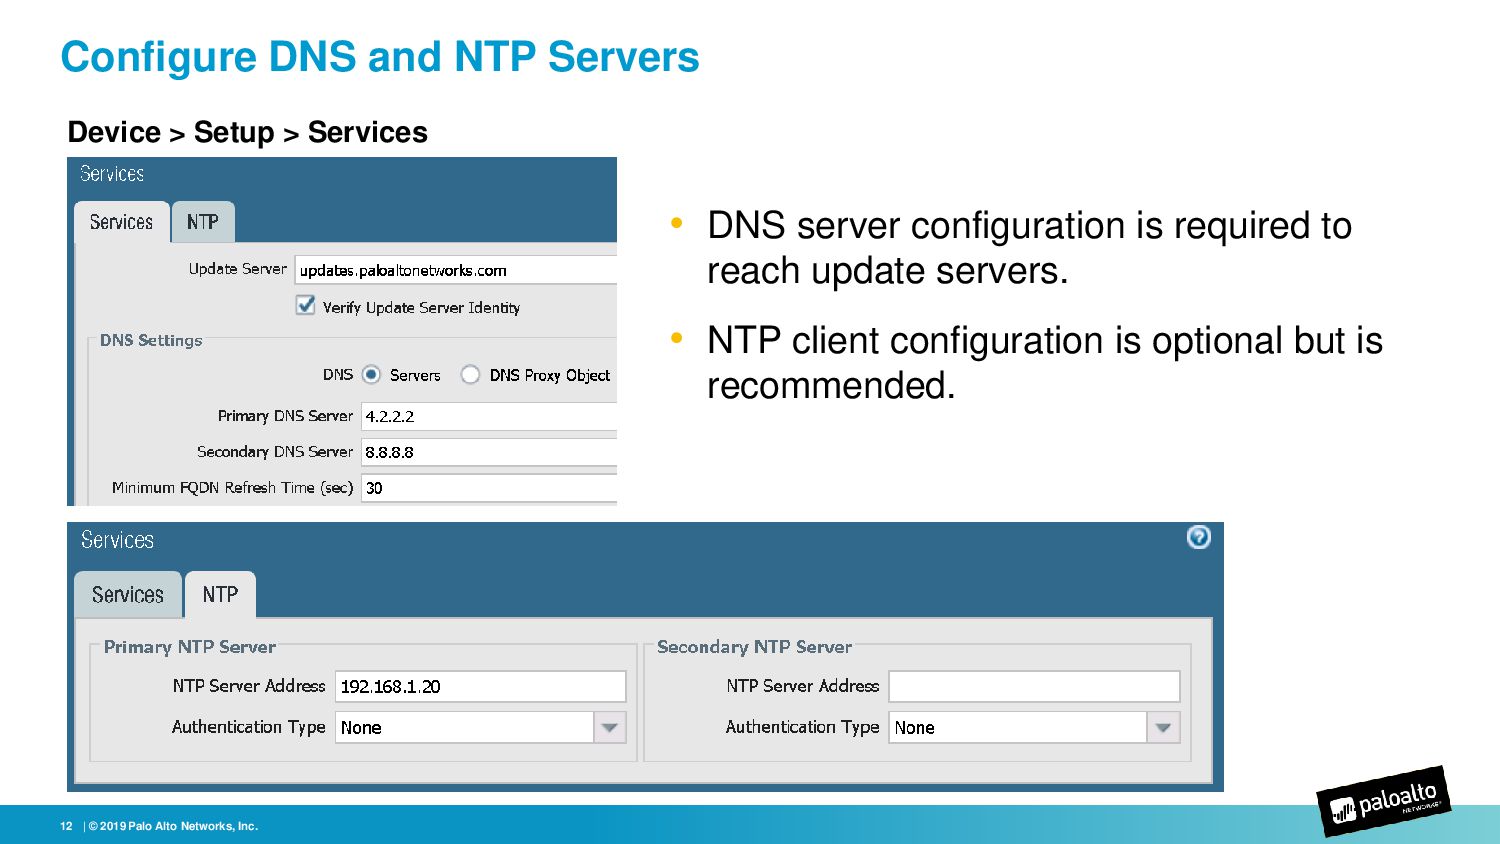
  9. Configure DNS and NTP Servers • DNS server configuration is

    required to reach update servers. • NTP client configuration is optional but is recommended. Device > Setup > Services | © 2019 Palo Alto Networks, Inc. 12
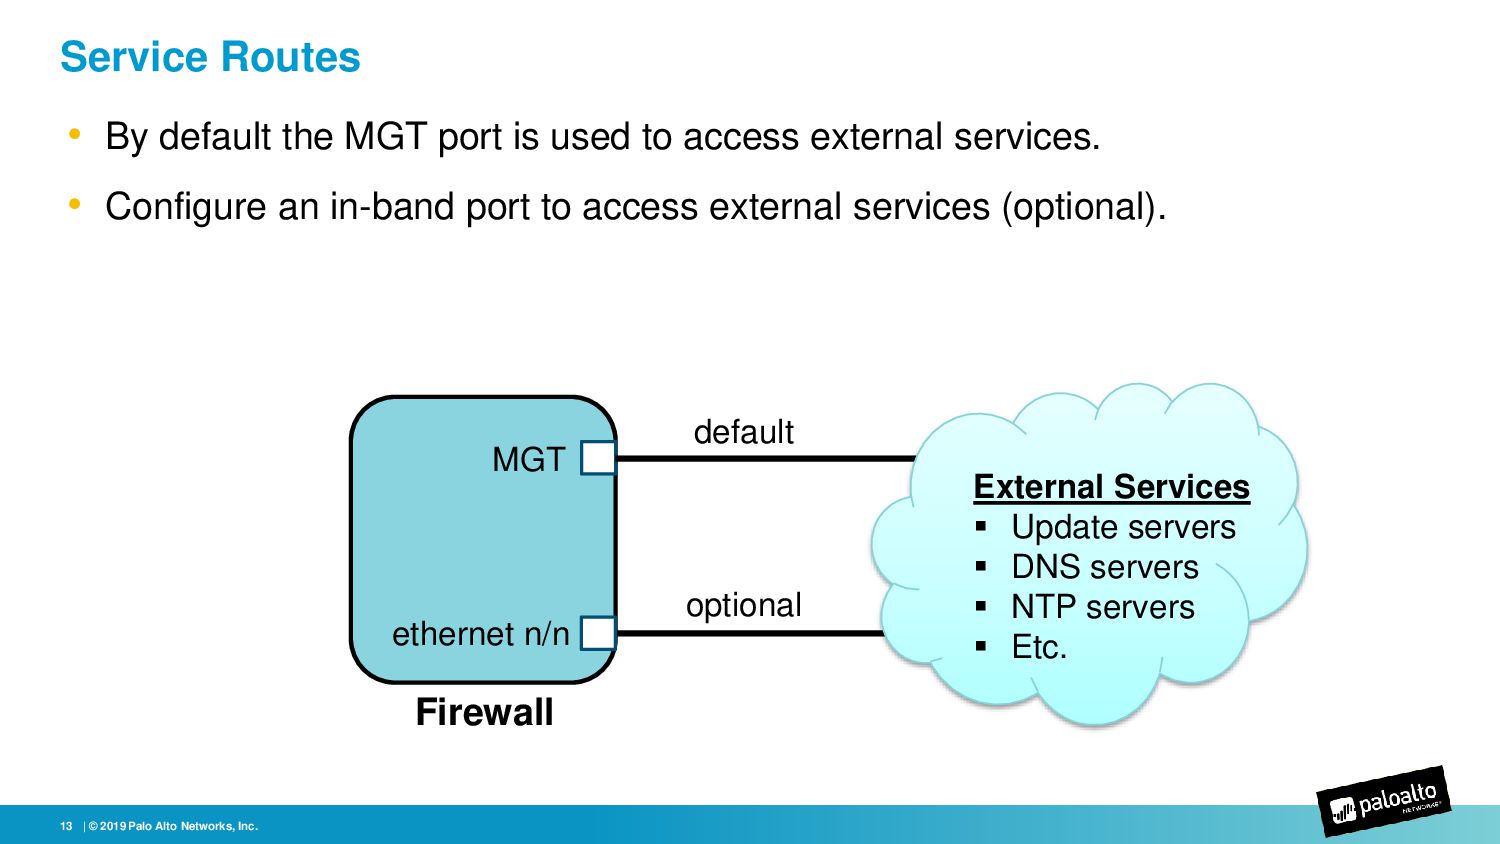
  10. Service Routes • By default the MGT port is used

    to access external services. • Configure an in-band port to access external services (optional). Firewall ethernet n/n MGT External Services  Update servers  DNS servers  NTP servers  Etc. default optional | © 2019 Palo Alto Networks, Inc. 13
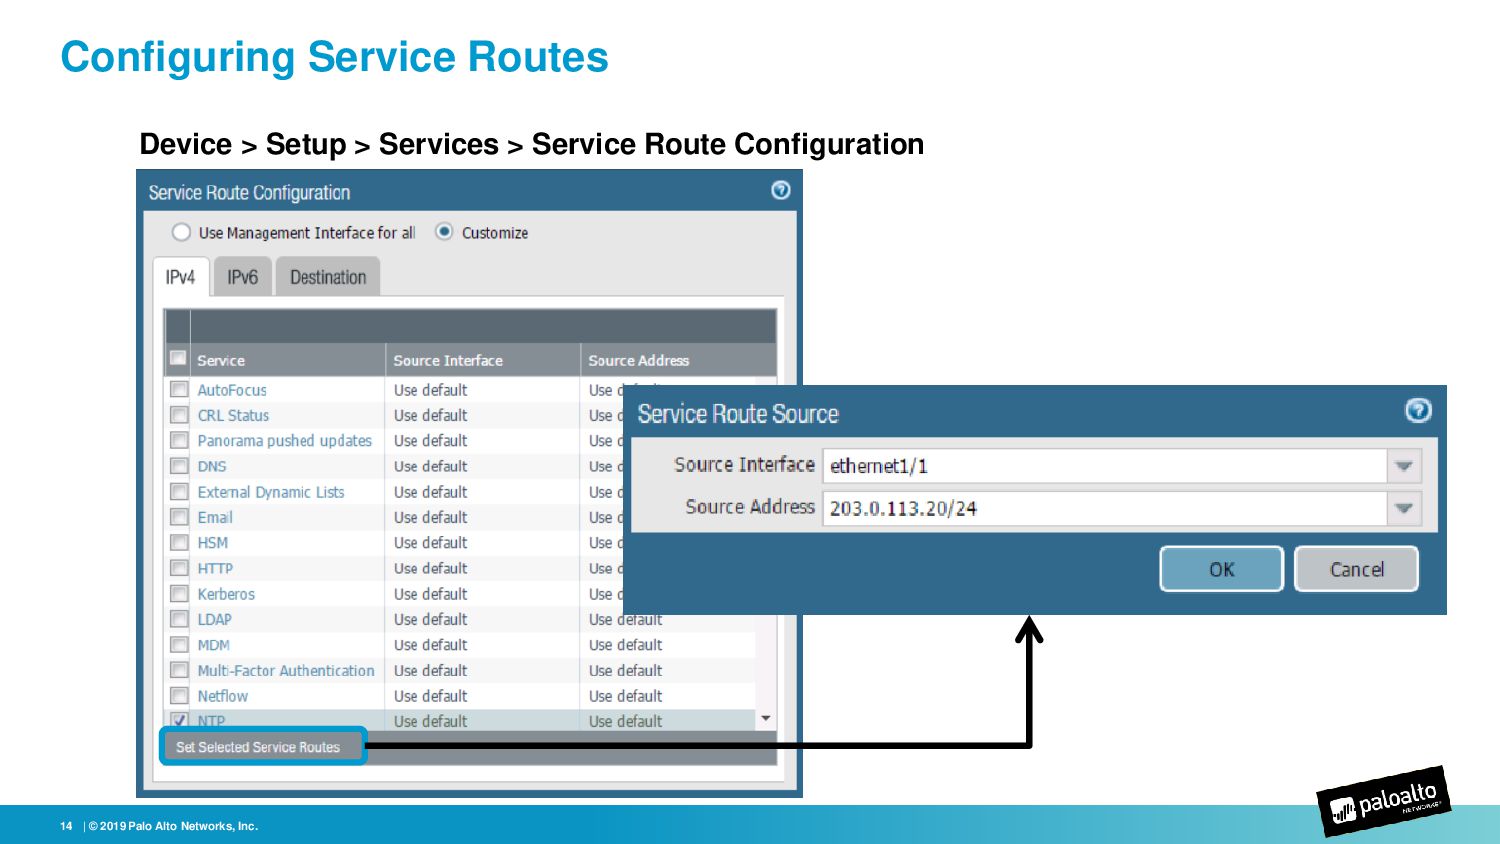
  11. Configuring Service Routes Device > Setup > Services > Service

    Route Configuration | © 2019 Palo Alto Networks, Inc. 14
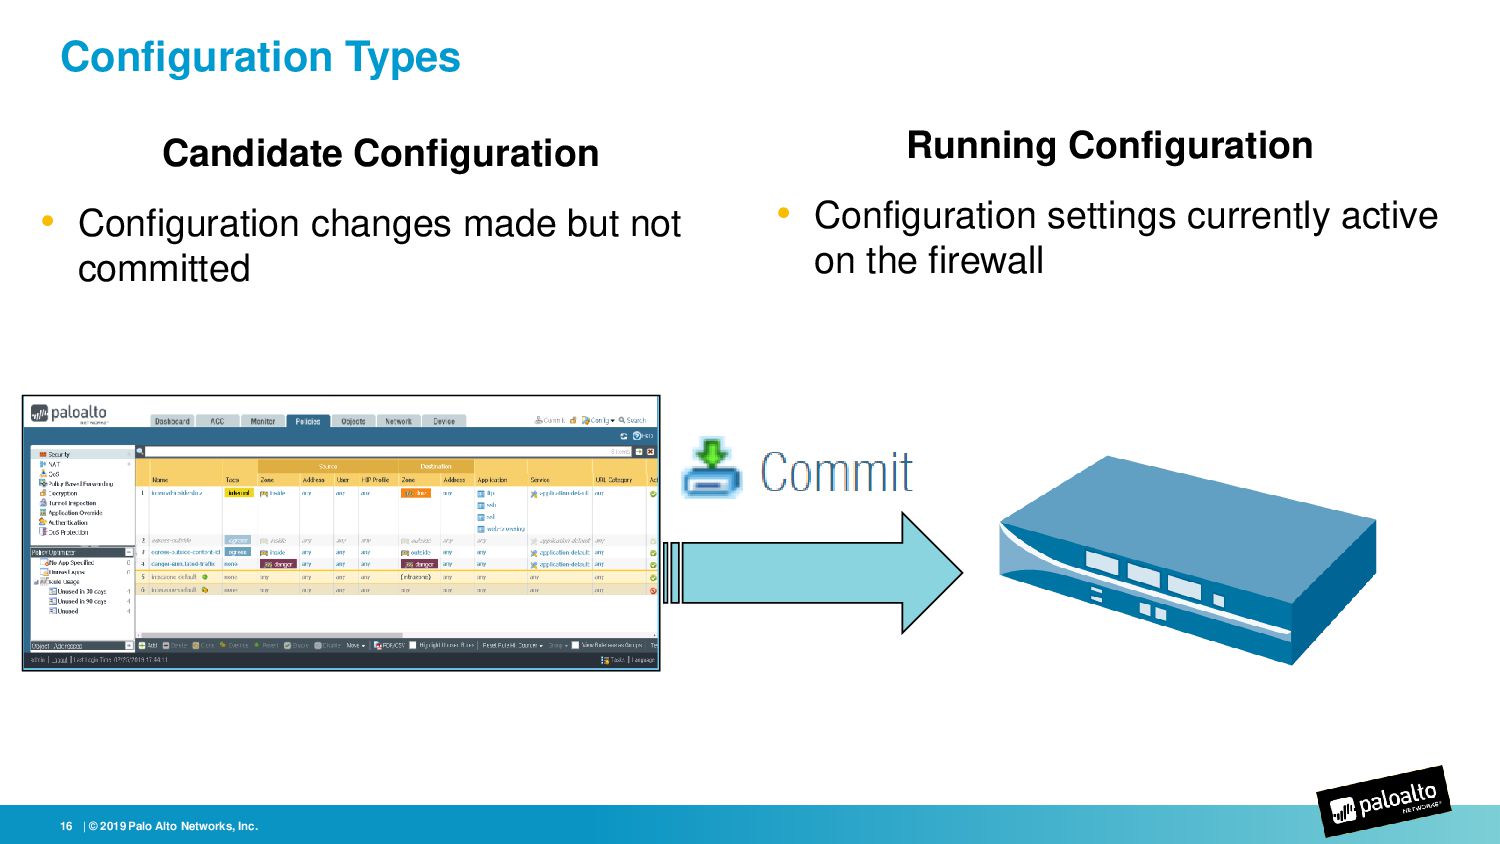
  12. Configuration Types Running Configuration • Configuration settings currently active on

    the firewall Candidate Configuration • Configuration changes made but not committed | © 2019 Palo Alto Networks, Inc. 16
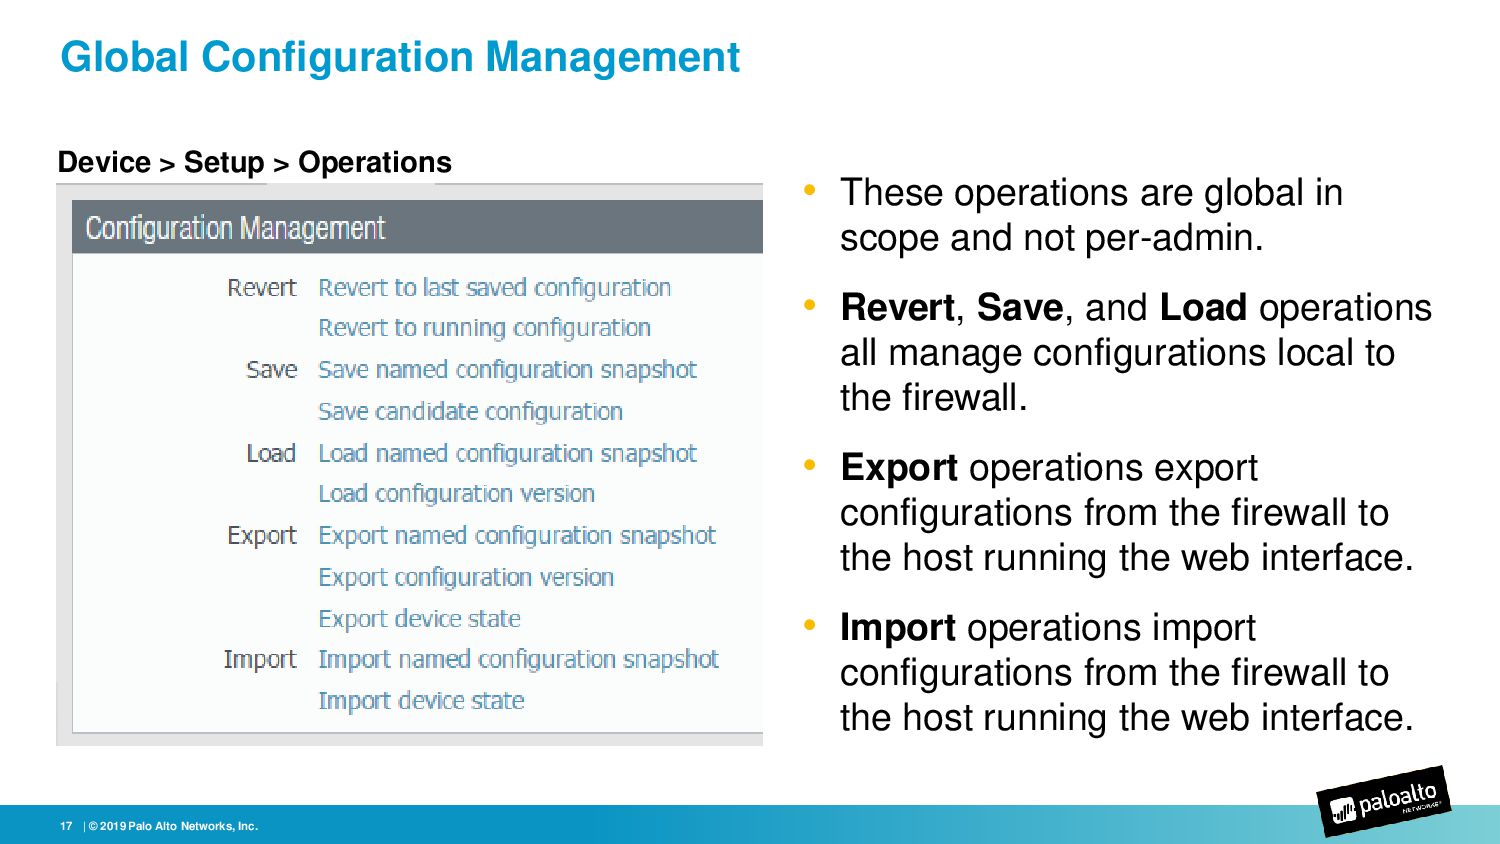
  13. Global Configuration Management • These operations are global in scope

    and not per-admin. • Revert, Save, and Load operations all manage configurations local to the firewall. • Export operations export configurations from the firewall to the host running the web interface. • Import operations import configurations from the firewall to the host running the web interface. Device > Setup > Operations | © 2019 Palo Alto Networks, Inc. 17
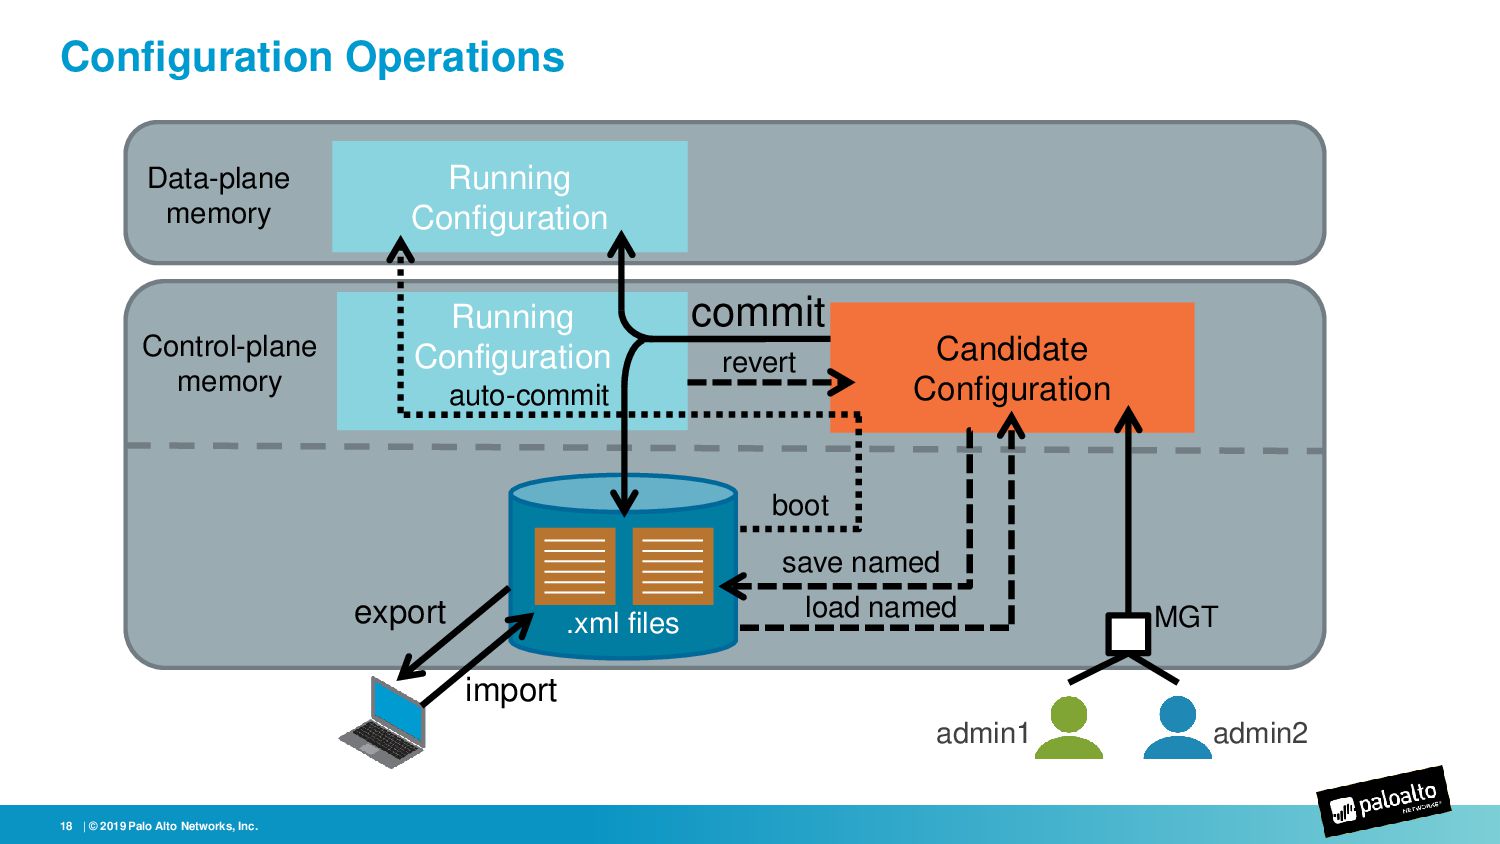
  14. Configuration Operations Candidate Configuration Running Configuration Data-plane memory Control-plane memory

    boot .xml files export import revert auto-commit MGT admin1 admin2 load named save named commit Running Configuration | © 2019 Palo Alto Networks, Inc. 18
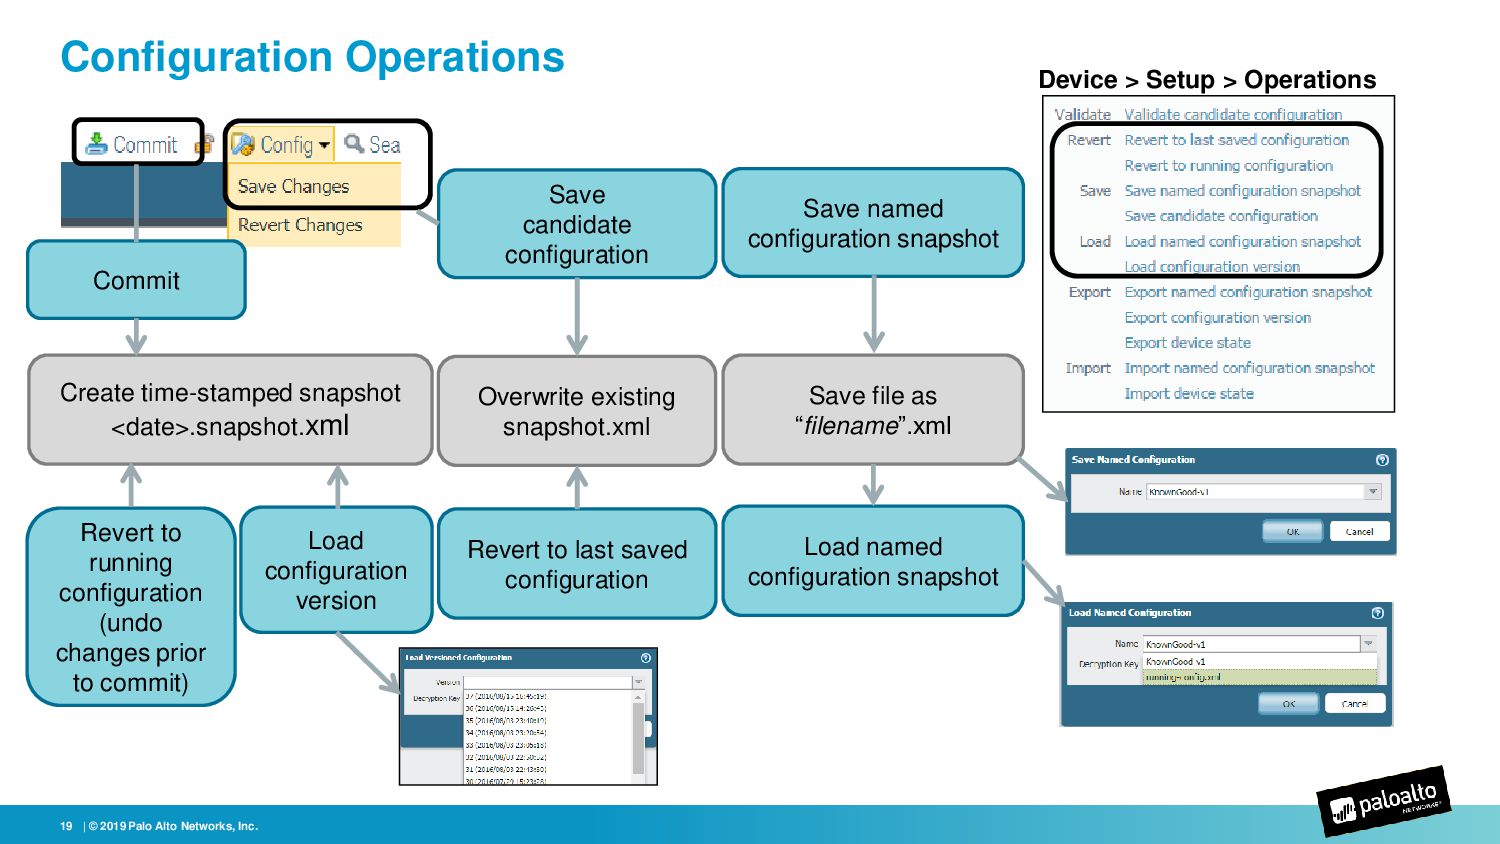
  15. Configuration Operations Commit Create time-stamped snapshot <date>.snapshot.xml Save named configuration

    snapshot Save file as “filename”.xml Revert to last saved configuration Revert to running configuration (undo changes prior to commit) Load configuration version Load named configuration snapshot Save candidate configuration Overwrite existing snapshot.xml Device > Setup > Operations | © 2019 Palo Alto Networks, Inc. 19
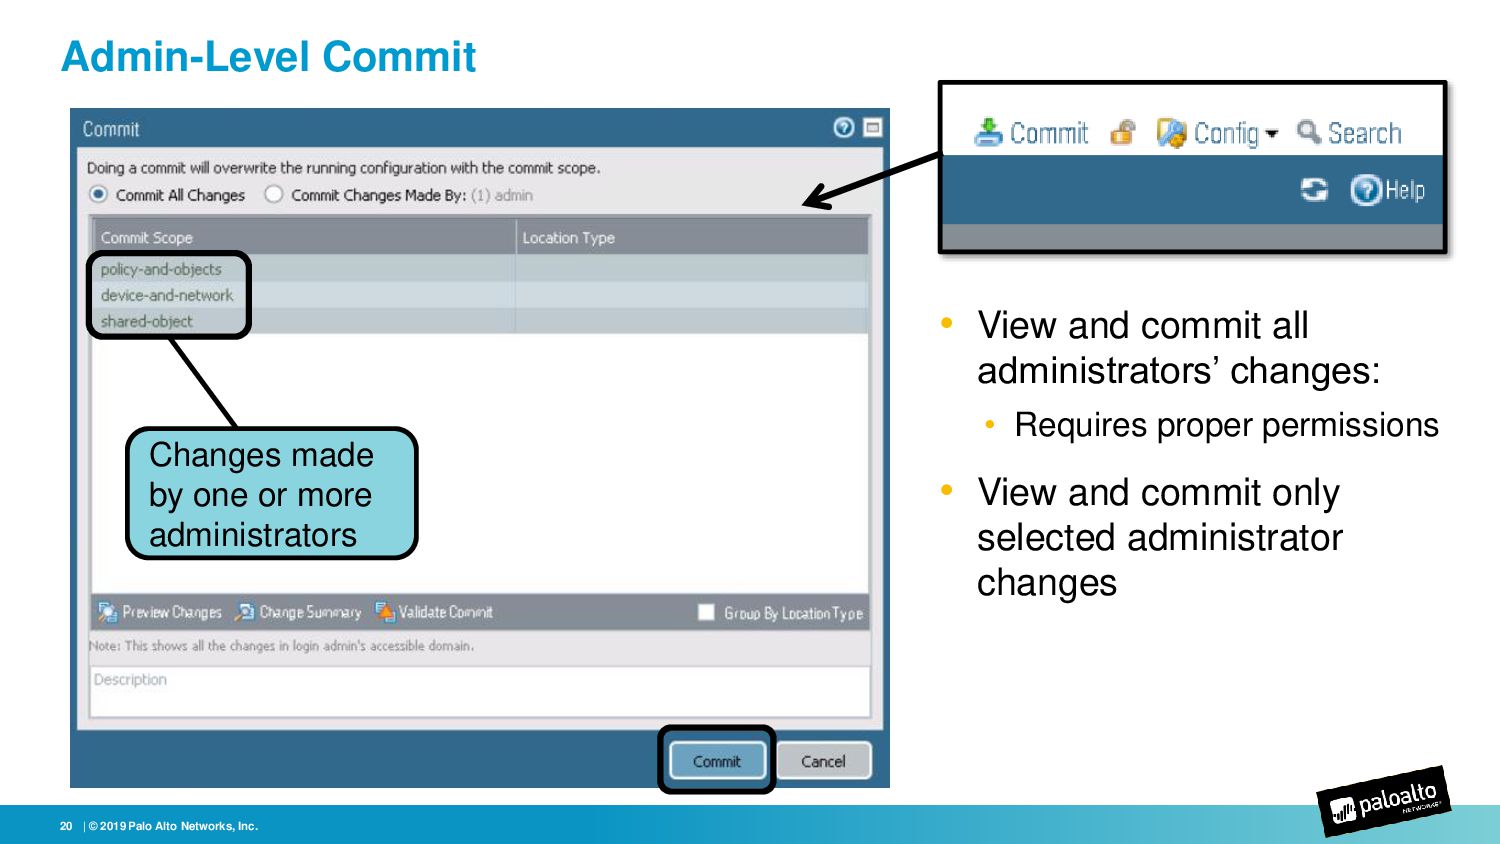
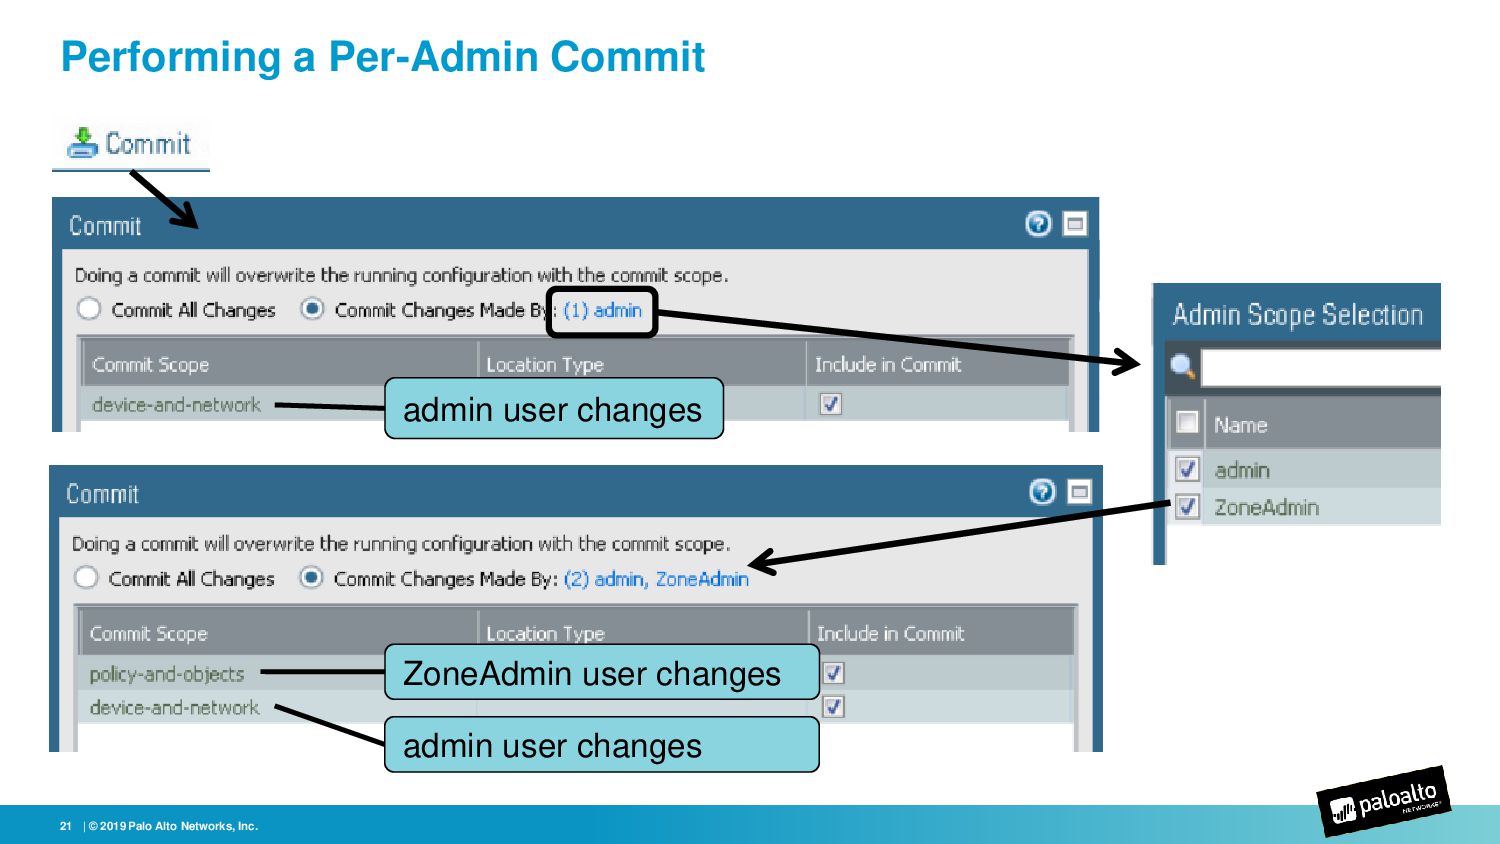
  16. Admin-Level Commit • View and commit all administrators’ changes: •

    Requires proper permissions • View and commit only selected administrator changes Changes made by one or more administrators | © 2019 Palo Alto Networks, Inc. 20
  17. Performing a Per-Admin Commit admin user changes ZoneAdmin user changes

    admin user changes | © 2019 Palo Alto Networks, Inc. 21
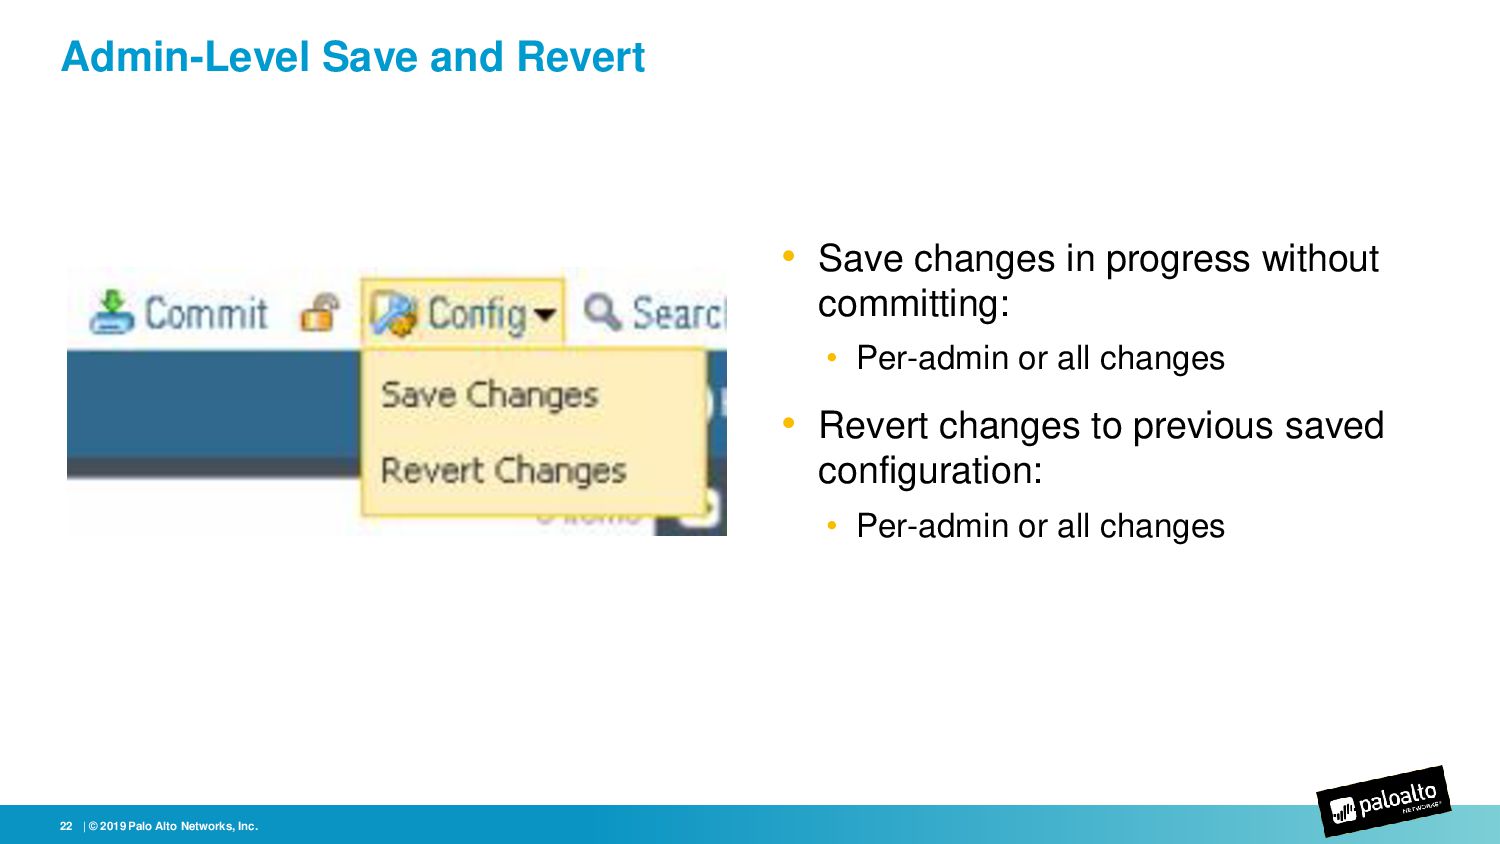
  18. Admin-Level Save and Revert • Save changes in progress without

    committing: • Per-admin or all changes • Revert changes to previous saved configuration: • Per-admin or all changes | © 2019 Palo Alto Networks, Inc. 22
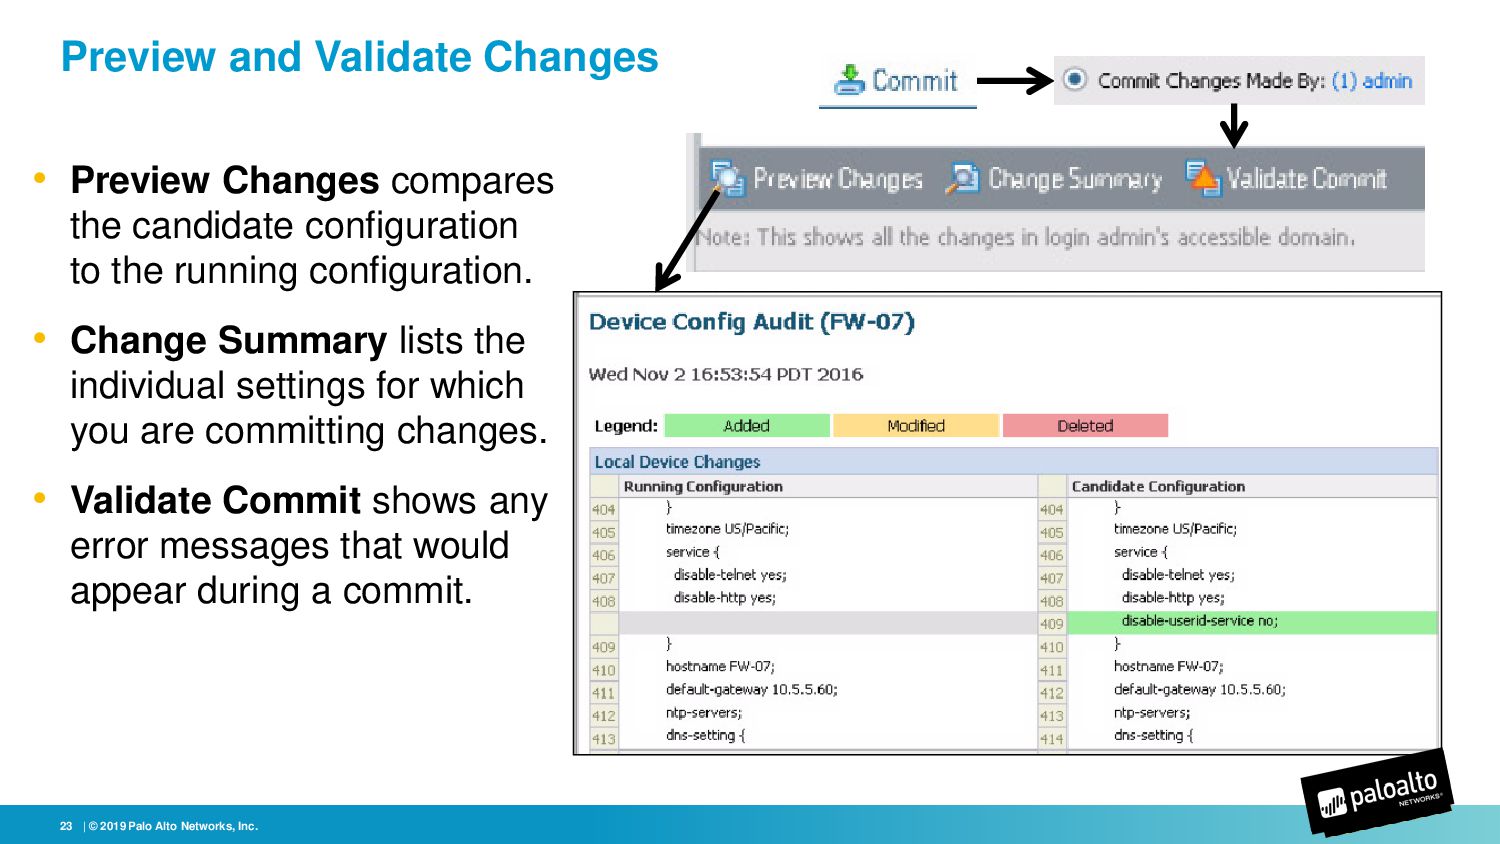
  19. Preview and Validate Changes • Preview Changes compares the candidate

    configuration to the running configuration. • Change Summary lists the individual settings for which you are committing changes. • Validate Commit shows any error messages that would appear during a commit. | © 2019 Palo Alto Networks, Inc. 23
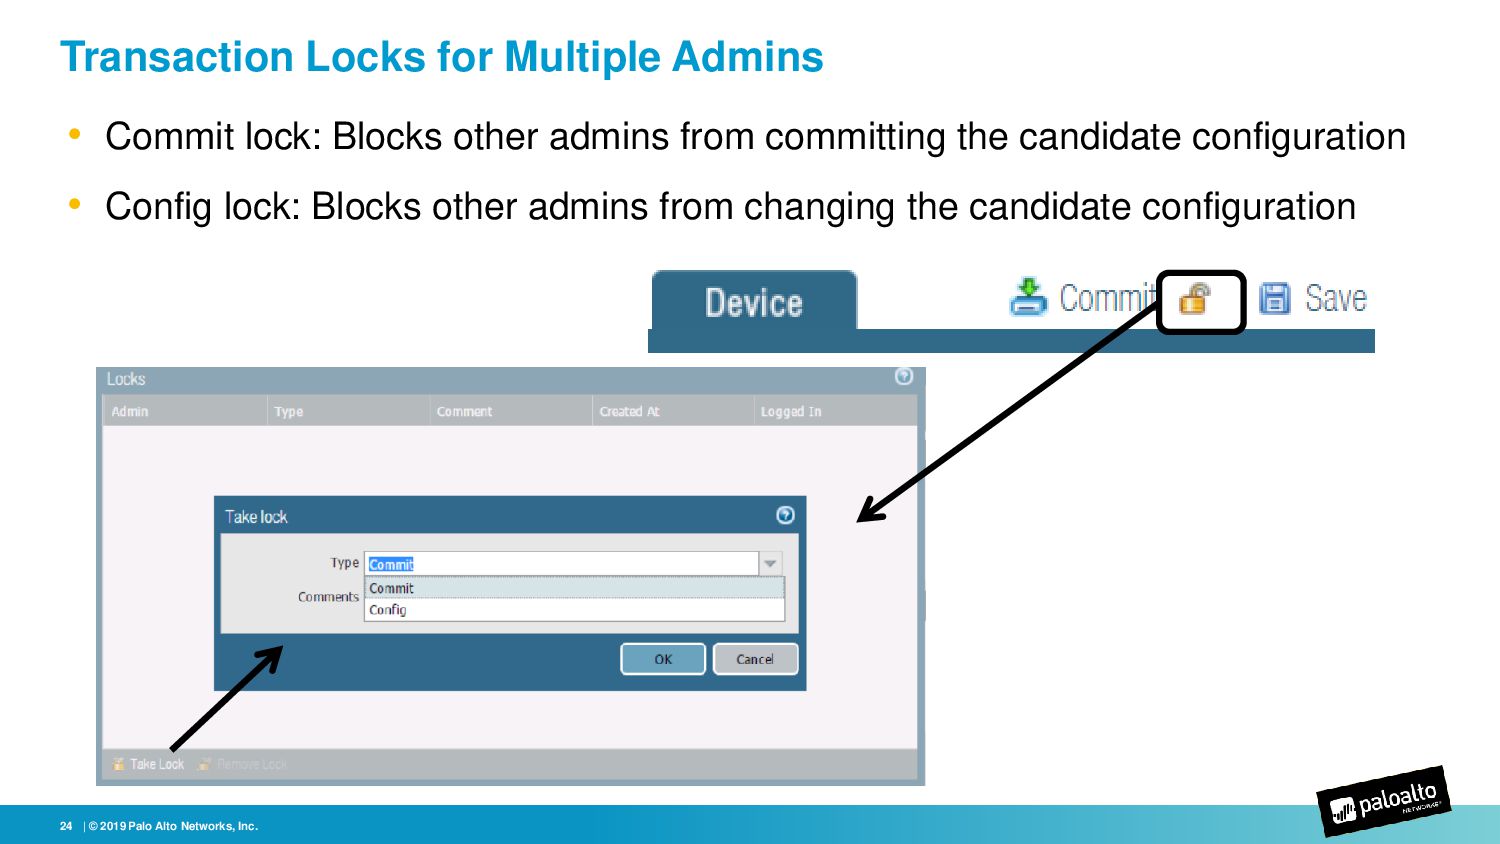
  20. Transaction Locks for Multiple Admins • Commit lock: Blocks other

    admins from committing the candidate configuration • Config lock: Blocks other admins from changing the candidate configuration | © 2019 Palo Alto Networks, Inc. 24
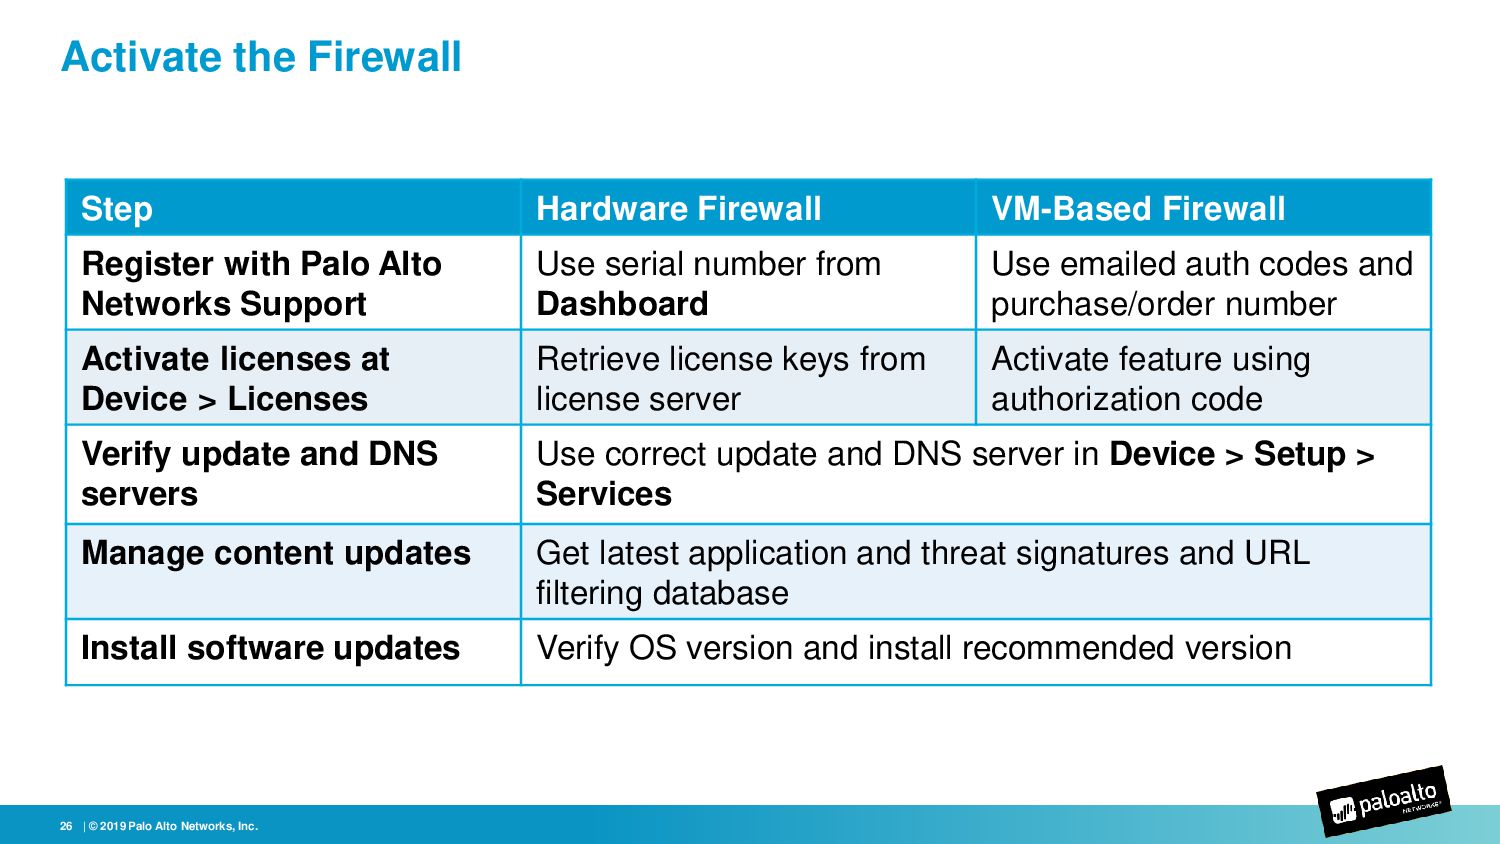
  21. Step Hardware Firewall VM-Based Firewall Register with Palo Alto Networks

    Support Use serial number from Dashboard Use emailed auth codes and purchase/order number Activate licenses at Device > Licenses Retrieve license keys from license server Activate feature using authorization code Verify update and DNS servers Use correct update and DNS server in Device > Setup > Services Manage content updates Get latest application and threat signatures and URL filtering database Install software updates Verify OS version and install recommended version Activate the Firewall | © 2019 Palo Alto Networks, Inc. 26
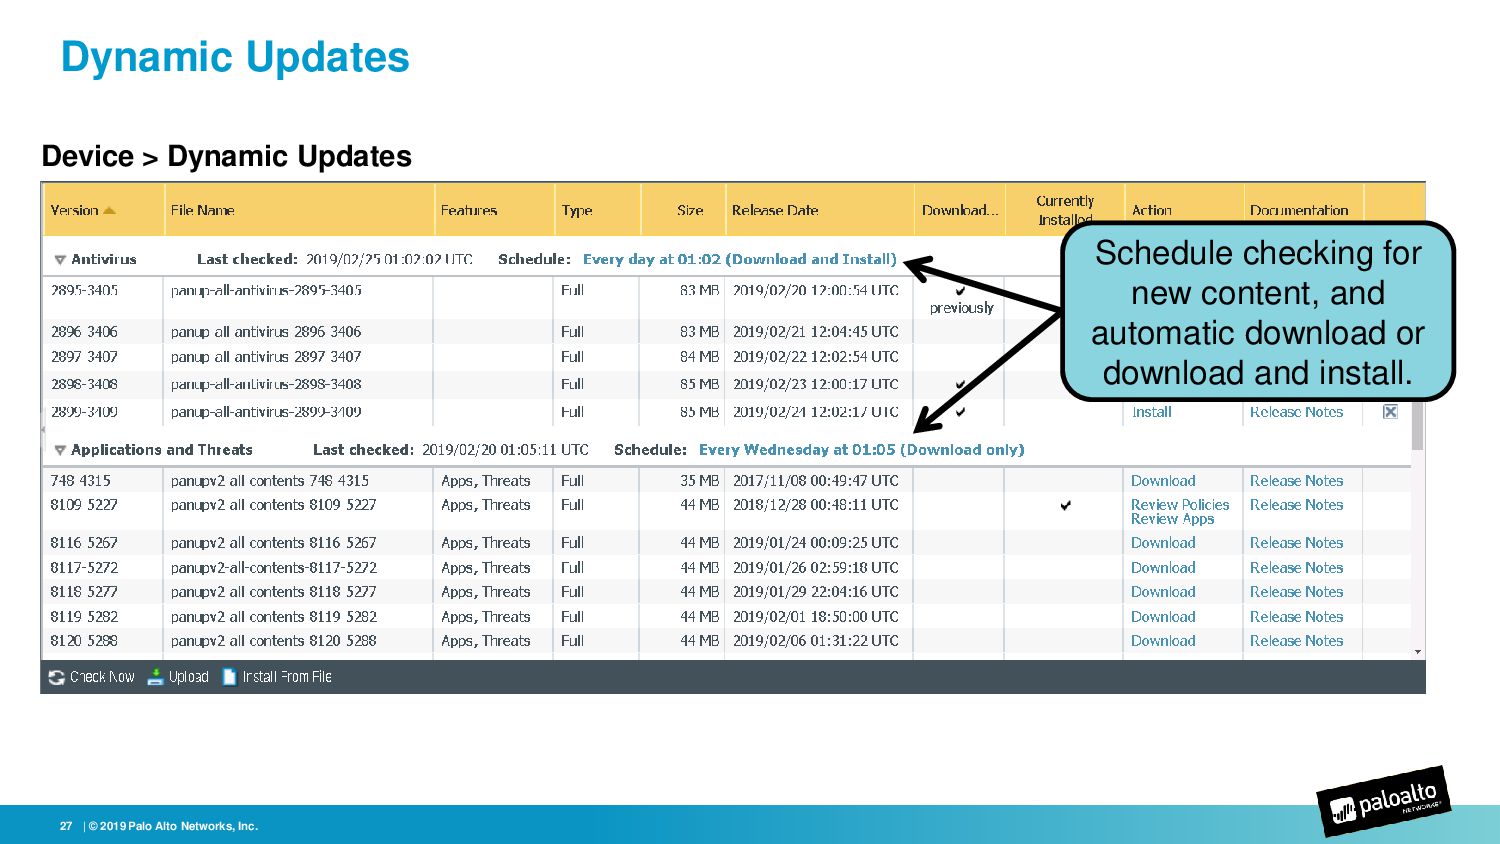
  22. Device > Dynamic Updates Dynamic Updates | © 2019 Palo

    Alto Networks, Inc. 27 Schedule checking for new content, and automatic download or download and install.
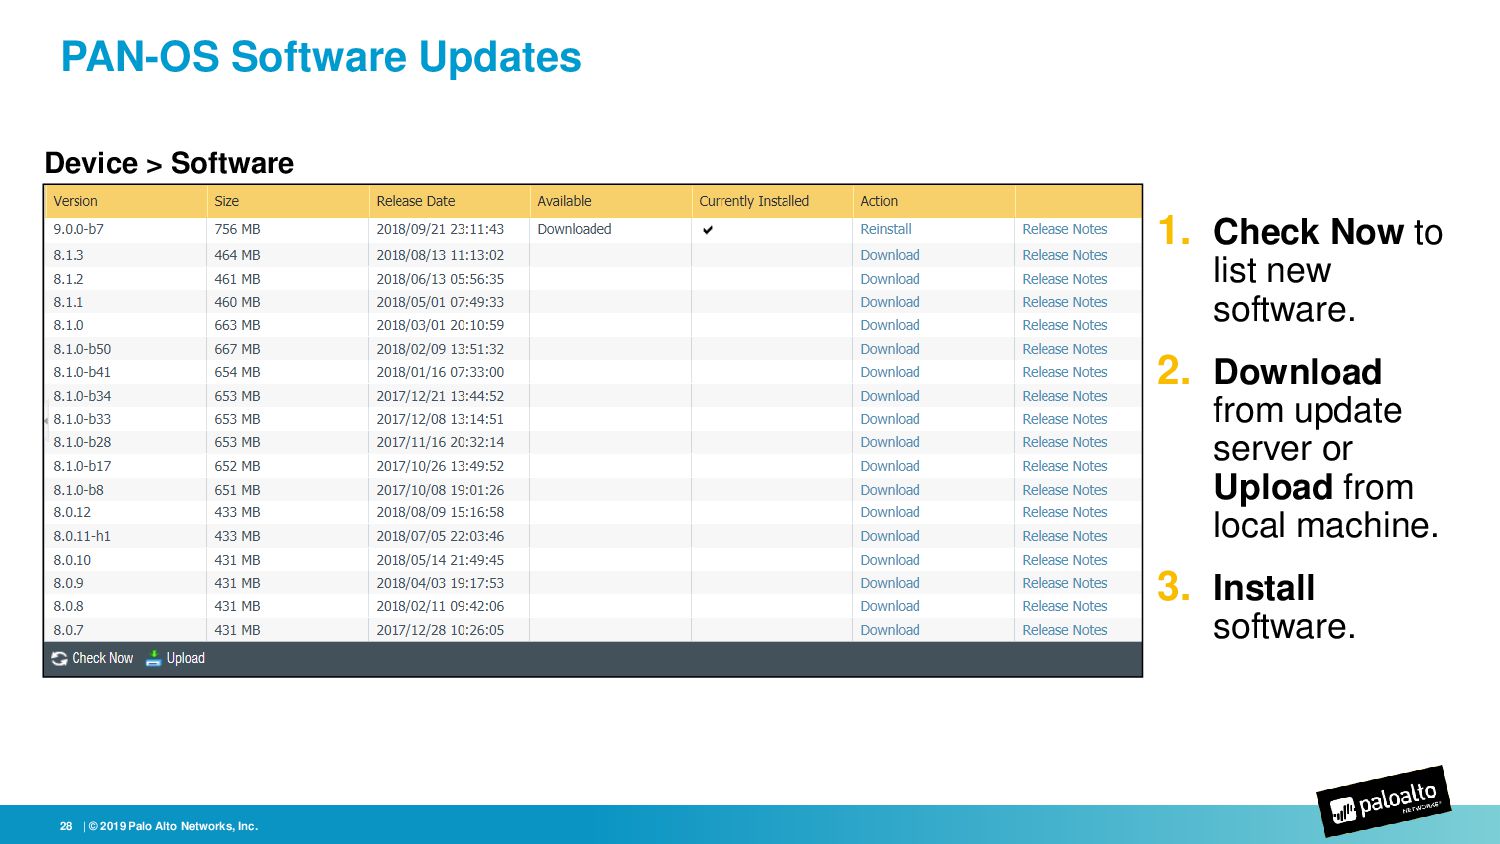
  23. PAN-OS Software Updates 1. Check Now to list new software.

    2. Download from update server or Upload from local machine. 3. Install software. Device > Software | © 2019 Palo Alto Networks, Inc. 28
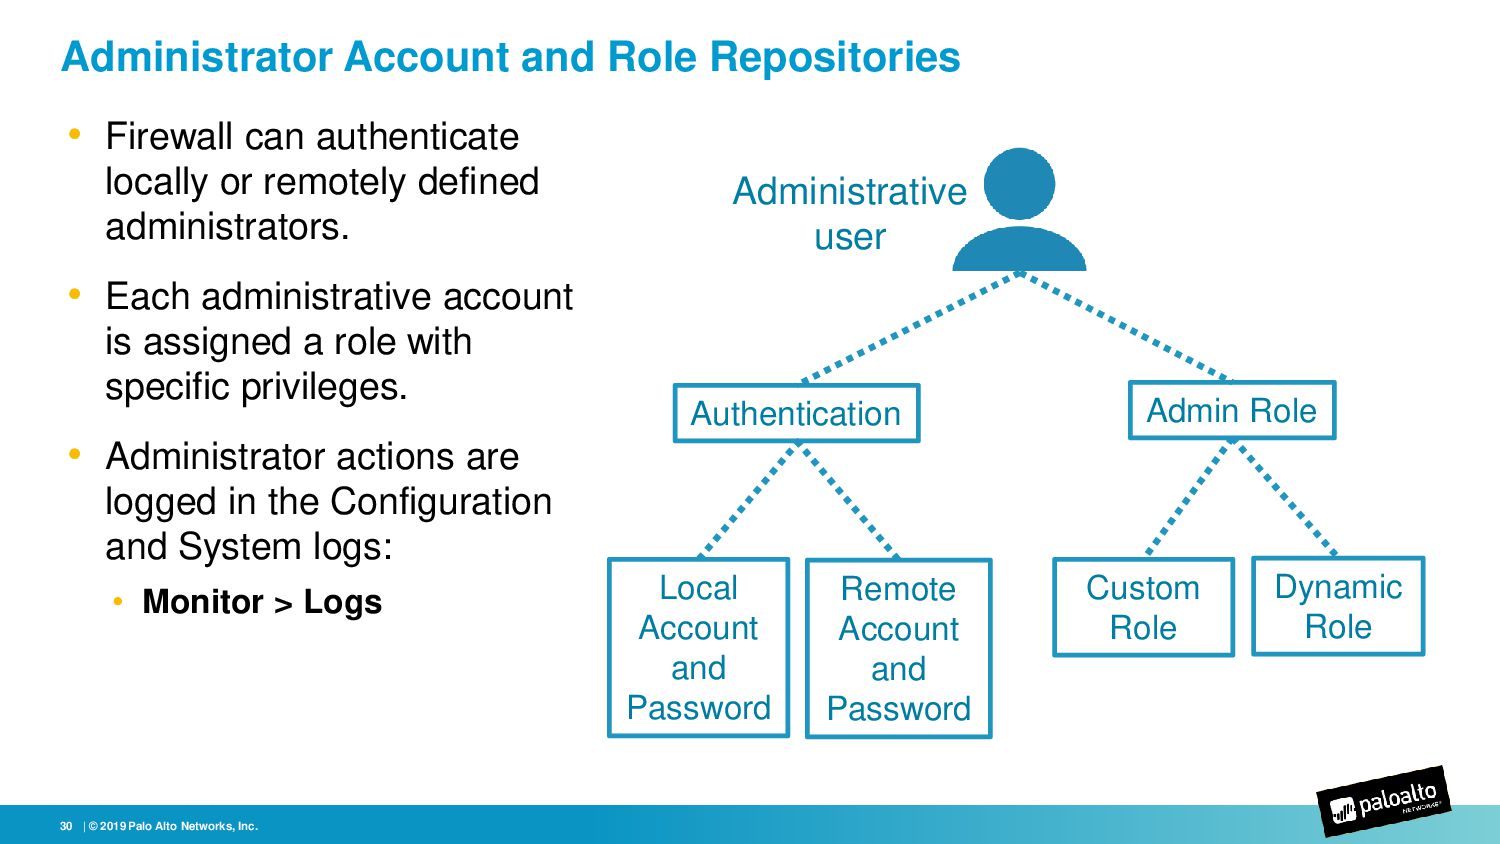
  24. Administrator Account and Role Repositories • Firewall can authenticate locally

    or remotely defined administrators. • Each administrative account is assigned a role with specific privileges. • Administrator actions are logged in the Configuration and System logs: • Monitor > Logs Administrative user Authentication Custom Role Remote Account and Password Admin Role Local Account and Password Dynamic Role | © 2019 Palo Alto Networks, Inc. 30
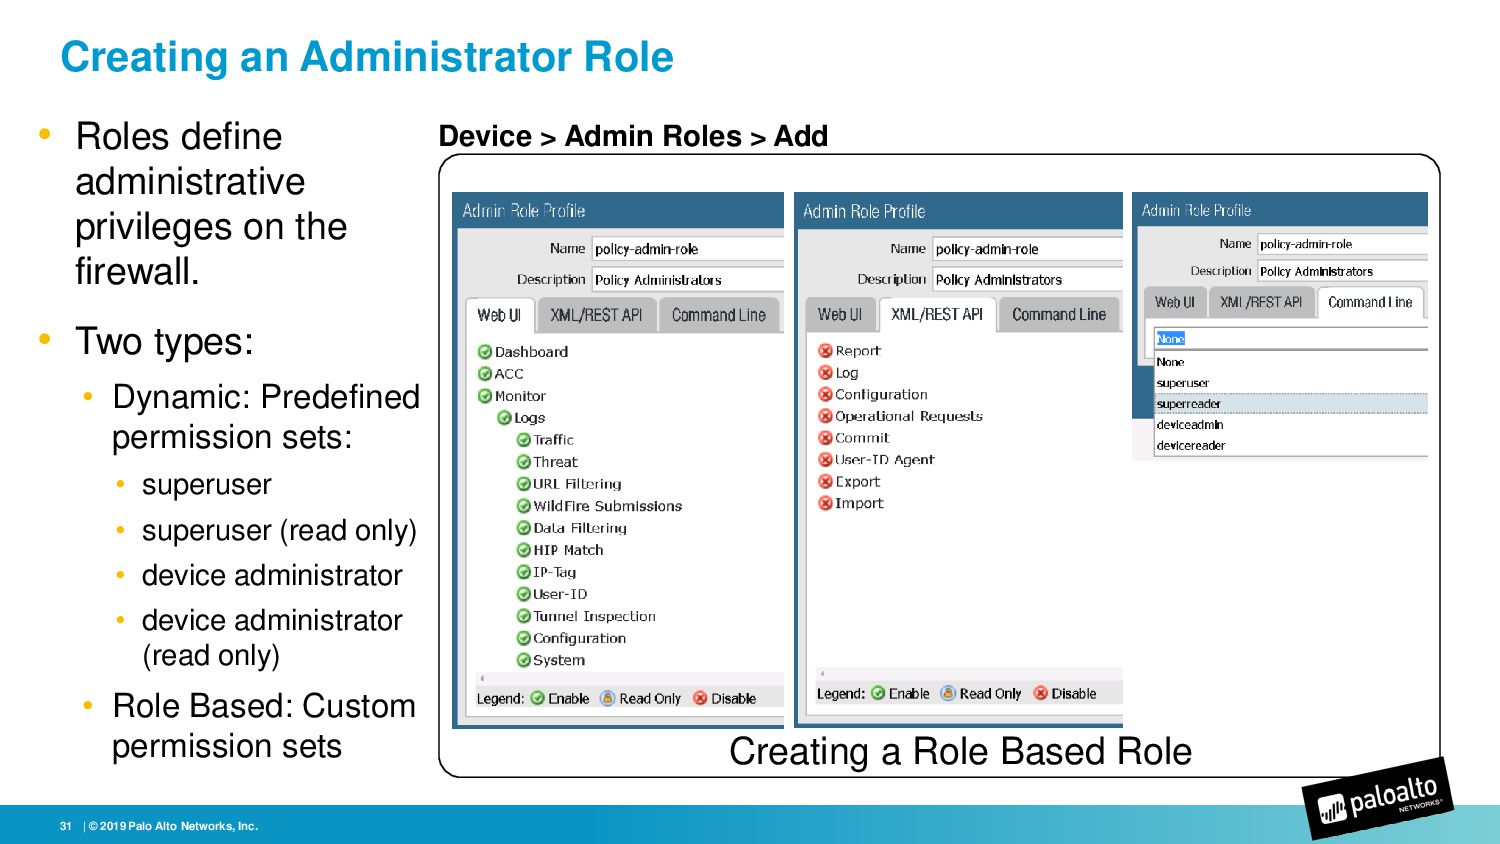
  25. Creating an Administrator Role • Roles define administrative privileges on

    the firewall. • Two types: • Dynamic: Predefined permission sets: • superuser • superuser (read only) • device administrator • device administrator (read only) • Role Based: Custom permission sets Device > Admin Roles > Add Creating a Role Based Role | © 2019 Palo Alto Networks, Inc. 31
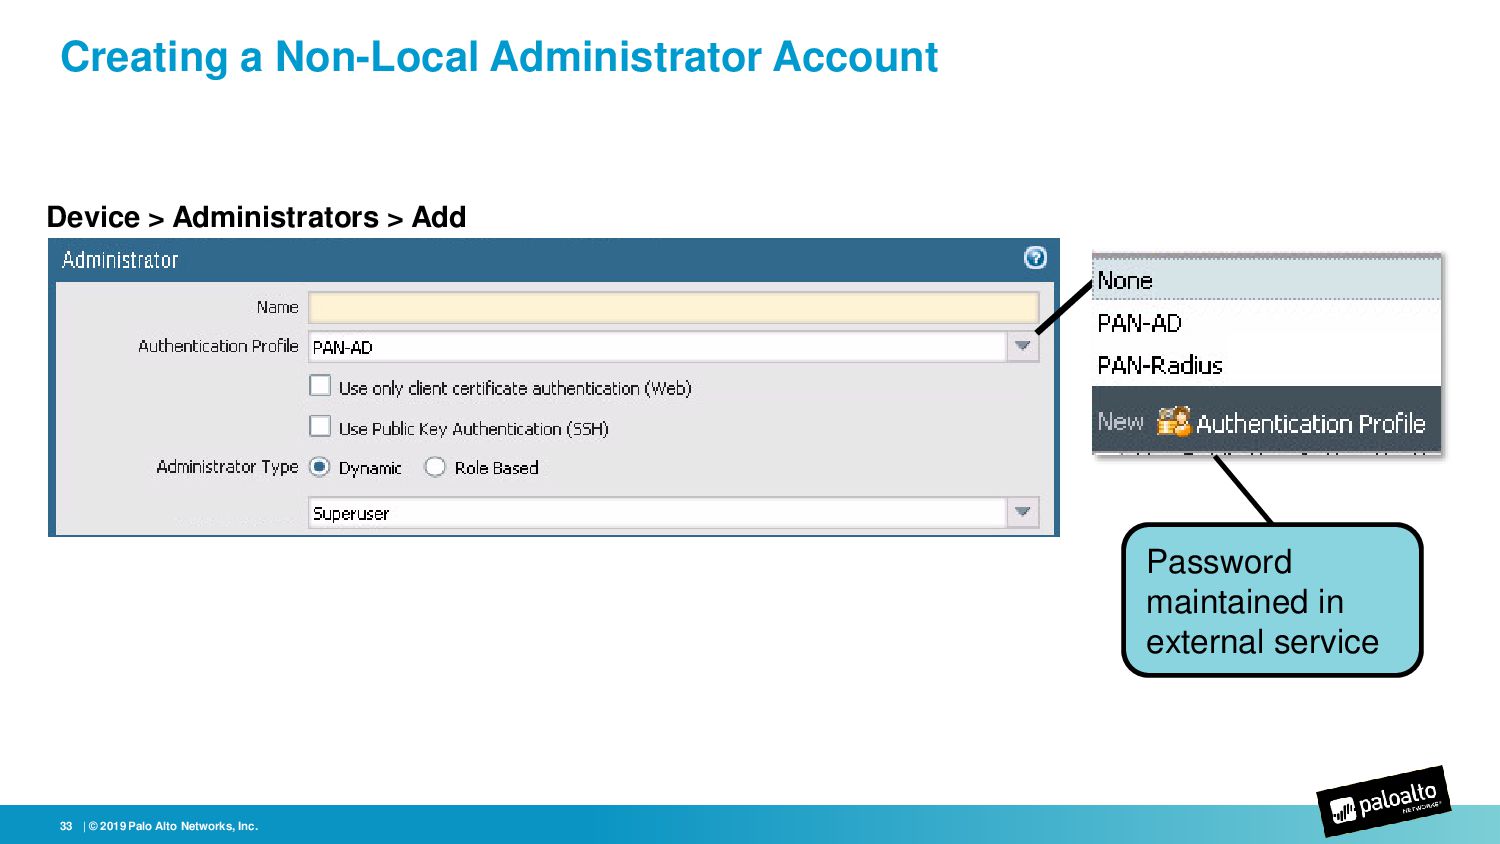
  26. Creating a Non-Local Administrator Account Device > Administrators > Add

    Password maintained in external service | © 2019 Palo Alto Networks, Inc. 33
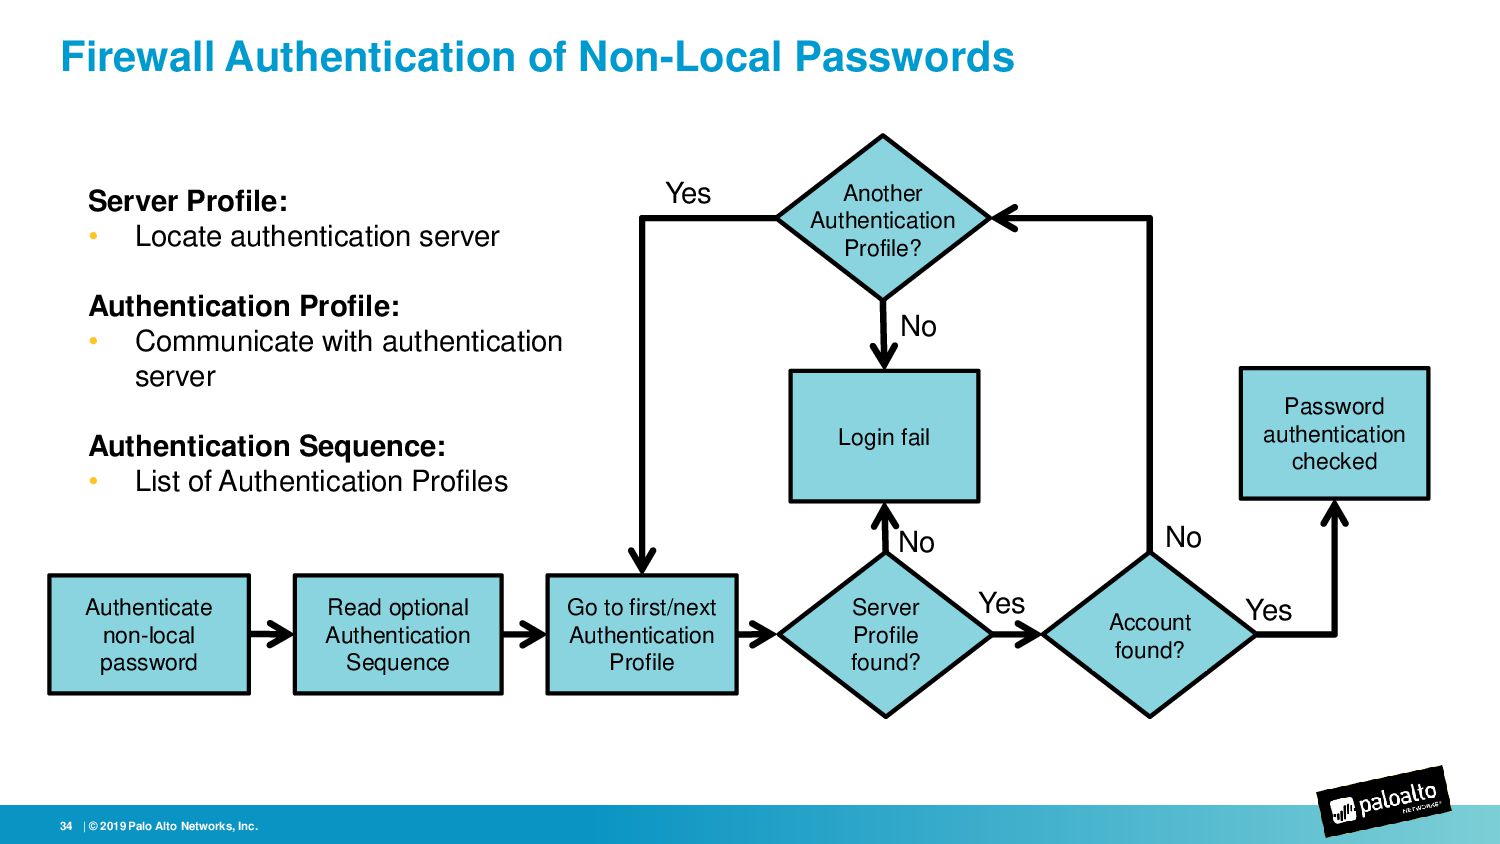
  27. Firewall Authentication of Non-Local Passwords Authenticate non-local password Server Profile

    found? Account found? Password authentication checked Login fail Yes No No Yes Server Profile: • Locate authentication server Authentication Profile: • Communicate with authentication server Authentication Sequence: • List of Authentication Profiles Go to first/next Authentication Profile Read optional Authentication Sequence Yes No Another Authentication Profile? | © 2019 Palo Alto Networks, Inc. 34
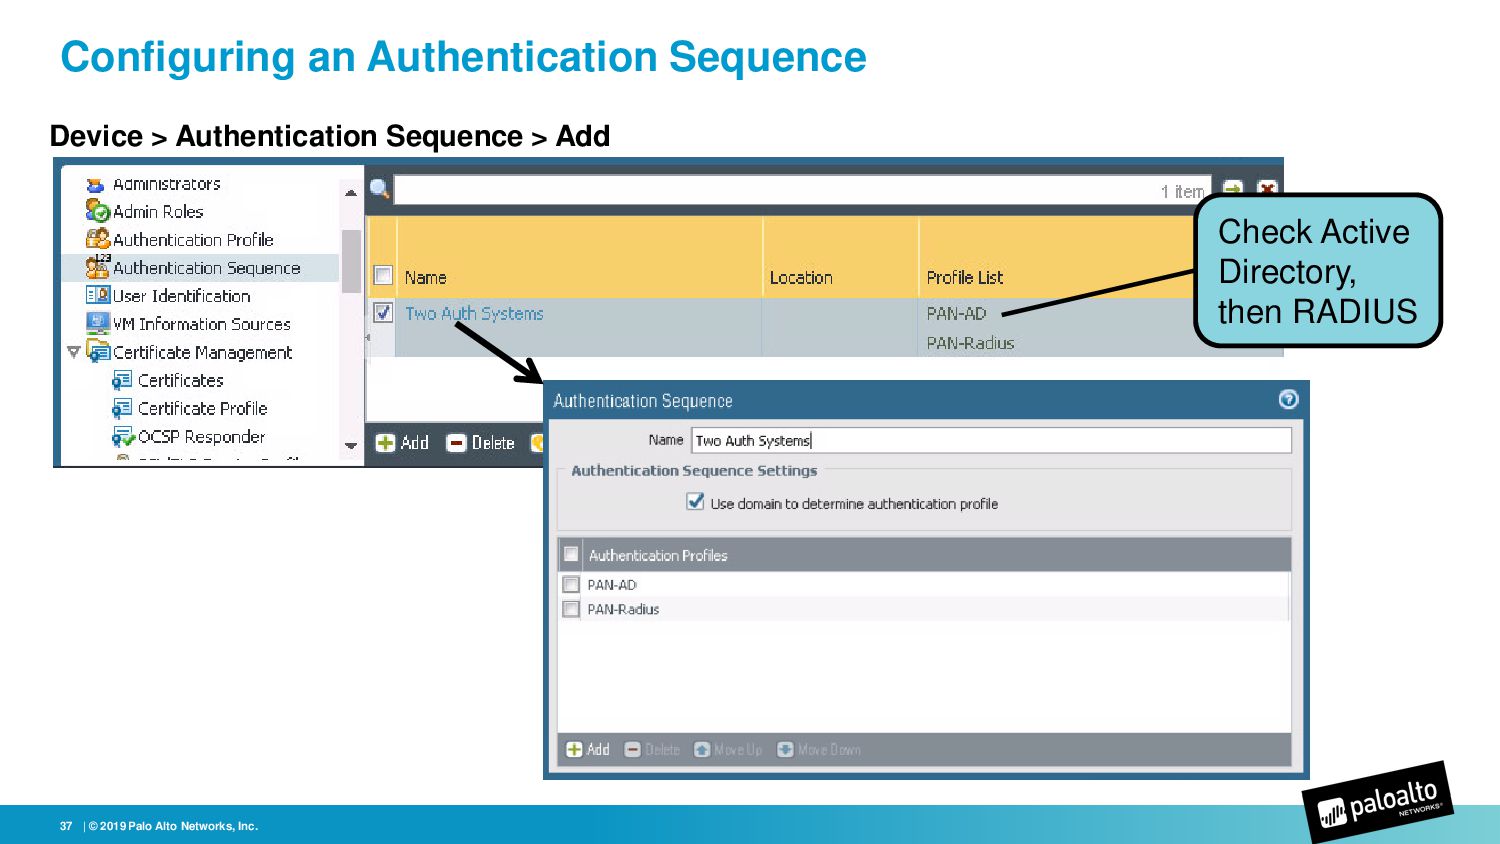
  28. Configuring an Authentication Sequence Device > Authentication Sequence > Add

    Check Active Directory, then RADIUS | © 2019 Palo Alto Networks, Inc. 37
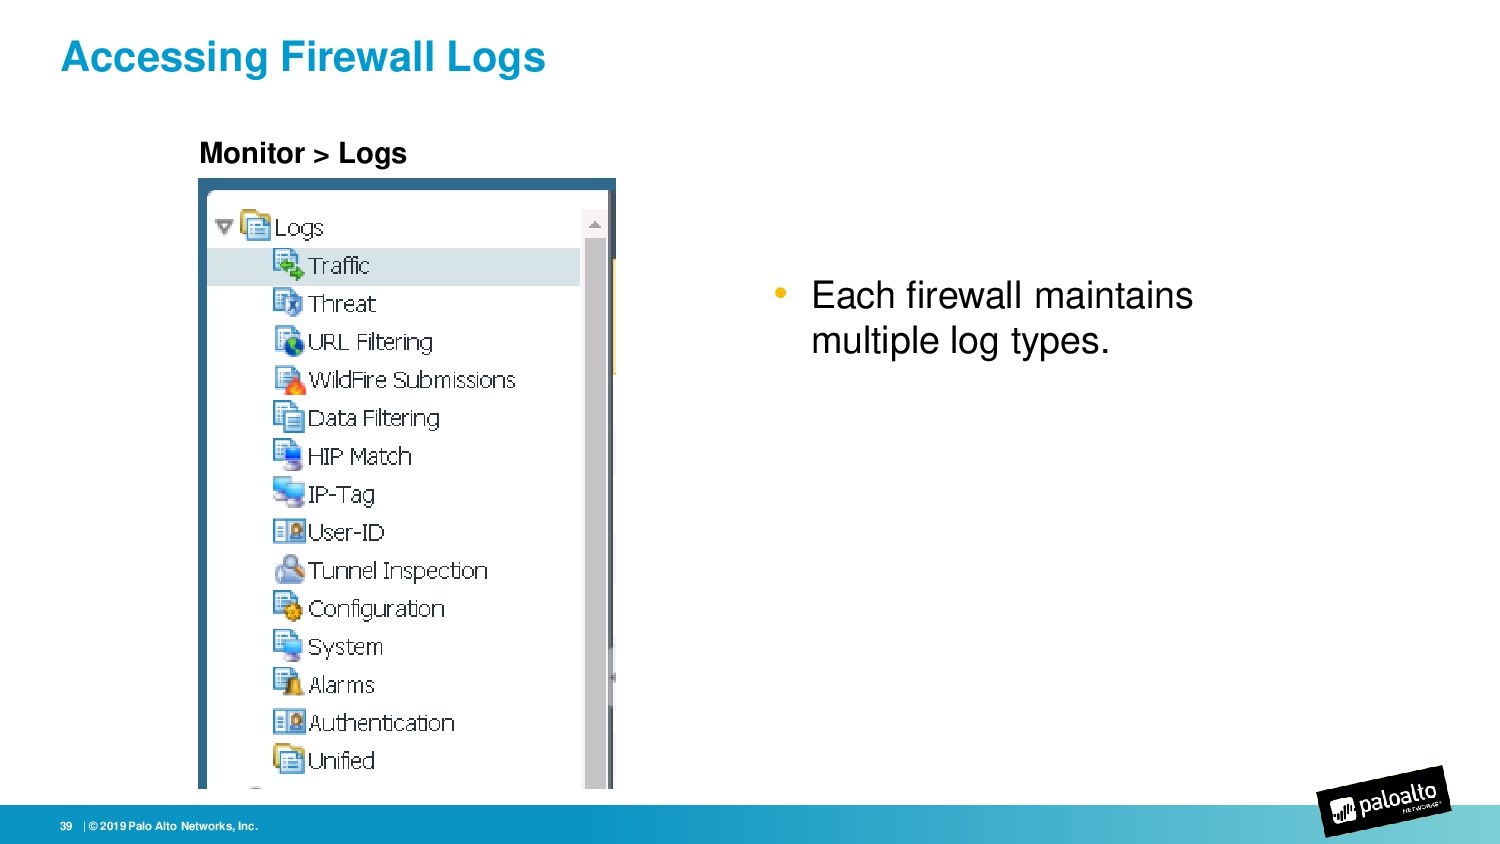
  29. Accessing Firewall Logs • Each firewall maintains multiple log types.

    Monitor > Logs | © 2019 Palo Alto Networks, Inc. 39
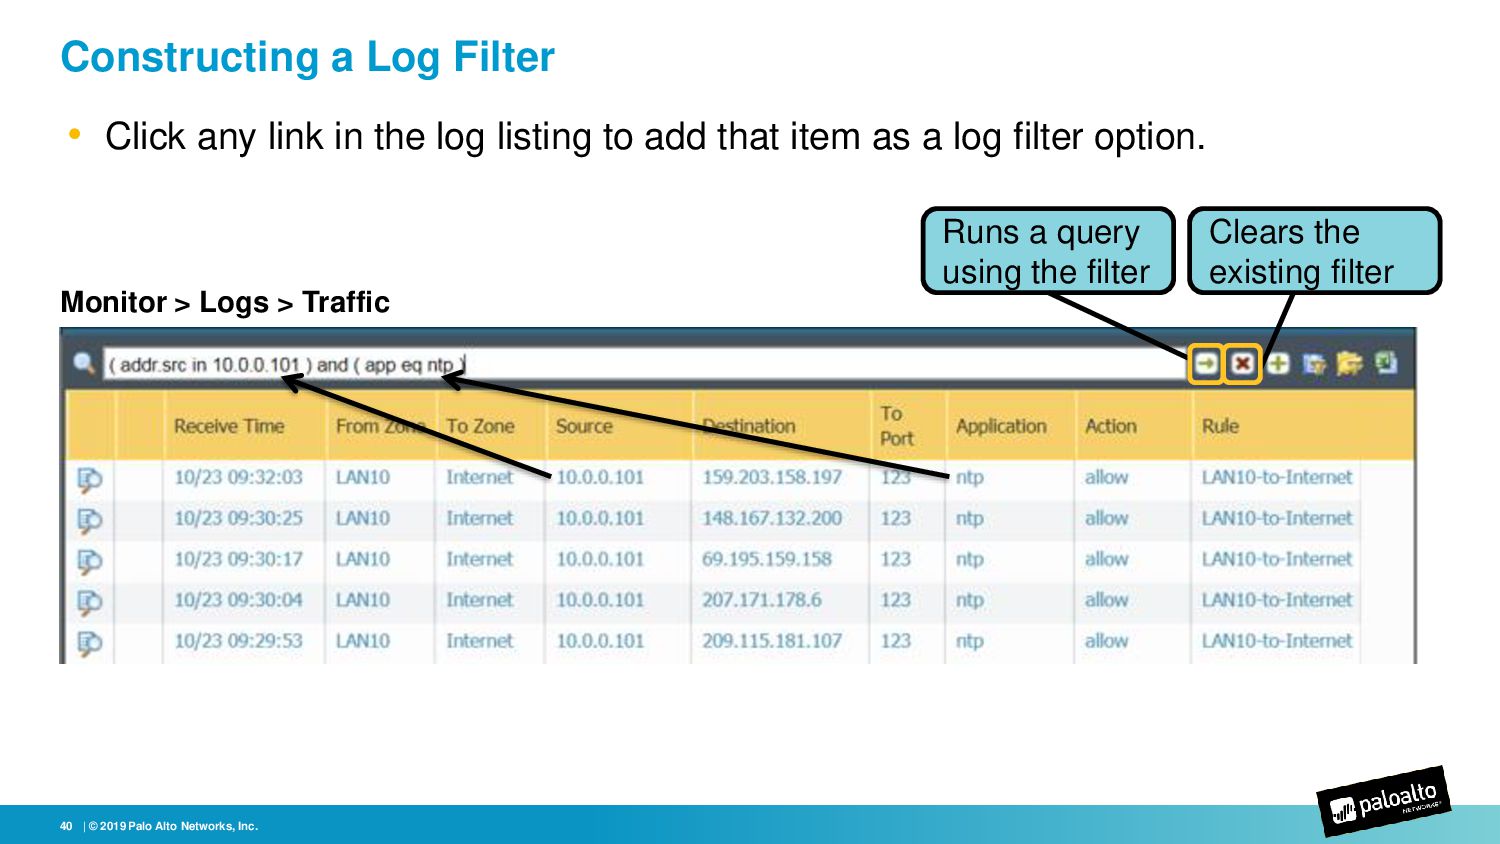
  30. Constructing a Log Filter • Click any link in the

    log listing to add that item as a log filter option. Monitor > Logs > Traffic Runs a query using the filter Clears the existing filter | © 2019 Palo Alto Networks, Inc. 40
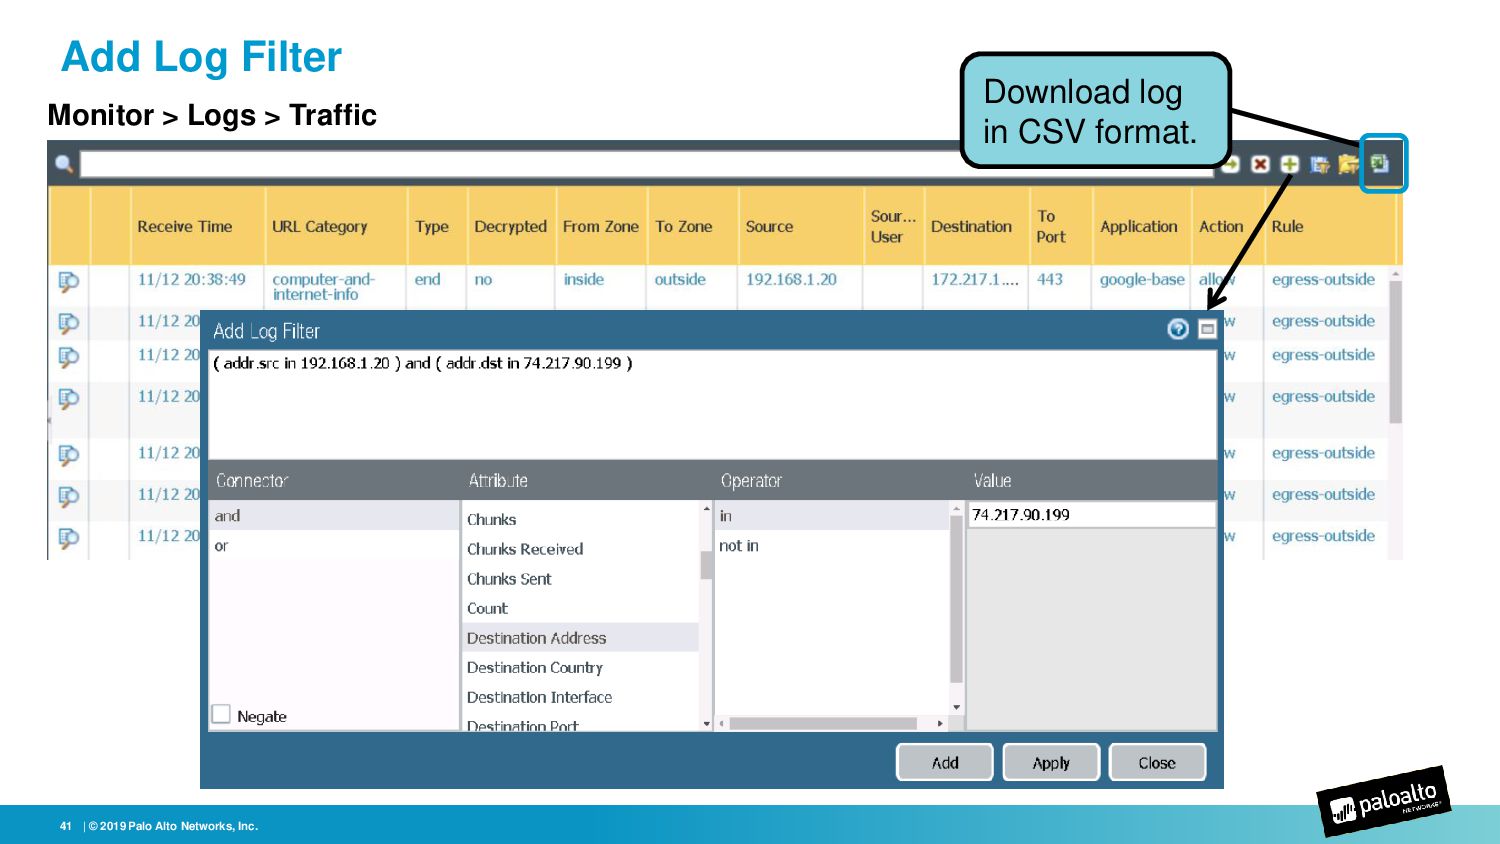
  31. Add Log Filter Monitor > Logs > Traffic Download log

    in CSV format. | © 2019 Palo Alto Networks, Inc. 41
  32. Now that you have completed this module, you should be

    able to: Module Summary • Connect to the firewall and log in as admin • Configure the network settings for the management interface port • Describe the difference between the running config and the candidate config • Configure dynamic firewall updates to update the applications and threats databases • Create a local firewall administrative account • Access the firewall logs | © 2019 Palo Alto Networks, Inc. 42
  33. Initial Configuration Lab (Pages 12-24 in the Lab Guide) •

    Load a firewall lab configuration file • Create an admin role • Create an administrator account • Manage commit locks • Manage external firewall services • Schedule dynamic updates | © 2019 Palo Alto Networks, Inc. 44 Password: Oslokijc URL: https://sin.panwlabs.net User name: tafe-X (X=1-20)
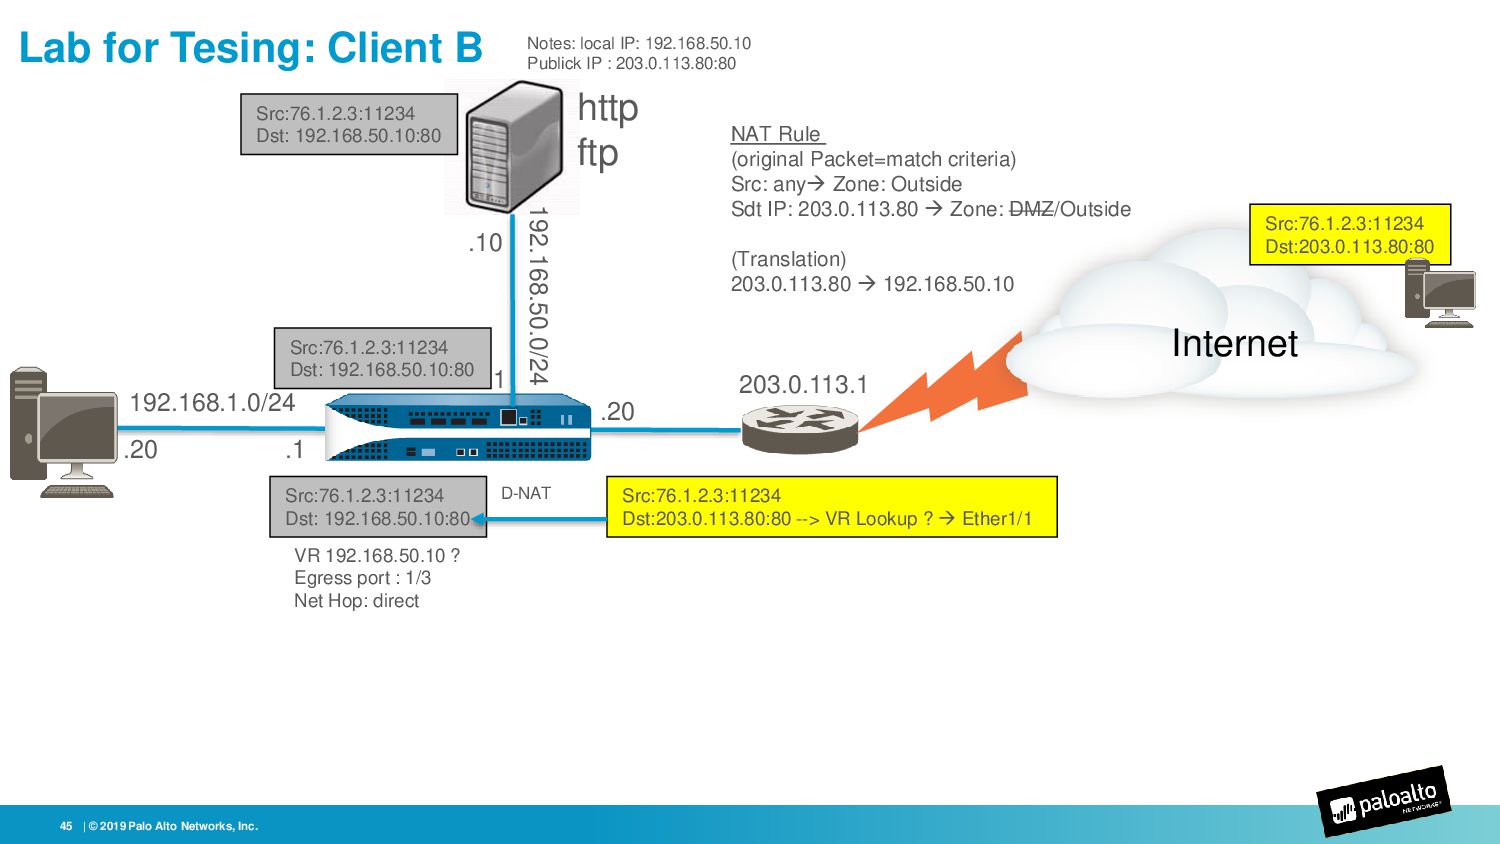
  34. Lab for Tesing: Client B 45 | © 2019 Palo

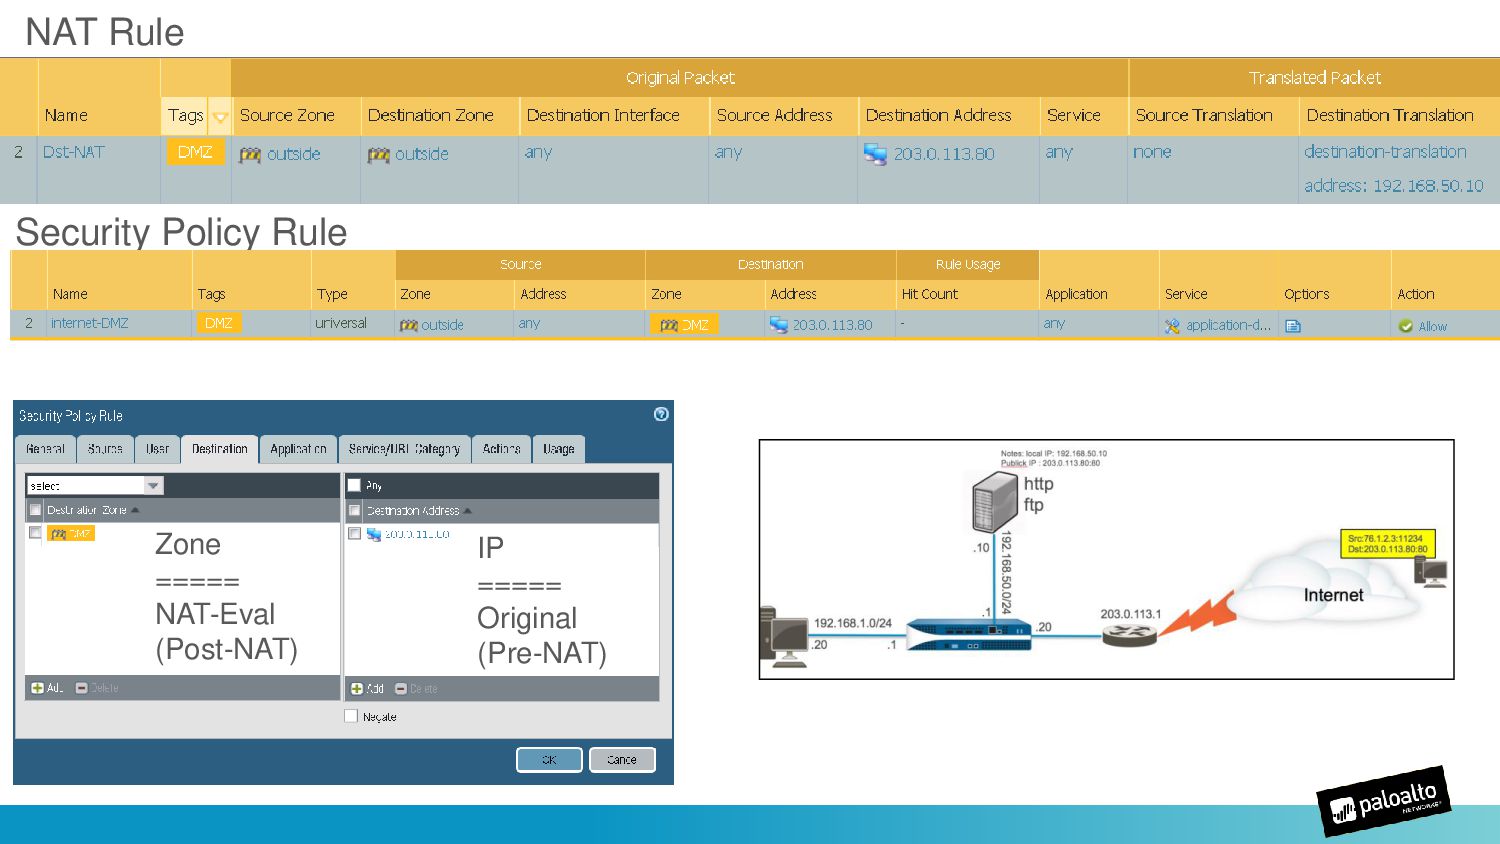
    Alto Networks, Inc. Internet 192.168.1.0/24 .1 .20 203.0.113.1 .20 192.168.50.0/24 .1 .10 http ftp Src:76.1.2.3:11234 Dst:203.0.113.80:80 Notes: local IP: 192.168.50.10 Publick IP : 203.0.113.80:80 Src:76.1.2.3:11234 Dst:203.0.113.80:80 --> VR Lookup ?  Ether1/1 Src:76.1.2.3:11234 Dst: 192.168.50.10:80 D-NAT VR 192.168.50.10 ? Egress port : 1/3 Net Hop: direct Src:76.1.2.3:11234 Dst: 192.168.50.10:80 Src:76.1.2.3:11234 Dst: 192.168.50.10:80 NAT Rule (original Packet=match criteria) Src: any Zone: Outside Sdt IP: 203.0.113.80  Zone: DMZ/Outside (Translation) 203.0.113.80  192.168.50.10
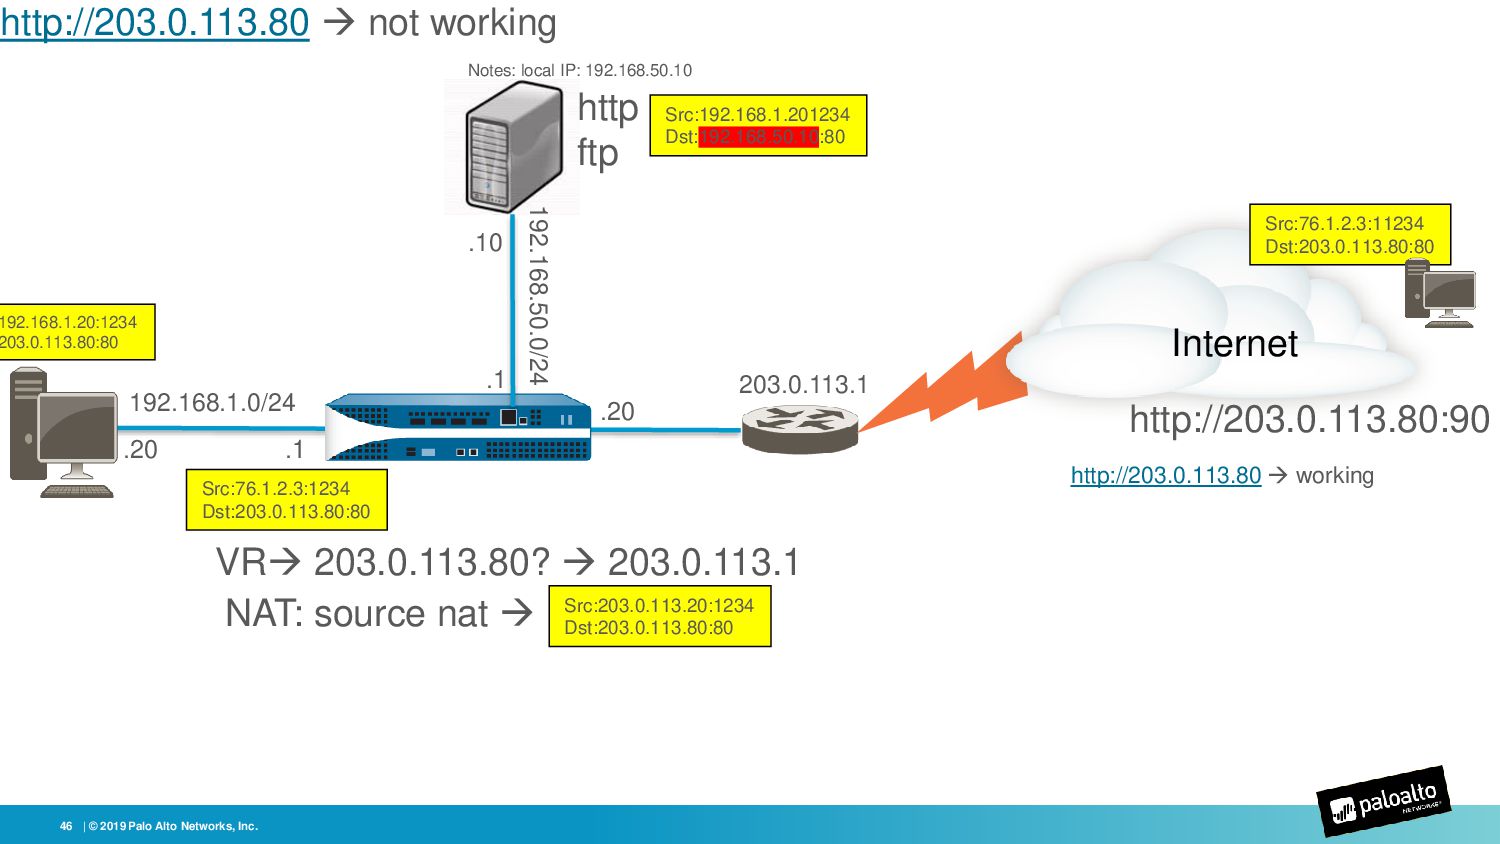
  35. 46 | © 2019 Palo Alto Networks, Inc. Internet 192.168.1.0/24

    .1 .20 203.0.113.1 .20 192.168.50.0/24 .1 .10 http ftp Src:76.1.2.3:11234 Dst:203.0.113.80:80 Notes: local IP: 192.168.50.10 http://203.0.113.80:90 http://203.0.113.80  not working http://203.0.113.80  working 192.168.1.20:1234 203.0.113.80:80 Src:76.1.2.3:1234 Dst:203.0.113.80:80 VR 203.0.113.80?  203.0.113.1 Src:203.0.113.20:1234 Dst:203.0.113.80:80 NAT: source nat  Src:192.168.1.201234 Dst:192.168.50.10:80
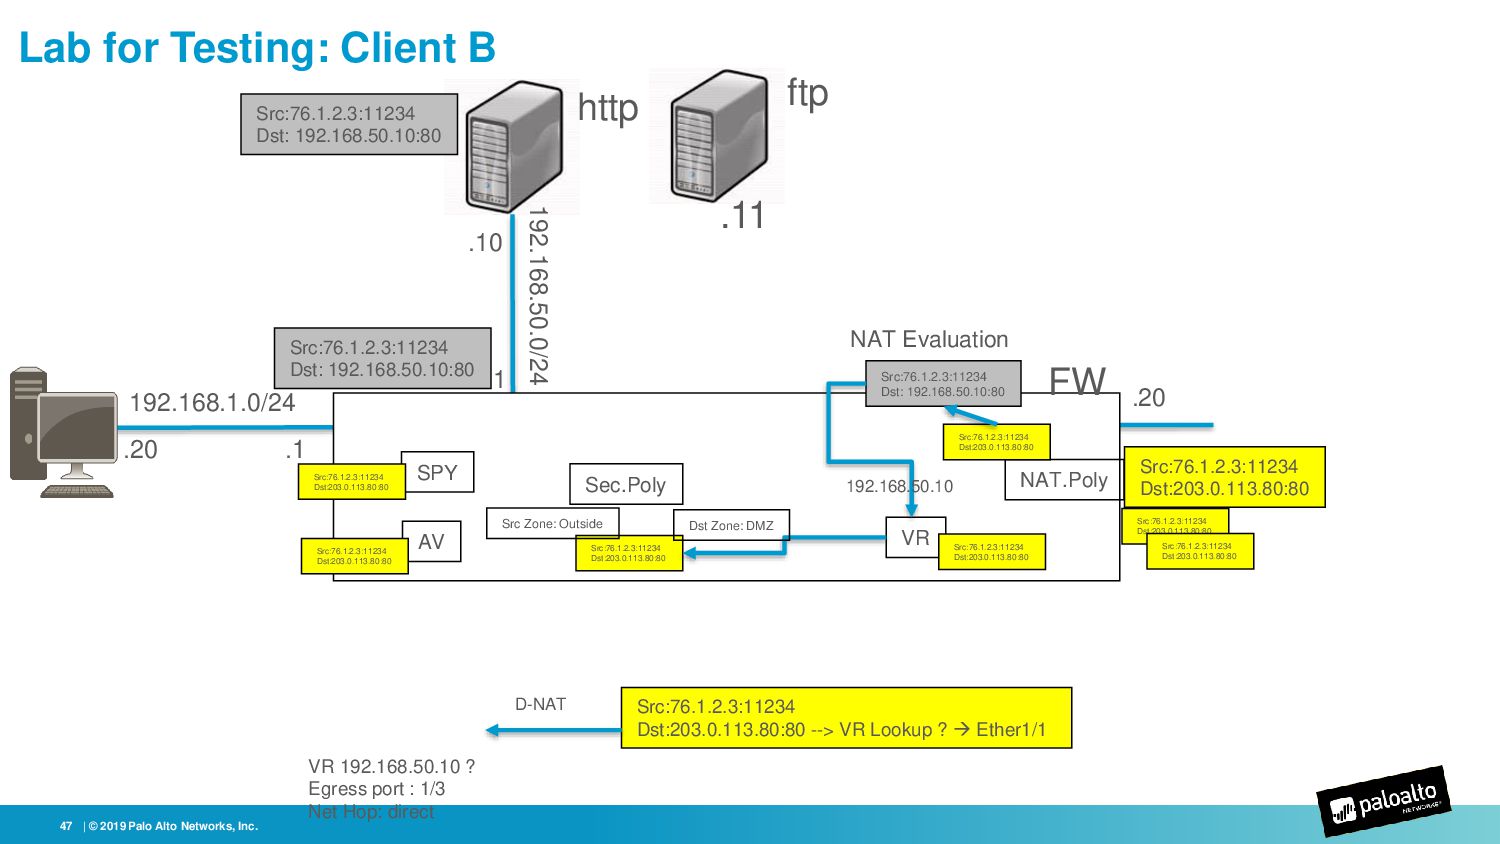
  36. Lab for Testing: Client B 47 | © 2019 Palo

    Alto Networks, Inc. 192.168.1.0/24 .1 .20 .20 192.168.50.0/24 .1 .10 http Src:76.1.2.3:11234 Dst:203.0.113.80:80 Src:76.1.2.3:11234 Dst:203.0.113.80:80 --> VR Lookup ?  Ether1/1 D-NAT VR 192.168.50.10 ? Egress port : 1/3 Net Hop: direct Src:76.1.2.3:11234 Dst: 192.168.50.10:80 Src:76.1.2.3:11234 Dst: 192.168.50.10:80 FW Sec.Poly NAT.Poly VR AV SPY Src:76.1.2.3:11234 Dst:203.0.113.80:80 Src:76.1.2.3:11234 Dst:203.0.113.80:80 Src:76.1.2.3:11234 Dst:203.0.113.80:80 Src:76.1.2.3:11234 Dst:203.0.113.80:80 Src:76.1.2.3:11234 Dst:203.0.113.80:80 Src:76.1.2.3:11234 Dst:203.0.113.80:80 Src:76.1.2.3:11234 Dst:203.0.113.80:80 Src:76.1.2.3:11234 Dst: 192.168.50.10:80 NAT Evaluation 192.168.50.10 Dst Zone: DMZ Src Zone: Outside ftp .11
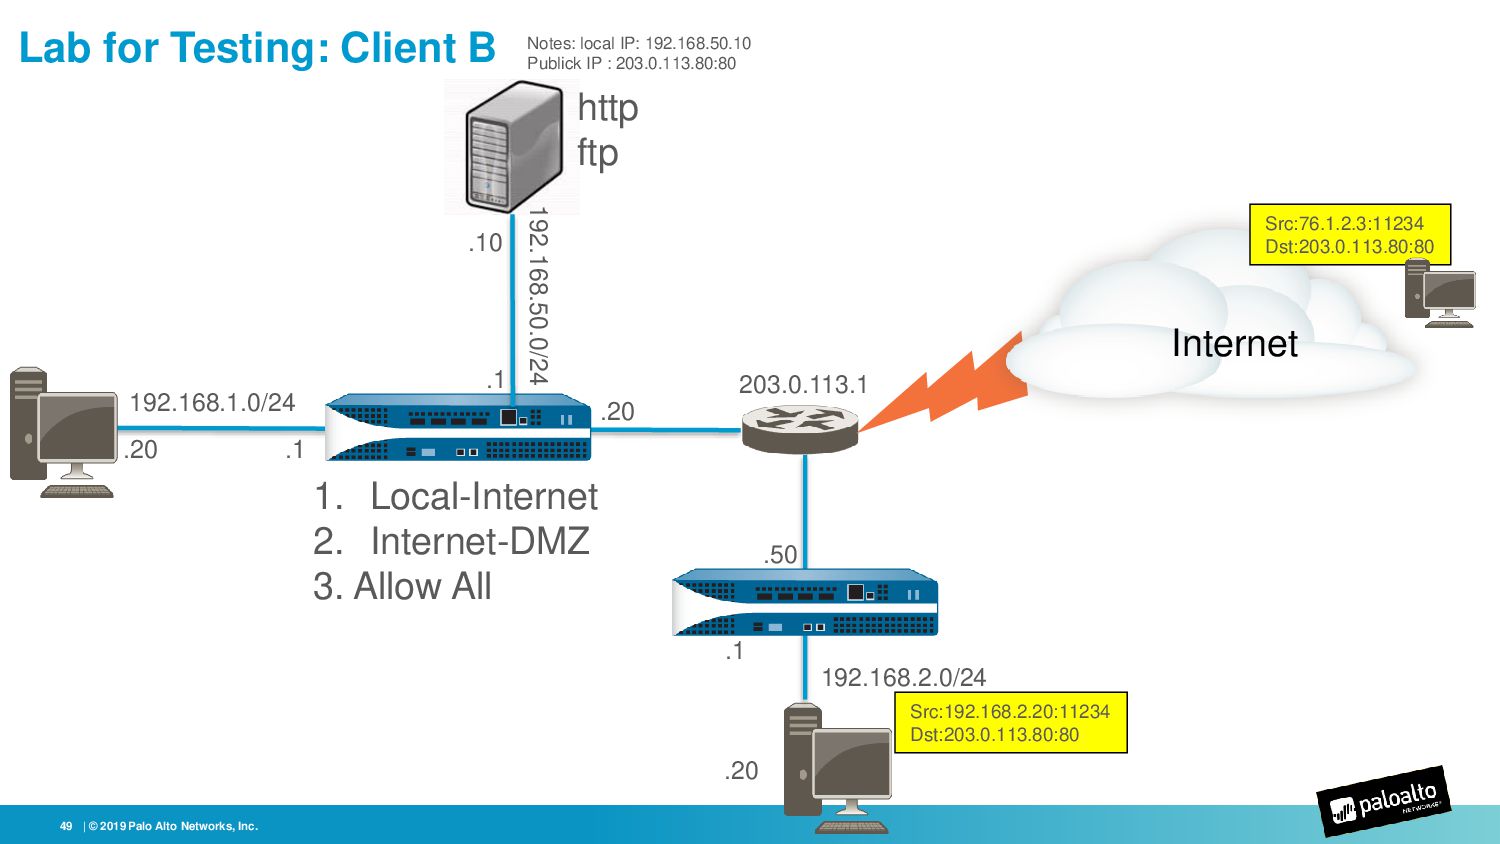
  37. Lab for Testing: Client B 49 | © 2019 Palo

    Alto Networks, Inc. Internet 192.168.1.0/24 .1 .20 192.168.2.0/24 .20 .1 203.0.113.1 .50 .20 192.168.50.0/24 .1 .10 http ftp Src:76.1.2.3:11234 Dst:203.0.113.80:80 Notes: local IP: 192.168.50.10 Publick IP : 203.0.113.80:80 Src:192.168.2.20:11234 Dst:203.0.113.80:80 1. Local-Internet 2. Internet-DMZ 3. Allow All
  38. 50 | © 2019 Palo Alto Networks, Inc. Login to

    Client-B computer: Update IP to match topology 1 2 4 3 5