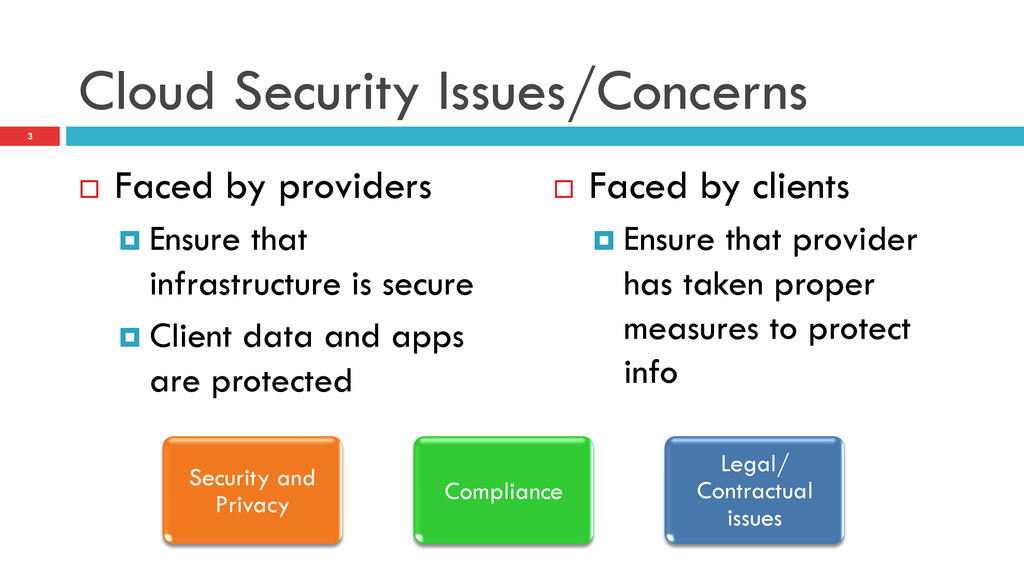
infrastructure is secure ¤ Client data and apps are protected ¨ Faced by clients ¤ Ensure that provider has taken proper measures to protect info 3 Security and Privacy Compliance Legal/ Contractual issues
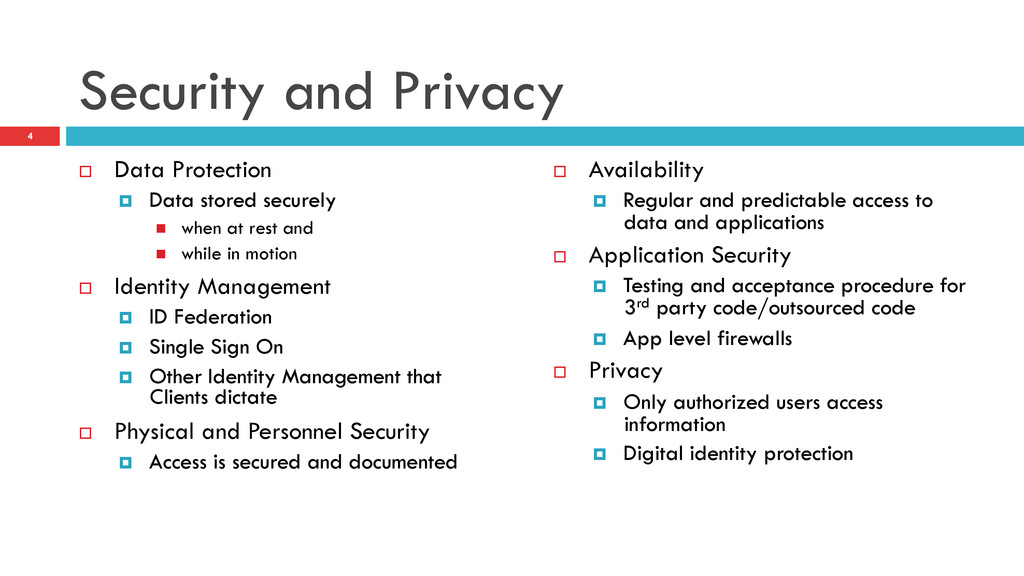
n when at rest and n while in motion ¨ Identity Management ¤ ID Federation ¤ Single Sign On ¤ Other Identity Management that Clients dictate ¨ Physical and Personnel Security ¤ Access is secured and documented ¨ Availability ¤ Regular and predictable access to data and applications ¨ Application Security ¤ Testing and acceptance procedure for 3rd party code/outsourced code ¤ App level firewalls ¨ Privacy ¤ Only authorized users access information ¤ Digital identity protection 4
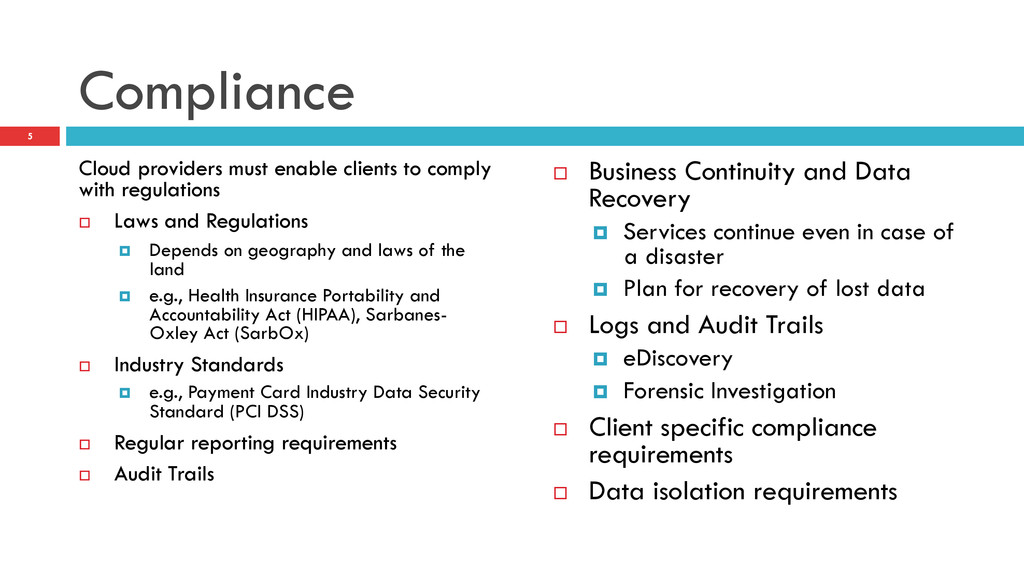
¨ Laws and Regulations ¤ Depends on geography and laws of the land ¤ e.g., Health Insurance Portability and Accountability Act (HIPAA), Sarbanes- Oxley Act (SarbOx) ¨ Industry Standards ¤ e.g., Payment Card Industry Data Security Standard (PCI DSS) ¨ Regular reporting requirements ¨ Audit Trails ¨ Business Continuity and Data Recovery ¤ Services continue even in case of a disaster ¤ Plan for recovery of lost data ¨ Logs and Audit Trails ¤ eDiscovery ¤ Forensic Investigation ¨ Client specific compliance requirements ¨ Data isolation requirements 5
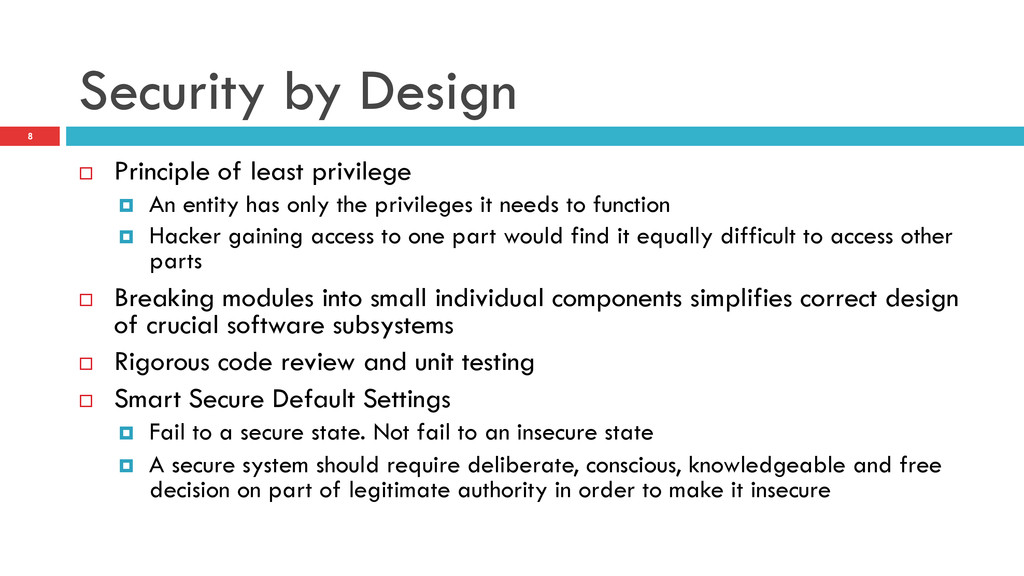
An entity has only the privileges it needs to function ¤ Hacker gaining access to one part would find it equally difficult to access other parts ¨ Breaking modules into small individual components simplifies correct design of crucial software subsystems ¨ Rigorous code review and unit testing ¨ Smart Secure Default Settings ¤ Fail to a secure state. Not fail to an insecure state ¤ A secure system should require deliberate, conscious, knowledgeable and free decision on part of legitimate authority in order to make it insecure
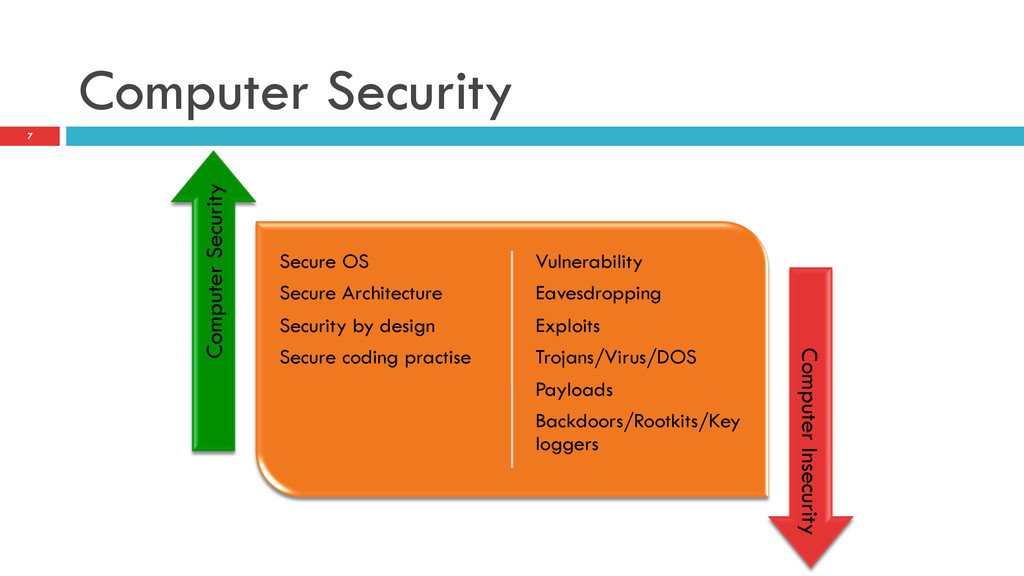
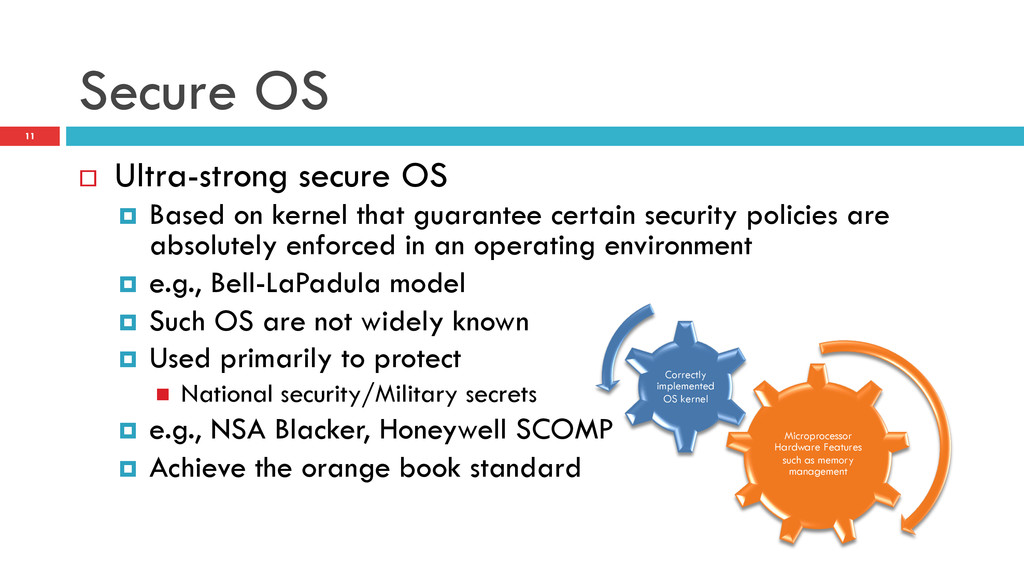
kernel that guarantee certain security policies are absolutely enforced in an operating environment ¤ e.g., Bell-LaPadula model ¤ Such OS are not widely known ¤ Used primarily to protect n National security/Military secrets ¤ e.g., NSA Blacker, Honeywell SCOMP ¤ Achieve the orange book standard Microprocessor Hardware Features such as memory management Correctly implemented OS kernel
“low security” category so applications must make themselves resistant to malicious subversion ¨ Common software defects include ¤ buffer overflows ¤ format string vulnerabilities ¤ integer overflow ¤ code/command injection ¤ dangling pointers
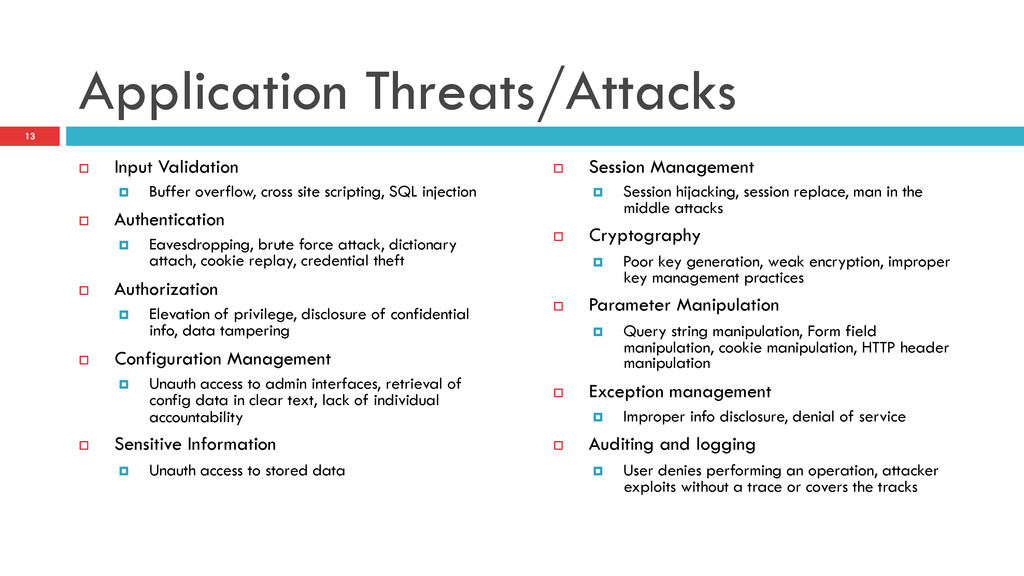
scripting, SQL injection ¨ Authentication ¤ Eavesdropping, brute force attack, dictionary attach, cookie replay, credential theft ¨ Authorization ¤ Elevation of privilege, disclosure of confidential info, data tampering ¨ Configuration Management ¤ Unauth access to admin interfaces, retrieval of config data in clear text, lack of individual accountability ¨ Sensitive Information ¤ Unauth access to stored data ¨ Session Management ¤ Session hijacking, session replace, man in the middle attacks ¨ Cryptography ¤ Poor key generation, weak encryption, improper key management practices ¨ Parameter Manipulation ¤ Query string manipulation, Form field manipulation, cookie manipulation, HTTP header manipulation ¨ Exception management ¤ Improper info disclosure, denial of service ¨ Auditing and logging ¤ User denies performing an operation, attacker exploits without a trace or covers the tracks 13


 cloudgenius
 hiola
 ak679839
 adeputra13
 baltimoreniso
 dragon2
 segadevtech
 ssmedikasda
 signer
 minorun365
 yatabe
 aisw77
 skipperchong
 lfama
 axbom
 akihiro_kokubo
 destraynor
 marcoroth
 sarafernandez
 chriscoyier
 baasie
 pauljervisheath
 eileencodes
 cassininazir