Upgrade to Pro — share decks privately, control downloads, hide ads and more …

Securing PHP in the LLM age

Sponsored · Your Podcast. Everywhere. Effortlessly. Share. Educate. Inspire. Entertain. You do you. We'll handle the rest. →

Securing PHP in the LLM age

How do we help maintainers deal with the rising number of security reports from LLM based security analysis? Can we scan through PHP libraries and projects ourselves to ensure good quality reports are there to help the ecosystem become more secure?

Questions like these led The PHP Foundation to launch an Ecosystem Security Team. Kicked off by a grant from Alpha-Omega through the Linux Foundation, and drawing on findings from models like Fable/Mythos, we started working towards dealing with these new challenges.

In this talk I will share the findings of the Team I'm leading and talk you through what we learned along the way and what suggestions we have and why.

Volker Dusch

November 19, 2026

Transcript

54 slides
  1. Securing PHP in the LLM age Volker "edorian" Dusch Ecosystem

    Security Lead at The PHP Foundation PHP 8.5 Release Manager Head of Engineering at Tideways IPC Munich 2026
  2. Why am I here? In March, the Linux Foundation announced

    a grant to strengthen open source security. https://www.linuxfoundation.org/press/linux-foundation-announces-12.5-million-in-grantfunding-from-leading-organizations-to-advance-open-source-security Alpha-Omega’s mission is to protect society by catalyzing sustainable security improvements across open source. https://alpha-omega.dev/
  3. The Ecosystem Security Team The grant funded the new Ecosystem

    Security Team at The PHP Foundation. Secure the PHP ecosystem and support maintainers. Today I'll share what we learned.
  4. My background ~20 years of PHP Working at Tideways on

    PHP performance tooling PHP 8.5 Release Manager Ecosystem Security Lead at The PHP Foundation Thank you to Tideways for making this work possible.
  5. Agentic Security Models inspect code and use tools to test

    hypotheses. Static and dynamic analysis plus fuzzing.
  6. My experiences 2025 was the year of the slop, things

    have changed. No fundamentally new class of exploits It's still all just software With all the problems of a young industry There are impactful findings, at scale Finding issues takes a lot less effort now
  7. NO new class of exploits? Well, not entirely... The new

    tools have new classes of issues OWASP Top 10 For Large Language Model Applications https://owasp.org/projects/top-10-for-large-language-model-applications
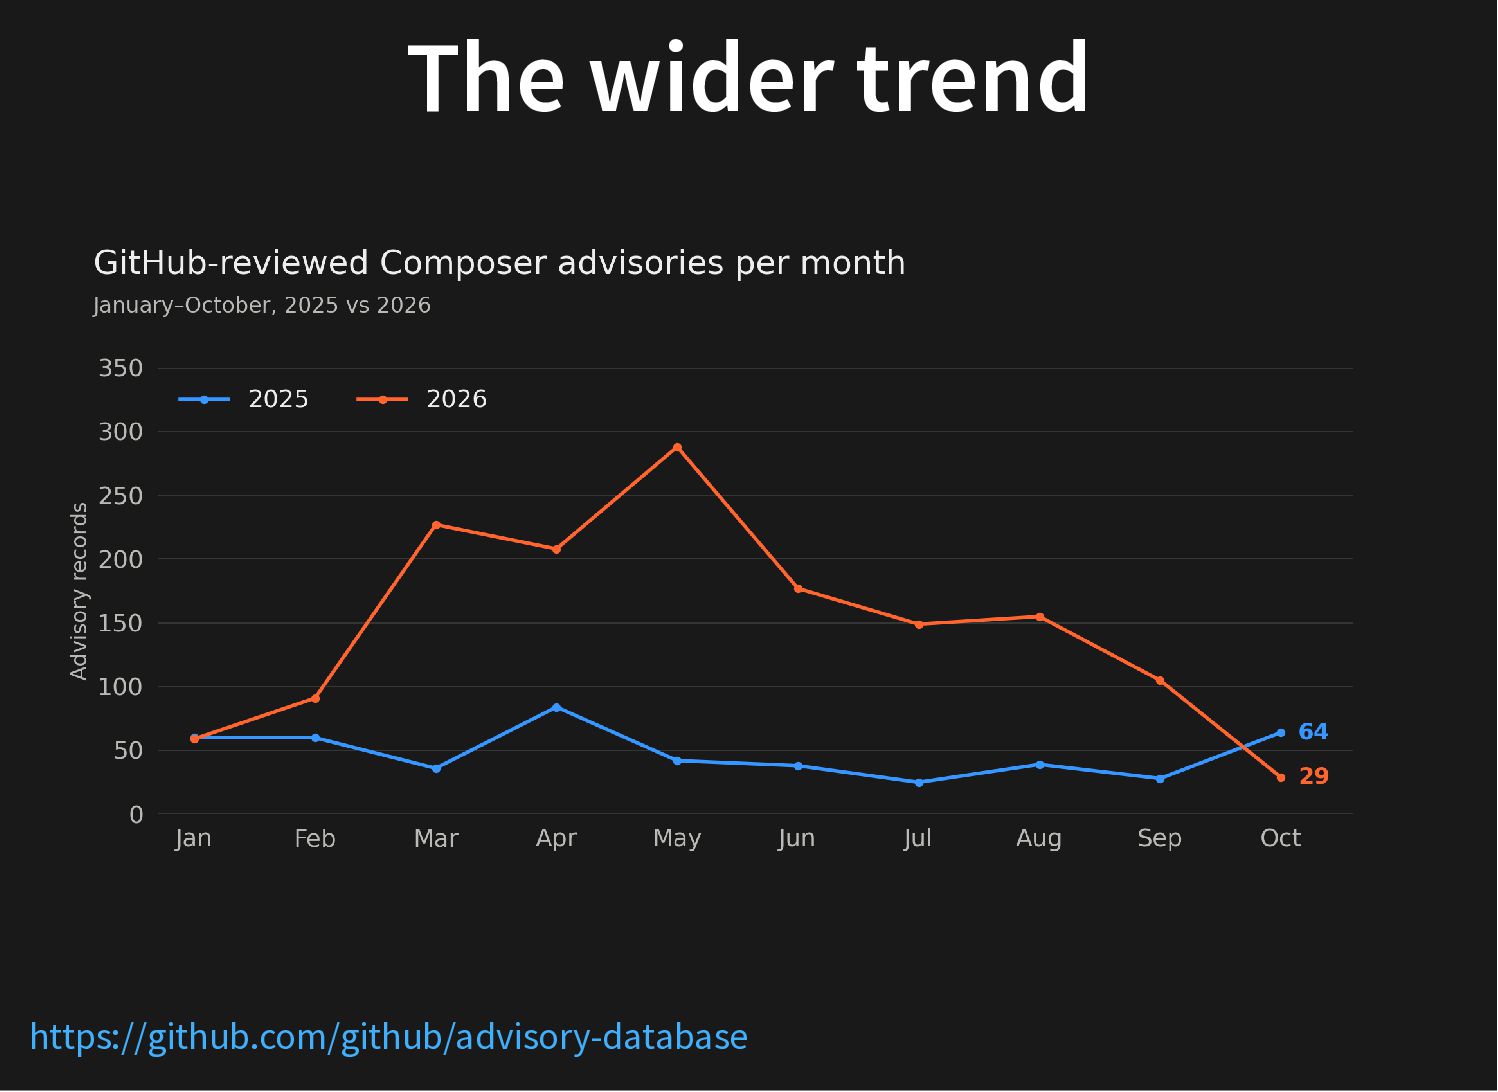
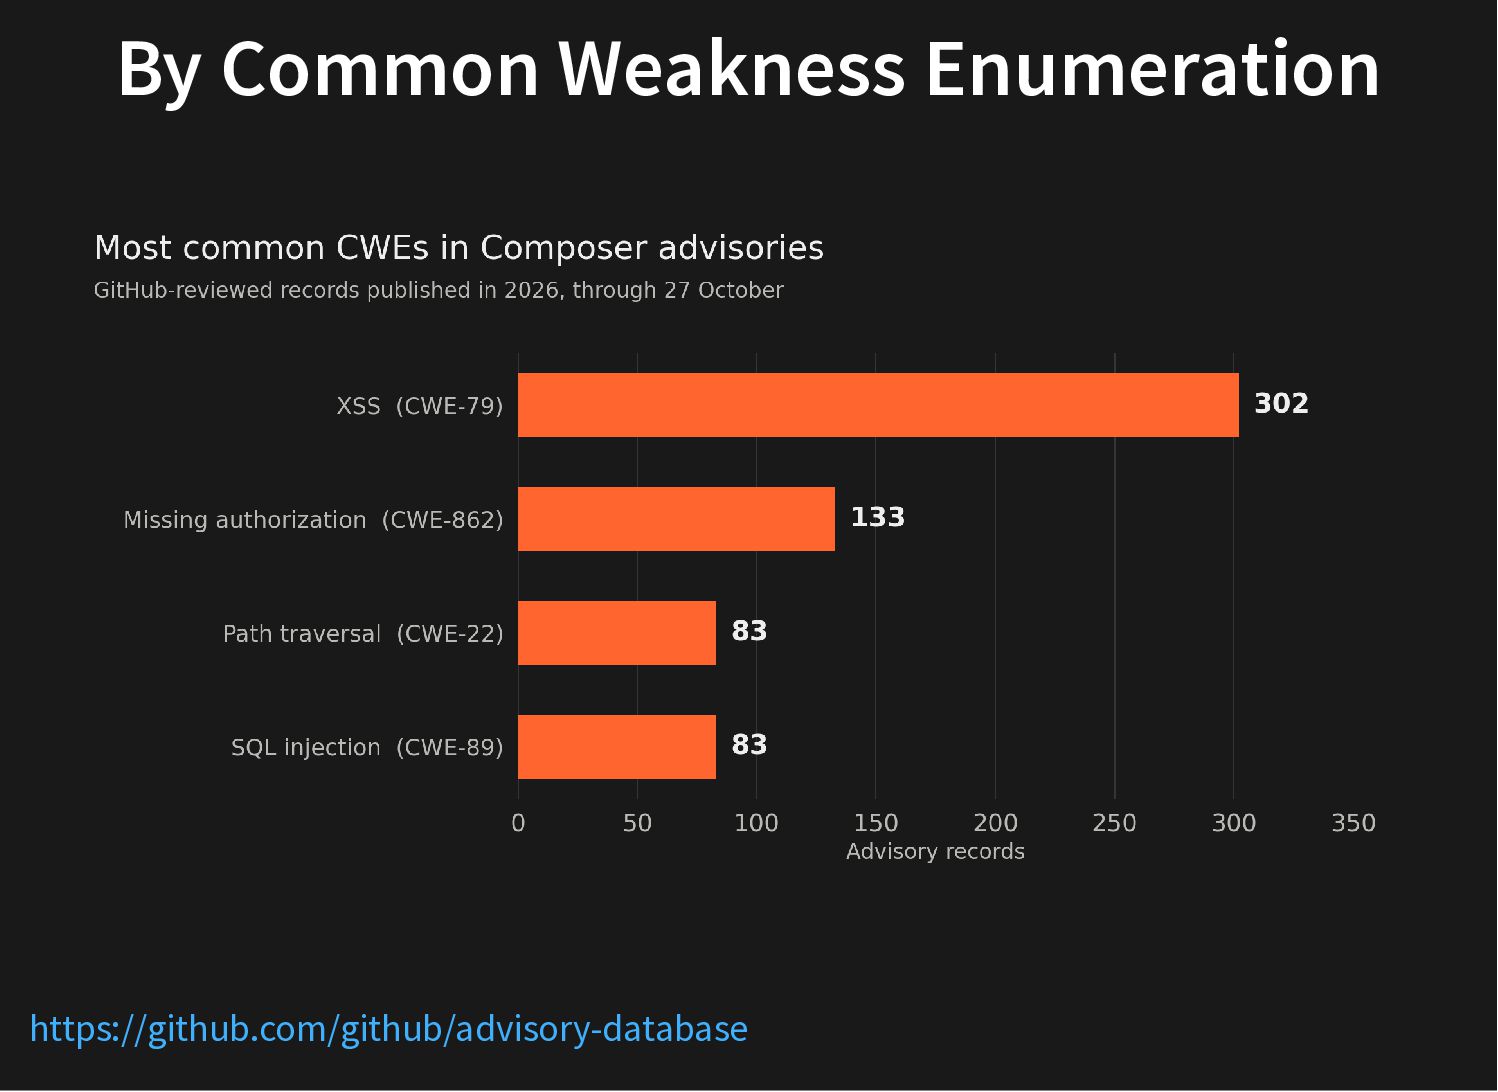
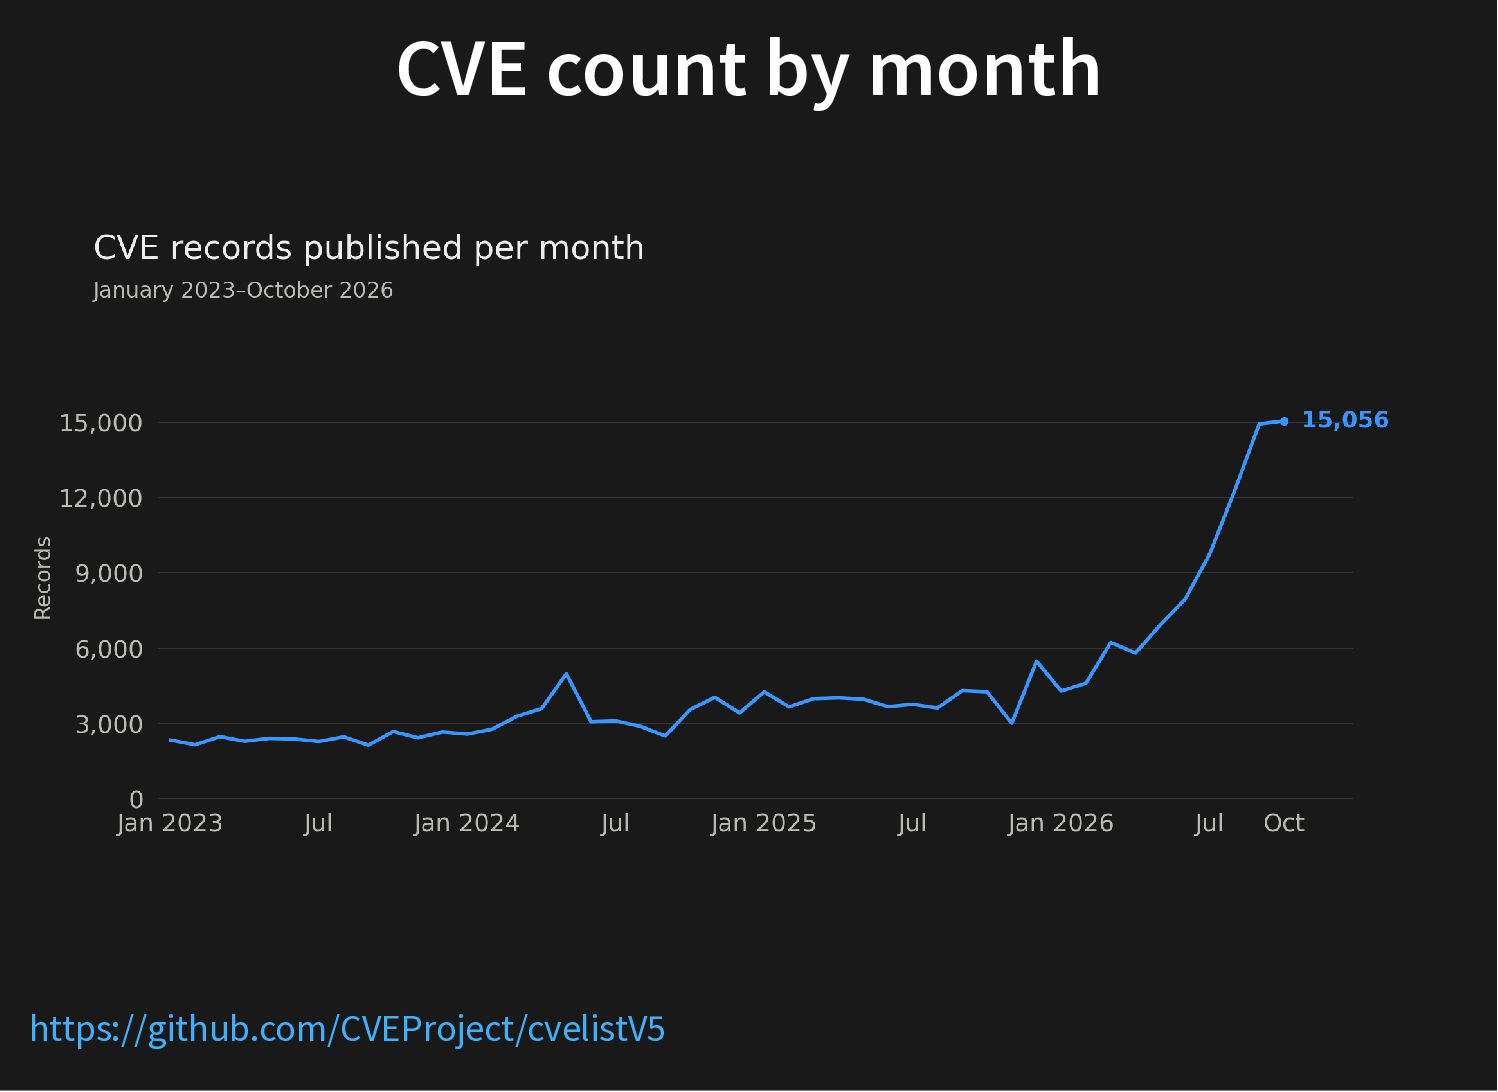
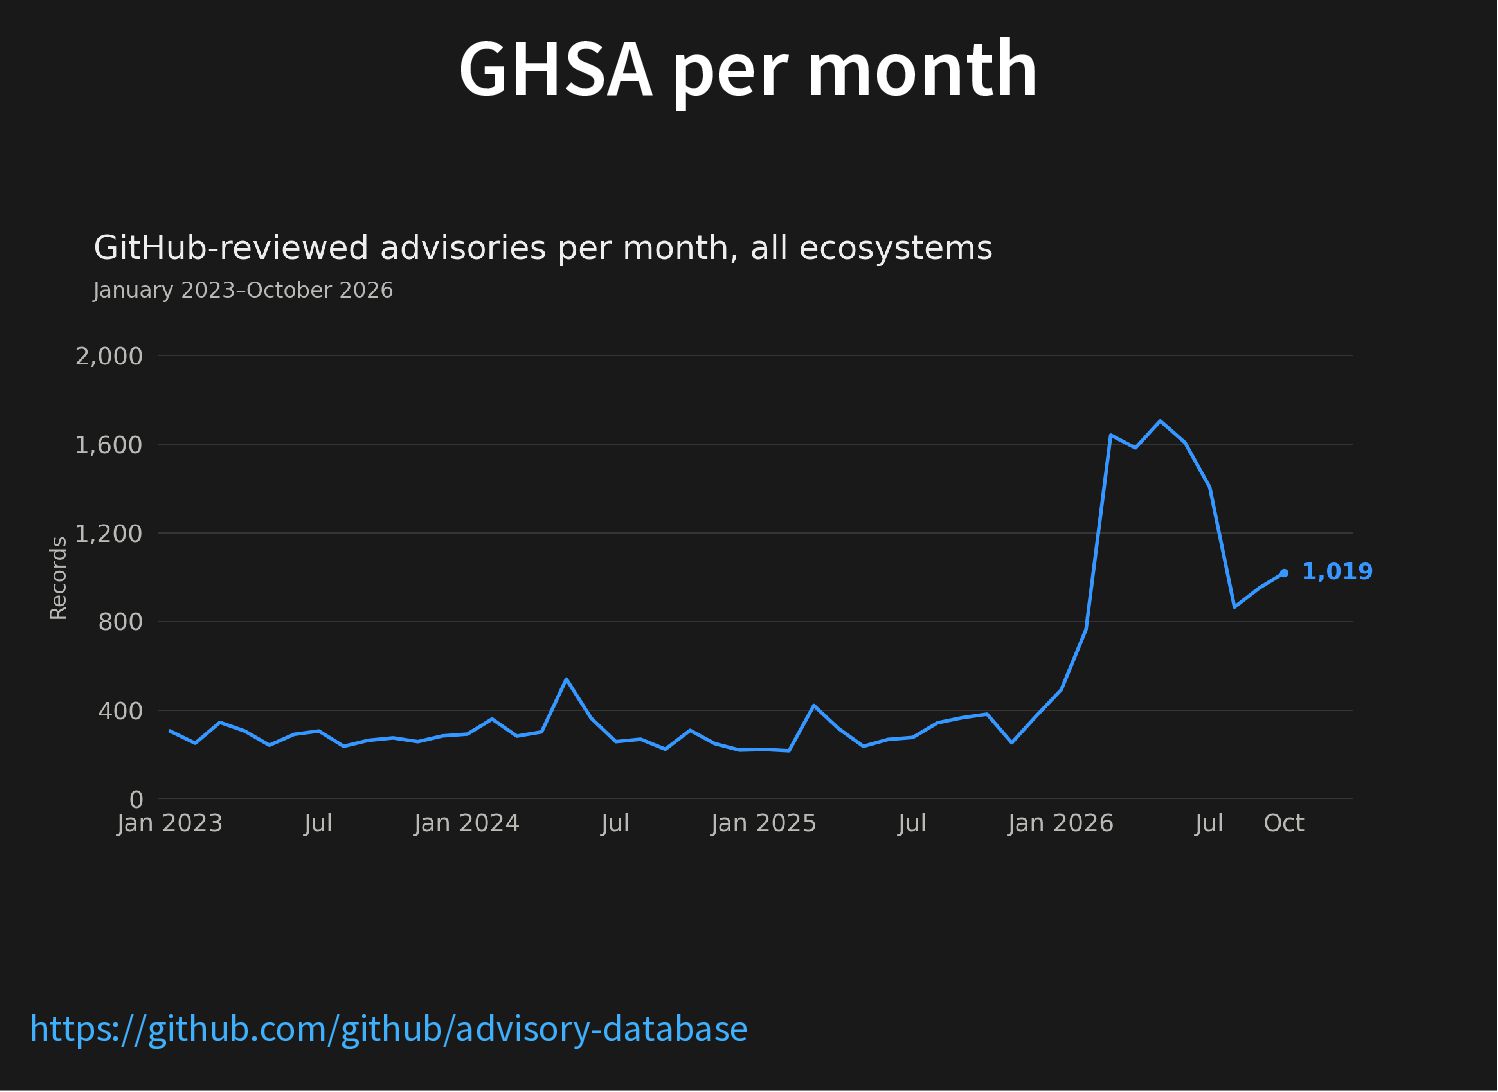
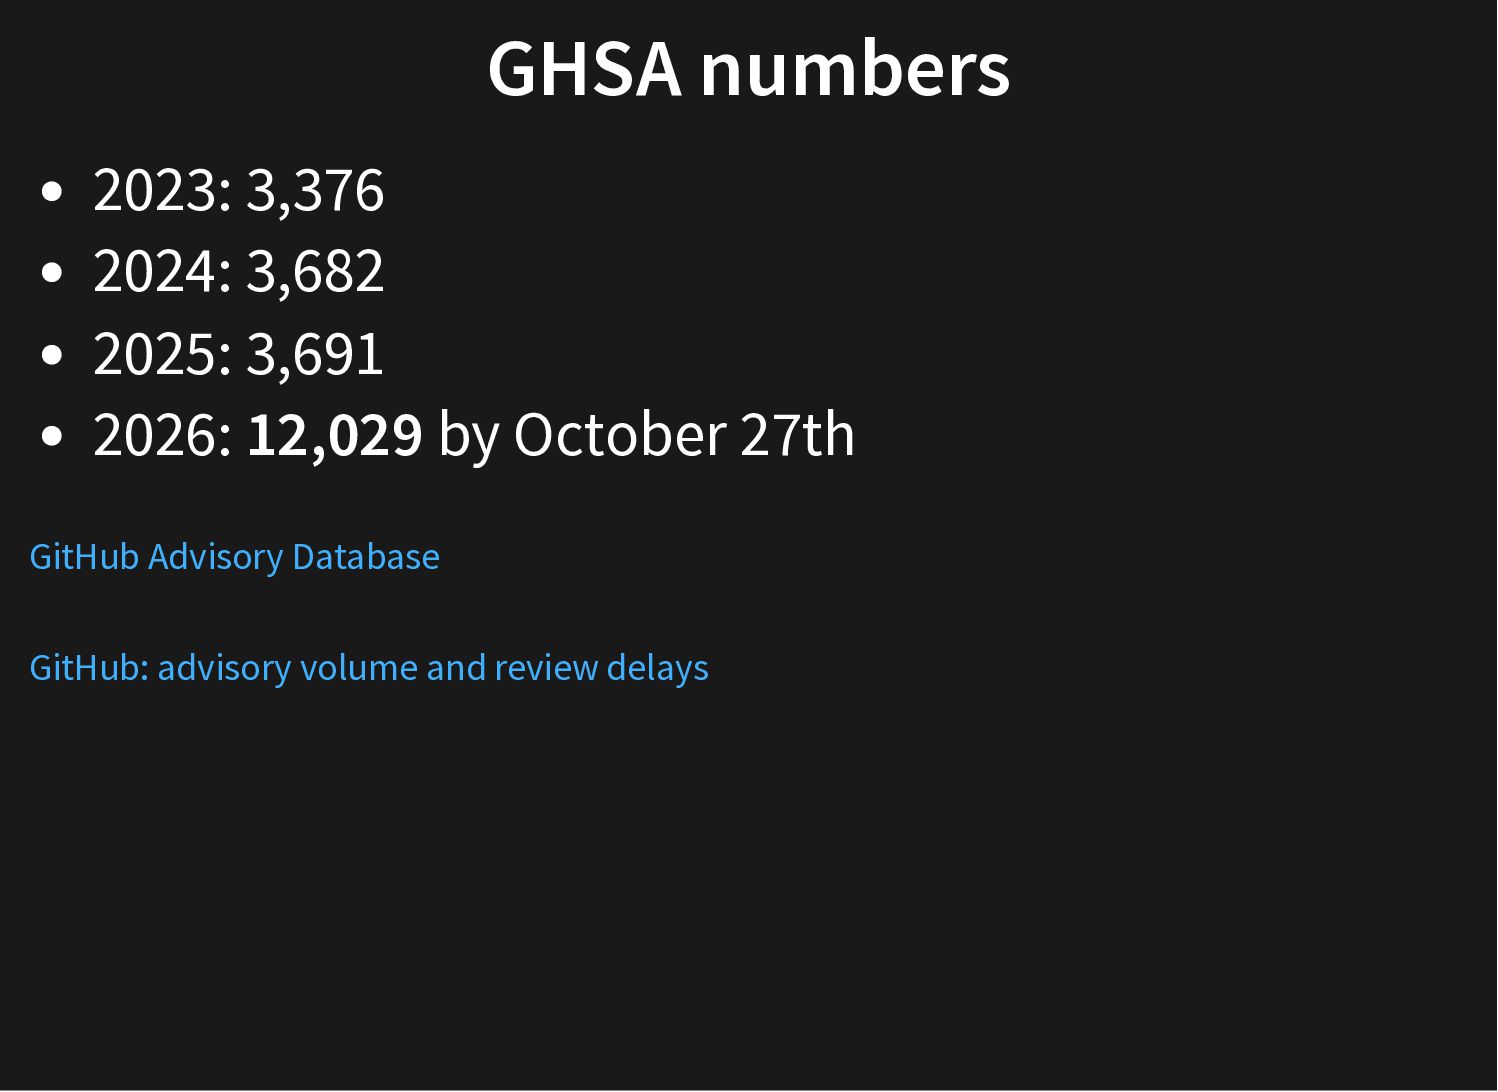
  8. GHSA numbers 2023: 3,376 2024: 3,682 2025: 3,691 2026: 12,029

    by October 27th GitHub Advisory Database GitHub: advisory volume and review delays
  9. Asymmetry in security An attacker only needs to find one

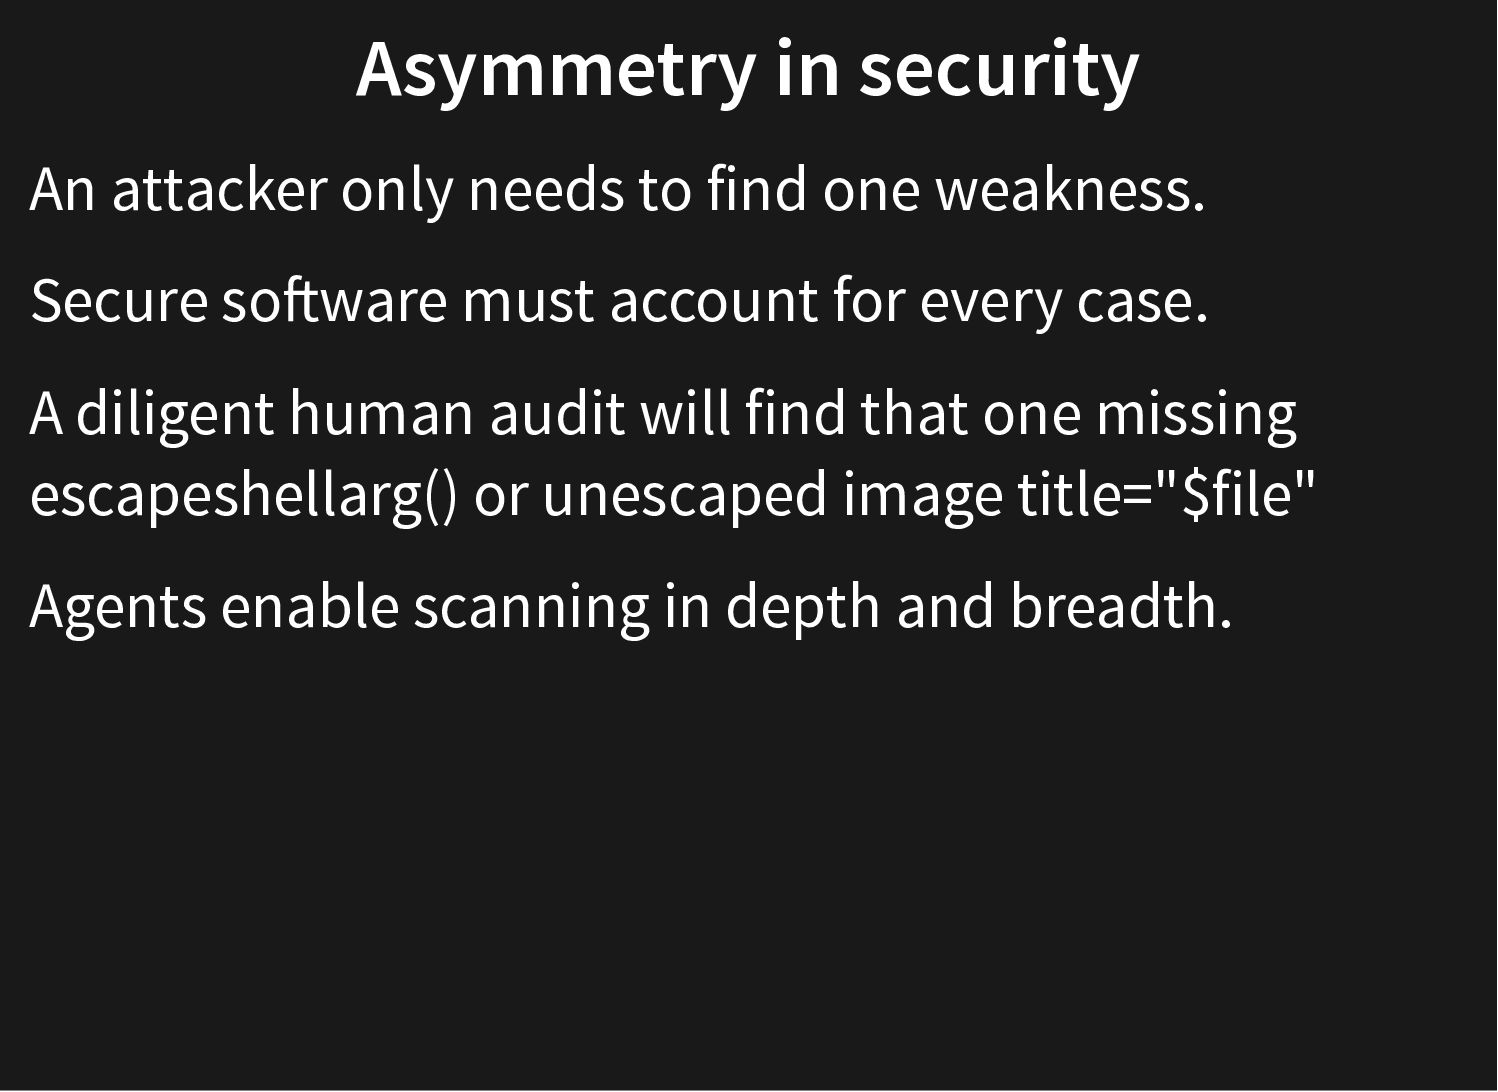
    weakness. Secure software must account for every case. A diligent human audit will find that one missing escapeshellarg() or unescaped image title="$file" Agents enable scanning in depth and breadth.
  10. Where's the impact? There are a couple big news stories.

    But not many. Why is everything still working? Remember Y2K? Dates saved as 2 digits instead of 4! We've been here before. Successful prevention looks like nothing happened. A lot of people, doing their jobs, fixing things.
  11. So, why am I here? Leading the Ecosystem Security Team

    https://thephp.foundation/blog/2026/05/18/announcing-ecosystem-security-team/ Core guideline: Respond to every request for support. It's open source and it's PHP? We're here for you!
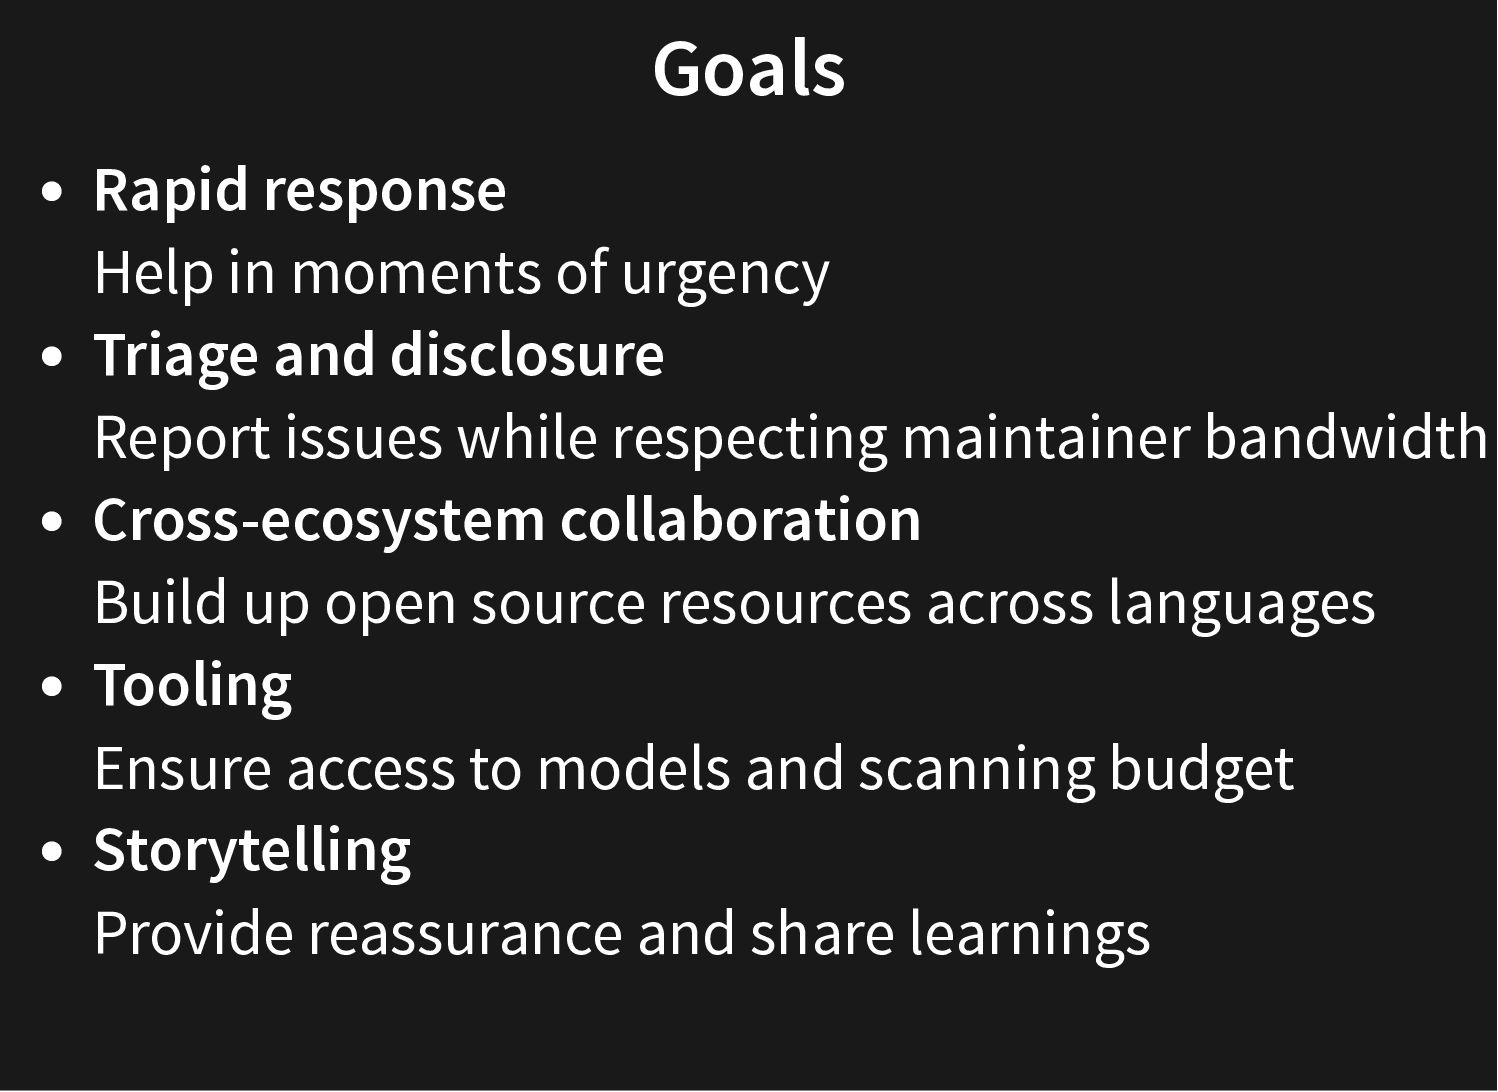
  12. Goals Rapid response Help in moments of urgency Triage and

    disclosure Report issues while respecting maintainer bandwidth Cross-ecosystem collaboration Build up open source resources across languages Tooling Ensure access to models and scanning budget Storytelling Provide reassurance and share learnings
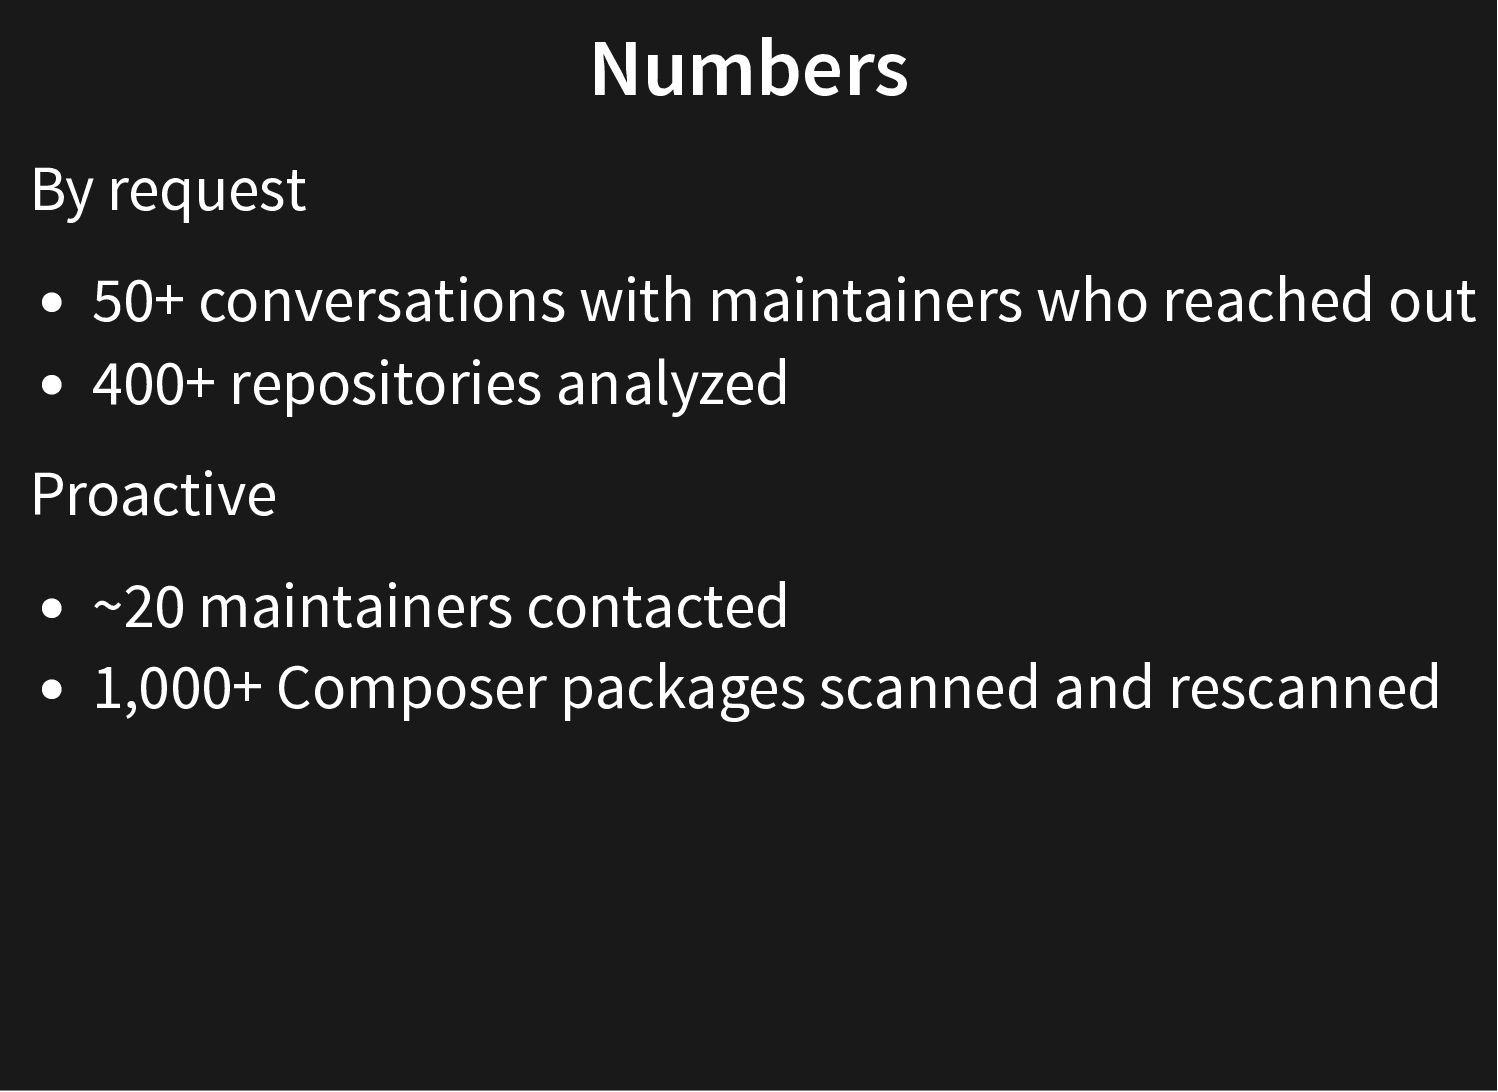
  13. Numbers By request 50+ conversations with maintainers who reached out

    400+ repositories analyzed Proactive ~20 maintainers contacted 1,000+ Composer packages scanned and rescanned
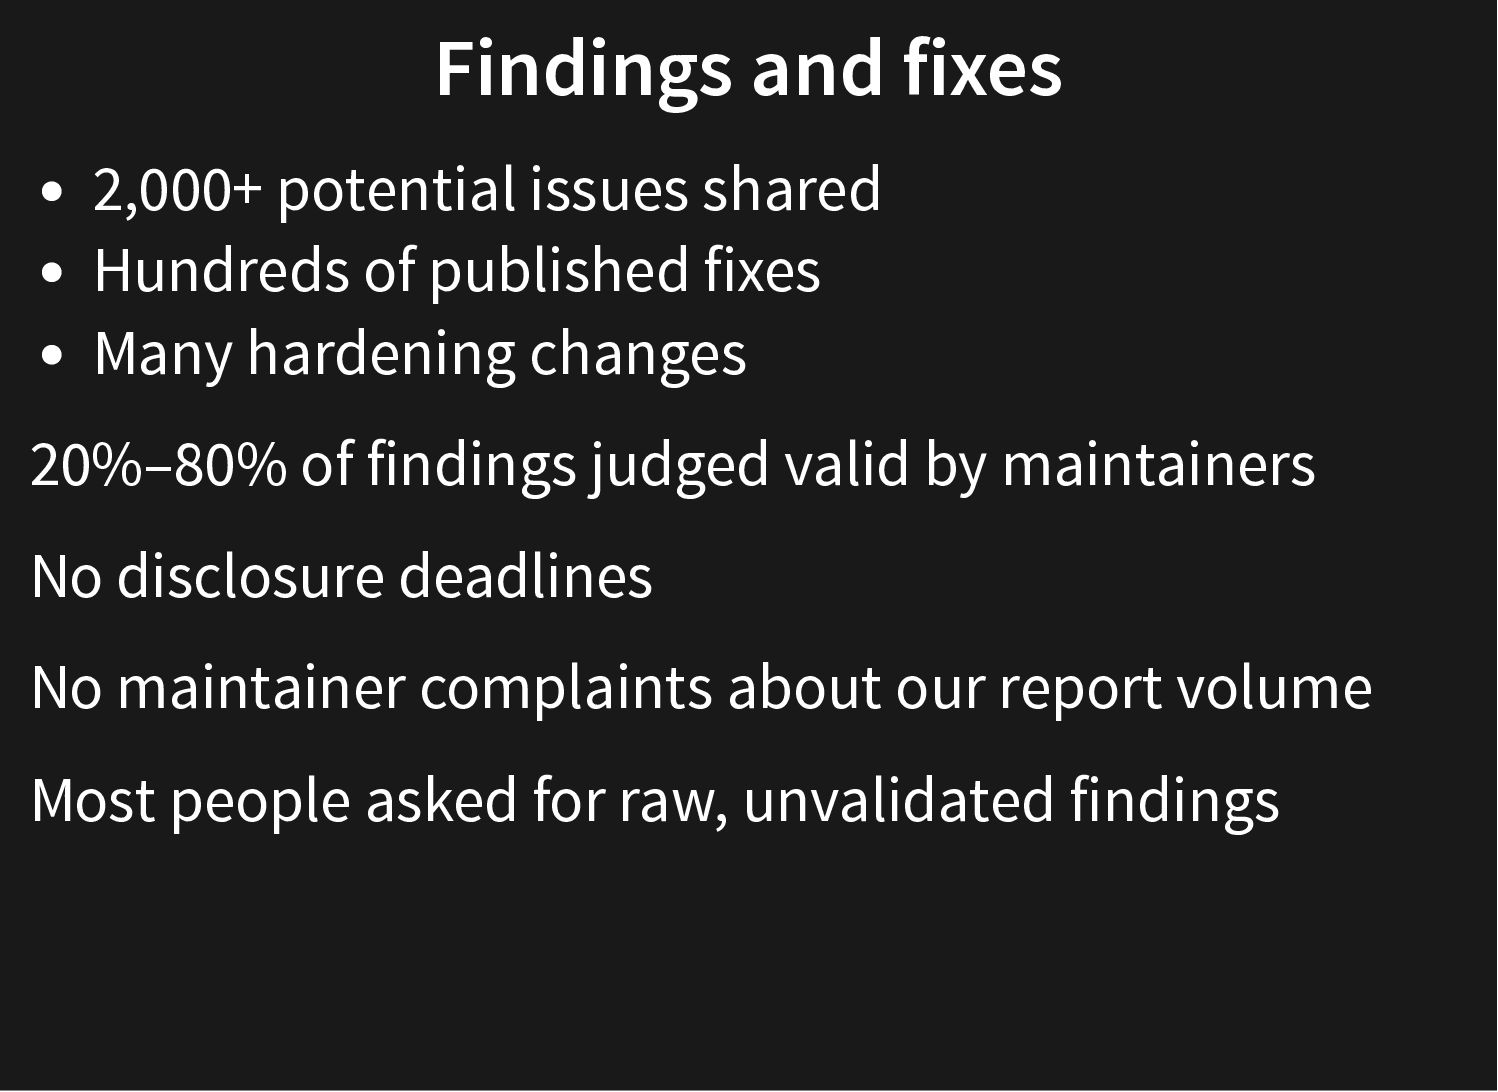
  14. Findings and fixes 2,000+ potential issues shared Hundreds of published

    fixes Many hardening changes 20%–80% of findings judged valid by maintainers No disclosure deadlines No maintainer complaints about our report volume Most people asked for raw, unvalidated findings
  15. Work on php-src 15 CVEs published since July 1 (as

    of October 14) 106 reports closed: invalid, duplicates, or not reproducible Every action reviewed and carried out by a human https://thephp.foundation/blog/2026/10/14/how-the-php-security-team-handles-yourreports/
  16. PIE PHP Installer for Extensions New core PHP infrastructure piece

    Accepted RFC: Unbundle PEAR in PHP 8.7 Web archive available through December 31, 2027 https://wiki.php.net/rfc/end_pear_endorsement
  17. Working with security teams AI companies fund security firms scanning

    projects. The Foundation enables us to participate.
  18. Open Source Technology Improvement Fund One very positive example: OSTIF

    https://ostif.org Performed the Sovereign Tech Fund PHP Audit in 2024 https://ostif.org/php-audit-complete/ Facilitated early Mythos scans on PHP frameworks Big personal thank you to Derek Zimmer
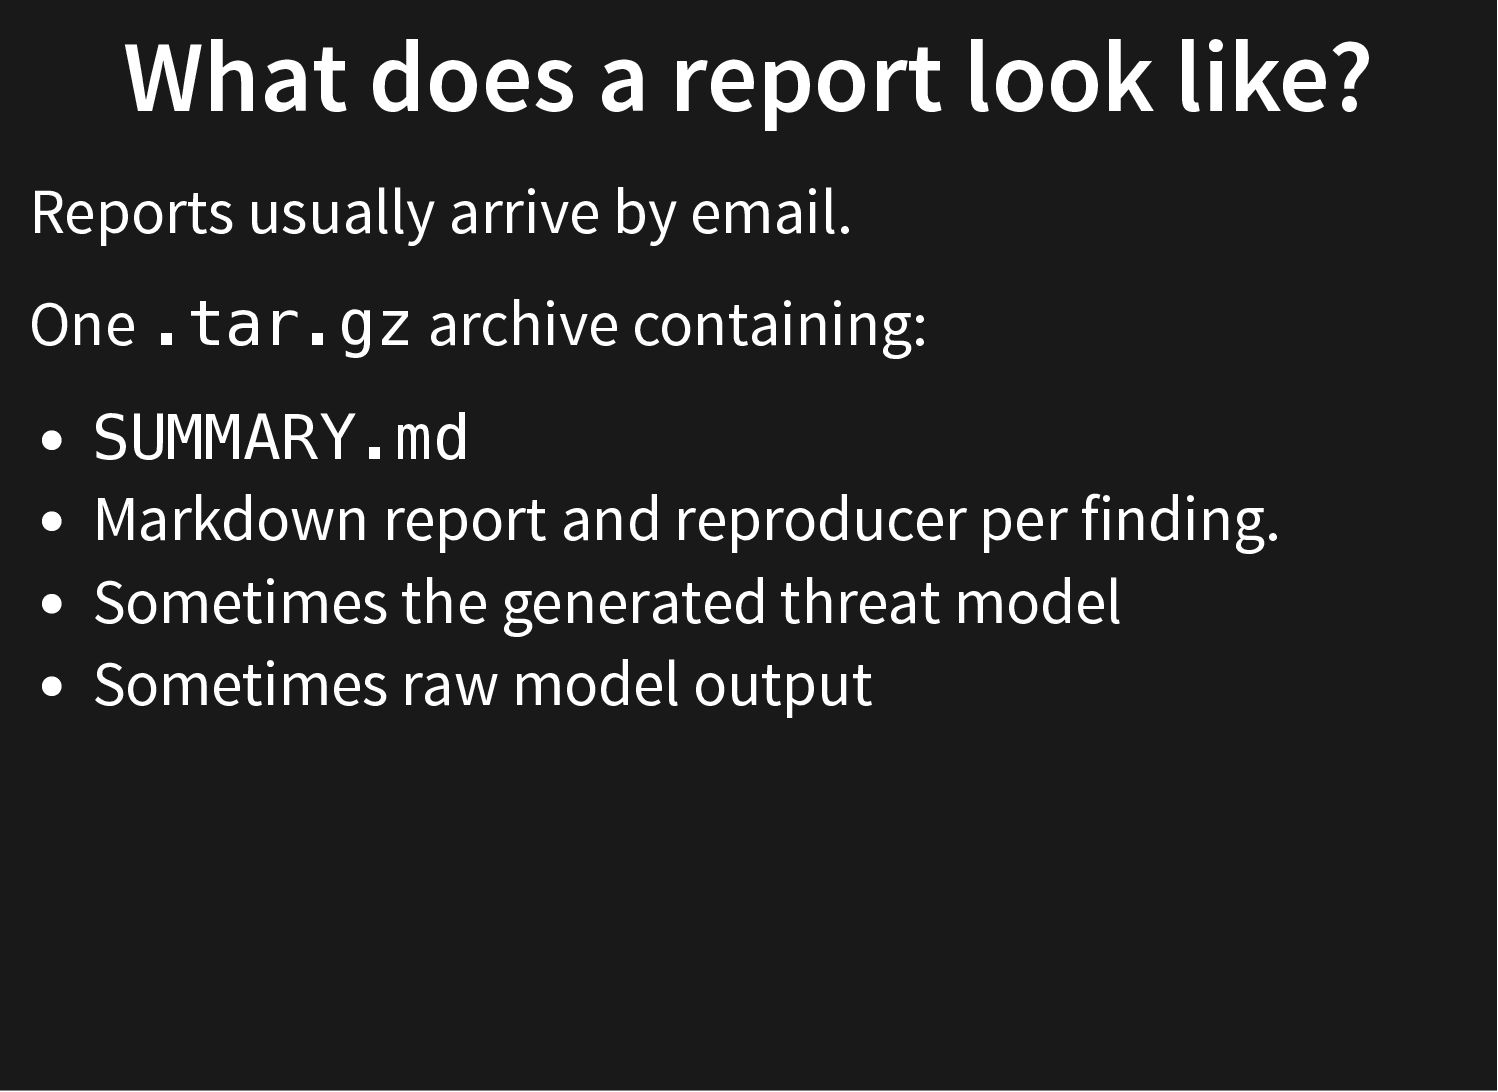
  19. What does a report look like? Reports usually arrive by

    email. One .tar.gz archive containing: SUMMARY.md Markdown report and reproducer per finding. Sometimes the generated threat model Sometimes raw model output
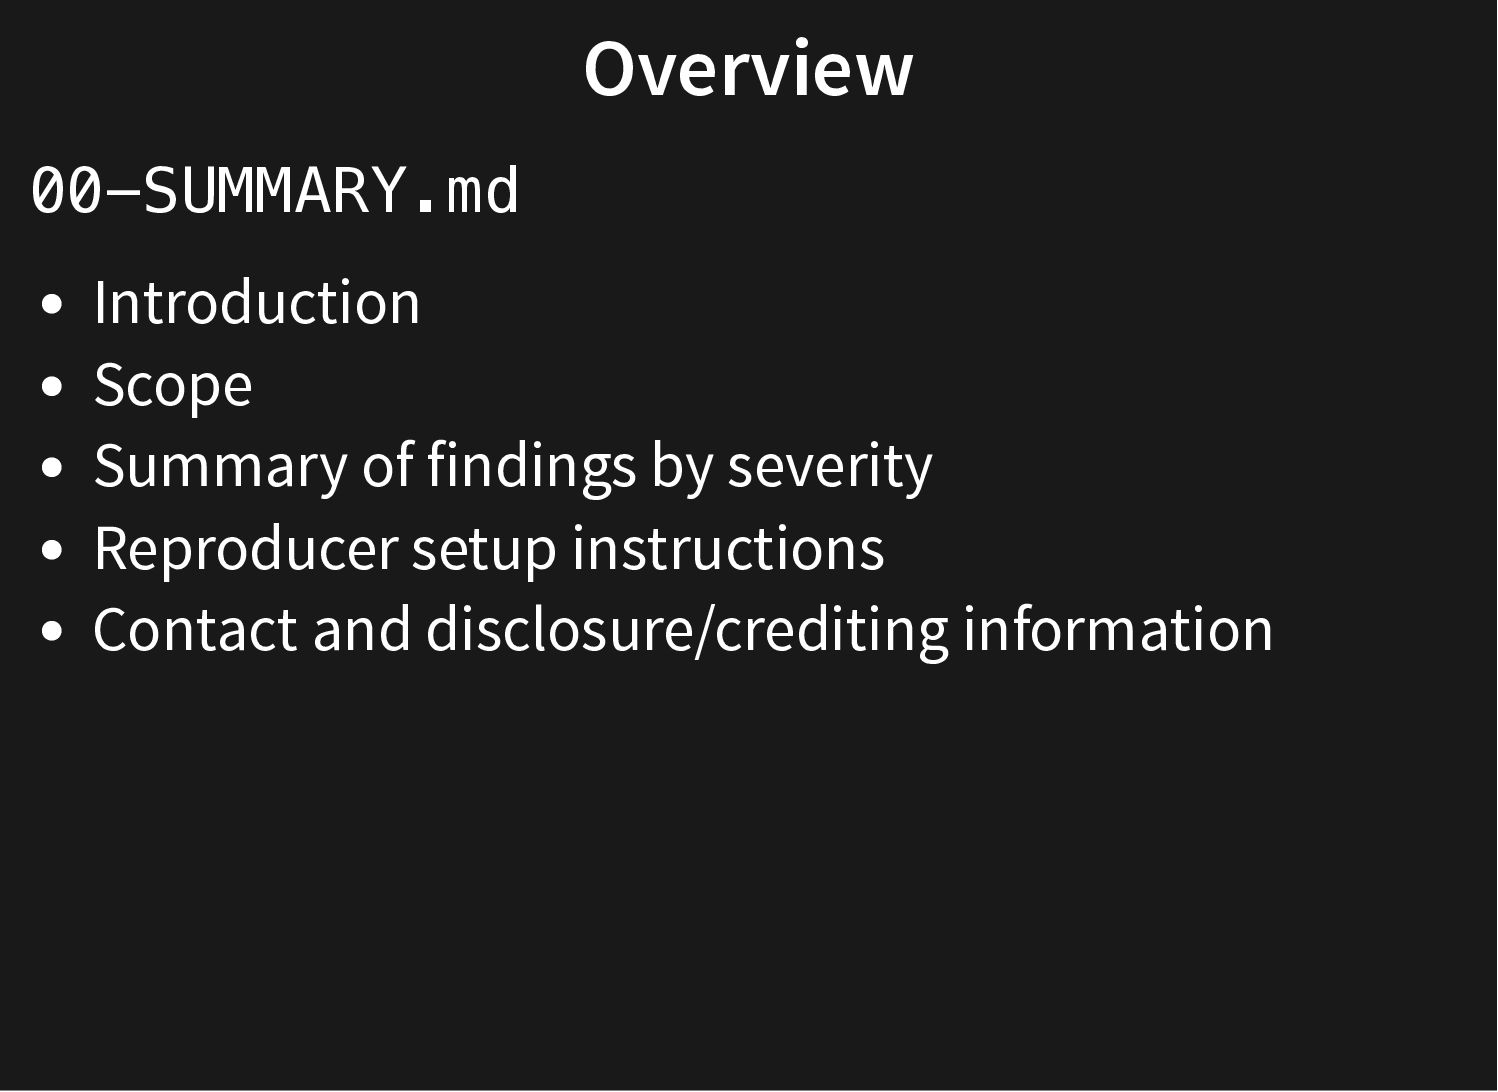
  20. Overview 00-SUMMARY.md Introduction Scope Summary of findings by severity Reproducer

    setup instructions Contact and disclosure/crediting information
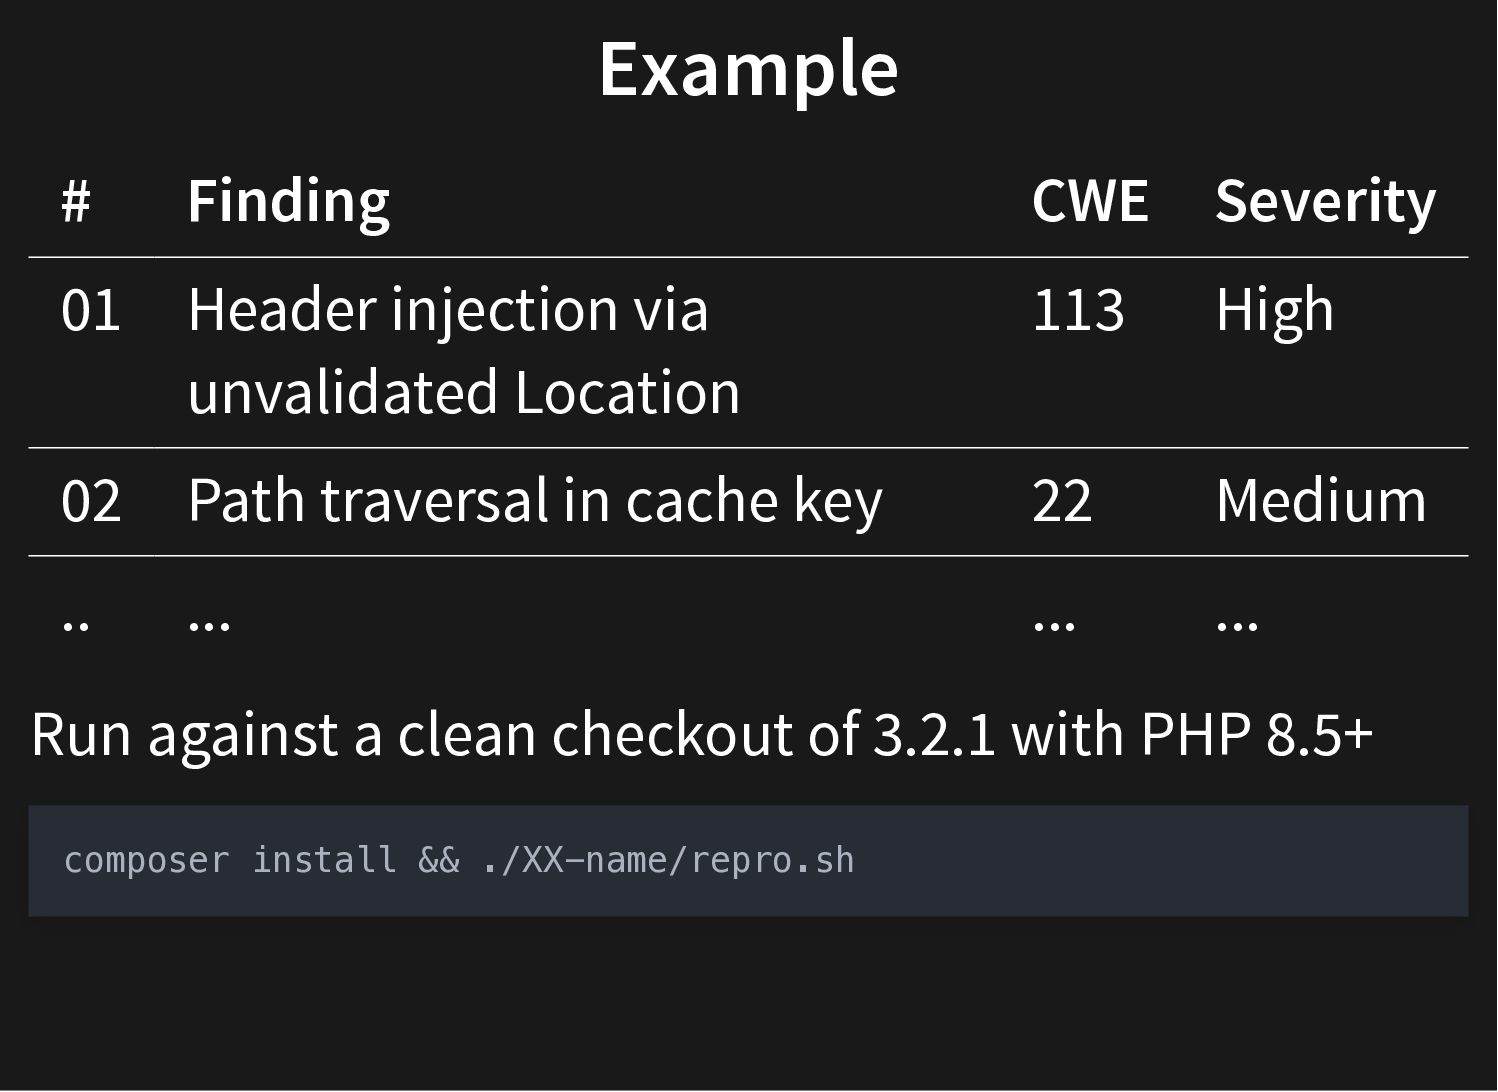
  21. Example # Finding CWE Severity 01 Header injection via unvalidated

    Location 113 High 02 Path traversal in cache key 22 Medium .. ... ... ... Run against a clean checkout of 3.2.1 with PHP 8.5+ composer install && ./XX-name/repro.sh
  22. Proactive security scanning You know your software best. Have a

    look at what the machines report. Run your own scans or work with people you trust. Avoid pressure, deadlines, and surprises.
  23. Reproduce safely Be ready to look at untrusted code. Evaluate

    what works for you. Docker Sandbox Full VM Throwaway cloud instances Dedicated machine The best approach is the one you actually will use. Targeted attacks do happen: https://blog.rust-lang.org/2026/09/17/targeted-attacks/
  24. Fix, Document, Define, Ignore Fix what needs fixing Hardening patches

    when it's not a security issue Document security boundaries E.g.: Only parse trusted input. Pre-sanitize filenames. Define your policy Put scope and threat model in your SECURITY.md Tell scanners what you don't care about Ignore/Close You owe nobody a rebuttal
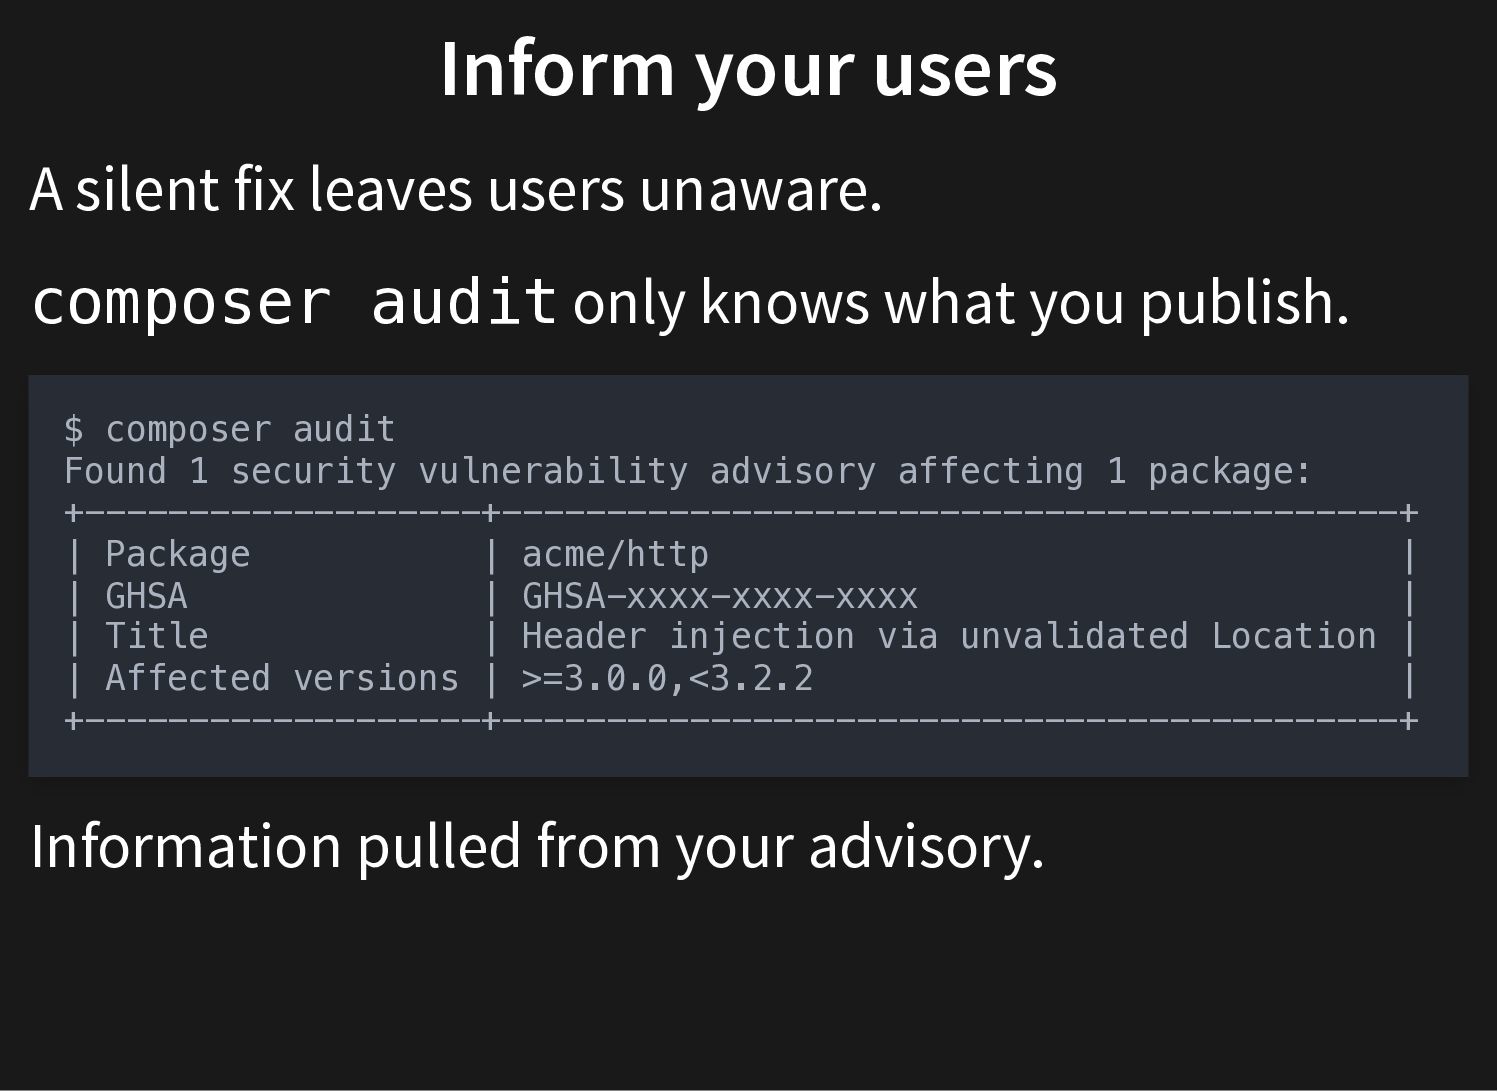
  25. Inform your users A silent fix leaves users unaware. composer

    audit only knows what you publish. $ composer audit Found 1 security vulnerability advisory affecting 1 package: +-------------------+-------------------------------------------+ | Package | acme/http | | GHSA | GHSA-xxxx-xxxx-xxxx | | Title | Header injection via unvalidated Location | | Affected versions | >=3.0.0,<3.2.2 | +-------------------+-------------------------------------------+ Information pulled from your advisory.
  26. Current troubles In our experience, requesting a CVE from GitHub

    can take 4 to 8 weeks. We have seen GHSA approval take 2 weeks. Delaying fixes due to paperwork is frustrating
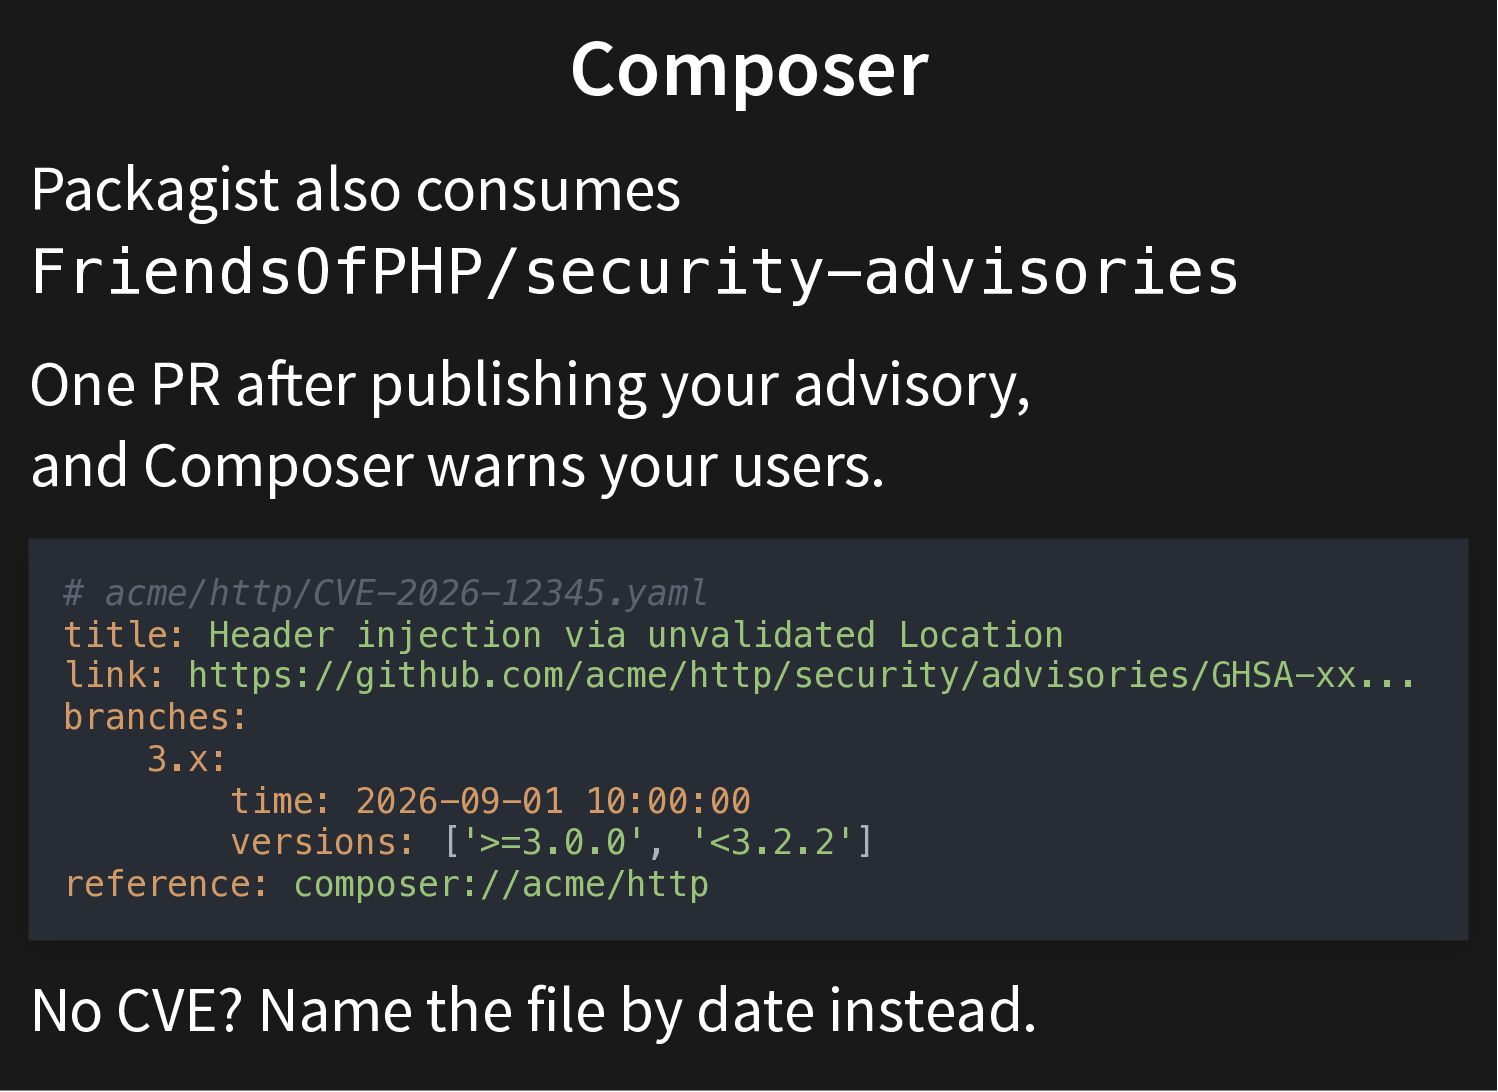
  27. Composer Packagist also consumes FriendsOfPHP/security-advisories One PR after publishing your

    advisory, and Composer warns your users. # acme/http/CVE-2026-12345.yaml title: Header injection via unvalidated Location link: https://github.com/acme/http/security/advisories/GHSA-xx... branches: 3.x: time: 2026-09-01 10:00:00 versions: ['>=3.0.0', '<3.2.2'] reference: composer://acme/http No CVE? Name the file by date instead.
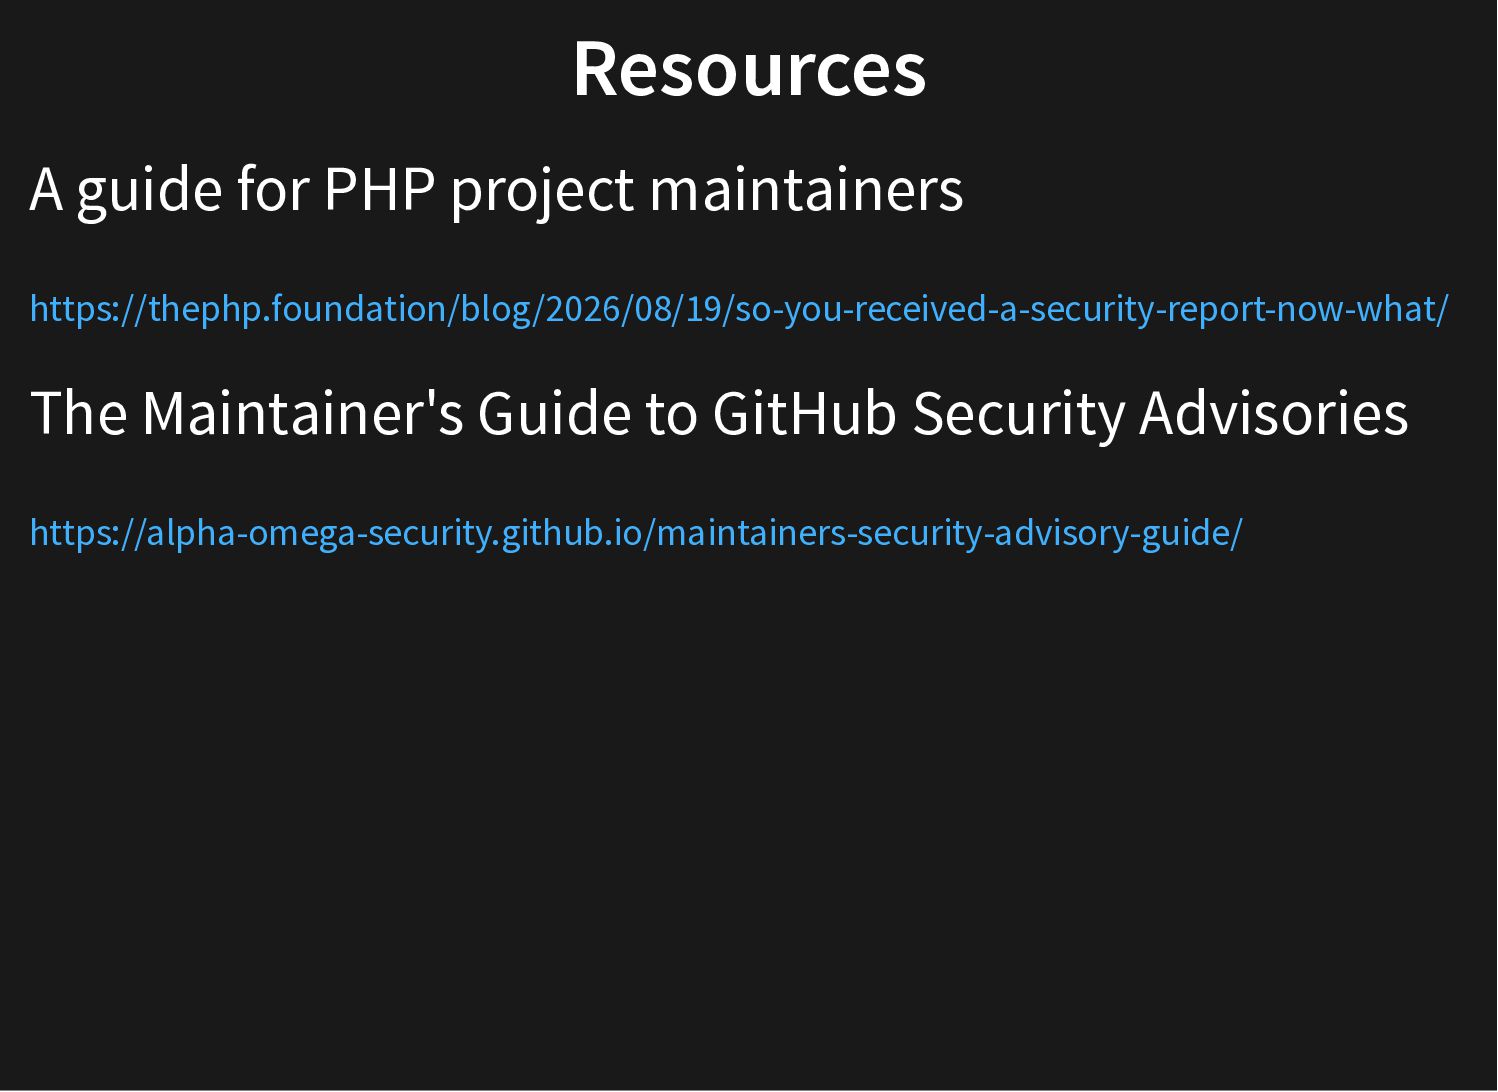
  28. Resources A guide for PHP project maintainers https://thephp.foundation/blog/2026/08/19/so-you-received-a-security-report-now-what/ The Maintainer's

    Guide to GitHub Security Advisories https://alpha-omega-security.github.io/maintainers-security-advisory-guide/
  29. Commercial Everyone is fixing things at the moment. Patch! OS:

    unattended-upgrades, or a rebuild pipeline Containers: Rebuild base images regularly PHP: Stay up to date Dependencies: composer update on a cadence Investment in your infrastructure is security.
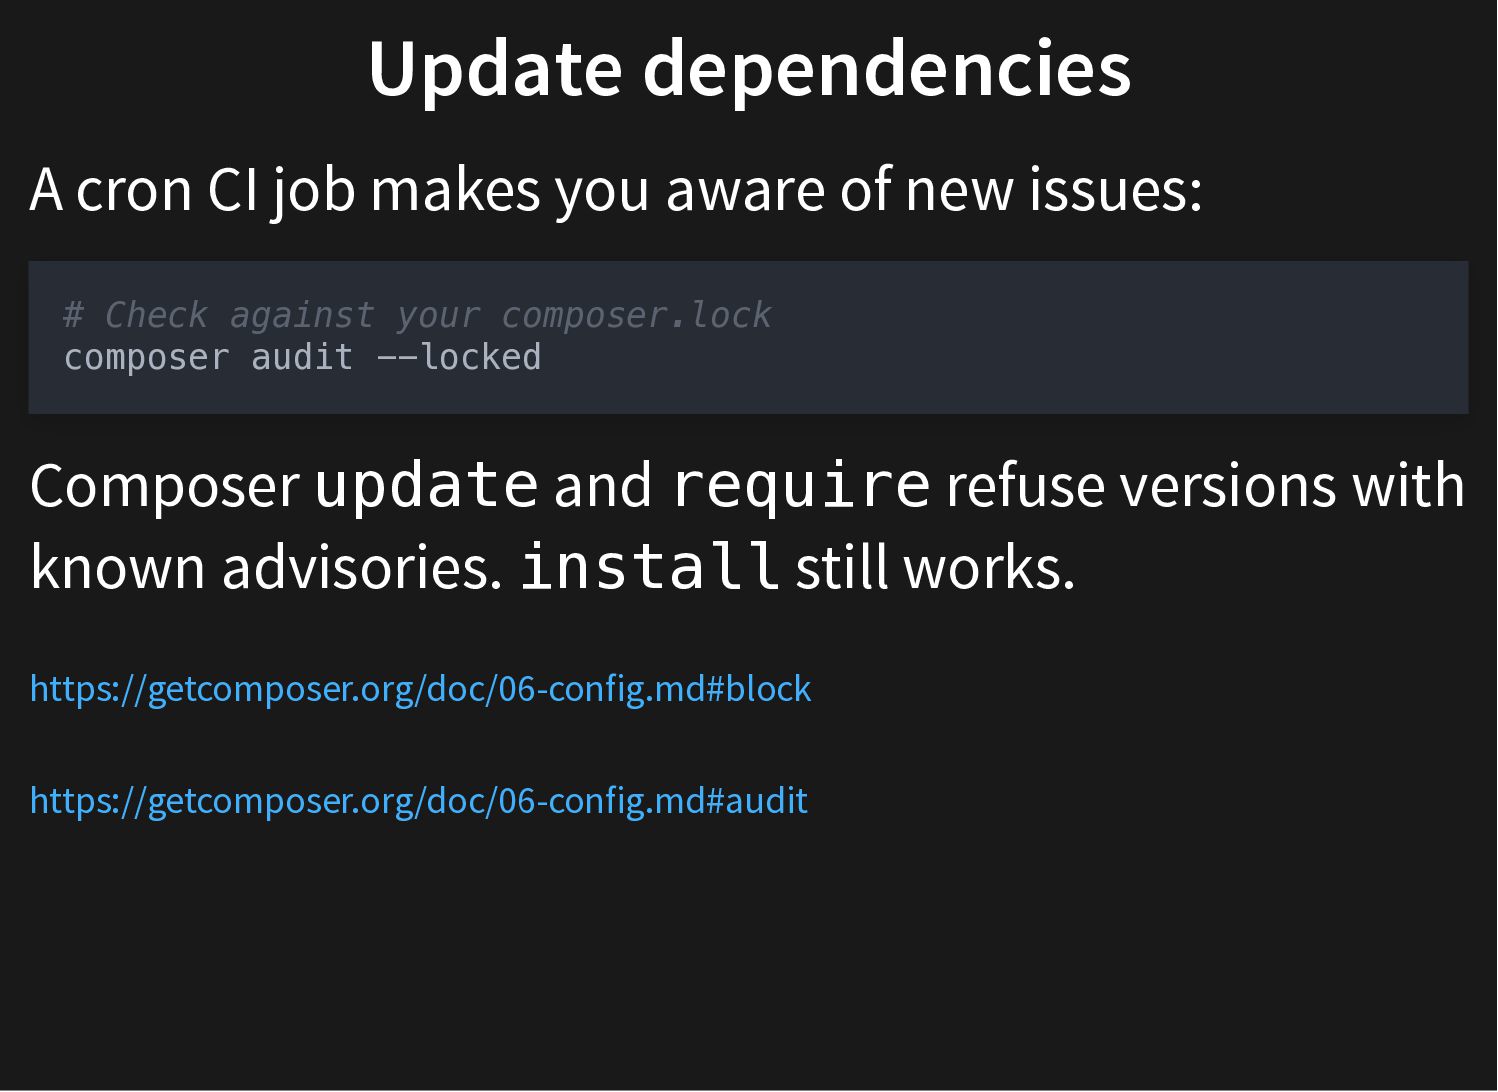
  30. Update dependencies A cron CI job makes you aware of

    new issues: # Check against your composer.lock composer audit --locked Composer update and require refuse versions with known advisories. install still works. https://getcomposer.org/doc/06-config.md#block https://getcomposer.org/doc/06-config.md#audit
  31. Private Packagist Proactive notifications Usage Tracking showing affected applications when

    a security advisory is released. https://packagist.com Support PHP's supply chain security
  32. First party approaches What you can do with a subscription

    https://openai.com/form/codex-for-oss/ https://claude.com/contact-sales/claude-for-oss Ad hoc review: Ask the agent Structured workflow skills: /security @Codex-Security Validating reports Full permission agent in a secure env
  33. The trouble with access Cybersecurity firms have unlocked models. The

    model AI companies sell you might just refuse to work on a security fix. Relaxed cyber safeguards: https://portal.anthropic.com/programs/cvp https://chatgpt.com/cyber Open-weight models as an alternative?
  34. Scrutineer A local tool for structured scanning Pluggable agent backends

    (Codex, Claude, OpenCode Uses your container infrastructure (Docker/Podman) Local web UI Workflow automation Custom SKILL support https://github.com/alpha-omega-security/scrutineer/
  35. How a Scrutineer scan works 1. Add a repository or

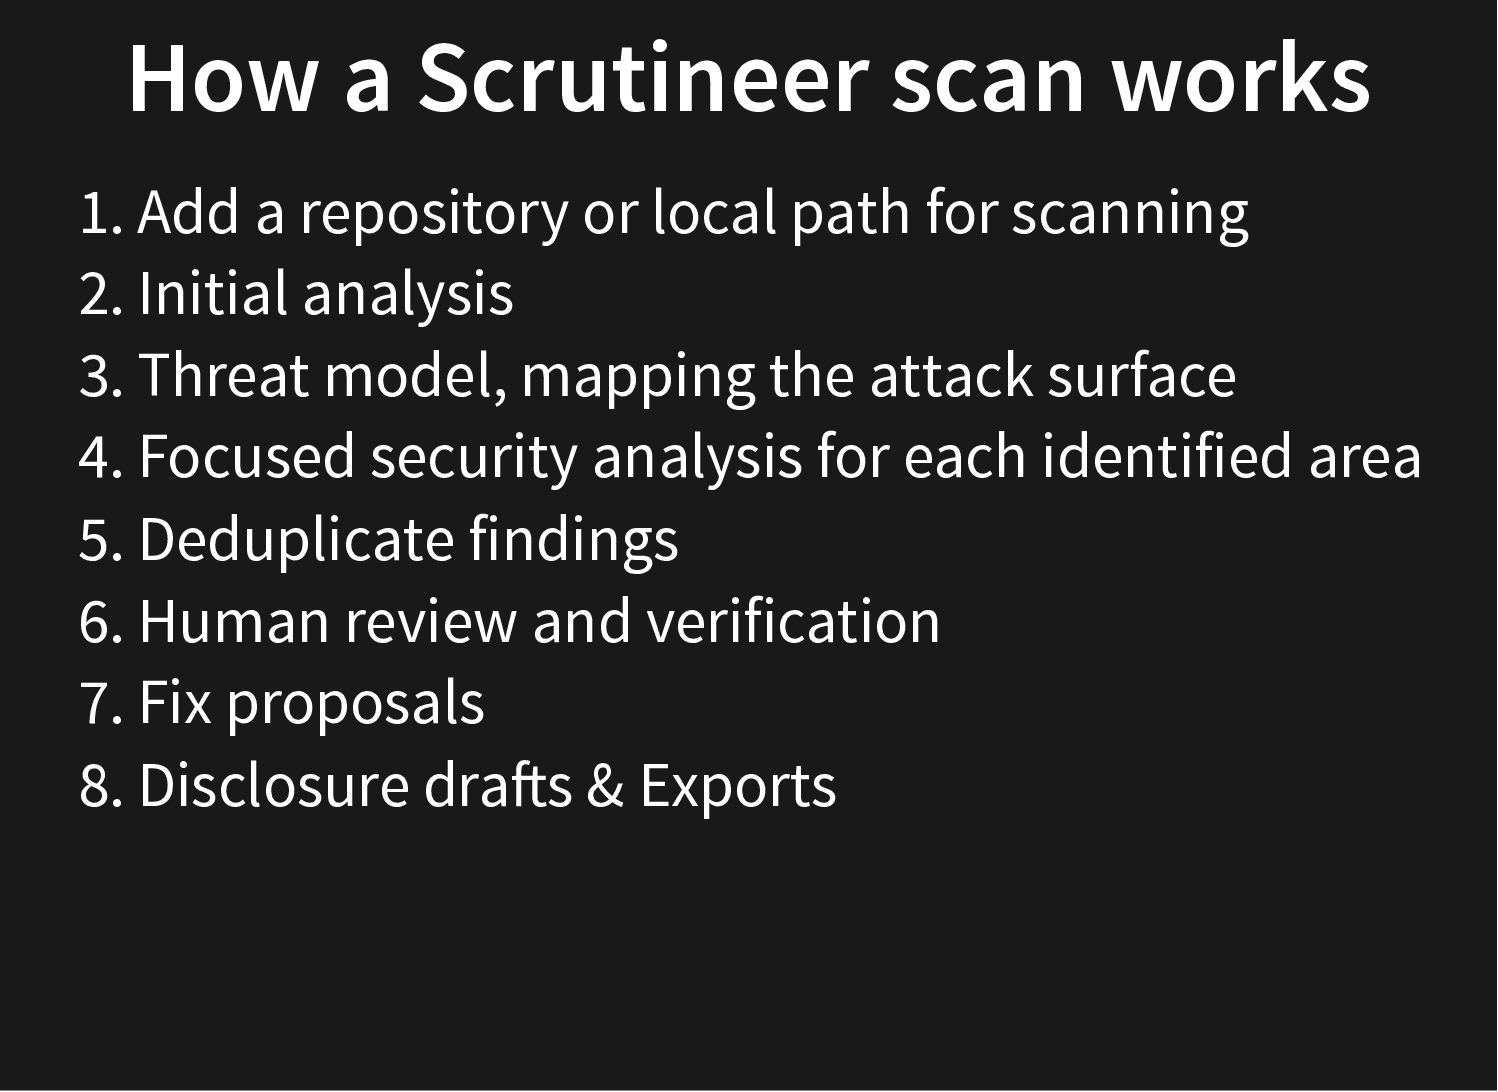
    local path for scanning 2. Initial analysis 3. Threat model, mapping the attack surface 4. Focused security analysis for each identified area 5. Deduplicate findings 6. Human review and verification 7. Fix proposals 8. Disclosure drafts & Exports
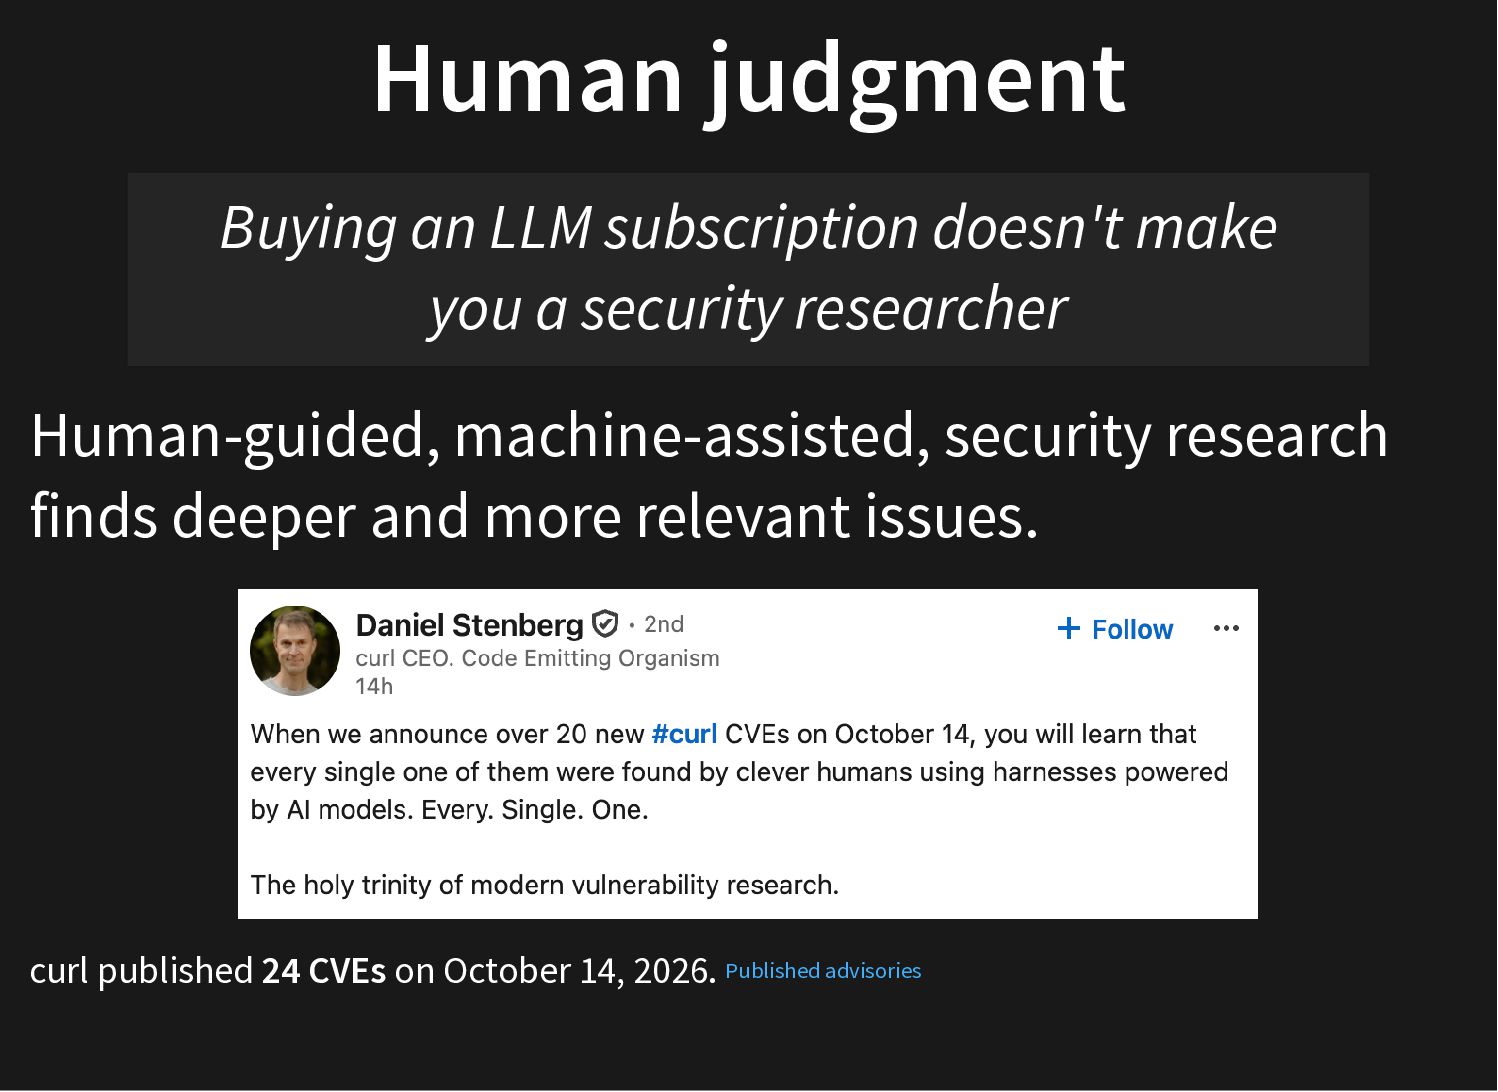
  36. Human judgment Buying an LLM subscription doesn't make you a

    security researcher Human-guided, machine-assisted, security research finds deeper and more relevant issues. curl published 24 CVEs on October 14, 2026. Published advisories
  37. Fixes are even harder In our reviews, ~50% of machine-suggested

    fixes are just wrong. Finding issues is easier than fixing them.
  38. Three things to take home Maintainers: automate your releases, document

    your boundaries, scan proactively. Teams shipping PHP: composer audit in CI, patch on a schedule, know your dependency graph. "The bugs are old, the pace is new." Talk to your business leaders about AI & Security.
  39. Things might be less fun right now This too shall

    pass. In a few years it might look like nothing much happened. Thanks to you.
  40. Thank you! Slides: https://speakerdeck.com/edorian Anything I can help with? Talk

    to me today! Reach out later: [email protected] Discord: #ecosystem-security@phpc Invite: https://discord.com/invite/RYajXKxuuK

More Decks by Volker Dusch

Other Decks in Programming