Share
Embed
Fixing PHP2Shell
This talk reflects on the PHP2Shell vulnerability, telling the full story of what happened and discussing its impact and why it gained so much attention.
We will cover the whole process, from what led to its discovery to testing and validation to remediation and how the PHP team coordinated and rolled out the fix.
Discussion will include how agentic security research combined with human expertise led researchers to the exploit and how LLMs are changing the landscape of security going forward.
We will reflect on lessons learned, share advice for other projects and the wider PHP ecosystem, and provide practical suggestions for organizations and projects.
Volker Dusch
November 13, 2026
Transcript
52 slides
-
Fixing PHP2Shell Volker "edorian" Dusch Ecosystem Security Lead at The
PHP Foundation PHP 8.5 Release Manager Head of Engineering at Tideways Berlin PHP UserGroup 2026 -
My background ~20 years of PHP Working at Tideways on
PHP performance tooling PHP 8.5 Release Manager Ecosystem Security Lead at The PHP Foundation Thank you to Tideways for making this work possible. -
How did we get here? In March, the Linux Foundation
announced a grant to strengthen open source security. https://www.linuxfoundation.org/press/linux-foundation-announces-12.5-million-in-grantfunding-from-leading-organizations-to-advance-open-source-security Alpha-Omega’s mission is to protect society by catalyzing sustainable security improvements across open source. https://alpha-omega.dev/ -
Ecosystem Security The grant funded the new Ecosystem Security Team
at The PHP Foundation. Our goal: Secure the PHP ecosystem and support maintainers. It's open source and it's PHP? We're here for you! https://thephp.foundation/blog/2026/05/18/announcing-ecosystem-security-team/ -
Ecosystem Security work Part of what we're doing: Scan projects
Inform maintainers of issues in a sustainable way High-quality reports No deadlines, no pressure Create guides Help people deal with reports Respond to all requests from the ecosystem -
Reaching out to auditors I also worked on soliciting audits
for php-src, our frameworks and our critical libraries. E.g. early Mythos audits from OSTIF Scanning Symfony and Laravel when the model was still hard to access. Big personal thank you to Derek Zimmer for those. -
The audit that found PHP2Shell I reached out to Patch
the Planet for php-src. Calif got in touch, and we set up a PHP audit. Ryan at Calif, familiar with PHP, leveraging LLMs, begins his work. -
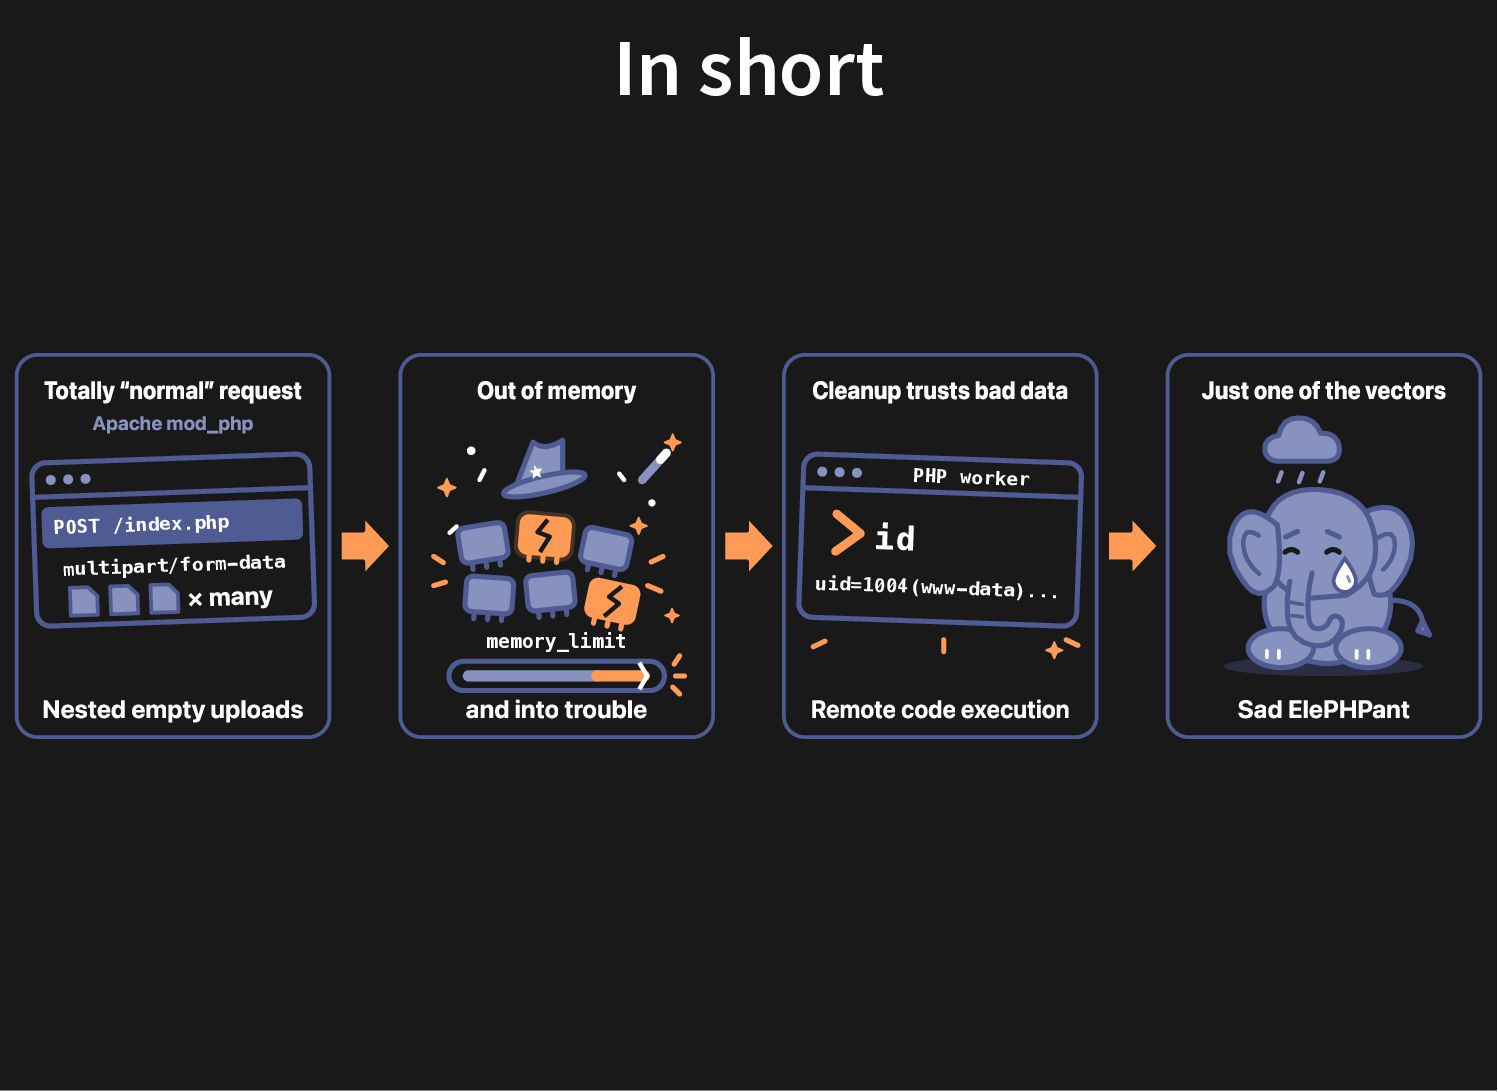
What is PHP2Shell? Engine-level vulnerability. Attackers can execute code on
servers running PHP. Hit memory_limit at the wrong moment, and PHP trusts half-initialized data. OOM errors longjmp() out of the error handler in zend_bailout(). The code in the calling function never finishes. https://ilia.ws/blog/php2shell-two-ways-php-corrupts-its-own-memory -
From longjmp() to RCE 1. A request hits memory_limit during
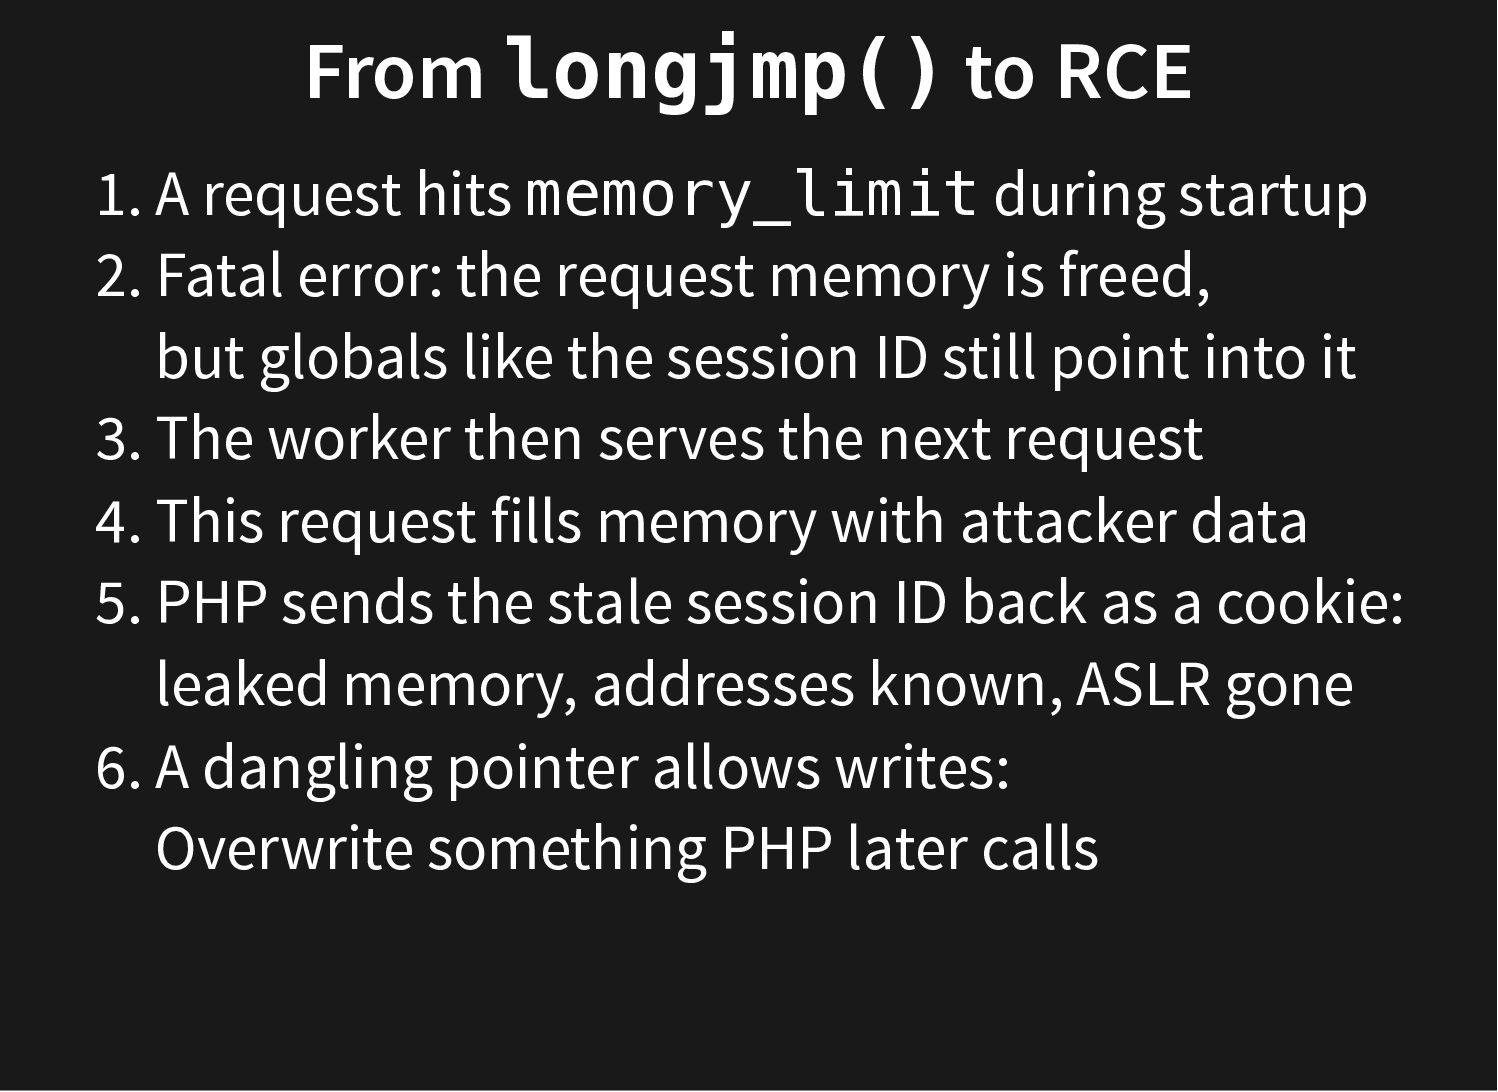
startup 2. Fatal error: the request memory is freed, but globals like the session ID still point into it 3. The worker then serves the next request 4. This request fills memory with attacker data 5. PHP sends the stale session ID back as a cookie: leaked memory, addresses known, ASLR gone 6. A dangling pointer allows writes: Overwrite something PHP later calls -
RCE Put a call to system('id; ...') into that memory
location: Remote code execution. https://calif.io/php2shell/ https://www.wiz.io/blog/php2shell-php-rce -
In short Totally “normal” request Apache mod_php Out of memory
Cleanup trusts bad data Just one of the vectors PHP worker POST /index.php id multipart/form-data × many uid=1004(www-data)... memory_limit Nested empty uploads and into trouble Remote code execution Sad ElePHPant -
2024 - OSTIF/Quarkslab Audit Big security audit of php-src thanks
to the Sovereign Tech Fund A lot of fixes were released. https://ostif.org/php-audit-complete/ https://blog.quarkslab.com/security-audit-of-php-src.html -
Early signs During one of these fixes, a php-src developer
found the first signs of the OOM problem. No concrete exploit. No proven problems. Several possible ideas for fixes, each with trade-offs and BC considerations. Meanwhile: Tons of concrete work and things to fix from the audit and other reports. These got priority. -
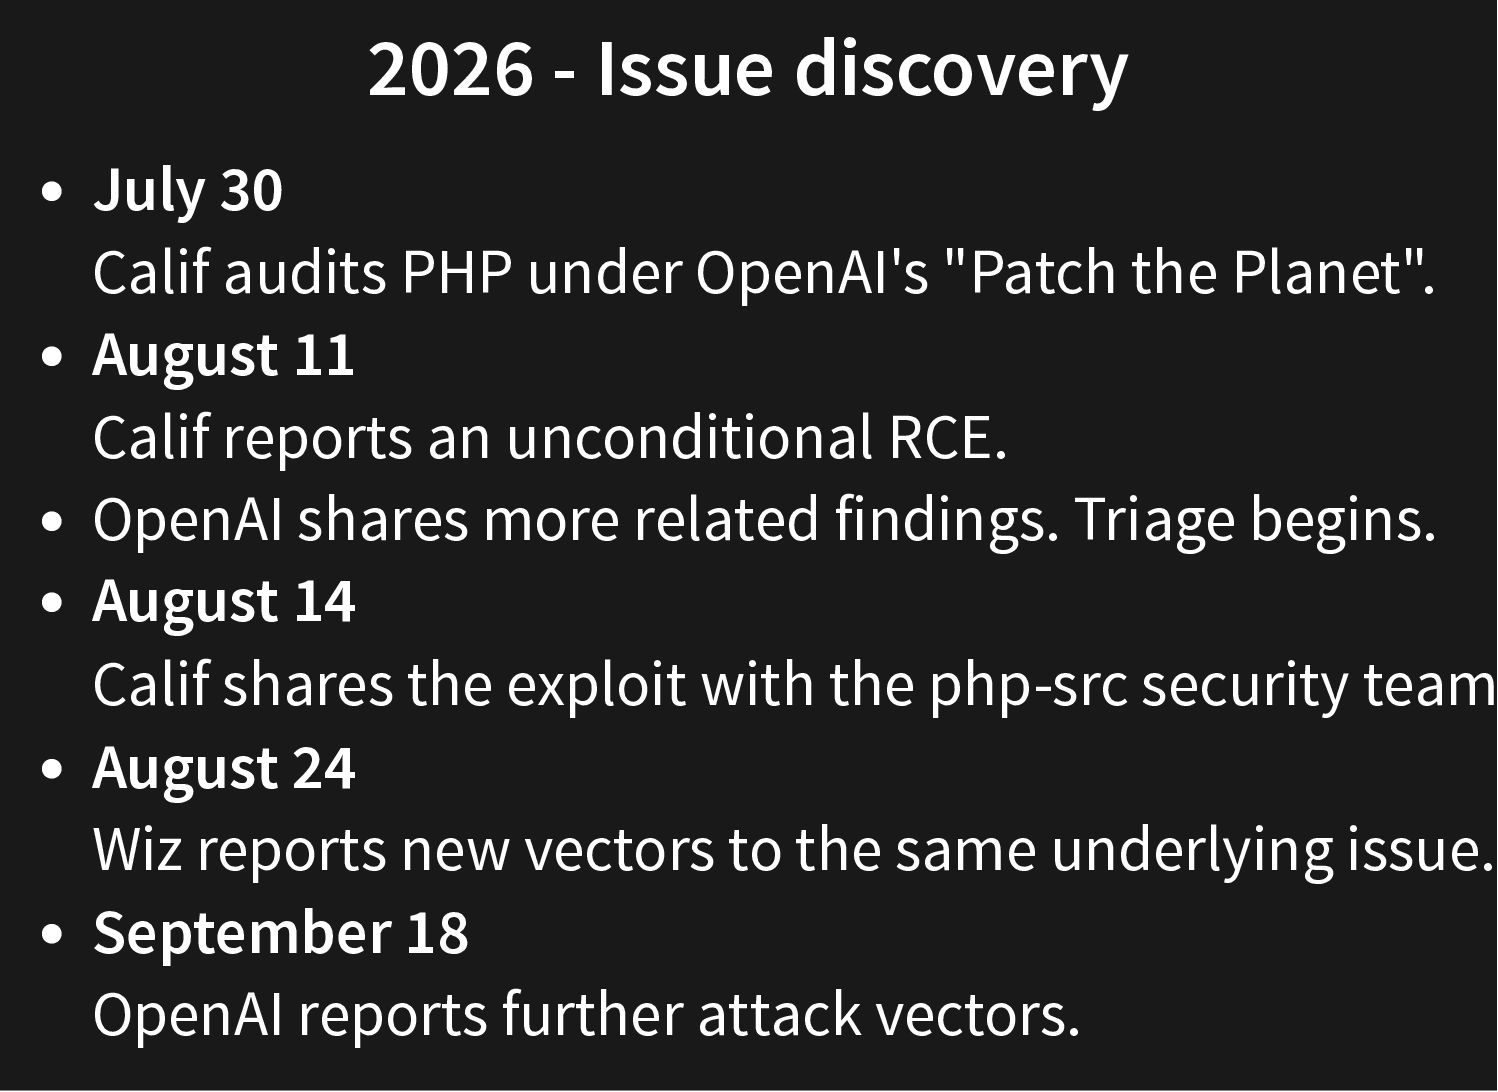
2026 - Issue discovery July 30 Calif audits PHP under
OpenAI's "Patch the Planet". August 11 Calif reports an unconditional RCE. OpenAI shares more related findings. Triage begins. August 14 Calif shares the exploit with the php-src security team August 24 Wiz reports new vectors to the same underlying issue. September 18 OpenAI reports further attack vectors. -
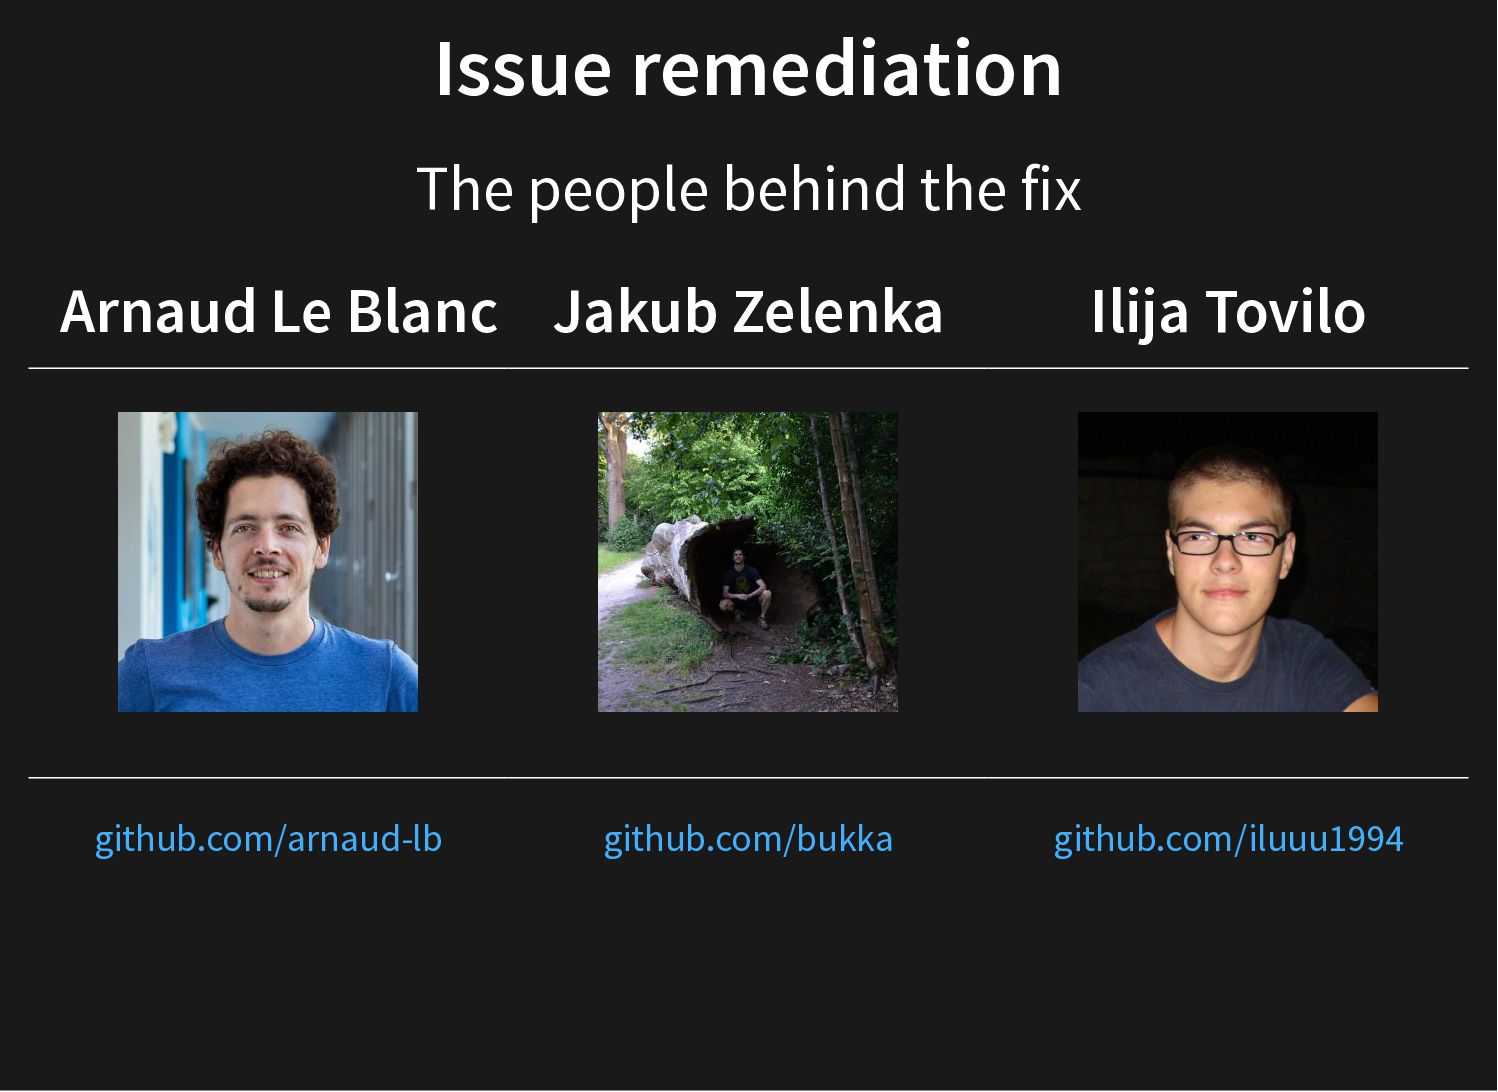
Issue remediation The people behind the fix Arnaud Le Blanc
Jakub Zelenka github.com/arnaud-lb github.com/bukka Ilija Tovilo github.com/iluuu1994 -
Issue remediation Many weeks of focused work. All funded by
The PHP Foundation. A proper fix needed full-time people. I did the coordination work and helped with scanning. Ilija, Arnaud and Jakub did the complicated technical details, diligently. -
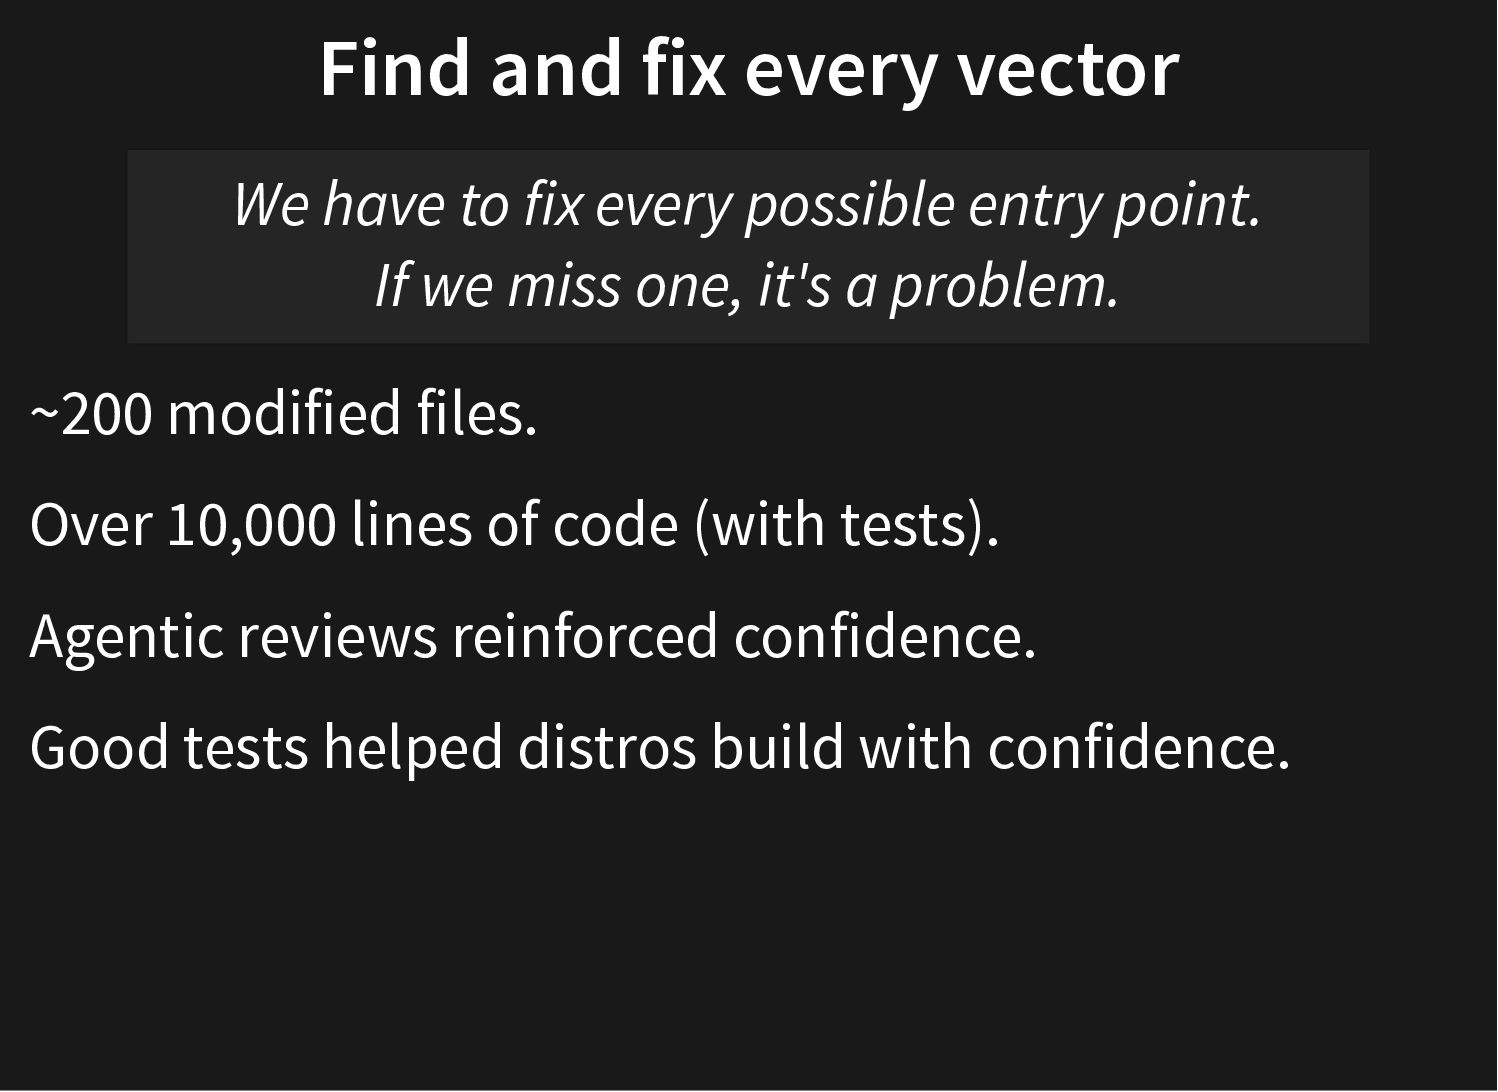
Find and fix every vector We have to fix every
possible entry point. If we miss one, it's a problem. ~200 modified files. Over 10,000 lines of code (with tests). Agentic reviews reinforced confidence. Good tests helped distros build with confidence. -
Working with security teams A team of experts to rely
on was a massive help. Daily sync calls in the weeks leading up to the release. Working with people using LLMs for security research every day. Different harnesses, different ideas. Every change got validated by their models. OpenAI provided access and credits to help us doublecheck our own work. -
Communication How the Slack interactions went: No AI in the
communication. No meeting transcripts. People paid attention, took notes and followed up on things. The people using AI to find the bugs didn't use it to talk to each other or to make decisions. -
Informing governments We informed CISA and ENISA and others ahead
of time. They pass it on to national CERTs and partners. https://www.cisa.gov/news-events/alerts/2026/10/21/critical-vulnerabilities-php-requireimmediate-patching https://enisa.europa.eu/news/joint-statement-on-critical-php-vulnerabilities -
On release day CISA alert, with NSA, NCSC UK, Canada,
Australia, New Zealand and the Netherlands Joint EU statement: ENISA, CERT-EU, Europol and the CSIRTs Network ENISA: "consider isolating exposed applications from public networks until fixes can be applied" BSI: Warnstufe 3 / Orange -
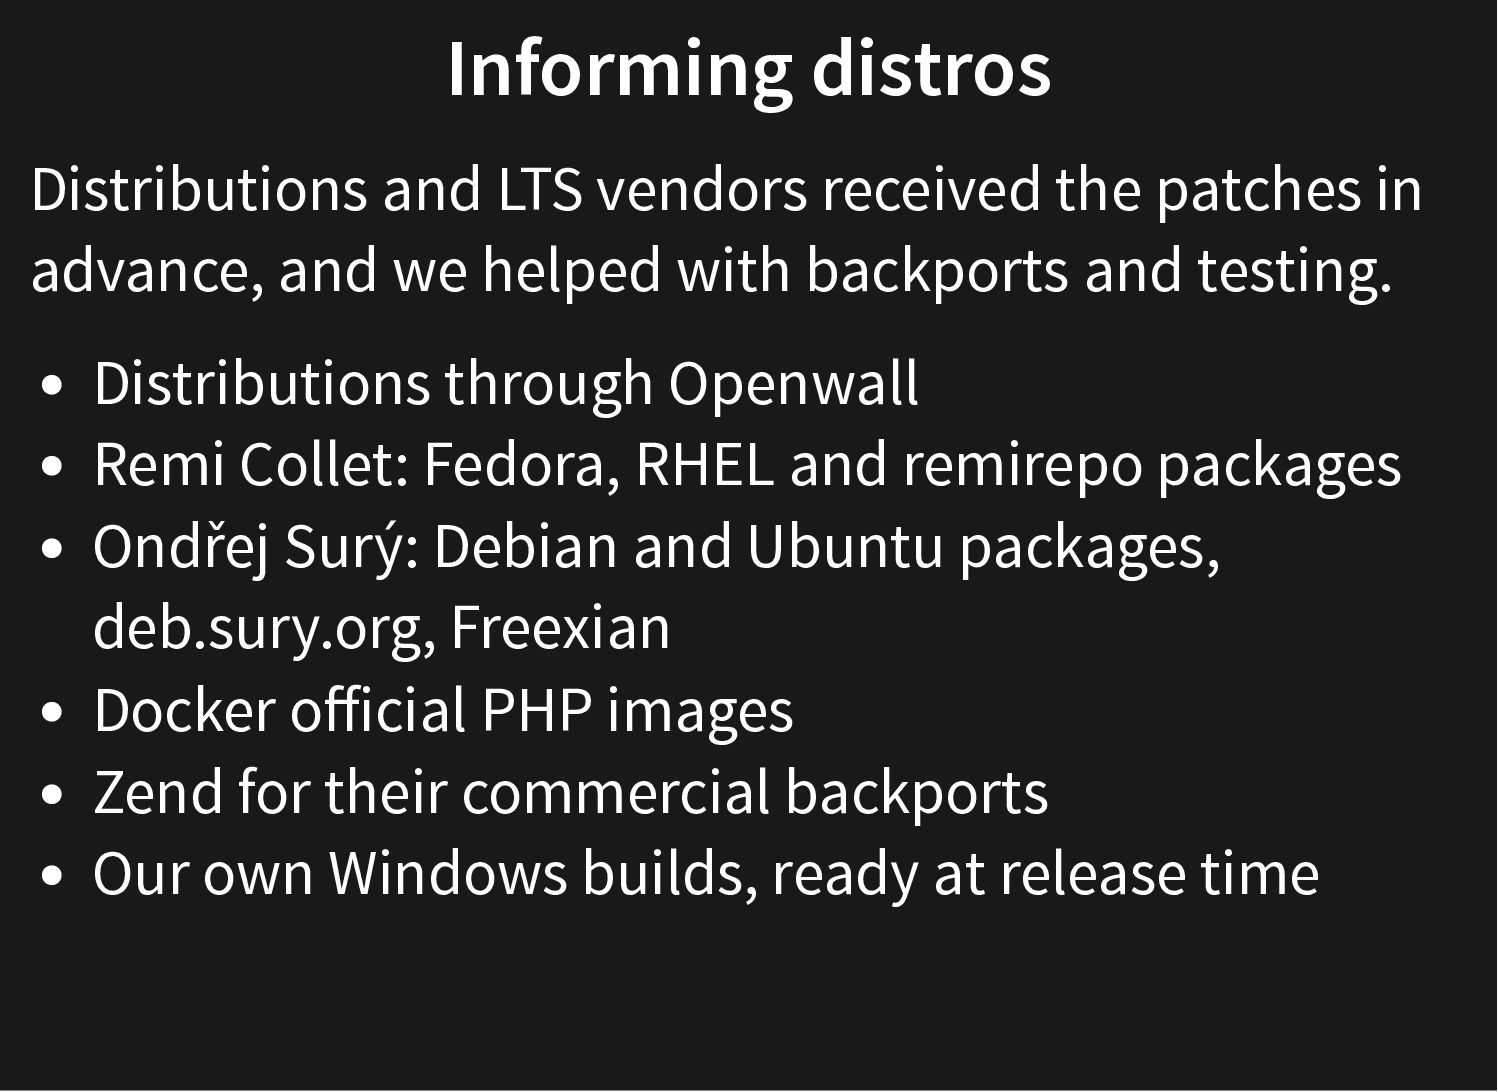
Informing distros Distributions and LTS vendors received the patches in
advance, and we helped with backports and testing. Distributions through Openwall Remi Collet: Fedora, RHEL and remirepo packages Ondřej Surý: Debian and Ubuntu packages, deb.sury.org, Freexian Docker official PHP images Zend for their commercial backports Our own Windows builds, ready at release time -
Monitoring the situation We got in touch with WAF vendors.
Pre-established mutual non-disclosure agreements (mNDAs) from Wiz helped a lot in reaching everyone. They helped with early detection and mitigation. Looking for in-the-wild exploitation attempts. Michael Winser from Alpha-Omega had brought up the idea of doing this with me a while back. -
Prepared for a potential leak With more people in the
loop, a leak was more likely. So we prepared. Announcement drafted Mitigations written Release tags and tarballs built on Monday A plan for moving the date -
Tuesday, October 20 ~15:00 UTC CVE IDs are leaked. "Wrong"
details, CVSS of 10.0. We were prepared and discussed our options. Zero reports of in-the-wild exploitation. 19:30 UTC Announcement: release tomorrow. A good balance of informing defenders while not giving attackers too much time to develop exploits. -
Wednesday, October 21 Release Through the work up to that
point we were well prepared, had time to coordinate and the opportunity to protect users. -
The days after Screenshots of "working exploits" everywhere. Many only
worked against specially modified Docker containers or other shortcuts the AIs took. My agent said it's working! So it's real! Others claimed it's impossible to exploit. -
Media management I prepared a small media strategy for the
team. No live interviews. We lack the media training for that. Have background calls with journalists. Tell our story. Approve quotes. Help them get the facts correct. People are always looking for a human angle for the story. Give them a genuine one. Tell your story. Everything else is up to them. We can't control what people will make of it. Just be truthful. Worked well for us. -
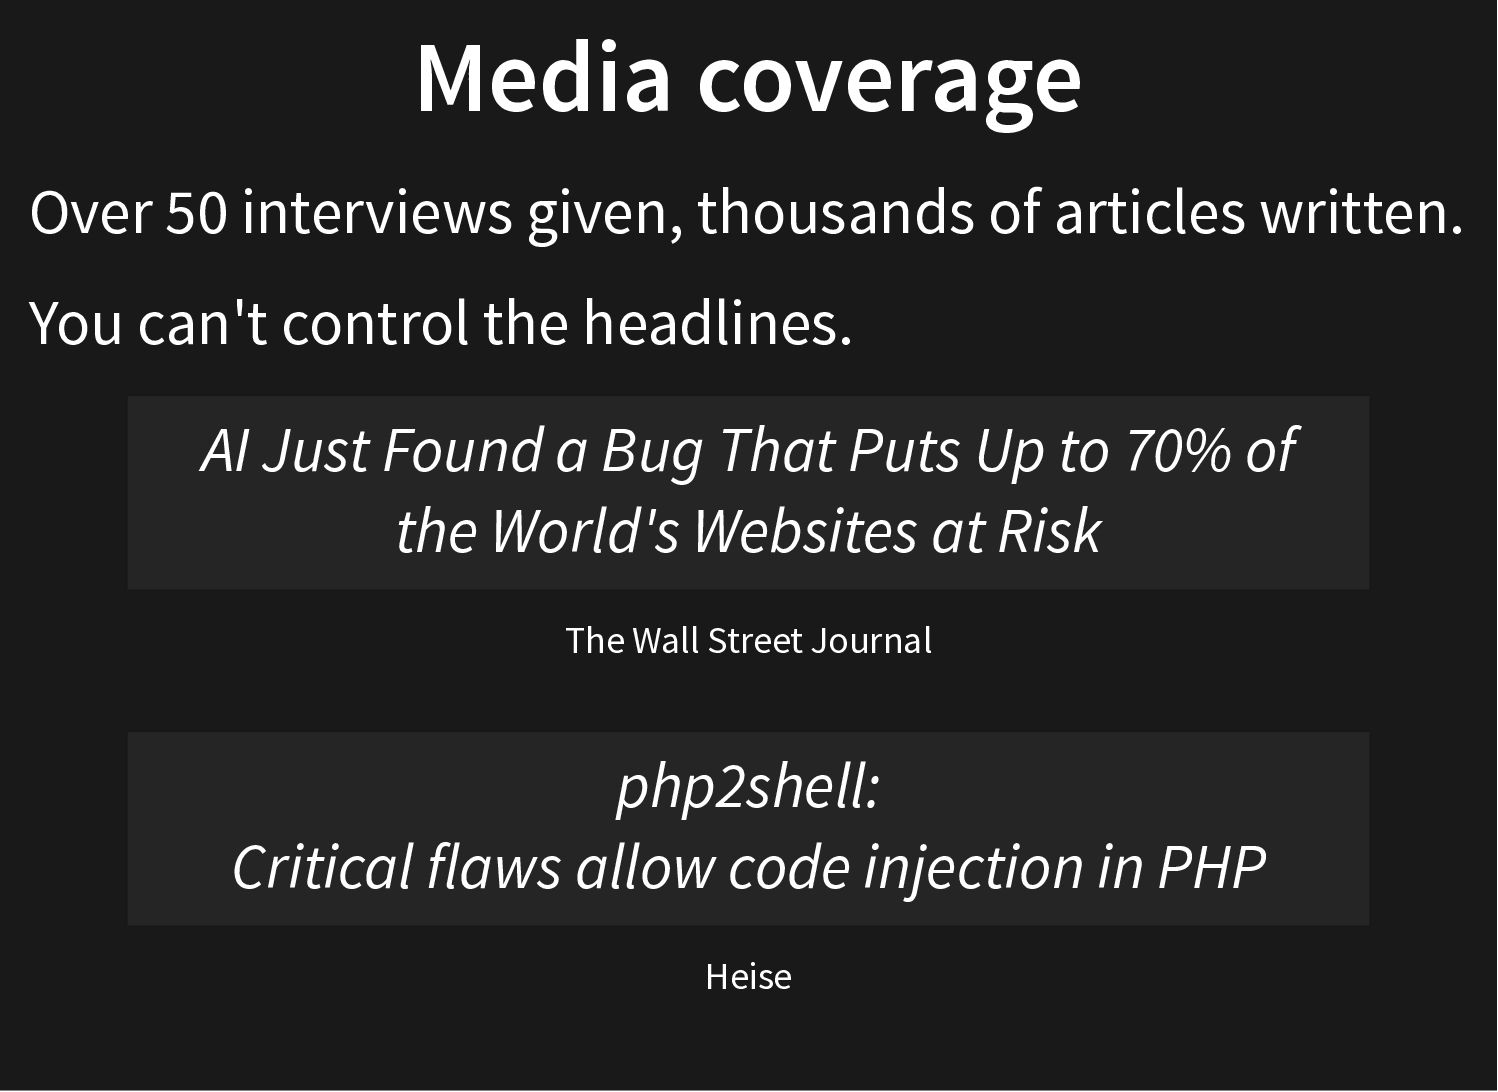
Media coverage Over 50 interviews given, thousands of articles written.
You can't control the headlines. AI Just Found a Bug That Puts Up to 70% of the World's Websites at Risk The Wall Street Journal php2shell: Critical flaws allow code injection in PHP Heise -
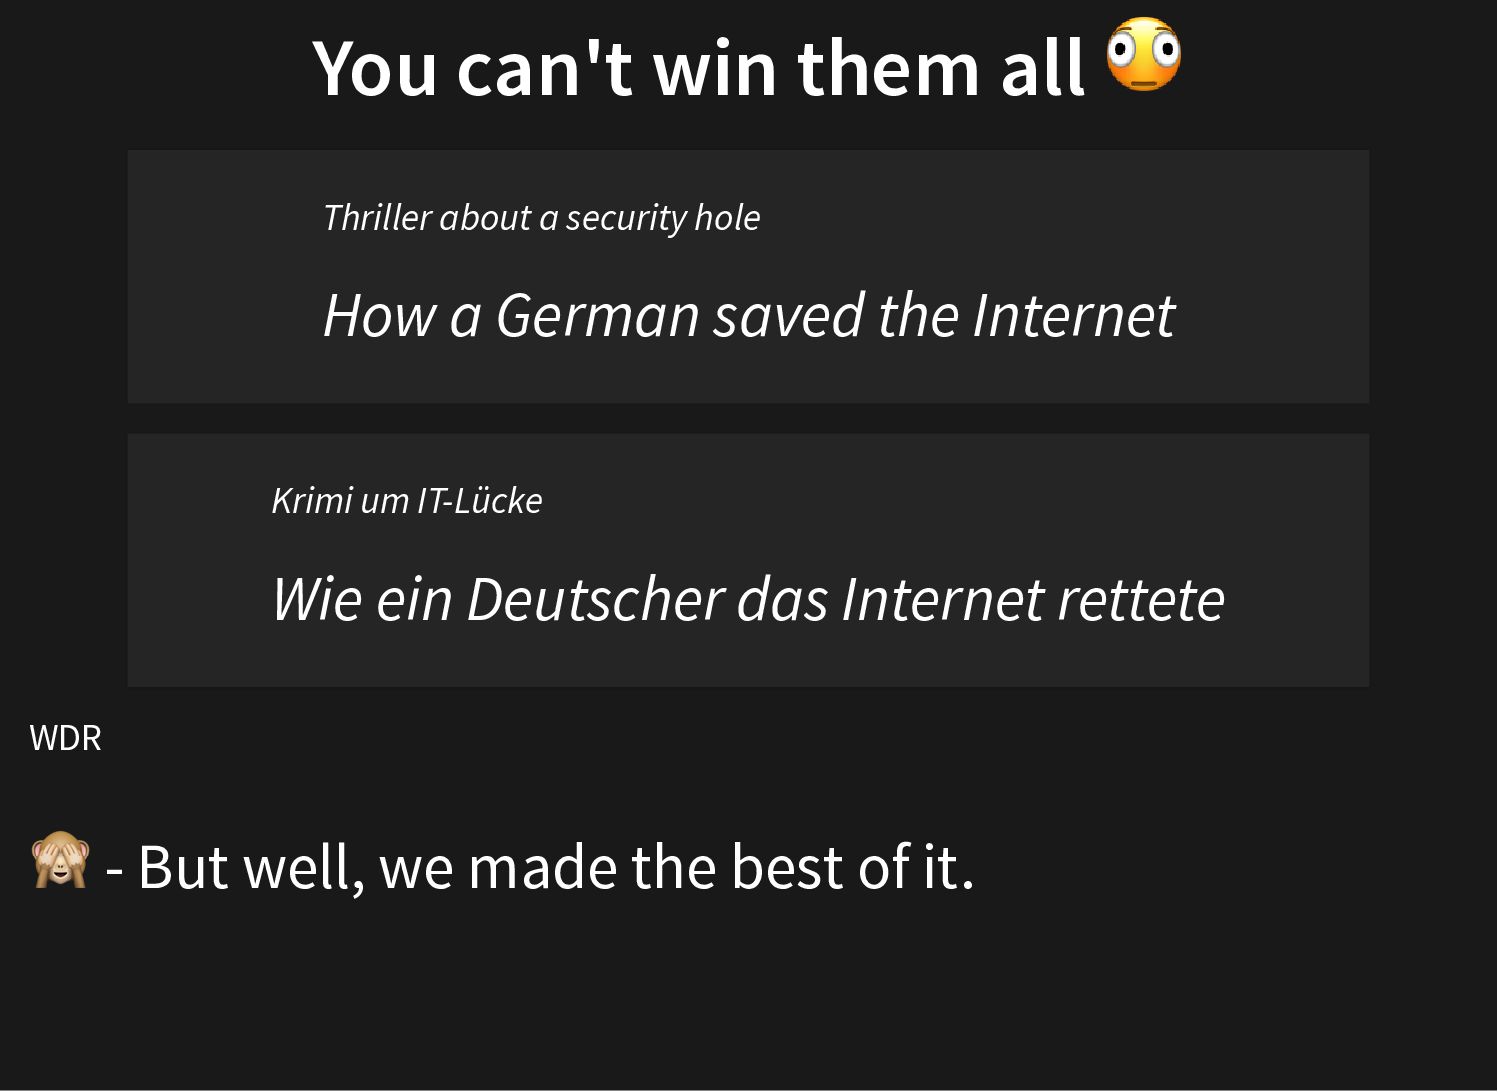
You can't win them all Thriller about a security
hole How a German saved the Internet Krimi um IT-Lücke Wie ein Deutscher das Internet rettete WDR 🙈 - But well, we made the best of it. -
But you can win some Genuine quotes humanized the whole
affair. Einer muss es ja machen. Well, someone's gotta do it. -
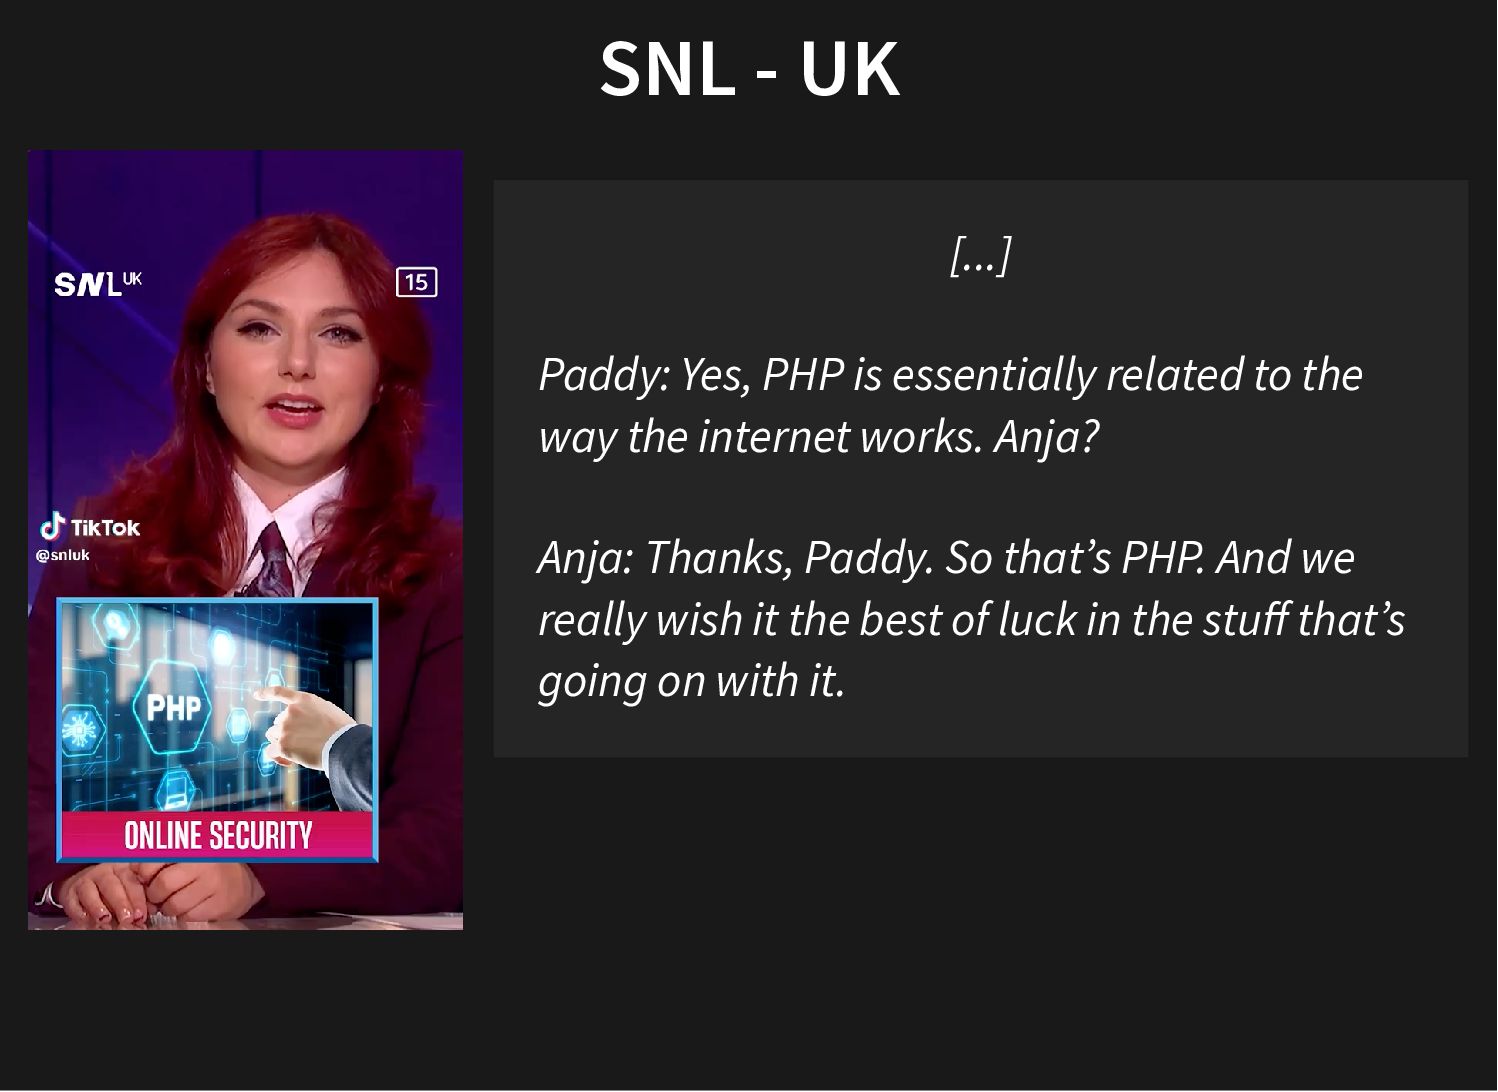
SNL - UK [...] Paddy: Yes, PHP is essentially related
to the way the internet works. Anja? Anja: Thanks, Paddy. So that’s PHP. And we really wish it the best of luck in the stuff that’s going on with it. -
Why so much attention? PHP matters. We took this seriously
and informed everyone who needed to know. A named vulnerability with a website. "Up to 70% of the world's websites". "AI found it". Governments gave the advice to turn off systems. -
Industry reactions Very positive feedback from the PHP community. Kind
sentiment from the rest of the internet as well. Sure, there are always some outliers, but I'm happy with the response and our work. Lots of love from other language communities. Everyone paying even the slightest attention knows this is an industry-wide effort. -
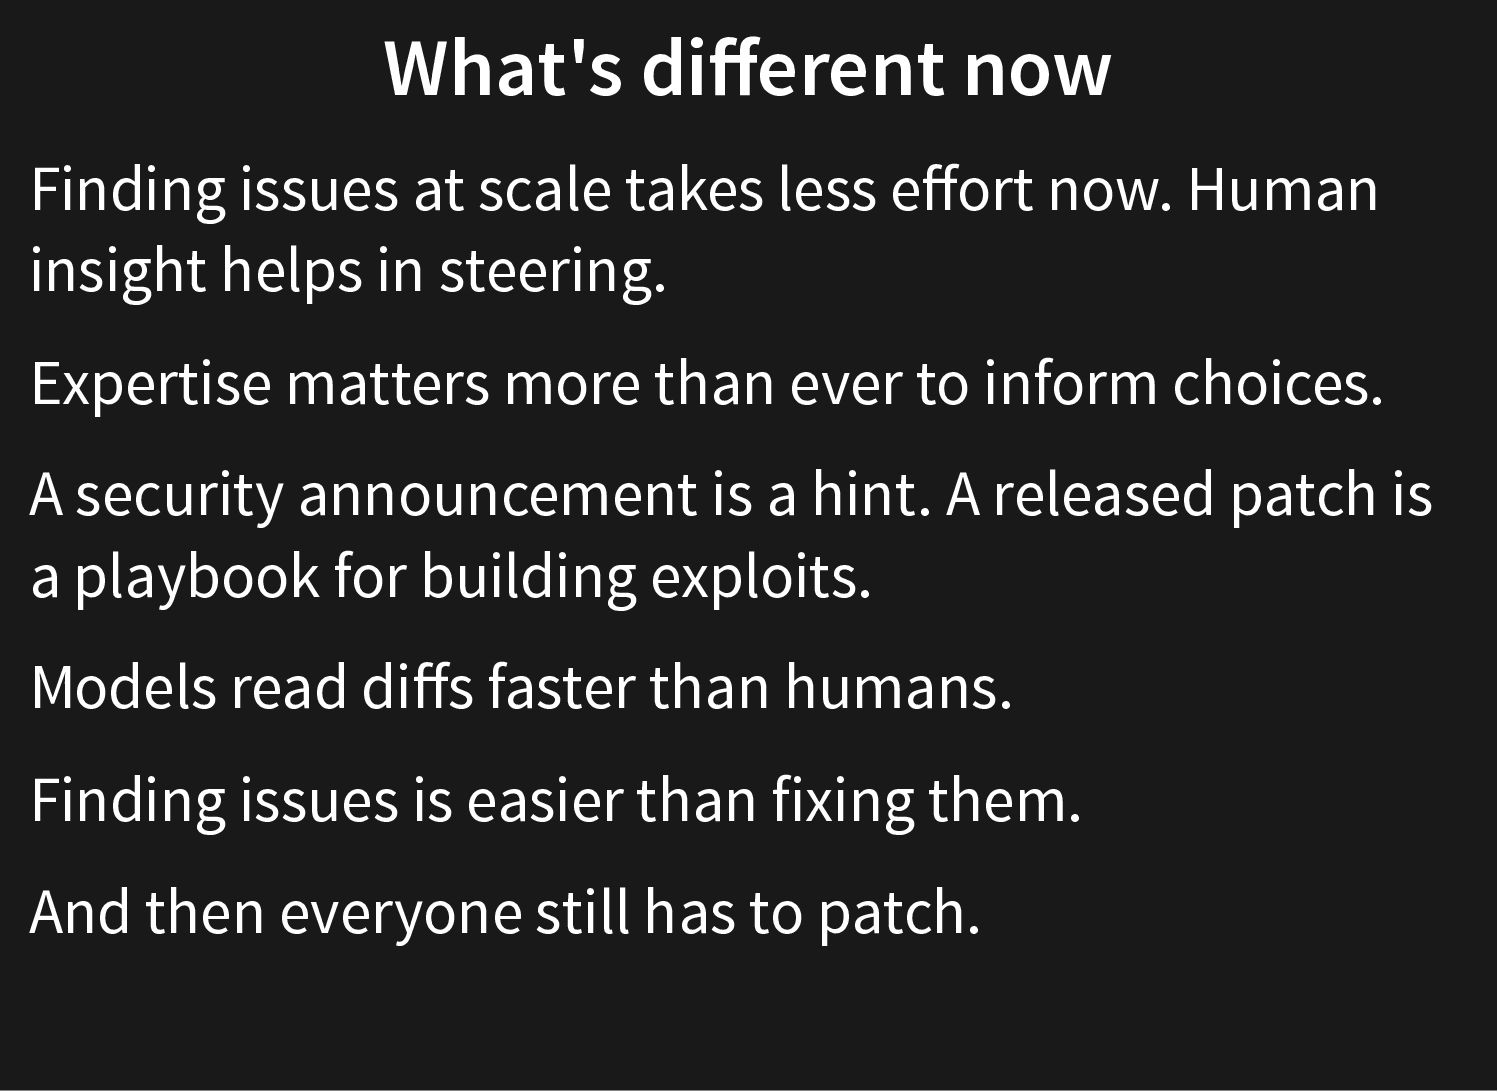
What's different now Finding issues at scale takes less effort
now. Human insight helps in steering. Expertise matters more than ever to inform choices. A security announcement is a hint. A released patch is a playbook for building exploits. Models read diffs faster than humans. Finding issues is easier than fixing them. And then everyone still has to patch. -
Now every day is patch day Happy #CyberSecurityAwarenessMonth 2026! October
2026 & November 2026 & December 2026 (most likely) -
So much happened GitLab CVE-2026-97229 Integer Overflow issue in Regular
Expression Compiler allows for Remote Code Execution Ruby response https://www.ruby-lang.org/en/news/2026/10/23/regexp-fixes-for-gitlab-cves/ -
And now everyone together! Node CVE-2026-111497, Python, .NET, ... Out-of-bounds
write in the Brotli decoder. Remote code execution. -
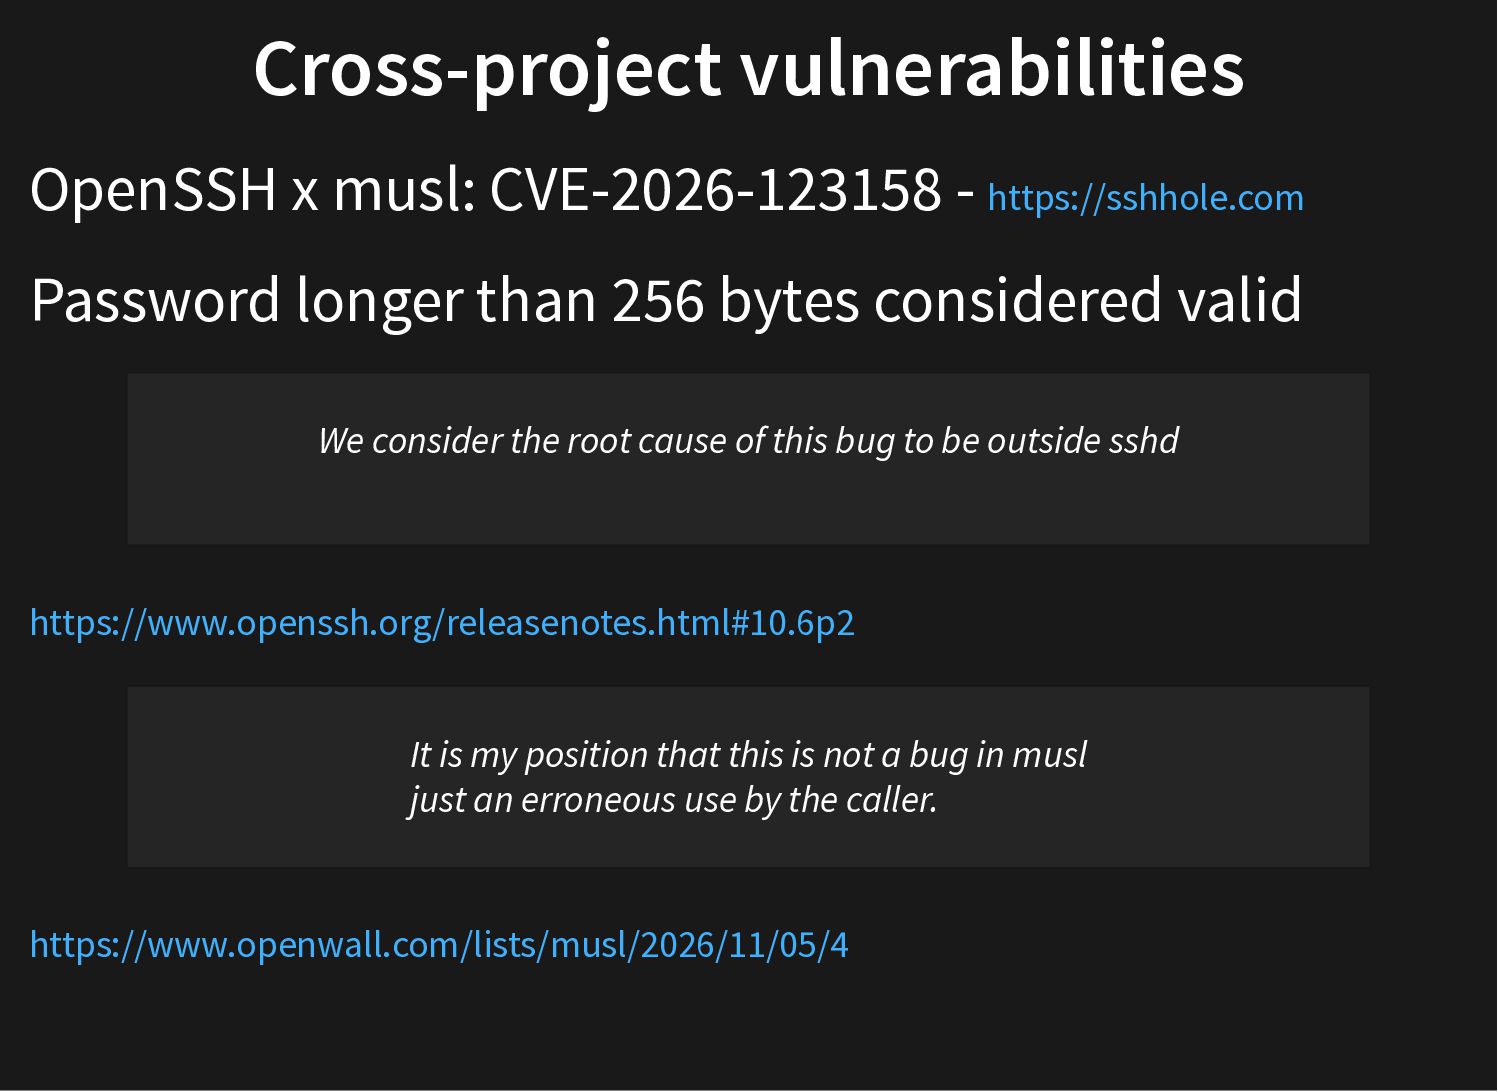
Cross-project vulnerabilities OpenSSH x musl: CVE-2026-123158 - https://sshhole.com Password longer
than 256 bytes considered valid We consider the root cause of this bug to be outside sshd https://www.openssh.org/releasenotes.html#10.6p2 It is my position that this is not a bug in musl just an erroneous use by the caller. https://www.openwall.com/lists/musl/2026/11/05/4 -
Open source projects Be prepared Fully automate your release process
Get audits/scans proactively Nobody cares more about your project than you Inform your users Help people update what matters A guide the Foundation prepared: https://thephp.foundation/blog/2026/08/19/so-you-received-a-security-report-now-what/ -
Organizations Everyone is fixing things at the moment. Patch! OS:
unattended-upgrades or a rebuild pipeline. Containers: Rebuild base images regularly. PHP: Stay up to date. Libraries and frameworks: Get on supported versions. Not every fix is announced: Update regularly. Investment in your infrastructure is security. -
Support PHP Sponsoring the PHP Foundation is the most direct
way to ensure structural issues like the OOM vulnerability are addressed sustainably, before they turn into emergencies. https://thephp.foundation/blog/2026/10/21/todays-php-security-release-and-how-werestrengthening-php-security/ https://thephp.foundation/sponsor/ -
Three things to take home Infrastructure management isn't optional anymore.
#justPatch AI doesn't write secure code by default either. Rewrites won't absolve you from caring. Talk to your business leaders about AI, all of it. -
Thank you! Slides: https://speakerdeck.com/edorian Anything I can help with? Talk
to me today! Reach out later: [email protected] Discord: #ecosystem-security@phpc Invite: https://discord.com/invite/RYajXKxuuK