a grant to strengthen open source security. https://www.linuxfoundation.org/press/linux-foundation-announces-12.5-million-in-grantfunding-from-leading-organizations-to-advance-open-source-security Alpha-Omega’s mission is to protect society by catalyzing sustainable security improvements across open source. https://alpha-omega.dev/
have changed. No fundamentally new class of exploits It's still all just software With all the problems of a young industry There are impactful findings, at scale Finding issues takes a lot less effort now
tools have new classes of issues OWASP Top 10 For Large Language Model Applications https://owasp.org/projects/top-10-for-large-language-model-applications
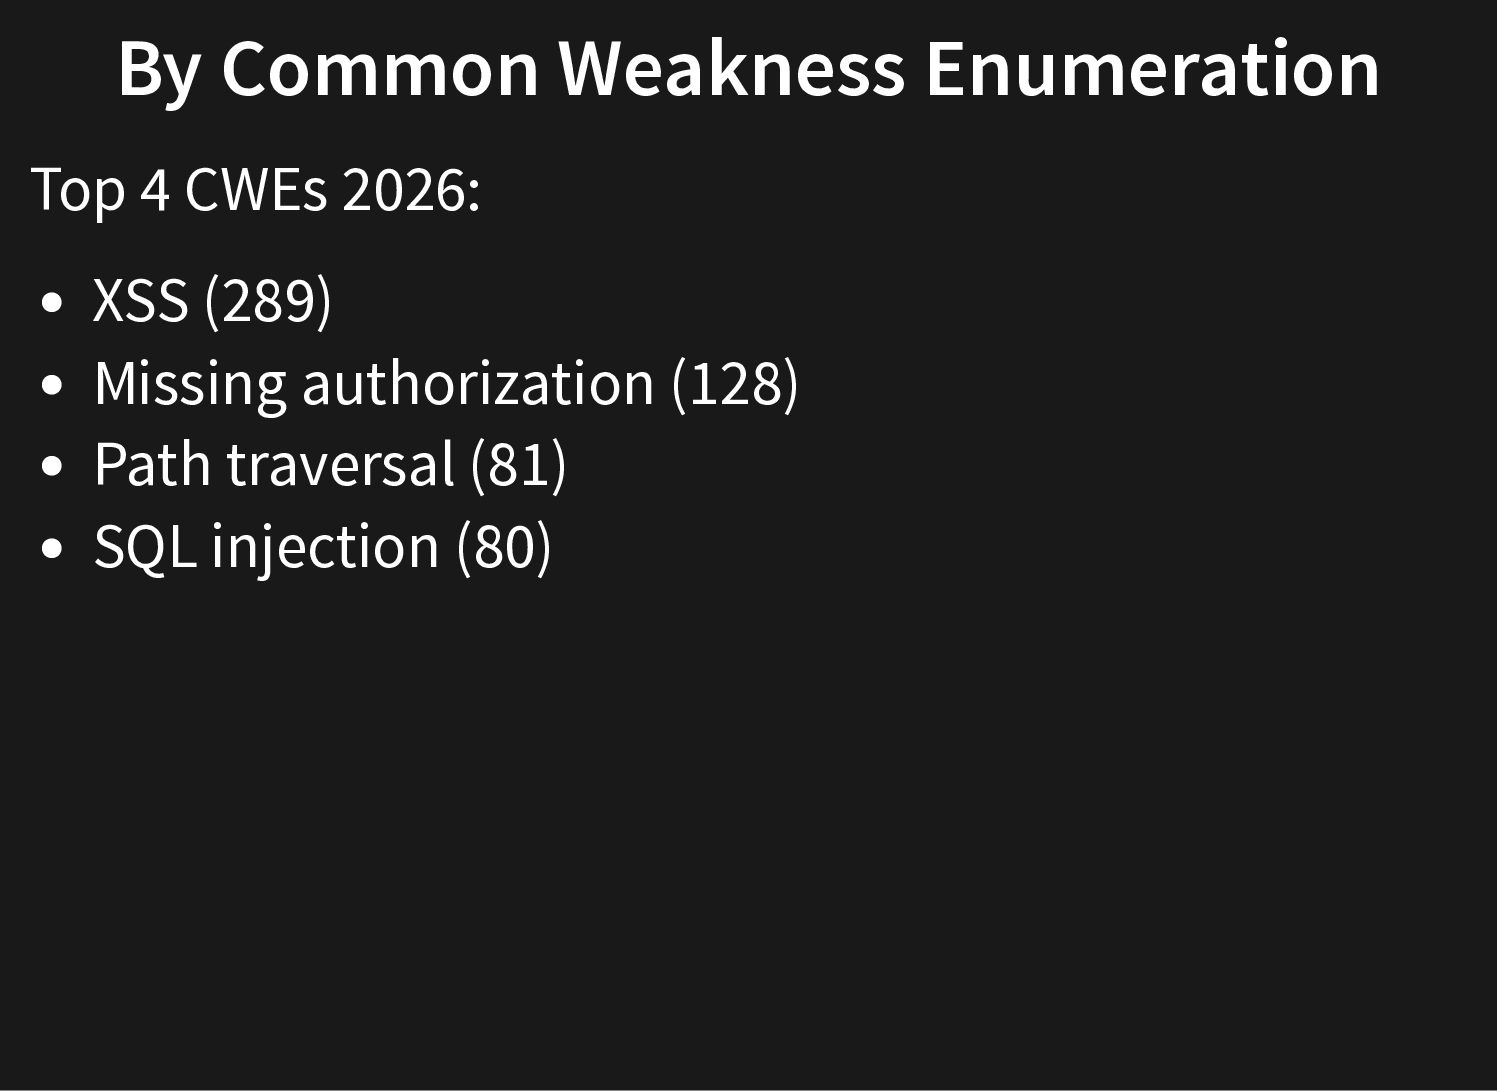
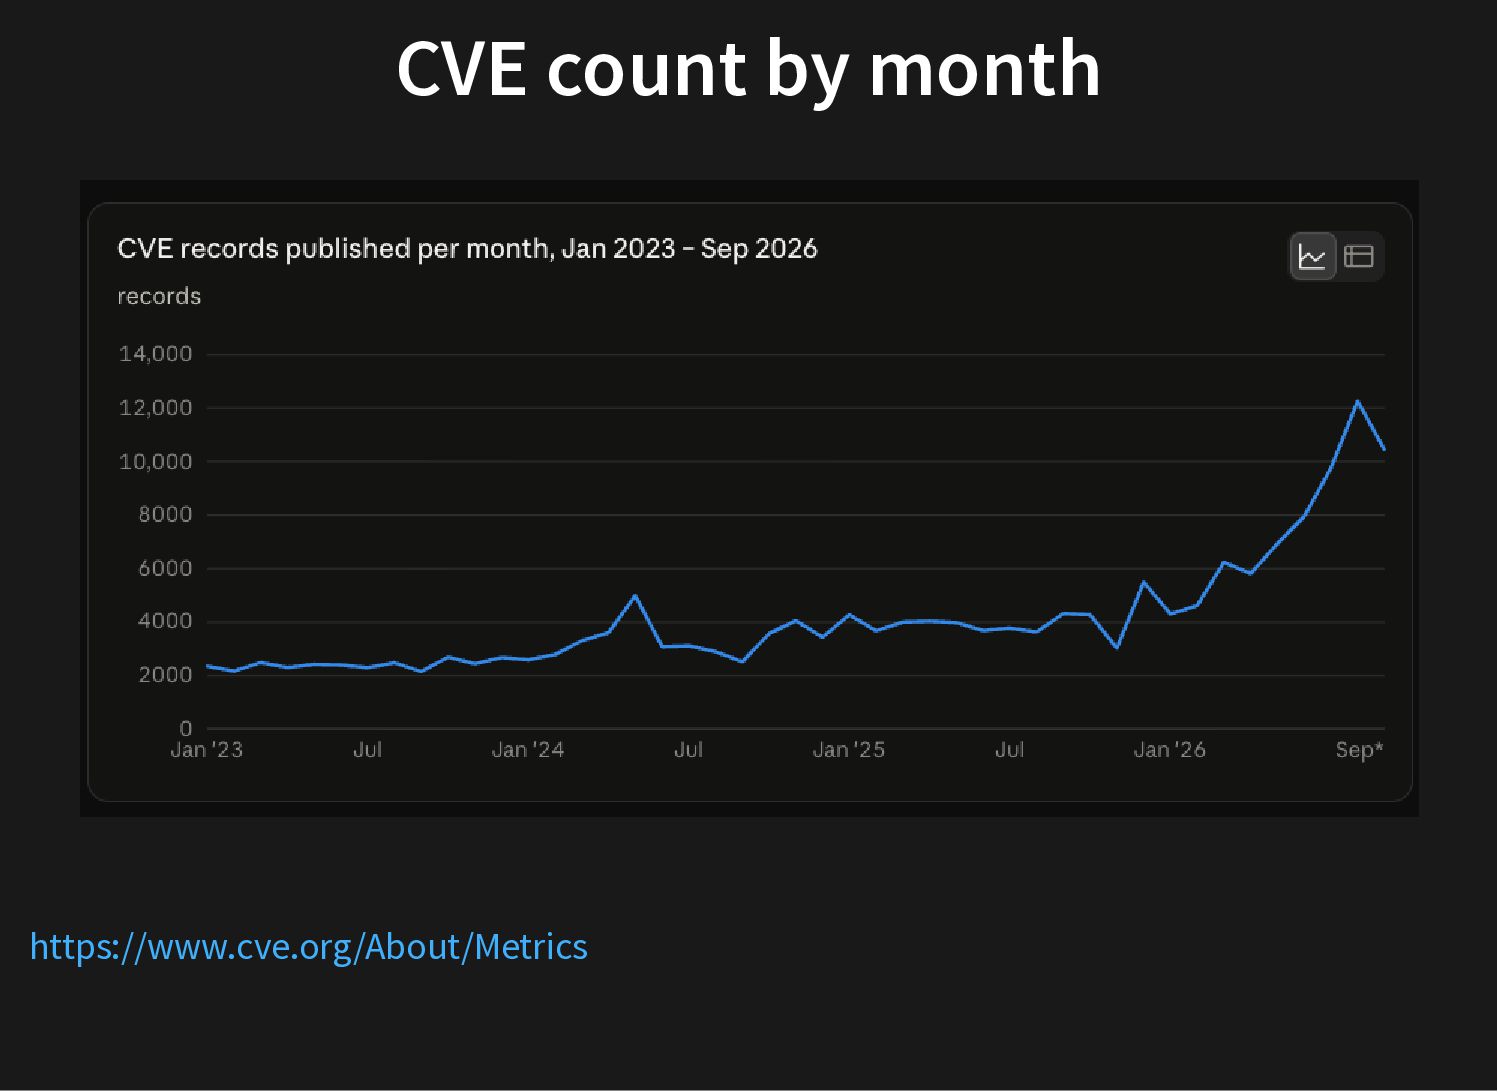
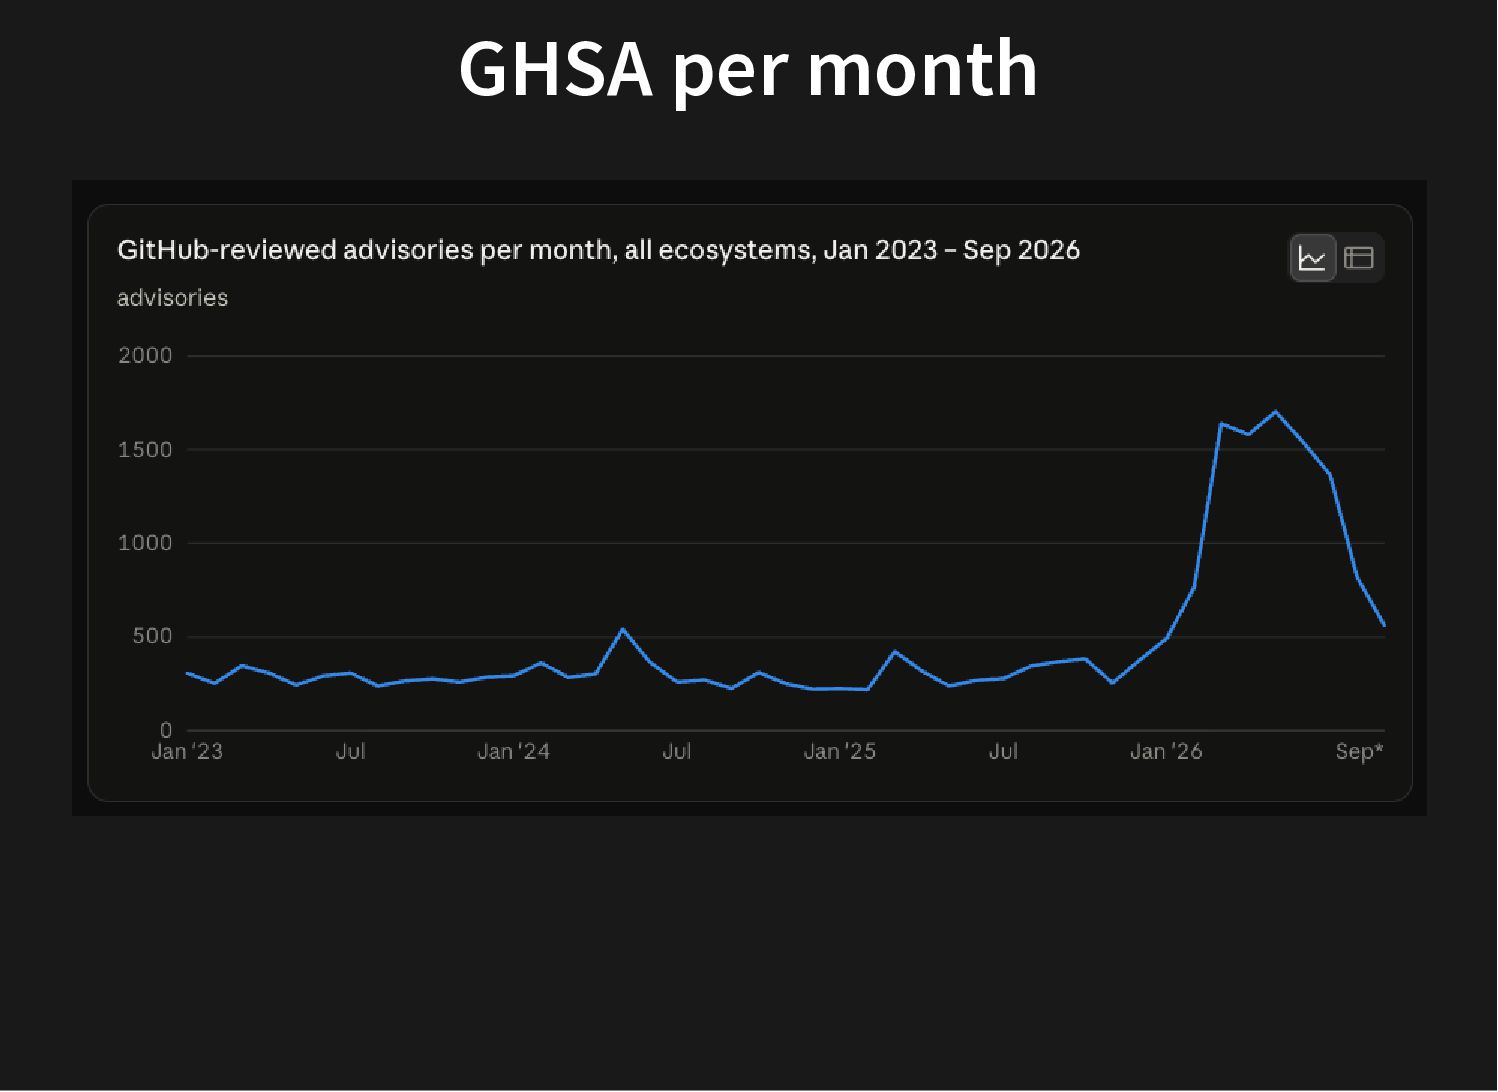
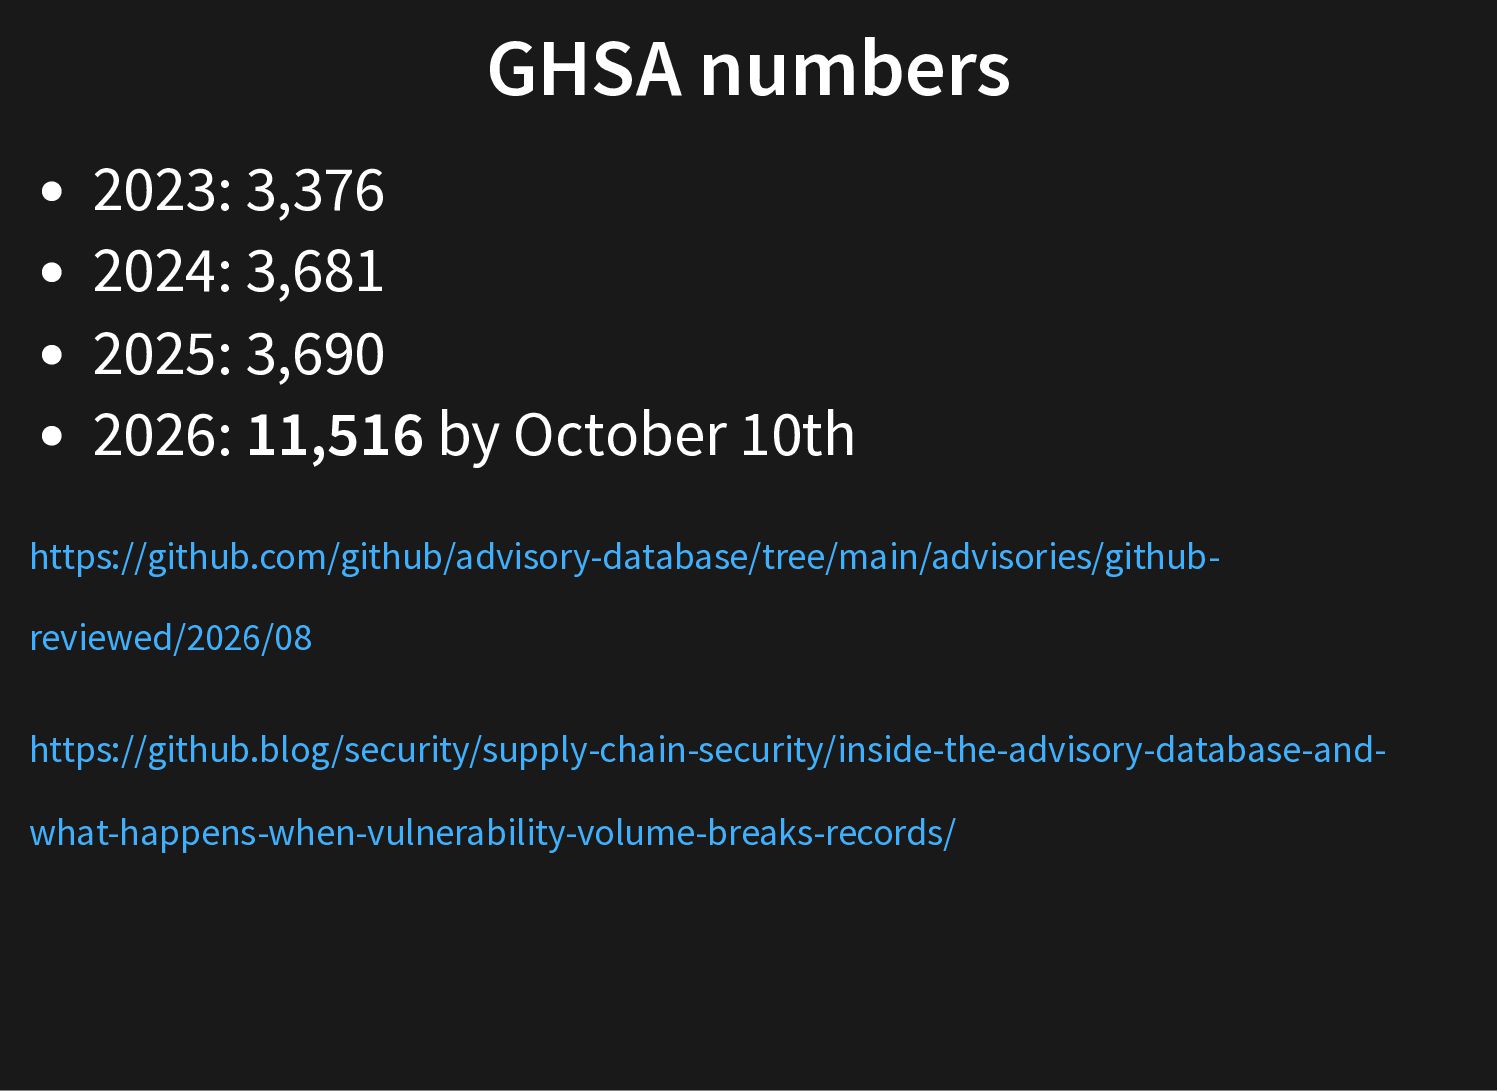
by October 10th https://github.com/github/advisory-database/tree/main/advisories/githubreviewed/2026/08 https://github.blog/security/supply-chain-security/inside-the-advisory-database-andwhat-happens-when-vulnerability-volume-breaks-records/
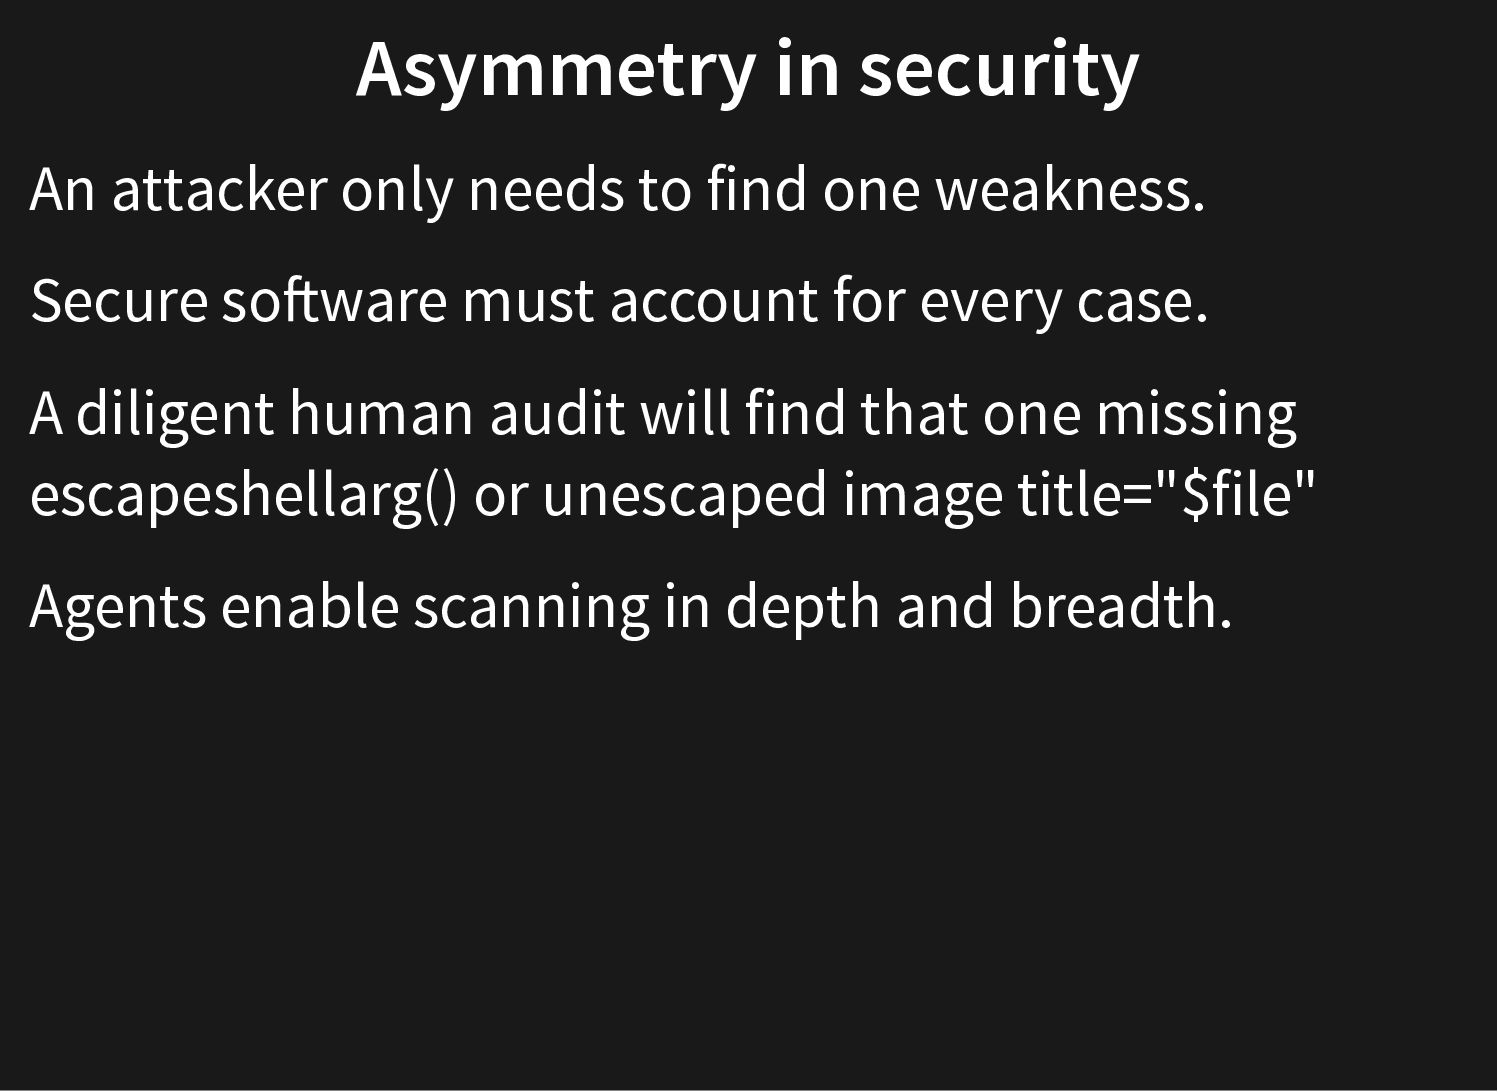
weakness. Secure software must account for every case. A diligent human audit will find that one missing escapeshellarg() or unescaped image title="$file" Agents enable scanning in depth and breadth.
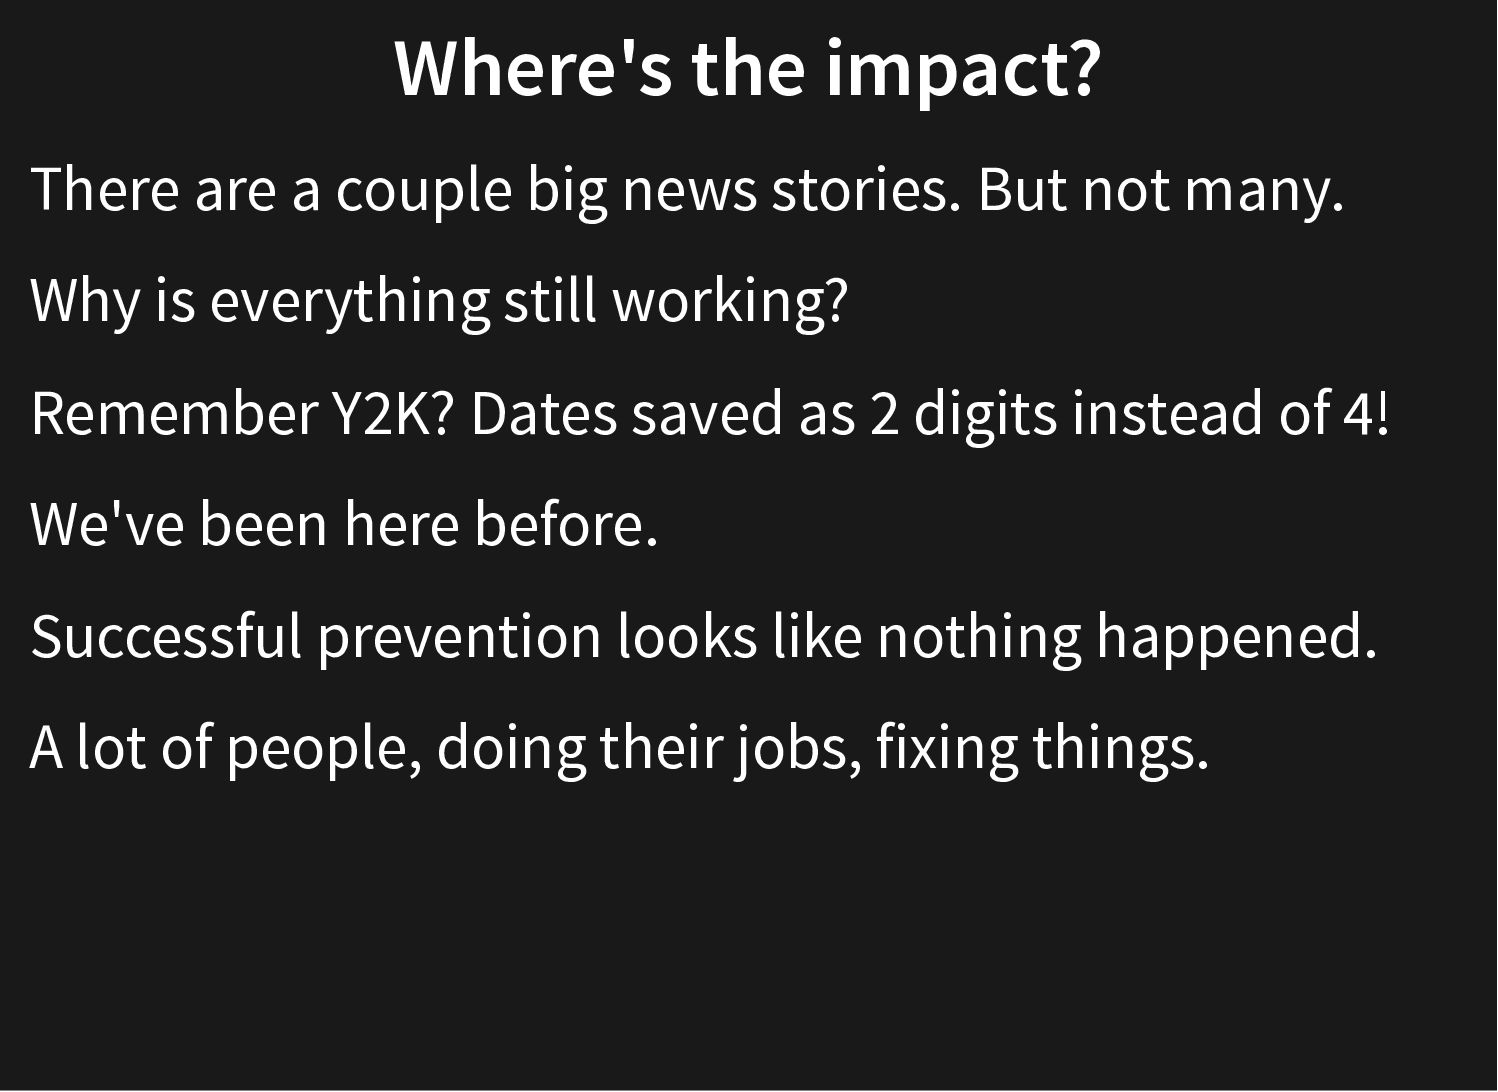
But not many. Why is everything still working? Remember Y2K? Dates saved as 2 digits instead of 4! We've been here before. Successful prevention looks like nothing happened. A lot of people, doing their jobs, fixing things.
https://thephp.foundation/blog/2026/05/18/announcing-ecosystem-security-team/ Core guideline: Respond to every request for support. It's open source and it's PHP? We're here for you!
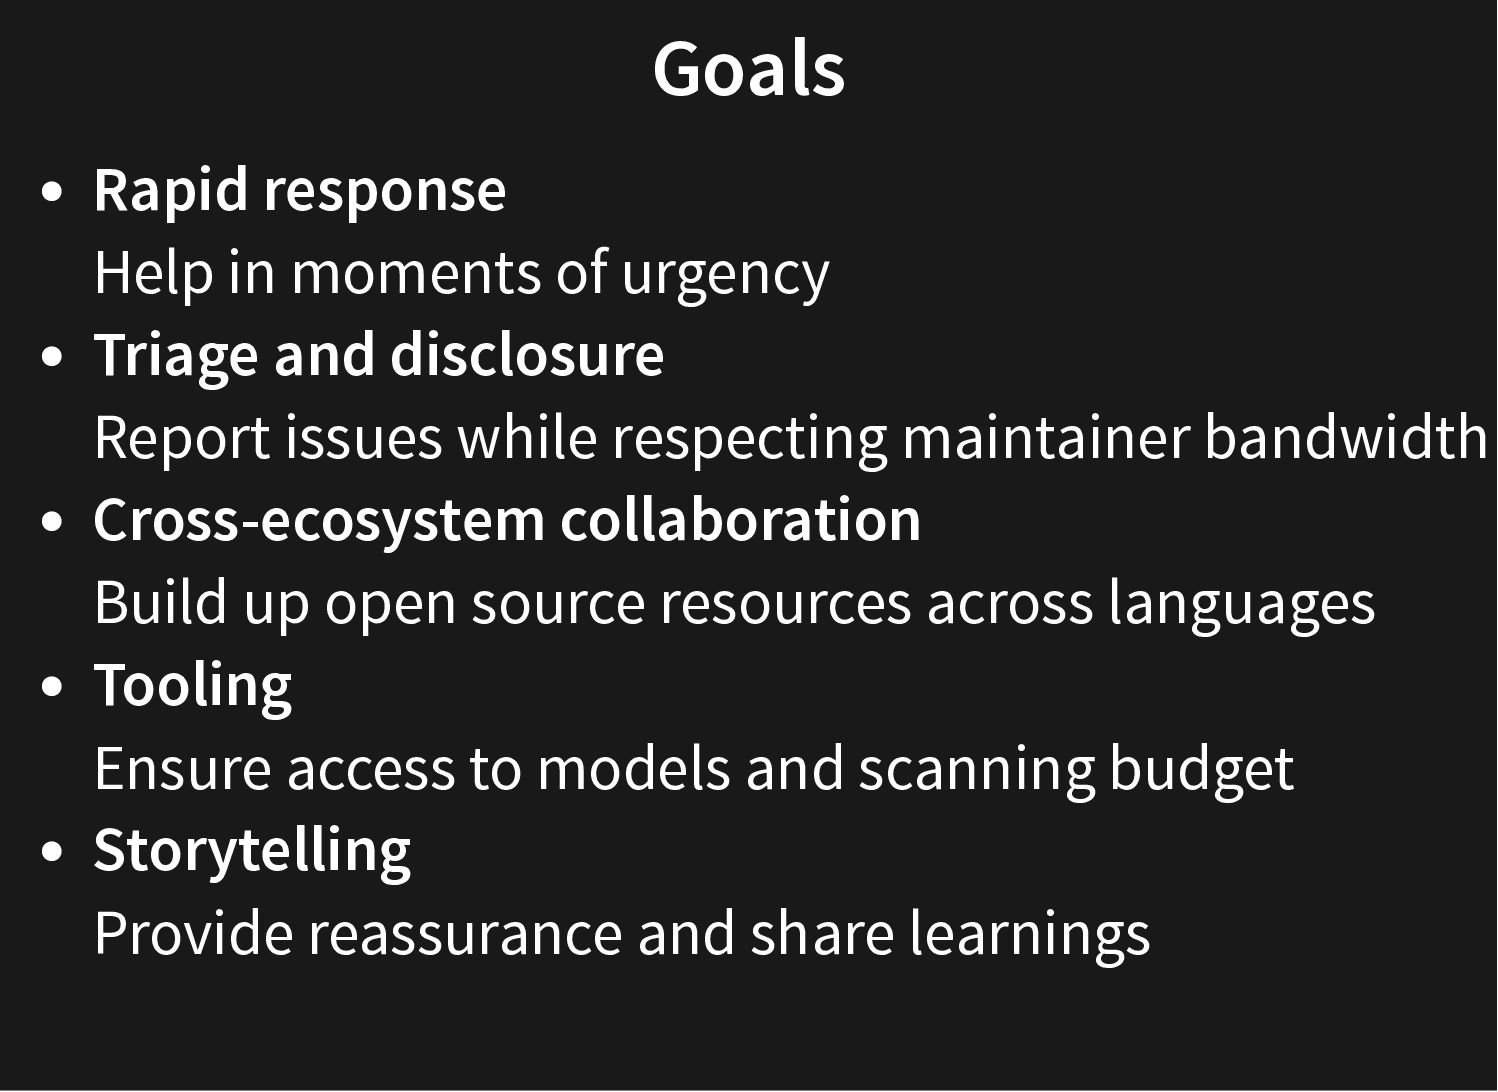
disclosure Report issues while respecting maintainer bandwidth Cross-ecosystem collaboration Build up open source resources across languages Tooling Ensure access to models and scanning budget Storytelling Provide reassurance and share learnings
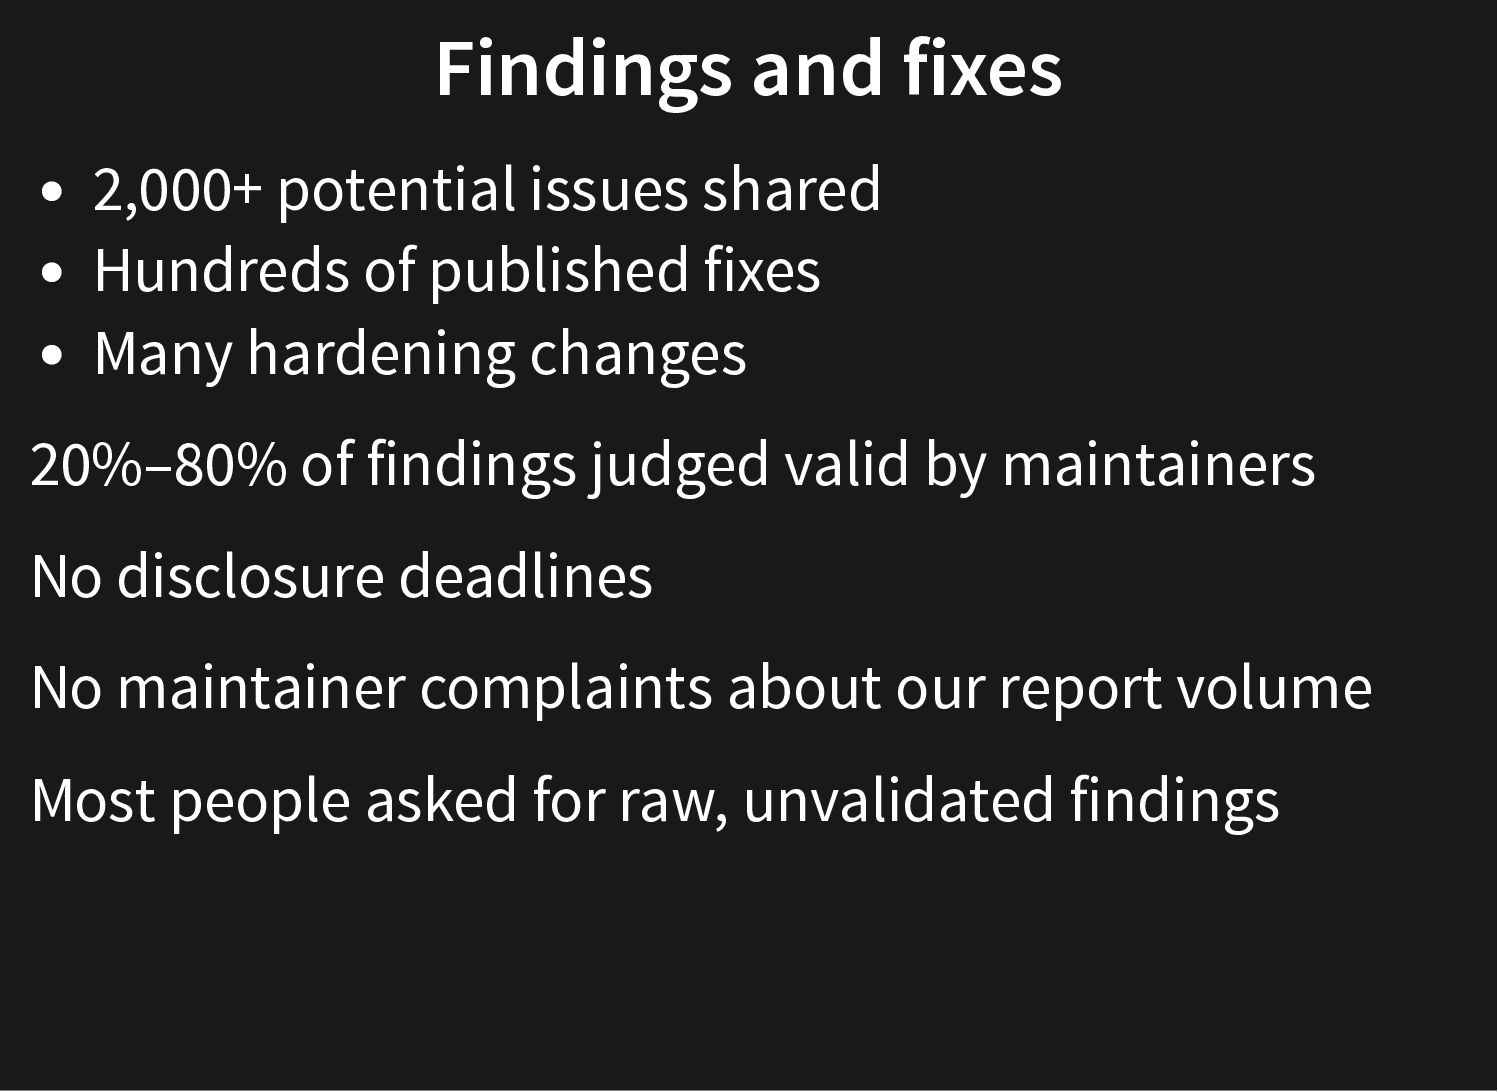
fixes Many hardening changes 20%–80% of findings judged valid by maintainers No disclosure deadlines No maintainer complaints about our report volume Most people asked for raw, unvalidated findings
https://ostif.org Performed the Sovereign Tech Fund PHP Audit in 2024 https://ostif.org/php-audit-complete/ Facilitated early Mythos scans on PHP frameworks Big personal thank you to Derek Zimmer
email. One .tar.gz archive containing: SUMMARY.md Markdown report and reproducer per finding. Sometimes the generated threat model Sometimes raw model output
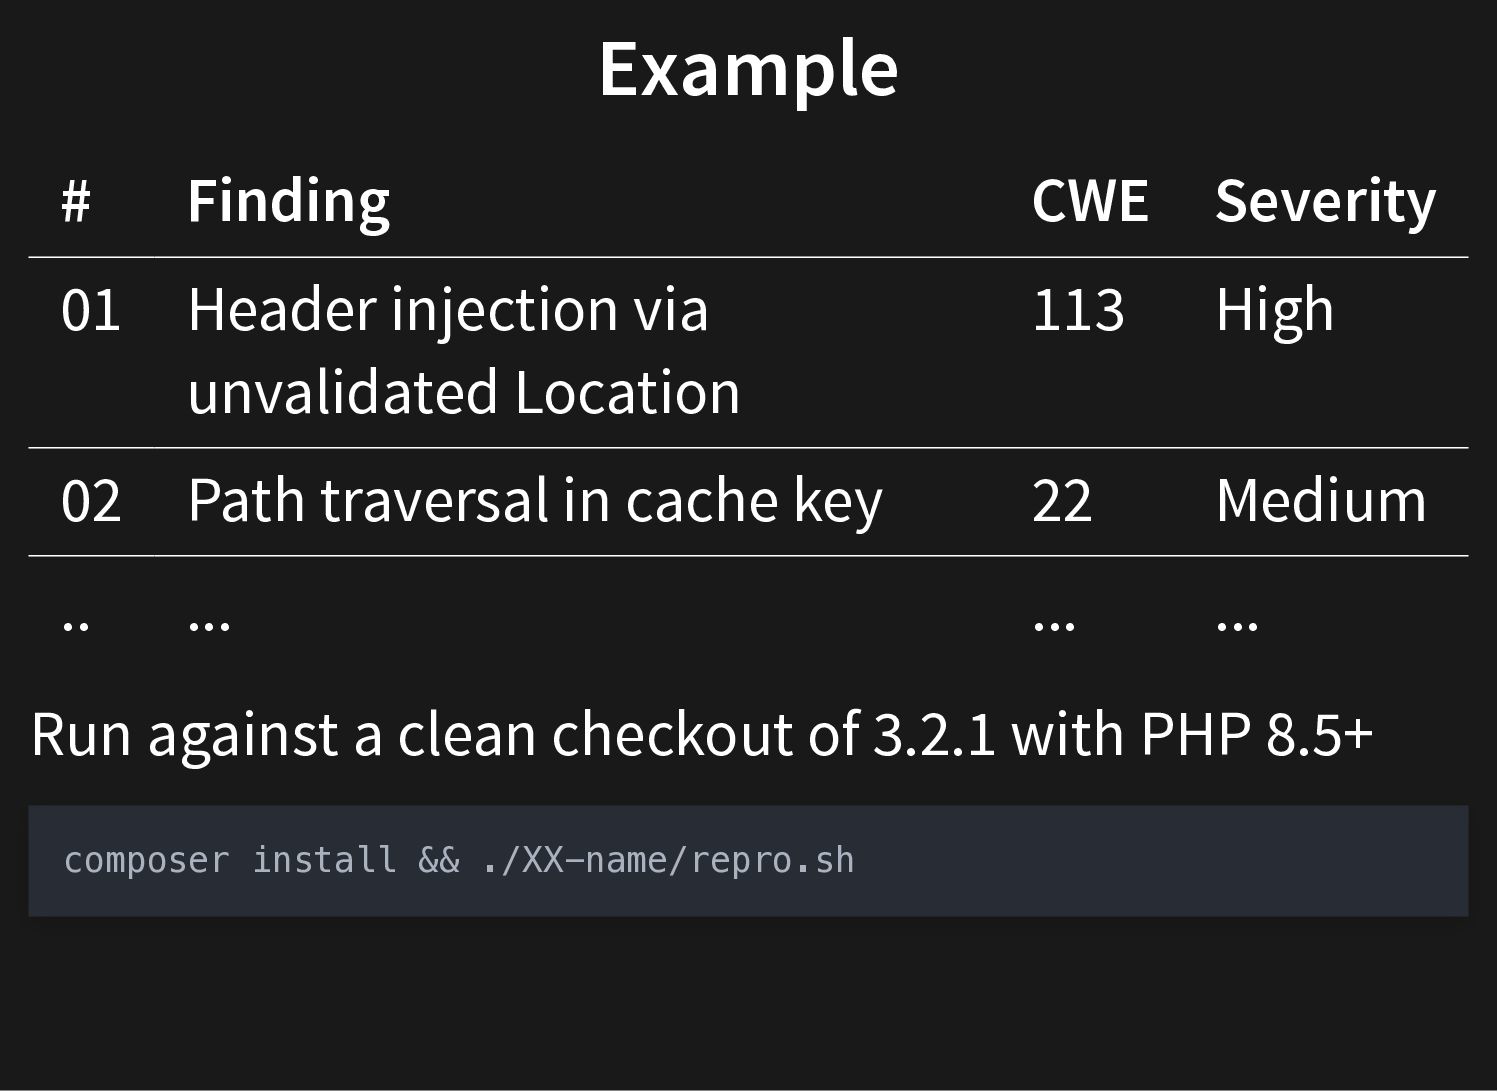
Location 113 High 02 Path traversal in cache key 22 Medium .. ... ... ... Run against a clean checkout of 3.2.1 with PHP 8.5+ composer install && ./XX-name/repro.sh
what works for you. Docker Sandbox Full VM Throwaway cloud instances Dedicated machine The best approach is the one you actually will use. Targeted attacks do happen: https://blog.rust-lang.org/2026/09/17/targeted-attacks/
when it's not a security issue Document security boundaries E.g.: Only parse trusted input. Pre-sanitize filenames. Define your policy Put scope and threat model in your SECURITY.md Tell scanners what you don't care about Ignore/Close You owe nobody a rebuttal
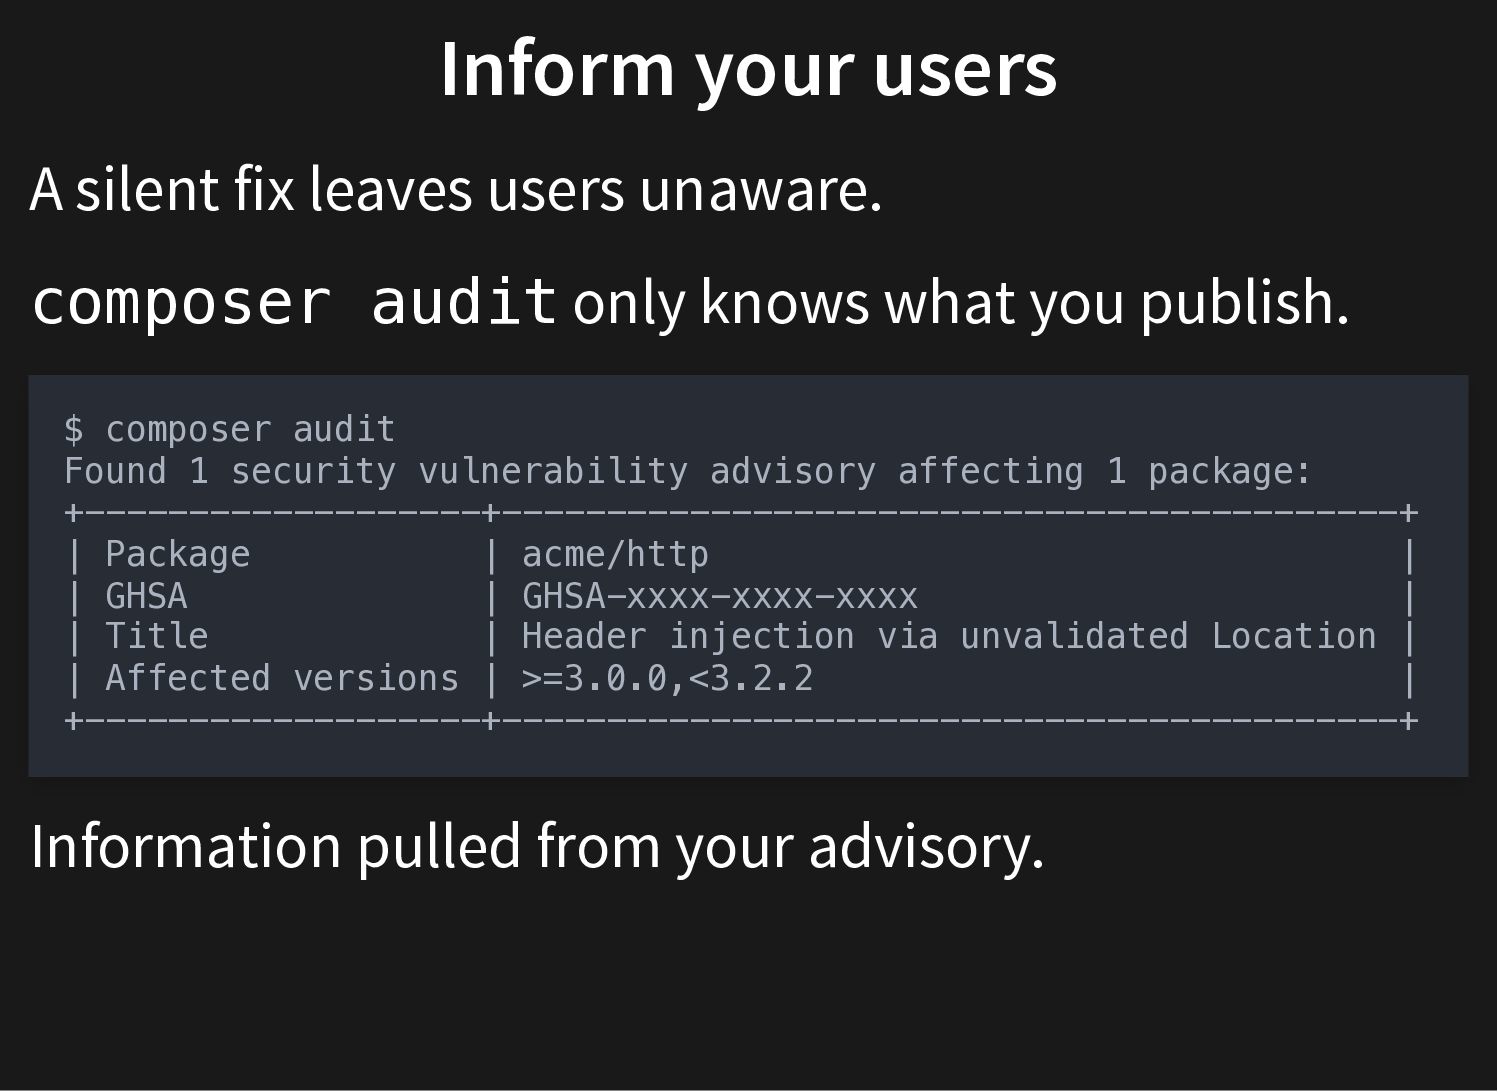
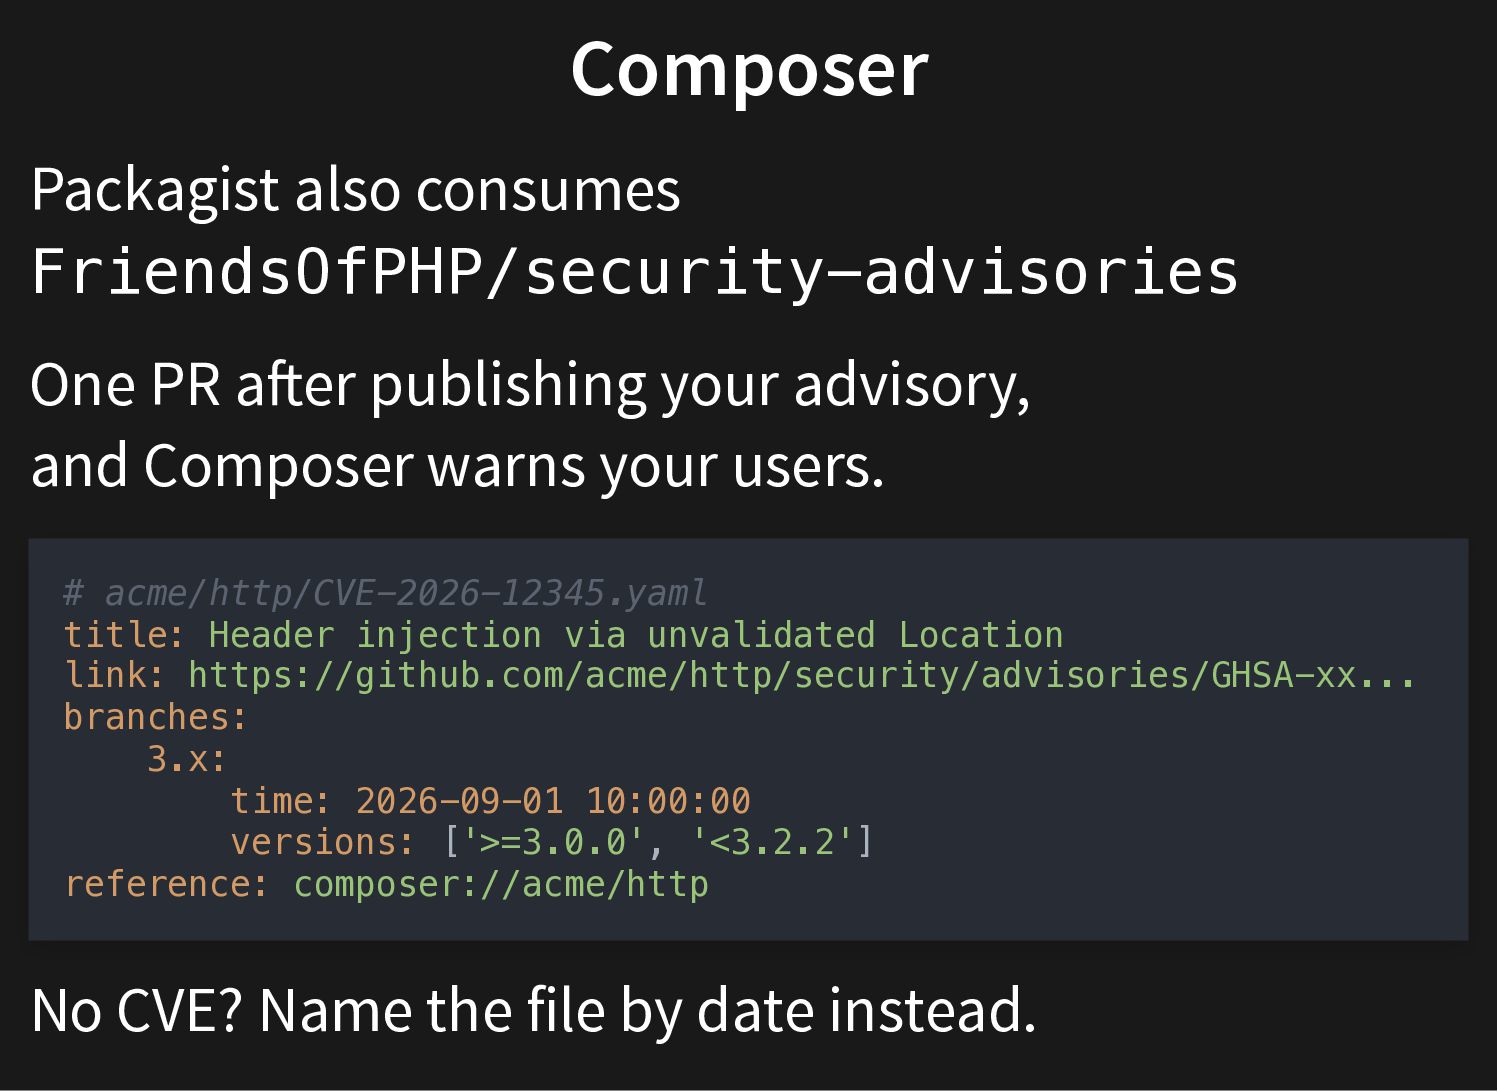
advisory, and Composer warns your users. # acme/http/CVE-2026-12345.yaml title: Header injection via unvalidated Location link: https://github.com/acme/http/security/advisories/GHSA-xx... branches: 3.x: time: 2026-09-01 10:00:00 versions: ['>=3.0.0', '<3.2.2'] reference: composer://acme/http No CVE? Name the file by date instead.
unattended-upgrades, or a rebuild pipeline Containers: Rebuild base images regularly PHP: Stay up to date Dependencies: composer update on a cadence Investment in your infrastructure is security.
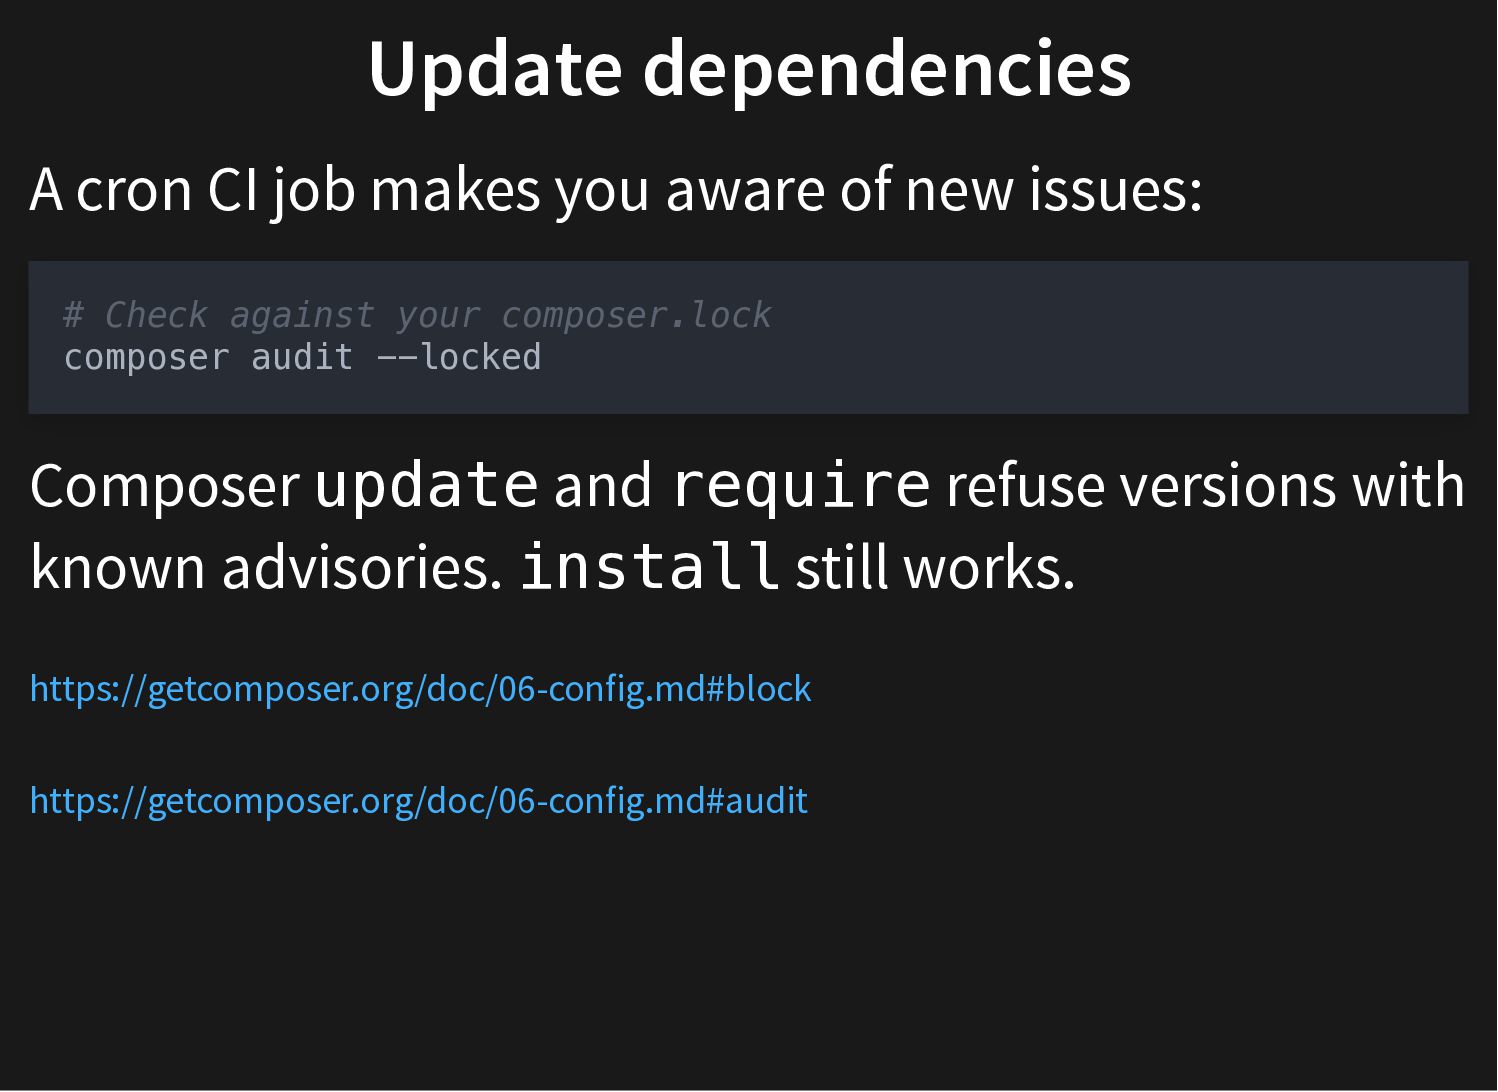
new issues: # Check against your composer.lock composer audit --locked Composer update and require refuse versions with known advisories. install still works. https://getcomposer.org/doc/06-config.md#block https://getcomposer.org/doc/06-config.md#audit
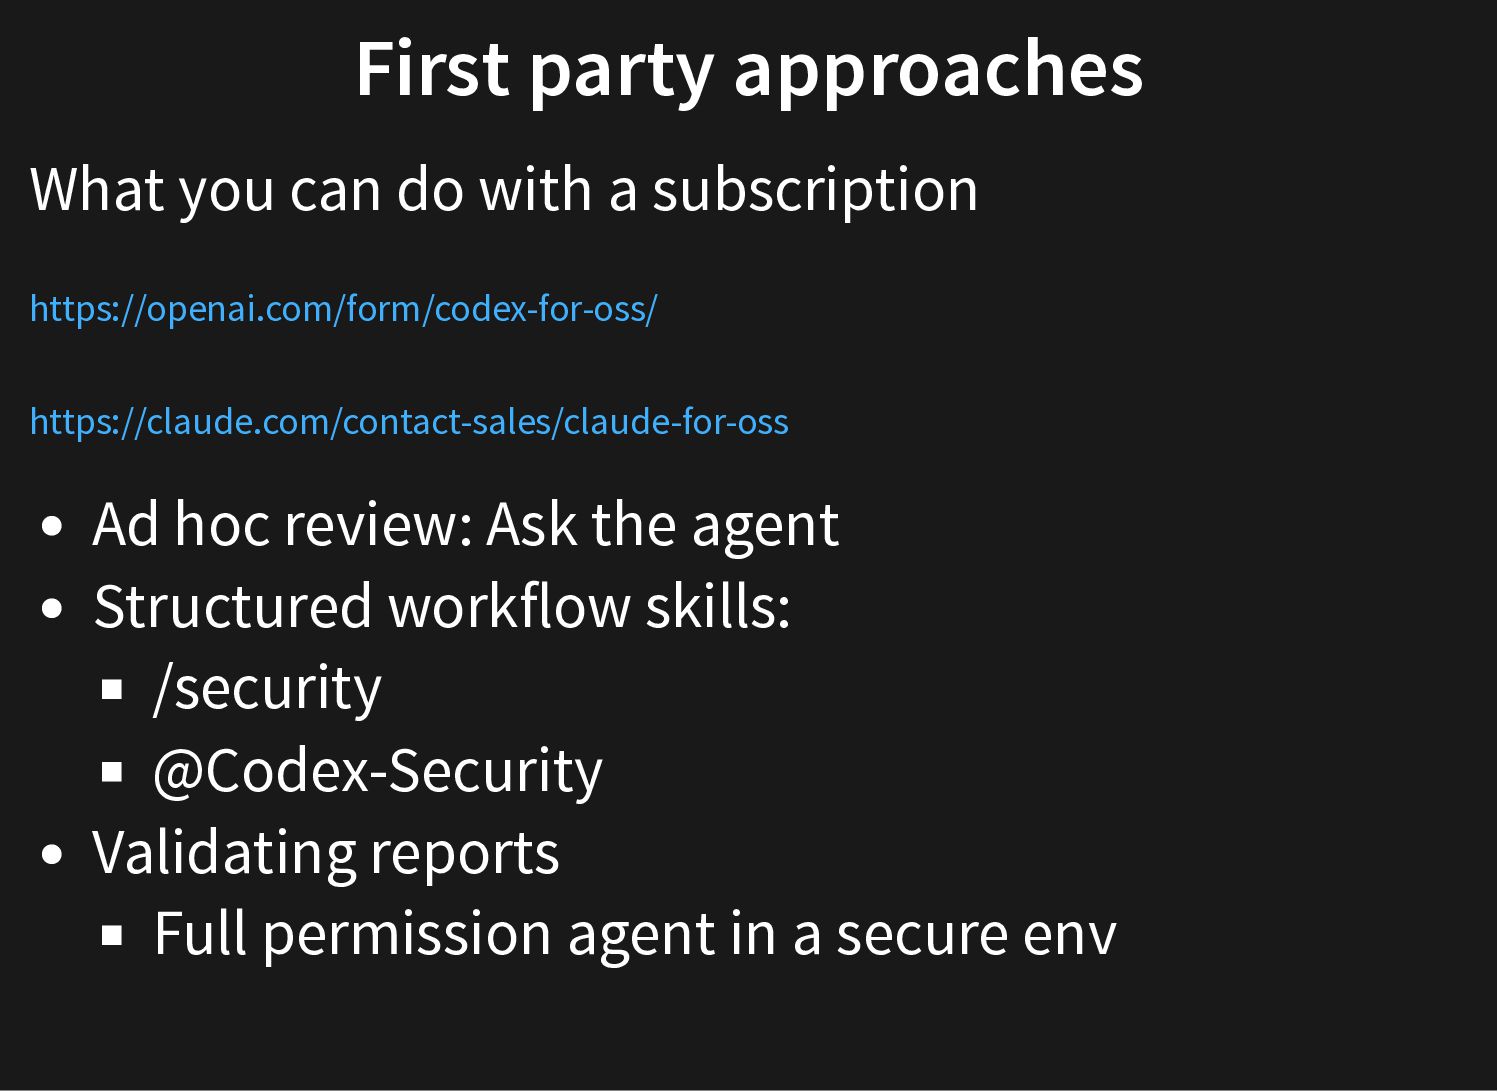
https://openai.com/form/codex-for-oss/ https://claude.com/contact-sales/claude-for-oss Ad hoc review: Ask the agent Structured workflow skills: /security @Codex-Security Validating reports Full permission agent in a secure env
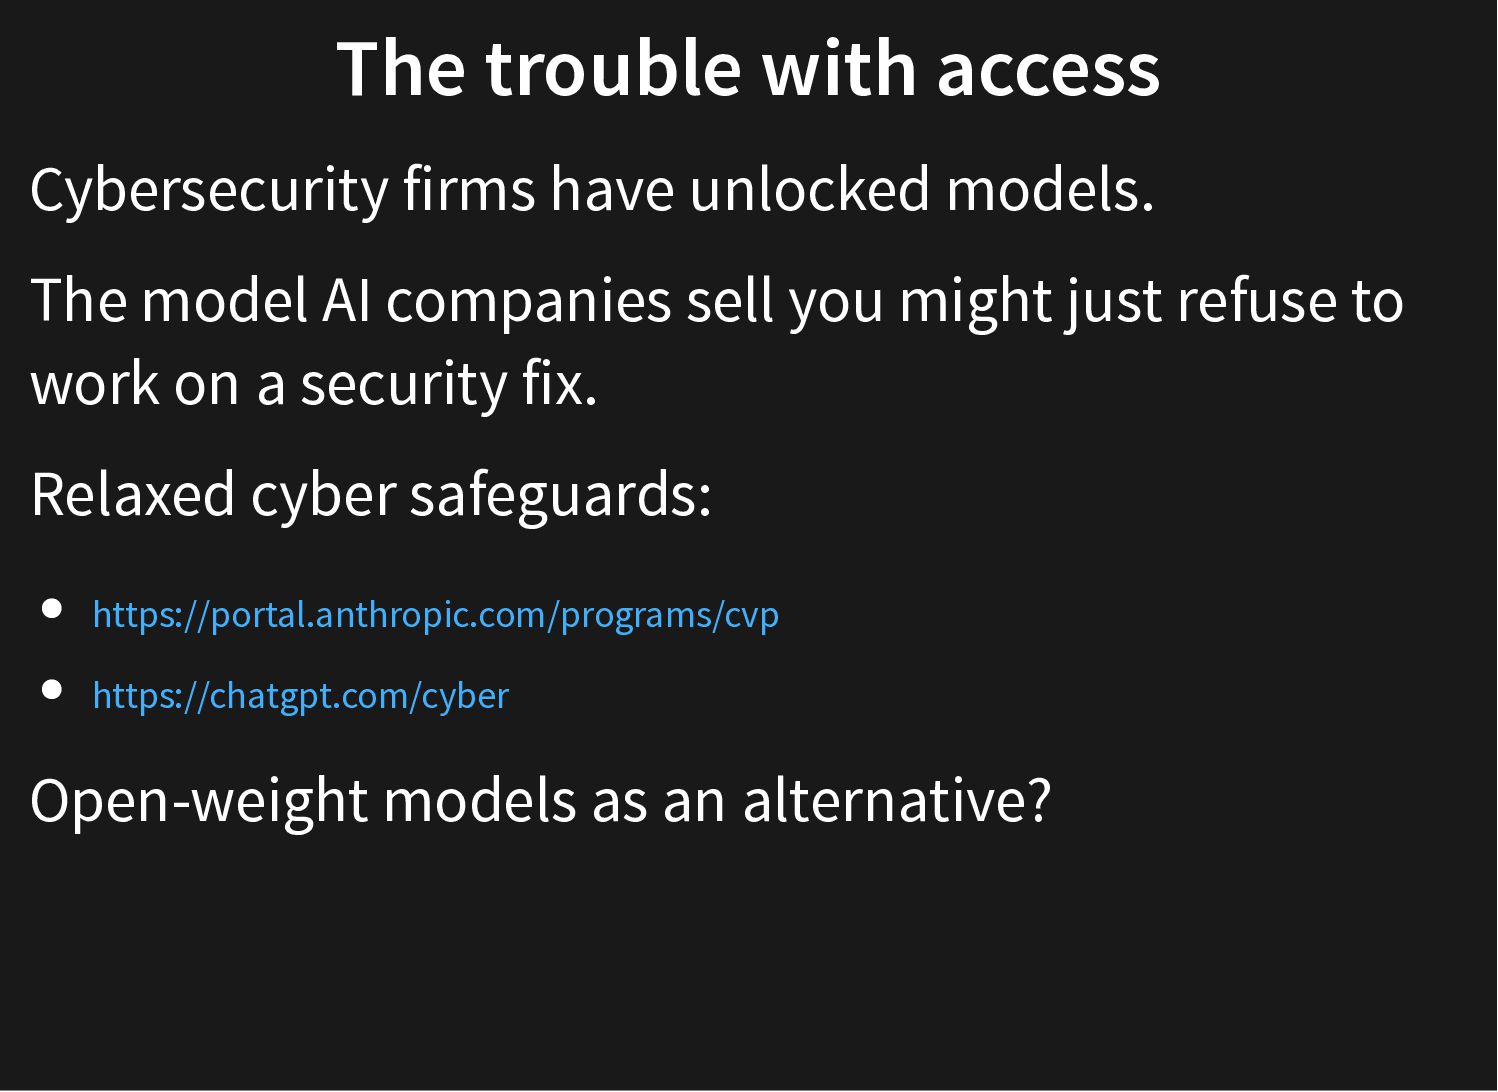
model AI companies sell you might just refuse to work on a security fix. Relaxed cyber safeguards: https://portal.anthropic.com/programs/cvp https://chatgpt.com/cyber Open-weight models as an alternative?
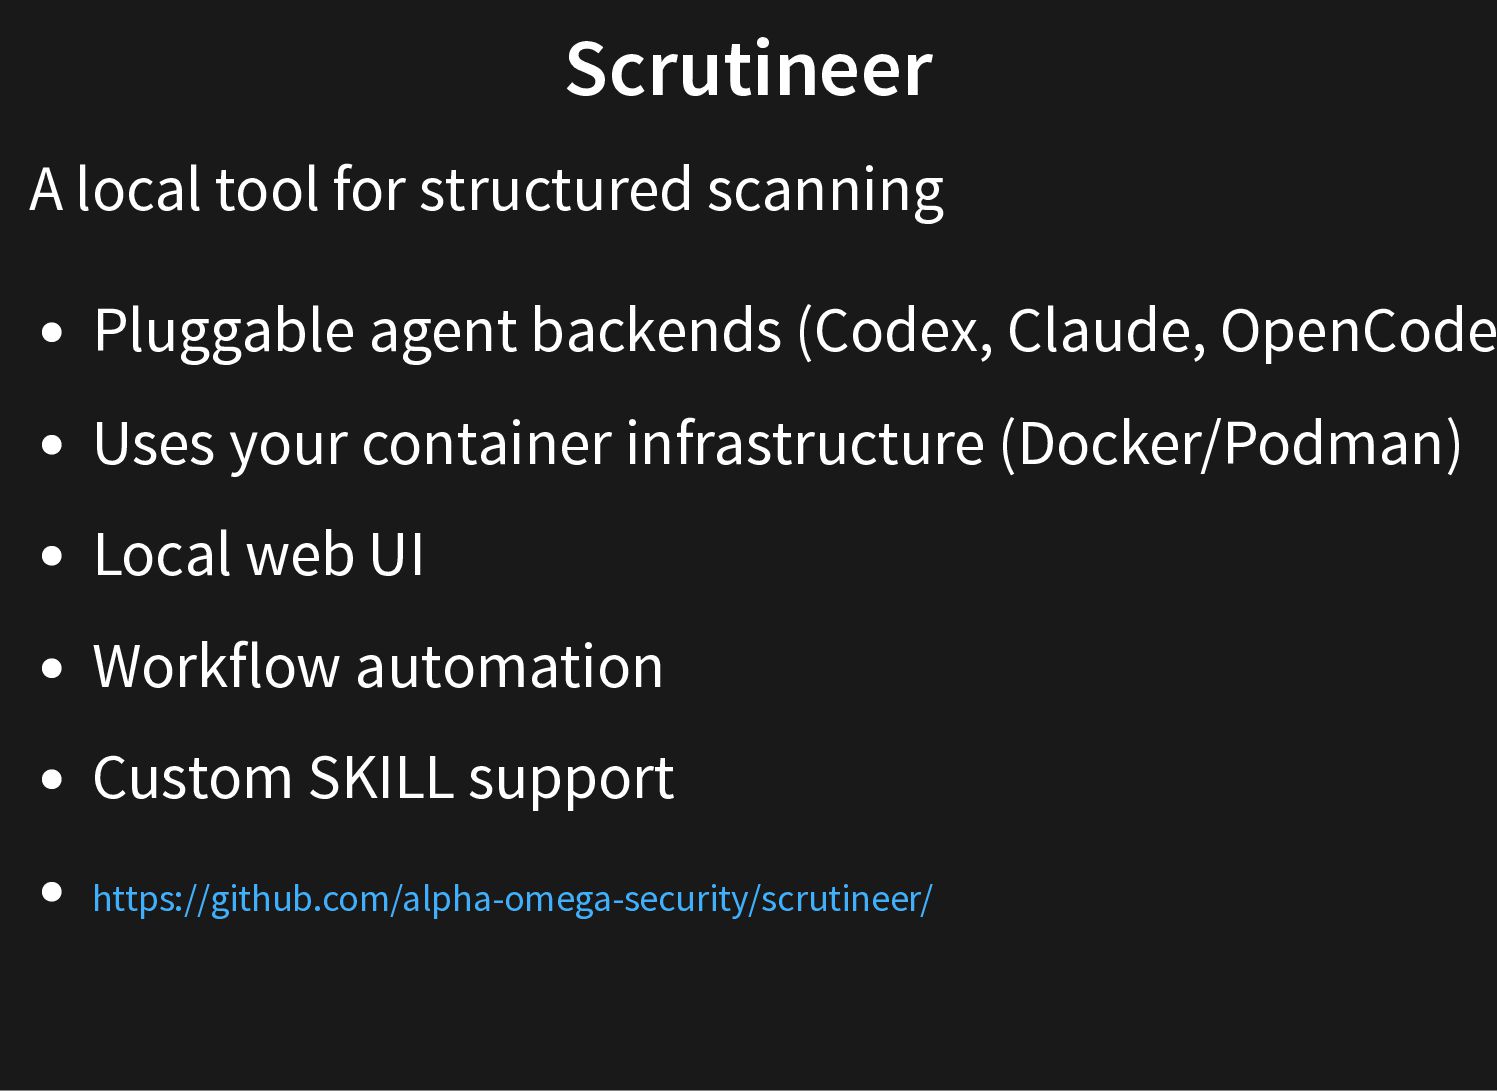
(Codex, Claude, OpenCode Uses your container infrastructure (Docker/Podman) Local web UI Workflow automation Custom SKILL support https://github.com/alpha-omega-security/scrutineer/
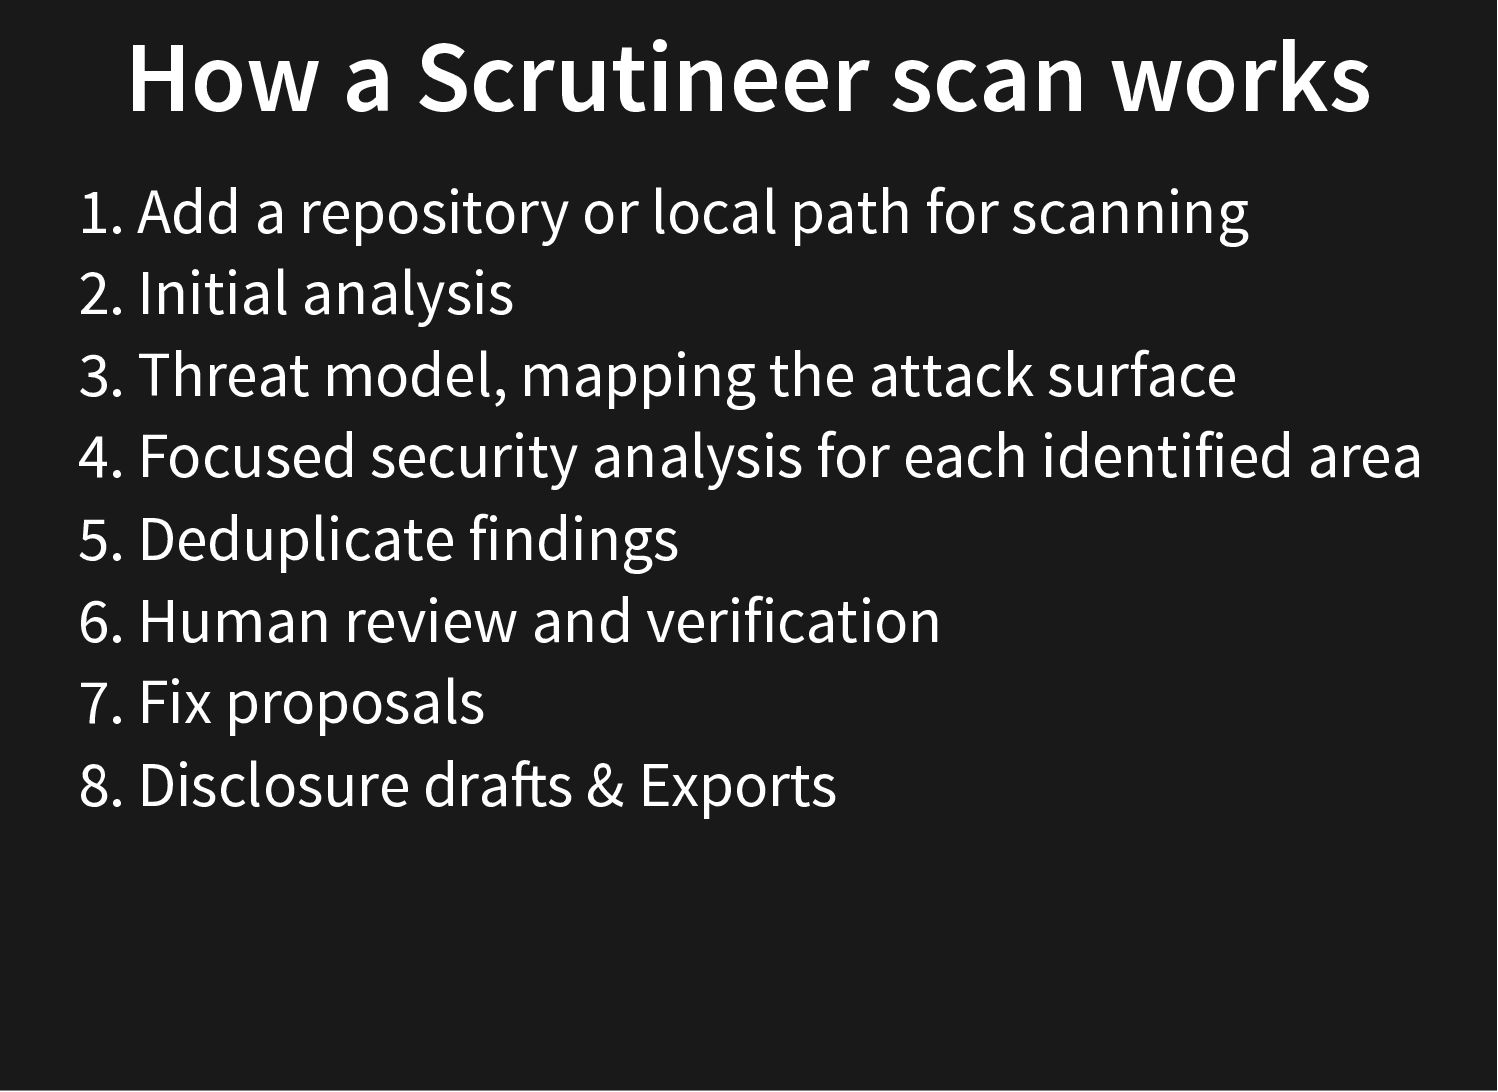
local path for scanning 2. Initial analysis 3. Threat model, mapping the attack surface 4. Focused security analysis for each identified area 5. Deduplicate findings 6. Human review and verification 7. Fix proposals 8. Disclosure drafts & Exports
your boundaries, scan proactively. Teams shipping PHP: composer audit in CI, patch on a schedule, know your dependency graph. "The bugs are old, the pace is new." Talk to your business leaders about AI & Security.


 edorian
 marcoroth
 elmetal
 tmikov2023
 kenjiyoneyama
 ryu1013
 kishida
 nokomoro3
 satoshi256kbyte
 teyamagu
 seike460
 rockname
 findyinc
 mza
 keavy
 livdayseo
 yeseniaperezcruz
 helenjbeal
 addyosmani
 davetheseo
 chrislema
 rocio
 axbom
 jdejongh
 konakalab