Upgrade to Pro — share decks privately, control downloads, hide ads and more …

Red Hat Hardened Images

Avatar for Emre Özkan Emre Özkan
September 29, 2026

Red Hat Hardened Images

23 Eylül 2026 tarihinde gerçekleştirdiğim webinar sunumu

Günümüz bulut yerlisi mimarilerinde, otomatik tarayıcılar ve yapay zeka destekli araçlar mühendislik ekiplerinin üzerine devasa miktarda güvenlik uyarısı yığmaktadır. Nitekim, güvenlik ve uyumluluk görevleri günümüzde geliştirici tükenmişliğinin en önemli nedenlerinden biri haline gelmiştir. Standart konteyner imajları; gereksiz yazılımlar, araçlar ve kütüphanelerden oluşan geniş bir içerikle gelir. Bu durum hem saldırı yüzeyinizi genişletir hem de ekiplerinizi kod yazmak yerine saatlerce yanlış alarmları ayıklamak zorunda bırakır.

Hummingbird adlı bir projeden doğan Red Hat Hardened Images (RHHI), üretime hazır ve ücretsiz bir alternatif sunar. Tamamen "distroless" (işletim sistemi araçlarından arındırılmış) bir tasarımı benimseyen bu mikro boyutlu bileşenler; geleneksel yardımcı araçları, shell ve paket yöneticilerini imajdan tamamen kaldırır. İmajın içinde bulunmayan bir güvenlik açığı ise istismar edilemez.

Avatar for Emre Özkan

Emre Özkan

September 29, 2026

Other Decks in Technology

Transcript

  1. Webinar | OpenShift Tech Journey series Red Hat Hardened Images

    Konteyner Güvenliğinde Yeni Dönem: CVE Yükünü Azaltın ve İnovasyona Zaman Ayırın Emre Özkan Senior Solution Architect 1
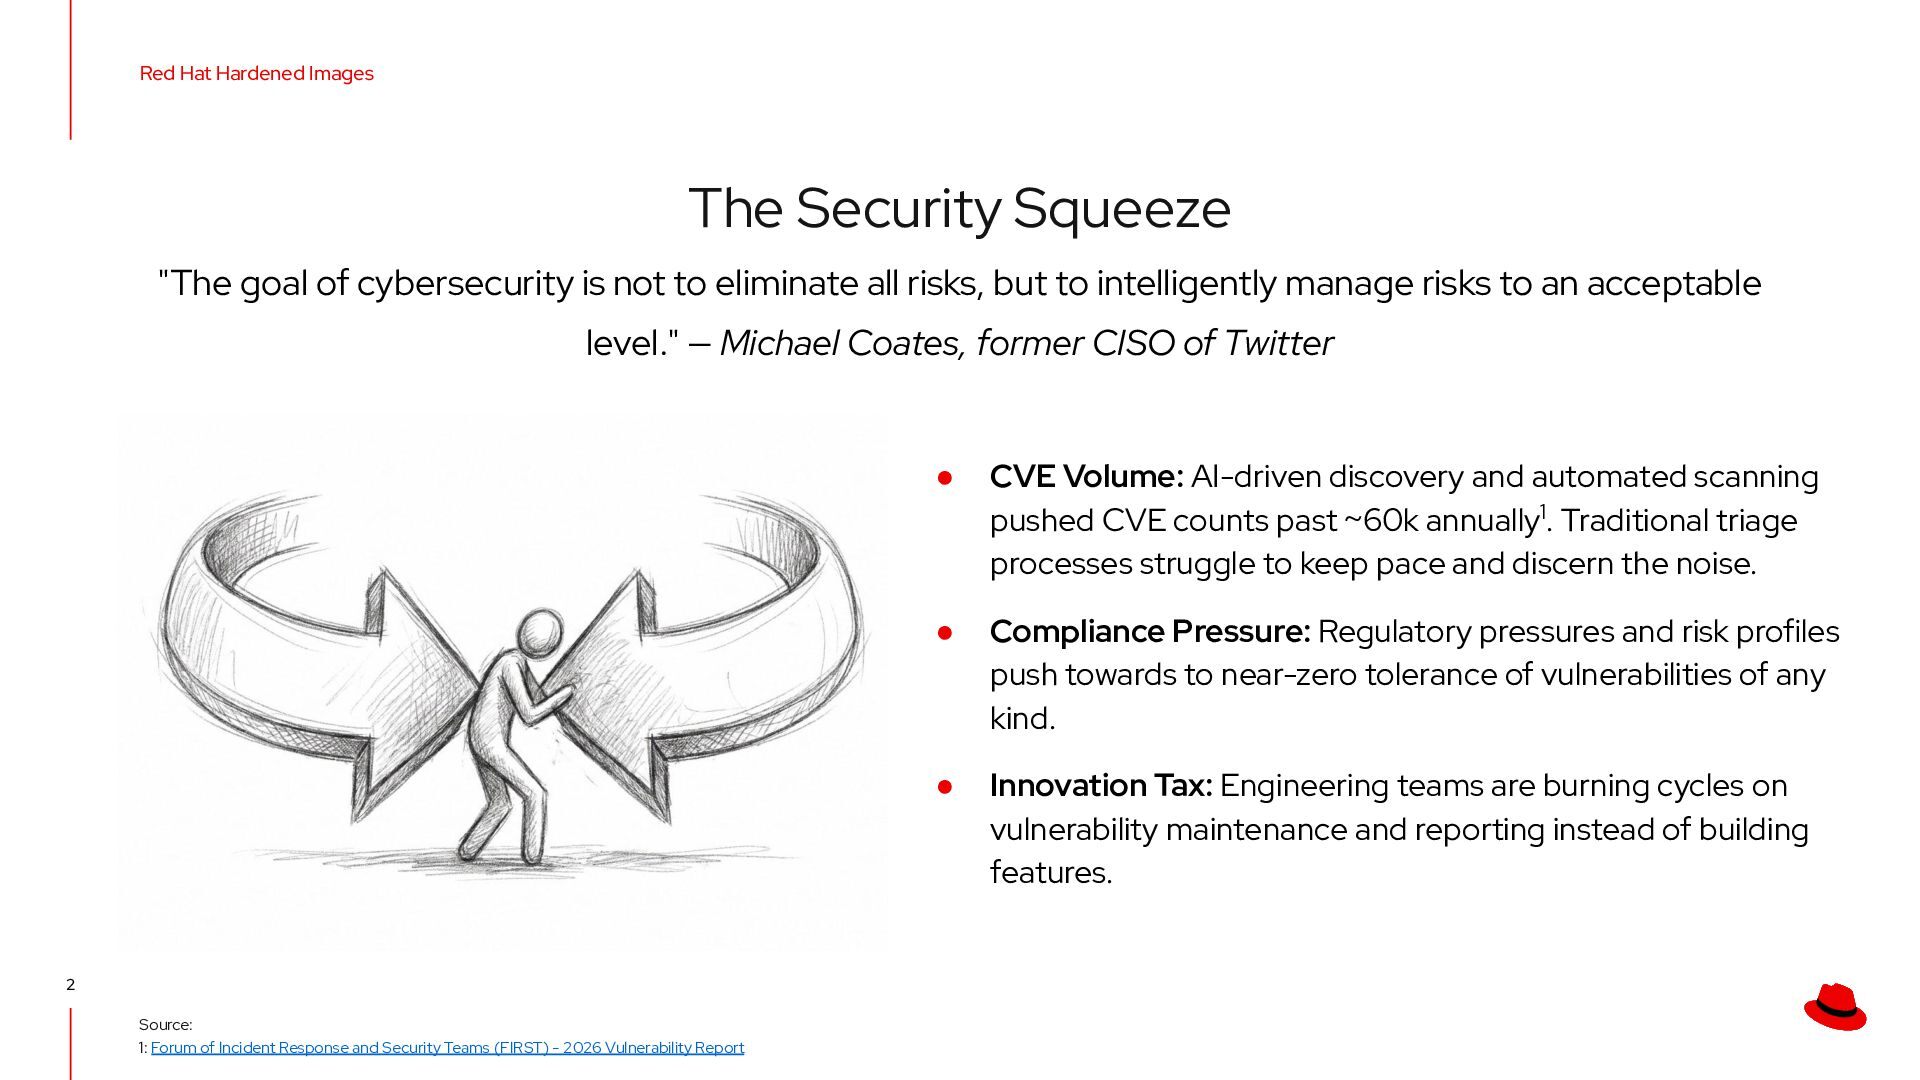
  2. Red Hat Hardened Images The Security Squeeze "The goal of

    cybersecurity is not to eliminate all risks, but to intelligently manage risks to an acceptable level." — Michael Coates, former CISO of Twitter 2 Source: 1: Forum of Incident Response and Security Teams (FIRST) - 2026 Vulnerability Report • CVE Volume: AI-driven discovery and automated scanning pushed CVE counts past ~60k annually1. Traditional triage processes struggle to keep pace and discern the noise. • Compliance Pressure: Regulatory pressures and risk profiles push towards to near-zero tolerance of vulnerabilities of any kind. • Innovation Tax: Engineering teams are burning cycles on vulnerability maintenance and reporting instead of building features.
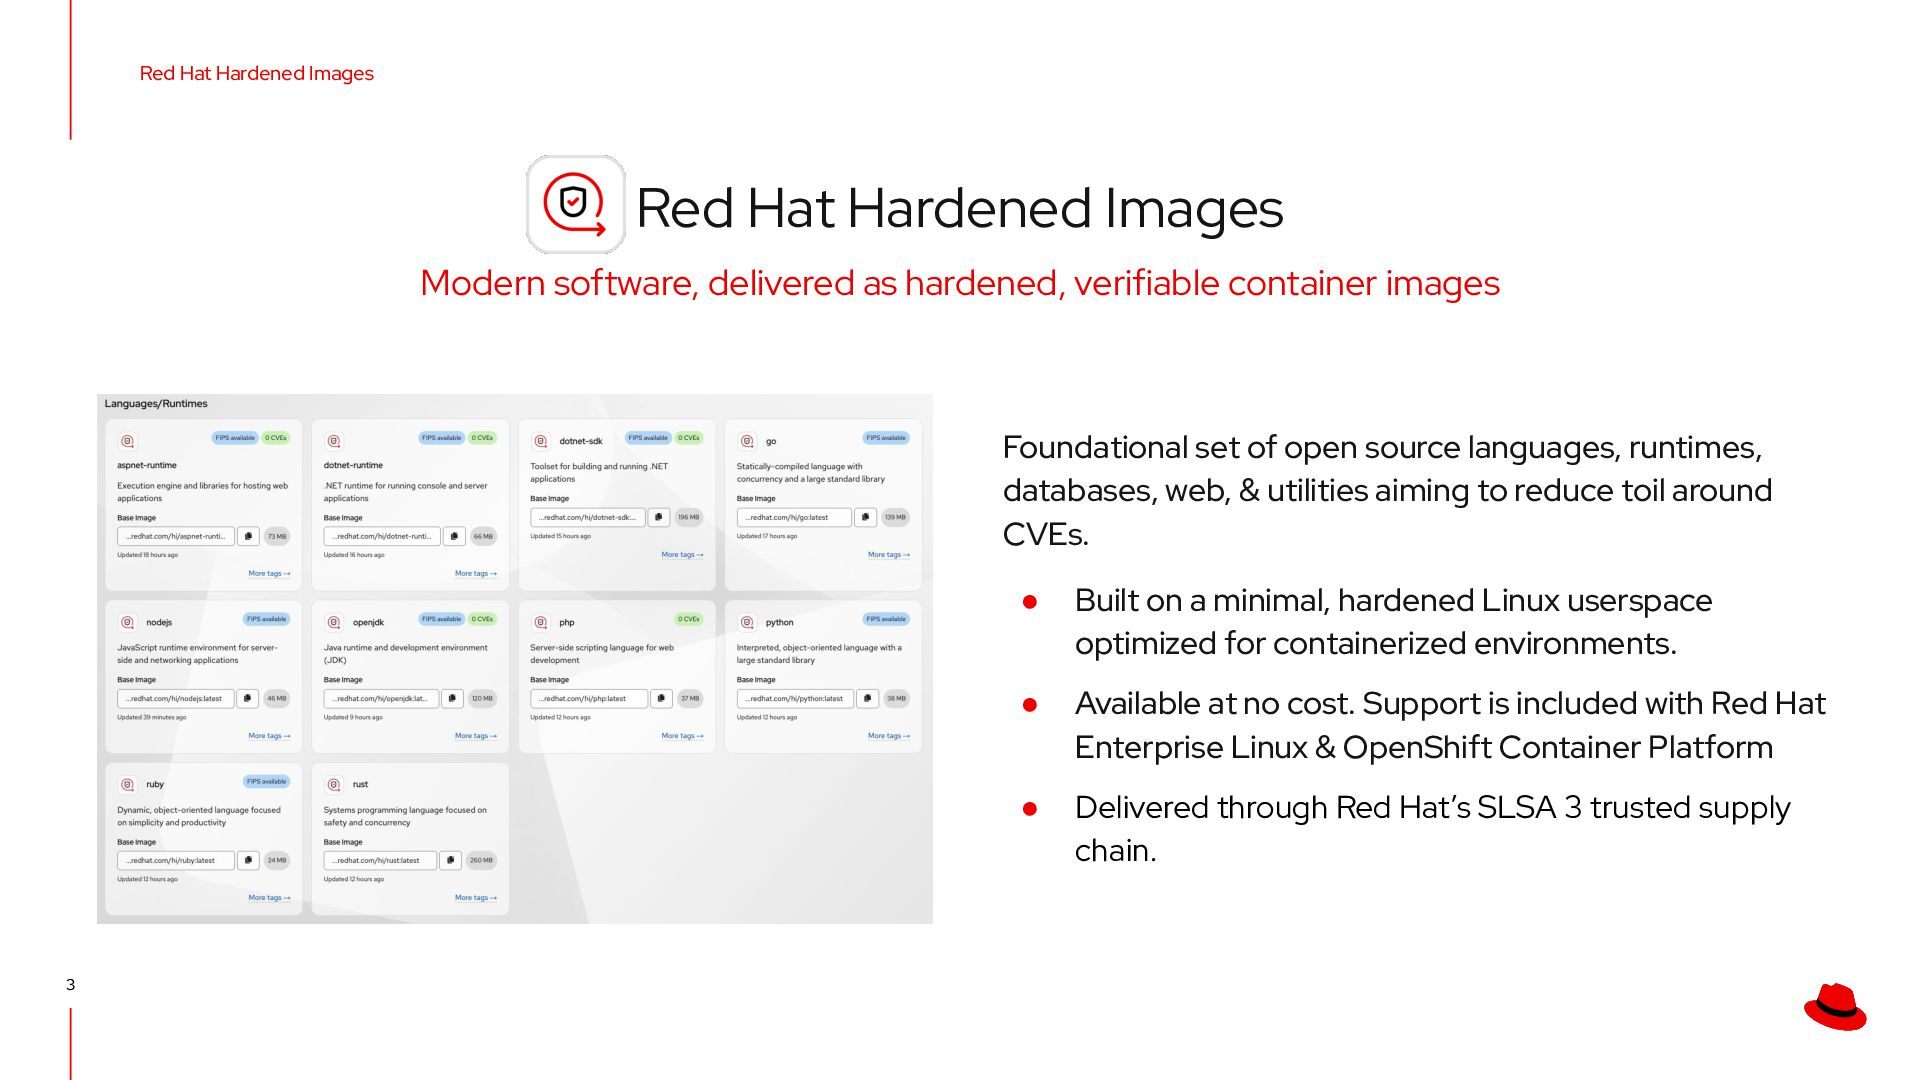
  3. Red Hat Hardened Images Red Hat Hardened Images Modern software,

    delivered as hardened, verifiable container images Foundational set of open source languages, runtimes, databases, web, & utilities aiming to reduce toil around CVEs. 3 • Built on a minimal, hardened Linux userspace optimized for containerized environments. • Available at no cost. Support is included with Red Hat Enterprise Linux & OpenShift Container Platform • Delivered through Red Hat’s SLSA 3 trusted supply chain.
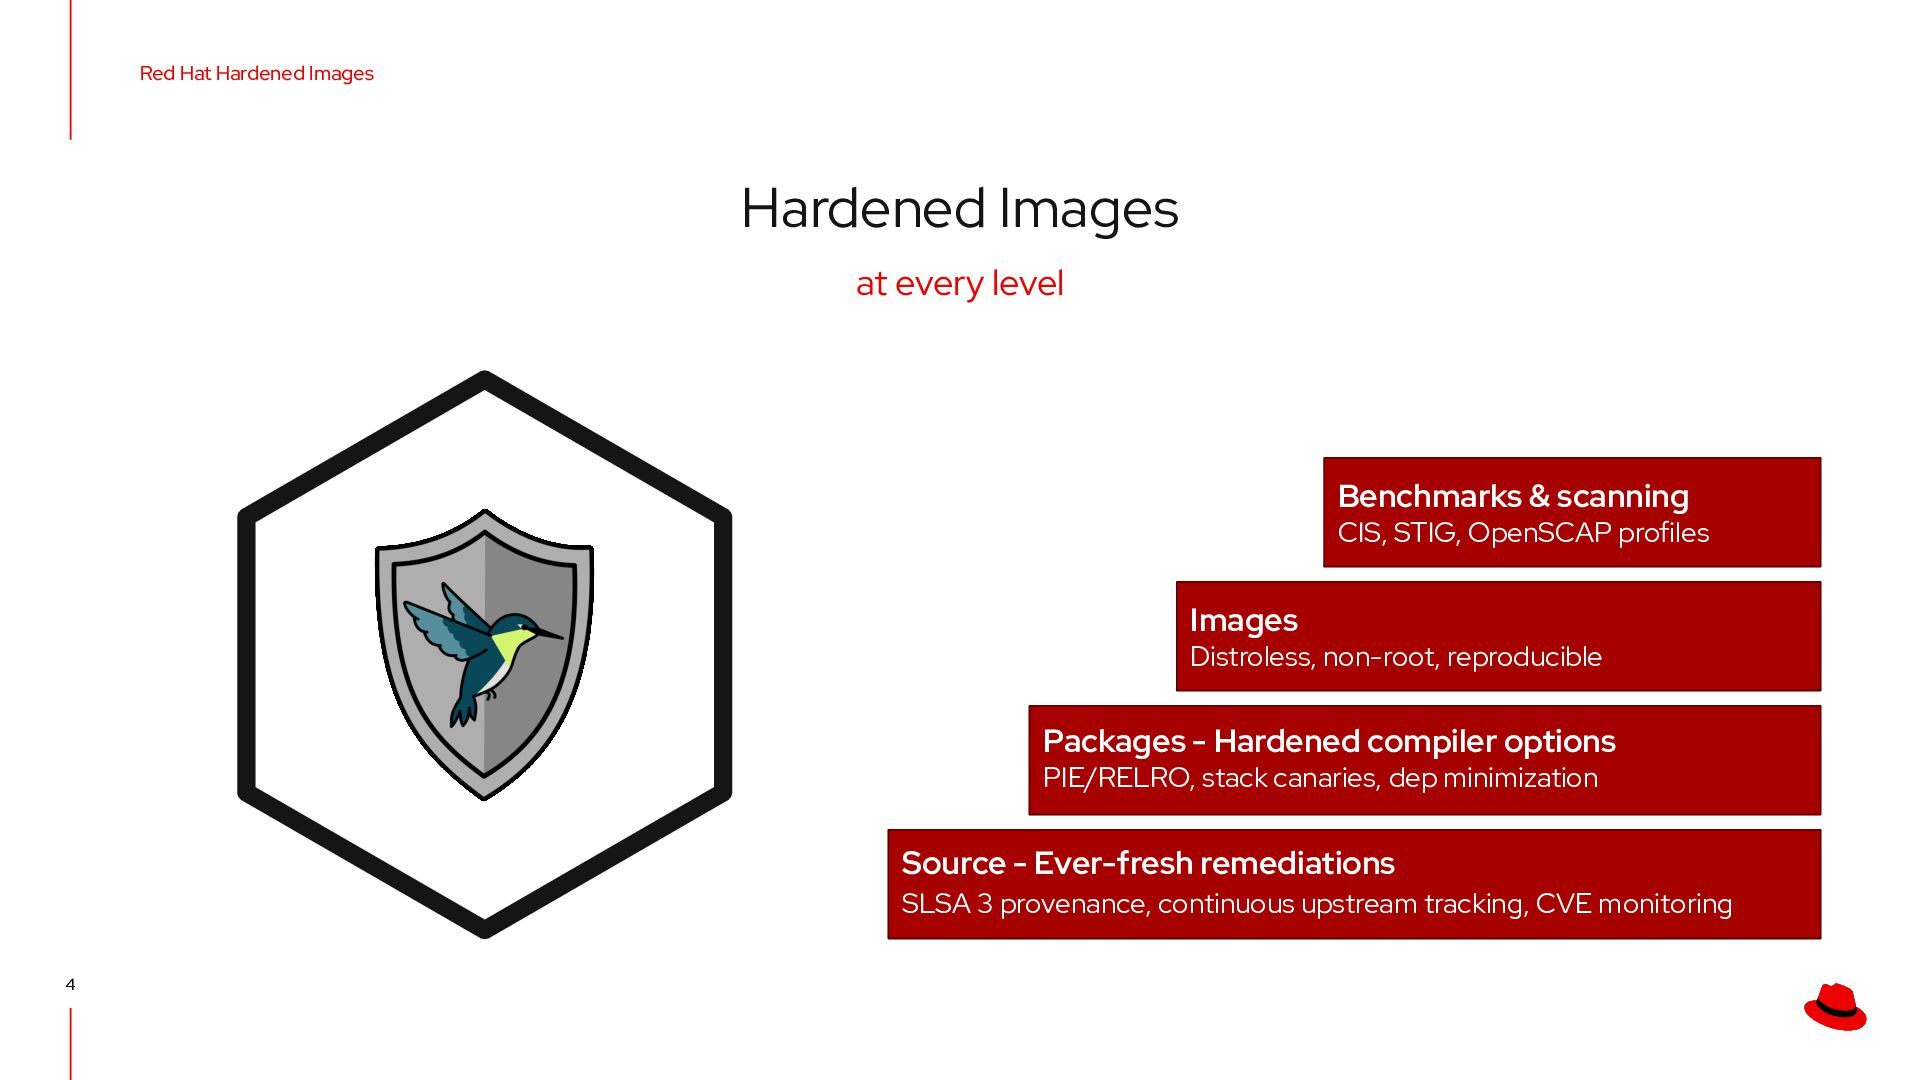
  4. Red Hat Hardened Images Hardened Images at every level Benchmarks

    & scanning CIS, STIG, OpenSCAP profiles Images Distroless, non-root, reproducible Packages - Hardened compiler options PIE/RELRO, stack canaries, dep minimization Source - Ever-fresh remediations SLSA 3 provenance, continuous upstream tracking, CVE monitoring 4
  5. Red Hat Hardened Images Hardened Images reduce friction Different teams

    have disconnected goals and success metrics Security Engineers Love 5 Developers Love • Secure–by-default posture • Clean security scans • Fast remediations to meet internal SLAs • Easy adoption & drop-in compatibility • Anything to make compliance easier • Excellent documentation • Freedom of choice in components and versions
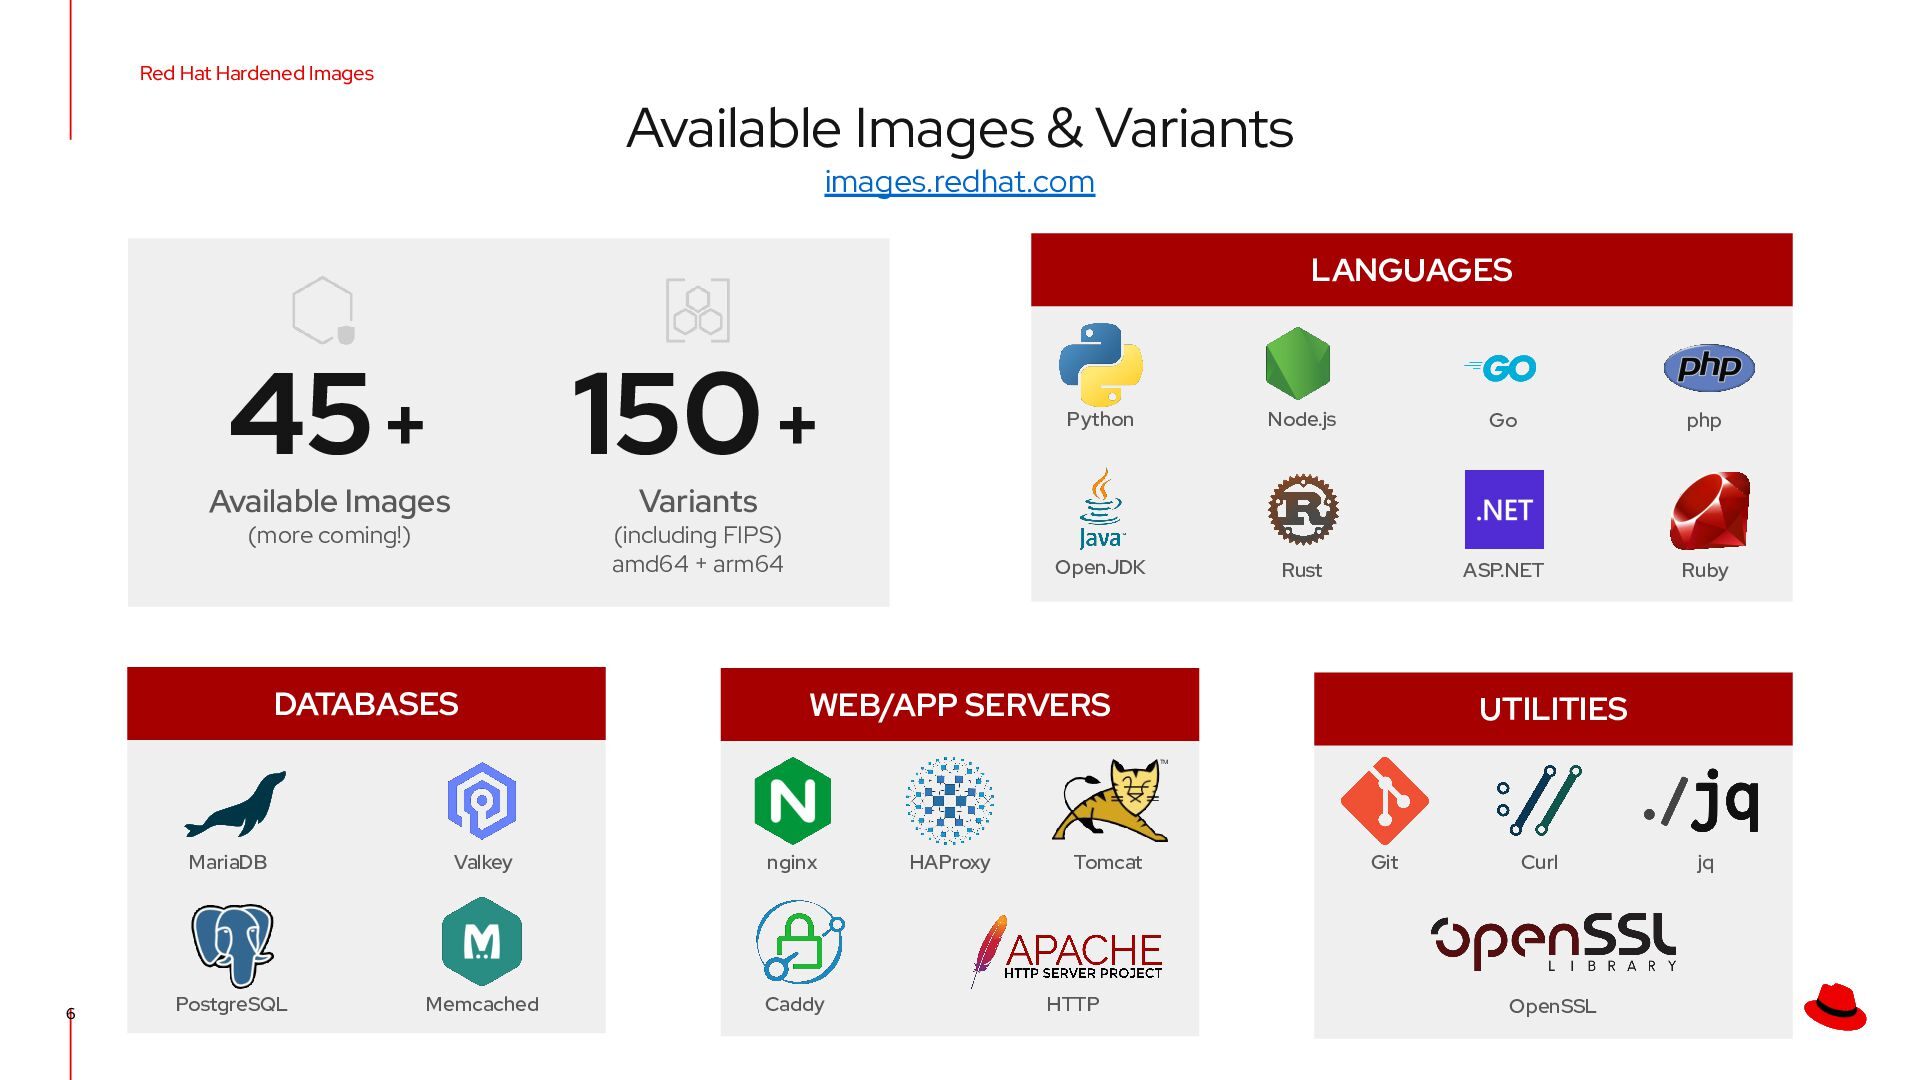
  6. Red Hat Hardened Images Available Images & Variants images.redhat.com LANGUAGES

    45 + 150 + (more coming!) (including FIPS) amd64 + arm64 Available Images Node.js Go php OpenJDK Rust ASP.NET Ruby Variants DATABASES 6 Python WEB/APP SERVERS MariaDB Valkey nginx PostgreSQL Memcached Caddy HAProxy Tomcat HTTP UTILITIES Git Curl OpenSSL jq
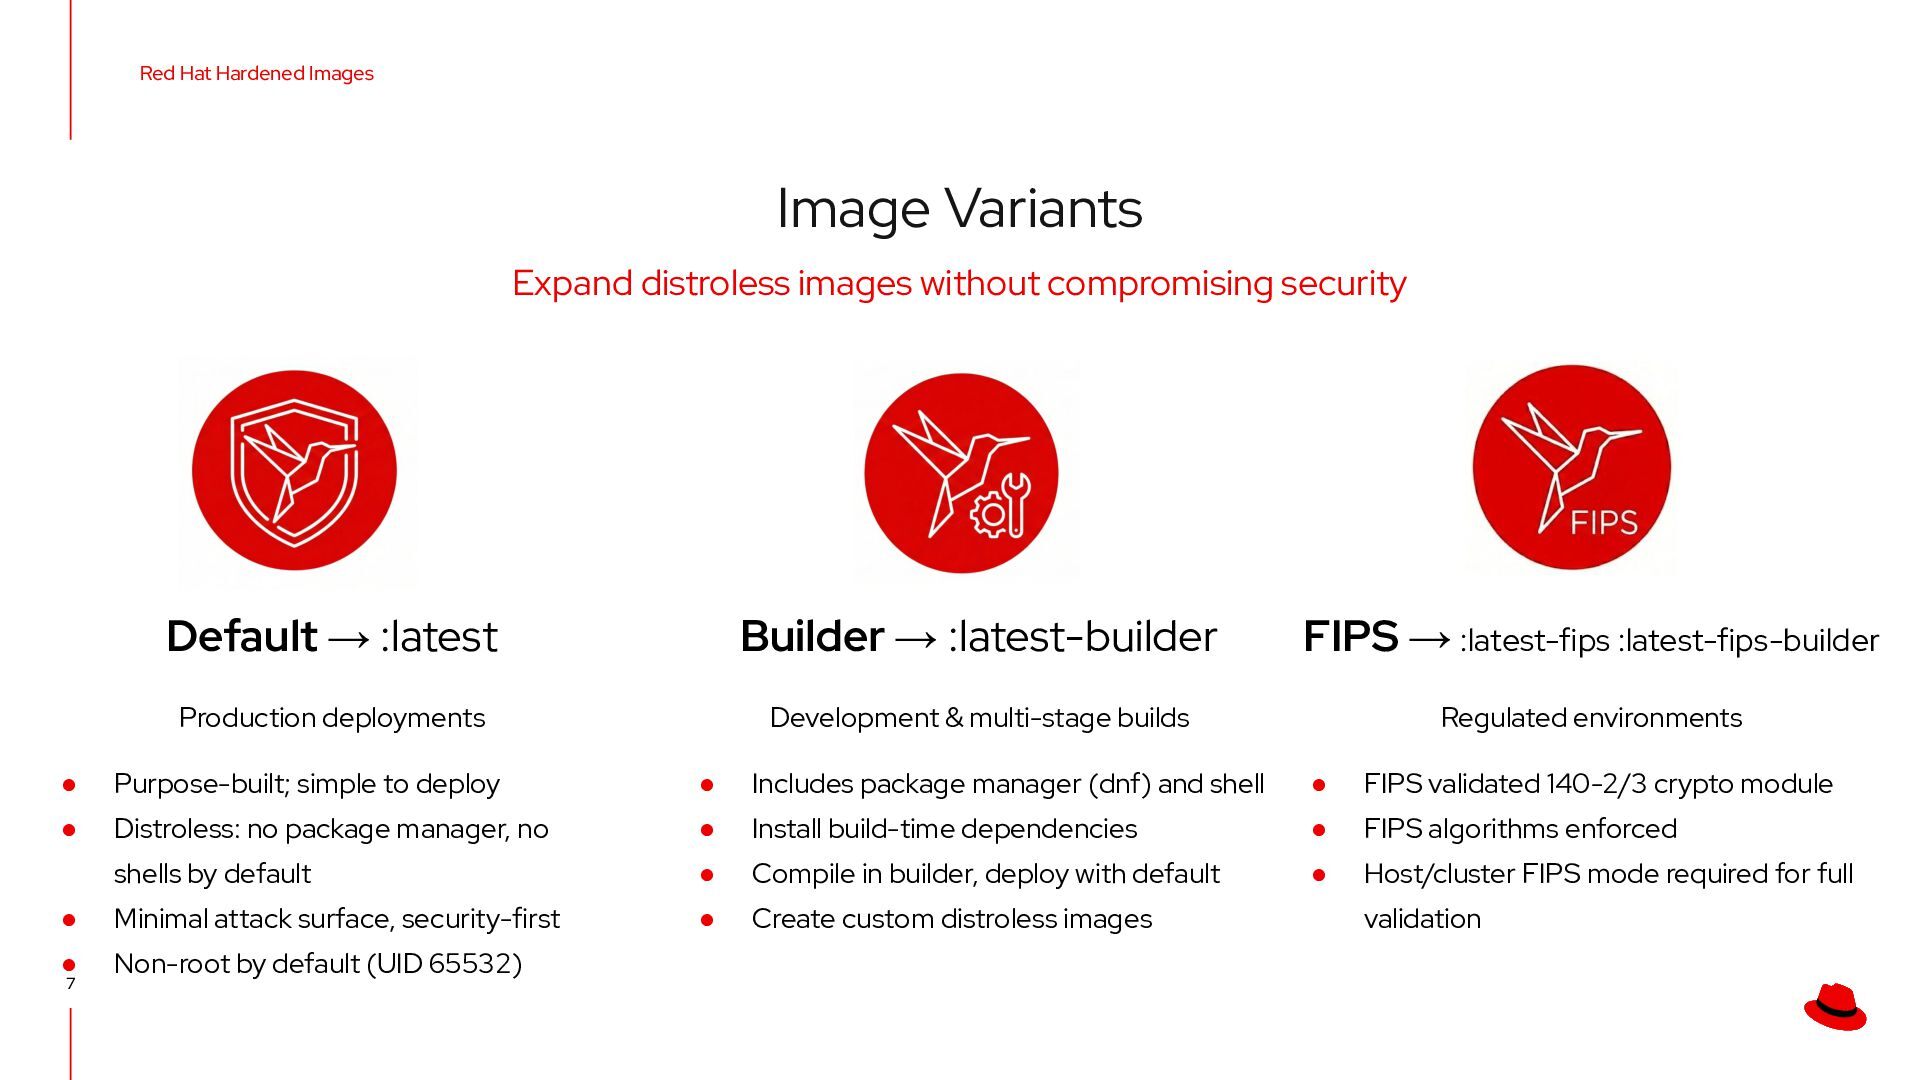
  7. Red Hat Hardened Images Image Variants Expand distroless images without

    compromising security Default → :latest Builder → :latest-builder FIPS → :latest-fips :latest-fips-builder Production deployments Development & multi-stage builds Regulated environments • Purpose-built; simple to deploy • Includes package manager (dnf) and shell • FIPS validated 140-2/3 crypto module • Distroless: no package manager, no • Install build-time dependencies • FIPS algorithms enforced shells by default • Compile in builder, deploy with default • Host/cluster FIPS mode required for full • Minimal attack surface, security-first • Create custom distroless images • Non-root by default (UID 65532) 7 validation
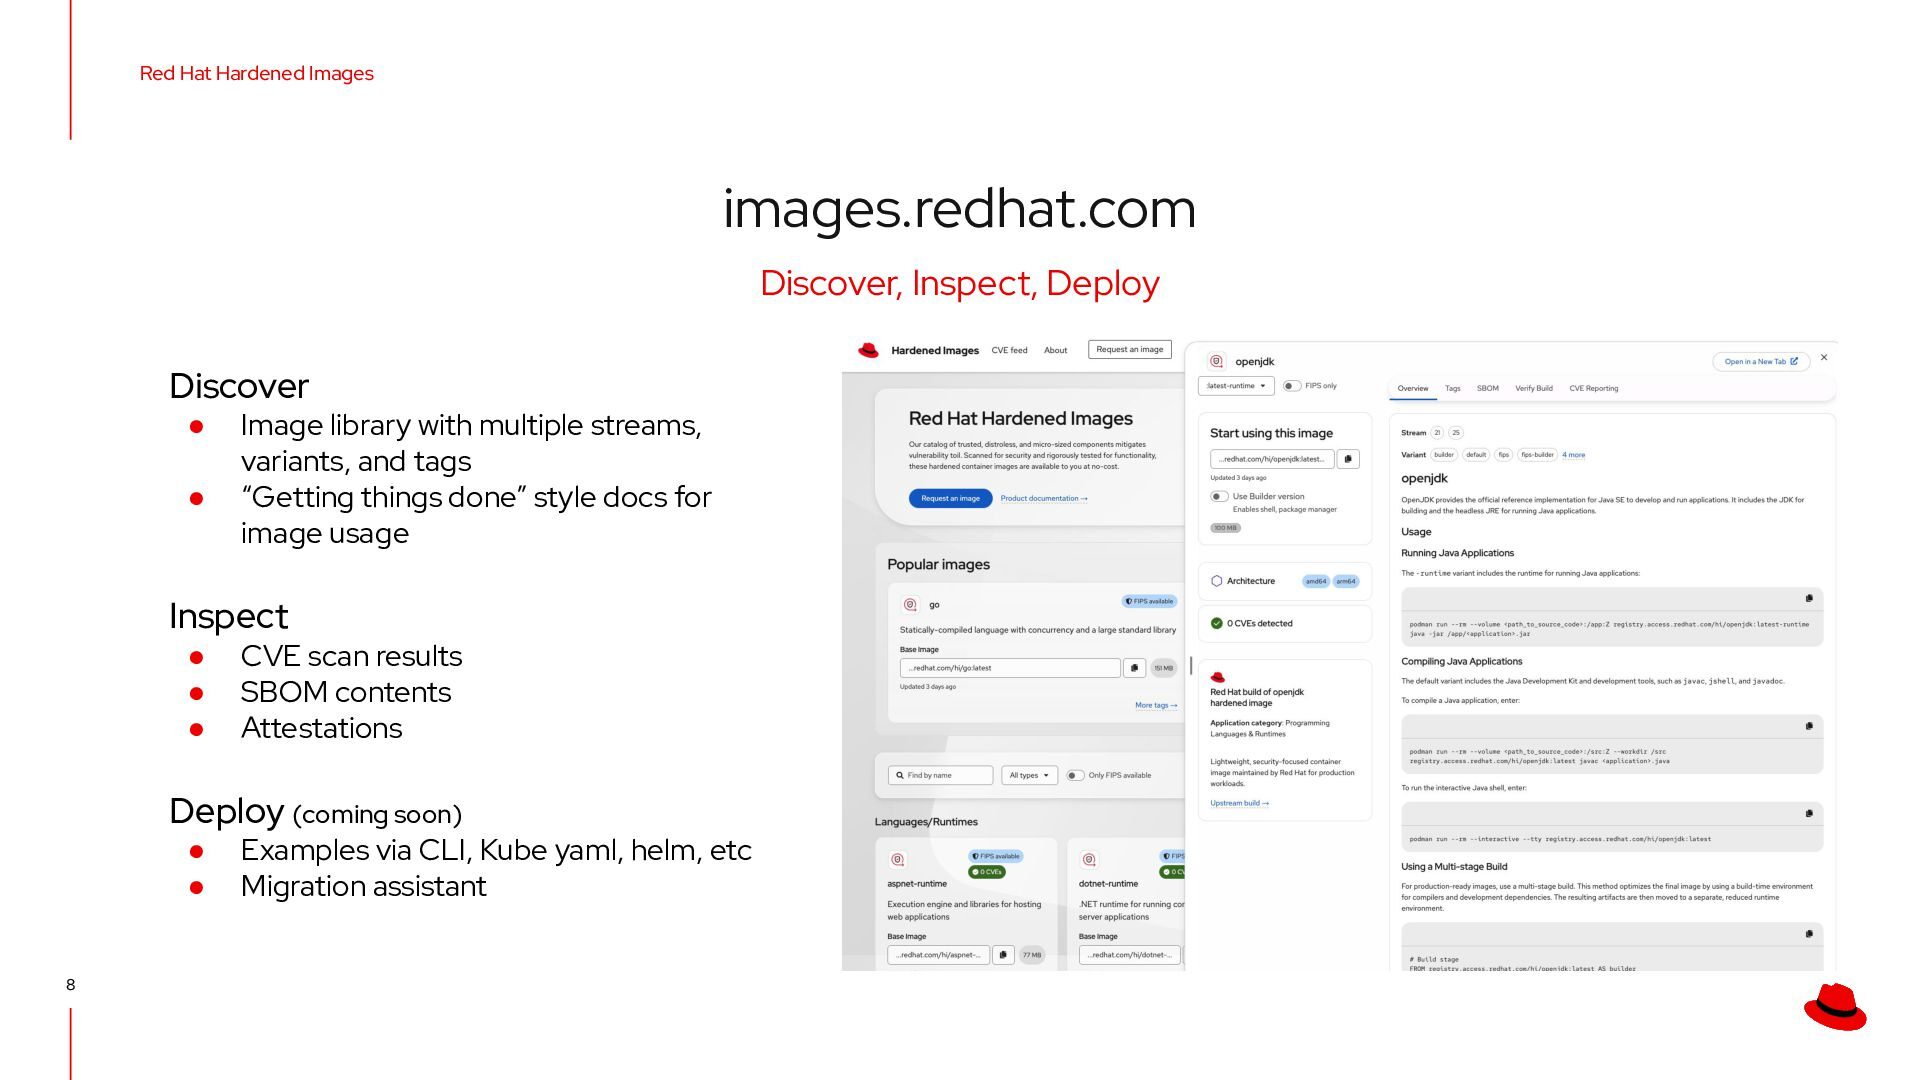
  8. Red Hat Hardened Images images.redhat.com Discover, Inspect, Deploy Discover •

    • Image library with multiple streams, variants, and tags “Getting things done” style docs for image usage Inspect • • • CVE scan results SBOM contents Attestations Deploy (coming soon) • • 8 Examples via CLI, Kube yaml, helm, etc Migration assistant
  9. Red Hat Hardened Images Hummingbird OS Fast. Minimal. Hardened packaging

    A container-native OS that’s always up-to-date • A rolling release model focused on the latest stable upstream • Not a general-purpose distribution - it’s inside the images. • Slimmed dependencies - drop features that are irrelevant for containers • 10 Stats: Package Count: 85% reduction Image Size: 60% smaller CVE Count: Near-zero target Update Frequency: <24hrs typical Build Time: Hermetic, reproducible
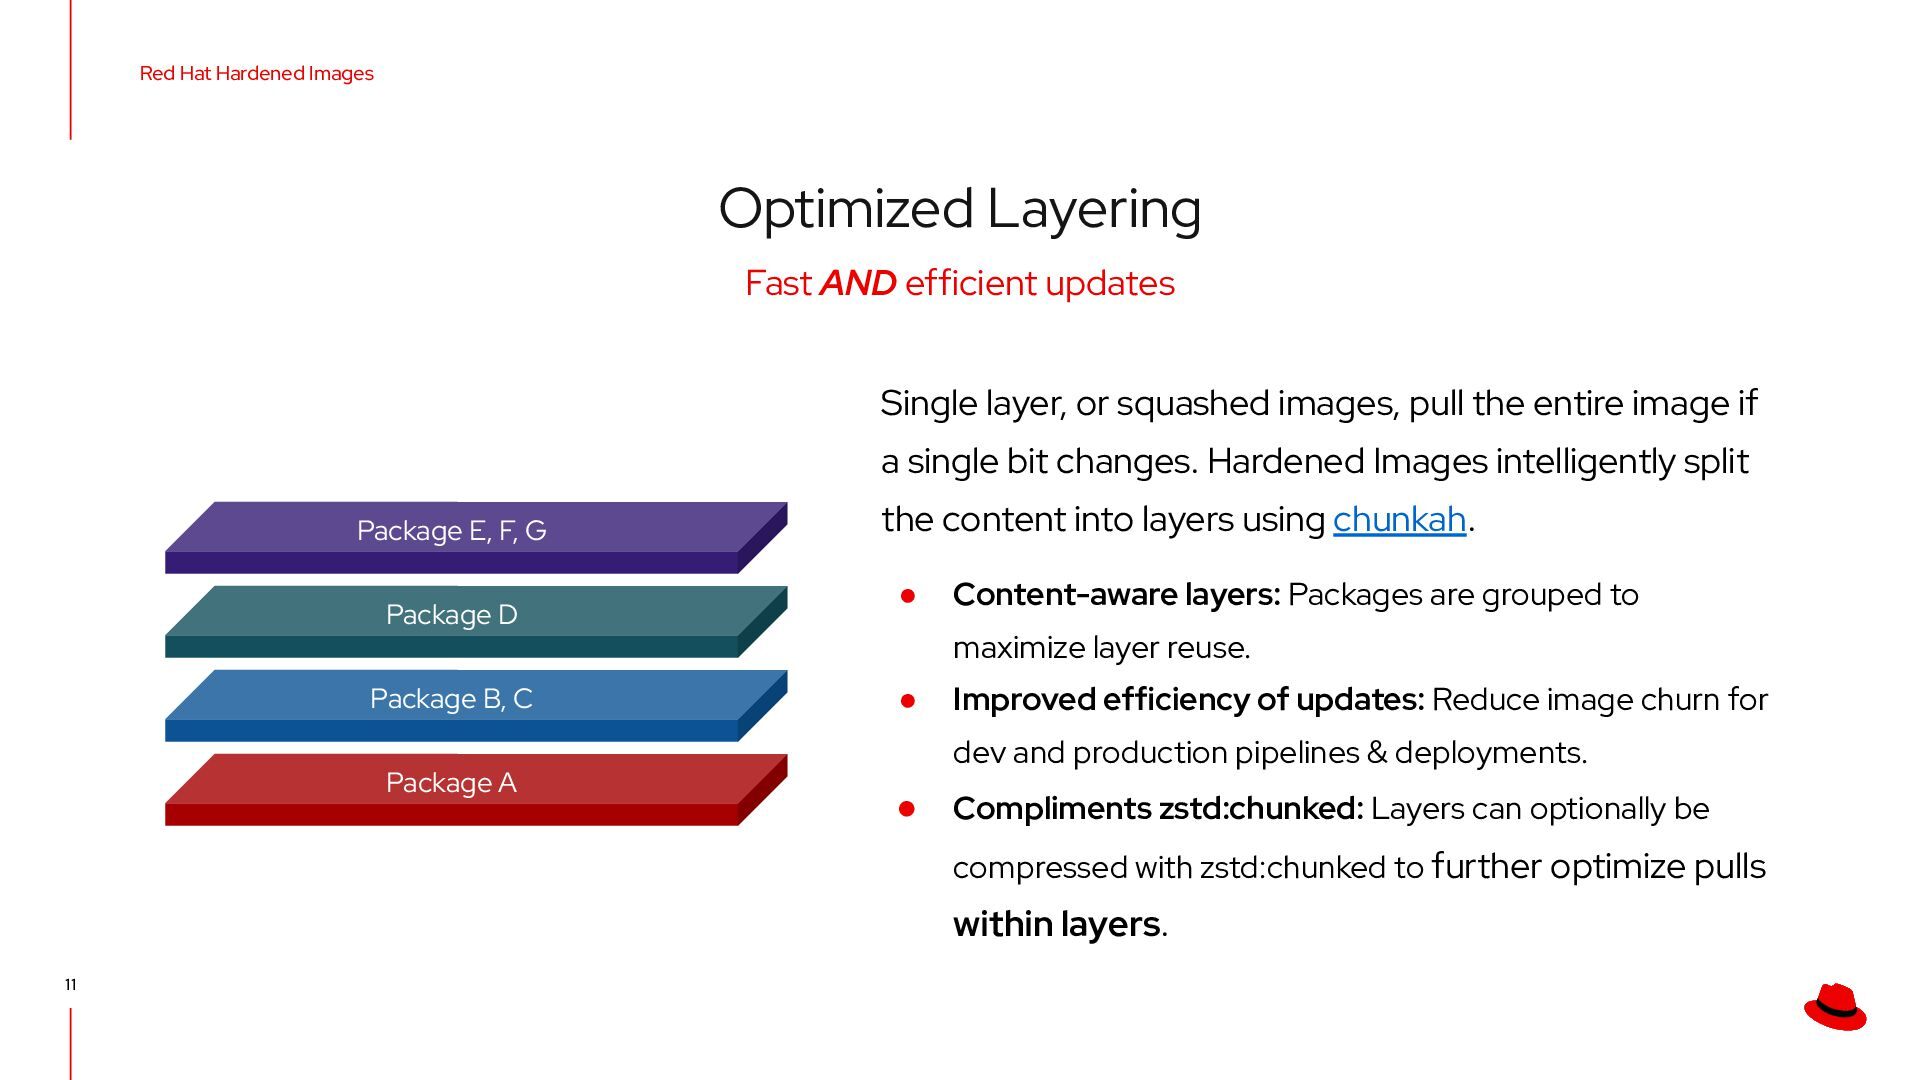
  10. Red Hat Hardened Images Optimized Layering Fast AND efficient updates

    Single layer, or squashed images, pull the entire image if a single bit changes. Hardened Images intelligently split Package E, F, G the content into layers using chunkah. Package D • Package B, C • Package A Content-aware layers: Packages are grouped to maximize layer reuse. Improved efficiency of updates: Reduce image churn for dev and production pipelines & deployments. • Compliments zstd:chunked: Layers can optionally be compressed with zstd:chunked to further optimize pulls within layers. 11
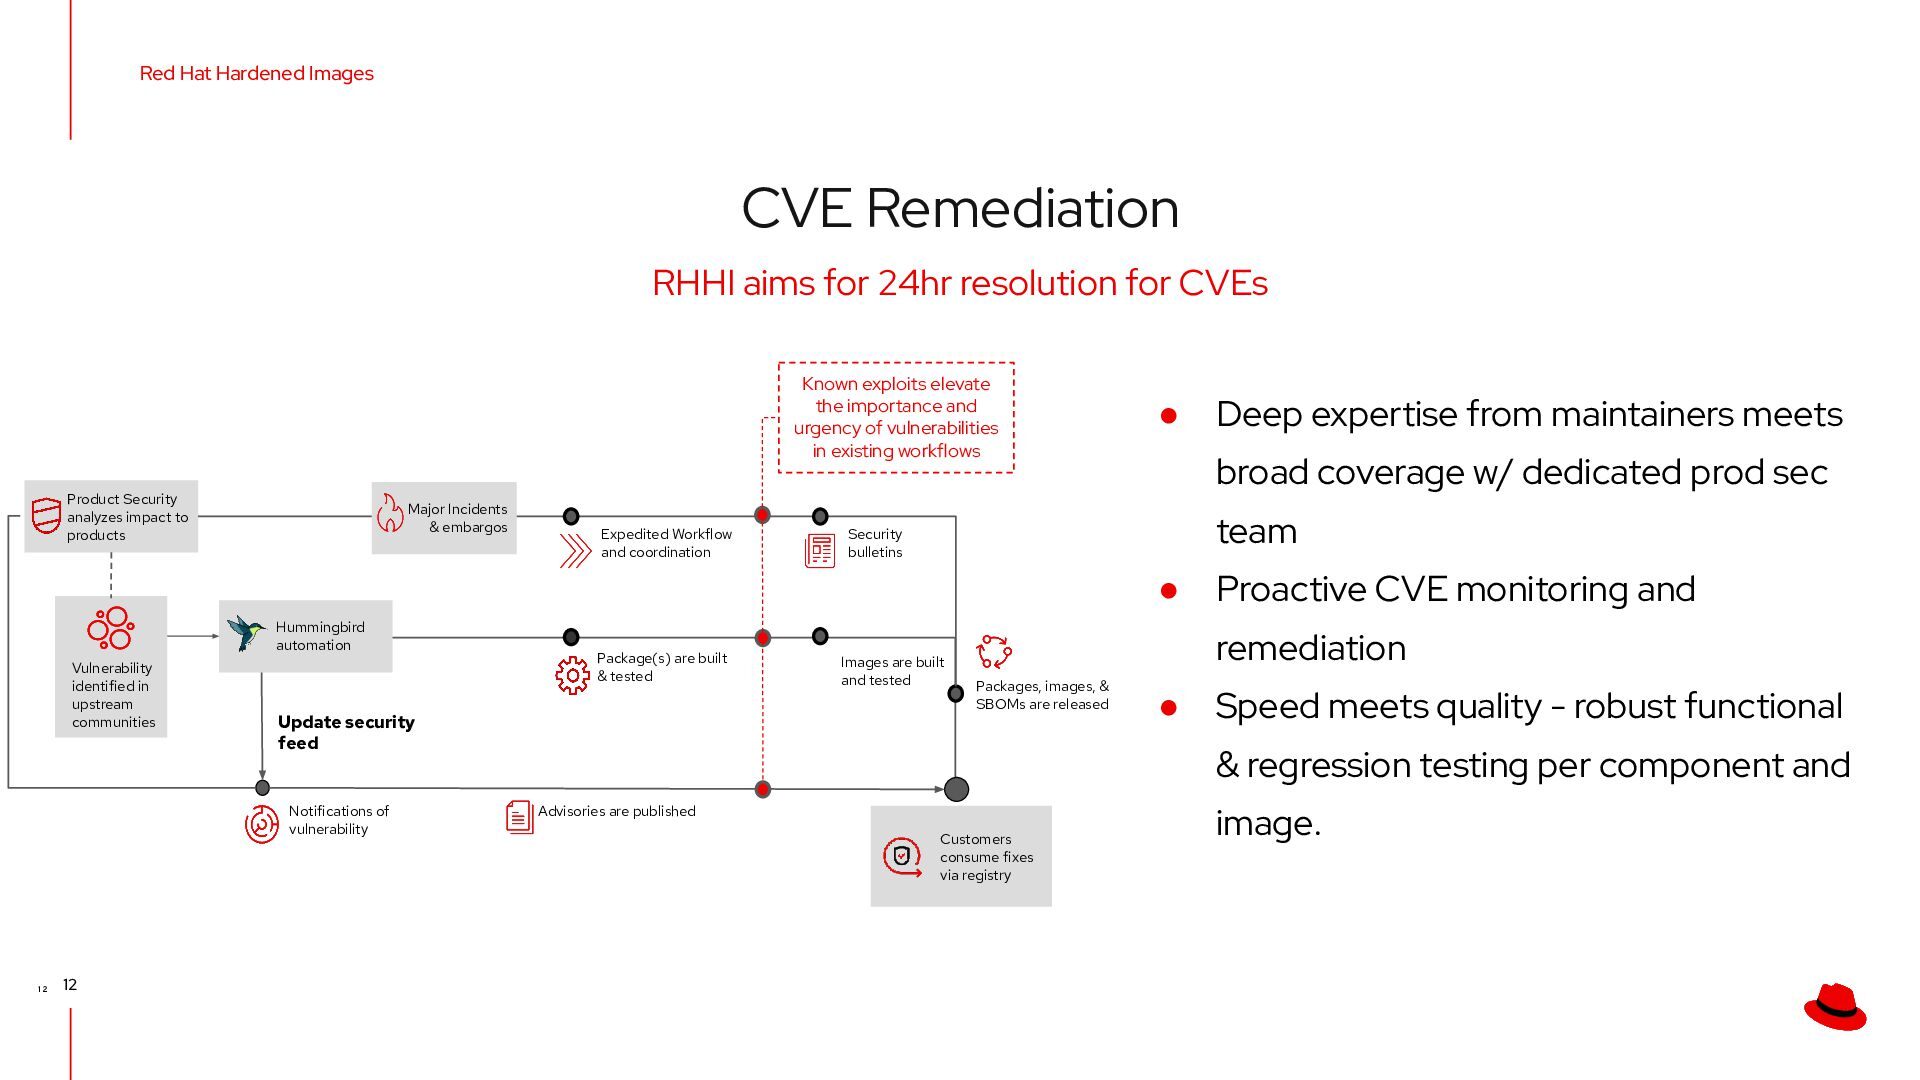
  11. Red Hat Hardened Images CVE Remediation RHHI aims for 24hr

    resolution for CVEs Known exploits elevate the importance and urgency of vulnerabilities in existing workflows Product Security analyzes impact to products Major Incidents & embargos Expedited Workflow and coordination • broad coverage w/ dedicated prod sec team Security bulletins • Hummingbird automation Vulnerability identified in upstream communities Update security feed Notifications of vulnerability 12 12 Package(s) are built & tested Deep expertise from maintainers meets Images are built and tested Proactive CVE monitoring and remediation Packages, images, & SBOMs are released • Speed meets quality - robust functional & regression testing per component and Advisories are published Customers consume fixes via registry image.
  12. Red Hat Hardened Images Consuming image updates Build early and

    often; release as needed Recommend to consume updates automatically • Images are infrastructure agnostic: use what you have to build what you need • Regularly sync to internal container registry (Artifactory, Sonatype, Quay, Docker etc) • Tools like Renovate and Dependabot can automate checking for and applying updates to build pipelines. • Use skopeo to move images across registries or air-gapped environments 13
  13. Red Hat Hardened Images Multi-stage Builds Using builder & default

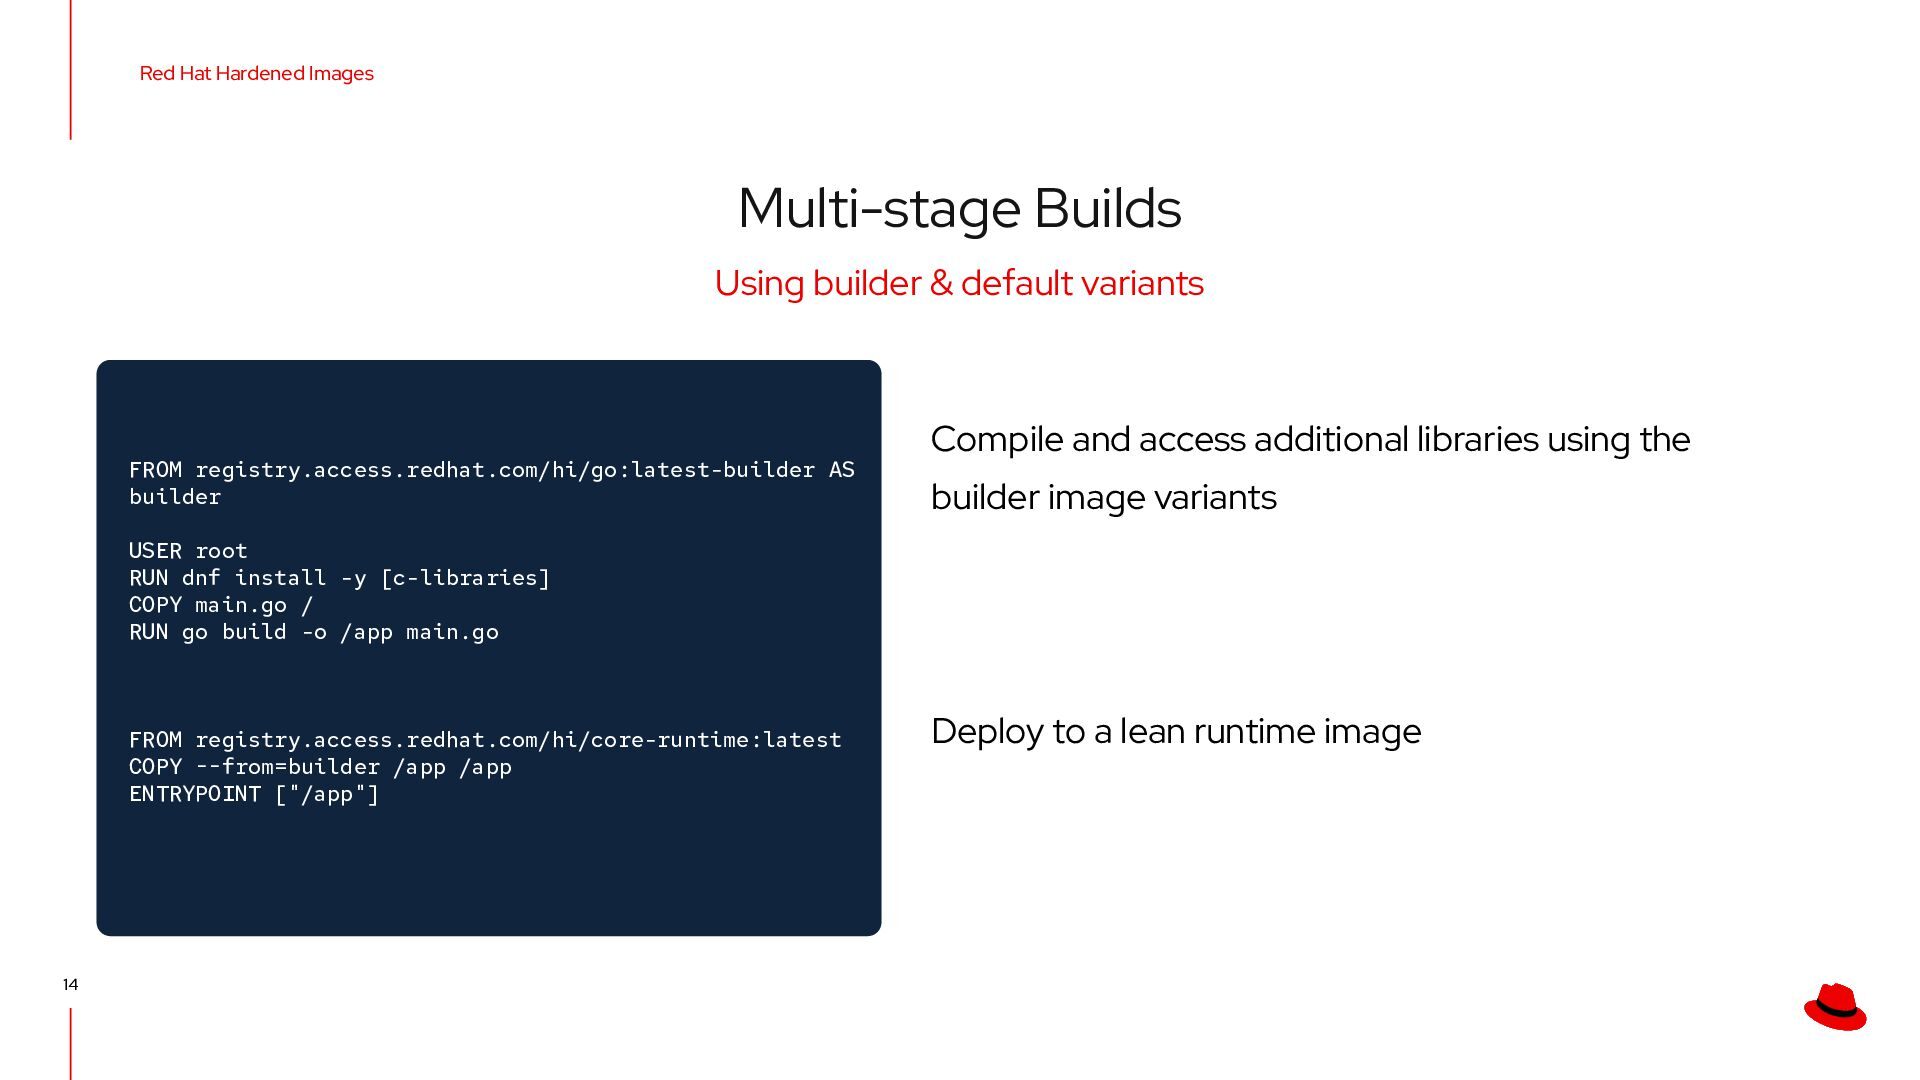
    variants FROM registry.access.redhat.com/hi/go:latest-builder AS builder Compile and access additional libraries using the builder image variants USER root RUN dnf install -y [c-libraries] COPY main.go / RUN go build -o /app main.go FROM registry.access.redhat.com/hi/core-runtime:latest COPY --from=builder /app /app ENTRYPOINT ["/app"] 14 Deploy to a lean runtime image
  14. Red Hat Hardened Images Debugging Different options for different environments

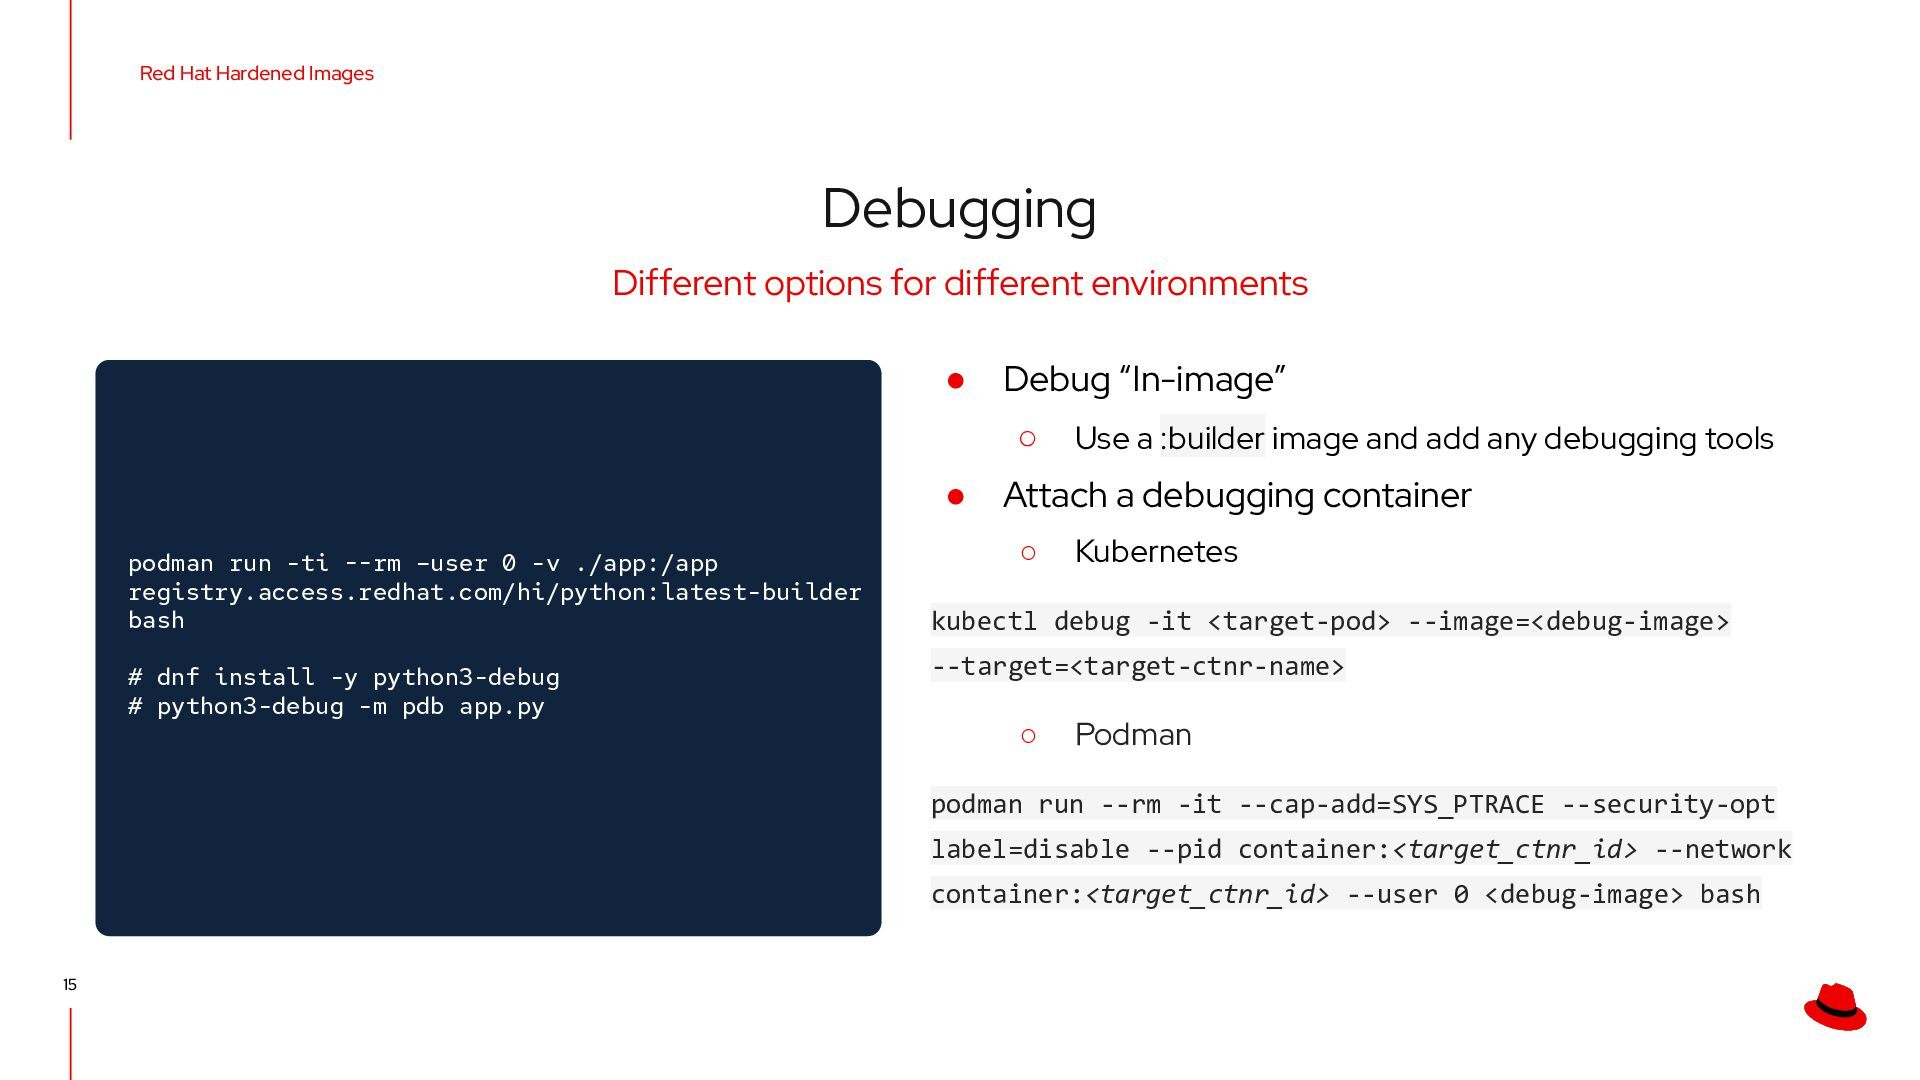
    • Debug “In-image” ◦ • podman run -ti --rm –user 0 -v ./app:/app registry.access.redhat.com/hi/python:latest-builder bash # dnf install -y python3-debug # python3-debug -m pdb app.py Use a :builder image and add any debugging tools Attach a debugging container ◦ Kubernetes kubectl debug -it <target-pod> --image=<debug-image> --target=<target-ctnr-name> ◦ Podman podman run --rm -it --cap-add=SYS_PTRACE --security-opt label=disable --pid container:<target_ctnr_id> --network container:<target_ctnr_id> --user 0 <debug-image> bash 15
  15. Red Hat Hardened Images UBI AND RHHI Freely choose which

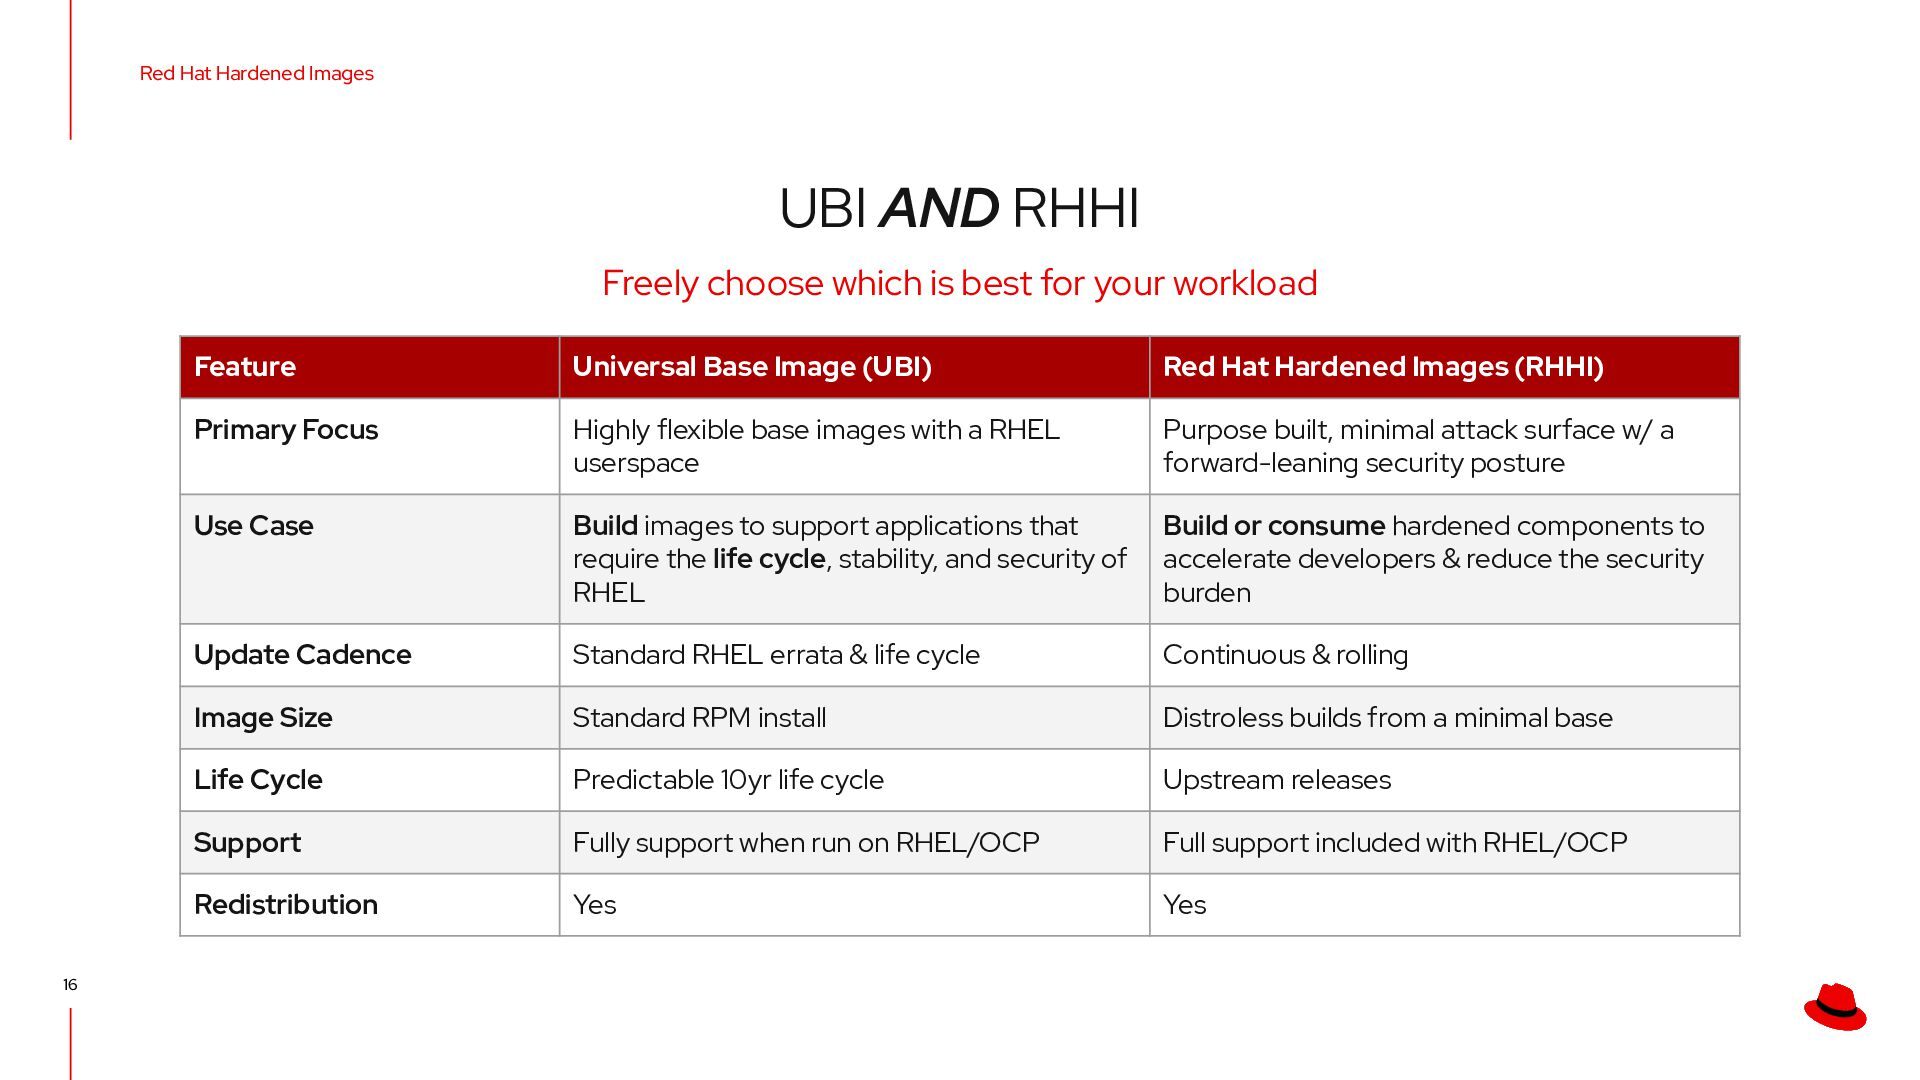
    is best for your workload 16 Feature Universal Base Image (UBI) Red Hat Hardened Images (RHHI) Primary Focus Highly flexible base images with a RHEL userspace Purpose built, minimal attack surface w/ a forward-leaning security posture Use Case Build images to support applications that require the life cycle, stability, and security of RHEL Build or consume hardened components to accelerate developers & reduce the security burden Update Cadence Standard RHEL errata & life cycle Continuous & rolling Image Size Standard RPM install Distroless builds from a minimal base Life Cycle Predictable 10yr life cycle Upstream releases Support Fully support when run on RHEL/OCP Full support included with RHEL/OCP Redistribution Yes Yes
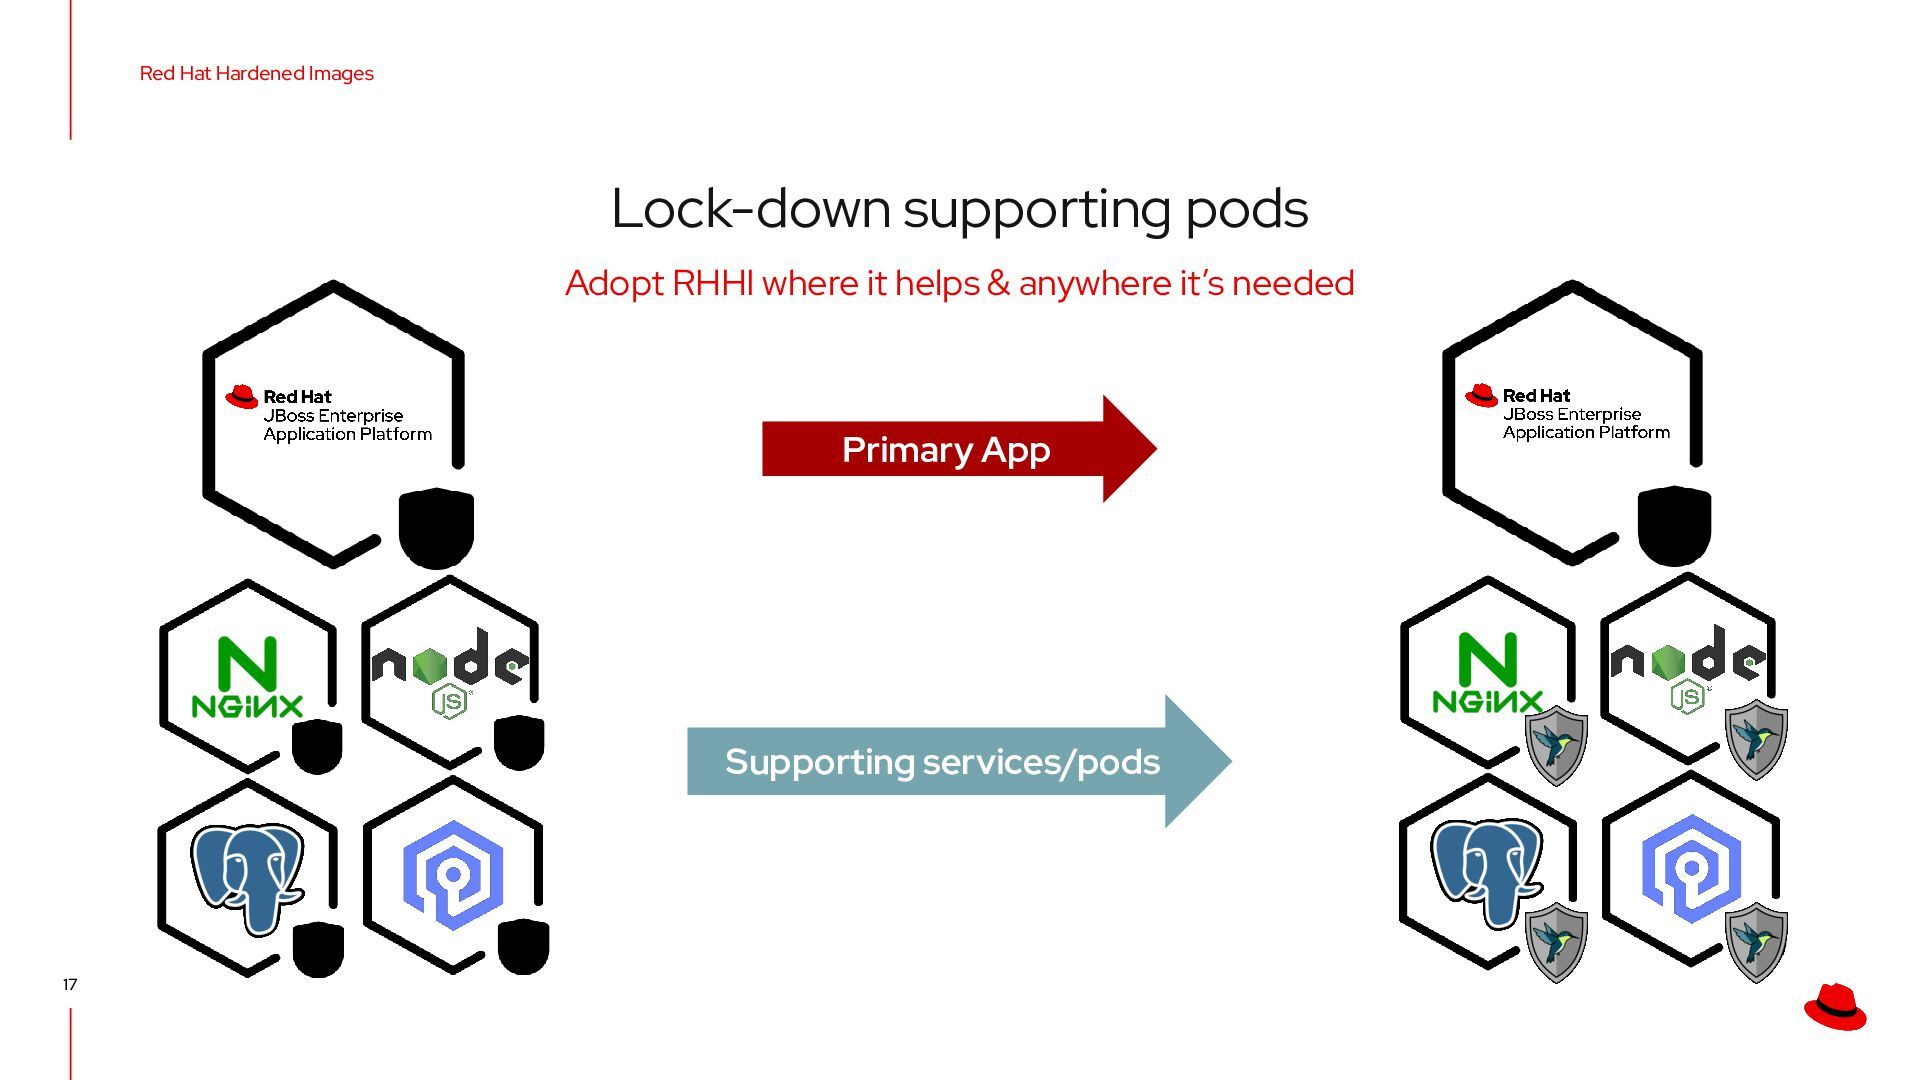
  16. Red Hat Hardened Images Lock-down supporting pods Adopt RHHI where

    it helps & anywhere it’s needed Primary App Supporting services/pods 17
  17. Next sessions: Red Hat OpenShift Webinar Skill Builders (Red Hat

    Training and Certification) Own the platform: Your roadmap to expertise in OpenShift administration July 15th 2026, 10:00 a.m. CEST (UTC+ 2)
  18. Tech Journey: Explore. Test. Scale. Red Hat Ansible Automation Platform

    Tech Journey hub Red Hat OpenShift Virtualization Tech Journey hub Red Hat OpenShift AI Tech Journey hub Red Hat Enterprise Linux Tech Journey hub Red Hat Security Tech Journey hub Red Hat OpenShift Tech Journey hub Red Hat Network Automation Tech Journey hub
  19. Update confidential designator here Thank you Red Hat is the

    world’s leading provider of enterprise open source software solutions. Award-winning support, training, and consulting services make Red Hat a trusted adviser to the Fortune 500. linkedin.com/company/red-hat facebook.com/redhatinc youtube.com/user/RedHatVideos twitter.com/RedHat 20 Version number here V00000
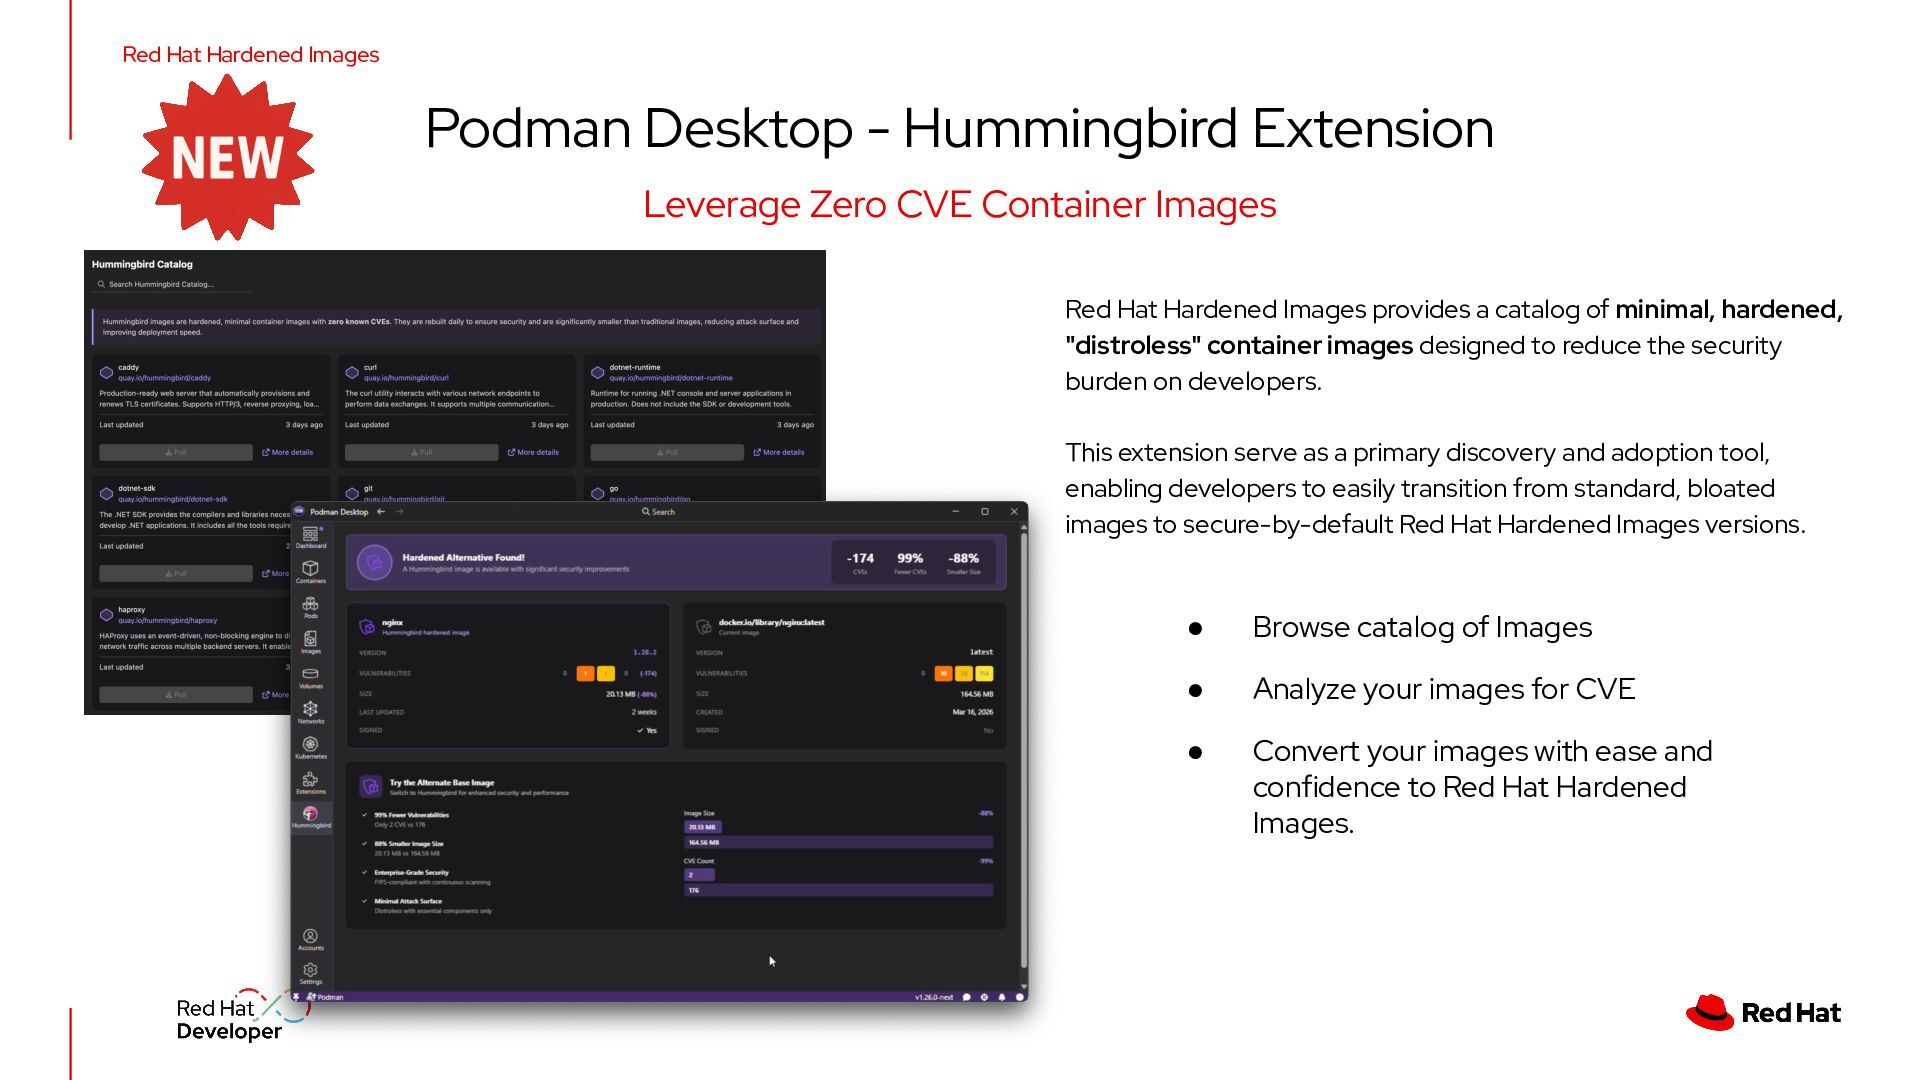
  20. Red Hat Hardened Images Podman Desktop - Hummingbird Extension Leverage

    Zero CVE Container Images Red Hat Hardened Images provides a catalog of minimal, hardened, "distroless" container images designed to reduce the security burden on developers. This extension serve as a primary discovery and adoption tool, enabling developers to easily transition from standard, bloated images to secure-by-default Red Hat Hardened Images versions. • Browse catalog of Images • Analyze your images for CVE • Convert your images with ease and confidence to Red Hat Hardened Images.