Upgrade to Pro
— share decks privately, control downloads, hide ads and more …
Speaker Deck
Sign up for free
Menu
Search
Features
All features
Private URLs
Password Protection
Custom URLS
Scheduled publishing
Remove Branding
Restrict embedding
Deck Collections
Notes
Features
All features
Private URLs
Password Protection
Custom URLS
Scheduled publishing
Remove Branding
Restrict embedding
Deck Collections
Notes
Explore
Featured decks
Featured speakers
Programming
Technology
Storyboards
Explore
Featured decks
Featured speakers
Programming
Technology
Storyboards
Pricing
Search
Sign in
Sign up for free
Going Password-Free
Search
Eric Mann
February 03, 2017
Technology
240
0
Share
Embed
Copy iframe code
Copy JS code
Copy link
Start on current slide
Going Password-Free
Passwordless authentication via Tozny as presented at SunshinePHP 2017
Eric Mann
February 03, 2017
More Decks by Eric Mann
See All by Eric Mann
The Commit You Can't Take Back: Conscience in a Career That Builds the Future
ericmann
0
26
Break It, Then Fix It: An OWASP Top 10 Workshop for PHP Developers
ericmann
0
45
Kubernetes for PHP Developers: From Docker Compose to Production
ericmann
0
95
Semantic Search and Embeddings: Modernizing PHP Search with Vector Databases
ericmann
0
110
Evolution of PHP Security
ericmann
0
160
PHP, Meet AI
ericmann
0
140
Asynchronous Awesome
ericmann
0
240
WordPress, Meet AI
ericmann
0
110
Cooking with Credentials
ericmann
0
93
Other Decks in Technology
See All in Technology
AI Agent 時代のデータ基盤: ClickHouse で実現する 超高速分析とコスト削減の両立
jozono
0
120
Active Directory と Entra ID のむむむな関係
murachiakira
PRO
0
460
自律的なチームを作るためにTechPMがやらないこと
ny7760
0
500
2026 Apache Flink Community Checkpoint
rmetzger
0
140
Building Audio Plugin Ecosystem for Android in 2026
atsushieno
2
140
re:Invent の去年のスケジュールを公開します!
miu_crescent
PRO
0
270
eBPF 簡介 2026 版
shunghsiyu
0
170
Jev の中身は50行で再現できる。でも本物との差はどこにあるのか
hisuzuya
0
290
SLOを阻む不安
sraku2159
0
220
[re:Invent2026事前勉強会(有志開催)]続きは、ラスベガスの廊下で / continue-in-the-vegas-hallway
sh_fk2
0
500
あなたのDartコードは丸見えかもしれない ~reFlutterで暴くFlutterアプリの中身と多層防御~
zozotech
PRO
0
770
20261016_Nagoya Tech Talk #4 データ活用のリアル AIも人も間違える
bessaralink55
0
160
Featured
See All Featured
The World Runs on Bad Software
bkeepers
PRO
72
12k
The Cult of Friendly URLs
andyhume
79
7.1k
Fantastic passwords and where to find them - at NoRuKo
philnash
53
4k
Prompt Engineering for Job Search
mfonobong
0
570
Making Projects Easy
brettharned
120
6.8k
AI Search: Where Are We & What Can We Do About It?
aleyda
0
8.2k
How GitHub (no longer) Works
holman
316
150k
Optimising Largest Contentful Paint
csswizardry
37
4k
Building the Perfect Custom Keyboard
takai
2
940
Jess Joyce - The Pitfalls of Following Frameworks
techseoconnect
PRO
1
470
[RailsConf 2023 Opening Keynote] The Magic of Rails
eileencodes
31
10k
Organizational Design Perspectives: An Ontology of Organizational Design Elements
kimpetersen
PRO
1
870
Transcript
Going Password-Free Sunshine PHP 2017
90
19
hunter2
None
How can we fix it? Password managers help Password strength
meters (zxcvbn) help Two-factor authentication helps But why require a password at all?
None
A PHP Example Defer to a 3rd party for email
& validation Use the SlimPHP framework for quick bootstrapping Allow either password or password-less authentication
Authentication Provider Free developer preview Powers both link-based and push-based
auth Supports PHP (and other langs)
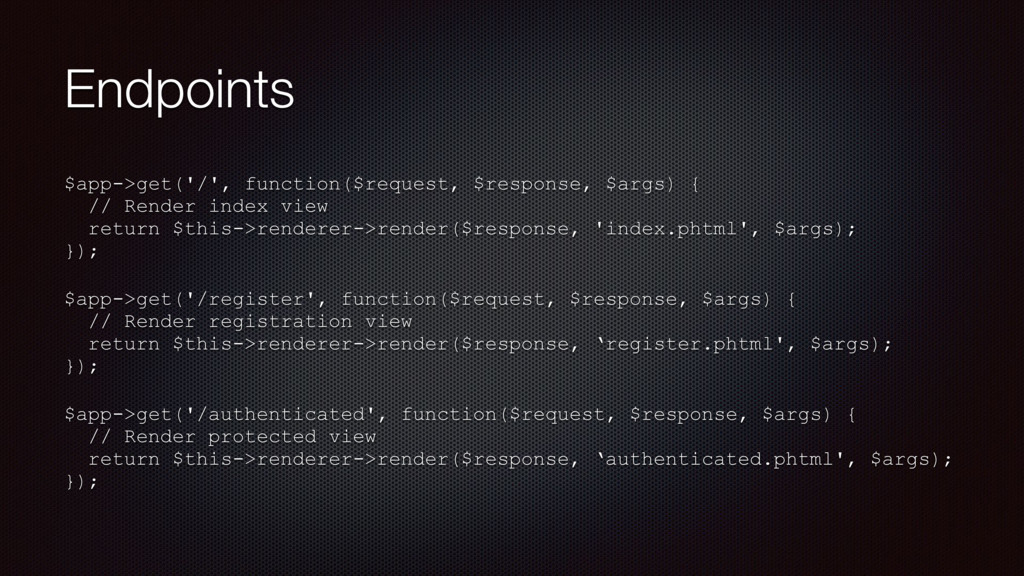
Endpoints $app->get('/', function($request, $response, $args) { // Render index view
return $this->renderer->render($response, 'index.phtml', $args); }); $app->get('/register', function($request, $response, $args) { // Render registration view return $this->renderer->render($response, ‘register.phtml', $args); }); $app->get('/authenticated', function($request, $response, $args) { // Render protected view return $this->renderer->render($response, ‘authenticated.phtml', $args); });
Endpoints $app->get('/authenticated', function($request, $response, $args) { if ( !
isset( $_SESSION['username'] ) || ! $this->users->get( $_SESSION['username'] ) ) { return $response->withRedirect('/?error=notloggedin'); } // Render protected view return $this->renderer->render($response, ‘authenticated.phtml', $args); });
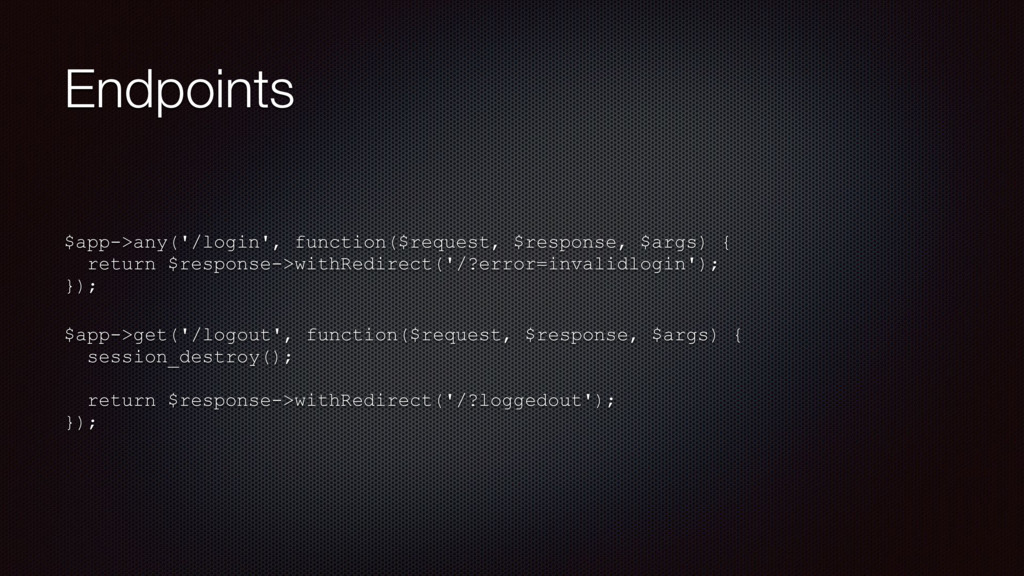
Endpoints $app->any('/login', function($request, $response, $args) { return $response->withRedirect('/?error=invalidlogin'); }); $app->get('/logout',
function($request, $response, $args) { session_destroy(); return $response->withRedirect('/?loggedout'); });
None
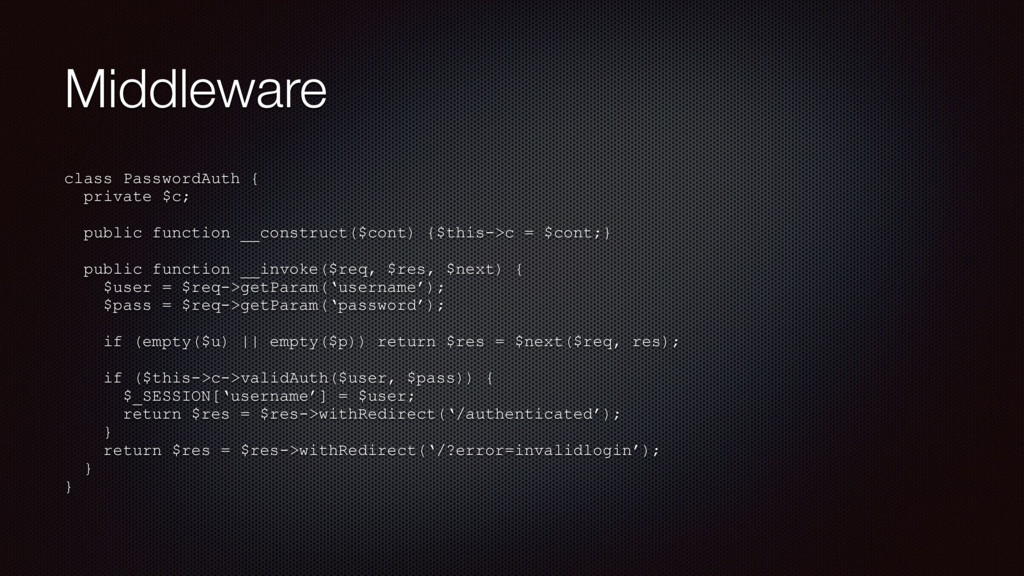
Middleware class PasswordAuth { private $c; public function __construct($cont)
{$this->c = $cont;} public function __invoke($req, $res, $next) { $user = $req->getParam(‘username’); $pass = $req->getParam(‘password’); if (empty($u) || empty($p)) return $res = $next($req, res); if ($this->c->validAuth($user, $pass)) { $_SESSION[‘username’] = $user; return $res = $res->withRedirect(‘/authenticated’); } return $res = $res->withRedirect(‘/?error=invalidlogin’); } }
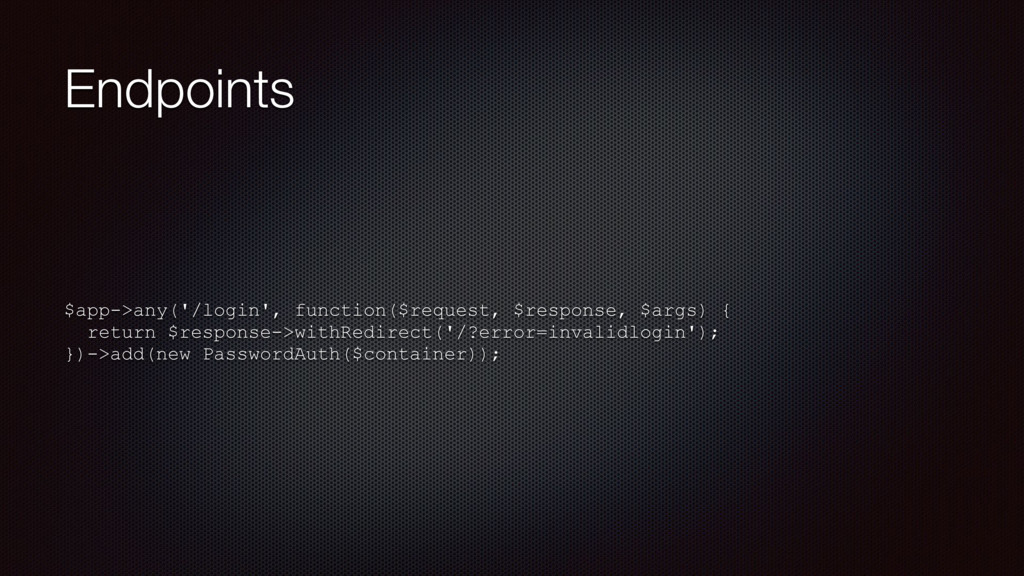
Endpoints $app->any('/login', function($request, $response, $args) { return $response->withRedirect('/?error=invalidlogin'); })->add(new PasswordAuth($container));
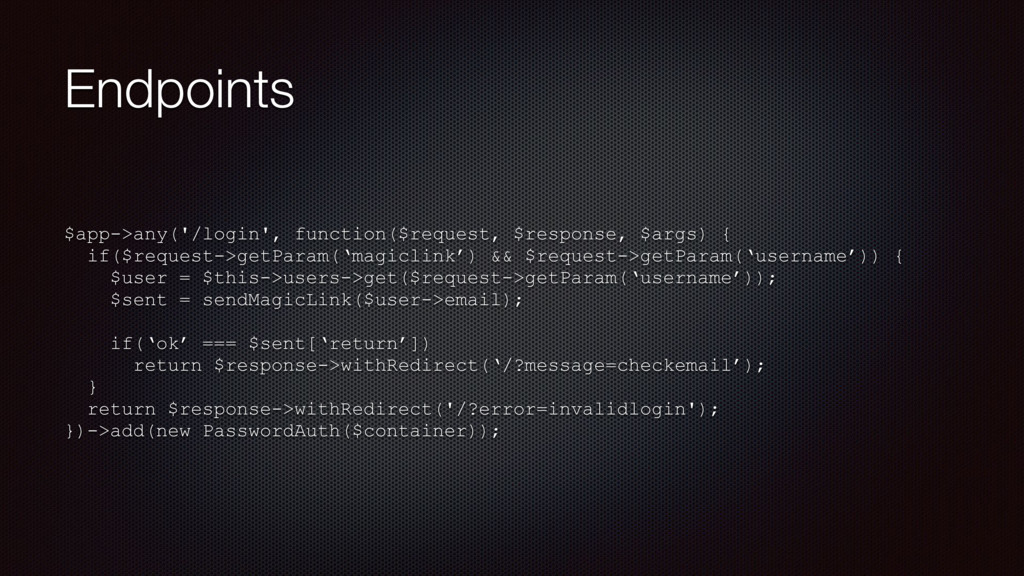
Endpoints $app->any('/login', function($request, $response, $args) { if($request->getParam(‘magiclink’) && $request->getParam(‘username’)) {
$user = $this->users->get($request->getParam(‘username’)); $sent = sendMagicLink($user->email); if(‘ok’ === $sent[‘return’]) return $response->withRedirect(‘/?message=checkemail’); } return $response->withRedirect('/?error=invalidlogin'); })->add(new PasswordAuth($container));
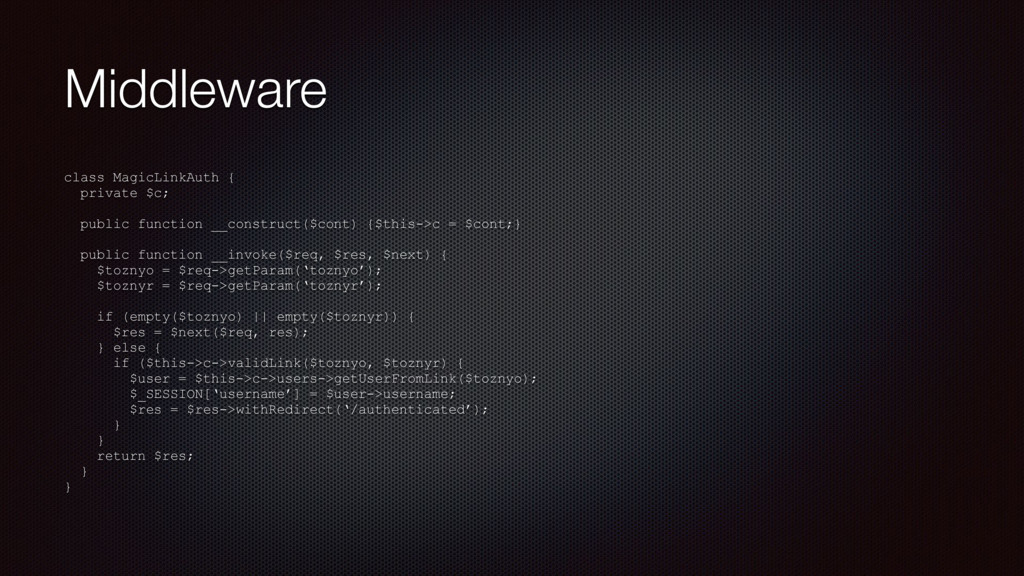
Middleware class MagicLinkAuth { private $c; public function __construct($cont)
{$this->c = $cont;} public function __invoke($req, $res, $next) { $toznyo = $req->getParam(‘toznyo’); $toznyr = $req->getParam(‘toznyr’); if (empty($toznyo) || empty($toznyr)) { $res = $next($req, res); } else { if ($this->c->validLink($toznyo, $toznyr) { $user = $this->c->users->getUserFromLink($toznyo); $_SESSION[‘username’] = $user->username; $res = $res->withRedirect(‘/authenticated’); } } return $res; } }
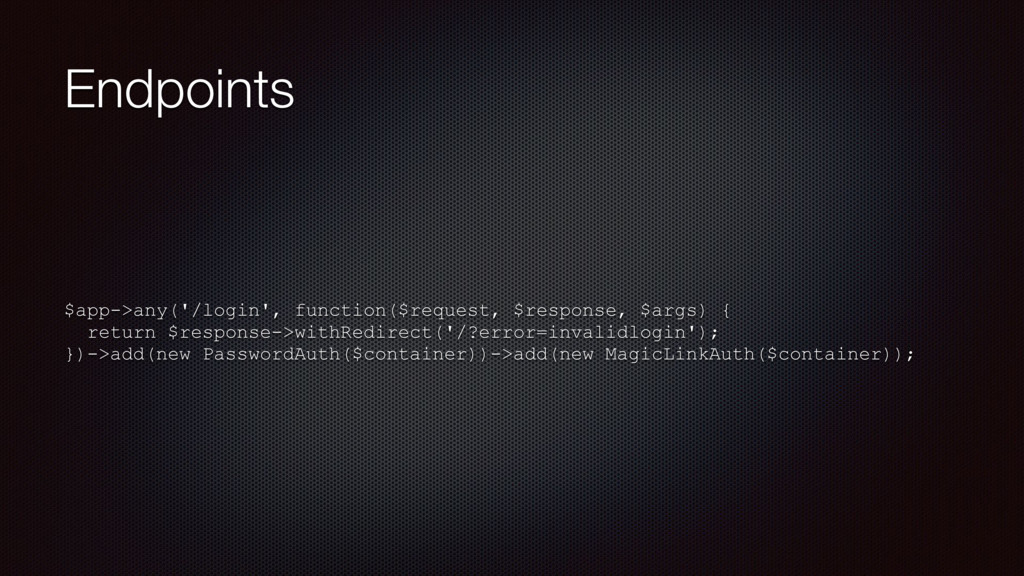
Endpoints $app->any('/login', function($request, $response, $args) { return $response->withRedirect('/?error=invalidlogin'); })->add(new PasswordAuth($container))->add(new
MagicLinkAuth($container));
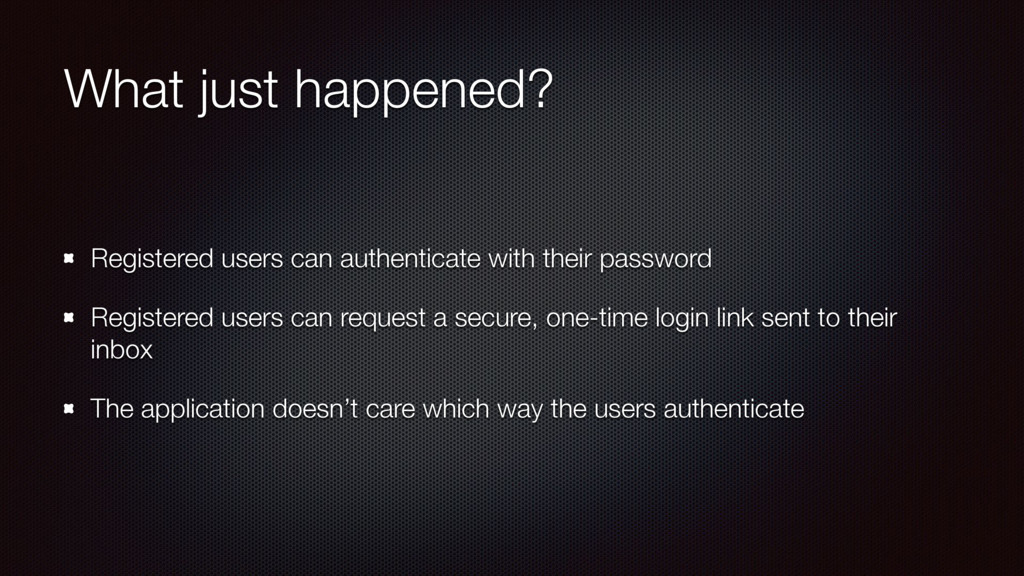
What just happened? Registered users can authenticate with their password
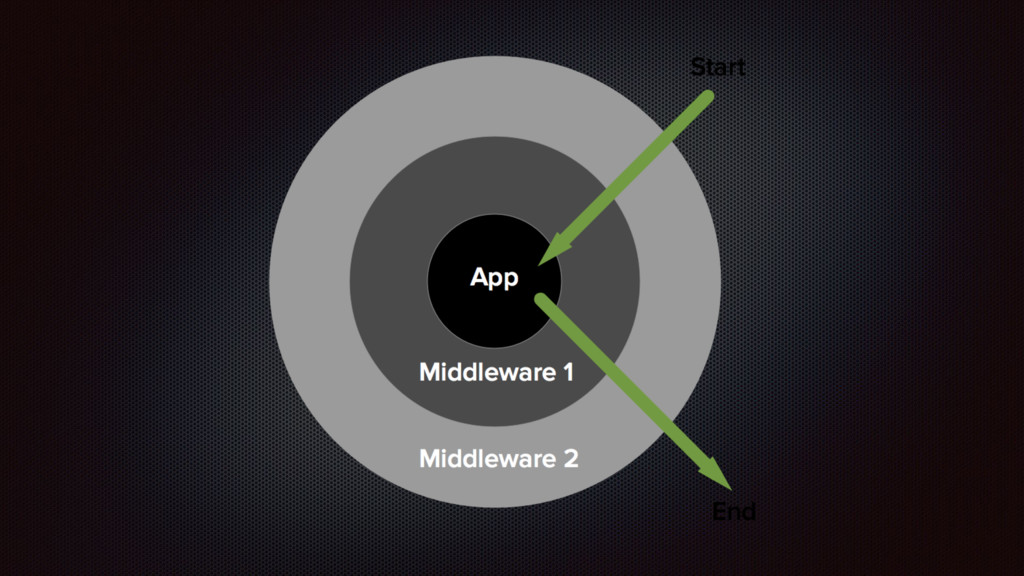
Registered users can request a secure, one-time login link sent to their inbox The application doesn’t care which way the users authenticate
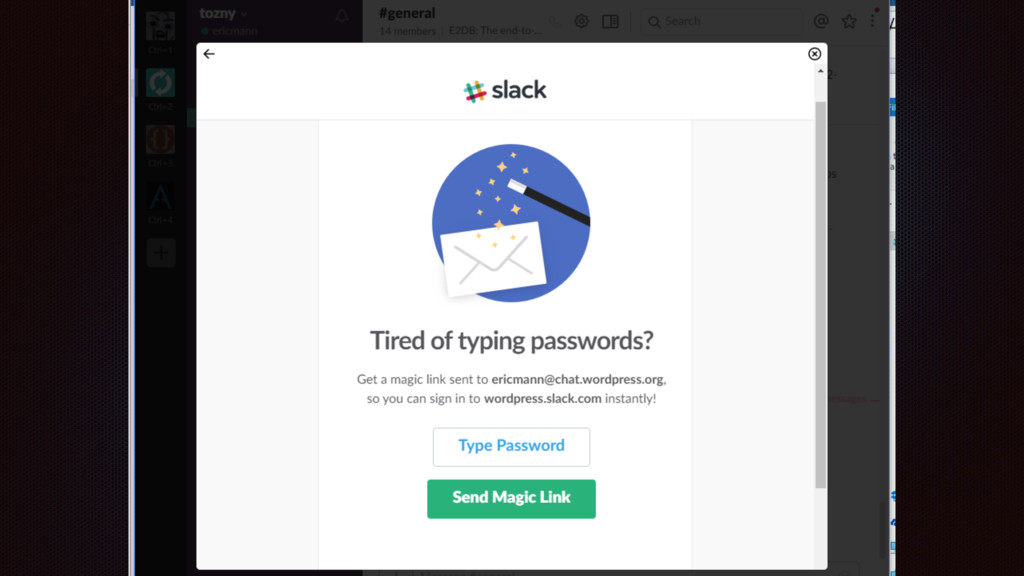
How does this benefit us? One less password for users
to remember More flexible authentication schemes for existing users The middleware stack could be further extended to support TOTP/HOTP/ U2F/etc
What are the risks? Your users’ accounts are only as
secure as their email
Questions?
Thank You! Eric Mann - @ericmann - http://eam.me/10v - https://tozny.com


 ericmann
 jozono
 murachiakira
 ny7760
 rmetzger
 atsushieno
 miu_crescent
 shunghsiyu
 hisuzuya
 sraku2159
 sh_fk2
 zozotech
 bessaralink55
 bkeepers
 andyhume
 philnash
 mfonobong
 brettharned
 aleyda
 holman
 csswizardry
 takai
 techseoconnect
 eileencodes
 kimpetersen