Share
Embed
Transcript
57 slides
-
2 Injection Broken Authentication Sensitive Data Exposure XML External Entities
Broken Access Control Security Misconfiguration Cross-Site Scripting (XSS) Insecure Deserialization Using Components with Known Vulnerabilities Insufficient Logging & Monitoring 1 2 3 4 5 6 7 8 9 10 -
The attacker's hostile data can trick the interpreter into executing
unintended commands or accessing data without proper authorization. -
6 $db = new \PDO(...); $name = $_POST['name']; $sql =
"SELECT * FROM users WHERE email='$name'"; foreach($db->query($sql) as $user) { // ... } curl -X POST -d "[email protected]' OR 1=1;--" http://yoursite.com SELECT * FROM users WHERE email='[email protected]' OR 1=1;--' -
7 $db = new \PDO(...); $name = $_POST['name']; $sql =
"SELECT * FROM users WHERE email=:email"; $statement = $db->prepare($sql); $params = [':email' => $name]; foreach($db->execute($statement, $params) as $user) { // ... } curl -X POST -d "[email protected]' OR 1=1;--" http://yoursite.com SELECT * FROM users WHERE email='[email protected]\' OR 1=1;--' -
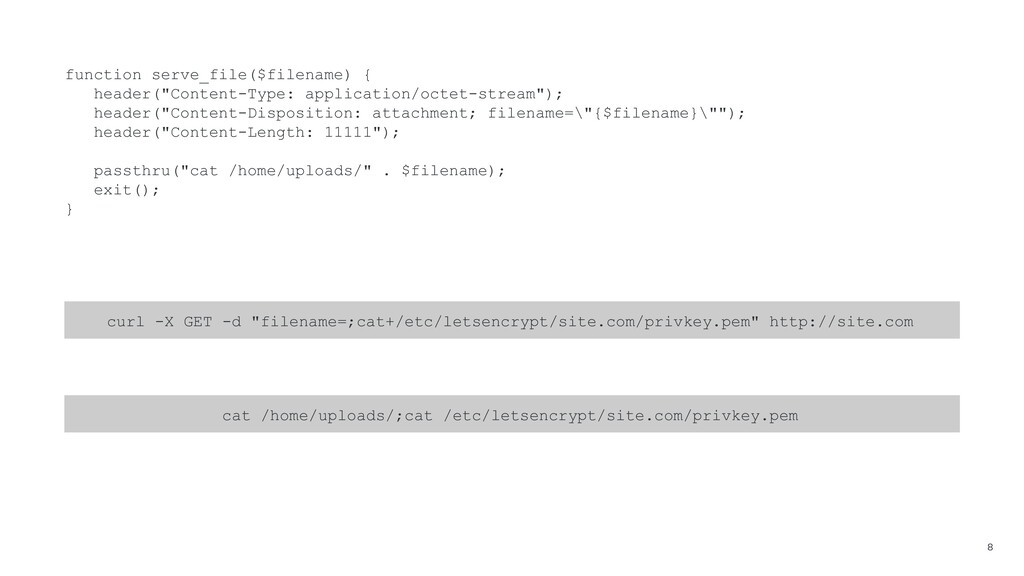
8 function serve_file($filename) { header("Content-Type: application/octet-stream"); header("Content-Disposition: attachment; filename=\"{$filename}\""); header("Content-Length:
11111"); passthru("cat /home/uploads/" . $filename); exit(); } curl -X GET -d "filename=;cat+/etc/letsencrypt/site.com/privkey.pem" http://site.com cat /home/uploads/;cat /etc/letsencrypt/site.com/privkey.pem -
9 function serve_file($filename) { // Sanitize the filename before it's
used $sanitized = basename($filename); header("Content-Type: application/octet-stream"); header("Content-Disposition: attachment; filename=\"{$sanitized}\""); header("Content-Length: 11111"); $path = "/home/uploads/{$sanitized}"; passthru('cat ' . escapeshellarg($path)); exit(); } curl -X GET -d "filename=;cat+/etc/letsencrypt/site.com/privkey.pem" http://site.com cat /home/uploads/privkey.pem -
Application functions related to authentication and session management are often
not implemented correctly... -
12 Client-side Sessions Don’t trust the user to store sensitive
information Don’t trust information provided by the user Don’t store sensitive information with an untrusted party Don’t use cookies to store sensitive data (If you are using cookies, use secure cookies - but only store identifiers) -
13 Password Management Passwords should NEVER be stored in plaintext.
Passwords should NEVER be stored with encryption. Passwords should ONLY be stored using one-way hashes. Try to avoid passwords in the first place... -
16 Problems with JWT Leaking sensitive information The `none` algorithm
is required by the spec Algorithm confusion - RSA vs HMAC Weak algorithms are allowed -
17 What you should do Only store session data on
the server Ensure strong authentication protects user identities Lock down insecure algorithms and primitives Only use trusted third-party library implementations -
Many web applications do not adequately protect sensitive data, such
as credit cards, tax IDs, and authentication credentials. -
21 Sensitive Data Retention What data do you retain? Why
do you need this data in the first place? Who has access to the data? Where are backups stored? Who has access to the data via the backup system? -
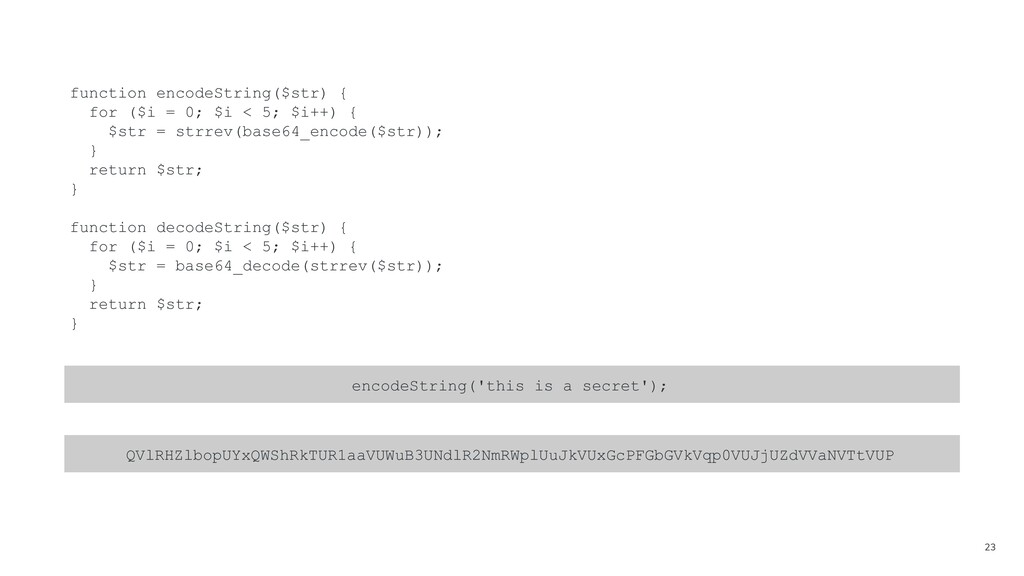
23 function encodeString($str) { for ($i = 0; $i <
5; $i++) { $str = strrev(base64_encode($str)); } return $str; } function decodeString($str) { for ($i = 0; $i < 5; $i++) { $str = base64_decode(strrev($str)); } return $str; } encodeString('this is a secret'); QVlRHZlbopUYxQWShRkTUR1aaVUWuB3UNdlR2NmRWplUuJkVUxGcPFGbGVkVqp0VUJjUZdVVaNVTtVUP -
Untrusted XML input containing a reference to an external entity
is processed by a weakly configured XML parser ... -
26 <?xml version="1.0"?> <!DOCTYPE info [<!ENTITY name "php[tek]">]> <info> <author>Friend
of &name;</author> <conference>&name;</conference> <event>&name; - 2019</event> </info> <!DOCTYPE vulnerable [<!ENTITY info SYSTEM "php://filter/read=convert.base64-encode/resource=/var/www/config.ini">]> <vulnerable> <config>&info;</config> </vulnerable> -
27 <!DOCTYPE bomb [ <!ENTITY x0 "BOOM!"> <!ENTITY x1 "&x0;&x0;">
<!ENTITY x2 "&x1;&x1;"> <!ENTITY x3 "&x2;&x2;"> <!ENTITY x4 "&x3;&x3;"> <!-- ... Repeat for entities from x5 through x98 --> <!ENTITY x99 "&x98;&x98;"> <!ENTITY bomb "&x99;&x99;"> ]> <vulnerable> <explosive>&bomb;</explosive> </vulnerable> -
28 $default = libxml_disable_entity_loader(true); $dom = new DOMDocument(); $dom->loadXML($xml); //
Do things with XML // Restore the previous value libxml_disable_entity_loader($default); What you should do -
Restrictions on what authenticated users are allowed to do are
not properly enforced. -
31 $app->post( '/profile', function ($request, $response, $args) { if (!isset($_SESSION['user_id'])
|| !$this->users->get($_SESSION['user_id'])) { return $response->withRedirect('/?error=notloggedin'); } $userID = $request->getParam('user_id'); $fname = $request->getParam('fname'); $lname = $request->getParam('lname'); $email = $request->getParam('email'); // Retrieve the user's account from the database (via the app container) $user = $this->users->get(intval($userID)); $user->profile->fname = filter_var($fname, FILTER_SANITIZE_STRING); $user->profile->lname = filter_var($lname, FILTER_SANITIZE_STRING); $user->profile->email = filter_var($email, FILTER_SANITIZE_EMAIL); $this->users->update($user); } ); -
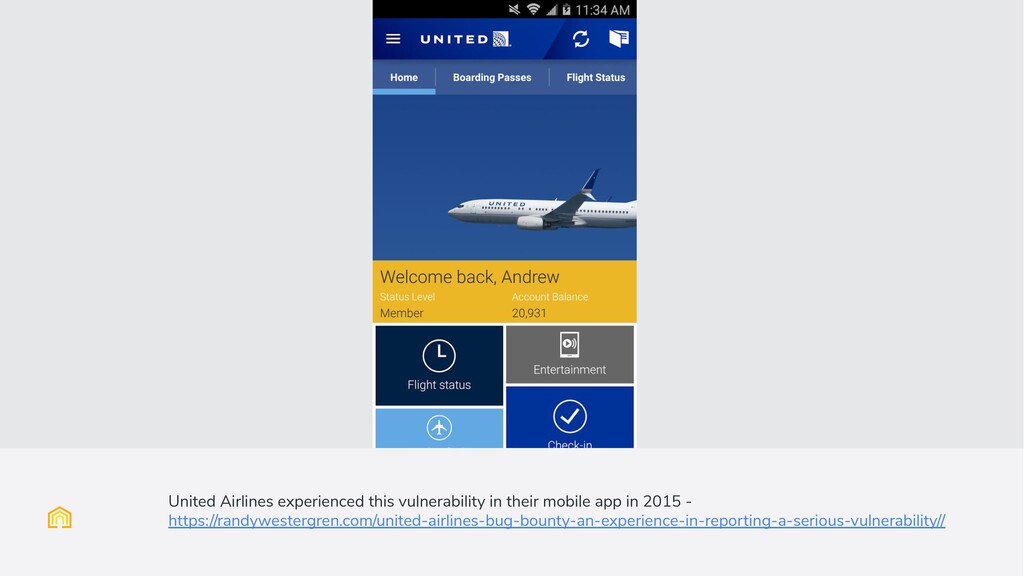
United Airlines experienced this vulnerability in their mobile app in
2015 - https://randywestergren.com/united-airlines-bug-bounty-an-experience-in-reporting-a-serious-vulnerability// -
Secure settings should be defined, implemented, and maintained, as defaults
are often insecure. -
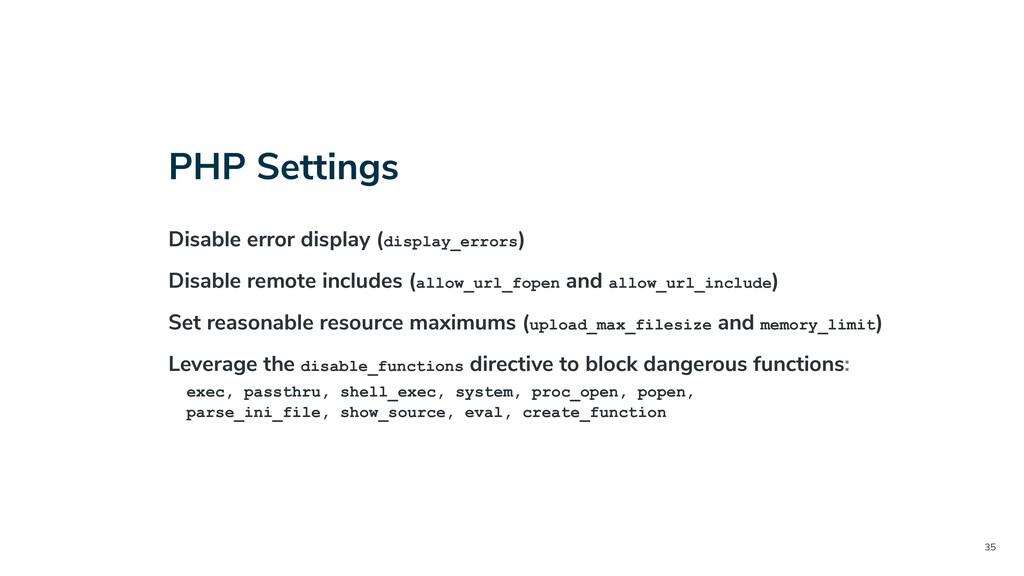
35 PHP Settings Disable error display (display_errors) Disable remote includes
(allow_url_fopen and allow_url_include) Set reasonable resource maximums (upload_max_filesize and memory_limit) Leverage the disable_functions directive to block dangerous functions: exec, passthru, shell_exec, system, proc_open, popen, parse_ini_file, show_source, eval, create_function -
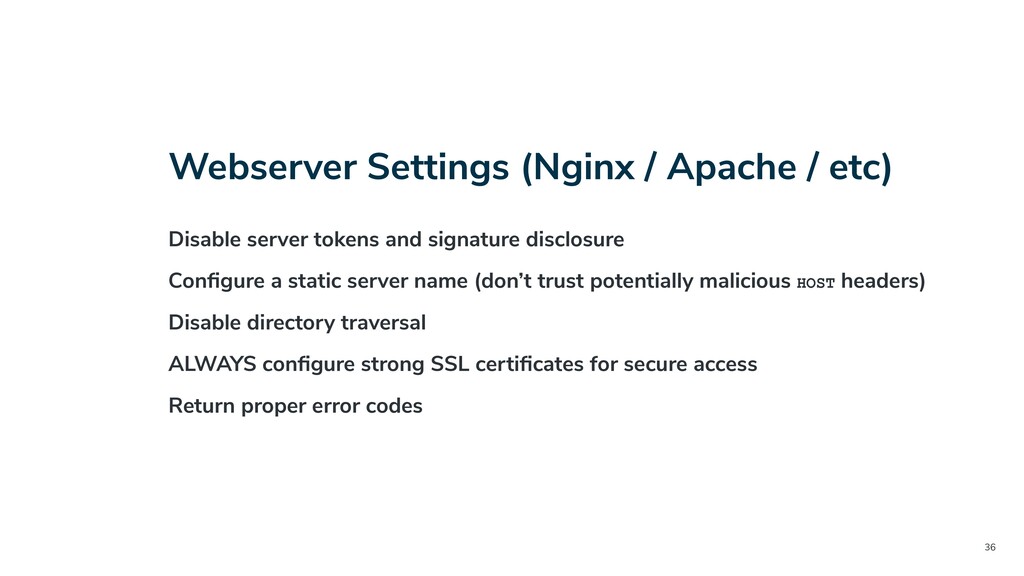
36 Webserver Settings (Nginx / Apache / etc) Disable server
tokens and signature disclosure Configure a static server name (don’t trust potentially malicious HOST headers) Disable directory traversal ALWAYS configure strong SSL certificates for secure access Return proper error codes -
37 Database (MySQL) Settings Set an appropriate bind-address Ensure users
are configured from the correct host, not a % wildcard Limit user permissions on the database to just what the application needs -
An application takes untrusted data and sends it to a
web browser without proper validation or escaping. -
40 <div id="results"> <span>Search results for: "<?php echo $data['s']; ?>"</span>
<?php if ($results) : ?> <ul> <?php foreach( $results as $result ) : ?> <li><a href="<?php echo $result->href; ?>"> <?php echo $result->title; ?></a></li> <?php endforeach; ?> </ul> <?php else : ?> <span>No results for '<?php echo $data['s']; ?>'</span> <?php endif; ?> </div> <div id="results"> <span>Search results for: <script src="..."></script></span> <span>No results for '<script src="..."></script>'</span> </div> -
41 <?php $query = filter_var( $data['s'], FILTER_SANITIZE_STRING ); ?> <div
id="results"> <span>Search results for: "<?php echo $query; ?>"</span> <?php if ($results) : ?> <ul> <?php foreach( $results as $result ) : ?> <li><a href="<?php echo $result->href; ?>"><?php echo $result->title; ?></a></li> <?php endforeach; ?> </ul> <?php else : ?> <span>No results for '<?php echo $query ?>'</span> <?php endif; ?> </div> <div id="results"> <span>Search results for: ""</span> <span>No results for ''</span> </div> -
Languages’ native deserialization mechanisms can be repurposed for malicious effect
when operating on untrusted data. -
44 class CartCache { $cache_file; $data = []; // ...
/** * Automatically purge the cache file from disk to clean up */ public function __destruct() { $file = "/var/www/cache/tmp/carts/{$this->cache_file}"; if ($this->cleanup && file_exists($file)) { @unlink($file); } } } $data = unserialize($_GET['data']); https://yoursite.com/endpoint.php?data=O:9:"CartCache":2:{s:10:"cache_file";s:18:"../../../i ndex.php";s:4:"data";a:0:{}} -
Do not pass untrusted user input to unserialize() regardless of
the options value of allowed_classes. -
Applications using components with known vulnerabilities may undermine application defenses
and enable a range of possible attacks and impacts. -
48 Audit Application Dependencies Monitor Composer-installed dependencies for outdated or
vulnerable libraries Leverage unattended-upgrades to keep system packages up-to-date Audit the packages installed on your server - don’t install things you don’t need -
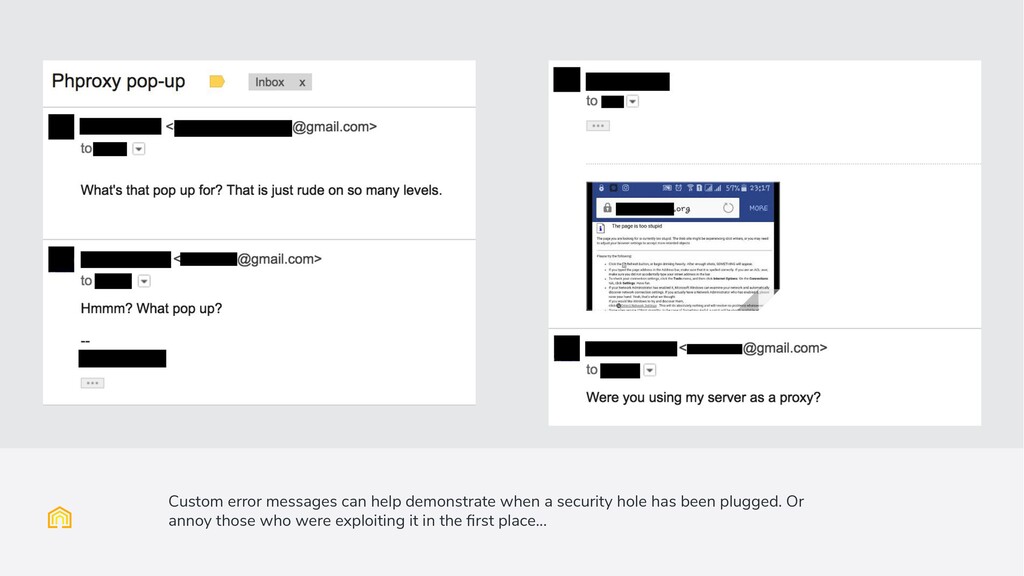
Custom error messages can help demonstrate when a security hole
has been plugged. Or annoy those who were exploiting it in the first place... -
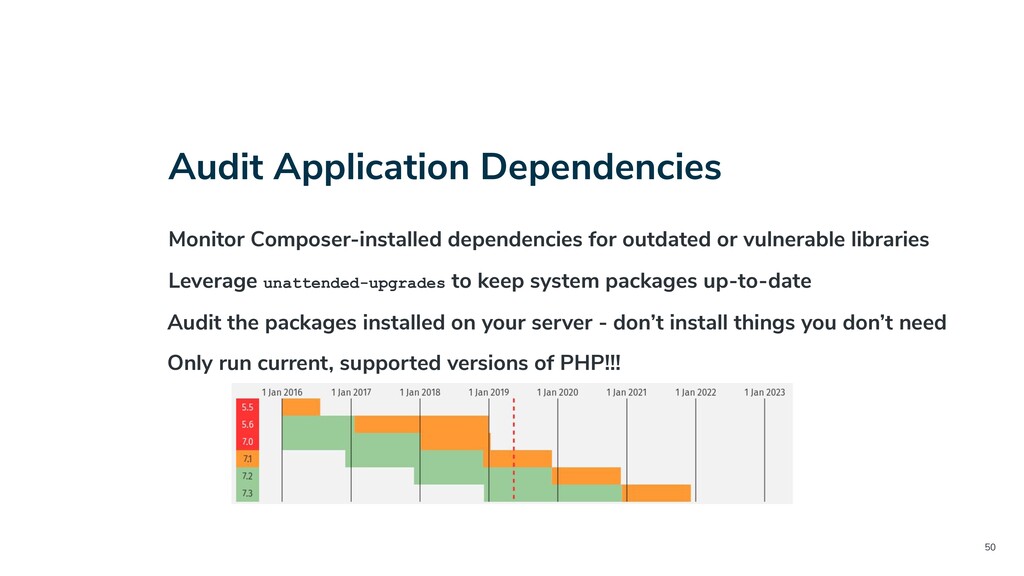
50 Audit Application Dependencies Monitor Composer-installed dependencies for outdated or
vulnerable libraries Leverage unattended-upgrades to keep system packages up-to-date Audit the packages installed on your server - don’t install things you don’t need Only run current, supported versions of PHP!!! -
Attackers rely on the lack of monitoring and timely response
to achieve their goals without being detected. -
53 It’s Important to Track: What happened When it happened
Where it happened (in terms of code and the IP of the server) To whom it happened What input triggered the event -
54 Event Classes Input Validation Errors Output Validation Errors Authentication
Events Authorization (Access Control) Failures Application Errors Application Startup/Shutdown High-risk Operations