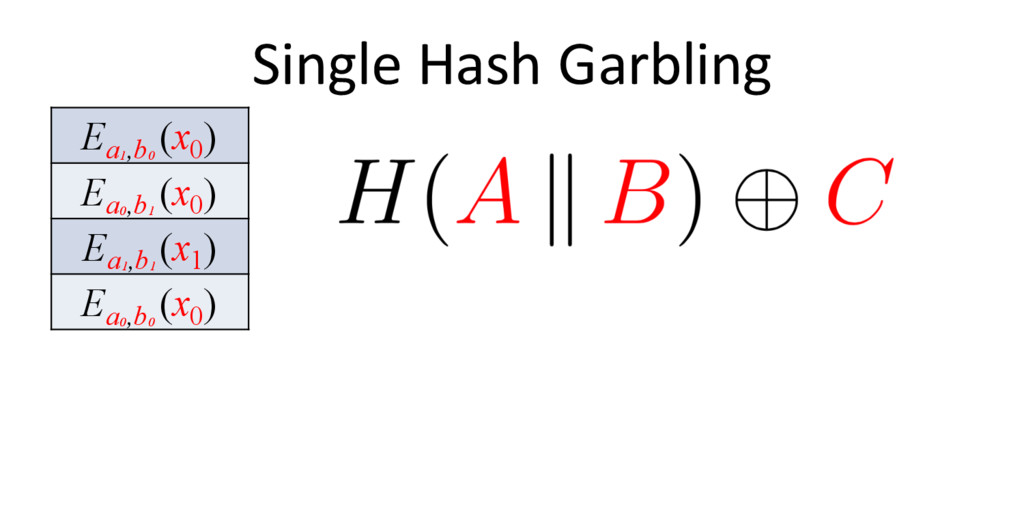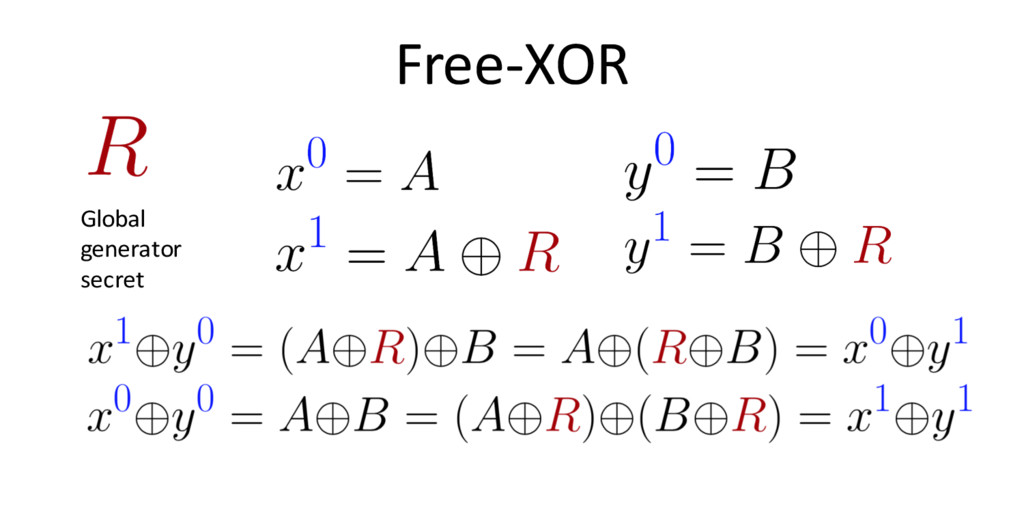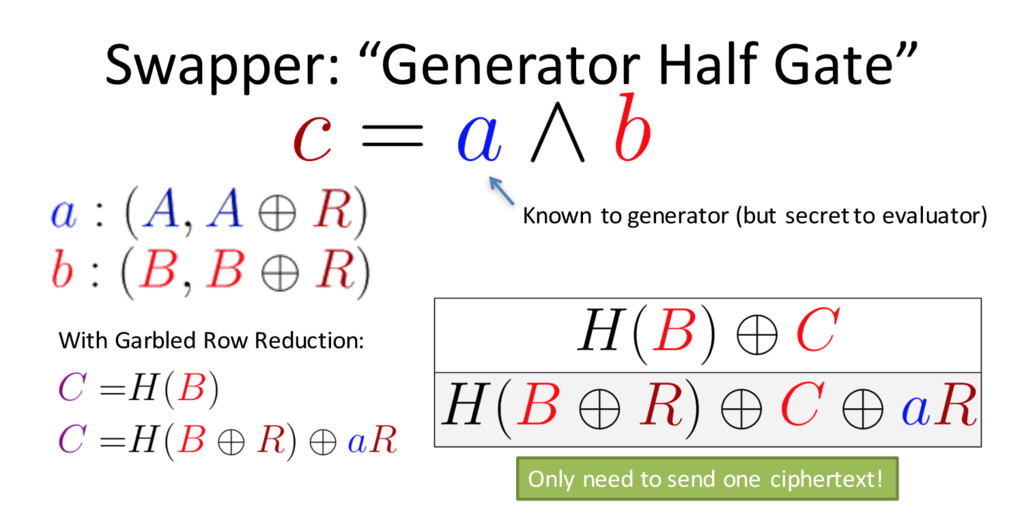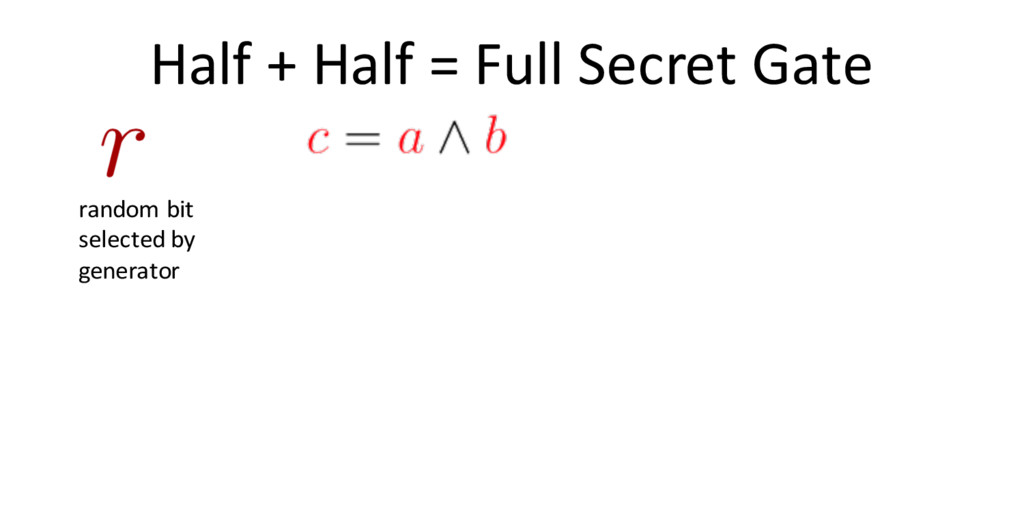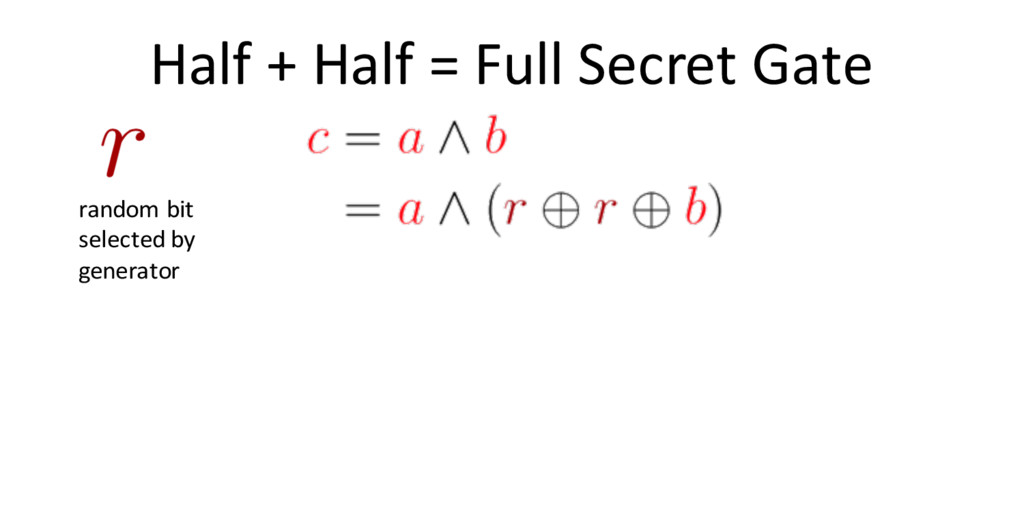Share
Embed
Introduction to Secure Multi-Party Computation in Practice
Tutorial talk at ShanghaiTech Symposium on Information Science and Technology
23 June 2016
David Evans
June 23, 2016
Transcript
75 slides
-
Tutorial: Introduction to Secure Multi-Party Computation in Practice David Evans
University of Virginia www.JeffersonsWheel.org -
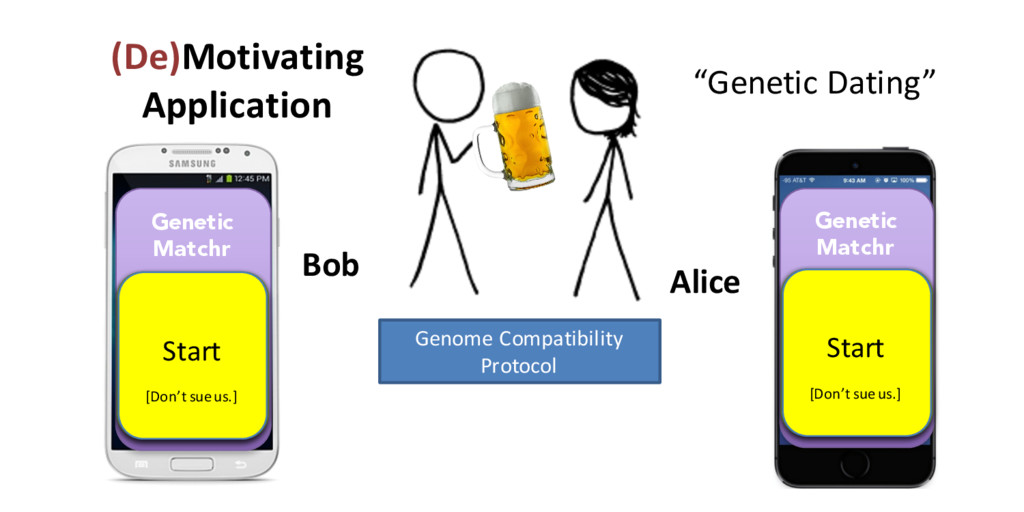
Alice Bob Genome Compatibility Protocol “Genetic Dating” Genetic Matchr WARNING!
Reproduction not recommended Your offspring would have good immune systems! processing… Start [Don’t sue us.] Genetic Matchr WARNING! Reproduction not recommended Your offspring would have good immune systems! processing… Start [Don’t sue us.] (De)Motivating Application -
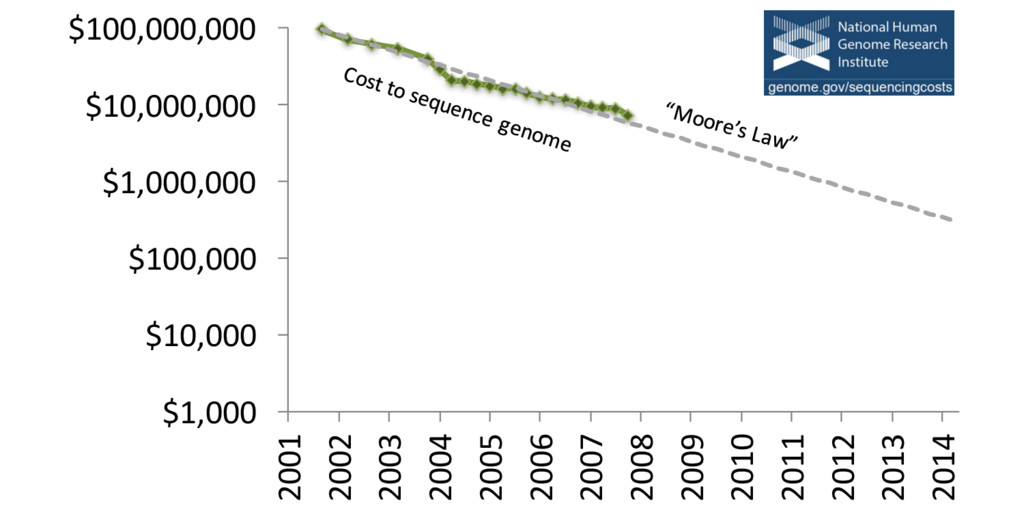
$1,000 $10,000 $100,000 $1,000,000 $10,000,000 $100,000,000 2001 2002 2003 2004
2005 2006 2007 2008 2009 2010 2011 2012 2013 2014 -
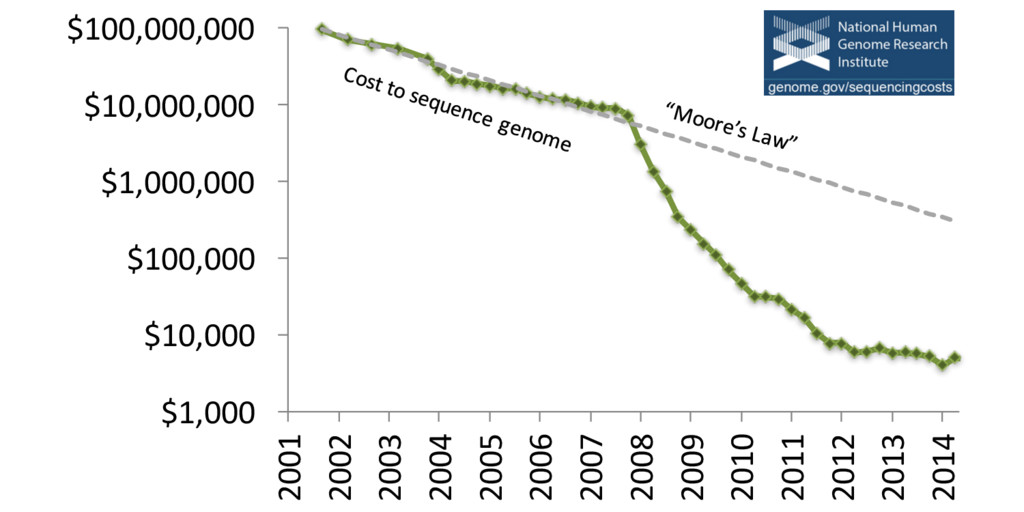
$1,000 $10,000 $100,000 $1,000,000 $10,000,000 $100,000,000 2001 2002 2003 2004
2005 2006 2007 2008 2009 2010 2011 2012 2013 2014 -
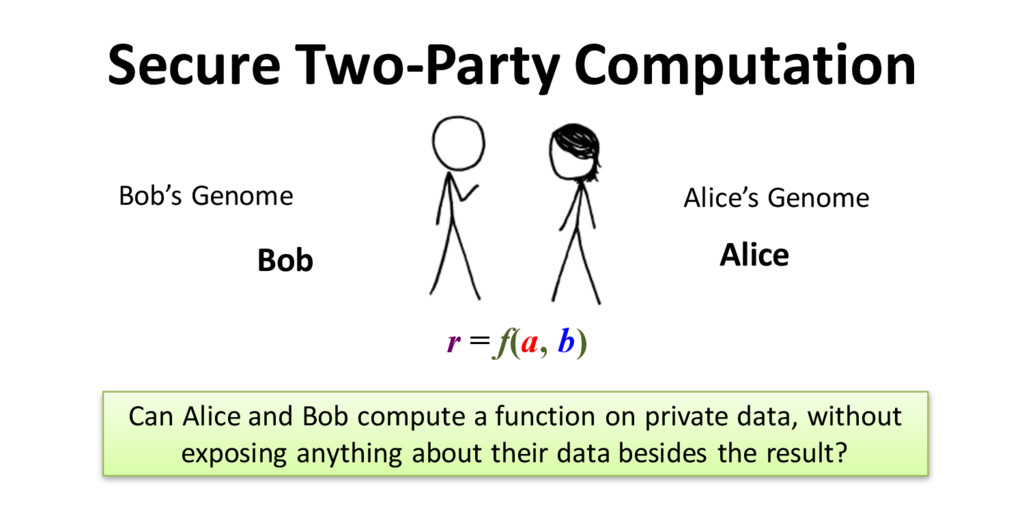
Secure Two-Party Computation Alice Bob Bob’s Genome Alice’s Genome Can
Alice and Bob compute a function on private data, without exposing anything about their data besides the result? r = f(a, b) -
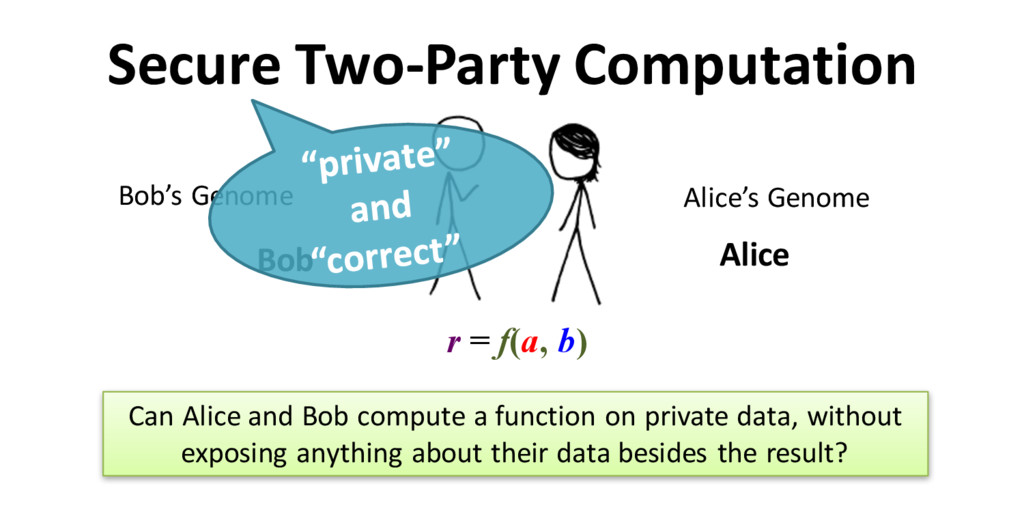
Bob’s Genome Secure Two-Party Computation Alice Bob r = f(a,
b) Alice’s Genome Can Alice and Bob compute a function on private data, without exposing anything about their data besides the result? -
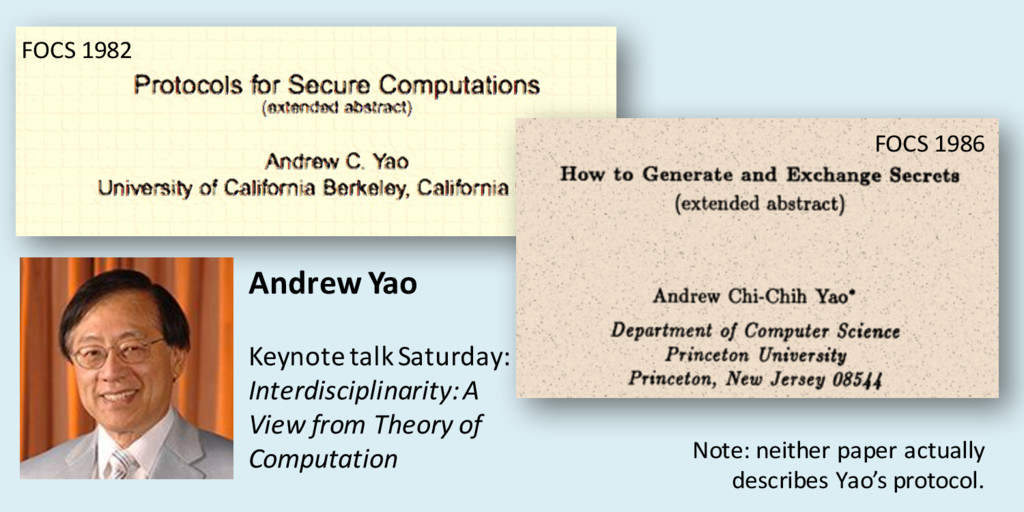
FOCS 1982 FOCS 1986 Note: neither paper actually describes Yao’s
protocol. Andrew Yao Keynote talk Saturday: Interdisciplinarity: A View from Theory of Computation -
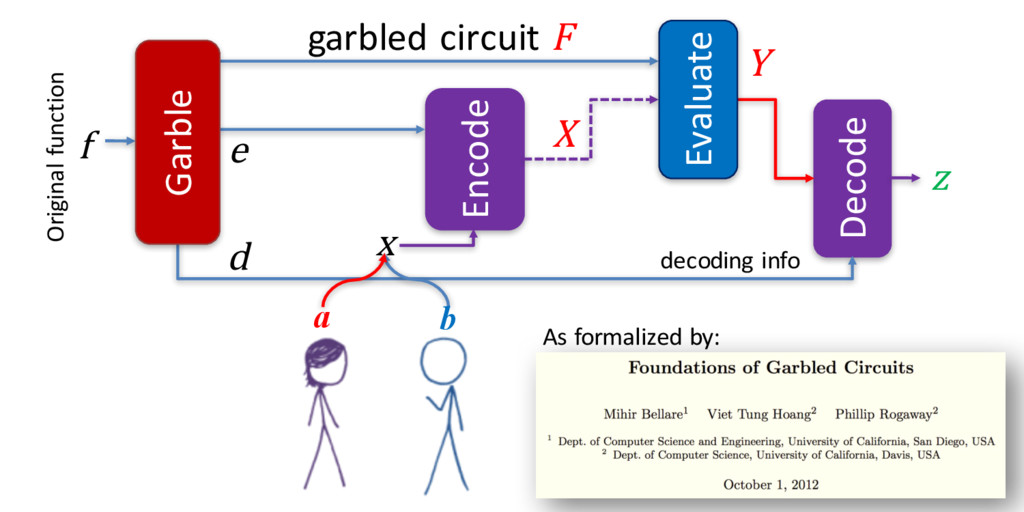
Encode Decode f garbled circuit F e X Y z
d x As formalized by: Original function decoding info a b Garble Evaluate -
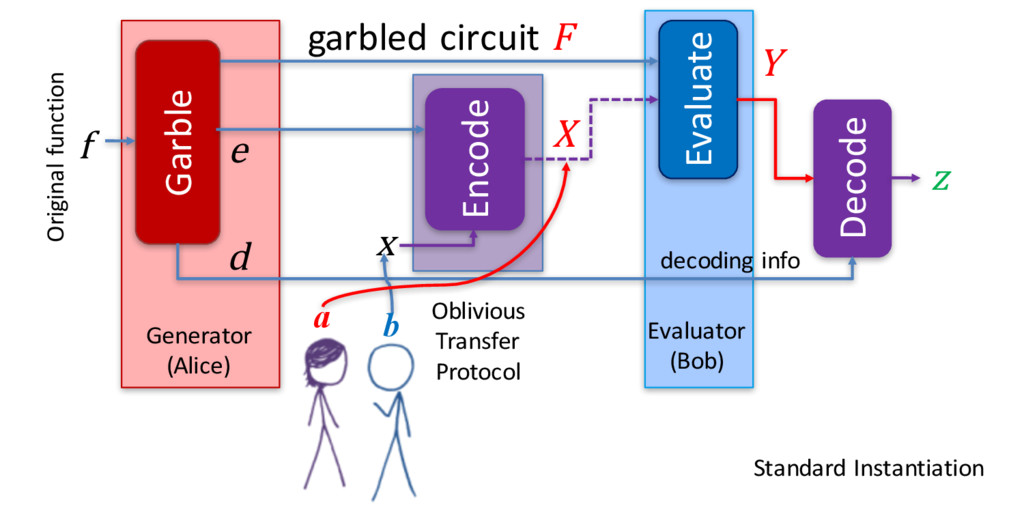
Garble Encode Evaluate Decode f garbled circuit F e X
Y z d x Standard Instantiation Original function decoding info a b Generator (Alice) Evaluator (Bob) Oblivious Transfer Protocol -
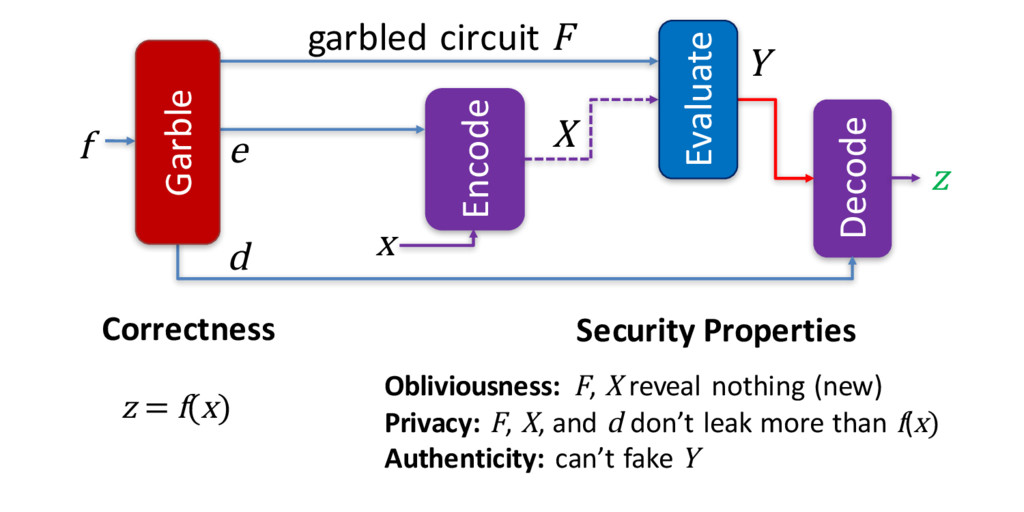
Encode Decode f garbled circuit F e X Y d
x Security Properties Obliviousness: F, X reveal nothing (new) Privacy: F, X, and d don’t leak more than f(x) Authenticity: can’t fake Y Garble Evaluate Correctness z = f(x) z -
Threat Model “Honest-but-Curious” (also called “Semi-Honest”) Security and correctness only
guaranteed if participants follow protocol. Later: hardening techniques can strengthen to active adversaries. -
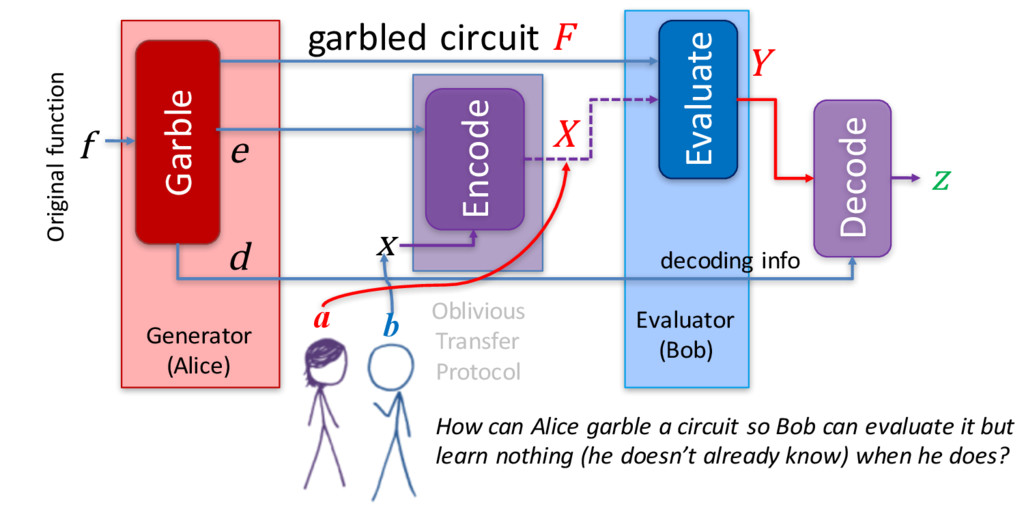
Garble Encode Evaluate Decode f garbled circuit F e X
Y z d x How can Alice garble a circuit so Bob can evaluate it but learn nothing (he doesn’t already know) when he does? Original function decoding info a b Generator (Alice) Evaluator (Bob) Oblivious Transfer Protocol -
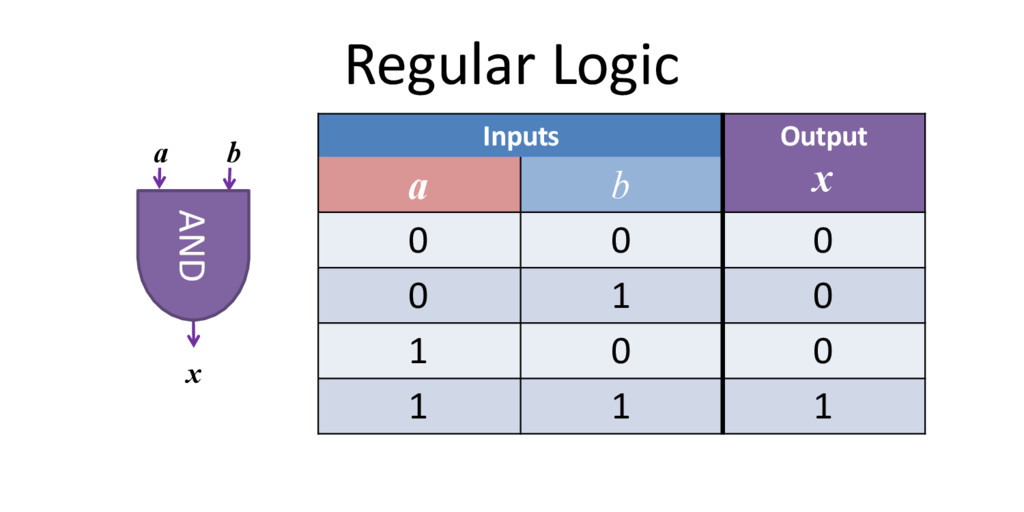
Regular Logic Inputs Output x a b 0 0 0
0 1 0 1 0 0 1 1 1 a b x AND -
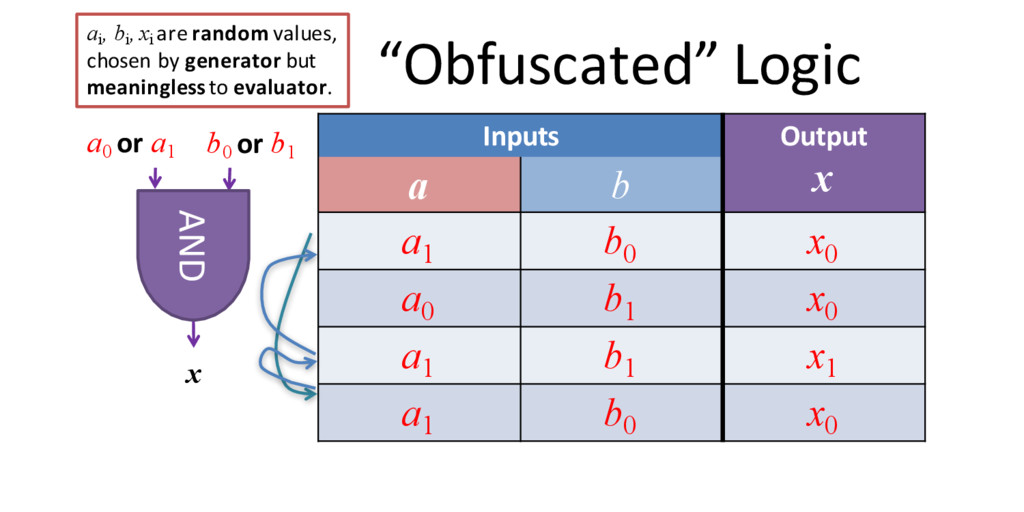
“Obfuscated” Logic Inputs Output x a b a1 b0 x0
a0 b1 x0 a1 b1 x1 a1 b0 x0 a0 or a1 x AND b0 or b1 ai , bi , xi are random values, chosen by generator but meaningless to evaluator. -
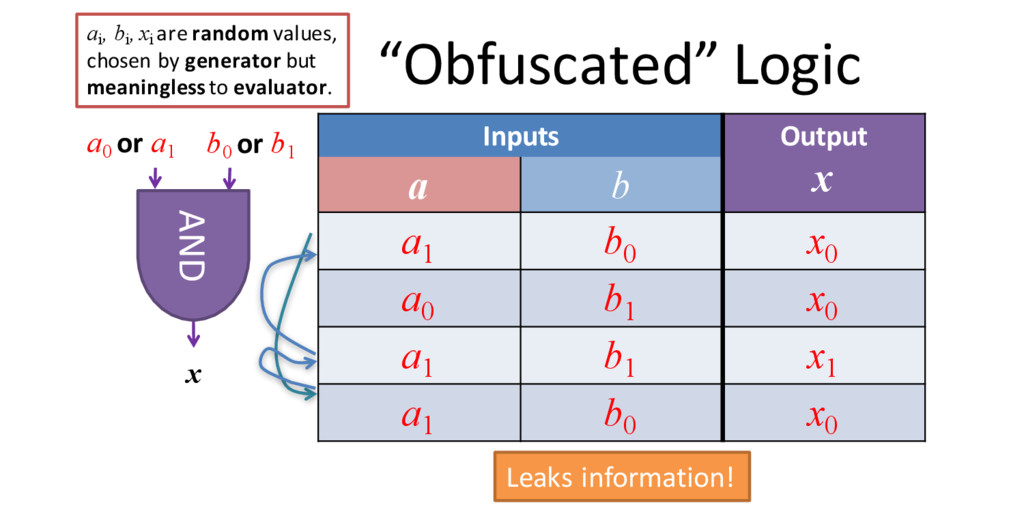
Inputs Output x a b a1 b0 x0 a0 b1
x0 a1 b1 x1 a1 b0 x0 a0 or a1 x AND b0 or b1 Leaks information! “Obfuscated” Logic ai , bi , xi are random values, chosen by generator but meaningless to evaluator. -
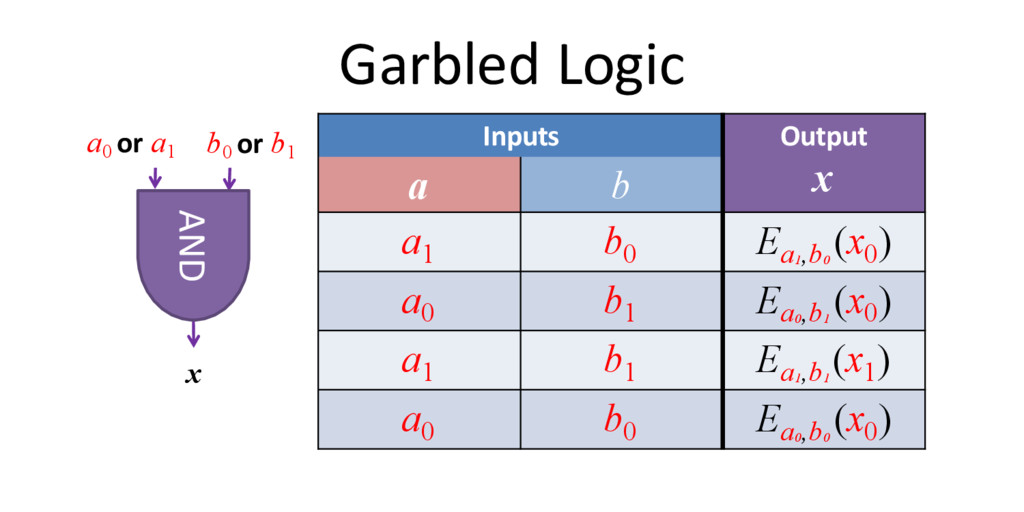
Garbled Logic Inputs Output x a b a1 b0 Ea1
,b0 (x0 ) a0 b1 Ea0 ,b1 (x0 ) a1 b1 Ea1 ,b1 (x1 ) a0 b0 Ea0 ,b0 (x0 ) a0 or a1 x AND b0 or b1 -
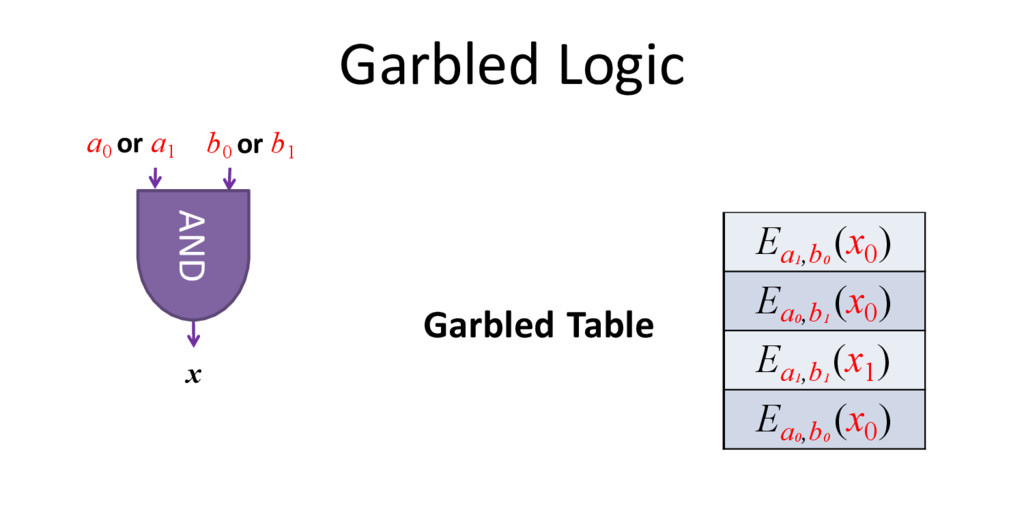
Garbled Logic Inputs Output x a b a1 b0 Ea1
,b0 (x0 ) a0 b1 Ea0 ,b1 (x0 ) a1 b1 Ea1 ,b1 (x1 ) a0 b0 Ea0 ,b0 (x0 ) a0 or a1 x AND b0 or b1 G Garbled Table -
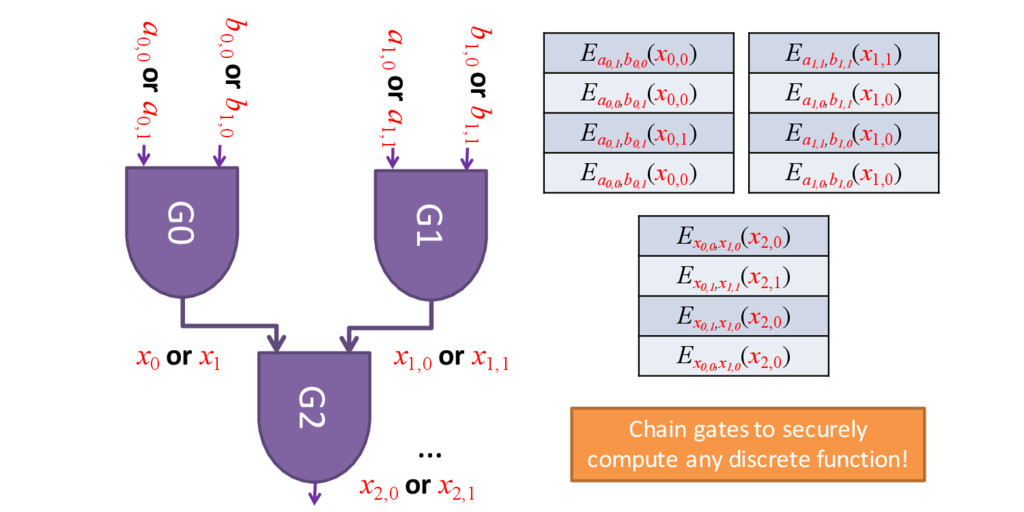
a0,0 or a0,1 G0 b0,0 or b1,0 G1 … x0
or x1 G2 x1,0 or x1,1 a1,0 or a1,1 b1,0 or b1,1 Ea0,1 ,b0,0 (x0,0 ) Ea0,0 ,b0,1 (x0,0 ) Ea0,1 ,b0,1 (x0,1 ) Ea0,0 ,b0,1 (x0,0 ) Ea1,1 ,b1,1 (x1,1 ) Ea1,0 ,b1,1 (x1,0 ) Ea1,1 ,b1,0 (x1,0 ) Ea1,0 ,b1,0 (x1,0 ) x2,0 or x2,1 Chain gates to securely compute any discrete function! Ex0,0 ,x1,0 (x2,0 ) Ex0,1 ,x1,1 (x2,1 ) Ex0,1 ,x1,0 (x2,0 ) Ex0,0 ,x1,0 (x2,0 ) -
Building Computing Systems 23 Digital Electronic Circuits Garbled Circuits Operate
on known data Operate on encrypted wire labels One-bit logical operation requires moving some electrons a few nanometers One-bit logical operation requires performing four encryption operations Reuse is great! Reuse is not allowed! Ea1 ||b0 (x0 ) Ea0 ||b1 (x0 ) Ea1 ||b1 (x1 ) -
Fairplay 24 Malkhi, Nisan, Pinkas and Sella [USENIX Sec 2004]
SFDL Program SFDL Compiler Circuit Garbled Tables Generator Garbled Tables Evaluator SFDL Compiler -
[Fairplay, USENIX Sec 2004] ∼$1M Estimated cost of 10k x
10k Smith-Waterman, 4T gates $1,000 $10,000 $100,000 $1,000,000 $10,000,000 $100,000,000 2001 2002 2003 2004 2005 2006 2007 2008 2009 2010 2011 2012 2013 2014 2015 2016 -
Fairplay 26 Malkhi, Nisan, Pinkas and Sella [USENIX Sec 2004]
SFDL Program SFDL Compiler Circuit (SHDL) Alice Bob Garbled Tables Generator Garbled Tables Evaluator SFDL Compiler 4T gates ~ 1.2 PB of storage -
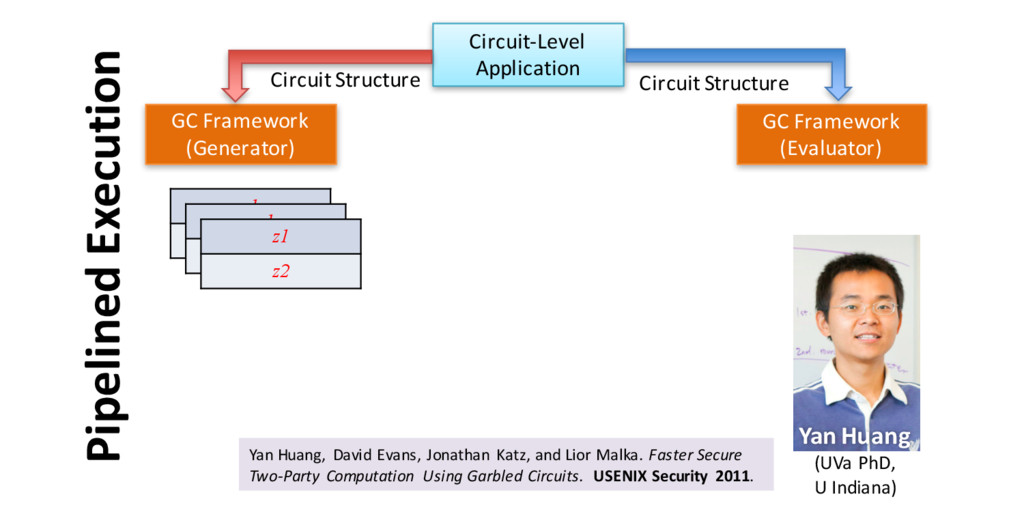
Pipelined Execution Circuit-Level Application GC Framework (Evaluator) GC Framework (Generator)
Circuit Structure Circuit Structure Yan Huang (UVa PhD, U Indiana) Yan Huang, David Evans, Jonathan Katz, and Lior Malka. Faster Secure Two-Party Computation Using Garbled Circuits. USENIX Security 2011. x1 x2 y1 y2 z1 z2 -
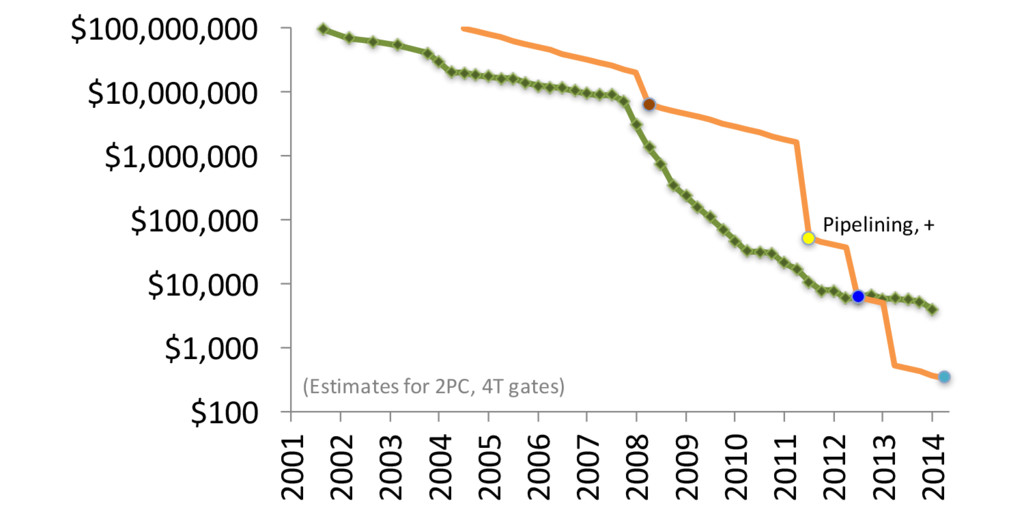
$100 $1,000 $10,000 $100,000 $1,000,000 $10,000,000 $100,000,000 2001 2002 2003
2004 2005 2006 2007 2008 2009 2010 2011 2012 2013 2014 Pipelining, + (Estimates for 2PC, 4T gates) -
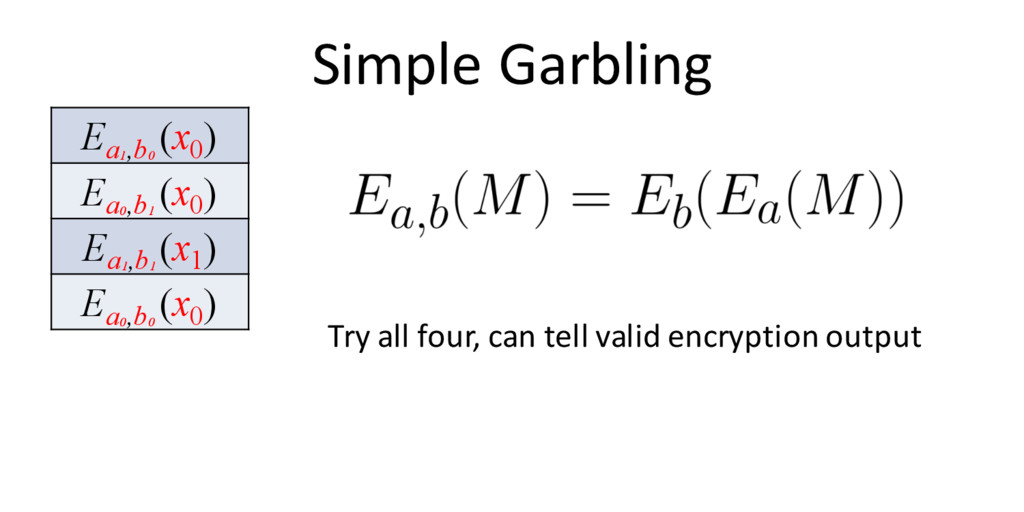
Ea1 ,b0 (x0 ) Ea0 ,b1 (x0 ) Ea1 ,b1
(x1 ) Ea0 ,b0 (x0 ) Simple Garbling Try all four, can tell valid encryption output -
Ea1 ,b0 (x0 ) Ea0 ,b1 (x0 ) Ea1 ,b1
(x1 ) Ea0 ,b0 (x0 ) Single Hash Garbling -
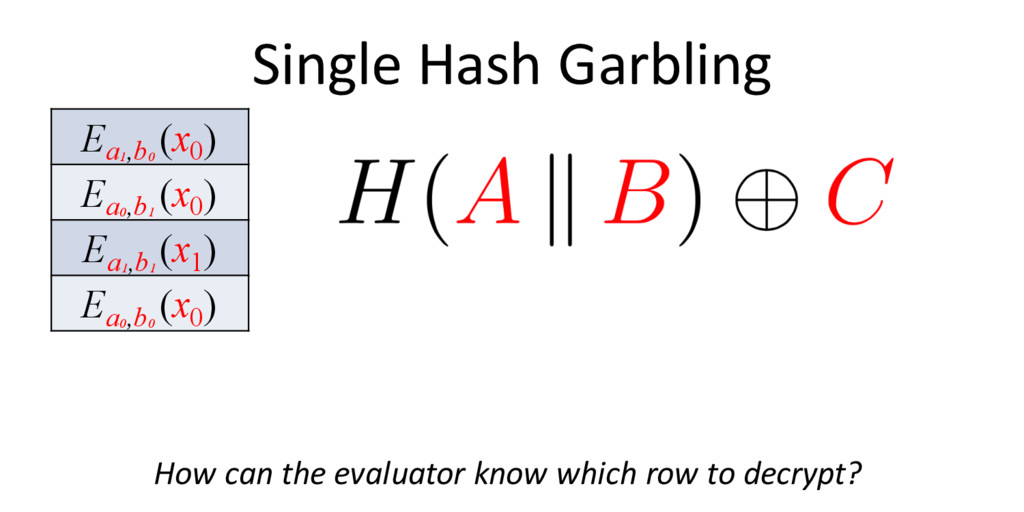
Ea1 ,b0 (x0 ) Ea0 ,b1 (x0 ) Ea1 ,b1
(x1 ) Ea0 ,b0 (x0 ) Single Hash Garbling How can the evaluator know which row to decrypt? -
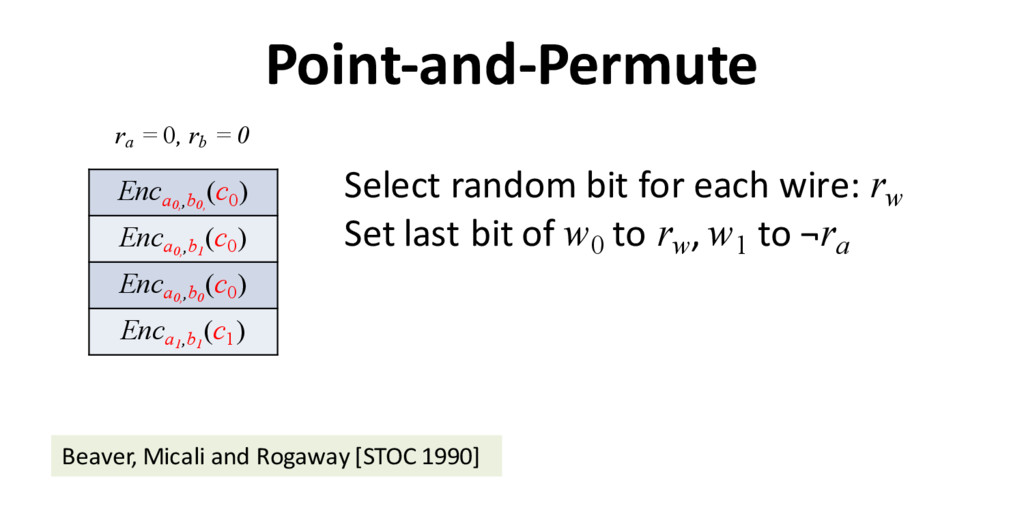
Point-and-Permute Enca0, ,b0, (c0 ) Enca0, ,b1 (c0 ) Enca0,
,b0 (c0 ) Enca1 ,b1 (c1 ) Beaver, Micali and Rogaway [STOC 1990] Select random bit for each wire: rw Set last bit of w0 to rw , w1 to ¬ra ra = 0, rb = 0 -
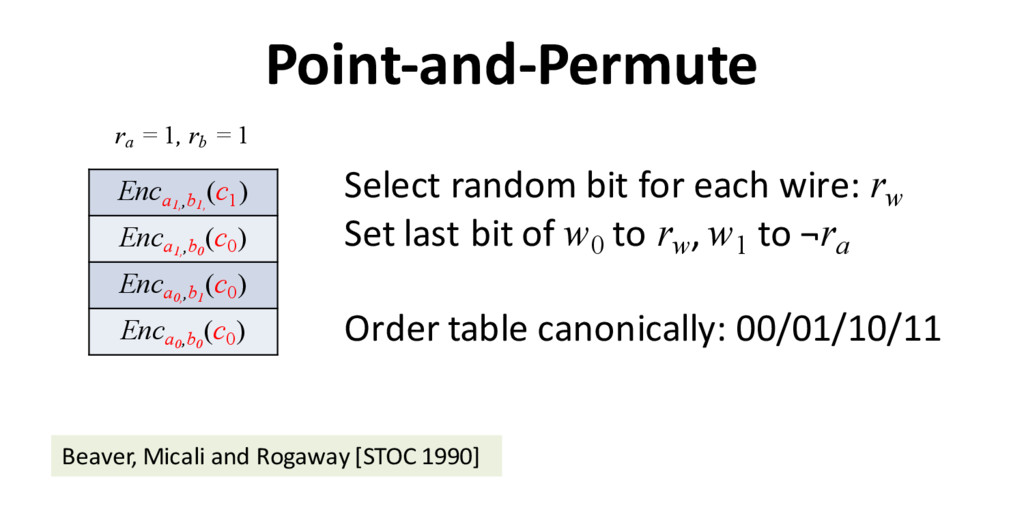
Point-and-Permute Enca1, ,b1, (c1 ) Enca1, ,b0 (c0 ) Enca0,
,b1 (c0 ) Enca0 ,b0 (c0 ) Select random bit for each wire: rw Set last bit of w0 to rw , w1 to ¬ra Order table canonically: 00/01/10/11 ra = 1, rb = 1 Beaver, Micali and Rogaway [STOC 1990] -
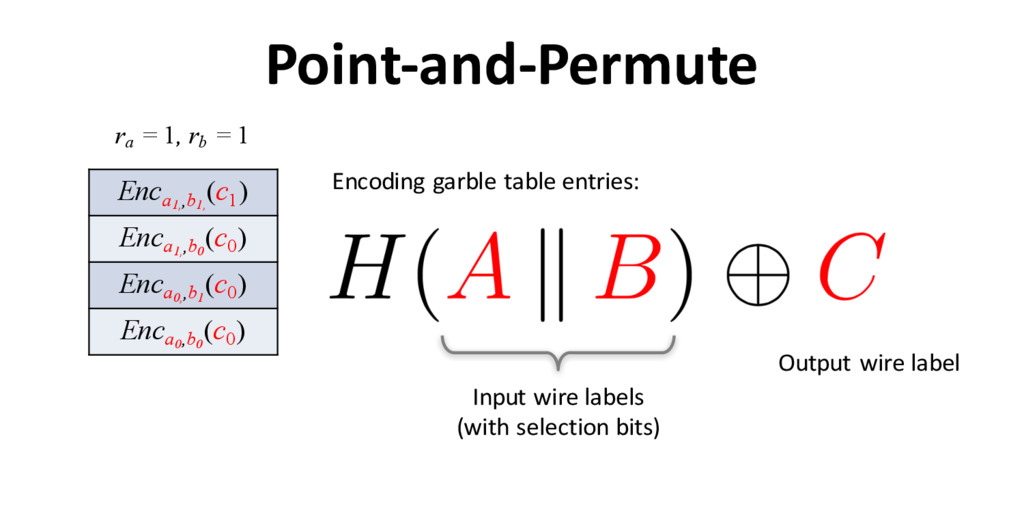
Point-and-Permute Encoding garble table entries: Input wire labels (with selection
bits) Output wire label Enca1, ,b1, (c1 ) Enca1, ,b0 (c0 ) Enca0, ,b1 (c0 ) Enca0 ,b0 (c0 ) ra = 1, rb = 1 -
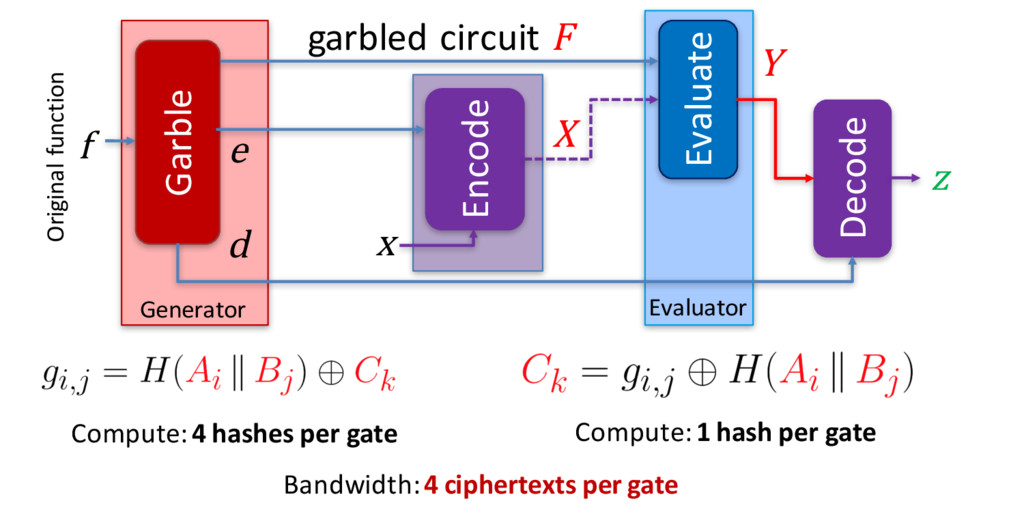
Bandwidth: 4 ciphertexts per gate Compute: 4 hashes per gate
Compute: 1 hash per gate Garble Encode Evaluate Decode f garbled circuit F e X Y z d x Original function Generator Evaluator -
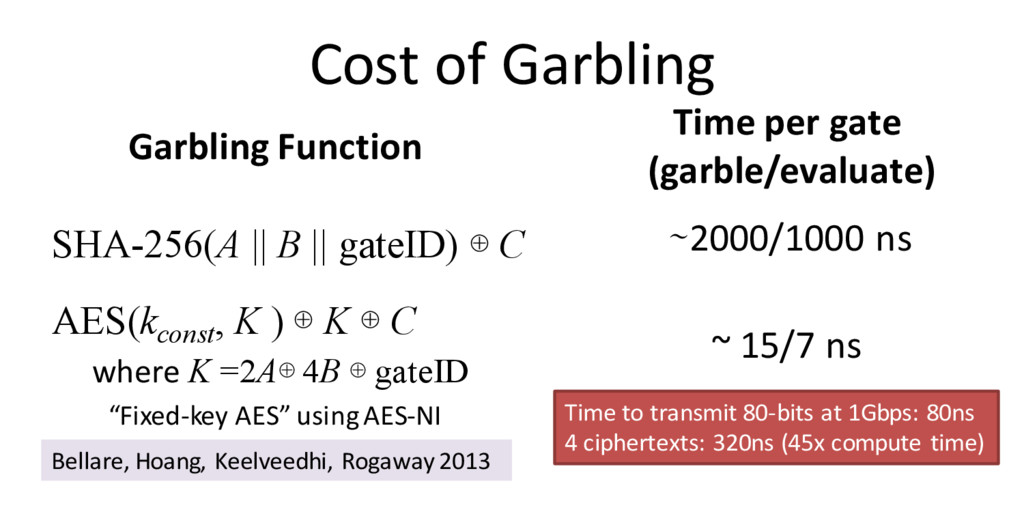
Cost of Garbling Garbling Function AES(kconst , K ) ⊕
K ⊕ C where K =2A⊕ 4B ⊕ gateID SHA-256(A || B || gateID) ⊕ C ∼2000/1000 ns Bellare, Hoang, Keelveedhi, Rogaway 2013 “Fixed-key AES” using AES-NI ~ 15/7 ns Time per gate (garble/evaluate) Time to transmit 80-bits at 1Gbps: 80ns 4 ciphertexts: 320ns (45x compute time) -
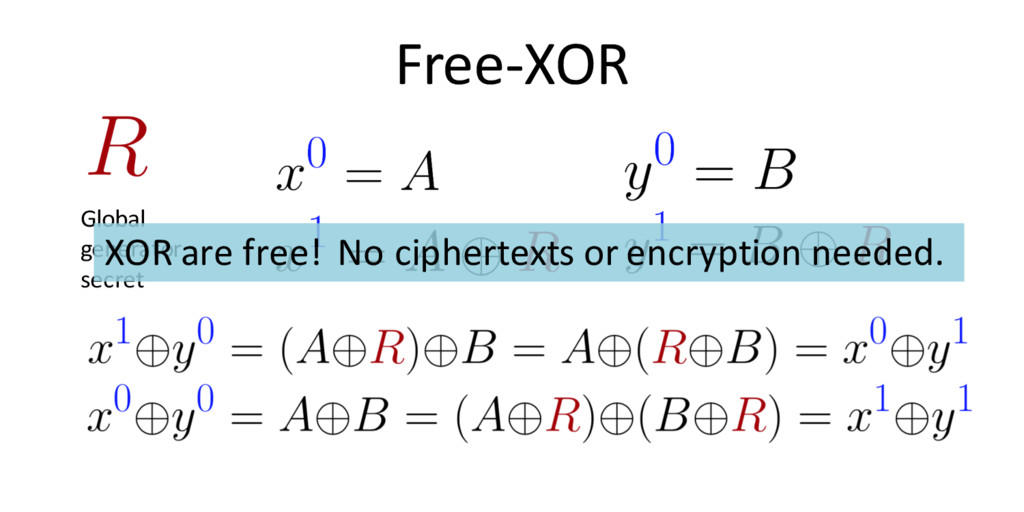
Free-XOR Global generator secret XOR are free! No ciphertexts or
encryption needed. -
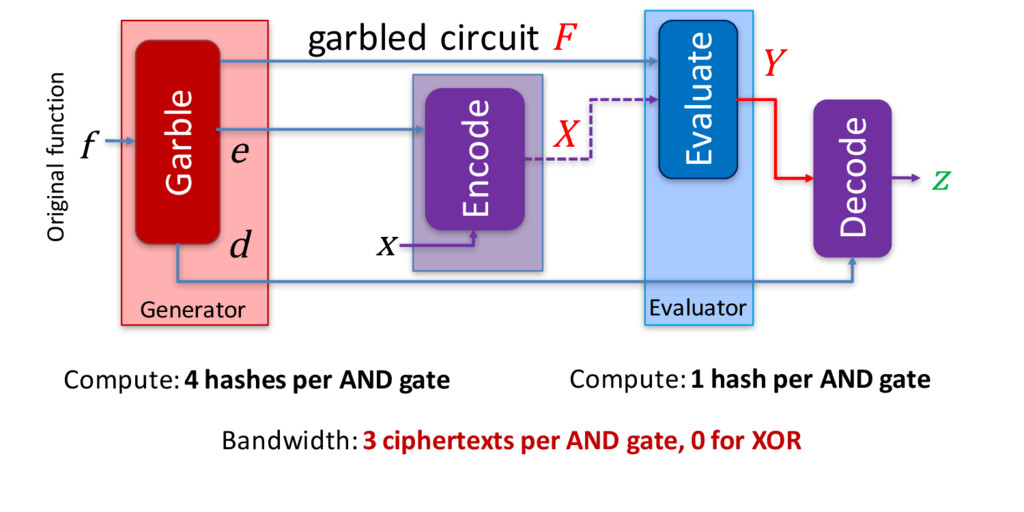
Bandwidth: 3 ciphertexts per AND gate, 0 for XOR Compute:
4 hashes per AND gate Compute: 1 hash per AND gate Garble Encode Evaluate Decode f garbled circuit F e X Y z d x Original function Generator Evaluator -
Half Gates Samee Zahur, Mike Rosulek, and David Evans. Two
Halves Make a Whole: Reducing Data Transfer in Garbled Circuits using Half Gates. [EuroCrypt 2015] Samee Zahur (UVA) Mike Rosulek (Oregon State) -
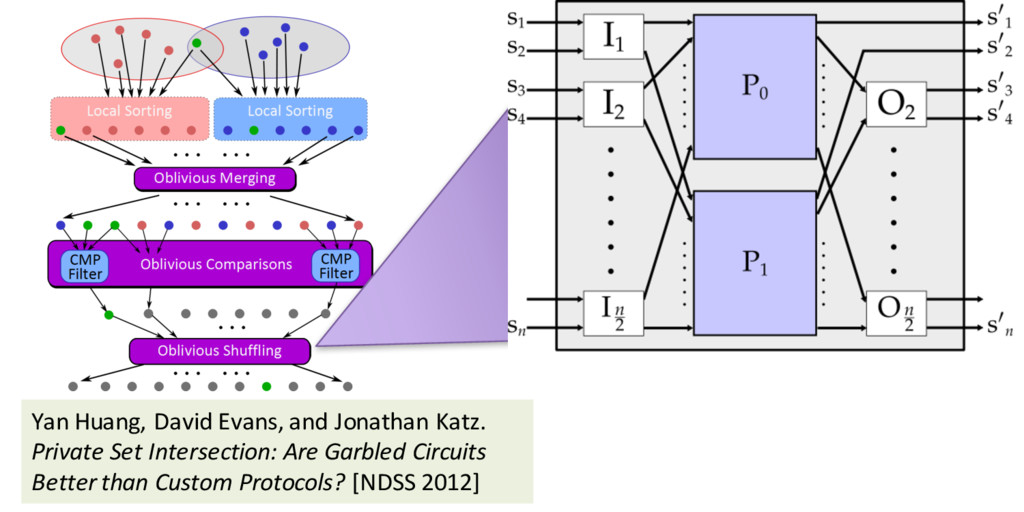
Yan Huang, David Evans, and Jonathan Katz. Private Set Intersection:
Are Garbled Circuits Better than Custom Protocols? [NDSS 2012] -
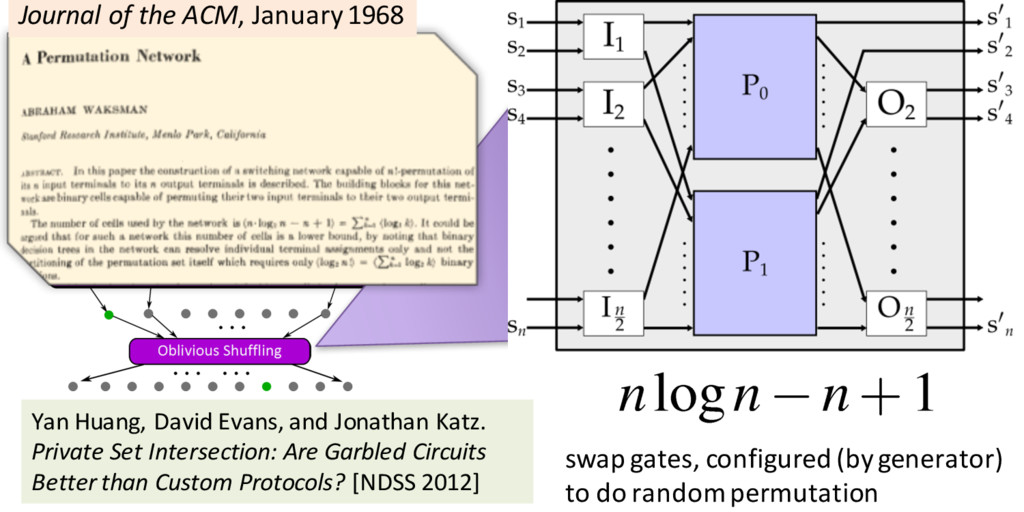
Journal of the ACM, January 1968 swap gates, configured (by
generator) to do random permutation Yan Huang, David Evans, and Jonathan Katz. Private Set Intersection: Are Garbled Circuits Better than Custom Protocols? [NDSS 2012] -
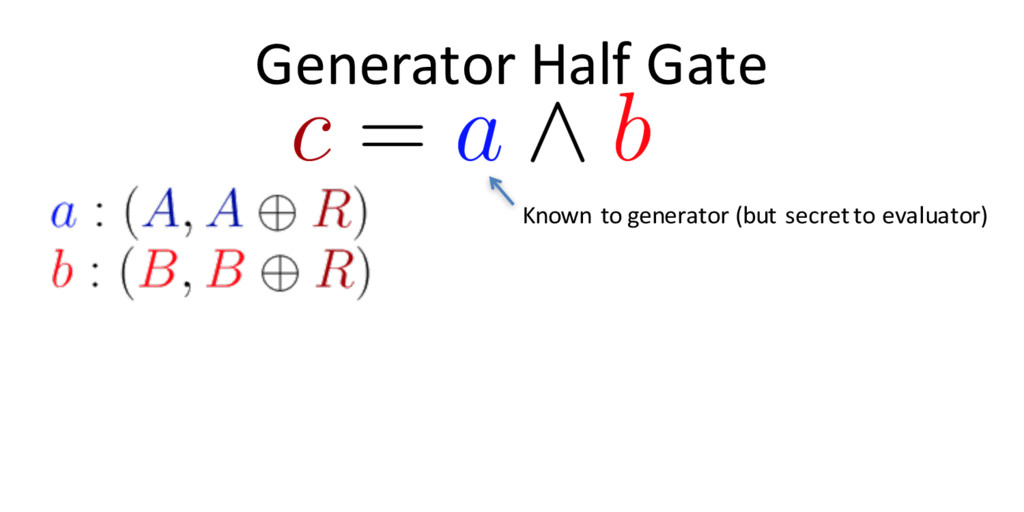
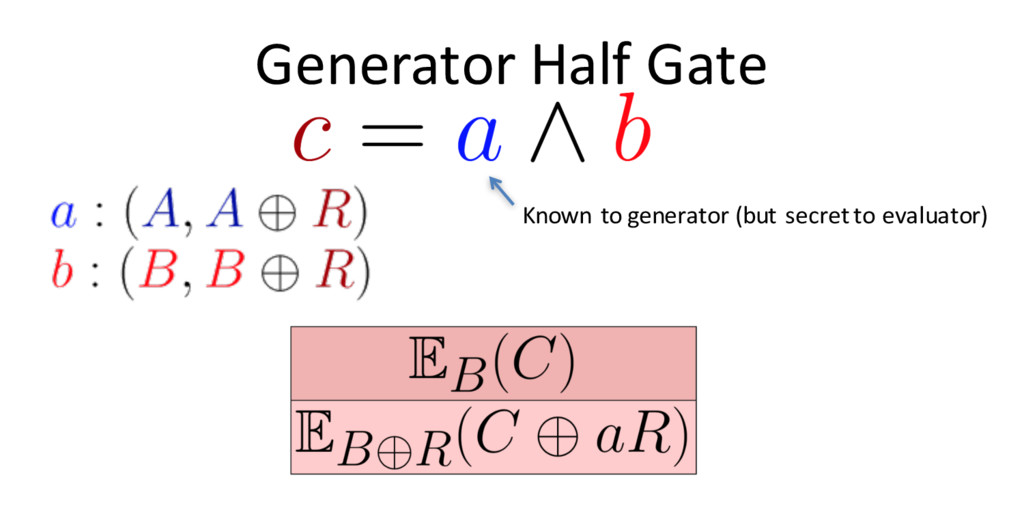
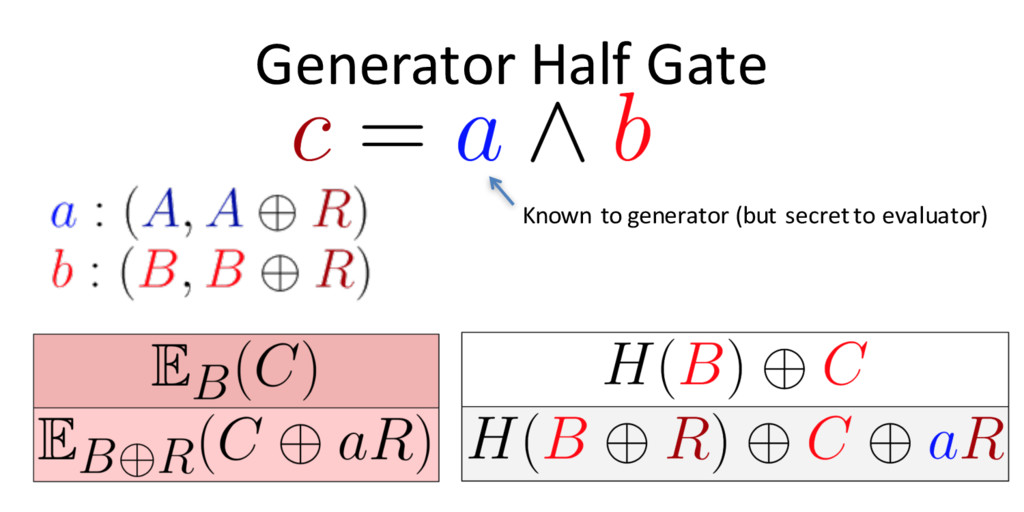
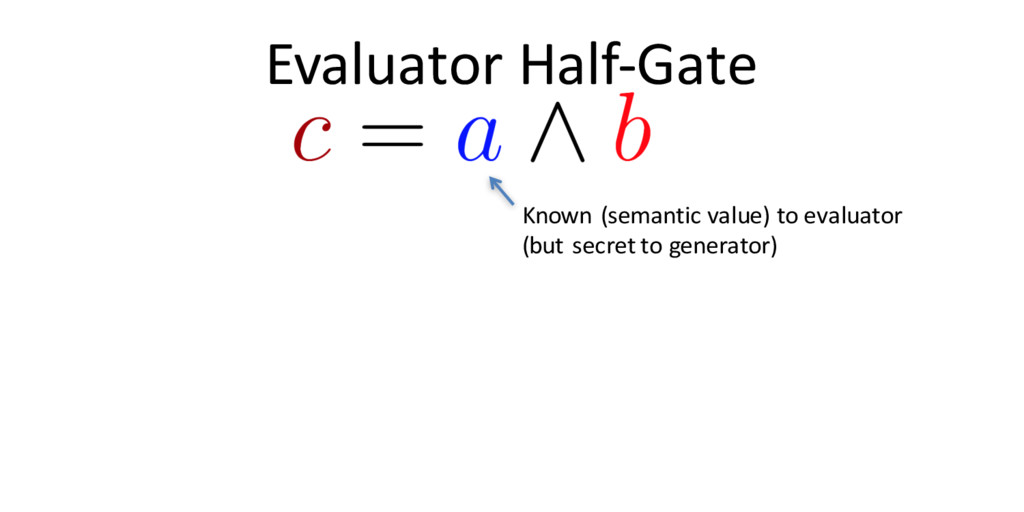
Swapper: “Generator Half Gate” Known to generator (but secret to
evaluator) With Garbled Row Reduction: Only need to send one ciphertext! -
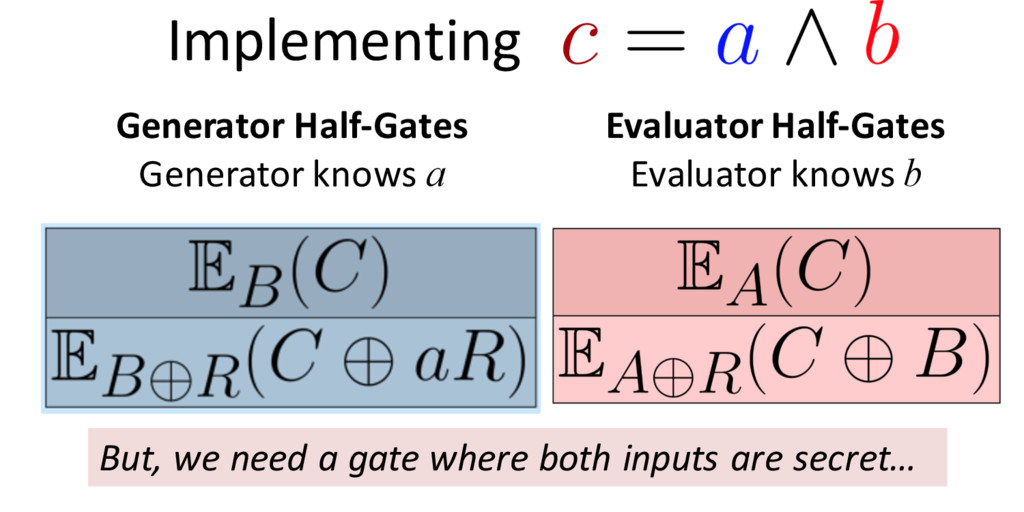
Generator Half-Gates Generator knows a Evaluator Half-Gates Evaluator knows b
Implementing But, we need a gate where both inputs are secret… -
Half + Half = Full Secret Gate random bit selected
by generator “leaked” unknown known unknown -
Half + Half = Full Secret Gate random bit selected
by generator “leaked” unknown known unknown -
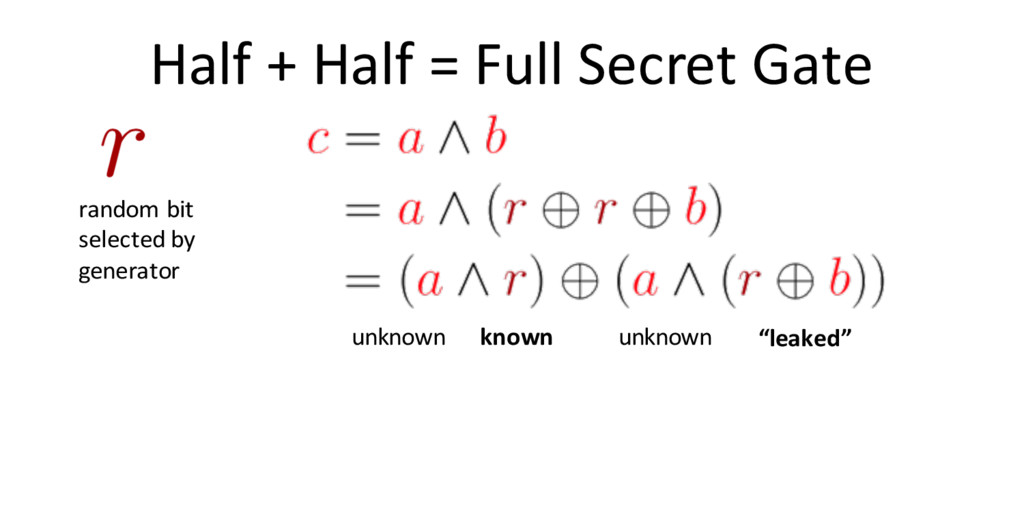
Half + Half = Full Secret Gate random bit selected
by generator “leaked” unknown known unknown -
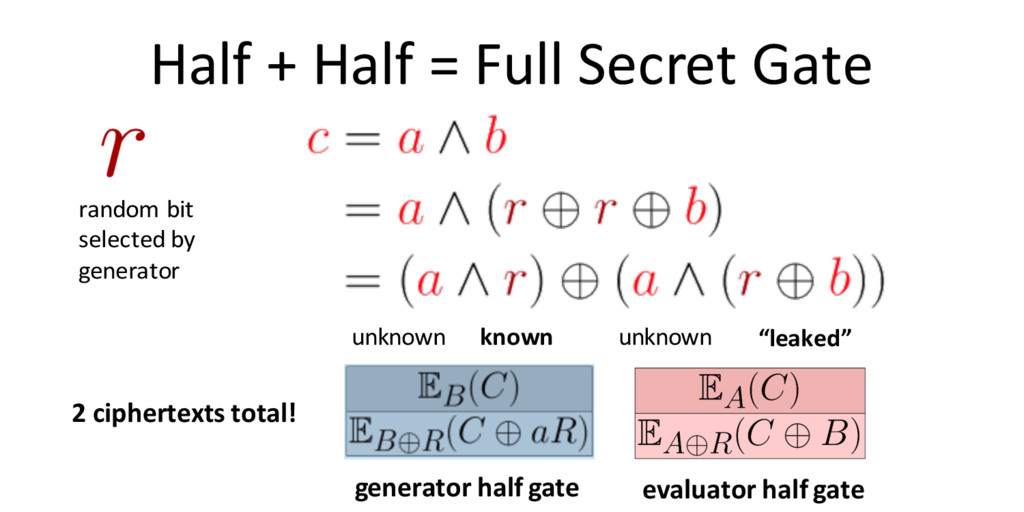
Half + Half = Full Secret Gate random bit selected
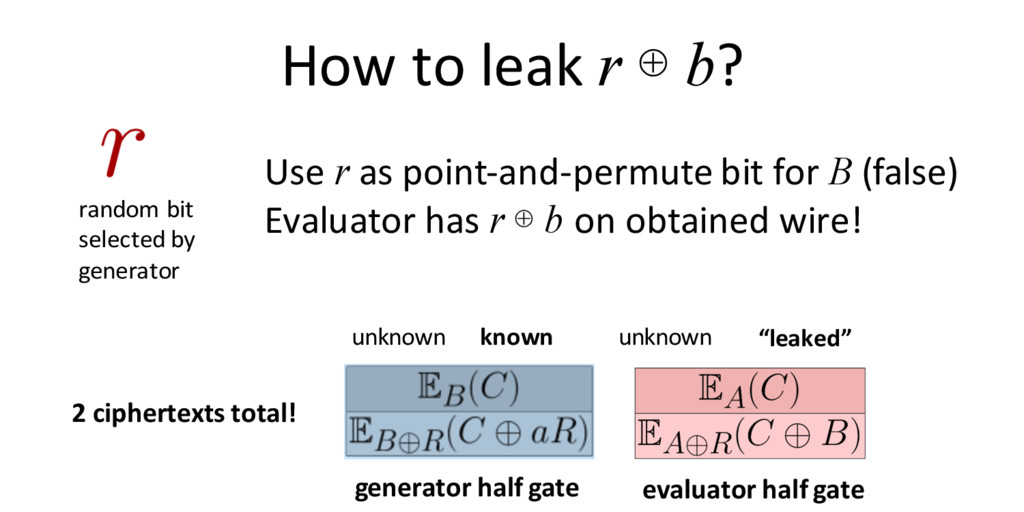
by generator generator half gate evaluator half gate “leaked” unknown known unknown 2 ciphertexts total! -
How to leak r ⊕ b? random bit selected by
generator generator half gate evaluator half gate “leaked” unknown known unknown 2 ciphertexts total! Use r as point-and-permute bit for B (false) Evaluator has r ⊕ b on obtained wire! -
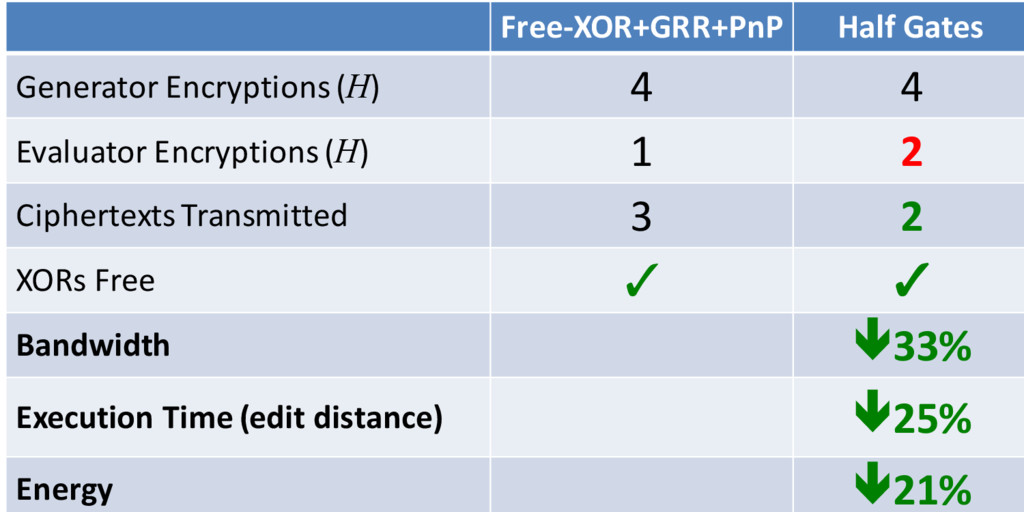
Free-XOR+GRR+PnP Half Gates Generator Encryptions (H) 4 4 Evaluator Encryptions
(H) 1 2 Ciphertexts Transmitted 3 2 XORs Free ✓ ✓ Bandwidth ê33% Execution Time (edit distance) ê25% Energy ê21% -
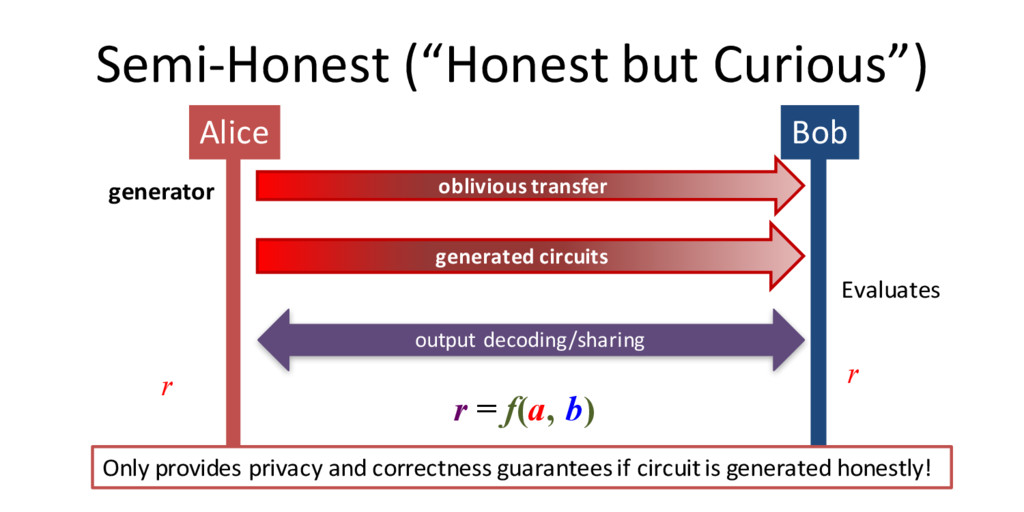
Semi-Honest (“Honest but Curious”) Alice Bob generated circuits generator oblivious
transfer Evaluates r r output decoding/sharing r = f(a, b) Only provides privacy and correctness guarantees if circuit is generated honestly! -
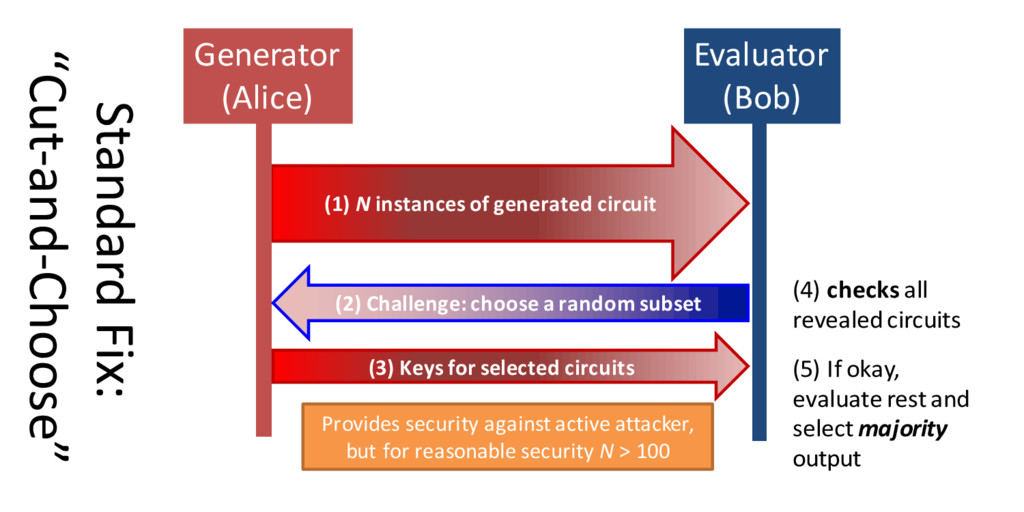
Standard Fix: “Cut-and-Choose” Generator (Alice) Evaluator (Bob) (1) N instances
of generated circuit (5) If okay, evaluate rest and select majority output (4) checks all revealed circuits (2) Challenge: choose a random subset (3) Keys for selected circuits Provides security against active attacker, but for reasonable security N > 100 -
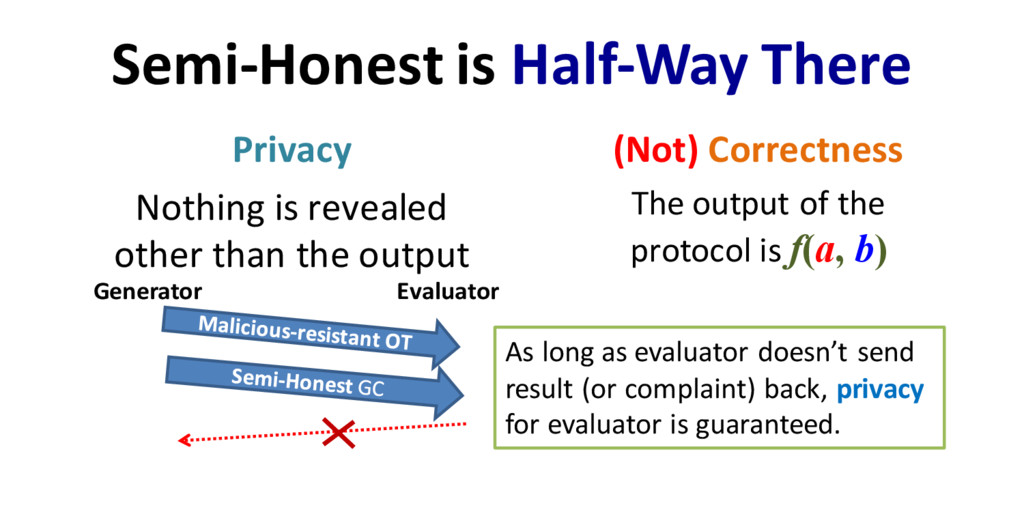
Semi-Honest is Half-Way There Privacy Nothing is revealed other than
the output (Not) Correctness The output of the protocol is f(a, b) Generator Evaluator As long as evaluator doesn’t send result (or complaint) back, privacy for evaluator is guaranteed. -
Dual Execution Protocols Mohassel & Franklin [PKC 2006] Huang, Katz,
Evans. [IEEE S&P 2012] -
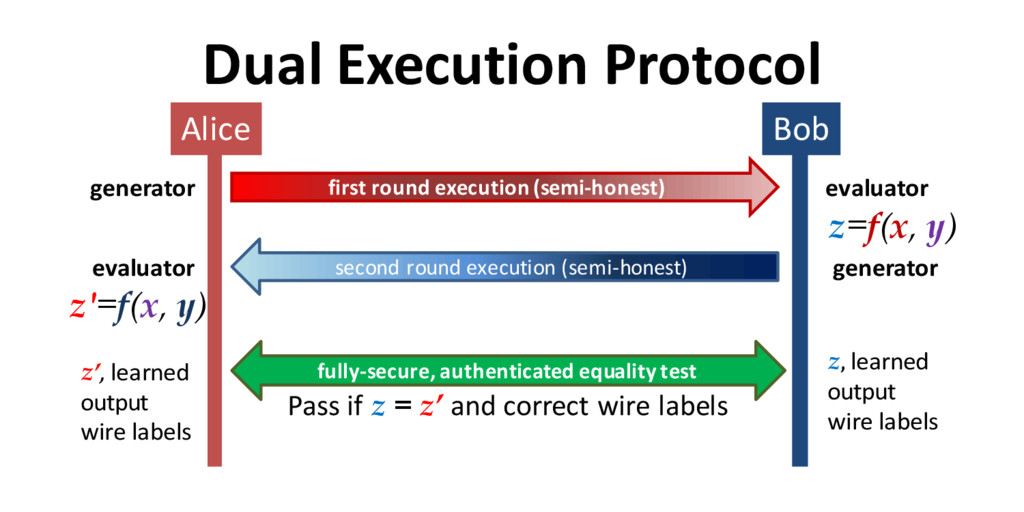
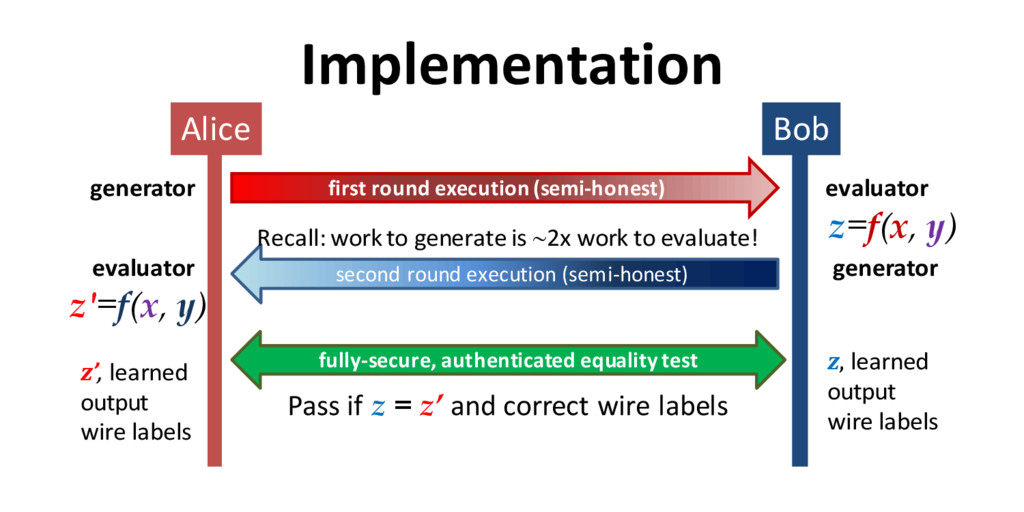
Dual Execution Protocol Alice Bob first round execution (semi-honest) generator
evaluator generator evaluator z=f(x, y) Pass if z = z’ and correct wire labels z’, learned output wire labels second round execution (semi-honest) z'=f(x, y) z, learned output wire labels fully-secure, authenticated equality test -
Proving Security: Malicious A B Ideal World y x Adversary
receives: f (x, y) Trusted Party in Ideal World Standard Malicious Model: can’t prove this for Dual Execution Real World A B y x Show equivalence Corrupted party behaves arbitrarily Secure Computation Protocol -
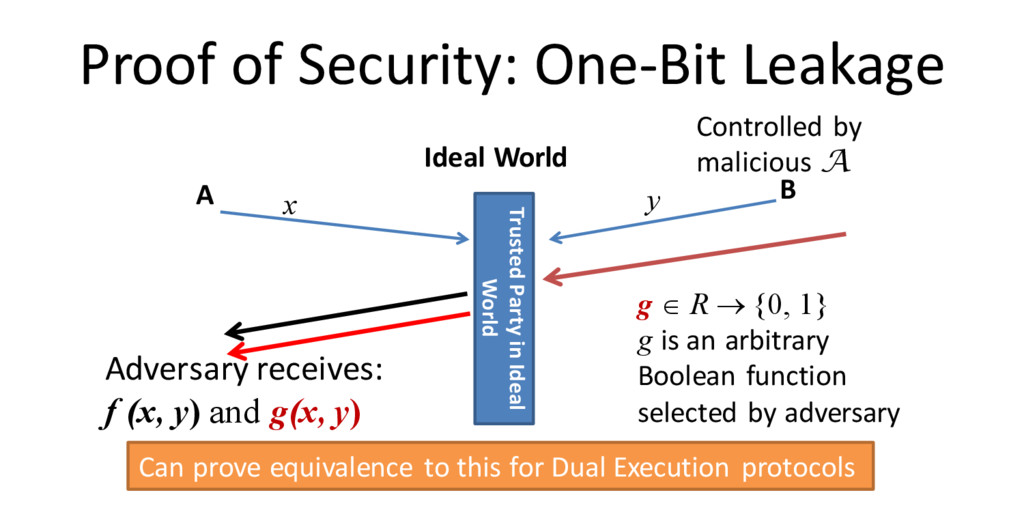
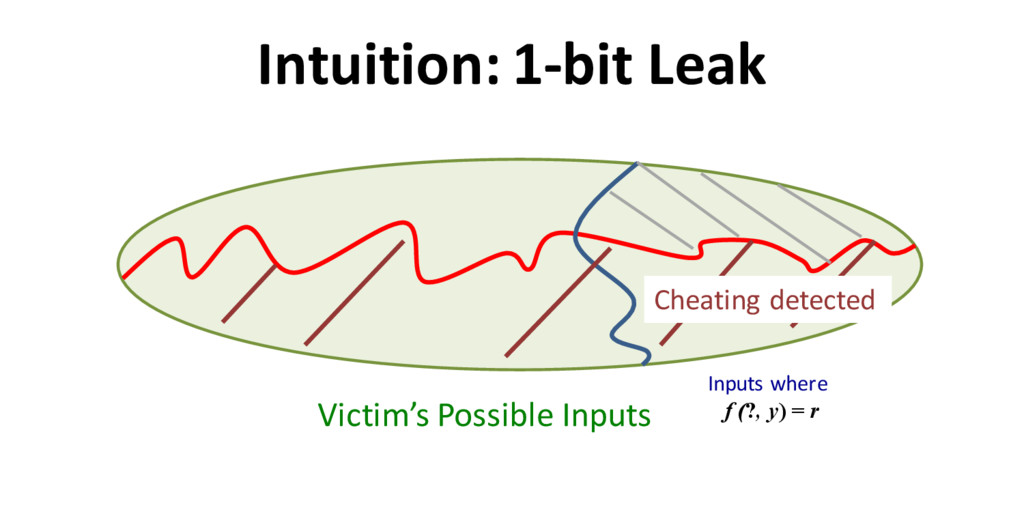
Proof of Security: One-Bit Leakage A B Ideal World y
x Controlled by malicious A g Î R ® {0, 1} g is an arbitrary Boolean function selected by adversary Adversary receives: f (x, y) and g(x, y) Trusted Party in Ideal World Can prove equivalence to this for Dual Execution protocols -
Implementation Alice Bob first round execution (semi-honest) generator evaluator z=f(x,
y) Pass if z = z’ and correct wire labels z’, learned output wire labels generator evaluator second round execution (semi-honest) z'=f(x, y) z, learned output wire labels Recall: work to generate is ~2x work to evaluate! fully-secure, authenticated equality test -
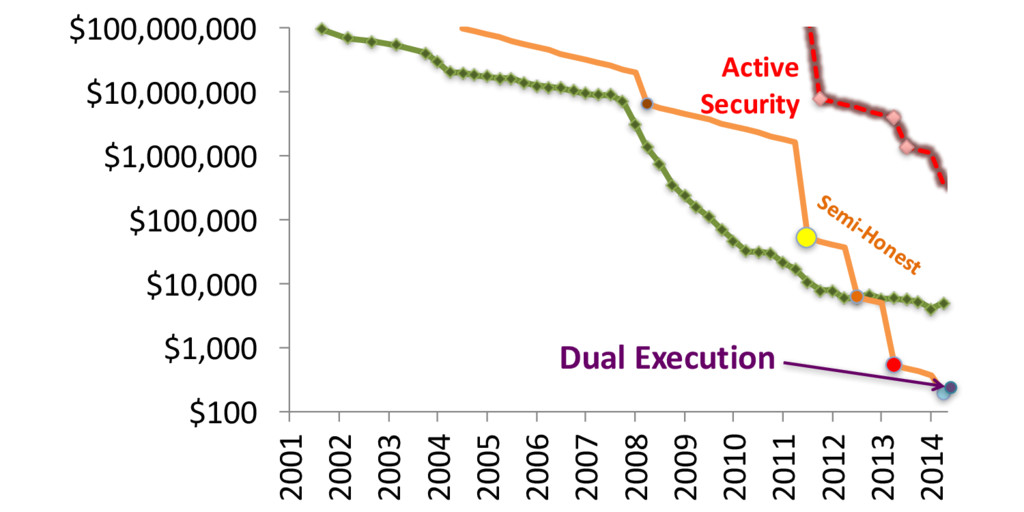
$100 $1,000 $10,000 $100,000 $1,000,000 $10,000,000 $100,000,000 2001 2002 2003
2004 2005 2006 2007 2008 2009 2010 2011 2012 2013 2014 Active Security Dual Execution -
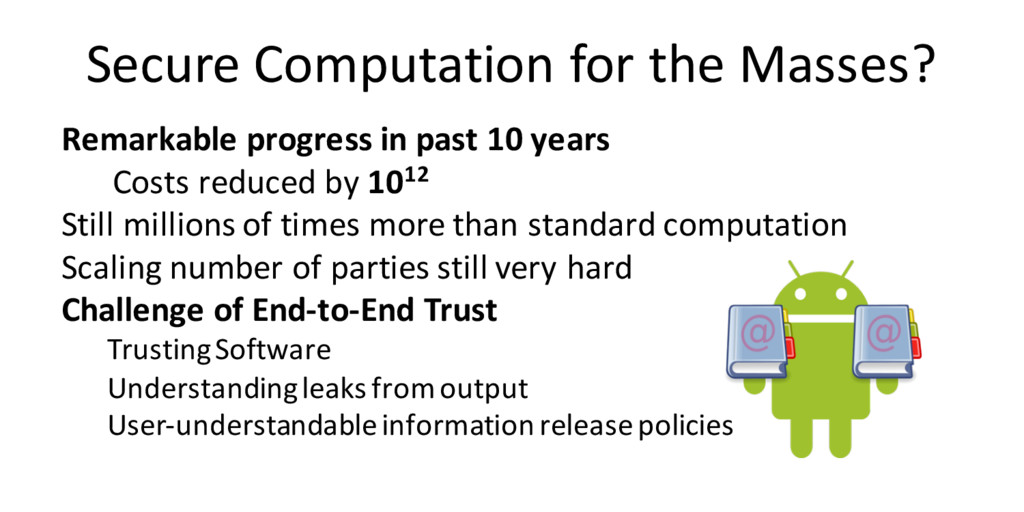
Secure Computation for the Masses? Remarkable progress in past 10
years Costs reduced by 1012 Still millions of times more than standard computation Scaling number of parties still very hard Challenge of End-to-End Trust Trusting Software Understanding leaks from output User-understandable information release policies