Upgrade to Pro — share decks privately, control downloads, hide ads and more …

CocoaHeads - iOS Reverse Engineering

Sponsored · Ship Features Fearlessly Turn features on and off without deploys. Used by thousands of Ruby developers. →

CocoaHeads - iOS Reverse Engineering

Showing several ways to reverse engineer iOS app: IPA analysis, binary disassembling, and code injection. Defense strategies to mitigate these attacks.

Avatar for Gaël Foppolo

Gaël Foppolo

November 21, 2019

Other Decks in Programming

Transcript

  1. ©2019 iOS Reverse Engineering 2 Summary A Closer Look of

    IPA Static analysis with Hopper Code injection with Cycript, Frida & Objection Mitigating & Defenses Strategies
  2. ©2019 iOS Reverse Engineering 3 Reverse engineering Analyzing how something

    is working by only examining the final product.
  3. ©2019 iOS Reverse Engineering 7 IPA Payloads iOS App Store

    Package — a container file (ZIP) A relatively flat structure Executable file, frameworks & resources Already, we can find a lot!
  4. ©2019 iOS Reverse Engineering 10 Static analysis Analysis of computer

    software that is performed without actually executing it.
  5. ©2019 iOS Reverse Engineering 11 Disassembling ARM architecture (AArch64 &

    AArch32) FAT binary (multi-architecture) Hopper
  6. ©2019 iOS Reverse Engineering 12 FairPlay™ DRM Every application downloaded

    is encrypted* Private key (device) + public key (Apple) Decrypted at each launch by iOS * Only native application from App Store — e.g. exclude Entreprise and React Native
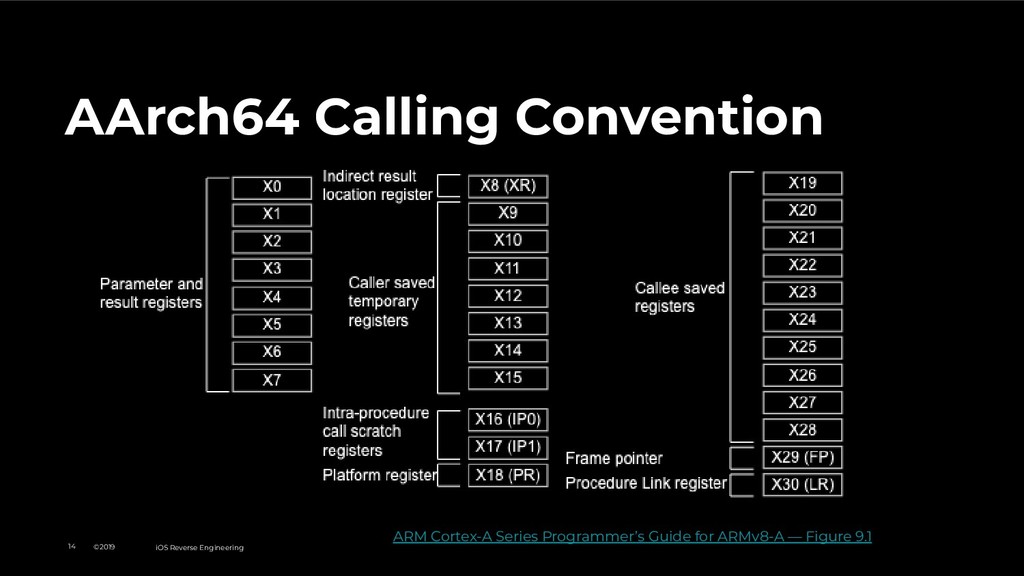
  7. ©2019 iOS Reverse Engineering 14 AArch64 Calling Convention ARM Cortex-A

    Series Programmer’s Guide for ARMv8-A — Figure 9.1
  8. ©2019 iOS Reverse Engineering 17 Dynamic analysis Analysis of computer

    software that is performed by executing it on a processor.
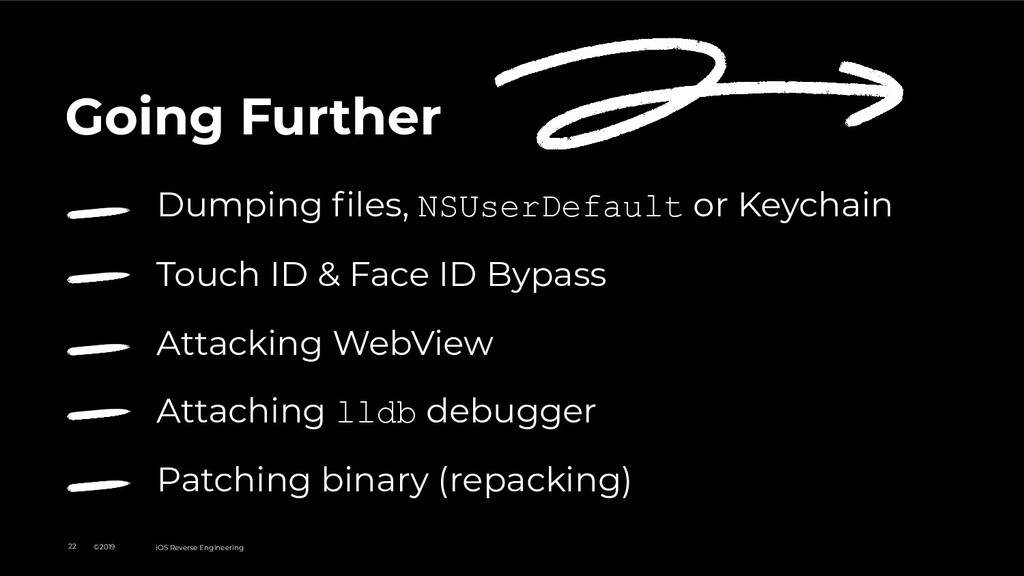
  9. ©2019 iOS Reverse Engineering 22 Going Further Dumping files, NSUserDefault

    or Keychain Touch ID & Face ID Bypass Attacking WebView Attaching lldb debugger Patching binary (repacking)
  10. ©2019 iOS Reverse Engineering 24 IPA analysis Remove useless and

    sensitive info & files Take a look at your IPA! You’ll be surprised!
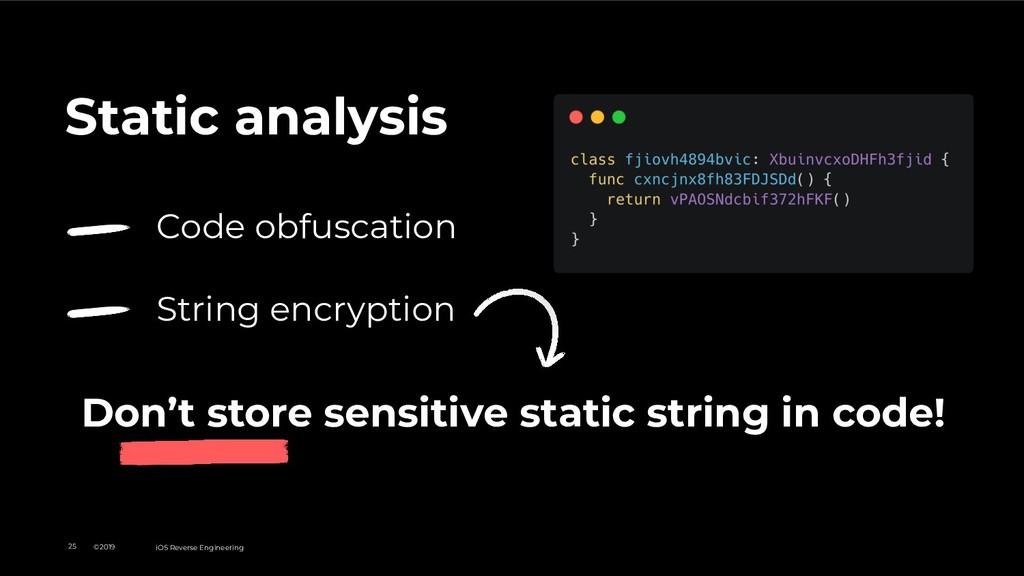
  11. ©2019 iOS Reverse Engineering 25 Static analysis String encryption Don’t

    store sensitive static string in code! Code obfuscation
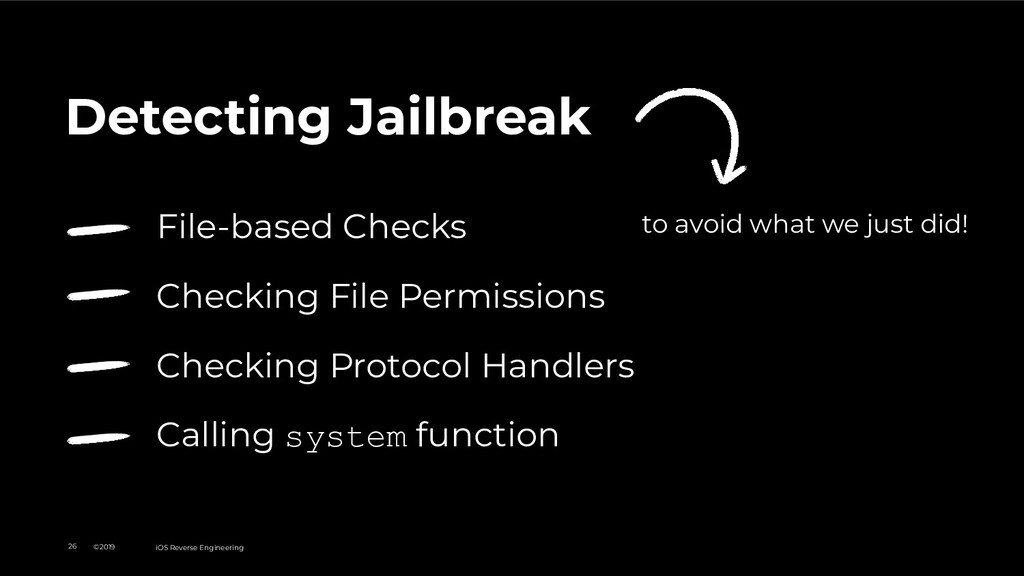
  12. ©2019 iOS Reverse Engineering 26 Detecting Jailbreak File-based Checks Checking

    File Permissions Checking Protocol Handlers Calling system function to avoid what we just did!
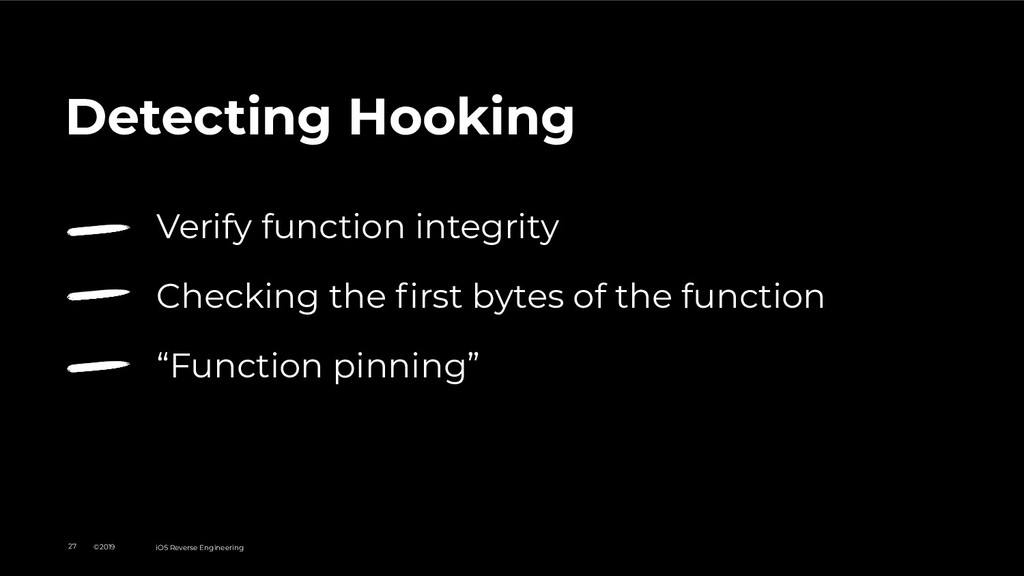
  13. ©2019 iOS Reverse Engineering 27 Detecting Hooking Verify function integrity

    Checking the first bytes of the function “Function pinning”
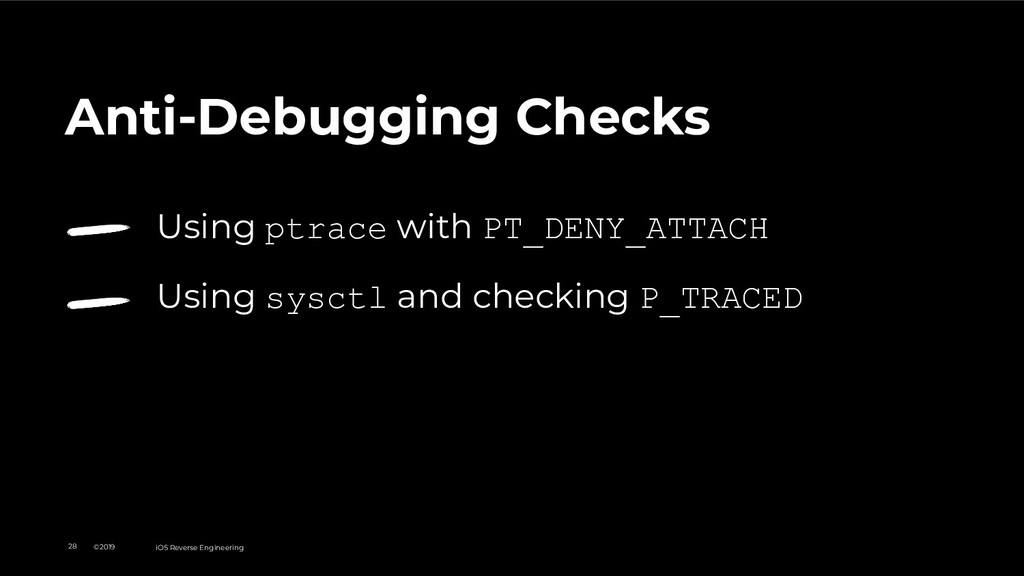
  14. ©2019 iOS Reverse Engineering 28 Anti-Debugging Checks Using ptrace with

    PT_DENY_ATTACH Using sysctl and checking P_TRACED
  15. ©2019 iOS Reverse Engineering 29 Be paranoid! Multiply security layers

    — like an onion Don’t trust — check Always validate access right!
  16. ©2019 iOS Reverse Engineering 30 Keep in mind No application

    is secure in the hands of a skilled attacker.
  17. ©2019 iOS Reverse Engineering 32 References OWASP Mobile Security Testing

    Guide OWASP Mobile AppSec Verification Standard ARM Cortex-A Series Programmer’s Guide for ARMv8-A QA1361 - Detecting the Debugger (Documentation Archive — Apple) Ghidra — Hopper — IDA Cycript — Frida — objection — usbmuxd Tools