Fluid XSS

Fluid XSS
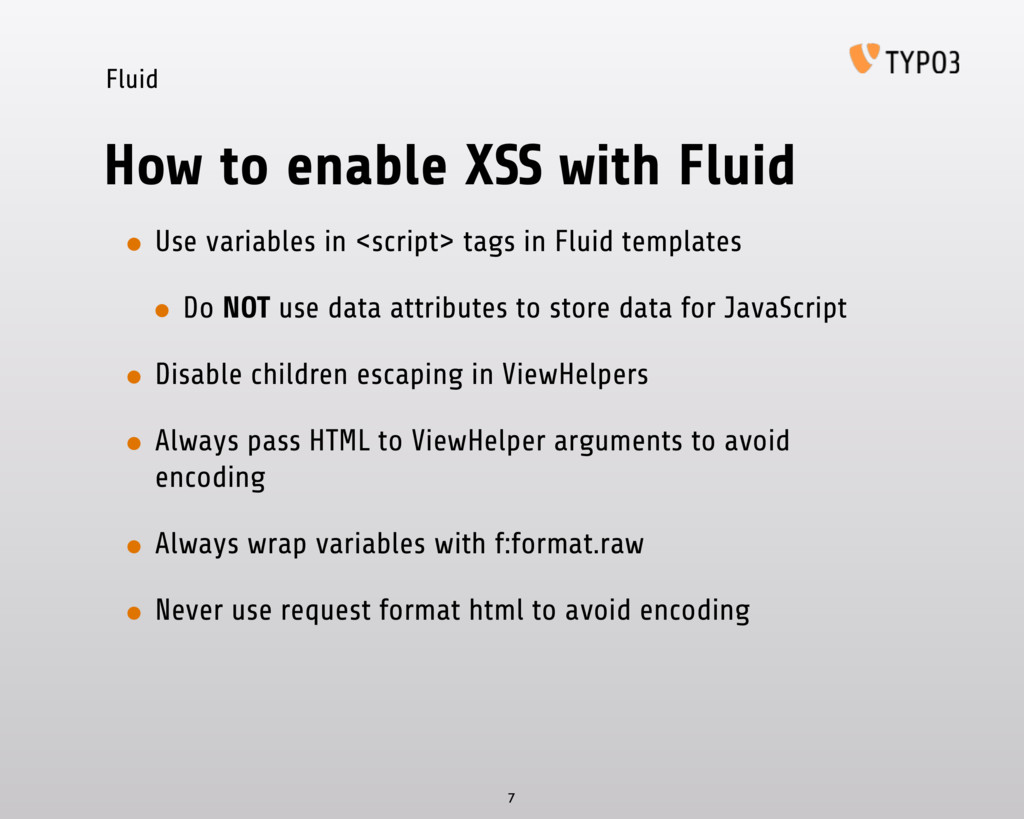
Following the advice given in this presentation, your Fluid templates and View Helpers will potentially enable various XSS attacks

Helmut Hummel
June 12, 2016
Following the advice given in this presentation, your Fluid templates and View Helpers will potentially enable various XSS attacks
 helhum
 ama_ch
 shift_evolve
 pipepasta
 yappli_developers
 pauli
 littlehands
 birgitta410
 tomoaki25
 inariku
 ballas_inc
 kobayashiyorimitsu
 lara
 mfonobong
 marketingsoph
 geshan
 khoart
 afnizarnur
 techseoconnect
 codingconduct
 frankvandijk
 tammyeverts
 deanohume
 soudai