Share
Embed
AWS and Ansible | Andrew Kurinnyi
AWS and Ansible integration using CloudFormation.
Matt Chung
February 11, 2015
Transcript
26 slides
-
Managing&mul*ple&stacks&with&Ansible --- - hosts: localhost connection: local gather_facts: False vars:
project: cftest environment: production region: us-east-1 tasks: - name: Create VPC cloudformation: stack_name={{ environment }}-{{ project }}-vpc state=present region="{{ region }}" template=vpc.json args: template_parameters: cidr: 10.8.0.0/16 register: vpc -
- name: Create RDS cloudformation: stack_name={{ environment }}-{{ project }}-rds
state=present region="{{ region }}" template=rds.json args: template_parameters: vpcid: {{ vpc['stack_outputs']['VPCID'] }} subnets: {{ vpc['stack_outputs']['DbSubnets'] }} subnet_index: 0 register: rds -
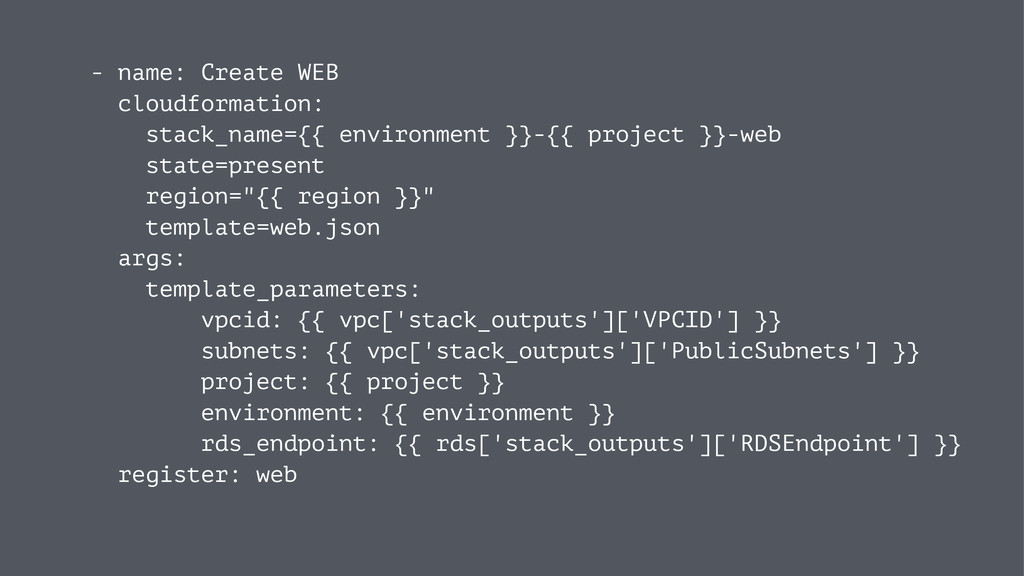
- name: Create WEB cloudformation: stack_name={{ environment }}-{{ project }}-web
state=present region="{{ region }}" template=web.json args: template_parameters: vpcid: {{ vpc['stack_outputs']['VPCID'] }} subnets: {{ vpc['stack_outputs']['PublicSubnets'] }} project: {{ project }} environment: {{ environment }} rds_endpoint: {{ rds['stack_outputs']['RDSEndpoint'] }} register: web -
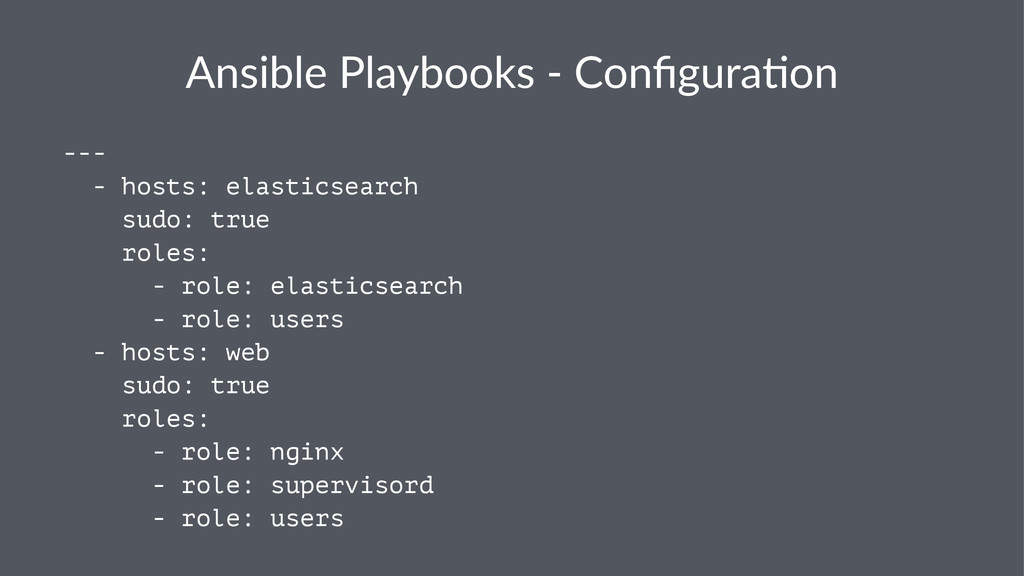
Ansible(Playbooks(.(Configura4on --- - hosts: elasticsearch sudo: true roles: - role:
elasticsearch - role: users - hosts: web sudo: true roles: - role: nginx - role: supervisord - role: users -
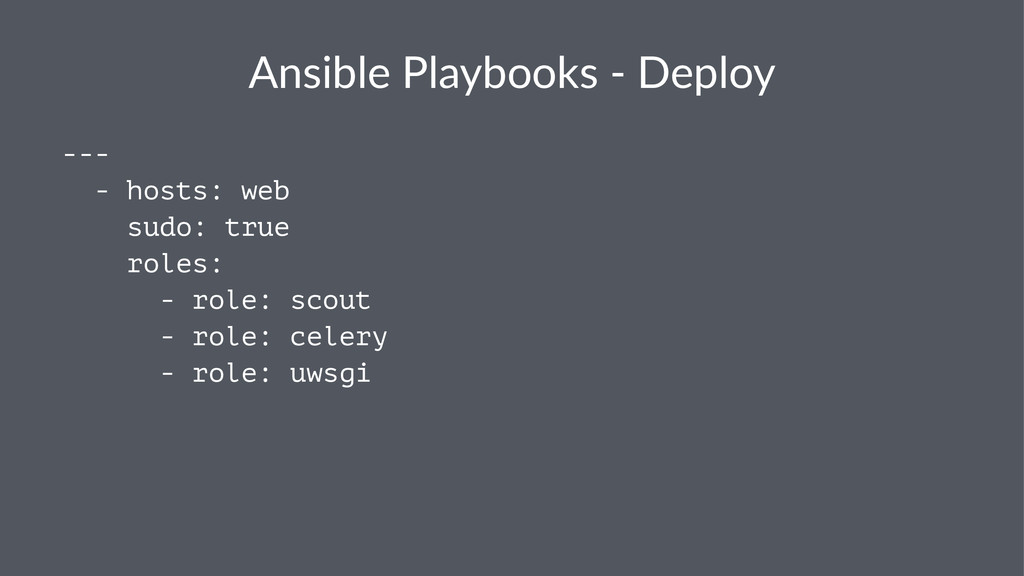
Ansible(Playbooks(.(Deploy --- - hosts: web sudo: true roles: - role:
scout - role: celery - role: uwsgi -
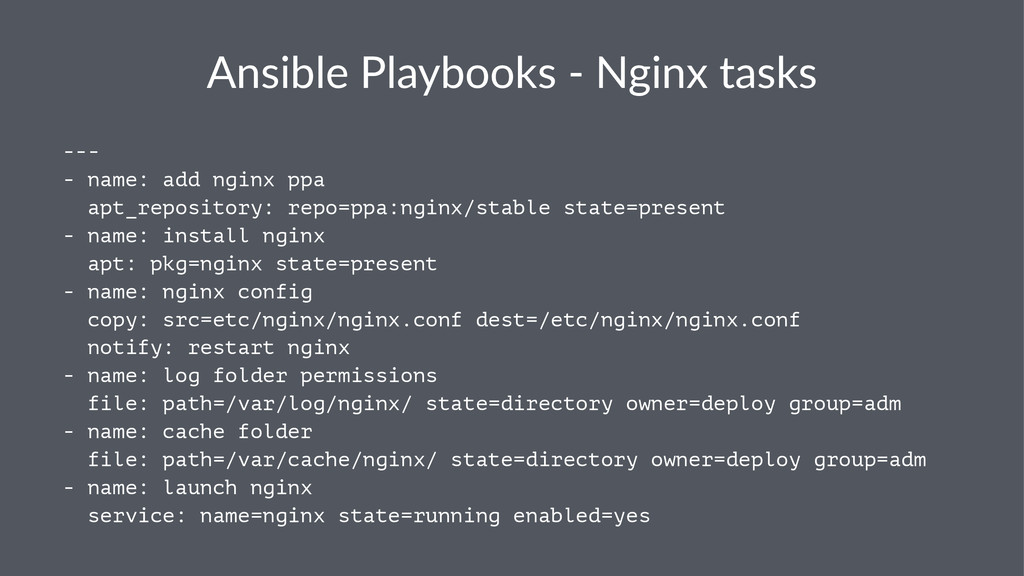
Ansible(Playbooks(.(Nginx(tasks --- - name: add nginx ppa apt_repository: repo=ppa:nginx/stable state=present
- name: install nginx apt: pkg=nginx state=present - name: nginx config copy: src=etc/nginx/nginx.conf dest=/etc/nginx/nginx.conf notify: restart nginx - name: log folder permissions file: path=/var/log/nginx/ state=directory owner=deploy group=adm - name: cache folder file: path=/var/cache/nginx/ state=directory owner=deploy group=adm - name: launch nginx service: name=nginx state=running enabled=yes -
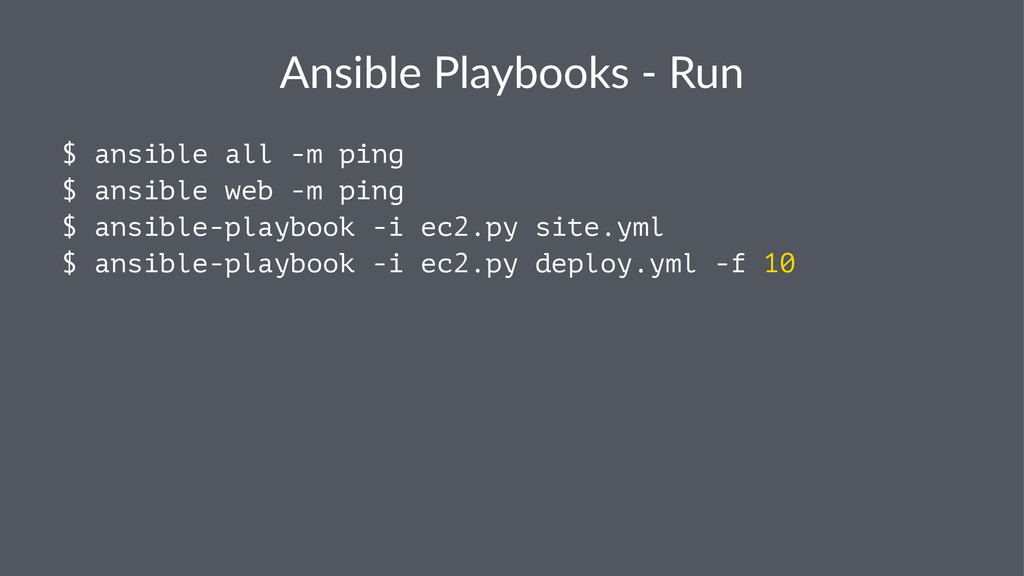
Ansible(Playbooks(.(Run $ ansible all -m ping $ ansible web -m
ping $ ansible-playbook -i ec2.py site.yml $ ansible-playbook -i ec2.py deploy.yml -f 10 -
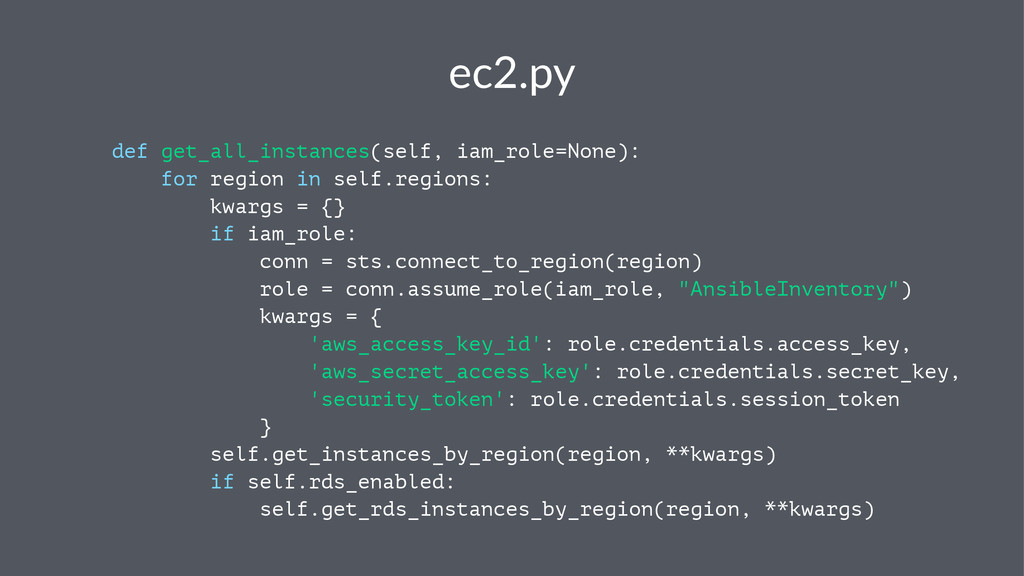
ec2.py def get_all_instances(self, iam_role=None): for region in self.regions: kwargs =
{} if iam_role: conn = sts.connect_to_region(region) role = conn.assume_role(iam_role, "AnsibleInventory") kwargs = { 'aws_access_key_id': role.credentials.access_key, 'aws_secret_access_key': role.credentials.secret_key, 'security_token': role.credentials.session_token } self.get_instances_by_region(region, **kwargs) if self.rds_enabled: self.get_rds_instances_by_region(region, **kwargs) -
Provisioning)on)startup #cloud-config # vim: syntax=yaml packages: - git-core - python-dev
- python-virtualenv - python-pip - awscli runcmd: - update-ca-certificates --fresh - aws --region us-east-1 s3 cp s3://<your_bucket_name>/ansible_config/$(aws --region us-east-1 s3 ls s3://<your_bucket_name>/ansible_config/ | awk '{print $4}' | tail -n1) /tmp/ansible_config.tar.gz - cd /tmp; tar -xzvf ansible_config.tar.gz - cd /tmp/ansible_config; pip install -r requirements.txt - cd /tmp/ansible_config; EC2_INI_PATH="/tmp/ansible_config/config/local.ini" ansible-playbook -i ec2.py site.yml --connection=local --limit `ec2metadata --local-ipv4`,localhost,127.0.0.1 - cd /tmp/ansible_config; EC2_INI_PATH="/tmp/ansible_config/config/local.ini" ansible-playbook -i ec2.py deploy.yml --connection=local --limit `ec2metadata --local-ipv4`,localhost,127.0.0.1 - cd /tmp/ansible_config; EC2_INI_PATH="/tmp/ansible_config/config/local.ini" ansible-playbook -i ec2.py notify.yml --connection=local --limit `ec2metadata --local-ipv4`,localhost,127.0.0.1