Upgrade to Pro — share decks privately, control downloads, hide ads and more …

Testing Android Security CA edition

Testing Android Security CA edition

Testing Android Security Codemotion Amsterdam edition

jmortegac

May 12, 2016

Transcript

88 slides
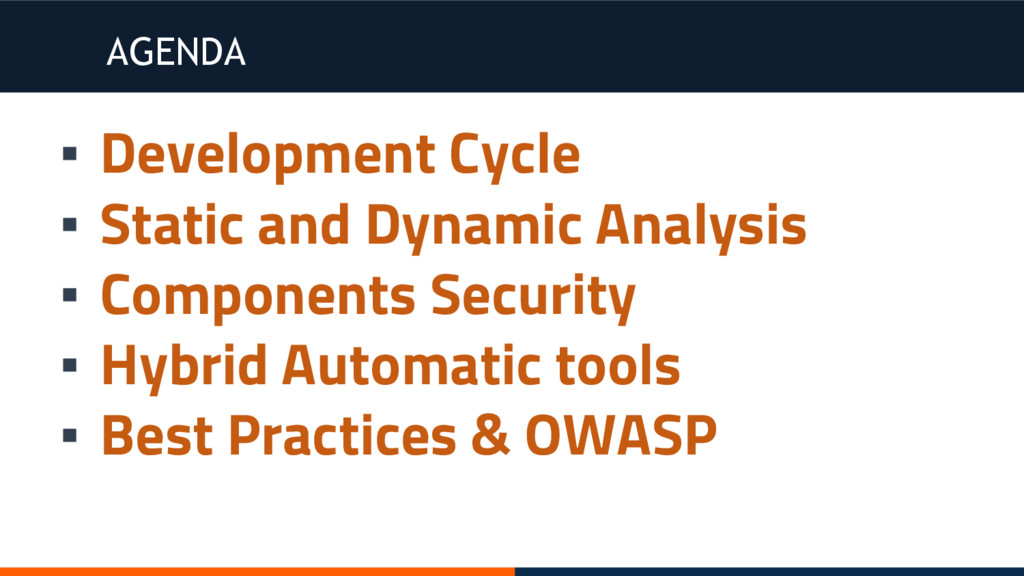
  1. AGENDA ▪ Development Cycle ▪ Static and Dynamic Analysis ▪
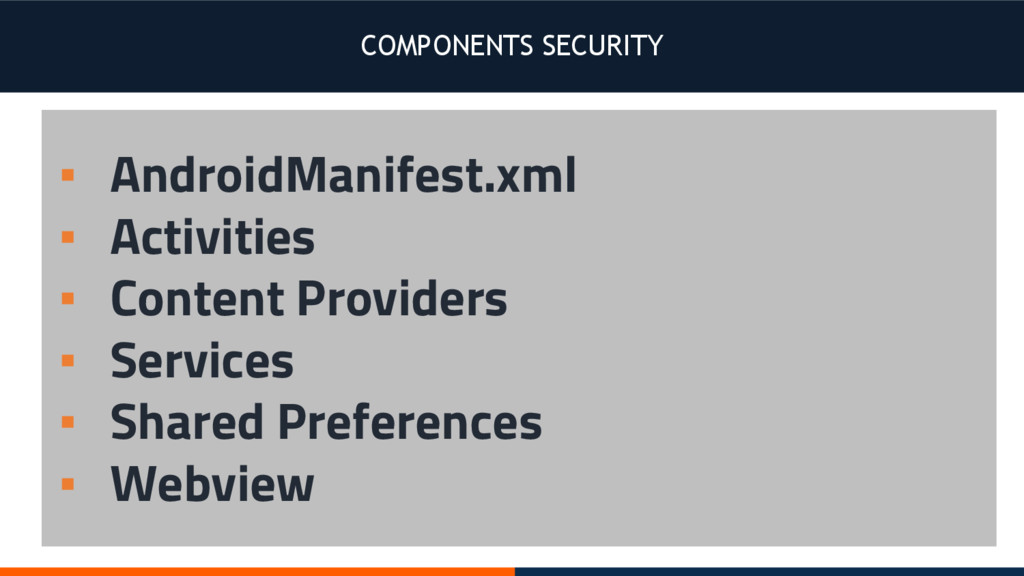
    Components Security ▪ Hybrid Automatic tools ▪ Best Practices & OWASP
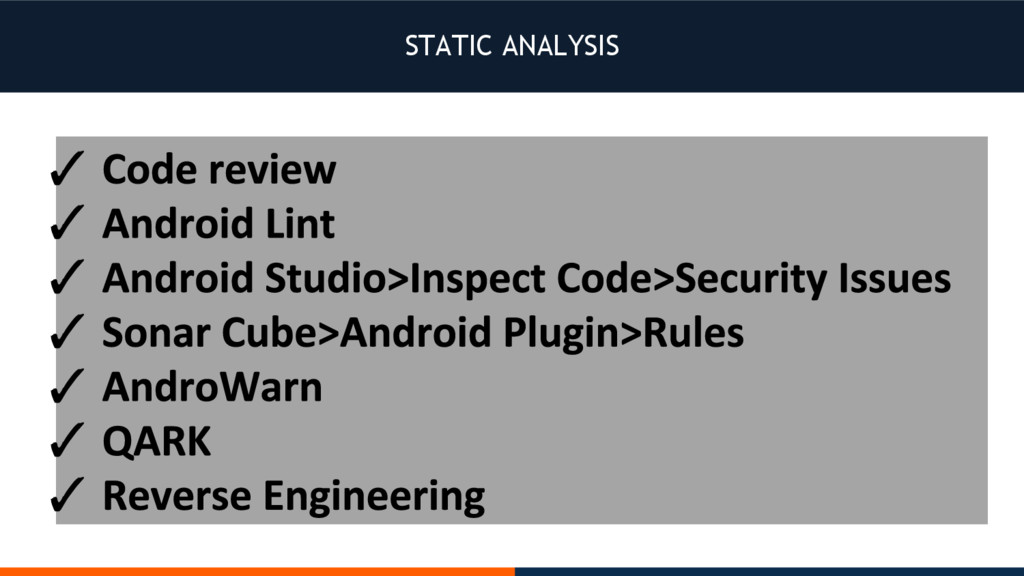
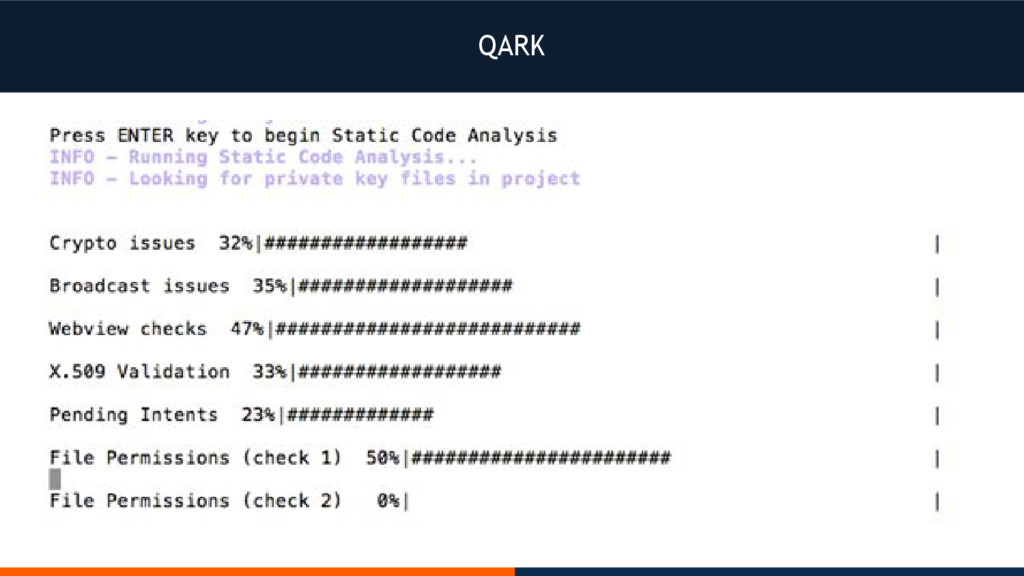
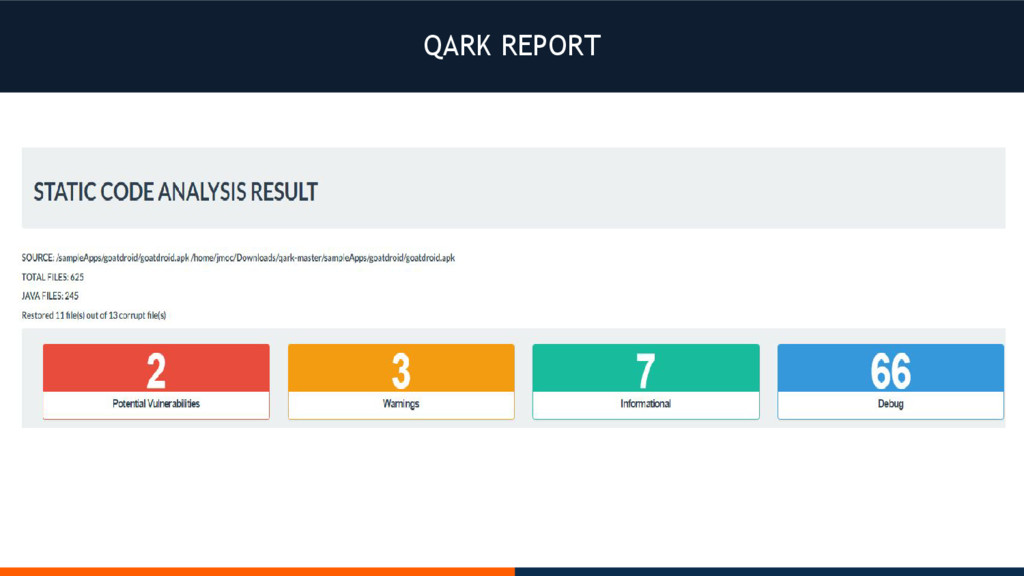
  2. QARK ▪ Quick Android Review Kit ▪ https://github.com/linkedin/qark ▪ Static

    code analysis tool ▪ Look for potential vulnerabilities
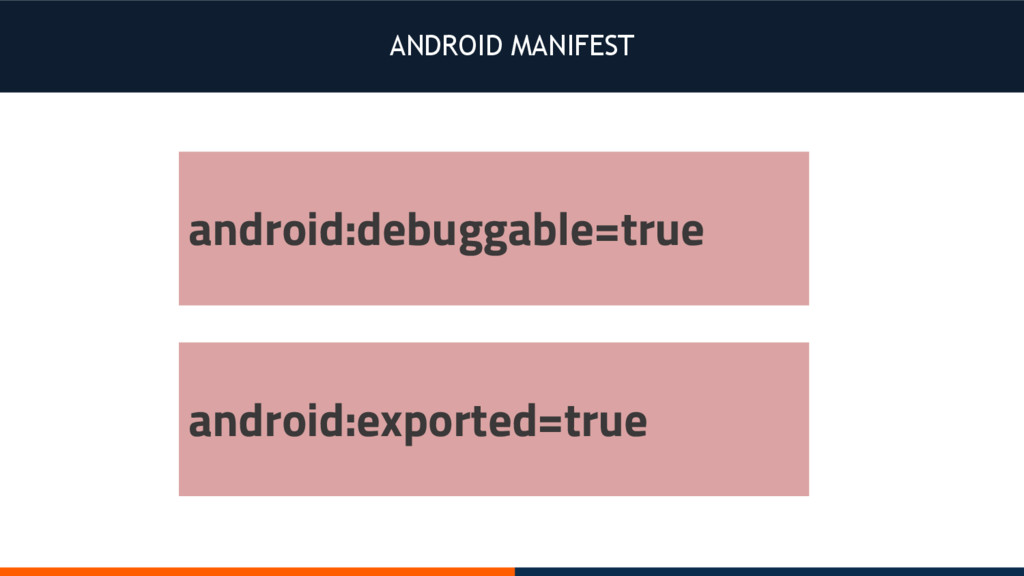
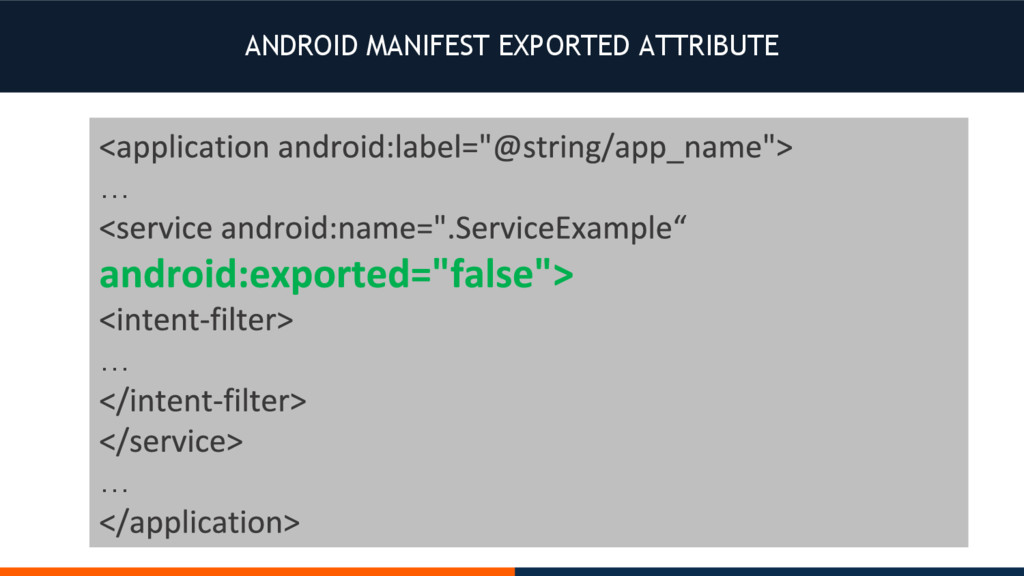
  3. QARK ▪ Identifies permissions and exported components (activities,services..) on Manifest

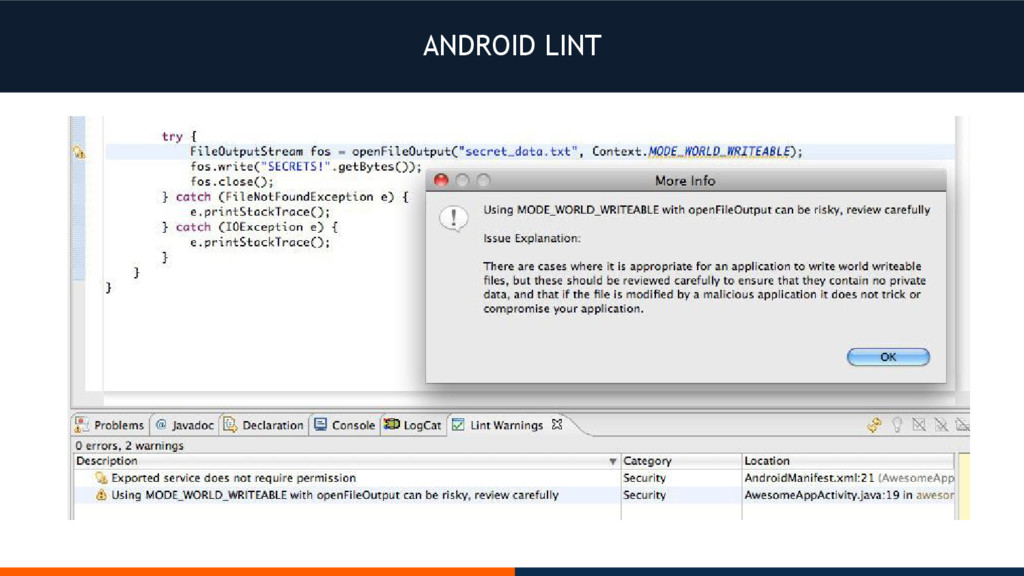
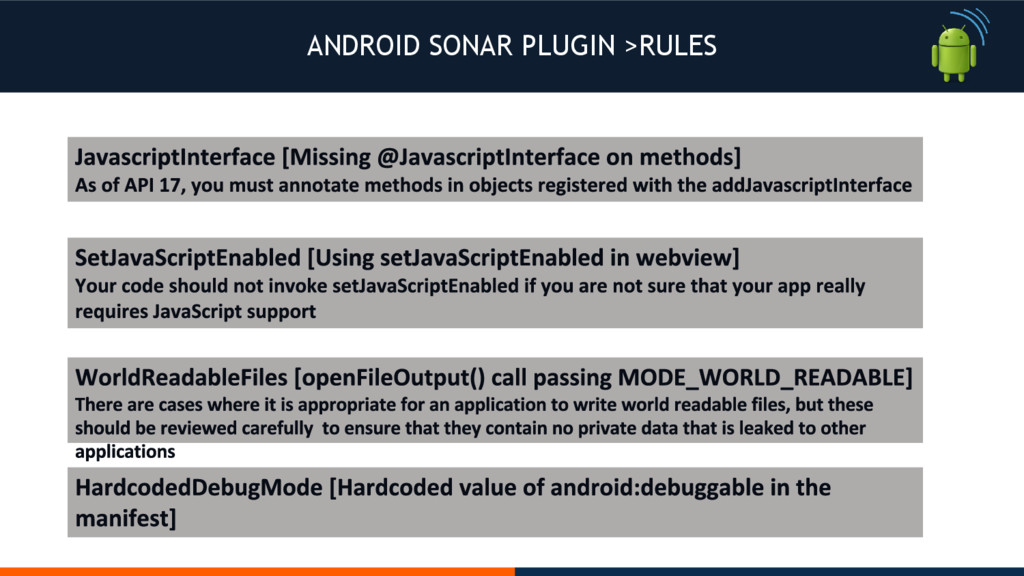
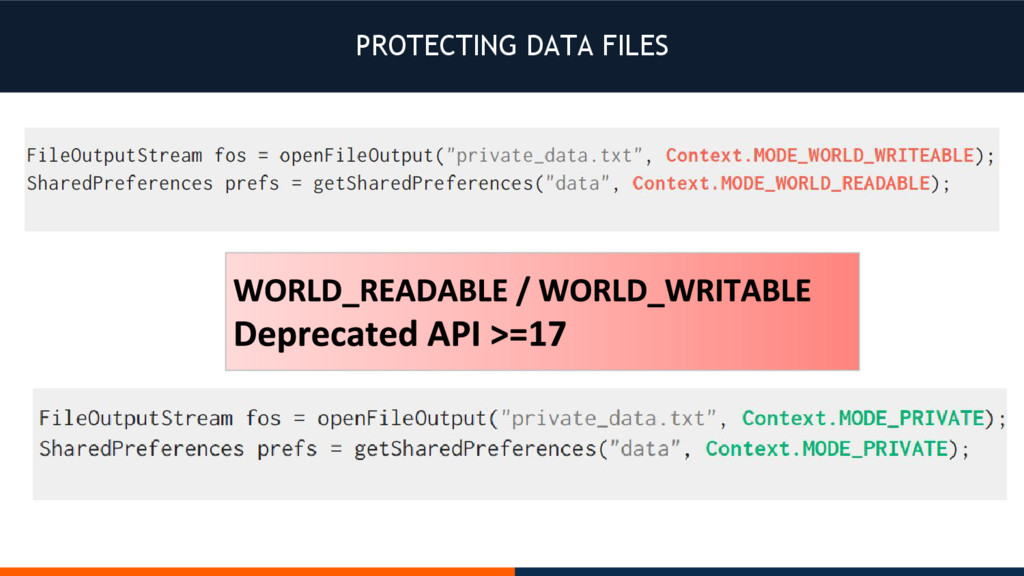
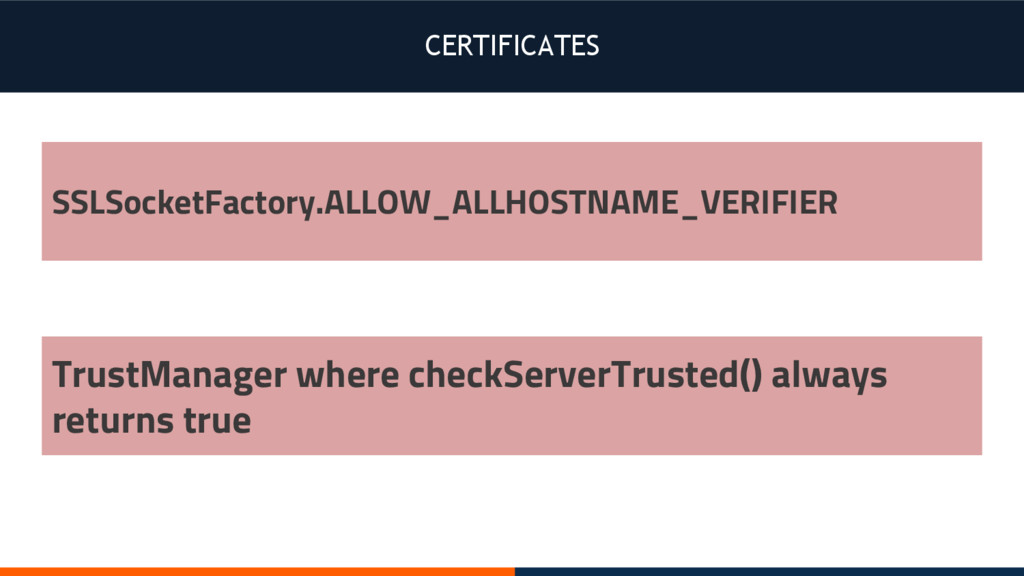
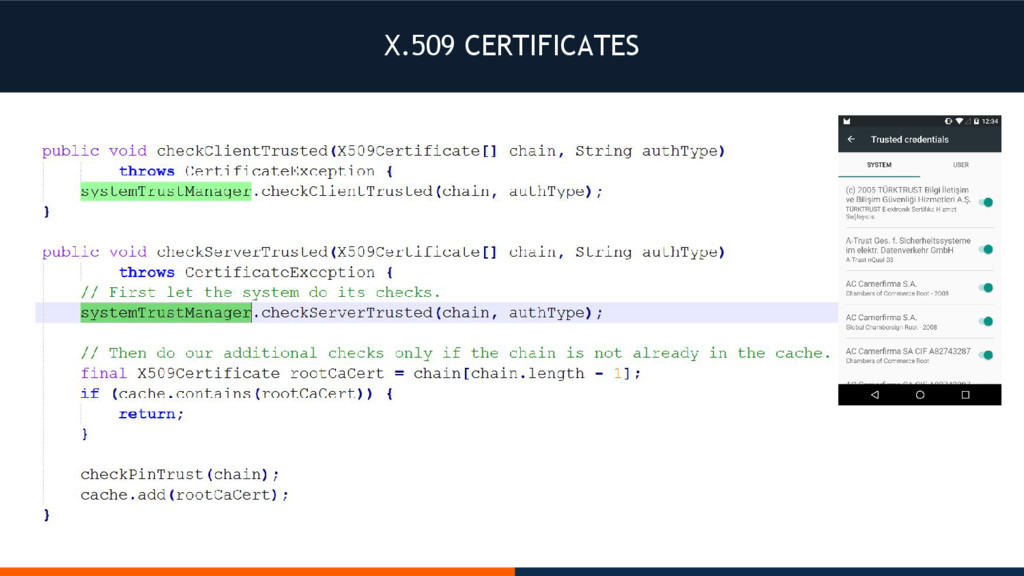
    ▪ Looks for WORLD_READABLE and WORLD_WRITABLE files ▪ Looks for X.509 certificates validation issues
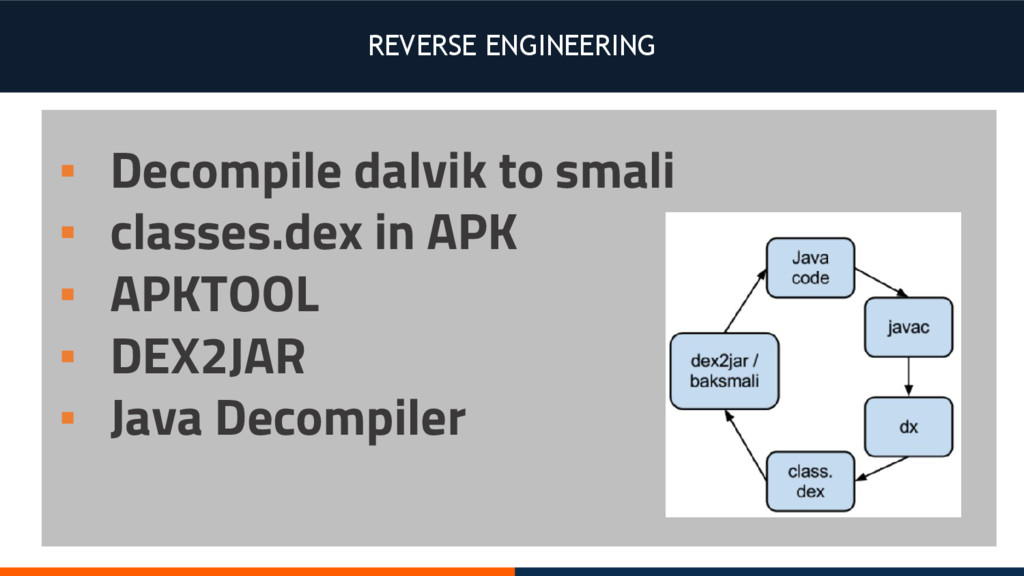
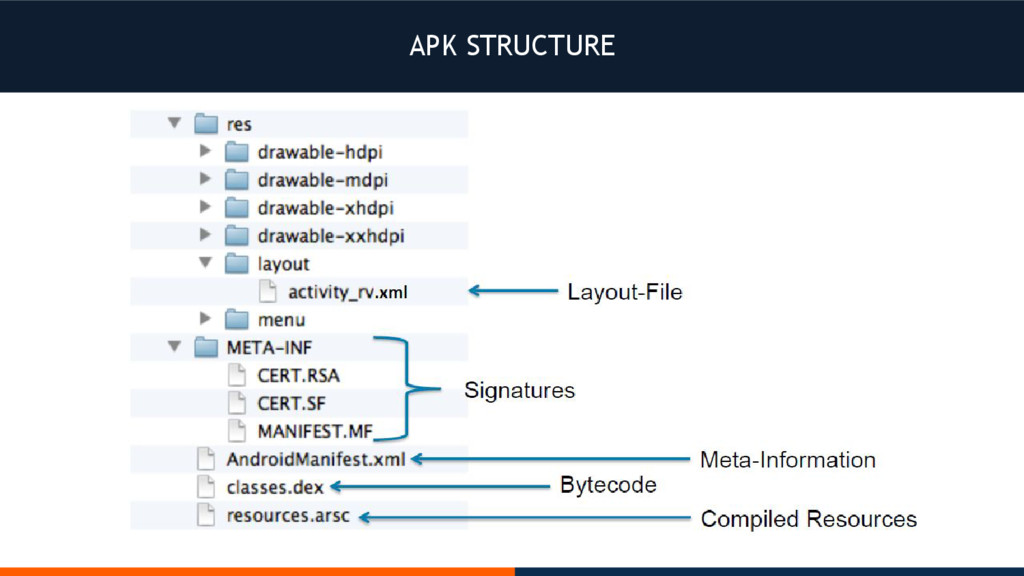
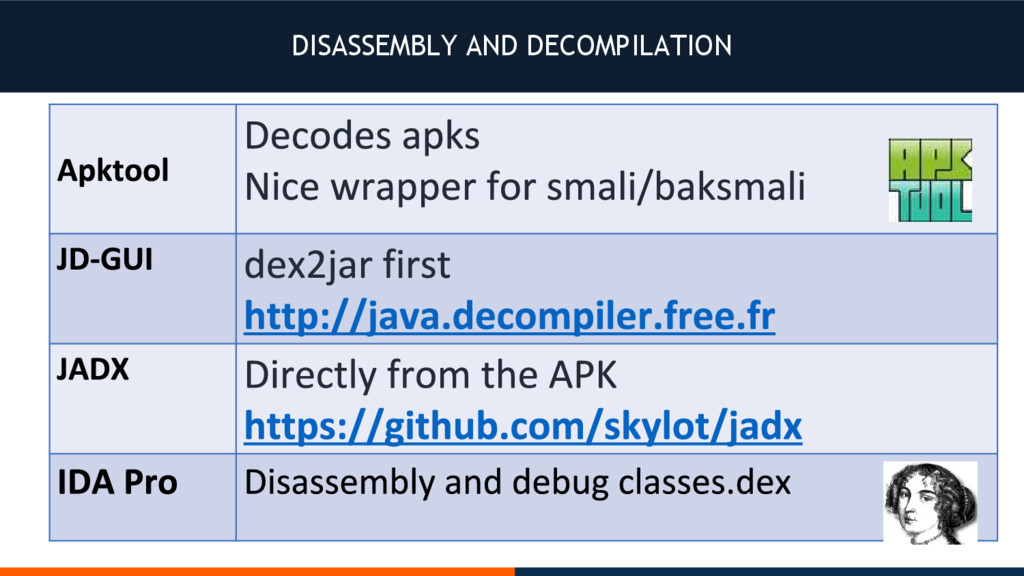
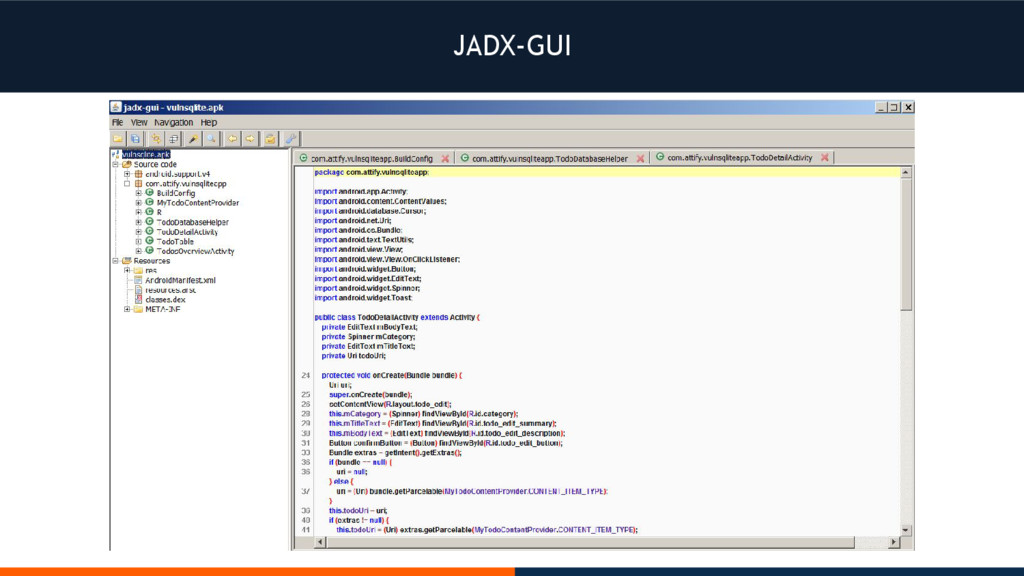
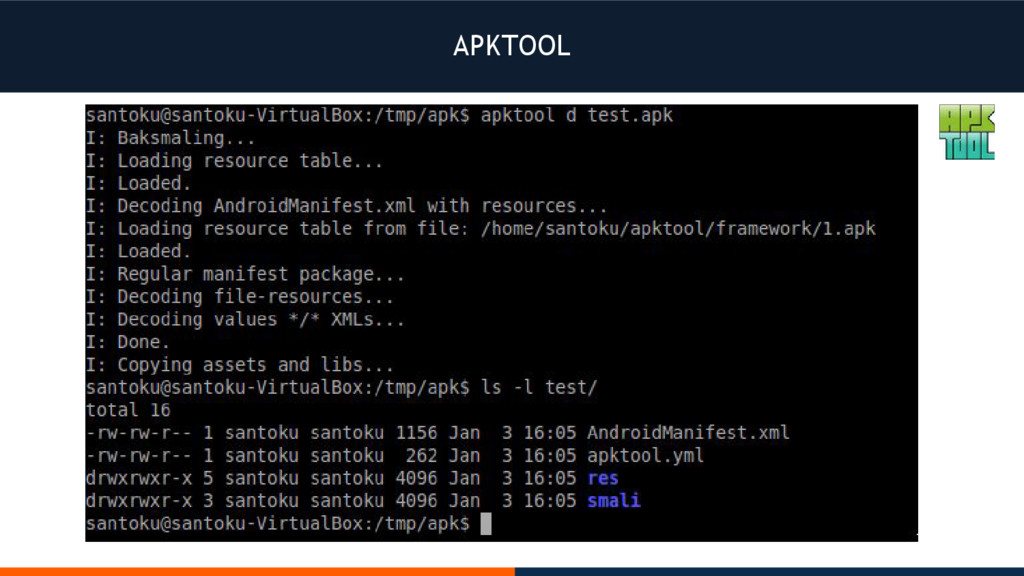
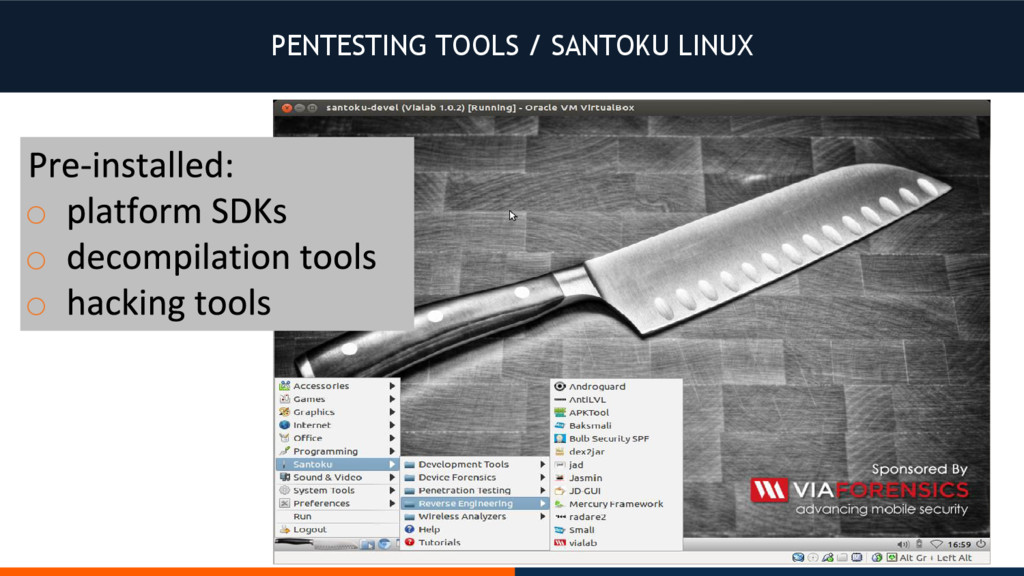
  4. REVERSE ENGINEERING ▪ Decompile dalvik to smali ▪ classes.dex in

    APK ▪ APKTOOL ▪ DEX2JAR ▪ Java Decompiler
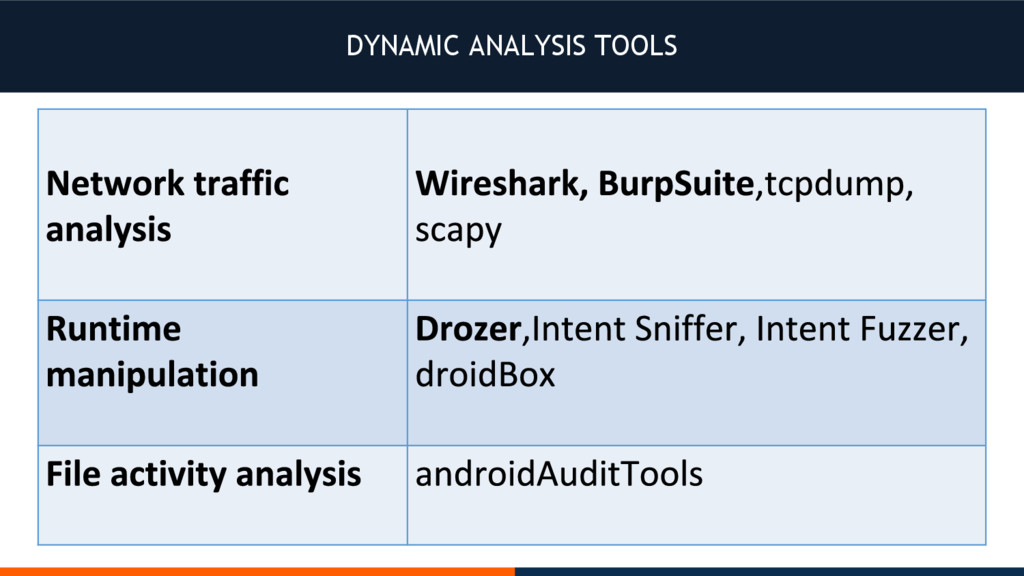
  5. BURP SUITE ▪ Intercepting network traffic ▪ HTTP proxy tool

    ▪ Able to intercept layer traffic and allows users to manipulate the HTTP request and response
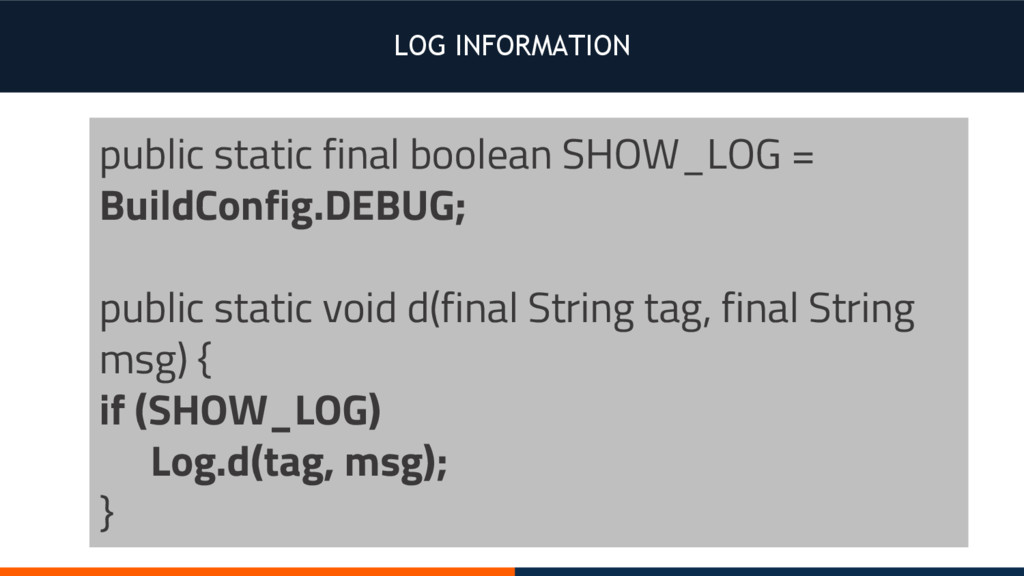
  6. LOG INFORMATION public static final boolean SHOW_LOG = BuildConfig.DEBUG; public

    static void d(final String tag, final String msg) { if (SHOW_LOG) Log.d(tag, msg); }
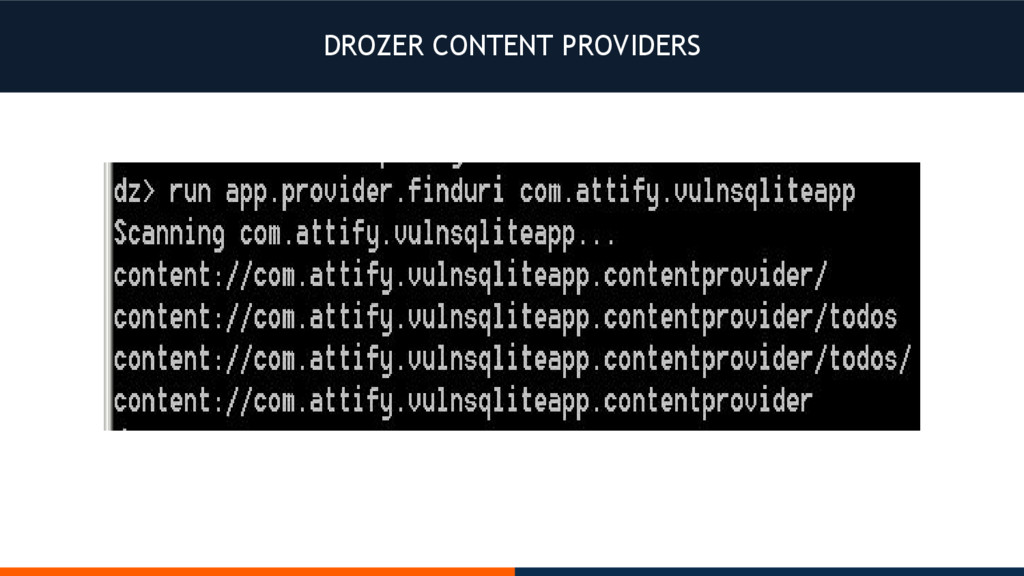
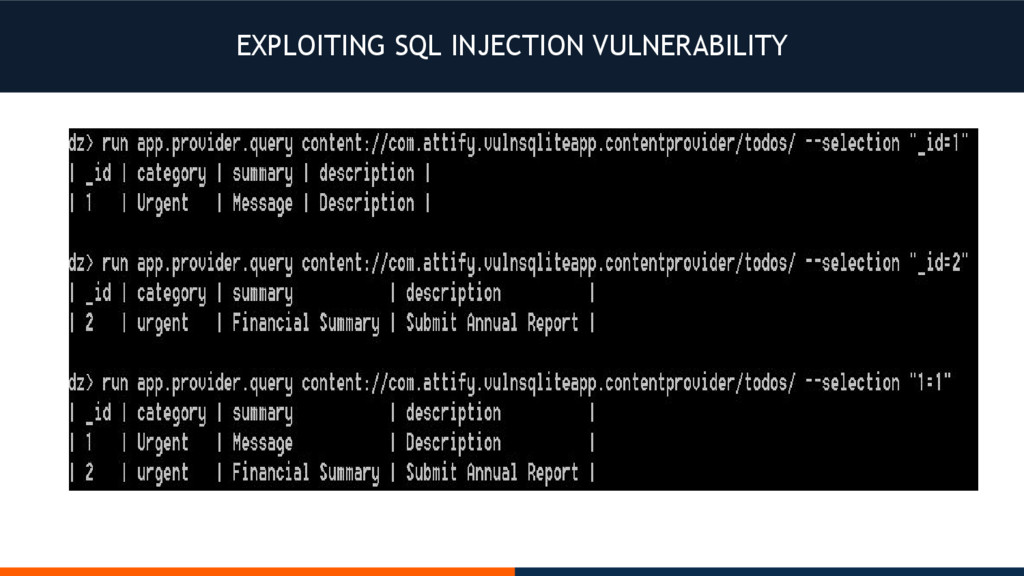
  7. SECURITY IN CONTENT PROVIDERS ▪ Components provide a standardized interface

    for sharing data between applications ▪ URI addressing scheme ▪ Can perform queries equivalent to SELECT, UPDATE,INSERT, DELETE
  8. SQLCIPHER ▪ SQLCipher is a SQL extension that provides transparent

    AES encryption of database files ▪ 256-bit AES Encrypt SQLite database ▪ http://sqlcipher.net/sqlcipher-for-android
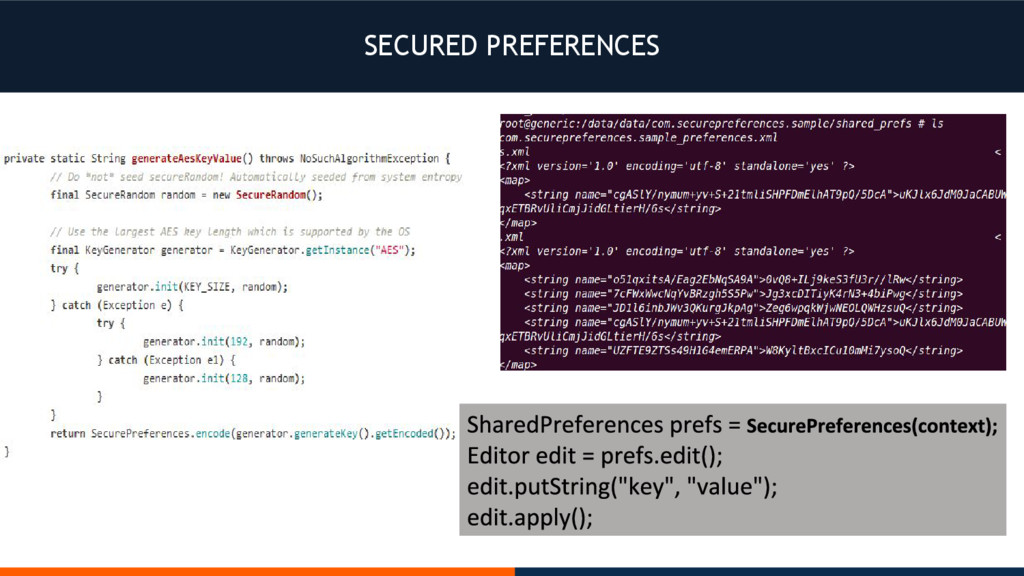
  9. SECURED PREFERENCES ▪ https://github.com/scottyab/secure-preferences ▪ Encrypt your app’s shared preferences

    ▪ Android Share Preferences wrapper that provides encryption for keys and values
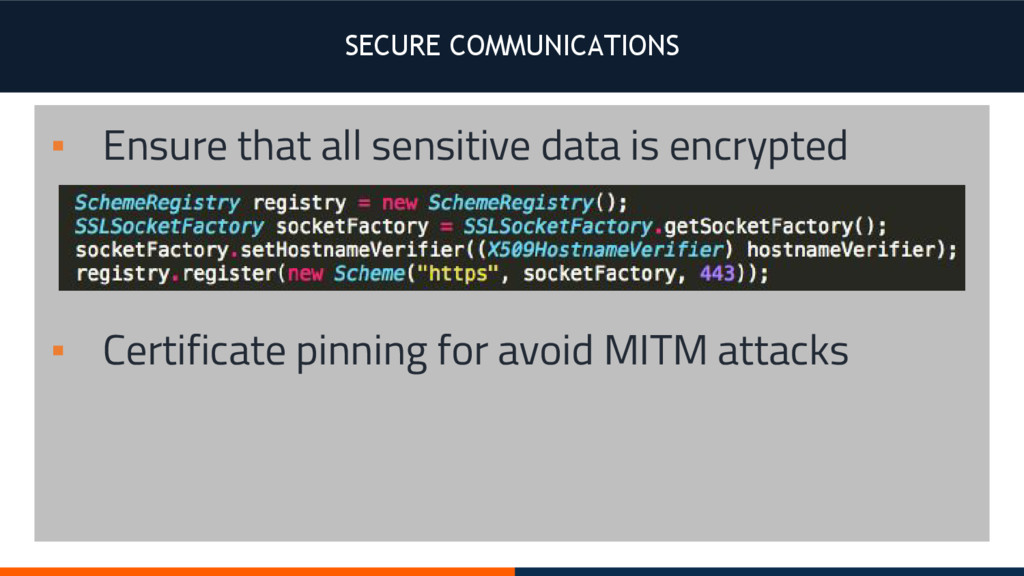
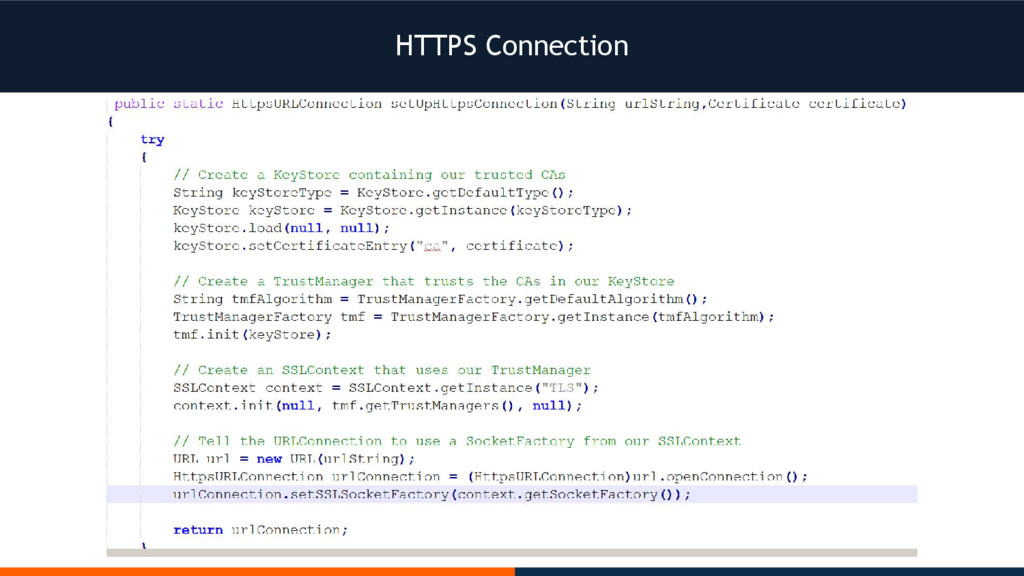
  10. SECURE COMMUNICATIONS ▪ Ensure that all sensitive data is encrypted

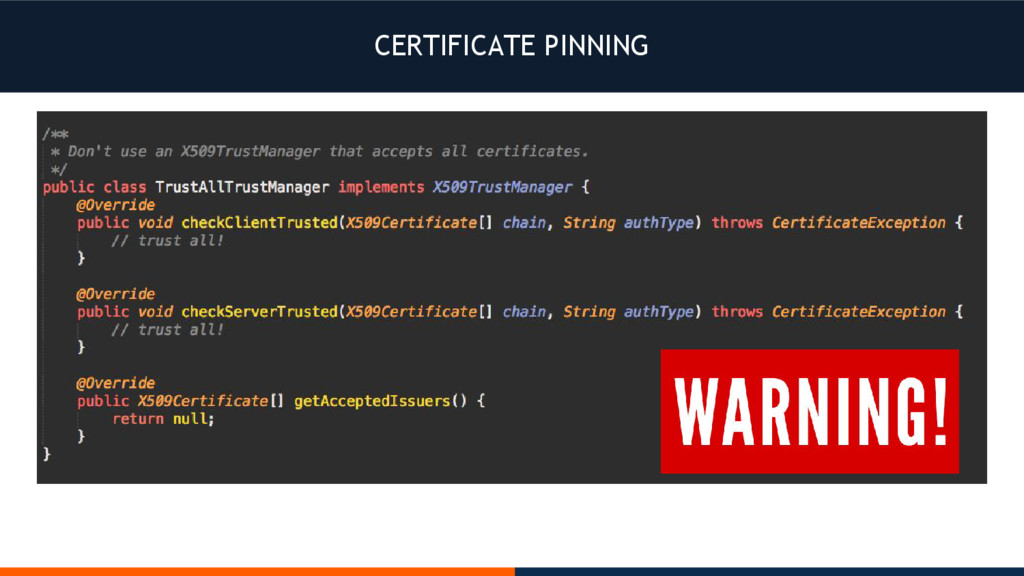
    ▪ Certificate pinning for avoid MITM attacks
  11. ENCRYPT NETWORK REQUESTS ▪ Best practice is to always encrypt

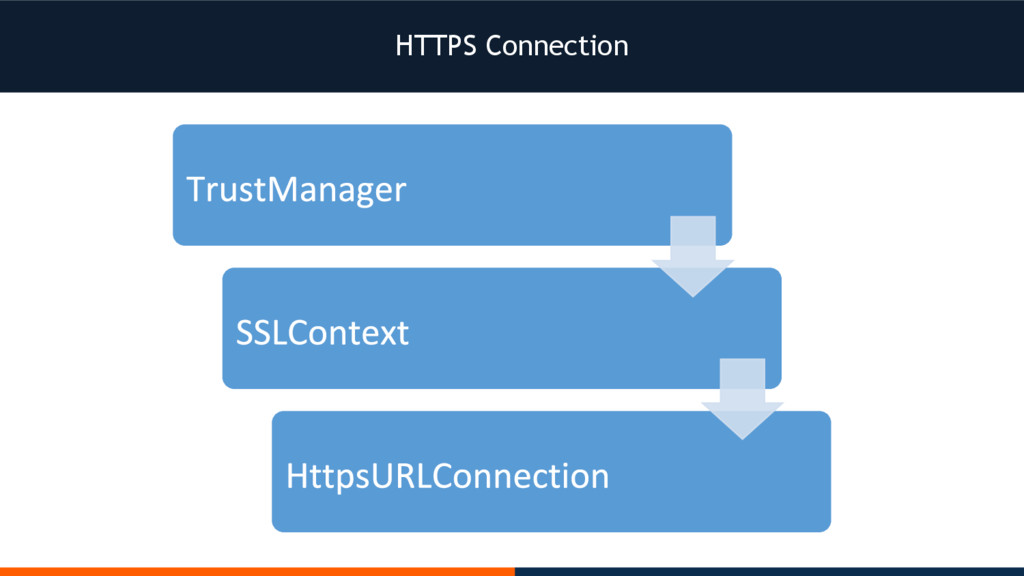
    network communications ▪ HTTPS and SSL can protect against MitM attacks and prevent casual sniffing traffic. ▪ Server certificate validity is checked by default
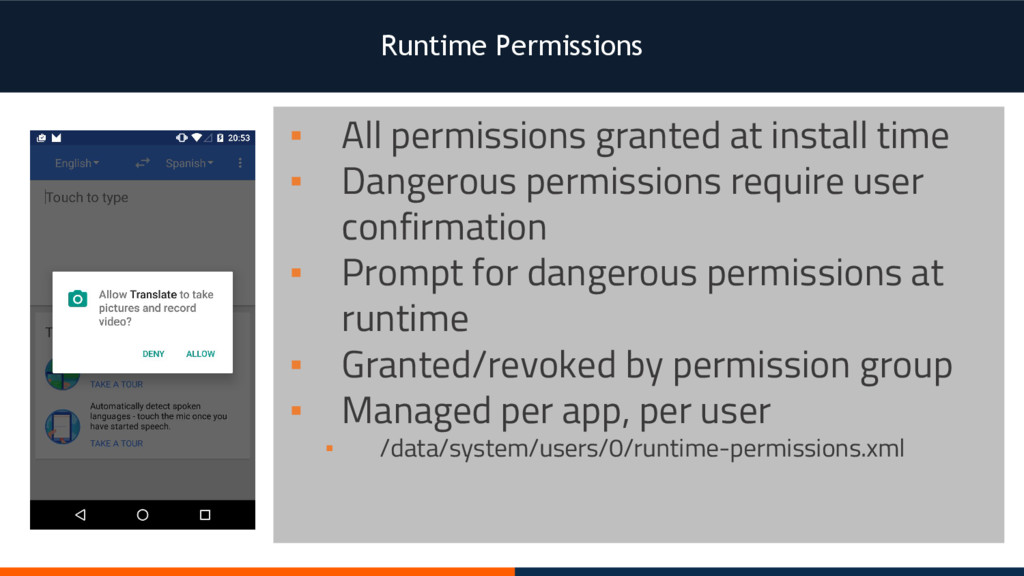
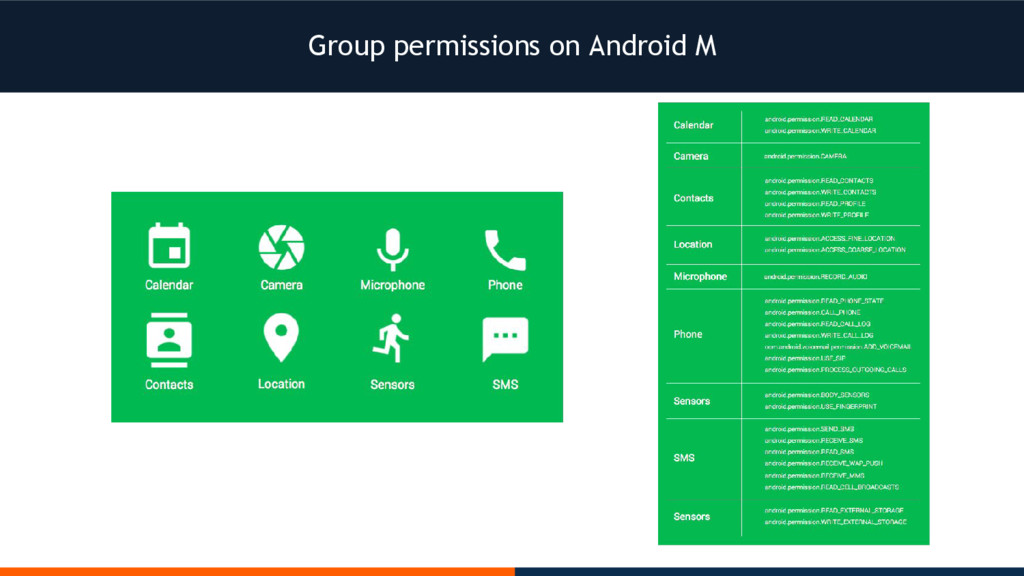
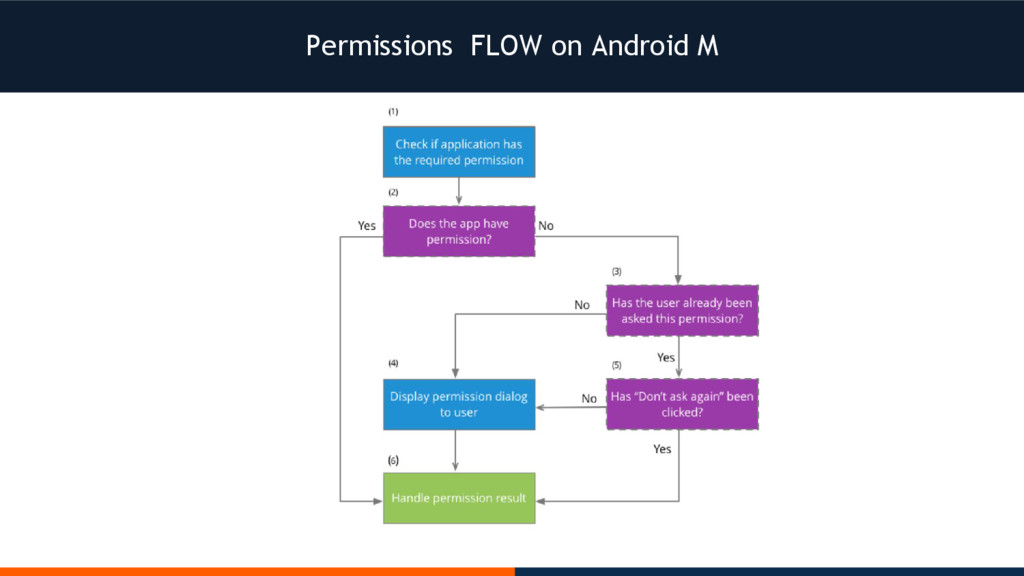
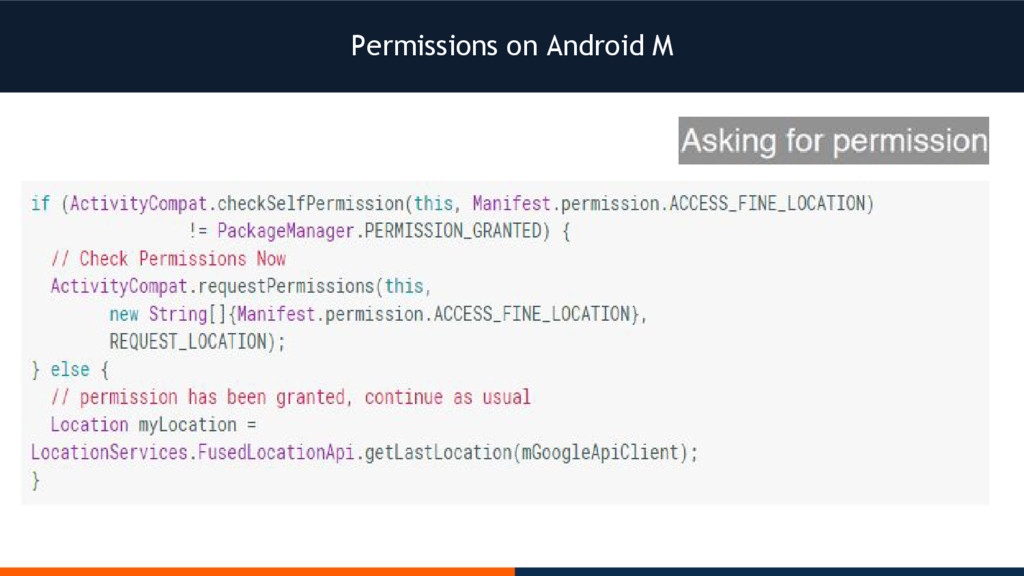
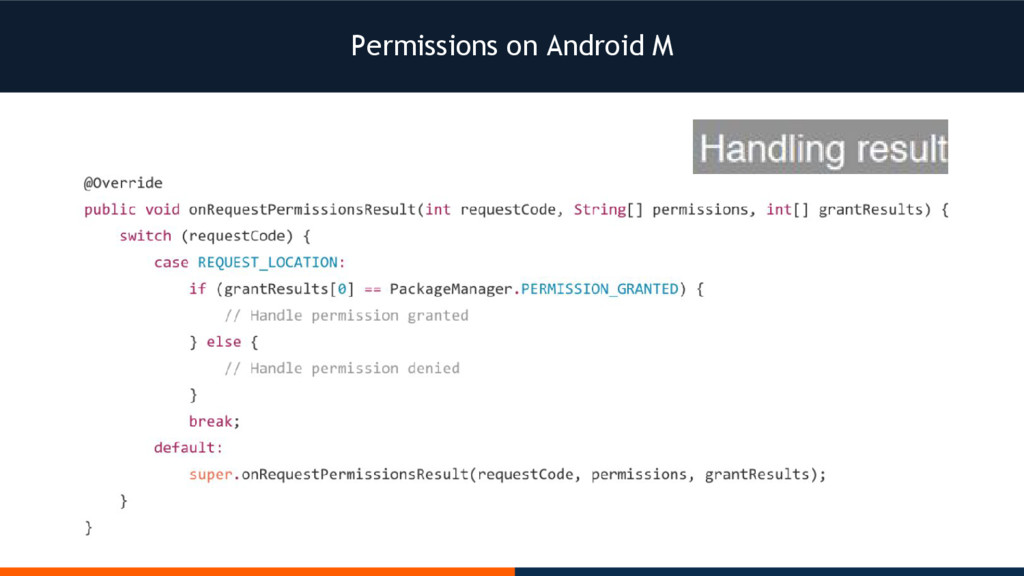
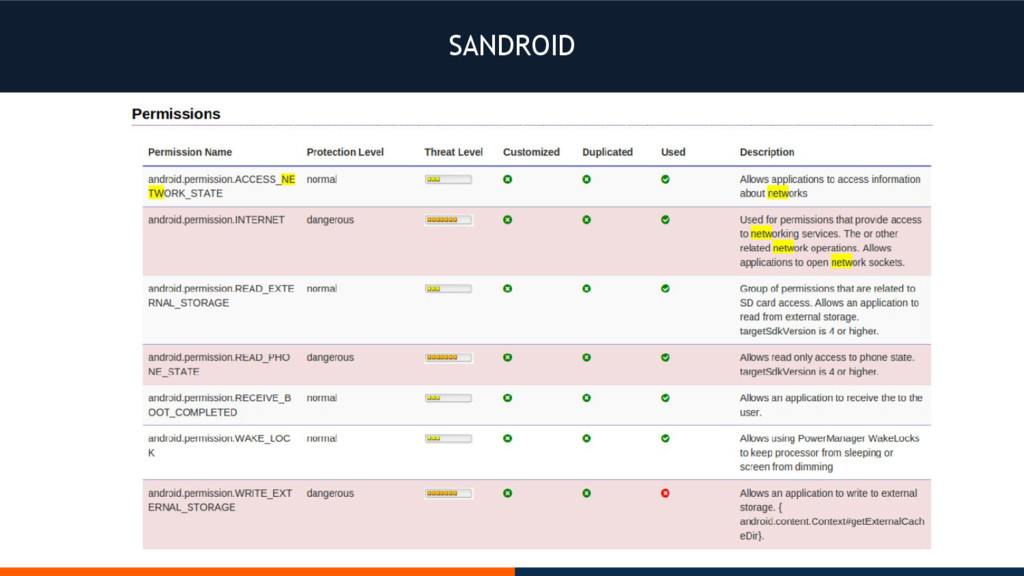
  12. Runtime Permissions ▪ All permissions granted at install time ▪

    Dangerous permissions require user confirmation ▪ Prompt for dangerous permissions at runtime ▪ Granted/revoked by permission group ▪ Managed per app, per user ▪ /data/system/users/0/runtime-permissions.xml
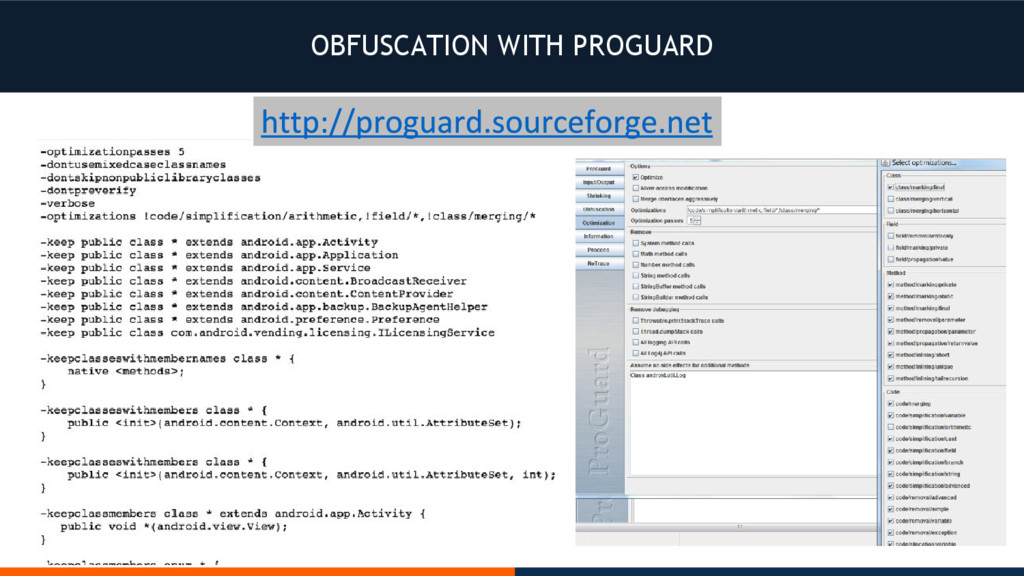
  13. OBFUSCATION ▪ The obfuscator can use several techniques to protect

    a Java/Android application: ▪ change names of classes, methods, fields ▪ modify the control flow ▪ code optimization ▪ dynamic code loading ▪ change instructions with metamorphic technique
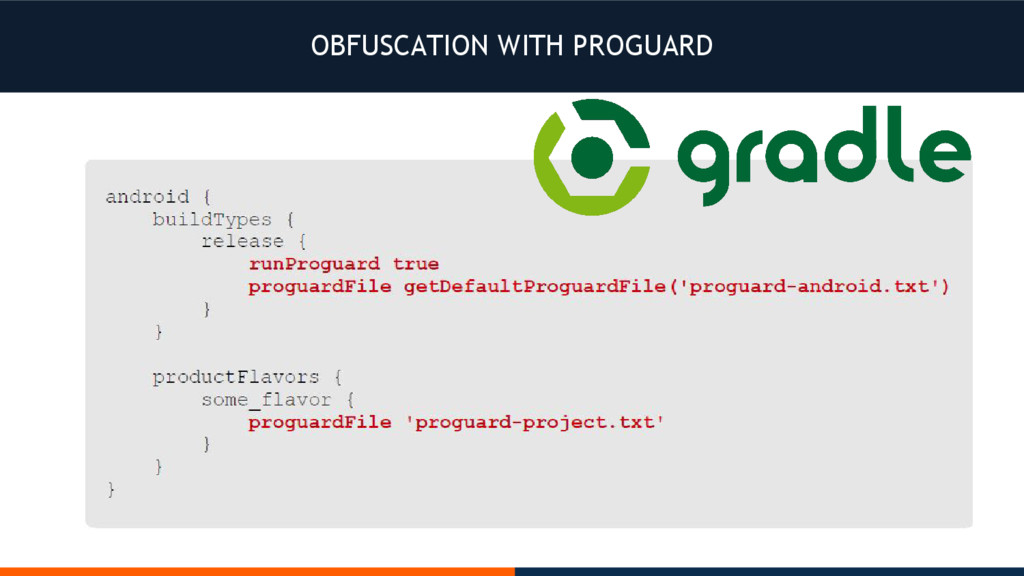
  14. PROGUARD ▪ File shrinker: detects and removes unused classes, fields,

    methods,and attributes ▪ Optimizer: optimizes bytecode and removes unused instructions ▪ Obfuscator: renames classes, fields, and methods using short meaningless names
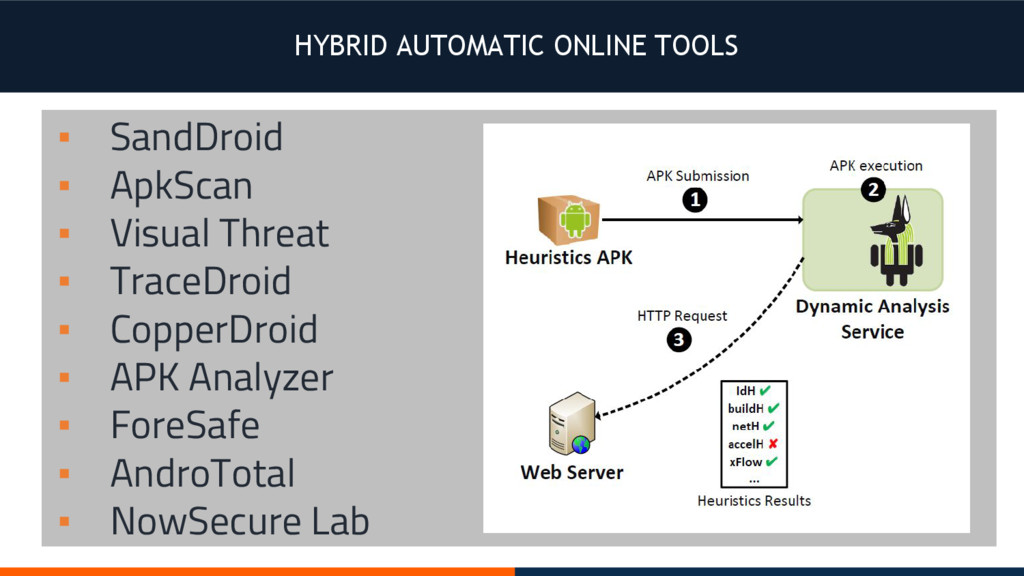
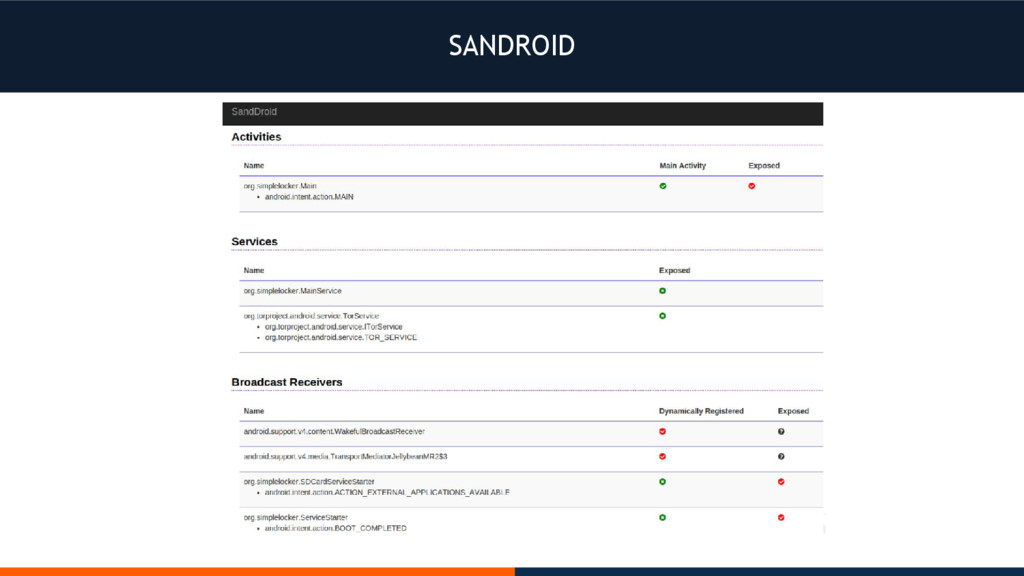
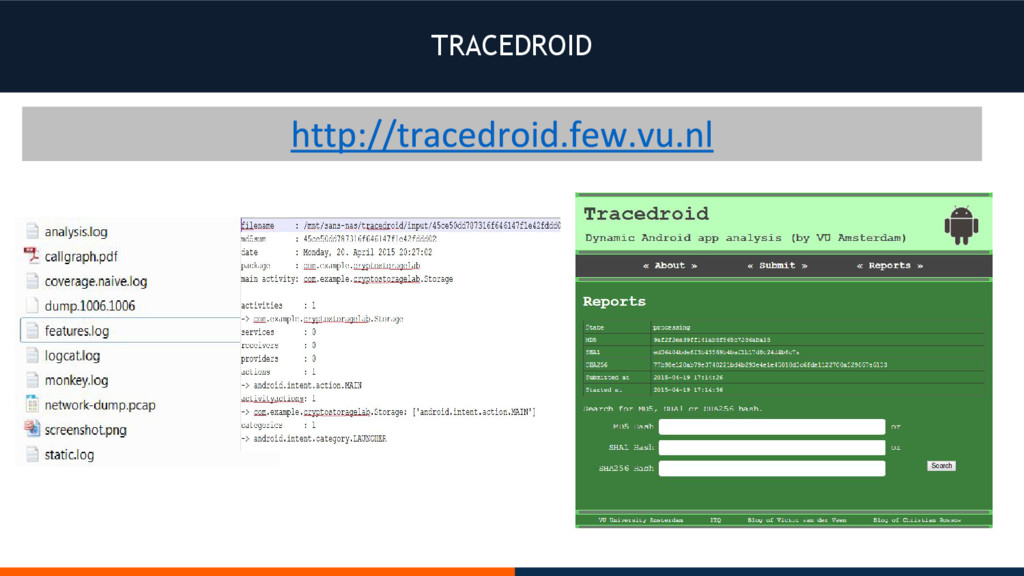
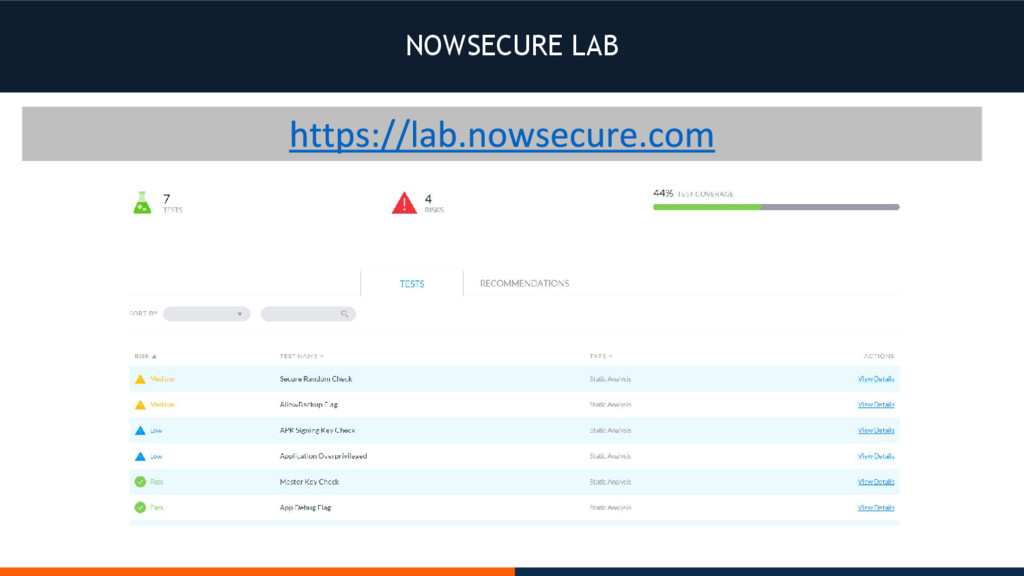
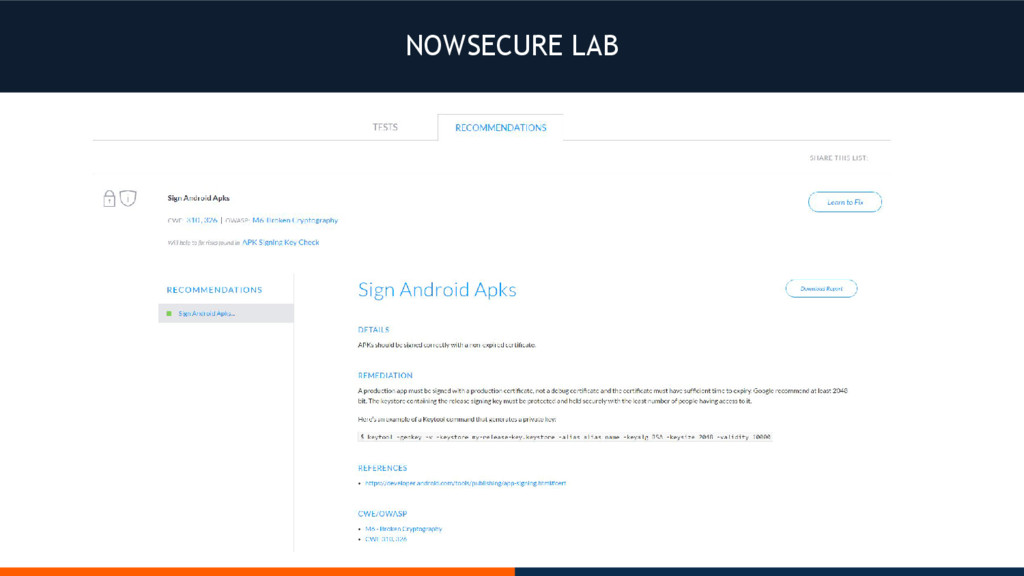
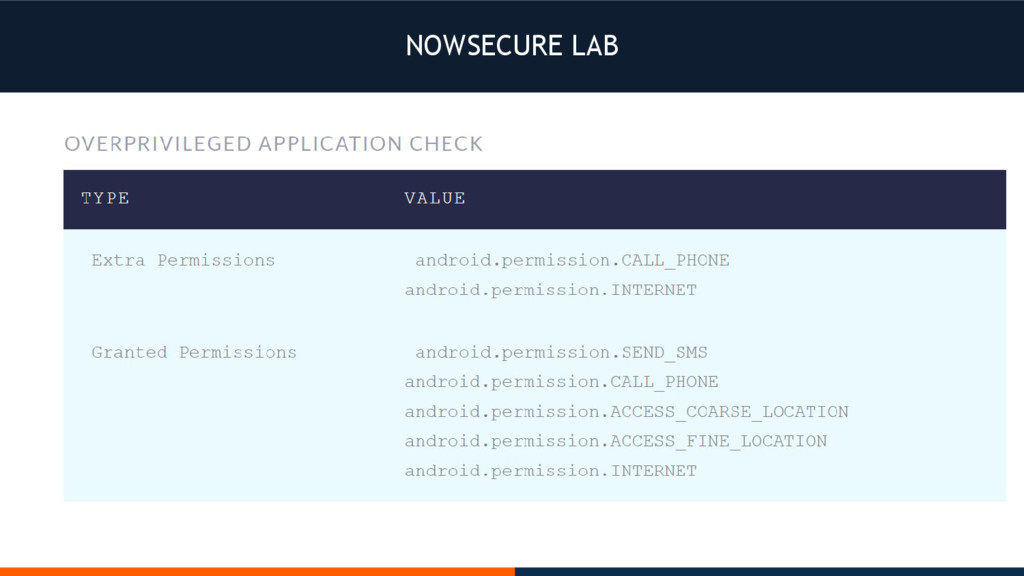
  15. HYBRID AUTOMATIC ONLINE TOOLS ▪ SandDroid ▪ ApkScan ▪ Visual

    Threat ▪ TraceDroid ▪ CopperDroid ▪ APK Analyzer ▪ ForeSafe ▪ AndroTotal ▪ NowSecure Lab
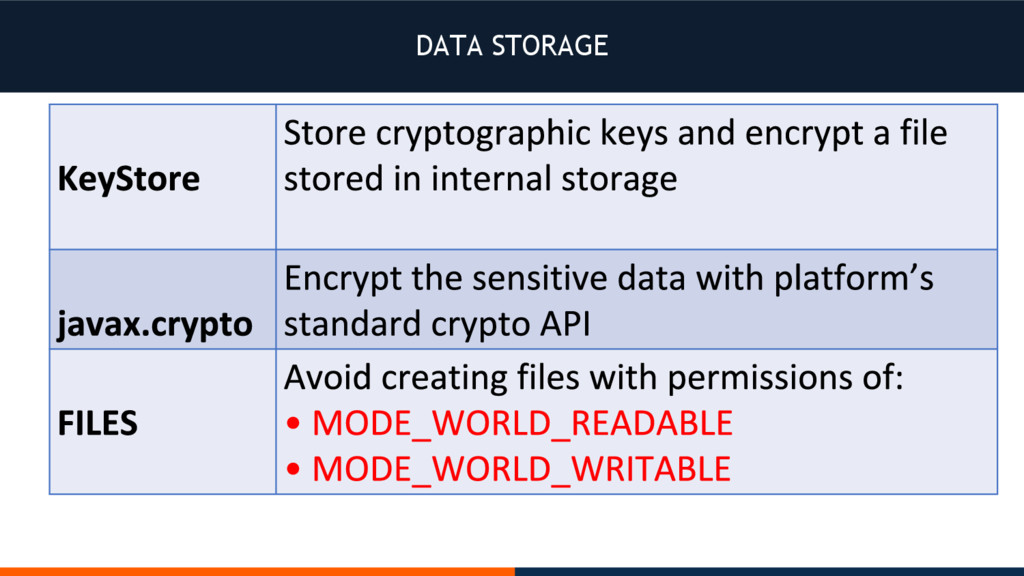
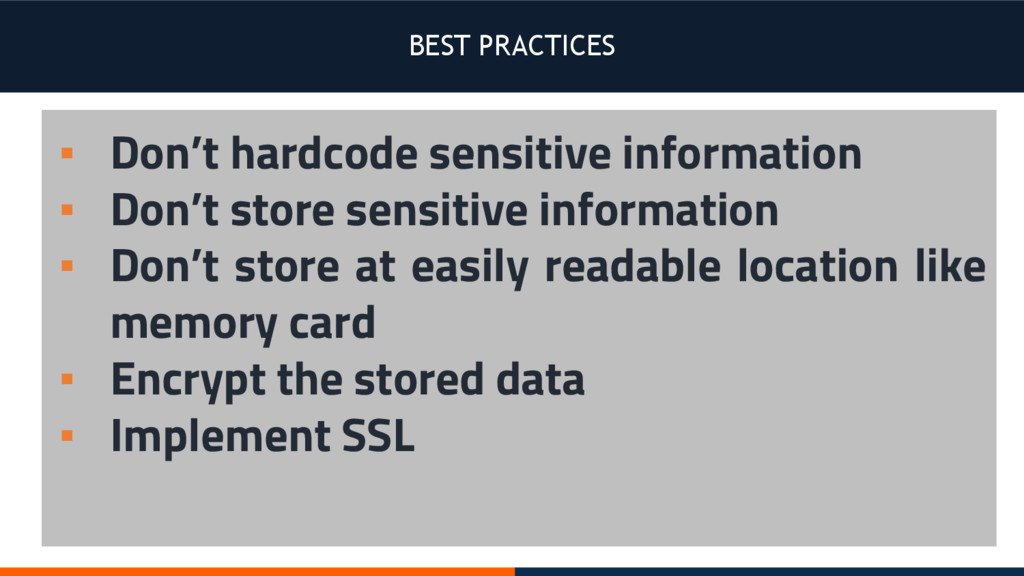
  16. BEST PRACTICES ▪ Don’t hardcode sensitive information ▪ Don’t store

    sensitive information ▪ Don’t store at easily readable location like memory card ▪ Encrypt the stored data ▪ Implement SSL
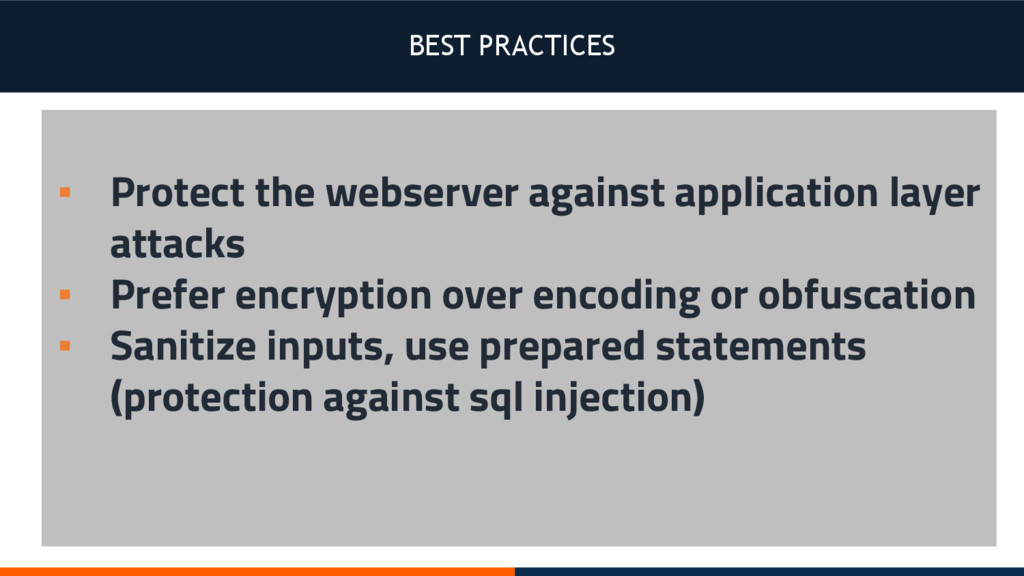
  17. BEST PRACTICES ▪ Protect the webserver against application layer attacks

    ▪ Prefer encryption over encoding or obfuscation ▪ Sanitize inputs, use prepared statements (protection against sql injection)
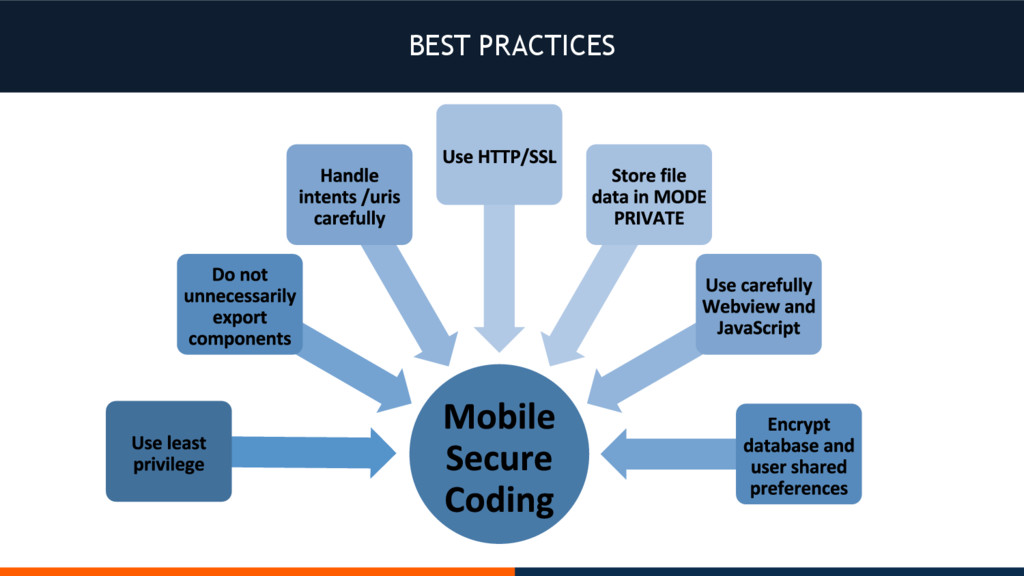
  18. Android Secure Coding Checklist ▪ Use least privilege in request

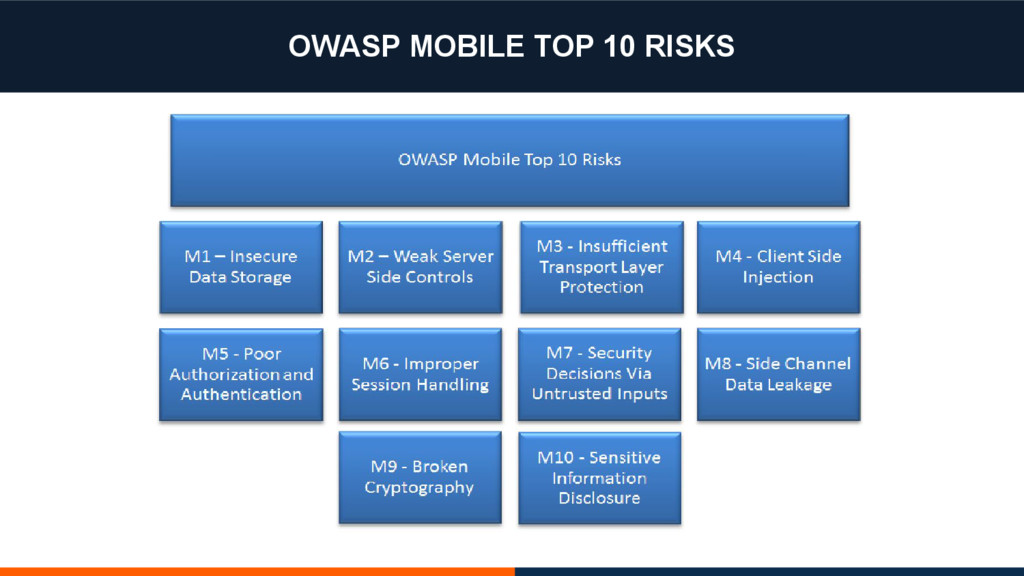
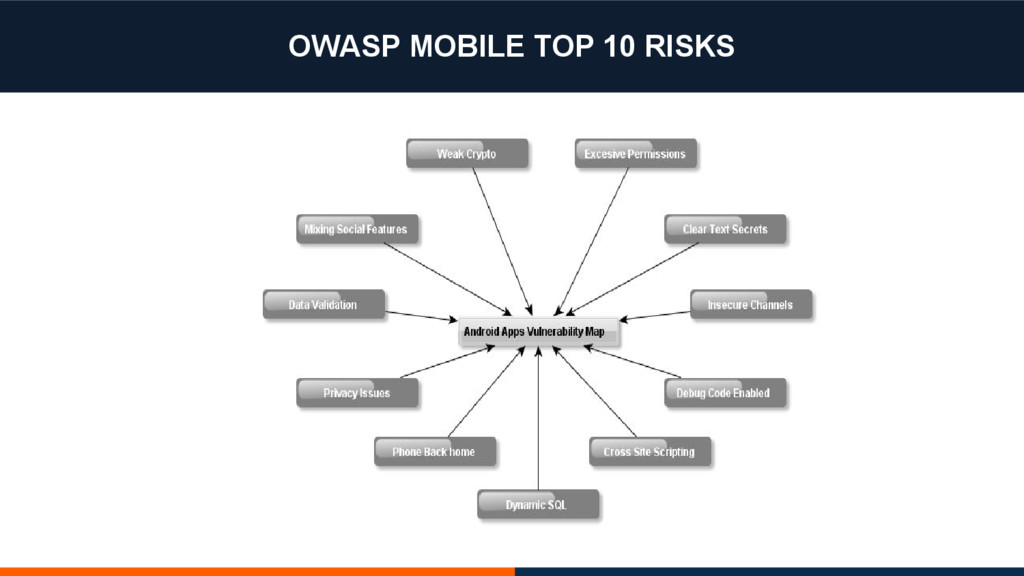
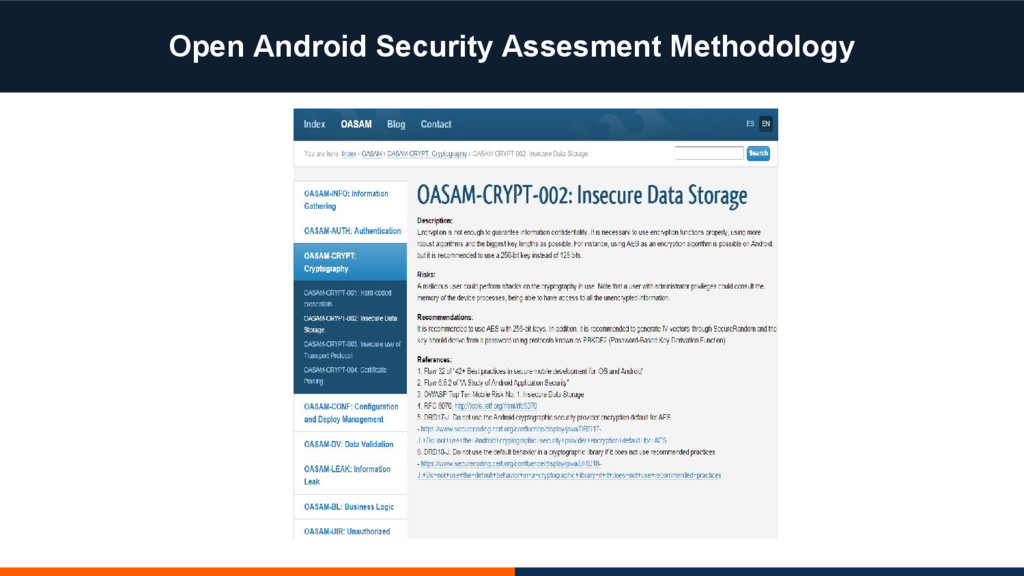
    permissions ▪ Don’t unnecessarily export components ▪ Handle intents carefully ▪ Justify any custom permissions ▪ Mutually authenticate services ▪ Use APIs to construct ContentProvider URIs ▪ Use HTTPS ▪ Follow best practices from OWASP project http://owasp. org/index.php/OWASP_Mobile_Security_Project
  19. REFERENCES ▪ http://proguard.sourceforge.net ▪ http://code.google.com/p/dex2jar ▪ http://code.google.com/p/android-apktool ▪ https://labs.mwrinfosecurity.com/tools/drozer ▪

    http://sqlcipher.net/sqlcipher-for-android ▪ https://www.owasp.org/index. php/OWASP_Mobile_Security_Project ▪ https://developer.android. com/training/articles/security-tips.html

More Decks by jmortegac

Other Decks in Technology