Upgrade to Pro
— share decks privately, control downloads, hide ads and more …
Speaker Deck
Sign up for free
Menu
Search
Features
All features
Private URLs
Password Protection
Custom URLS
Scheduled publishing
Remove Branding
Restrict embedding
Deck Collections
Notes
Features
All features
Private URLs
Password Protection
Custom URLS
Scheduled publishing
Remove Branding
Restrict embedding
Deck Collections
Notes
Explore
Featured decks
Featured speakers
Programming
Technology
Storyboards
Explore
Featured decks
Featured speakers
Programming
Technology
Storyboards
Pricing
Search
Sign in
Sign up for free
Testing NodeJS Security
Search
jmortegac
November 18, 2016
Programming
430
1
Share
Embed
Copy iframe code
Copy JS code
Copy link
Start on current slide
Testing NodeJS Security
Testing NodeJS Security
jmortegac
November 18, 2016
More Decks by jmortegac
See All by jmortegac
Security in Model Context Protocol: An Analysis of the OWASP MCP Top 10
jmortega
0
53
Simulando ataques adversarios con TextAttack: Vulnerabilidades y defensas en PLN
jmortega
0
47
Seguridad en la nube: defensa para activos digitales
jmortega
0
42
Simulando ataques adversarios con TextAttack: Vulnerabilidades y defensas en PLN
jmortega
1
69
Seguridad y auditorías en Modelos grandes del lenguaje (LLM)
jmortega
1
77
Seguridad y auditorías en Modelos grandes del lenguaje (LLM)
jmortega
1
160
Security and auditing tools in Large Language Models (LLM)
jmortega
1
110
Beyond the hype: The reality of AI security
jmortega
1
130
Seguridad y auditorías en Modelos grandes del lenguaje (LLM)
jmortega
1
160
Other Decks in Programming
See All in Programming
全ての永続トークンを、生まれる前に消し去りたい!
sylph01
2
1.1k
Event is what happens
moro
2
1.2k
Optunaを作ったときにやりたかったこと、その後 (2026/10/16, Optuna Meetup #3)
iwiwi
2
1.2k
個人開発者よ、Honoを使え(おじさんver)
tanahiro2010
2
270
AIで開発が速くなった先で、開発チームは何を目指すか
shihochan
1
1.7k
機械に任せるテスト、人が見るテスト ⽣成AIで引き直した、運⽤保守フェーズの線引き
dske104
0
200
Atomic Design, Enforced: Scaling Mobile Design Systems (next.app devCon / droidCon Berlin 2026)
steliosf
PRO
0
180
コーディング自動化の次へ。人の介入をゼロにするファクトリーとサポートAIによる実践
timakin
5
4.2k
RAG の “R” を Swift で覗いてみる 〜「意味から探す」検索の仕組み〜
nao_randd
0
170
S3 TablesのIcebergデータに、AIエージェントからアクセスしてみた / 20261016developersio2026joetsu-accessing-iceberg-in-s3tables-via-agent
kasacchiful
PRO
0
190
SalesForceを内製化!? ~ HR事業を支える顧客管理基盤のインフラを大公開 ~
oku053
0
190
作って学ぶSpring BootのAuto Configuration / JJUG Night Seminar 2026-10-19
rshindo
0
200
Featured
See All Featured
How to Align SEO within the Product Triangle To Get Buy-In & Support - #RIMC
aleyda
2
1.8k
The Illustrated Guide to Node.js - THAT Conference 2024
reverentgeek
1
580
What’s in a name? Adding method to the madness
productmarketing
PRO
24
4.2k
Believing is Seeing
oripsolob
1
250
VelocityConf: Rendering Performance Case Studies
addyosmani
331
25k
技術選定の審美眼(2025年版) / Understanding the Spiral of Technologies 2025 edition
twada
PRO
120
120k
Lightning talk: Run Django tests with GitHub Actions
sabderemane
0
300
The #1 spot is gone: here's how to win anyway
tamaranovitovic
4
1.2k
The Limits of Empathy - UXLibs8
cassininazir
2
730
Principles of Awesome APIs and How to Build Them.
keavy
128
18k
The MySQL Ecosystem @ GitHub 2015
samlambert
251
13k
For a Future-Friendly Web
brad_frost
184
10k
Transcript
Testing Node Security by @jmortegac NOV 18-19 · 2016
Agenda Introduction nodejS security Npm security packages
Node Goat project Tools
nodeJS introduction JavaScript in the backend Built on
Chrome´s Javascript runtime(V8) NodeJs is based on event loop Designed to be asynchronous Single Thread Concurrent requests.
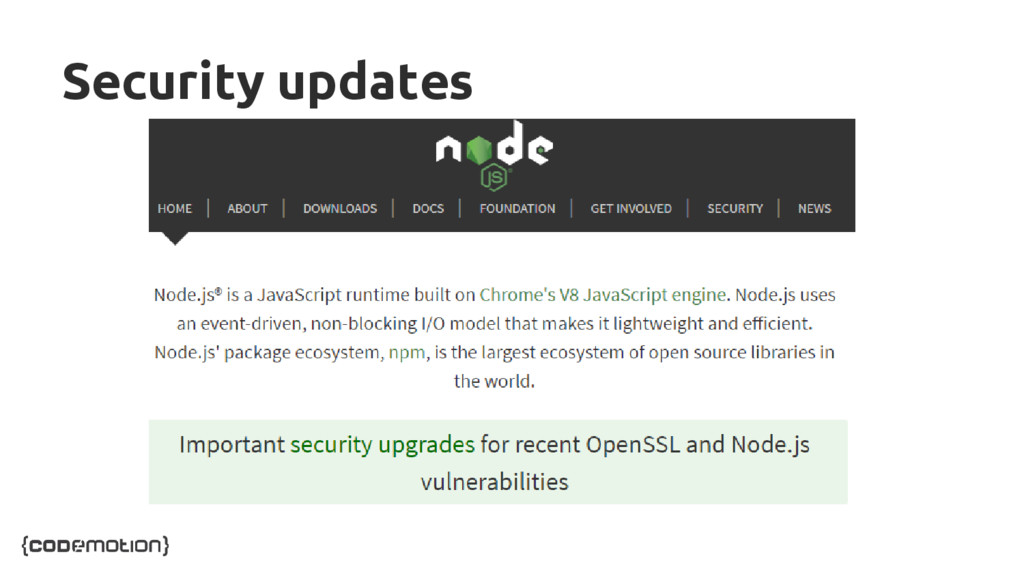
Security updates
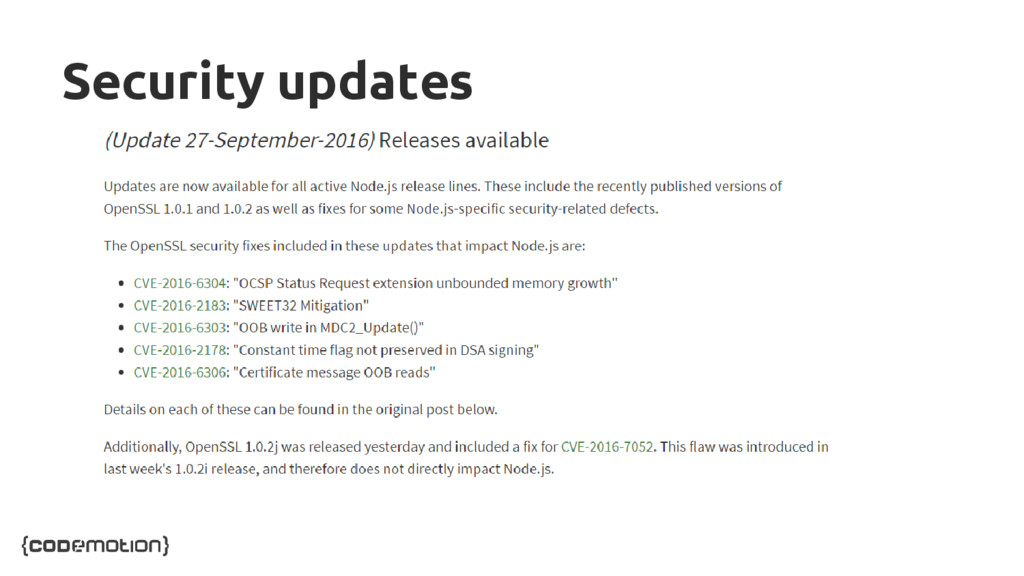
Security updates
Find nodeJS vulnerabilities http://cve.mitre.org/find/
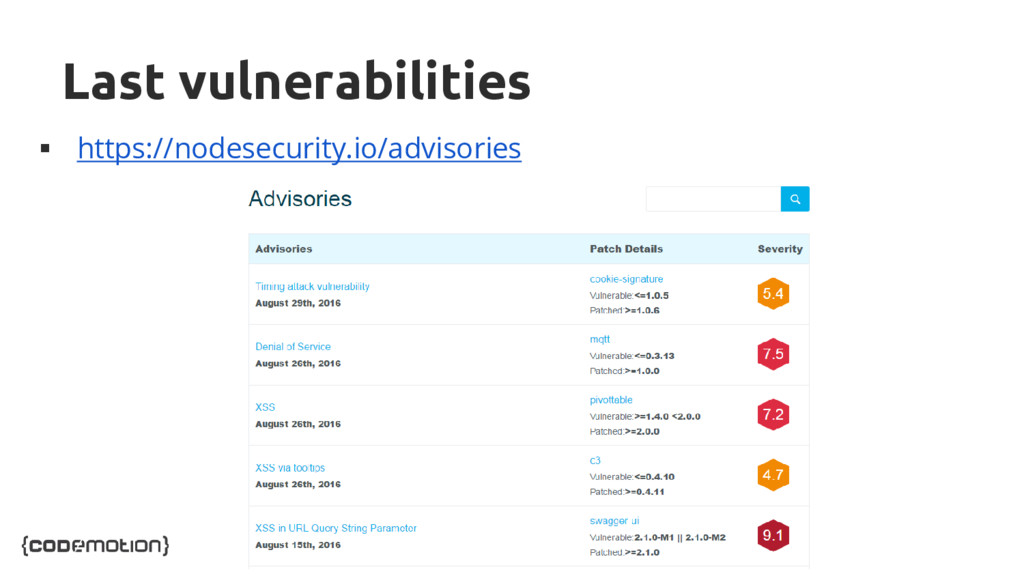
Last vulnerabilities https://nodesecurity.io/advisories
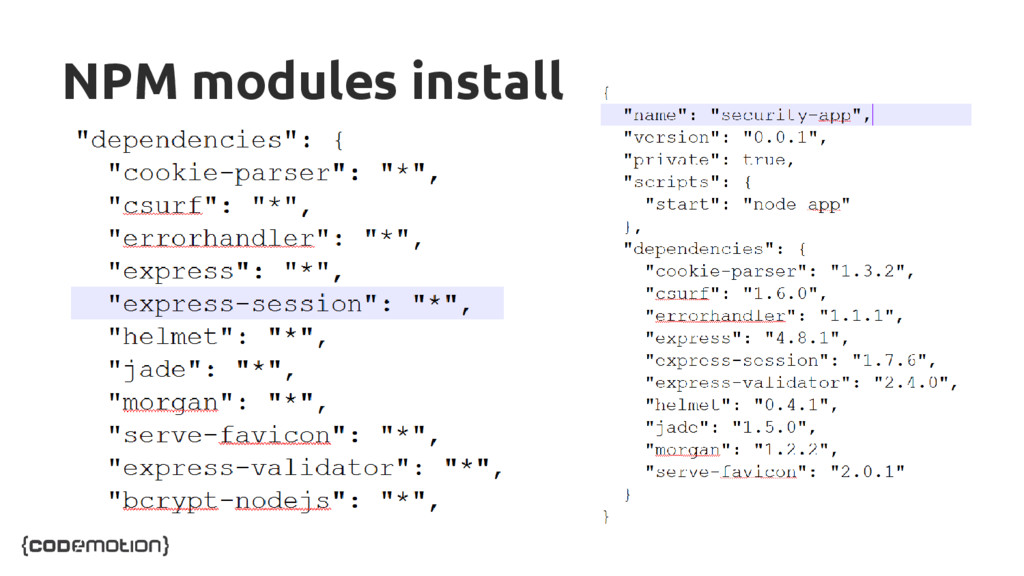
NPM modules install
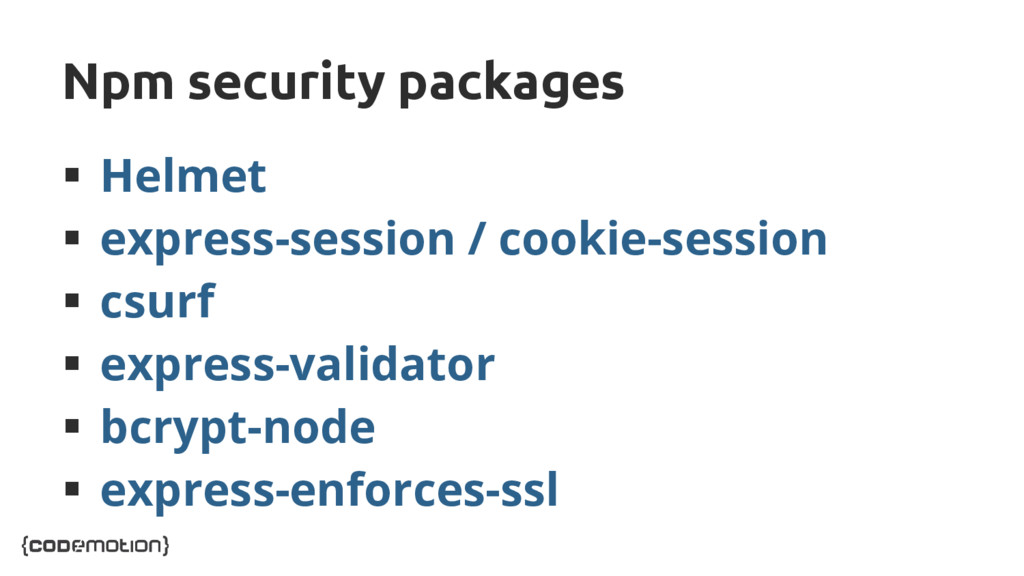
Npm security packages Helmet express-session / cookie-session
csurf express-validator bcrypt-node express-enforces-ssl
Security HTTP Headers Strict-Transport-Security X-Frame-Options X-XSS-Protection
X-Content-Type-Options Content-Security-Policy
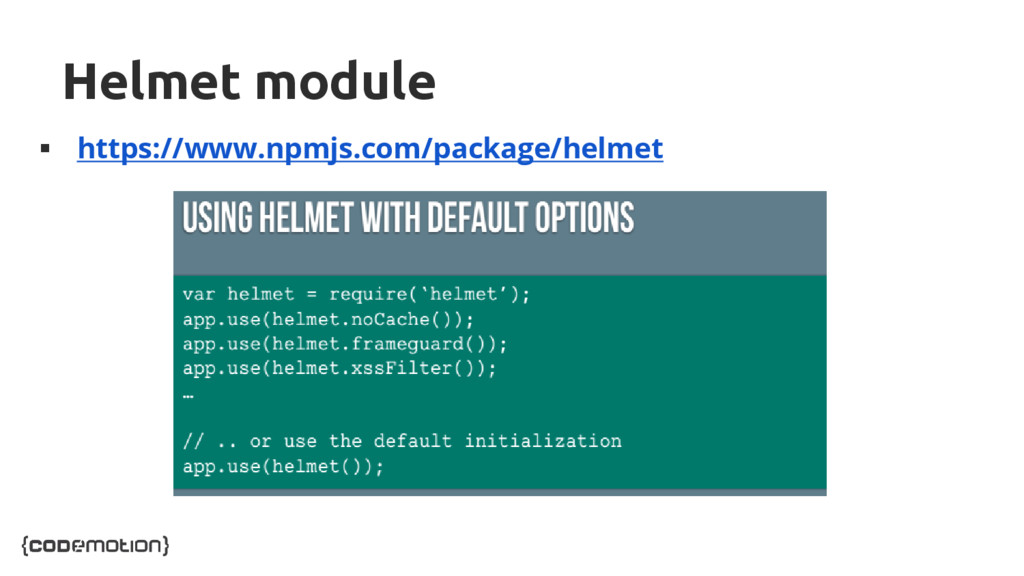
Helmet module https://www.npmjs.com/package/helmet
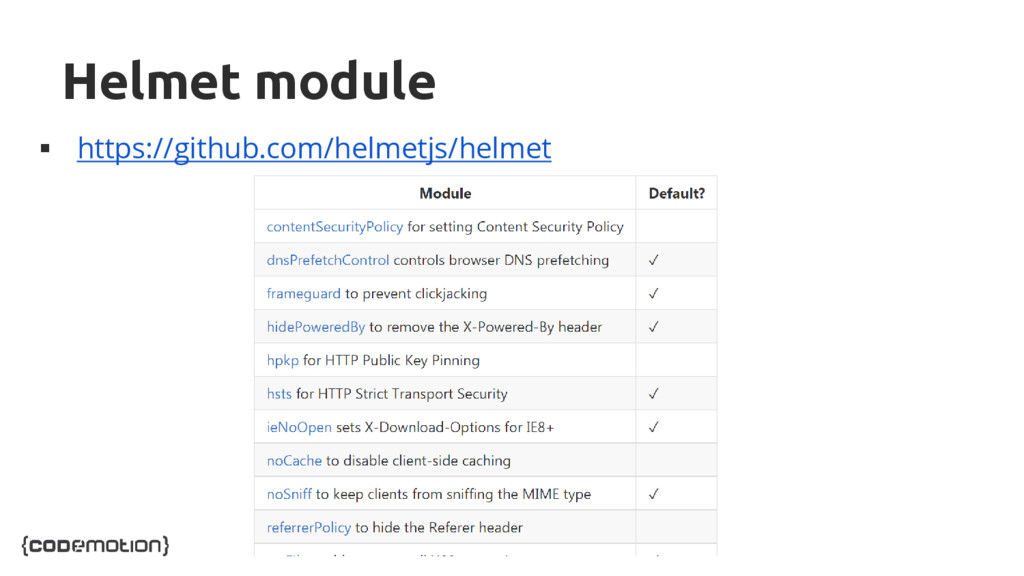
Helmet module https://github.com/helmetjs/helmet
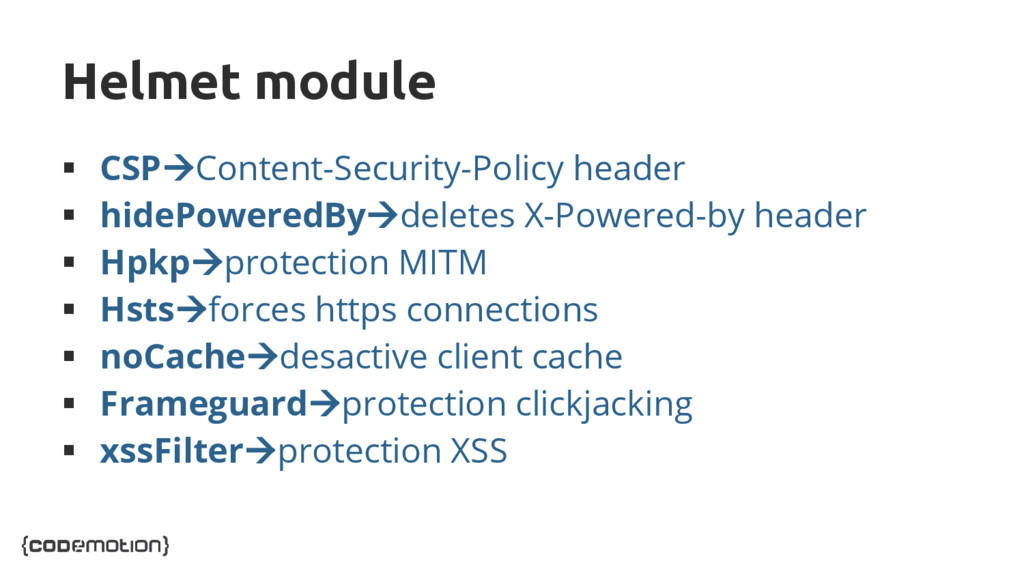
Helmet module CSPContent-Security-Policy header hidePoweredBydeletes X-Powered-by header
Hpkpprotection MITM Hstsforces https connections noCachedesactive client cache Frameguardprotection clickjacking xssFilterprotection XSS
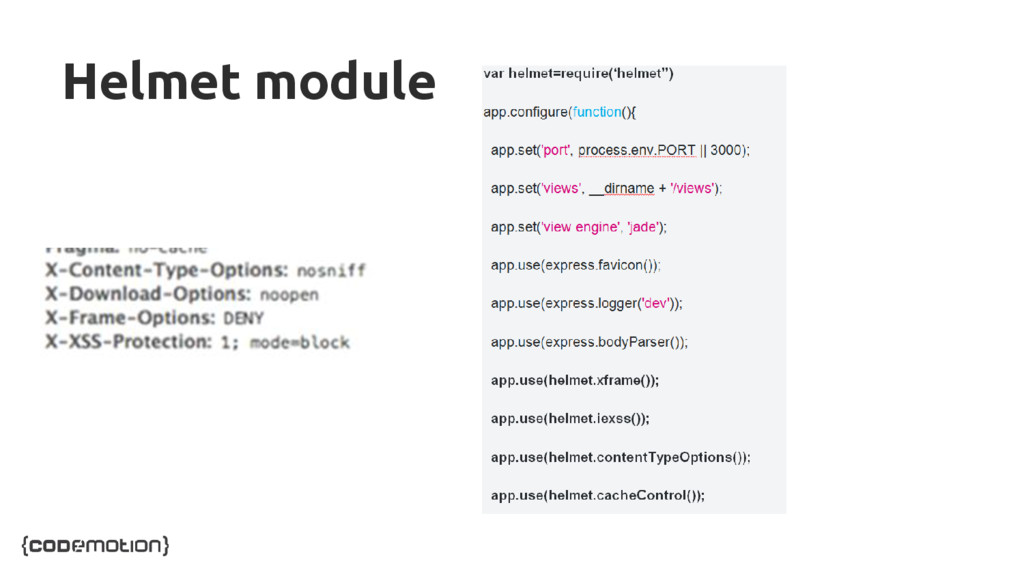
Helmet module
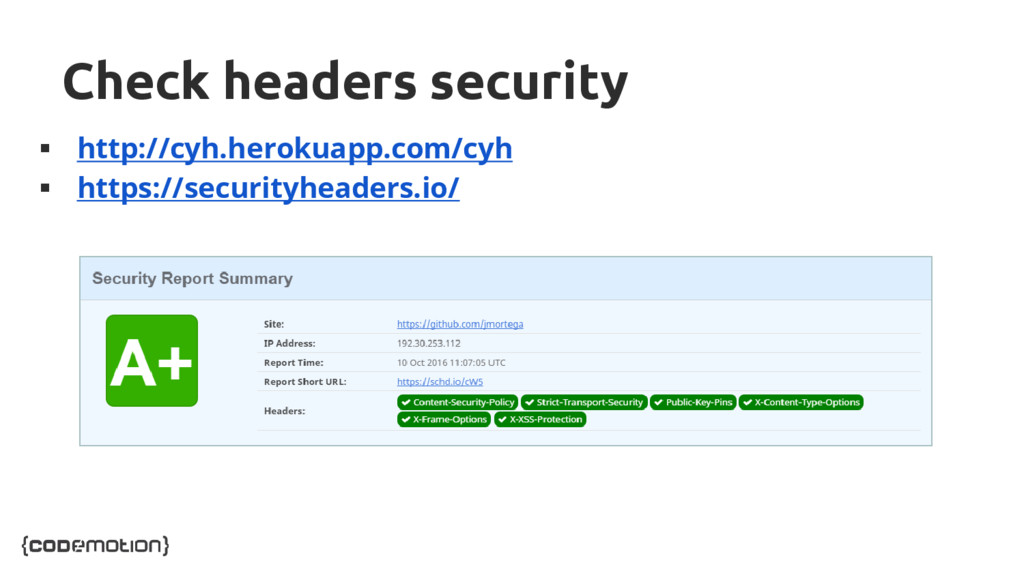
Check headers security http://cyh.herokuapp.com/cyh https://securityheaders.io/
Express versions https://www.shodan.io/search?query=express
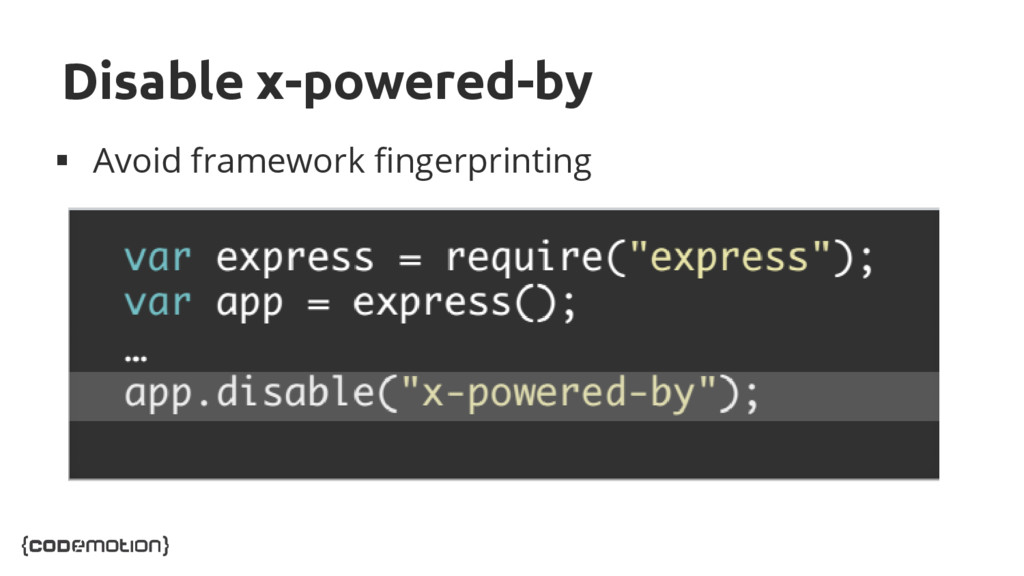
Disable x-powered-by Avoid framework fingerprinting
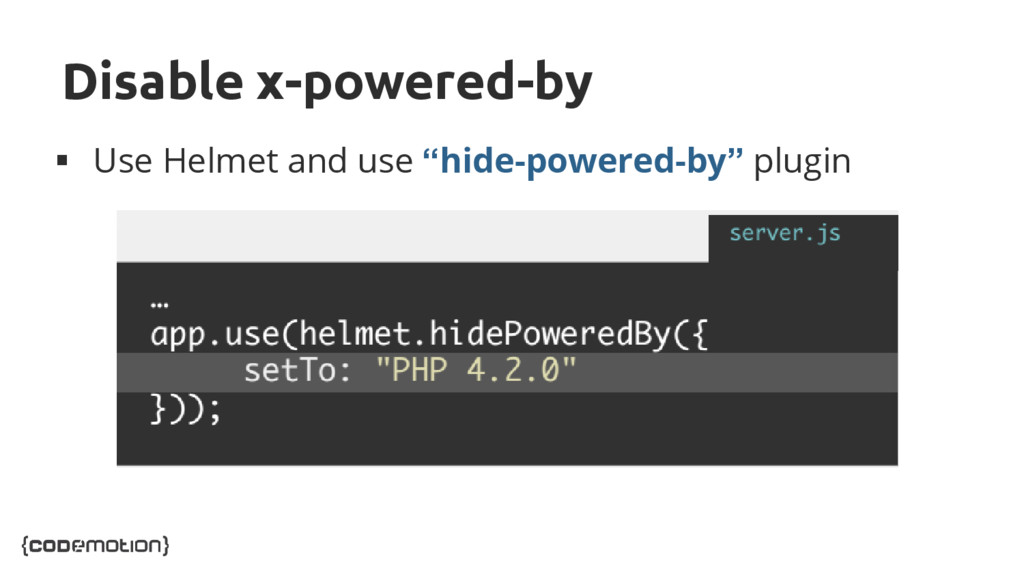
Disable x-powered-by Use Helmet and use “hide-powered-by” plugin
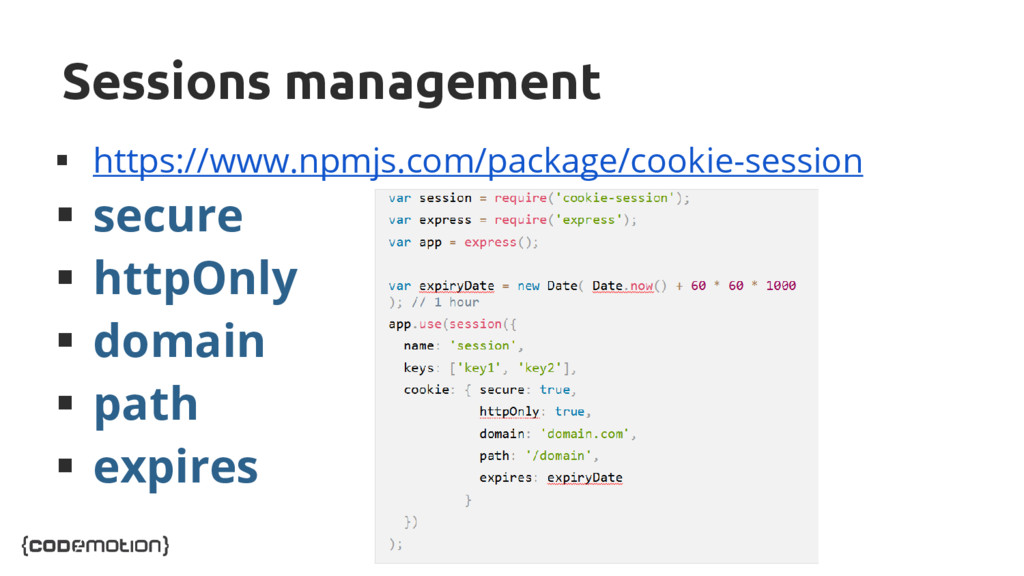
Sessions management https://www.npmjs.com/package/cookie-session secure httpOnly domain
path expires
httpOnly & secure:true
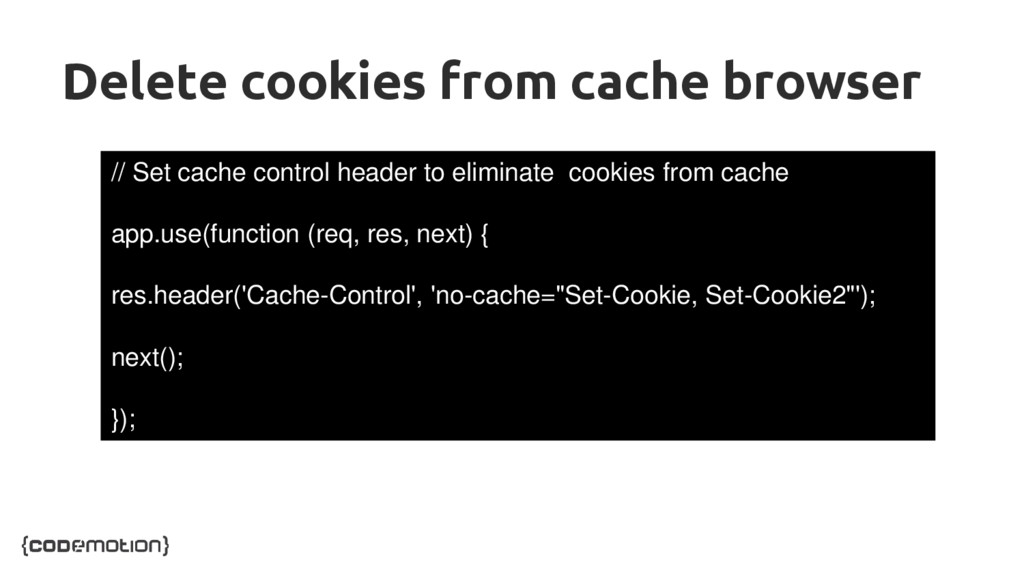
Delete cookies from cache browser // Set cache control header
to eliminate cookies from cache app.use(function (req, res, next) { res.header('Cache-Control', 'no-cache="Set-Cookie, Set-Cookie2"'); next(); });
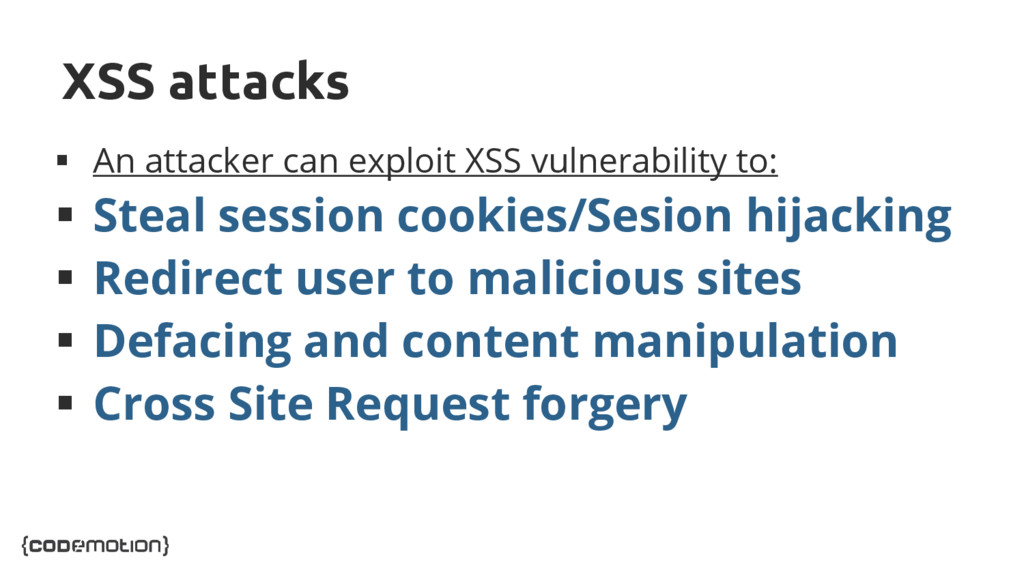
XSS attacks An attacker can exploit XSS vulnerability to:
Steal session cookies/Sesion hijacking Redirect user to malicious sites Defacing and content manipulation Cross Site Request forgery
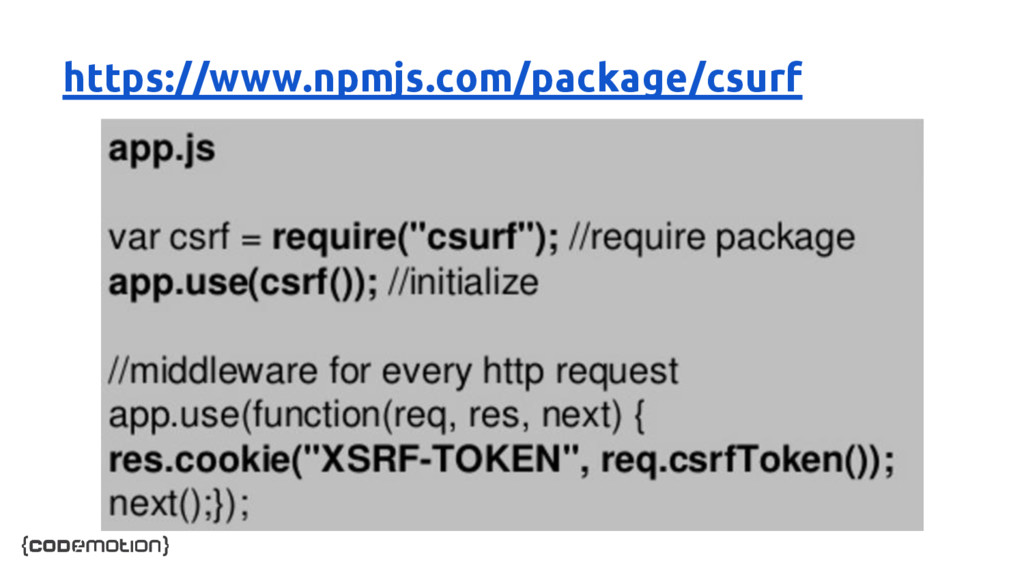
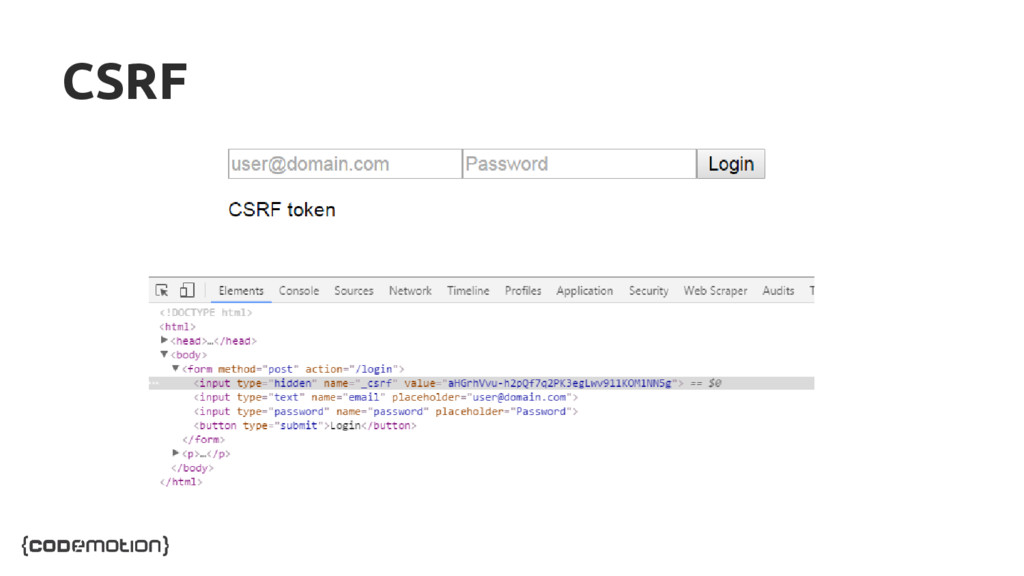
https://www.npmjs.com/package/csurf
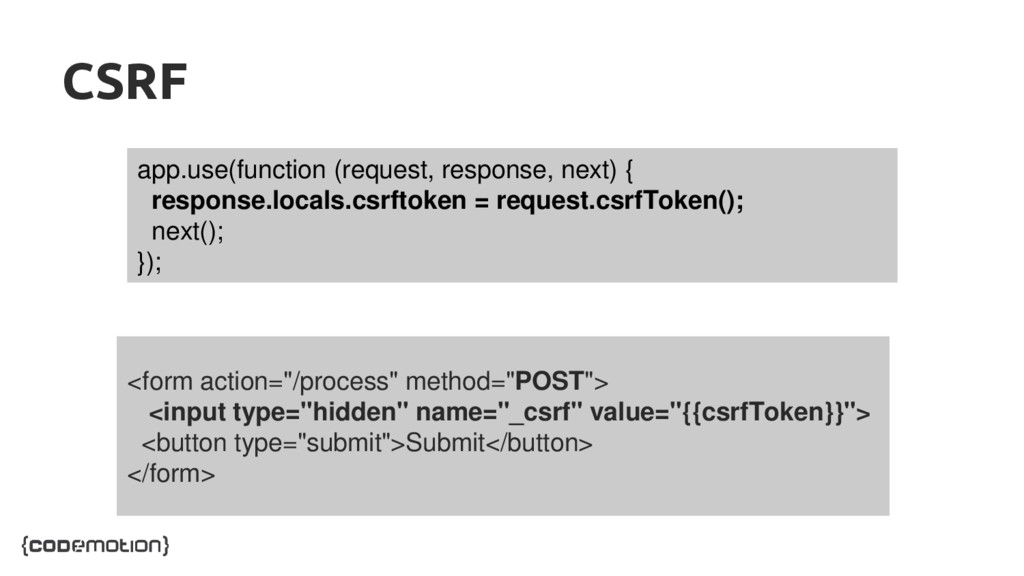
CSRF <form action="/process" method="POST"> <input type="hidden" name="_csrf" value="{{csrfToken}}"> <button type="submit">Submit</button>
</form> app.use(function (request, response, next) { response.locals.csrftoken = request.csrfToken(); next(); });
CSRF
Filter/sanitize user input Avoid XSS attacks https://www.npmjs.com/package/sanitizer
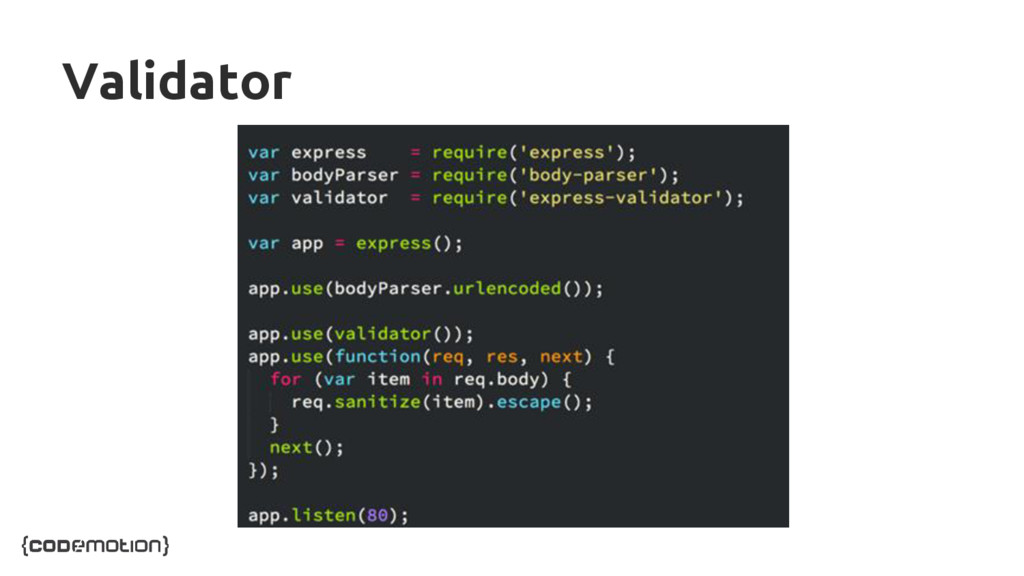
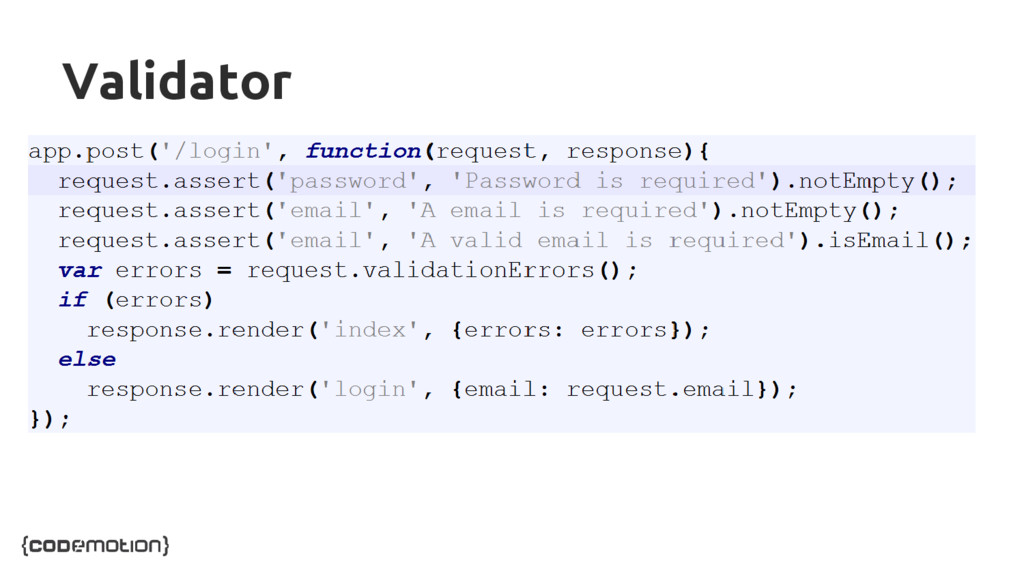
Module express-validator https://www.npmjs.com/package/express-validator
Validator
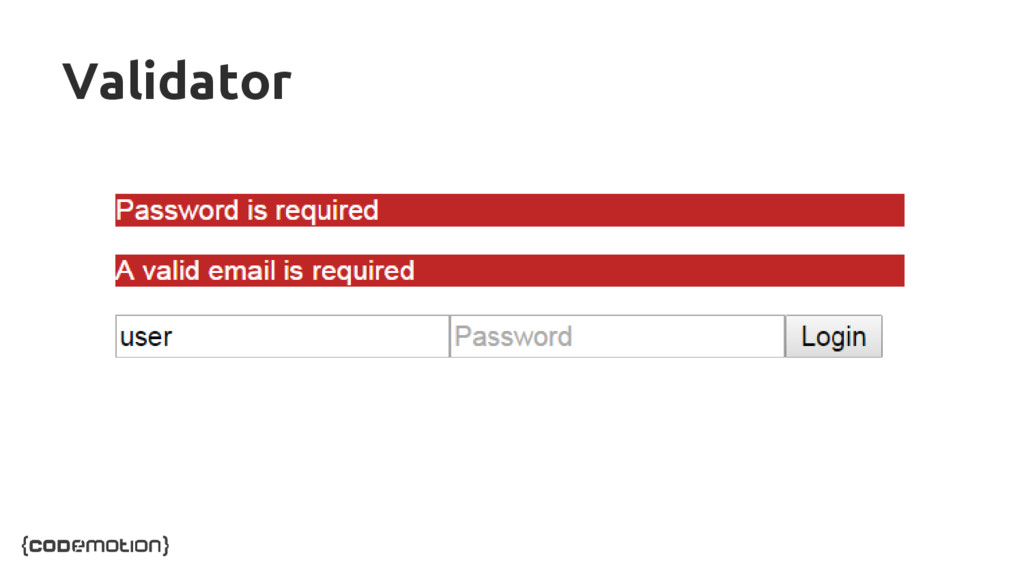
Validator
Validator
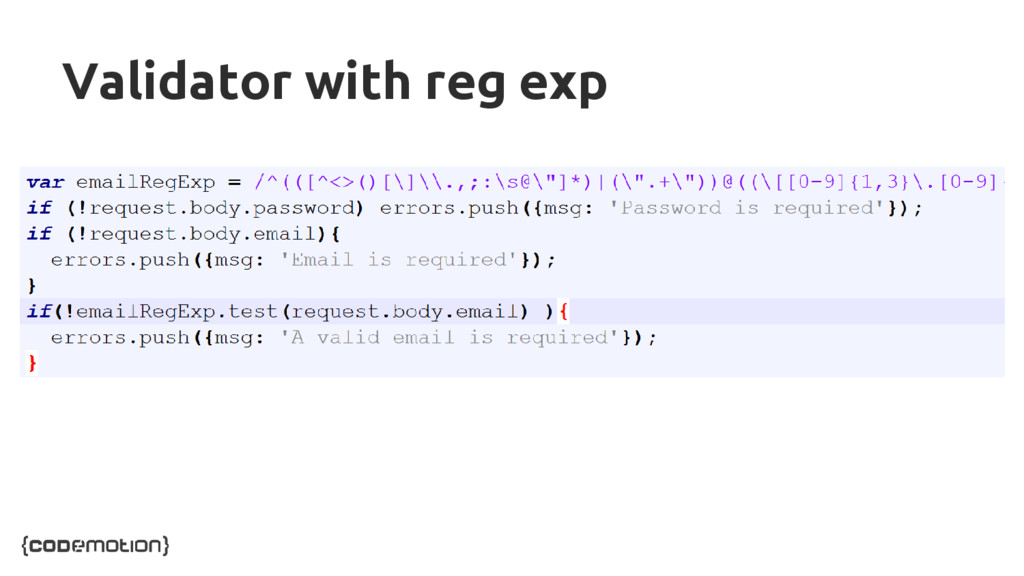
Validator with reg exp
Regular expressions https://www.npmjs.com/package/safe-regex Detect vulnerable regular expressions that
can cause DoS
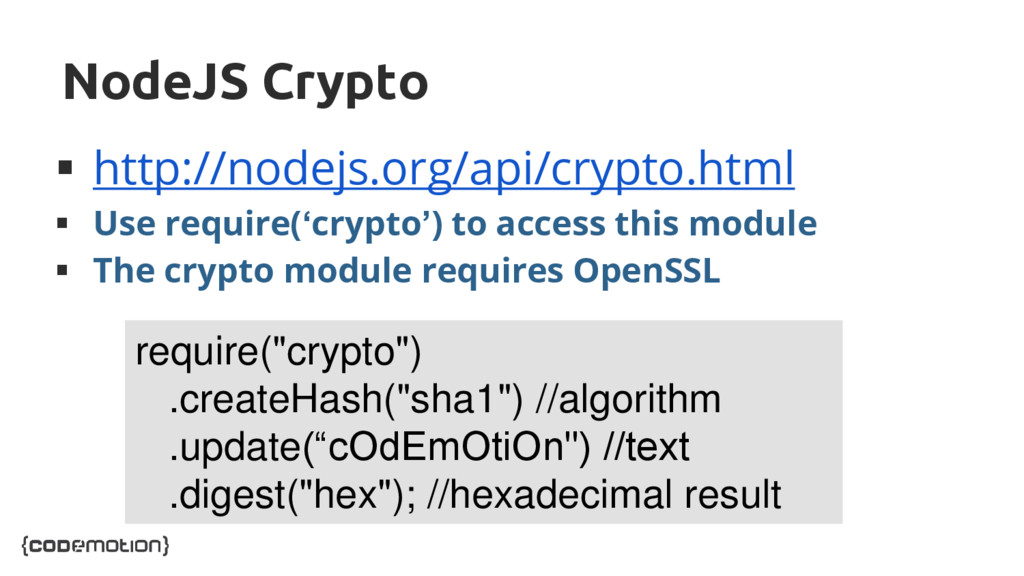
NodeJS Crypto http://nodejs.org/api/crypto.html Use require(‘crypto’) to access this
module The crypto module requires OpenSSL require("crypto") .createHash("sha1") //algorithm .update(“cOdEmOtiOn") //text .digest("hex"); //hexadecimal result
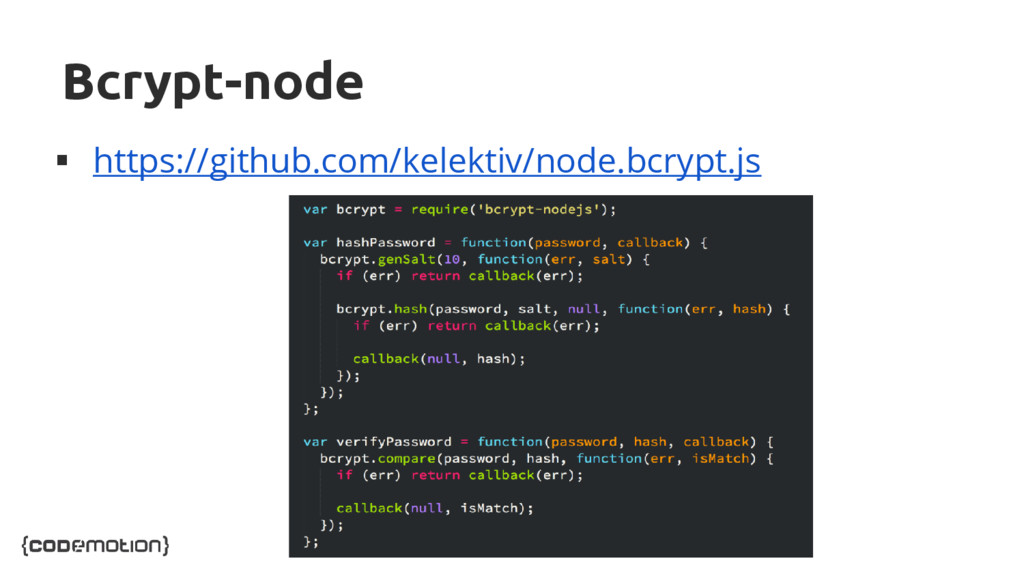
Bcrypt-node https://github.com/kelektiv/node.bcrypt.js
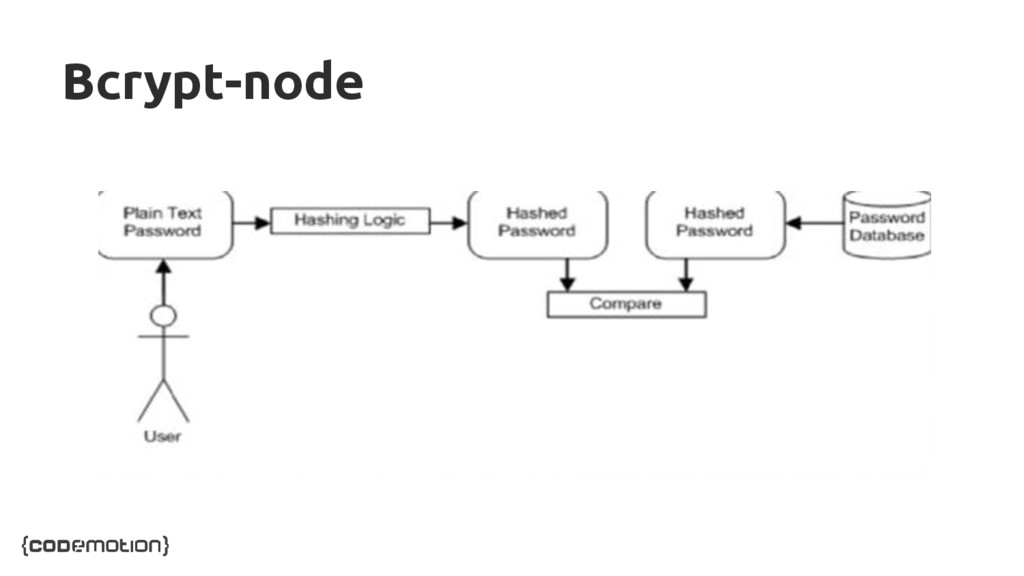
Bcrypt-node
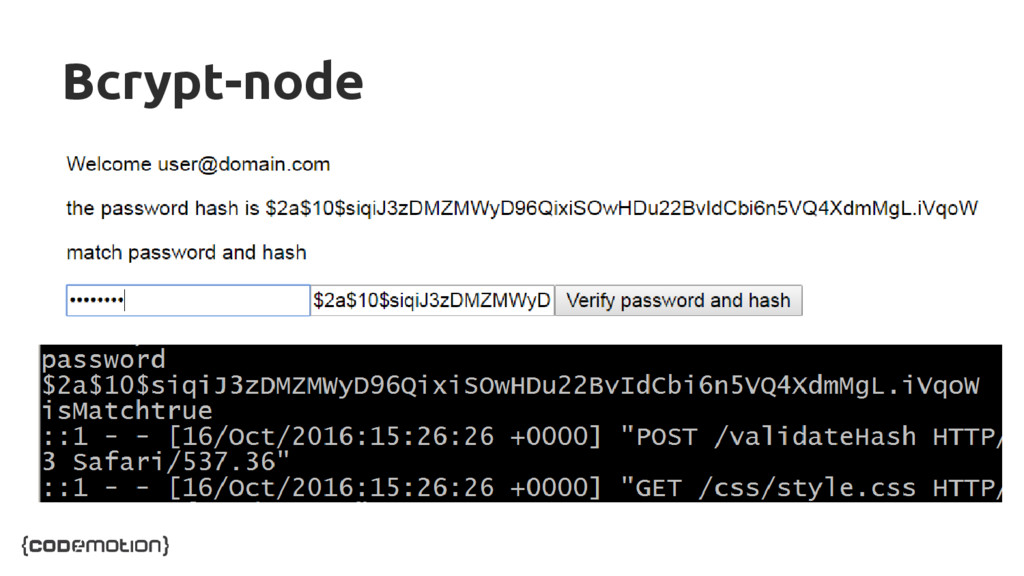
Bcrypt-node
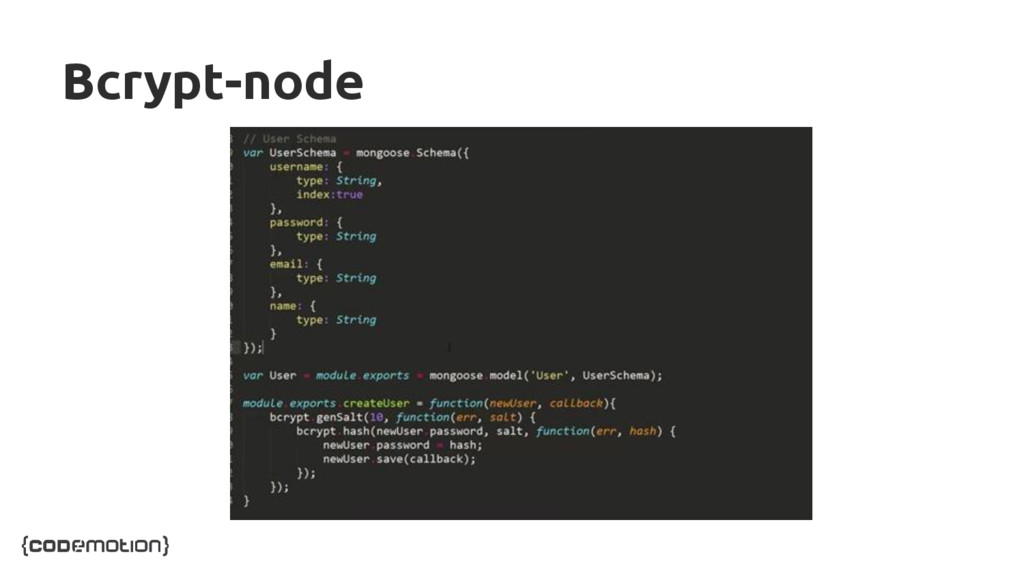
Bcrypt-node
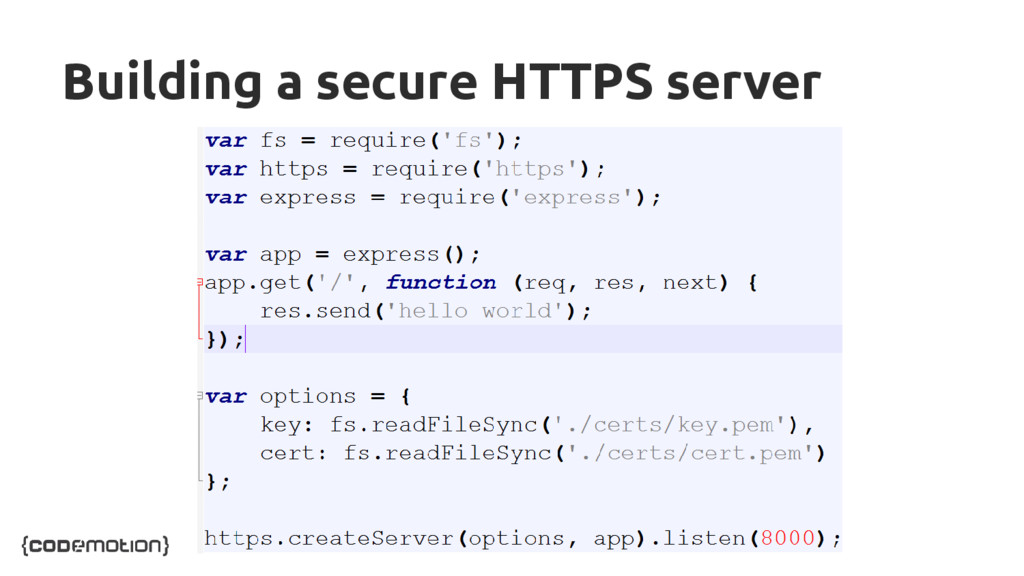
Building a secure HTTPS server
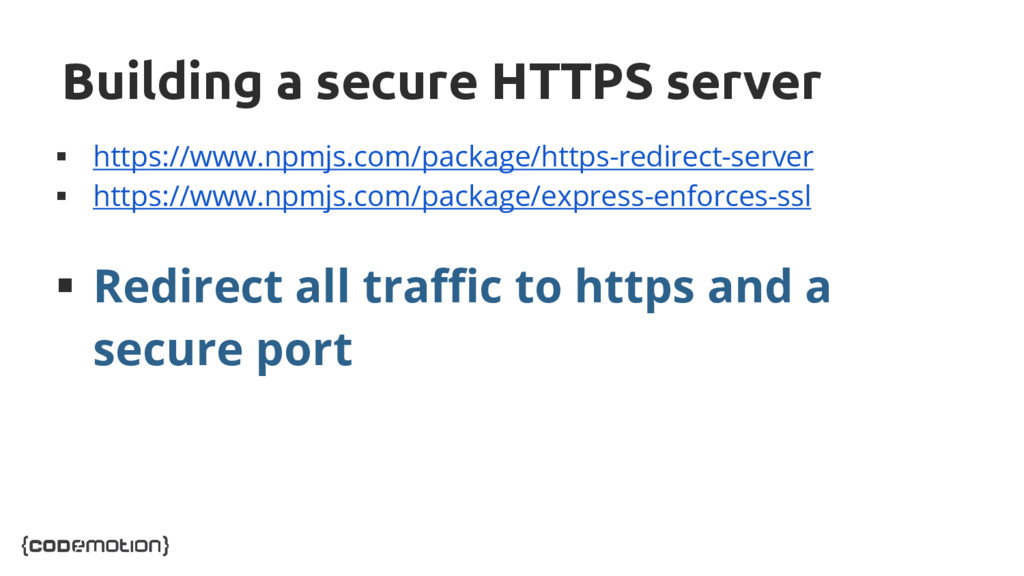
Building a secure HTTPS server https://www.npmjs.com/package/https-redirect-server https://www.npmjs.com/package/express-enforces-ssl
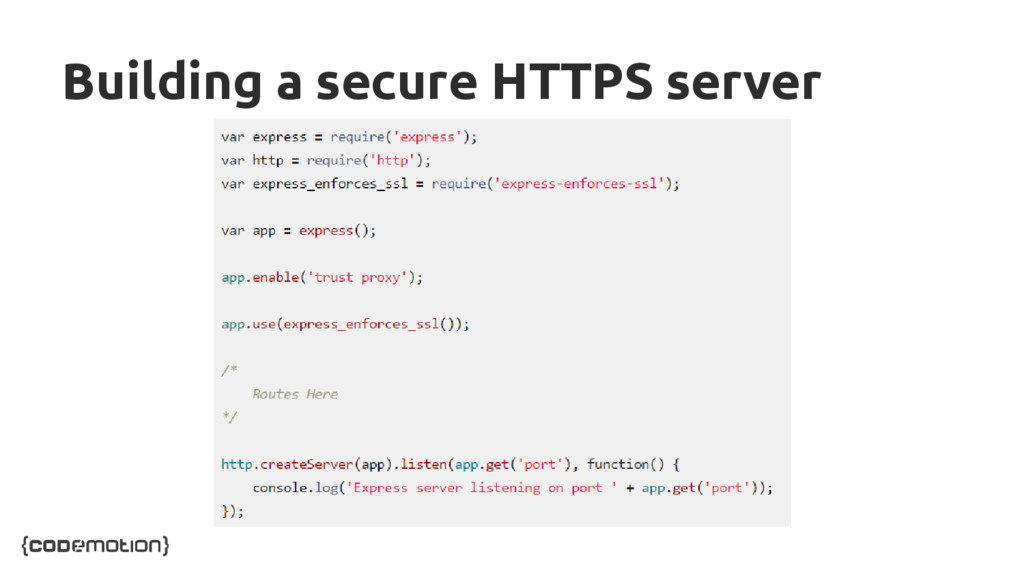
Redirect all traffic to https and a secure port
Building a secure HTTPS server
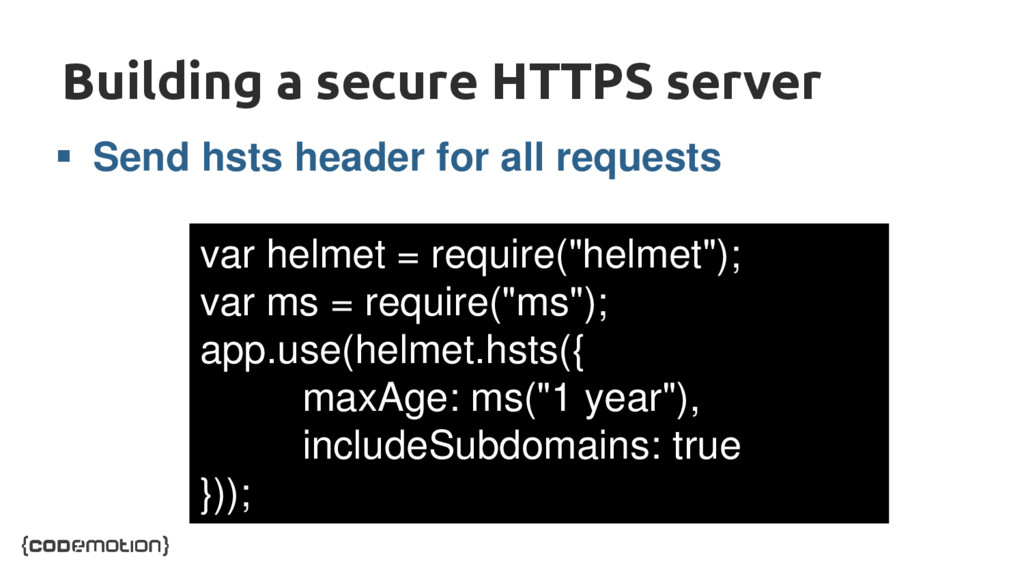
Building a secure HTTPS server var helmet = require("helmet"); var
ms = require("ms"); app.use(helmet.hsts({ maxAge: ms("1 year"), includeSubdomains: true })); Send hsts header for all requests
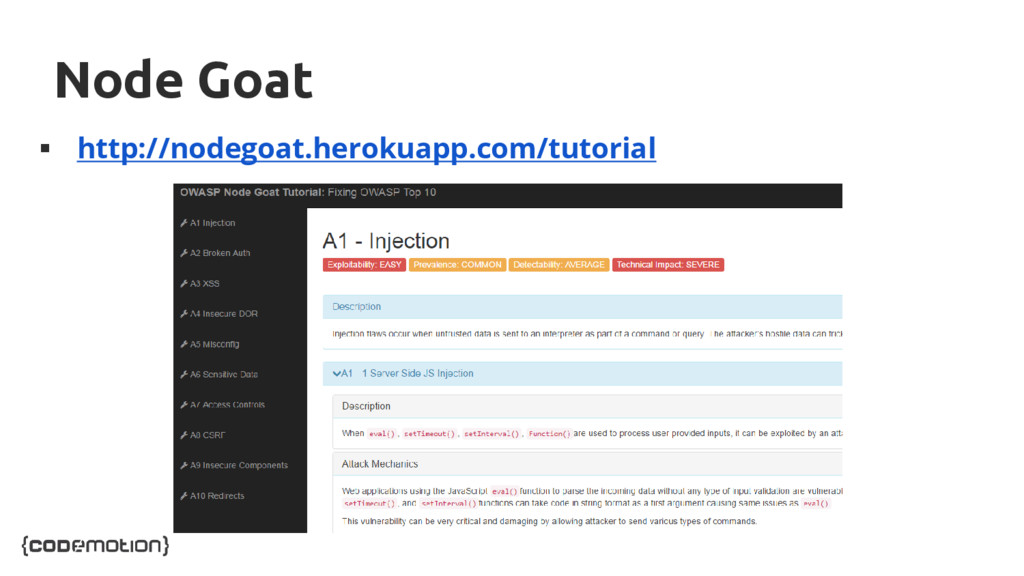
Node Goat http://nodegoat.herokuapp.com/tutorial
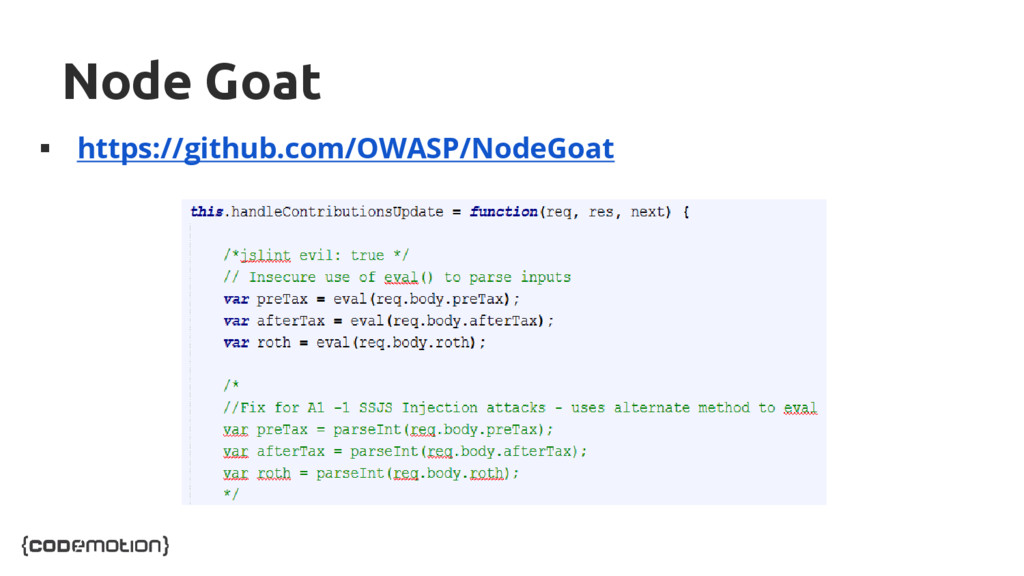
Node Goat https://github.com/OWASP/NodeGoat
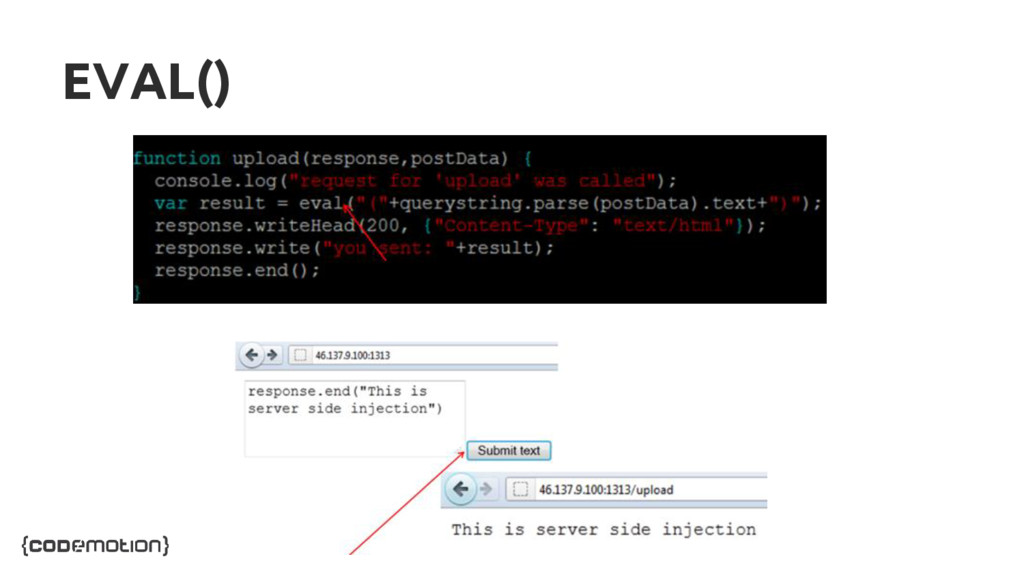
EVAL()
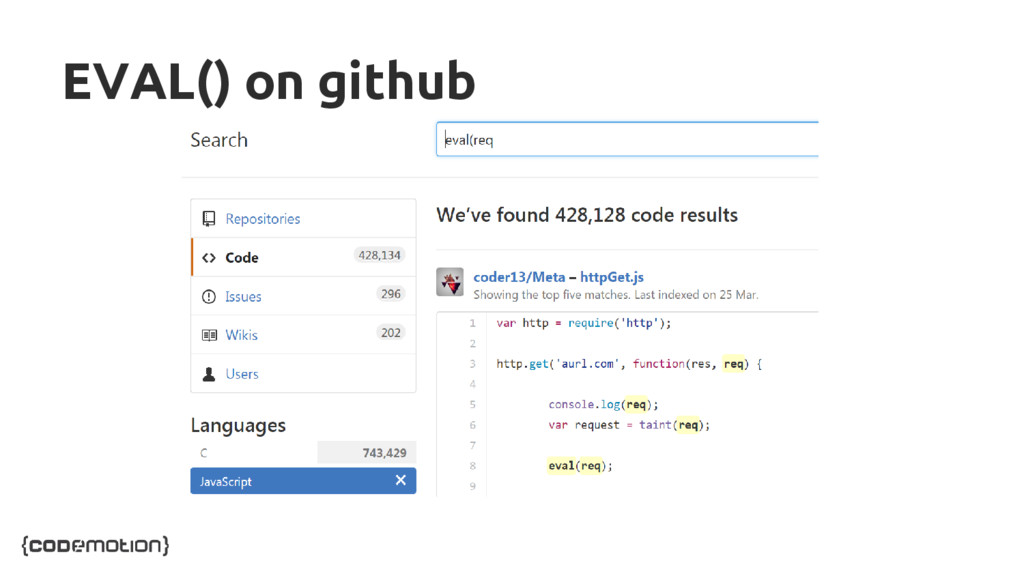
EVAL() on github
EVAL() ATTACKS res.end(require('fs').readdirSync('.').toString()) res.end(require('fs').readdirSync('..').toString())
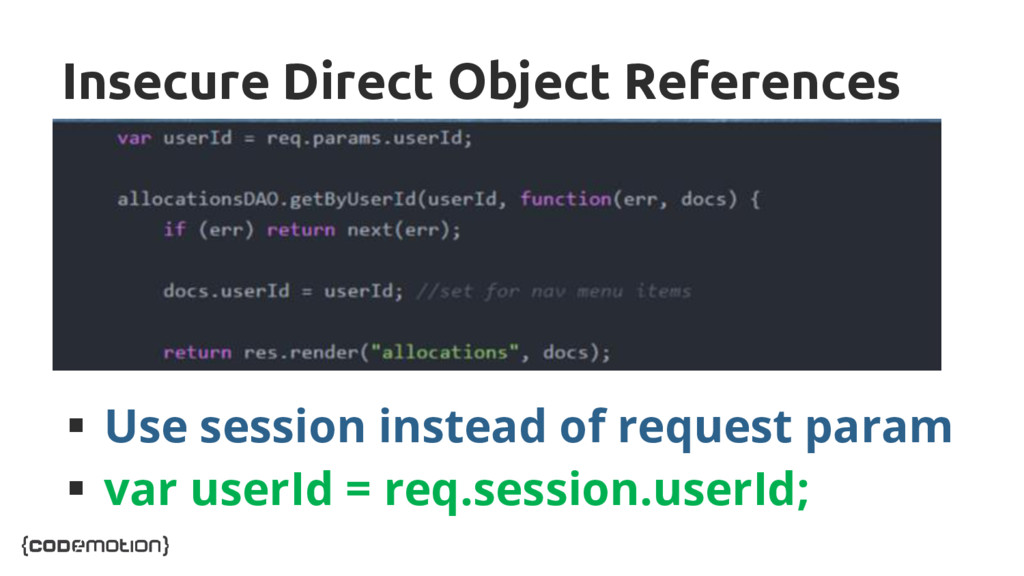
Insecure Direct Object References Use session instead of request
param var userId = req.session.userId;
Tools NSP Require Safe David KrakenJS
/ Lusca middleware Retire snyk.io
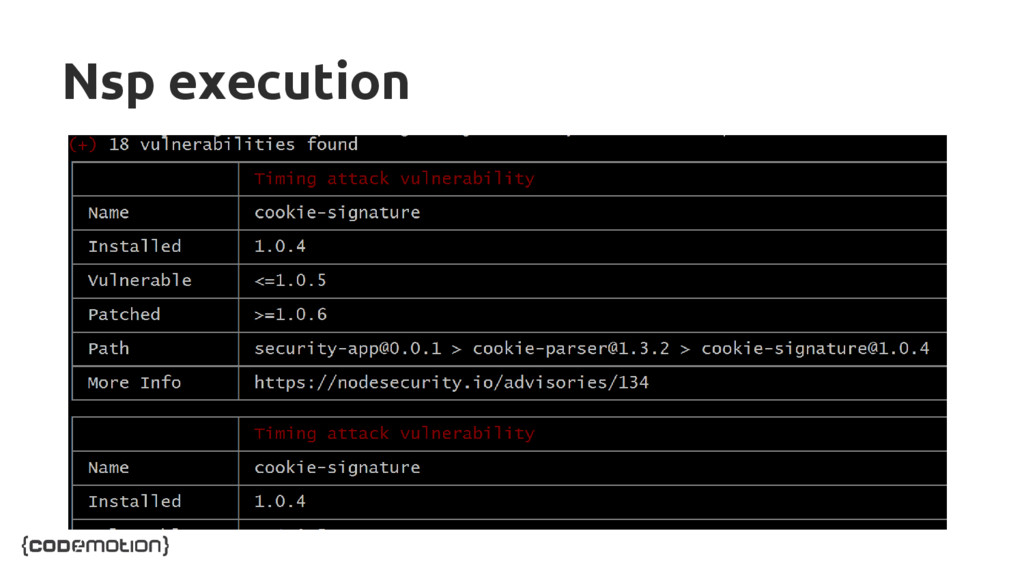
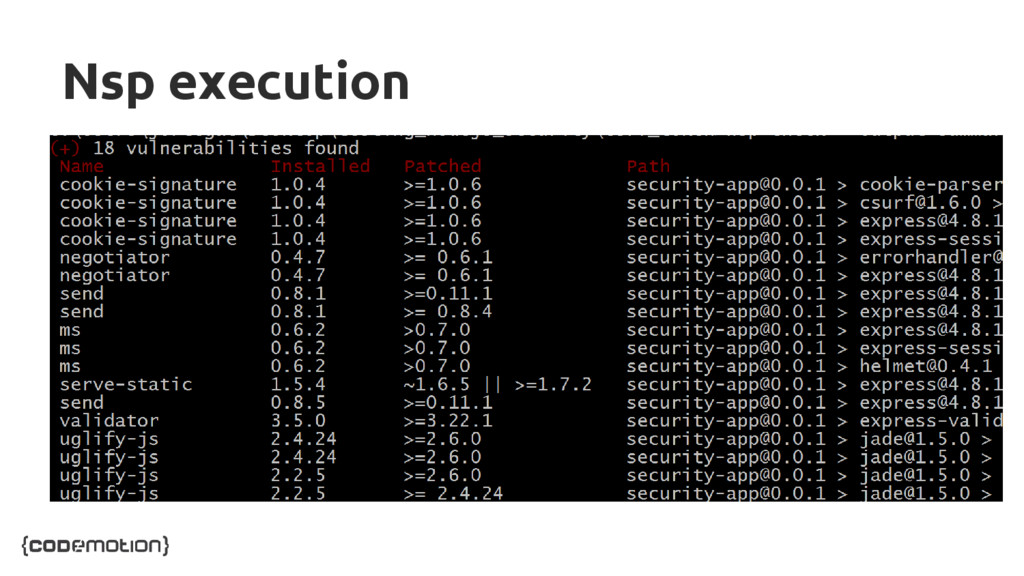
NSP https://github.com/nodesecurity/nsp npm install -g nsp Analyze
package.json nsp check --output summary
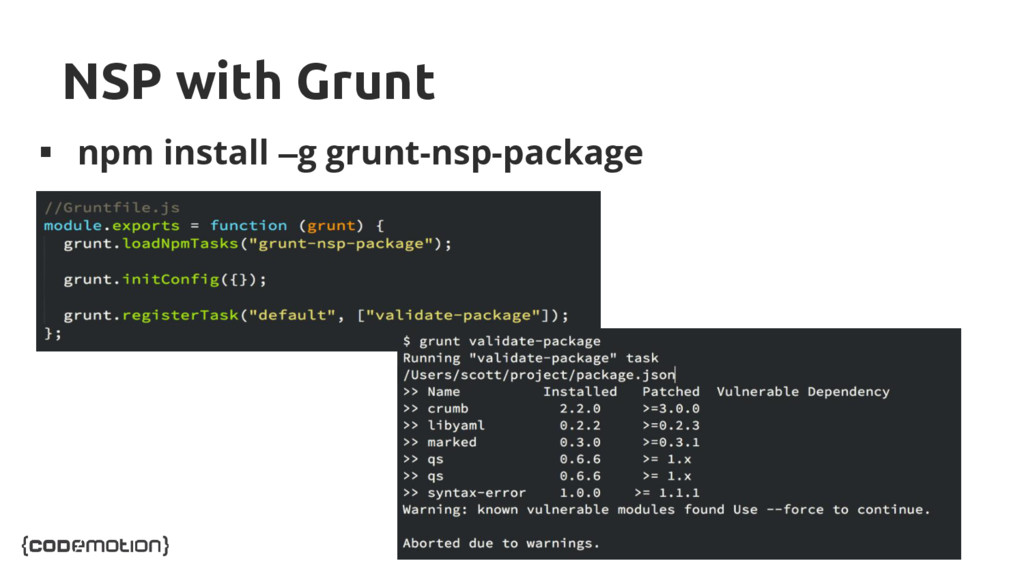
NSP with Grunt npm install –g grunt-nsp-package
Nsp execution
Nsp execution
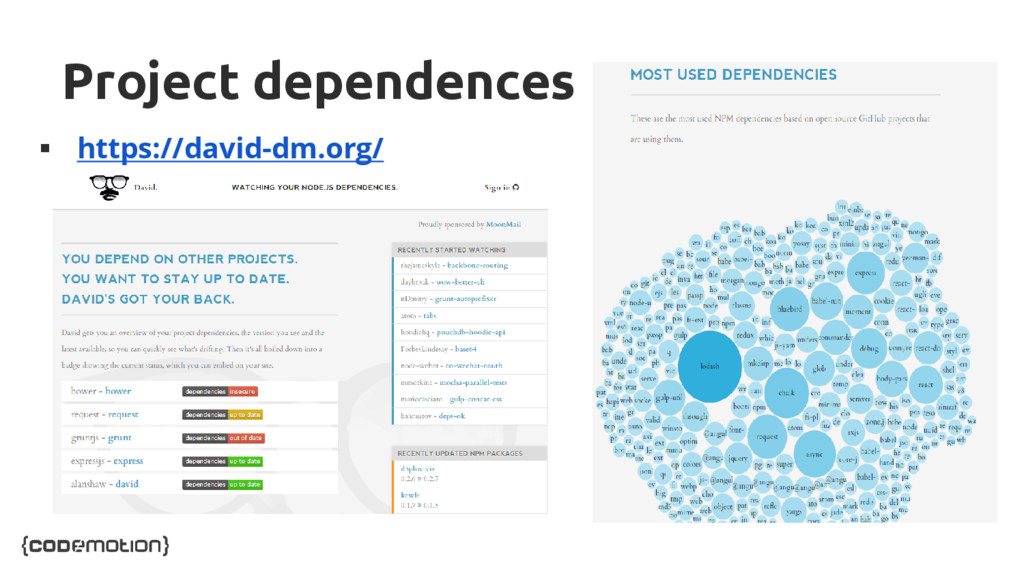
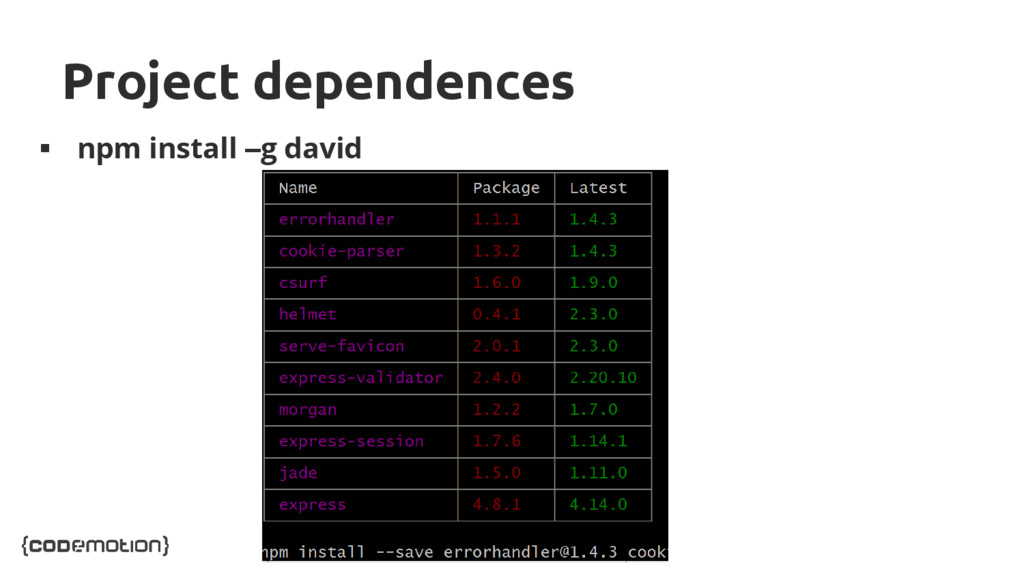
Project dependences https://david-dm.org/
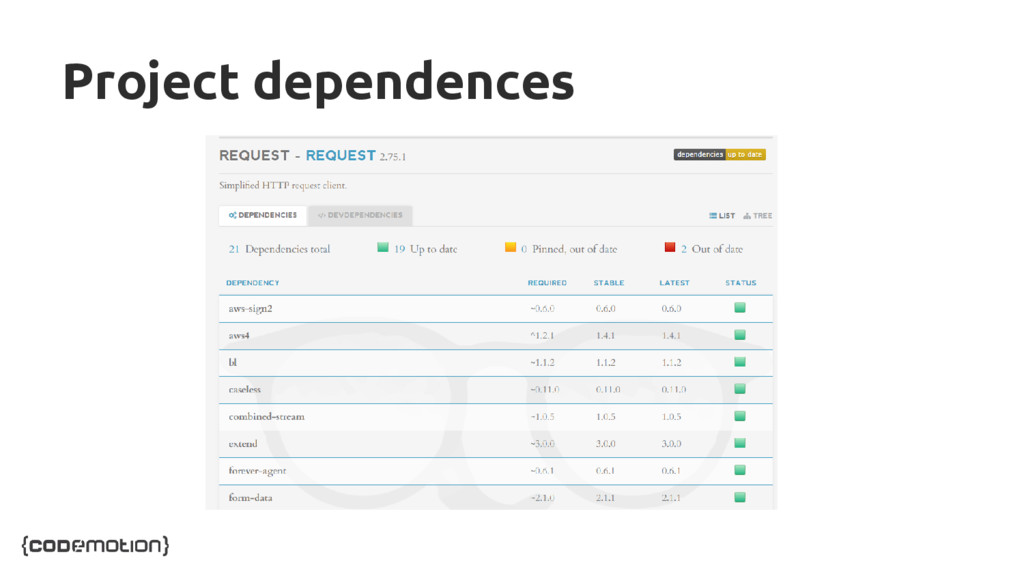
Project dependences
Project dependences npm install –g david
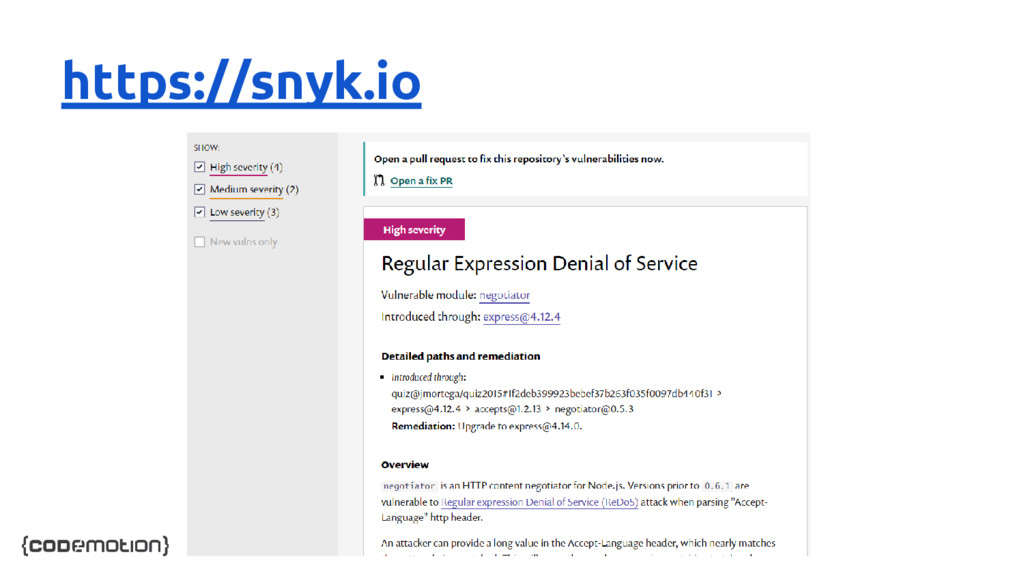
https://snyk.io
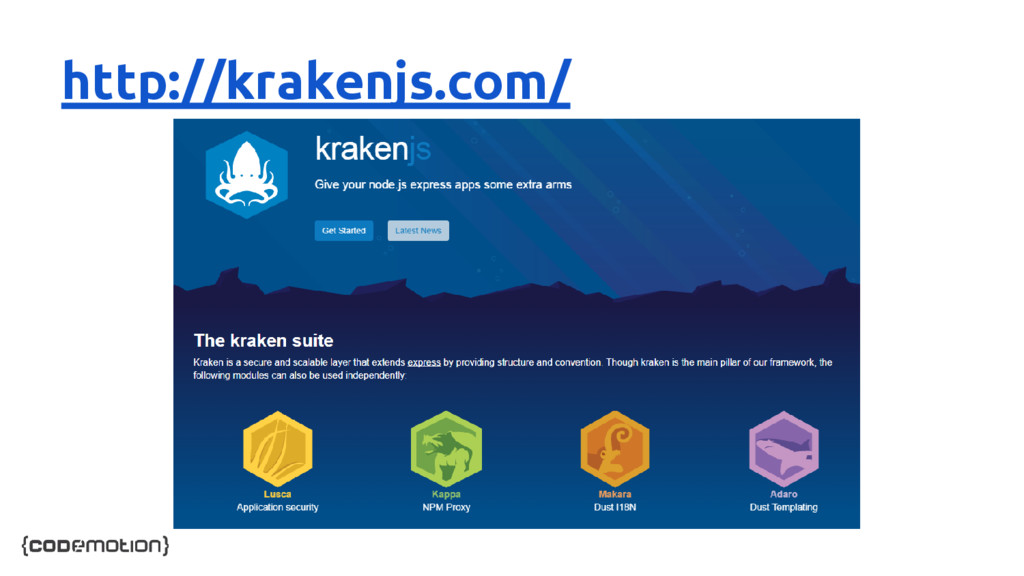
http://krakenjs.com/
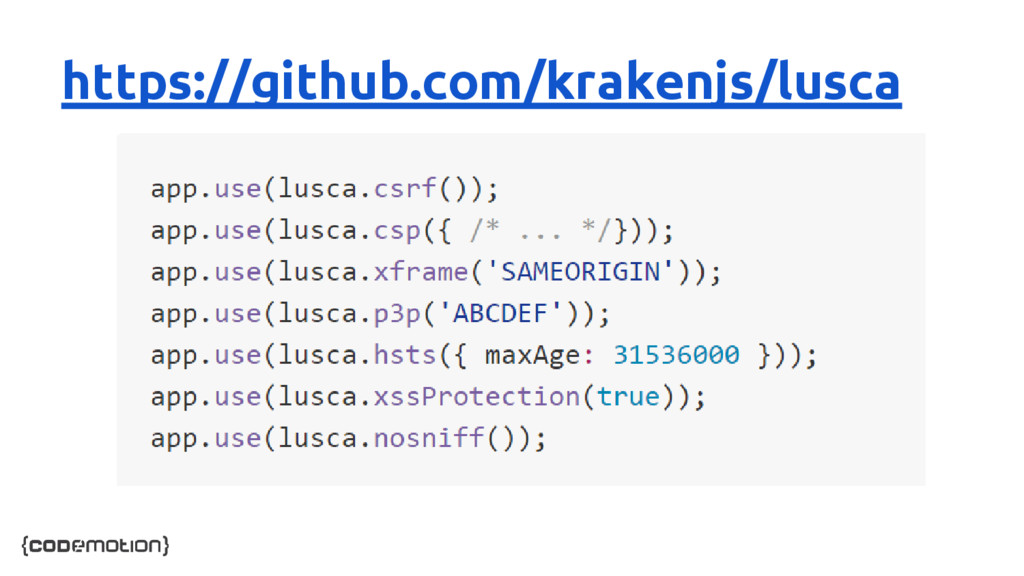
https://github.com/krakenjs/lusca
Retire.js http://retirejs.github.io/retire.js Detecting components and js libraries with
known vulnerabilities
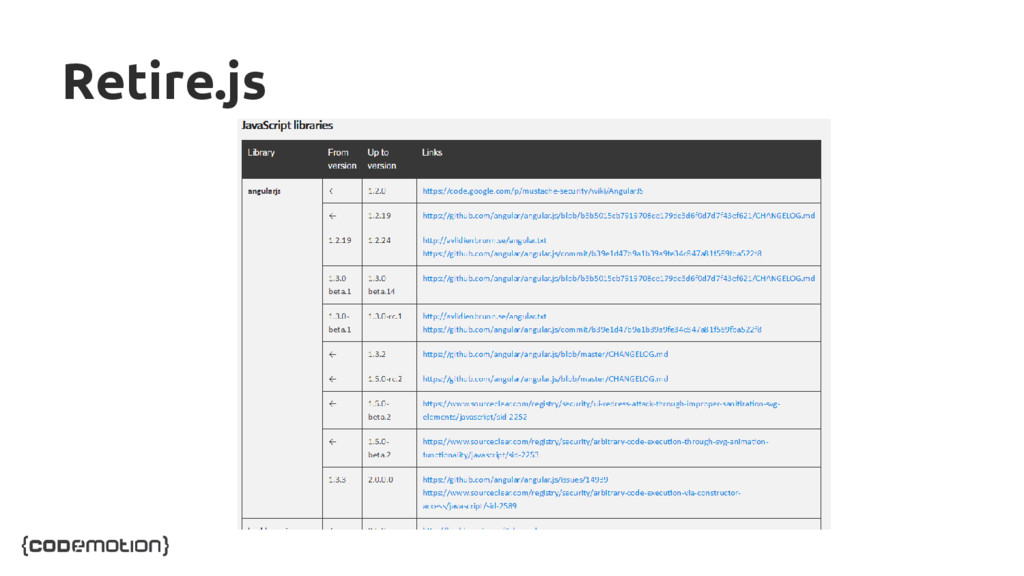
Retire.js
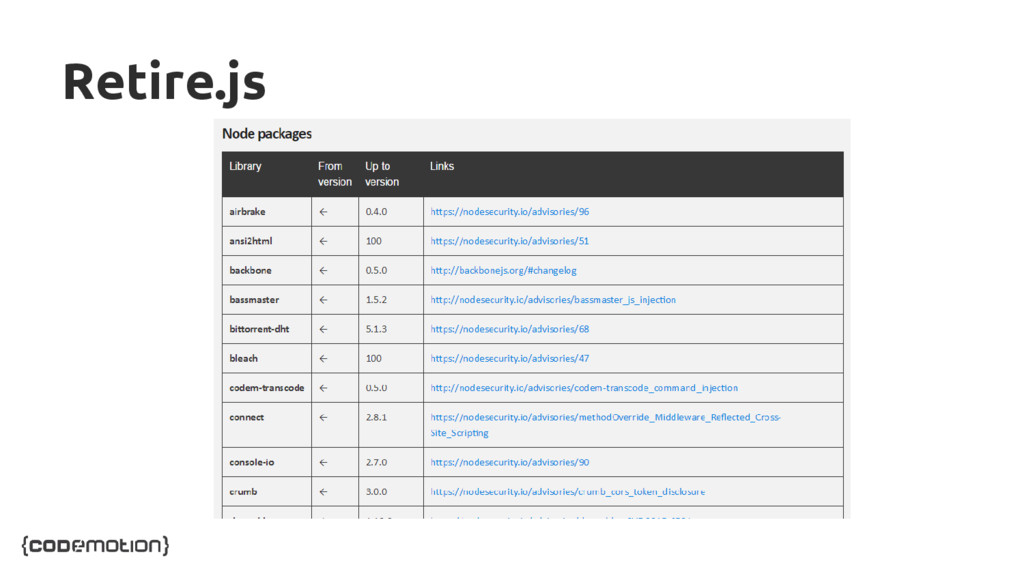
Retire.js
Retire.js
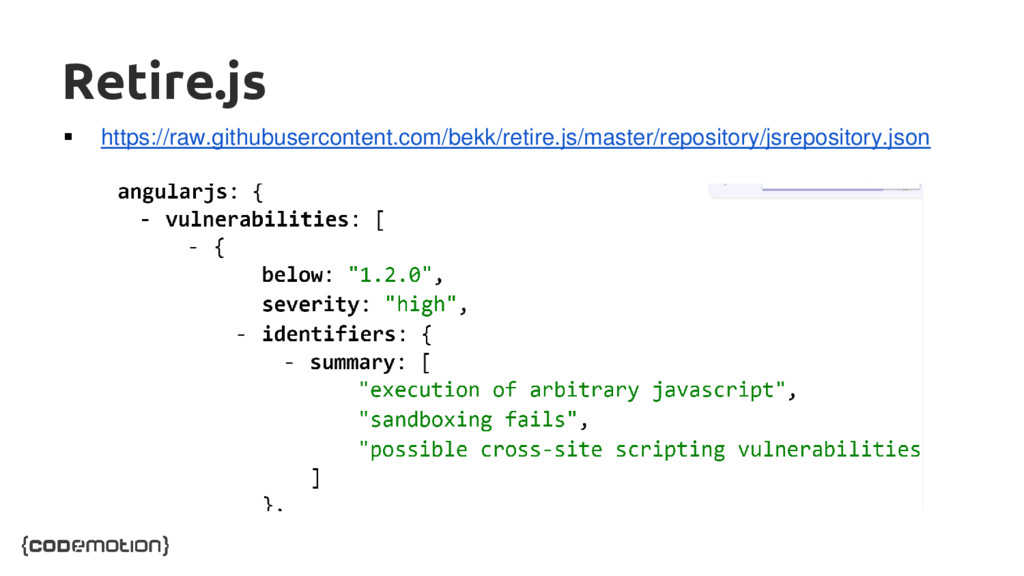
Retire.js https://raw.githubusercontent.com/bekk/retire.js/master/repository/jsrepository.json
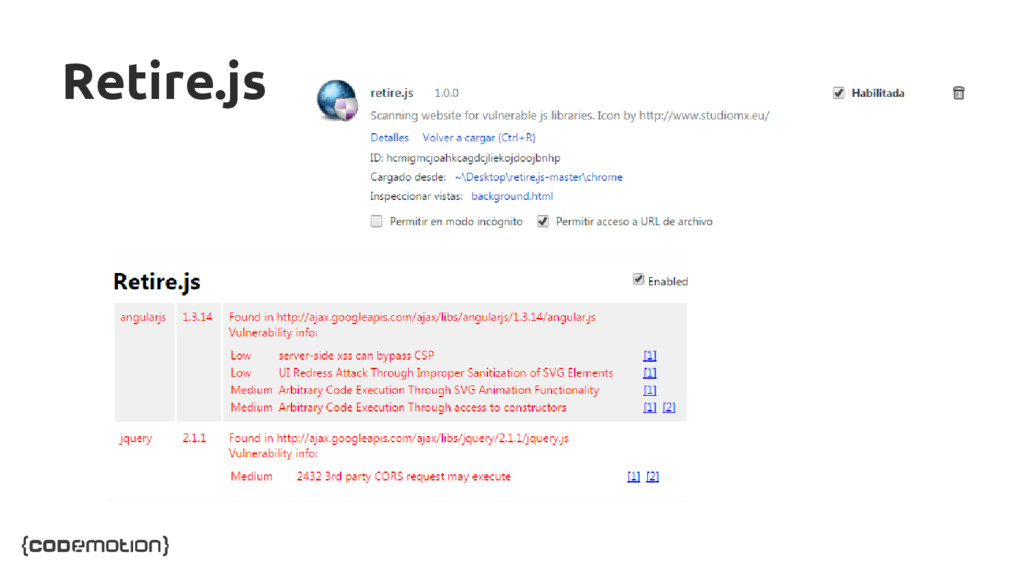
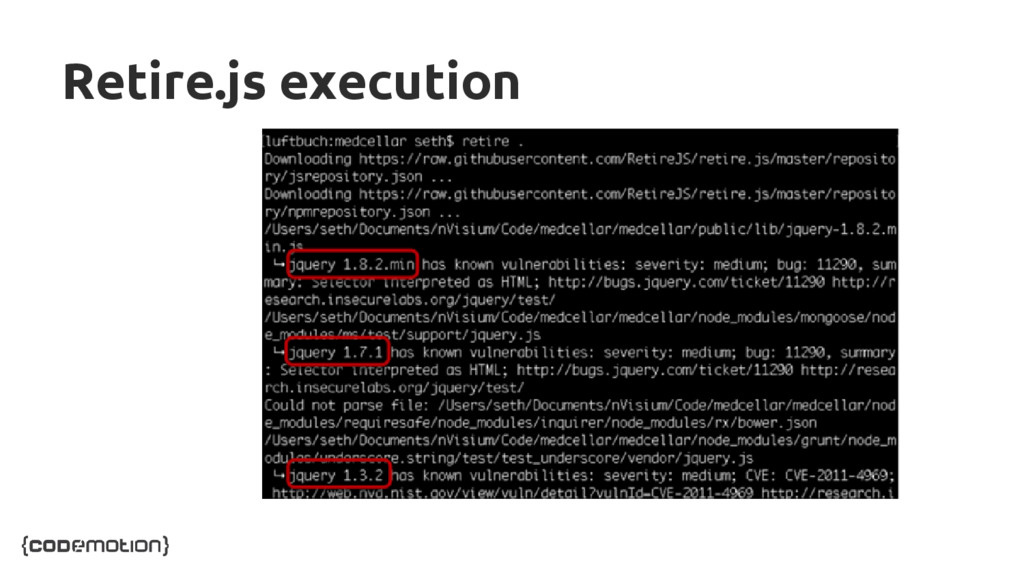
Retire.js execution
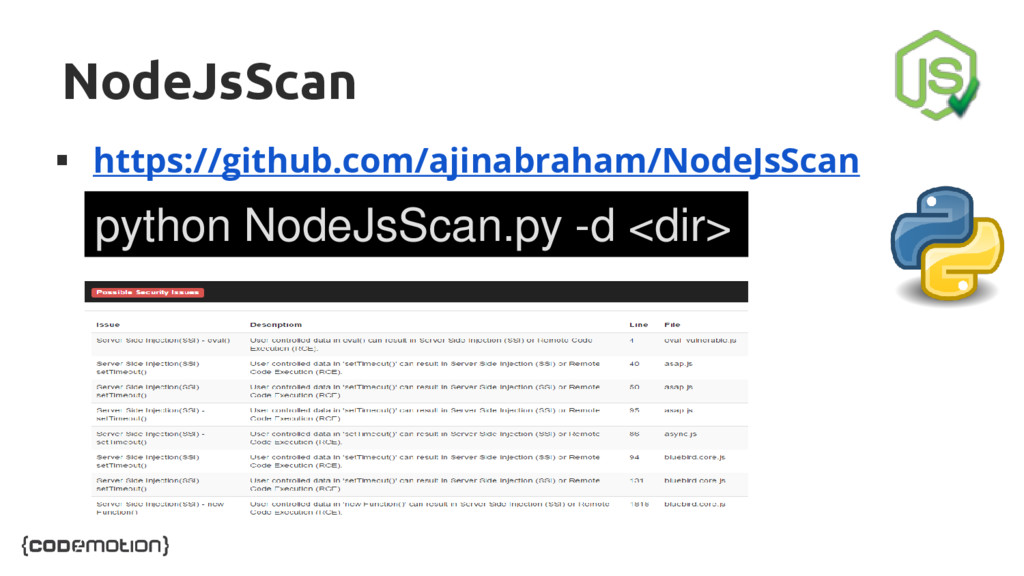
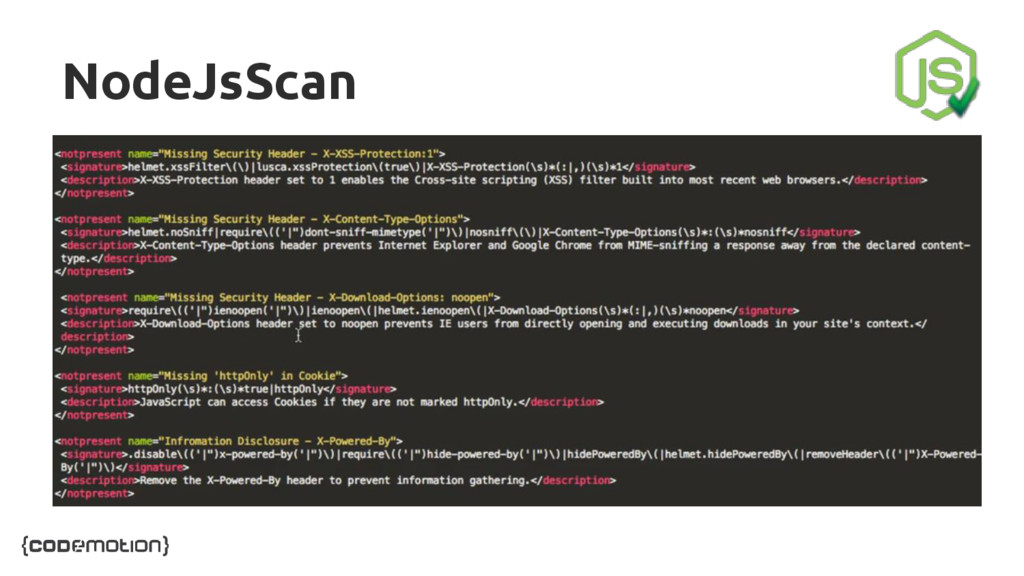
NodeJsScan https://github.com/ajinabraham/NodeJsScan python NodeJsScan.py -d <dir>
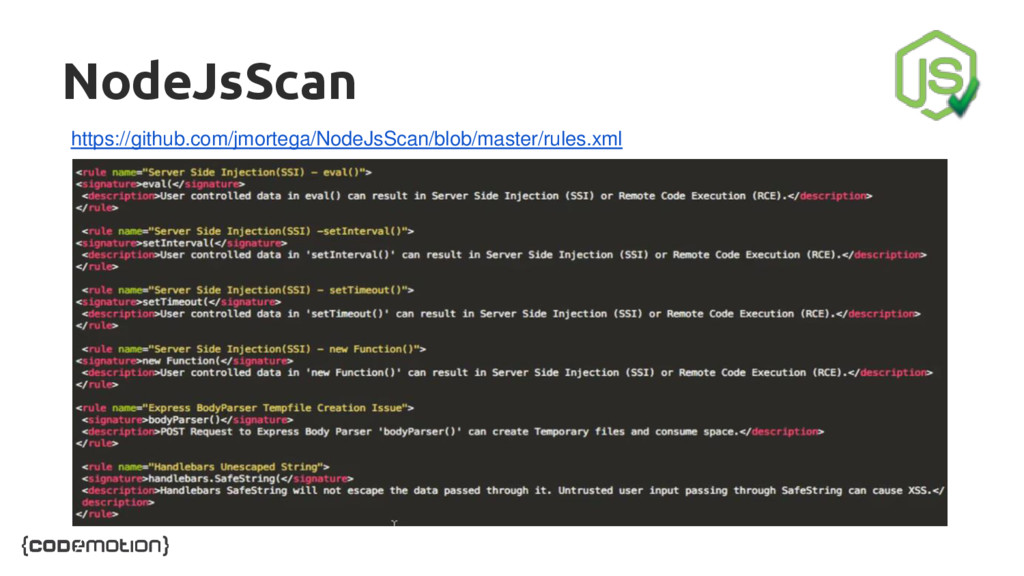
NodeJsScan https://github.com/jmortega/NodeJsScan/blob/master/rules.xml
NodeJsScan
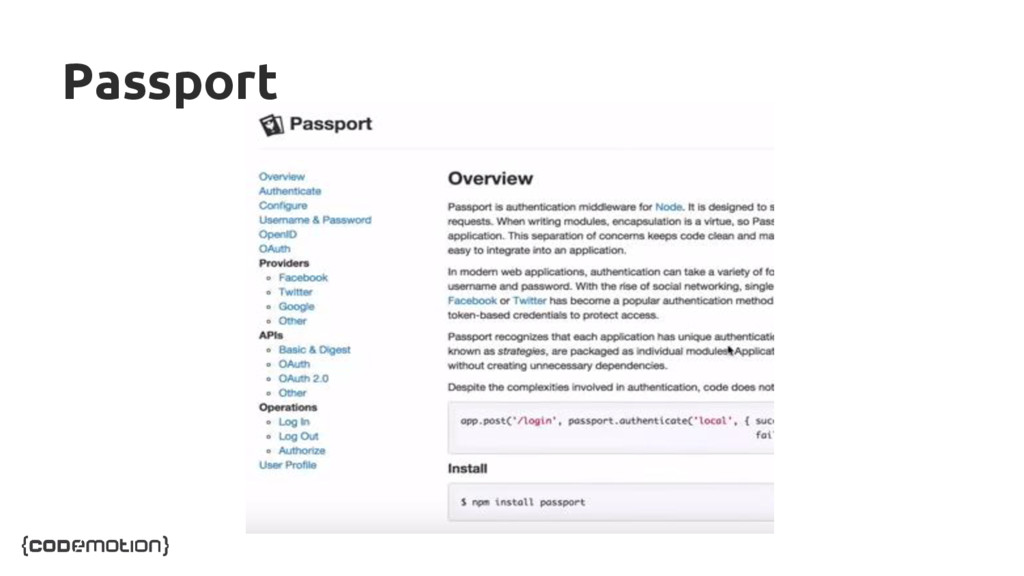
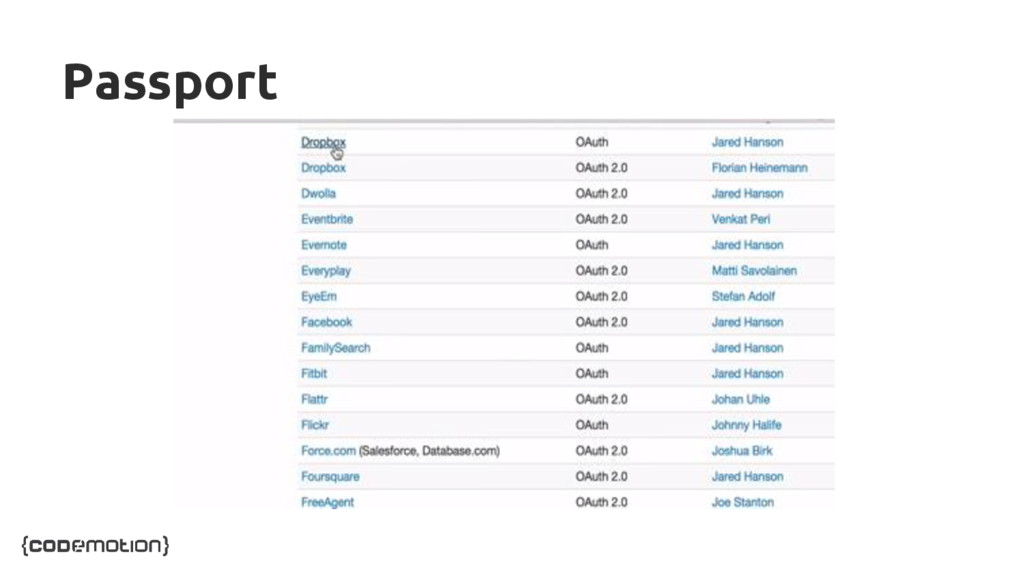
Passport
Passport
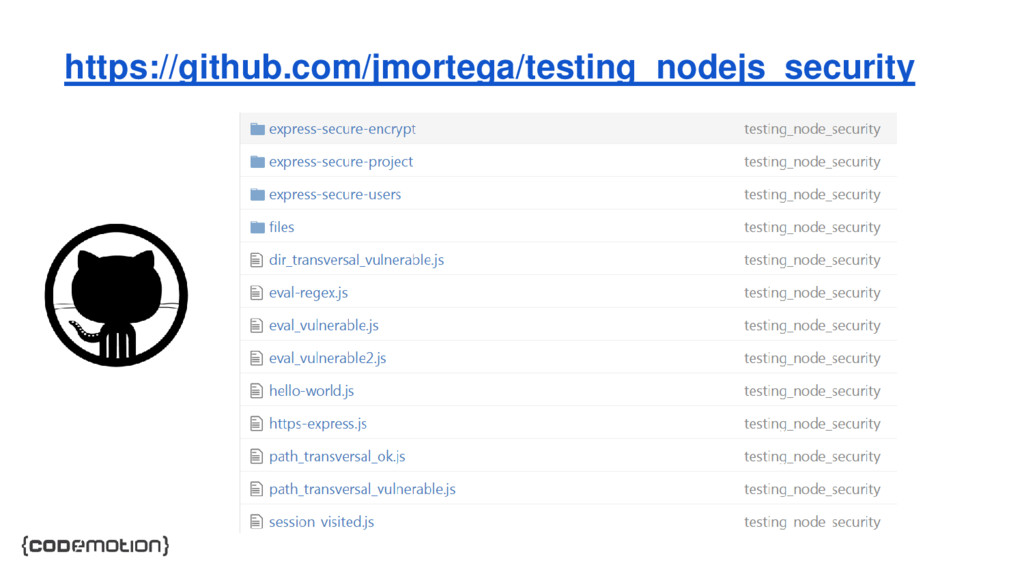
https://github.com/jmortega/testing_nodejs_security
GitHub repositories https://github.com/cr0hn/vulnerable-node https://github.com/rdegges/svcc-auth https://github.com/strongloop/loopback-getting-started- intermediate
References https://blog.risingstack.com/node-js-security-checklist/ https://blog.risingstack.com/node-js-security-tips/ https://groups.google.com/forum/#!forum/nodejs-sec https://nodejs.org/en/blog/vulnerability/september-2016- security-releases/
https://expressjs.com/en/advanced/security-updates.html http://opensecurity.in/nodejsscan/ http://stackabuse.com/securing-your-node-js-app/
Node security learning https://www.udemy.com/nodejs-security-pentesting-and-exploitation/
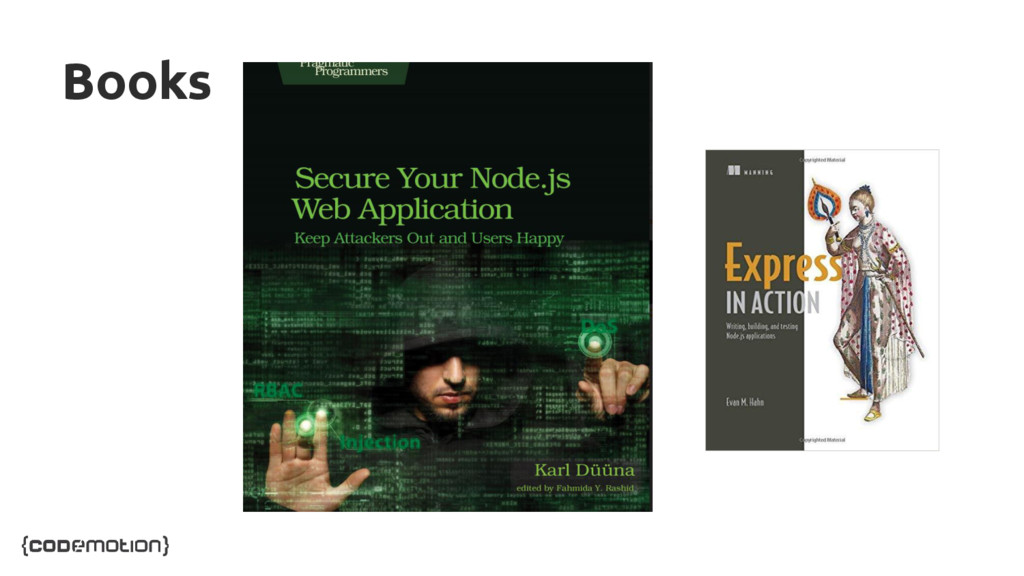
Books


 jmortega
 sylph01
 moro
 iwiwi
 tanahiro2010
 shihochan
 dske104
 steliosf
 timakin
 nao_randd
 kasacchiful
 oku053
 rshindo
 aleyda
 reverentgeek
 productmarketing
 oripsolob
 addyosmani
 twada
 sabderemane
 tamaranovitovic
 cassininazir
 keavy
 samlambert
 brad_frost