to prevent unescaping user input from making to your rendered HTML. Django templating system facilitates this by automatic escaping all variable inputs. If don't want to escape characters on the front end, you have to explicitly tell this to Django. If we generate HTML from templating system, there is always a danger that a variable will include characters that affect the resulting HTML. (#/2/1)
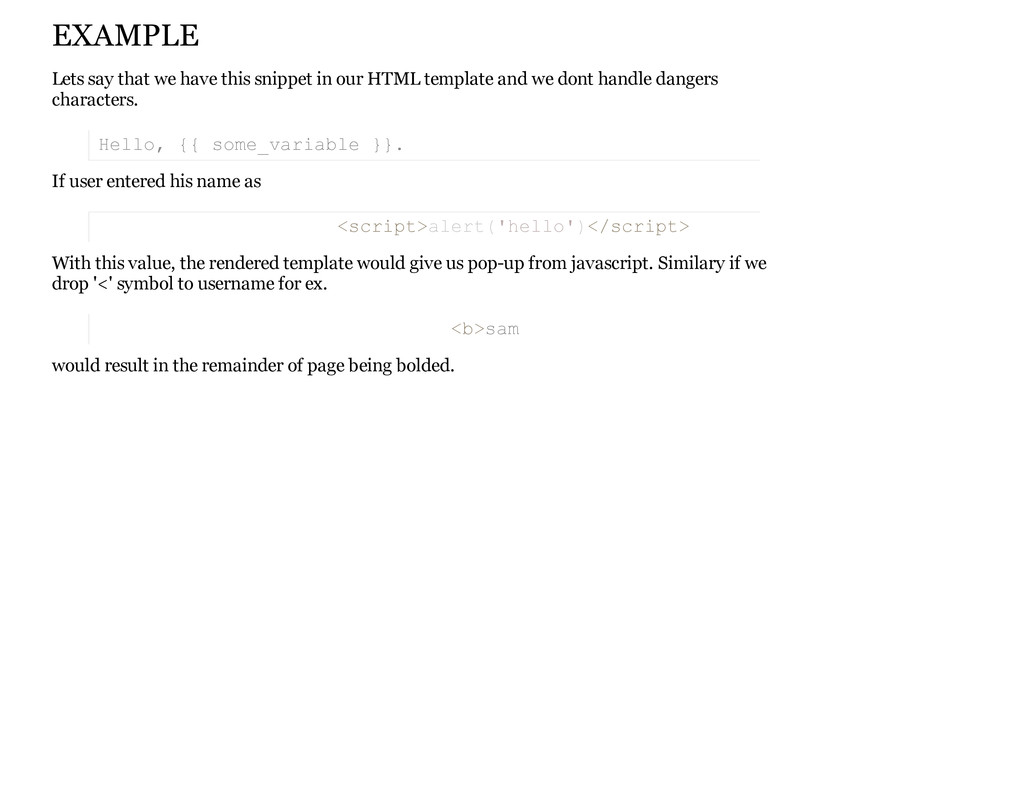
HTML template and we dont handle dangers characters. If user entered his name as With this value, the rendered template would give us pop-up from javascript. Similary if we drop '<' symbol to username for ex. would result in the remainder of page being bolded. H e l l o , { { s o m e _ v a r i a b l e } } . < s c r i p t > < / s c r i p t > a l e r t ( ' h e l l o ' ) < b > s a m
be trusted blindly. To solve this problem we have two options: We can make sure to run each untrusted template variable through |safe filter, which converts every potentially harmful HTML character to unharmfull ones. Make advantage of Django's automatic escaping.
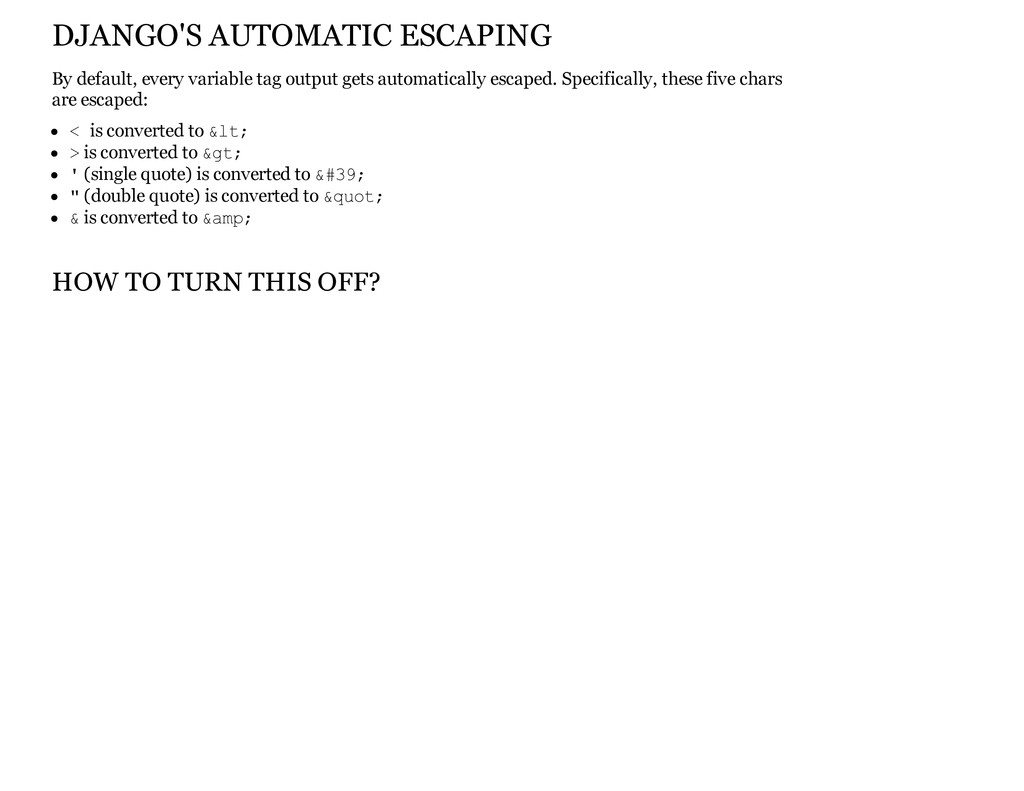
automatically escaped. Specifically, these five chars are escaped: < is converted to & l t ; > is converted to & g t ; ' (single quote) is converted to & # 3 9 ; " (double quote) is converted to & q u o t ; & is converted to & a m p ; HOW TO TURN THIS OFF?
data that you intend to be rendered as raw HTML, in this case you you don't want their contents to be escaped. exp. storing blob of HTML into database and want to embed it directly into your template exp. using django template to render text which is not html, like email message
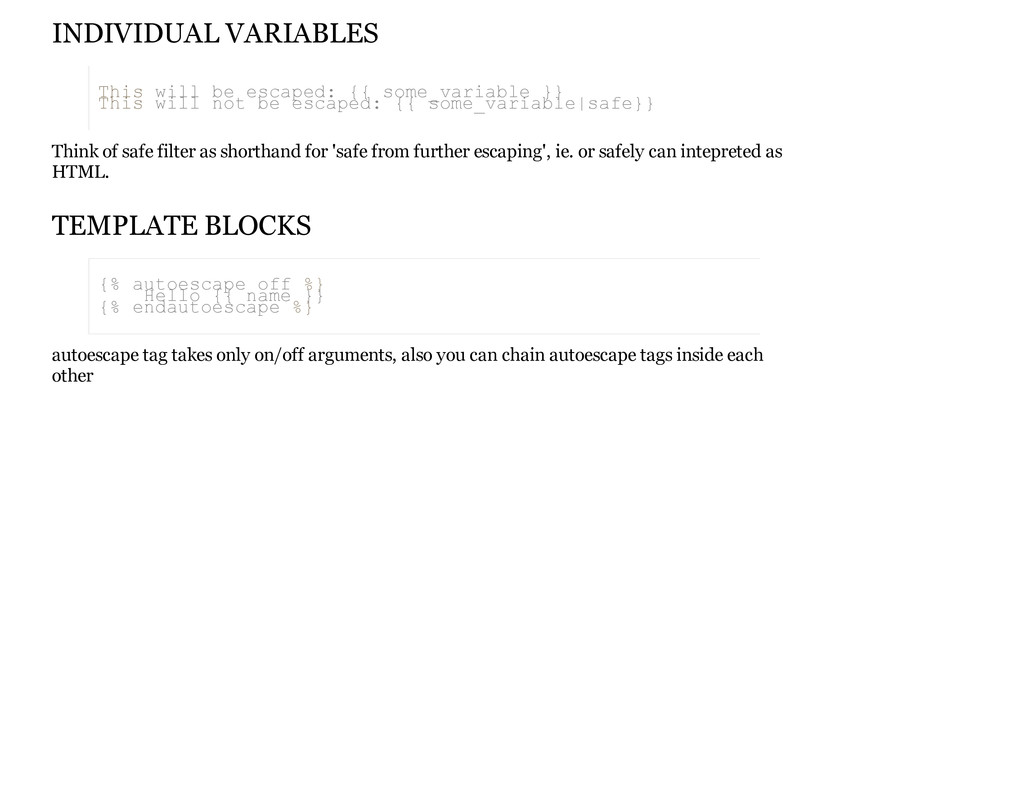
from further escaping', ie. or safely can intepreted as HTML. TEMPLATE BLOCKS autoescape tag takes only on/off arguments, also you can chain autoescape tags inside each other T h i s w i l l b e e s c a p e d : { { s o m e _ v a r i a b l e } } T h i s w i l l n o t b e e s c a p e d : { { s o m e _ v a r i a b l e | s a f e } } { % a u t o e s c a p e o f f % } H e l l o { { n a m e } } { % e n d a u t o e s c a p e % }
provides very strong ORM abstraction which protects developer from all SQL injections. HOWEVER! Django provides developers to perform raw SQL queries, and this code need to be manualy audited. If you are using raw SQL statements for optimization, be carefull for writing a smelly code.
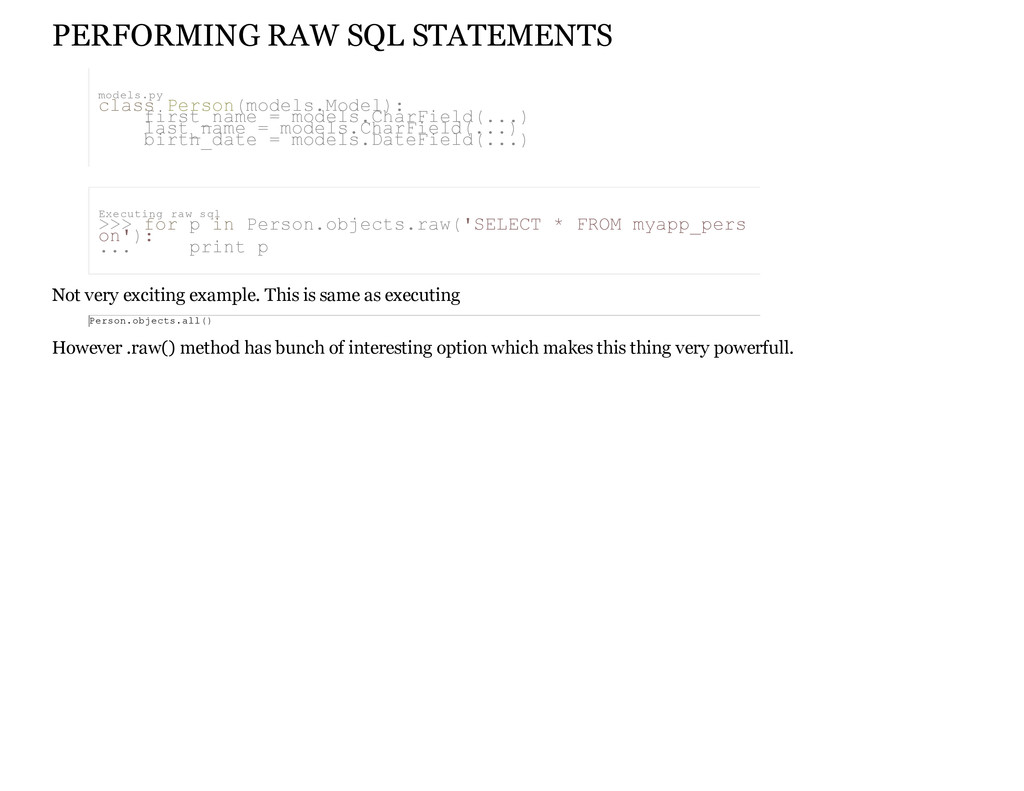
same as executing However .raw() method has bunch of interesting option which makes this thing very powerfull. m o d e l s . p y c l a s s P e r s o n ( m o d e l s . M o d e l ) : f i r s t _ n a m e = m o d e l s . C h a r F i e l d ( . . . ) l a s t _ n a m e = m o d e l s . C h a r F i e l d ( . . . ) b i r t h _ d a t e = m o d e l s . D a t e F i e l d ( . . . ) E x e c u t i n g r a w s q l > > > f o r p i n P e r s o n . o b j e c t s . r a w ( ' S E L E C T * F R O M m y a p p _ p e r s o n ' ) : . . . p r i n t p P e r s o n . o b j e c t s . a l l ( )
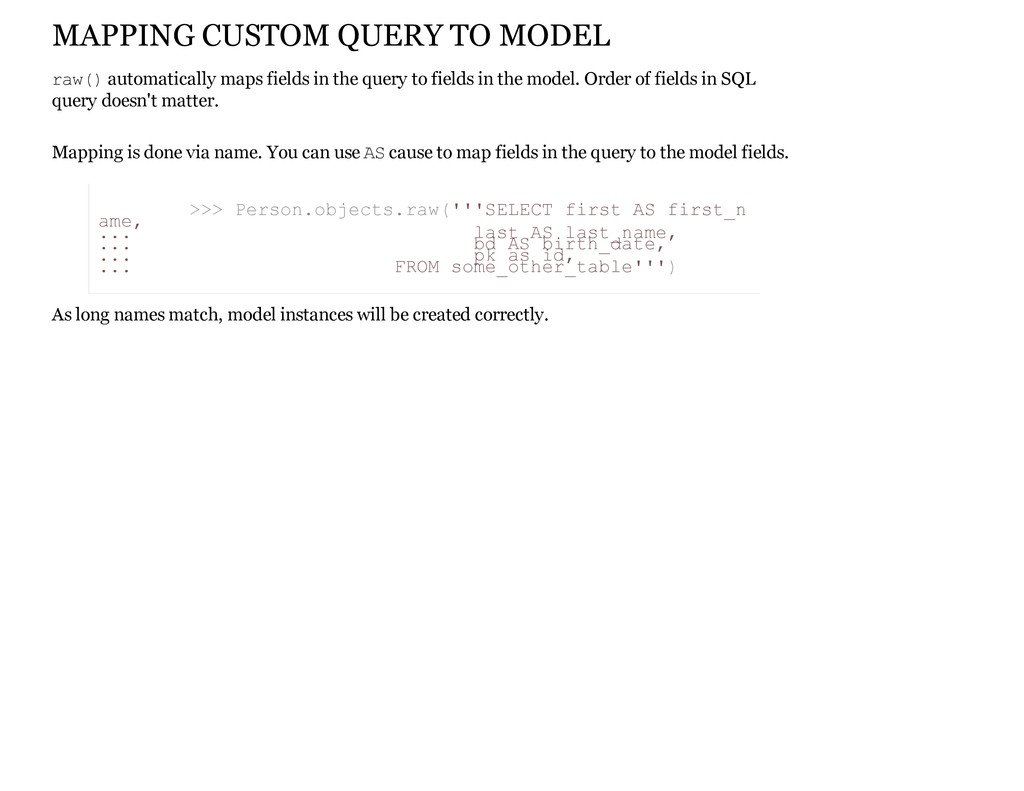
automatically maps fields in the query to fields in the model. Order of fields in SQL query doesn't matter. Mapping is done via name. You can use A S cause to map fields in the query to the model fields. As long names match, model instances will be created correctly. > > > P e r s o n . o b j e c t s . r a w ( ' ' ' S E L E C T f i r s t A S f i r s t _ n a m e , . . . l a s t A S l a s t _ n a m e , . . . b d A S b i r t h _ d a t e , . . . p k a s i d , . . . F R O M s o m e _ o t h e r _ t a b l e ' ' ' )
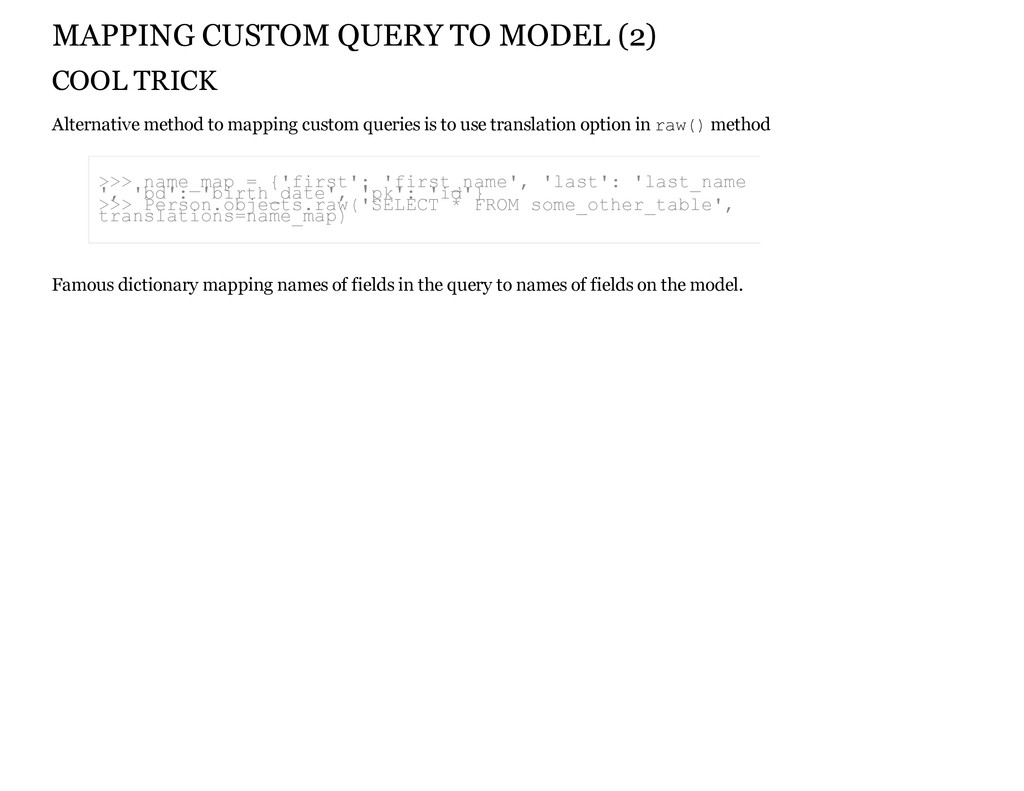
to mapping custom queries is to use translation option in r a w ( ) method Famous dictionary mapping names of fields in the query to names of fields on the model. > > > n a m e _ m a p = { ' f i r s t ' : ' f i r s t _ n a m e ' , ' l a s t ' : ' l a s t _ n a m e ' , ' b d ' : ' b i r t h _ d a t e ' , ' p k ' : ' i d ' } > > > P e r s o n . o b j e c t s . r a w ( ' S E L E C T * F R O M s o m e _ o t h e r _ t a b l e ' , t r a n s l a t i o n s = n a m e _ m a p )
means you can do this: This has more to do with python then database, so if we have big number of P e r s o n s in db, we should use L I M I T clause to optimize things. > > > f i r s t _ p e r s o n = P e r s o n . o b j e c t s . r a w ( ' S E L E C T * f r o m m y a p p _ p e r s o n ' ) [ 0 ] > > > f i r s t _ p e r s o n = P e r s o n . o b j e c t s . r a w ( ' S E L E C T * f r o m m y a p p _ p e r s o n L I M I T 1 ' ) [ 0 ]
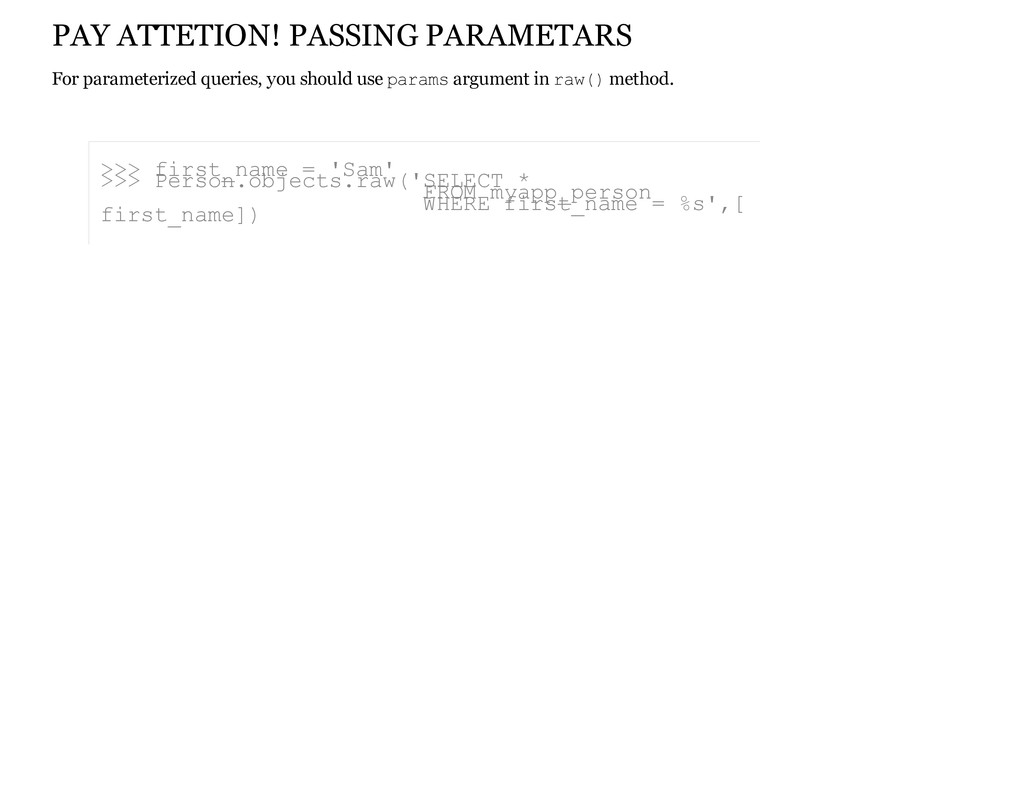
p a r a m s argument in r a w ( ) method. > > > f i r s t _ n a m e = ' S a m ' > > > P e r s o n . o b j e c t s . r a w ( ' S E L E C T * F R O M m y a p p _ p e r s o n W H E R E f i r s t _ n a m e = % s ' , [ f i r s t _ n a m e ] )
thing for every developer is doing this: DON'T DO THIS Using params argument in raw() method protects you from SQL injection attacks completly. > > > q u e r y = ' S E L E C T * F R O M m y a p p _ p e r s o n W H E R E l a s t _ n a m e = % s ' % l n a m e > > > P e r s o n . o b j e c t s . r a w ( q u e r y )
of thing. Instructions and a bit more info available . (https://github.com/hakimel/reveal.js#markdown) here < s e c t i o n d a t a m a r k d o w n > # # M a r k d o w n s u p p o r t F o r t h o s e o f y o u w h o l i k e t h a t s o r t o f t h i n g . I n s t r u c t i o n s a n d a b i t m o r e i n f o a v a i l a b l e [ h e r e ] ( h t t p s : / / g i t h u b . c o m / h a k i m e l / r e v e a l . j s # m a r k d o w n ) . < / s e c t i o n >
a t e = " s o m e t h i n g " on a slide and " s o m e t h i n g " will be added as a class to the document element when the slide is open. This lets you apply broader style changes, like switching the background. (#/7/1)
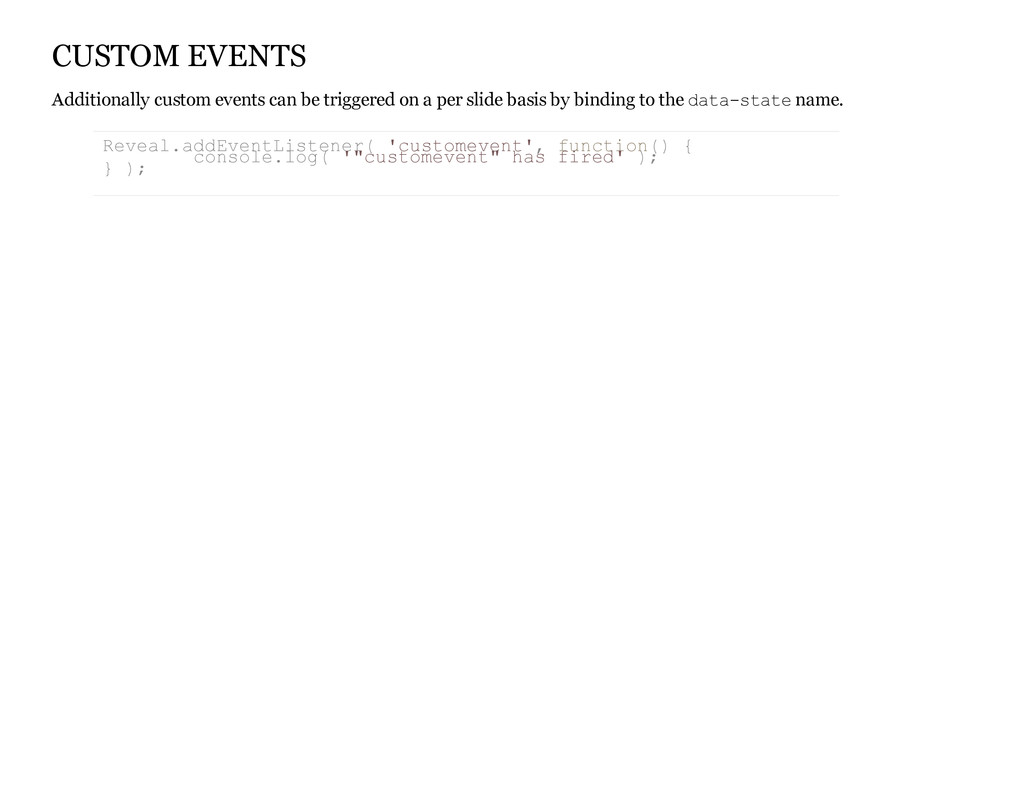
per slide basis by binding to the d a t a s t a t e name. R e v e a l . a d d E v e n t L i s t e n e r ( ' c u s t o m e v e n t ' , f u n c t i o n ( ) { c o n s o l e . l o g ( ' " c u s t o m e v e n t " h a s f i r e d ' ) ; } ) ;
The nice thing about standards is that there are so many to choose from” and block: “ For years there has been a theory that millions of monkeys typing at random on millions of typewriters would reproduce the entire works of Shakespeare. The Internet has proven this theory to be untrue. ”
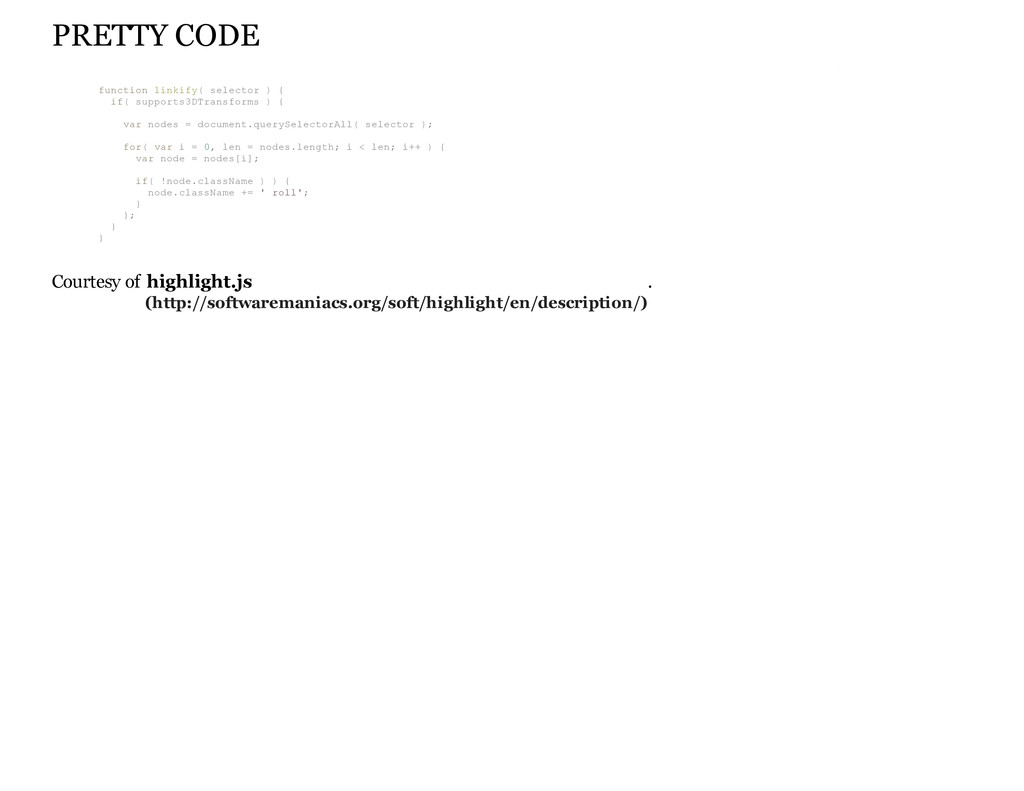
i o n l i n k i f y ( s e l e c t o r ) { i f ( s u p p o r t s 3 D T r a n s f o r m s ) { v a r n o d e s = d o c u m e n t . q u e r y S e l e c t o r A l l ( s e l e c t o r ) ; f o r ( v a r i = 0 , l e n = n o d e s . l e n g t h ; i < l e n ; i + + ) { v a r n o d e = n o d e s [ i ] ; i f ( ! n o d e . c l a s s N a m e ) ) { n o d e . c l a s s N a m e + = ' r o l l ' ; } } ; } } (http://softwaremaniacs.org/soft/highlight/en/description/) highlight.js


 syuchimu
 tagtag
 sshimizu2006
 trycycle
 aikinohara
 hanbao
 hayataka88
 ktatsuya
 kiyoshi
 auna
 paigeccino
 raygrieselhuber
 samlambert
 chriscoyier
 davetheseo
 uxyall
 watany
 mza
 lfama
 coloredviolet
 rmw