Upgrade to Pro — share decks privately, control downloads, hide ads and more …

Oops I forgot me password!

Oops I forgot me password!

Forget password feature is a common in website, but I can lead to a flaw. Using a weak random generator can leak and compromise important information. In this talk, we will see how we can attack it and how can we protect against.

Avatar for Thierry Thuon

Thierry Thuon

April 19, 2018

More Decks by Thierry Thuon

Other Decks in Programming

Transcript

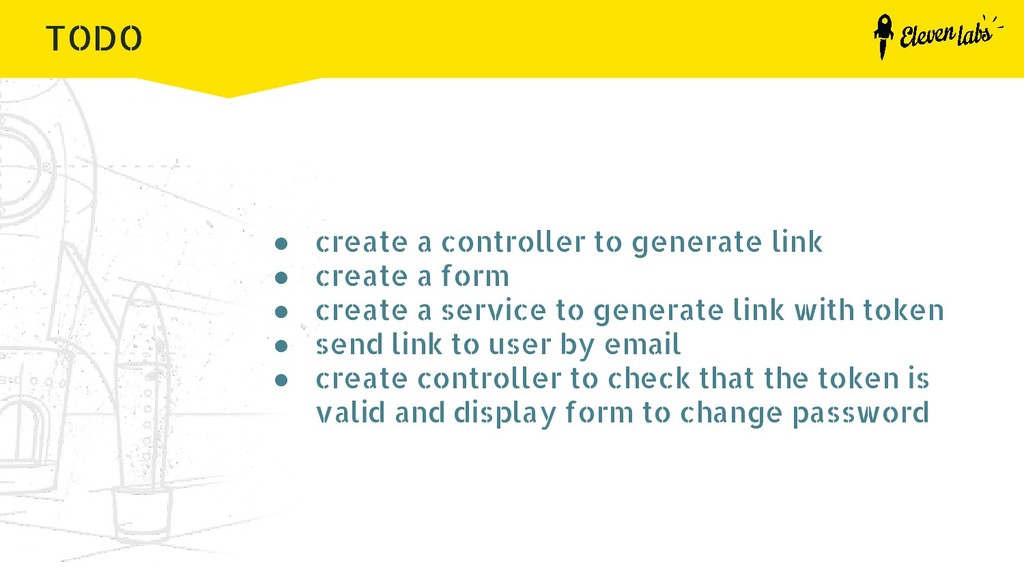
  1. TODO • create a controller to generate link • create

    a form • create a service to generate link with token • send link to user by email • create controller to check that the token is valid and display form to change password
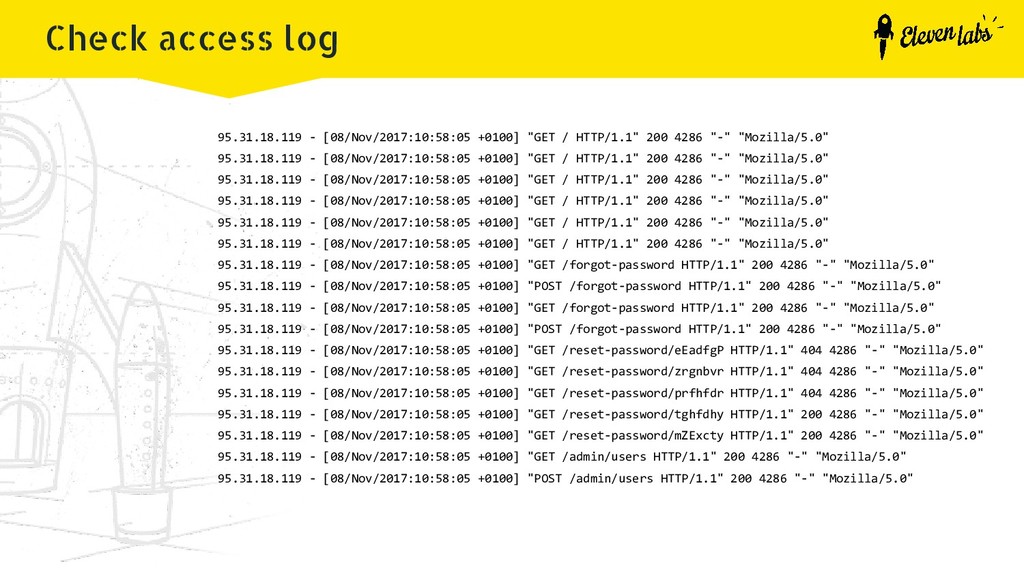
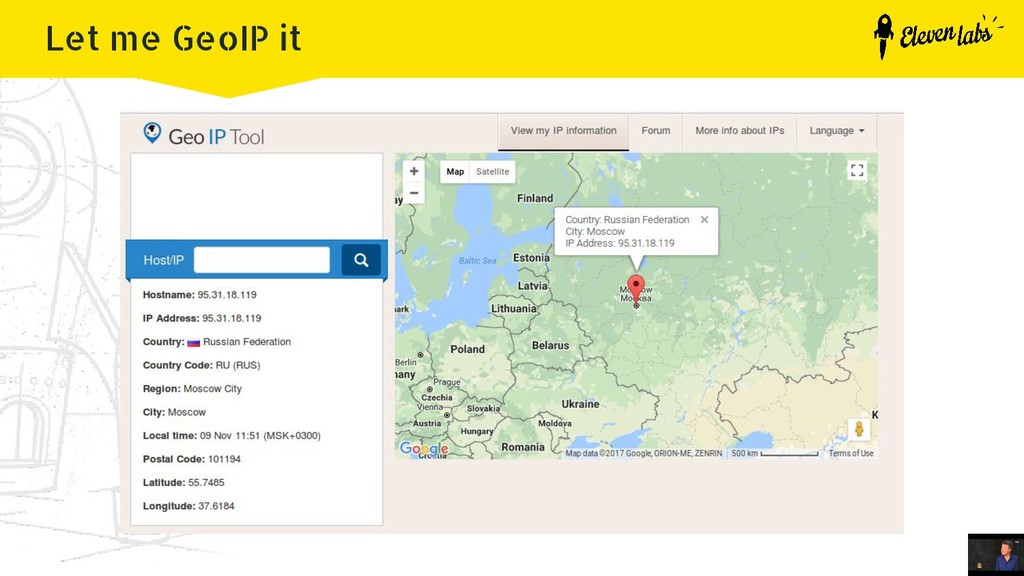
  2. Check access log 95.31.18.119 - [08/Nov/2017:10:58:05 +0100] "GET / HTTP/1.1"

    200 4286 "-" "Mozilla/5.0" 95.31.18.119 - [08/Nov/2017:10:58:05 +0100] "GET / HTTP/1.1" 200 4286 "-" "Mozilla/5.0" 95.31.18.119 - [08/Nov/2017:10:58:05 +0100] "GET / HTTP/1.1" 200 4286 "-" "Mozilla/5.0" 95.31.18.119 - [08/Nov/2017:10:58:05 +0100] "GET / HTTP/1.1" 200 4286 "-" "Mozilla/5.0" 95.31.18.119 - [08/Nov/2017:10:58:05 +0100] "GET / HTTP/1.1" 200 4286 "-" "Mozilla/5.0" 95.31.18.119 - [08/Nov/2017:10:58:05 +0100] "GET / HTTP/1.1" 200 4286 "-" "Mozilla/5.0" 95.31.18.119 - [08/Nov/2017:10:58:05 +0100] "GET /forgot-password HTTP/1.1" 200 4286 "-" "Mozilla/5.0" 95.31.18.119 - [08/Nov/2017:10:58:05 +0100] "POST /forgot-password HTTP/1.1" 200 4286 "-" "Mozilla/5.0" 95.31.18.119 - [08/Nov/2017:10:58:05 +0100] "GET /forgot-password HTTP/1.1" 200 4286 "-" "Mozilla/5.0" 95.31.18.119 - [08/Nov/2017:10:58:05 +0100] "POST /forgot-password HTTP/1.1" 200 4286 "-" "Mozilla/5.0" 95.31.18.119 - [08/Nov/2017:10:58:05 +0100] "GET /reset-password/eEadfgP HTTP/1.1" 404 4286 "-" "Mozilla/5.0" 95.31.18.119 - [08/Nov/2017:10:58:05 +0100] "GET /reset-password/zrgnbvr HTTP/1.1" 404 4286 "-" "Mozilla/5.0" 95.31.18.119 - [08/Nov/2017:10:58:05 +0100] "GET /reset-password/prfhfdr HTTP/1.1" 404 4286 "-" "Mozilla/5.0" 95.31.18.119 - [08/Nov/2017:10:58:05 +0100] "GET /reset-password/tghfdhy HTTP/1.1" 200 4286 "-" "Mozilla/5.0" 95.31.18.119 - [08/Nov/2017:10:58:05 +0100] "GET /reset-password/mZExcty HTTP/1.1" 200 4286 "-" "Mozilla/5.0" 95.31.18.119 - [08/Nov/2017:10:58:05 +0100] "GET /admin/users HTTP/1.1" 200 4286 "-" "Mozilla/5.0" 95.31.18.119 - [08/Nov/2017:10:58:05 +0100] "POST /admin/users HTTP/1.1" 200 4286 "-" "Mozilla/5.0"
  3. What’s wrong? The IT team asks the customer: - Is

    doge administrator’s here? He tries to access the platform. - No, he is in the Bahamas
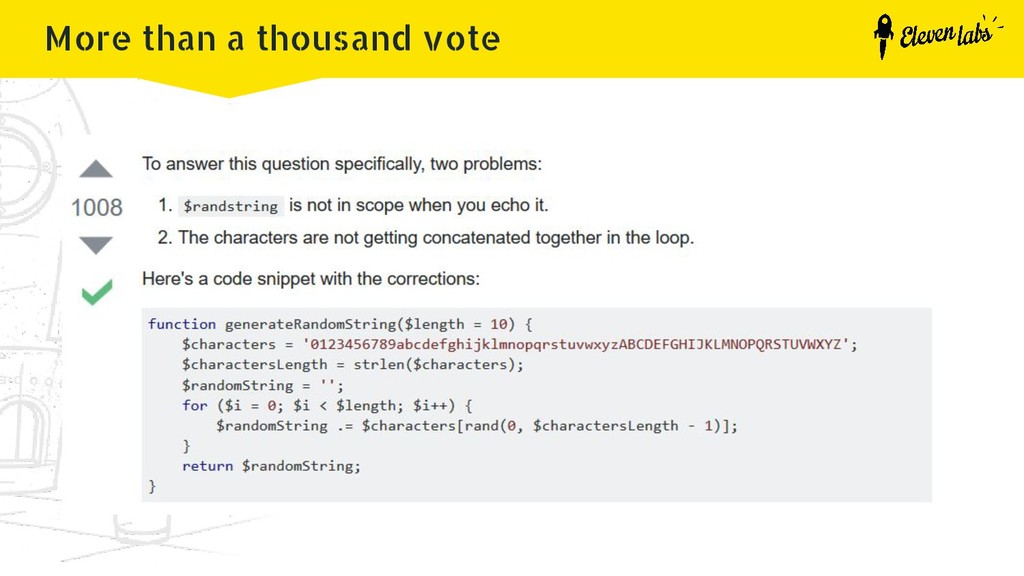
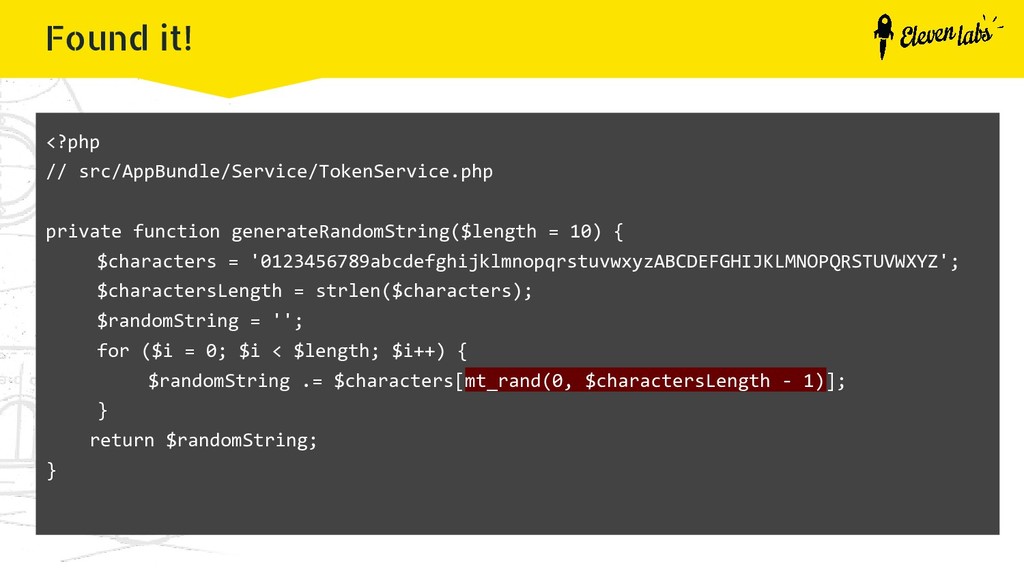
  4. Found it! <?php // src/AppBundle/Service/TokenService.php private function generateRandomString($length = 10)

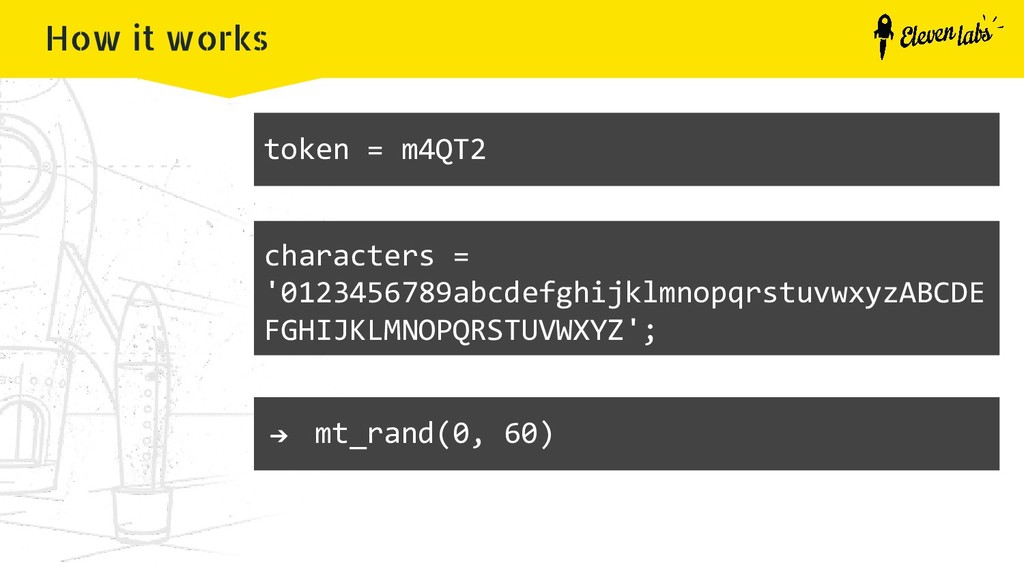
    { $characters = '0123456789abcdefghijklmnopqrstuvwxyzABCDEFGHIJKLMNOPQRSTUVWXYZ'; $charactersLength = strlen($characters); $randomString = ''; for ($i = 0; $i < $length; $i++) { $randomString .= $characters[mt_rand(0, $charactersLength - 1)]; } return $randomString; }
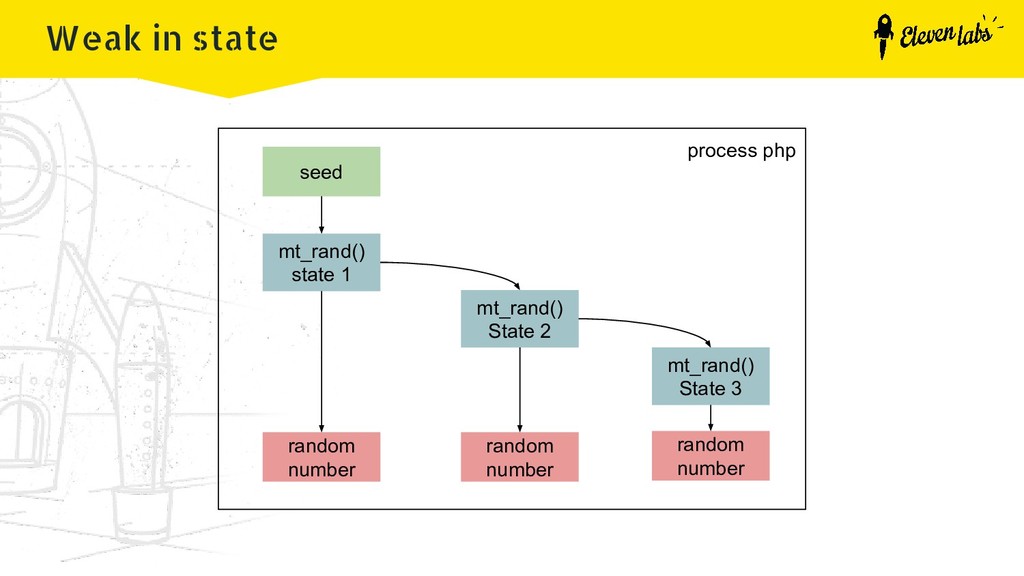
  5. Weak in state process php seed mt_rand() state 1 mt_rand()

    State 2 mt_rand() State 3 random number random number random number
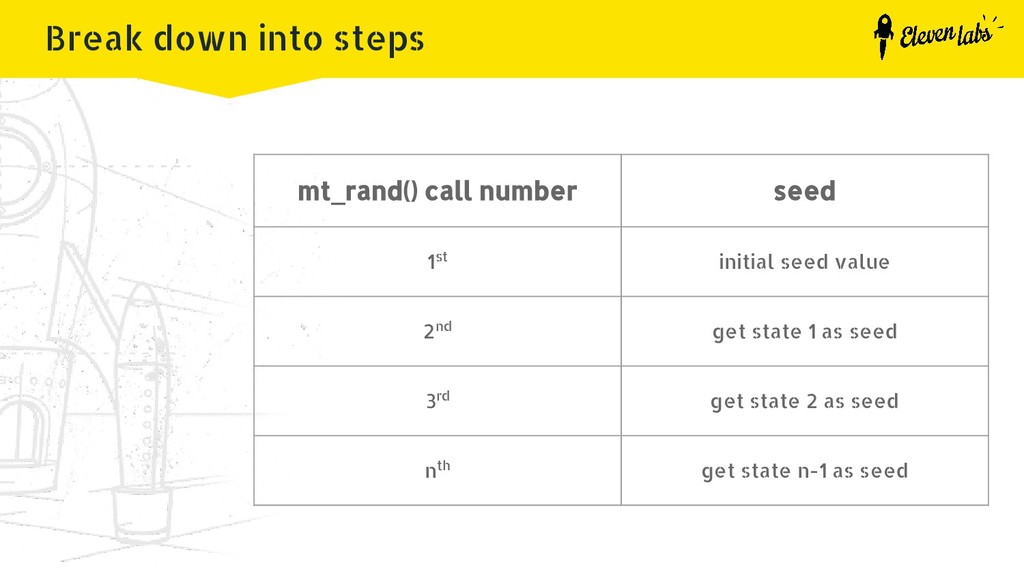
  6. Break down into steps mt_rand() call number seed 1st initial

    seed value 2nd get state 1 as seed 3rd get state 2 as seed nth get state n-1 as seed
  7. php_mt_seed Made by openwall (known for John the ripper) Re-implement

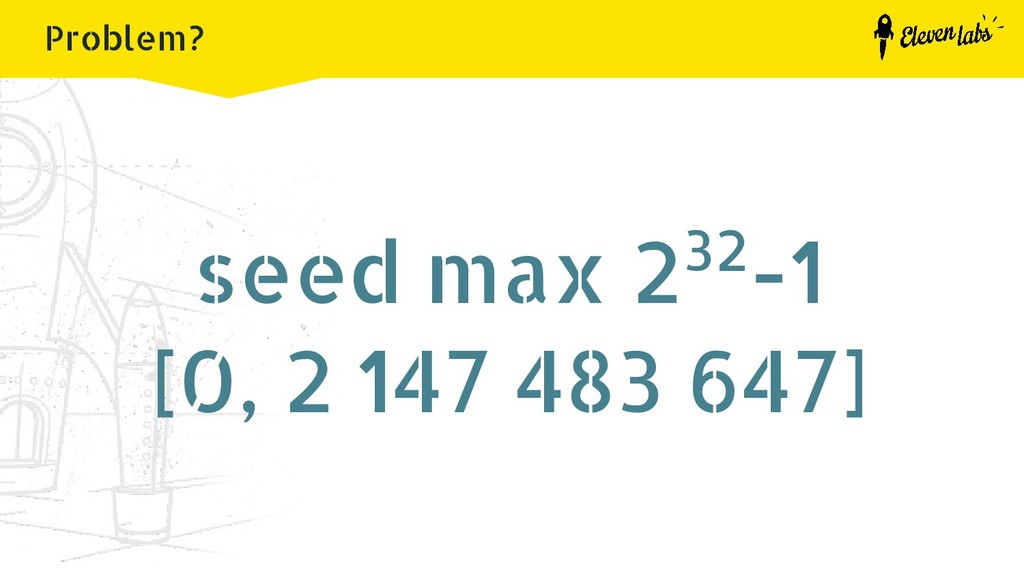
    mt_rand() in fast way Scan 32 bit space of seed
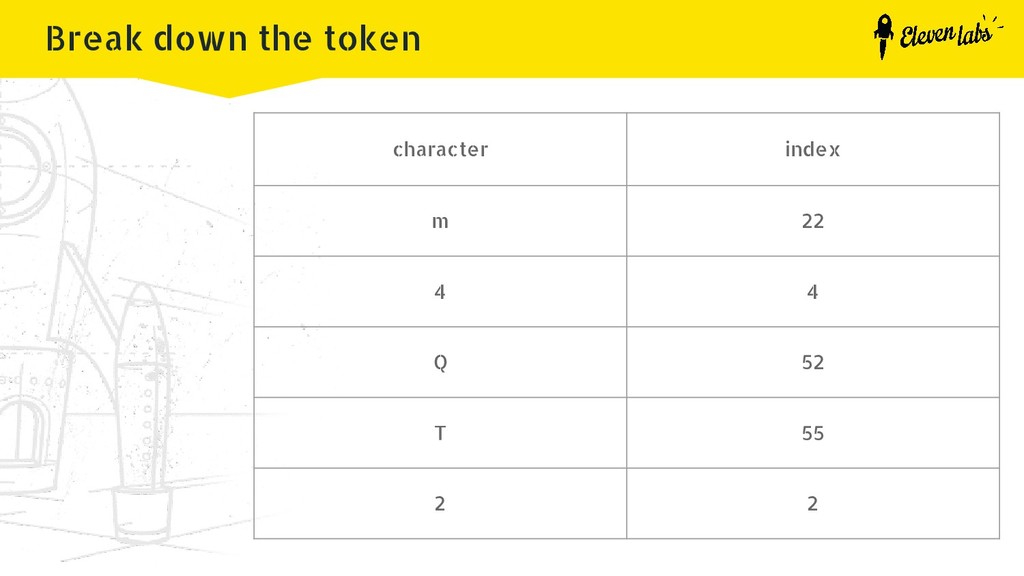
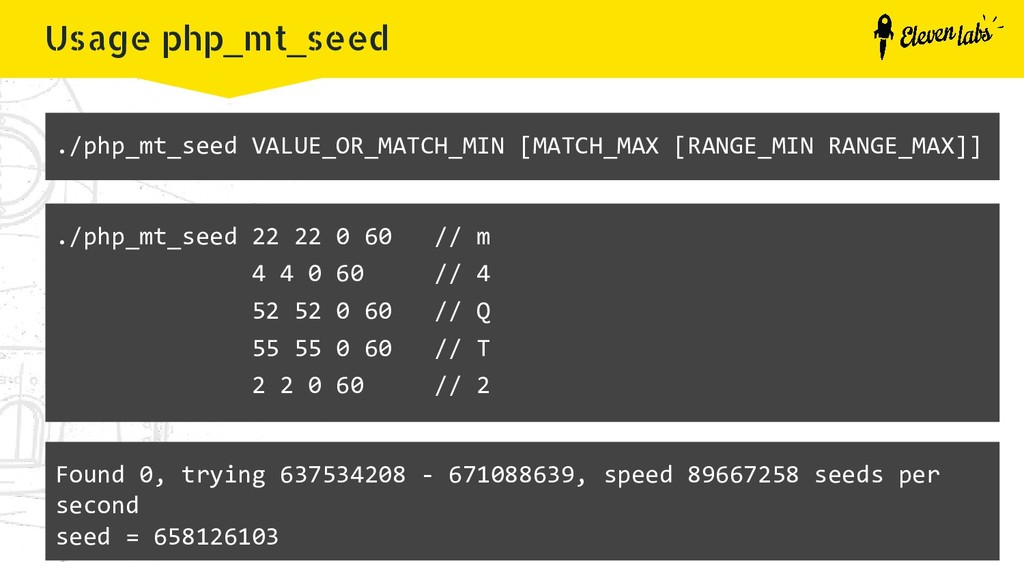
  8. Usage php_mt_seed ./php_mt_seed VALUE_OR_MATCH_MIN [MATCH_MAX [RANGE_MIN RANGE_MAX]] ./php_mt_seed 22 22

    0 60 // m 4 4 0 60 // 4 52 52 0 60 // Q 55 55 0 60 // T 2 2 0 60 // 2 Found 0, trying 637534208 - 671088639, speed 89667258 seeds per second seed = 658126103
  9. GOAL Take control of the admin account Demo scenario •

    Website with admin panel • Attacker has an user account
  10. Make some assumptions • Server Apache with PHP mod ➔

    Flood server to get fresh apache process
  11. Make some assumptions • How many calls of mt_rand() before

    generating token? ◦ We don’t know • We need to take it into account when using php_mt_seed
  12. Countermeasure - use CSPRNG function - in PHP 7: -

    use random_bytes() - use sodium_randombytes_buf() - include in PHP 7.2