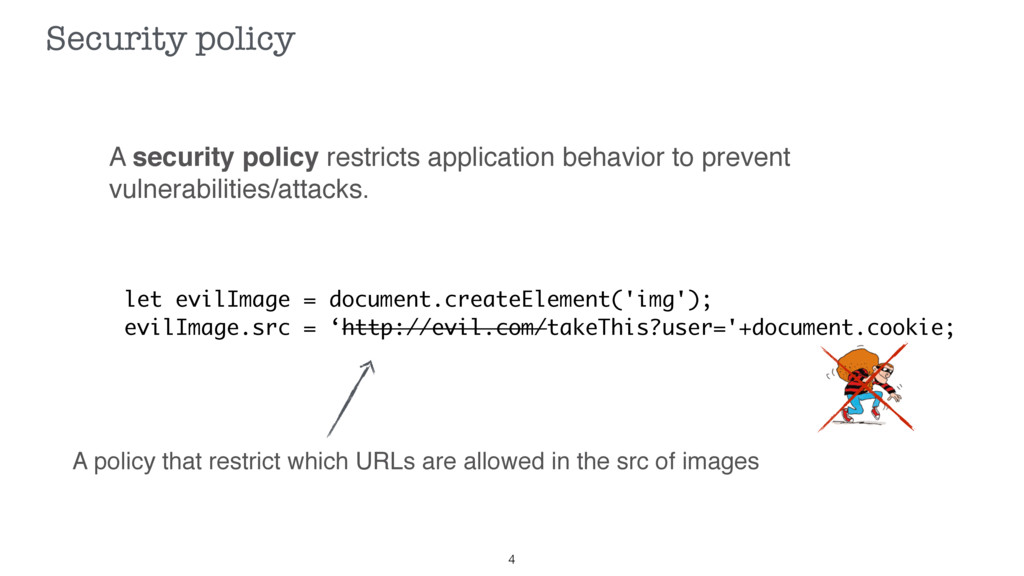
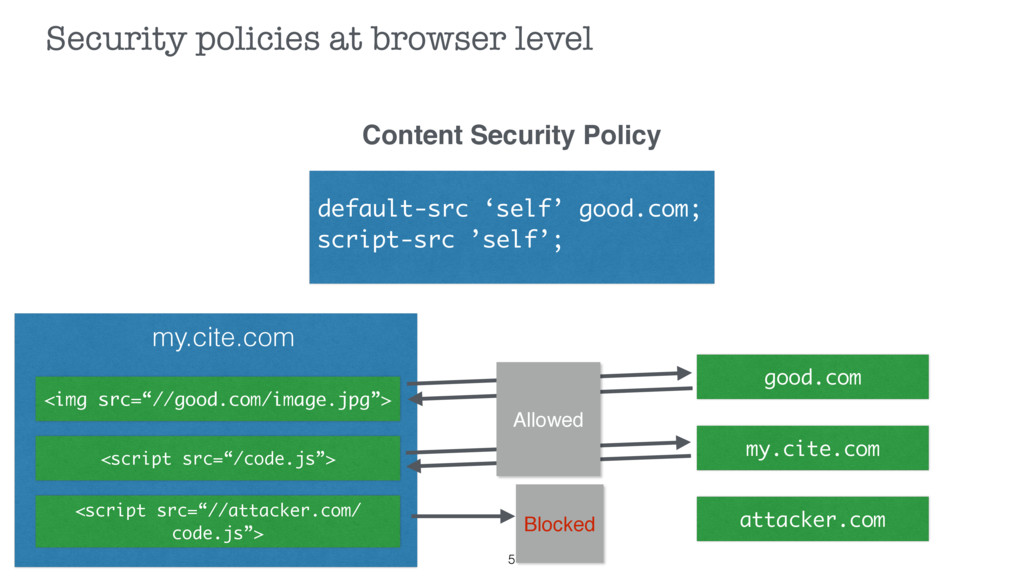
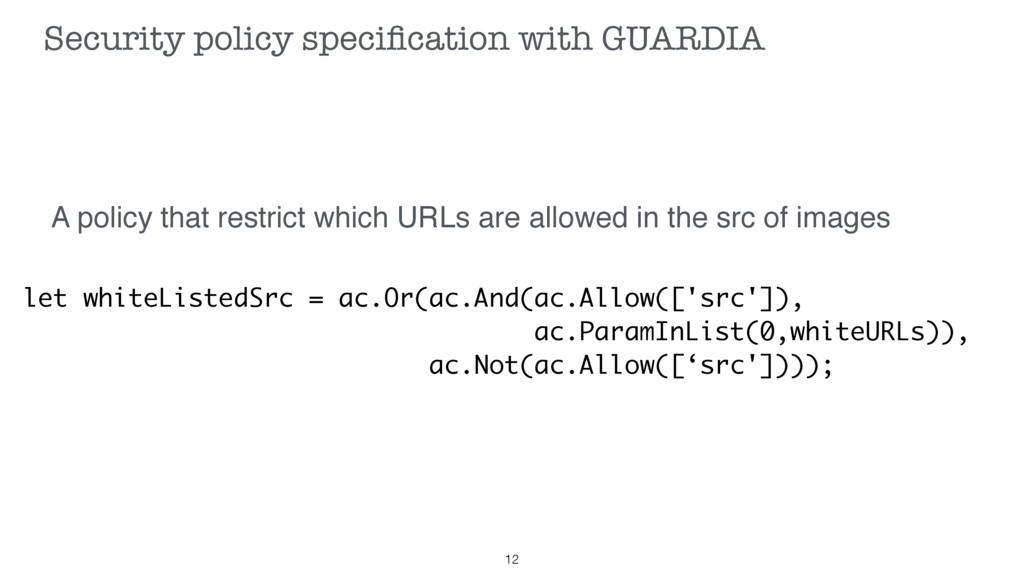
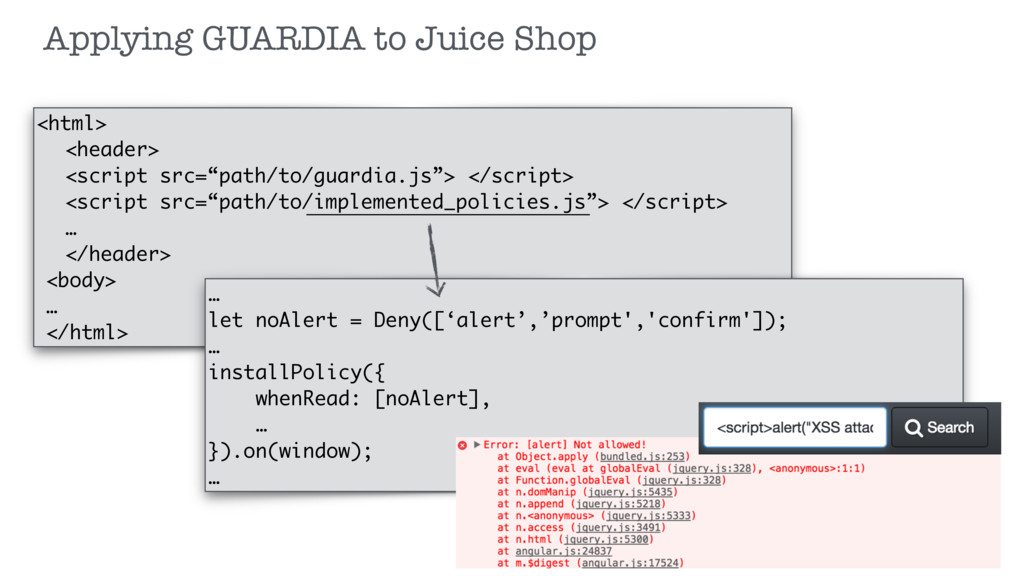
restrict which URLs are allowed in the src of images Security policy 4 A security policy restricts application behavior to prevent vulnerabilities/attacks.
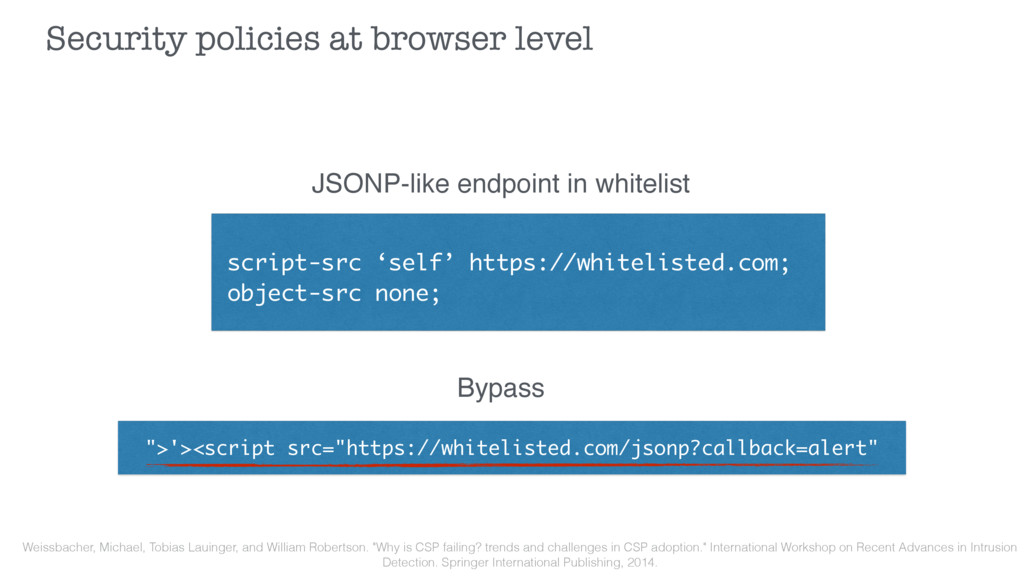
JSONP-like endpoint in whitelist ">'><script src="https://whitelisted.com/jsonp?callback=alert" Bypass Weissbacher, Michael, Tobias Lauinger, and William Robertson. "Why is CSP failing? trends and challenges in CSP adoption." International Workshop on Recent Advances in Intrusion Detection. Springer International Publishing, 2014.
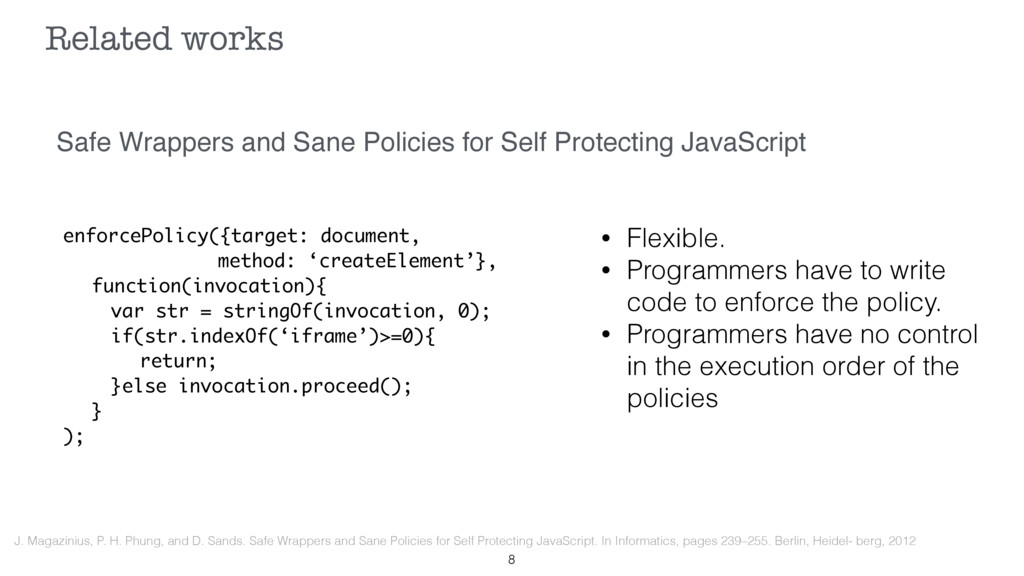
0); if(str.indexOf(‘iframe’)>=0){ return; }else invocation.proceed(); } ); Related works J. Magazinius, P. H. Phung, and D. Sands. Safe Wrappers and Sane Policies for Self Protecting JavaScript. In Informatics, pages 239–255. Berlin, Heidel- berg, 2012 • Flexible. • Programmers have to write code to enforce the policy. • Programmers have no control in the execution order of the policies Safe Wrappers and Sane Policies for Self Protecting JavaScript
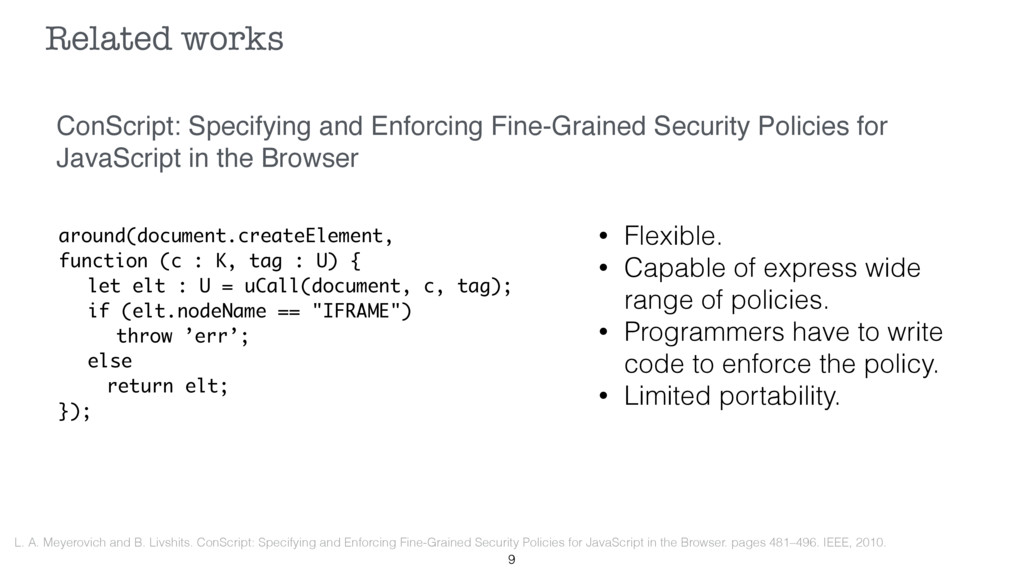
let elt : U = uCall(document, c, tag); if (elt.nodeName == "IFRAME") throw ’err’; else return elt; }); Related works L. A. Meyerovich and B. Livshits. ConScript: Specifying and Enforcing Fine-Grained Security Policies for JavaScript in the Browser. pages 481–496. IEEE, 2010. • Flexible. • Capable of express wide range of policies. • Programmers have to write code to enforce the policy. • Limited portability. ConScript: Specifying and Enforcing Fine-Grained Security Policies for JavaScript in the Browser
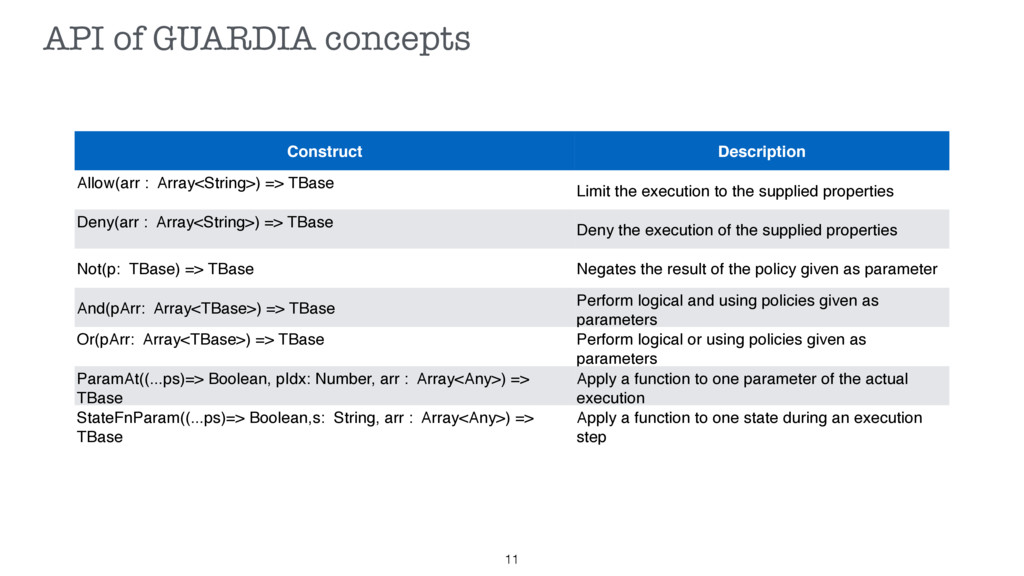
to the supplied properties Deny(arr : Array<String>) => TBase Deny the execution of the supplied properties Not(p: TBase) => TBase Negates the result of the policy given as parameter And(pArr: Array<TBase>) => TBase Perform logical and using policies given as parameters Or(pArr: Array<TBase>) => TBase Perform logical or using policies given as parameters ParamAt((...ps)=> Boolean, pIdx: Number, arr : Array<Any>) => TBase Apply a function to one parameter of the actual execution StateFnParam((...ps)=> Boolean,s: String, arr : Array<Any>) => TBase Apply a function to one state during an execution step API of GUARDIA concepts 11
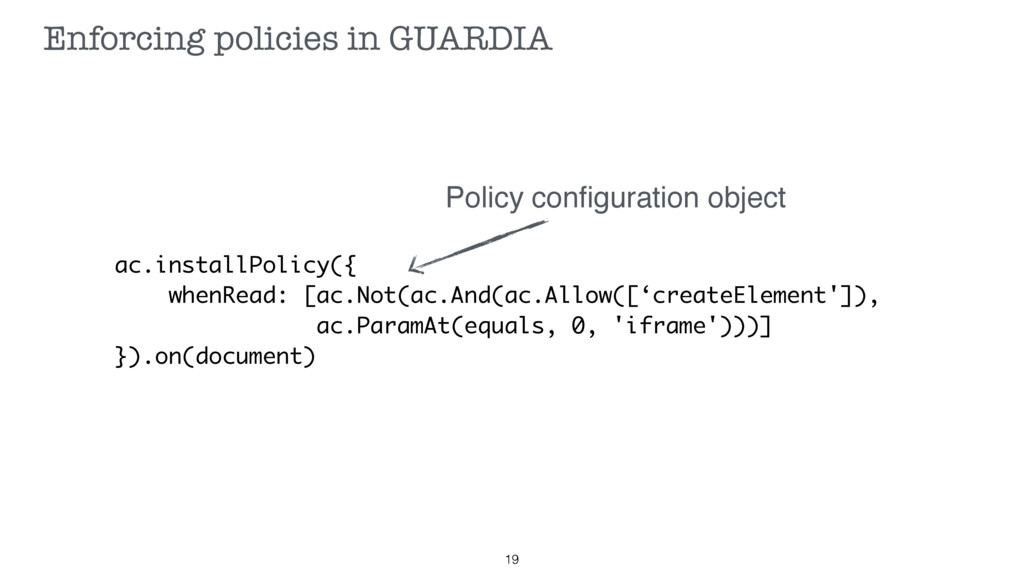
src of images Security policy specification with GUARDIA 12 let whiteListedSrc = ac.Or(ac.And(ac.Allow(['src']), ac.ParamInList(0,whiteURLs)), ac.Not(ac.Allow([‘src'])));
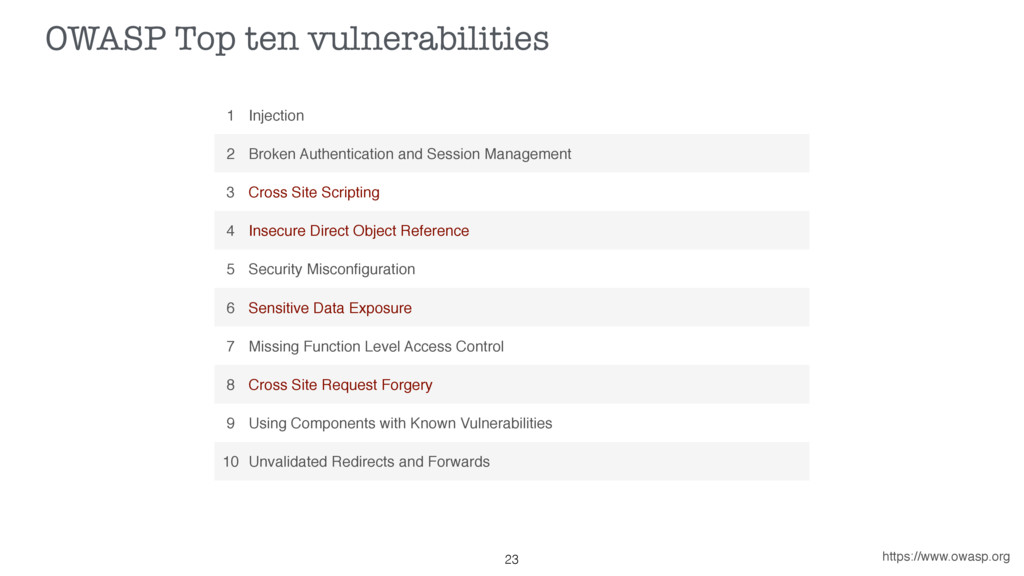
Site Scripting 4 Insecure Direct Object Reference 5 Security Misconfiguration 6 Sensitive Data Exposure 7 Missing Function Level Access Control 8 Cross Site Request Forgery 9 Using Components with Known Vulnerabilities 10 Unvalidated Redirects and Forwards https://www.owasp.org OWASP Top ten vulnerabilities 23
Phung et al. [20] ML [15] GUARDIA Forgery Limited number of popup windows opened (P1) 3 3 3 3 3 Forgery No popup windows without location and status bar 3 3 Resource abuse Prevent abuse of resources like modal dialogues (P2) 3 3 3 3 Restoring built-ins from frames Disallow dynamic iframe creation (P3) 3 3 3 Information leakage Disabling page redirects after document.cookie read (P4) 3 3 3 3 3 Information leakage Allowing redirections for a whitelist of URLs (P5) 3 3 3 Information leakage Restrict XMLHttpRequest to secure connections and whitelist URLs (P6) 3 3 Information leakage Disallow setting of src property 3 3 Information leakage Disallow setting of location property 3 3 3 Impersonation XMLHttpRequest is restricted to HTTPS connections (P6) 3 3 Impersonation / Information leakage Disallow open and send methods of XHR object 3 3 3 Man in the middle postMessage can only send to the origins in a whitelist (P7) 3 3 Run arbitrary code*(fix) Disallow string arguments to setInterval & setTimeout (P8) 3 3 Table 1. Comparison of approaches in security policies. Policy numbers P1 to P8 refer to the policies discussed in section 4. Results 24
applications. GUARDIA is agnostic of the underlying enforcement mechanism. GUARDIA is able to express wide range of security policies from related literature. 28


 meta
 gpeyre
 datascientistsociety
 shunk031
 asuna_jp
 kanekomasahiro
 rfujii
 kobayashi31
 kinoue_smarthr
 ayaniwa
 rikkabotan7
 stktu
 mikimhk
 shpigford
 jacobian
 zakiyama
 katiecoart
 aleyda
 uxyall
 cargoodrich
 skipperchong
 brad_frost
 ammeep
 honzajavorek
 sarafernandez