Upgrade to Pro
— share decks privately, control downloads, hide ads and more …
Speaker Deck
Sign up for free
Menu
Search
Features
All features
Private URLs
Password Protection
Custom URLS
Scheduled publishing
Remove Branding
Restrict embedding
Deck Collections
Notes
Features
All features
Private URLs
Password Protection
Custom URLS
Scheduled publishing
Remove Branding
Restrict embedding
Deck Collections
Notes
Explore
Featured decks
Featured speakers
Programming
Technology
Storyboards
Explore
Featured decks
Featured speakers
Programming
Technology
Storyboards
Pricing
Search
Sign in
Sign up for free
Intro to OAuth
Search
Frost
May 23, 2014
Technology
630
0
Share
Embed
Copy iframe code
Copy JS code
Copy link
Start on current slide
Intro to OAuth
Introduction to OAuth talk, given at PHP[tek] 2014
Frost
May 23, 2014
Transcript
100 slides
Intro to OAuth Matt Frost @shrtwhitebldguy https://joind.in/10630
Who Am I? • Senior Engineer - Synacor • Author
• OSS Contributor • Mentoring Proponent • Podcast co-host
What is OAuth?
None
Tokens
Statelessness
Applications have tokens too
So what you’re saying is…
Yep!
Tokens can be stolen though
This is bad
Good news though!
There are different versions
Technically OAuth 1 is deprecated
Just like the mysql extension You’re probably going to run
into it at some point anyway….
So here’s the plan
None
OAuth 1.0 Client
So we need tokens, right?
Token Definitions
Consumer Tokens
Temporary Credentials
Access Tokens
Token Request Flow
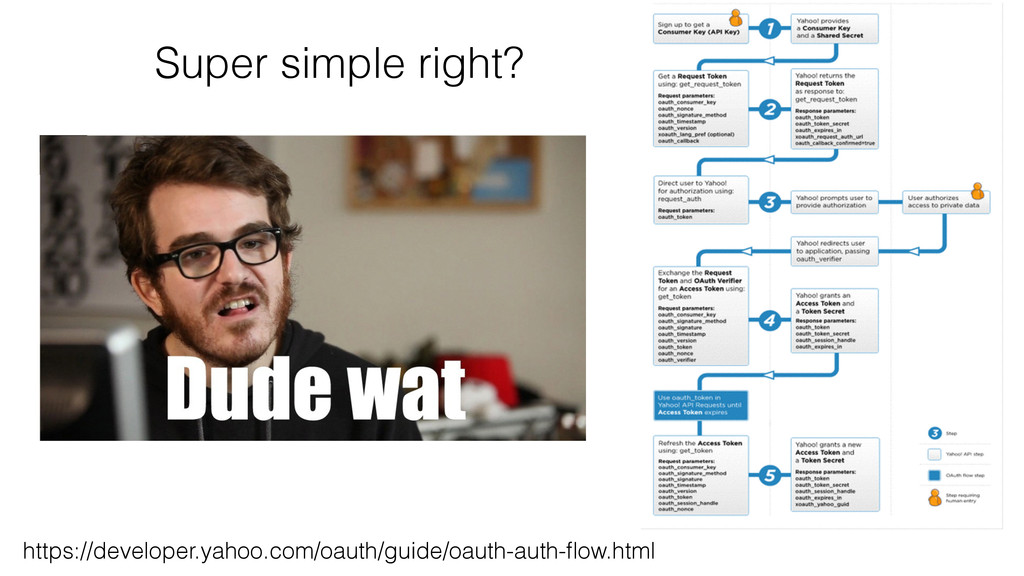
Super simple right? https://developer.yahoo.com/oauth/guide/oauth-auth-flow.html
Let’s break this down, eh?
You need an application
Request the temporary tokens
If you signed it right…
You’ll have temporary credentials
You now use these to request Access Tokens
If you sign that request right…
You’ll have your actual Access Tokens!
You can store them in a session or database and
use them now!
Remember all that signing talk?
This is the hardest part…
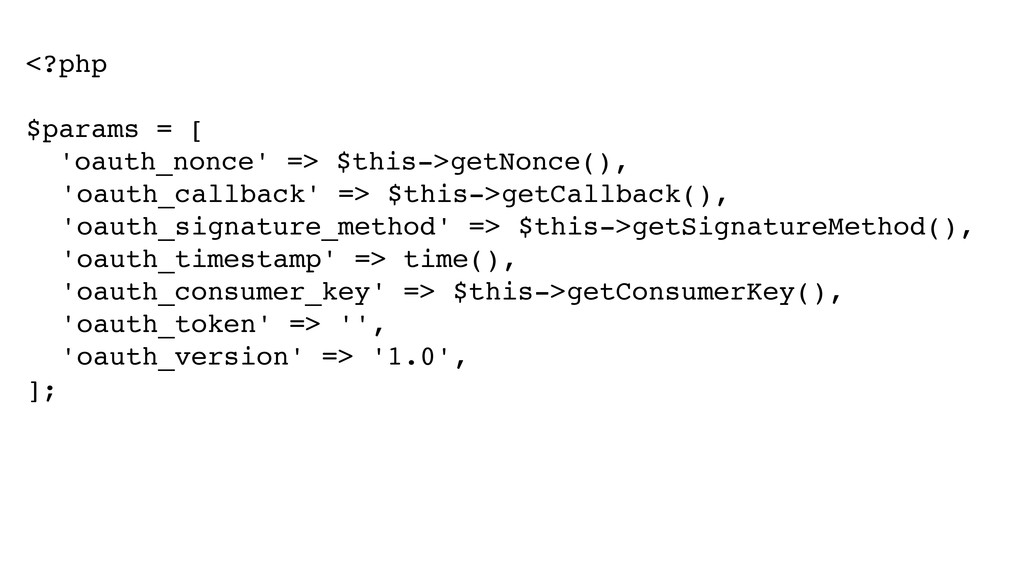
Base String
<?php! ! $params = [! 'oauth_nonce' => $this->getNonce(),! ! 'oauth_callback'
=> $this->getCallback(),! ! 'oauth_signature_method' => $this->getSignatureMethod(),! ! 'oauth_timestamp' => time(),! ! 'oauth_consumer_key' => $this->getConsumerKey(),! ! 'oauth_token' => '',! ! 'oauth_version' => '1.0',! ];
HTTP Method and URI
Let’s see how this actually works
<?php! $httpMethod = 'POST';! $uri = ‘http://api.example.com/request_tokens';! ! $params =
[! 'oauth_nonce' => $this->getNonce(),! 'oauth_callback' => $this->getCallback(),! 'oauth_signature_method' => $this->getSignatureMethod(),! 'oauth_timestamp' => time(),! ‘oauth_consumer_key' => $this->getConsumerKey(),! 'oauth_token' => ‘',! 'oauth_version' => '1.0',! ];! ! $tempArray = [];! ksort($params);! foreach($params as $key => $value) {! ! $tempArray = $key . '=' . rawurlencode($value);! }! ! $baseString = $httpMethod . '&';! $baseString .= rawurlencode($uri) . '&';! $baseString .= implode('&', $tempArray);
Composite Key This is way easier…
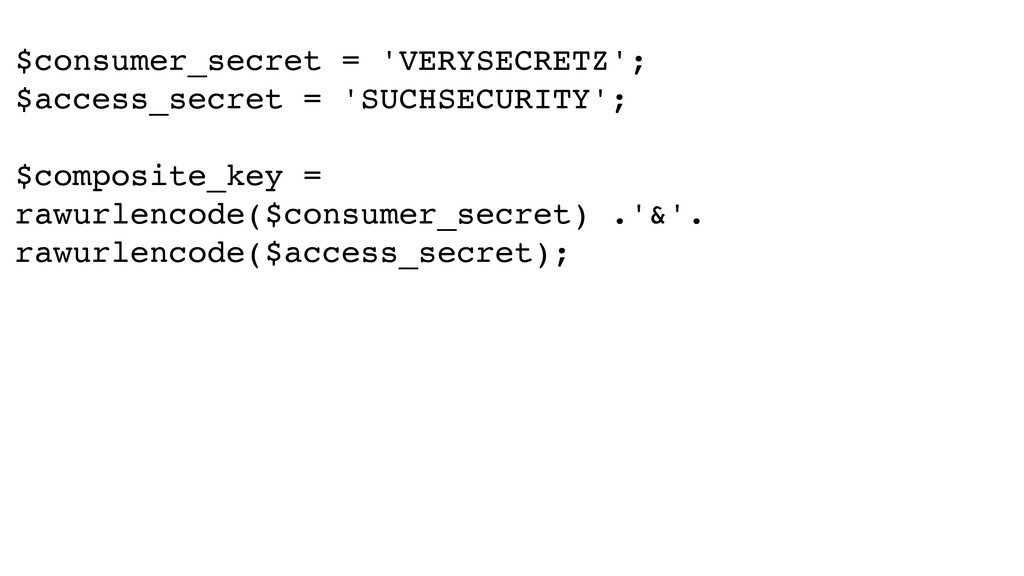
Cram the 2 secrets together…
$consumer_secret = 'VERYSECRETZ';! $access_secret = 'SUCHSECURITY';! ! $composite_key = rawurlencode($consumer_secret)
.'&'. rawurlencode($access_secret);
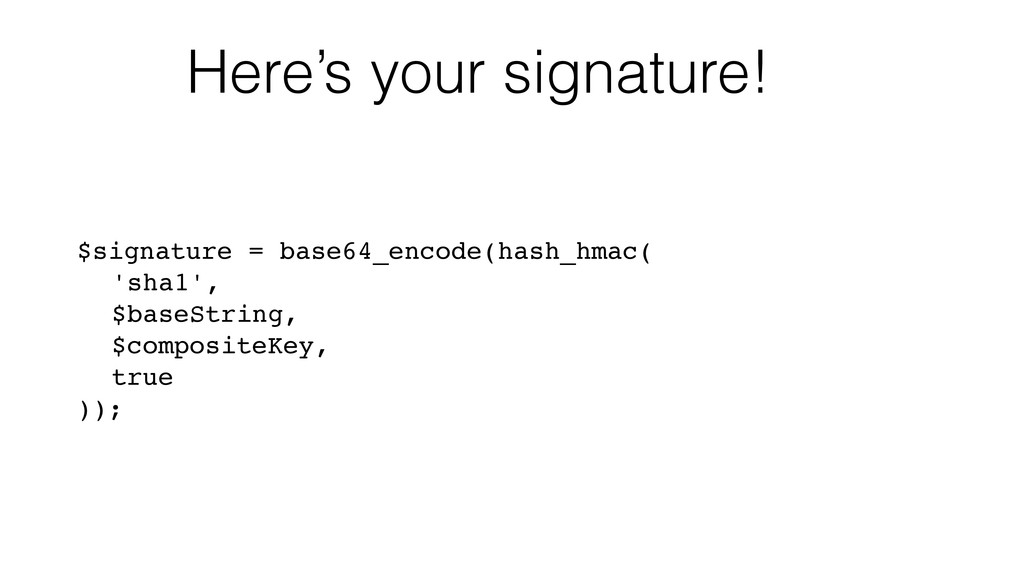
Signing with HMAC-SHA1
$signature = base64_encode(hash_hmac(! ! 'sha1',! ! $baseString,! ! $compositeKey,! !
true! )); Here’s your signature!
There are other signature types but…
However…
None
Authorization Header
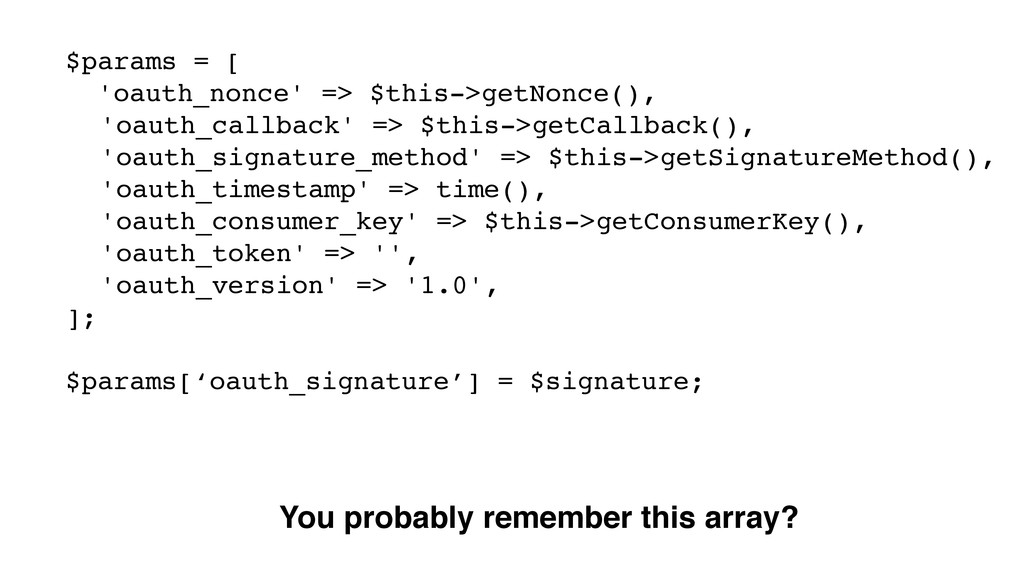
$params = [! 'oauth_nonce' => $this->getNonce(),! ! 'oauth_callback' => $this->getCallback(),!
! 'oauth_signature_method' => $this->getSignatureMethod(),! ! 'oauth_timestamp' => time(),! ! 'oauth_consumer_key' => $this->getConsumerKey(),! ! 'oauth_token' => '',! ! 'oauth_version' => '1.0',! ];! ! $params[‘oauth_signature’] = $signature; You probably remember this array?
$header = “Authorization: OAuth “;! $tempArray = [];! ! foreach($params
as $key => $value) {! $tempArray[] = $key . ‘=“‘. rawurlencode($value);! }! ! $header .= implode(‘,’, $tempArray);! We’ve seen similar code before…
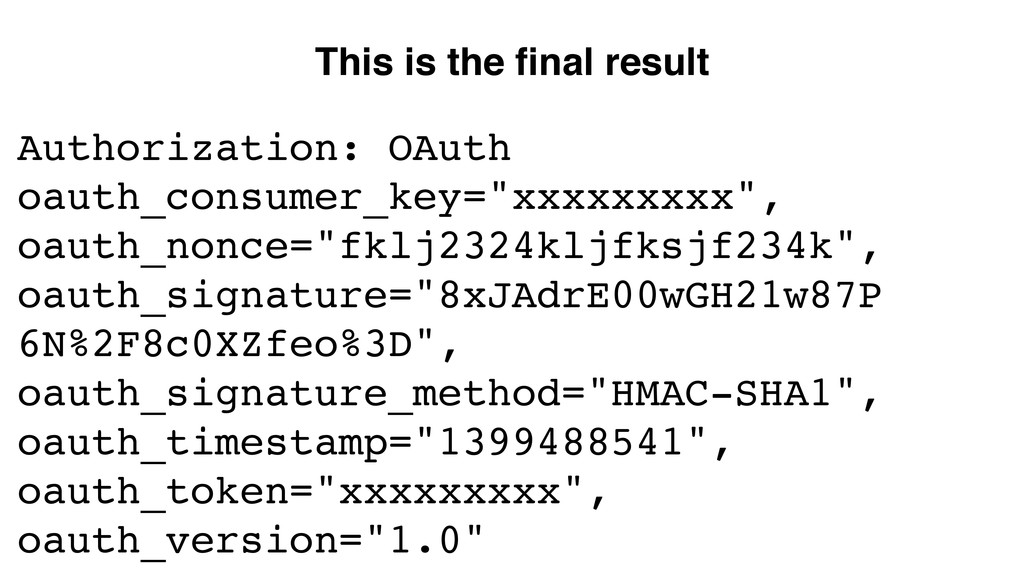
Authorization: OAuth oauth_consumer_key="xxxxxxxxx", oauth_nonce="fklj2324kljfksjf234k", oauth_signature="8xJAdrE00wGH21w87P 6N%2F8c0XZfeo%3D", oauth_signature_method="HMAC-SHA1", oauth_timestamp="1399488541", oauth_token="xxxxxxxxx", oauth_version="1.0"
This is the final result
Whew! That was some work
OAuth 1.0 Server
Token Generation
Recreate the signature with the info you received
If they match, they win!
If not…
None
Access Control…
OAuth 2 Client
Good news!
No signatures
Must use SSL/TLS
Consumer Credentials
Access Token
Grants
Authorization Code Grant
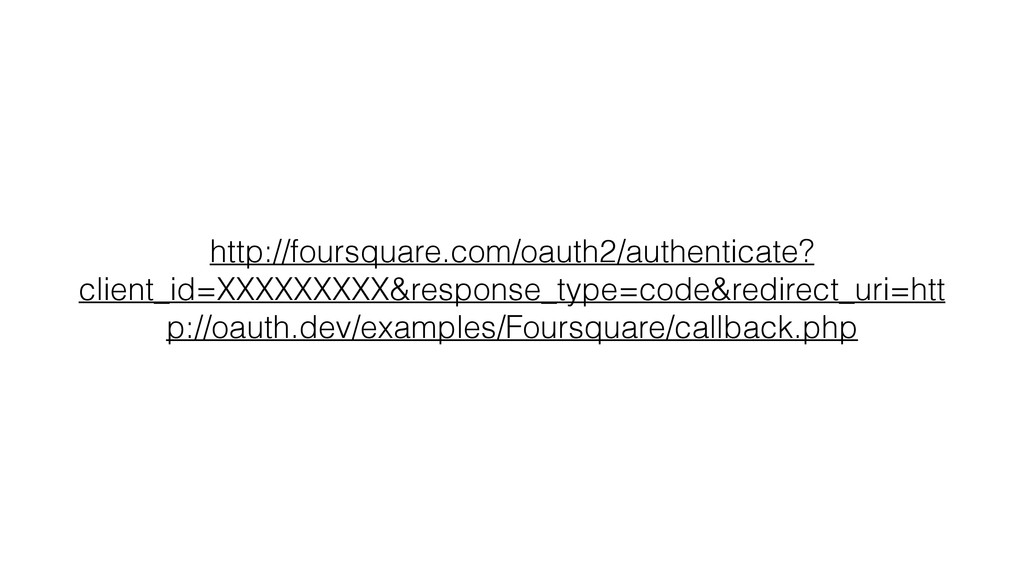
Authorization example - Foursquare
http://foursquare.com/oauth2/authenticate? client_id=XXXXXXXXX&response_type=code&redirect_uri=htt p://oauth.dev/examples/Foursquare/callback.php
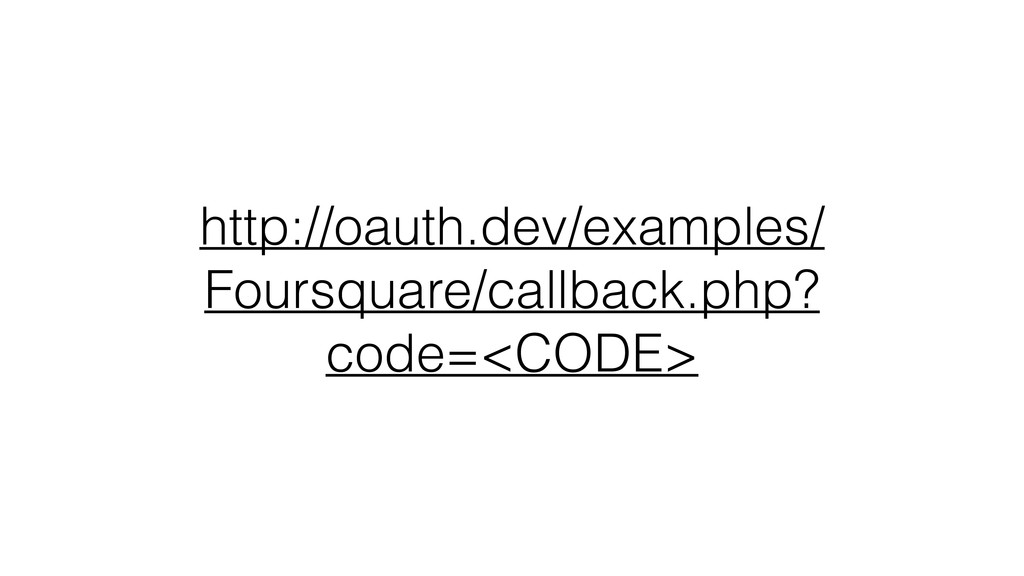
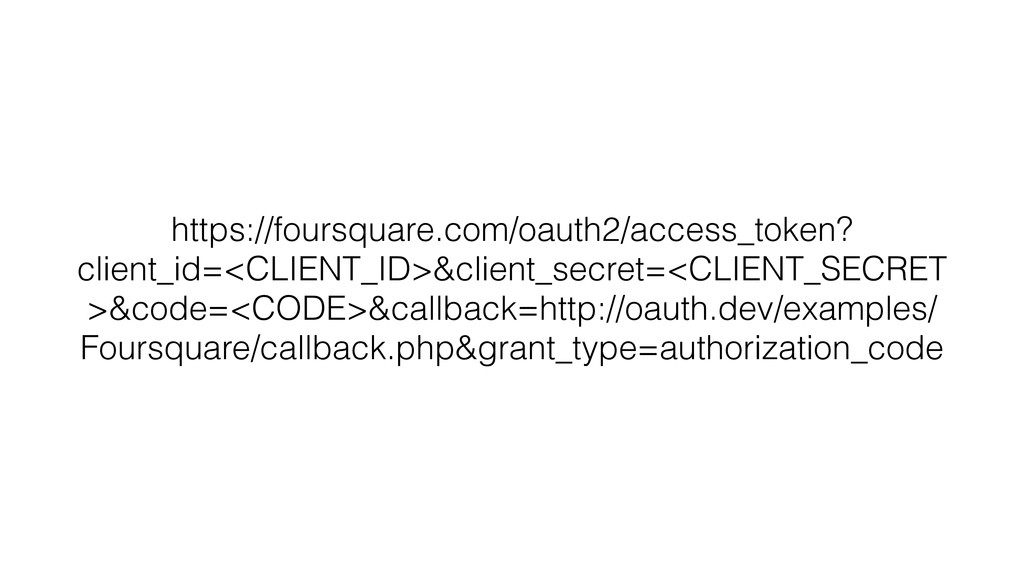
Token Request
http://oauth.dev/examples/ Foursquare/callback.php? code=<CODE>
https://foursquare.com/oauth2/access_token? client_id=<CLIENT_ID>&client_secret=<CLIENT_SECRET >&code=<CODE>&callback=http://oauth.dev/examples/ Foursquare/callback.php&grant_type=authorization_code
If you can use this, you should
Implicit Grant
http://foursquare.com/oauth2/authenticate? client_id=XXXXXXXXX&response_type=token&redirect_uri=ht tp://oauth.dev/examples/Foursquare/callback.php
Resource Owner Credentials Grant
Client Credentials Grant
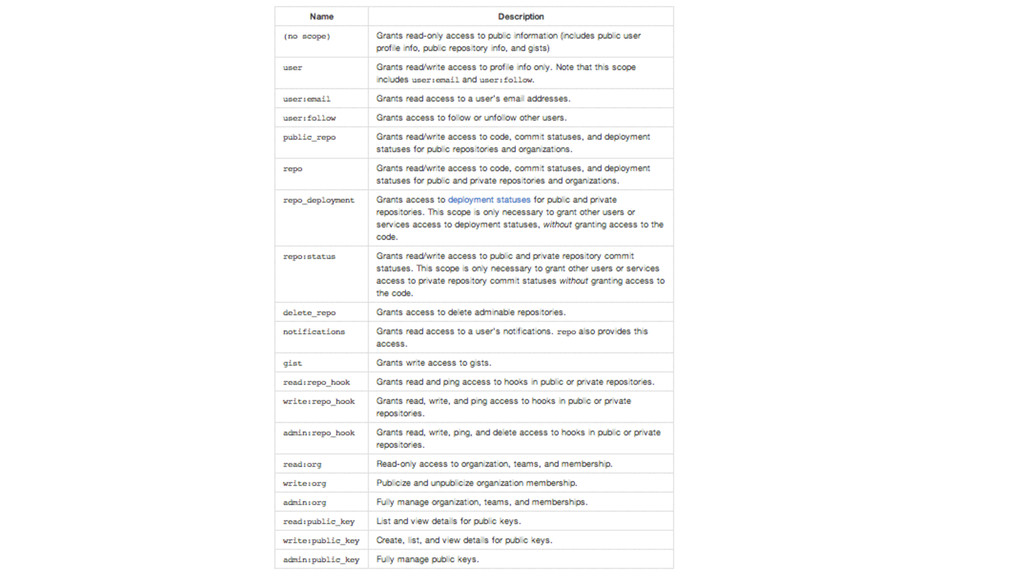
Scopes
“Scopes” in OAuth 1
Scopes in OAuth 2
None
Important Note on Scopes
Provides an ACL Framework
Refresh Tokens
Same Scope
OAuth 2 Server
Issuing Tokens
Should I Support All The Grants?
Maybe…
Authorization/Implicit Grants
Storing Token Info
Scopes
Reading Tokens
Query String, Header, Both?
A Caution Against Rolling Your Own
RFCs OAuth 1 RFC 5849 - http://tools.ietf.org/html/rfc5849 OAuth 2 RFC
6749 - http://tools.ietf.org/html/rfc6749
Questions?
Thank you! Matt Frost @shrtwhitebldguy https://joind.in/10630
More Decks by Frost
See All by Frost
Mocking Dependencies in PHPUnit
mfrost503
0
440
Mocking Dependencies in PHPUnit
mfrost503
1
460
Other Decks in Technology
See All in Technology
DevOps Agentにあらゆるセキュリティインシデントのトリアージを任せた件
jirtosterone
1
150
【Oracle AI SPOTLIGHT ウェビナー】【特別開催:日本語で解説!】Oracle AI World 2026 最新情報フィードバック
oracle4engineer
PRO
1
220
Kiro CLI 入門 (ターミナルと CI で使う) | 目指せ Kiro マスター 03
inariku
PRO
2
150
仕様と現実の間で落とし所を探るリモートMCPの認証・認可 — Sansanの認証基盤における課題と実践
sansantech
PRO
2
300
AI対話型分析を作成し、リリースするまでの話 / The Road to Release: Buiding AI Conversational Analytics
yappli_developers
0
130
顧客合意を取りながら進めるAWSコスト削減の実践
optim
0
170
狙われているAPIの脆弱性!今こそ手をつけるべき根本的な対策とは?
nagix
0
130
落とし穴にハマってわかった 開発生産性を測るときに気をつけたいこと
munakata
2
180
長い仕事を任せる (Workflows、クラウドセッション、Kiro Web) | 目指せ Kiro マスター 10
inariku
PRO
3
190
Kiro を使うコツ (頼み方、覚えさせ方、任せ方) | 目指せ Kiro マスター 09
inariku
PRO
3
160
MCPでネットワーク障害調査を自動化する前に直すべき3つのこと
yama3133
0
220
Context != Context: One window, many lifecycles (AI Native DevCon, Nov 2026)
birgitta410
0
140
Featured
See All Featured
Cheating the UX When There Is Nothing More to Optimize - PixelPioneers
stephaniewalter
287
14k
A Tale of Four Properties
chriscoyier
163
24k
How STYLIGHT went responsive
nonsquared
100
6.4k
HDC tutorial
michielstock
2
1k
Save Time (by Creating Custom Rails Generators)
garrettdimon
PRO
33
5.7k
10 Git Anti Patterns You Should be Aware of
lemiorhan
PRO
659
62k
The Spectacular Lies of Maps
axbom
PRO
1
1.1k
Leading Effective Engineering Teams in the AI Era
addyosmani
9
2.9k
Measuring & Analyzing Core Web Vitals
bluesmoon
9
1.1k
Public Speaking Without Barfing On Your Shoes - THAT 2023
reverentgeek
1
660
The Limits of Empathy - UXLibs8
cassininazir
2
780
The Cult of Friendly URLs
andyhume
79
7.1k


 mfrost503
 jirtosterone
 oracle4engineer
 inariku
 sansantech
 yappli_developers
 optim
 nagix
 munakata
 yama3133
 birgitta410
 stephaniewalter
 chriscoyier
 nonsquared
 michielstock
 garrettdimon
 lemiorhan
 axbom
 addyosmani
 bluesmoon
 reverentgeek
 cassininazir
 andyhume