Share
Embed
Continuous Code Quality Inspection
Ulugbek Miniyarov
November 16, 2017
Transcript
17 slides
-
What DEFINES Code Quality? 1. Software should be able to
perform all its functionality as expected (defined in acceptance criteria). 2. Software should meet all non-functional “abilities” (like scalability, reliability etc). 3. Code quality should be great with minimal technical debt. Ground term for Code Quality: “Code quality is an indicator of how quickly a developer can add business value to a software system” -
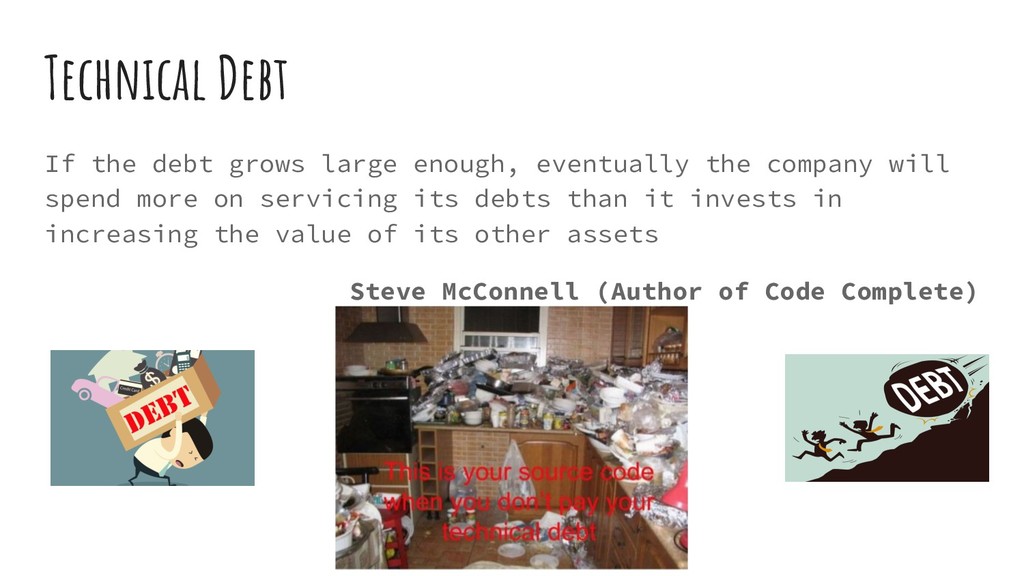
Technical Debt If the debt grows large enough, eventually the
company will spend more on servicing its debts than it invests in increasing the value of its other assets Steve McConnell (Author of Code Complete) -
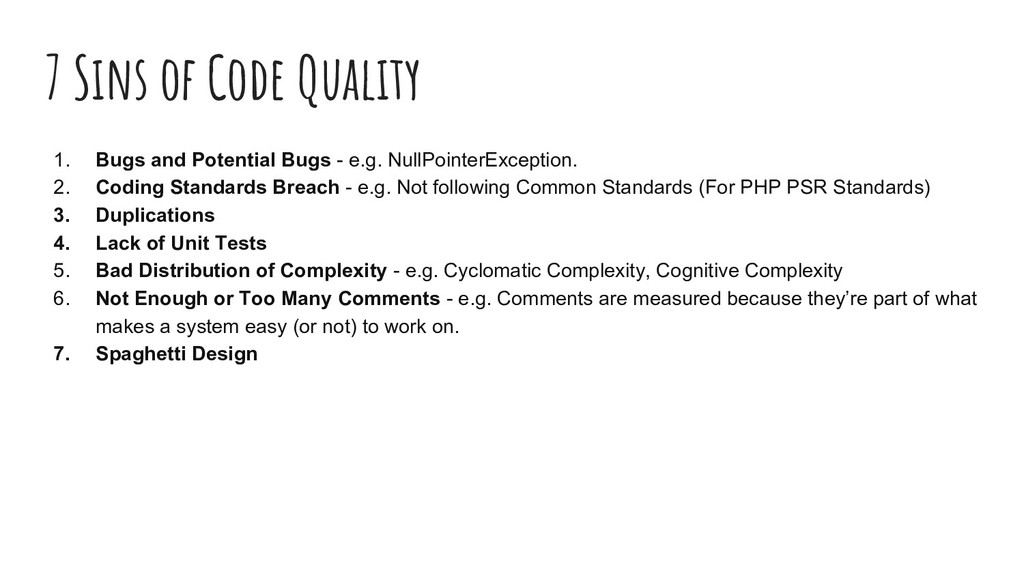
7 Sins of Code Quality 1. Bugs and Potential Bugs
- e.g. NullPointerException. 2. Coding Standards Breach - e.g. Not following Common Standards (For PHP PSR Standards) 3. Duplications 4. Lack of Unit Tests 5. Bad Distribution of Complexity - e.g. Cyclomatic Complexity, Cognitive Complexity 6. Not Enough or Too Many Comments - e.g. Comments are measured because they’re part of what makes a system easy (or not) to work on. 7. Spaghetti Design -
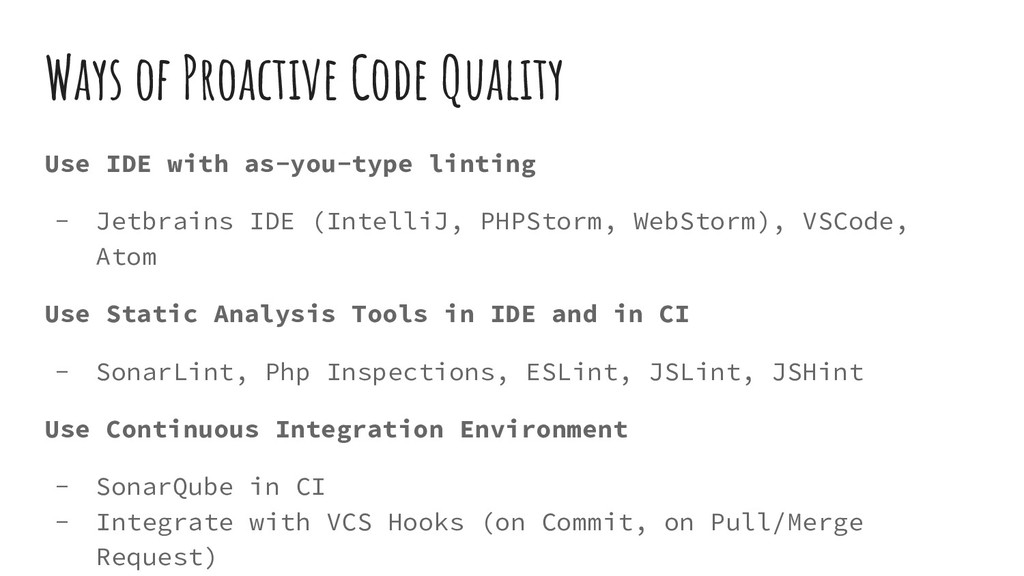
Ways of Proactive Code Quality Use IDE with as-you-type linting
- Jetbrains IDE (IntelliJ, PHPStorm, WebStorm), VSCode, Atom Use Static Analysis Tools in IDE and in CI - SonarLint, Php Inspections, ESLint, JSLint, JSHint Use Continuous Integration Environment - SonarQube in CI - Integrate with VCS Hooks (on Commit, on Pull/Merge Request) -
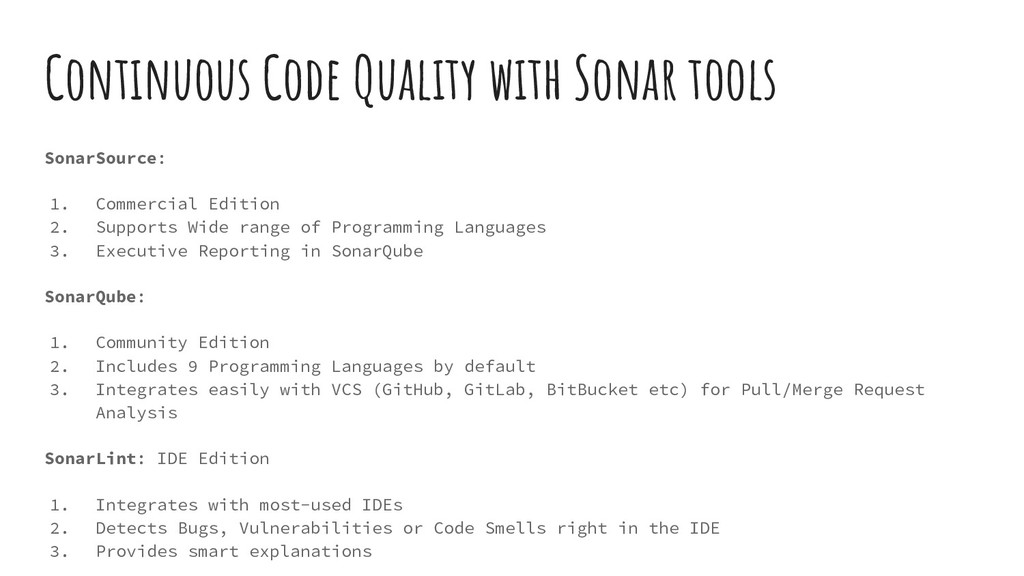
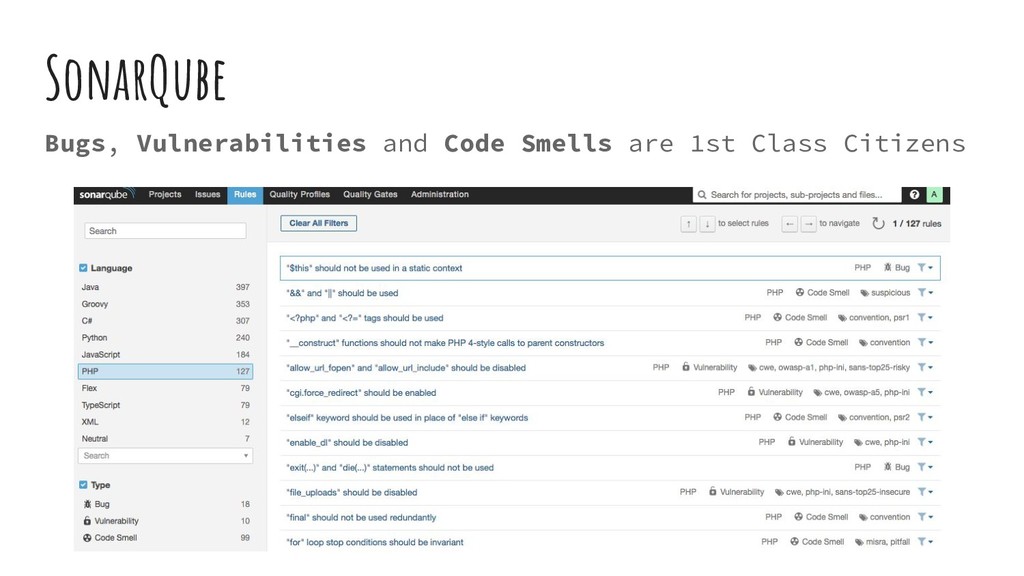
Continuous Code Quality with Sonar tools SonarSource: 1. Commercial Edition
2. Supports Wide range of Programming Languages 3. Executive Reporting in SonarQube SonarQube: 1. Community Edition 2. Includes 9 Programming Languages by default 3. Integrates easily with VCS (GitHub, GitLab, BitBucket etc) for Pull/Merge Request Analysis SonarLint: IDE Edition 1. Integrates with most-used IDEs 2. Detects Bugs, Vulnerabilities or Code Smells right in the IDE 3. Provides smart explanations -
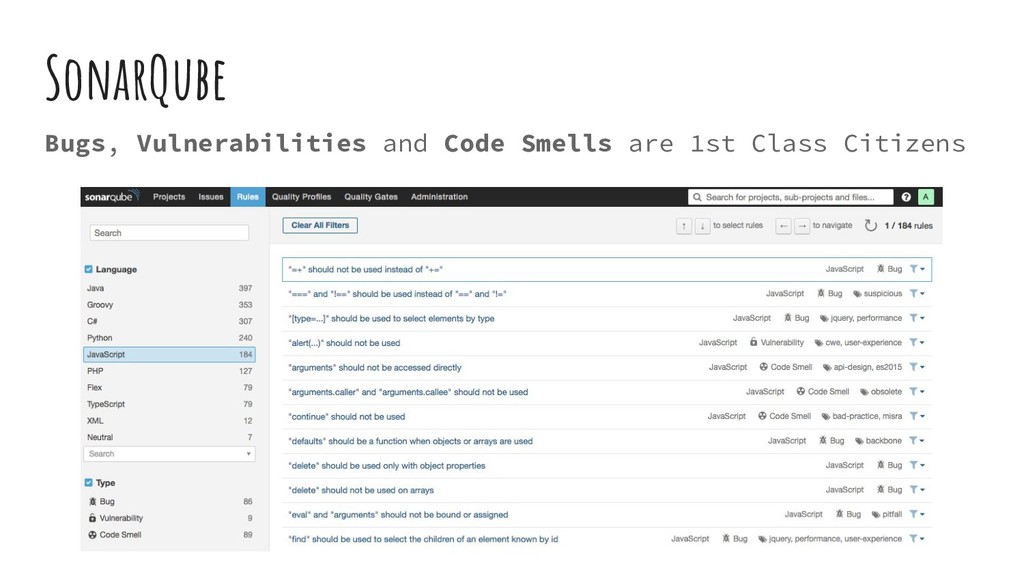
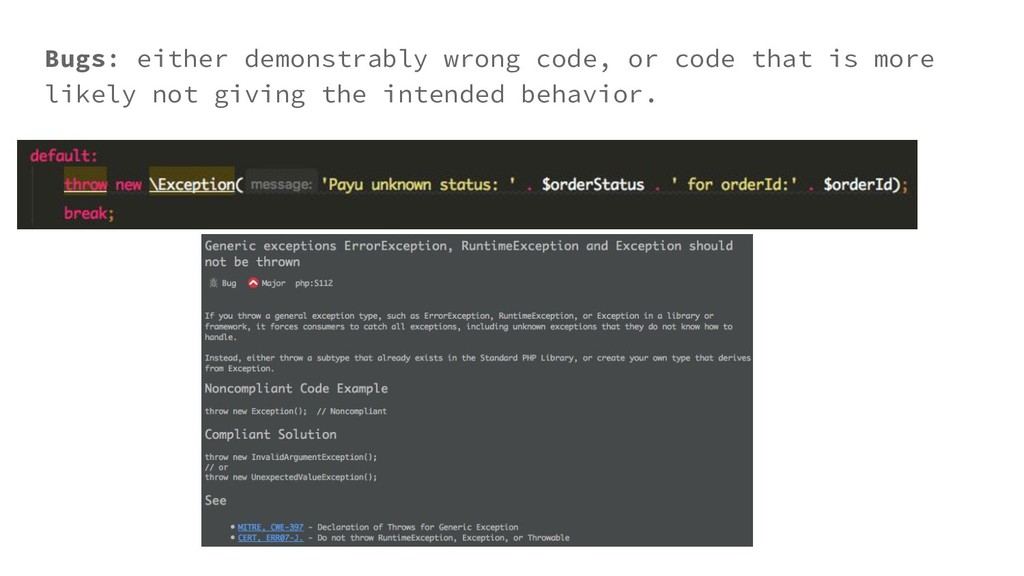
Bugs: either demonstrably wrong code, or code that is more
likely not giving the intended behavior. -
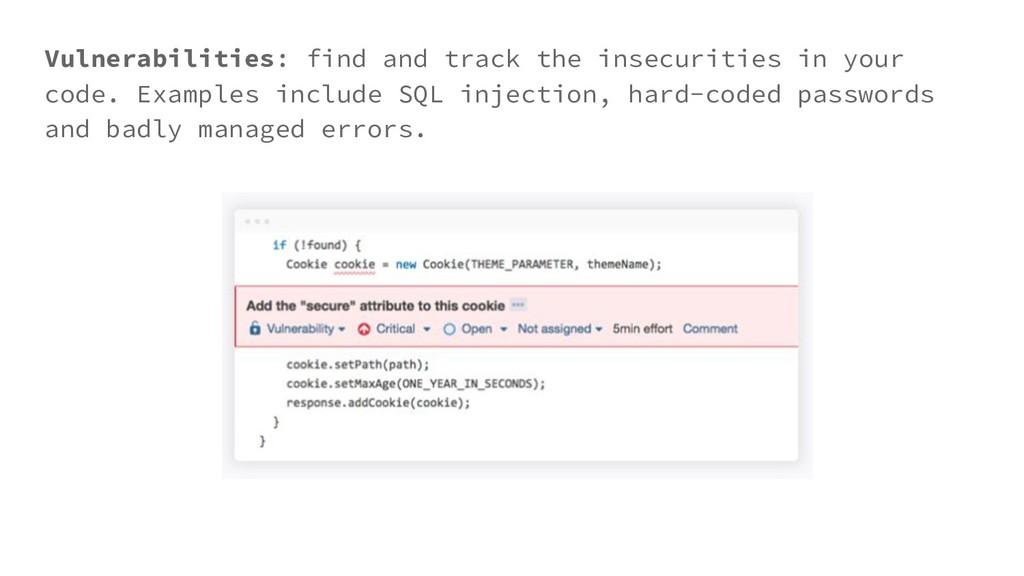
Vulnerabilities: find and track the insecurities in your code. Examples
include SQL injection, hard-coded passwords and badly managed errors. -
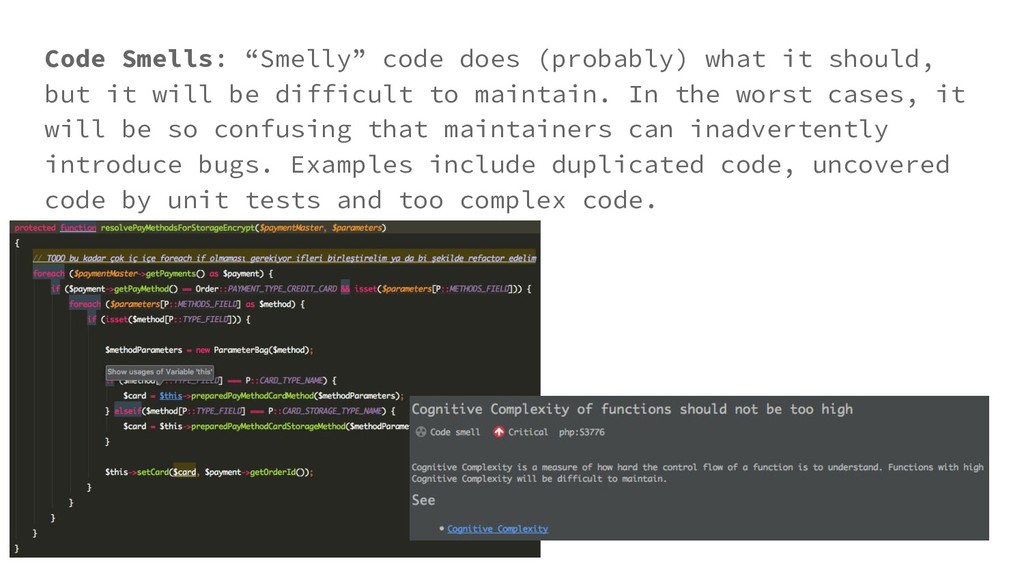
Code Smells: “Smelly” code does (probably) what it should, but
it will be difficult to maintain. In the worst cases, it will be so confusing that maintainers can inadvertently introduce bugs. Examples include duplicated code, uncovered code by unit tests and too complex code. -
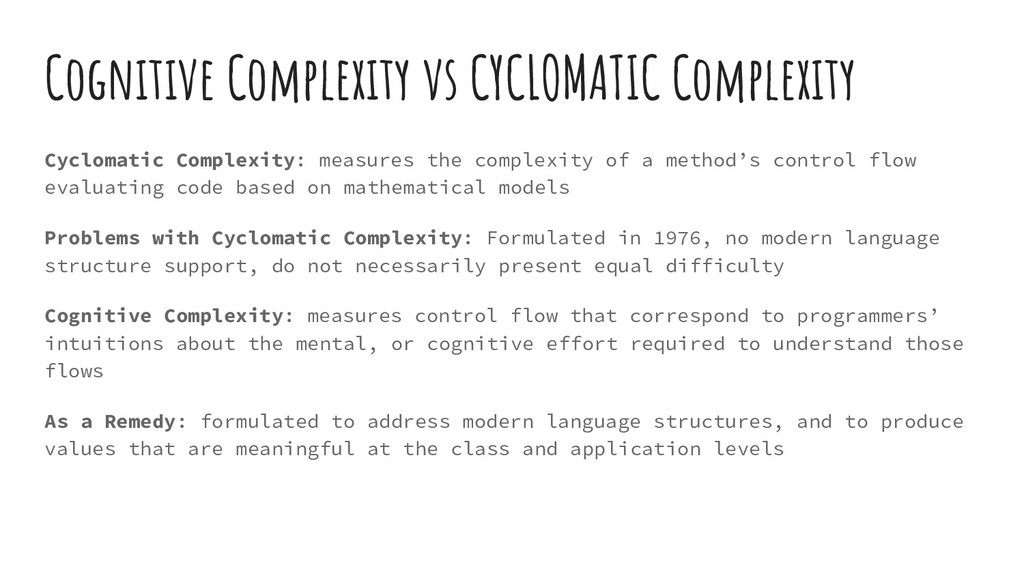
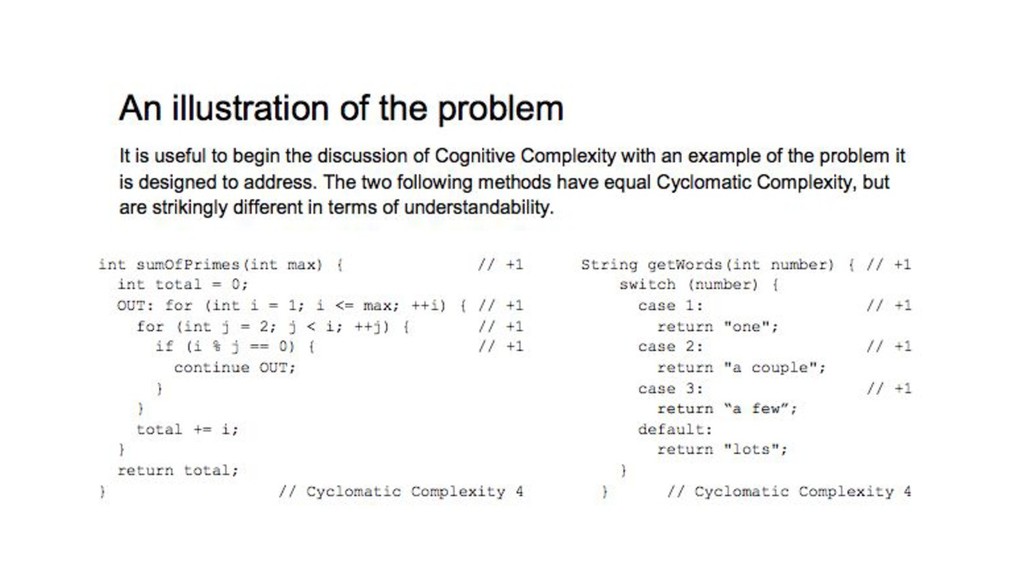
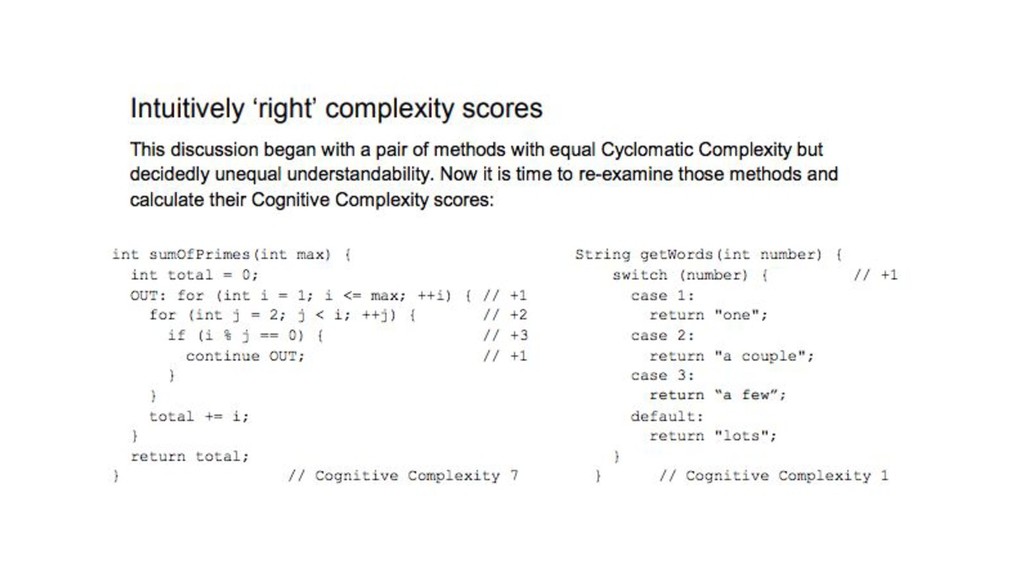
Cognitive Complexity vs CYCLOMATIC Complexity Cyclomatic Complexity: measures the complexity
of a method’s control flow evaluating code based on mathematical models Problems with Cyclomatic Complexity: Formulated in 1976, no modern language structure support, do not necessarily present equal difficulty Cognitive Complexity: measures control flow that correspond to programmers’ intuitions about the mental, or cognitive effort required to understand those flows As a Remedy: formulated to address modern language structures, and to produce values that are meaningful at the class and application levels -
Thank You! References: • http://www.agilebuddha.com/continuous-inspection/continuous-inspection-how -to-define-measure-and-continuously-improve-code-quality/ • https://www.sonarqube.org/ • https://www.sonarsource.com/
• https://www.sonarlint.org/ • https://www.slideshare.net/AhmedMGomaa/sonarqube-overview • https://www.sonarsource.com/docs/CognitiveComplexity.pdf