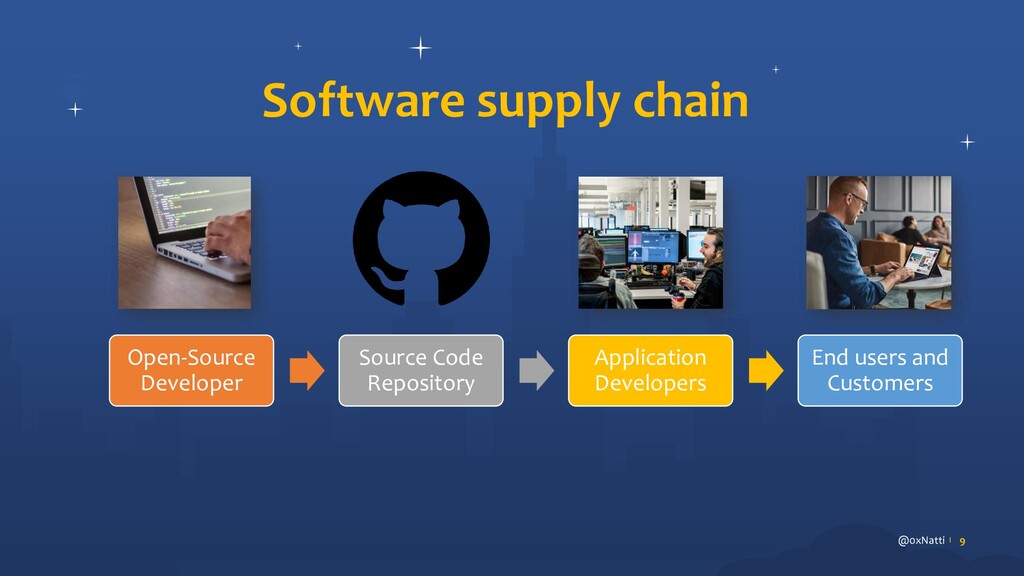
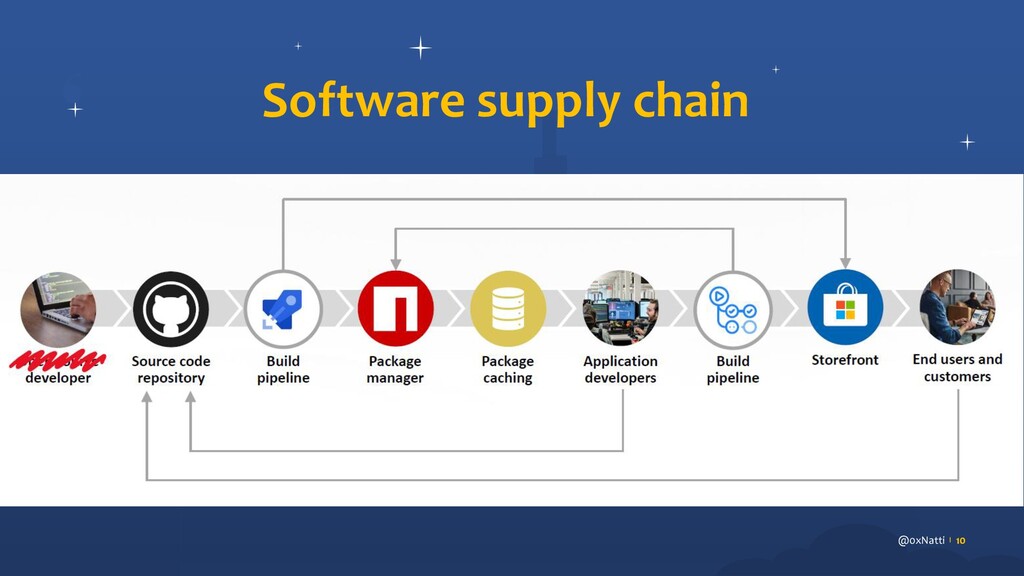
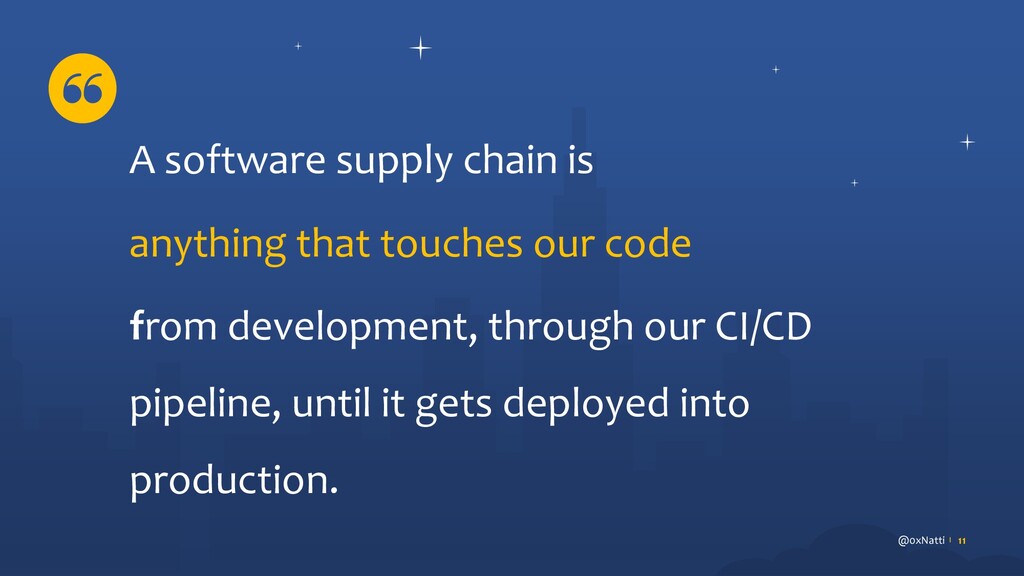
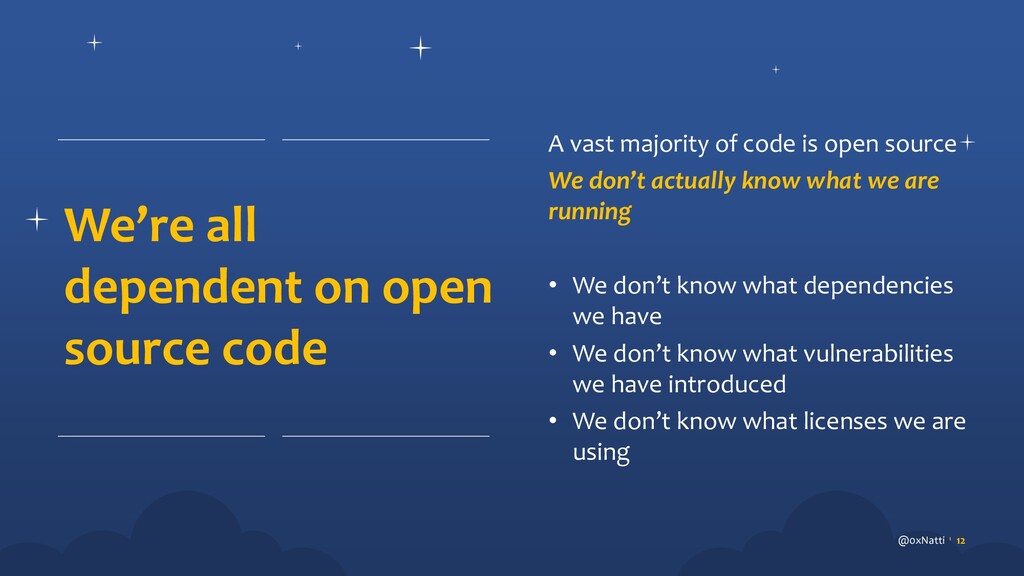
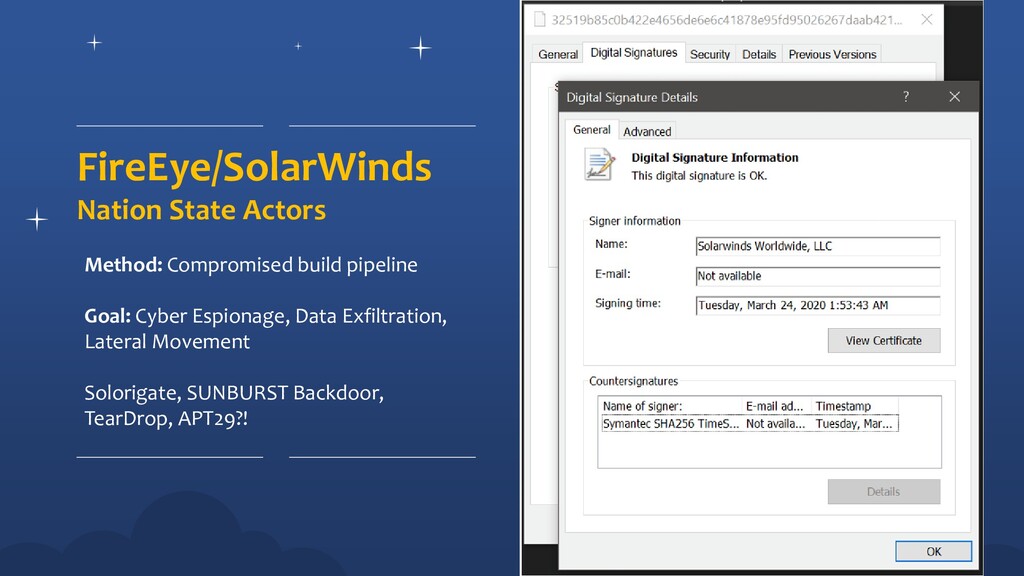
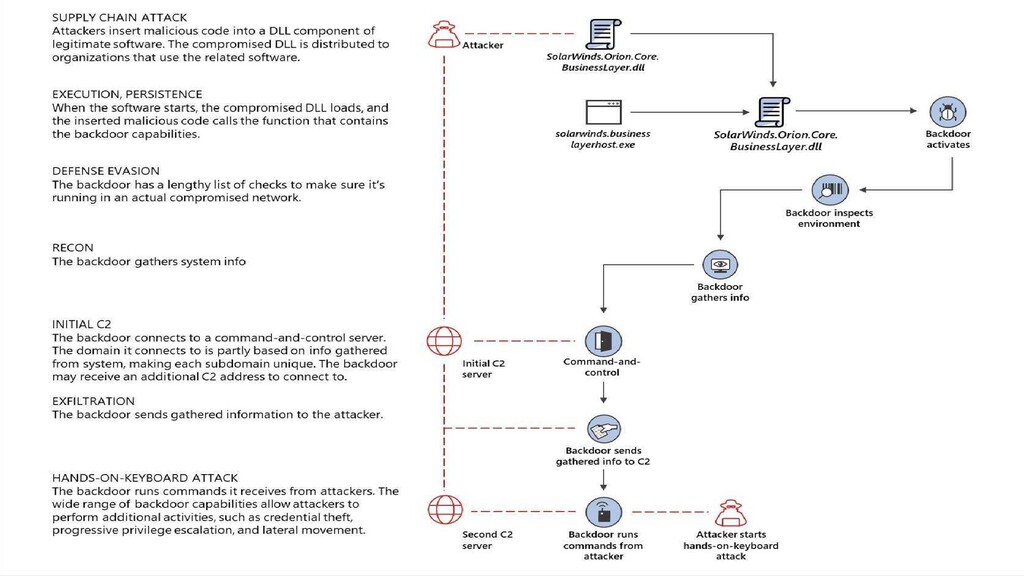
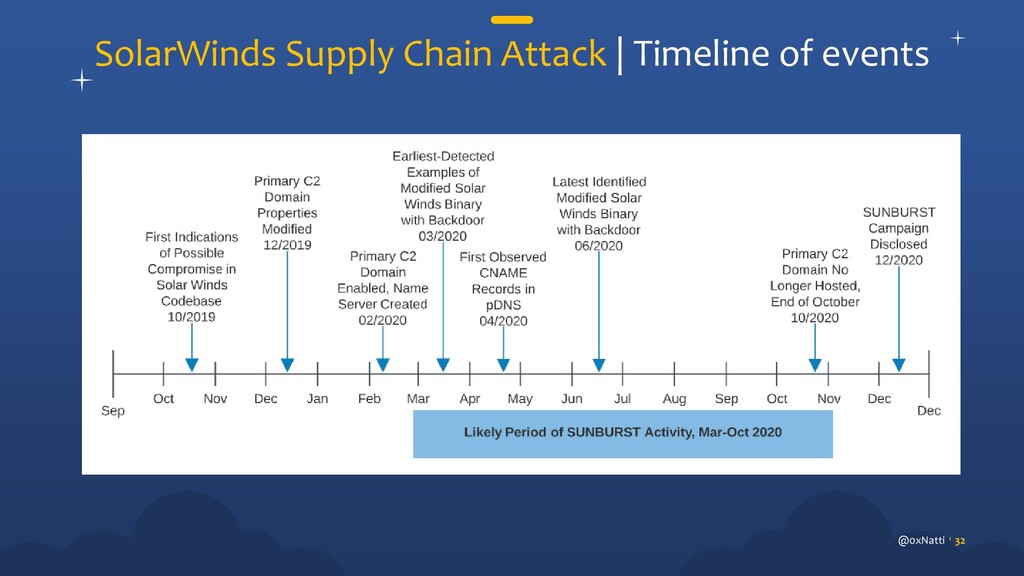
This is my presentation on software supply chain security and containers as a new beast impacting software supply chain security.
This was presented as part of OWASP Hyderabad Chapter December Meet 2020. https://www.meetup.com/hyderabad-owasp-meetup-group/events/275212537/
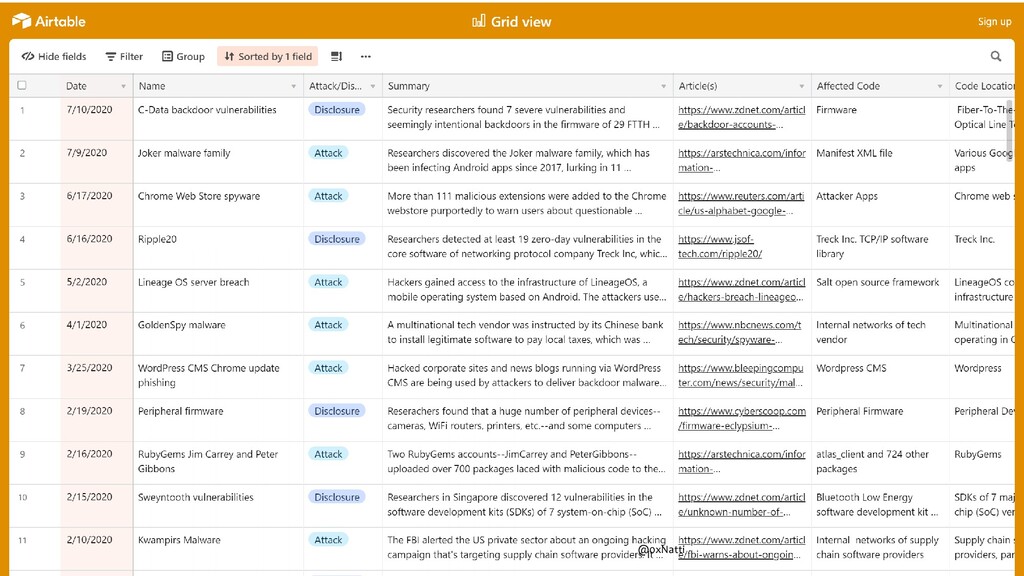
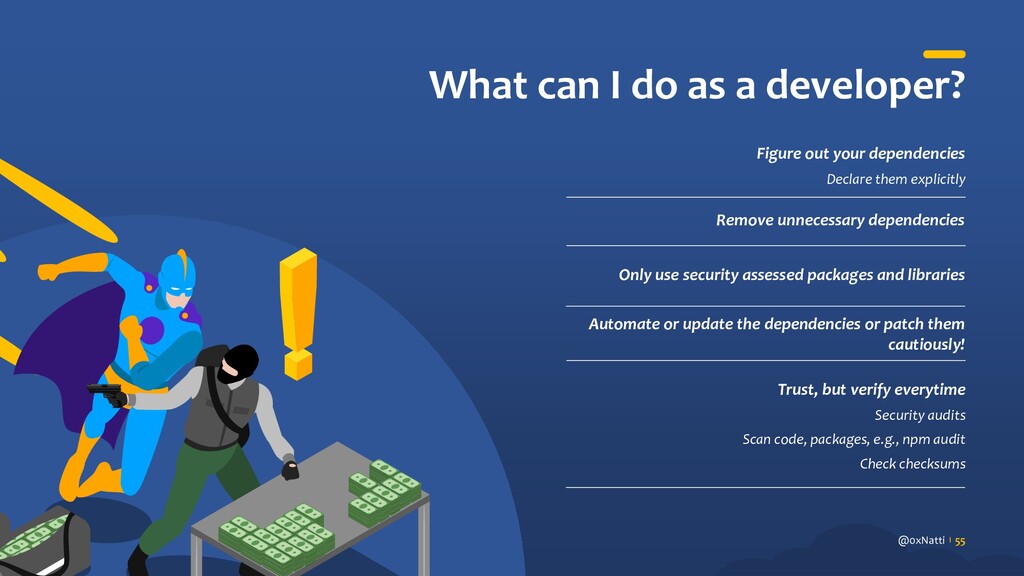
Description: Given the presumed state of Nation state actors conducting supply chain compromise against FireEye and US Govt targets, let's look at what is a software supply chain and what's its significance to enterprise cyber security and application security. Also will focus on what to do as a DevSecOps personnel in order to protect against such attacks and to understand cyber hygiene in this area.


 keeg
 genda
 daidaidai
 yahonda
 stomk
 namiki64
 akhino
 rfdnxbro
 bitkey
 yamad
 finengine
 riyaamemiya
 tanoku
 apolaine
 dougneiner
 akademiya2063
 marktimemedia
 badams
 popppiees
 schroneko
 marketingsoph
 tammyeverts
 baasie
 mfonobong